Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
What Android developers should know about security
Search
Sponsored
·
Ship Features Fearlessly
Turn features on and off without deploys. Used by thousands of Ruby developers.
→
bolot
February 24, 2017
Technology
360
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
What Android developers should know about security
Presented at DevNexus in Atlanta
bolot
February 24, 2017
Transcript
37 slides
What Android Developers Should Know About Security
Bolot Kerimbaev Android and iOS instructor and developer
Android App Developers https://www.bignerdranch.com/app-development/case-studies/
What Is Security?
None
What Is Security? • Confidentiality • Integrity • Availability
What Is Security? • Threats • Risks • Responses •
Remediations
Threat model • Malicious apps • Stolen phones • Wi-Fi
hotspots • Malicious HTML, SMS
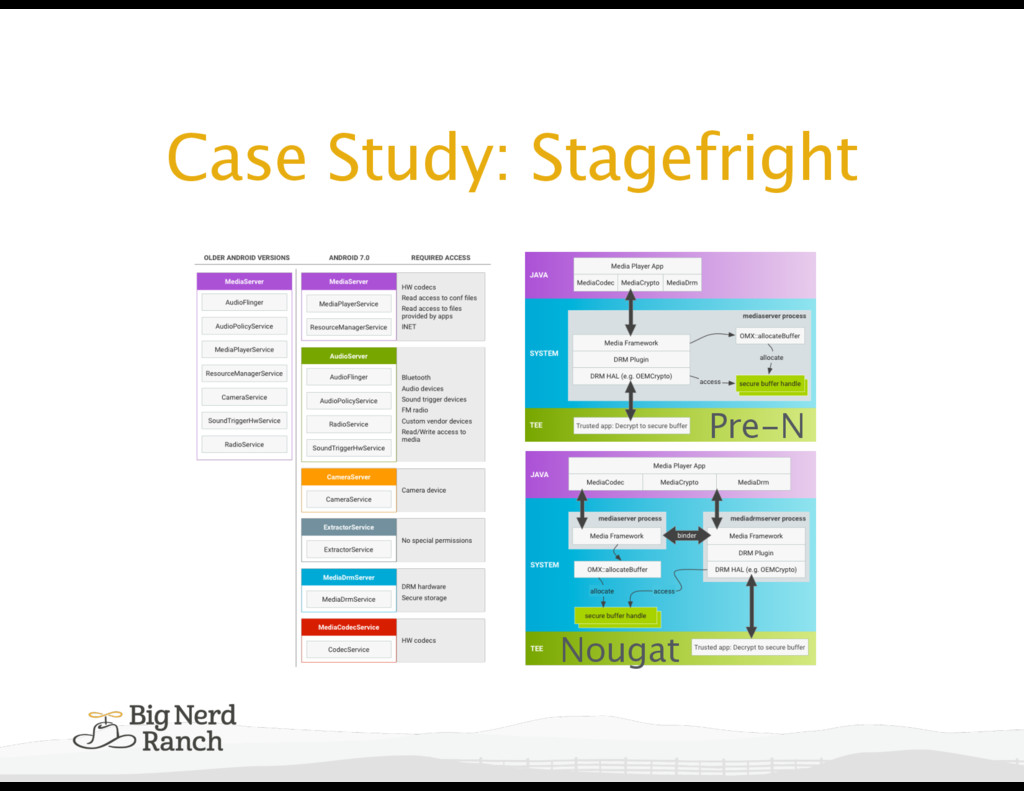
Case Study: Stagefright • Media server framework • Attack via
malicious MMS • Remote code execution • Privilege escalation • Publicly disclosed July 2015 • Apps are impacted
Demolition Man, 1993
Android Security
Android Security • Application Signing • (SE)Linux • Permissions •
Interprocess Communication • Verified Boot
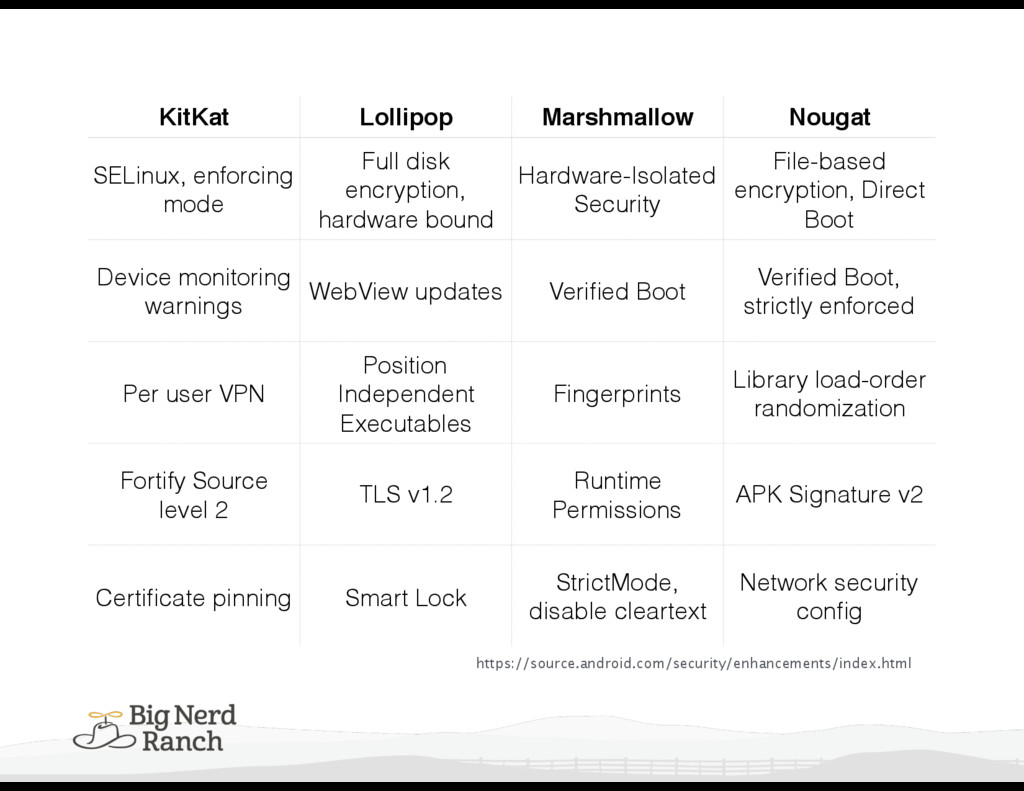
KitKat Lollipop Marshmallow Nougat SELinux, enforcing mode Full disk encryption,
hardware bound Hardware-Isolated Security File-based encryption, Direct Boot Device monitoring warnings WebView updates Verified Boot Verified Boot, strictly enforced Per user VPN Position Independent Executables Fingerprints Library load-order randomization Fortify Source level 2 TLS v1.2 Runtime Permissions APK Signature v2 Certificate pinning Smart Lock StrictMode, disable cleartext Network security config https://source.android.com/security/enhancements/index.html
Challenges • Fragmentation • Google vs OEMs vs Carriers vs
Qualcomm • Vulnerabilities
Case Study: Stagefright Pre-N Nougat
Who Cares About Security?
Security and Design • Most people think it’s important •
Cannot be applied at the end • Changes can be costly if not planned
None
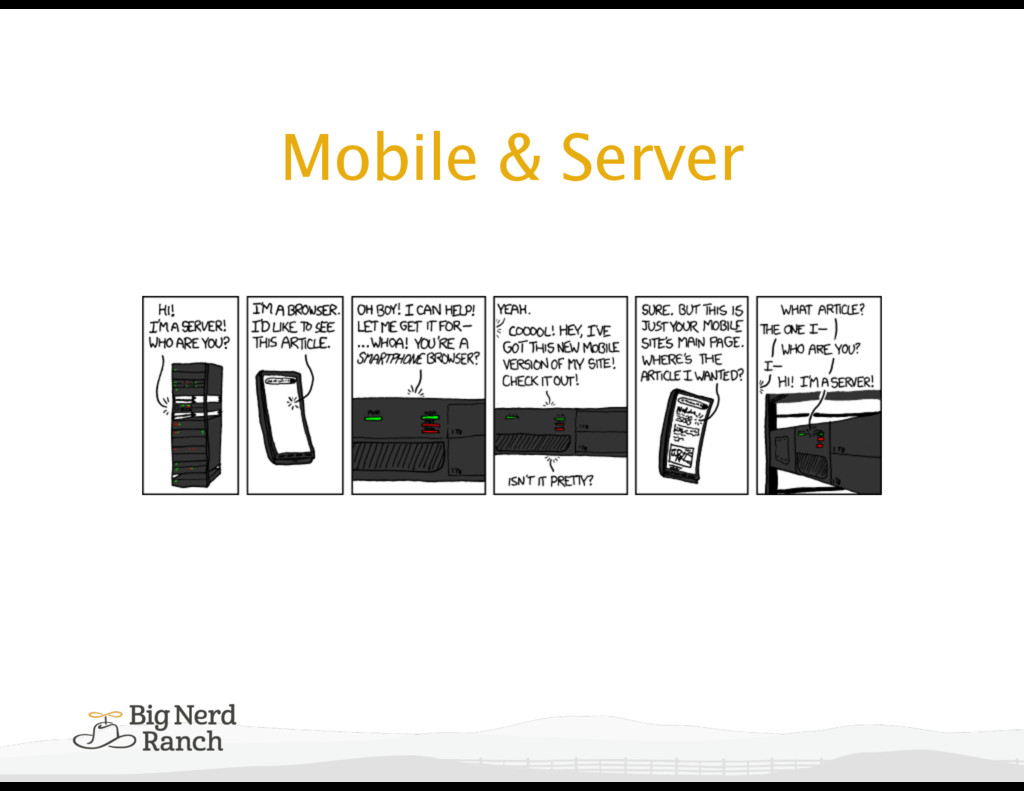
Mobile & Server
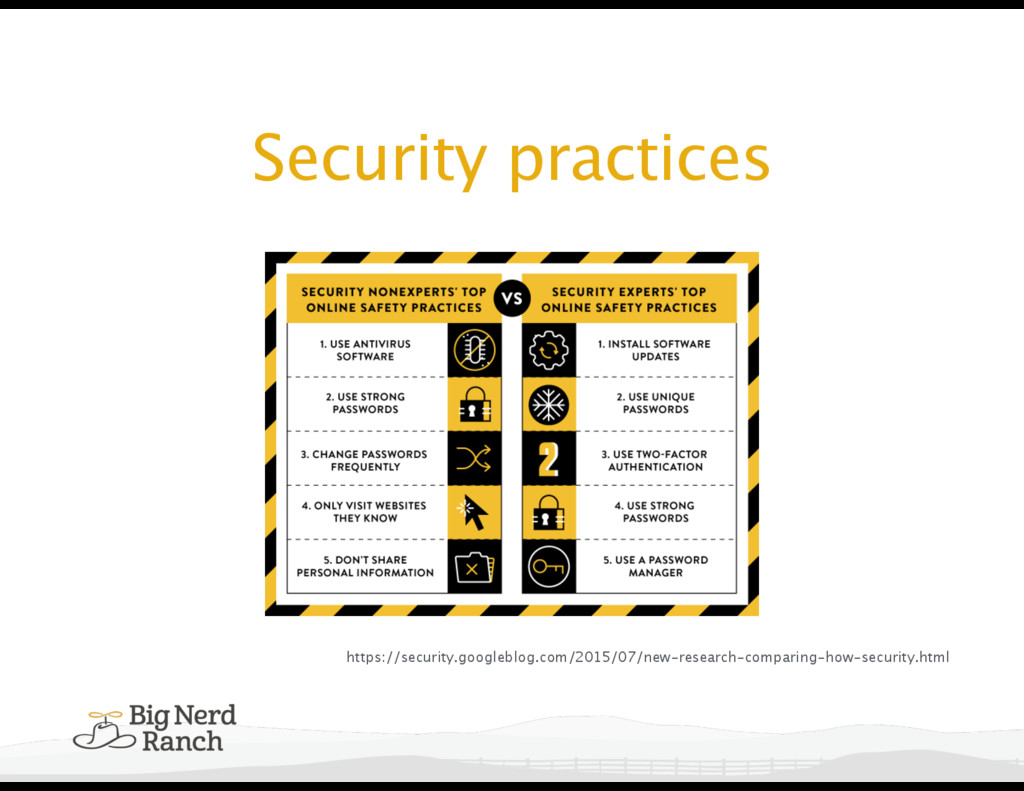
Security practices https://security.googleblog.com/2015/07/new-research-comparing-how-security.html
Security practices • Software Updates • Password Manager • 2-Factor
Authentication
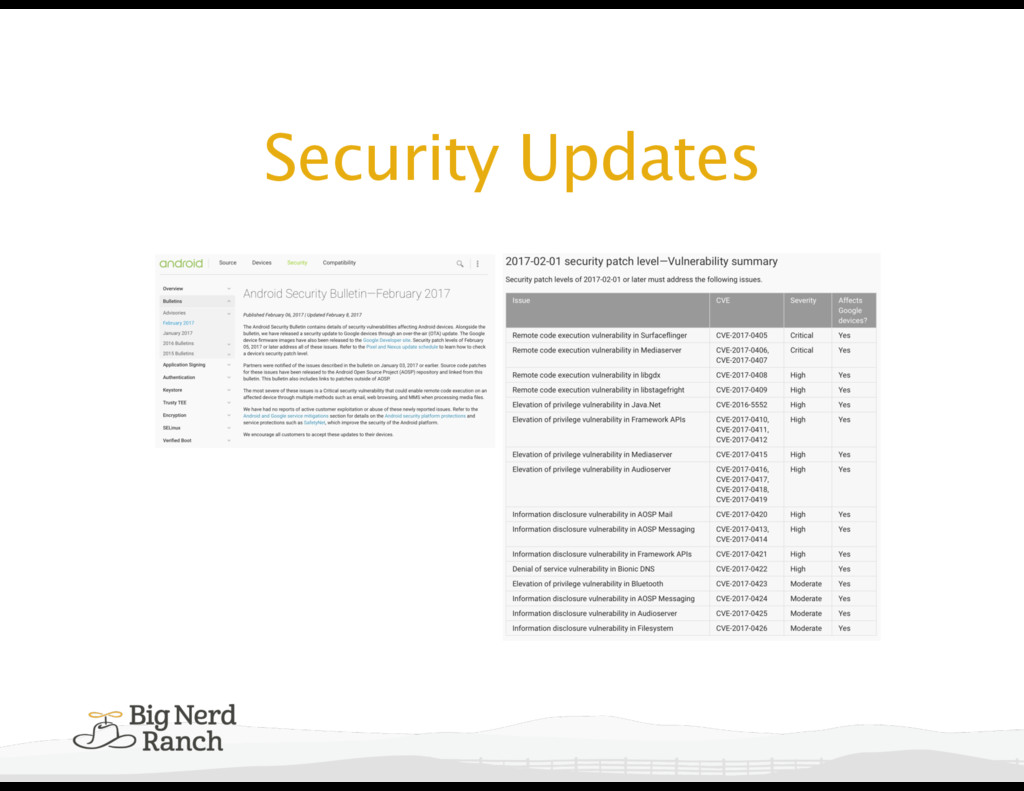
Security Updates
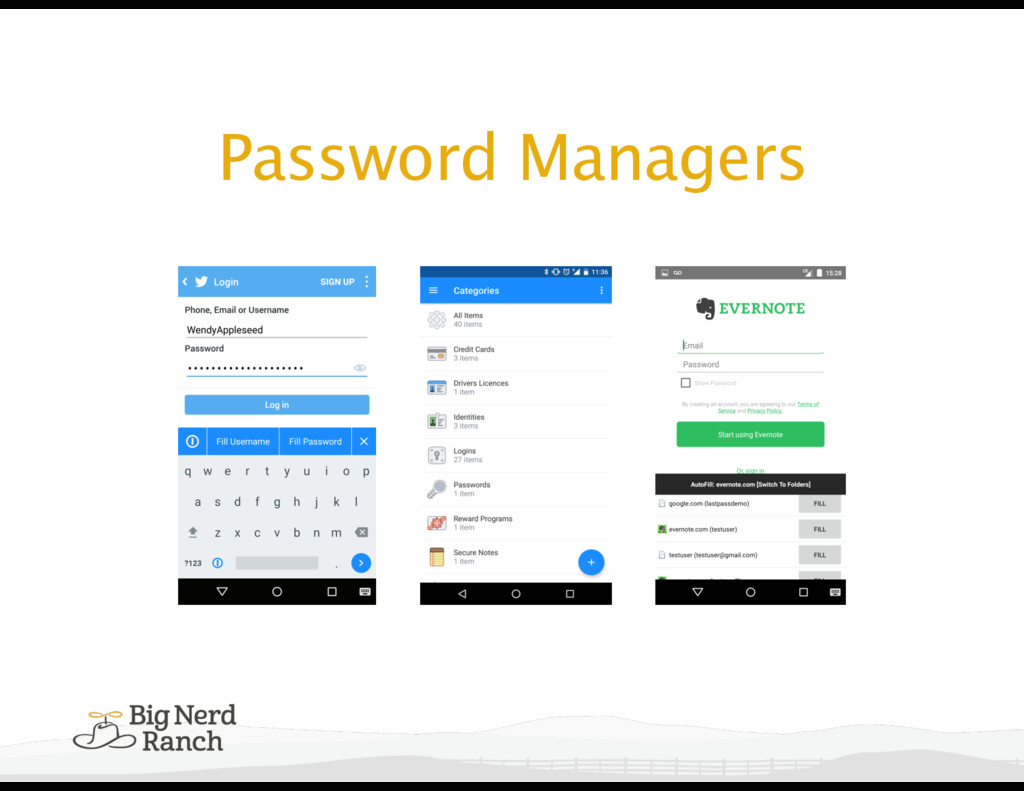
Password Managers
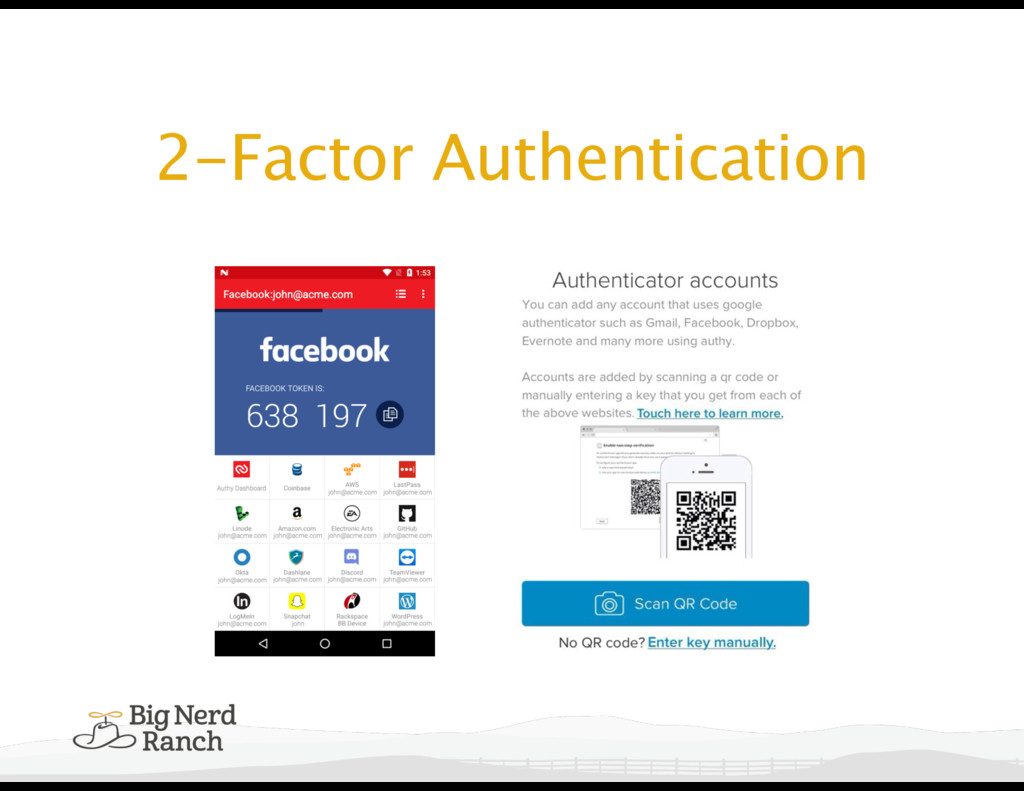
2-Factor Authentication
Security practices • Software Updates • Password Manager • 2-Factor
Authentication • VPN • Backups • Leak Notifications
What Can App Developers Do?
Checklists • Android Security Checklist • Industry Specific: PCI, HIPAA
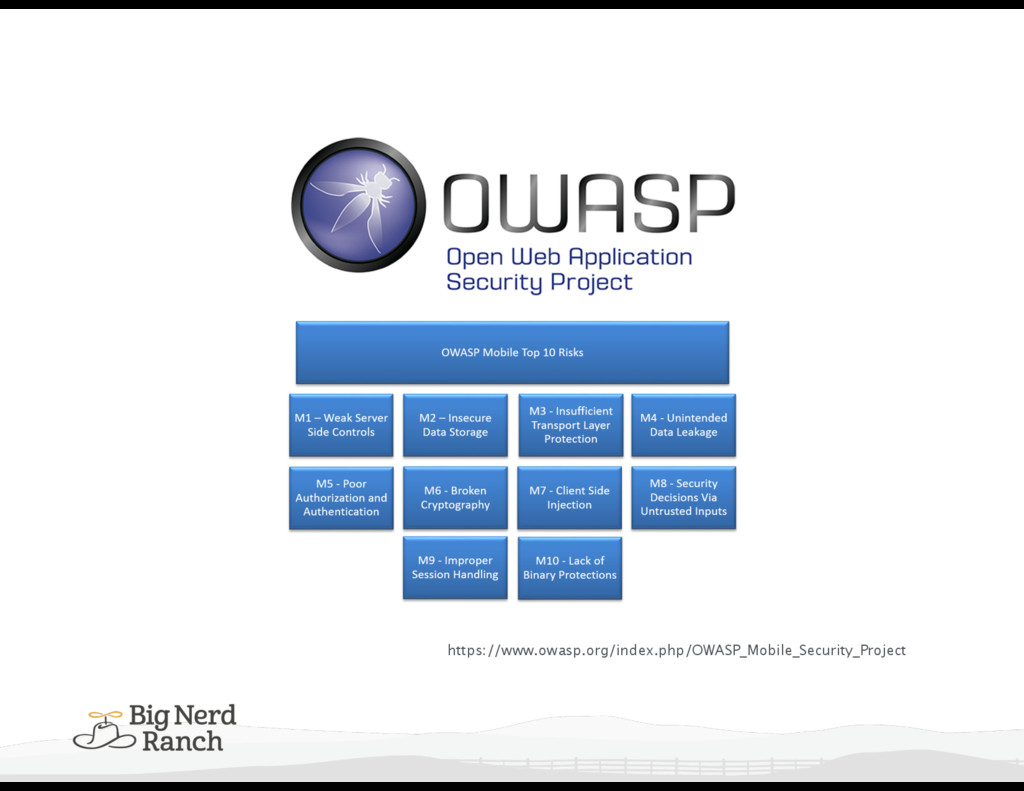
• OWASP
https://www.owasp.org/index.php/OWASP_Mobile_Security_Project
Software Updates • Follow best practices, plan for upgrades •
Train engineers • Perform audits • APIs: evolution, deprecation • Keep up with tools updates
Password Management • Integrate with password managers • Implement single
sign-on, OAuth, etc. • Don’t use device ID • Don’t store passwords • Careful about custom password text fields
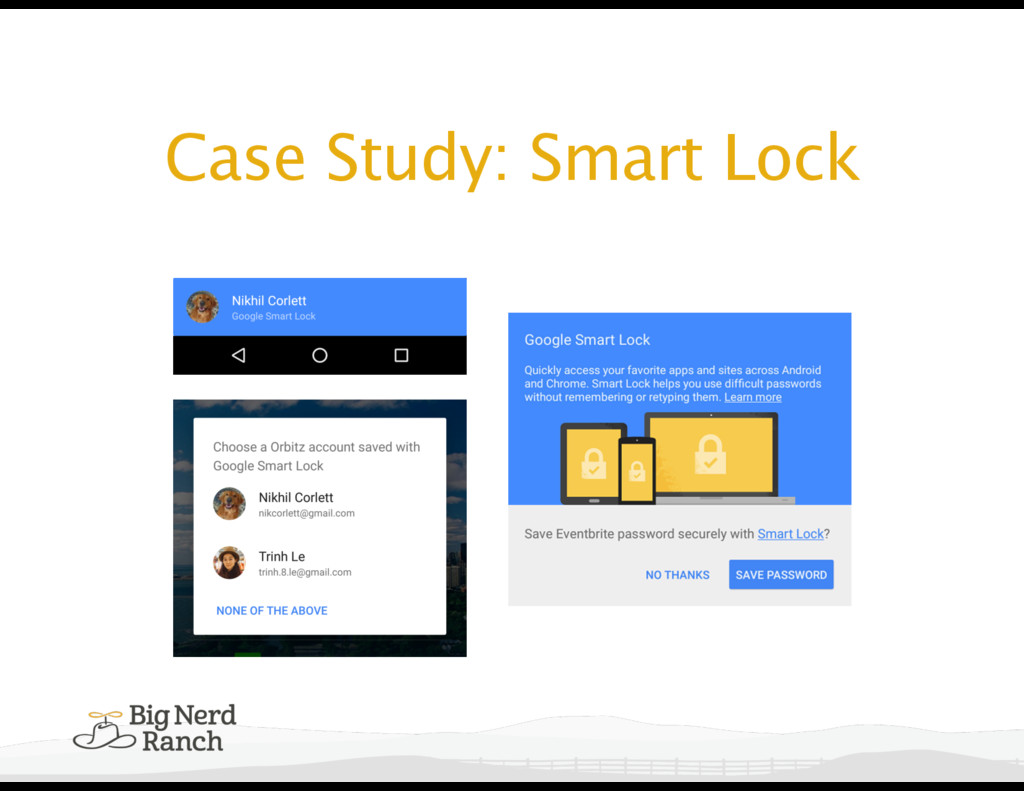
Case Study: Smart Lock
2-Factor Authentication • TOTP (Google Authenticator, Authy) • FIDO U2F
(Yubikey) • Don’t use SMS
Secure Communication • Use HTTPS (TLS) everywhere • Enable Network
Security Configuration • Certificate pinning
Protect User Data • Secure storage • Easy backups and
data restoration • Cryptography
Vulnerability Reporting • Make it easy to report issues in
your app • Track vulnerabilities
What Can Developers Do? • Practice security as a user
• Optimize for best security practices • Training • Checklists • Audits, Reviews
Questions? • @bolot • @bignerdranch • Android Security course, Q3
2017
More Decks by bolot
See All by bolot
Coroutines: Kotlin Versus DCSF18
bolot
2
950
MLKit DevFest18 ATL
bolot
0
210
Kotlin Coroutines: Beyond async-await
bolot
2
730
Kotlin - Class Destroyer
bolot
0
680
Secure Networking, Connect Tech 2017
bolot
0
120
Defensive Android Security
bolot
0
150
android transition framework
bolot
0
190
Other Decks in Technology
See All in Technology
人の努力に頼らないセキュリティをエンジニアリングする在り方 / An approach to engineering security that does not rely on human effort
carta_engineering
0
240
飯から始まるデータエンジニア
sansantech
PRO
0
130
Oracle Base Database Service 技術詳細
oracle4engineer
PRO
17
120k
エンタープライズ事業未経験のデータ屋、 AI時代にN回撃沈する.pdf
ryoskdara_
0
190
HTTP QUERY時代の型安全な検索APIをKotlinで設計する
sansantech
PRO
1
120
kubellの最新データ分析環境
kubell_hr
2
250
AWS Blocksで AIエージェント作れるの知ってます?
kmiya84377
1
160
閉域網でのAPI公開の選択肢全部比較!
takano0131
5
690
実測データからサービスの成長余力を測る。負荷シナリオ・テストデータ・限界値の設計
kazatohiei
0
160
CloudTrail を推したい
kazzpapa3
1
160
Terraform 0 to 100:100個以上のリポジトリを常に最新にし続けるための自動化
sue445
3
1.4k
AWS DevOps Agentの構造から読み解く運用 AI エージェントの設計原則/aws-devops-agent-design-principles
tomoki10
0
240
Featured
See All Featured
The Art of Delivering Value - GDevCon NA Keynote
reverentgeek
16
2.2k
The Anti-SEO Checklist Checklist. Pubcon Cyber Week
ryanjones
0
310
Rails Girls Zürich Keynote
gr2m
96
14k
Odyssey Design
rkendrick25
PRO
3
970
Measuring Dark Social's Impact On Conversion and Attribution
stephenakadiri
2
330
AI Search: Implications for SEO and How to Move Forward - #ShenzhenSEOConference
aleyda
1
1.4k
CoffeeScript is Beautiful & I Never Want to Write Plain JavaScript Again
sstephenson
162
16k
4 Signs Your Business is Dying
shpigford
187
23k
Why You Should Never Use an ORM
jnunemaker
PRO
61
10k
Introduction to Domain-Driven Design and Collaborative software design
baasie
1
1.1k
Done Done
chrislema
187
17k
The Invisible Side of Design
smashingmag
301
52k


 bolot
 carta_engineering
 sansantech
 oracle4engineer
 ryoskdara_
 kubell_hr
 kmiya84377
 takano0131
 kazatohiei
 kazzpapa3
 sue445
 tomoki10
 reverentgeek
 ryanjones
 gr2m
 rkendrick25
 stephenakadiri
 aleyda
 sstephenson
 shpigford
 jnunemaker
 baasie
 chrislema
 smashingmag