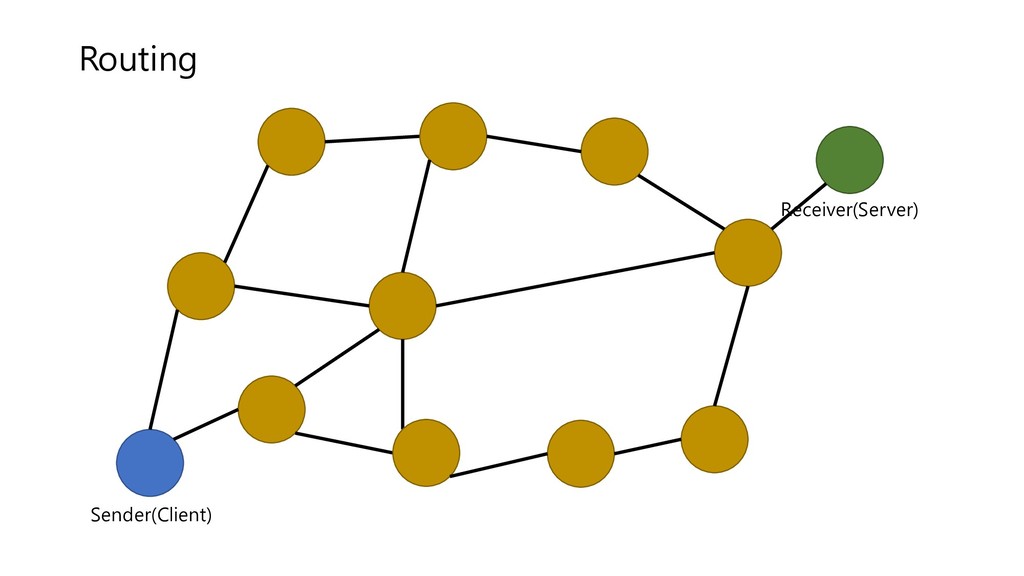
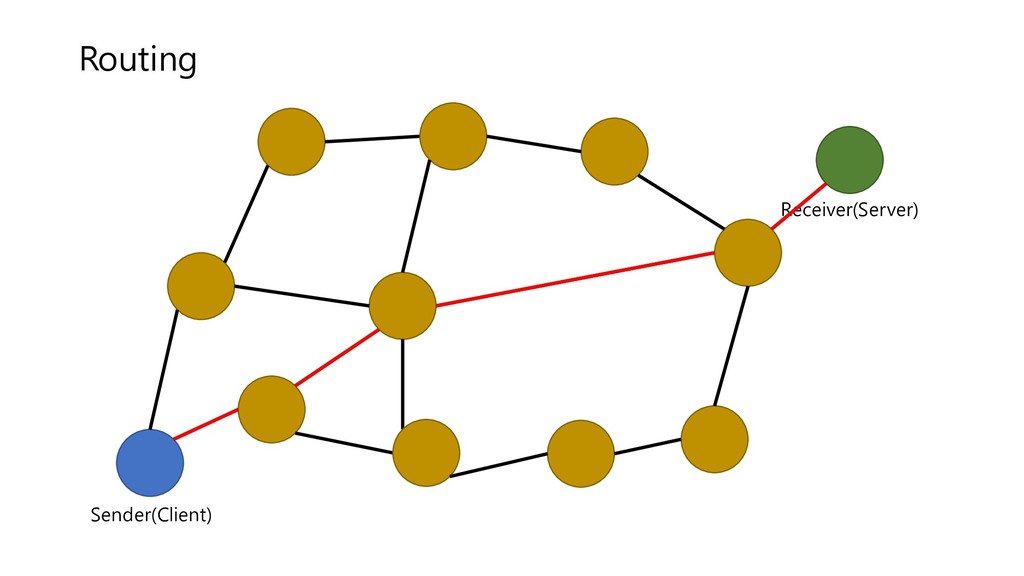
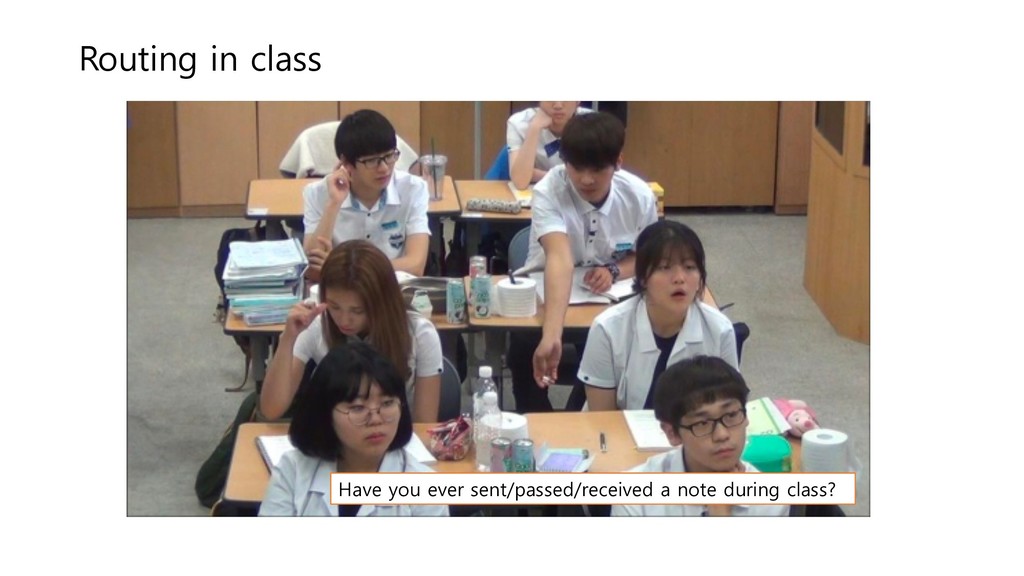
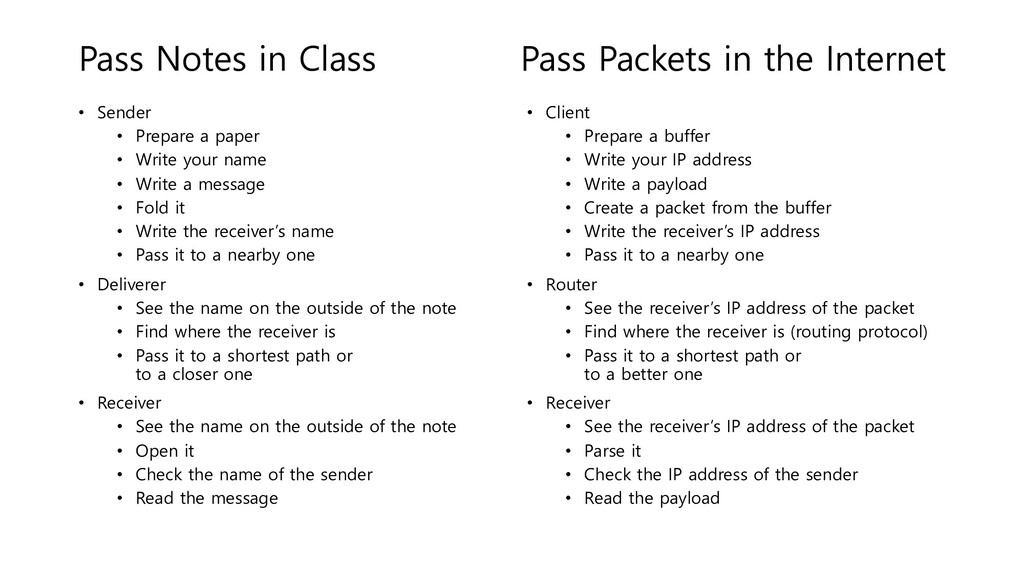
• Write your name • Write a message • Fold it • Write the receiver’s name • Pass it to a nearby one • Deliverer • See the name on the outside of the note • Find where the receiver is • Pass it to a shortest path or to a closer one • Receiver • See the name on the outside of the note • Open it • Check the name of the sender • Read the message
• Write your name • Write a message • Fold it • Write the receiver’s name • Pass it to a nearby one • Deliverer • See the name on the outside of the note • Find where the receiver is • Pass it to a shortest path or to a closer one • Receiver • See the name on the outside of the note • Open it • Check the name of the sender • Read the message • Client • Prepare a buffer • Write your IP address • Write a payload • Create a packet from the buffer • Write the receiver’s IP address • Pass it to a nearby one • Router • See the receiver’s IP address of the packet • Find where the receiver is (routing protocol) • Pass it to a shortest path or to a better one • Receiver • See the receiver’s IP address of the packet • Parse it • Check the IP address of the sender • Read the payload Pass Packets in the Internet
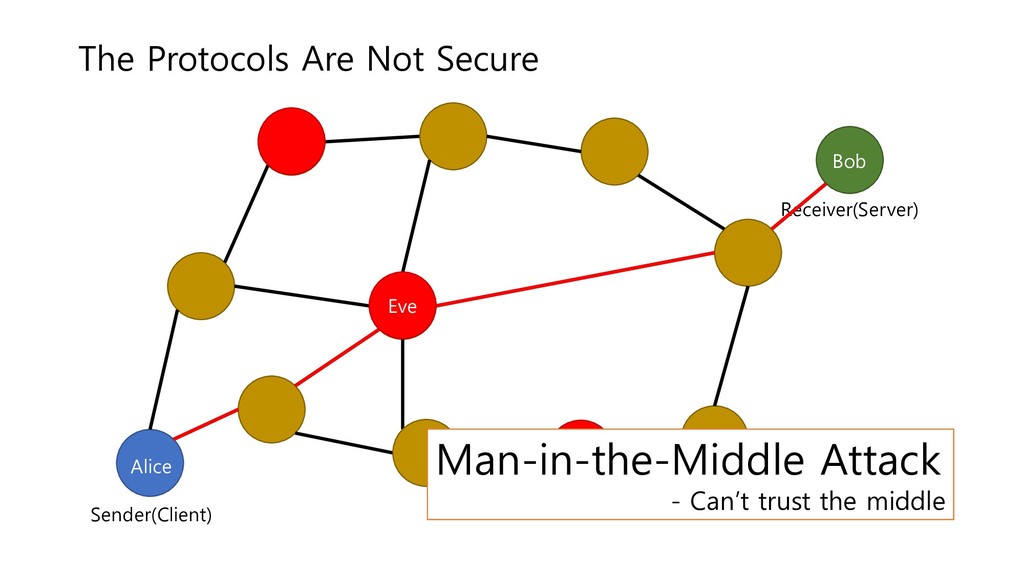
• Write your name • Write a message • Fold it • Write the receiver’s name • Pass it to a nearby one • Deliverer • See the name on the outside of the note • Find where the receiver is • Pass it to a shortest path or to a closer one • Receiver • See the name on the outside of the note • Open it • Check the name of the sender • Read the message • Client • Prepare a buffer • Write your IP address • Write a payload • Create a packet from the buffer • Write the receiver’s IP address • Pass it to a nearby one • Router • See the receiver’s IP address of the packet • Find where the receiver is (routing protocol) • Pass it to a shortest path or to a better one • Receiver • See the receiver’s IP address of the packet • Parse it • Check the IP address of the sender • Read the payload Pass Packets in the Internet Is it secure protocol?
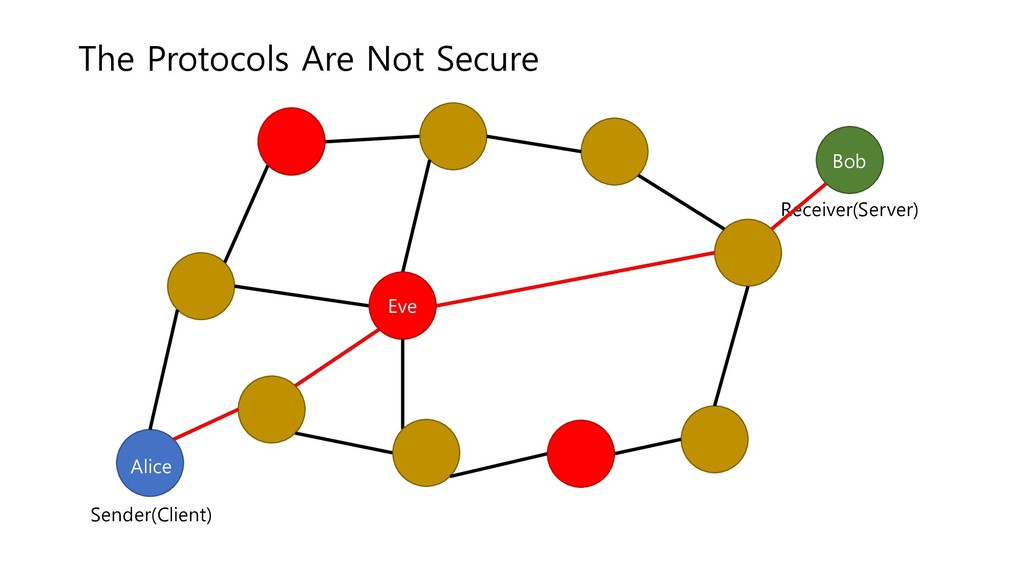
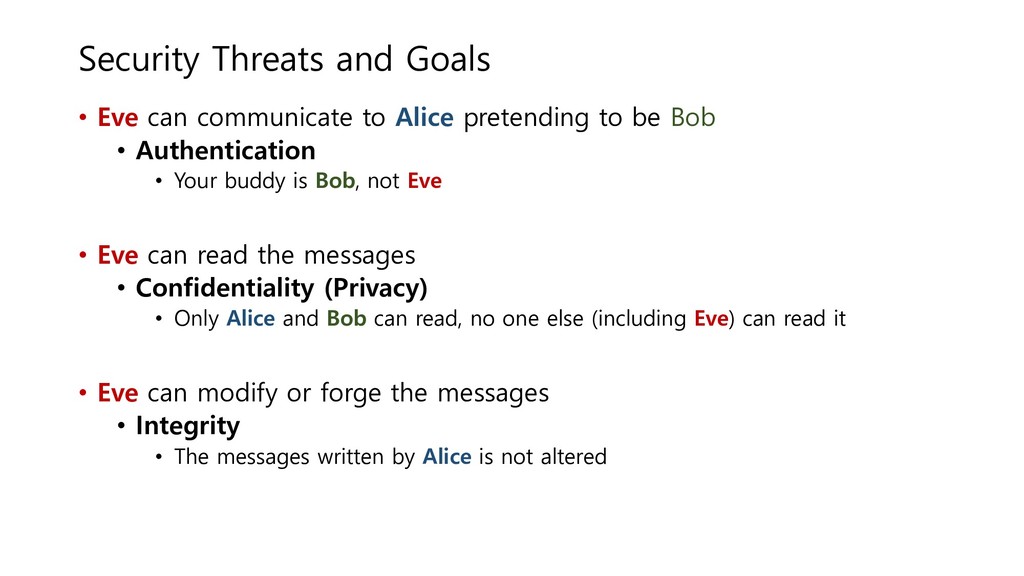
pretending to be Bob • Authentication • Your buddy is Bob, not Eve • Eve can read the messages • Confidentiality (Privacy) • Only Alice and Bob can read, no one else (including Eve) can read it • Eve can modify or forge the messages • Integrity • The messages written by Alice is not altered
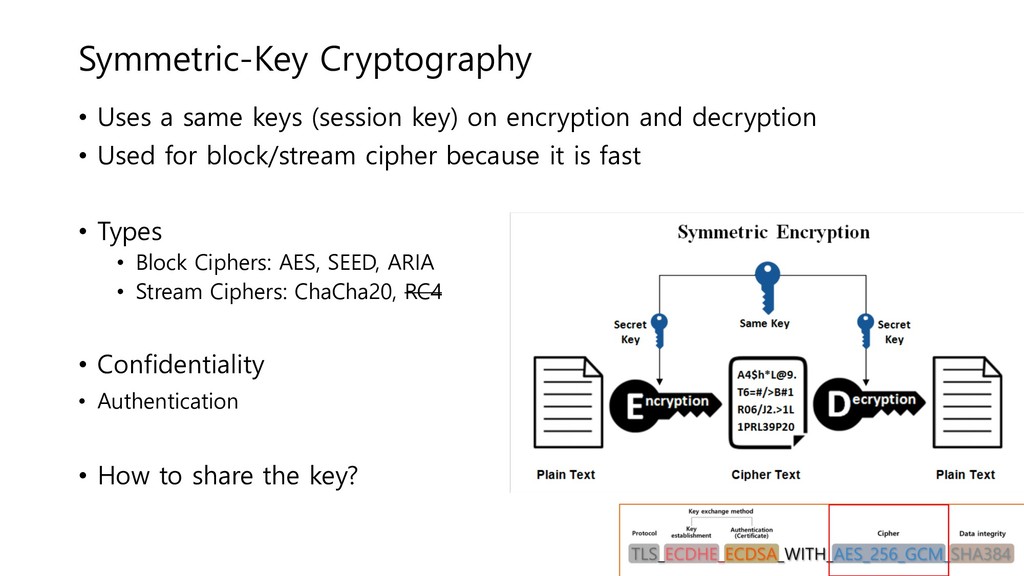
encryption and decryption • Used for block/stream cipher because it is fast • Types • Block Ciphers: AES, SEED, ARIA • Stream Ciphers: ChaCha20, RC4 • Confidentiality • Authentication • How to share the key?
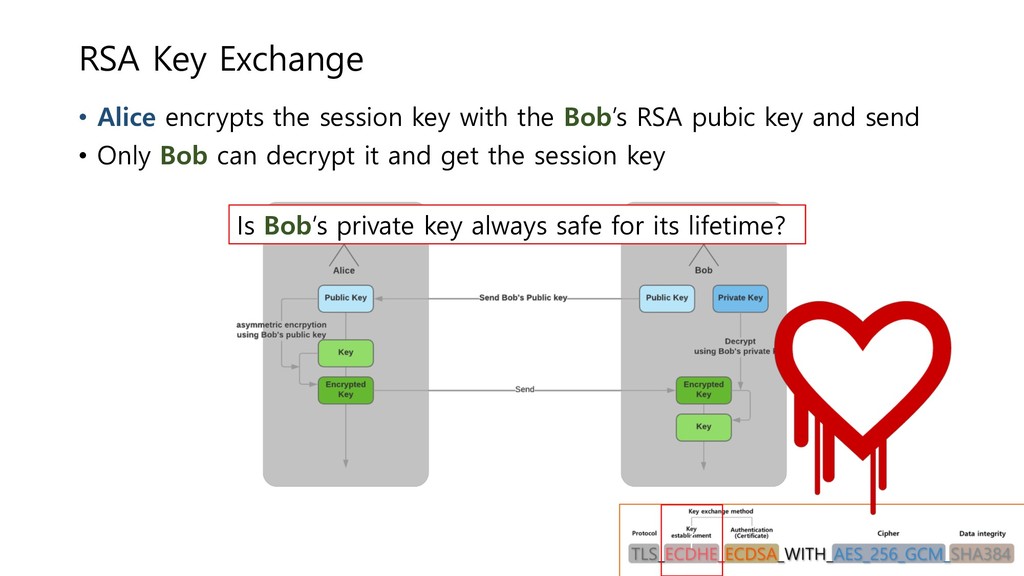
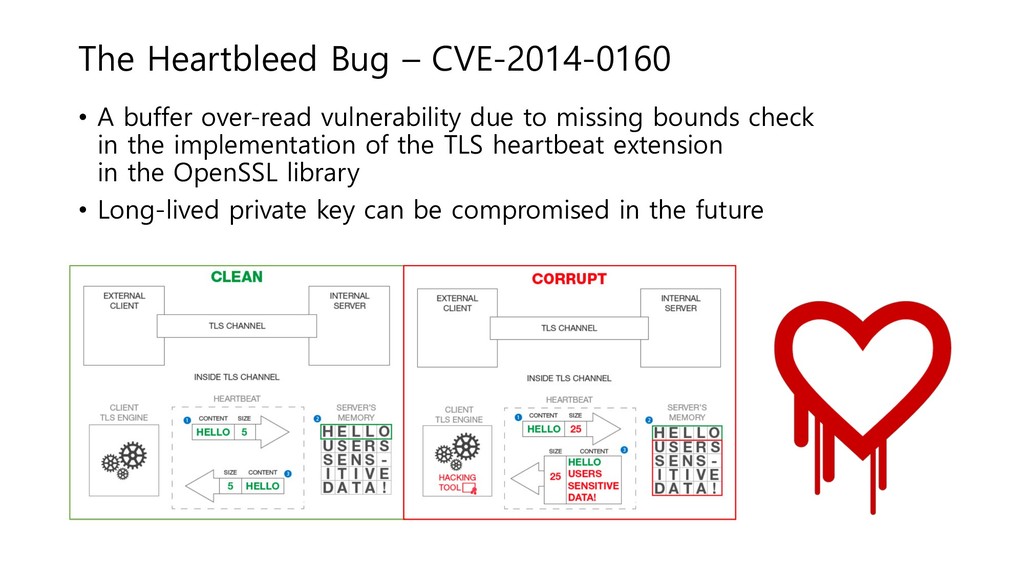
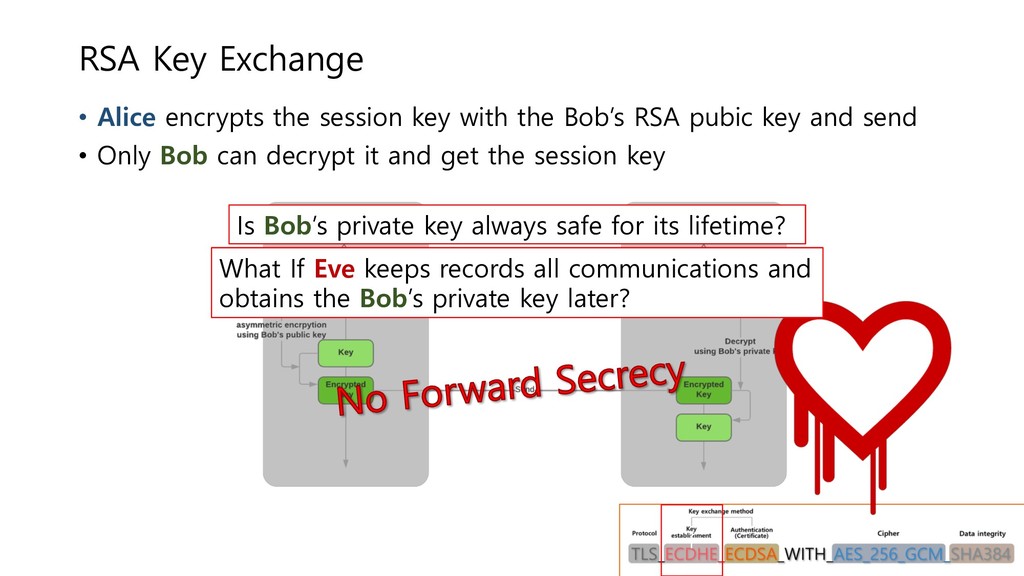
due to missing bounds check in the implementation of the TLS heartbeat extension in the OpenSSL library • Long-lived private key can be compromised in the future
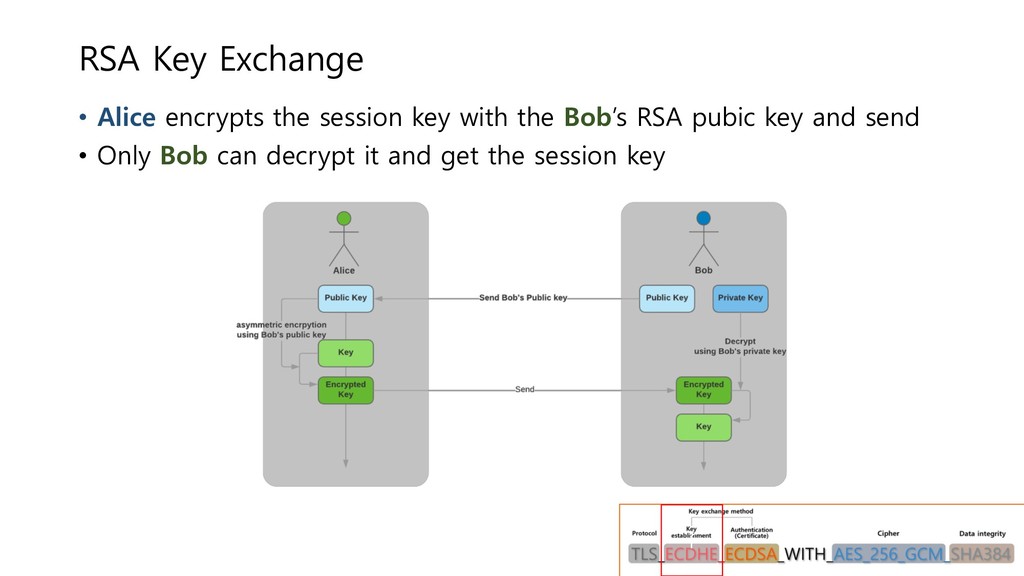
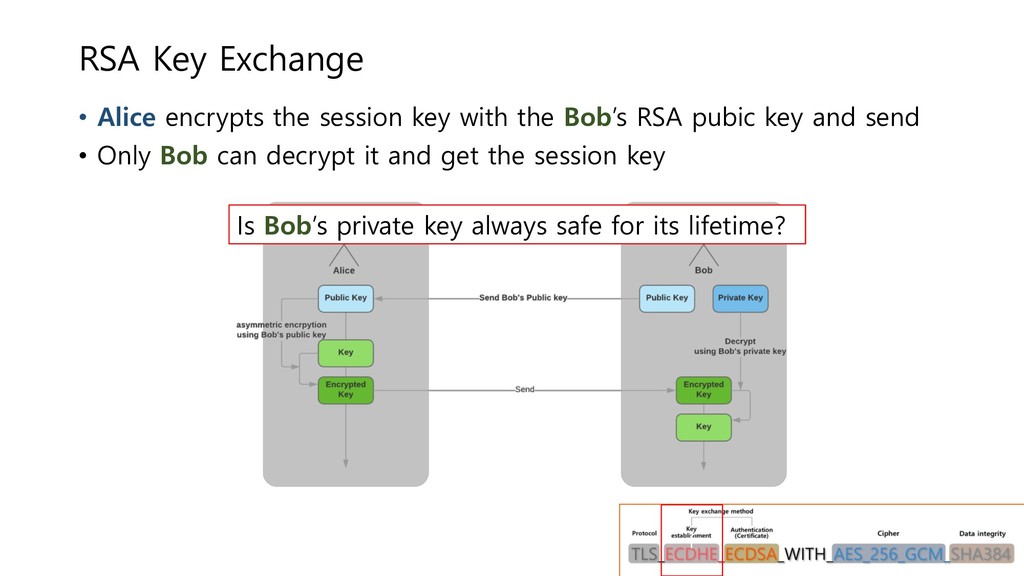
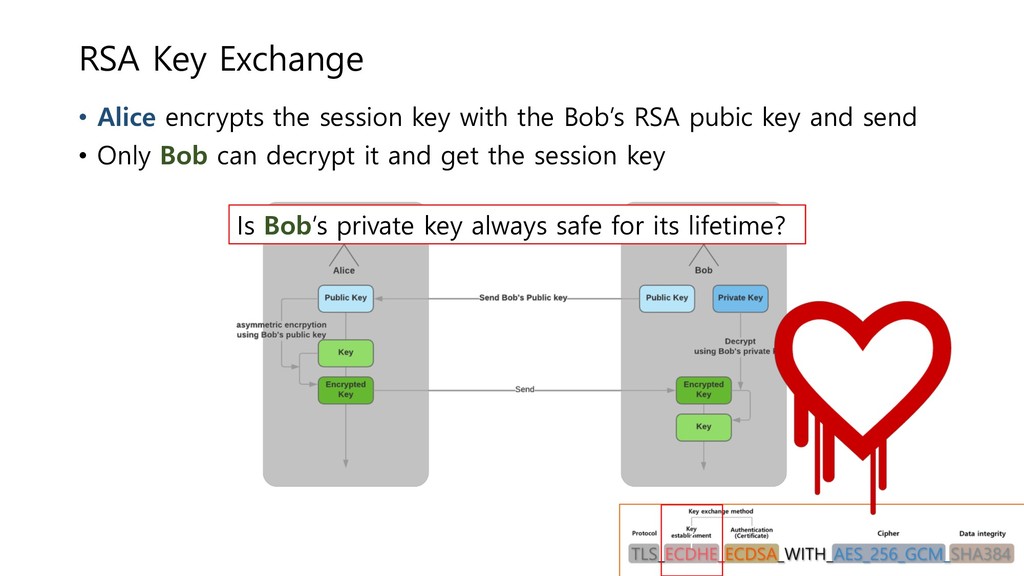
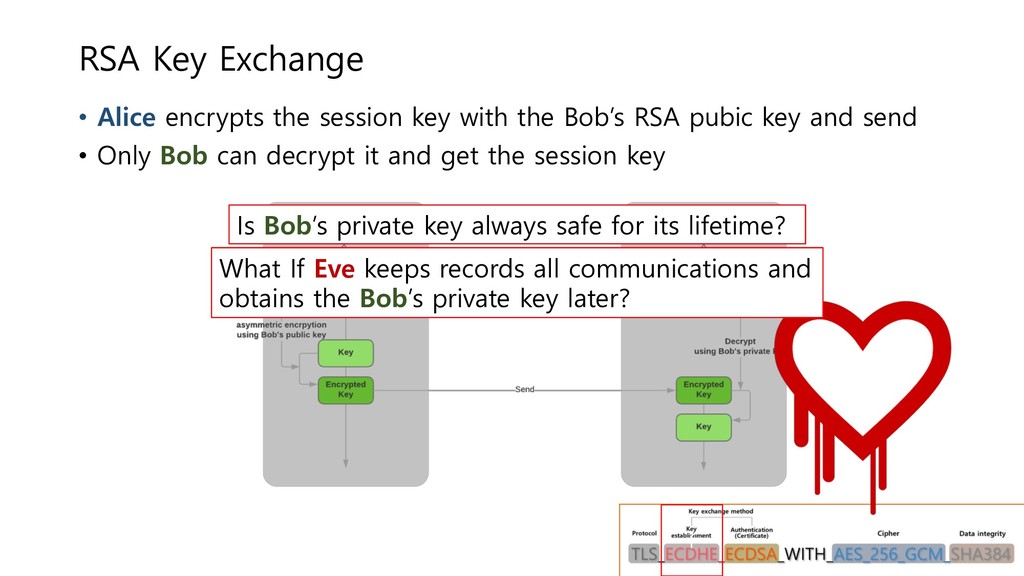
the Bob’s RSA pubic key and send • Only Bob can decrypt it and get the session key f What If Eve keeps records all communications and obtains the Bob’s private key later? Is Bob’s private key always safe for its lifetime?
the Bob’s RSA pubic key and send • Only Bob can decrypt it and get the session key f What If Eve keeps records all communications and obtains the Bob’s private key later? Is Bob’s private key always safe for its lifetime?
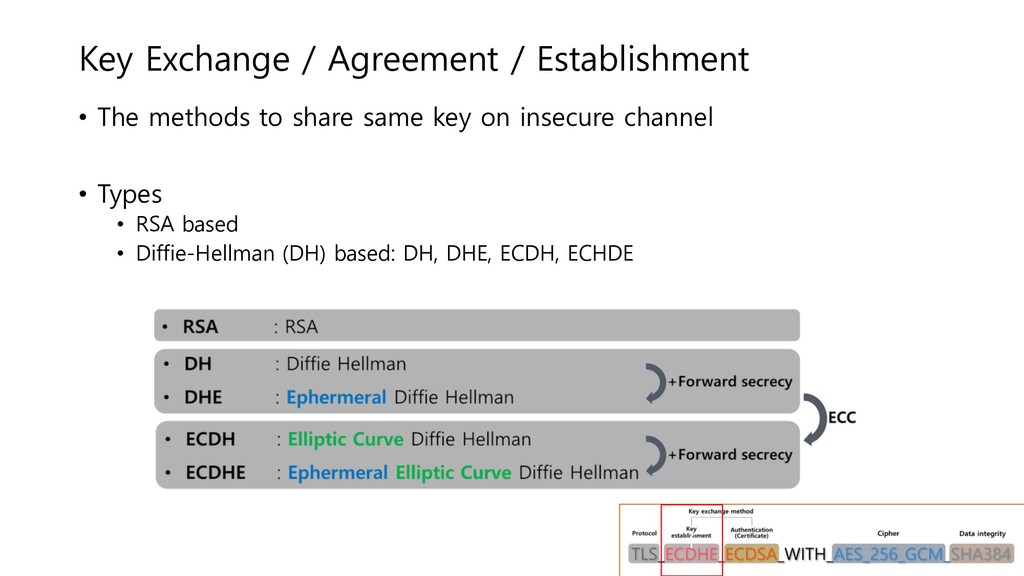
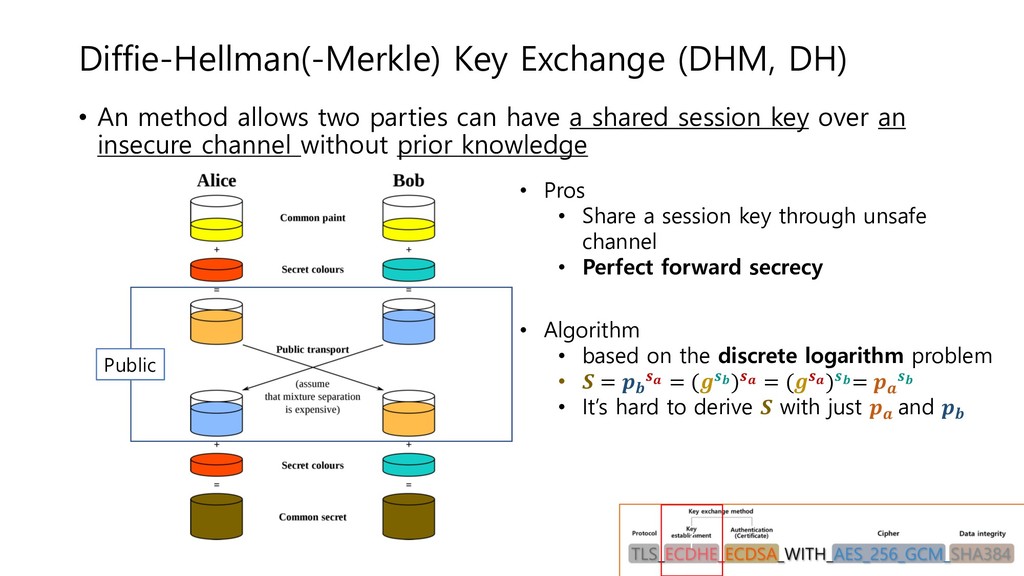
secure even if the long-term private key is compromised in the future To provide PFS • Use temporary session key • Do not save session key in permanent storage f
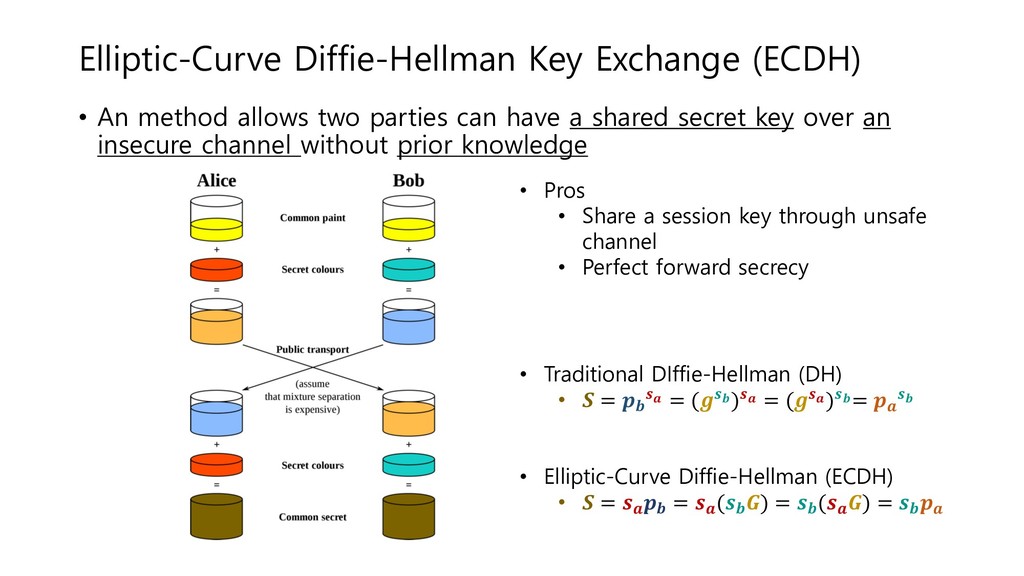
parties can have a shared session key over an insecure channel without prior knowledge • Algorithm • based on the discrete logarithm problem • ! = #$ %& = ((%$)%& = ((%&)%$= #& %$ • It’s hard to derive ! with just #& and #$ • Pros • Share a session key through unsafe channel • Perfect forward secrecy 38 f Public
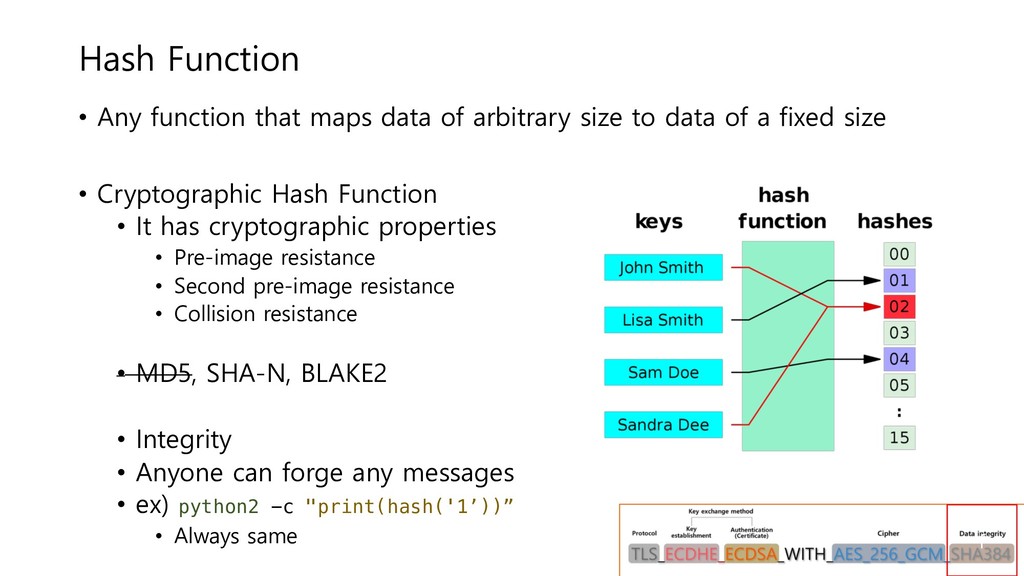
size to data of a fixed size • Cryptographic Hash Function • It has cryptographic properties • Pre-image resistance • Second pre-image resistance • Collision resistance • MD5, SHA-N, BLAKE2 • Integrity • Anyone can forge any messages • ex) python2 -c "print(hash('1’))” • Always same 40 f
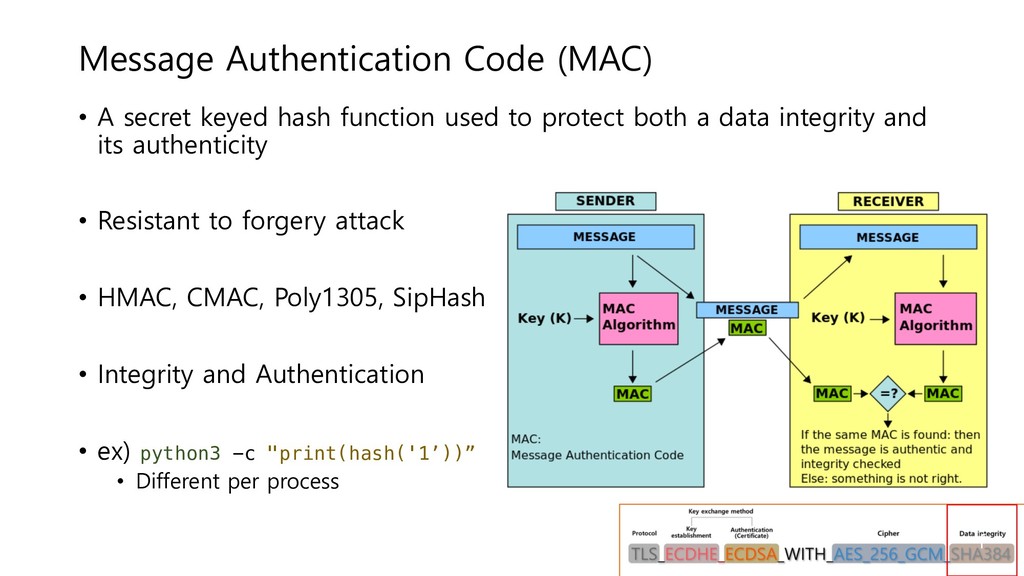
used to protect both a data integrity and its authenticity • Resistant to forgery attack • HMAC, CMAC, Poly1305, SipHash • Integrity and Authentication • ex) python3 -c "print(hash('1’))” • Different per process 41 f
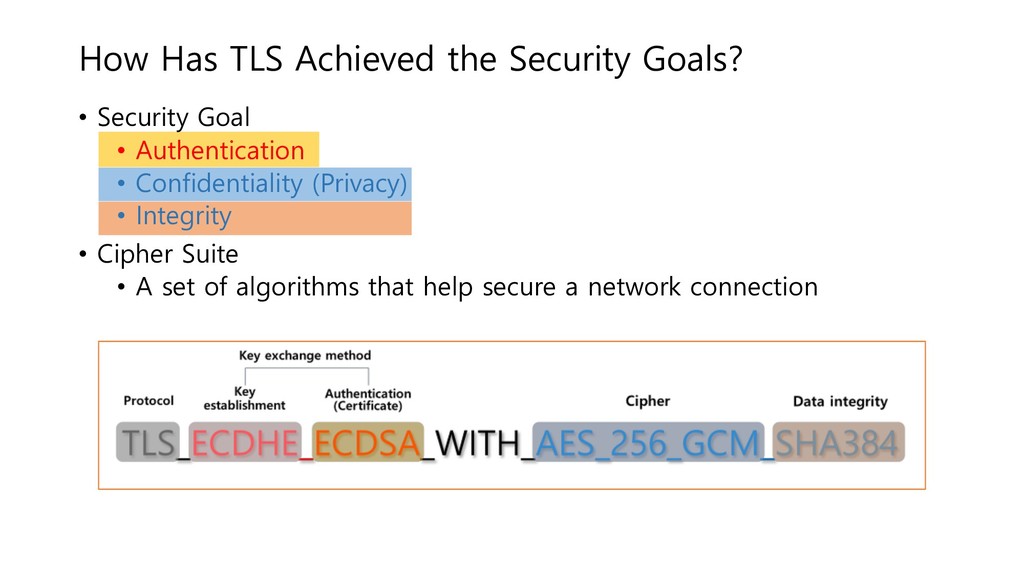
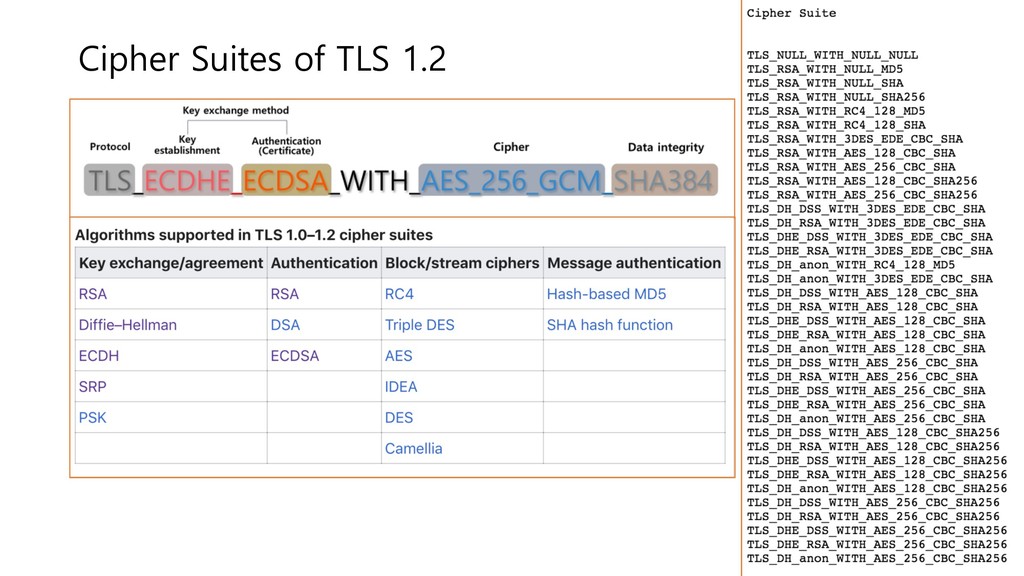
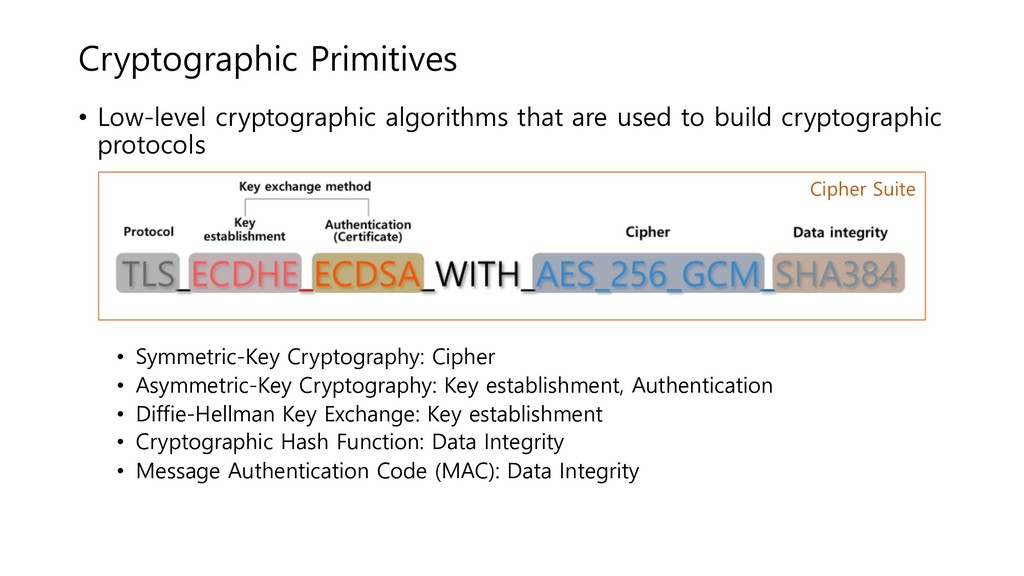
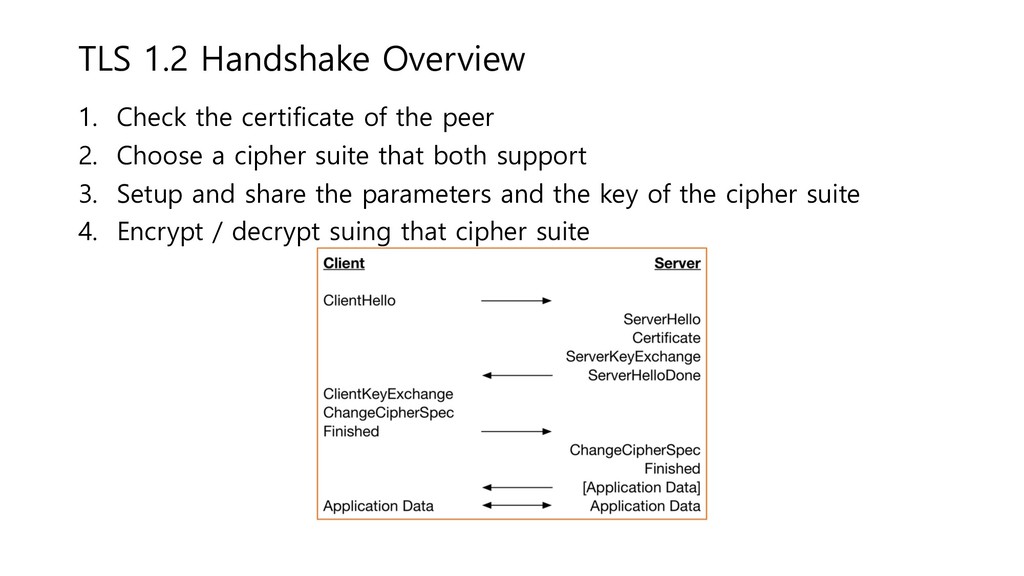
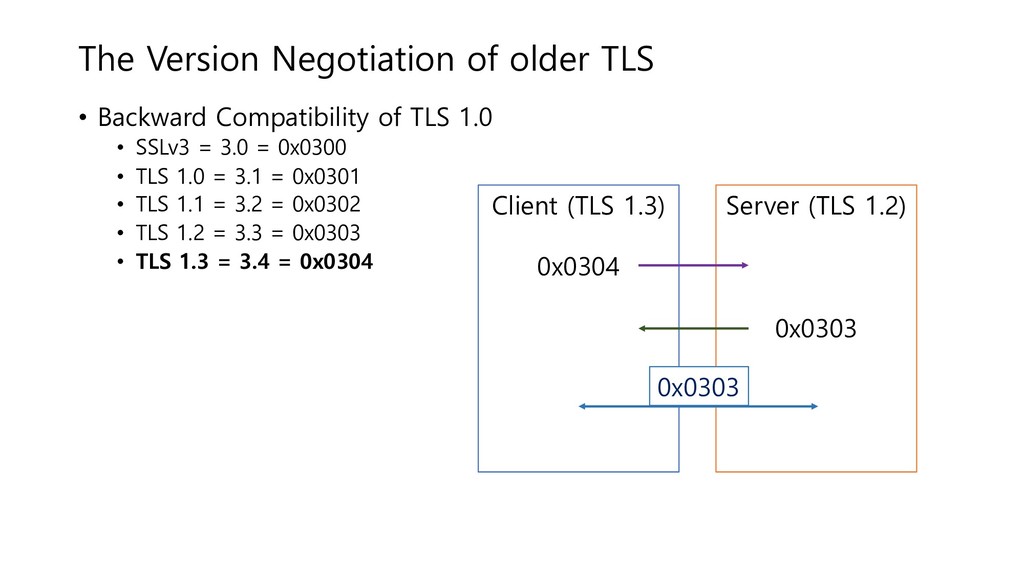
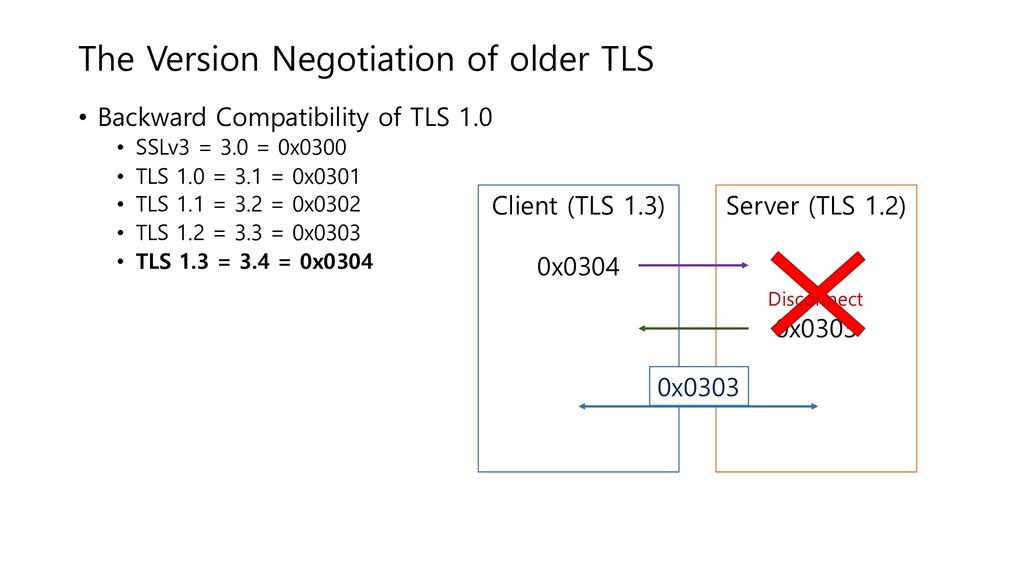
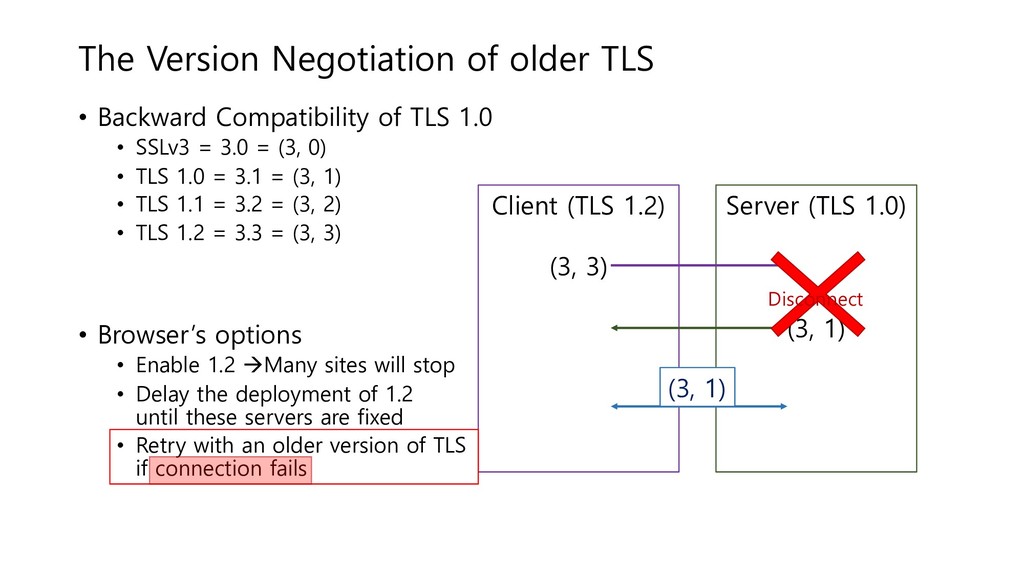
peer 2. Choose a cipher suite that both support 3. Setup and share the parameters and the key of the cipher suite 4. Encrypt / decrypt suing that cipher suite
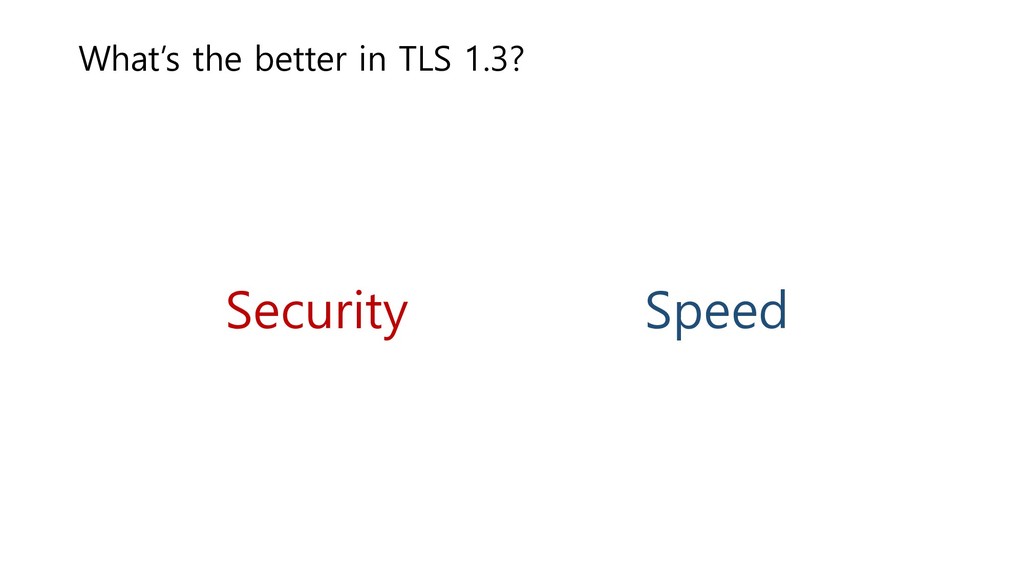
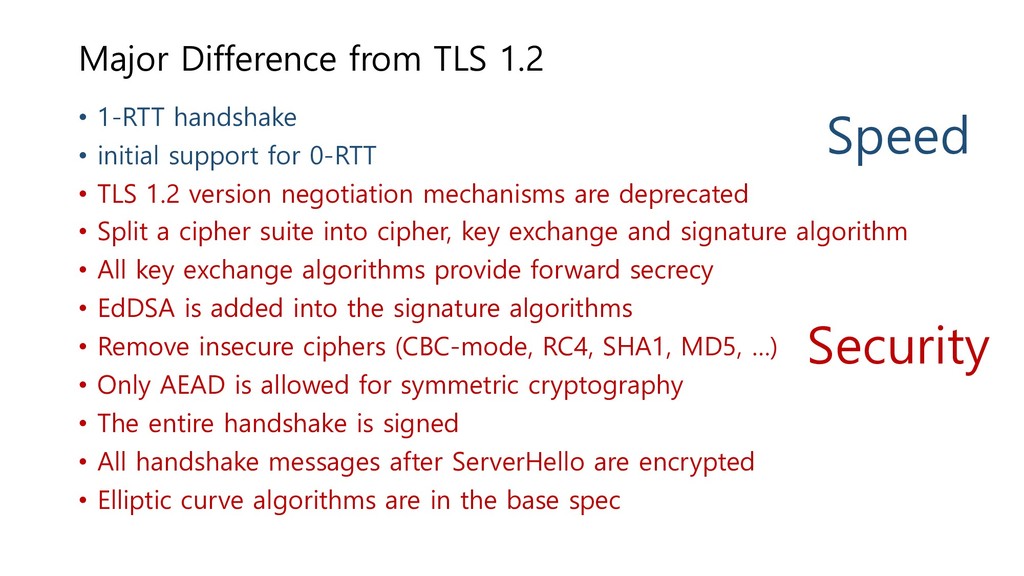
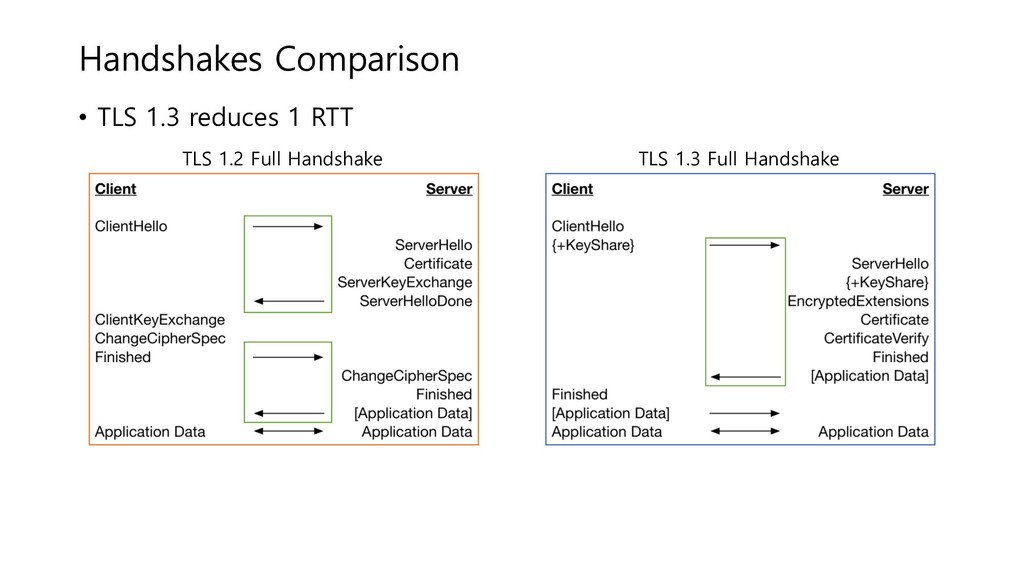
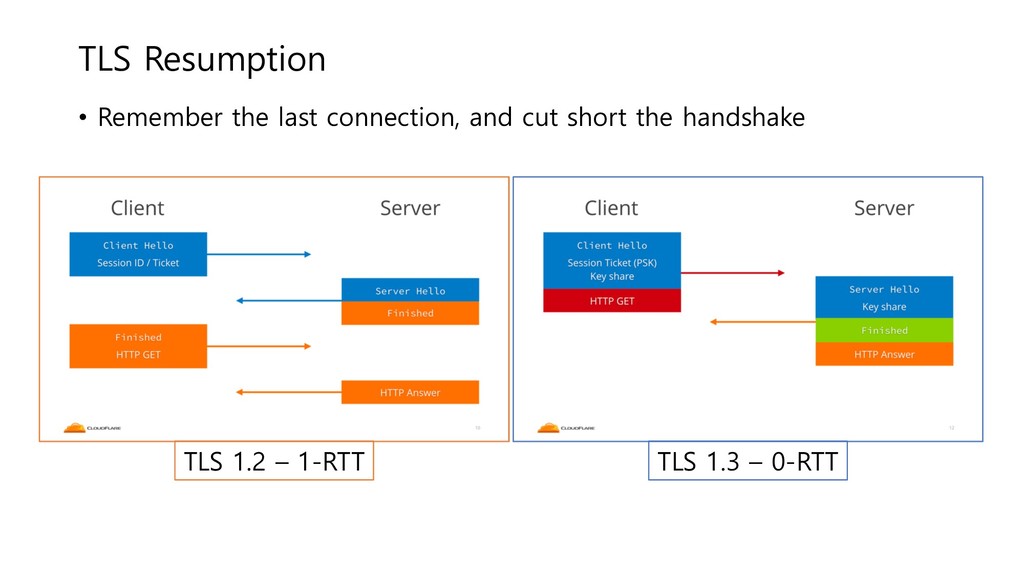
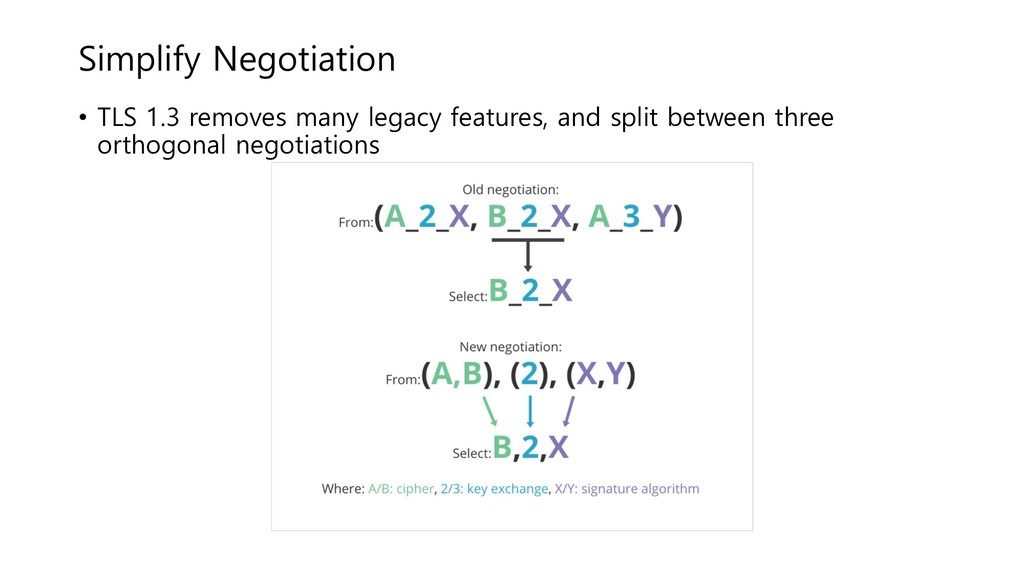
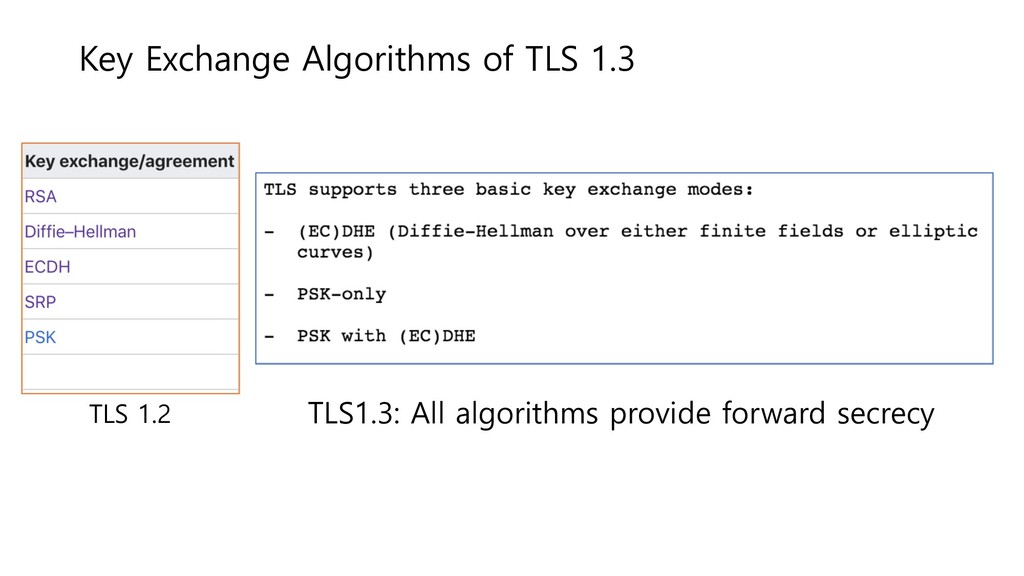
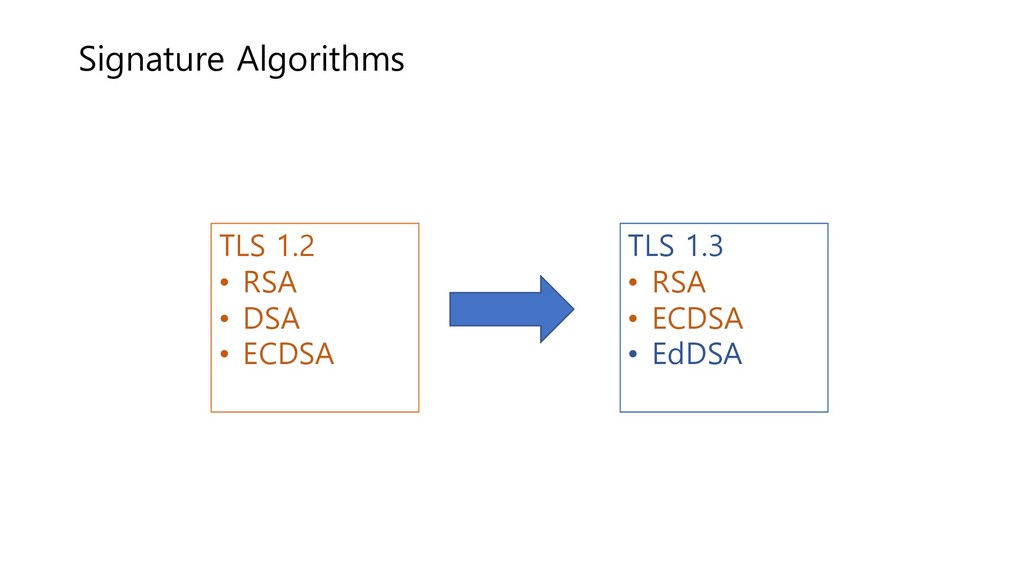
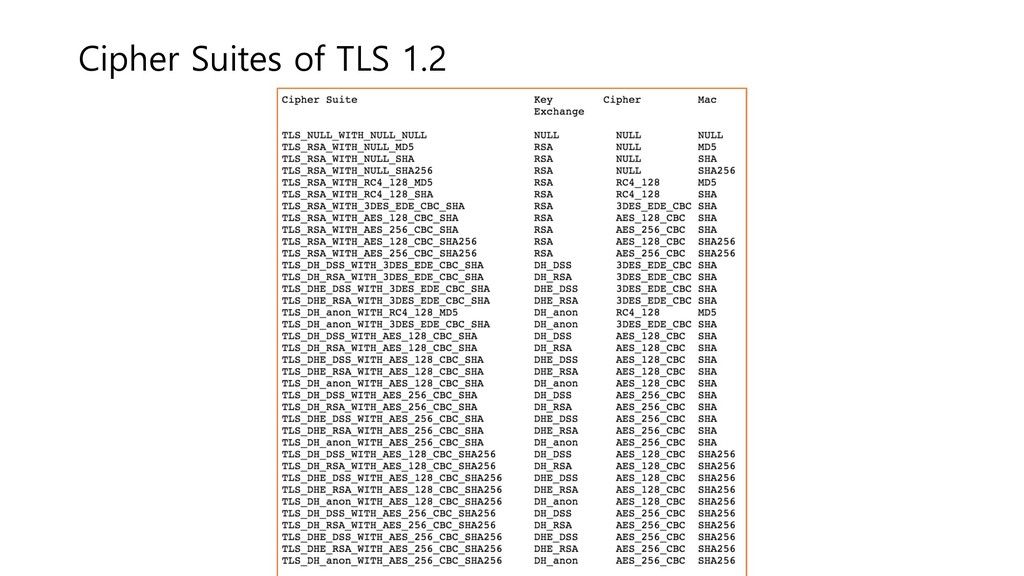
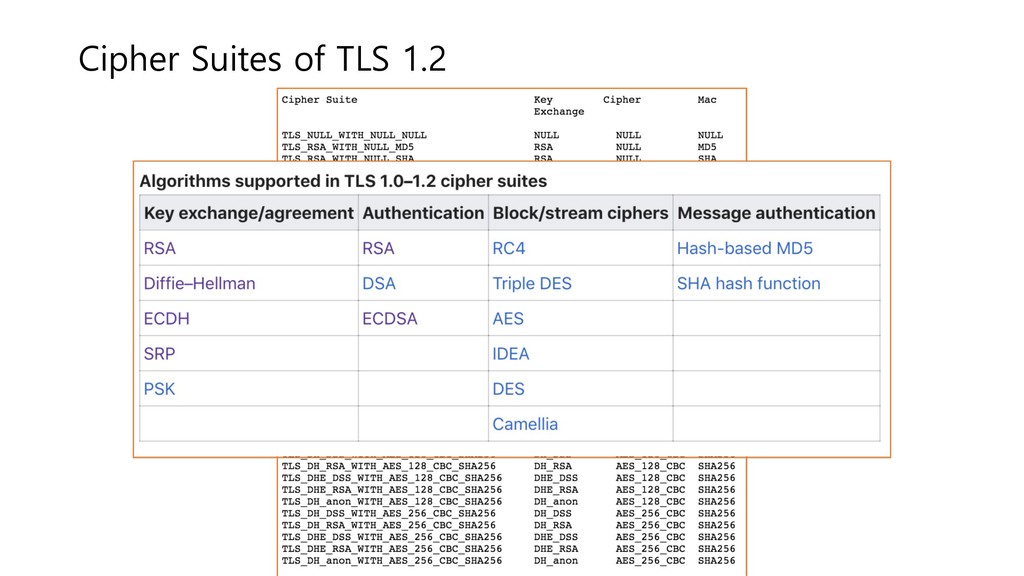
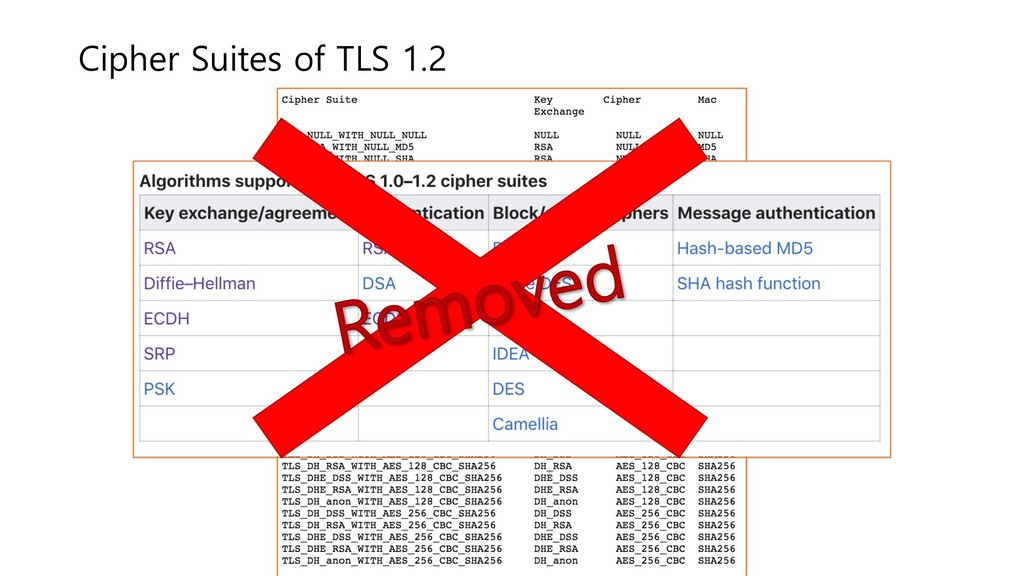
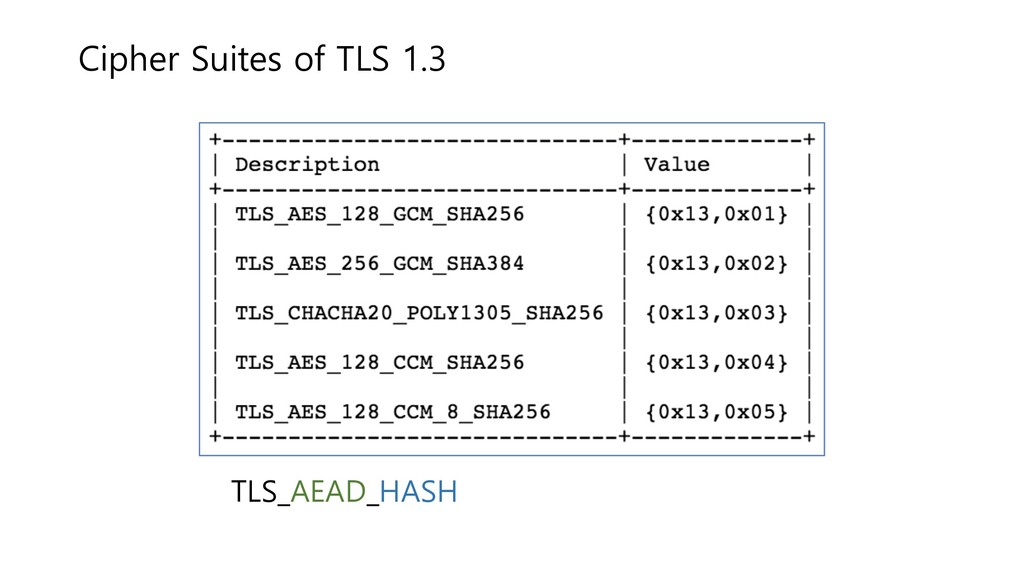
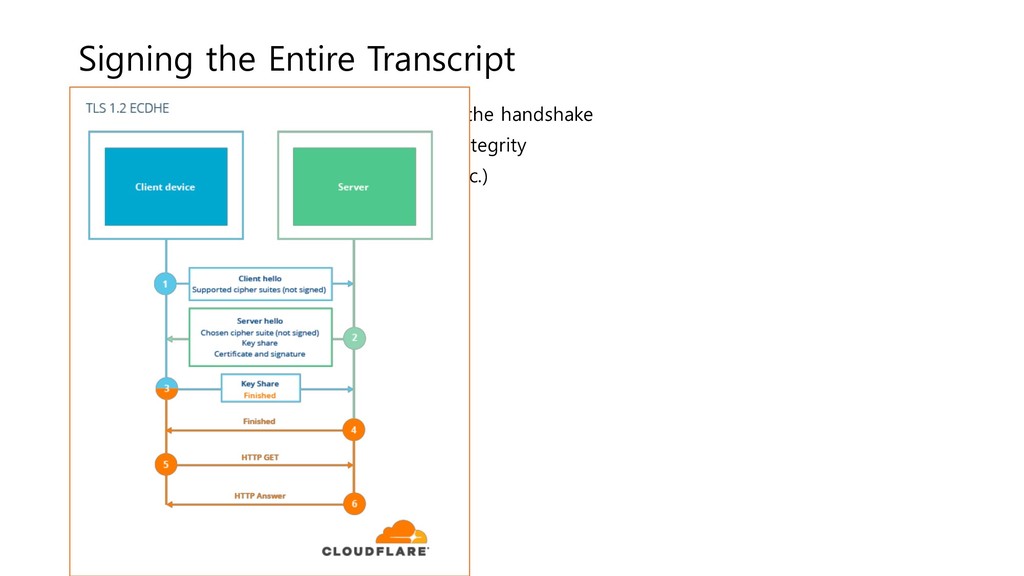
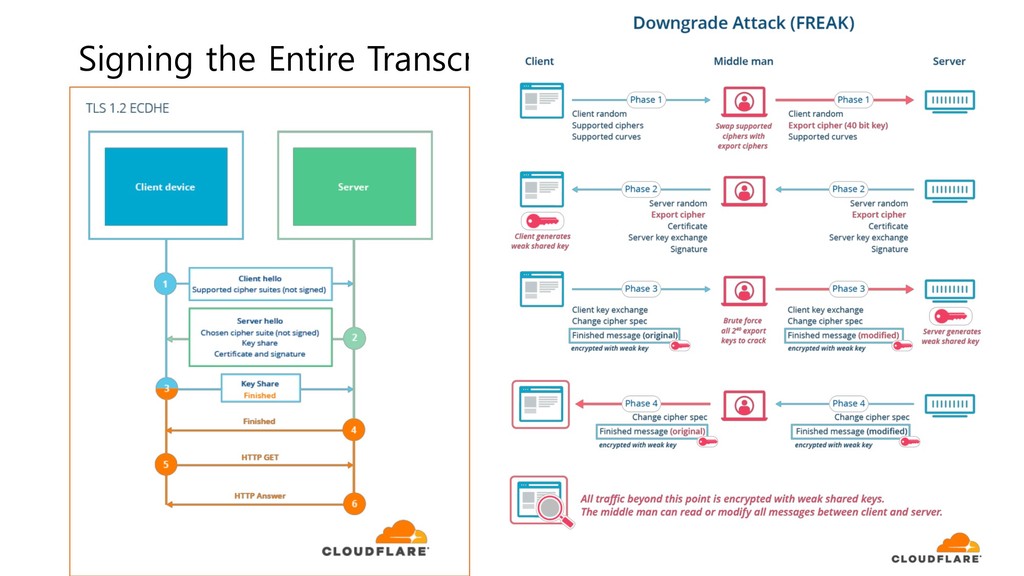
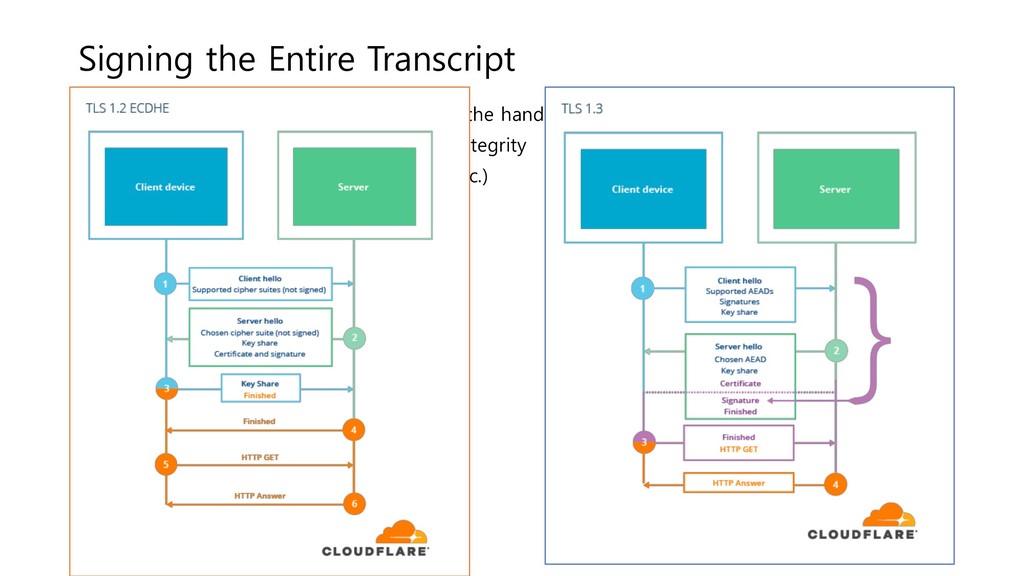
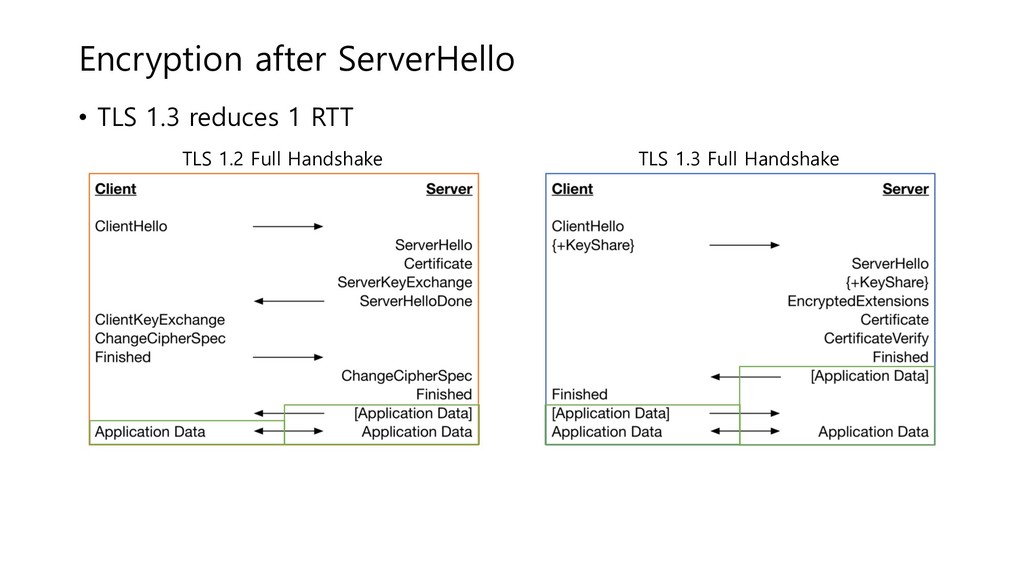
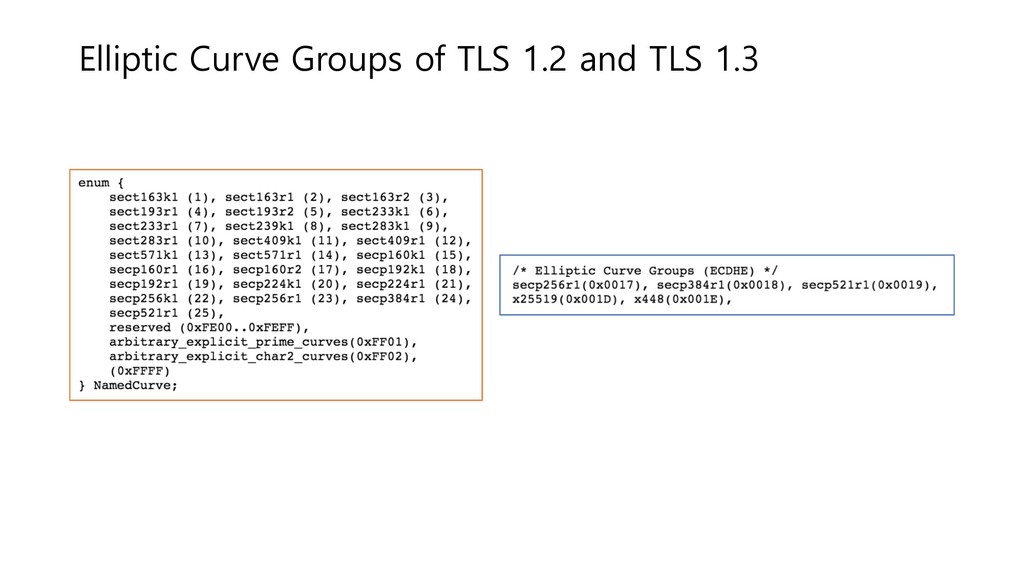
support for 0-RTT • TLS 1.2 version negotiation mechanisms are deprecated • Split a cipher suite into cipher, key exchange and signature algorithm • All key exchange algorithms provide forward secrecy • EdDSA is added into the signature algorithms • Remove insecure ciphers (CBC-mode, RC4, SHA1, MD5, …) • Only AEAD is allowed for symmetric cryptography • The entire handshake is signed • All handshake messages after ServerHello are encrypted • Elliptic curve algorithms are in the base spec Security Speed
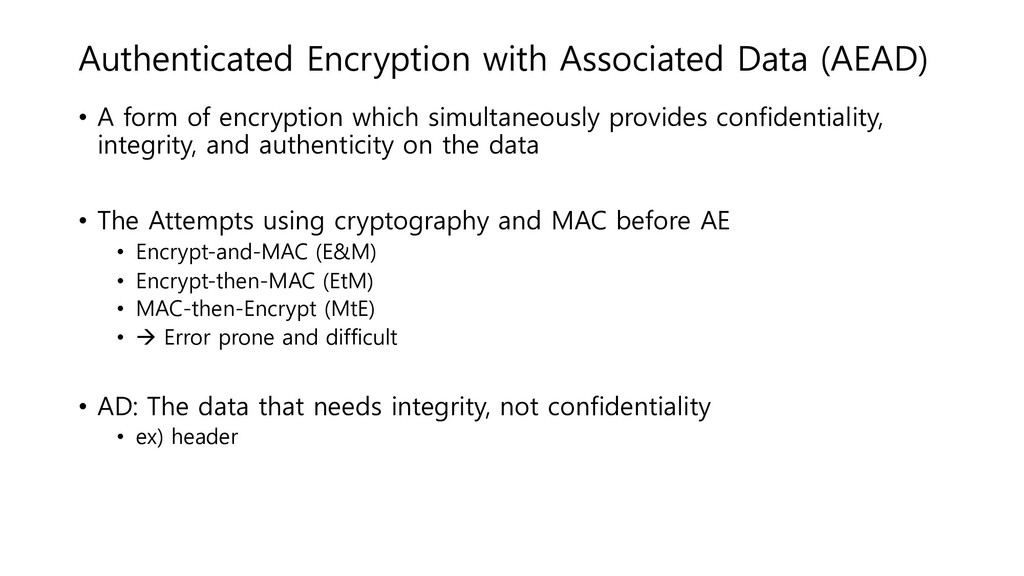
encryption which simultaneously provides confidentiality, integrity, and authenticity on the data • The Attempts using cryptography and MAC before AE • Encrypt-and-MAC (E&M) • Encrypt-then-MAC (EtM) • MAC-then-Encrypt (MtE) • à Error prone and difficult • AD: The data that needs integrity, not confidentiality • ex) header
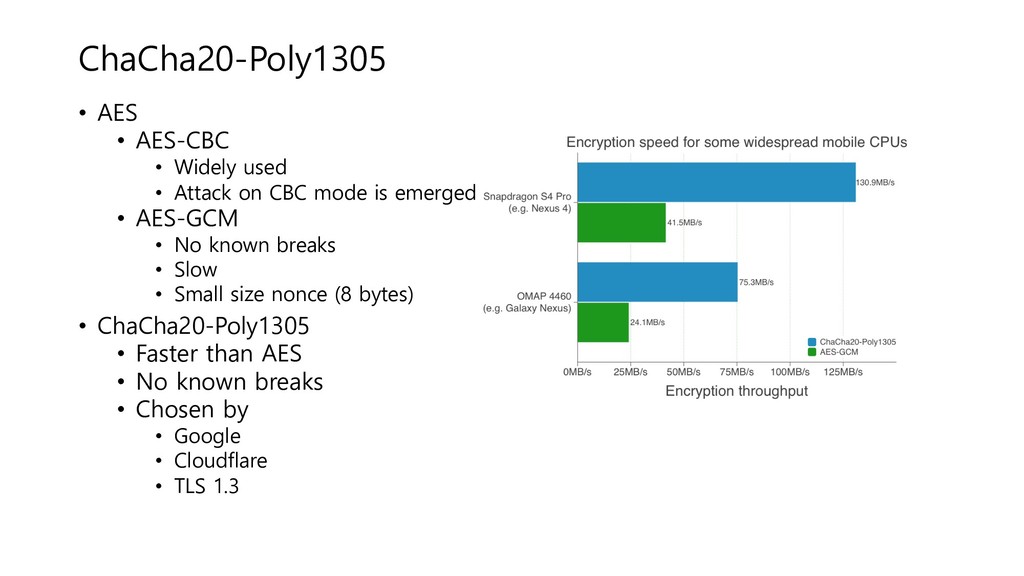
on CBC mode is emerged • AES-GCM • No known breaks • Slow • Small size nonce (8 bytes) • ChaCha20-Poly1305 • Faster than AES • No known breaks • Chosen by • Google • Cloudflare • TLS 1.3
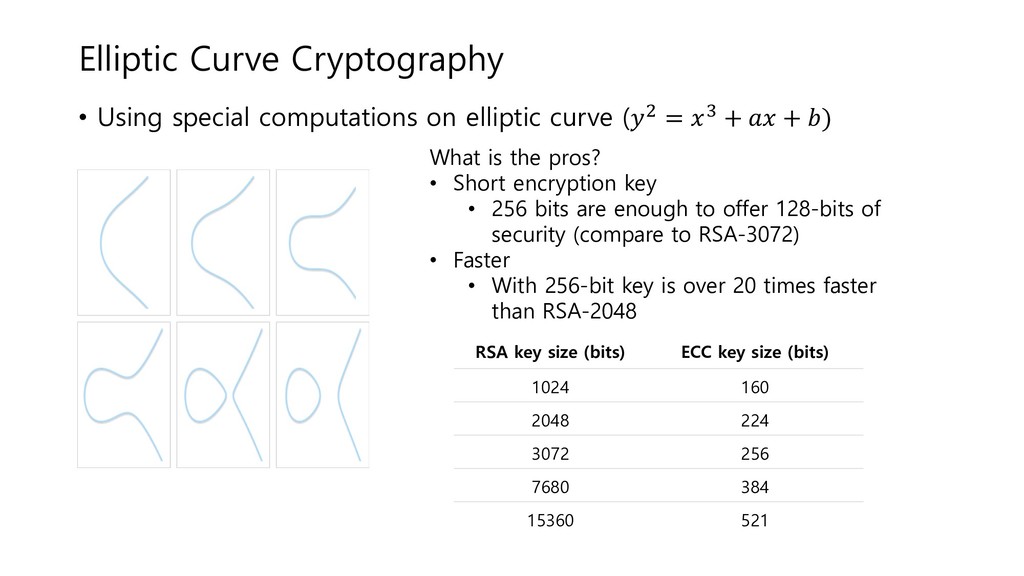
(!" = $% + '$ + () What is the pros? • Short encryption key • 256 bits are enough to offer 128-bits of security (compare to RSA-3072) • Faster • With 256-bit key is over 20 times faster than RSA-2048 RSA key size (bits) ECC key size (bits) 1024 160 2048 224 3072 256 7680 384 15360 521
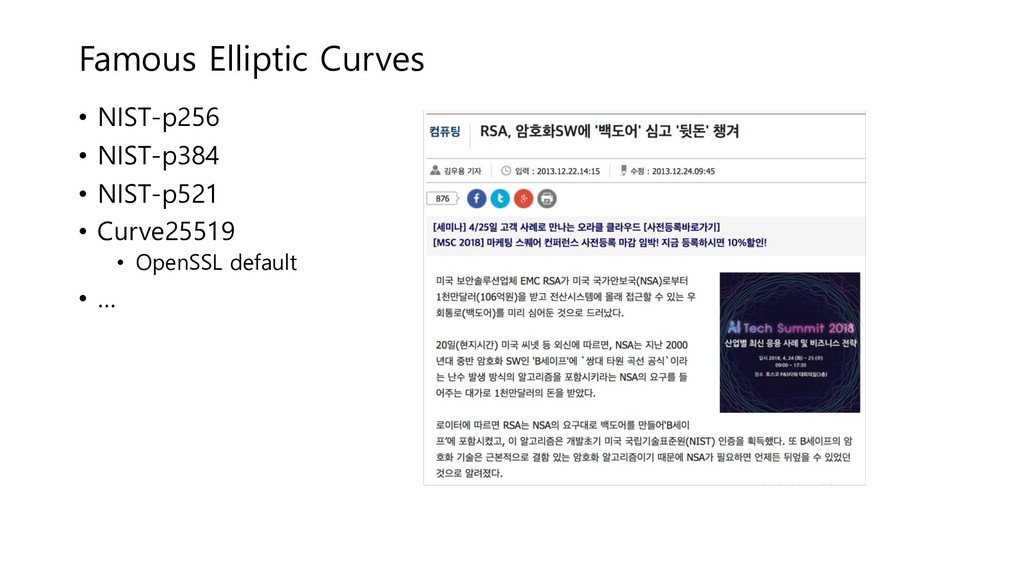
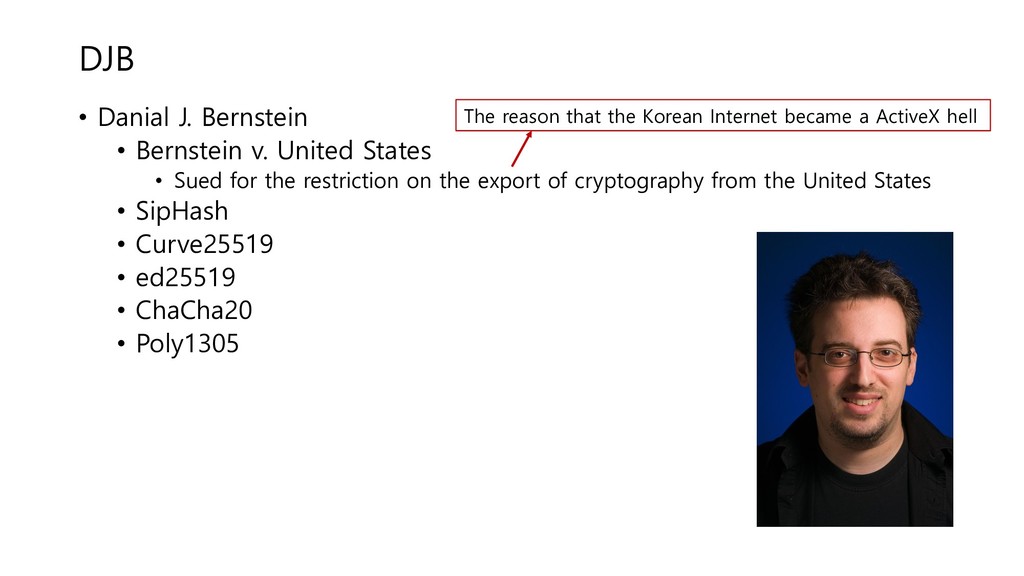
• Sued for the restriction on the export of cryptography from the United States • SipHash • Curve25519 • ed25519 • ChaCha20 • Poly1305 The reason that the Korean Internet became a ActiveX hell
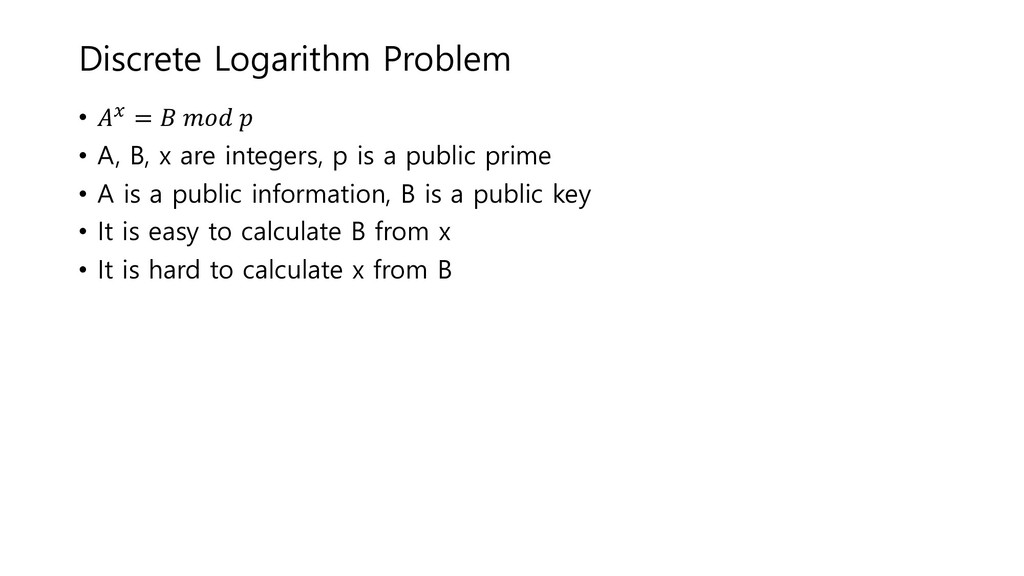
A, B, x are integers, p is a public prime • A is a public information, B is a public key • It is easy to calculate B from x • It is hard to calculate x from B
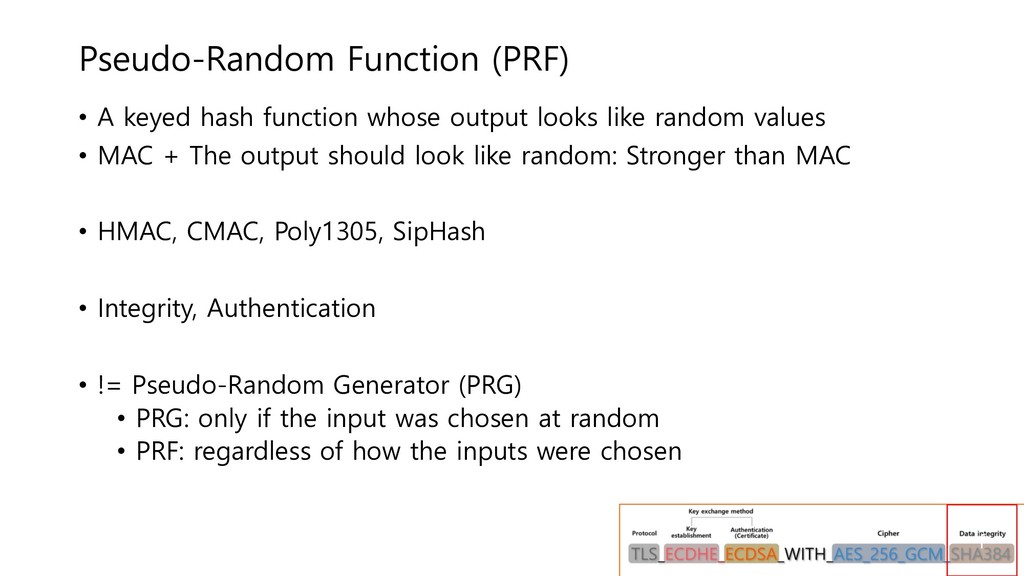
looks like random values • MAC + The output should look like random: Stronger than MAC • HMAC, CMAC, Poly1305, SipHash • Integrity, Authentication • != Pseudo-Random Generator (PRG) • PRG: only if the input was chosen at random • PRF: regardless of how the inputs were chosen 87 f
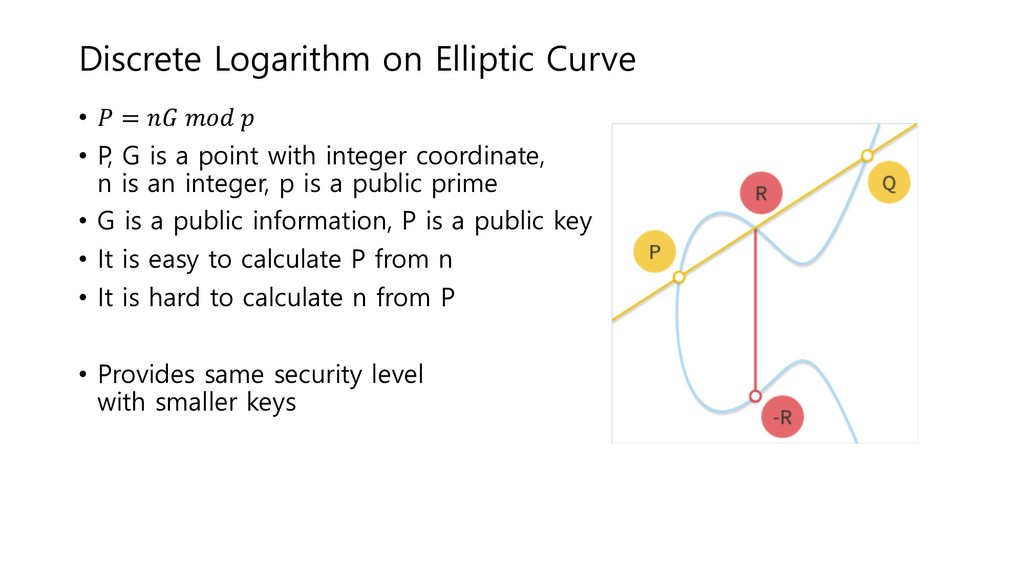
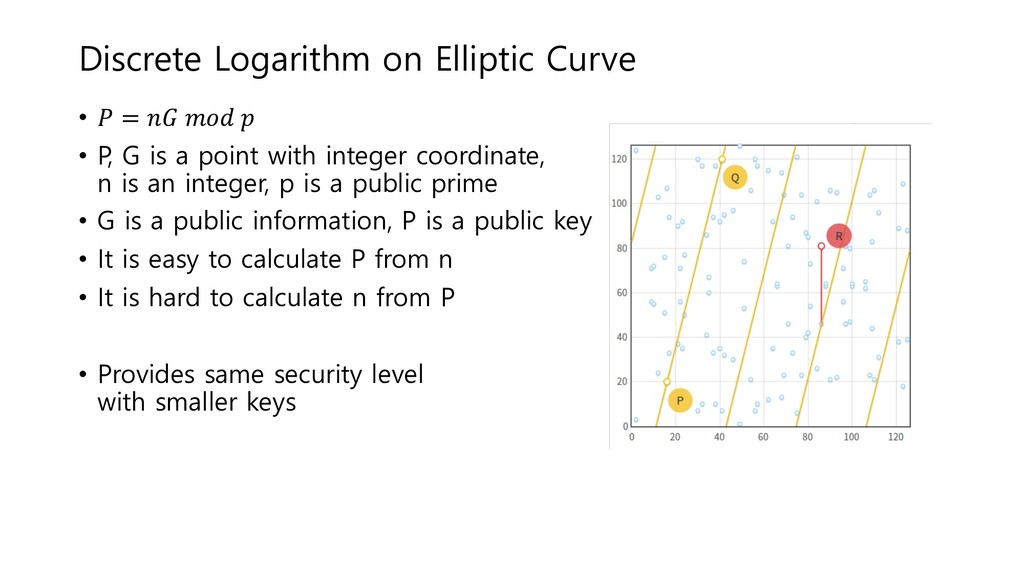
( • P, G is a point with integer coordinate, n is an integer, p is a public prime • G is a public information, P is a public key • It is easy to calculate P from n • It is hard to calculate n from P • Provides same security level with smaller keys
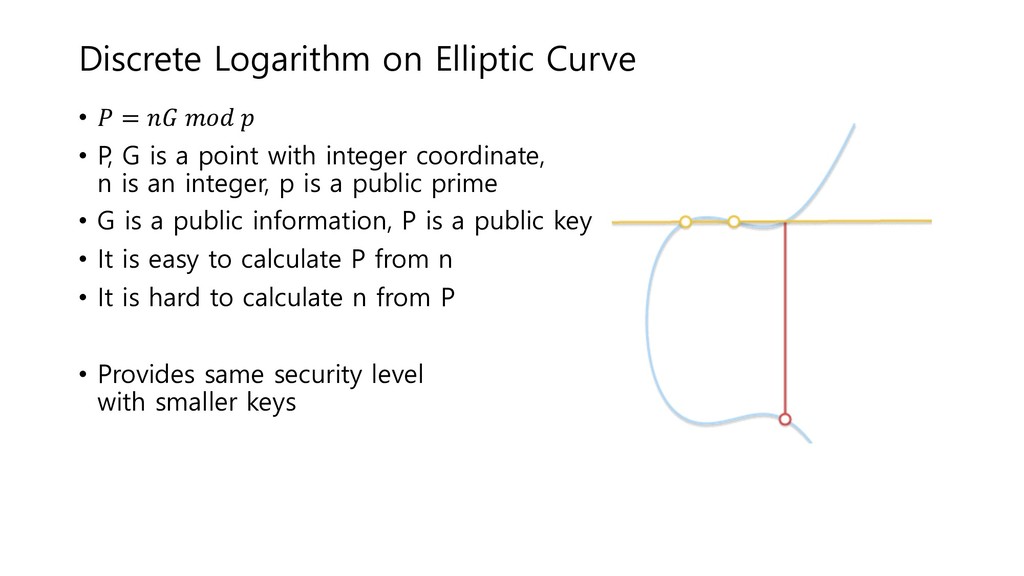
( • P, G is a point with integer coordinate, n is an integer, p is a public prime • G is a public information, P is a public key • It is easy to calculate P from n • It is hard to calculate n from P • Provides same security level with smaller keys
( • P, G is a point with integer coordinate, n is an integer, p is a public prime • G is a public information, P is a public key • It is easy to calculate P from n • It is hard to calculate n from P • Provides same security level with smaller keys
are needed to break it • Sufficient Length • 128 bits of security is sufficient until next revolutionary breakthrough in either mathematics or technology • 112 bits of security is sufficient until 2030 • Symmetric cryptography • Normally equal to the key size • AES-128 (key size 128 bits) offers a 128-bit security level • Asymmetric cryptography • The entropy is decrease because it have to provide asymmetric function • RSA-3072 offers a 128-bit security level


 buzzvil
 onozaty
 itsmedreamwalker
 kinakomoti321
 kumaiu
 kmkim
 t0yohei
 quramy
 shogogg
 nextbeatdev
 richargh
 vivion
 dalinaum
 aki_iinuma
 tammyeverts
 bermonpainter
 eileencodes
 ammeep
 takai
 elsirapls
 chikuwait
 csswizardry
 joshbly
 codingconduct
 akashhashmi