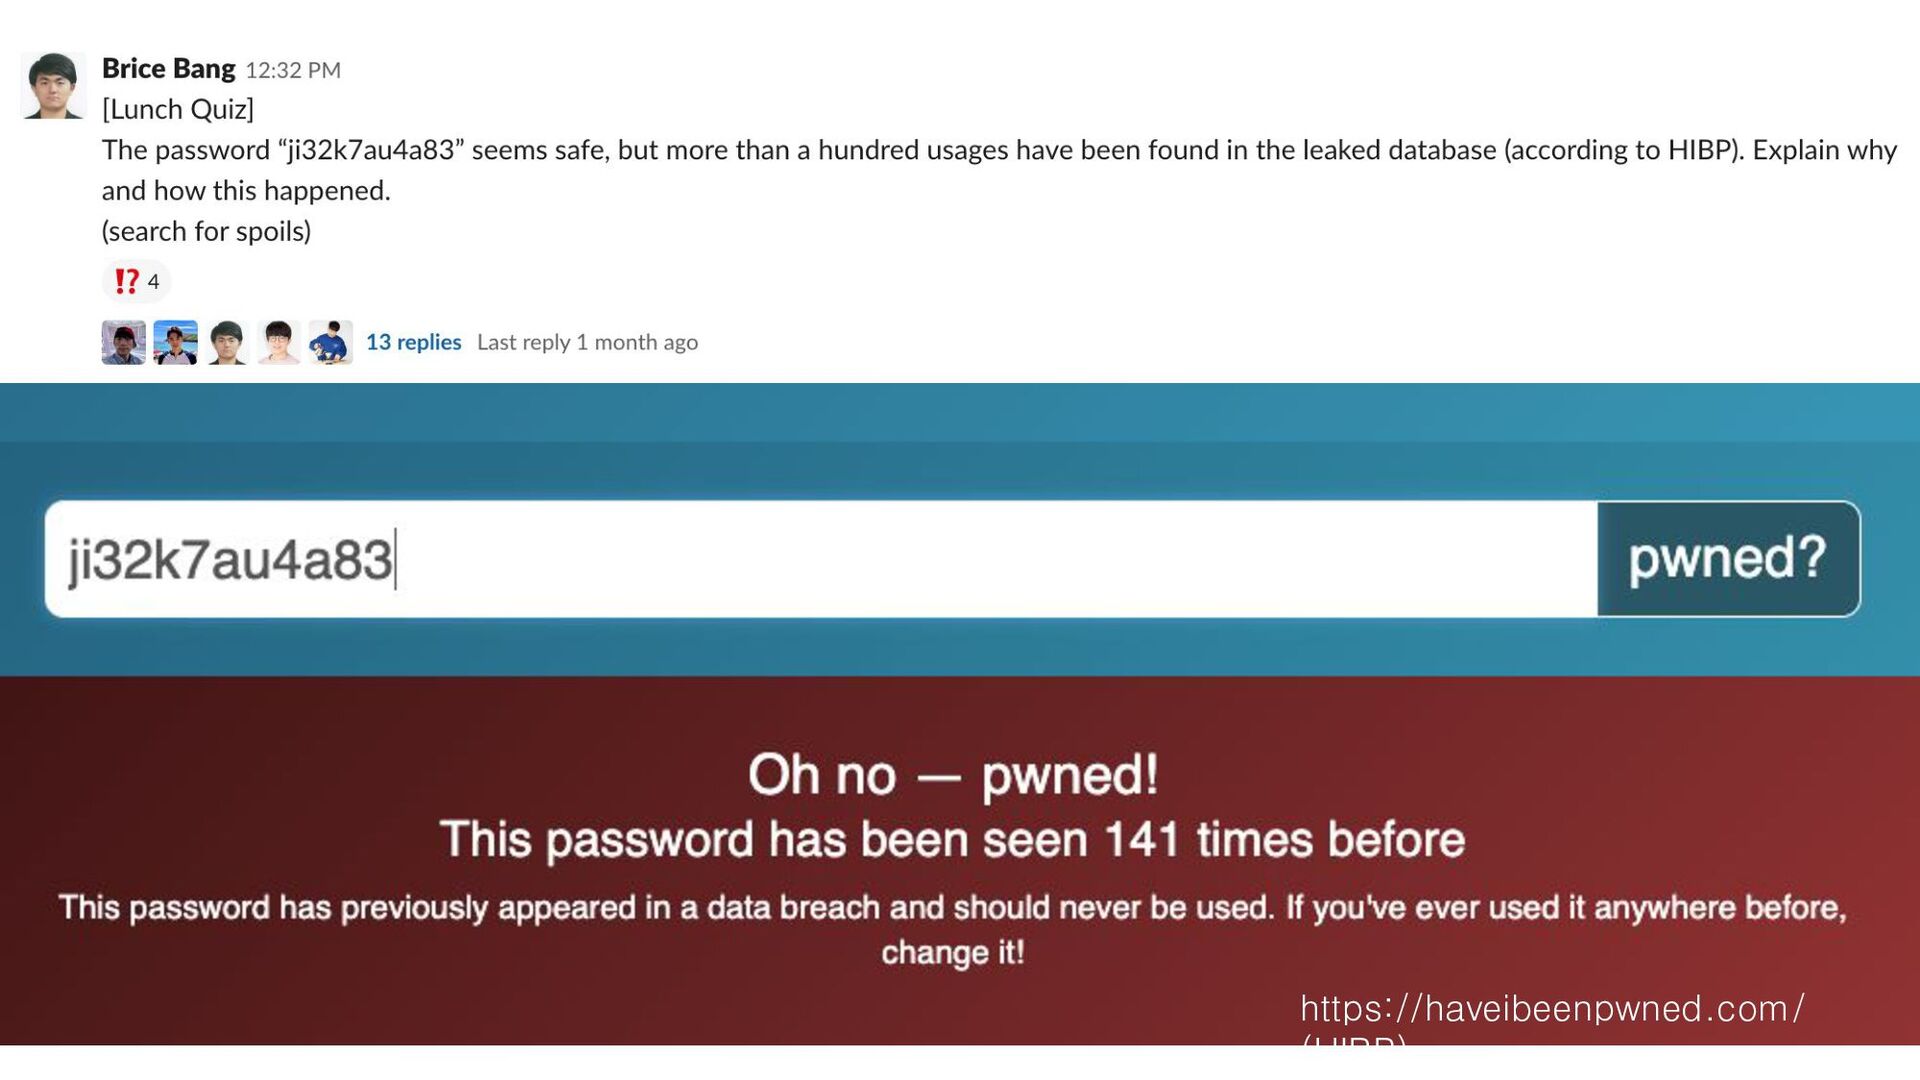
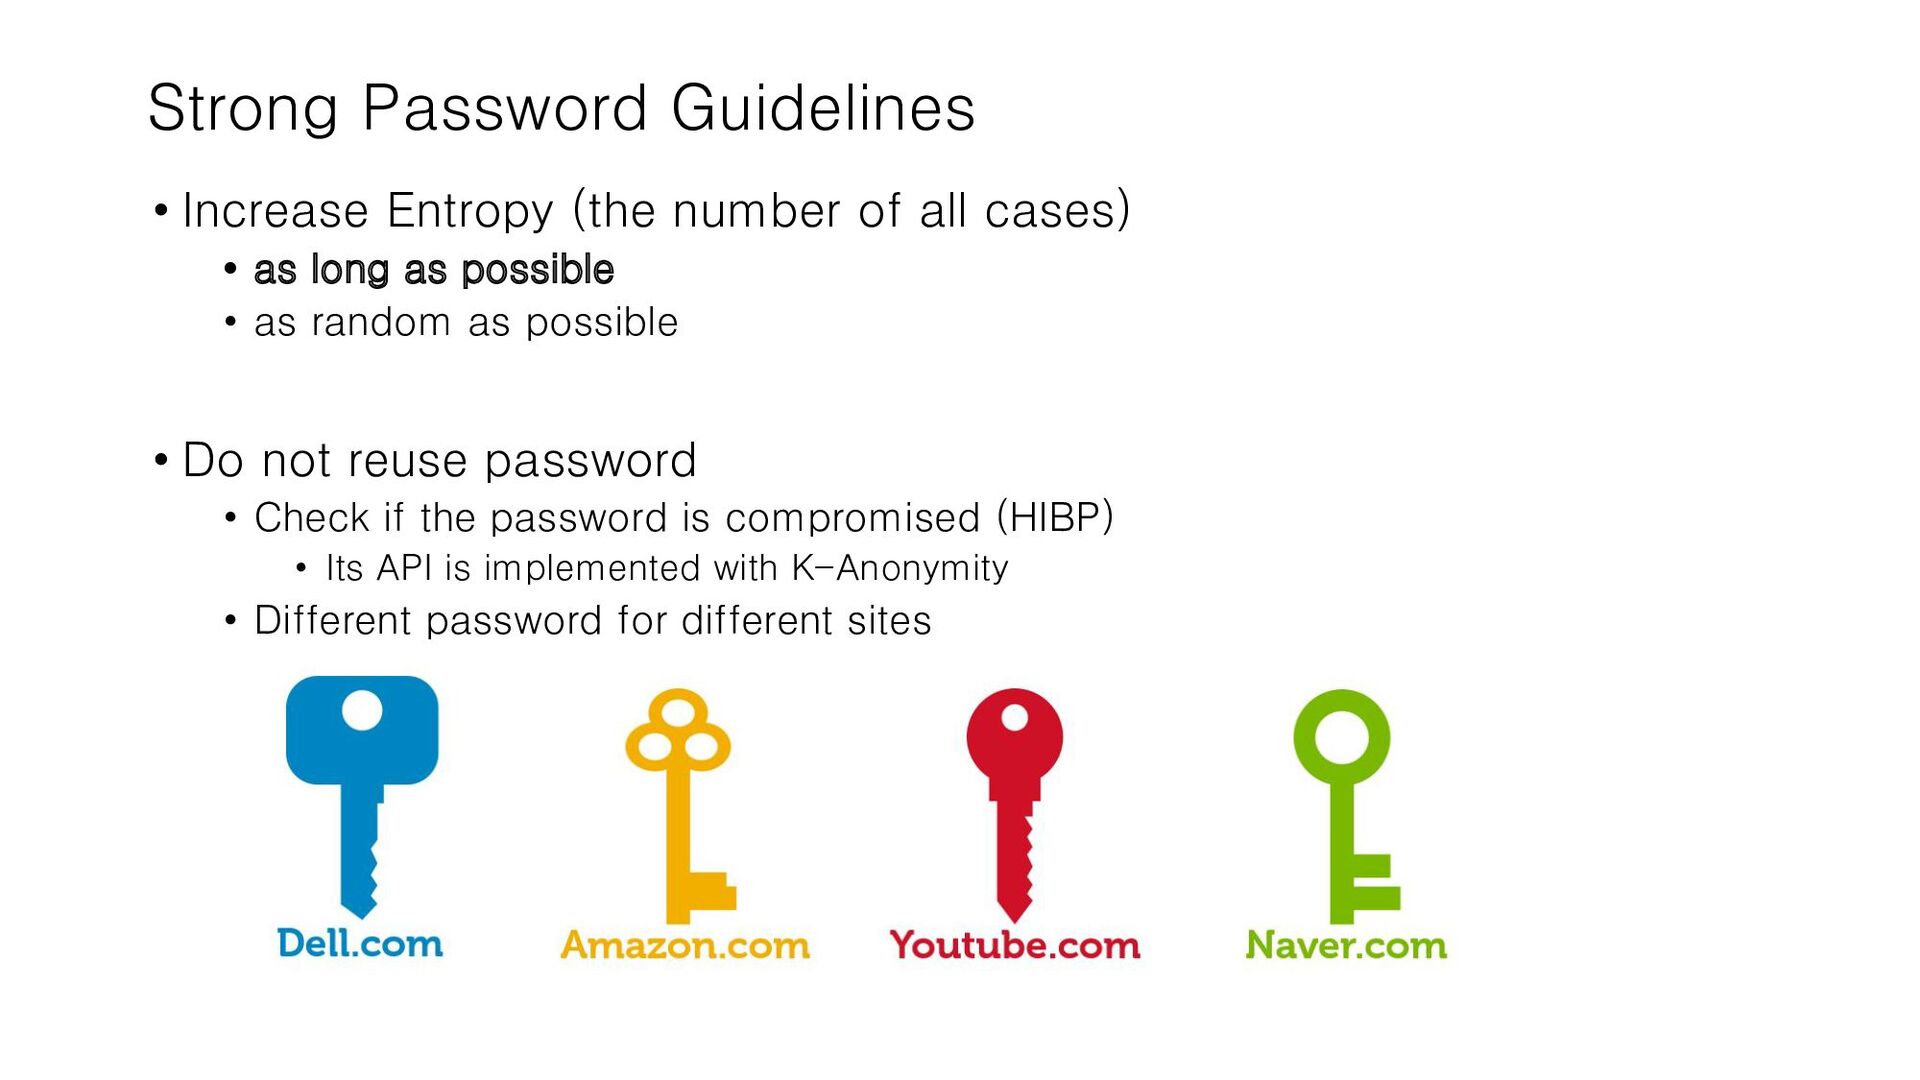
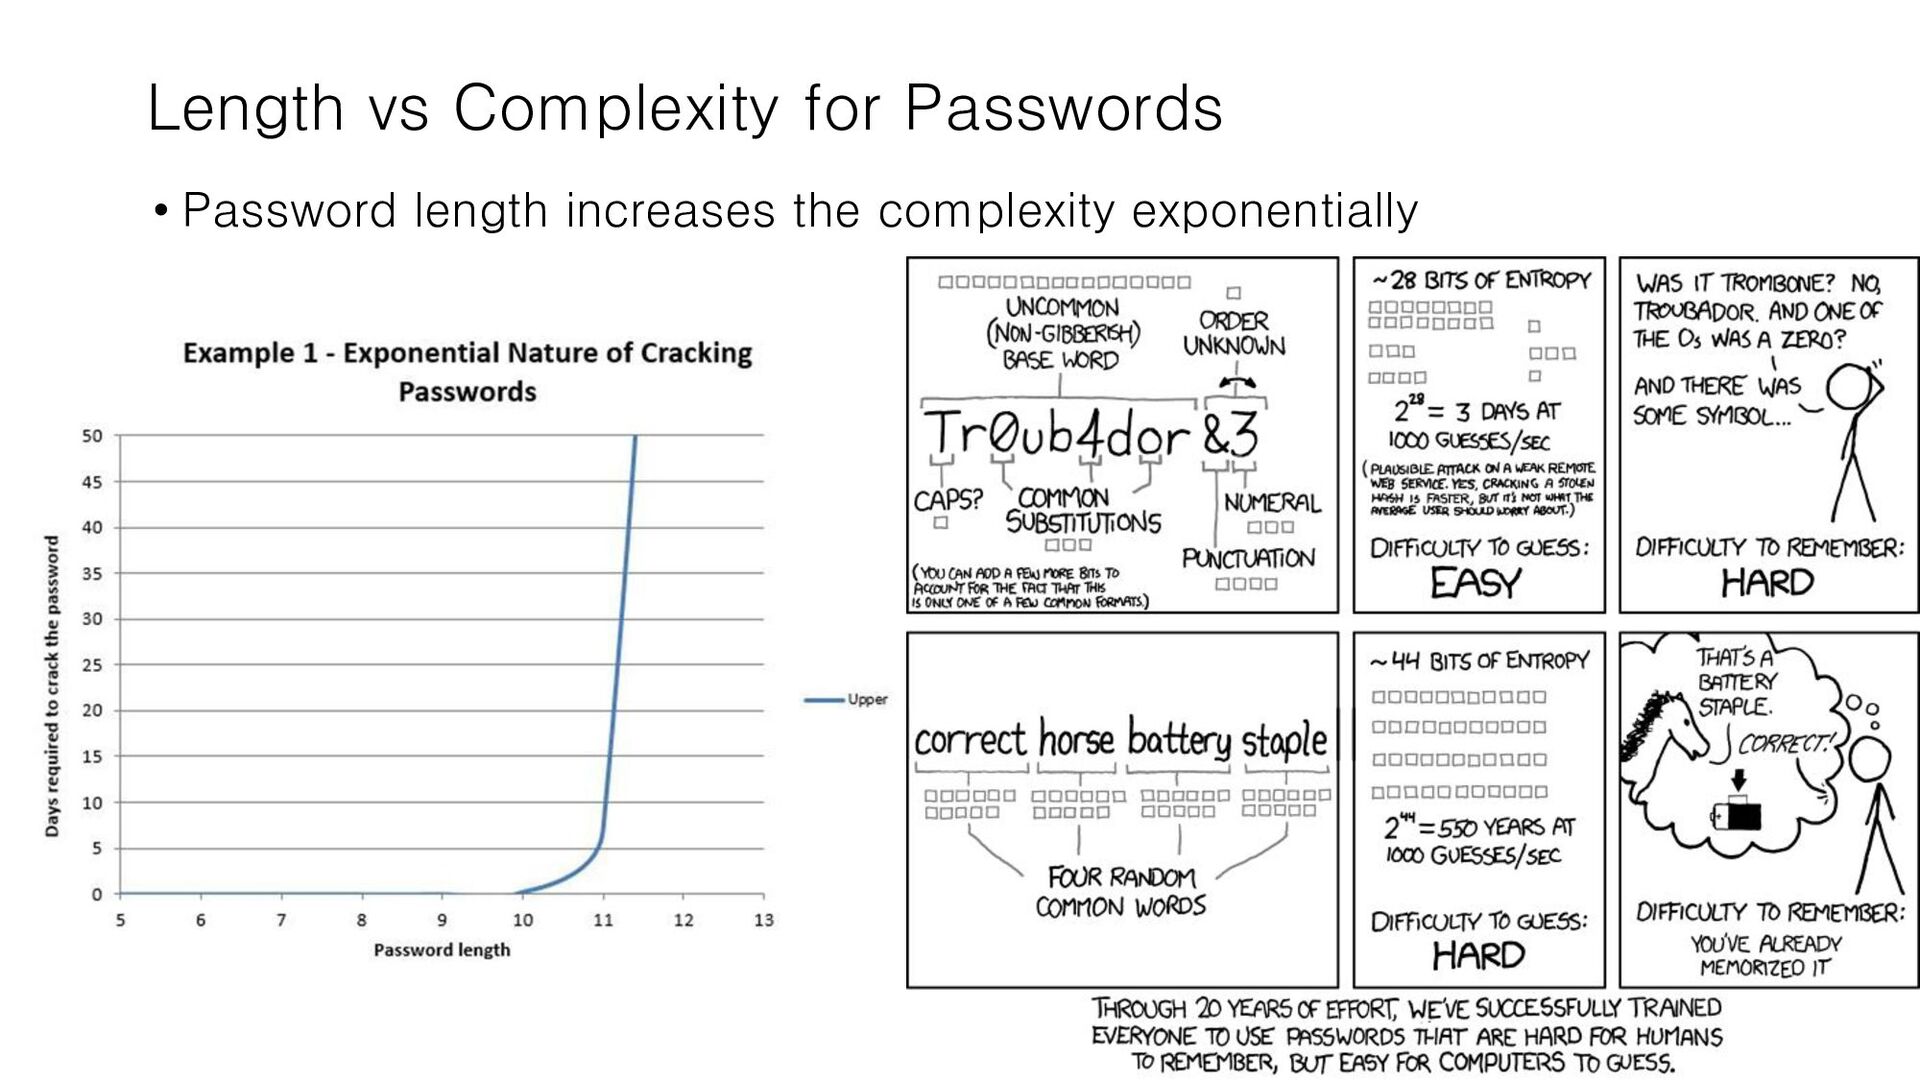
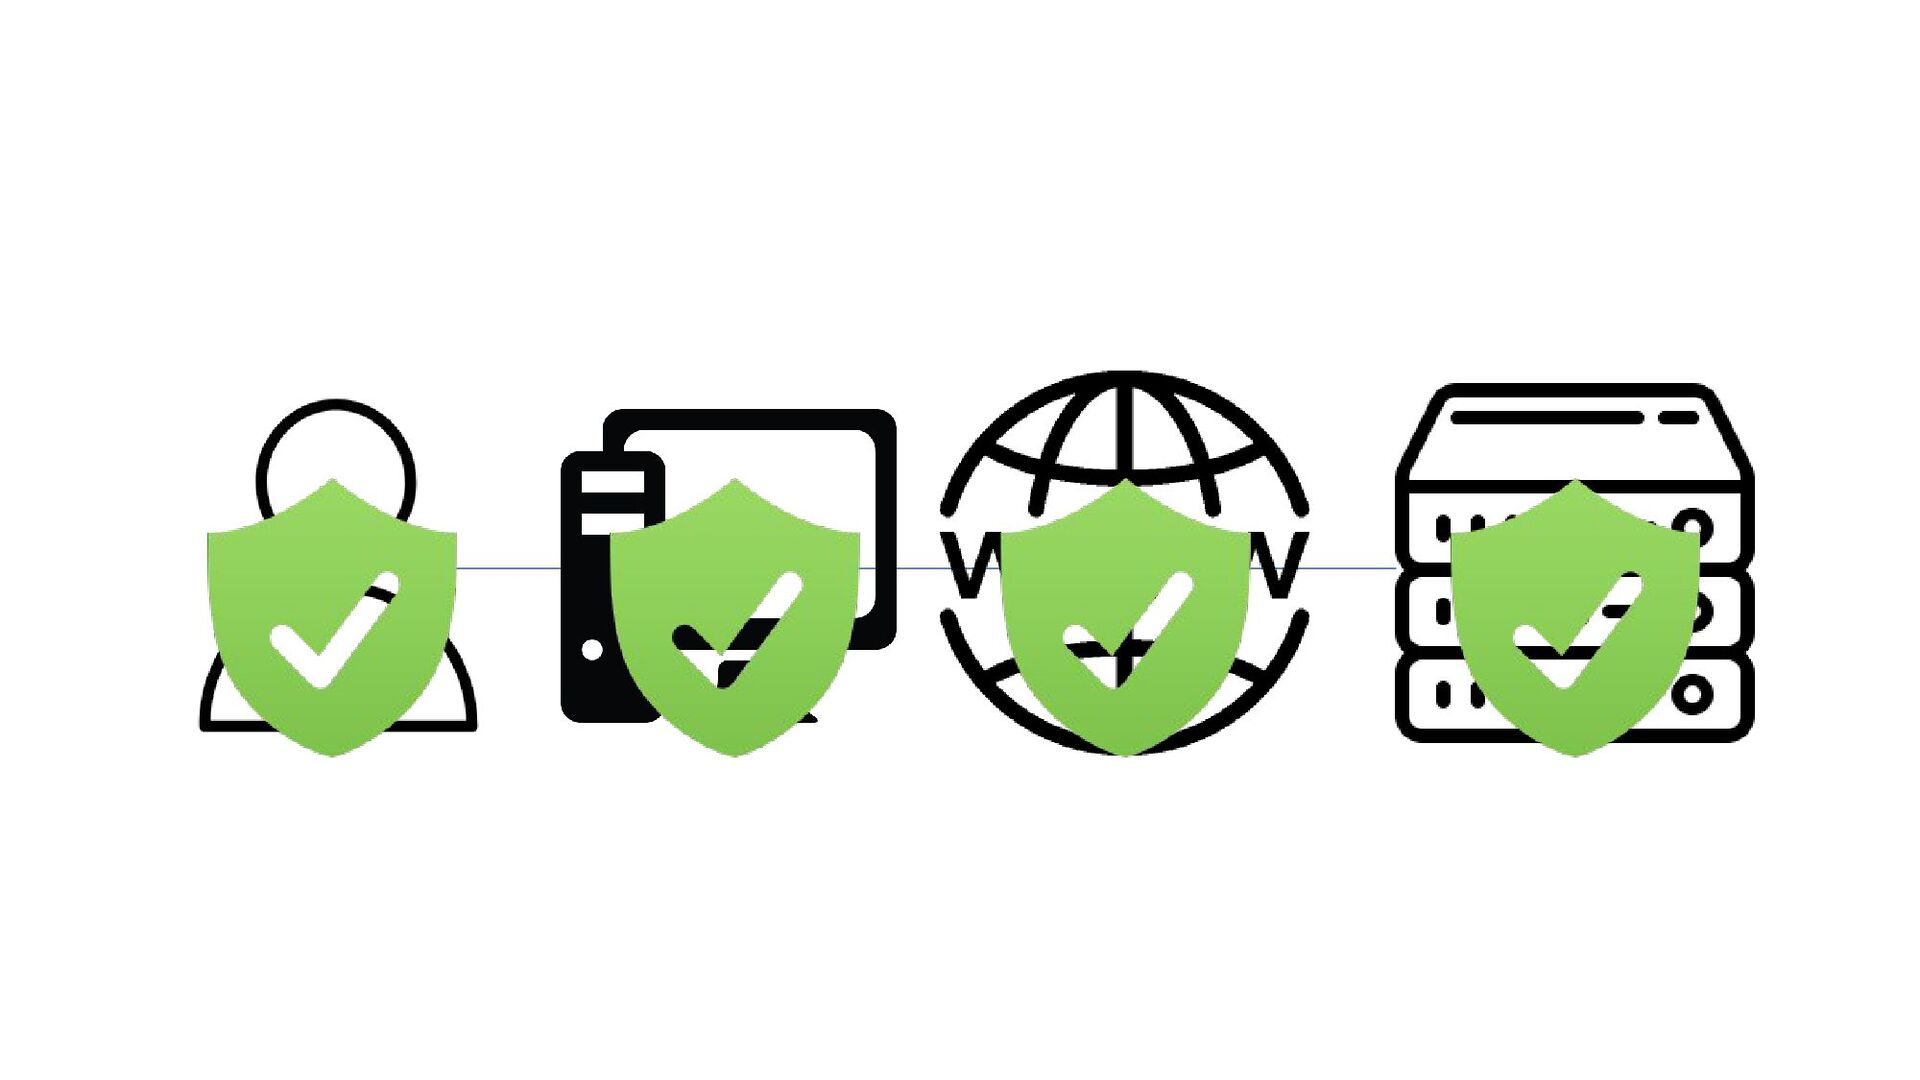
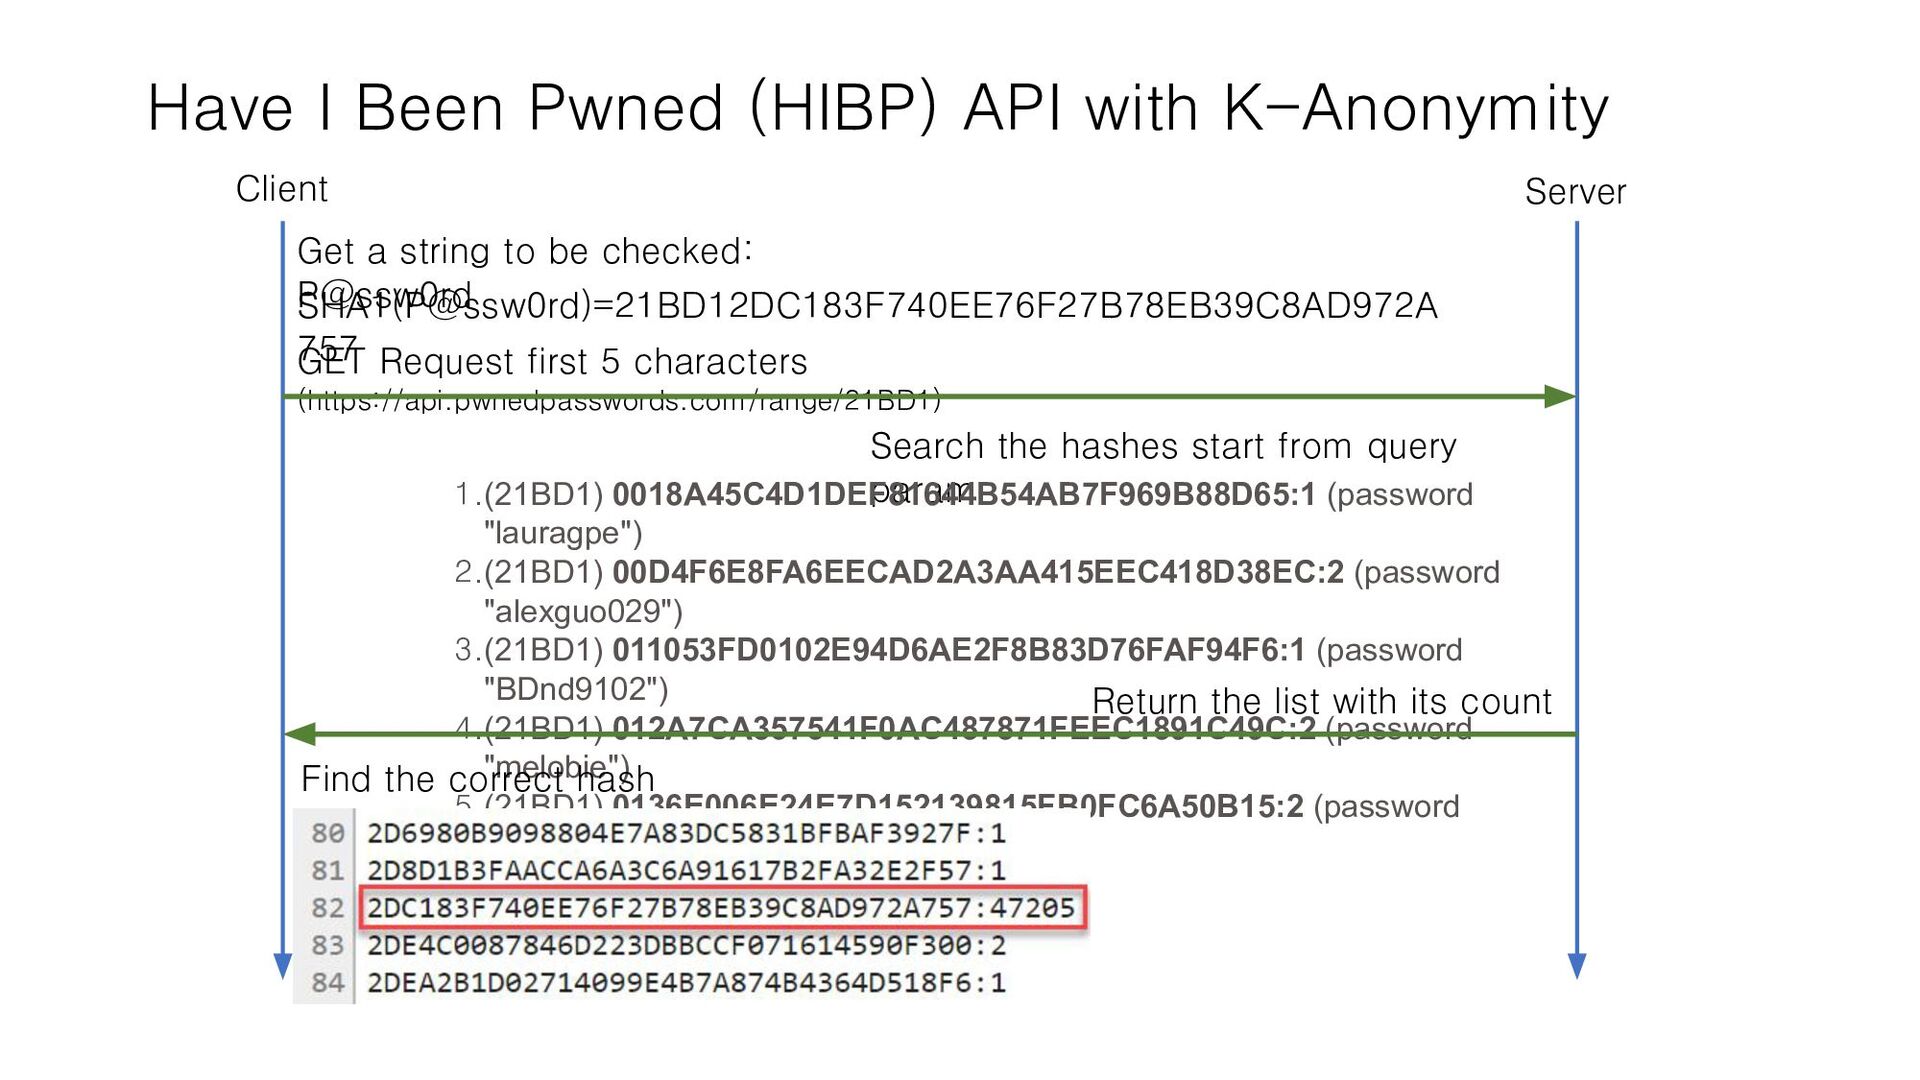
cases) • as long as possible • as random as possible • Do not reuse password • Check if the password is compromised (HIBP) • Its API is implemented with K-Anonymity • Different password for different sites
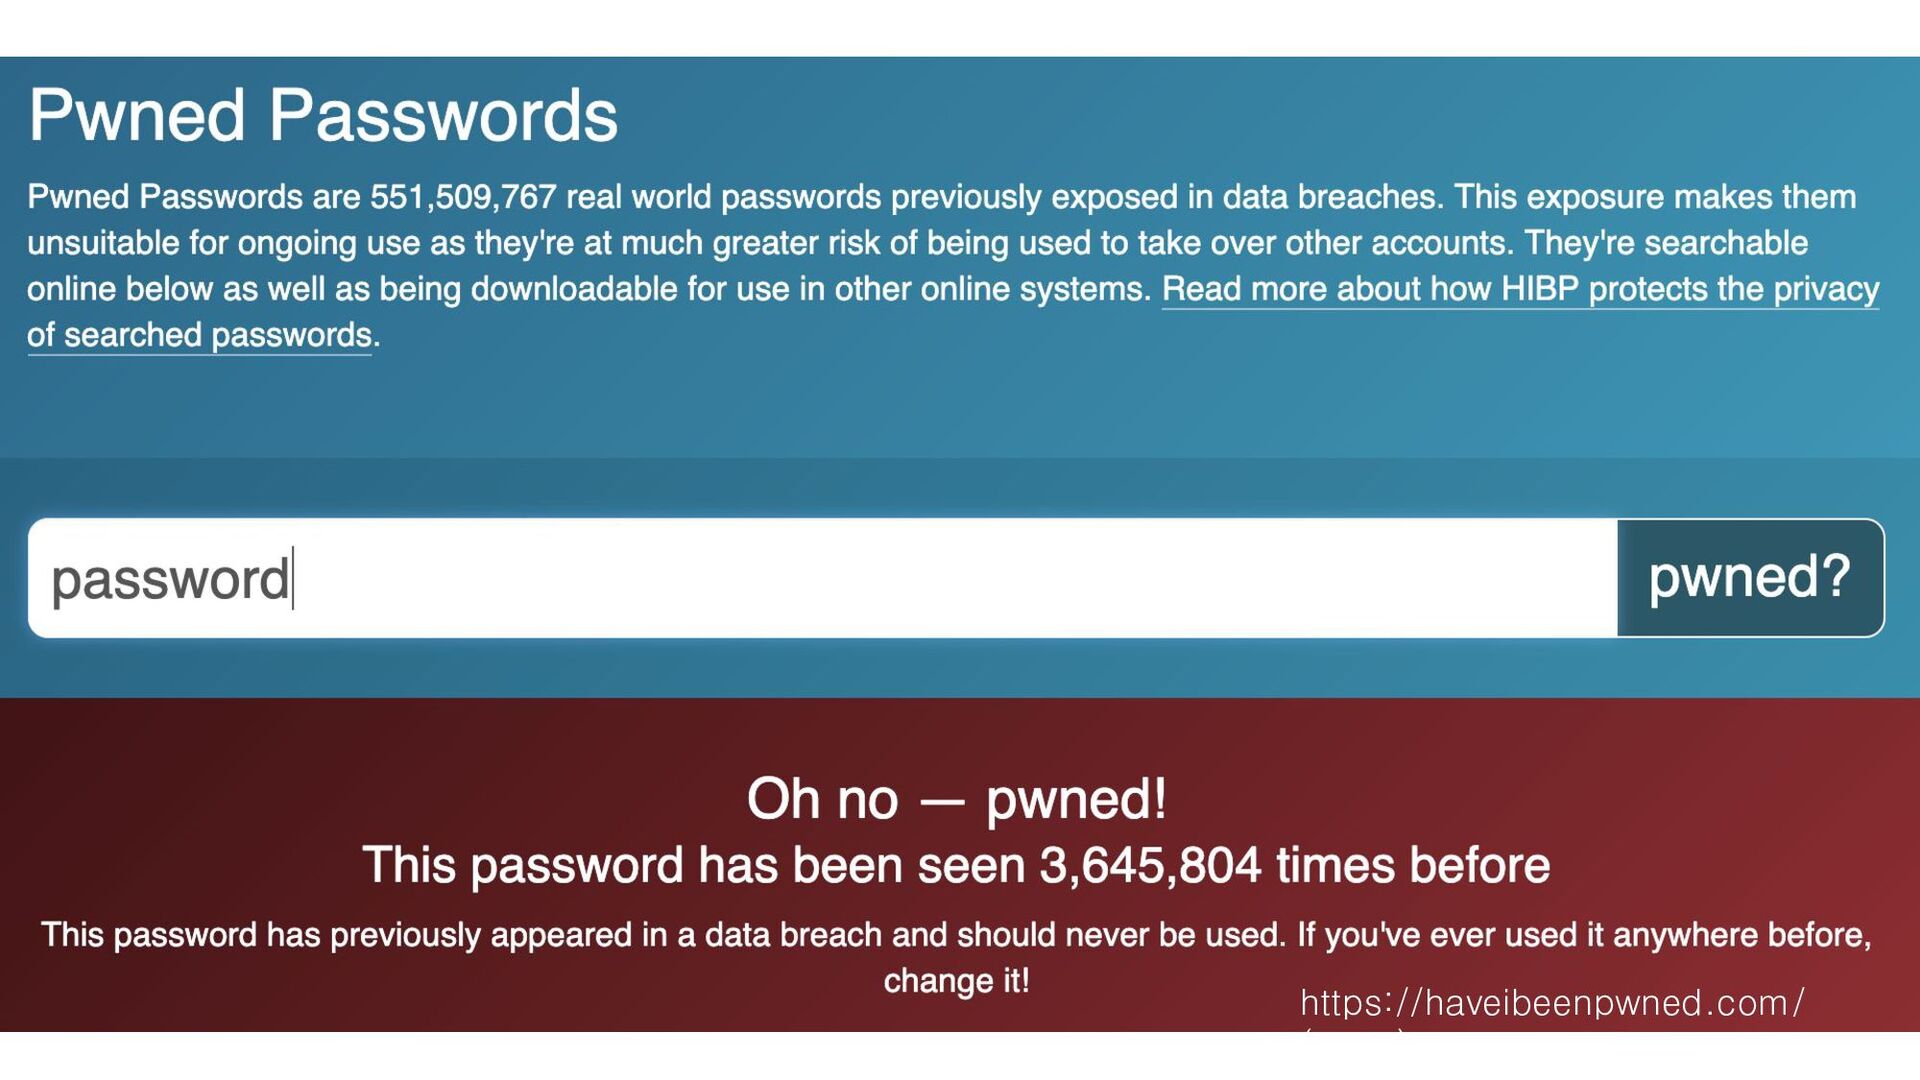
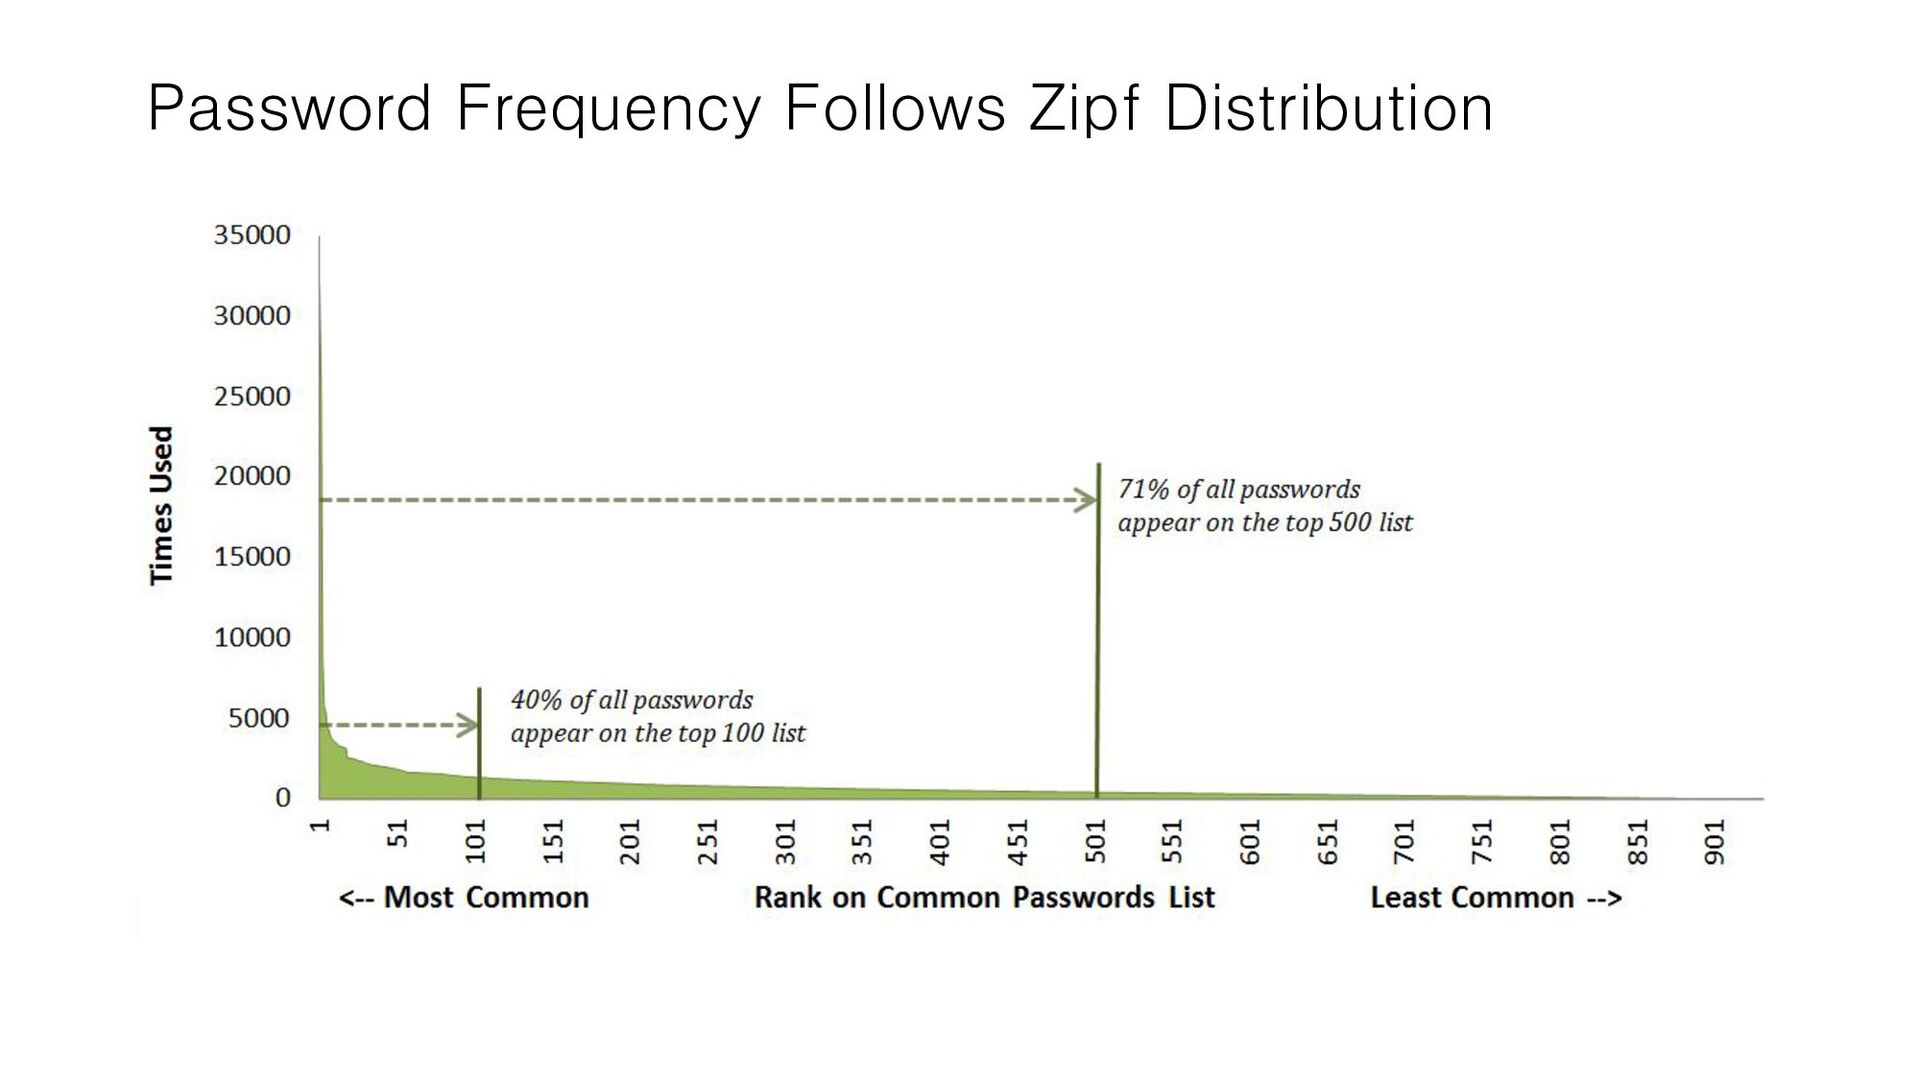
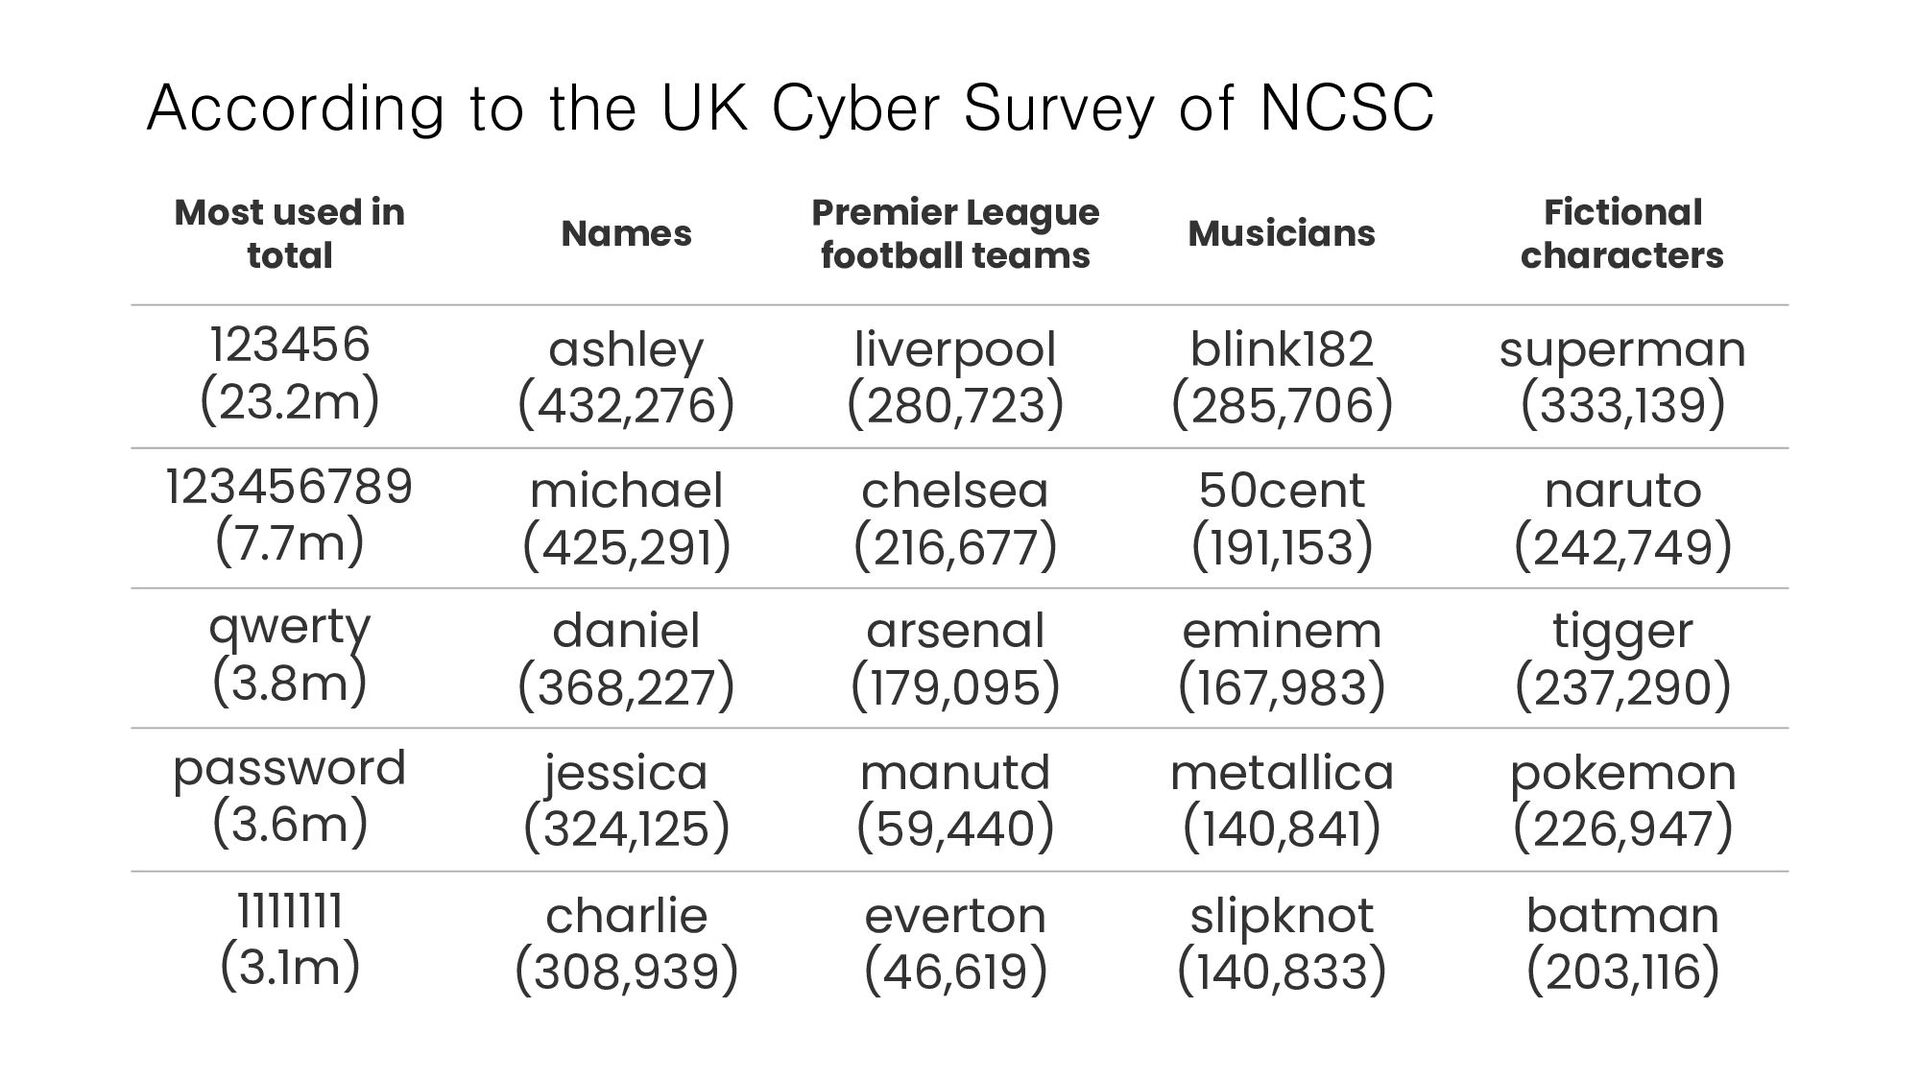
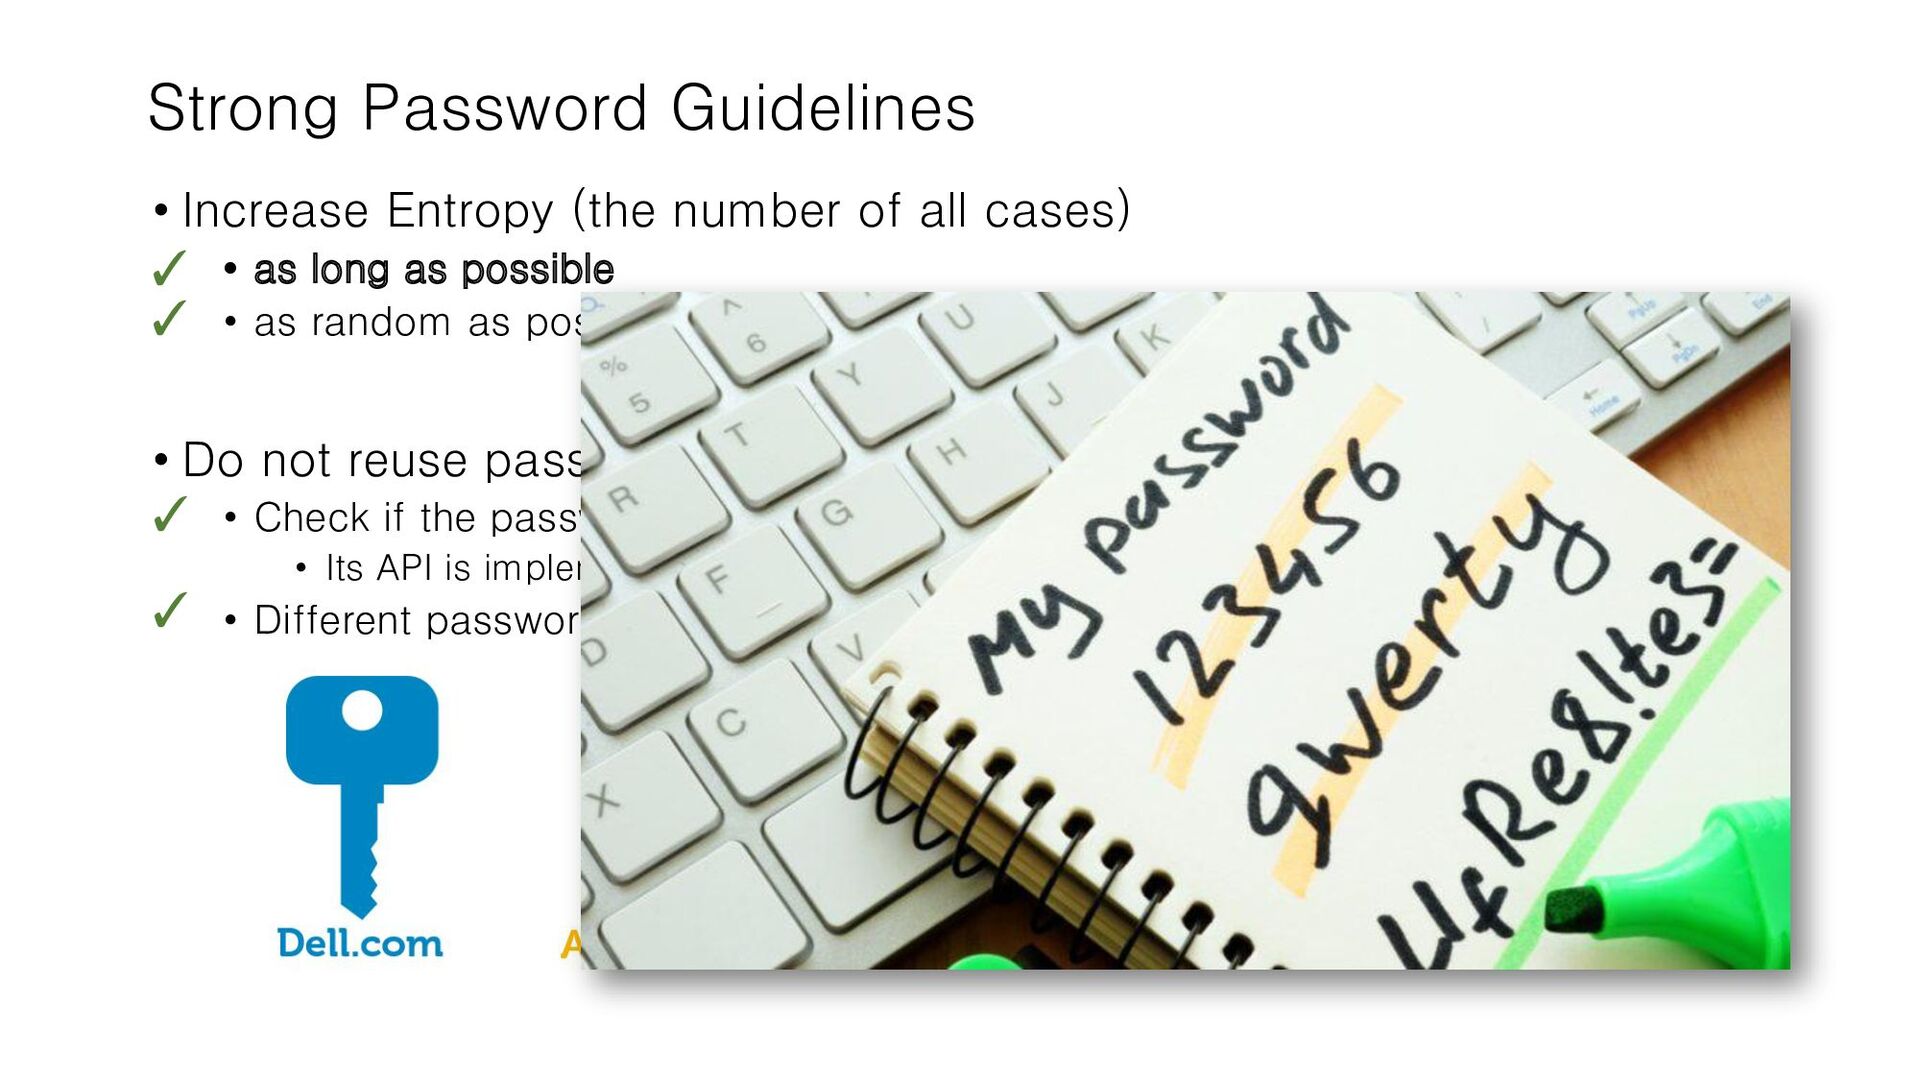
in total Names Premier League football teams Musicians Fictional characters 123456 (23.2m) ashley (432,276) liverpool (280,723) blink182 (285,706) superman (333,139) 123456789 (7.7m) michael (425,291) chelsea (216,677) 50cent (191,153) naruto (242,749) qwerty (3.8m) daniel (368,227) arsenal (179,095) eminem (167,983) tigger (237,290) password (3.6m) jessica (324,125) manutd (59,440) metallica (140,841) pokemon (226,947) 1111111 (3.1m) charlie (308,939) everton (46,619) slipknot (140,833) batman (203,116)
cases) • as long as possible • as random as possible • Do not reuse password • Check if the password is compromised (HIBP) • Its API is implemented with K-Anonymity • Different password for different sites ✓ ✓ ✓ ✓
cases) • as long as possible • as random as possible • Do not reuse password • Check if the password is compromised (HIBP) • Its API is implemented with K-Anonymity • Different password for different sites ✓ ✓ ✓ ✓
• Too many passwords to remember if we use different passwords for different sites • Do you remember the password Chrome suggested? • Write somewhere • In TXT file • Take pictures • In cloud storage with encryption (Evernote, Dropbox, Google Drive, …) • …
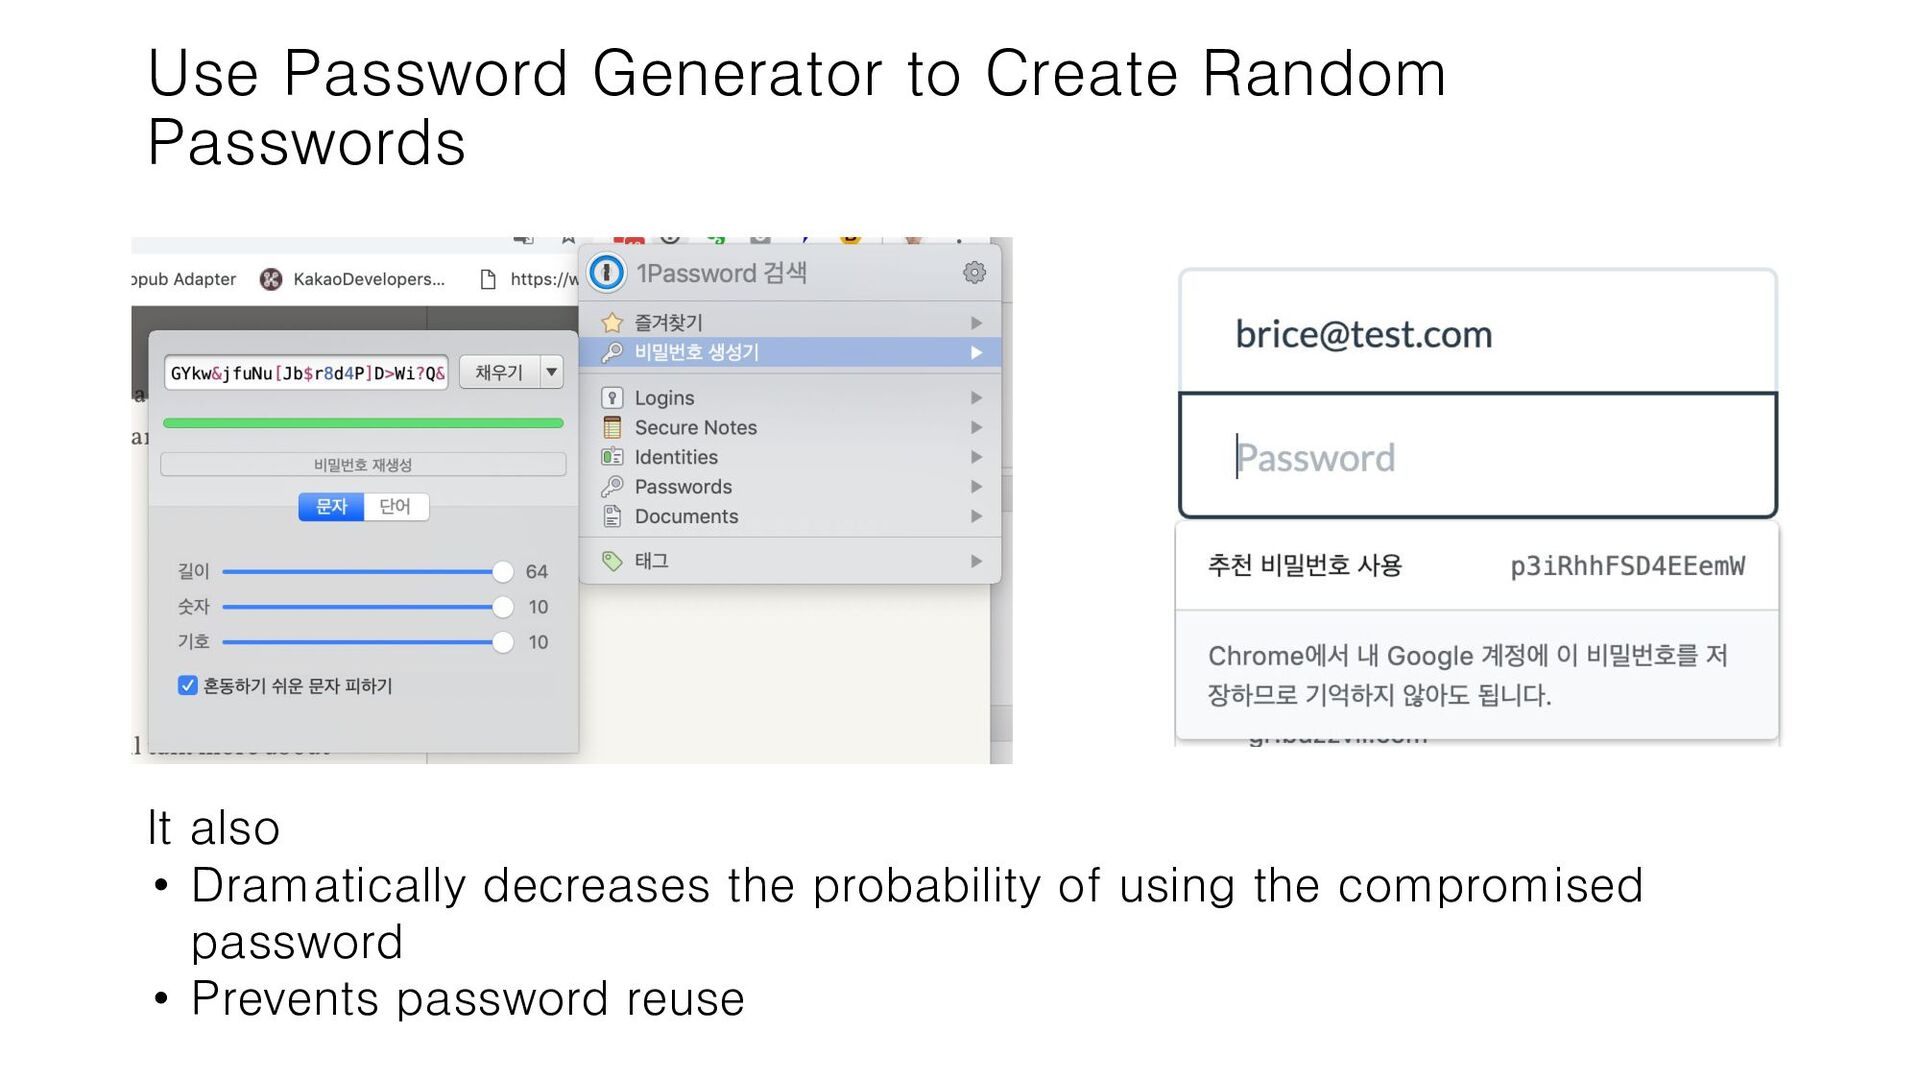
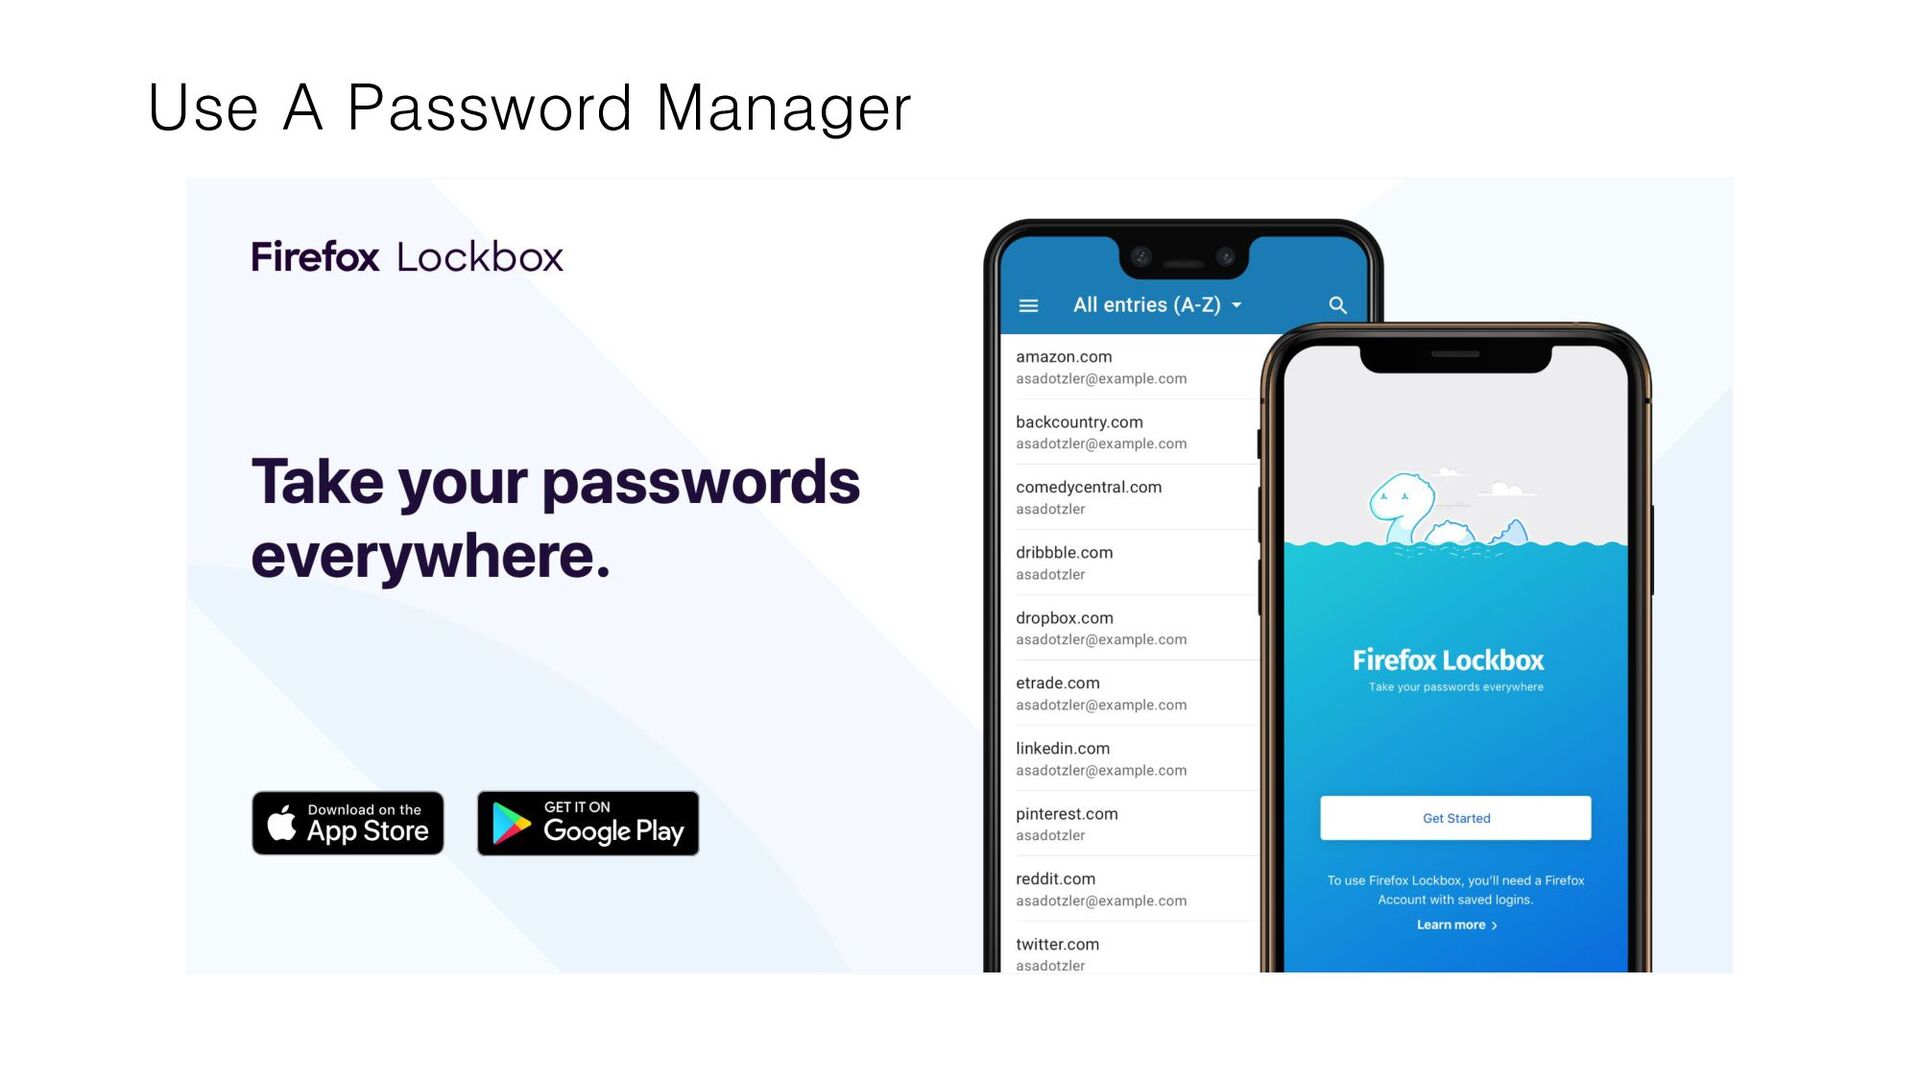
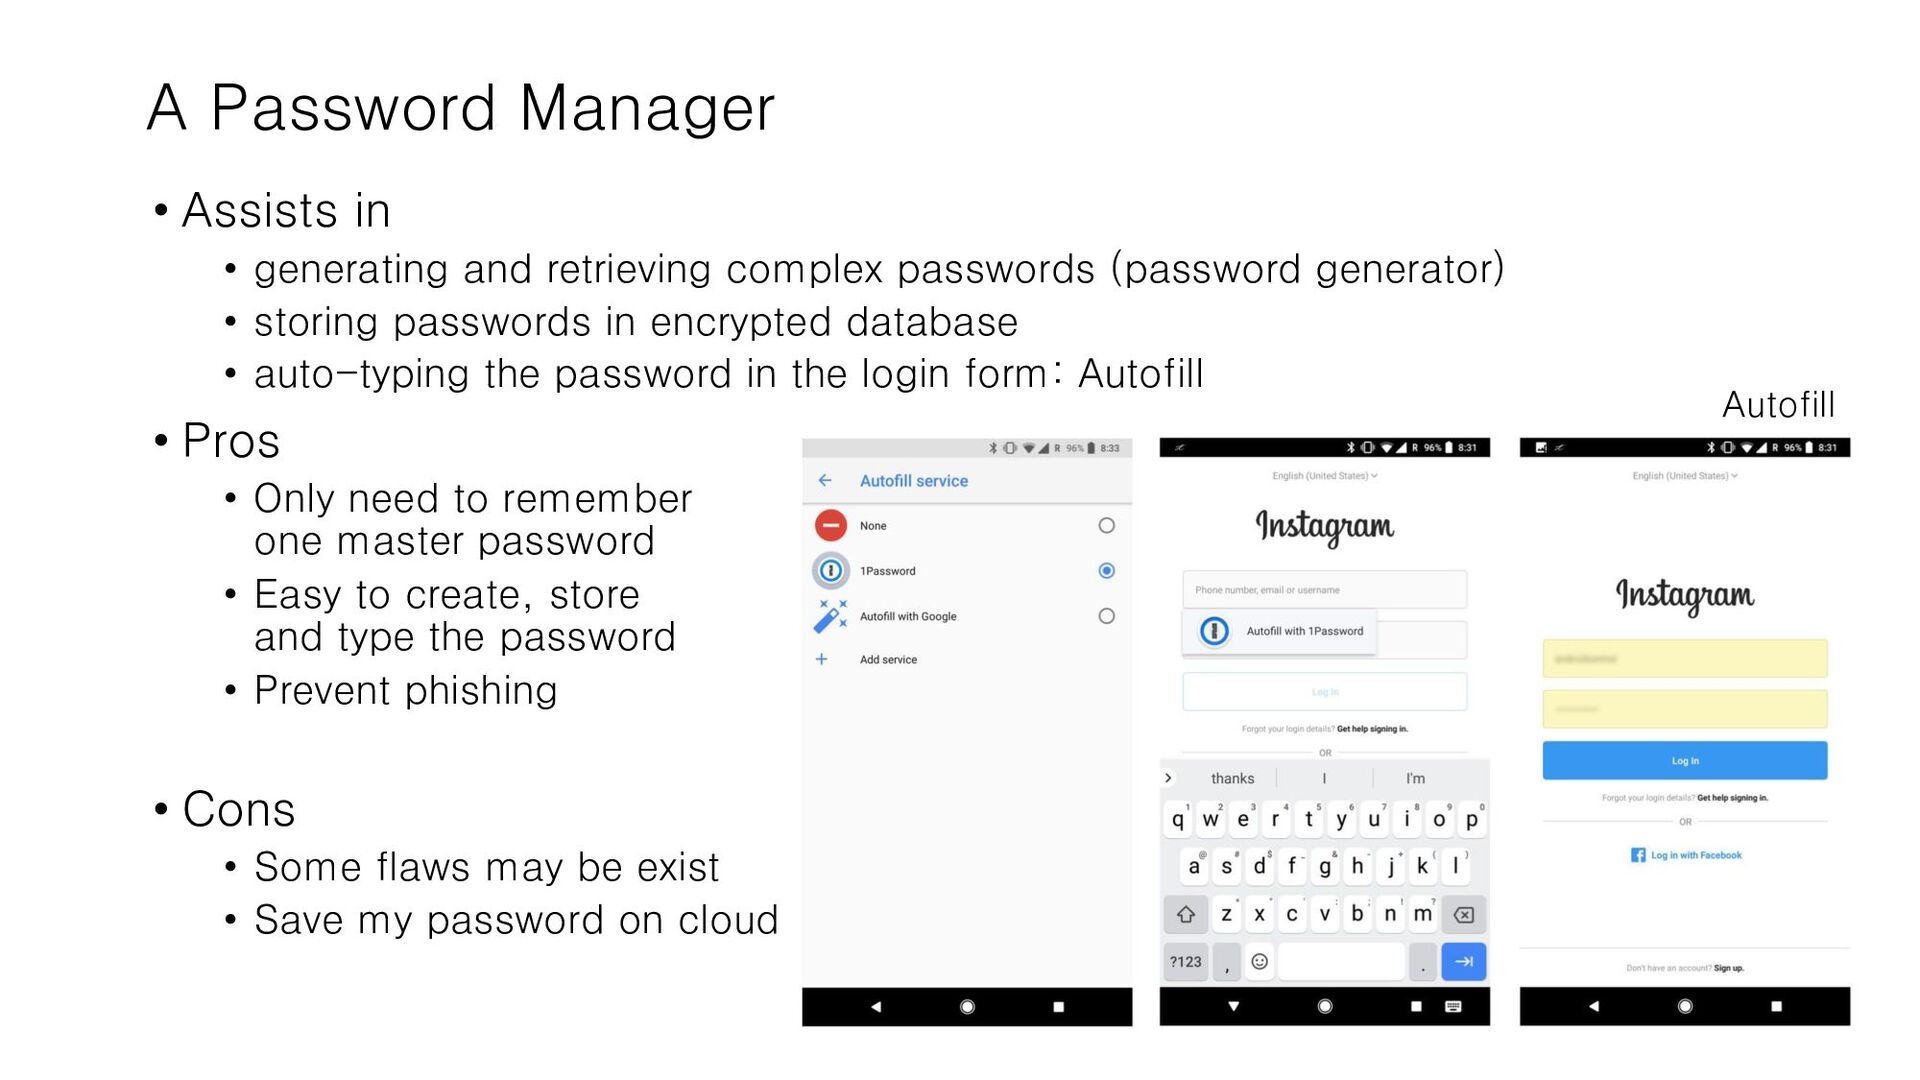
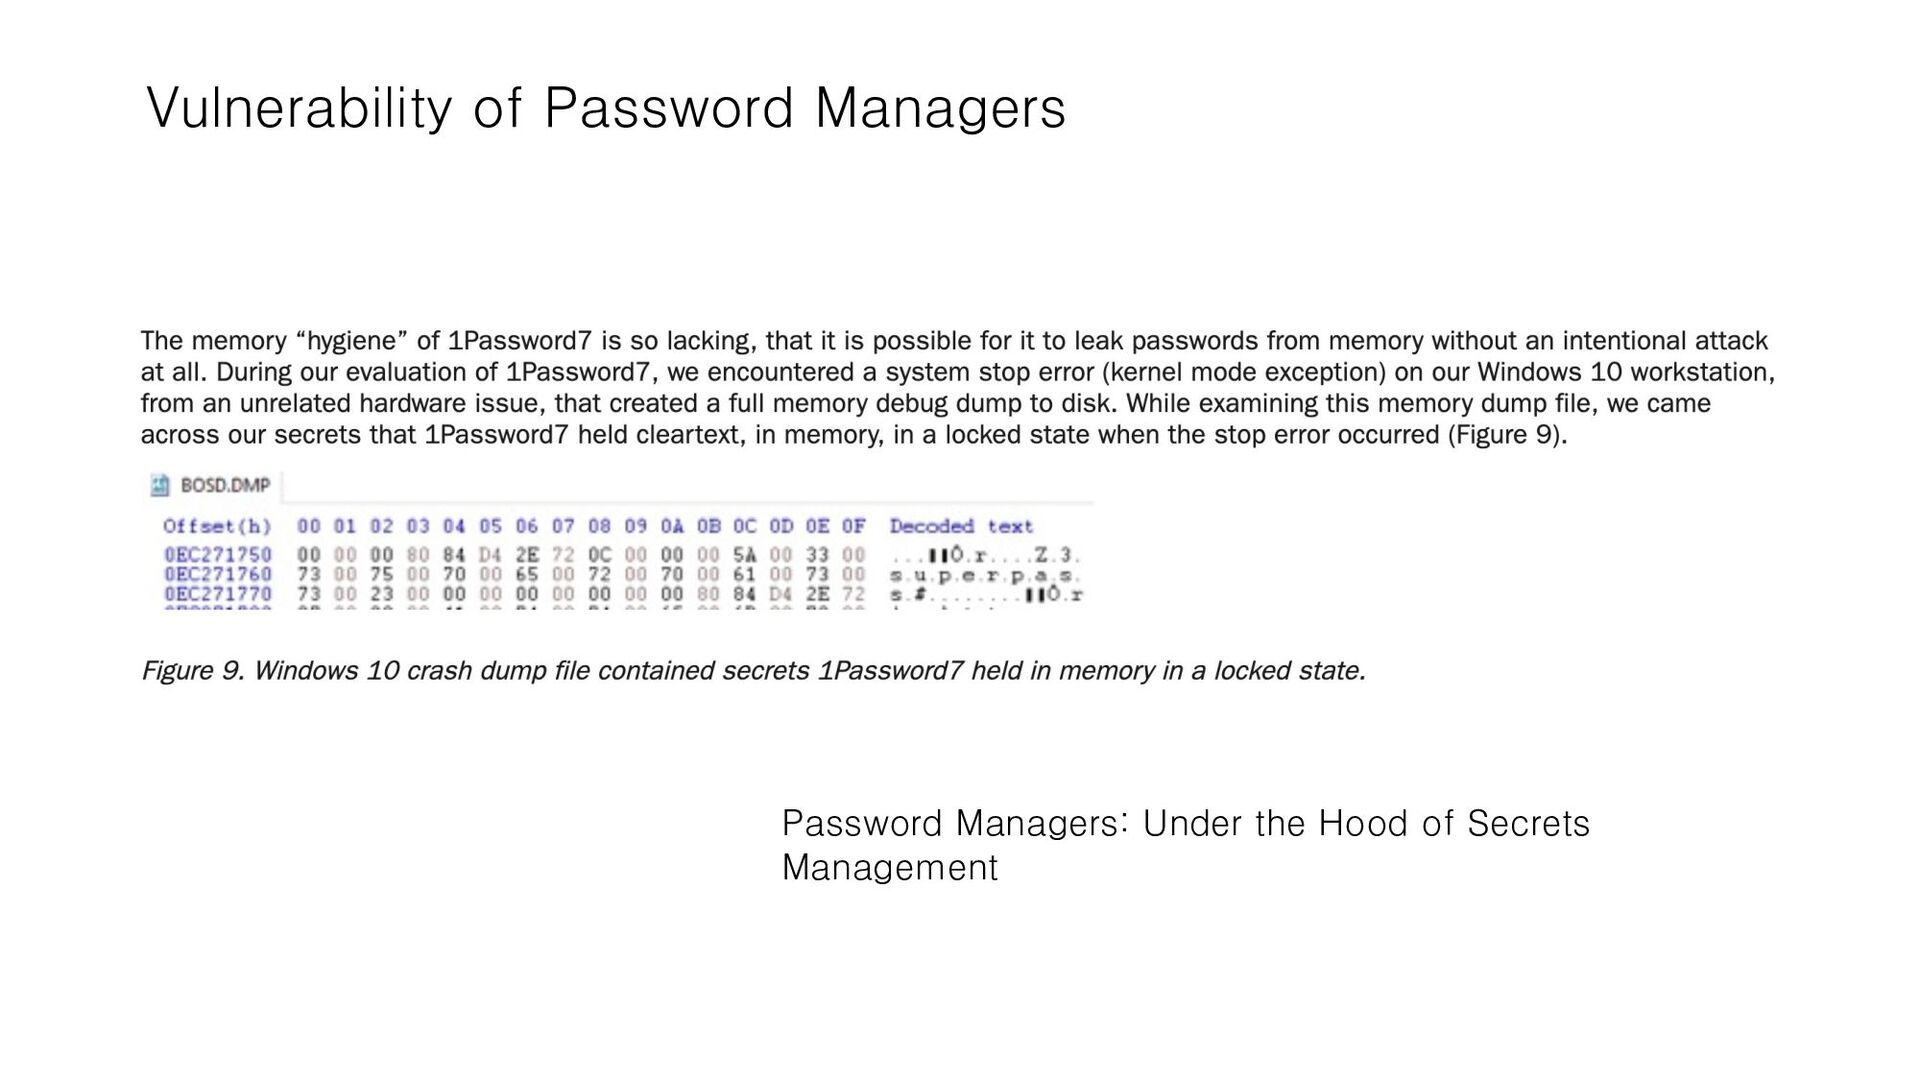
complex passwords (password generator) • storing passwords in encrypted database • auto-typing the password in the login form: Autofill • Pros • Only need to remember one master password • Easy to create, store and type the password • Prevent phishing • Cons • Some flaws may be exist • Save my password on cloud Autofill
on PasteBin Winwinsoft denied our proposal to negotiate with us. But, we are generous and our window to negotiations is still open. We will disclose every information we have in a few days if the negotiation is denied. Until then, stay tuned :) P.S. Here are some informations that we have.
on PasteBin Winwinsoft denied our proposal to negotiate with us. But, we are generous and our window to negotiations is still open. We will disclose every information we have in a few days if the negotiation is denied. Until then, stay tuned :) P.S. Here are some informations that we have.
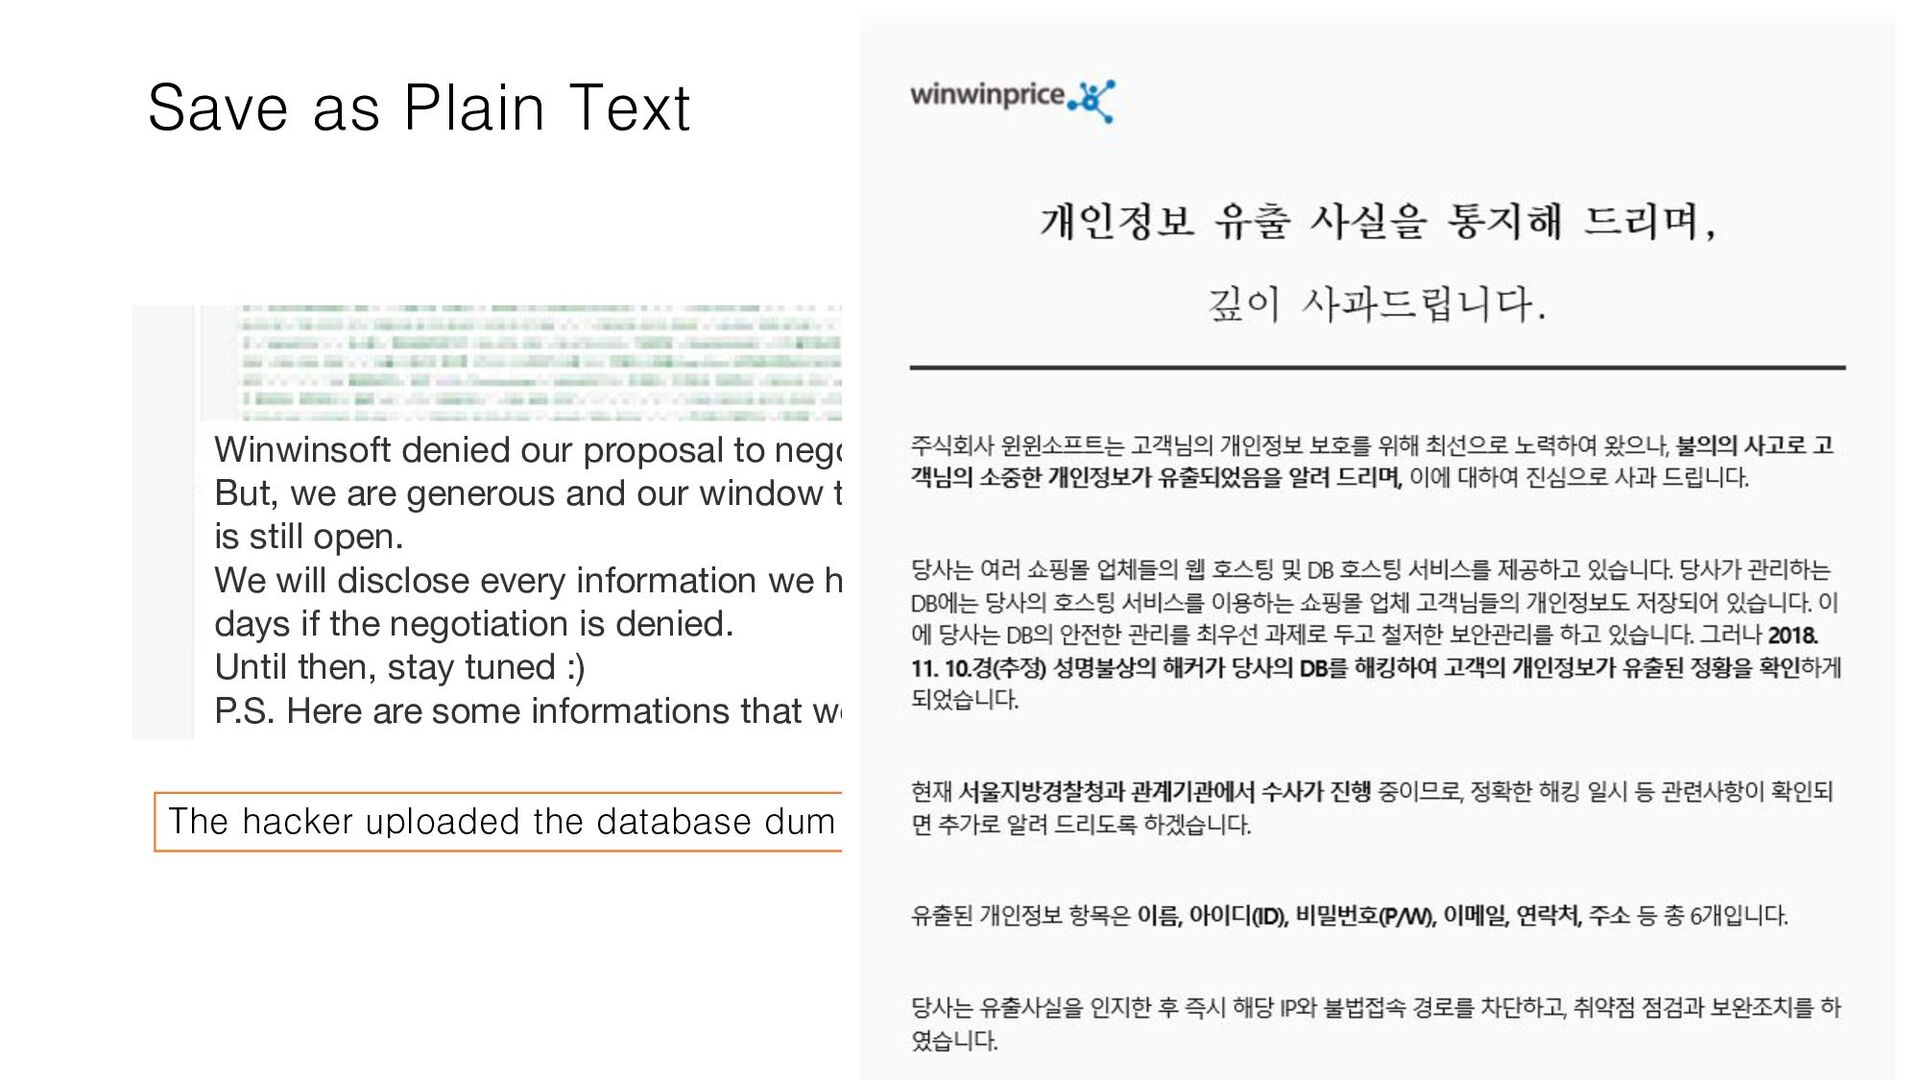
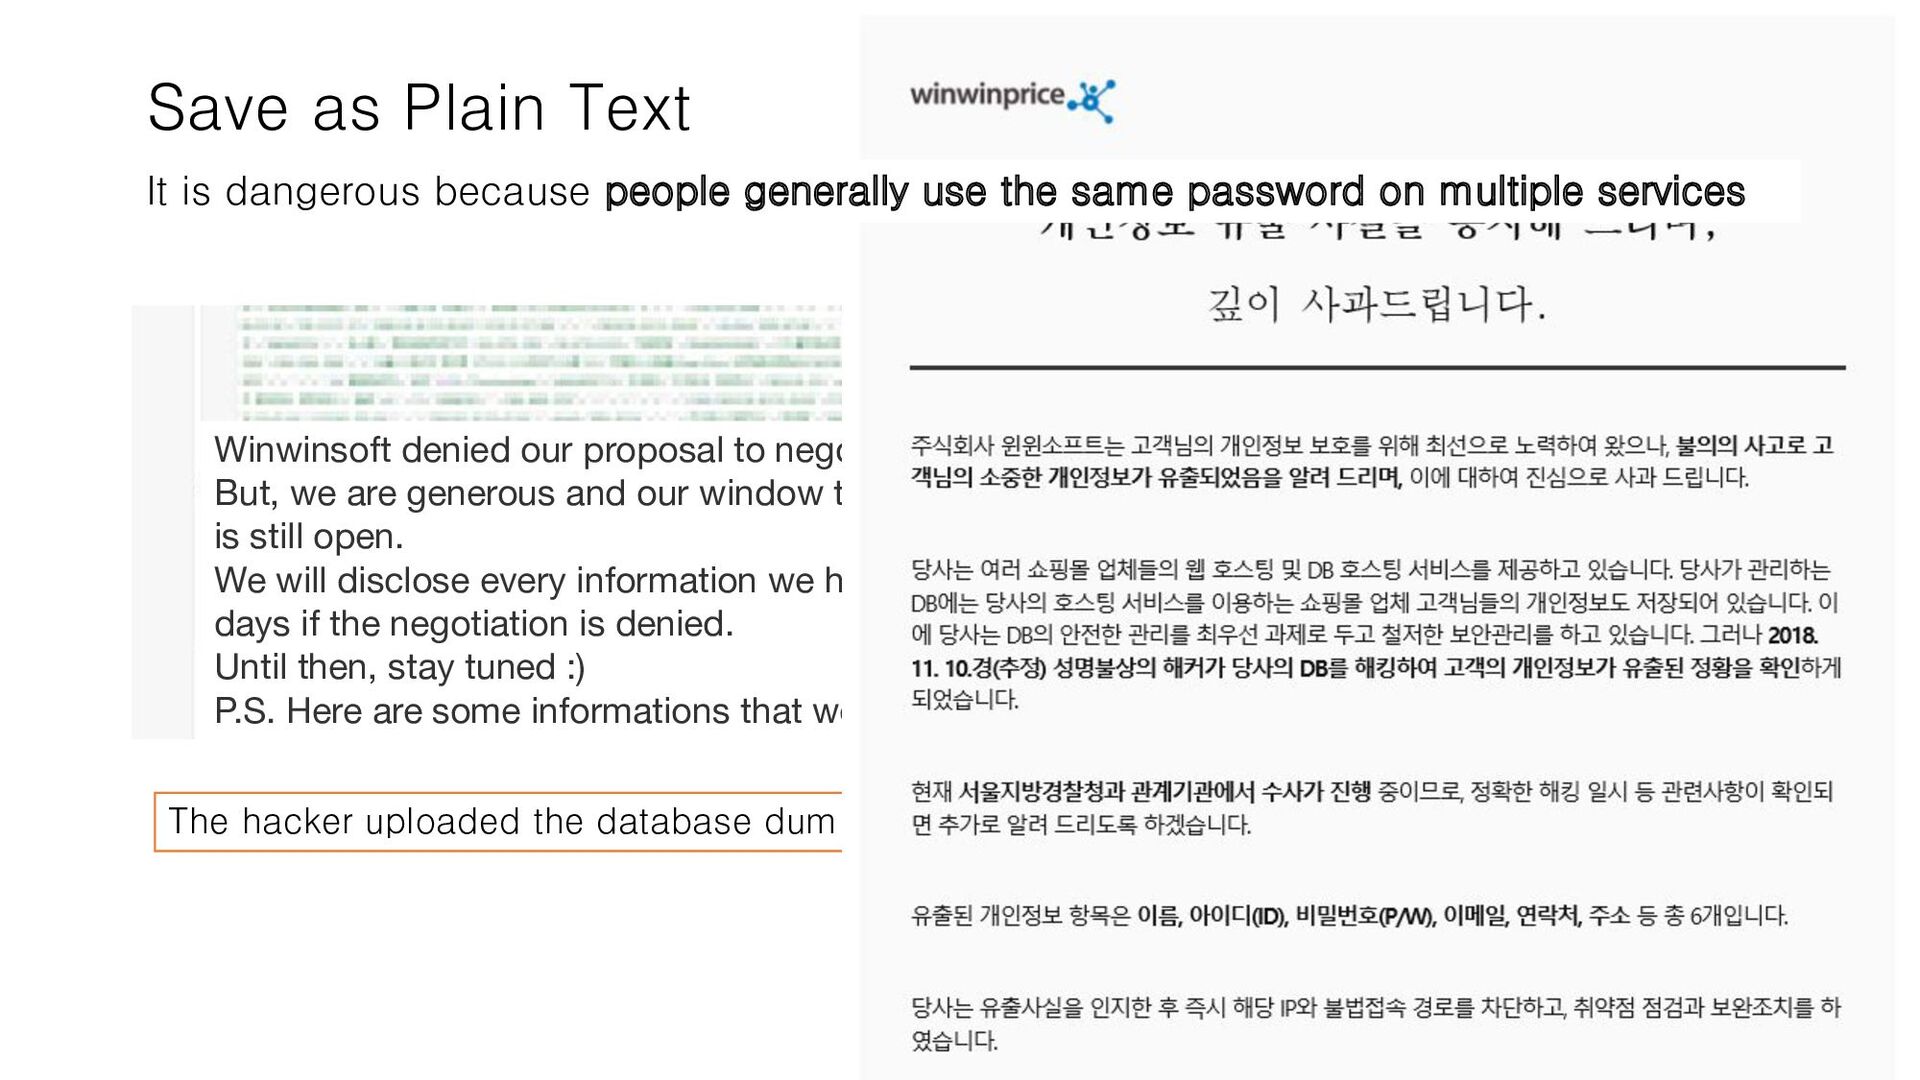
on PasteBin Winwinsoft denied our proposal to negotiate with us. But, we are generous and our window to negotiations is still open. We will disclose every information we have in a few days if the negotiation is denied. Until then, stay tuned :) P.S. Here are some informations that we have. It is dangerous because people generally use the same password on multiple services
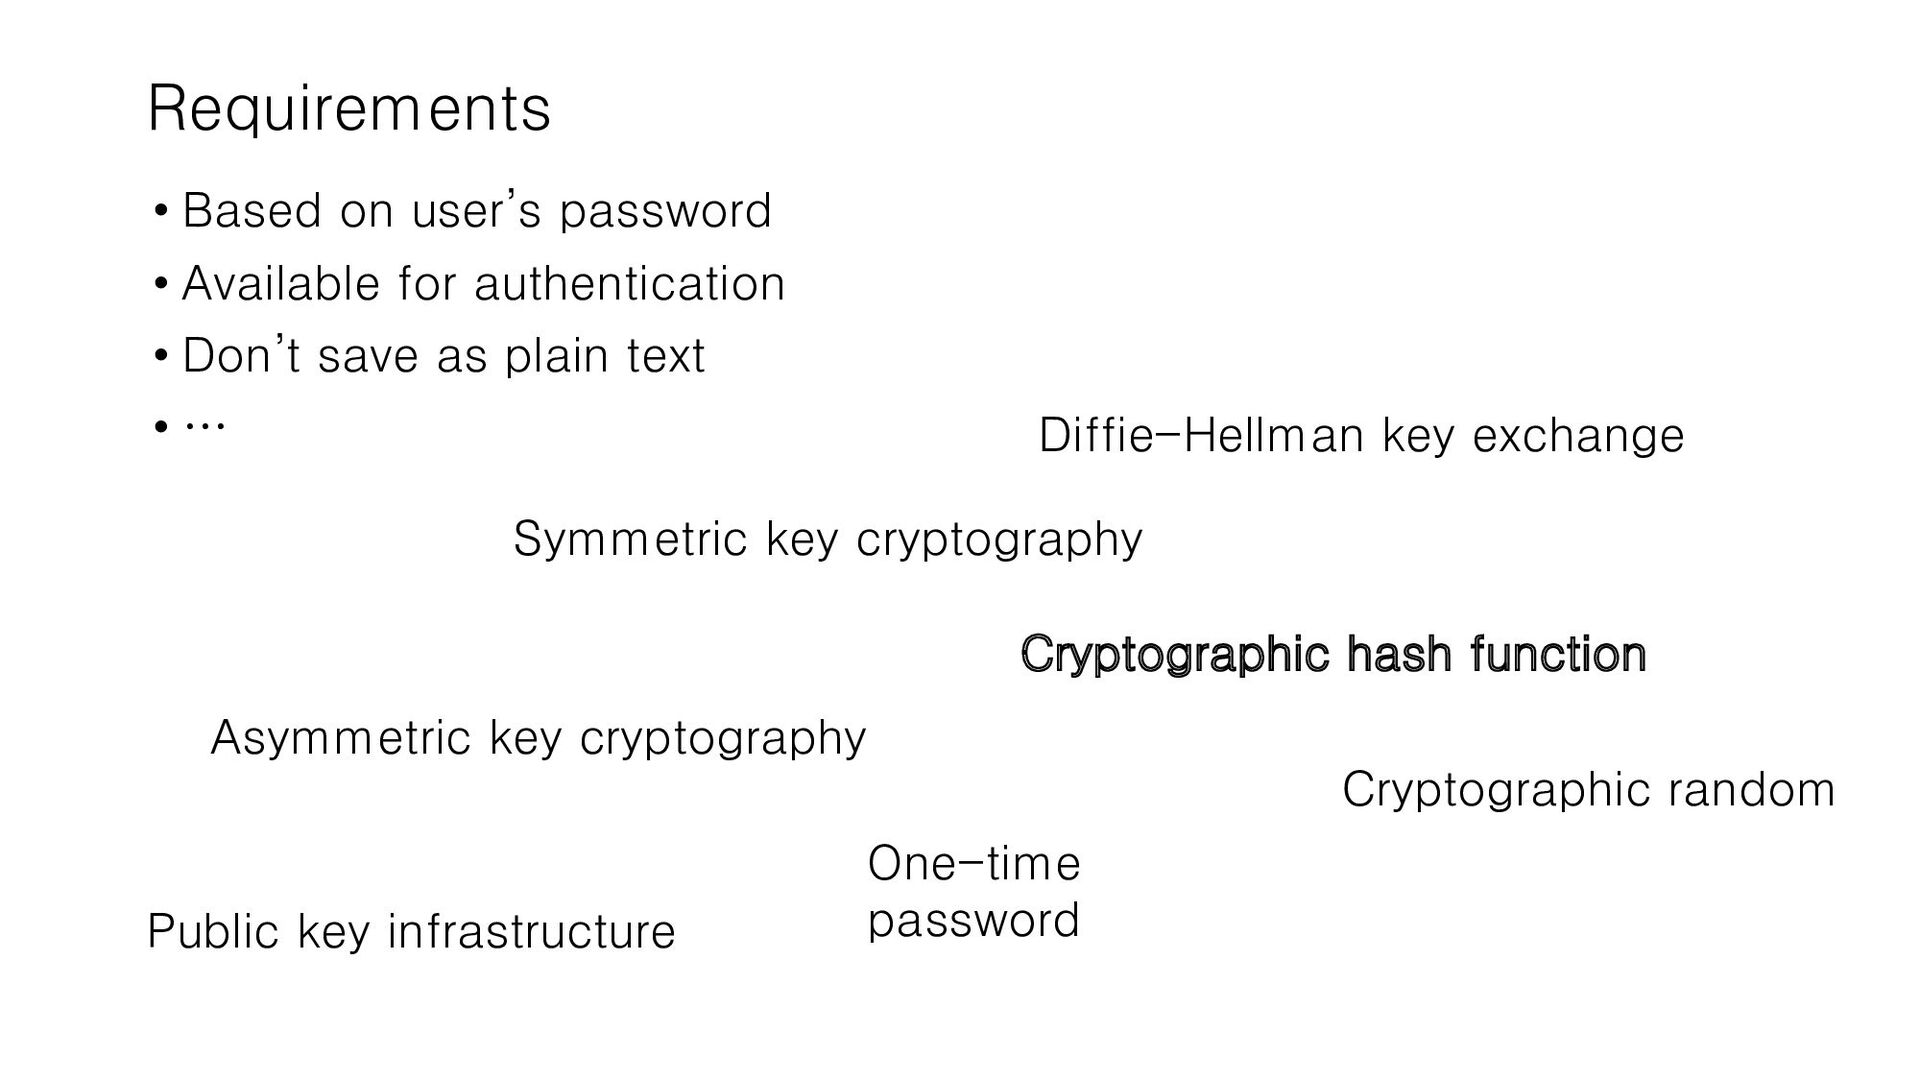
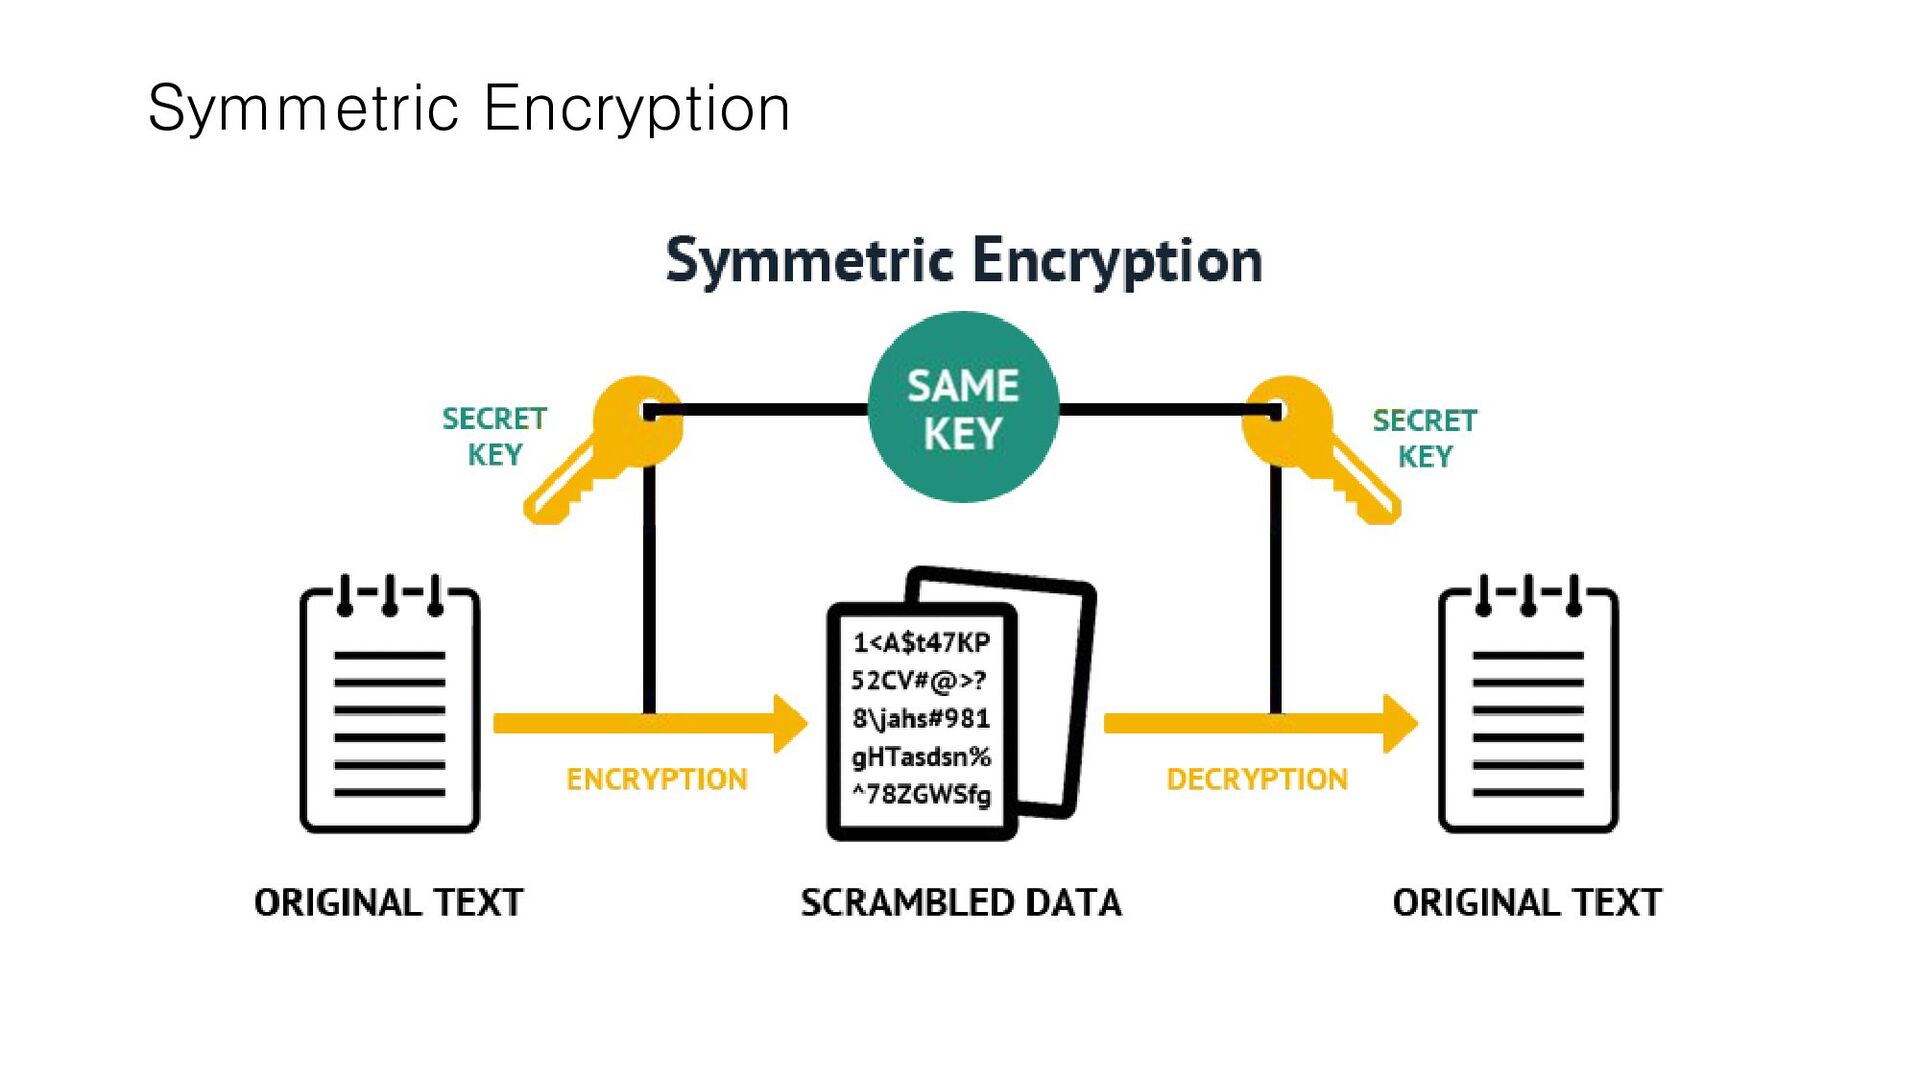
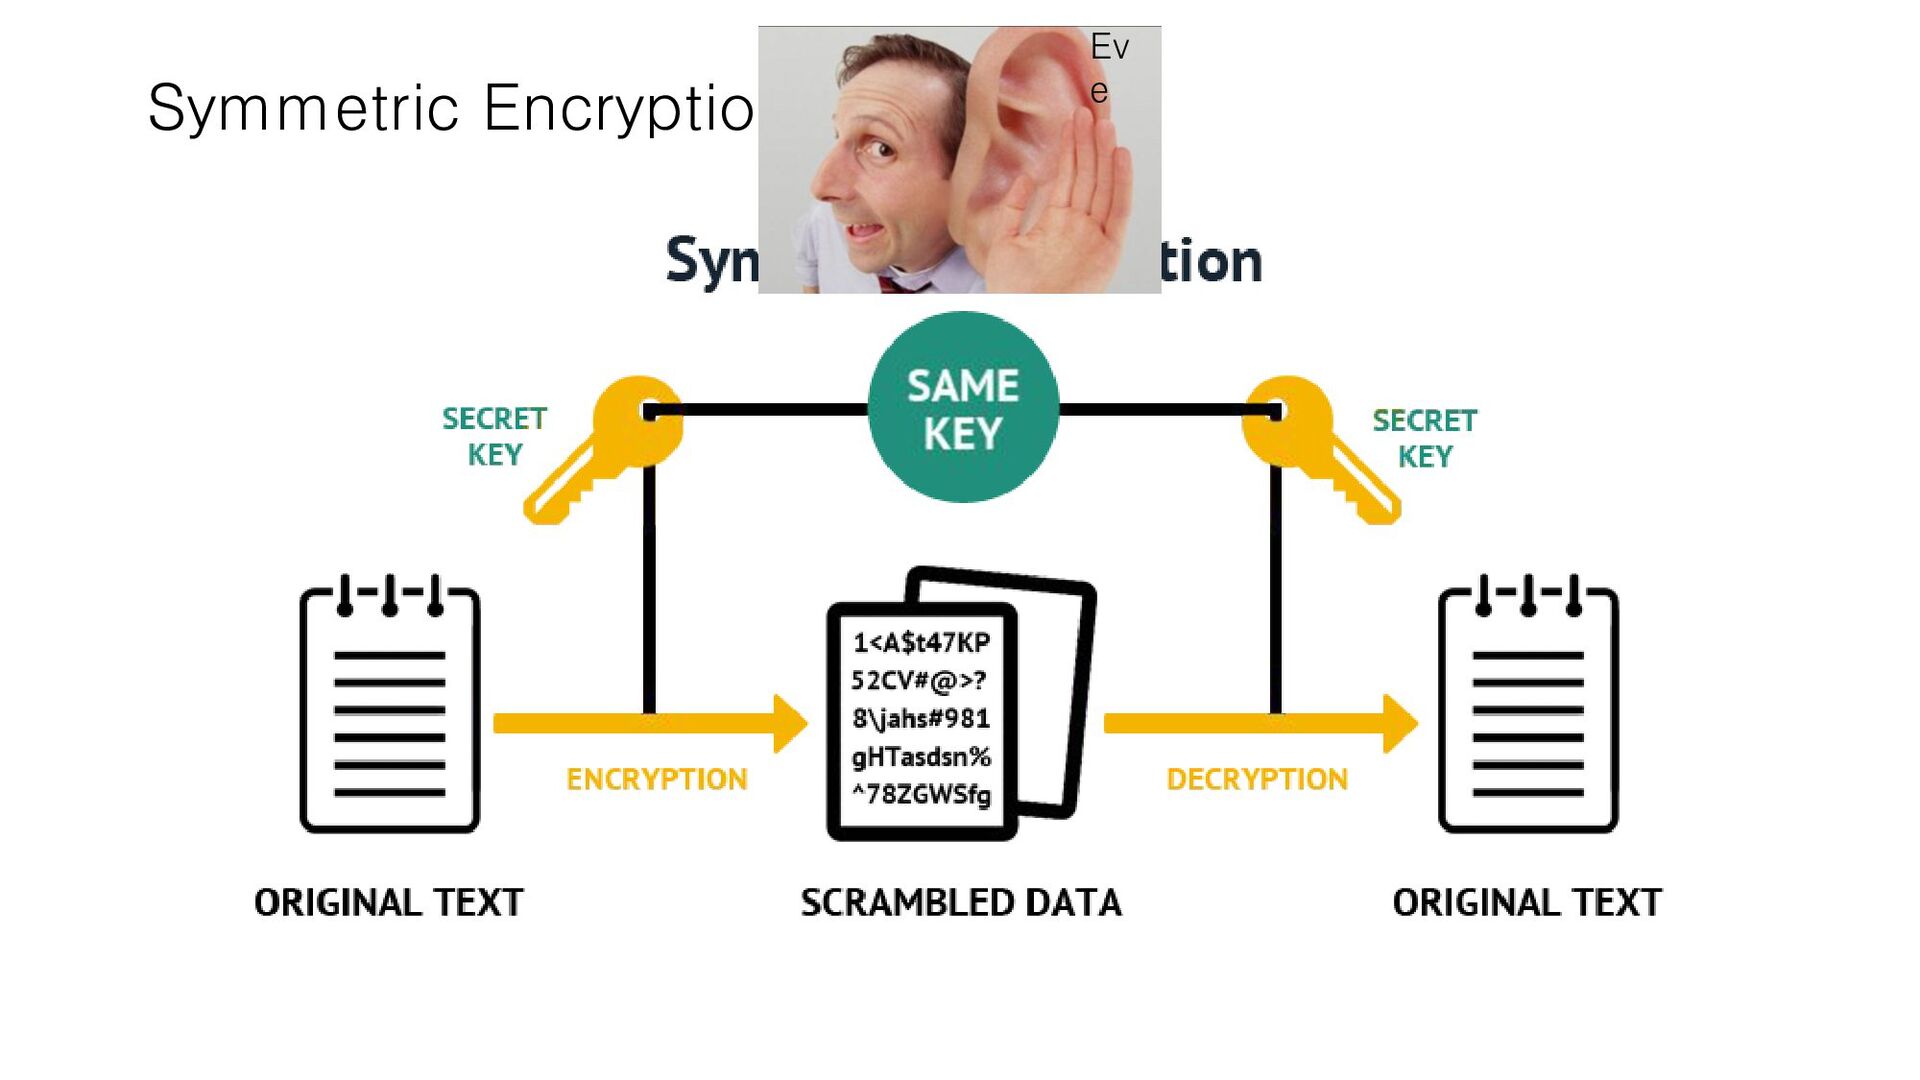
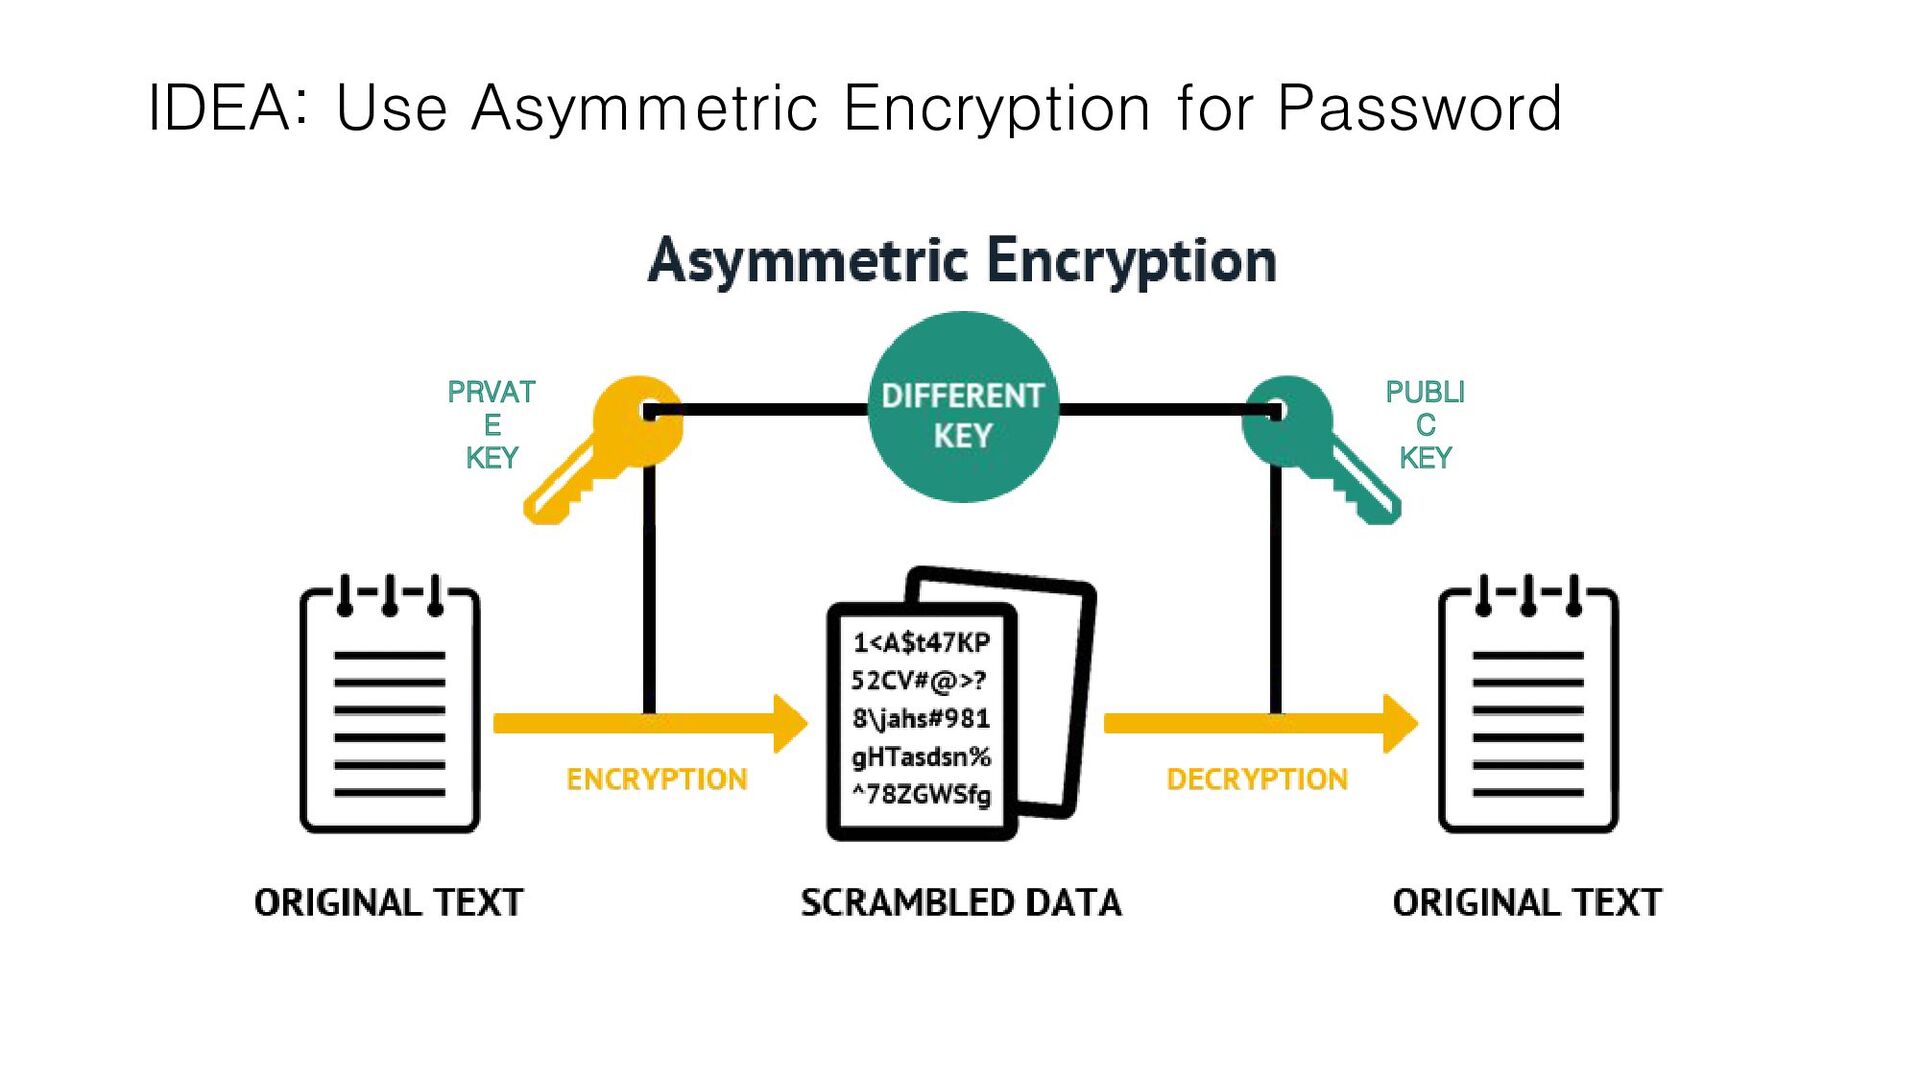
• Don’t save as plain text • … Symmetric key cryptography Asymmetric key cryptography Cryptographic hash function One-time password Cryptographic random Public key infrastructure Diffie-Hellman key exchange
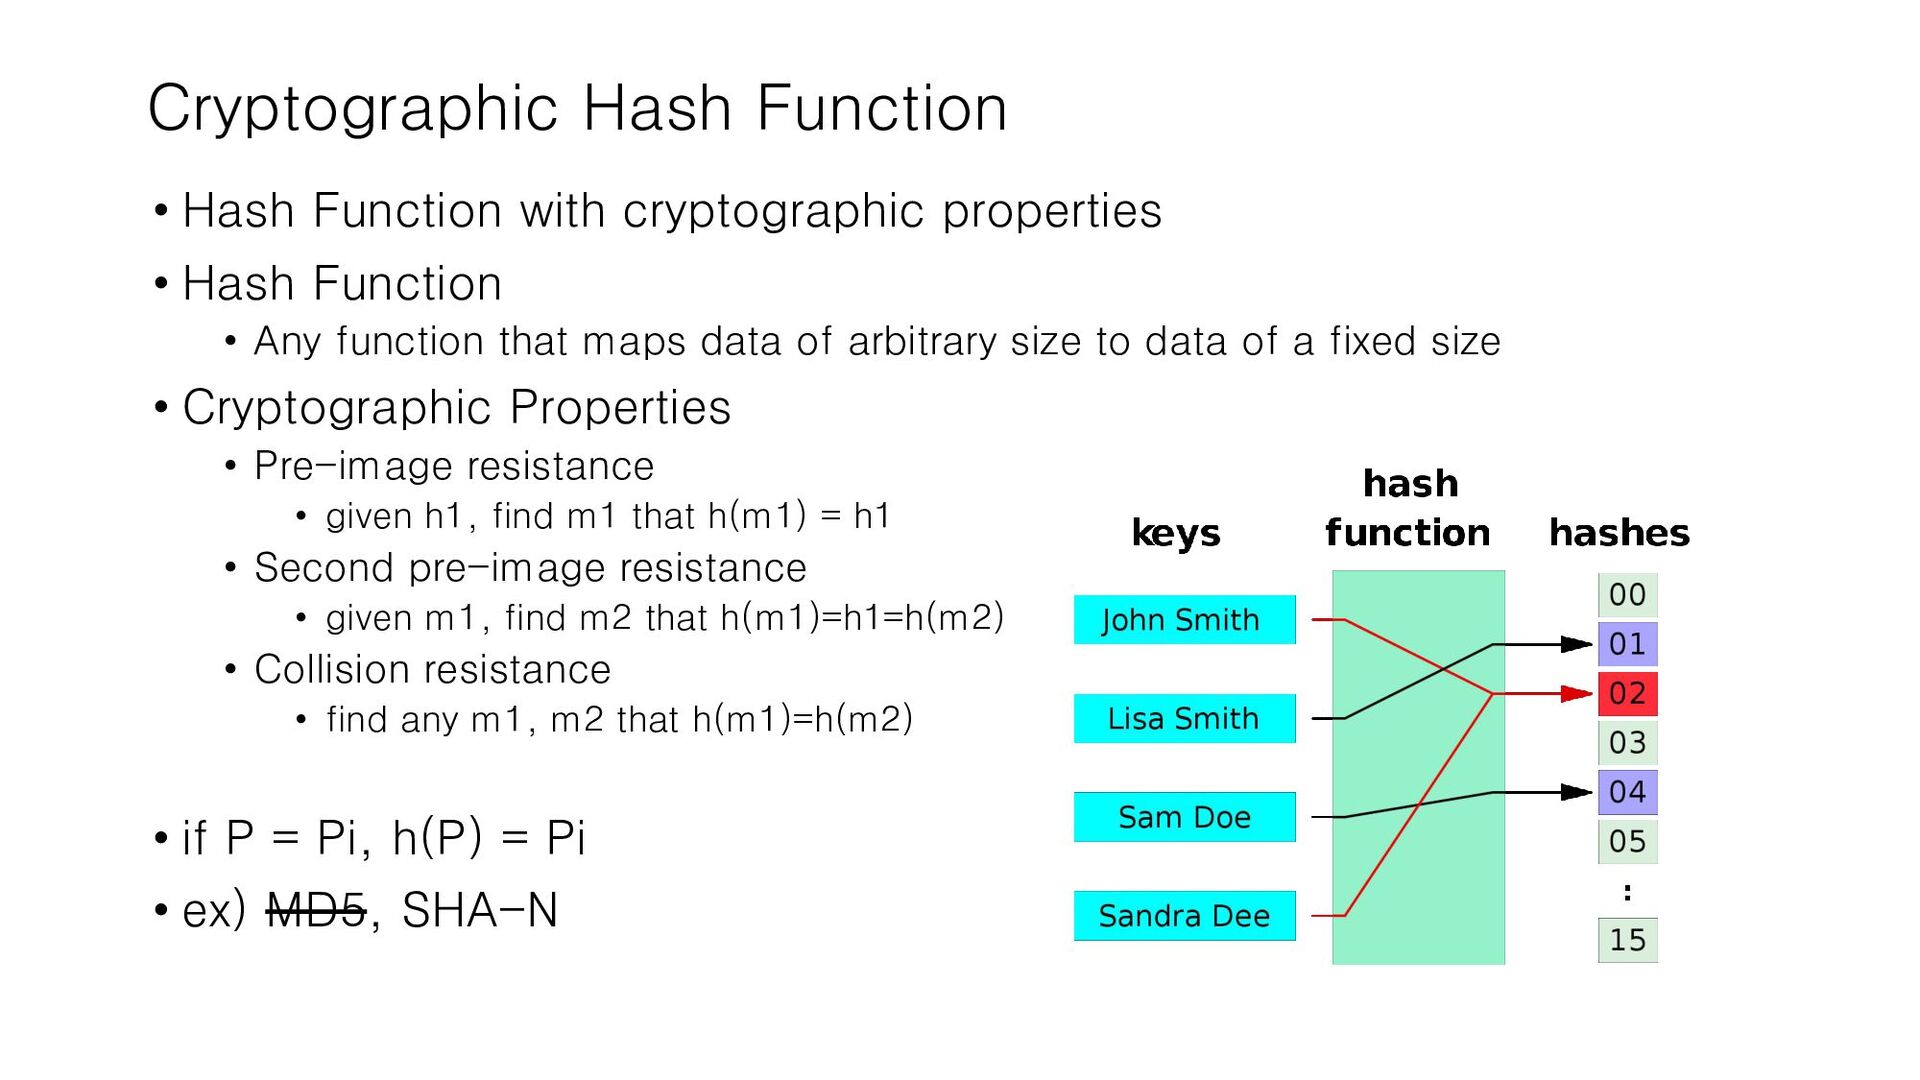
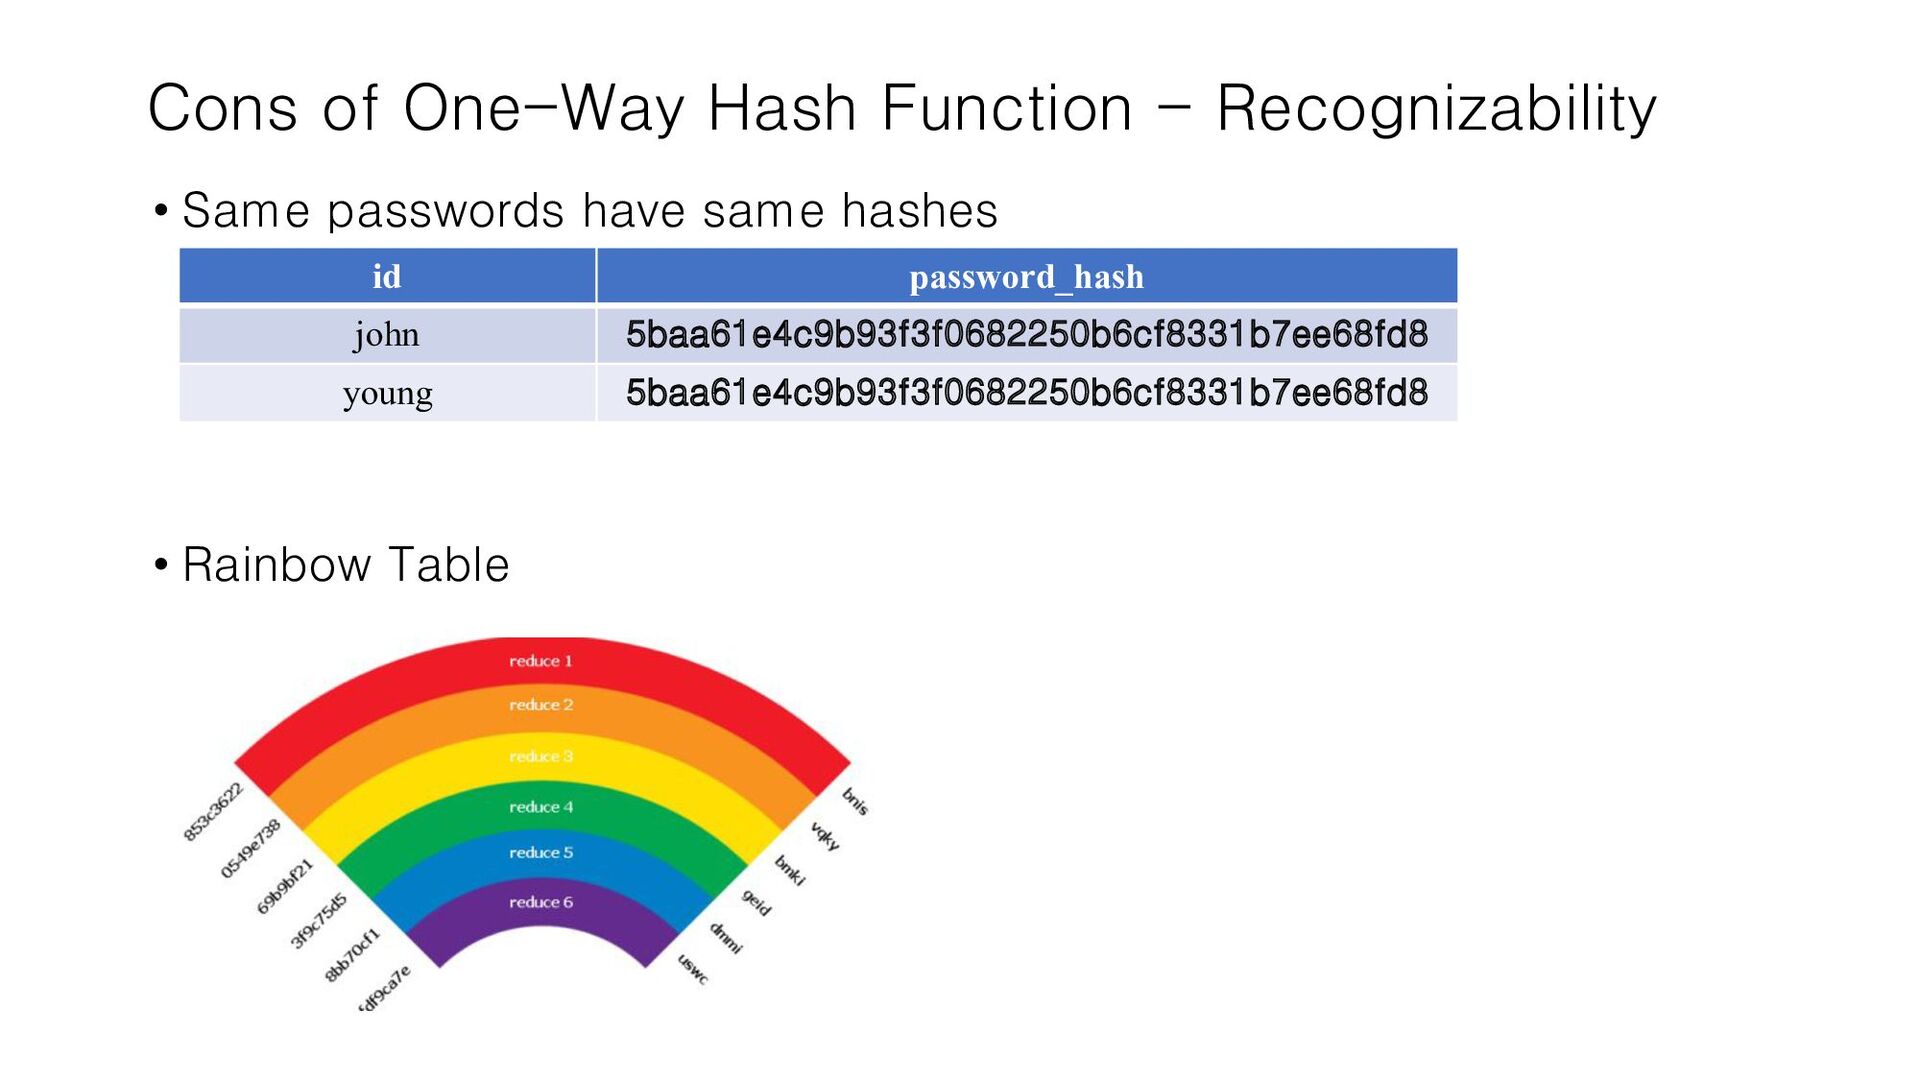
Hash Function • Any function that maps data of arbitrary size to data of a fixed size • Cryptographic Properties • Pre-image resistance • given h1, find m1 that h(m1) = h1 • Second pre-image resistance • given m1, find m2 that h(m1)=h1=h(m2) • Collision resistance • find any m1, m2 that h(m1)=h(m2) • if P = Pi, h(P) = Pi • ex) MD5, SHA-N
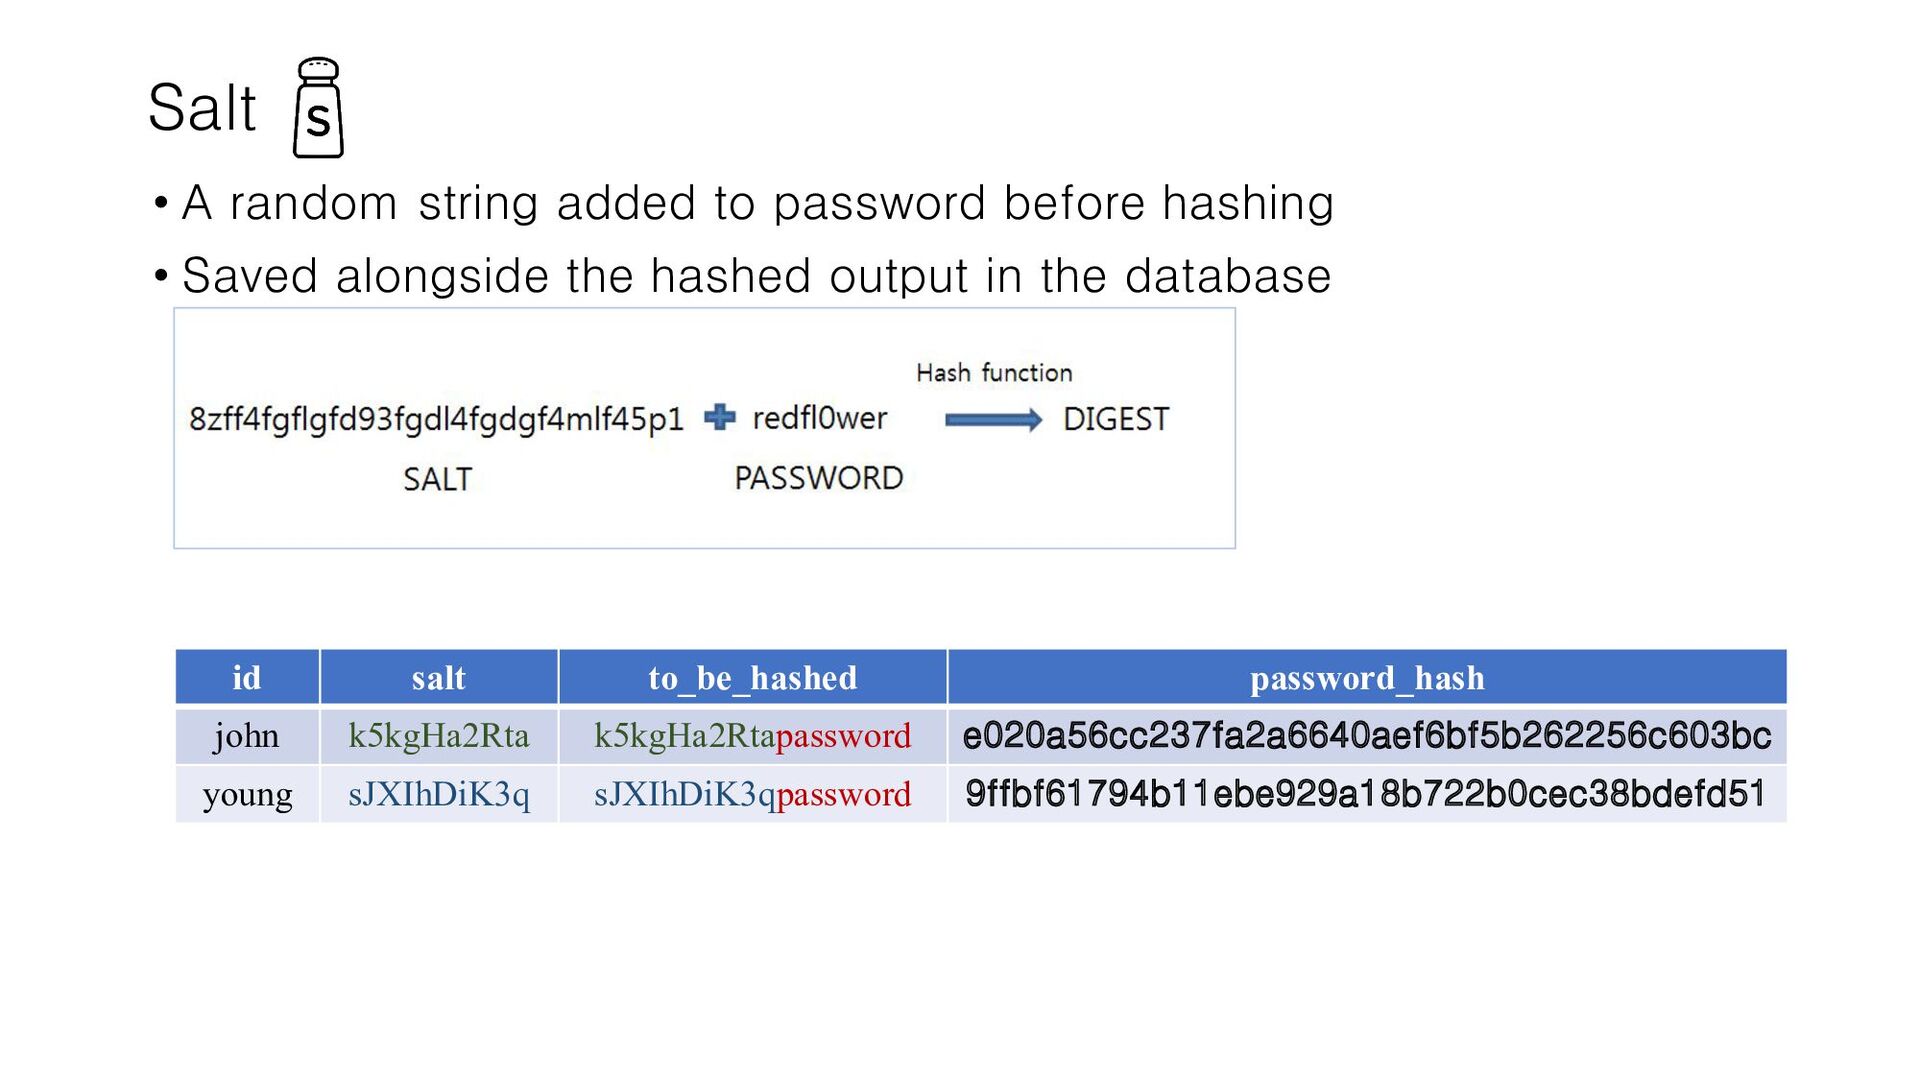
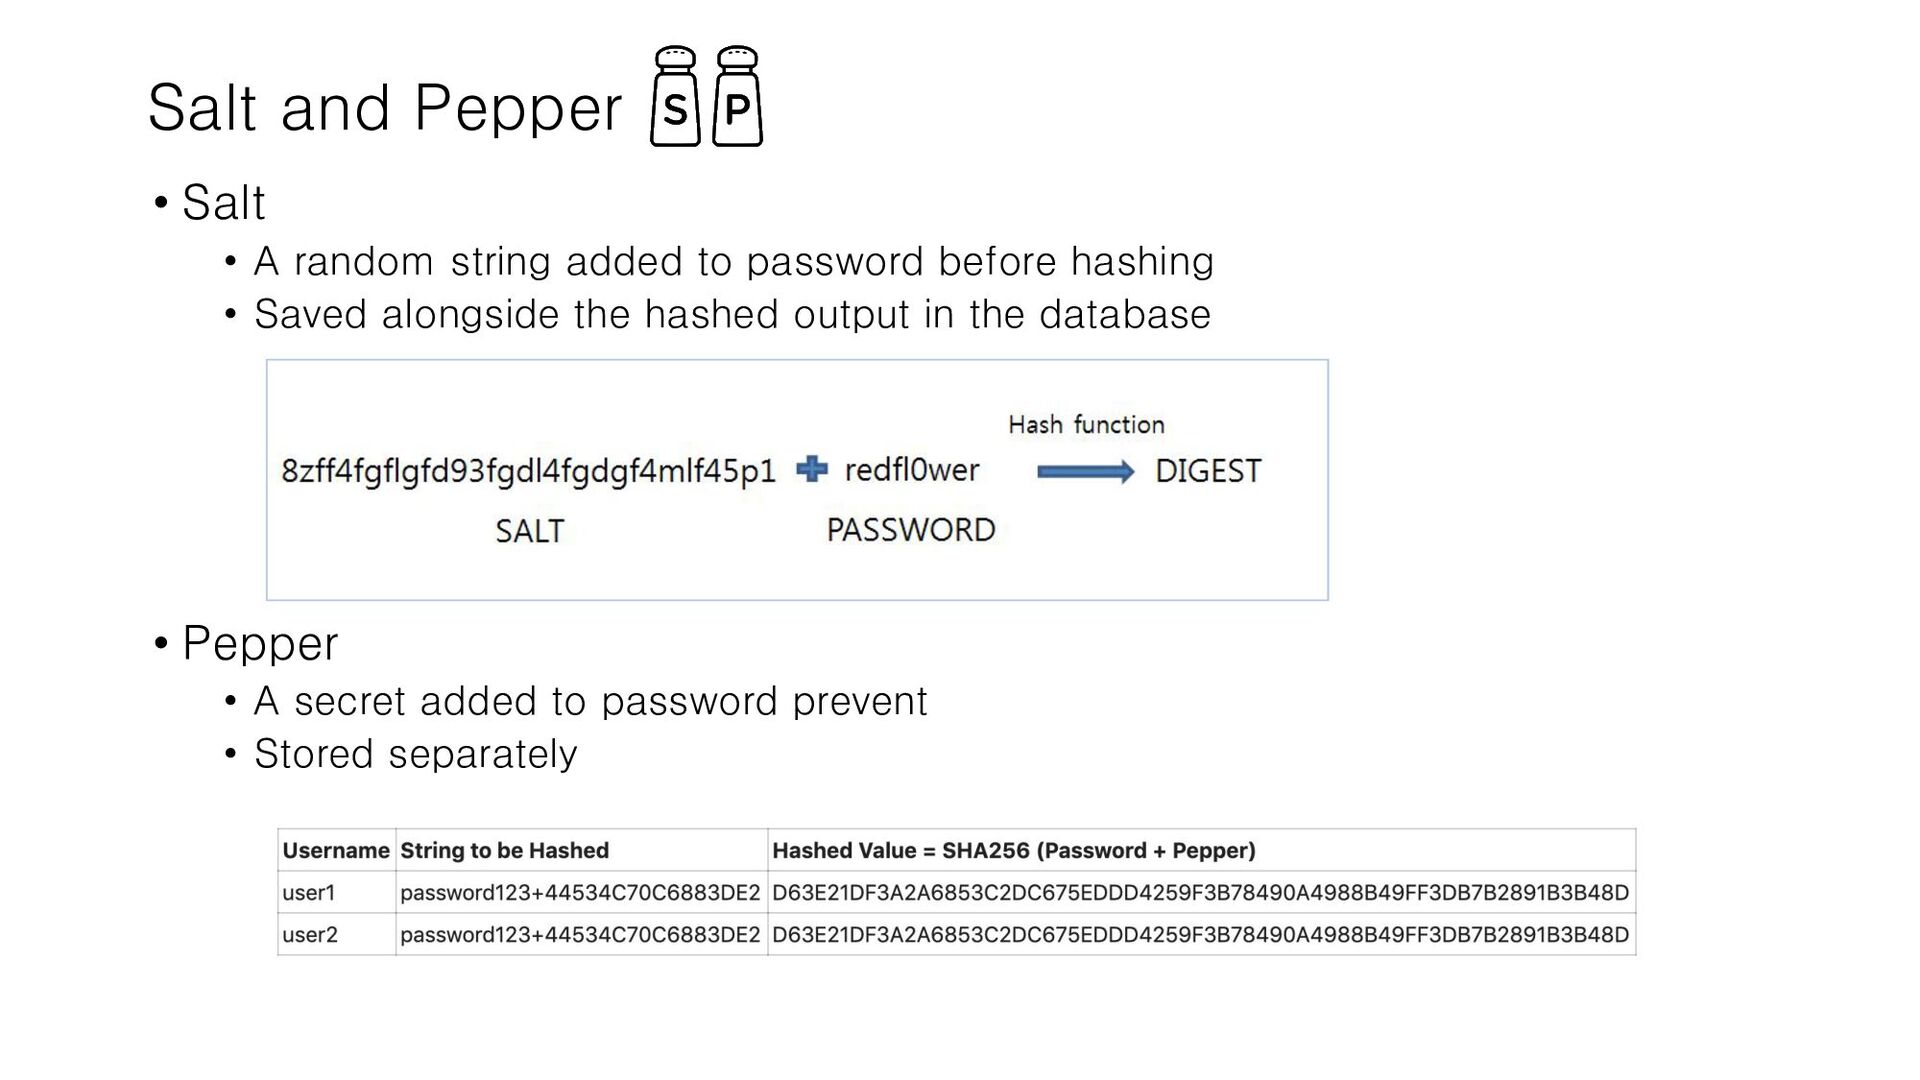
• Saved alongside the hashed output in the database id salt to_be_hashed password_hash john k5kgHa2Rta k5kgHa2Rtapassword e020a56cc237fa2a6640aef6bf5b262256c603bc young sJXIhDiK3q sJXIhDiK3qpassword 9ffbf61794b11ebe929a18b722b0cec38bdefd51
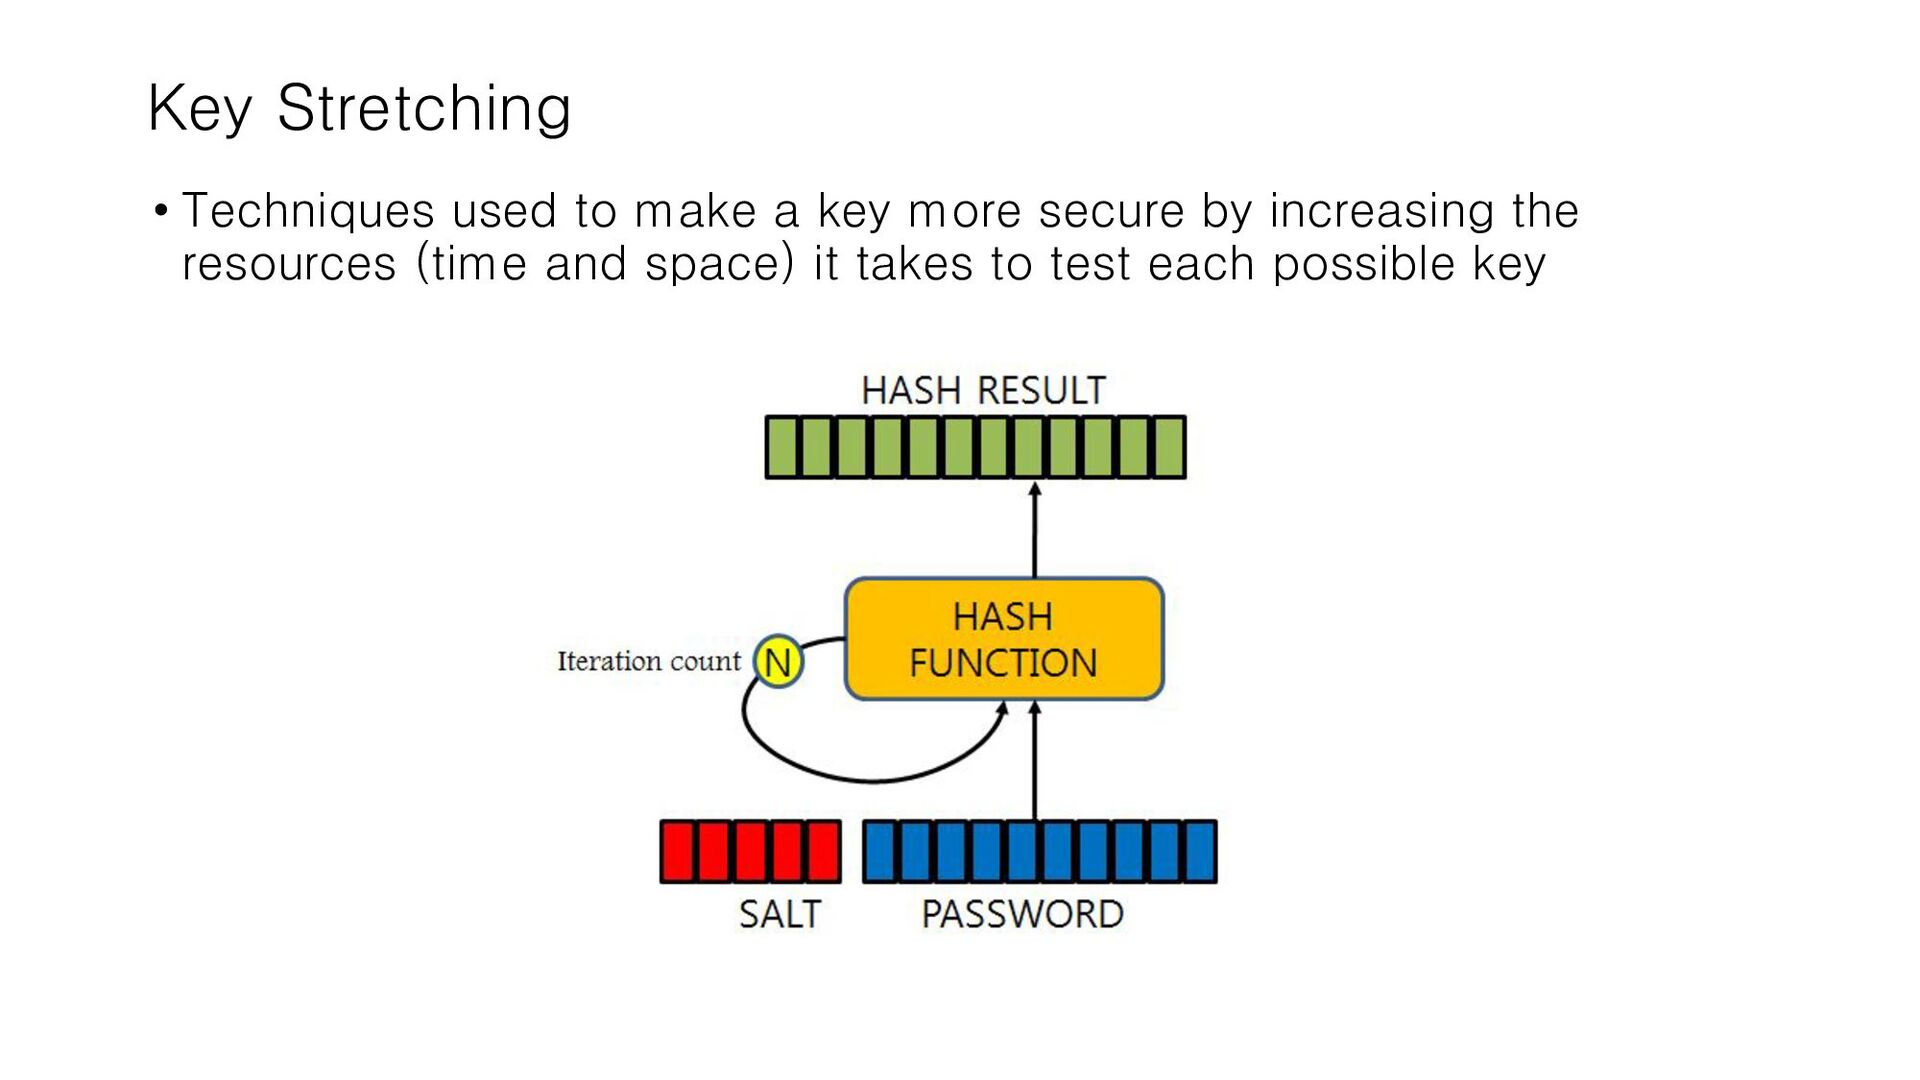
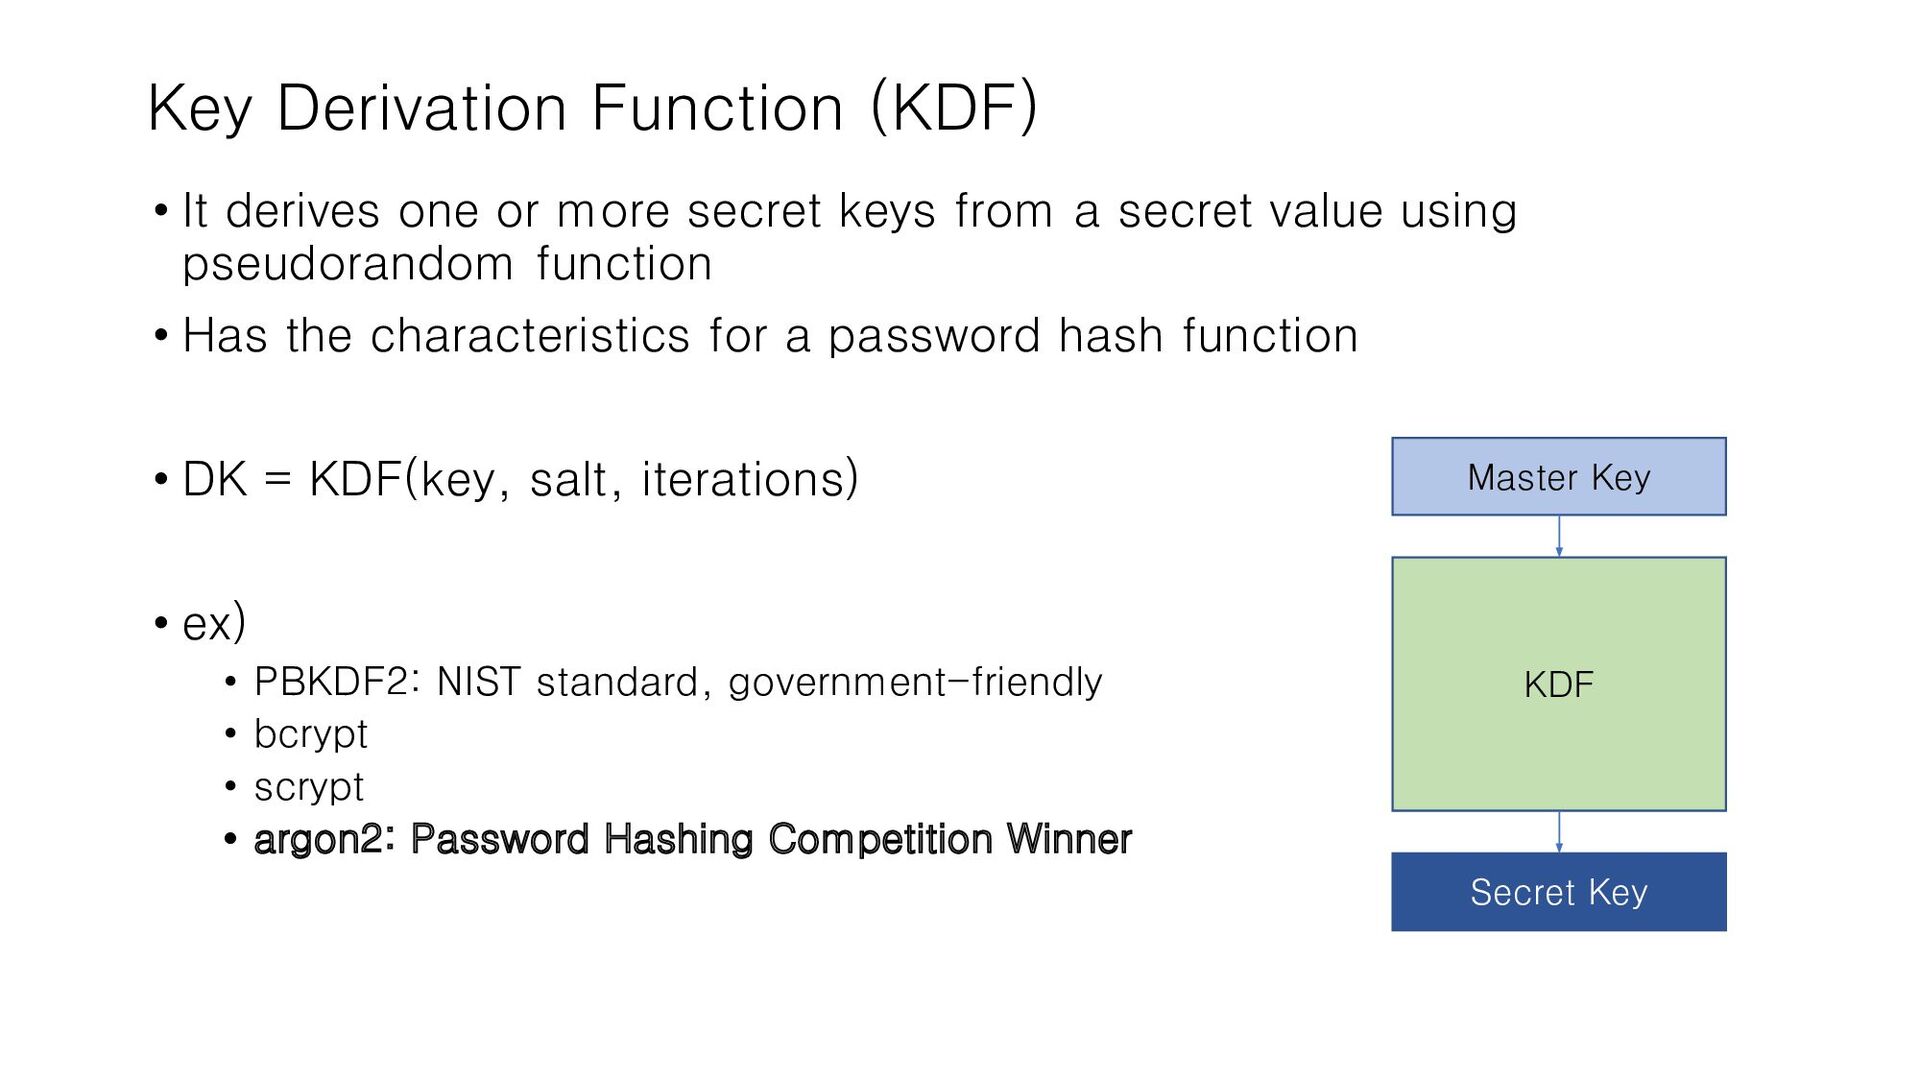
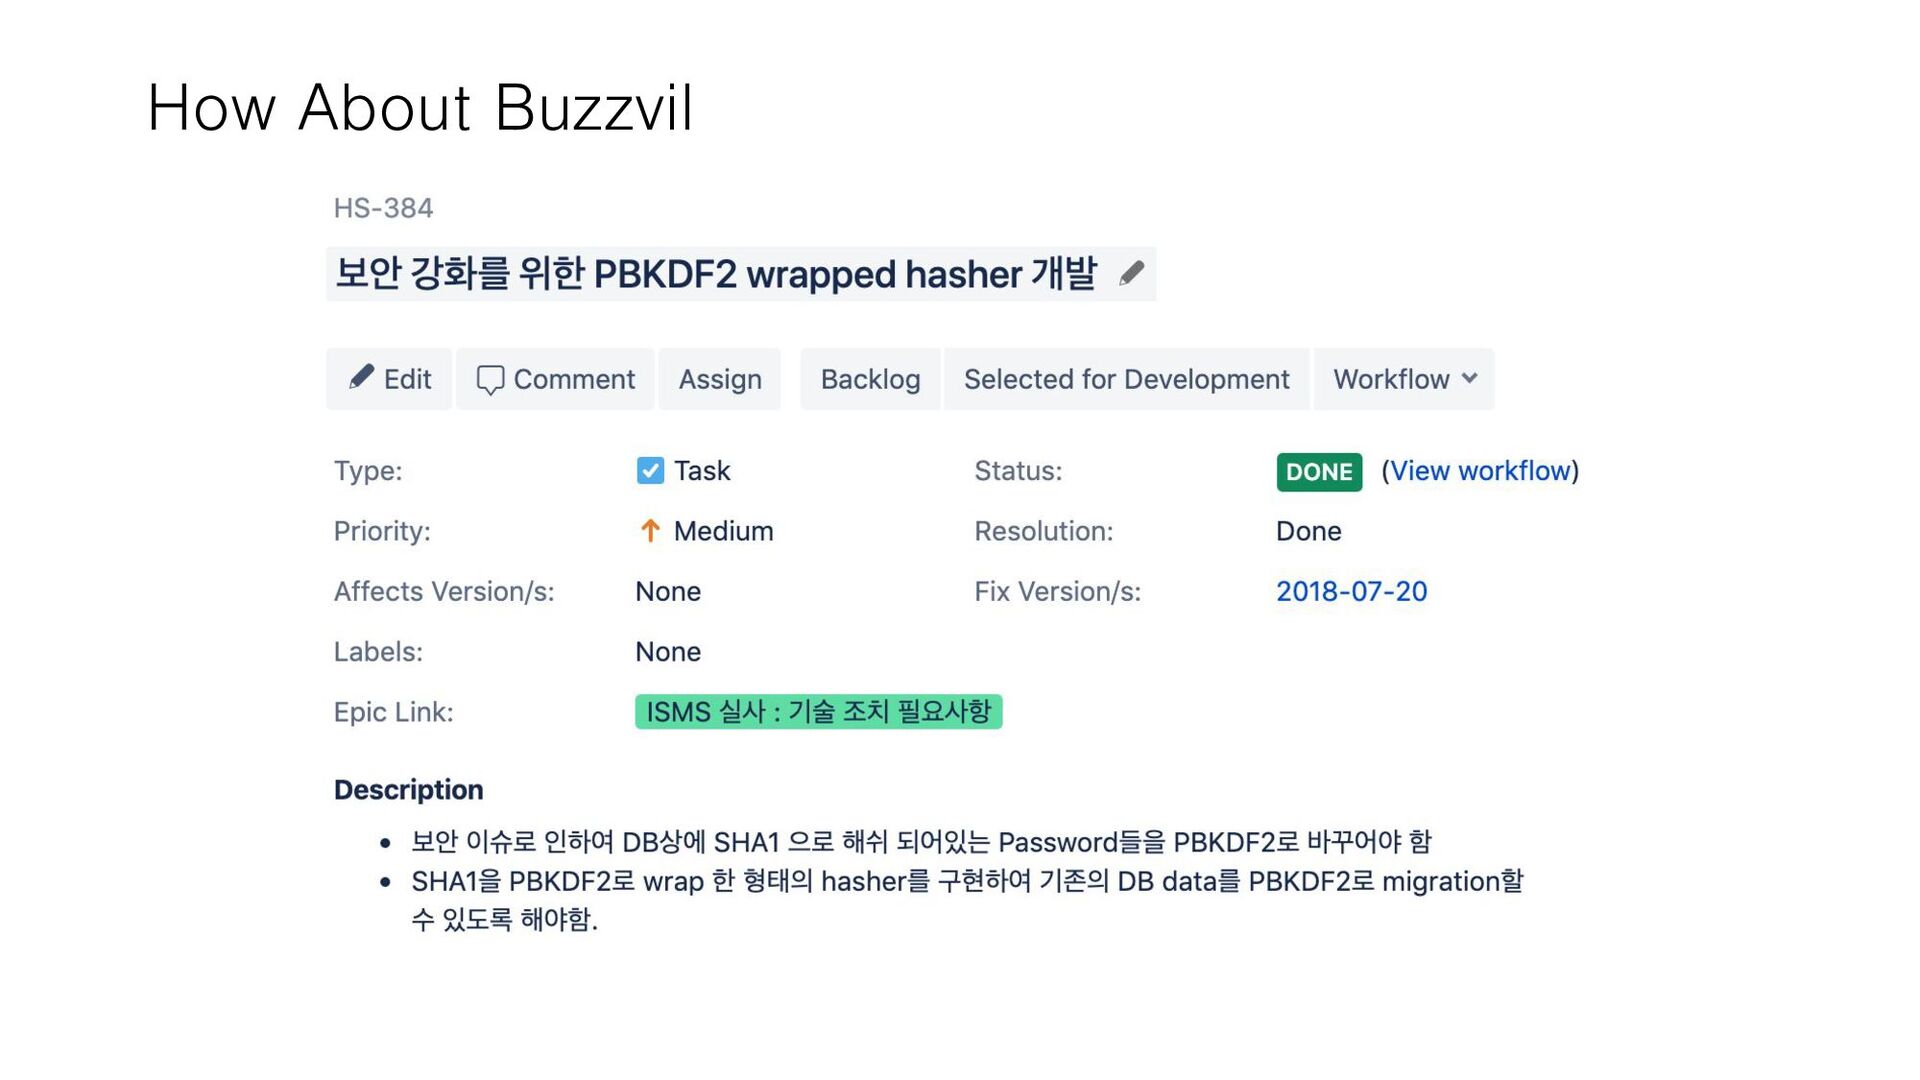
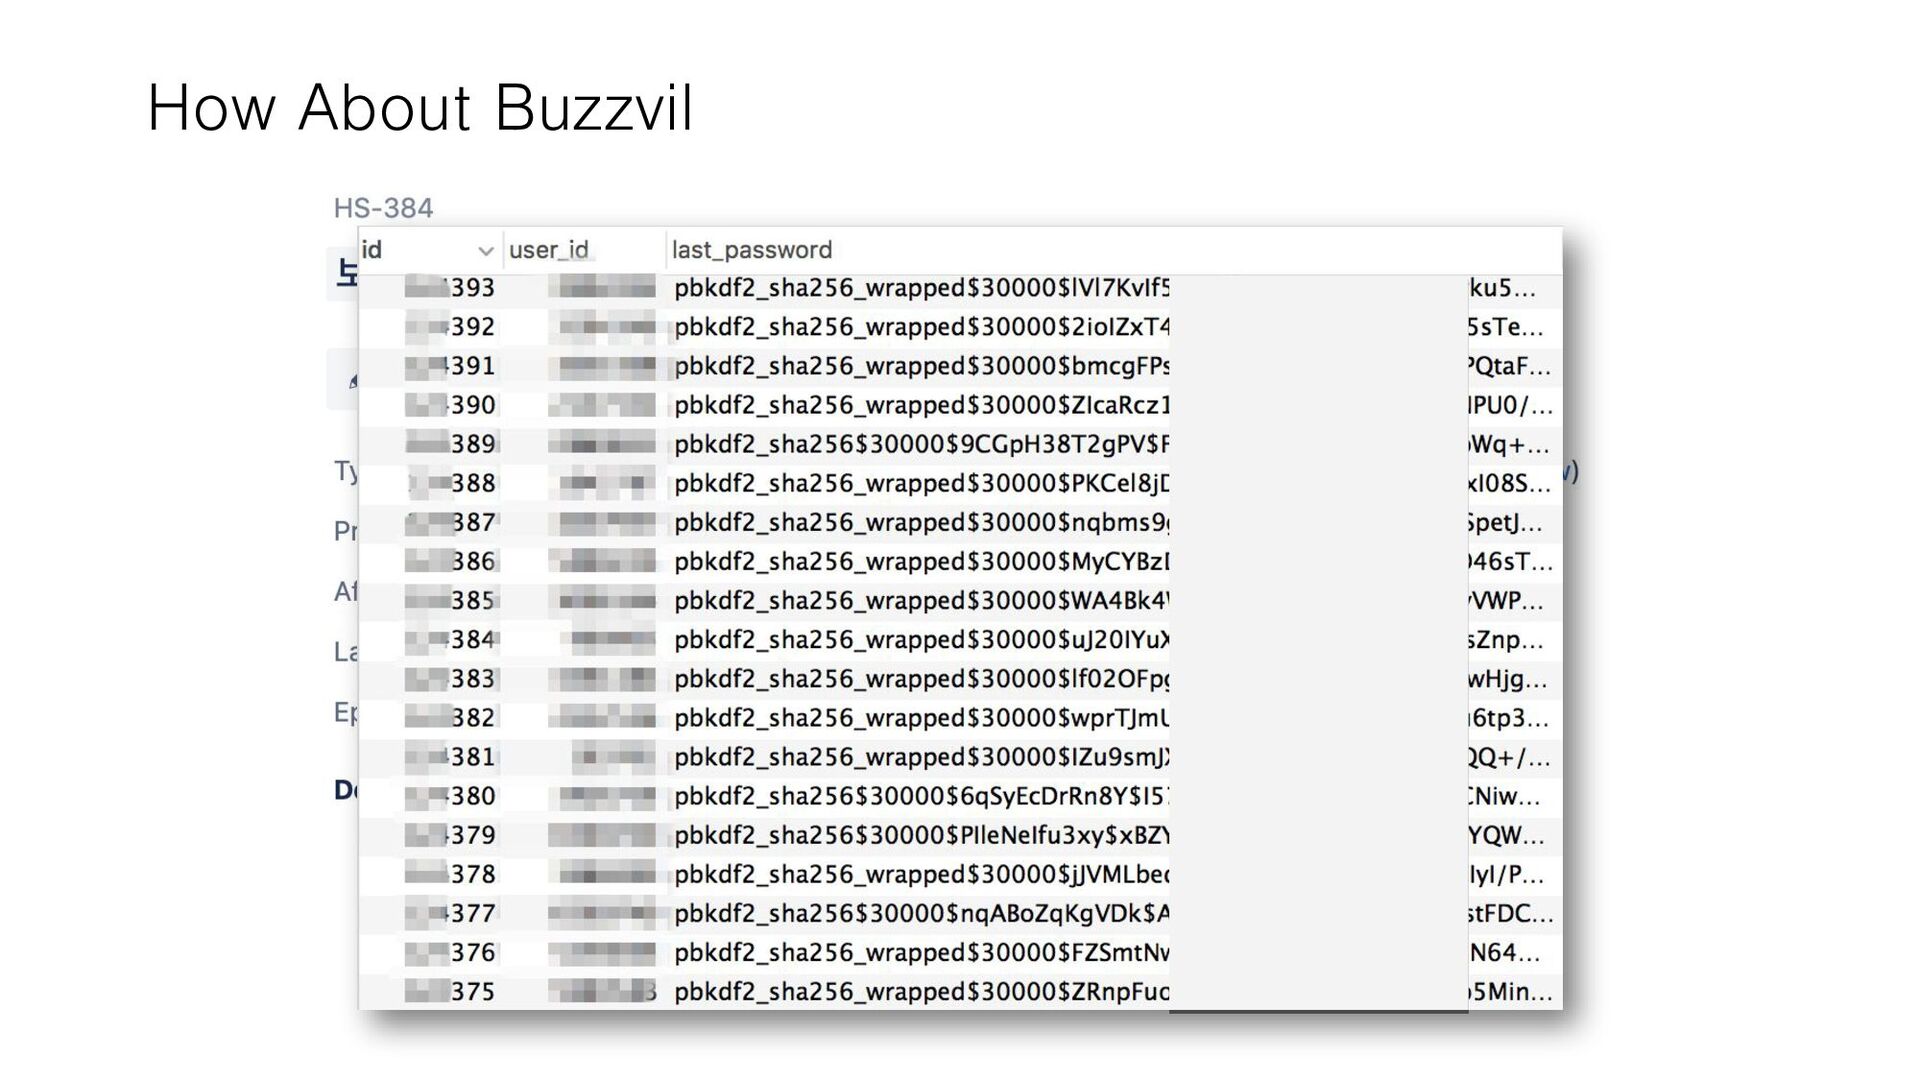
secret keys from a secret value using pseudorandom function • Has the characteristics for a password hash function • DK = KDF(key, salt, iterations) • ex) • PBKDF2: NIST standard, government-friendly • bcrypt • scrypt • argon2: Password Hashing Competition Winner Master Key KDF Secret Key
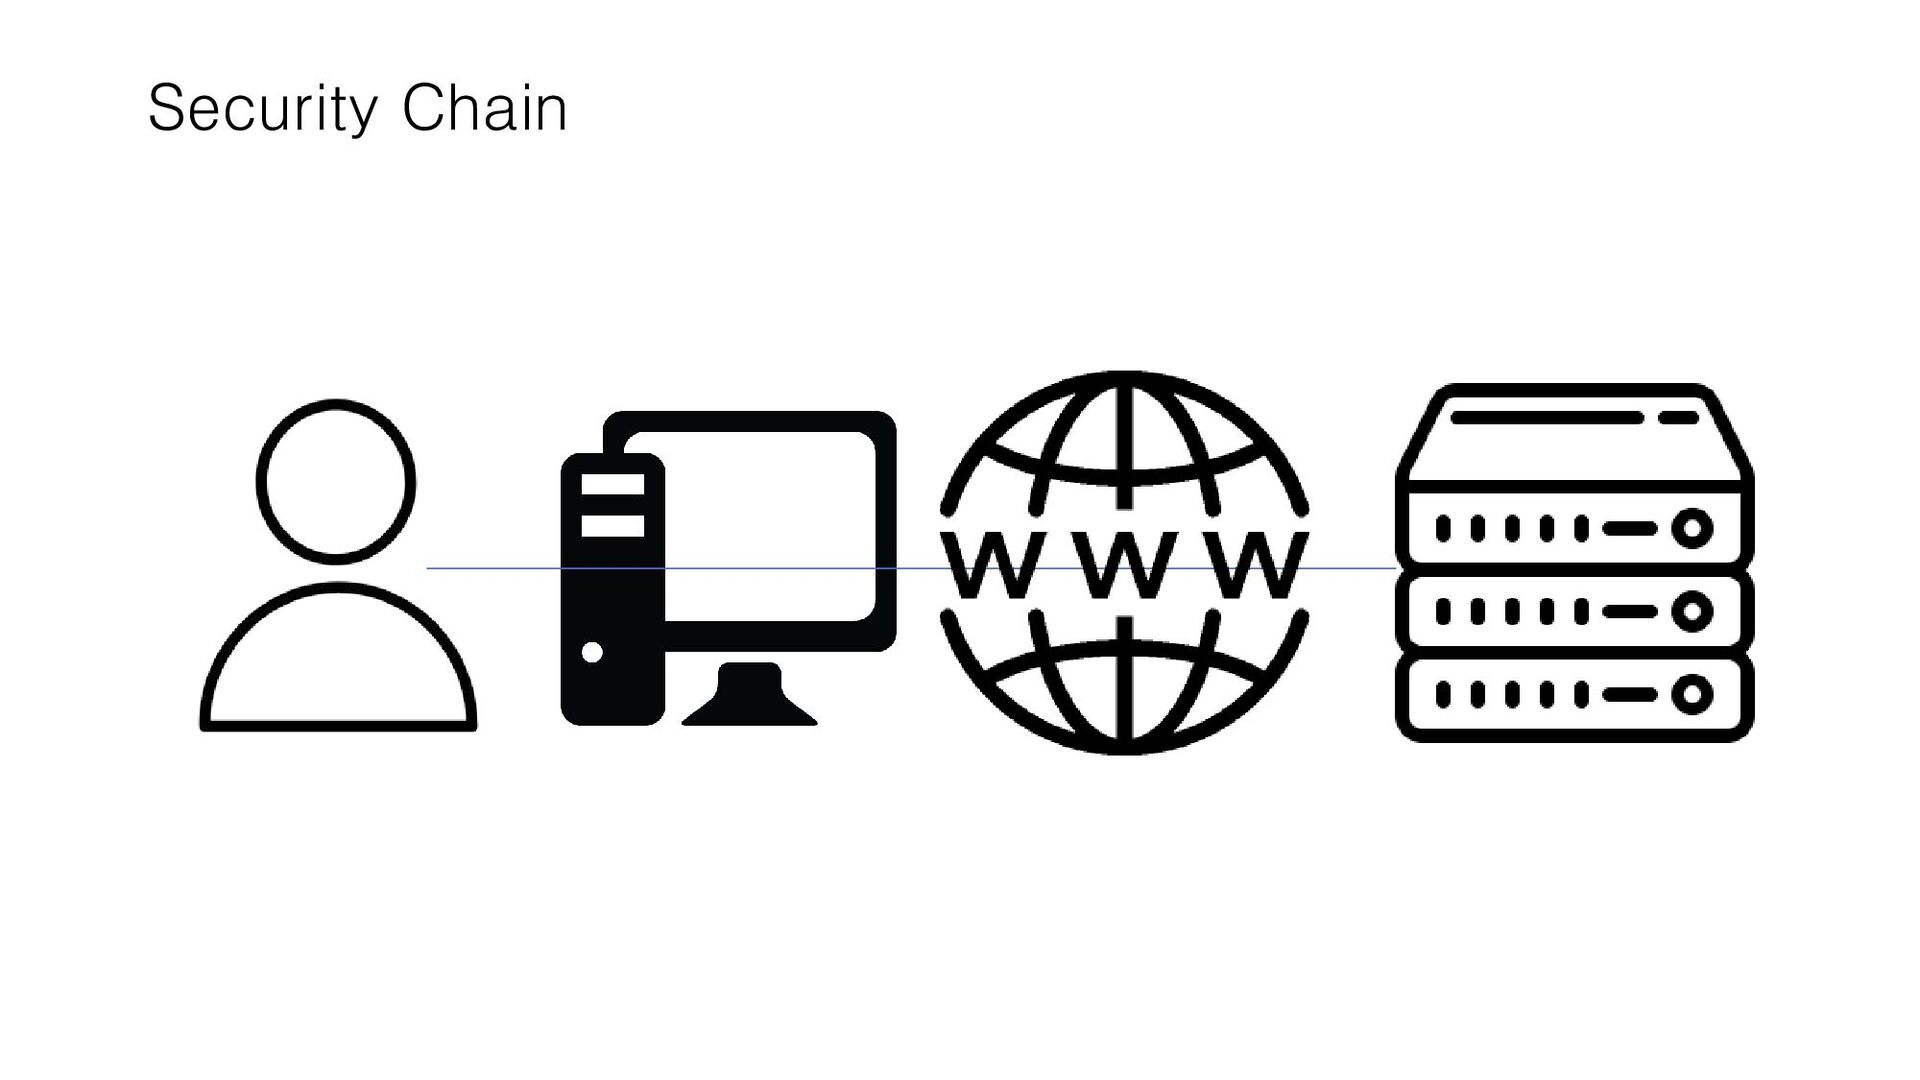
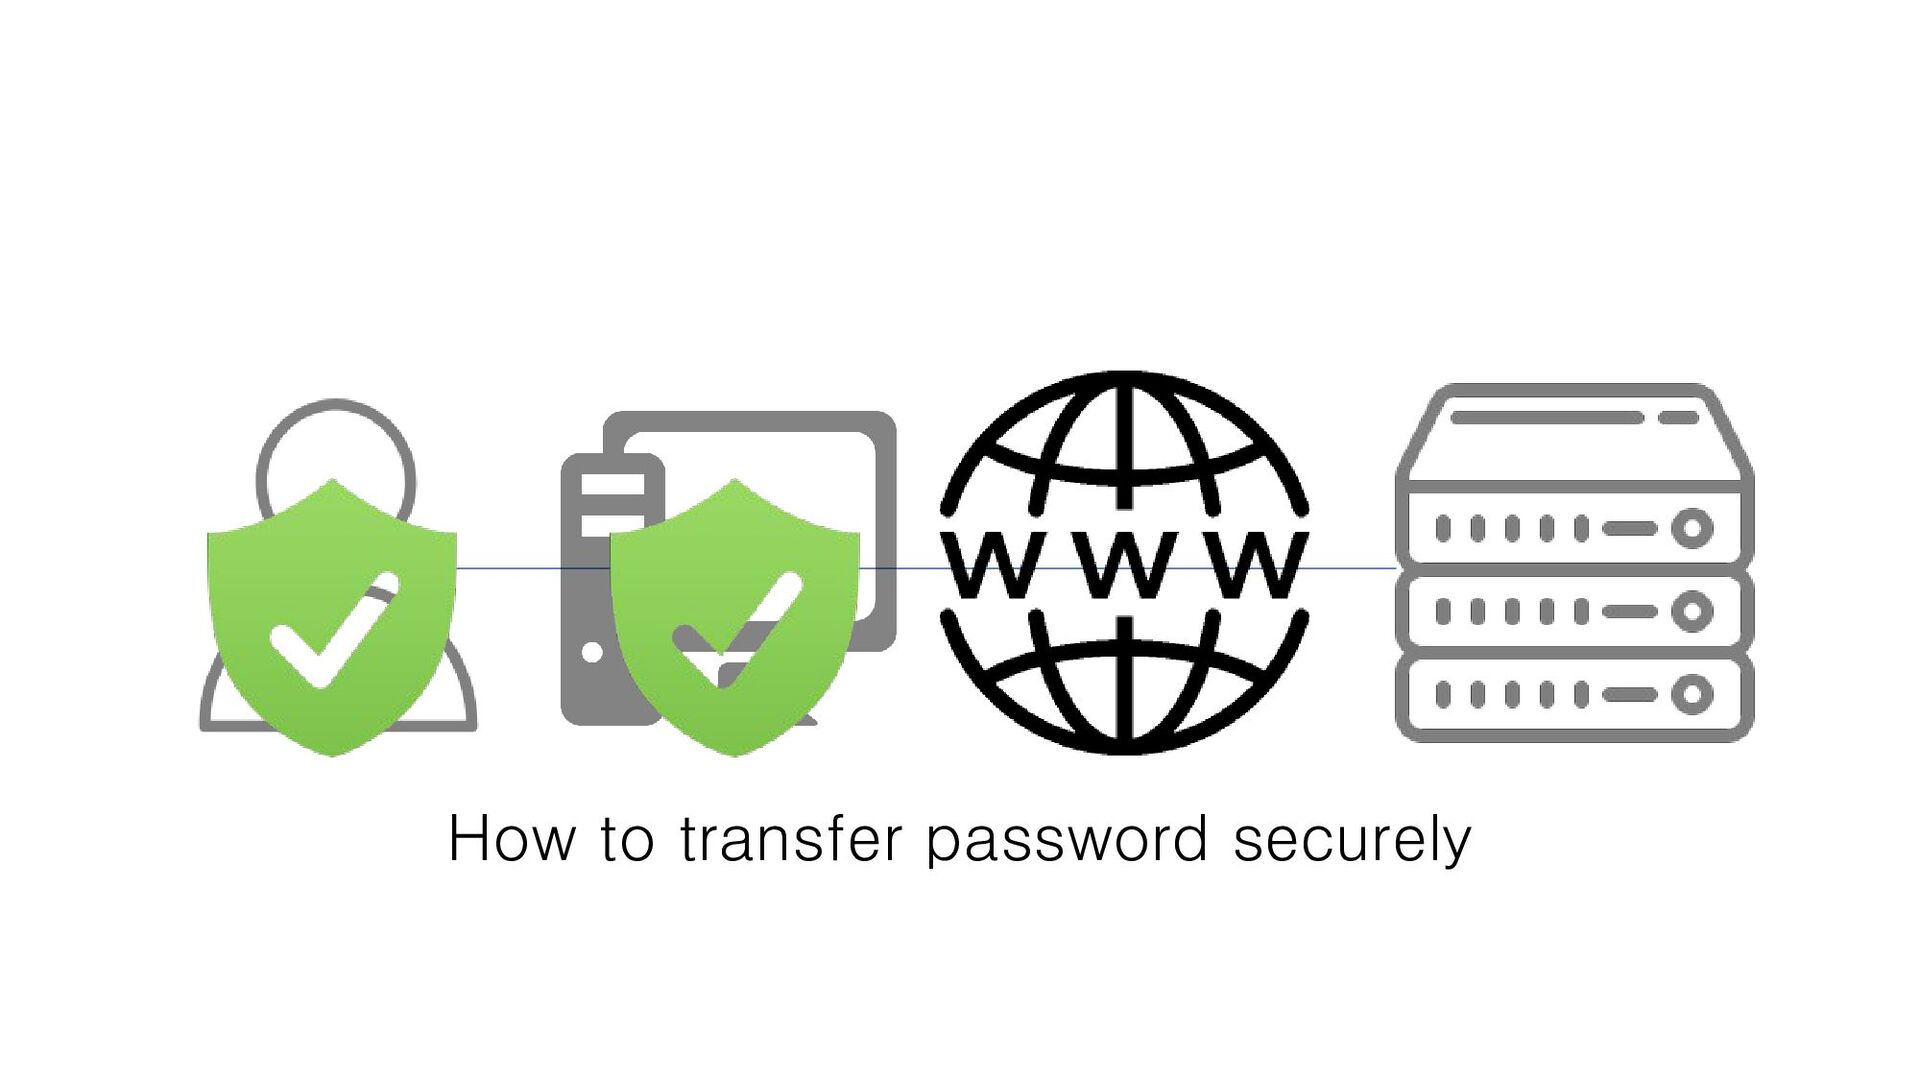
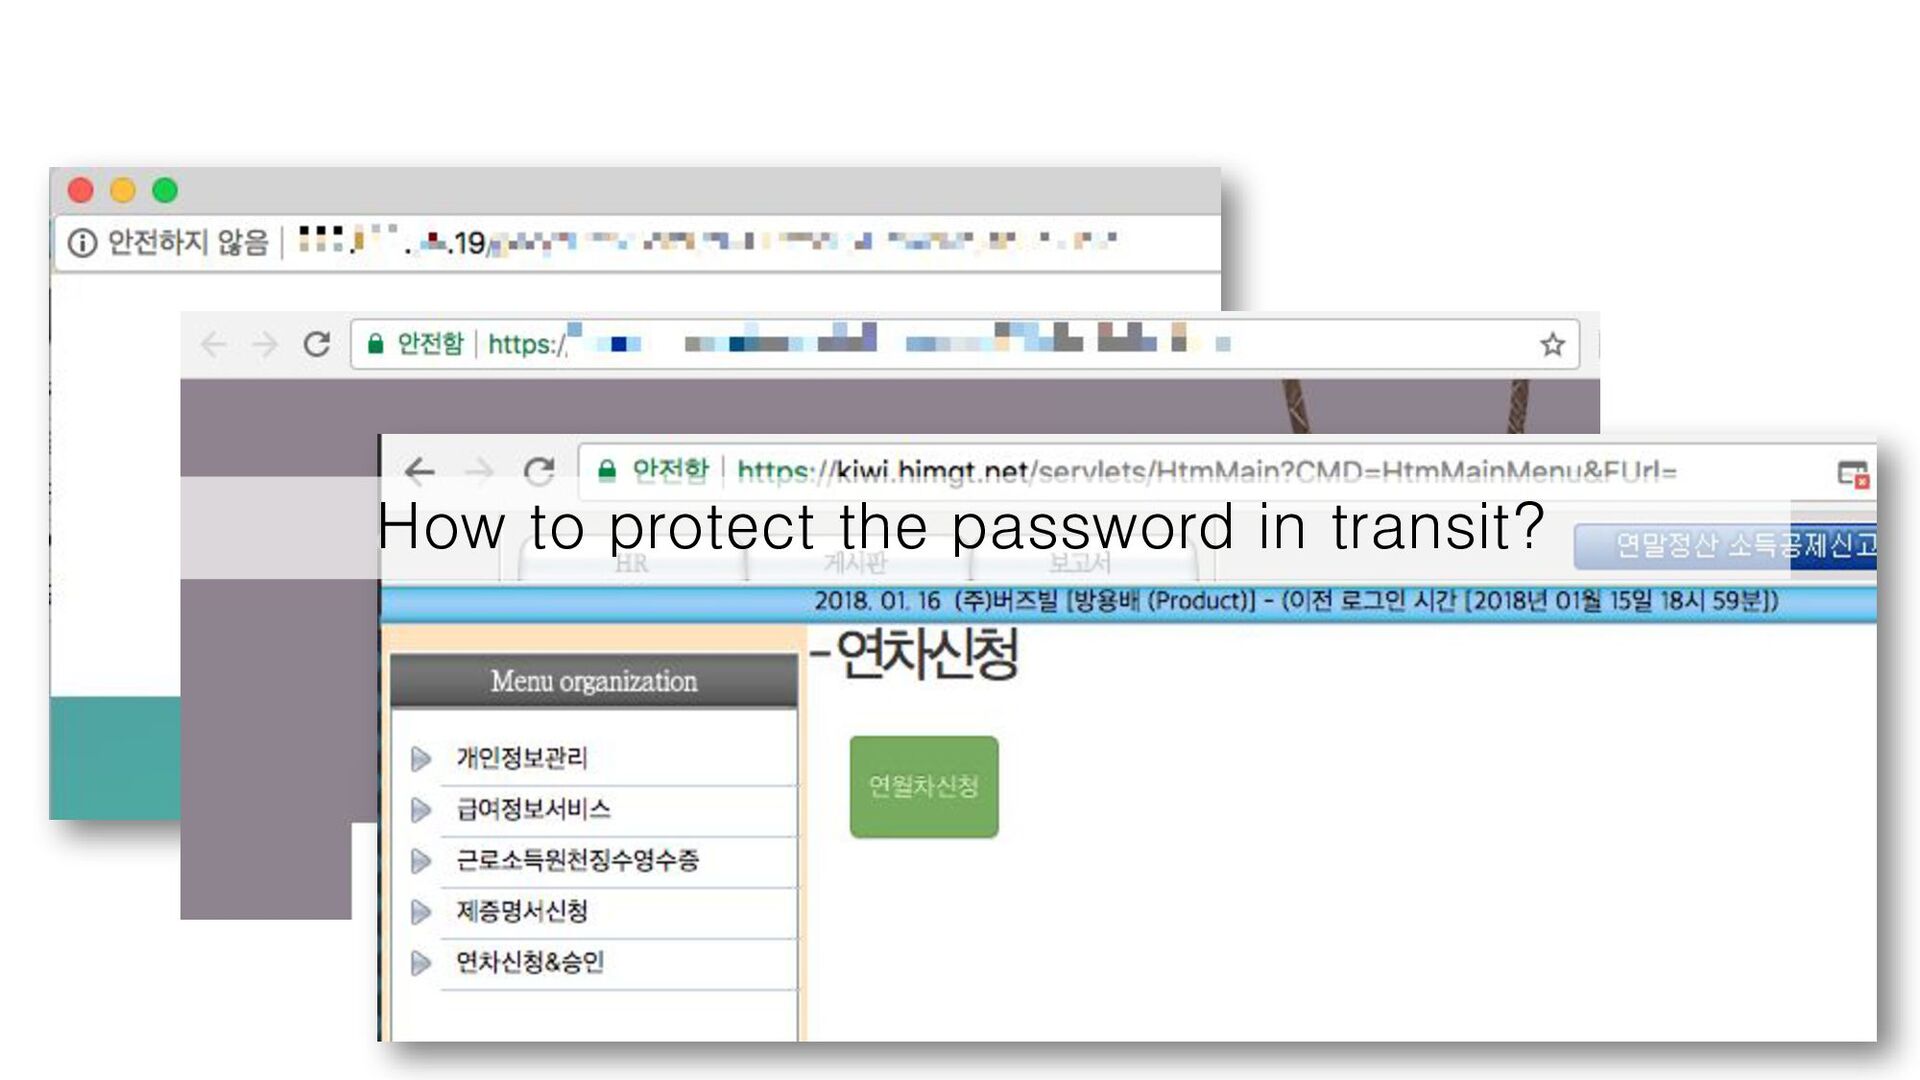
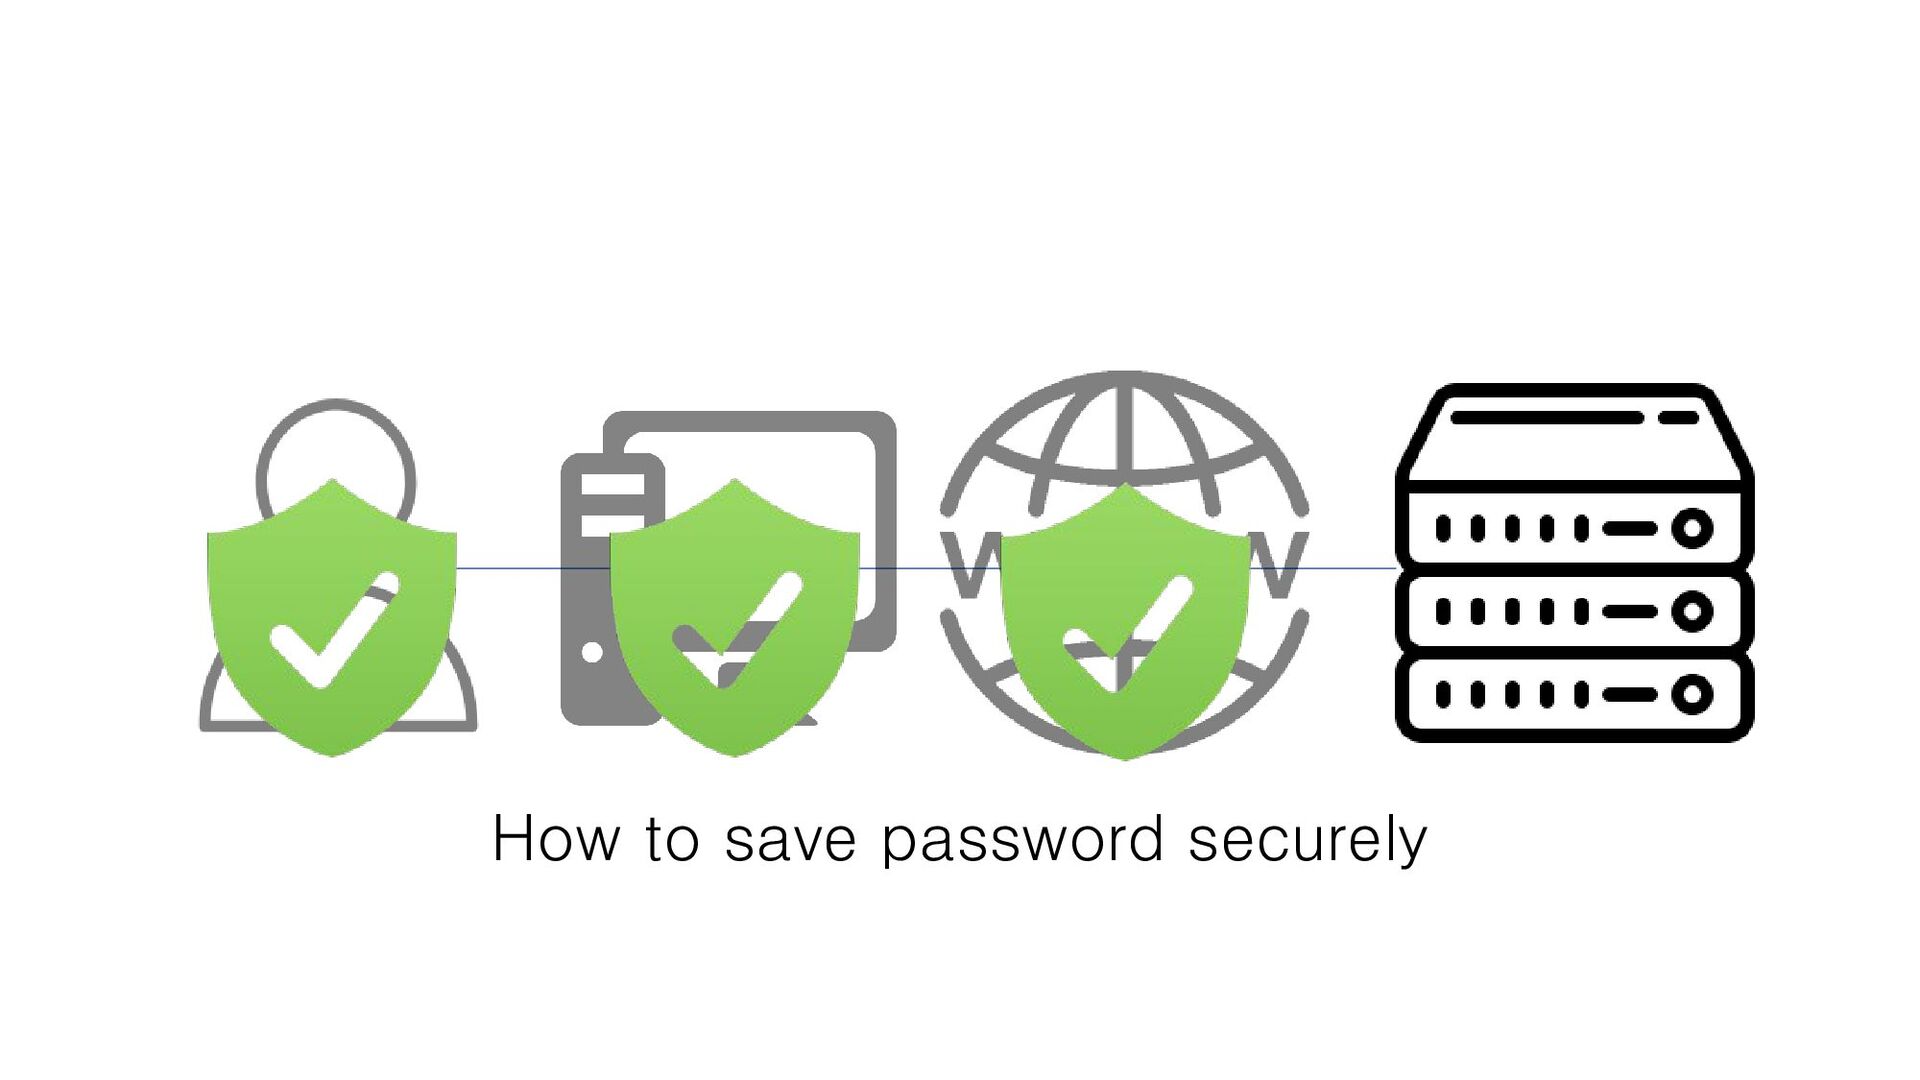
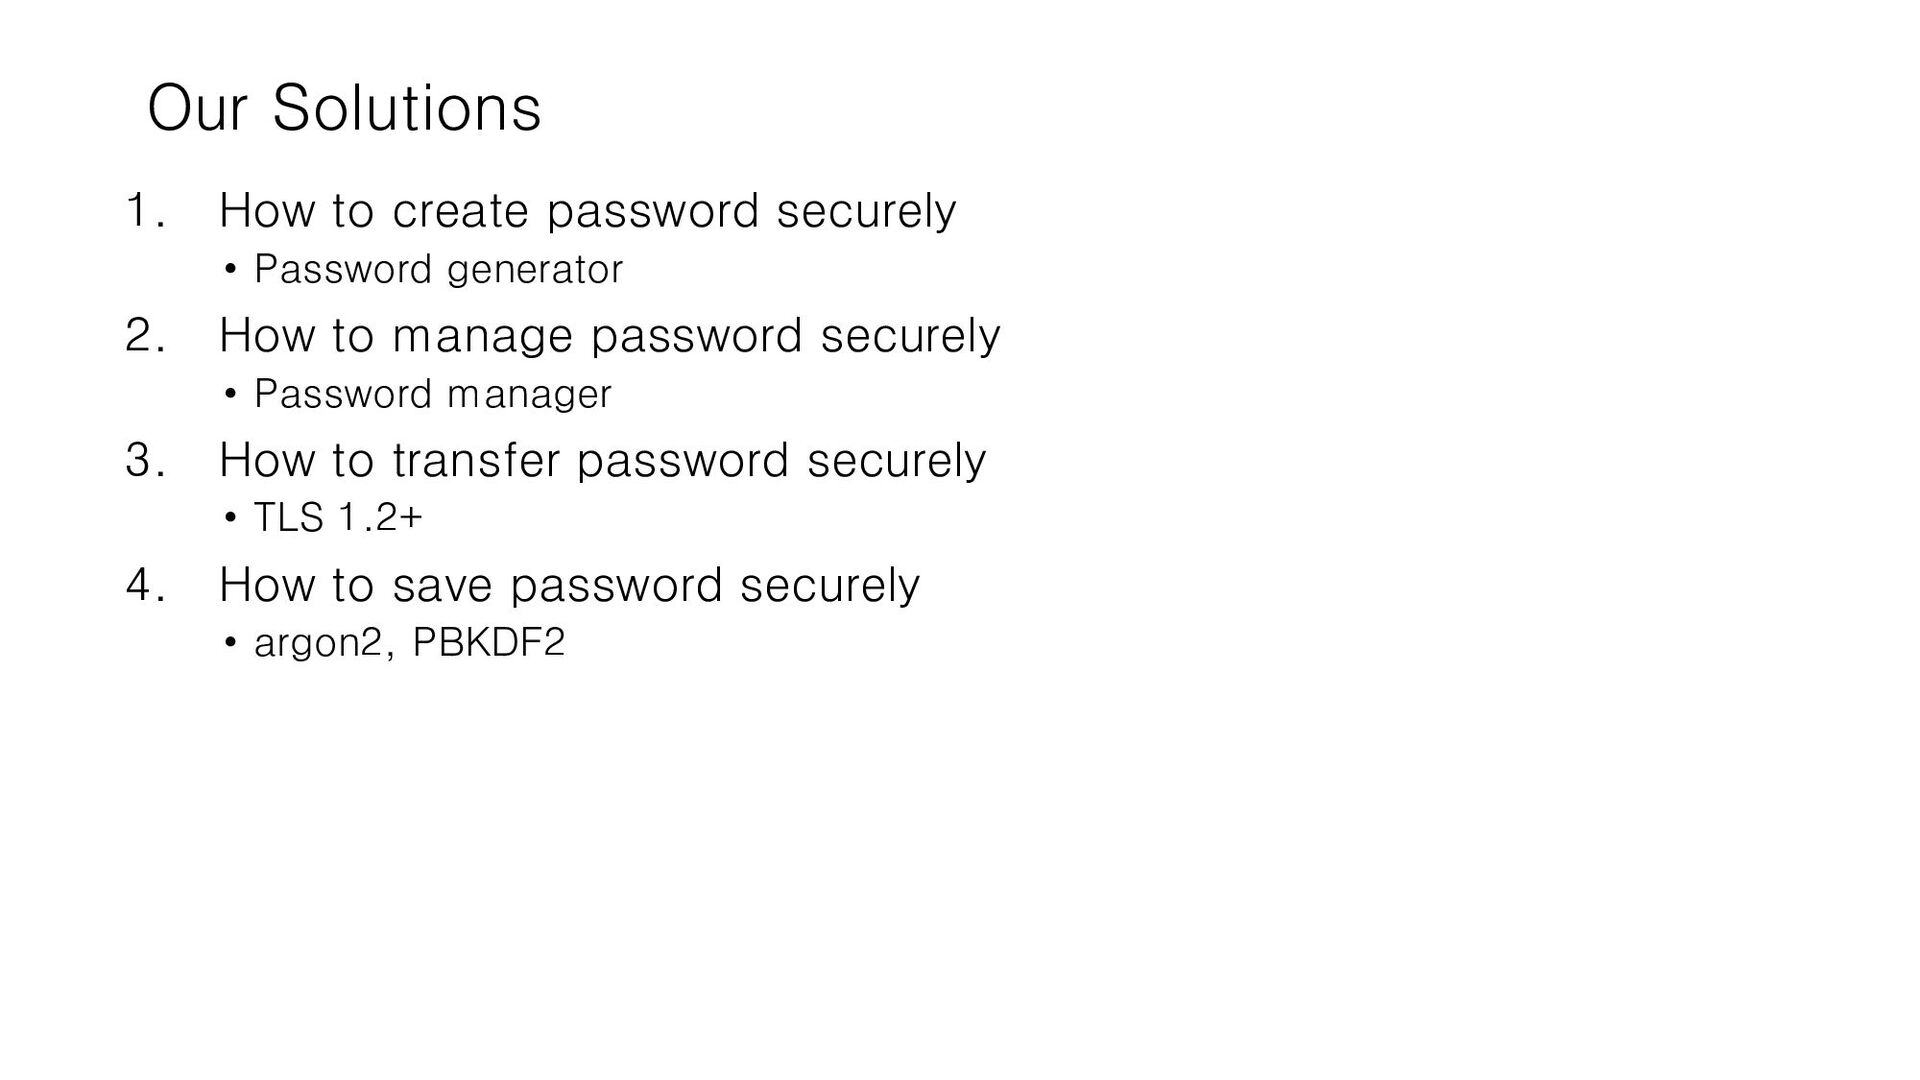
generator 2. How to manage password securely • Password manager 3. How to transfer password securely • TLS 1.2+ 4. How to save password securely • argon2, PBKDF2
generator 2. How to manage password securely • Password manager 3. How to transfer password securely • TLS 1.2+ 4. How to save password securely • argon2, PBKDF2 Do you feel safe?
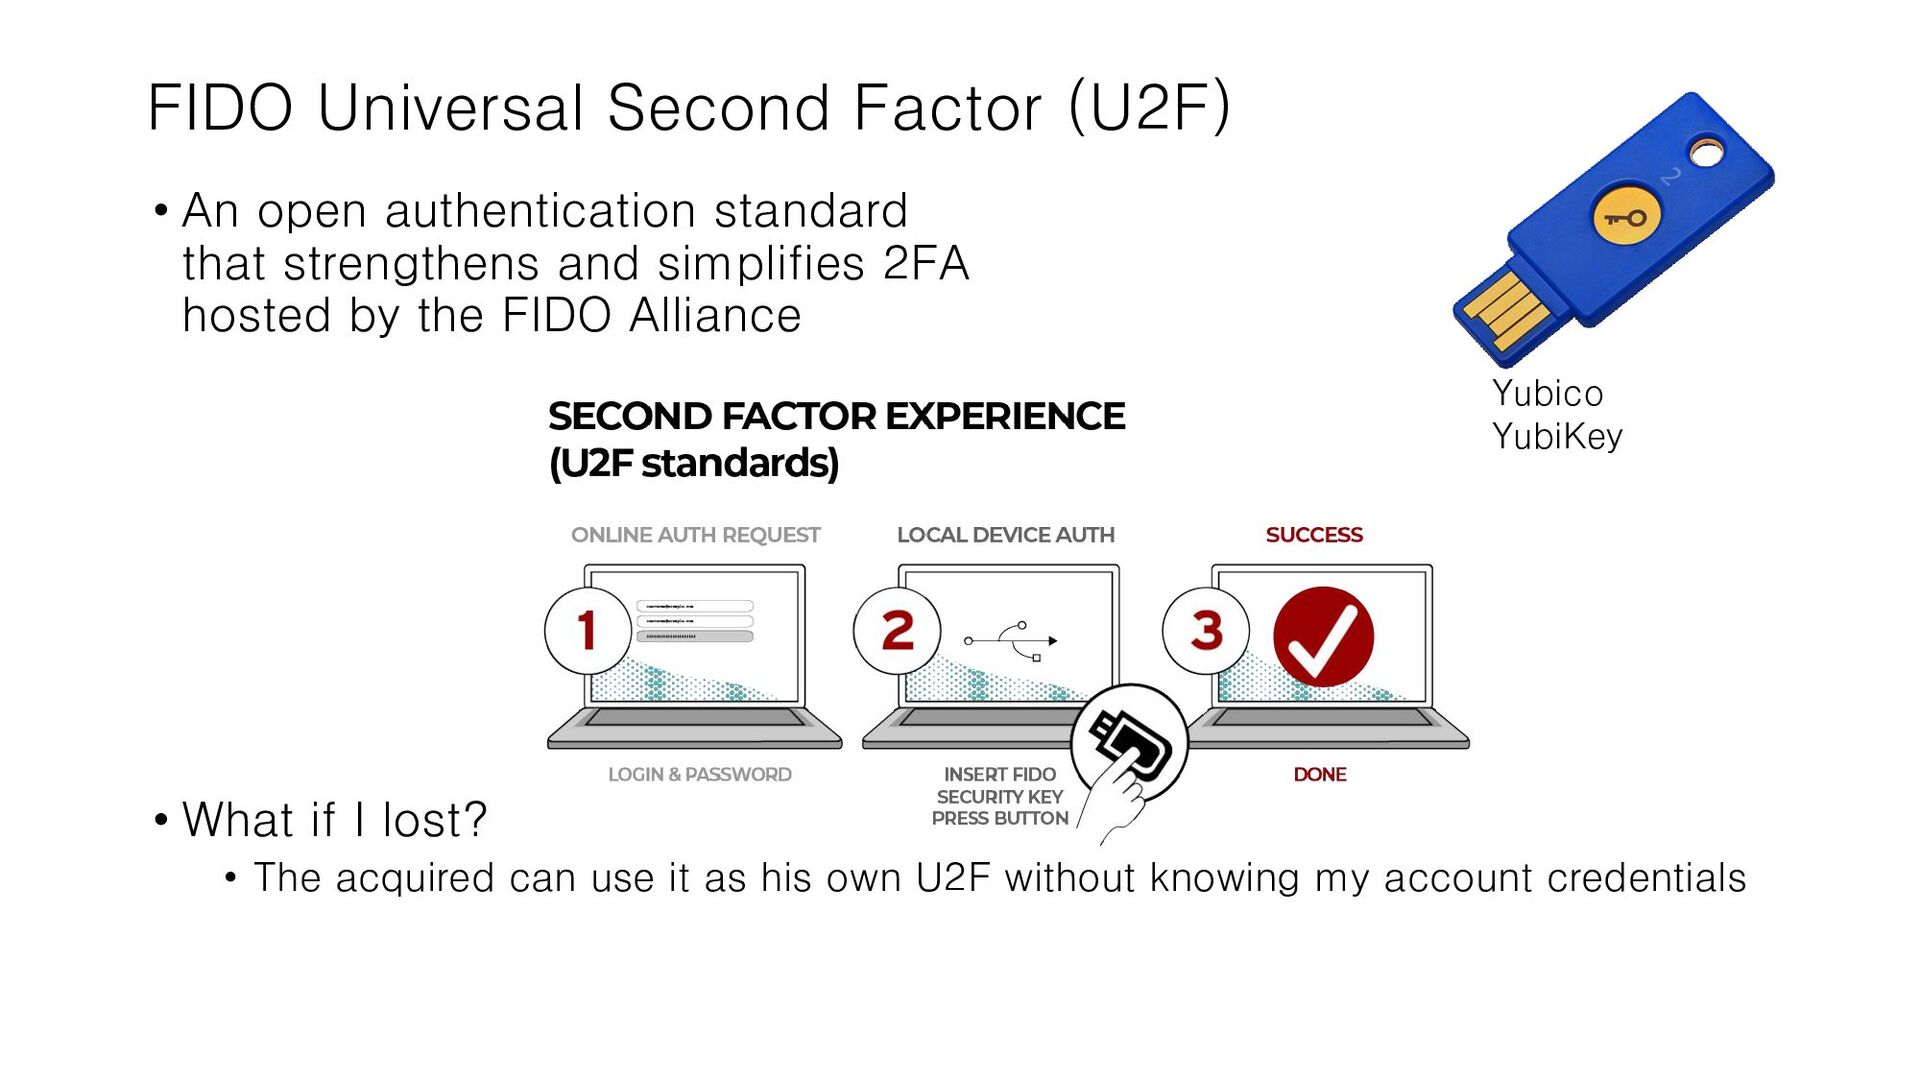
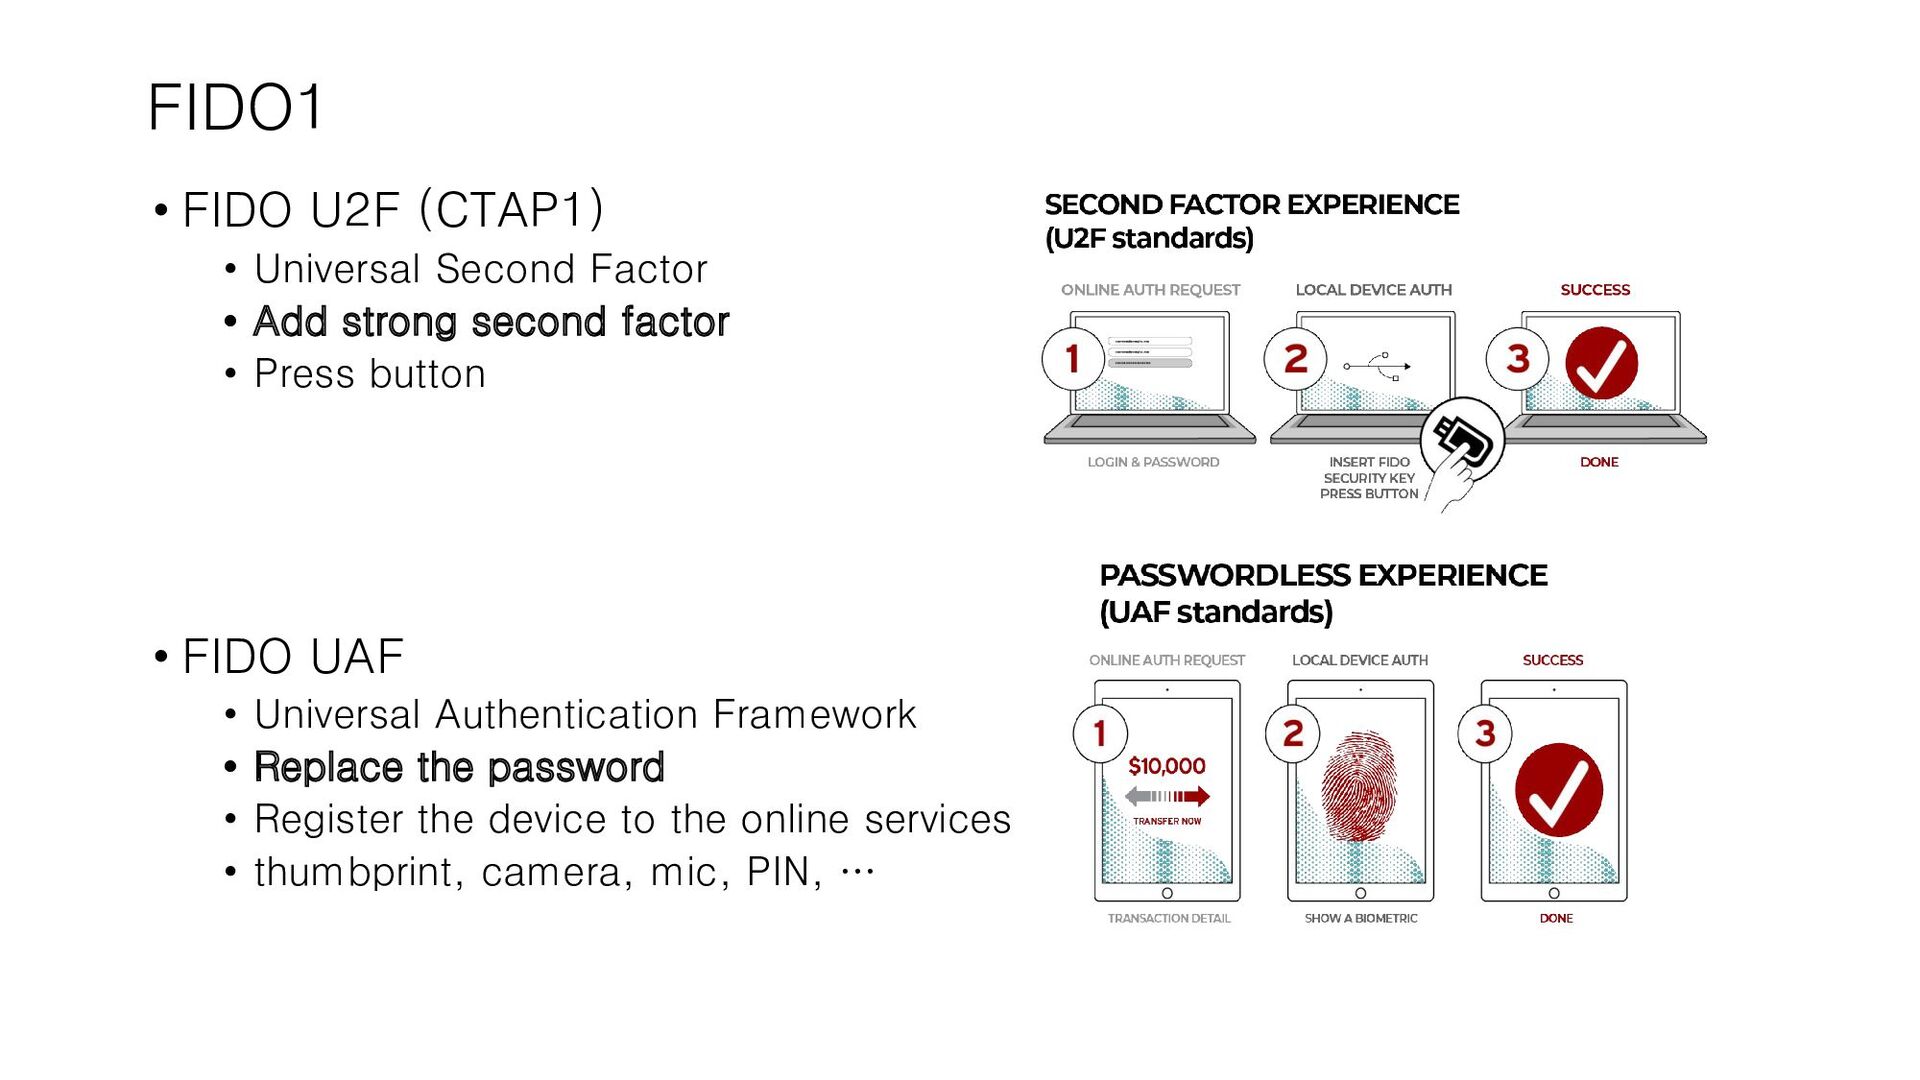
Create a standard for interoperability among strong authentication devices • Solve the problems users face creating and remembering multiple accounts • Core values • Easy of use • privacy and security • standardizations
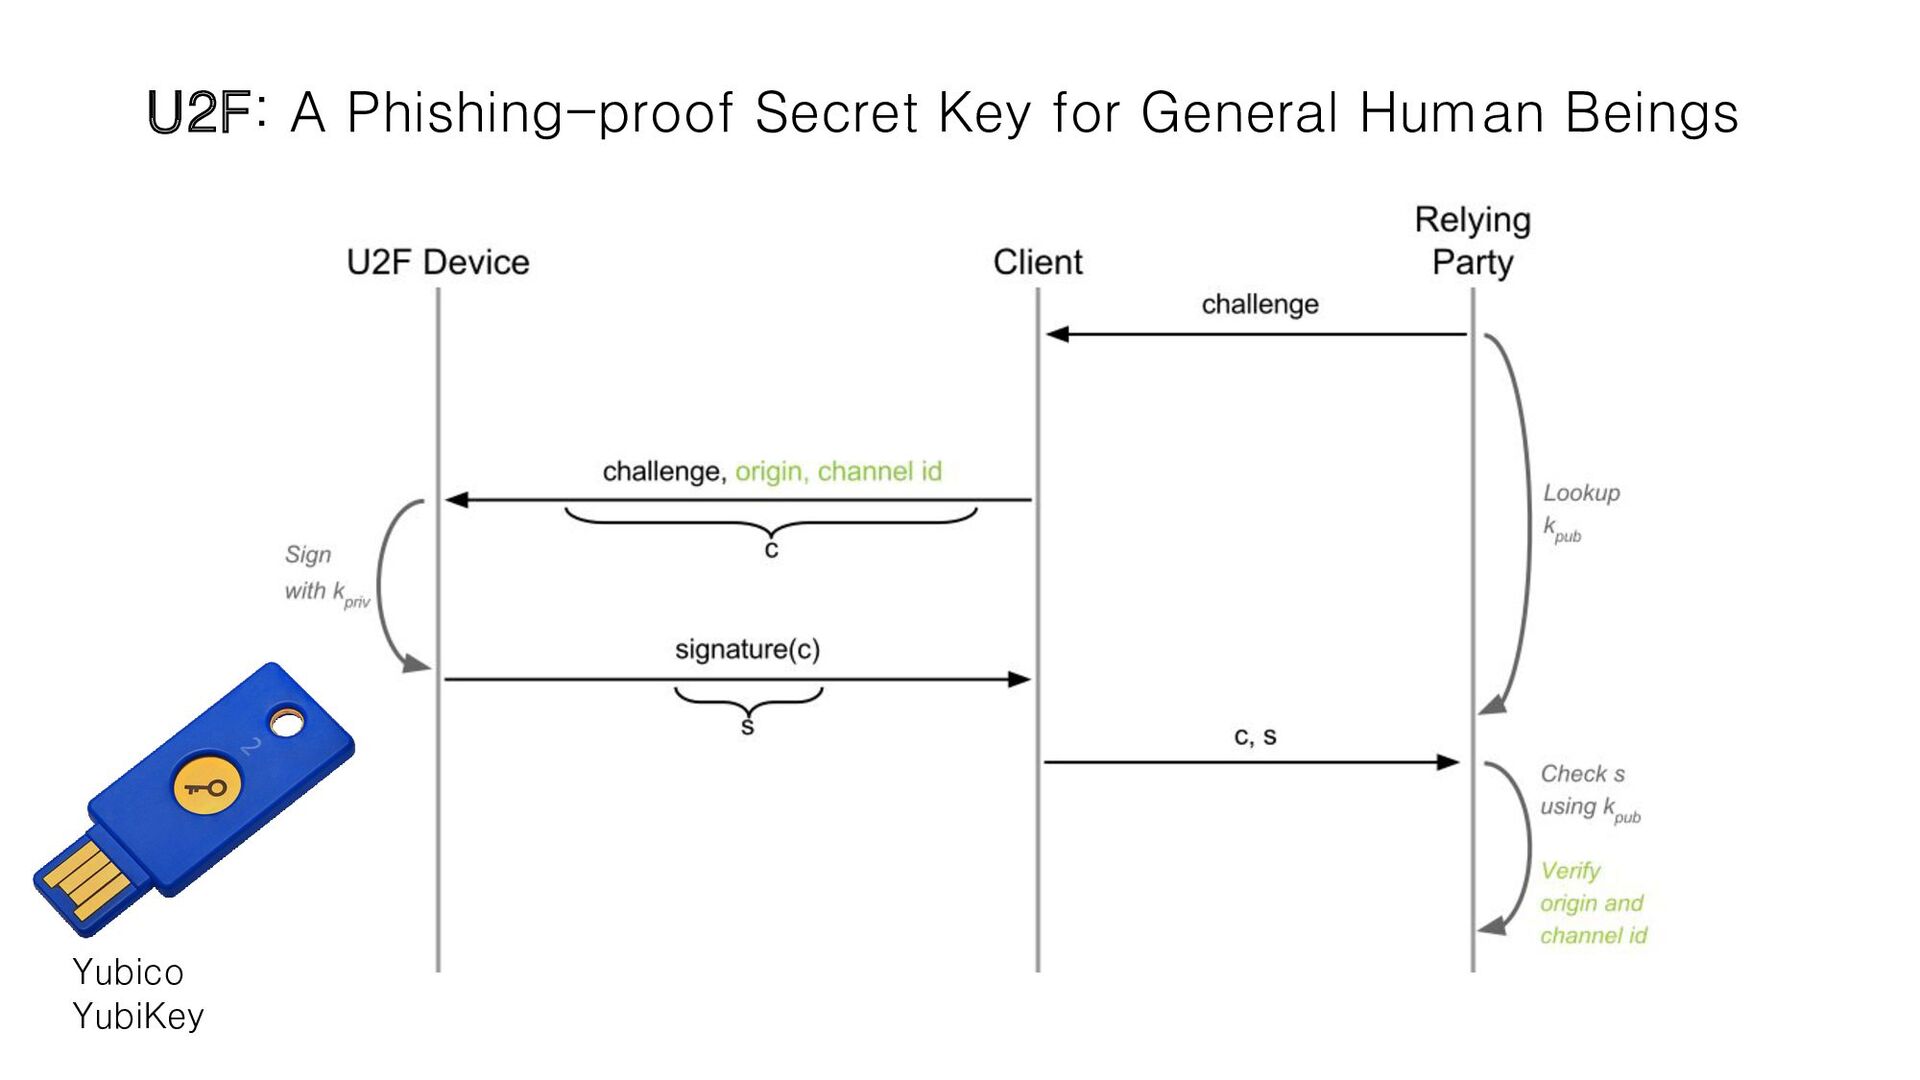
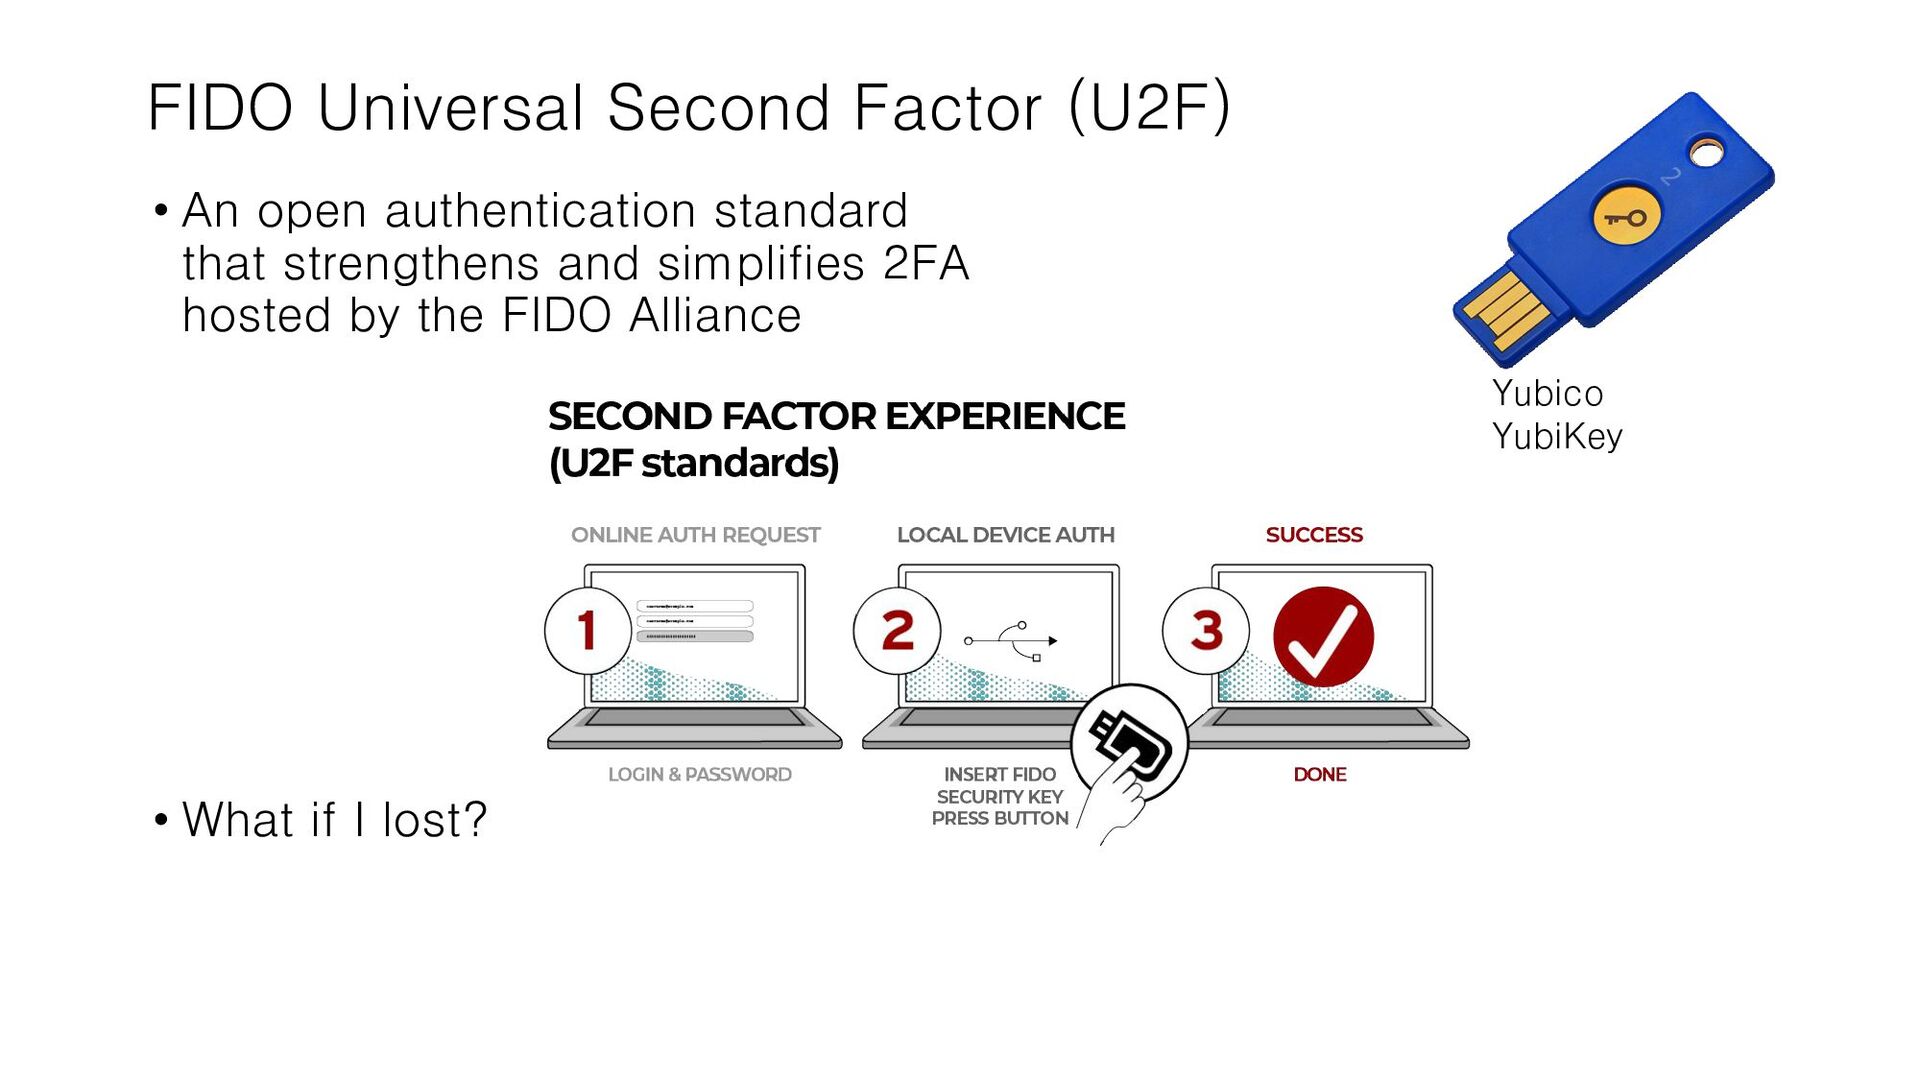
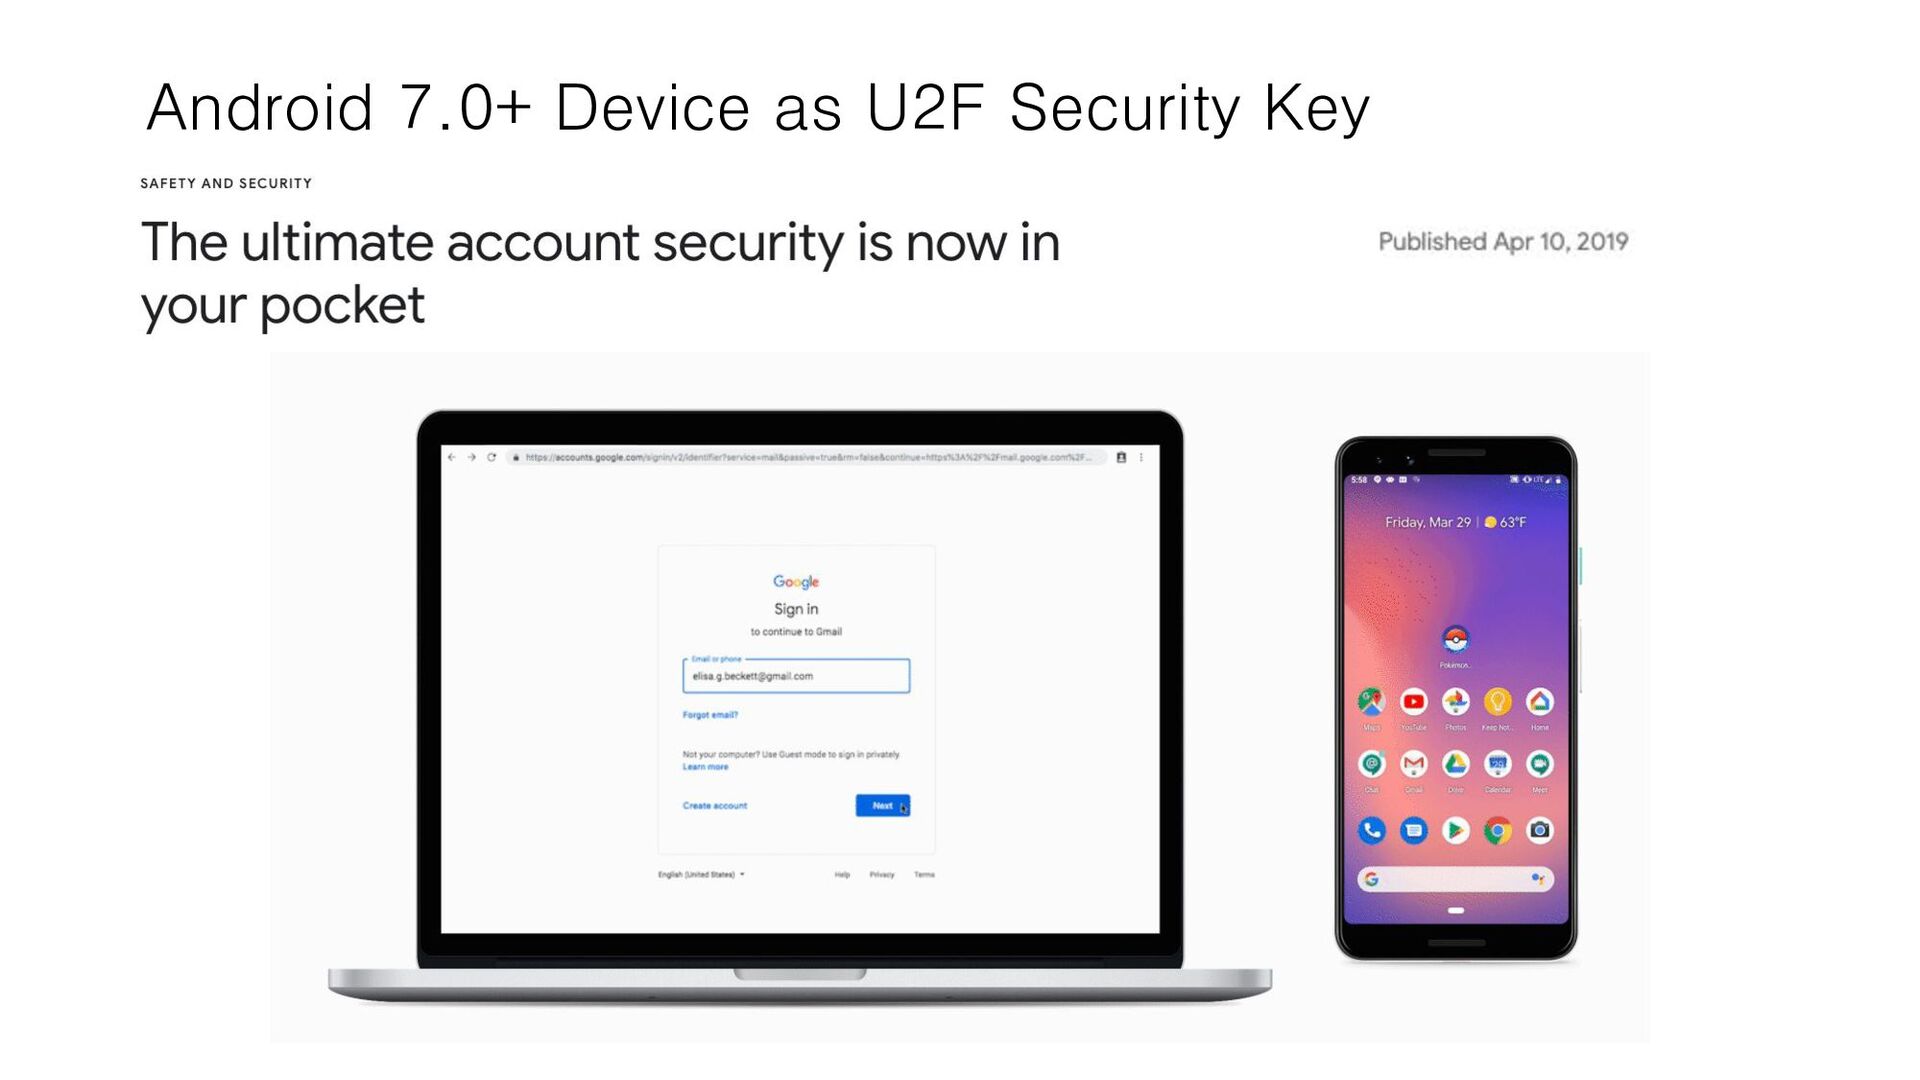
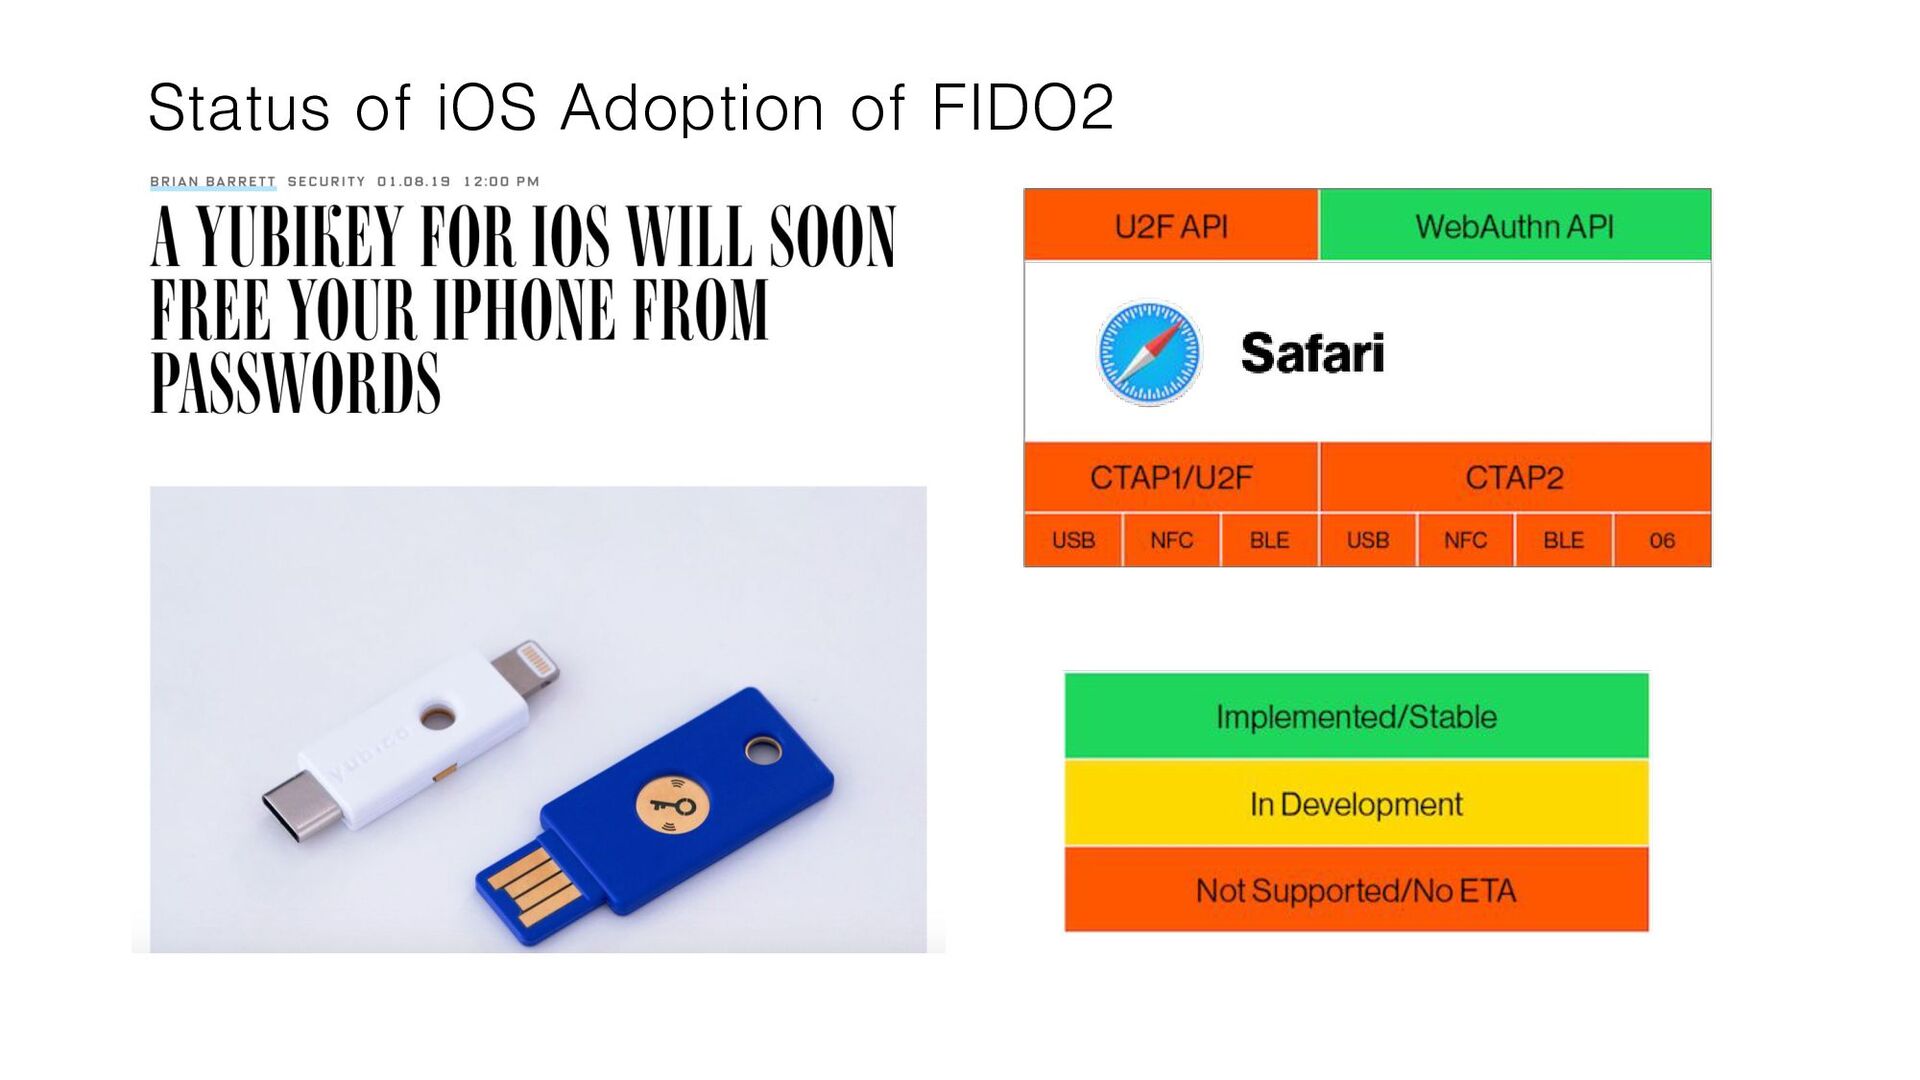
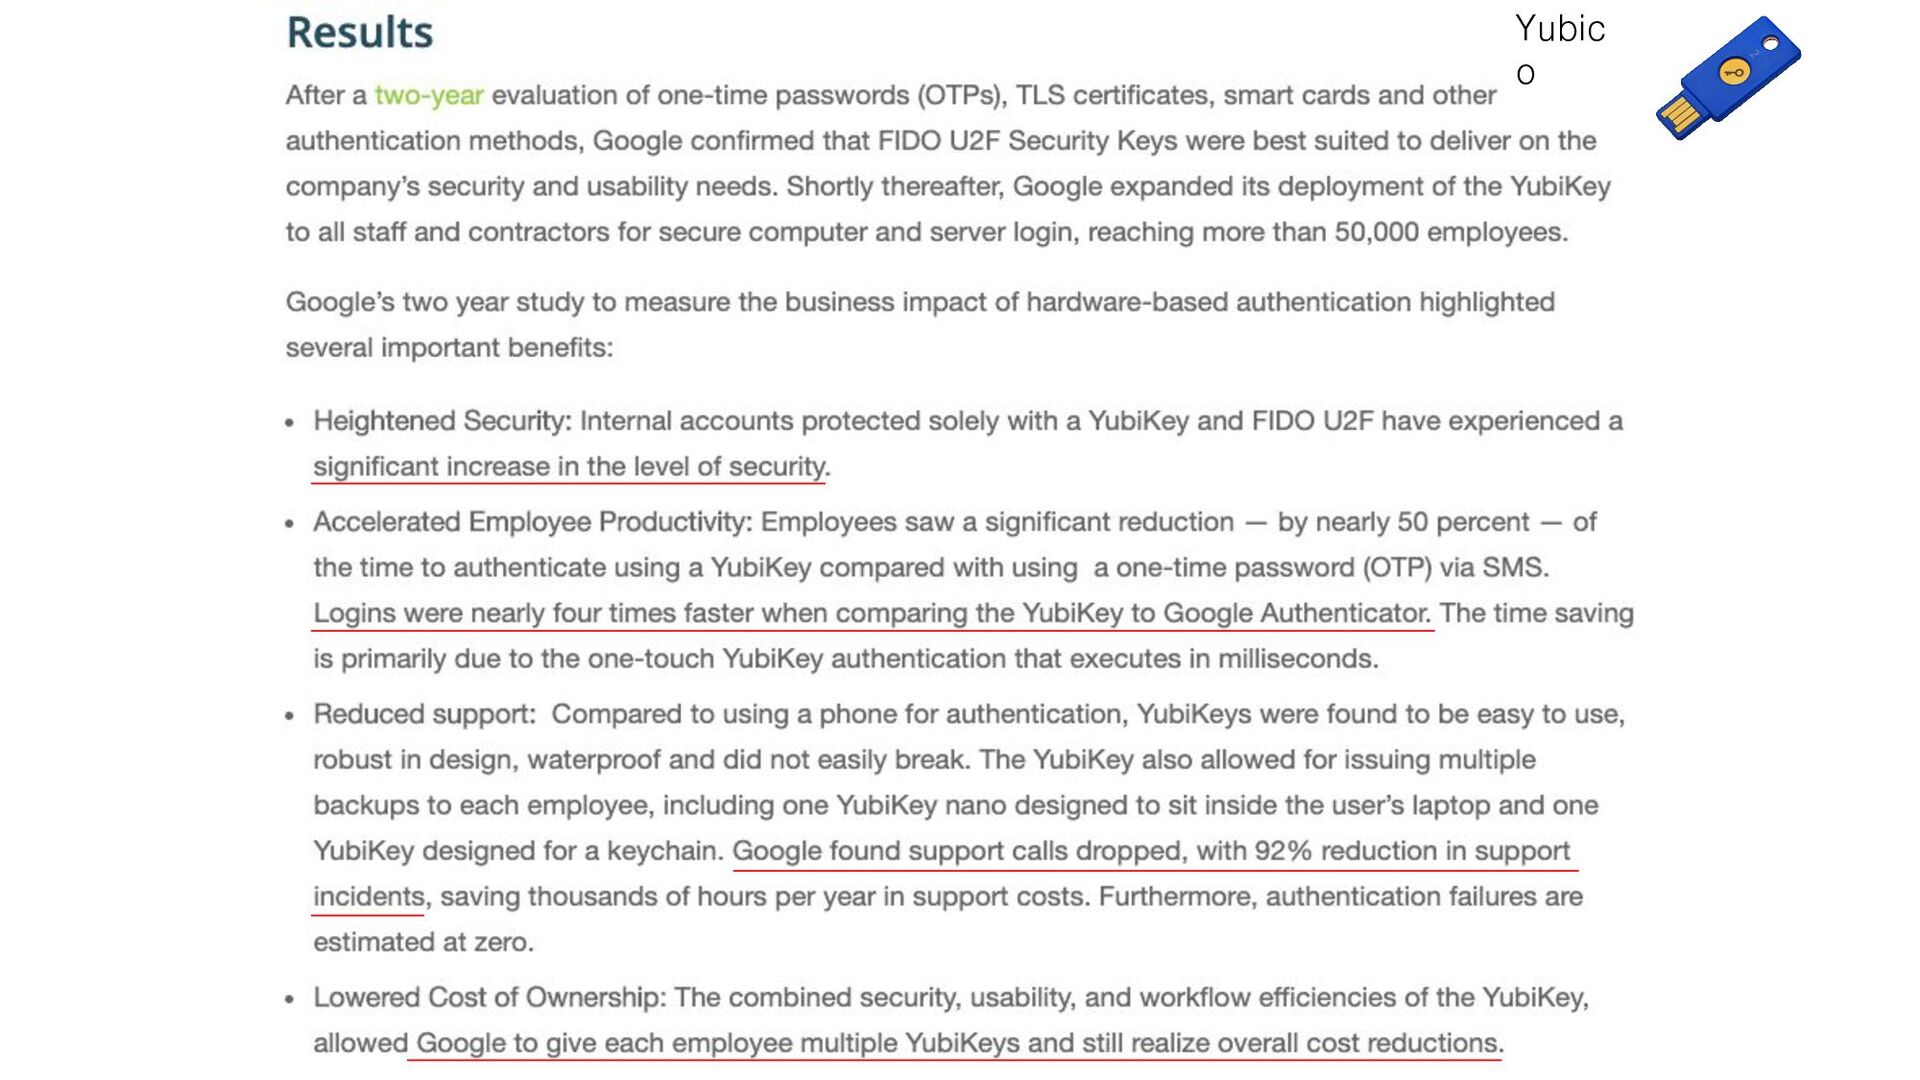
that strengthens and simplifies 2FA hosted by the FIDO Alliance • What if I lost? • The acquired can use it as his own U2F without knowing my account credentials Yubico YubiKey
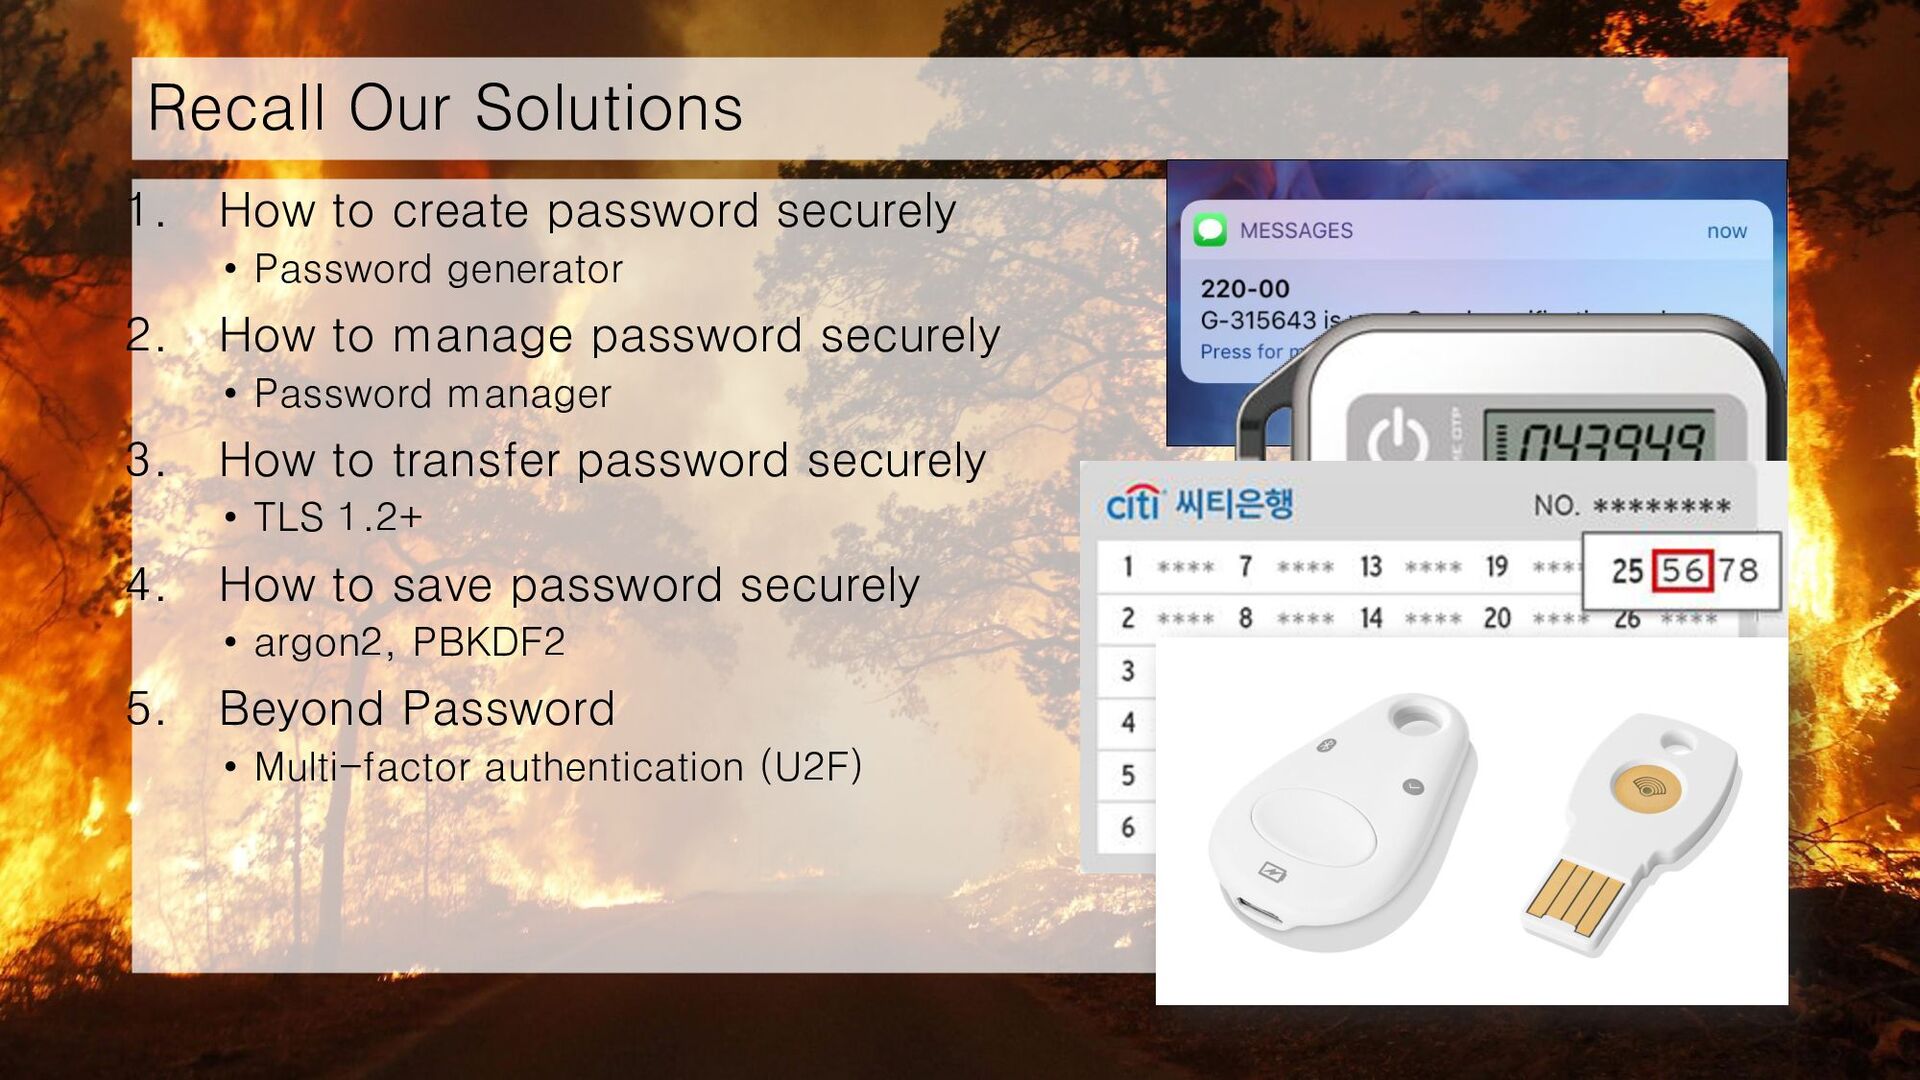
Password generator 2. How to manage password securely • Password manager 3. How to transfer password securely • TLS 1.2+ 4. How to save password securely • argon2, PBKDF2 5. Beyond Password • Multi-factor authentication (U2F)
Password generator 2. How to manage password securely • Password manager 3. How to transfer password securely • TLS 1.2+ 4. How to save password securely • argon2, PBKDF2 5. Beyond Password • Multi-factor authentication (U2F) What is the REAL problem?
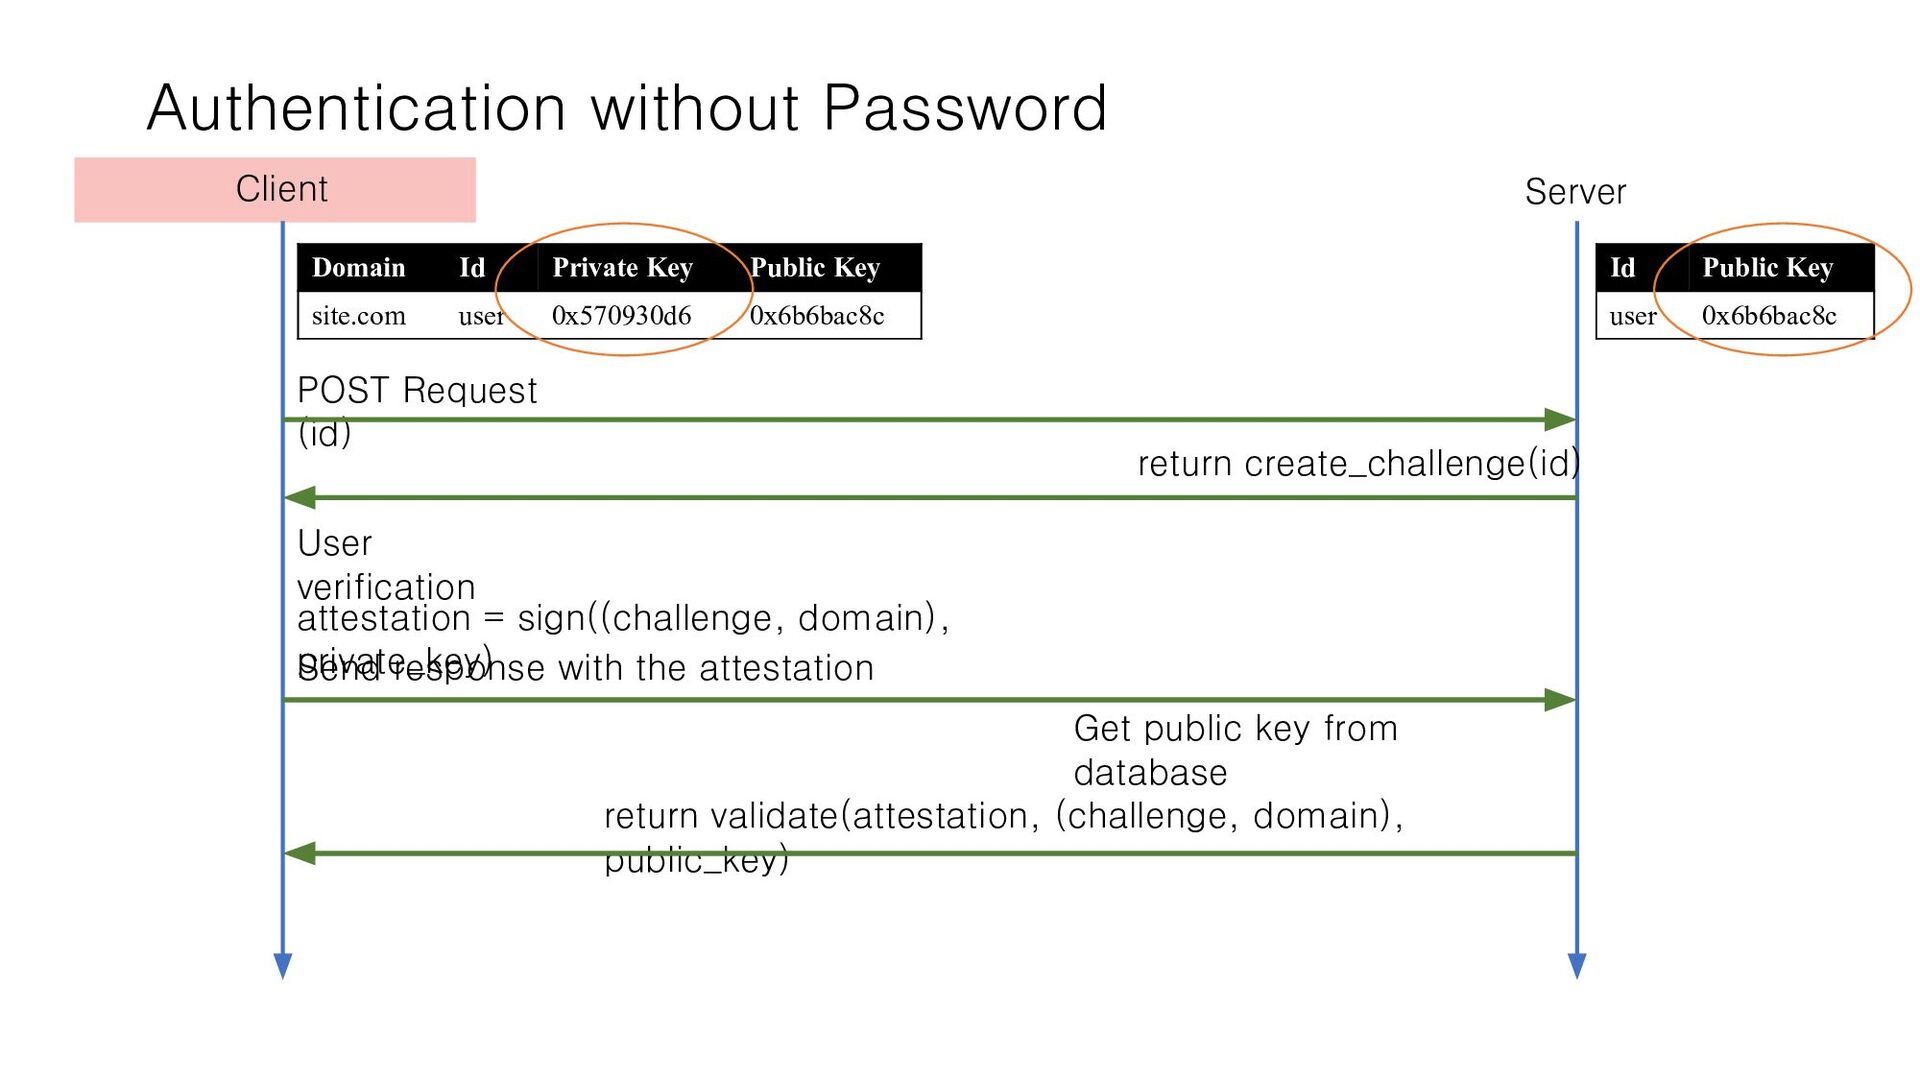
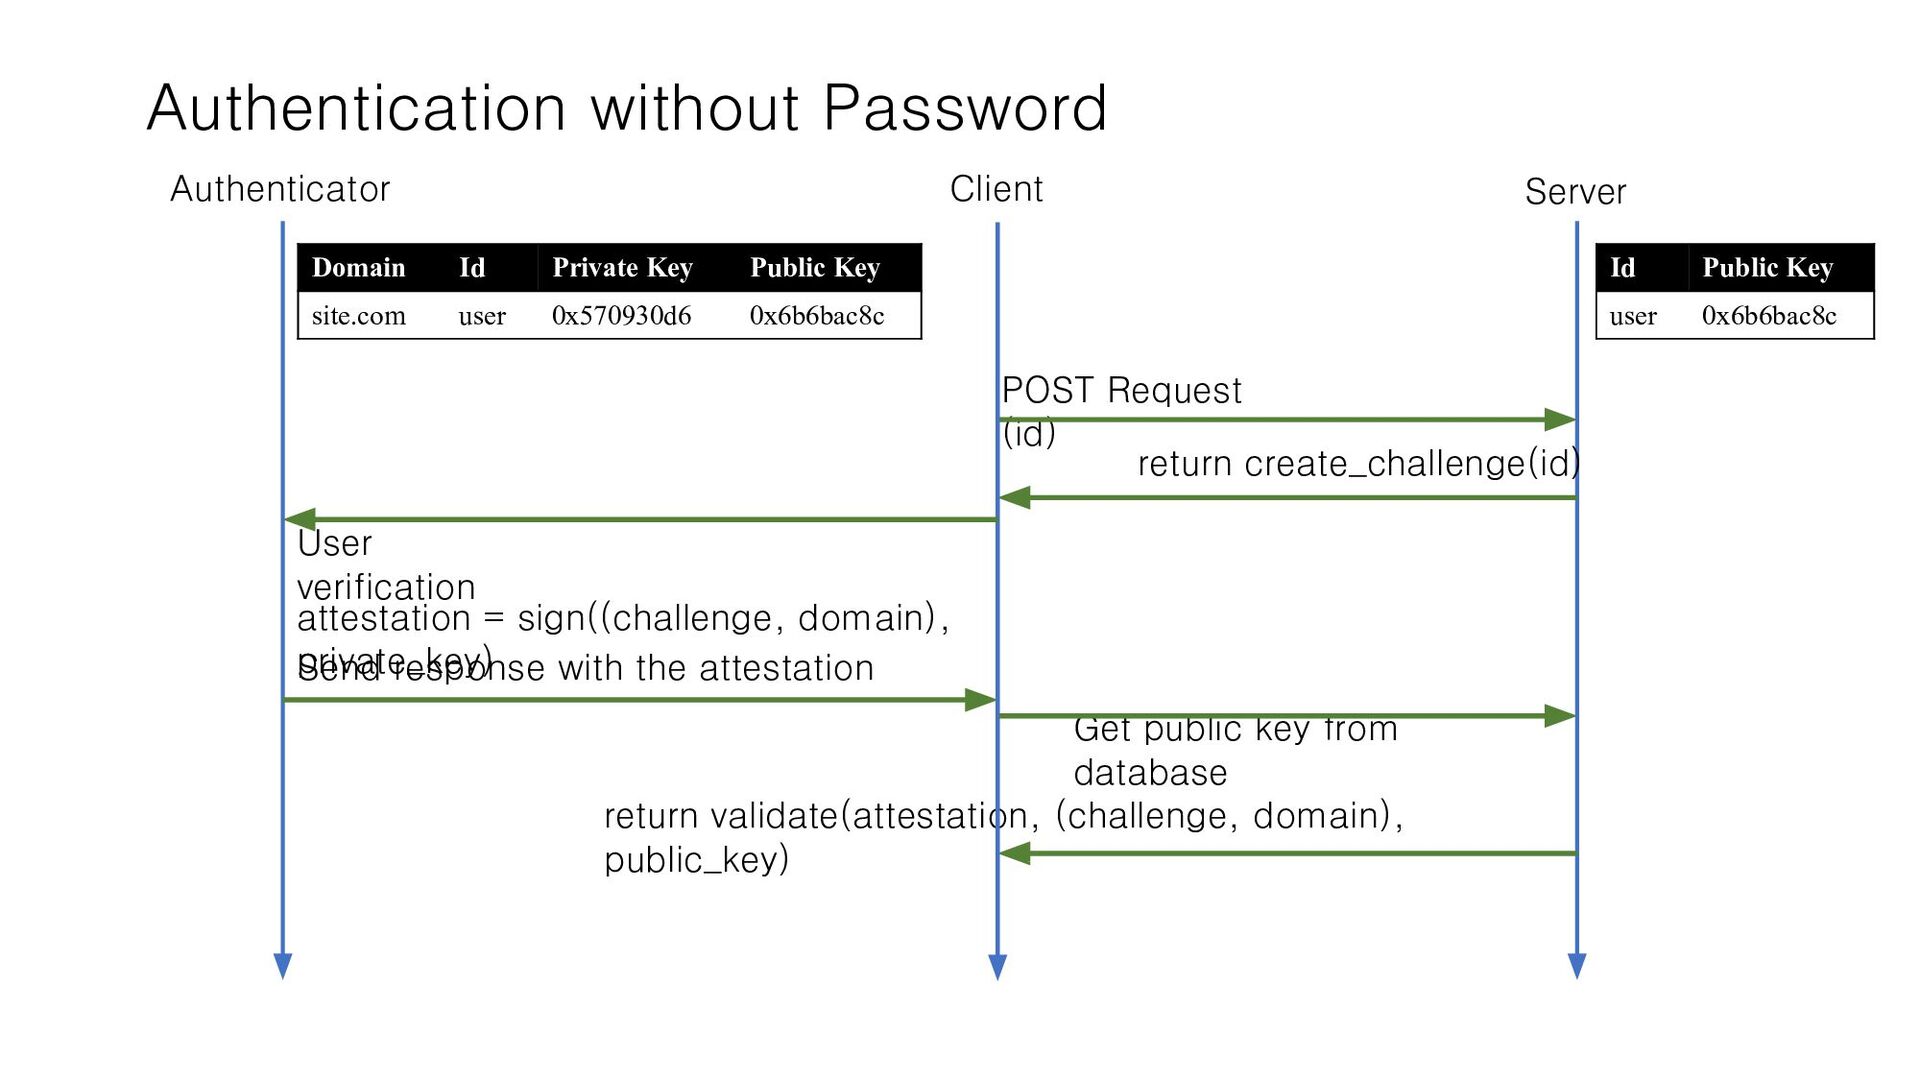
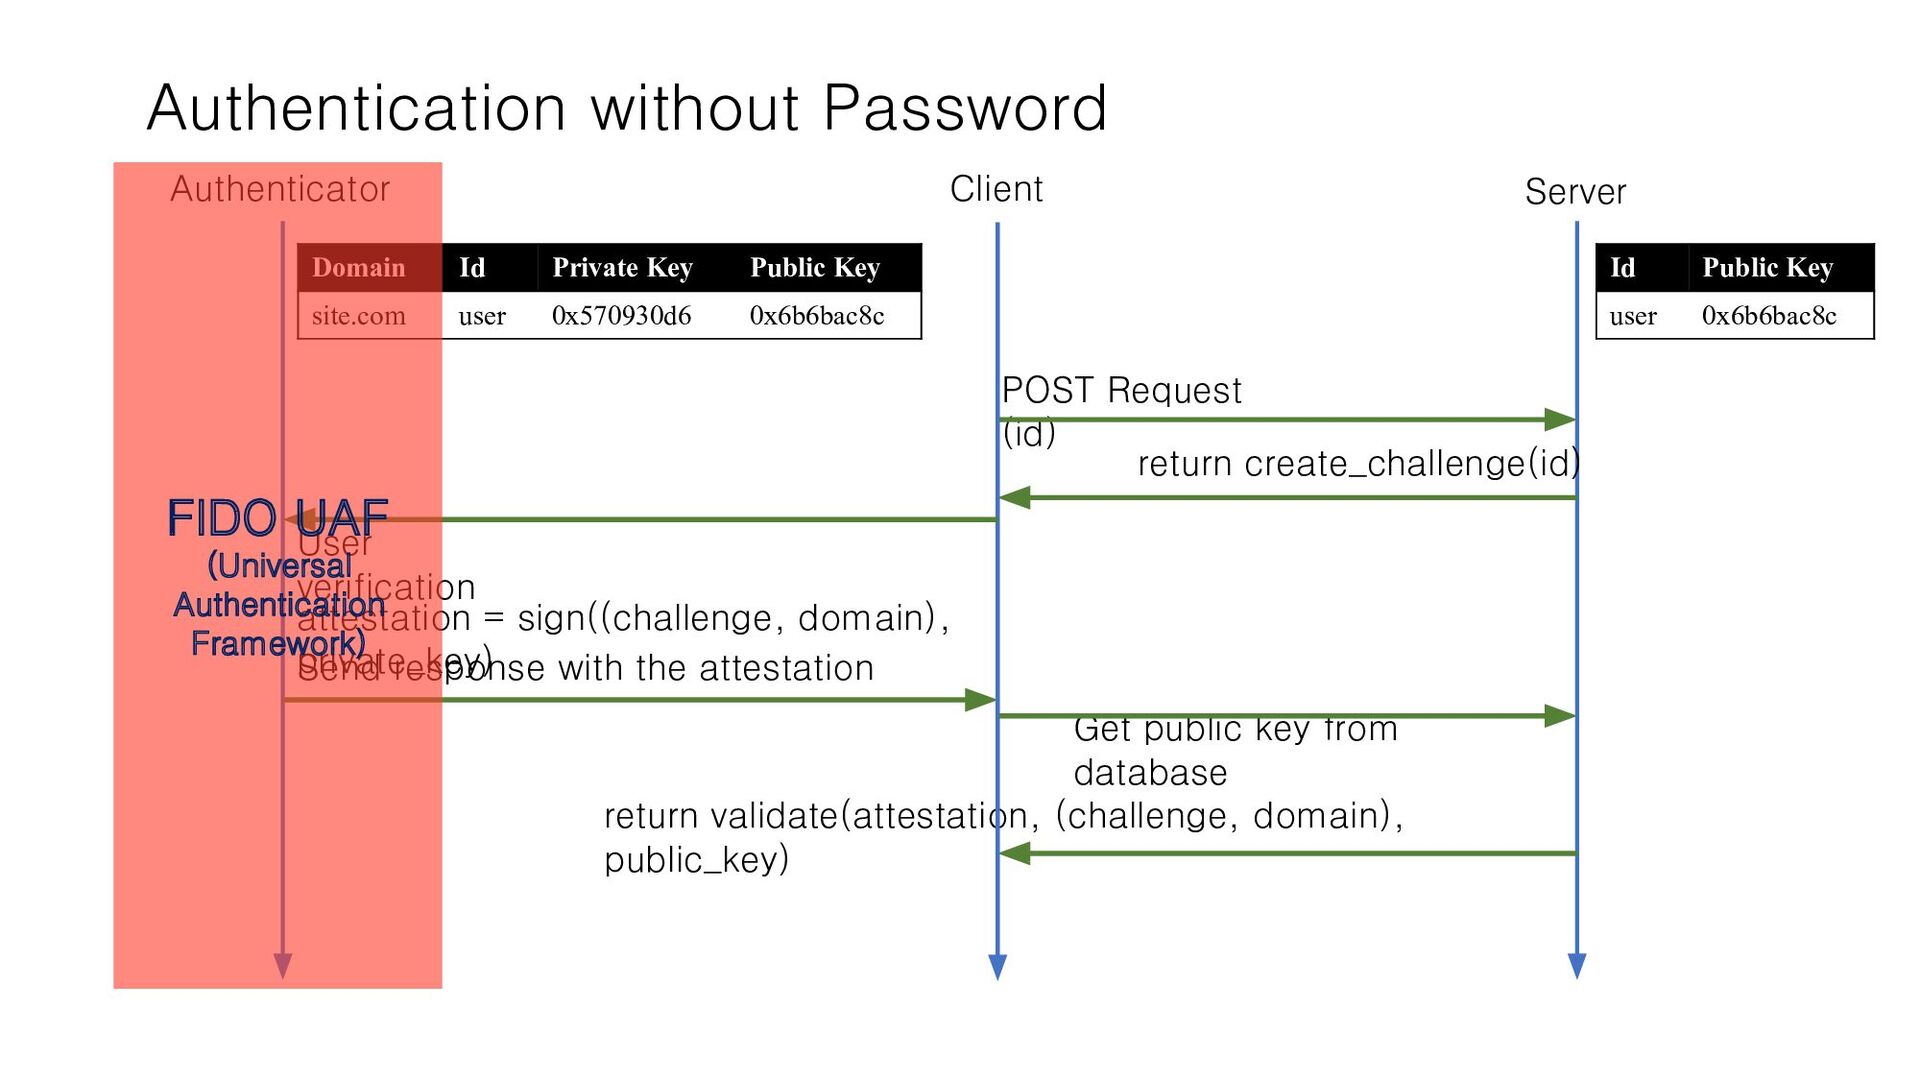
return validate(attestation, (challenge, domain), public_key) User verification attestation = sign((challenge, domain), private_key) Send response with the attestation Get public key from database Domain Id Private Key Public Key site.com user 0x570930d6 0x6b6bac8c Id Public Key user 0x6b6bac8c
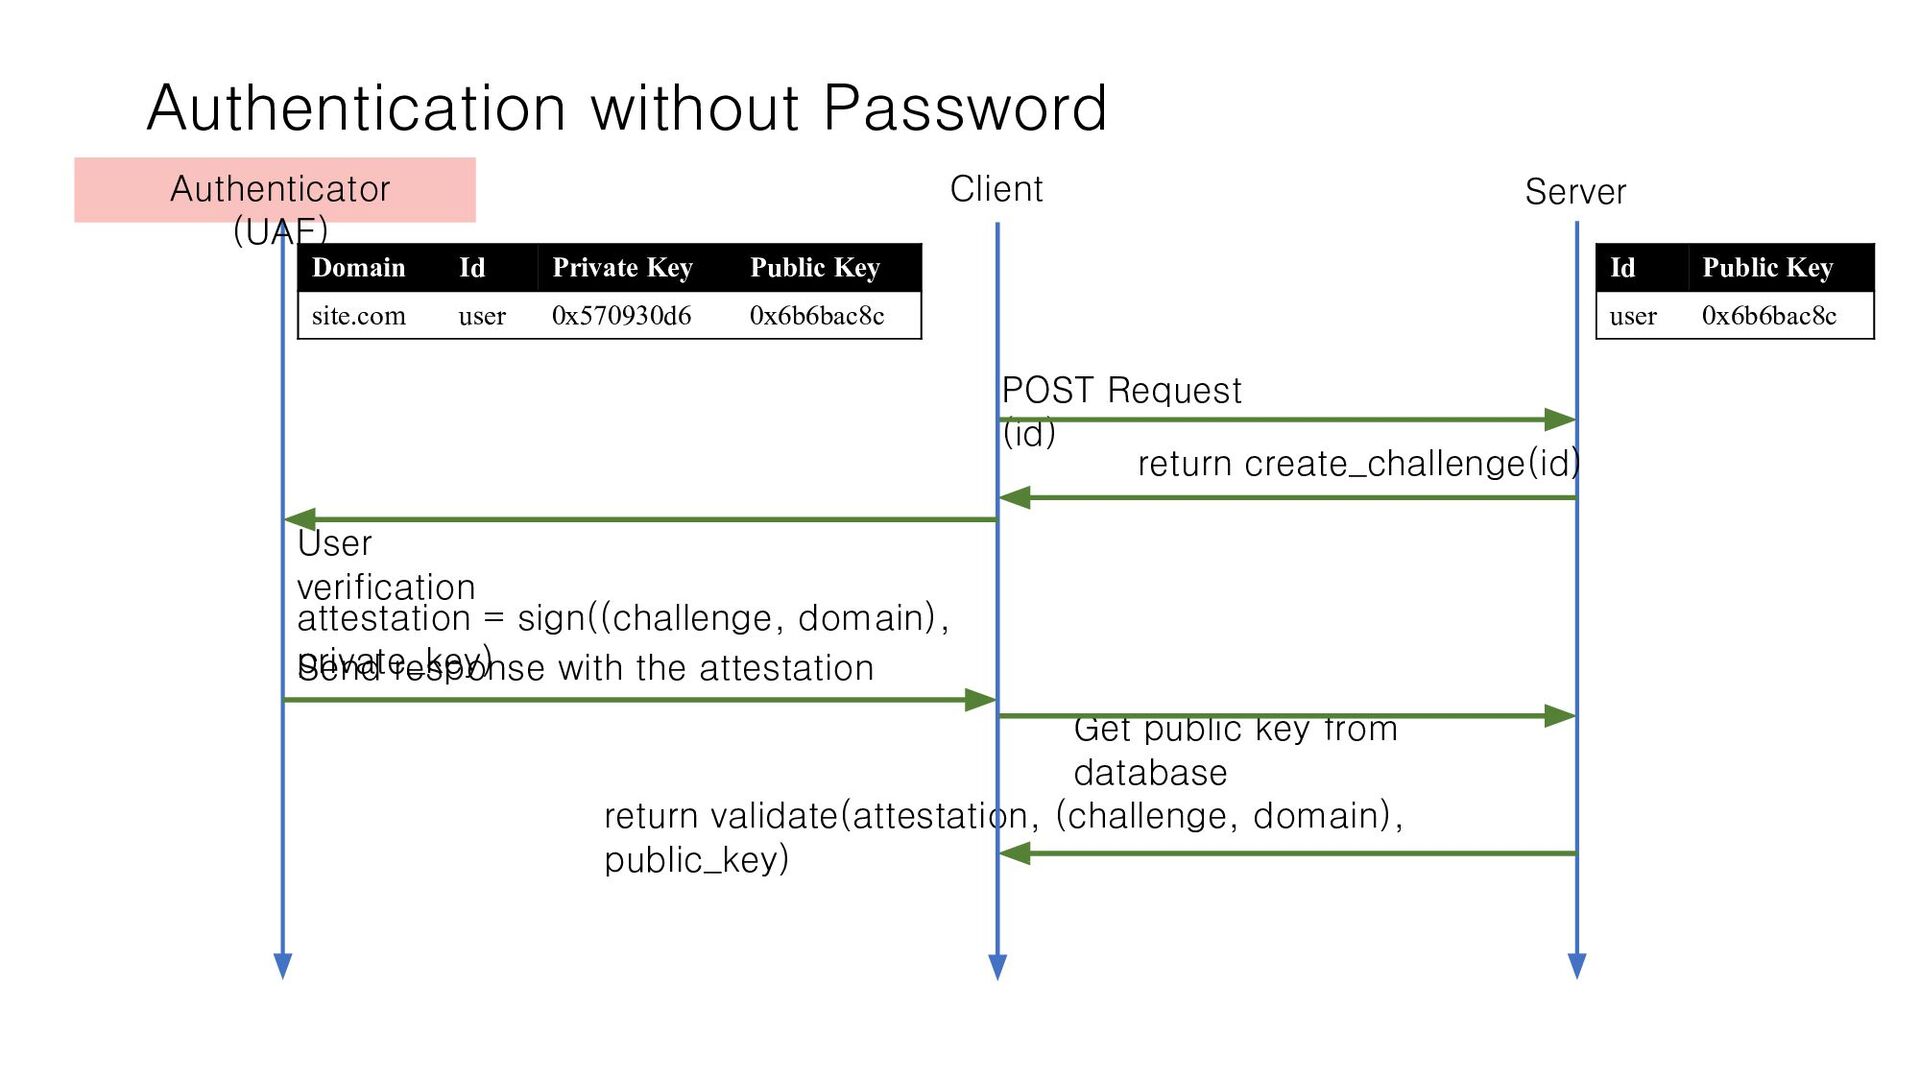
(id) return validate(attestation, (challenge, domain), public_key) User verification attestation = sign((challenge, domain), private_key) Send response with the attestation Get public key from database Domain Id Private Key Public Key site.com user 0x570930d6 0x6b6bac8c Id Public Key user 0x6b6bac8c Client
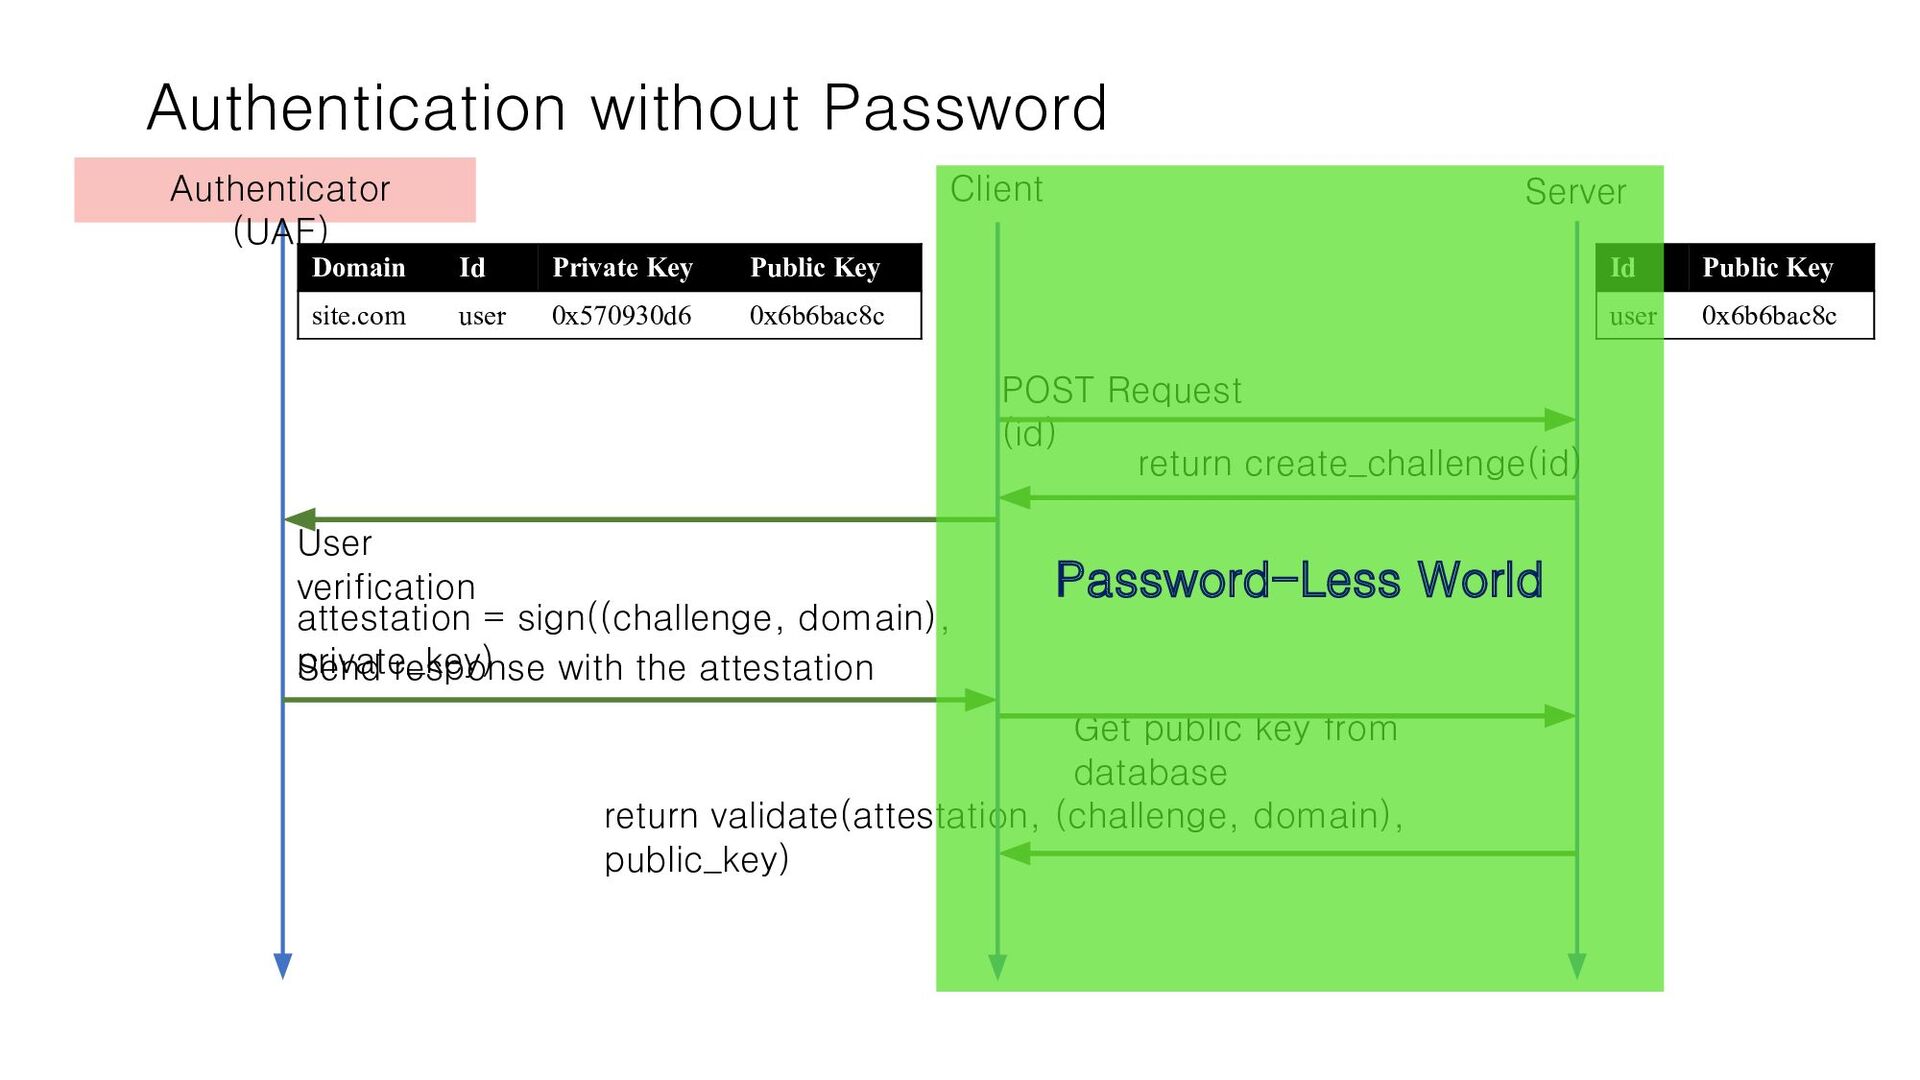
(id) return validate(attestation, (challenge, domain), public_key) User verification attestation = sign((challenge, domain), private_key) Send response with the attestation Get public key from database Domain Id Private Key Public Key site.com user 0x570930d6 0x6b6bac8c Id Public Key user 0x6b6bac8c Client Password-Less World
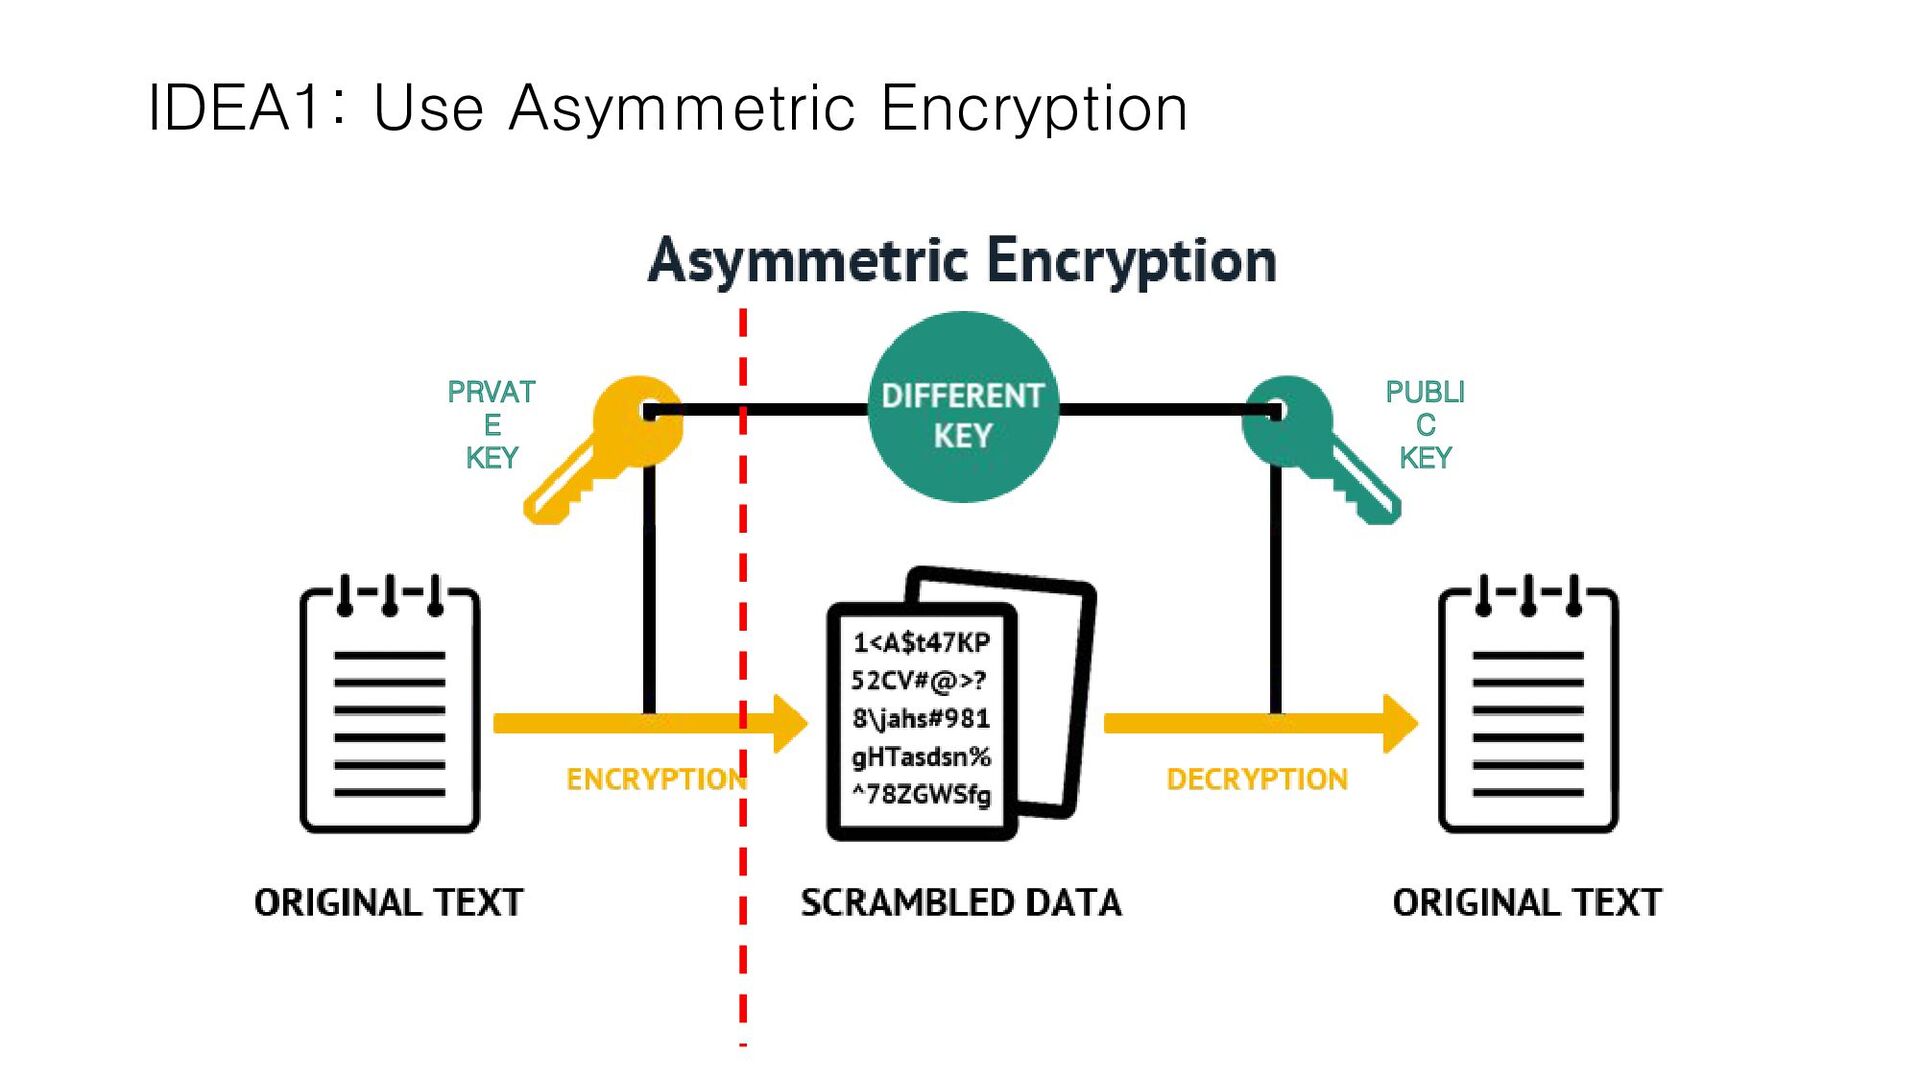
keys • Because it is not in the world • Servers save and manage the public key with a little less effort • Because it is meaningless for others • Client vulnerabilities are meaningless • Because there is no protocol that retrieves the private key from the authenticator • Easy to human beings • Don’t need to create, remember and type the complicated passwords
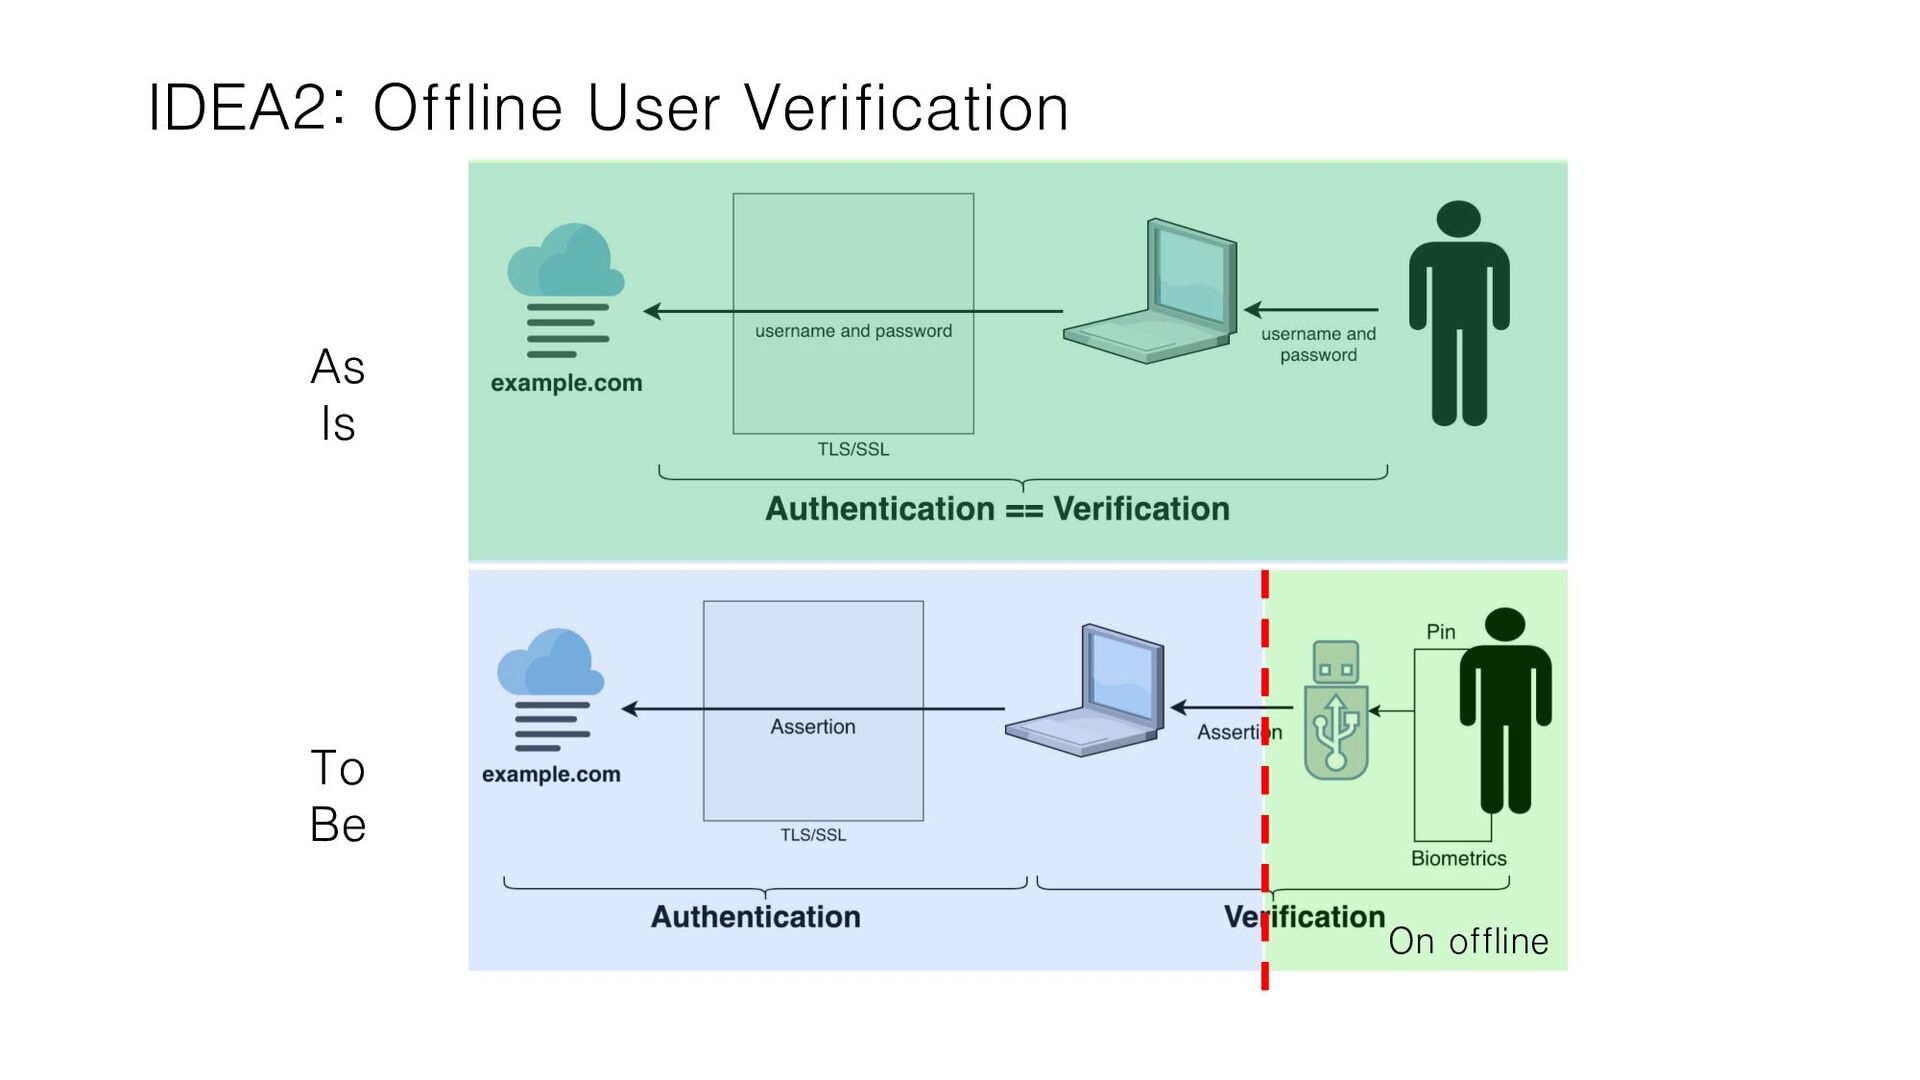
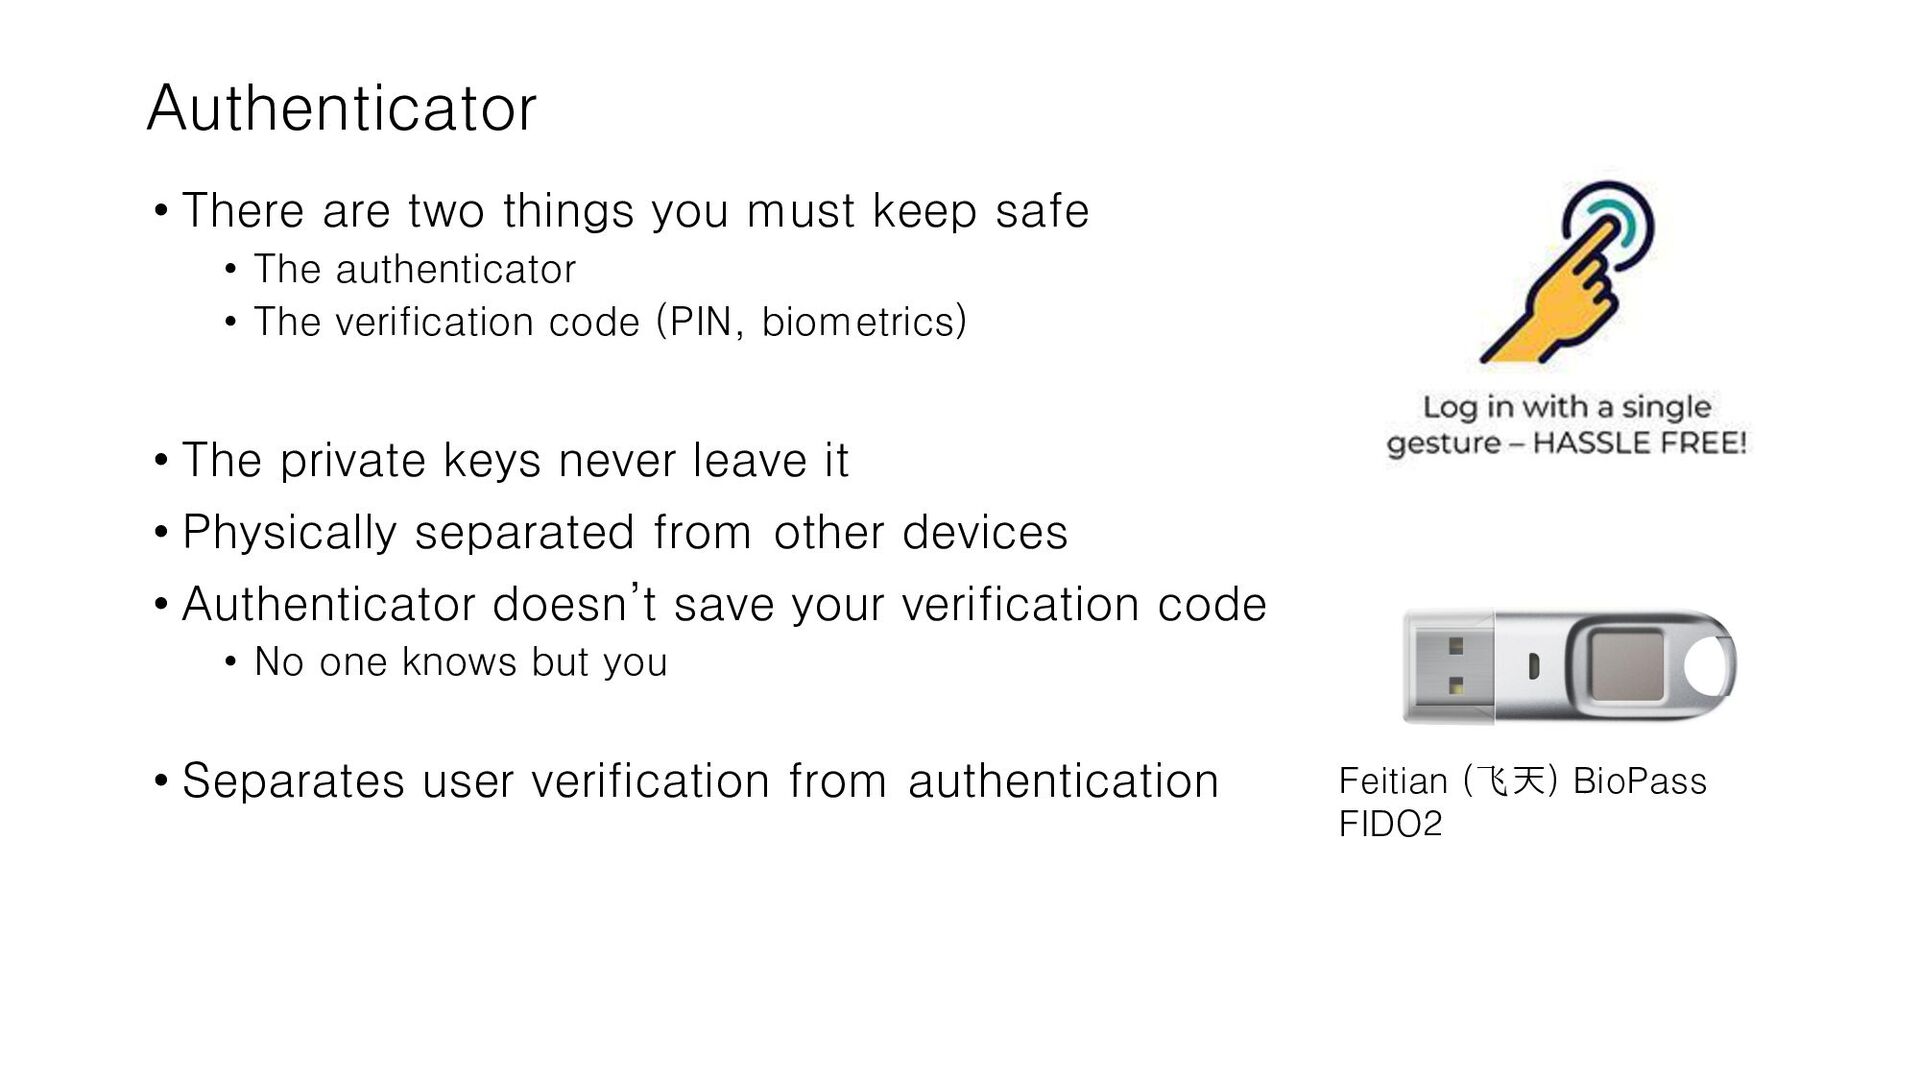
• The authenticator • The verification code (PIN, biometrics) • The private keys never leave it • Physically separated from other devices • Authenticator doesn’t save your verification code • No one knows but you • Separates user verification from authentication Feitian (飞天) BioPass FIDO2
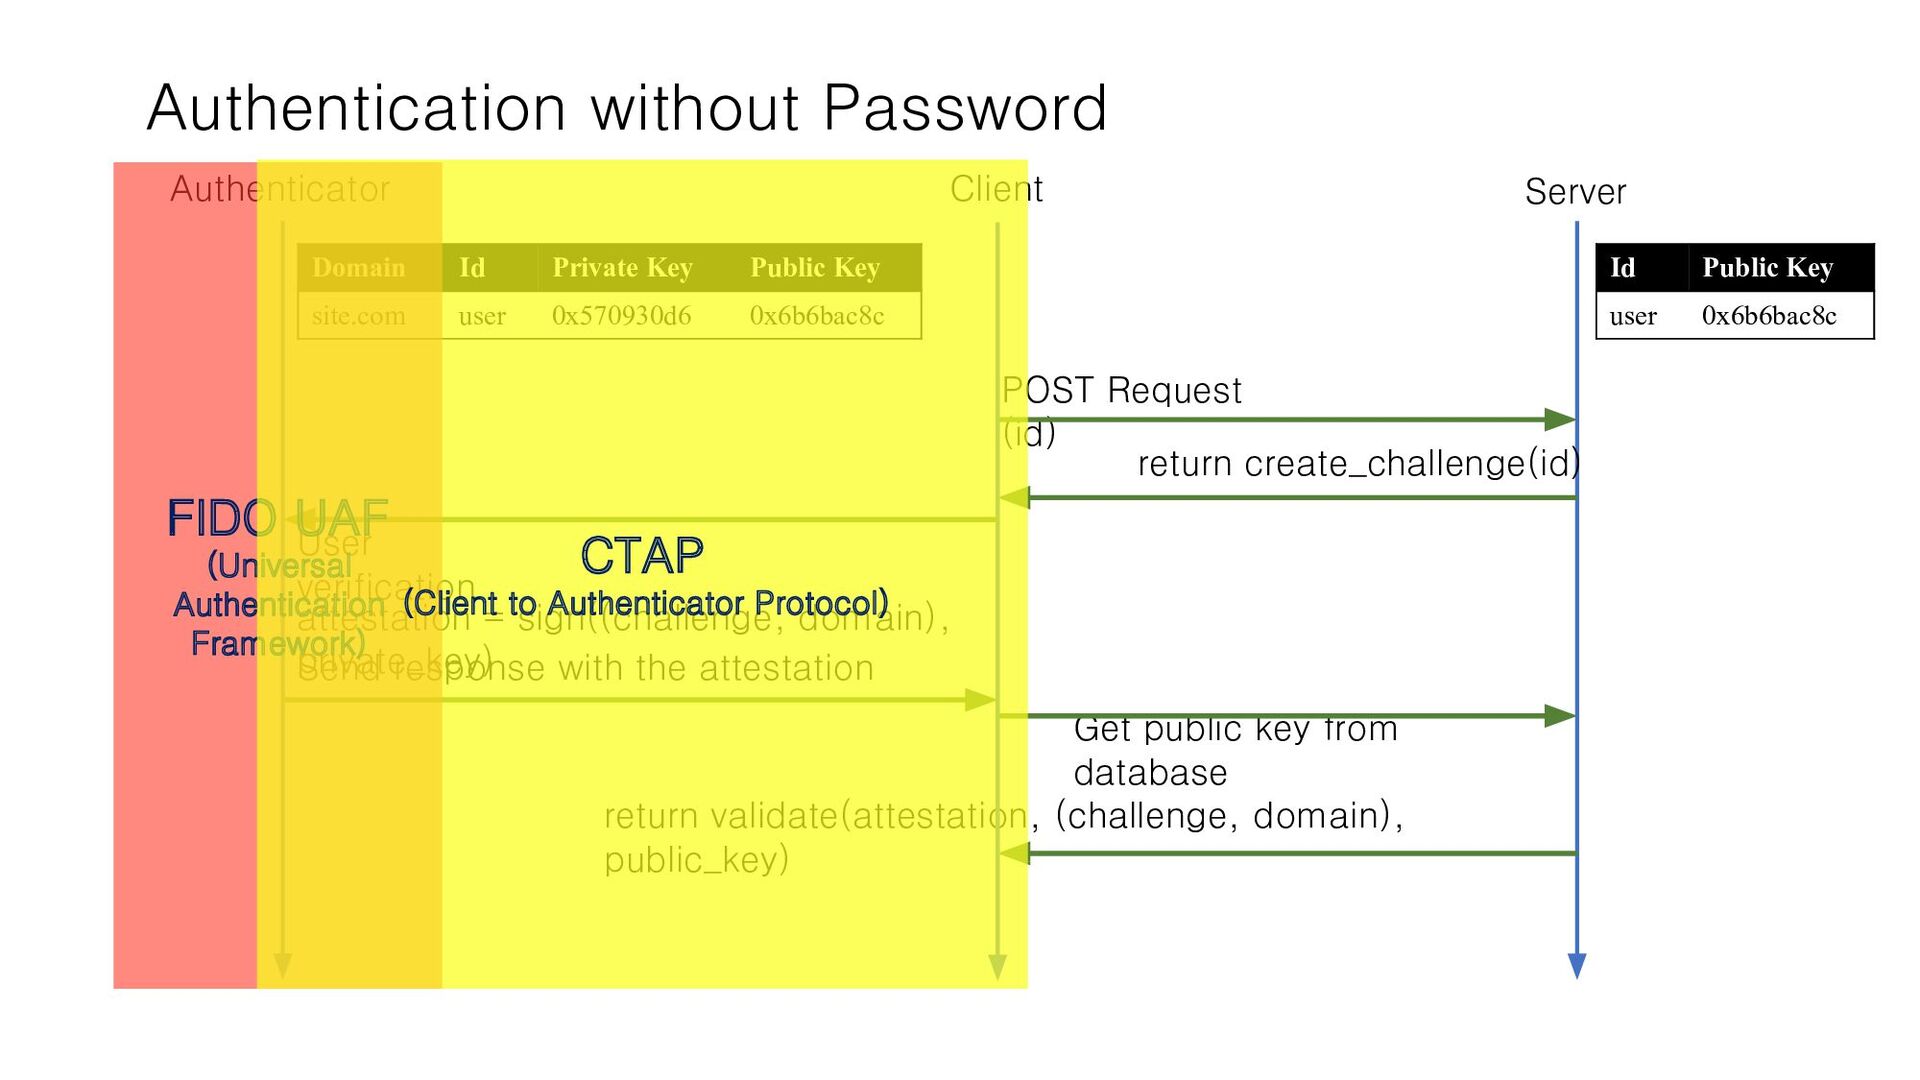
return validate(attestation, (challenge, domain), public_key) User verification attestation = sign((challenge, domain), private_key) Send response with the attestation Get public key from database Domain Id Private Key Public Key site.com user 0x570930d6 0x6b6bac8c Id Public Key user 0x6b6bac8c Client
return validate(attestation, (challenge, domain), public_key) User verification attestation = sign((challenge, domain), private_key) Send response with the attestation Get public key from database Domain Id Private Key Public Key site.com user 0x570930d6 0x6b6bac8c Id Public Key user 0x6b6bac8c Client FIDO UAF (Universal Authentication Framework)
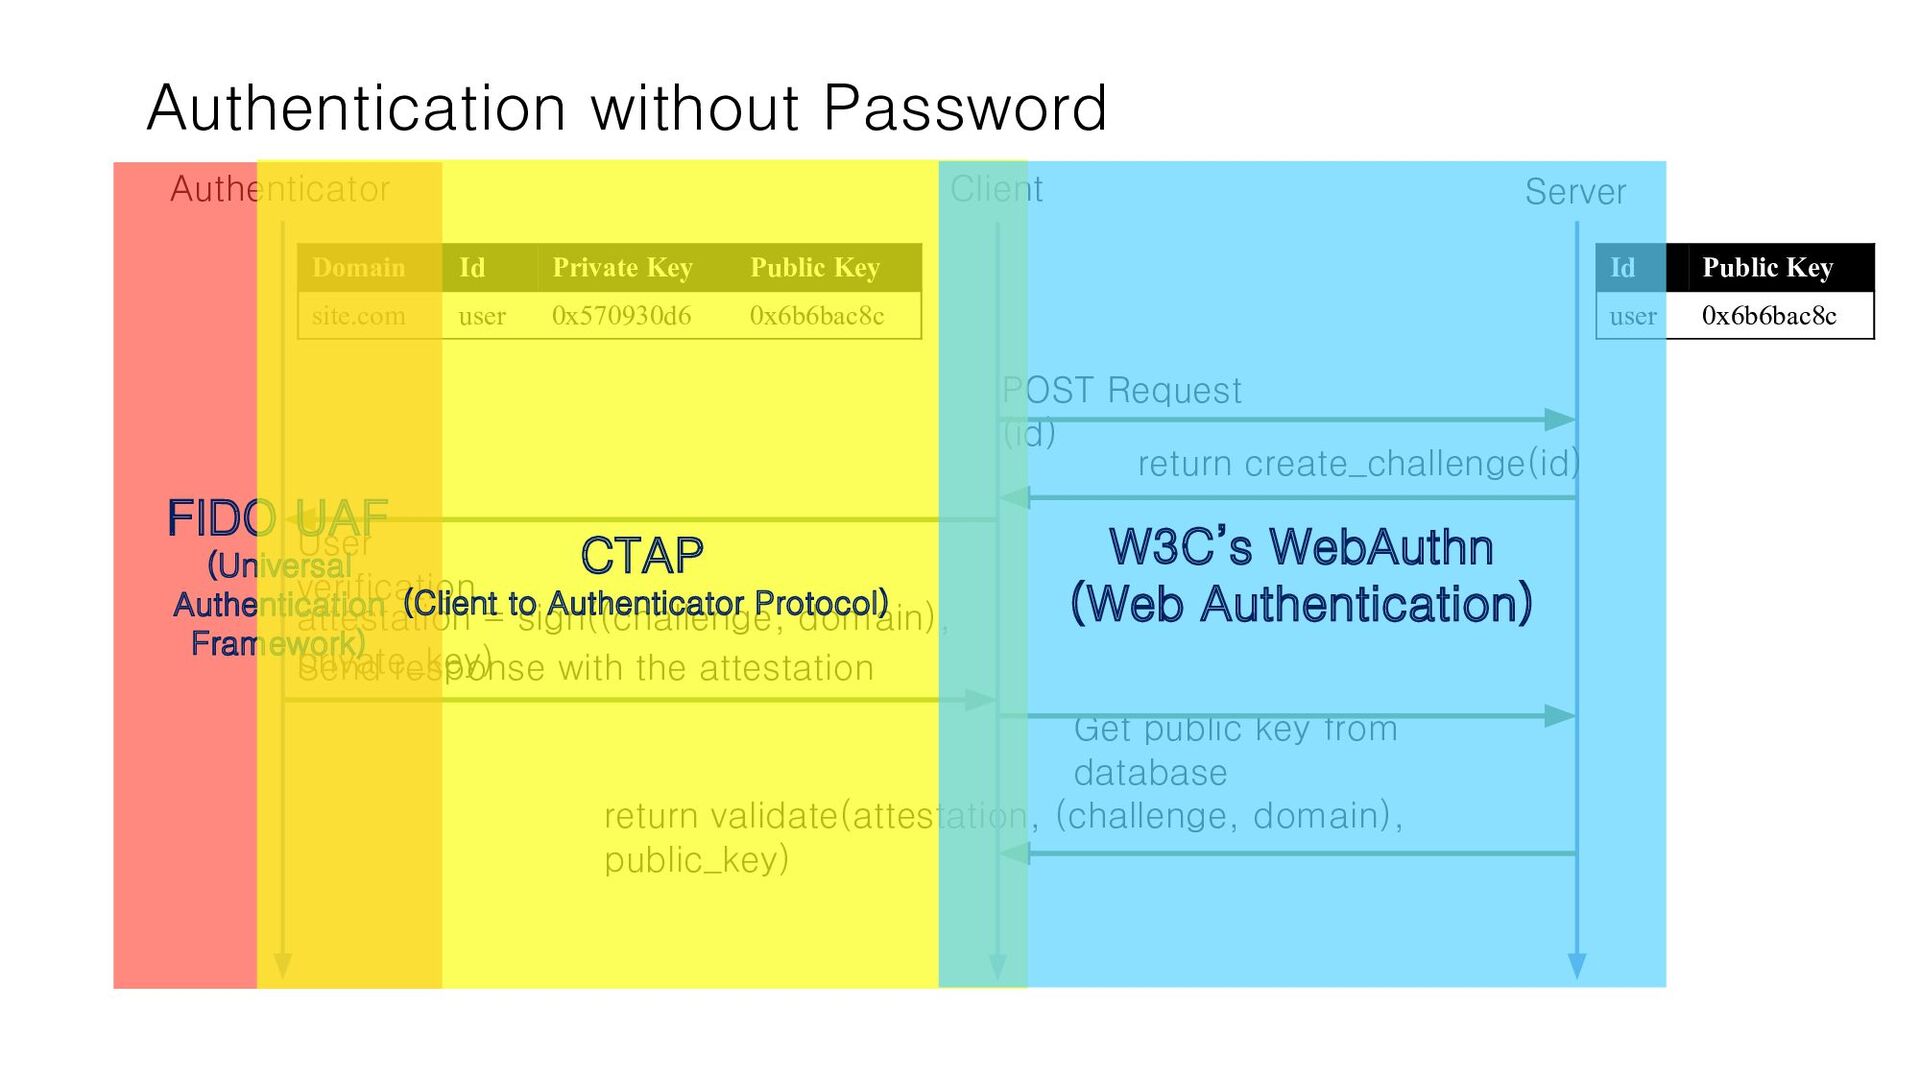
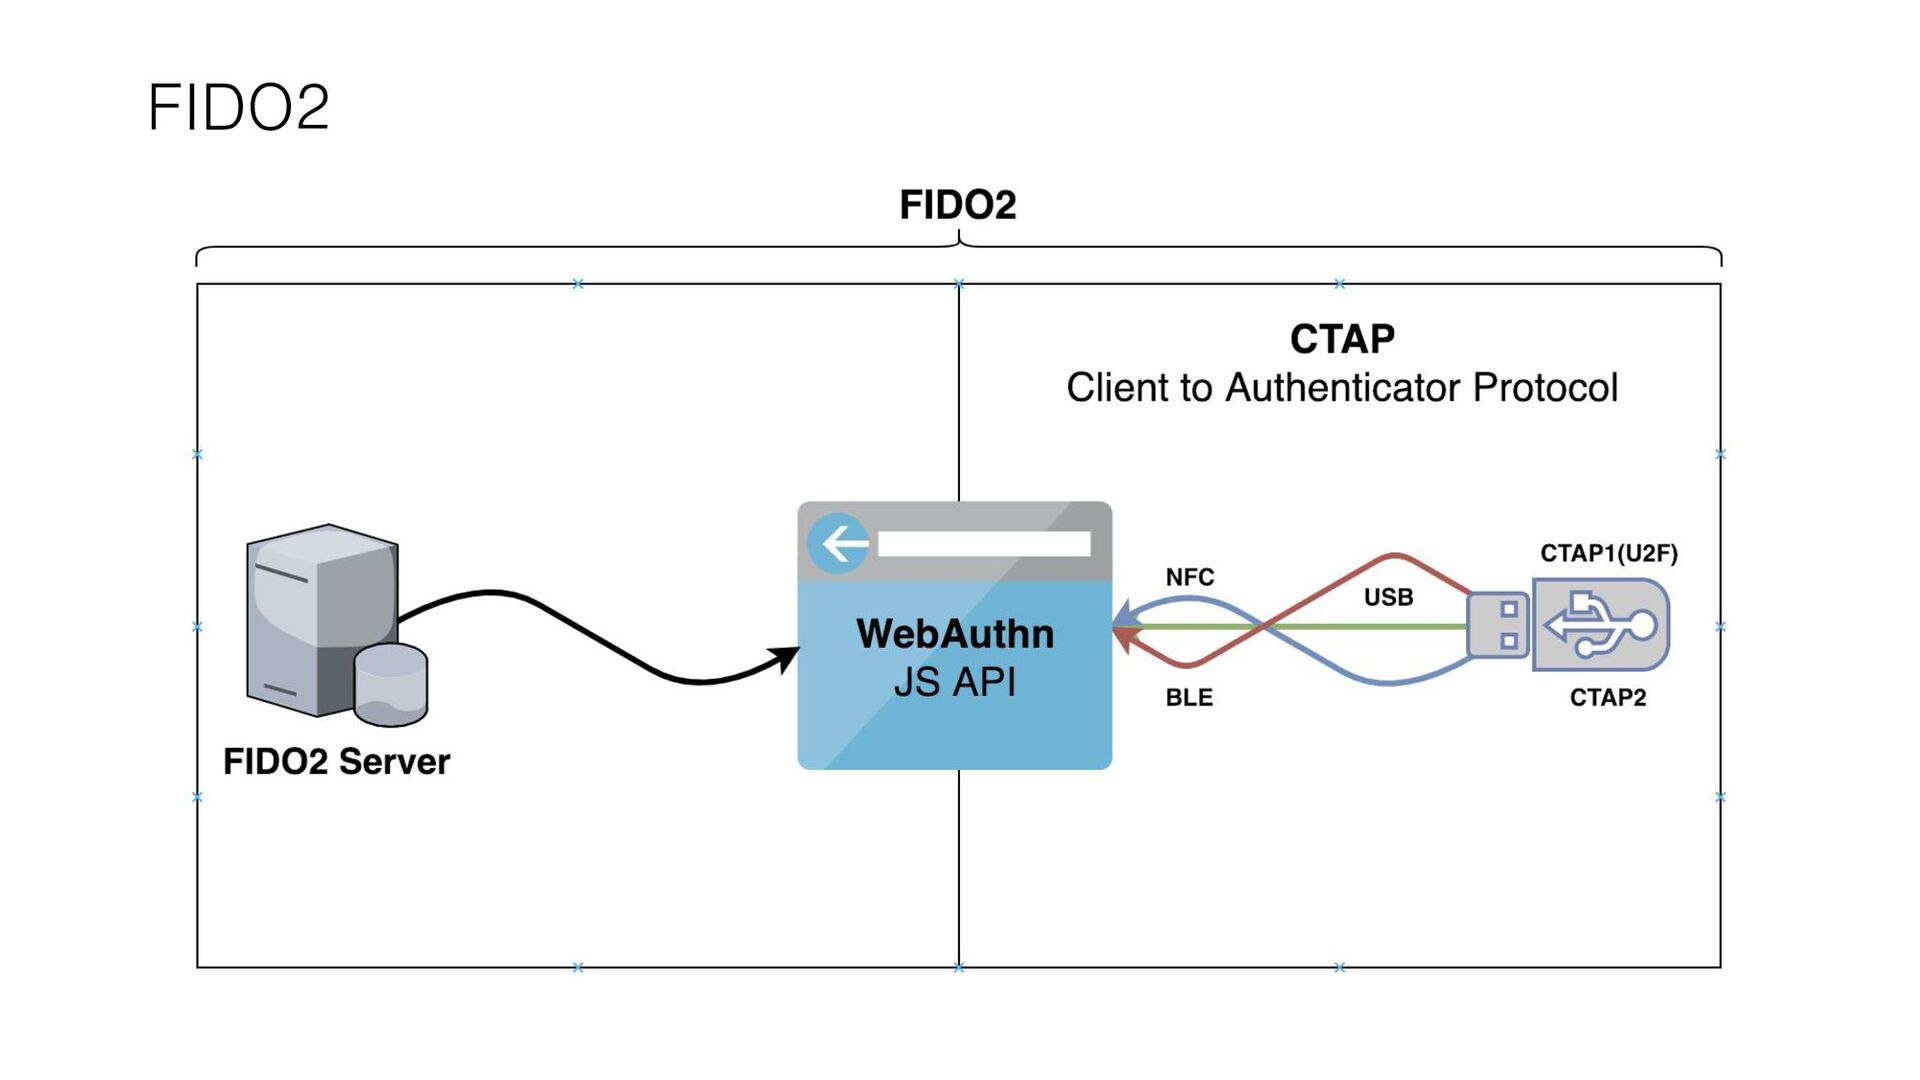
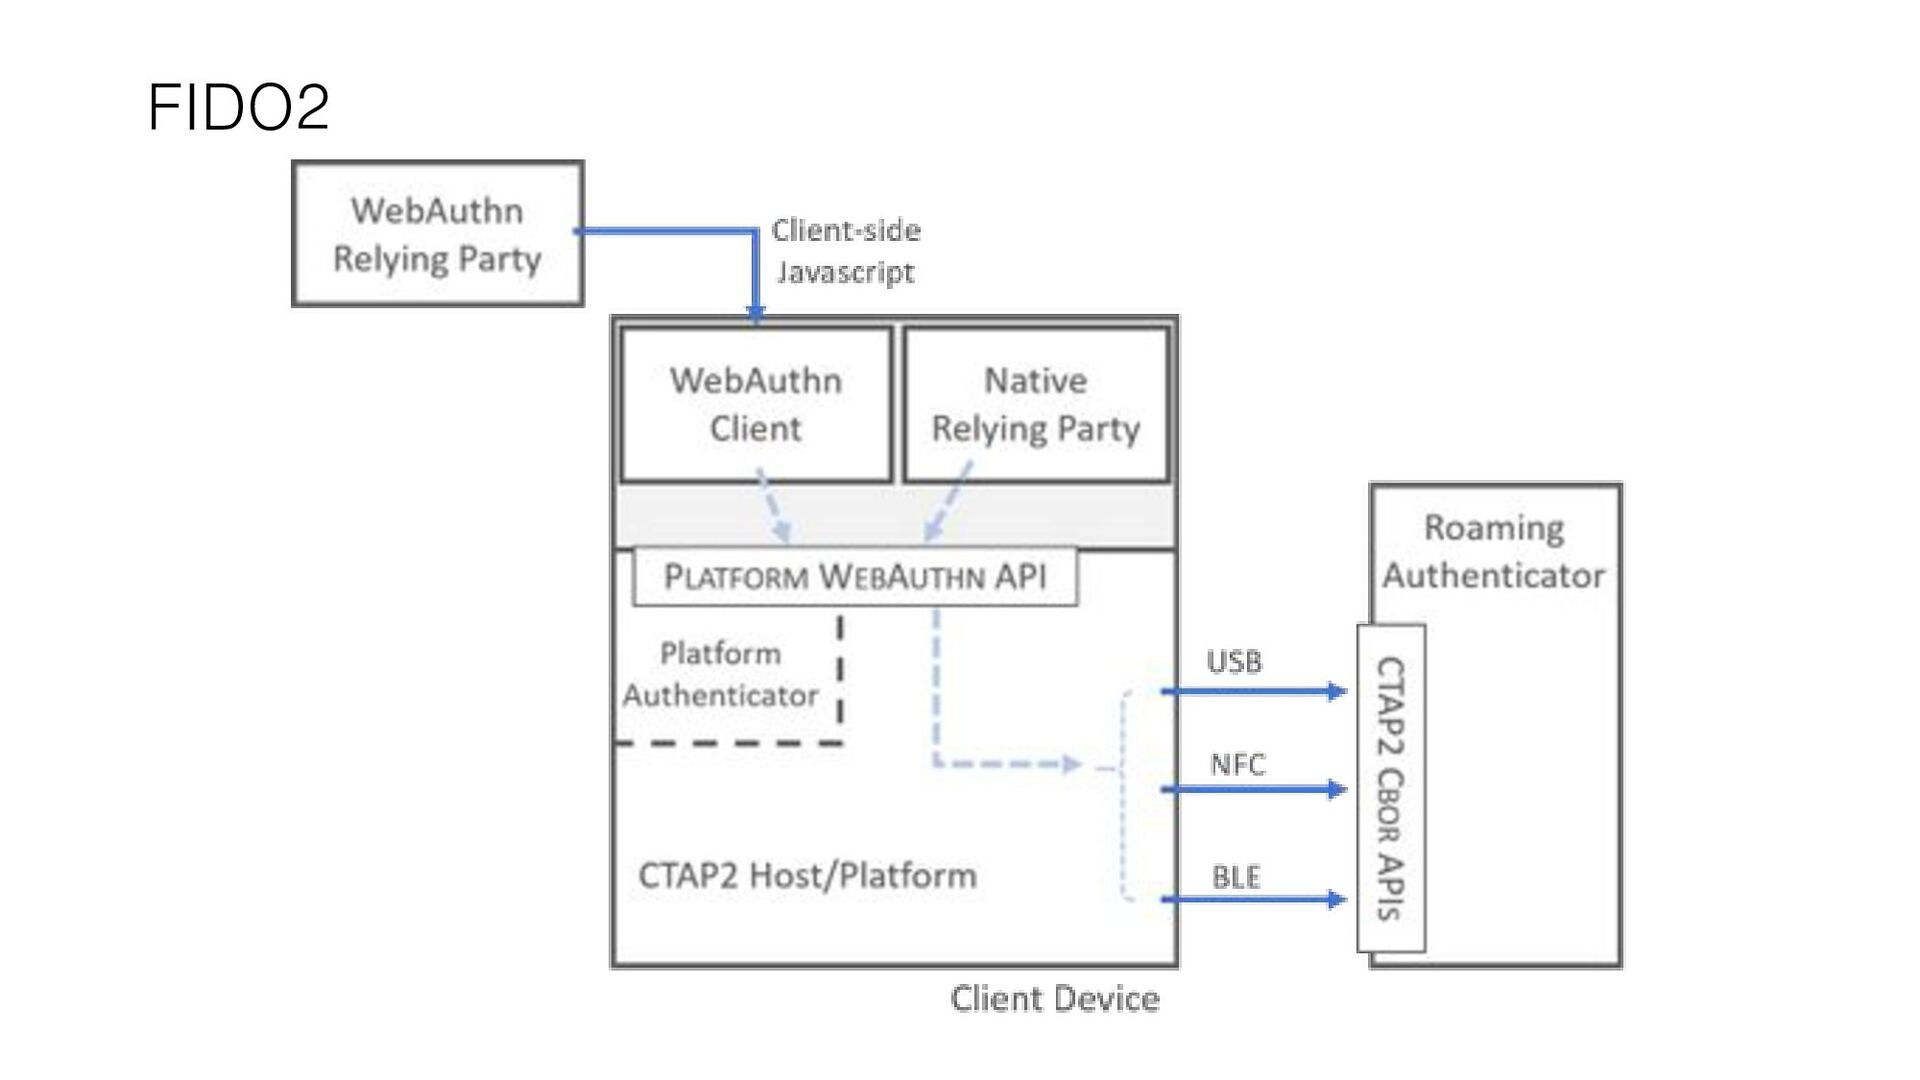
return validate(attestation, (challenge, domain), public_key) User verification attestation = sign((challenge, domain), private_key) Send response with the attestation Get public key from database Domain Id Private Key Public Key site.com user 0x570930d6 0x6b6bac8c Id Public Key user 0x6b6bac8c Client FIDO UAF (Universal Authentication Framework) CTAP (Client to Authenticator Protocol)
return validate(attestation, (challenge, domain), public_key) User verification attestation = sign((challenge, domain), private_key) Send response with the attestation Get public key from database Domain Id Private Key Public Key site.com user 0x570930d6 0x6b6bac8c Id Public Key user 0x6b6bac8c Client FIDO UAF (Universal Authentication Framework) CTAP (Client to Authenticator Protocol) W3C’s WebAuthn (Web Authentication)
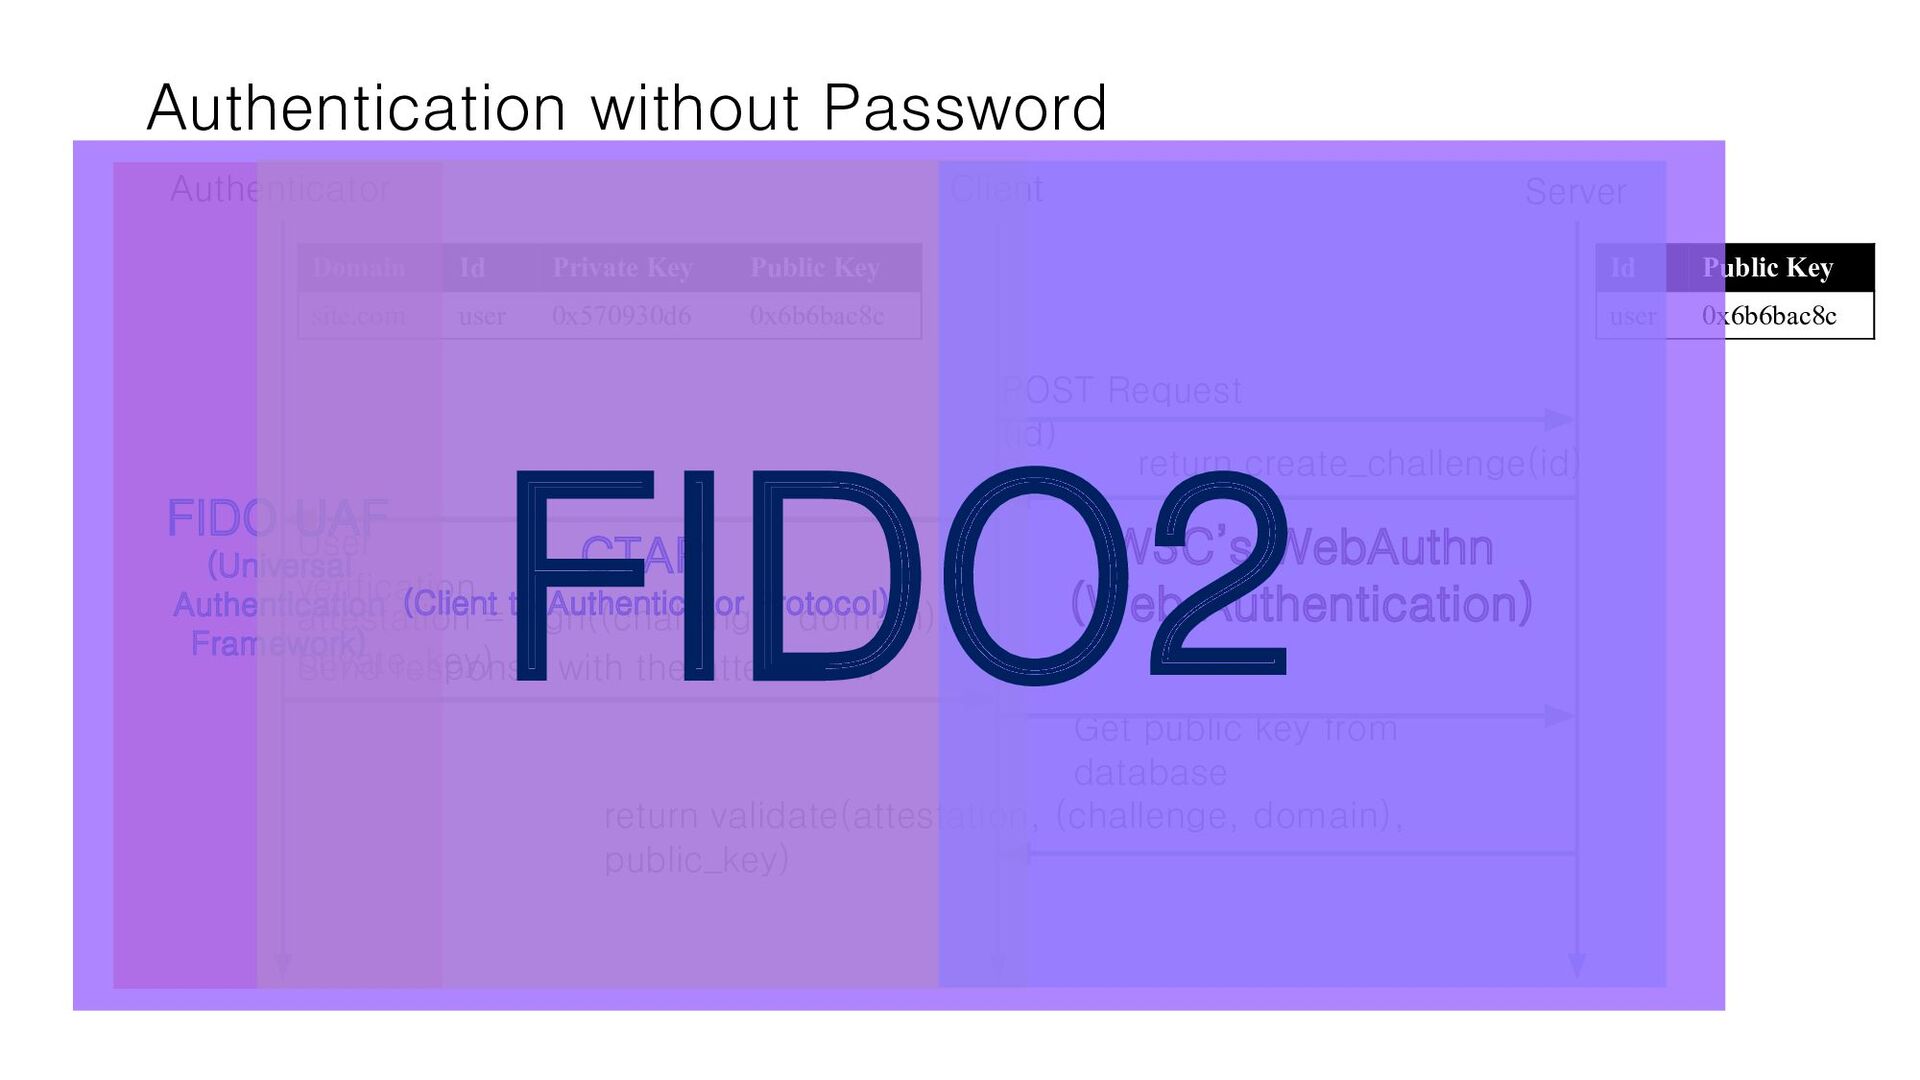
return validate(attestation, (challenge, domain), public_key) User verification attestation = sign((challenge, domain), private_key) Send response with the attestation Get public key from database Domain Id Private Key Public Key site.com user 0x570930d6 0x6b6bac8c Id Public Key user 0x6b6bac8c Client FIDO UAF (Universal Authentication Framework) CTAP (Client to Authenticator Protocol) W3C’s WebAuthn (Web Authentication) FIDO2
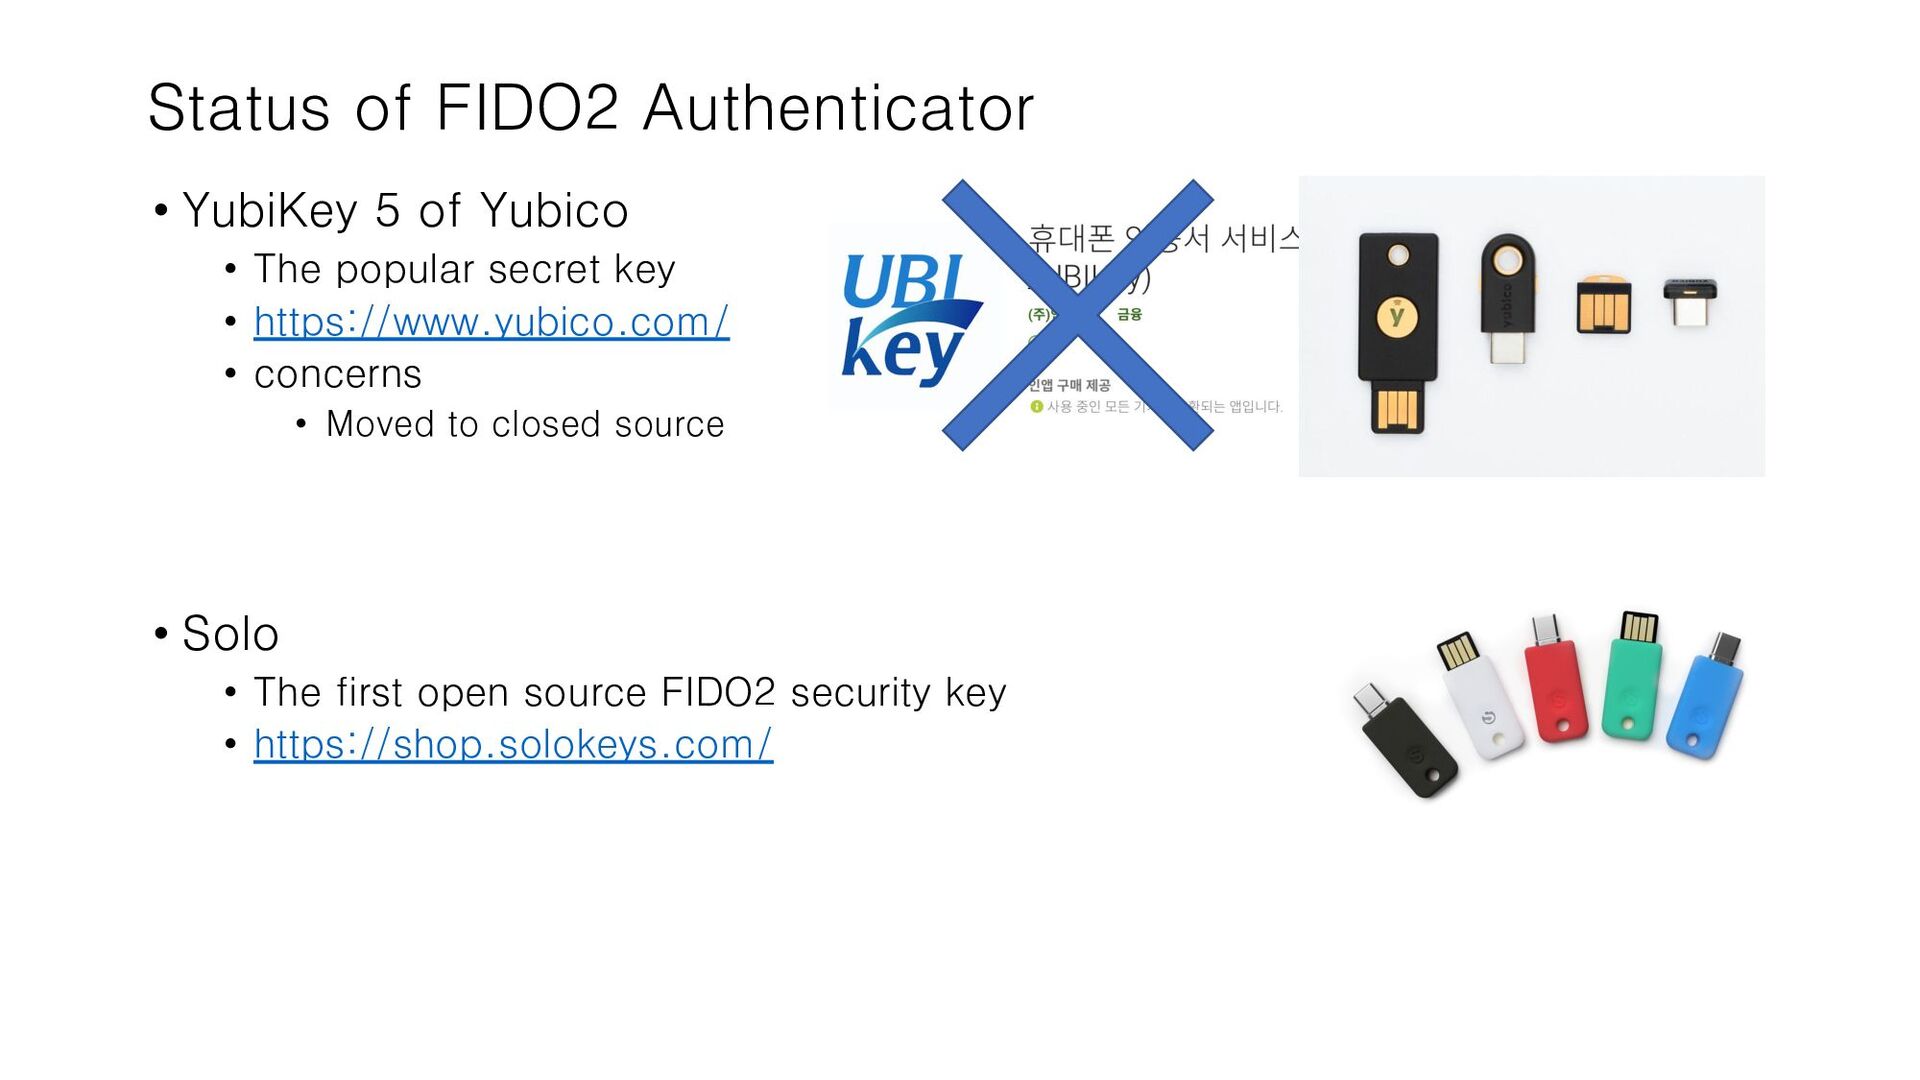
The popular secret key • https://www.yubico.com/ • concerns • Moved to closed source • Solo • The first open source FIDO2 security key • https://shop.solokeys.com/
https://slides.com/fidoalliance/jan-2018-fido-seminar-webauthn-tuto rial • PasswordsCon 2018: WebAuthn and security keys (video, slide) • Google I/O ‘18: What's new with sign up and sign in on the web • BSidesSF 2019 - Navigating Passwordless Authentication with FIDO2 & WebAuthn • Google and Microsoft Debut: Replacing Passwords with FIDO2 Authentication • https://www.reddit.com/r/passwords
Get a string to be checked: P@ssw0rd SHA1(P@ssw0rd)=21BD12DC183F740EE76F27B78EB39C8AD972A 757 GET Request first 5 characters (https://api.pwnedpasswords.com/range/21BD1) Search the hashes start from query param 1.(21BD1) 0018A45C4D1DEF81644B54AB7F969B88D65:1 (password "lauragpe") 2.(21BD1) 00D4F6E8FA6EECAD2A3AA415EEC418D38EC:2 (password "alexguo029") 3.(21BD1) 011053FD0102E94D6AE2F8B83D76FAF94F6:1 (password "BDnd9102") 4.(21BD1) 012A7CA357541F0AC487871FEEC1891C49C:2 (password "melobie") 5.(21BD1) 0136E006E24E7D152139815FB0FC6A50B15:2 (password "quvekyny") Return the list with its count Find the correct hash


 buzzvil
 henryofficial
 yusuke427
 ginjihayashi
 munakata
 imuta
 xkxaxkx
 oracle4engineer
 nejumi
 sansantech
 silmin_
 masasuzu
 munenick
 codingconduct
 pwiseman
 kimpetersen
 mongodb
 csswizardry
 frankvandijk
 wjessup
 baasie
 mfonobong
 khoart
 rmw
 twada