Upgrade to Pro — share decks privately, control downloads, hide ads and more …

Splunk: Interrogate your logs

Splunk: Interrogate your logs

Introduction to Splunk search, extraction, visualization and alerting for developers.

Avatar for Chase Seibert

Chase Seibert

August 30, 2013

Other Decks in Technology

Transcript

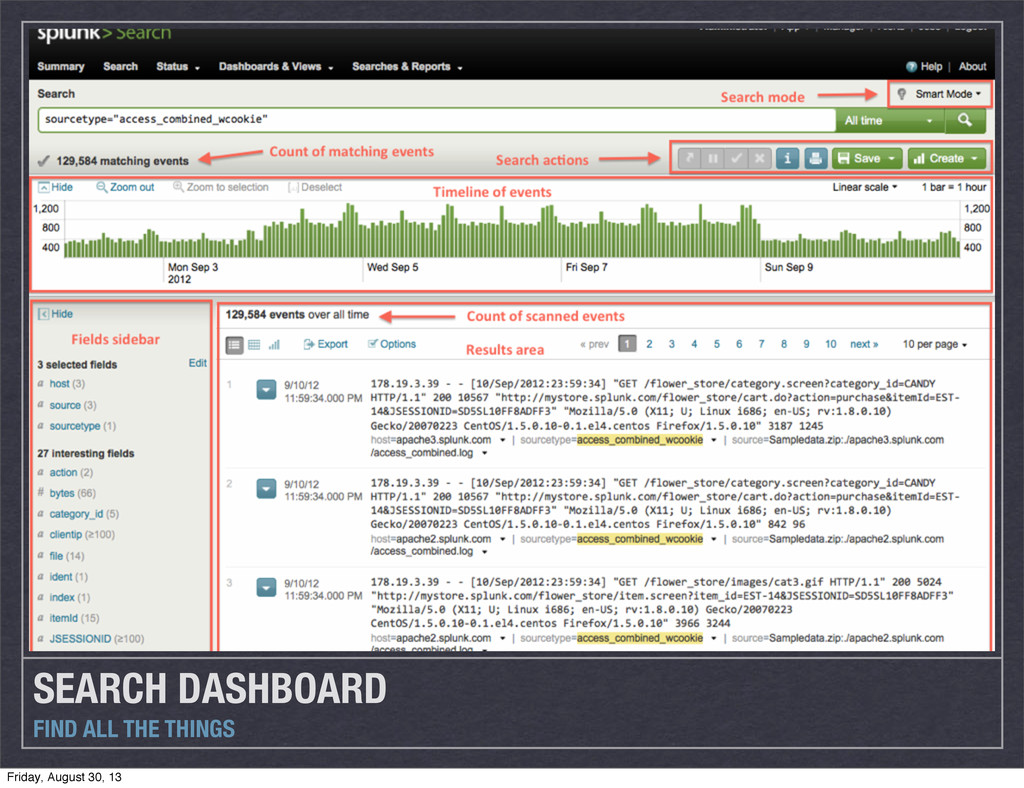
  1. What is Splunk ? Aggregates all your logs in one

    place Search Extract meaning Group, join, pivot and format results Visualization Email alerts Friday, August 30, 13
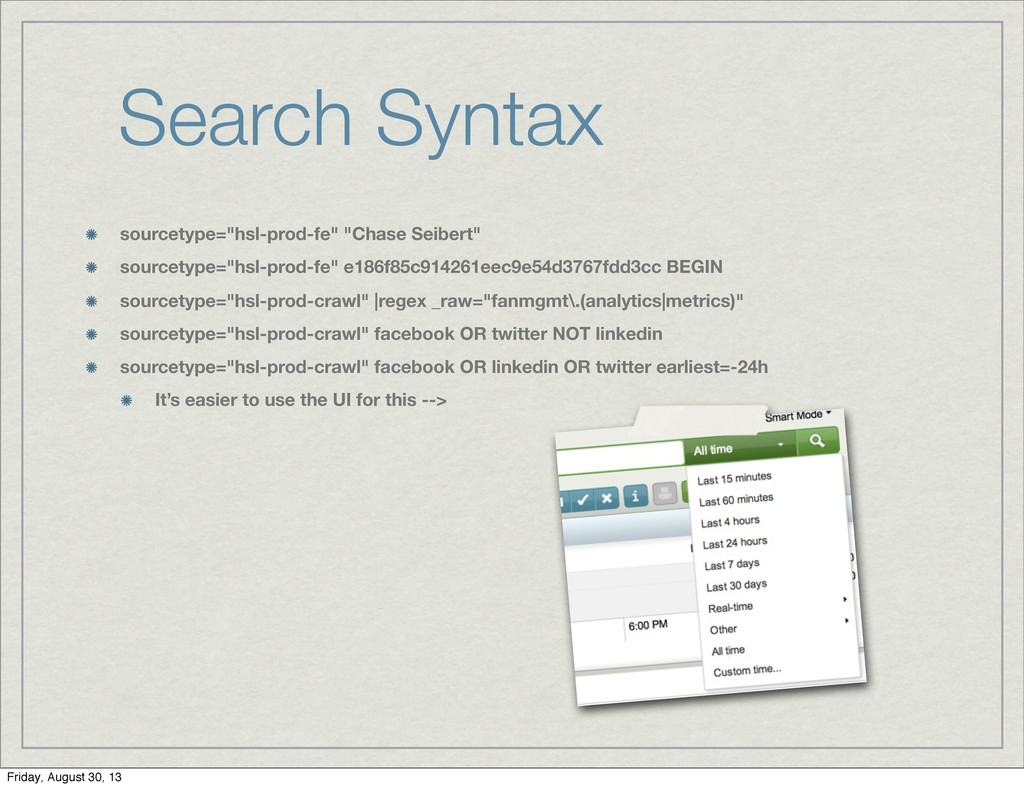
  2. Search Syntax sourcetype="hsl-prod-fe" "Chase Seibert" sourcetype="hsl-prod-fe" e186f85c914261eec9e54d3767fdd3cc BEGIN sourcetype="hsl-prod-crawl" |regex

    _raw="fanmgmt\.(analytics|metrics)" sourcetype="hsl-prod-crawl" facebook OR twitter NOT linkedin sourcetype="hsl-prod-crawl" facebook OR linkedin OR twitter earliest=-24h It’s easier to use the UI for this --> Friday, August 30, 13
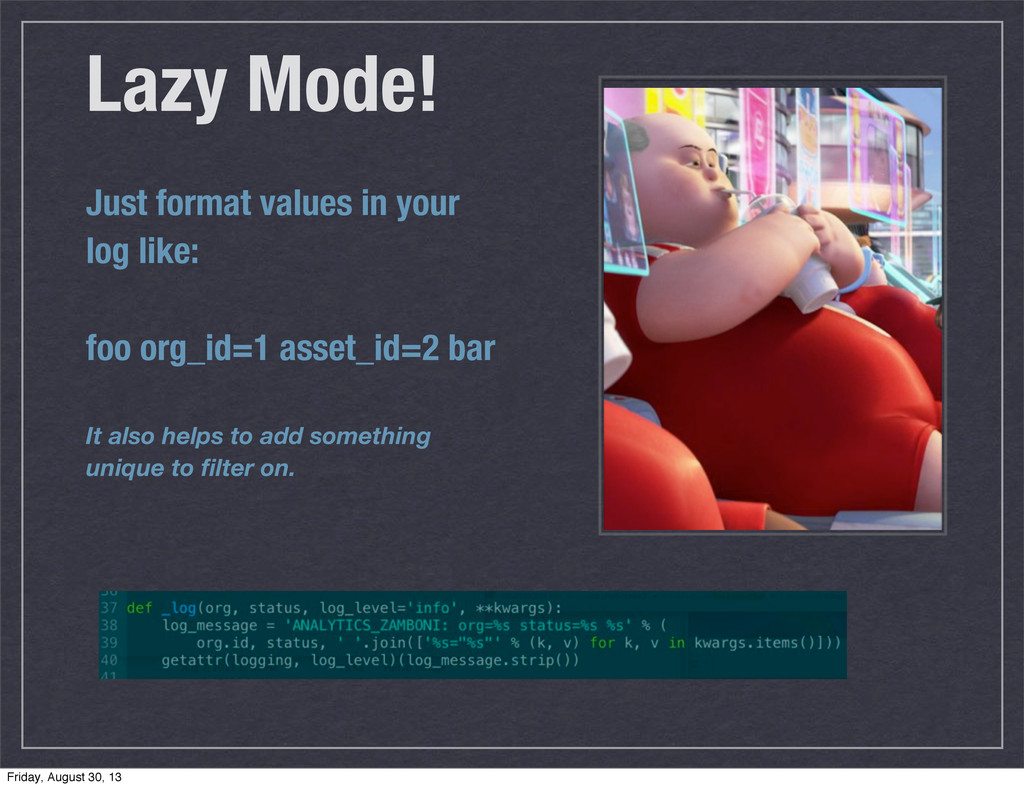
  3. Lazy Mode! Just format values in your log like: foo

    org_id=1 asset_id=2 bar It also helps to add something unique to filter on. Friday, August 30, 13
  4. More Pipe Commands | uniq | script python myscript myarg1

    myarg2 | bucket _time span=5m | eval name=coalesce(firstName, lastName) | rare, | anomalous | spath output=commit_author path=commits.author.name # extract xml/json values Friday, August 30, 13
  5. More Functions avg() | eval description=case(error == 404, "Not found",

    error == 200, "OK") floor(), ceiling() len() isbool(), isint(), etc upper(), lower() trim(), ltrim(), rtrim() md5() now() random() replace() split() substr() Friday, August 30, 13
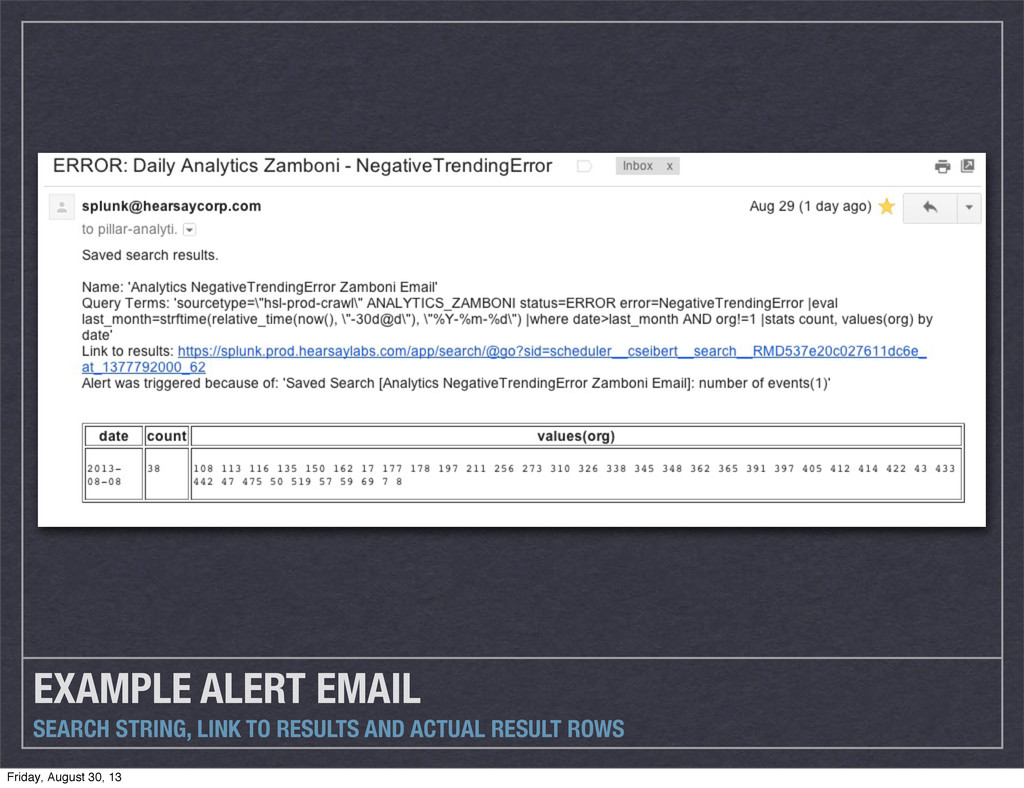
  6. Email Alerts Starts with a regular search Give the search

    a time window Schedule it (supports cron syntax) Can alert always, or when num rows > N Can remember not to re-alert on the same items Sends an email Friday, August 30, 13