bad ones. The bad ones probably came from Twitter. ▪ All examples are hypothetical, especially the bad ones. ▪ Nearly all of this is me showcasing other people's work. ▪ I strive for good attribution. If I missed someone, @ me.
▪ Secure all the things! ▪ Bend them to my will! ▪ SME all the projects! ▪ Make sure security signs off on EVERYTHING. ▪ Pen testing is the only testing. ▪ Don’t change anything after you build it.
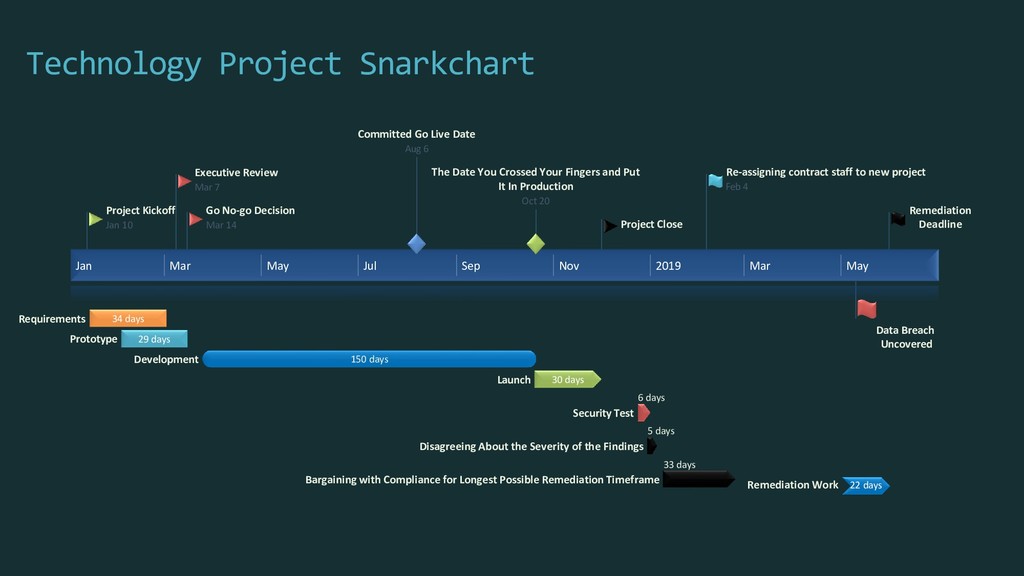
Jul Sep Nov 2019 Mar May Project Kickoff Jan 10 Executive Review Mar 7 Go No-go Decision Mar 14 Committed Go Live Date Aug 6 The Date You Crossed Your Fingers and Put It In Production Oct 20 Project Close Re-assigning contract staff to new project Feb 4 Remediation Deadline Data Breach Uncovered Requirements 34 days Prototype 29 days Development 150 days Launch 30 days Security Test 6 days Disagreeing About the Severity of the Findings 5 days Bargaining with Compliance for Longest Possible Remediation Timeframe 33 days
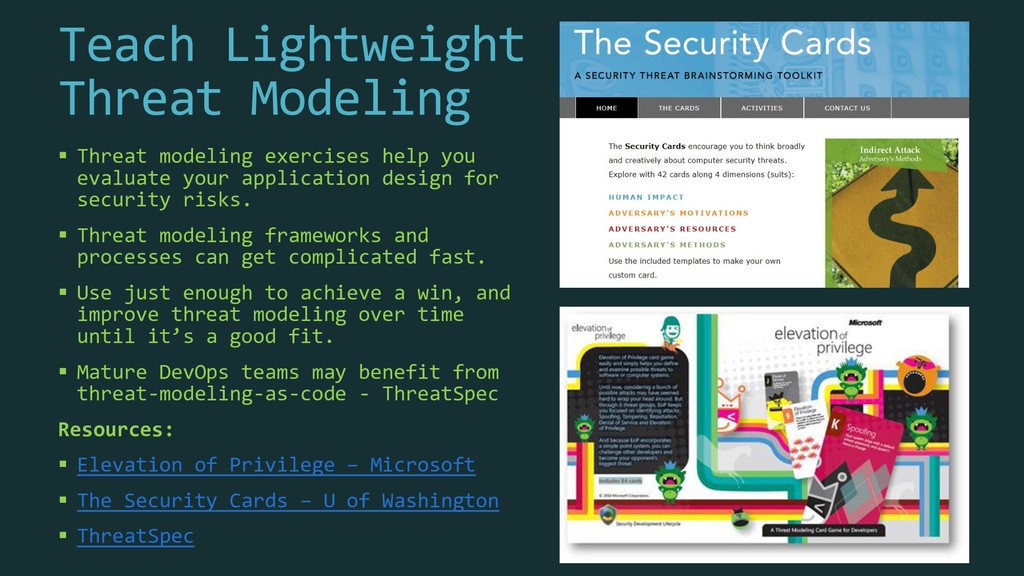
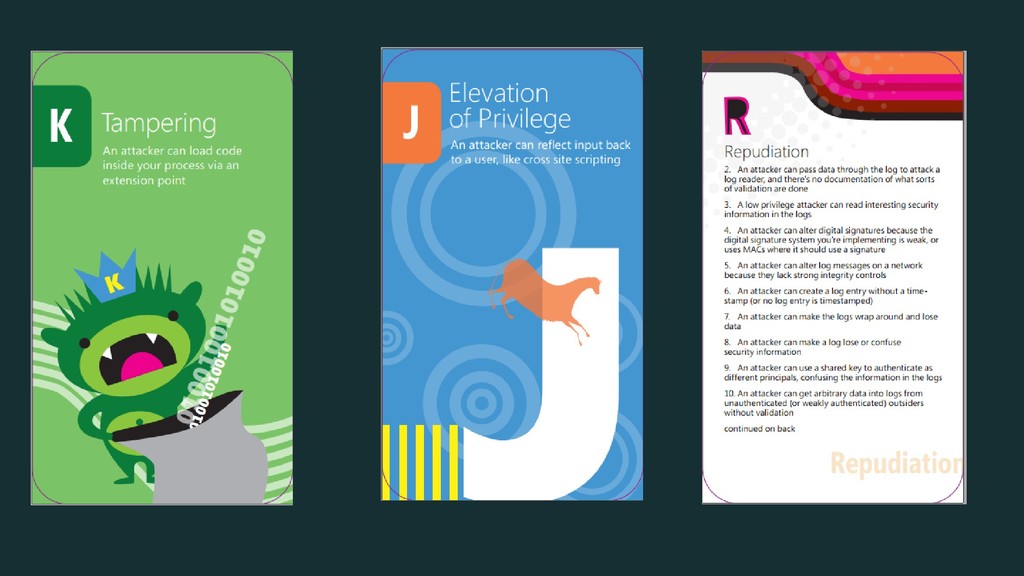
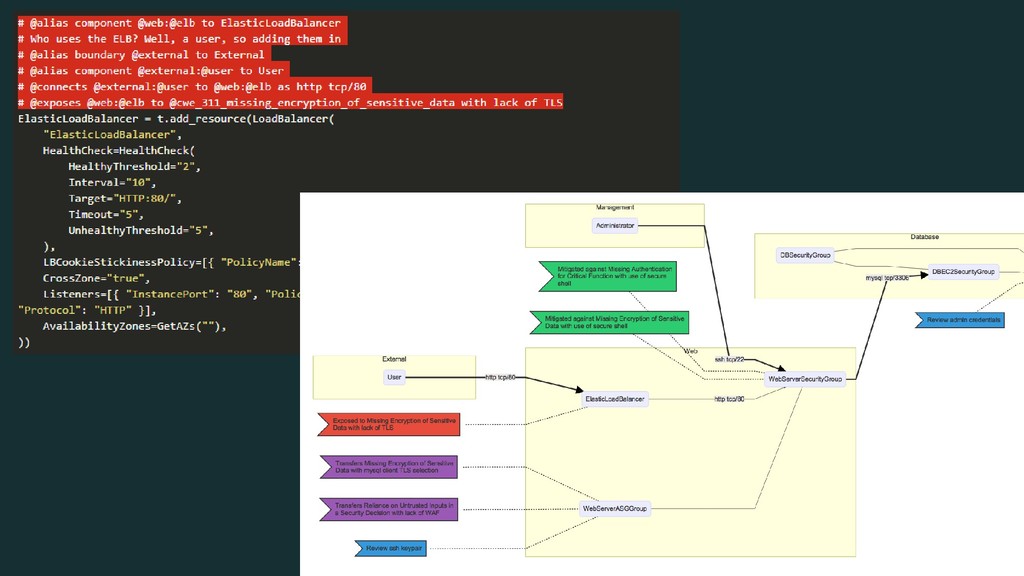
evaluate your application design for security risks. ▪ Threat modeling frameworks and processes can get complicated fast. ▪ Use just enough to achieve a win, and improve threat modeling over time until it’s a good fit. ▪ Mature DevOps teams may benefit from threat-modeling-as-code - ThreatSpec Resources: ▪ Elevation of Privilege – Microsoft ▪ The Security Cards – U of Washington ▪ ThreatSpec
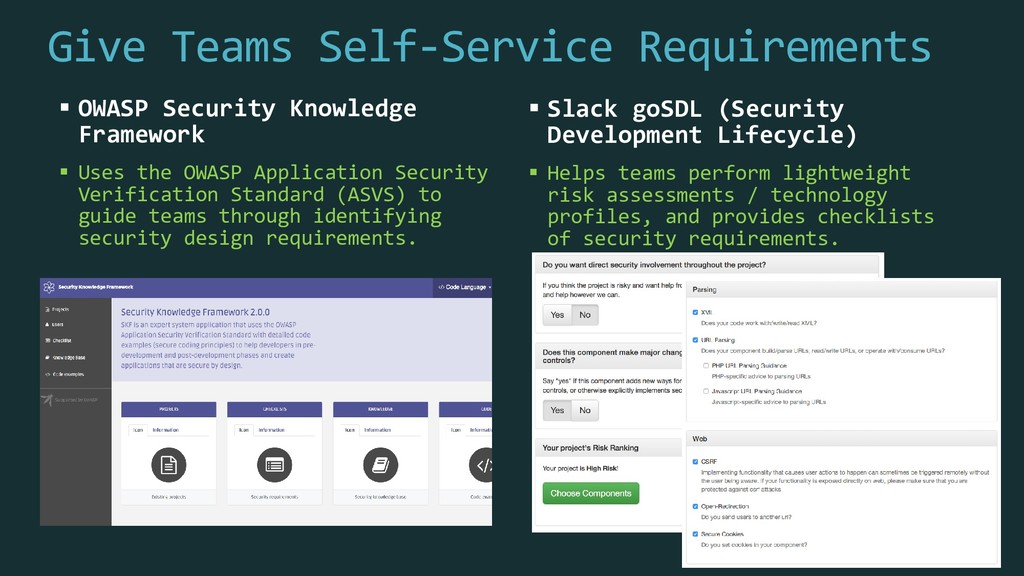
Uses the OWASP Application Security Verification Standard (ASVS) to guide teams through identifying security design requirements. ▪ Slack goSDL (Security Development Lifecycle) ▪ Helps teams perform lightweight risk assessments / technology profiles, and provides checklists of security requirements.
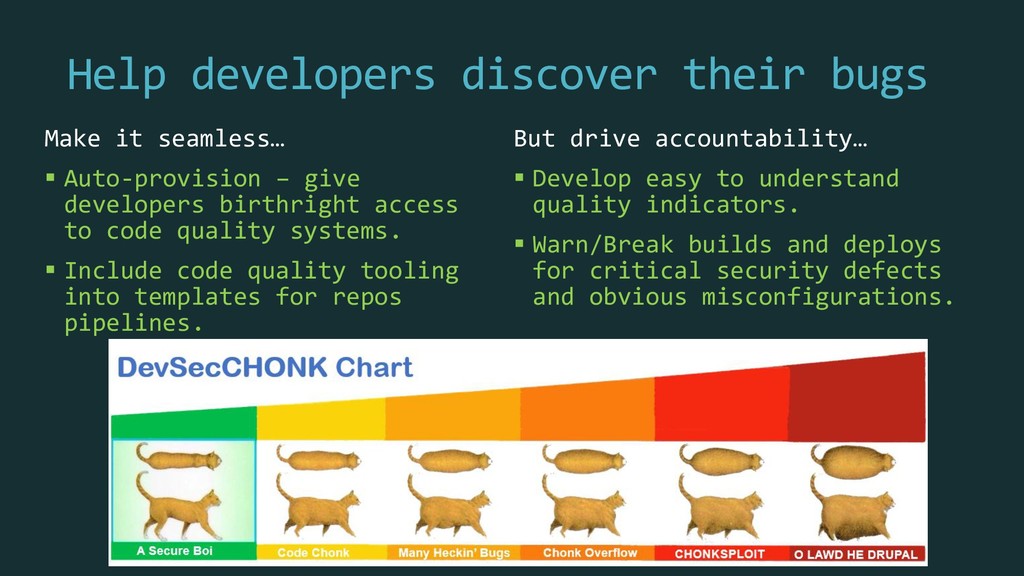
– give developers birthright access to code quality systems. ▪ Include code quality tooling into templates for repos pipelines. But drive accountability… ▪ Develop easy to understand quality indicators. ▪ Warn/Break builds and deploys for critical security defects and obvious misconfigurations.
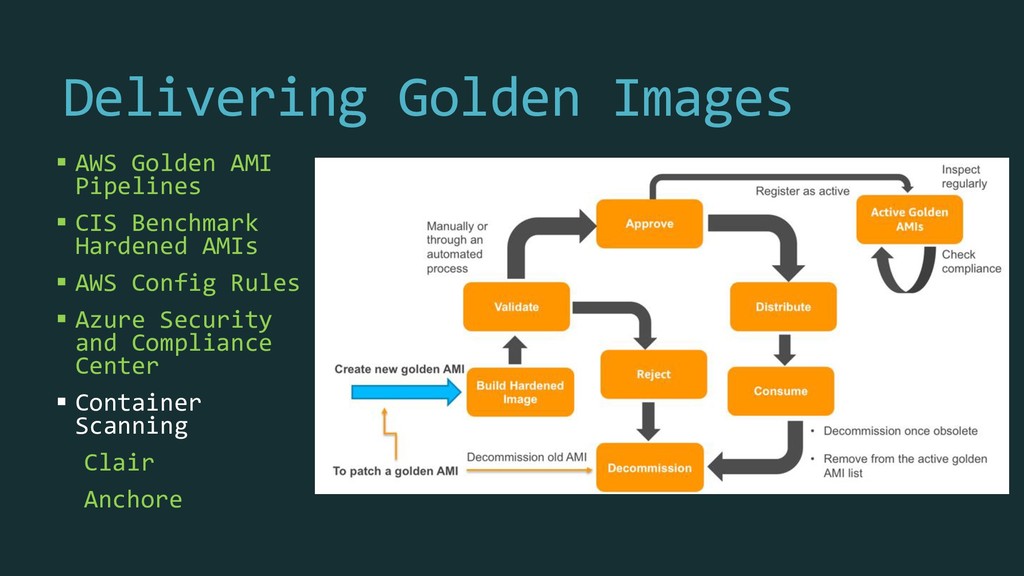
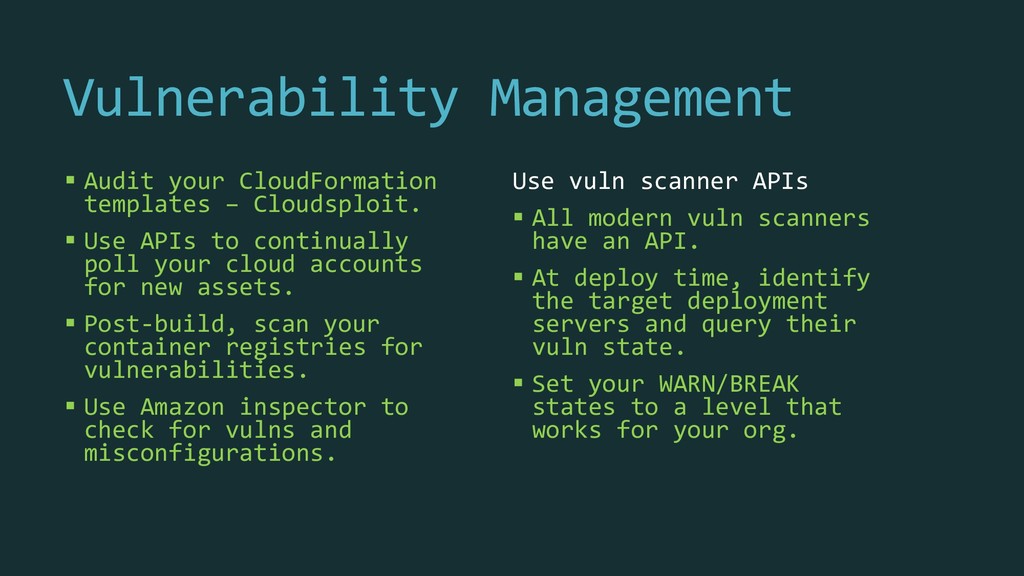
Use APIs to continually poll your cloud accounts for new assets. ▪ Post-build, scan your container registries for vulnerabilities. ▪ Use Amazon inspector to check for vulns and misconfigurations. Use vuln scanner APIs ▪ All modern vuln scanners have an API. ▪ At deploy time, identify the target deployment servers and query their vuln state. ▪ Set your WARN/BREAK states to a level that works for your org.
Room Forensics ▪ Ensure endpoint tools are baked into golden images. Monitor for unsafe behavior in GuardDuty: ▪ Bad firewall rules ▪ Opening unapproved ports ▪ Clearing logs ▪ Non-IAM user logins


 chrismerkel
 sansantech
 kentapapa
 minorun365
 satoshi7
 odashi
 takonda
 sue445
 y0hgi
 ezaki
 jyouryuusui
 yu23ki14
 skoyamalab
 stephaniewalter
 3n
 leimatthew05
 codingconduct
 rasmusluckow
 inesmontani
 techseoconnect
 rkendrick25
 thirion
 tmiket