Share
Embed
Terraform in 5 minutes
A lightning talk at the AWS meetup in Singapore
claudiomettler
September 07, 2016
Transcript
18 slides
-
terraform • software package by HashiCorp (the vagrant guys) •
describe your infrastructure in code • it's NOT a cloud abstraction layer • it's sort of similar to cloudformation (i guess) -
structure • create as many .tf files as needed in
your project directory • run terraform apply to transform current state into desired state -
variables • place them in .tf files • variable "foo"
{ default = "bar" } • override using .tfvars files or command line • terraform.tfvars gets included automatically • usage: ${var.foo} -
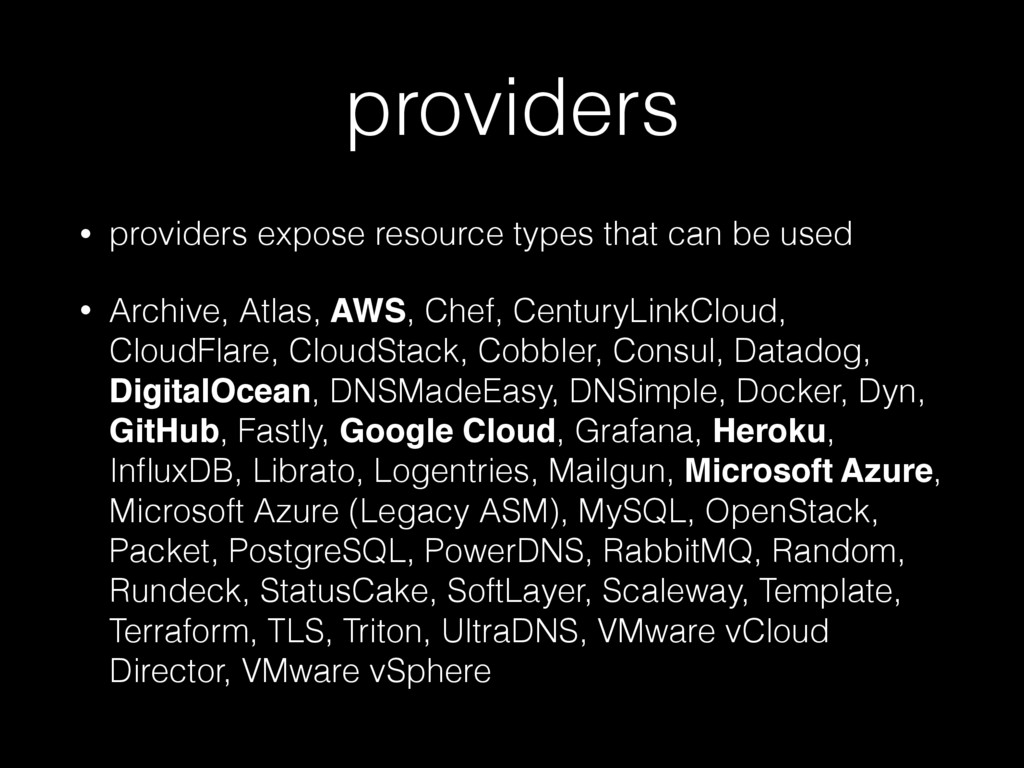
providers • providers expose resource types that can be used
• Archive, Atlas, AWS, Chef, CenturyLinkCloud, CloudFlare, CloudStack, Cobbler, Consul, Datadog, DigitalOcean, DNSMadeEasy, DNSimple, Docker, Dyn, GitHub, Fastly, Google Cloud, Grafana, Heroku, InfluxDB, Librato, Logentries, Mailgun, Microsoft Azure, Microsoft Azure (Legacy ASM), MySQL, OpenStack, Packet, PostgreSQL, PowerDNS, RabbitMQ, Random, Rundeck, StatusCake, SoftLayer, Scaleway, Template, Terraform, TLS, Triton, UltraDNS, VMware vCloud Director, VMware vSphere -
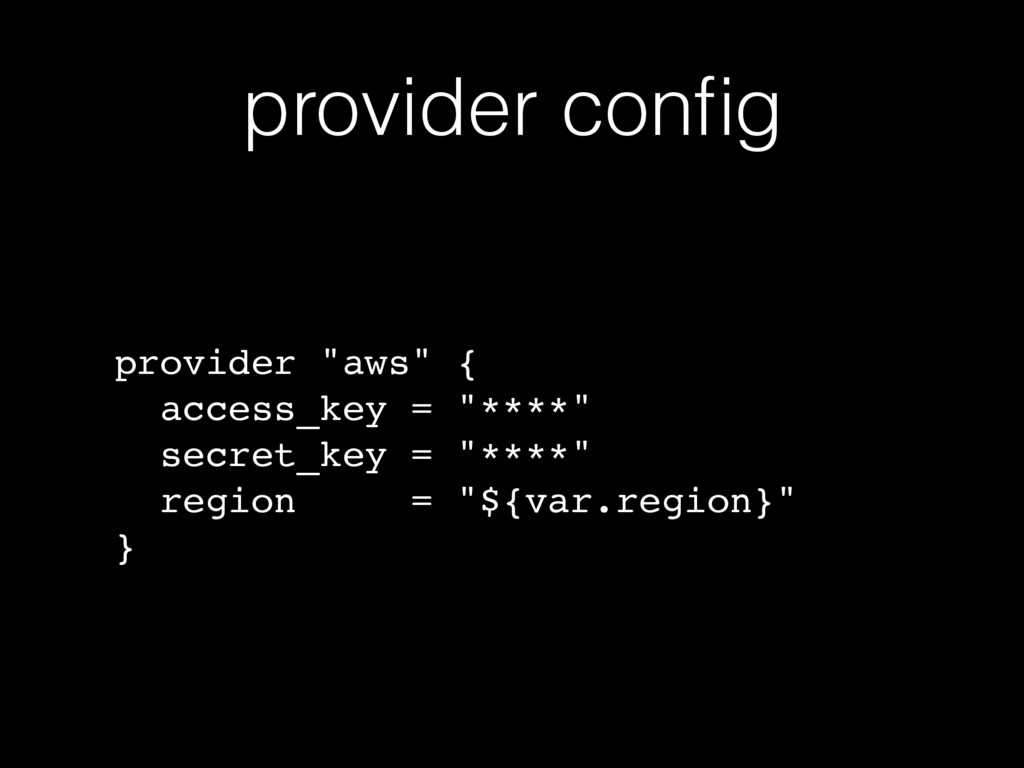
provider config provider "aws" { access_key = "****" secret_key =
"****" region = "${var.region}" } -
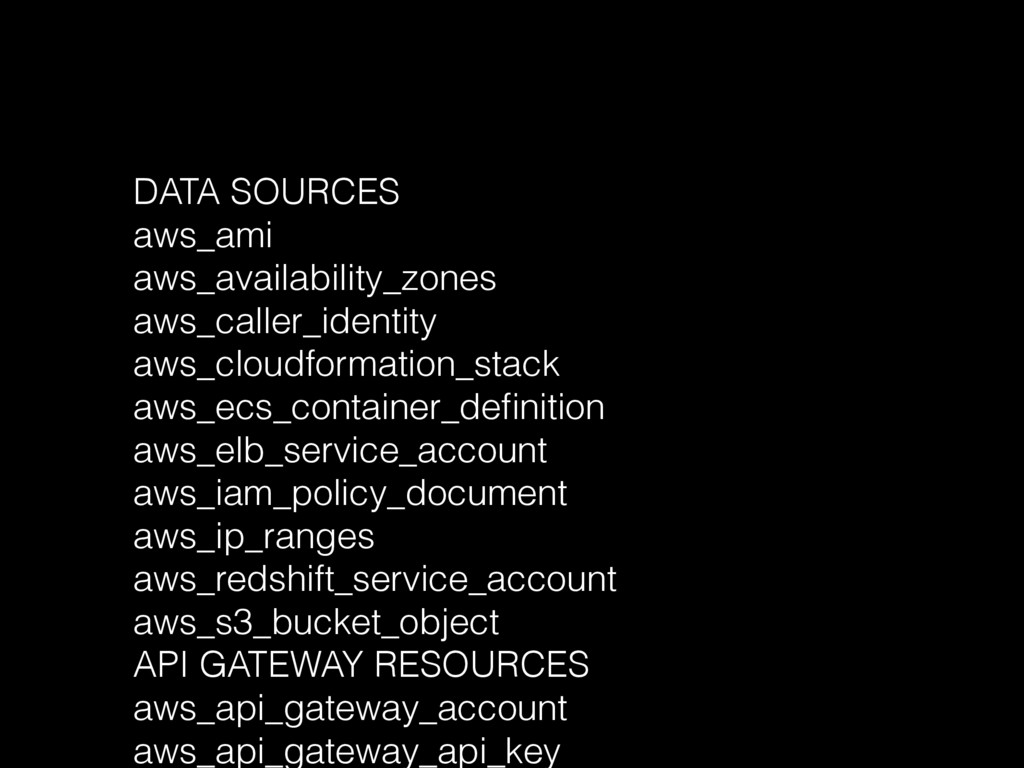
DATA SOURCES aws_ami aws_availability_zones aws_caller_identity aws_cloudformation_stack aws_ecs_container_definition aws_elb_service_account aws_iam_policy_document aws_ip_ranges
aws_redshift_service_account aws_s3_bucket_object API GATEWAY RESOURCES aws_api_gateway_account aws_api_gateway_api_key -
resources • have a type and a name • have
arguments (values going in) • have attributes (values going out) • dependency resolution based on attribute usage -
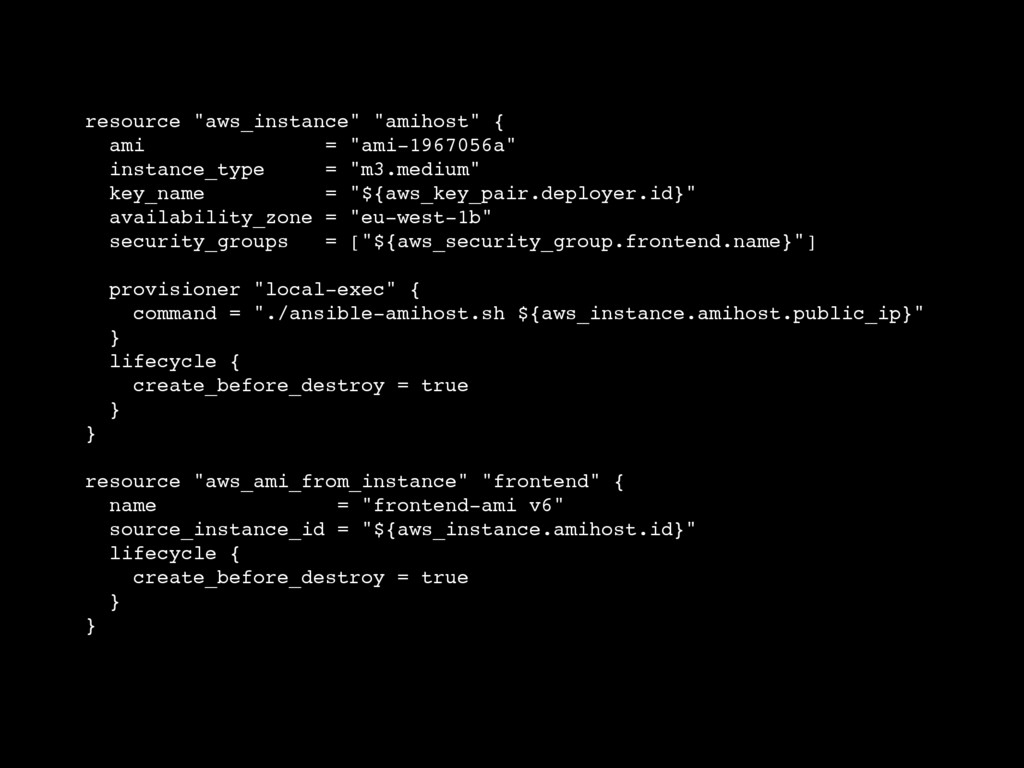
resource "aws_instance" "amihost" { ami = "ami-1967056a" instance_type = "m3.medium"
key_name = "${aws_key_pair.deployer.id}" availability_zone = "eu-west-1b" security_groups = ["${aws_security_group.frontend.name}"] provisioner "local-exec" { command = "./ansible-amihost.sh ${aws_instance.amihost.public_ip}" } lifecycle { create_before_destroy = true } } resource "aws_ami_from_instance" "frontend" { name = "frontend-ami v6" source_instance_id = "${aws_instance.amihost.id}" lifecycle { create_before_destroy = true } } -
resource "aws_launch_configuration" "frontend" { image_id = "${aws_ami_from_instance.frontend.id}" security_groups = ["${aws_security_group.vpc.id}"]
key_name = "${aws_key_pair.deployer.id}" instance_type = "m3.medium" iam_instance_profile = "${aws_iam_instance_profile.deploy_profile.id}" associate_public_ip_address = true lifecycle { create_before_destroy = true } } resource "aws_autoscaling_group" "frontend" { max_size = 5 min_size = 1 health_check_grace_period = 300 health_check_type = "ELB" vpc_zone_identifier = ["${aws_subnet.main.id}"] force_delete = true launch_configuration = "${aws_launch_configuration.frontend.name}" load_balancers = ["${aws_elb.frontend.name}"] tag { key = "Name" value = "frontend" propagate_at_launch = true } } -
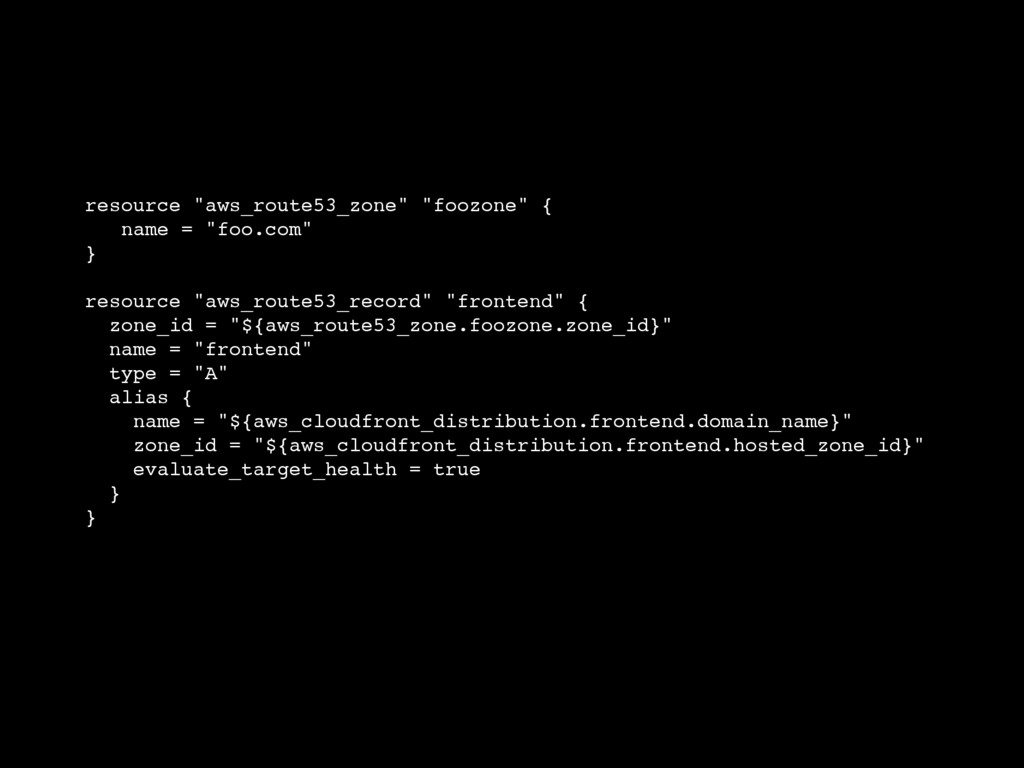
resource "aws_route53_zone" "foozone" { name = "foo.com" } resource "aws_route53_record"
"frontend" { zone_id = "${aws_route53_zone.foozone.zone_id}" name = "frontend" type = "A" alias { name = "${aws_cloudfront_distribution.frontend.domain_name}" zone_id = "${aws_cloudfront_distribution.frontend.hosted_zone_id}" evaluate_target_health = true } } -
state • terraform stores your current state in a file
• it's not recommended to commit it (ignore *.tfstate, .terraform/, *.tfstate.backup) • if you have multiple people working on the same infrastructure, use remote state (e.g. S3) -
modules • self contained configuration packages • can be included
directly from github • https://github.com/terraform-community- modules/