Share
Embed
Transcript
23 slides
-
vAPI : Vulnerable Adversely Programmed Interface GET /user/me HTTP/1.1 •
Security Research Engineer at Holm Security • Lead at OWASP Nagpur • Spoken at Blackhat , HITB, OWASP Appsecdays etc. • Like to play CTFs in my Free Time -
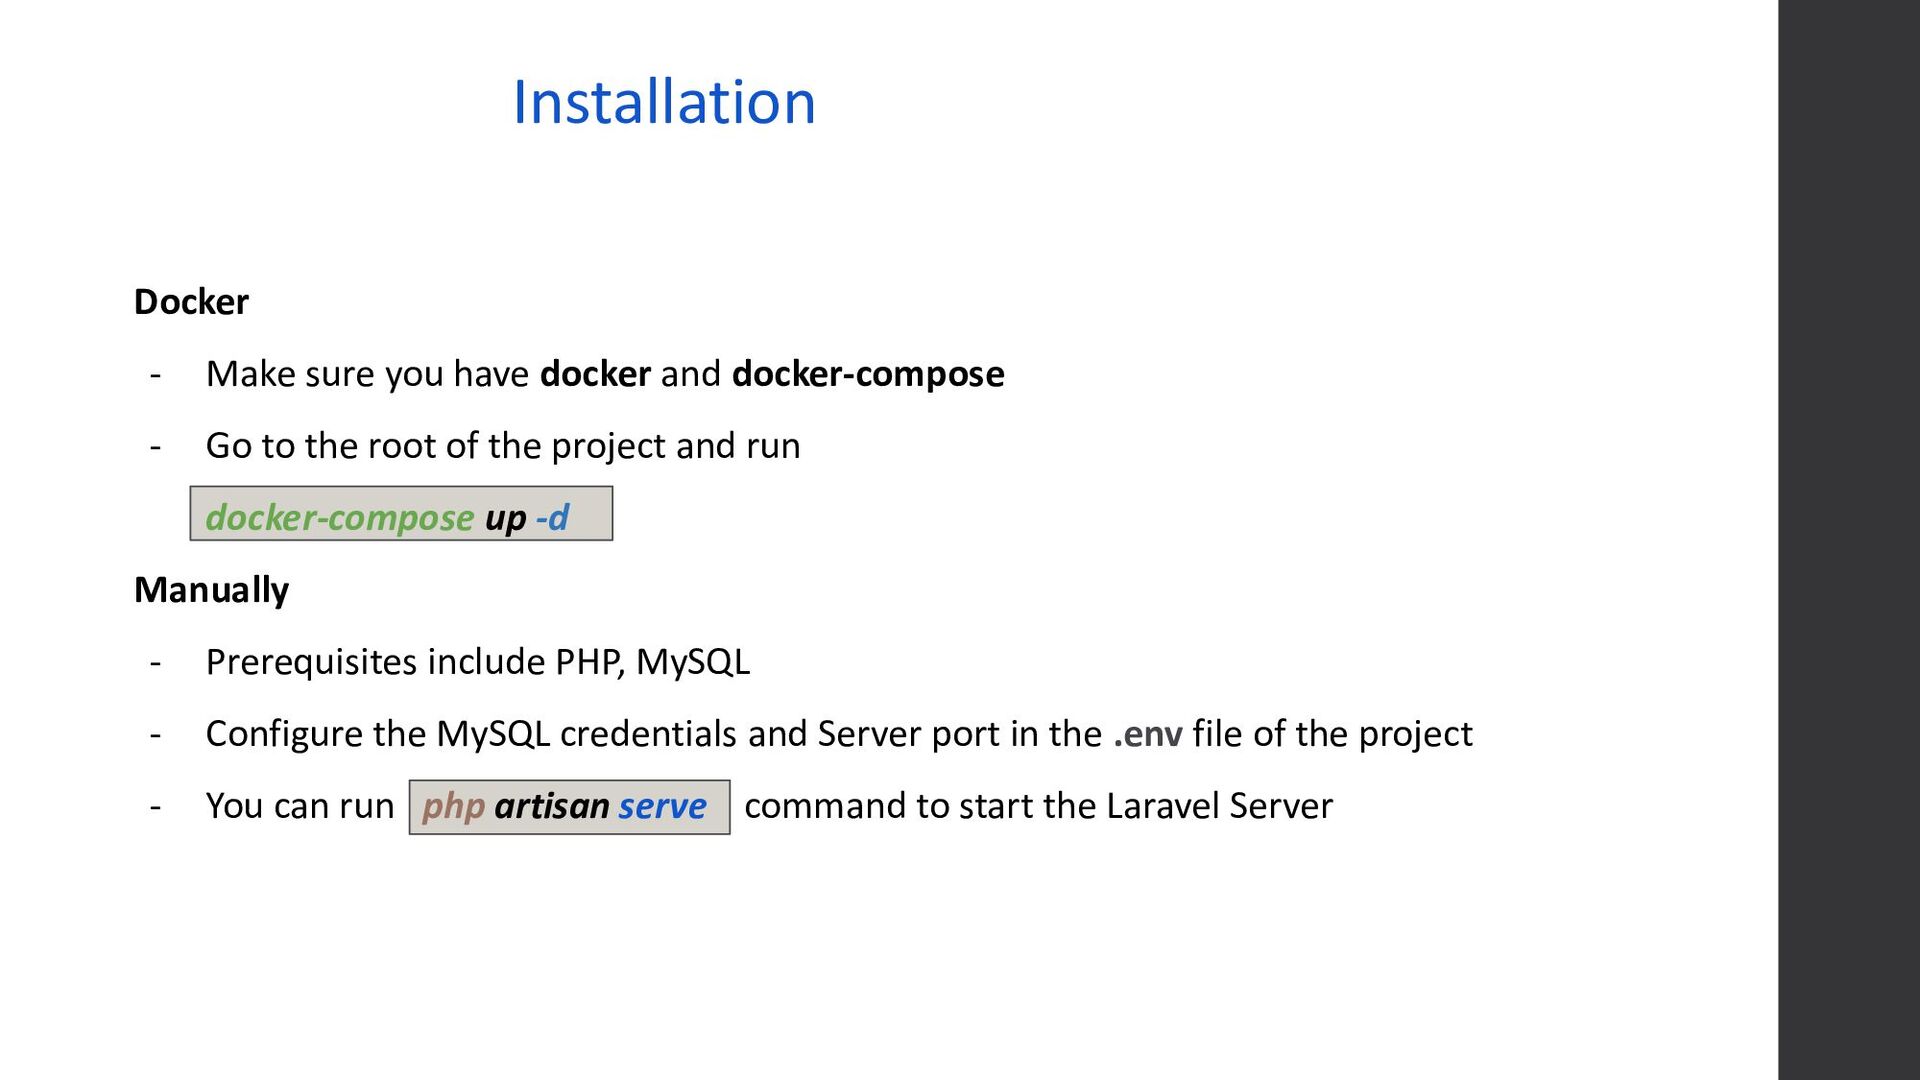
vAPI : Vulnerable Adversely Programmed Interface Installation Docker - Make
sure you have docker and docker-compose - Go to the root of the project and run docker-compose up -d Manually - Prerequisites include PHP, MySQL - Configure the MySQL credentials and Server port in the .env file of the project - You can run php artisan serve command to start the Laravel Server -
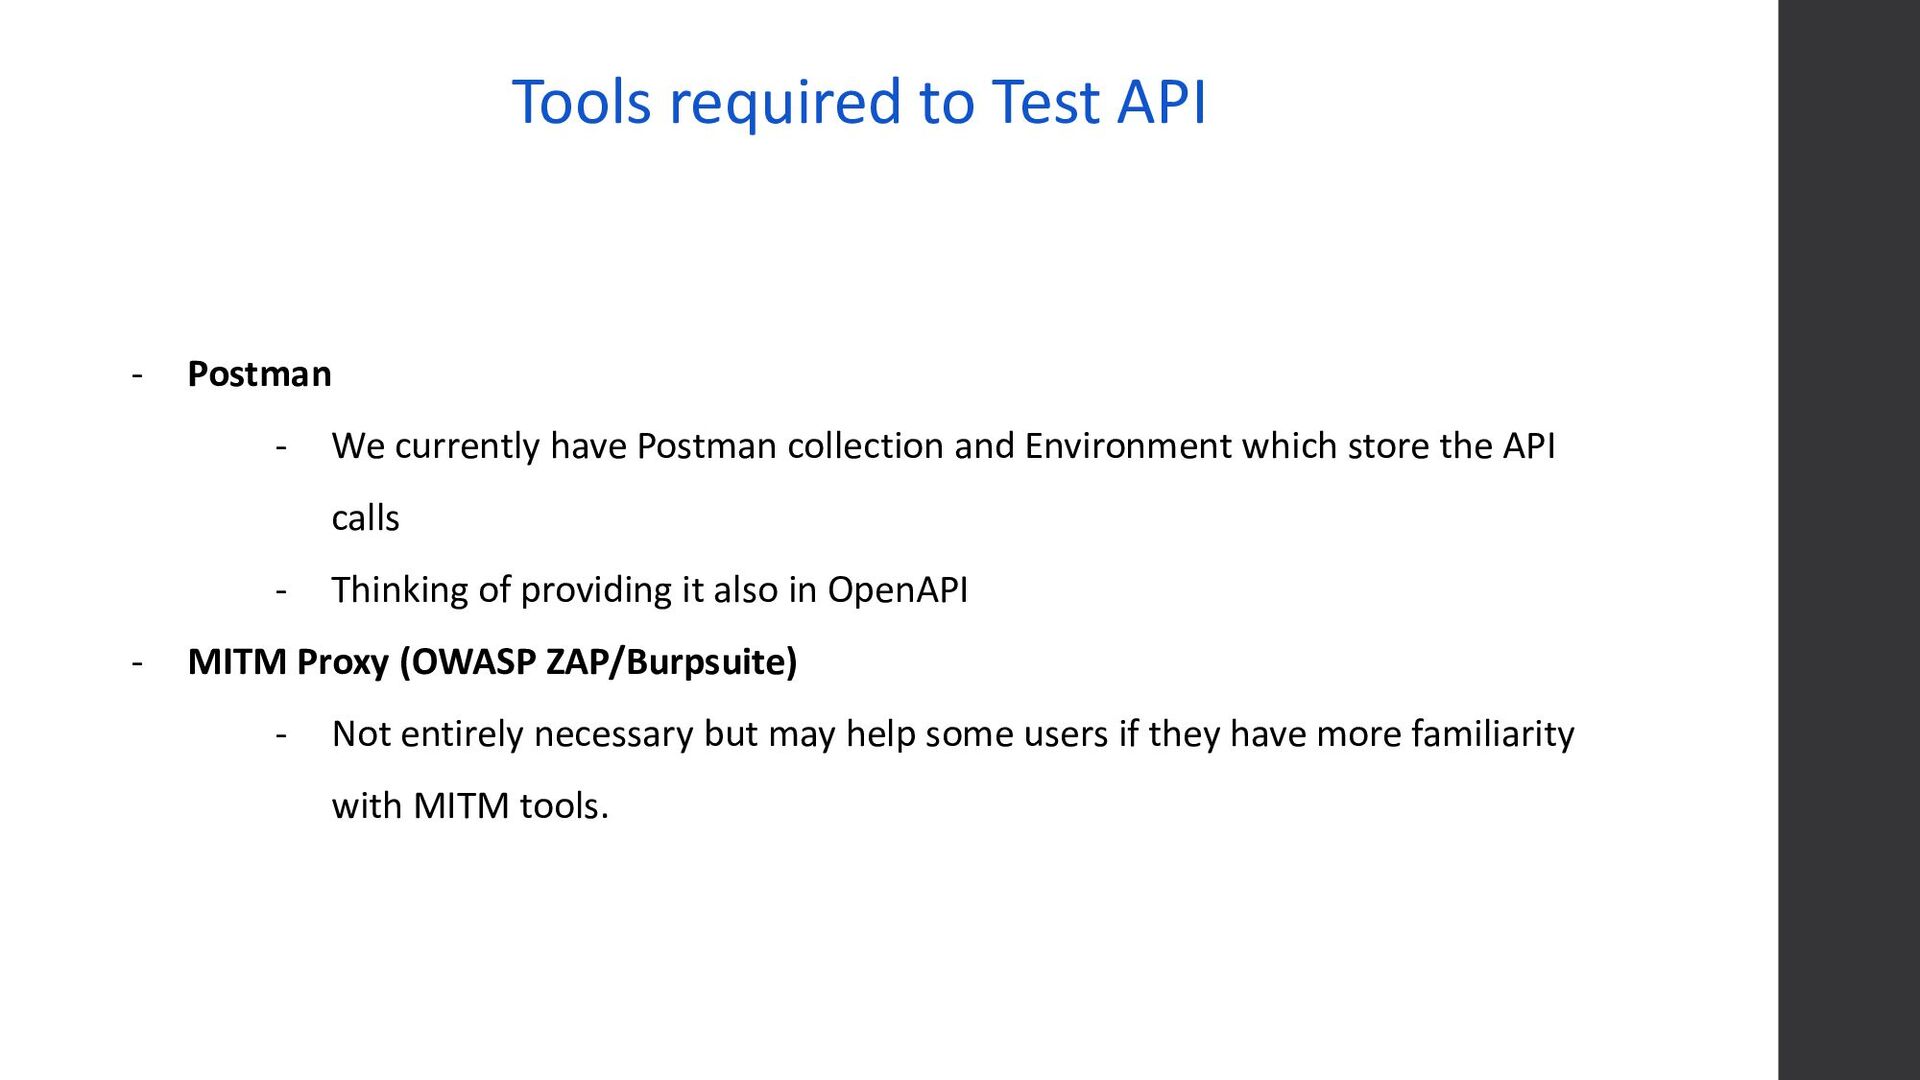
vAPI : Vulnerable Adversely Programmed Interface Tools required to Test
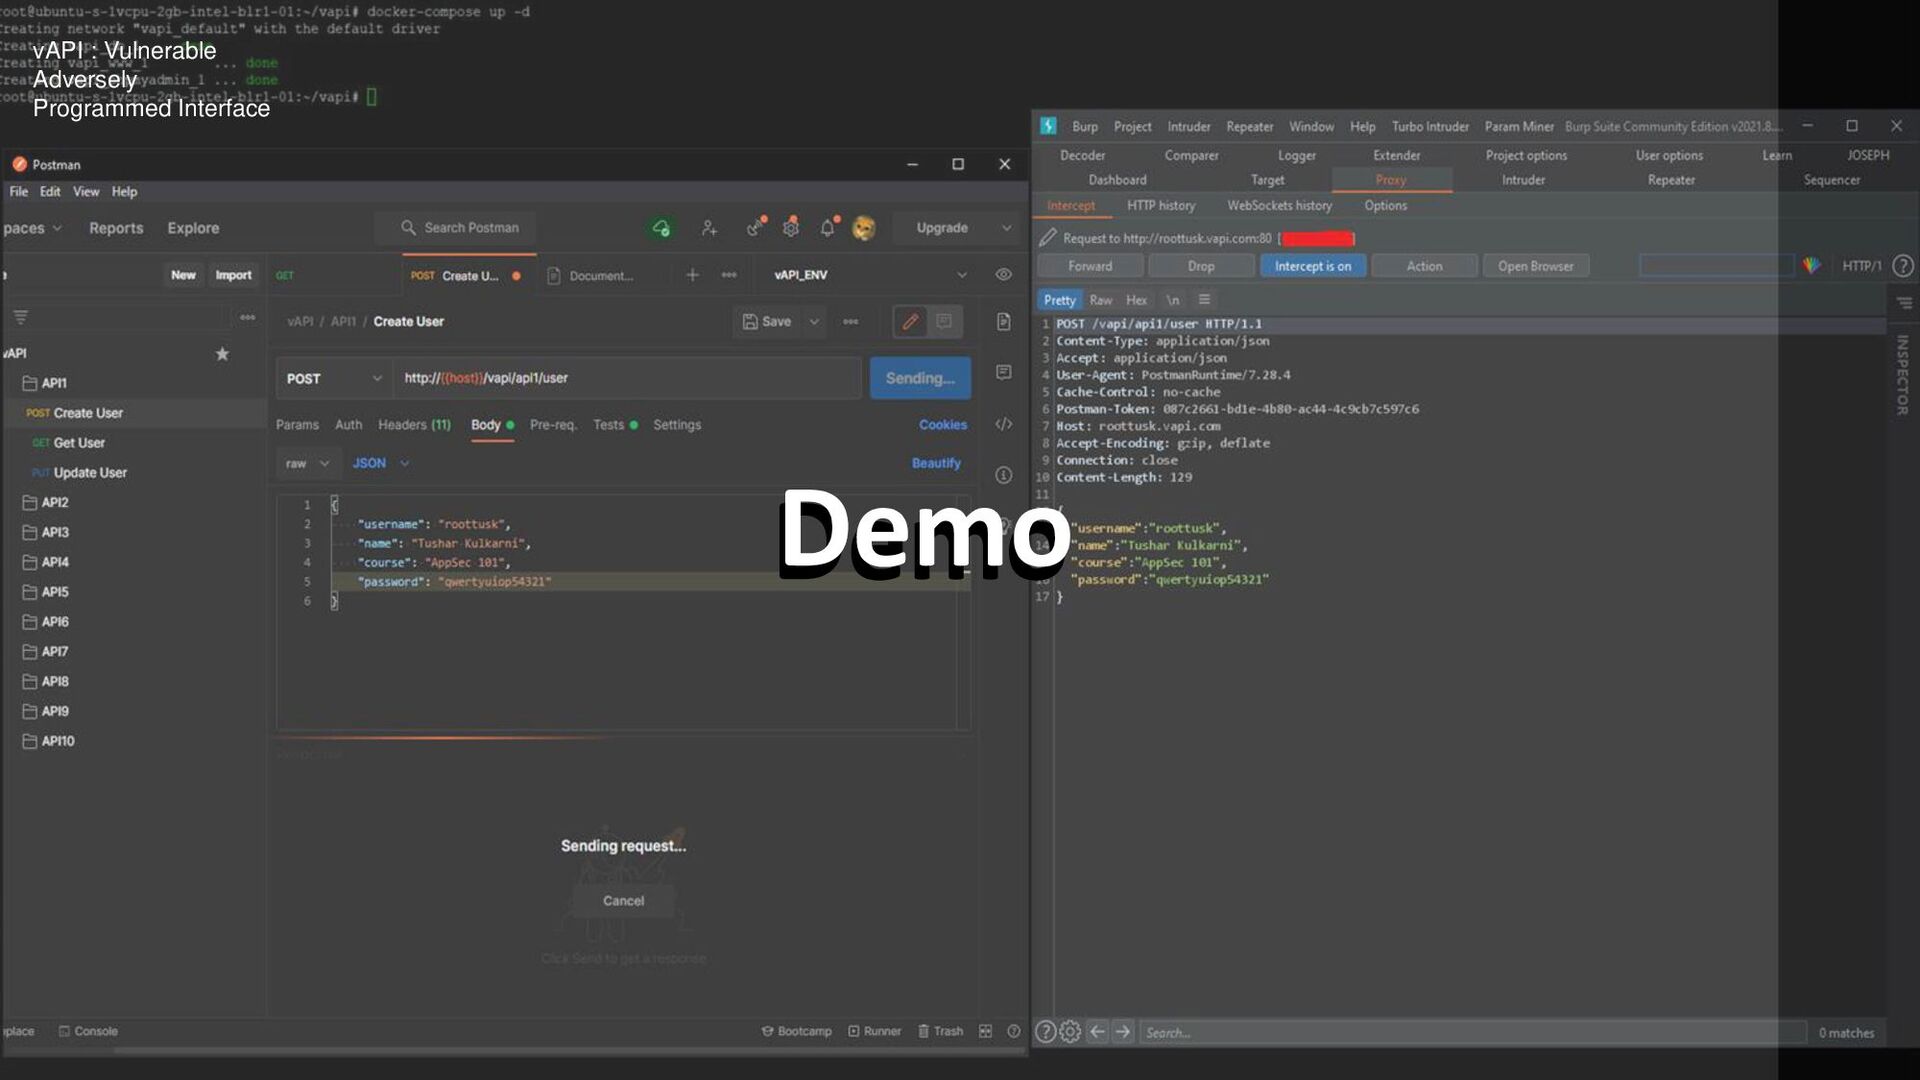
API - Postman - We currently have Postman collection and Environment which store the API calls - Thinking of providing it also in OpenAPI - MITM Proxy (OWASP ZAP/Burpsuite) - Not entirely necessary but may help some users if they have more familiarity with MITM tools. -
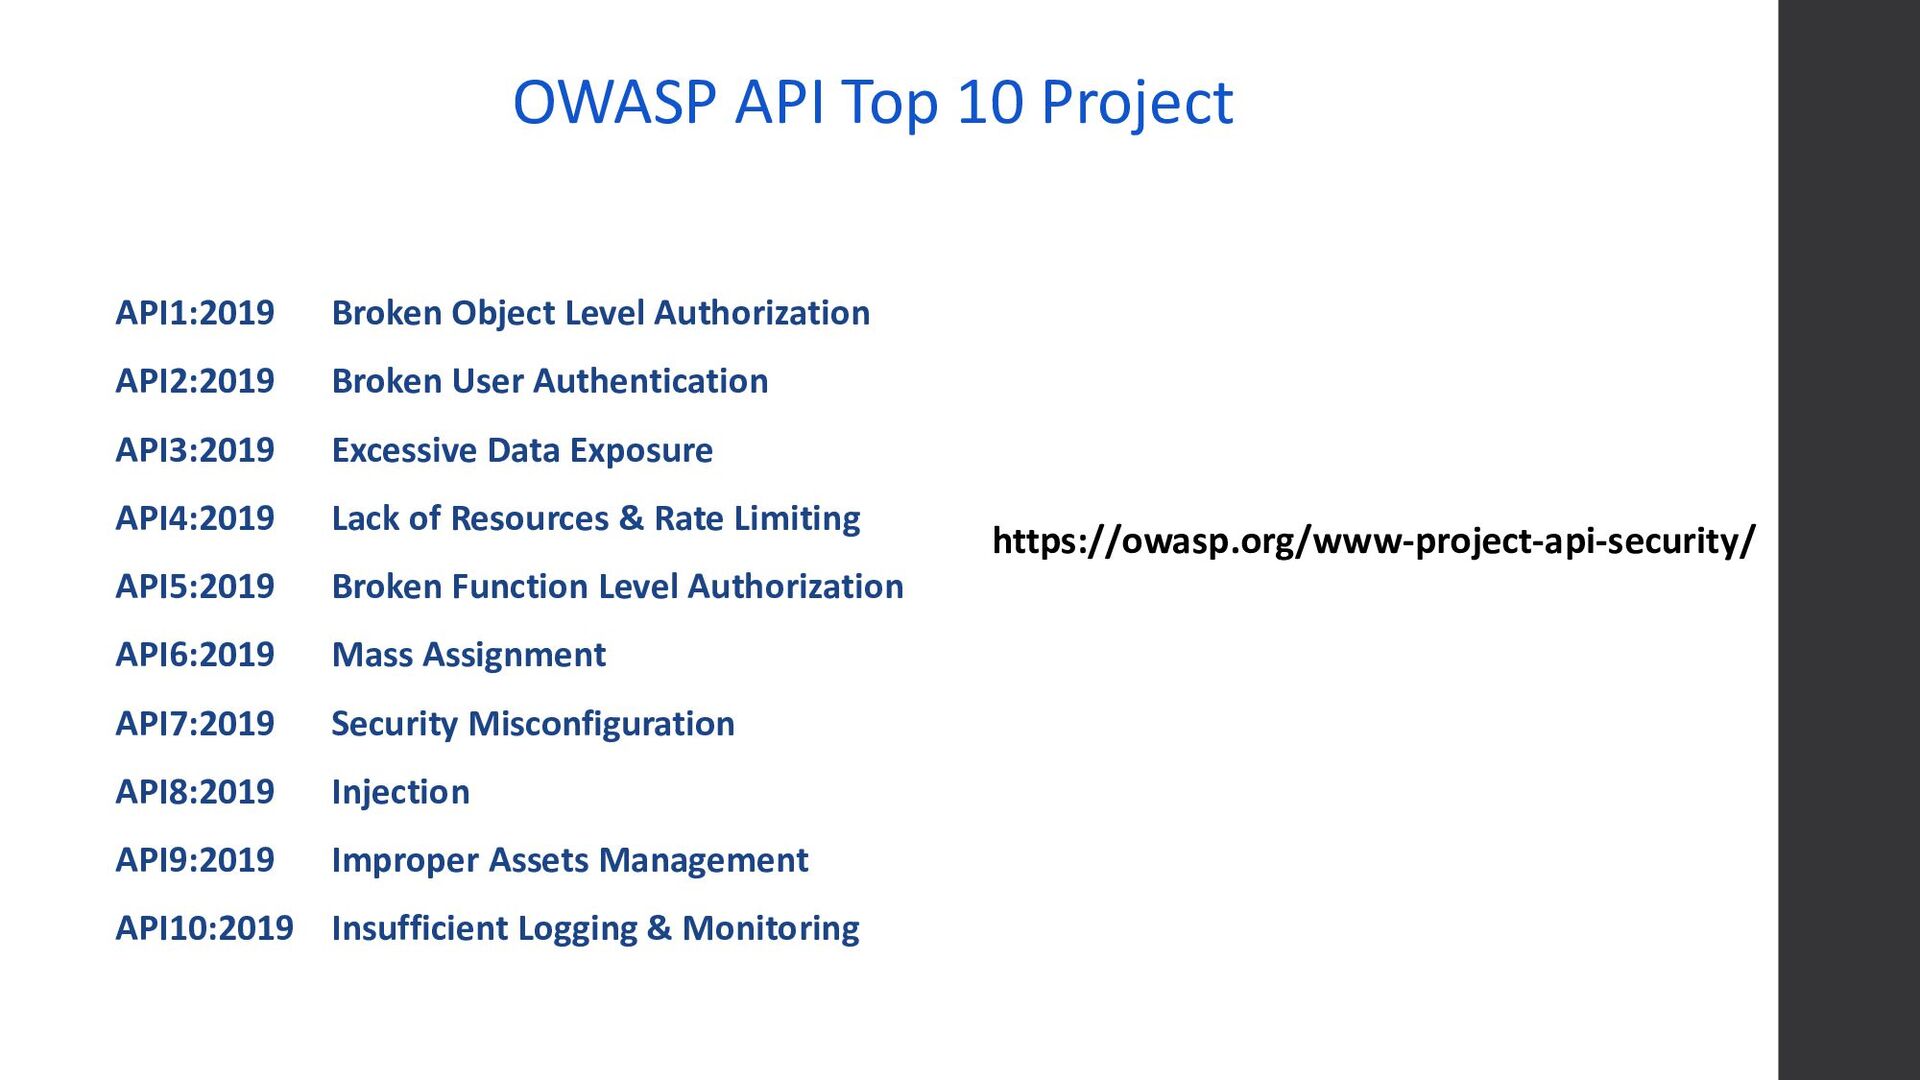
vAPI : Vulnerable Adversely Programmed Interface OWASP API Top 10
Project API1:2019 Broken Object Level Authorization API2:2019 Broken User Authentication API3:2019 Excessive Data Exposure API4:2019 Lack of Resources & Rate Limiting API5:2019 Broken Function Level Authorization API6:2019 Mass Assignment API7:2019 Security Misconfiguration API8:2019 Injection API9:2019 Improper Assets Management API10:2019 Insufficient Logging & Monitoring https://owasp.org/www-project-api-security/ -
vAPI : Vulnerable Adversely Programmed Interface API2:2019 Broken User Authentication
- Credential Stuffing - Weak Password Policies - Sensitive data in URL - Weak Encryption - Misconfigured Tokens/ Not Validating tokens properly -
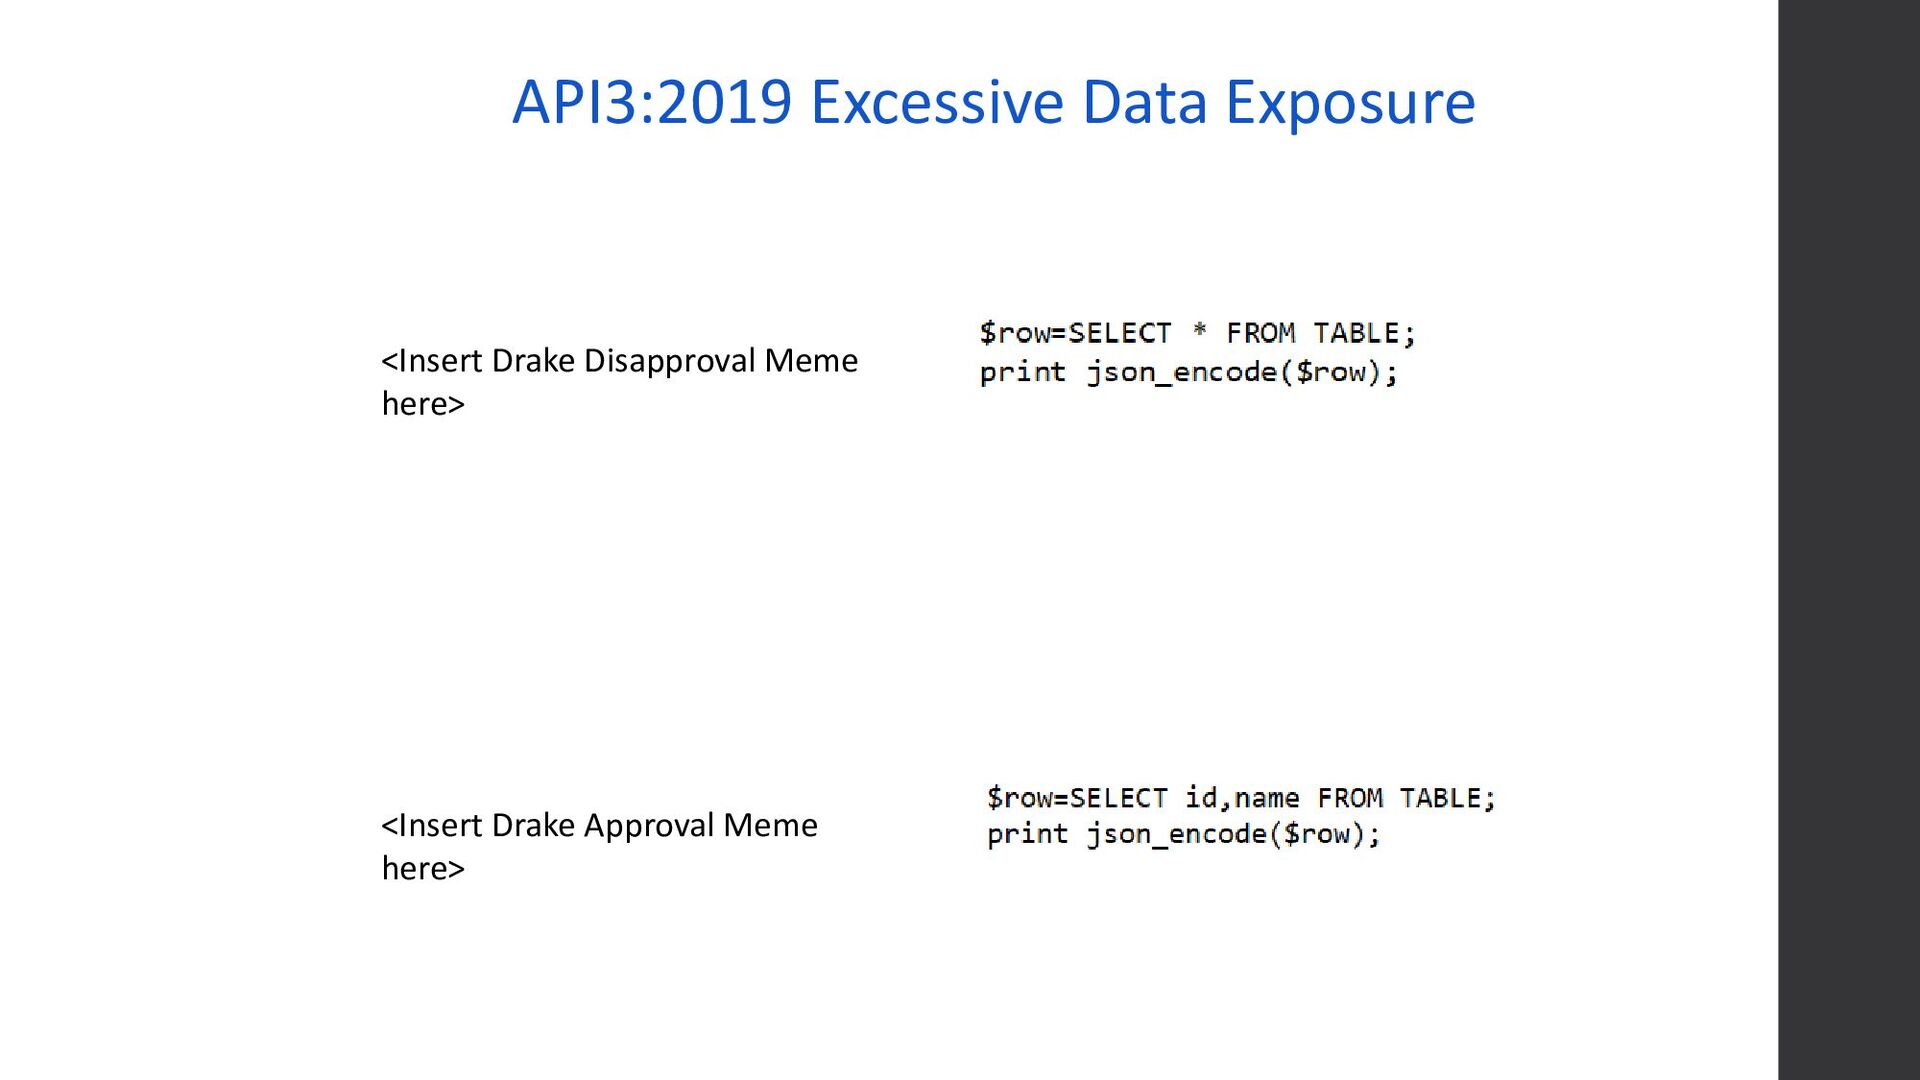
vAPI : Vulnerable Adversely Programmed Interface API3:2019 Excessive Data Exposure
<Insert Drake Disapproval Meme here> <Insert Drake Approval Meme here> -
vAPI : Vulnerable Adversely Programmed Interface API6:2019 Mass Assignment -
Automatically Adding User supplied parameters into Object Properties • Permission-related properties: user.is_admin, user.is_vip should only be set by admins. • Process-dependent properties: user.cash should only be set internally after payment verification. • Internal properties: article.created_time should only be set internally by the application. -
vAPI : Vulnerable Adversely Programmed Interface API8:2019 Injection - OS
Command, SQL, XML ,LDAP and a lot of others - Lack of Sanitization -
vAPI : Vulnerable Adversely Programmed Interface API9:2019 Improper Assets Management
- API versions v1,v2,v1.1 - Environment (Staging,Dev, Prod) - Handling PII/PHI -
vAPI : Vulnerable Adversely Programmed Interface API10:2019 Insufficient Logging and
Monitoring • It does not produce any logs, the logging level is not set correctly, or log messages do not include enough detail. • Log integrity is not guaranteed (e.g., Log Injection). • Logs are not continuously monitored. • API infrastructure is not continuously monitored. -
vAPI : Vulnerable Adversely Programmed Interface Vulnerabilities in Web Apps
VS Vulnerabilities in APIs - XSS? - A lot of Broken Authorization and Access Control - DAST on a Web App gives different results than on a Web API -
vAPI : Vulnerable Adversely Programmed Interface Project Roadmap - Acknowledgements
for Completion of Challenges / Dashboard - Crowdsourced Playground for API Security Challenges Image Source: dinosoftlabs -
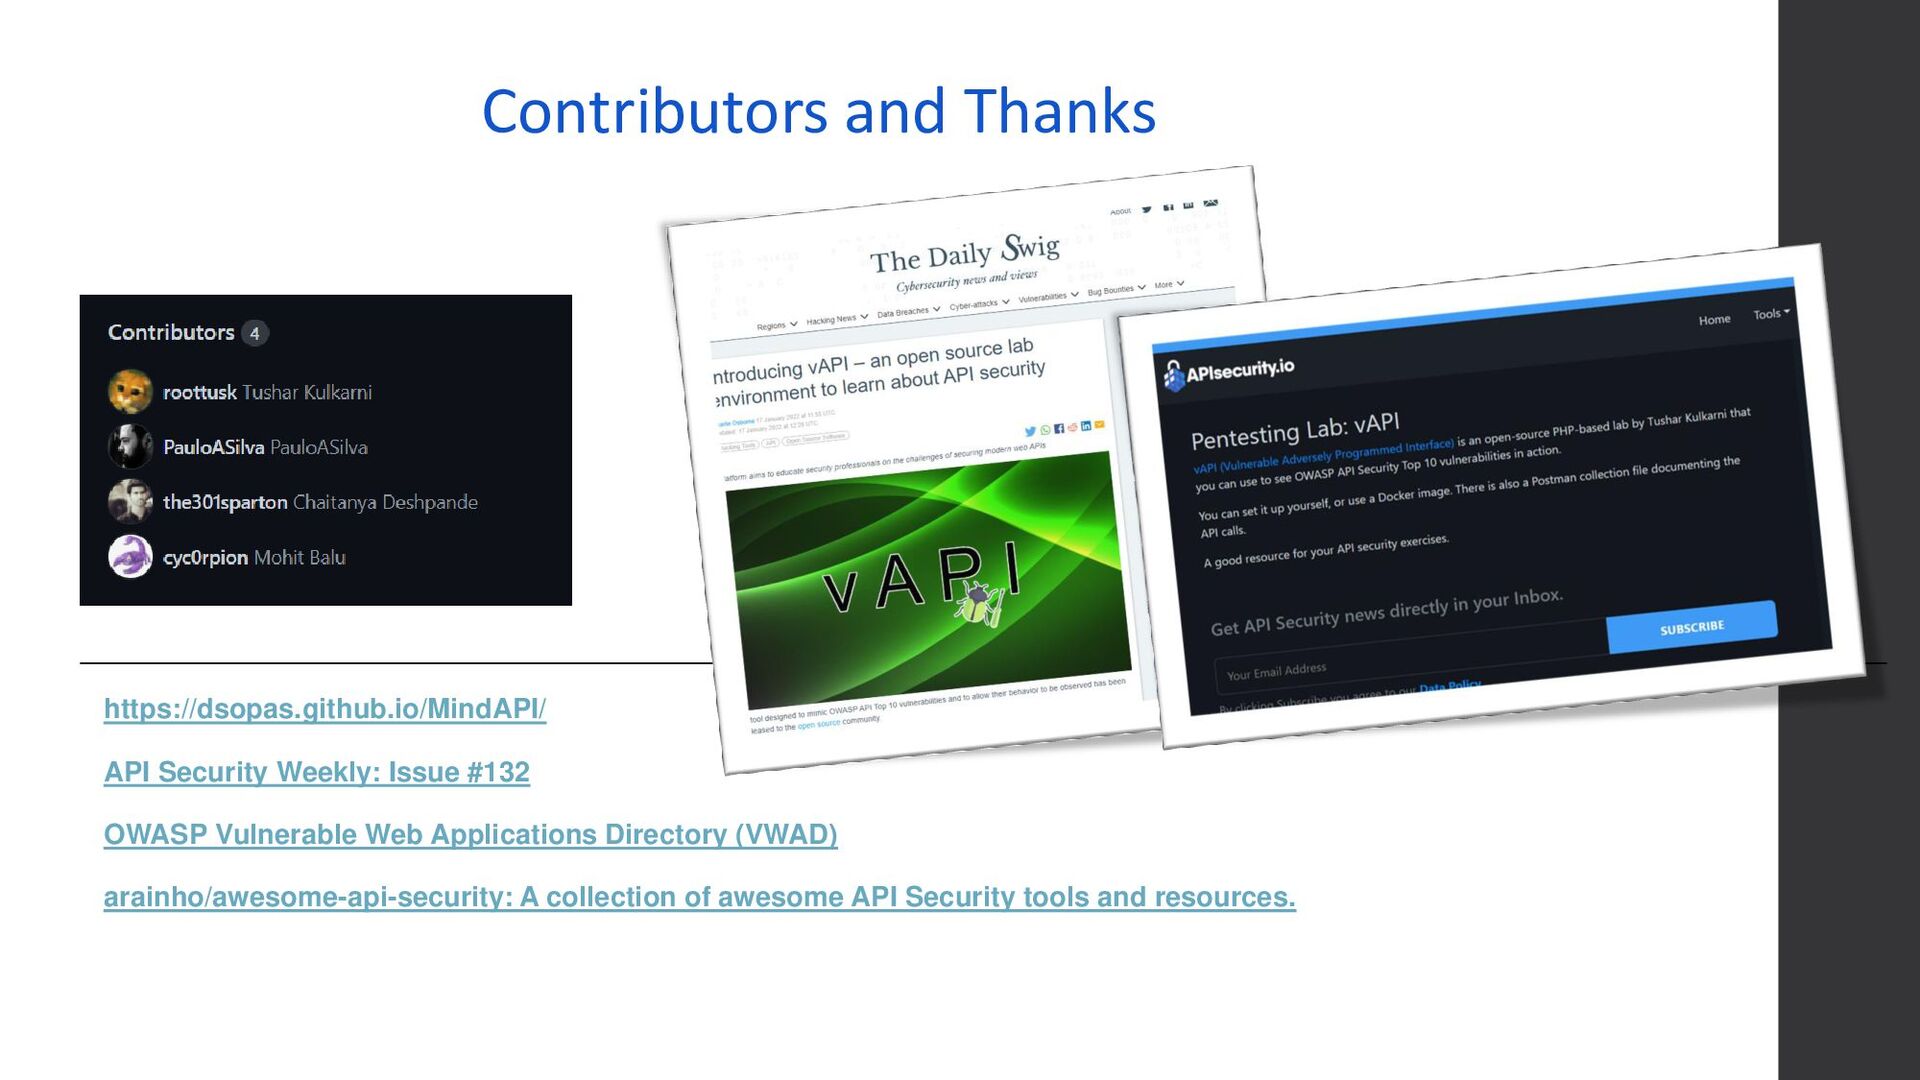
vAPI : Vulnerable Adversely Programmed Interface Contributors and Thanks https://dsopas.github.io/MindAPI/
API Security Weekly: Issue #132 OWASP Vulnerable Web Applications Directory (VWAD) arainho/awesome-api-security: A collection of awesome API Security tools and resources. -
vAPI : Vulnerable Adversely Programmed Interface References https://owasp.org/www-project-api-security/ https://blog.api.rakuten.net/api-benefits/ https://blog.api.rakuten.net/api-security/
http://helpcentral.componentone.com/nethelp/c1webapi/ https://dev.to/ricardo_borges/some-practices-to-design-restful-apis-interfaces-5a5i -
vAPI : Vulnerable Adversely Programmed Interface Q & A THANK
YOU • Twitter: @vk_tushar • Github: @roottusk • Mail: [email protected] • Web: roottusk.com