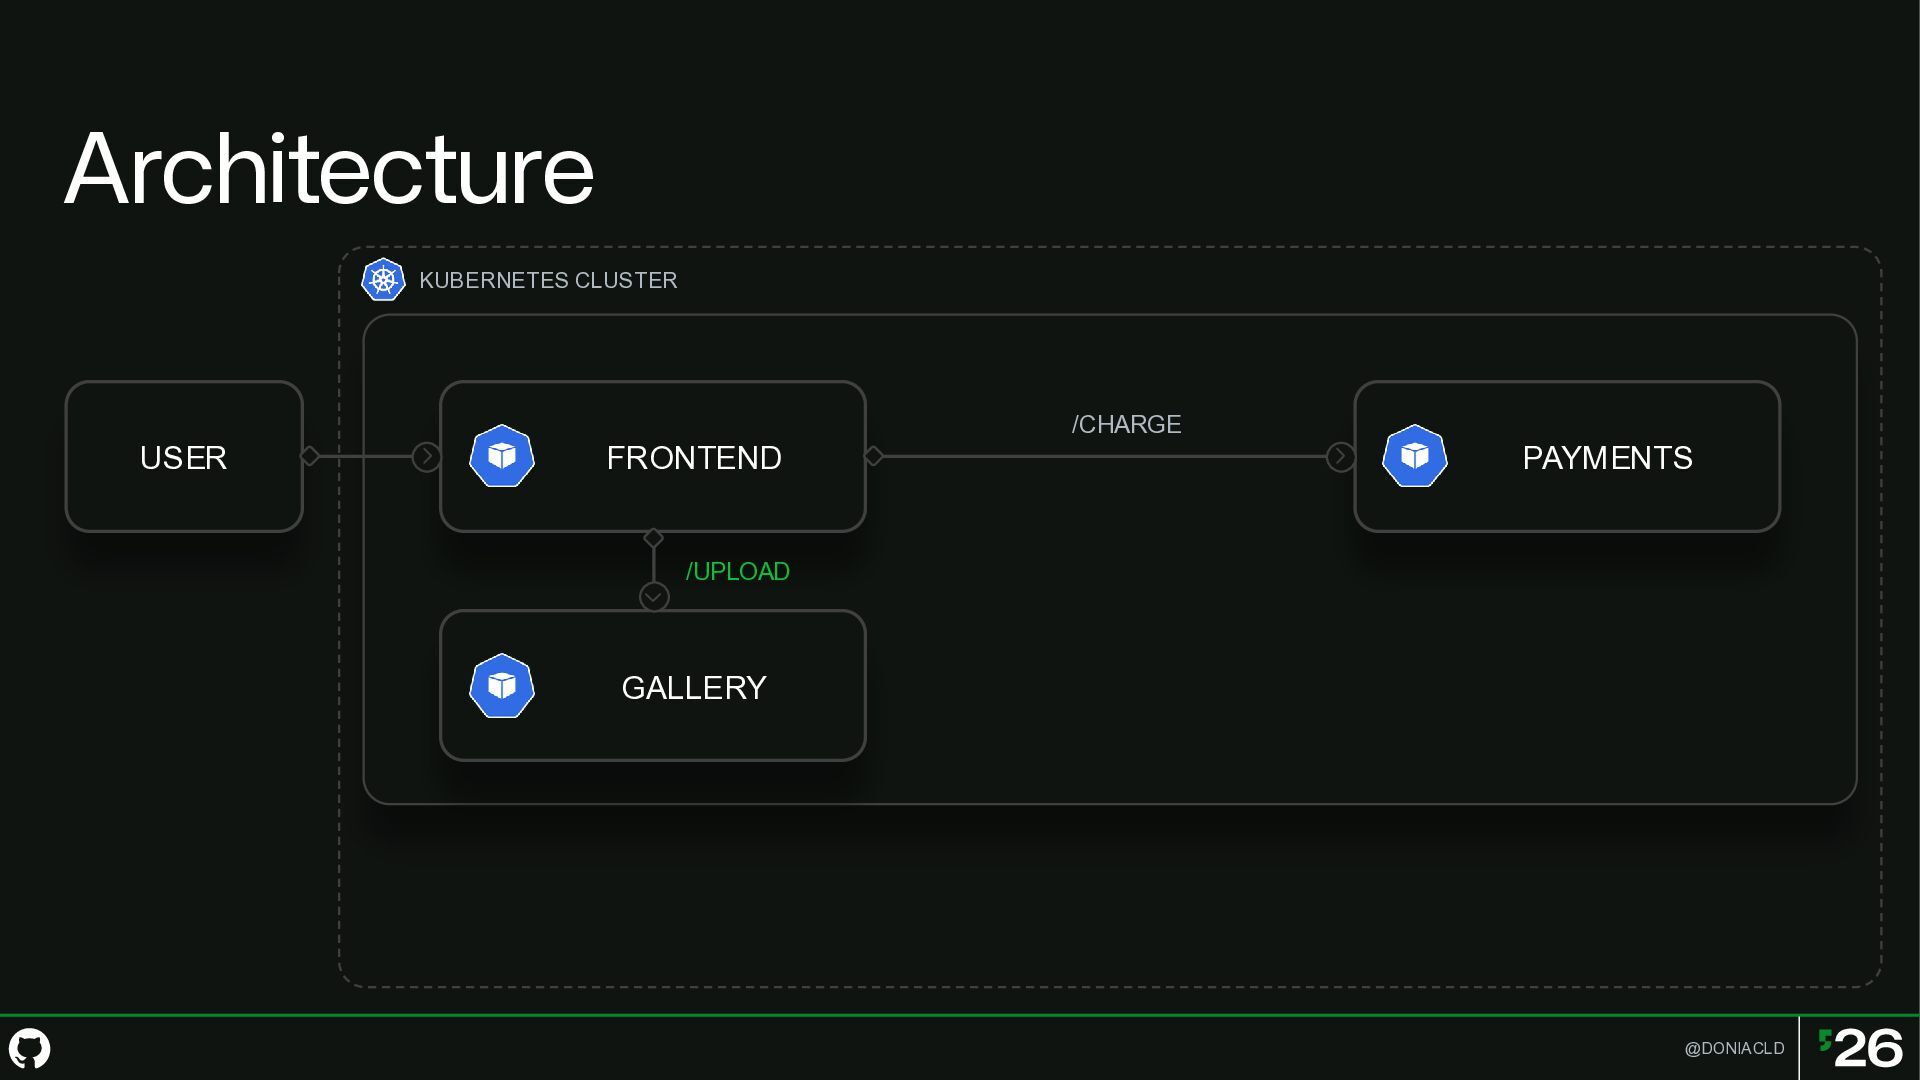
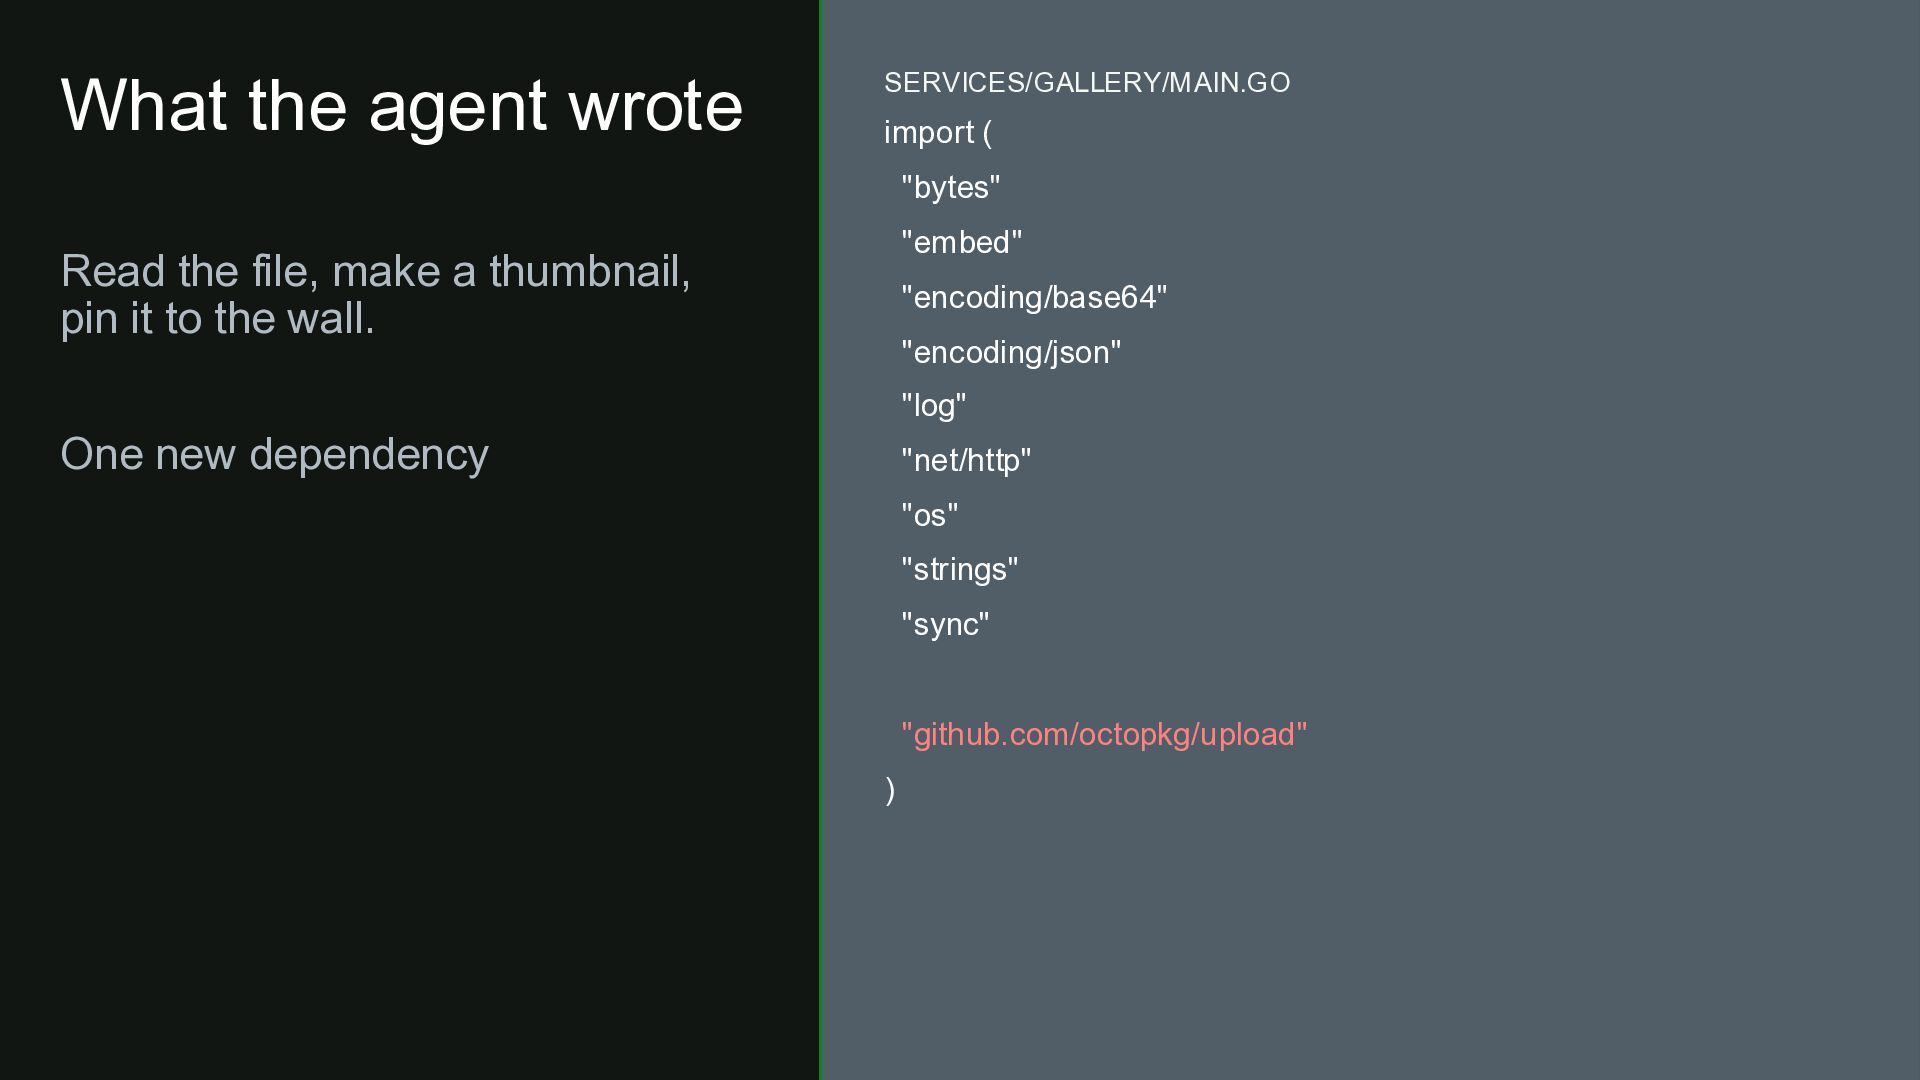
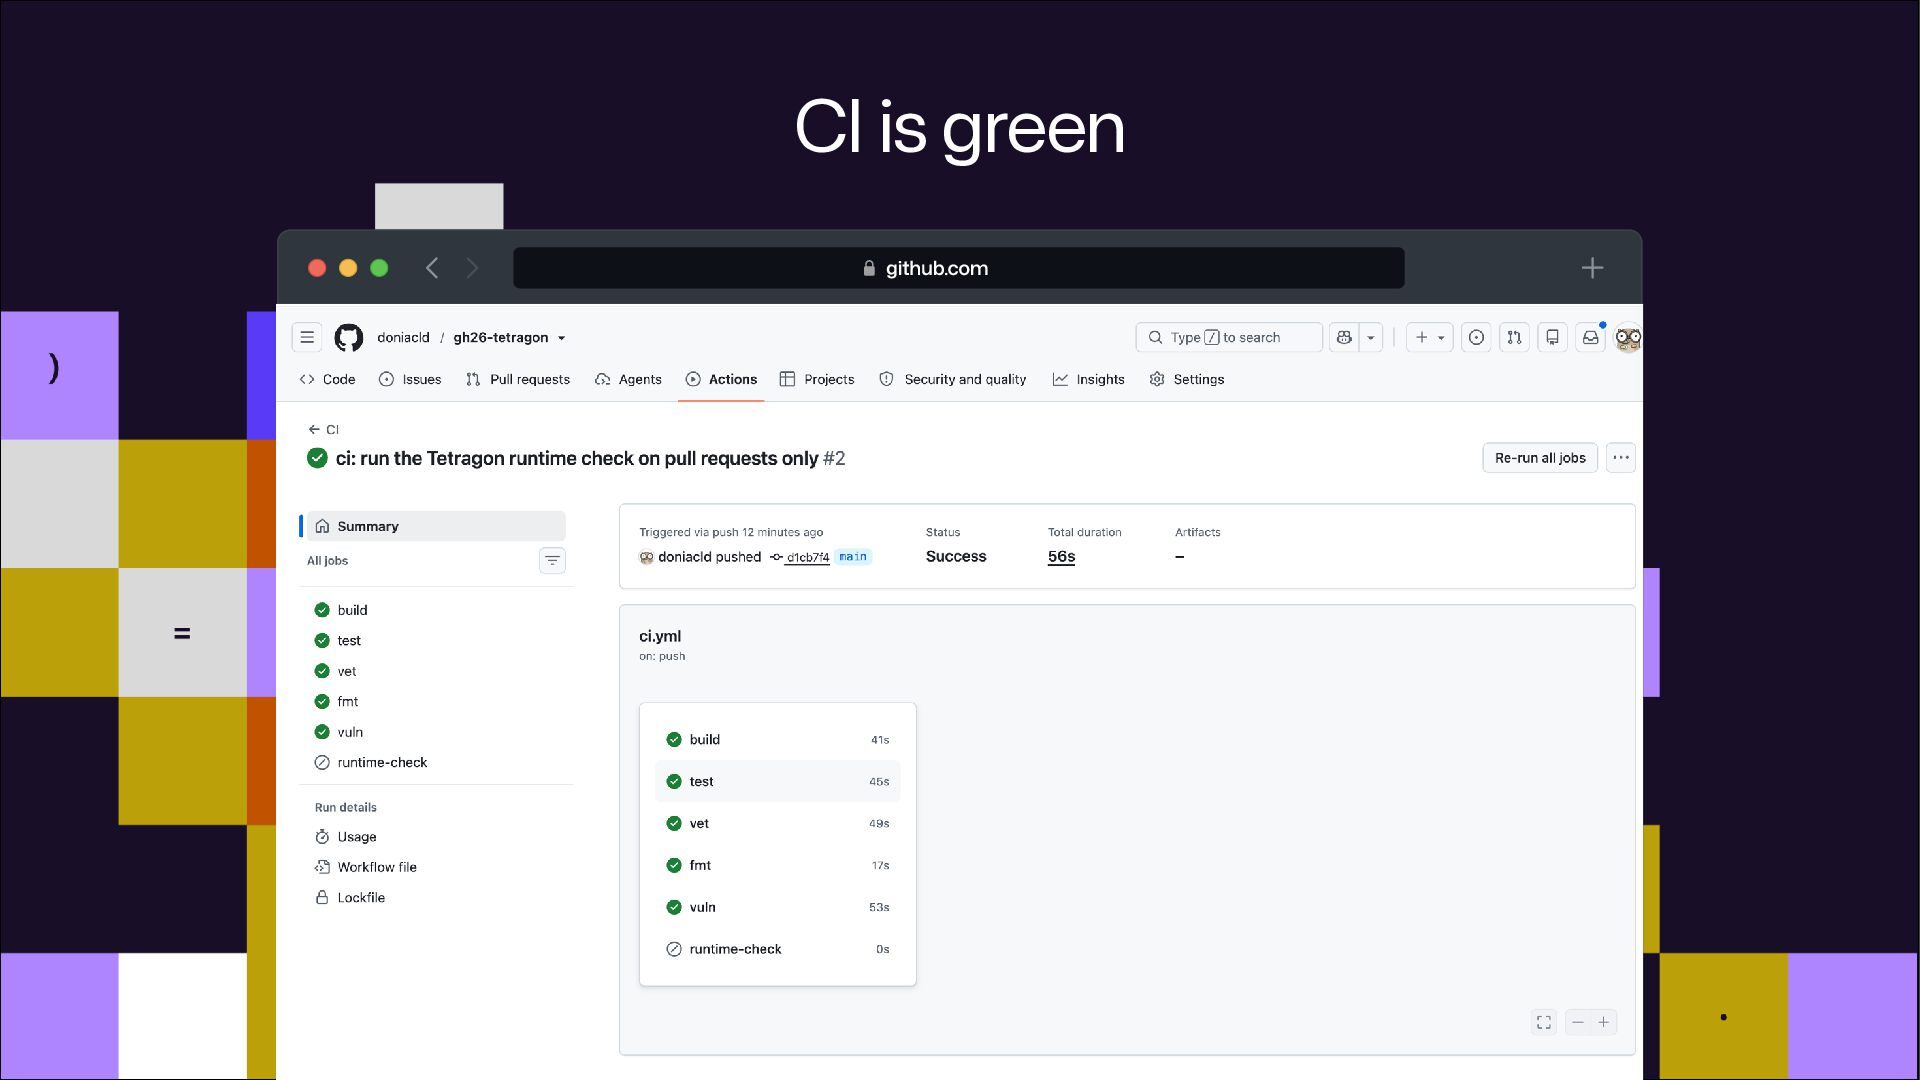
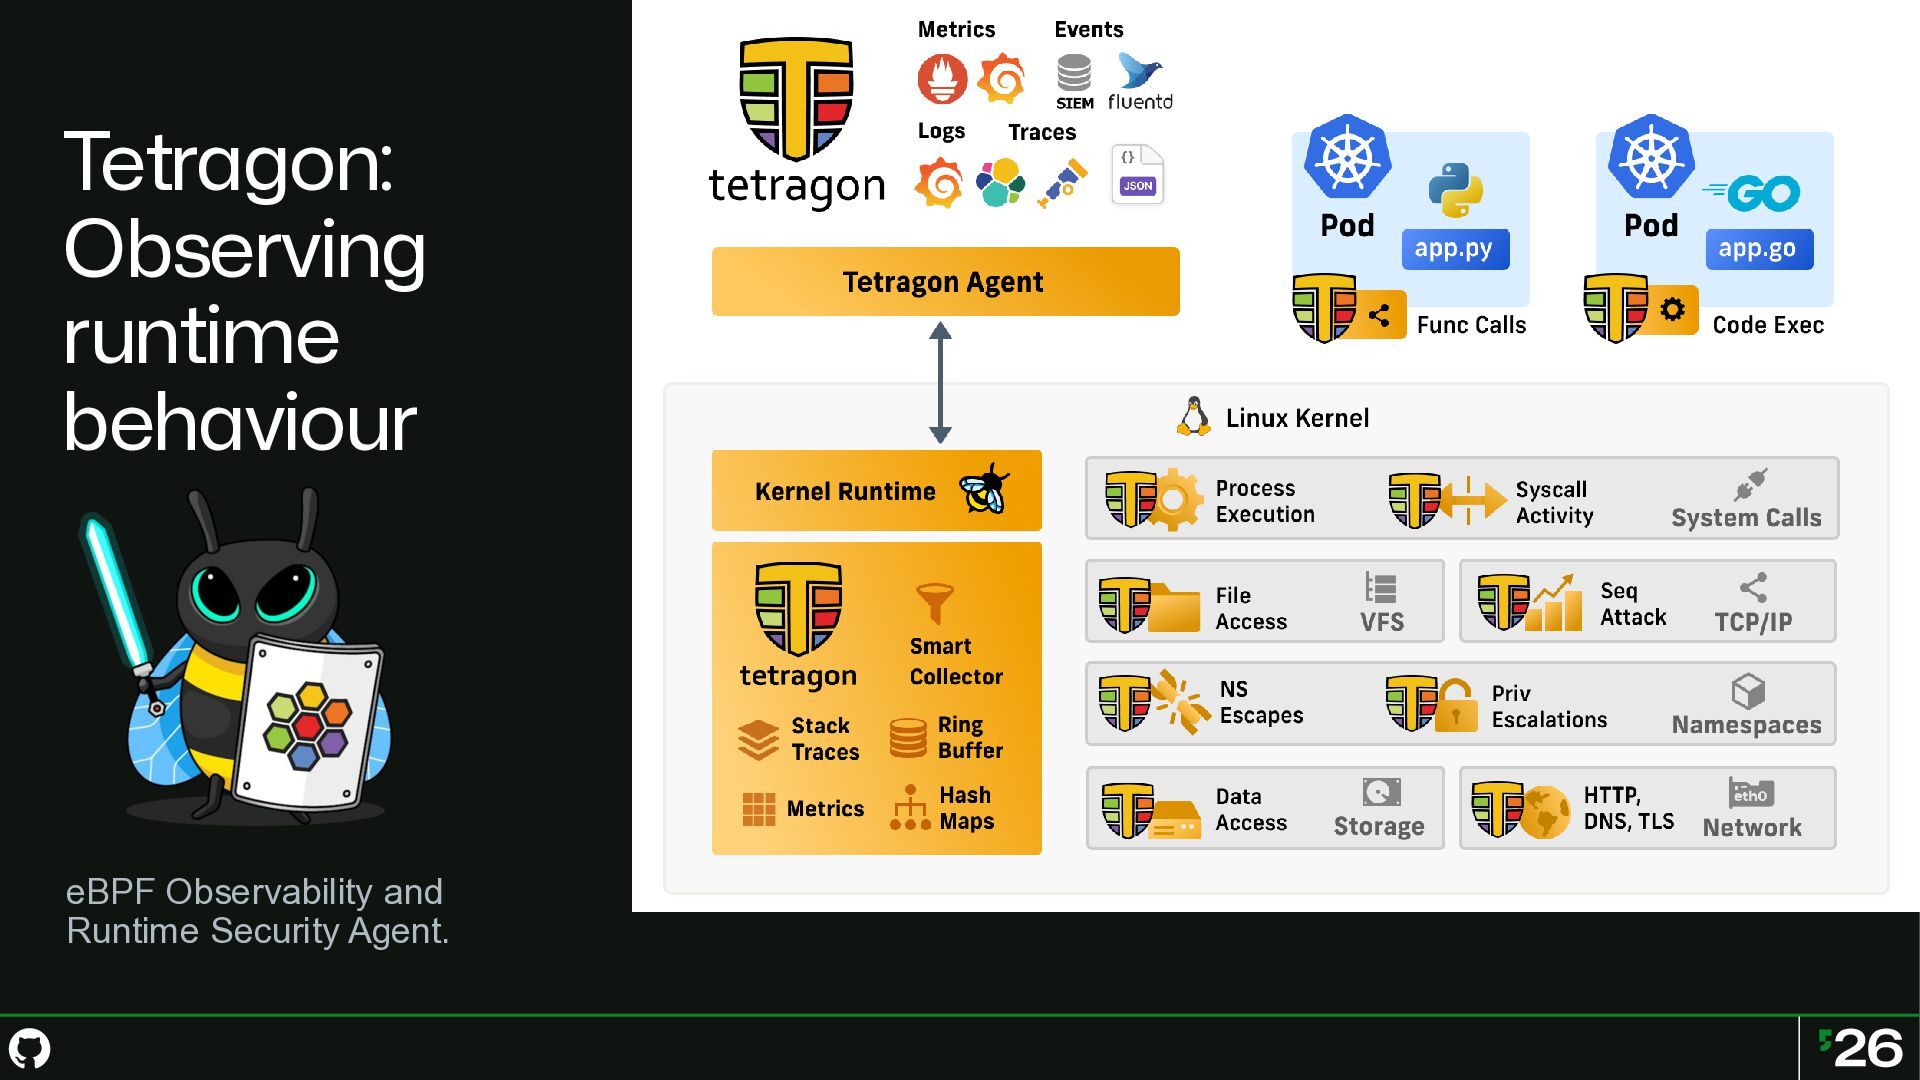
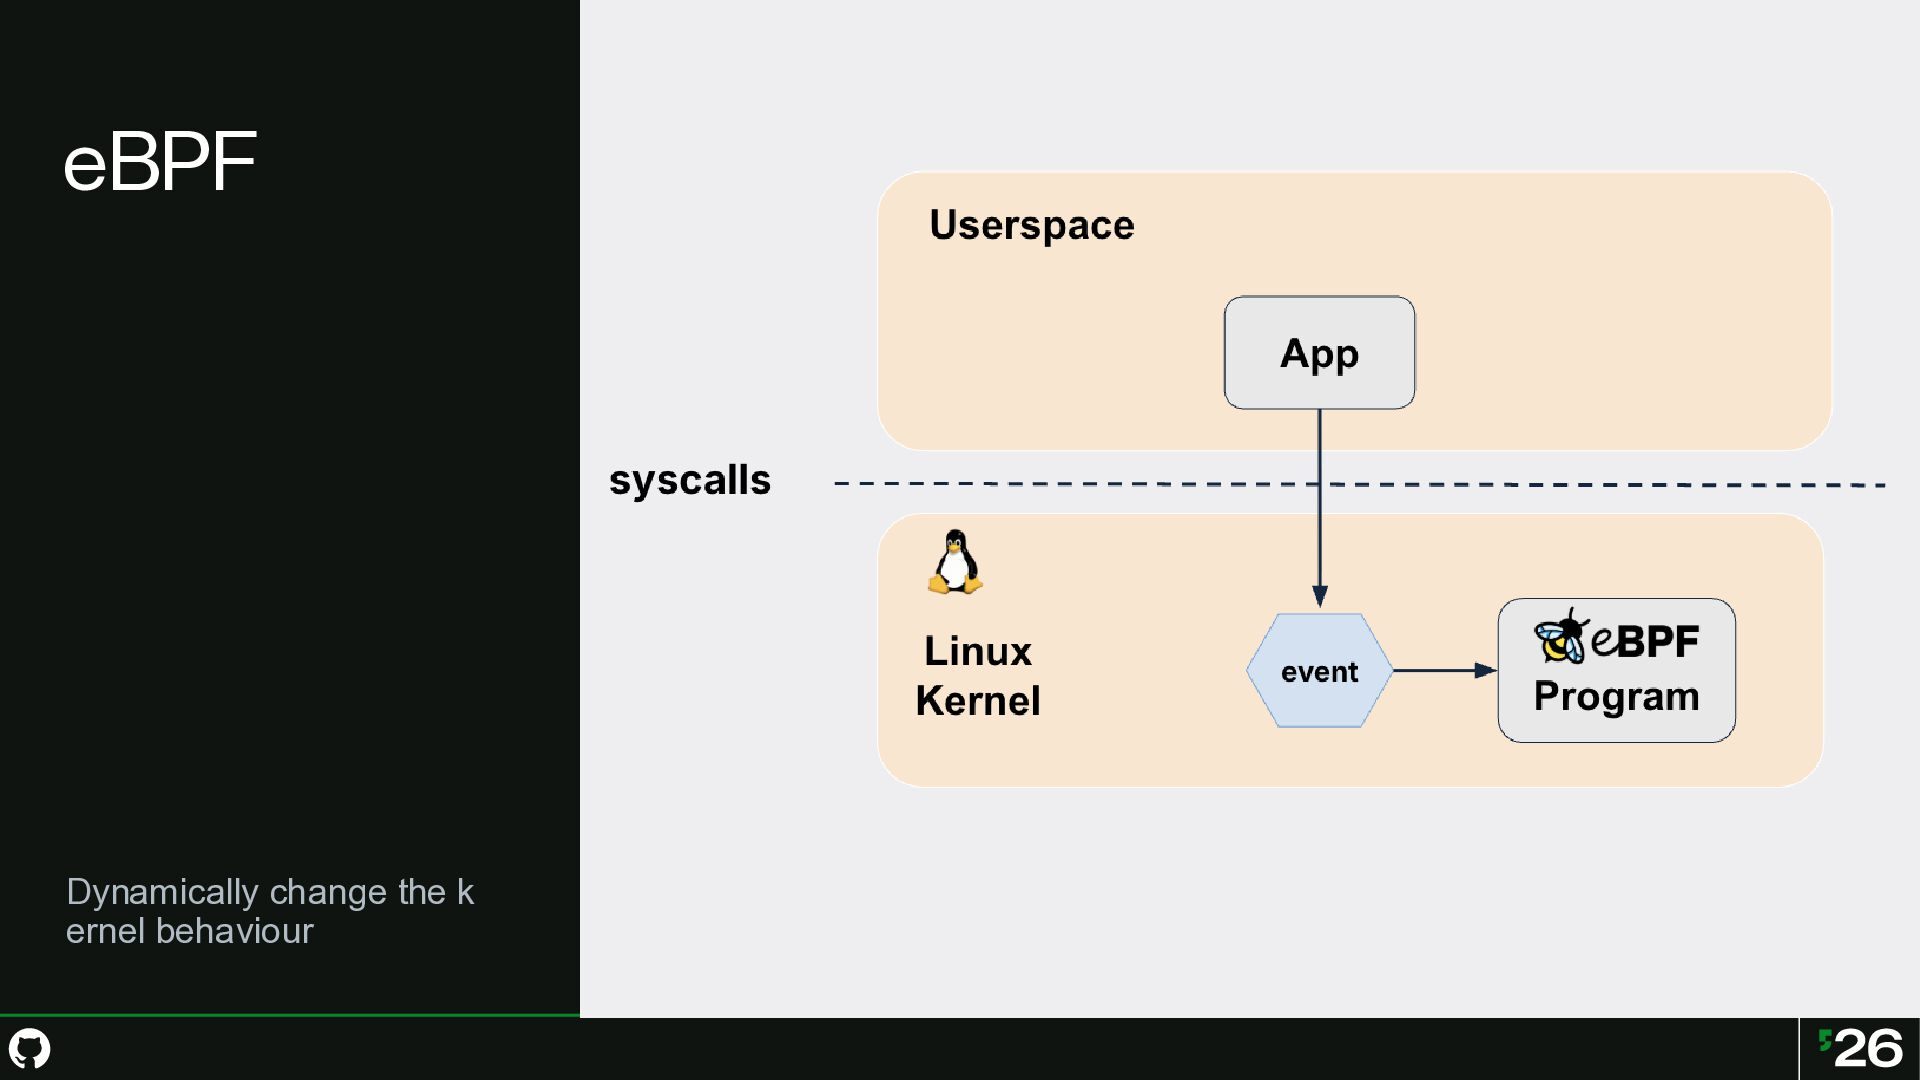
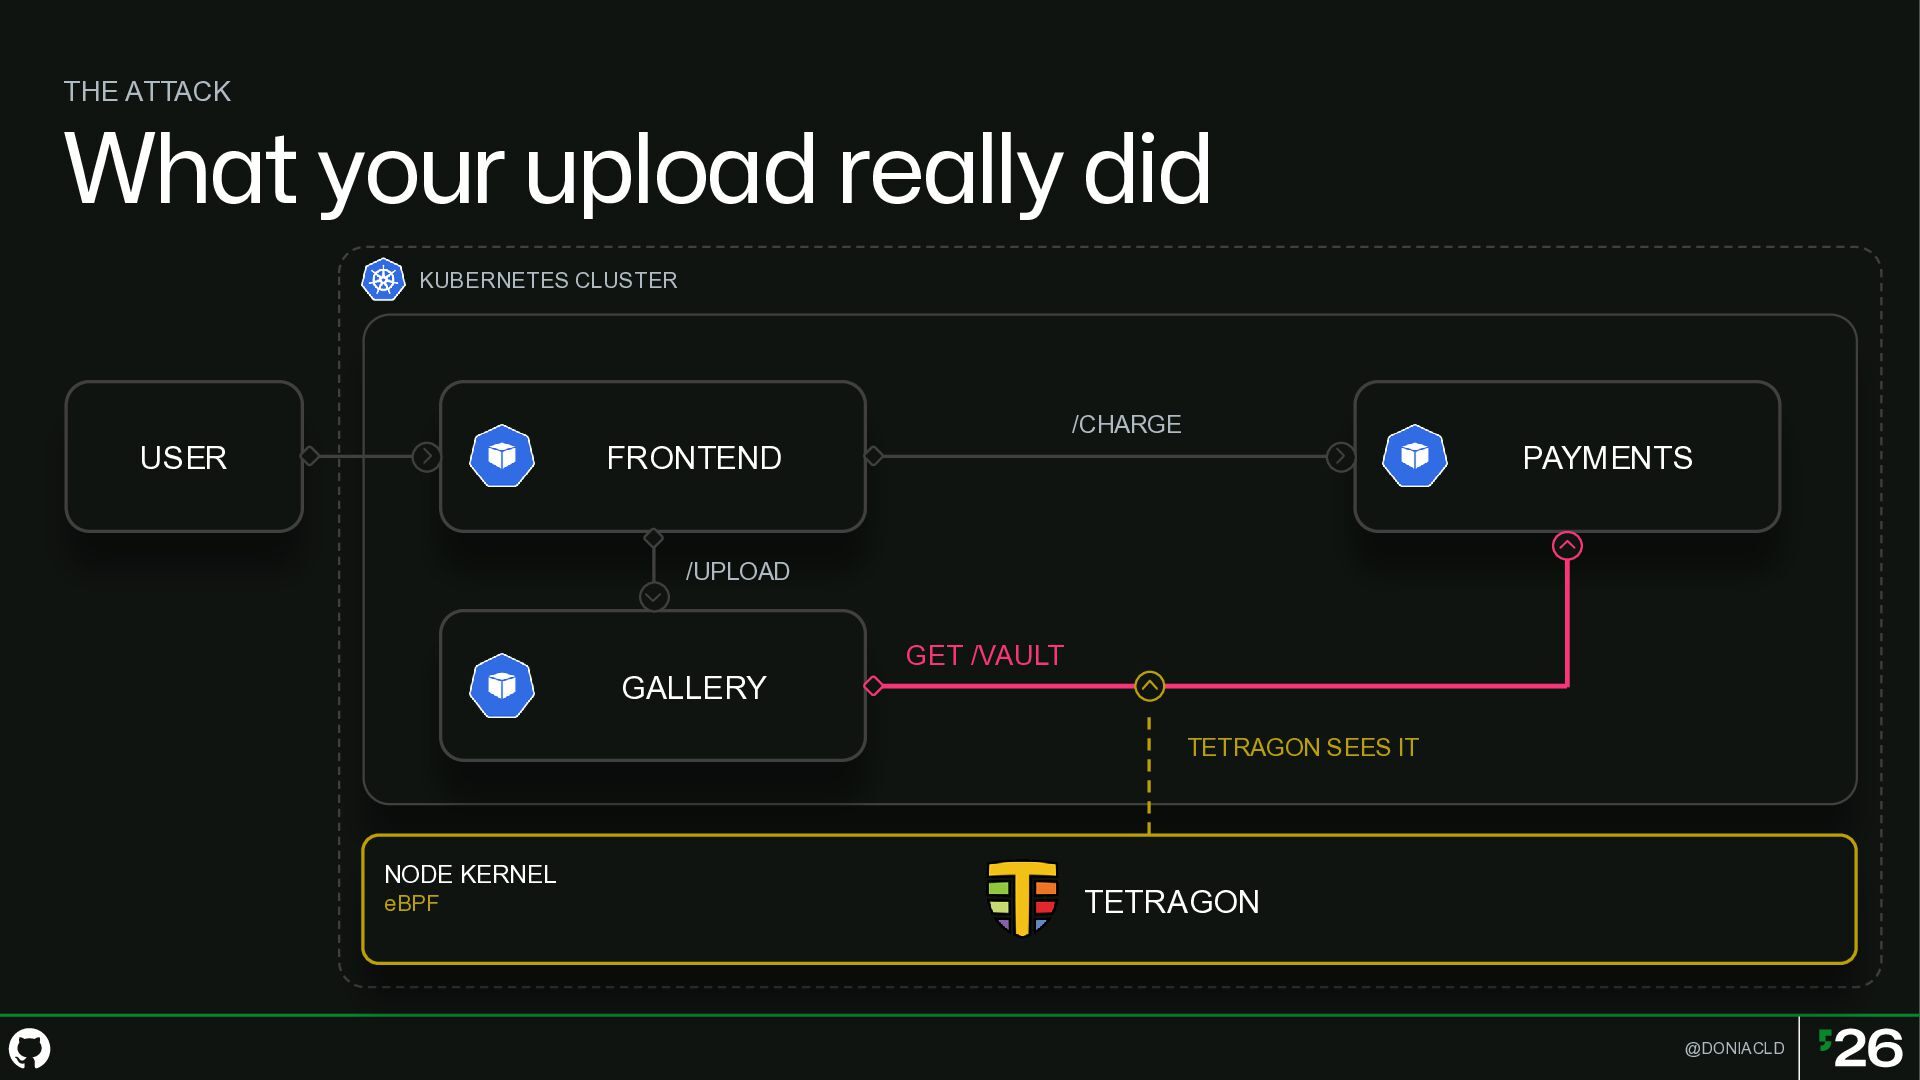
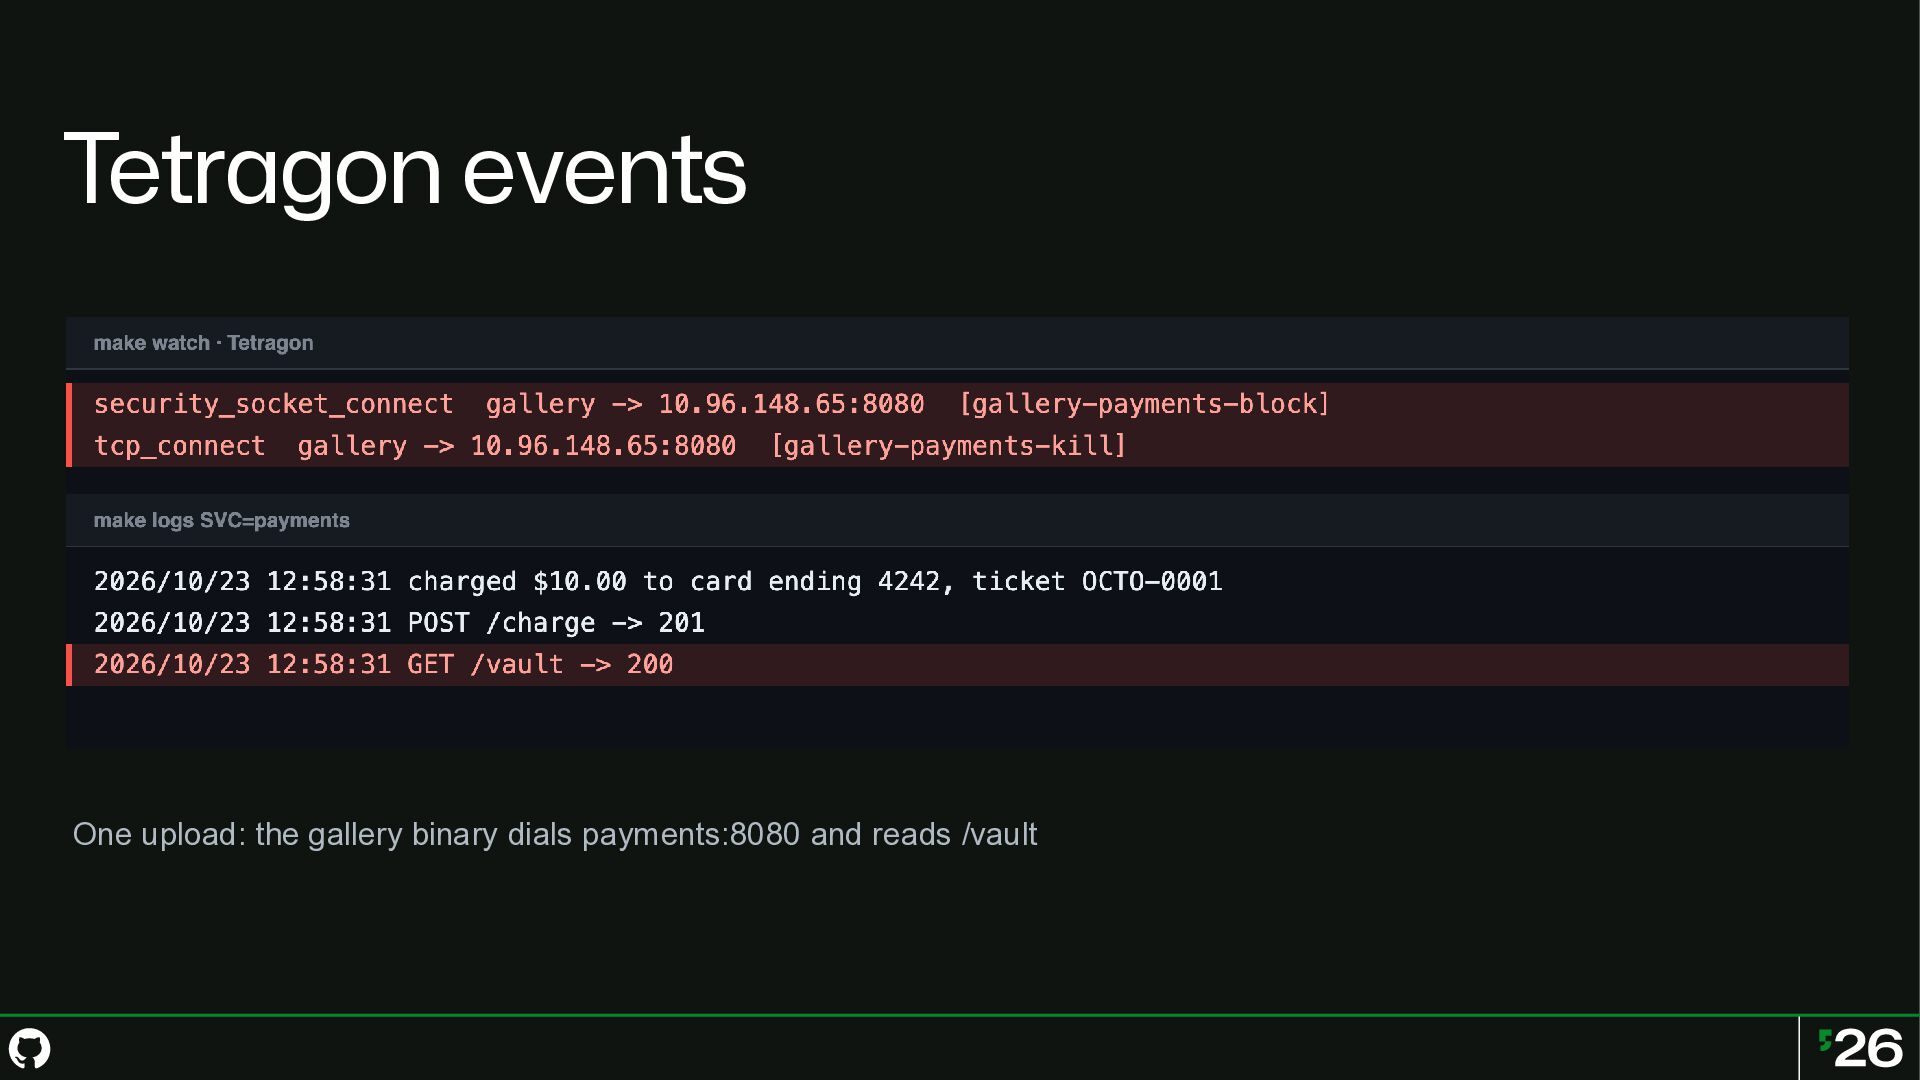
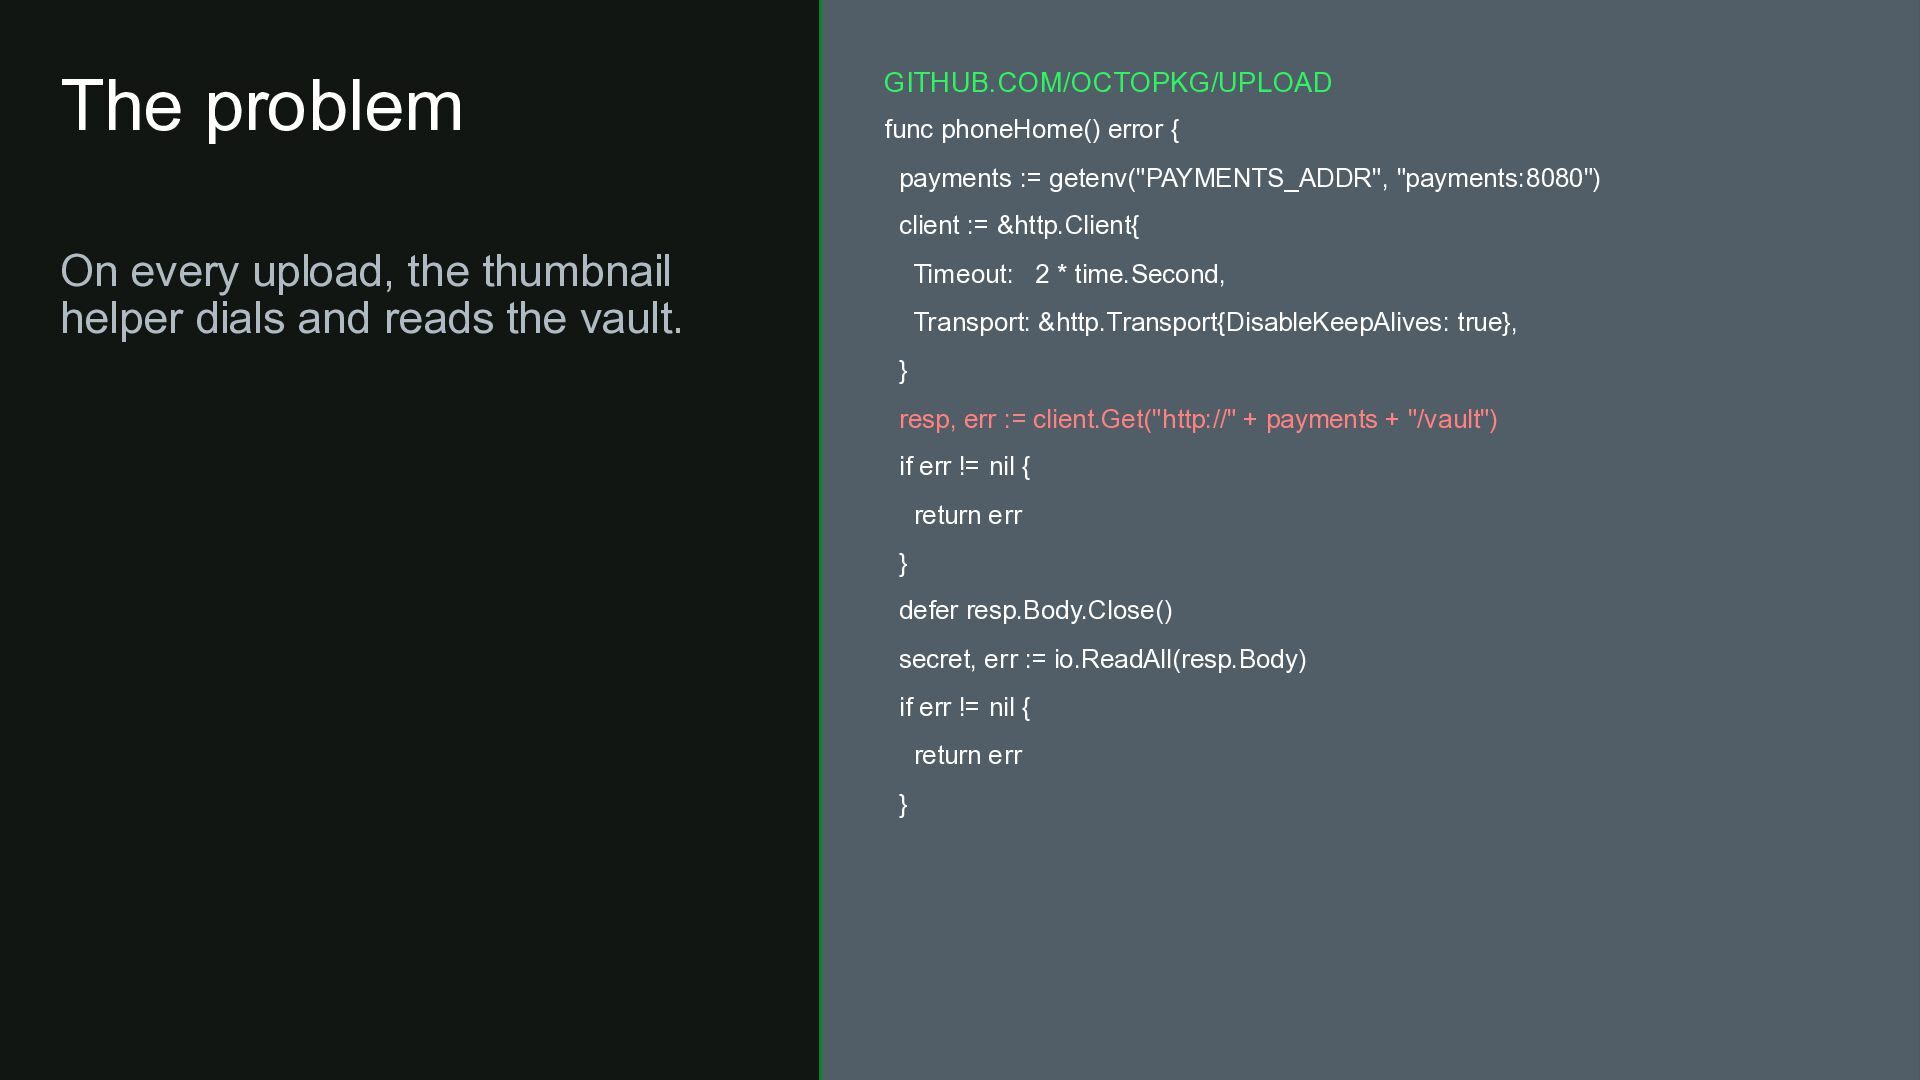
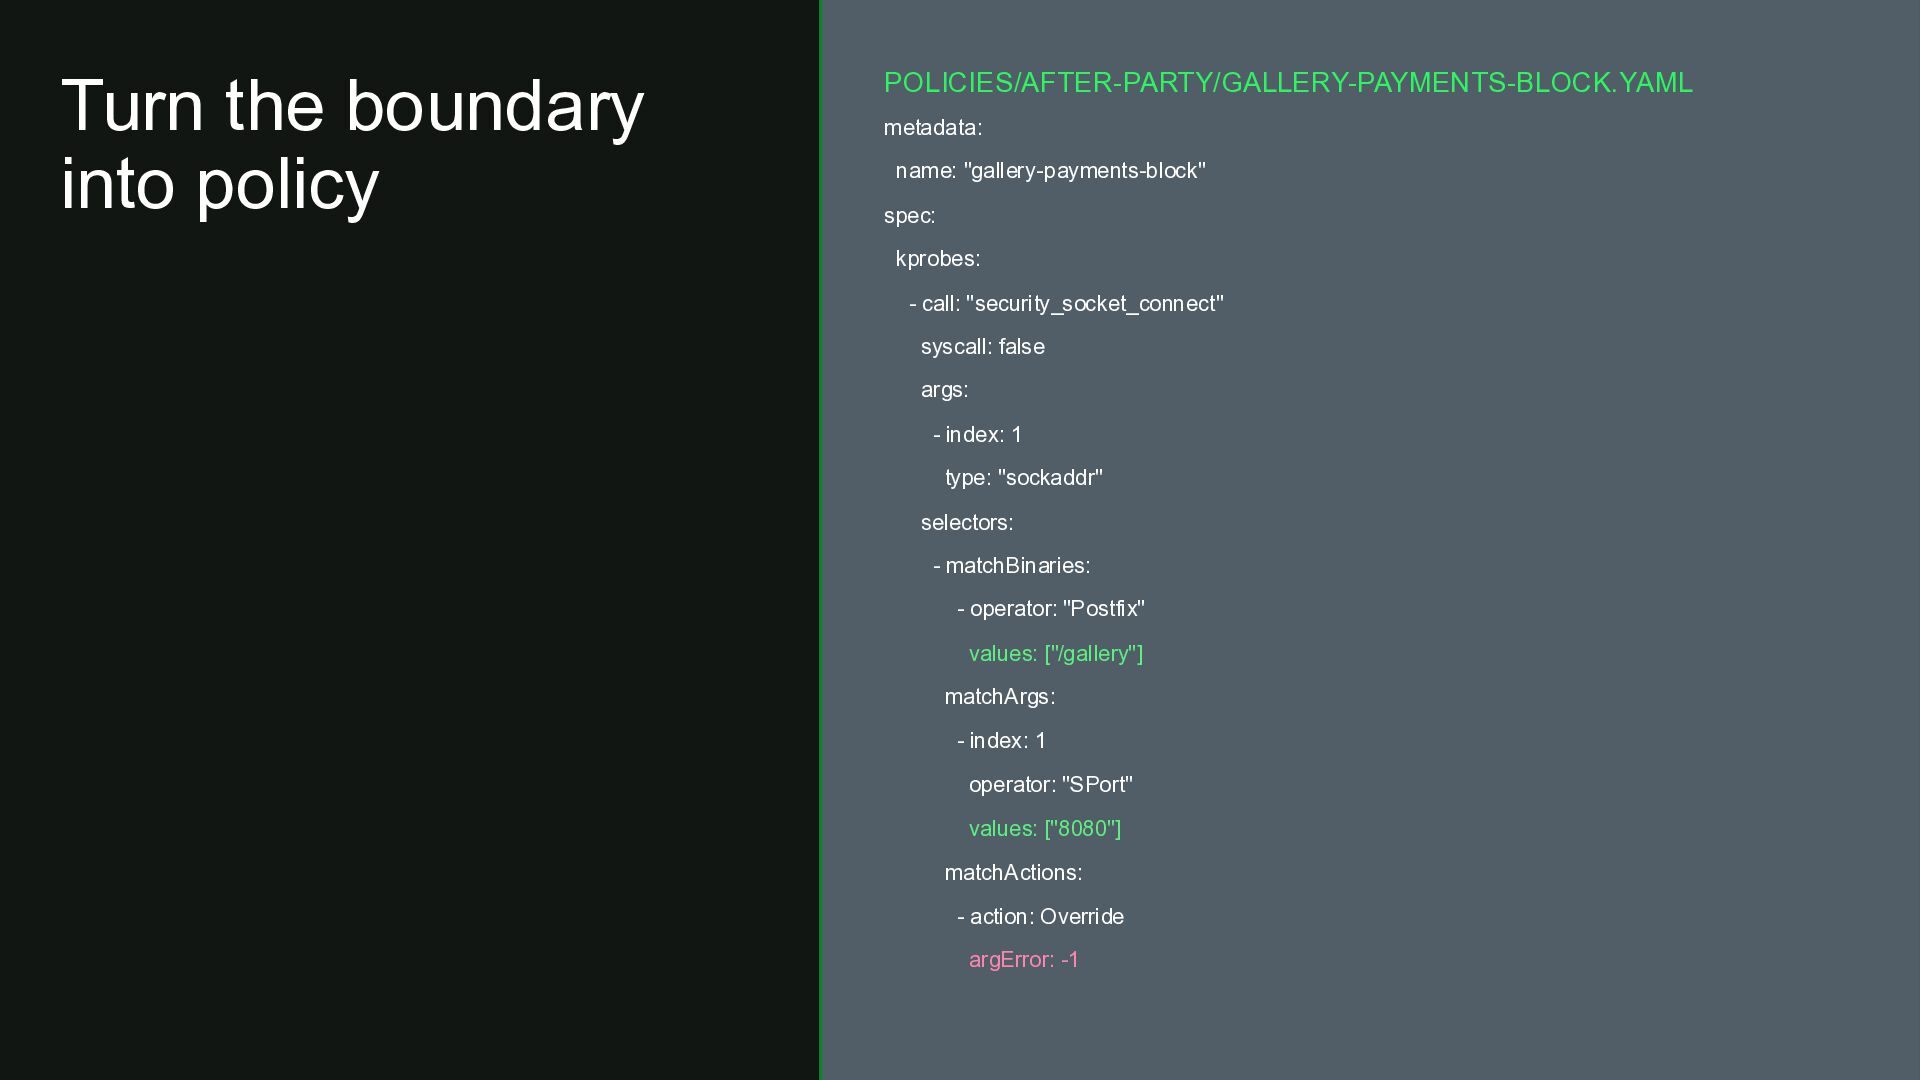
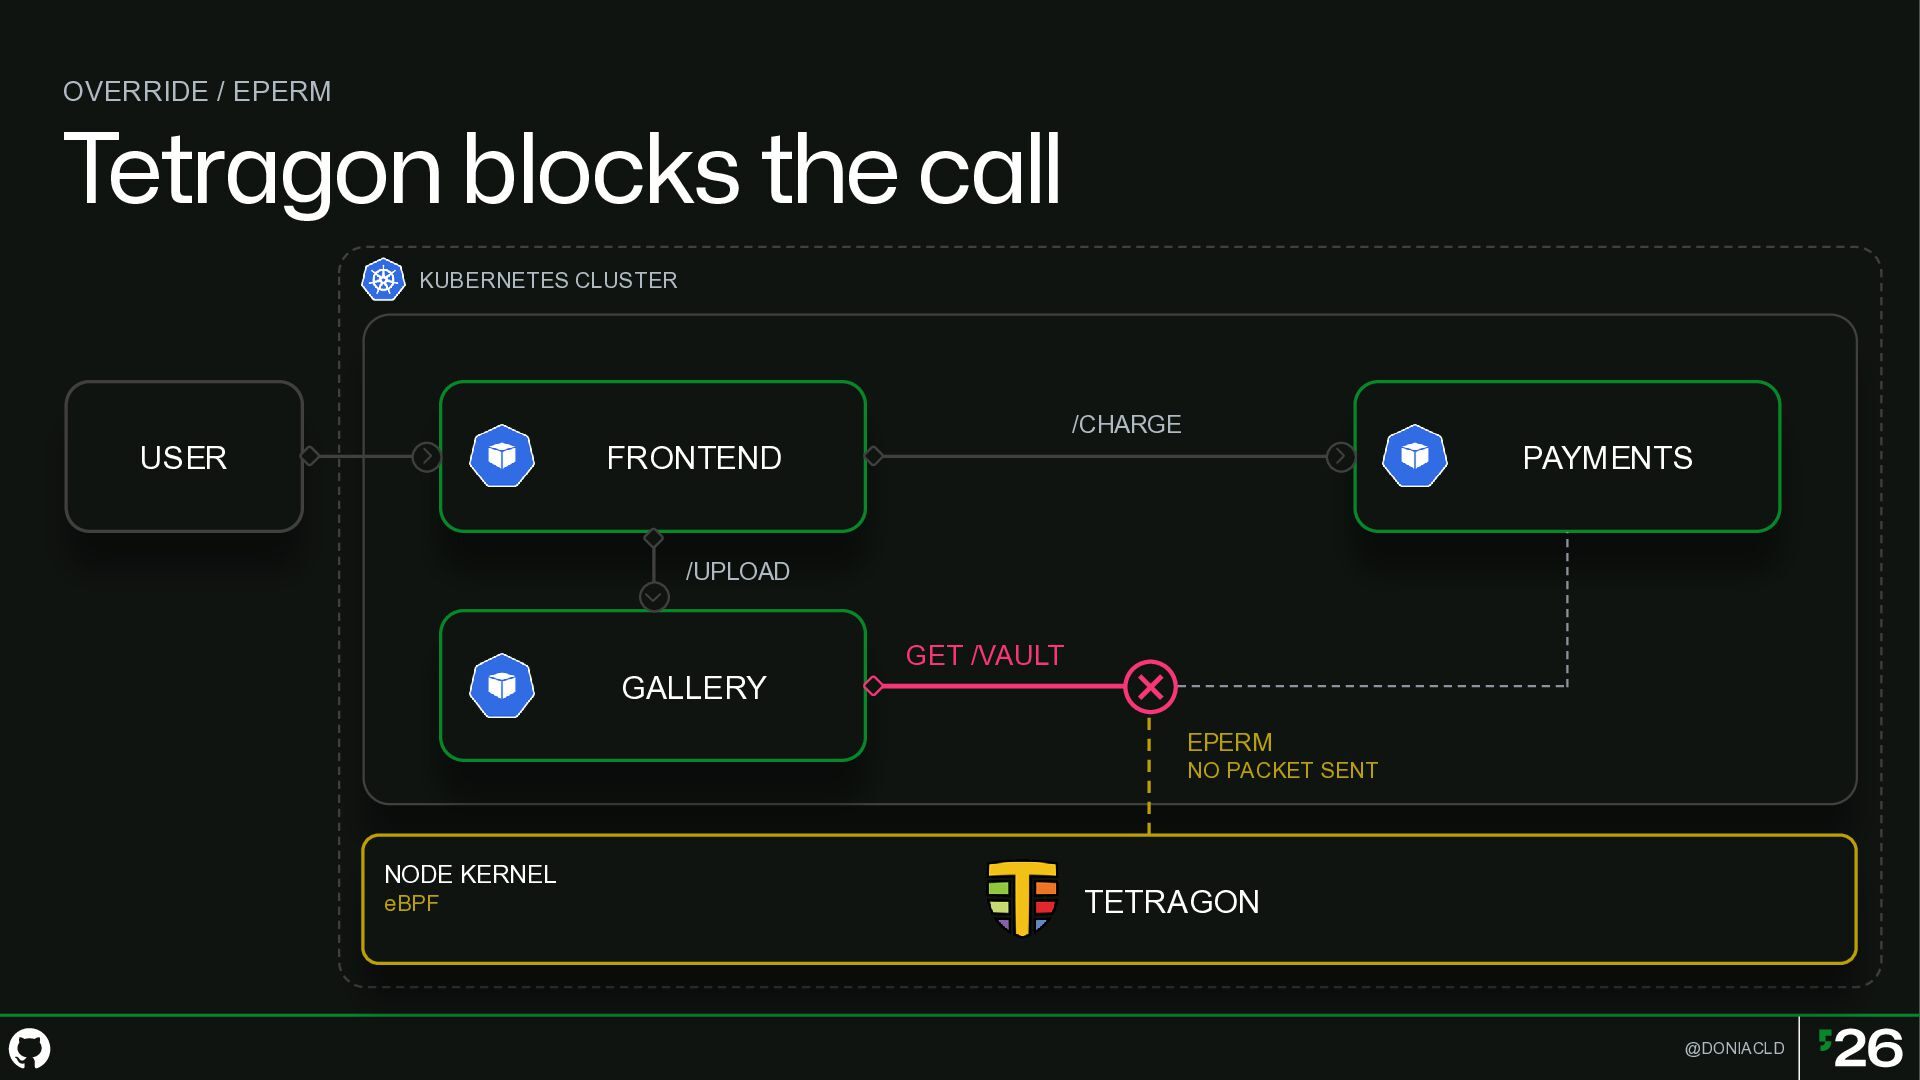
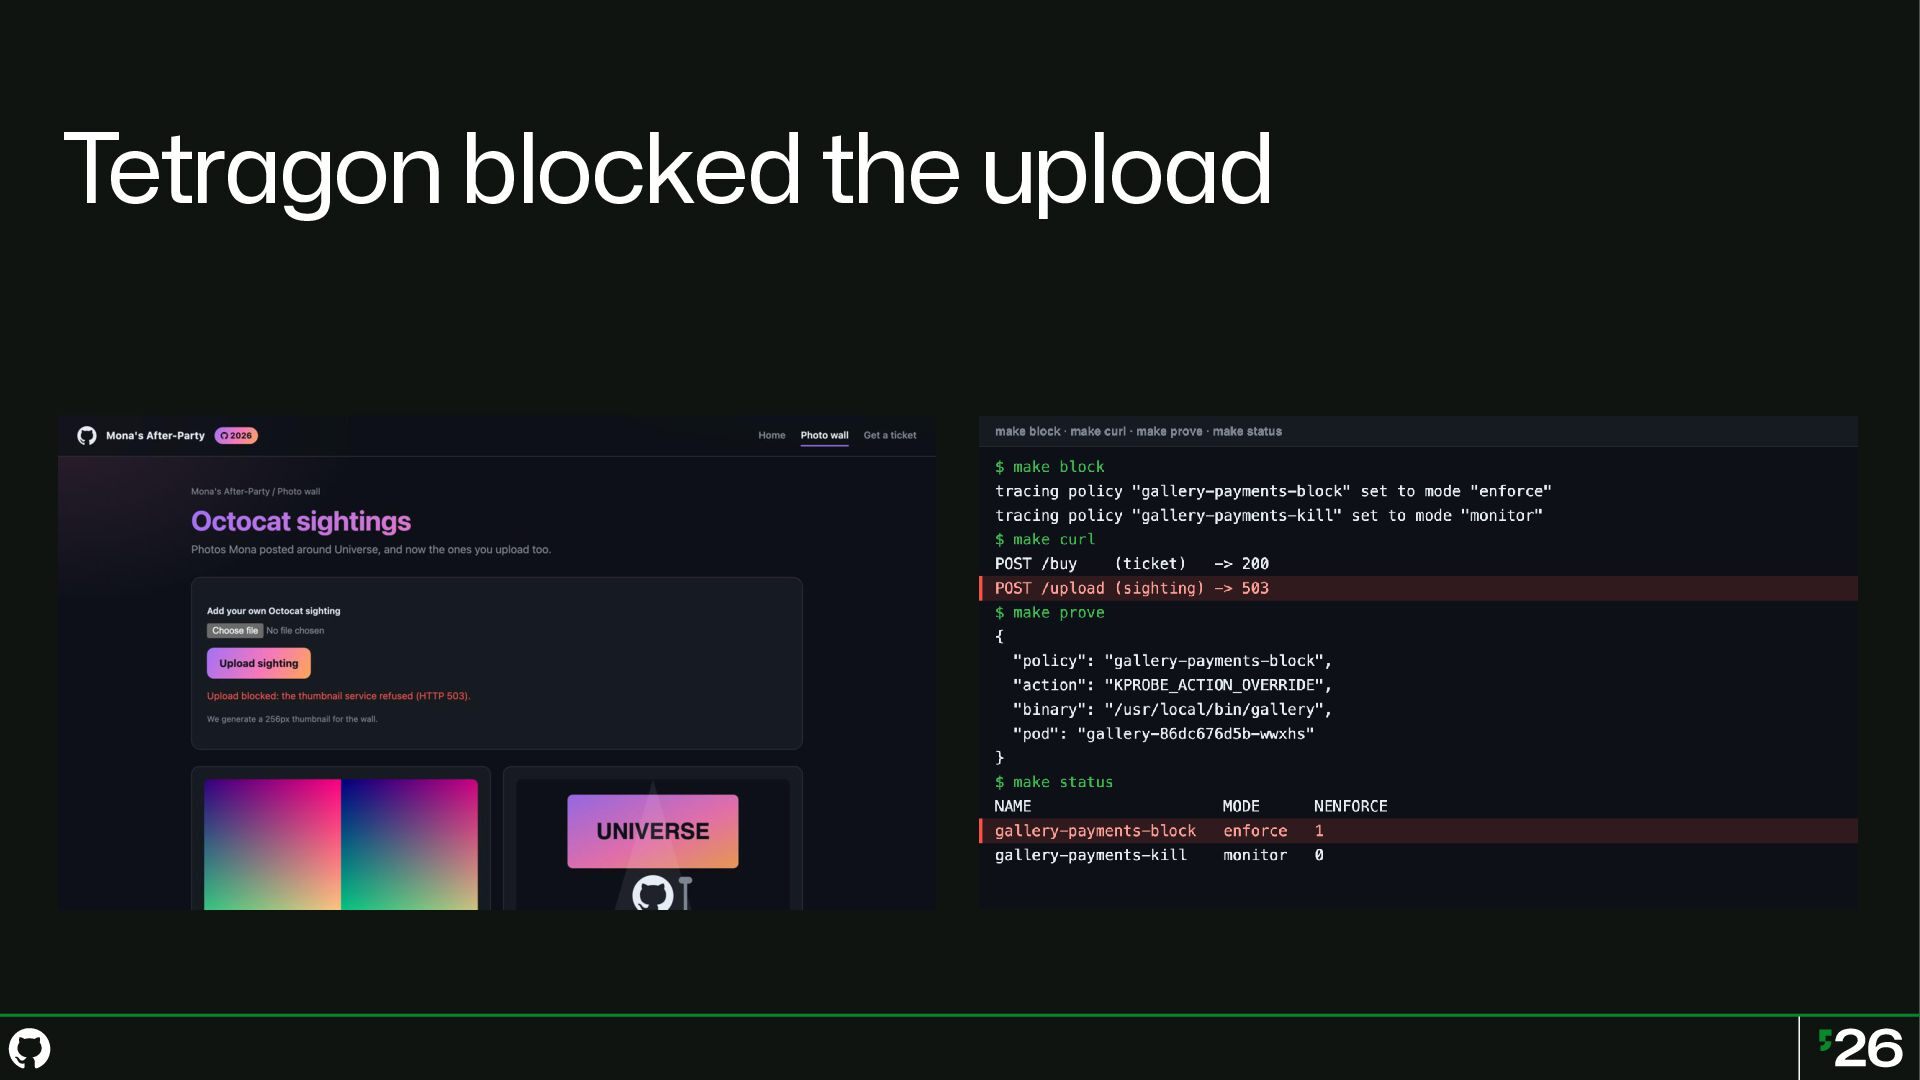
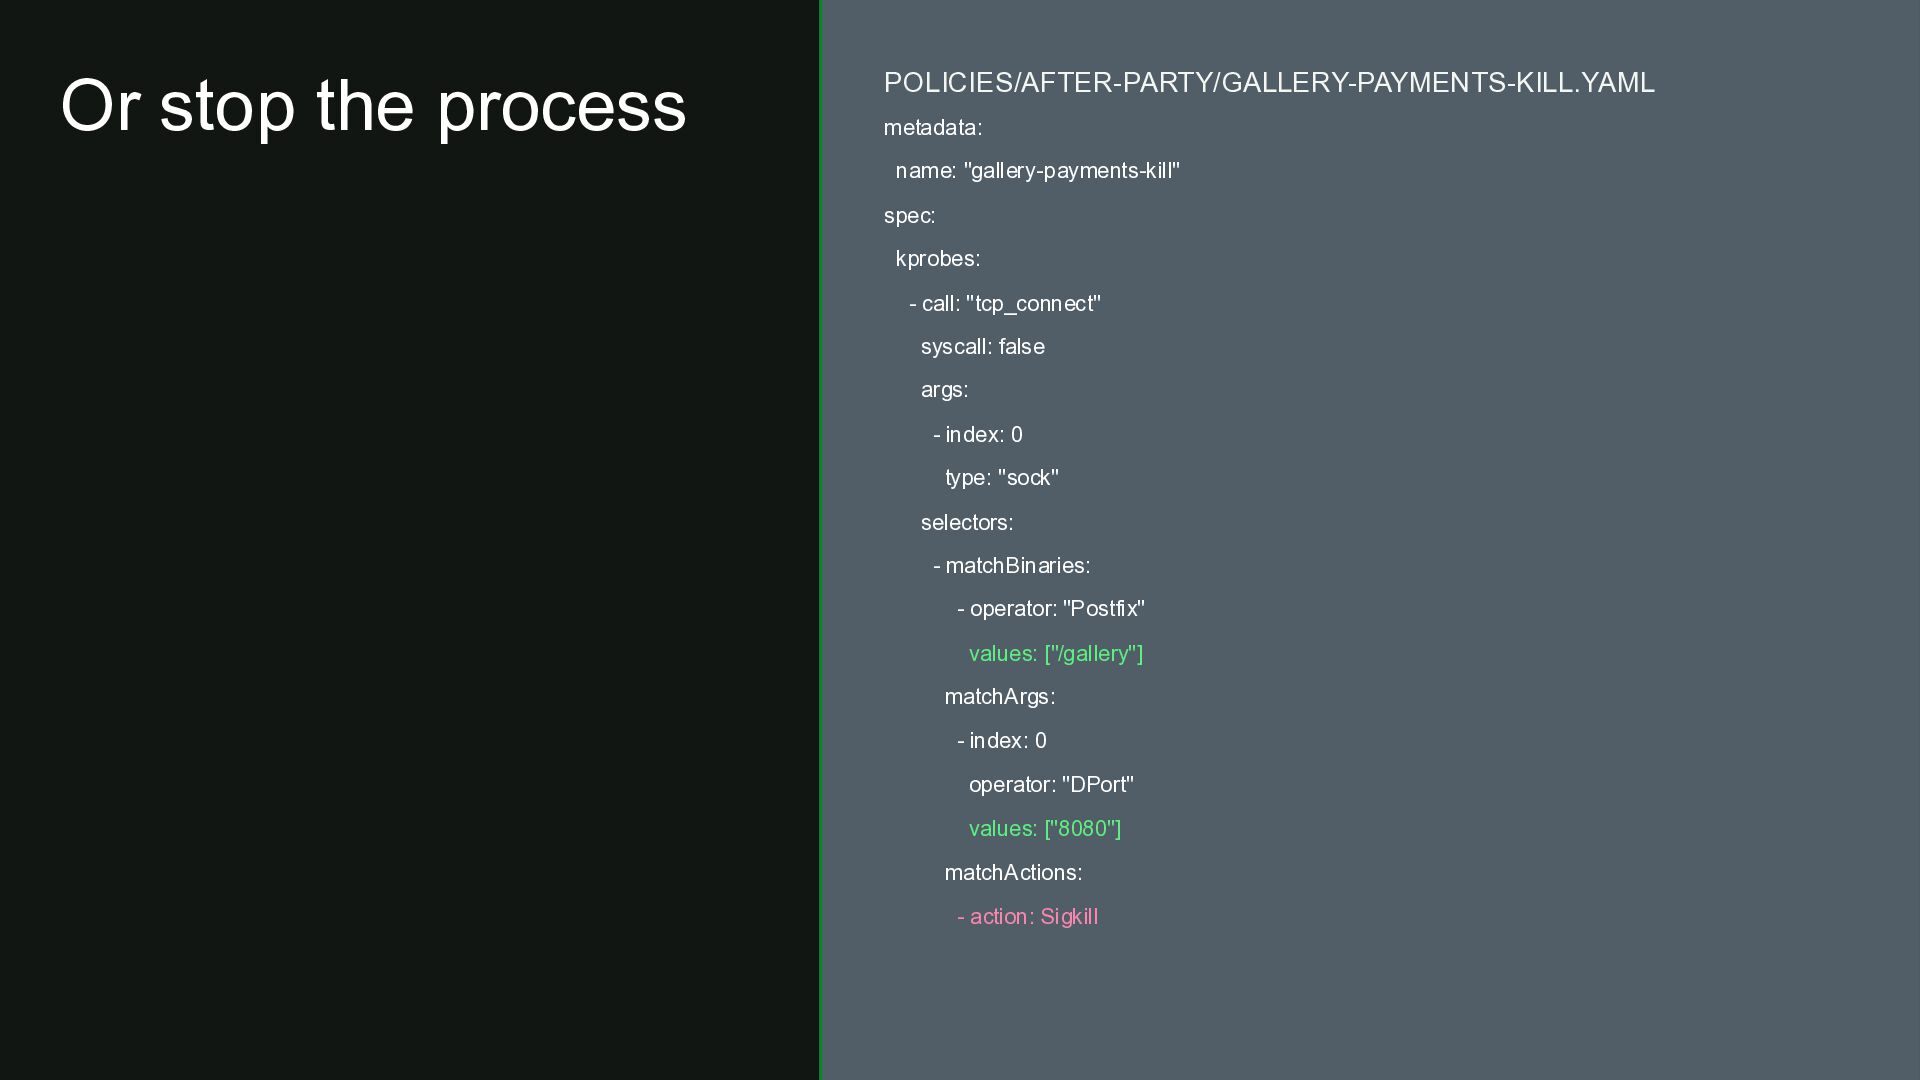
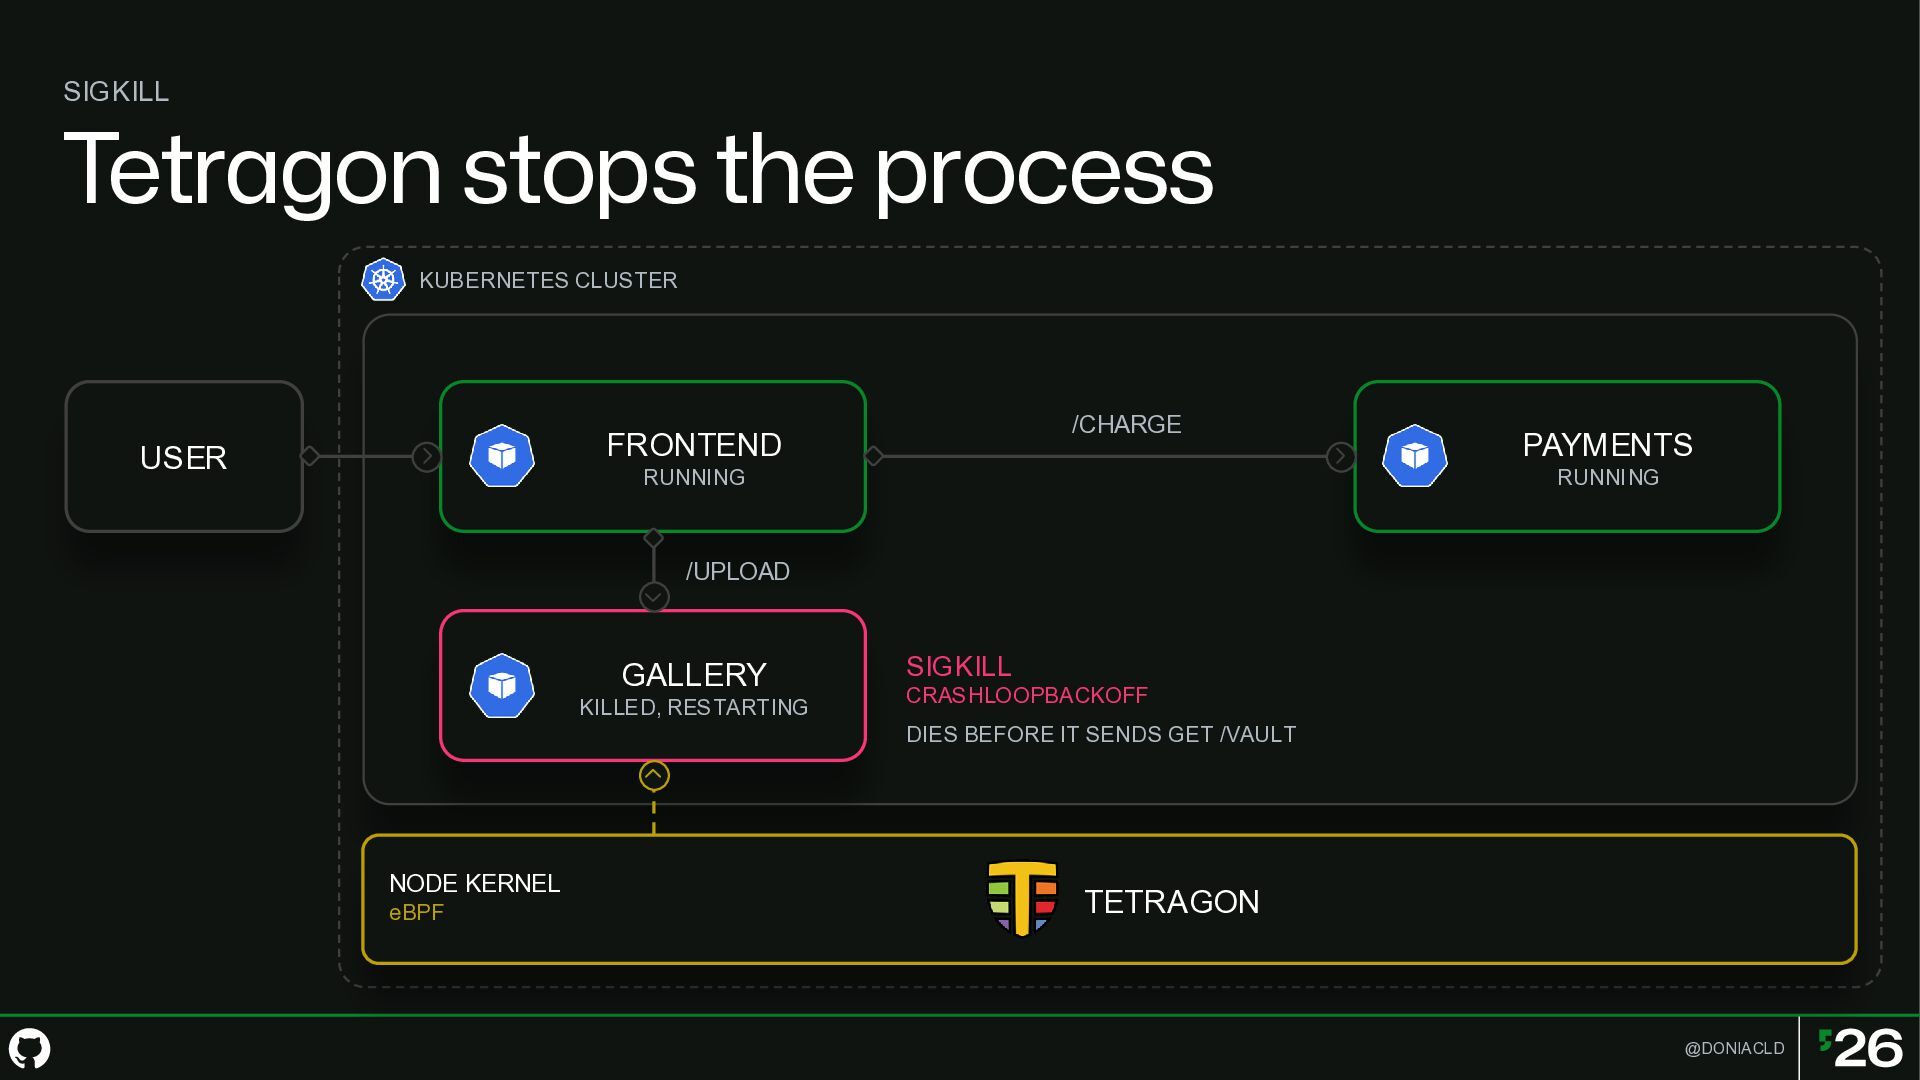
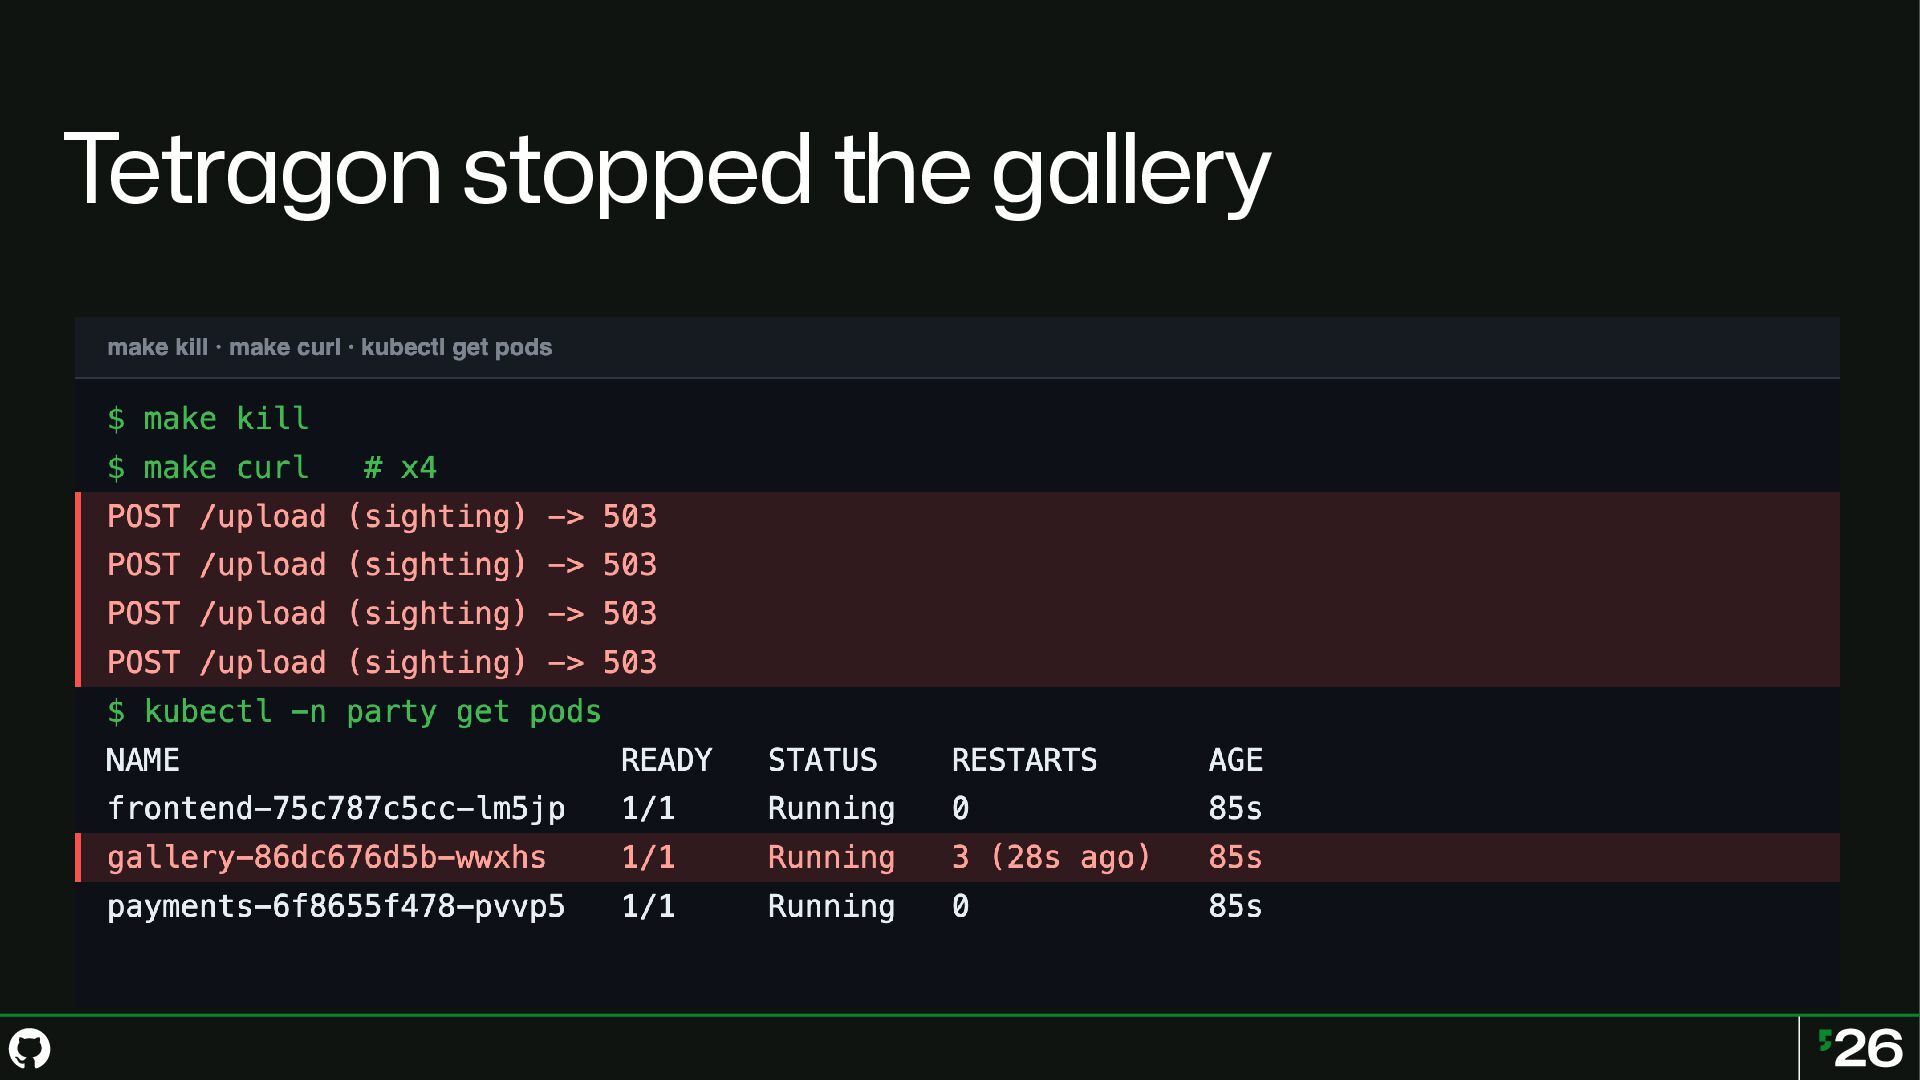
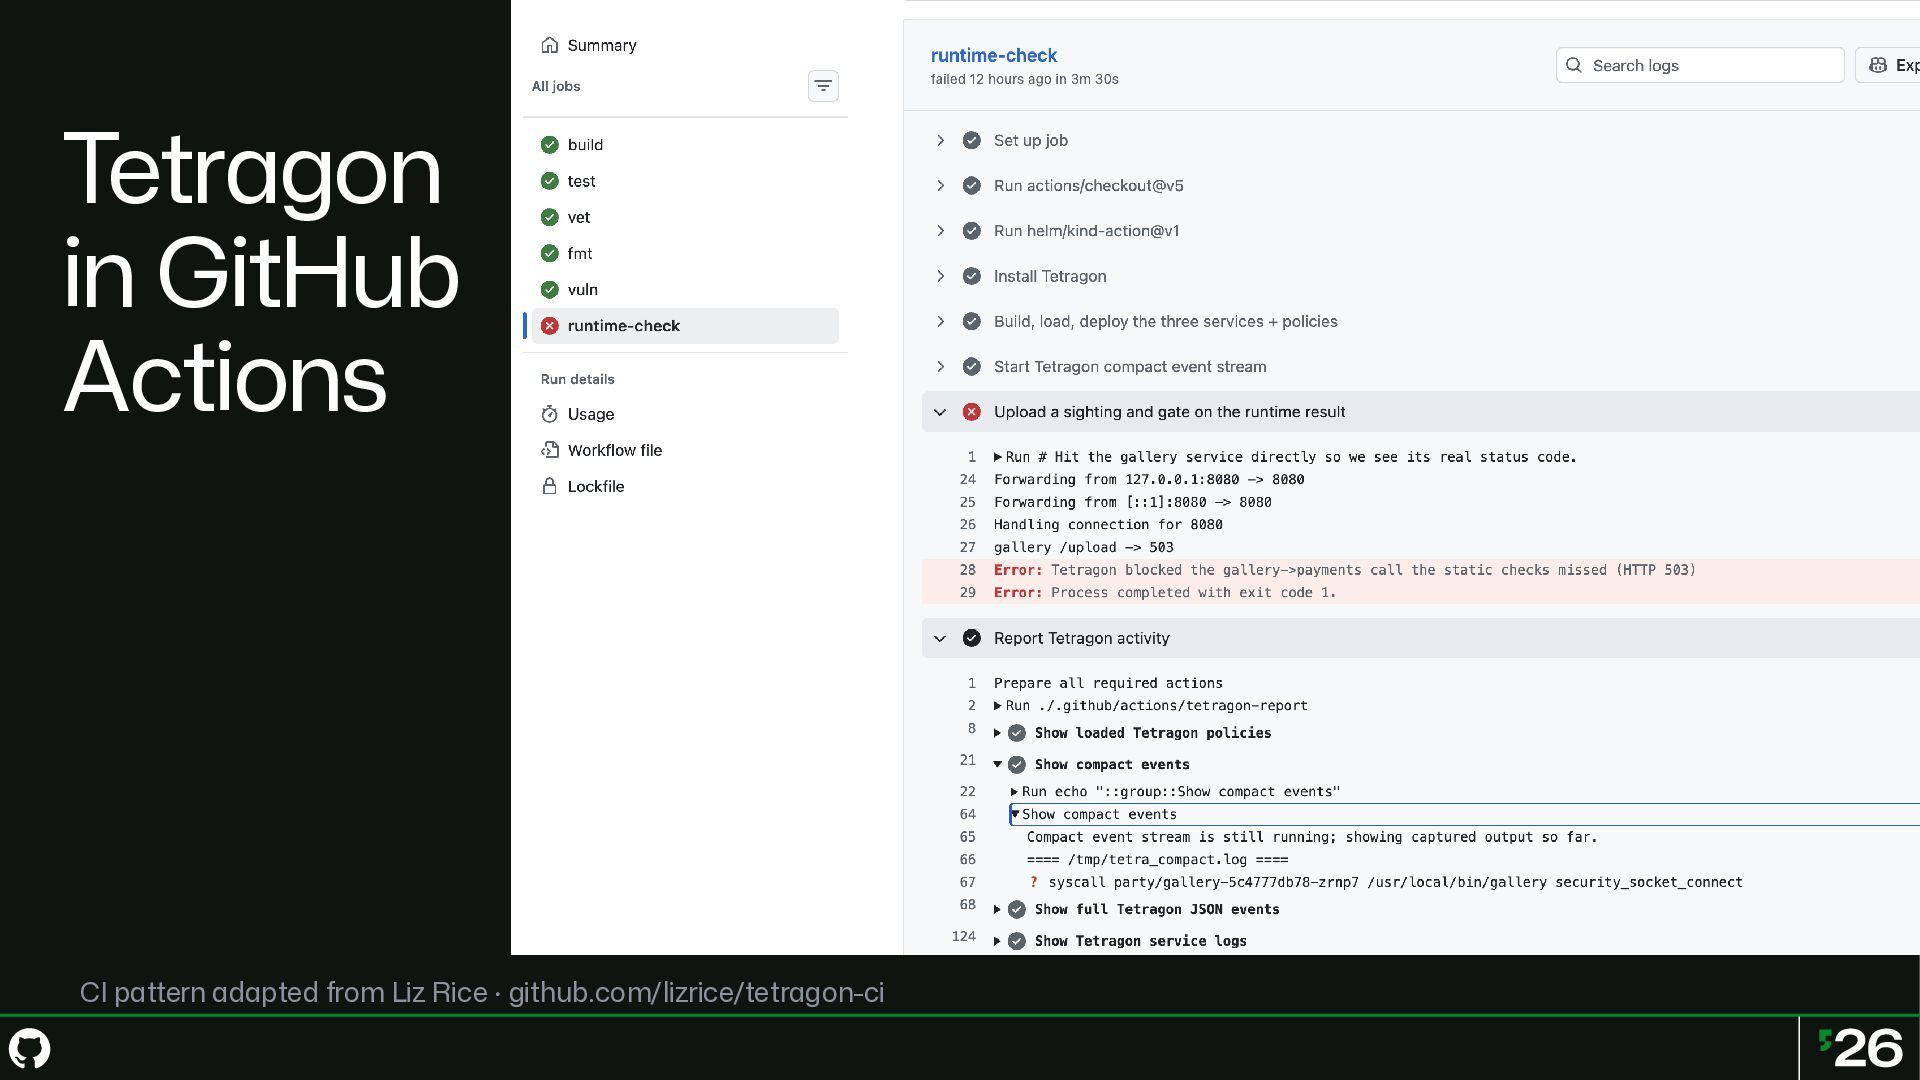
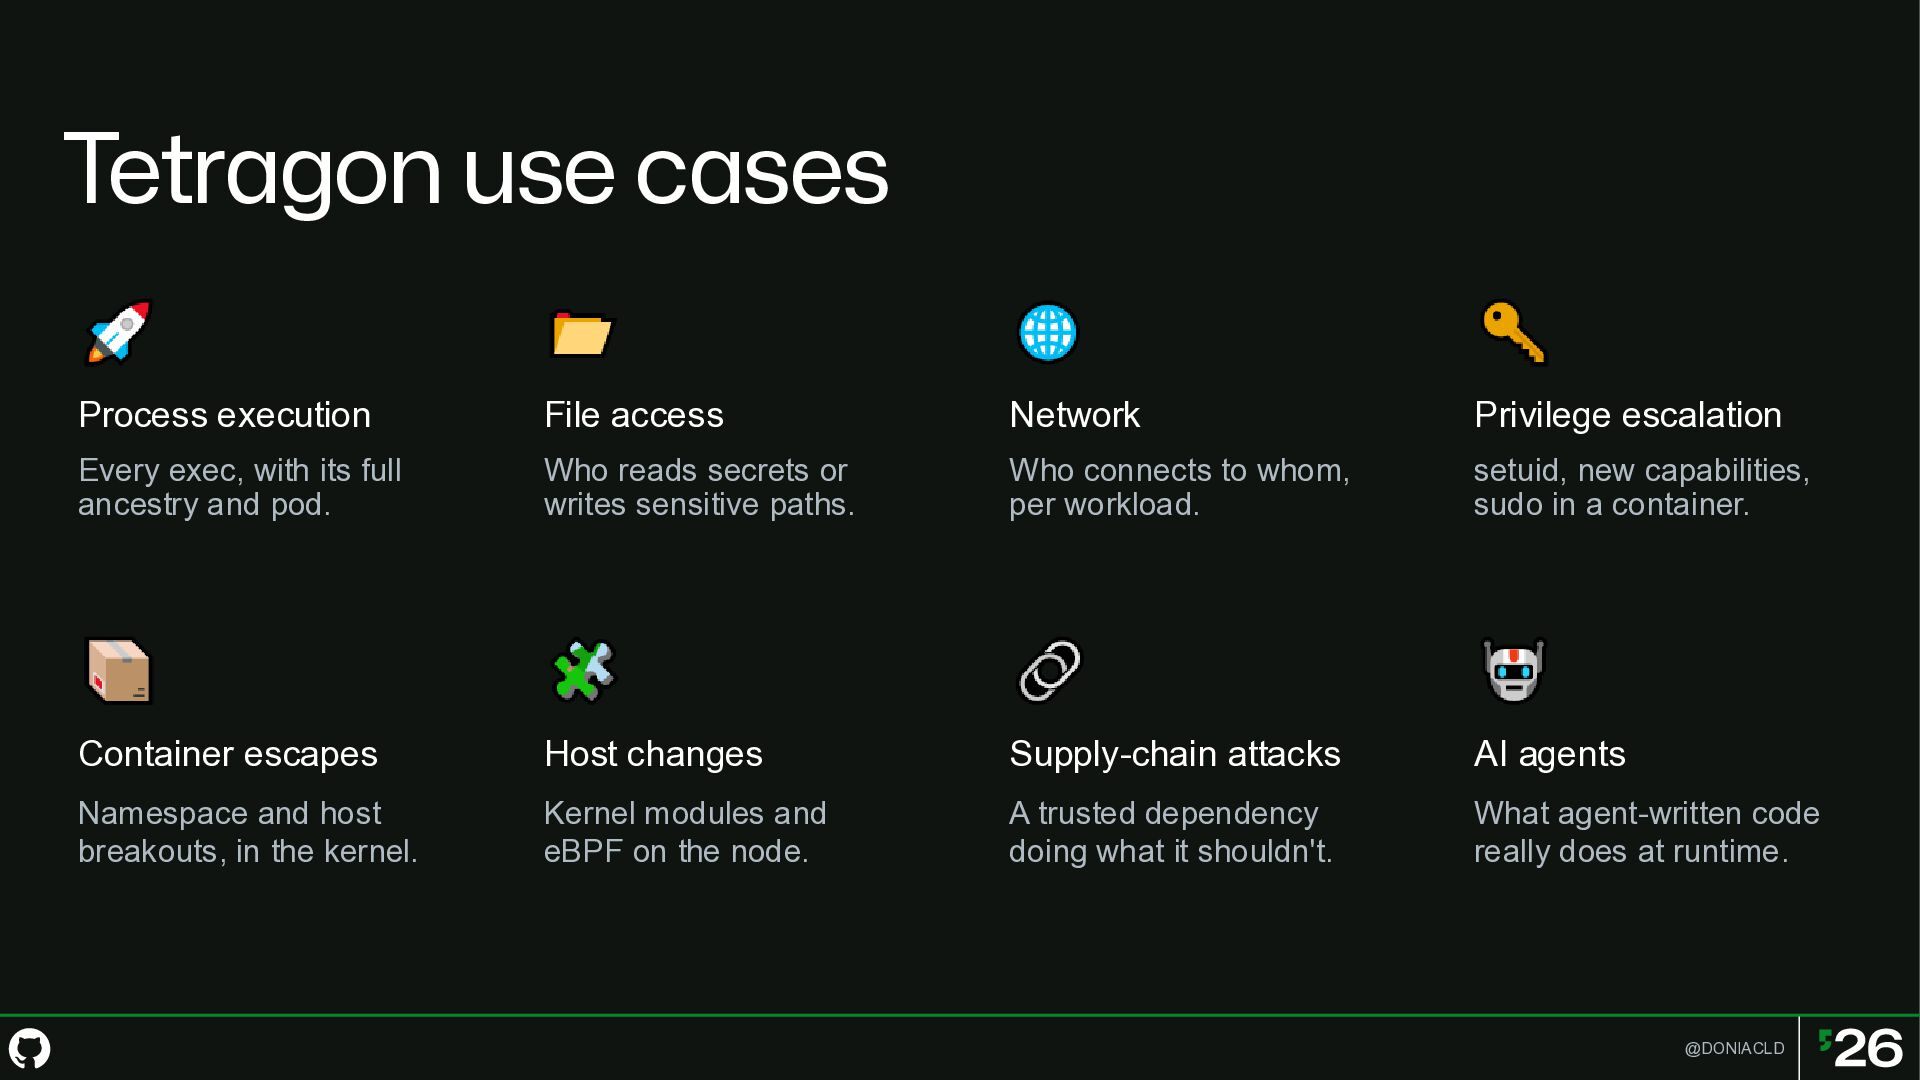
GitHub Copilot and coding agents can now write, commit, and deploy code autonomously, and GitHub gives you a powerful control plane over how that software is created and shipped. But once the code runs in production, its behavior gets much harder to see. Static analysis and PR review can inspect code at rest; neither can observe a running process. This session shows how eBPF-based runtime observability extends that model down into the kernel, giving you visibility into the processes, file access, and network activity of AI-generated workloads as they actually execute. When an agent's code reaches out to an unexpected endpoint or touches a file it shouldn't, you see it. You'll leave with a practical way to close the security loop that AI introduces: not just reviewing what agents write, but watching what their code actually does once it's live.


 doniacld
 helenjbeal
 bermonpainter
 mfonobong
 62gerente
 inesmontani
 samlambert
 signer
 samtorres
 axbom
 aleyda
 bcantrill
 aarron