the phone doesn't ring." Other nights, it changes everything. PRESENTER Eric Baldwin Director, Cyber Incident Response Engineering EVENT CackalackyCon 2026 Career Village Track Doubletree Durham, NC
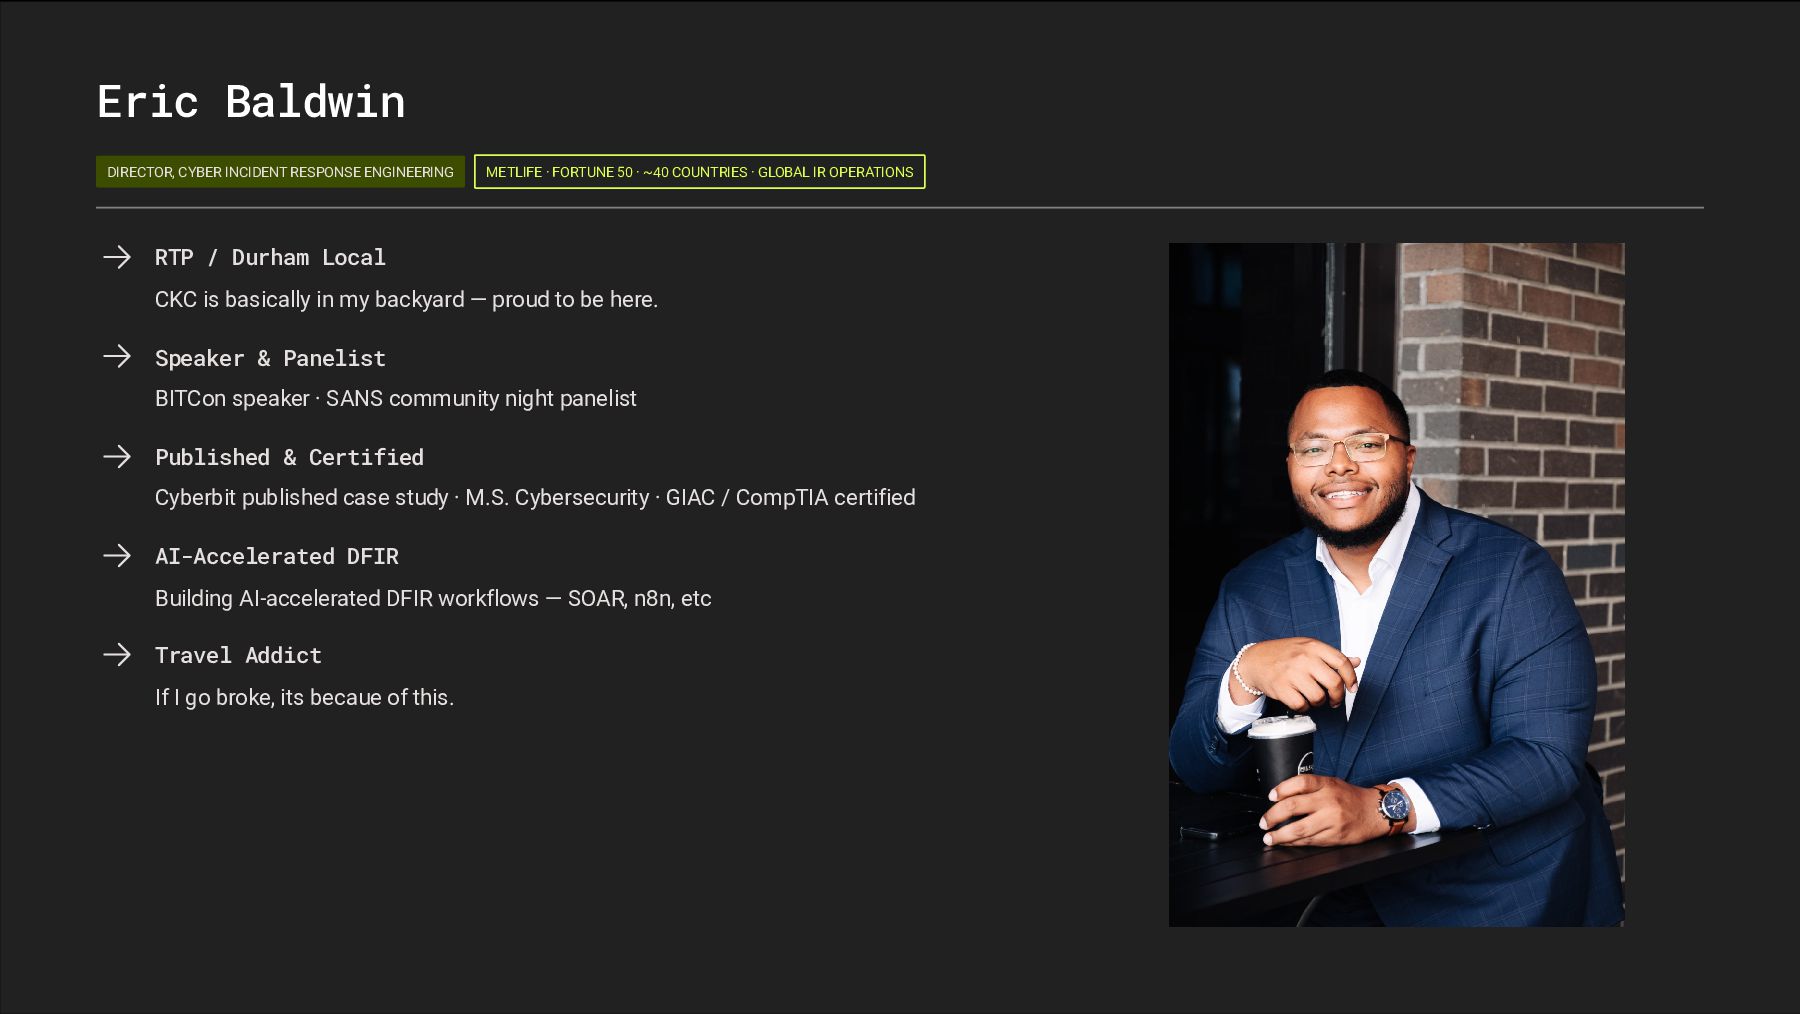
50 · ~40 COUNTRIES · GLOBAL IR OPERATIONS RTP / Durham Local CKC is basically in my backyard — proud to be here. Speaker & Panelist BITCon speaker · SANS community night panelist Published & Certified Cyberbit published case study · M.S. Cybersecurity · GIAC / CompTIA certified AI-Accelerated DFIR Building AI-accelerated DFIR workflows — SOAR, n8n, etc Travel Addict If I go broke, its becaue of this.
A reality check for the curious, the driven, and the slightly unhinged. This session is structured in two acts: first, a cinematic scenario that puts you inside a real incident — then, a clear-eyed breakdown of how to build the skills to belong in that room.
SOC Lead · Direct Message "We have a domain admin login from an unmanaged device. It doesn't look right." You open your laptop back up. You won't be closing it again for three days.
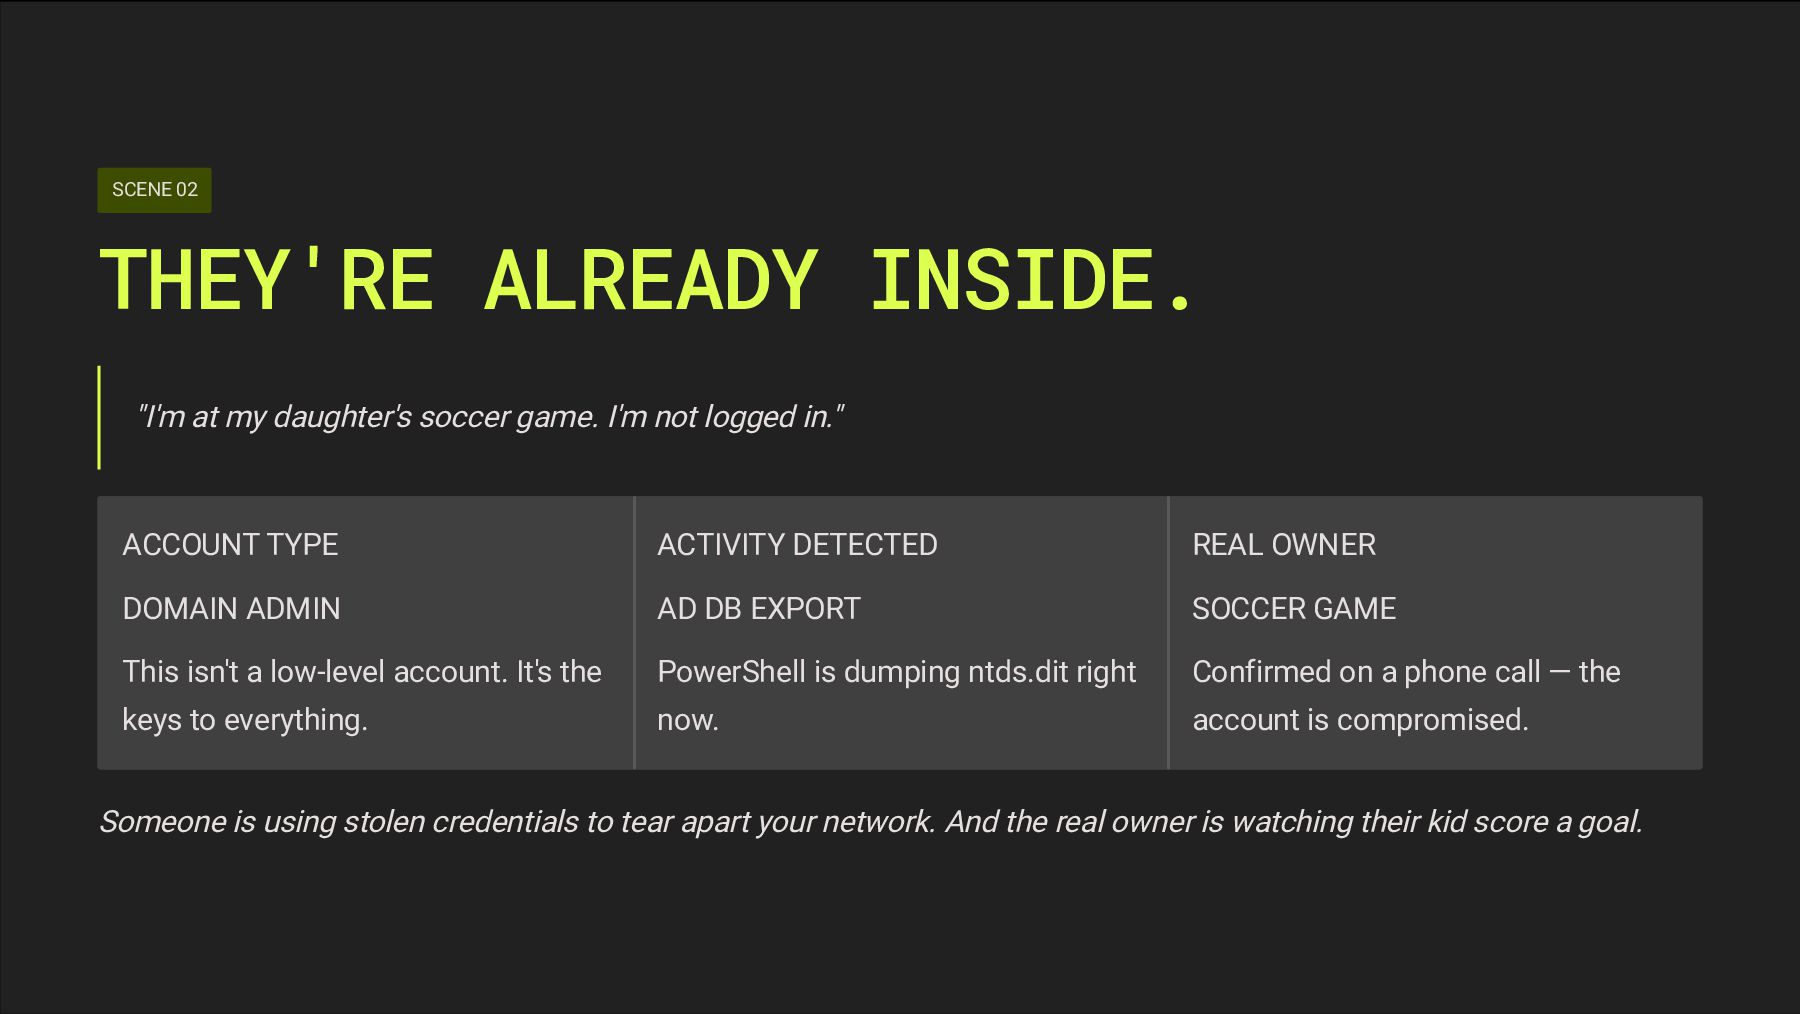
game. I'm not logged in." ACCOUNT TYPE DOMAIN ADMIN This isn't a low-level account. It's the keys to everything. ACTIVITY DETECTED AD DB EXPORT PowerShell is dumping ntds.dit right now. REAL OWNER SOCCER GAME Confirmed on a phone call — the account is compromised. Someone is using stolen credentials to tear apart your network. And the real owner is watching their kid score a goal.
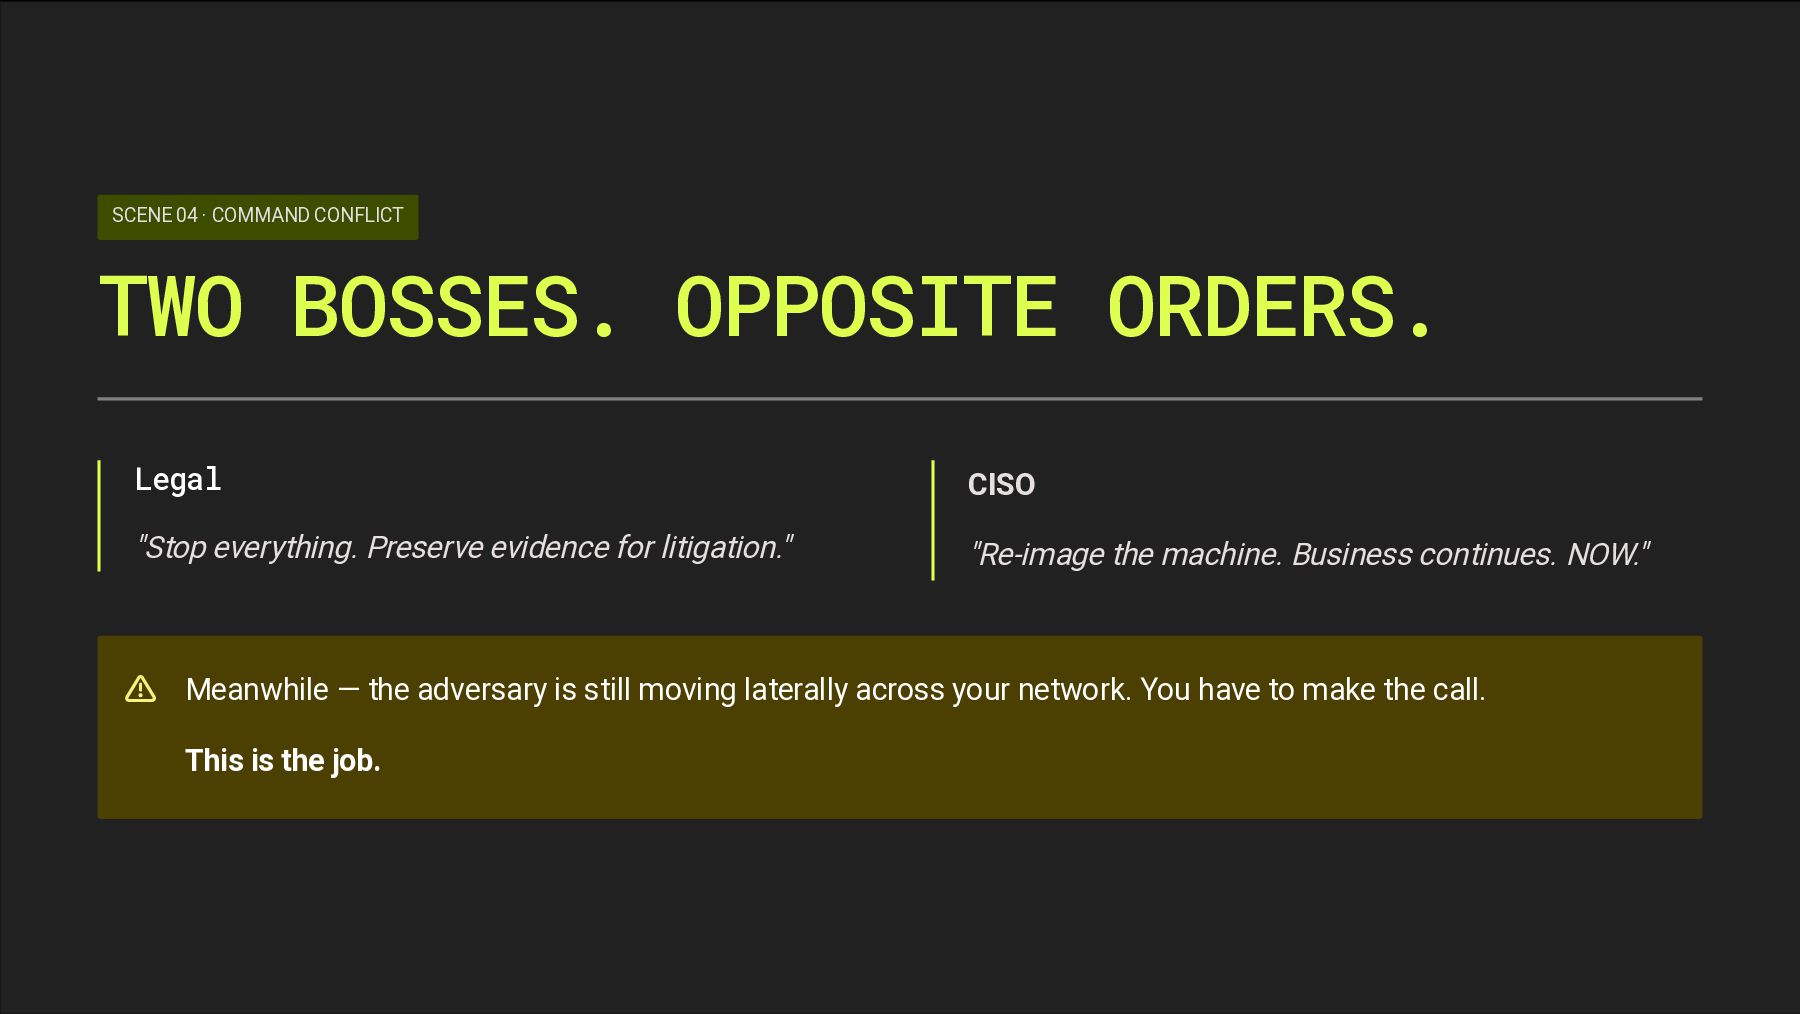
"Stop everything. Preserve evidence for litigation." CISO "Re-image the machine. Business continues. NOW." Meanwhile — the adversary is still moving laterally across your network. You have to make the call. This is the job.
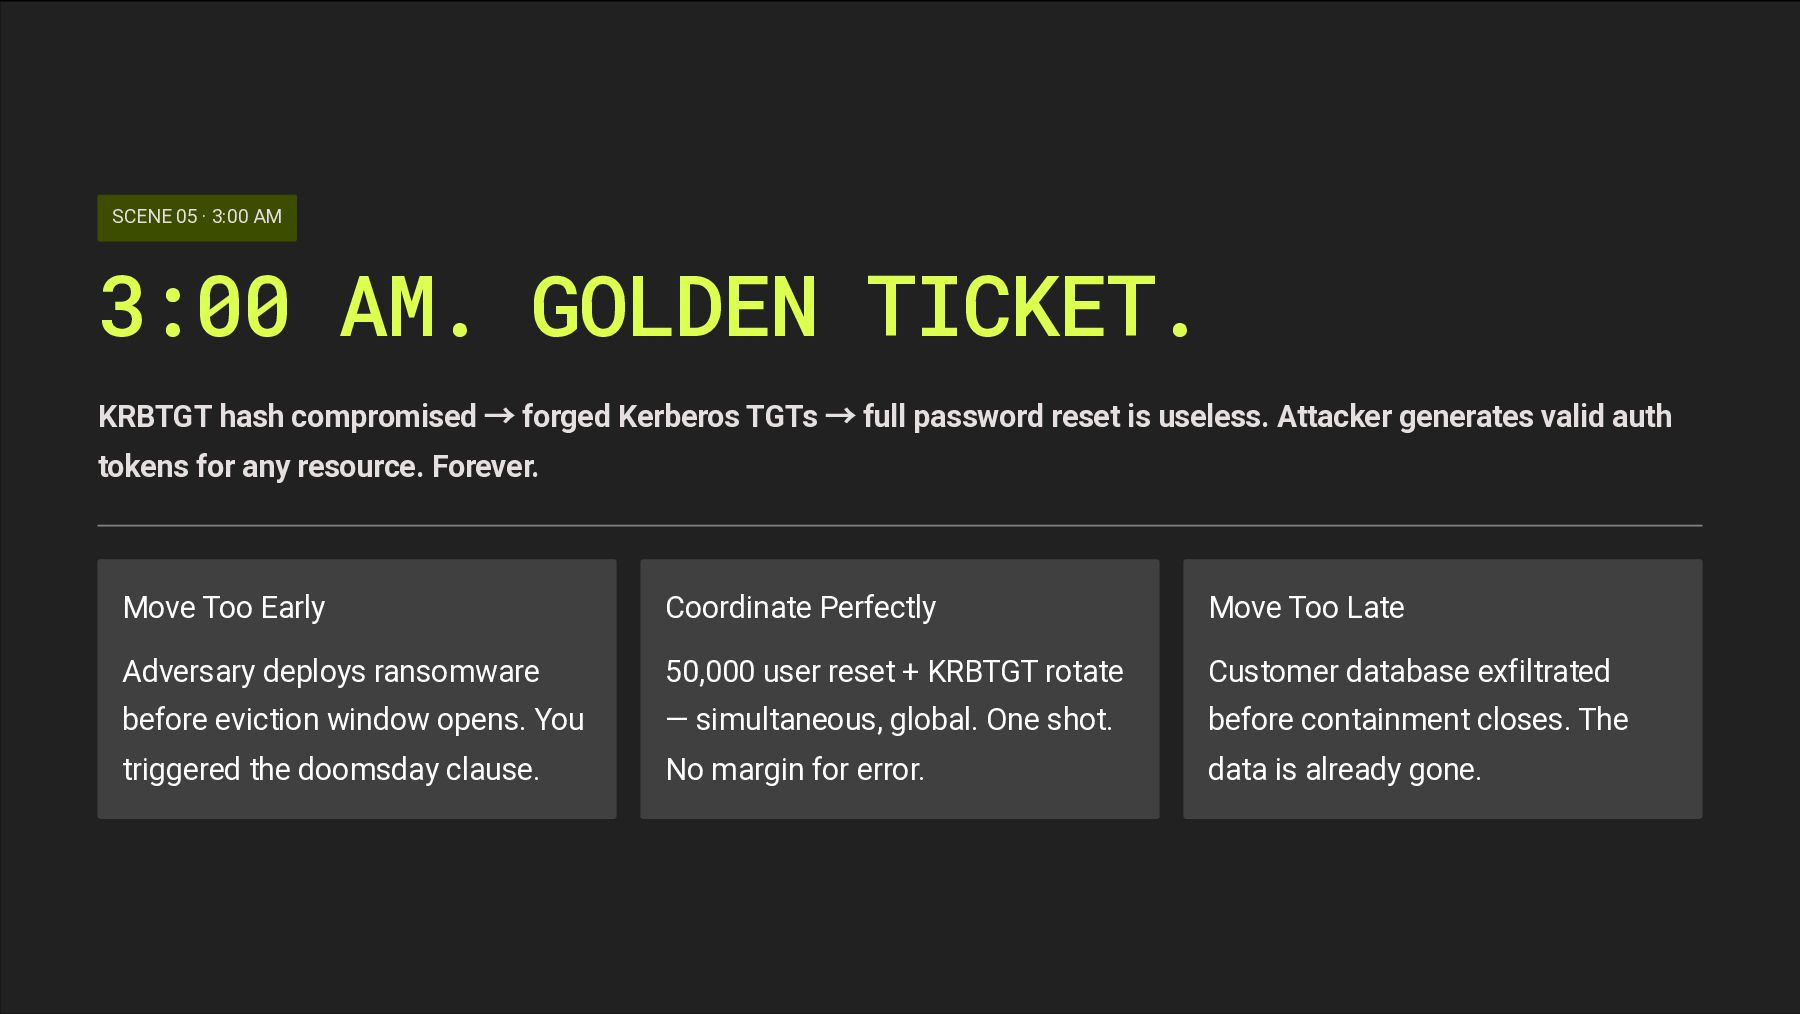
hash compromised → forged Kerberos TGTs → full password reset is useless. Attacker generates valid auth tokens for any resource. Forever. Move Too Early Adversary deploys ransomware before eviction window opens. You triggered the doomsday clause. Coordinate Perfectly 50,000 user reset + KRBTGT rotate — simultaneous, global. One shot. No margin for error. Move Too Late Customer database exfiltrated before containment closes. The data is already gone.
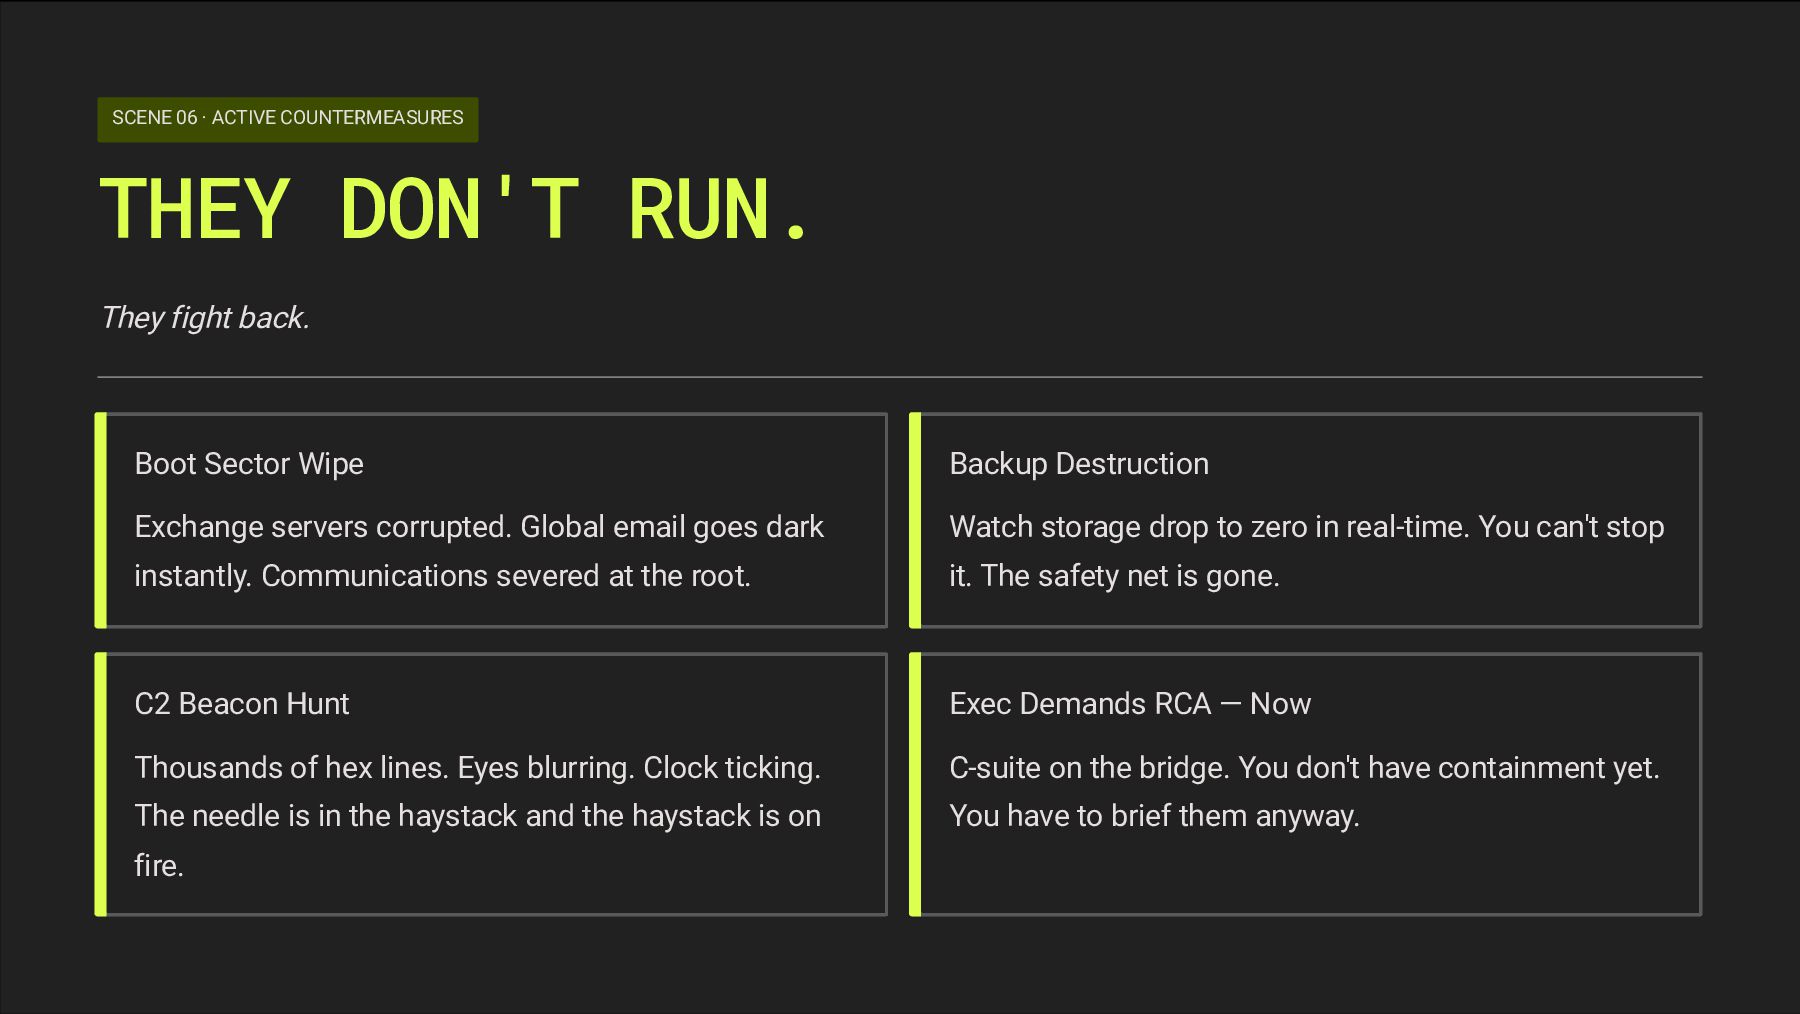
back. Boot Sector Wipe Exchange servers corrupted. Global email goes dark instantly. Communications severed at the root. Backup Destruction Watch storage drop to zero in real-time. You can't stop it. The safety net is gone. C2 Beacon Hunt Thousands of hex lines. Eyes blurring. Clock ticking. The needle is in the haystack and the haystack is on fire. Exec Demands RCA — Now C-suite on the bridge. You don't have containment yet. You have to brief them anyway.
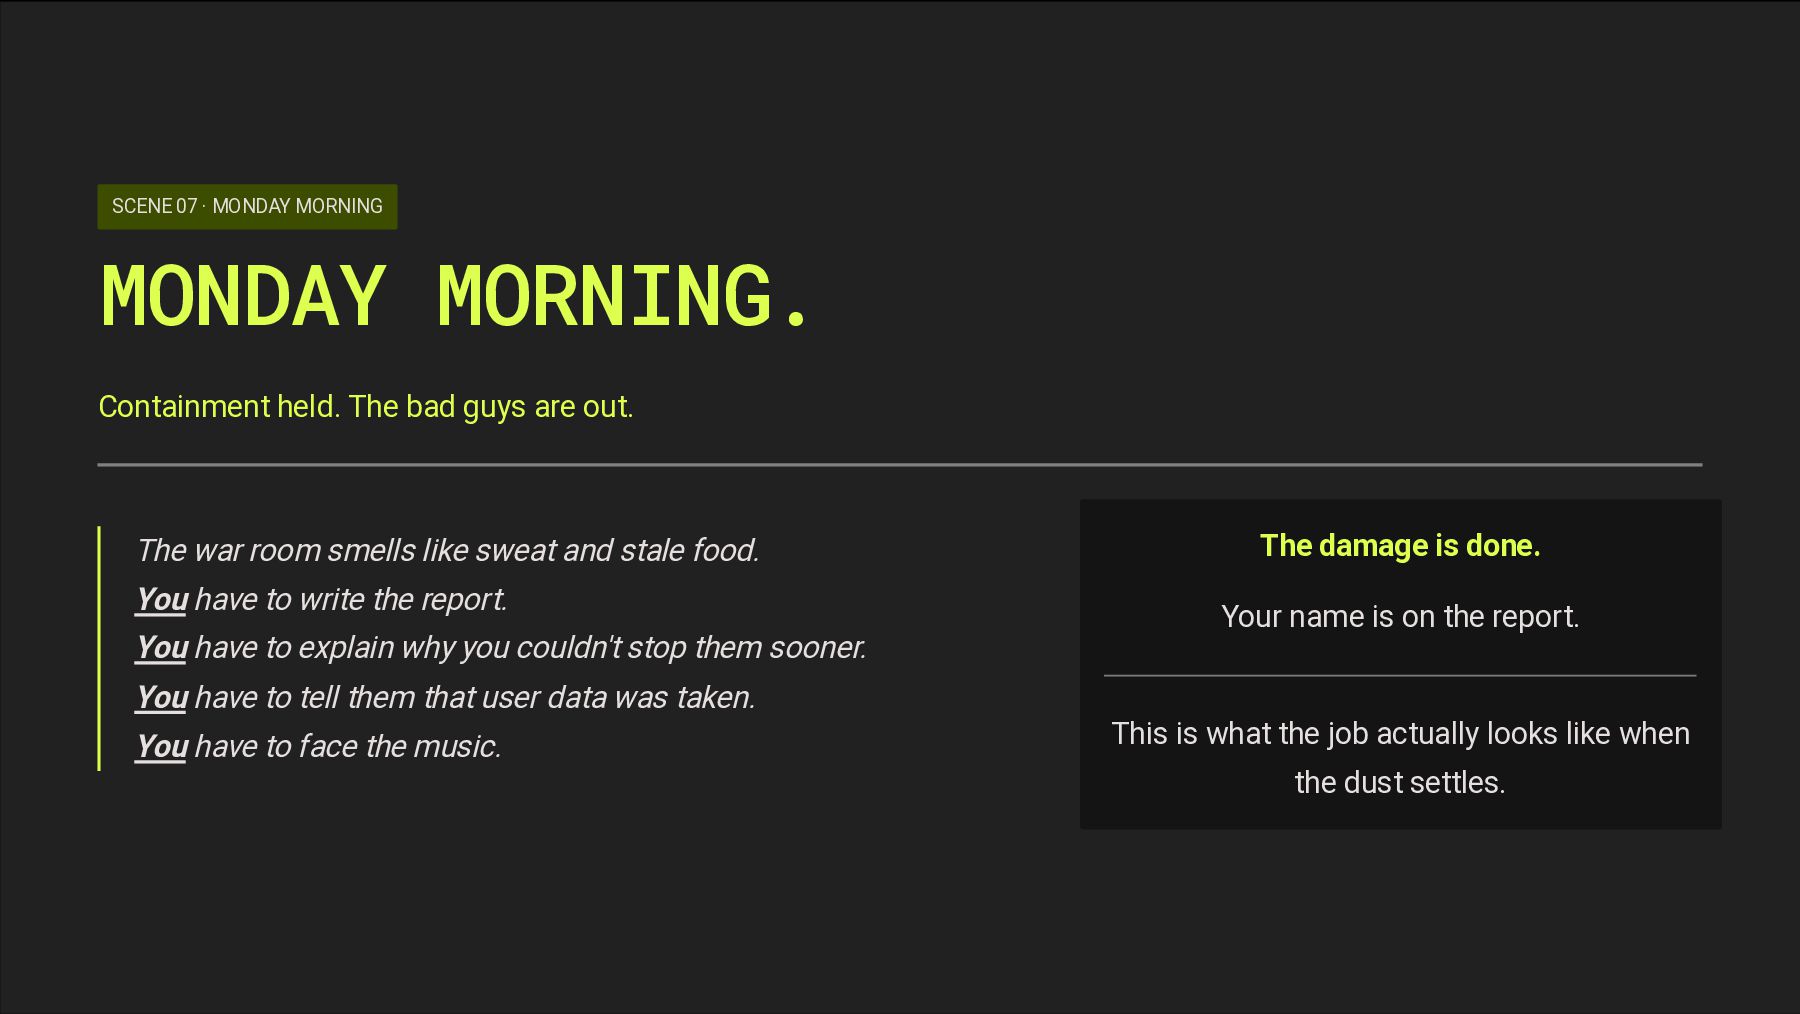
bad guys are out. The war room smells like sweat and stale food. You have to write the report. You have to explain why you couldn't stop them sooner. You have to tell them that user data was taken. You have to face the music. The damage is done. Your name is on the report. This is what the job actually looks like when the dust settles.
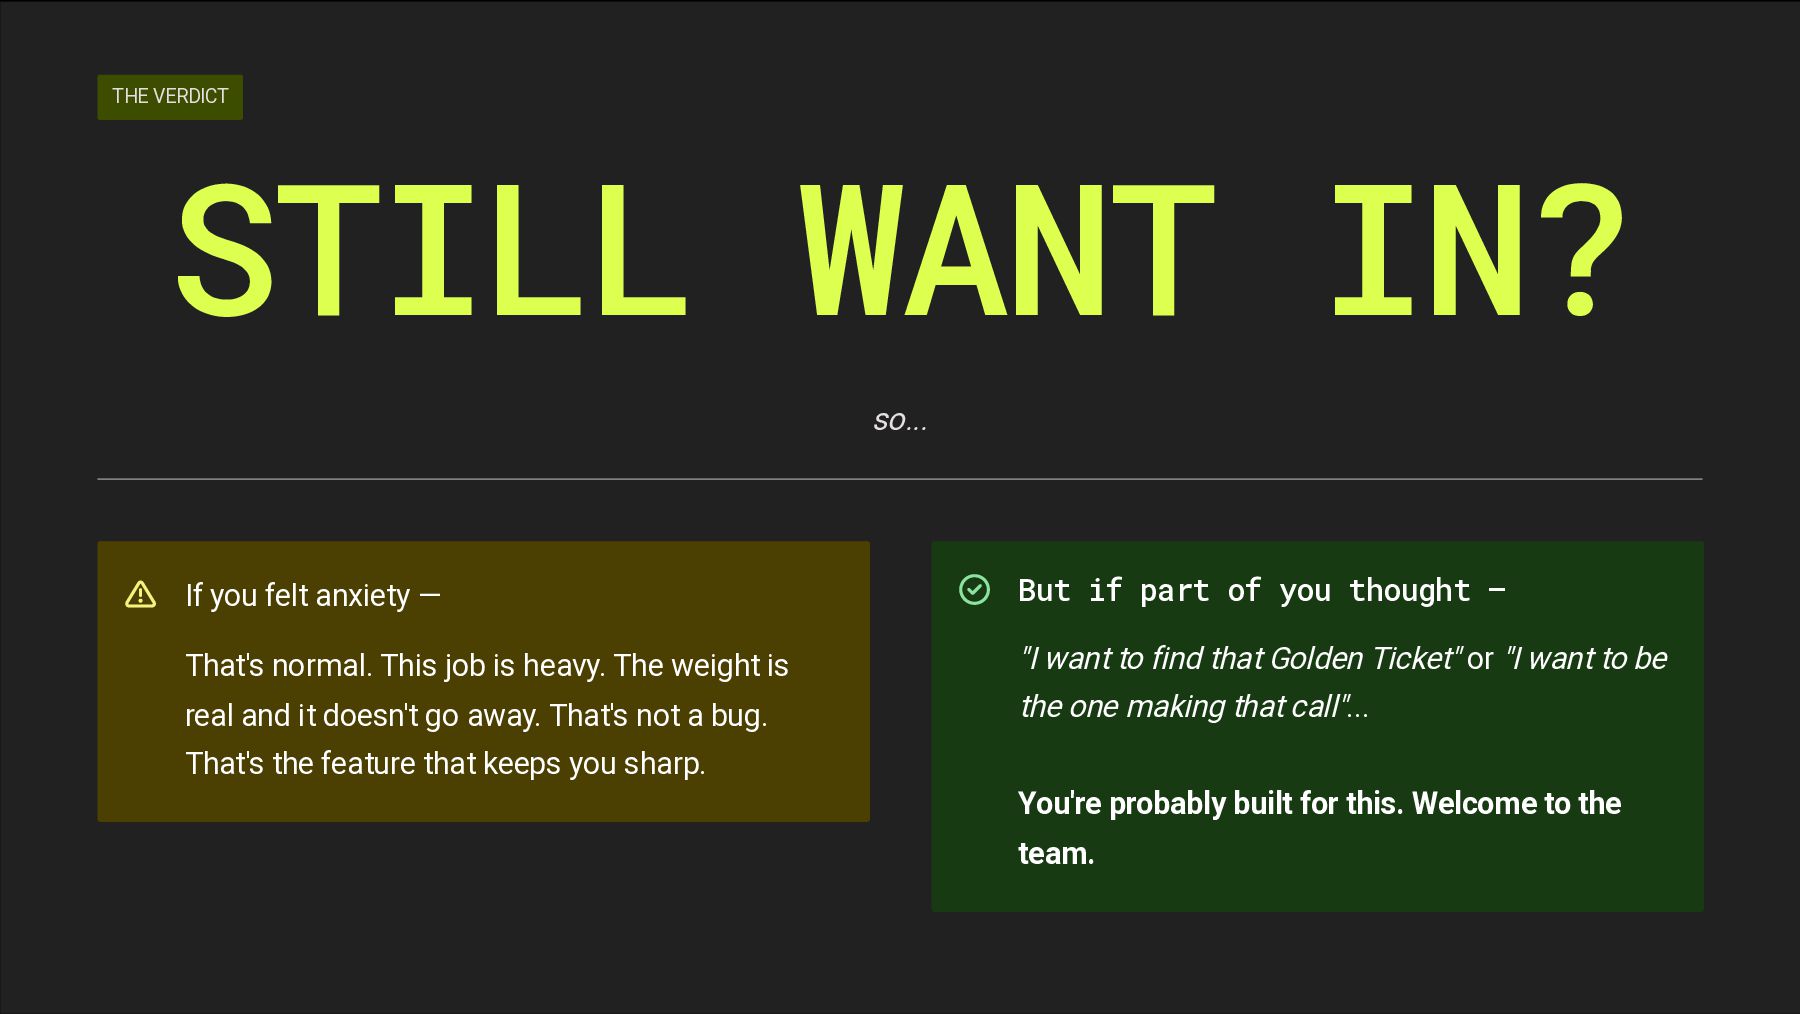
— That's normal. This job is heavy. The weight is real and it doesn't go away. That's not a bug. That's the feature that keeps you sharp. But if part of you thought — "I want to find that Golden Ticket" or "I want to be the one making that call"... You're probably built for this. Welcome to the team.
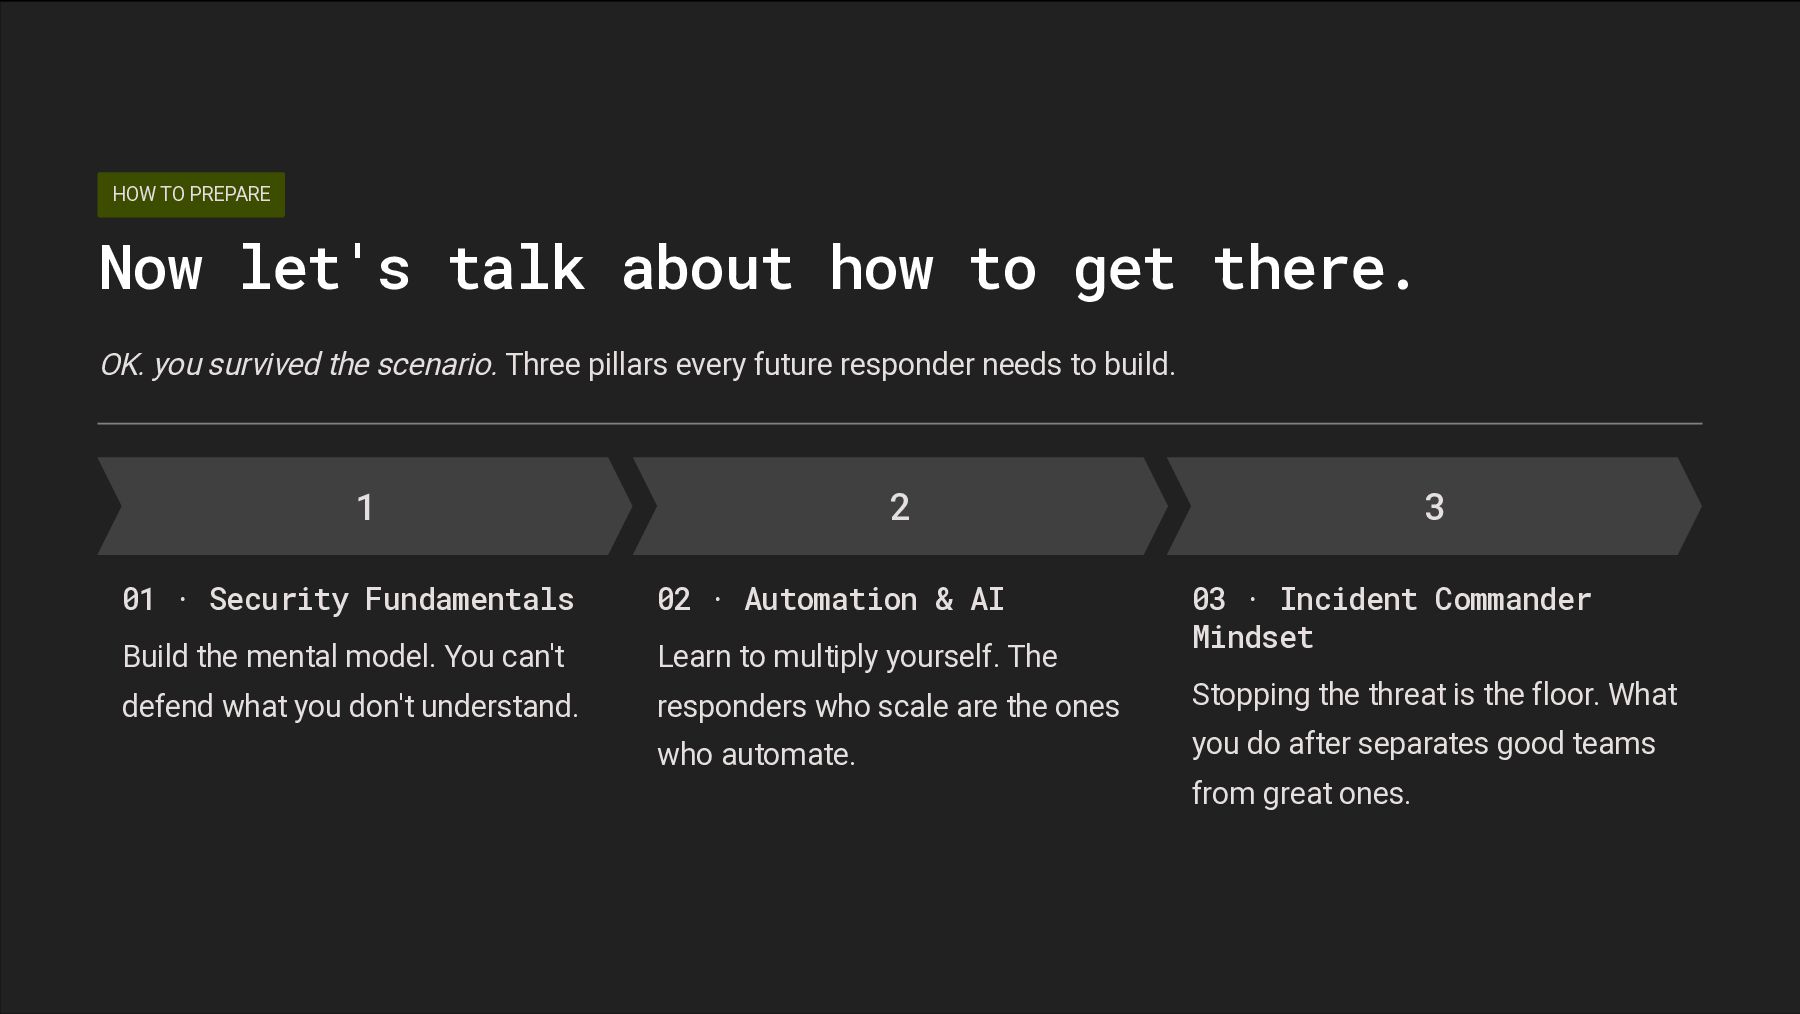
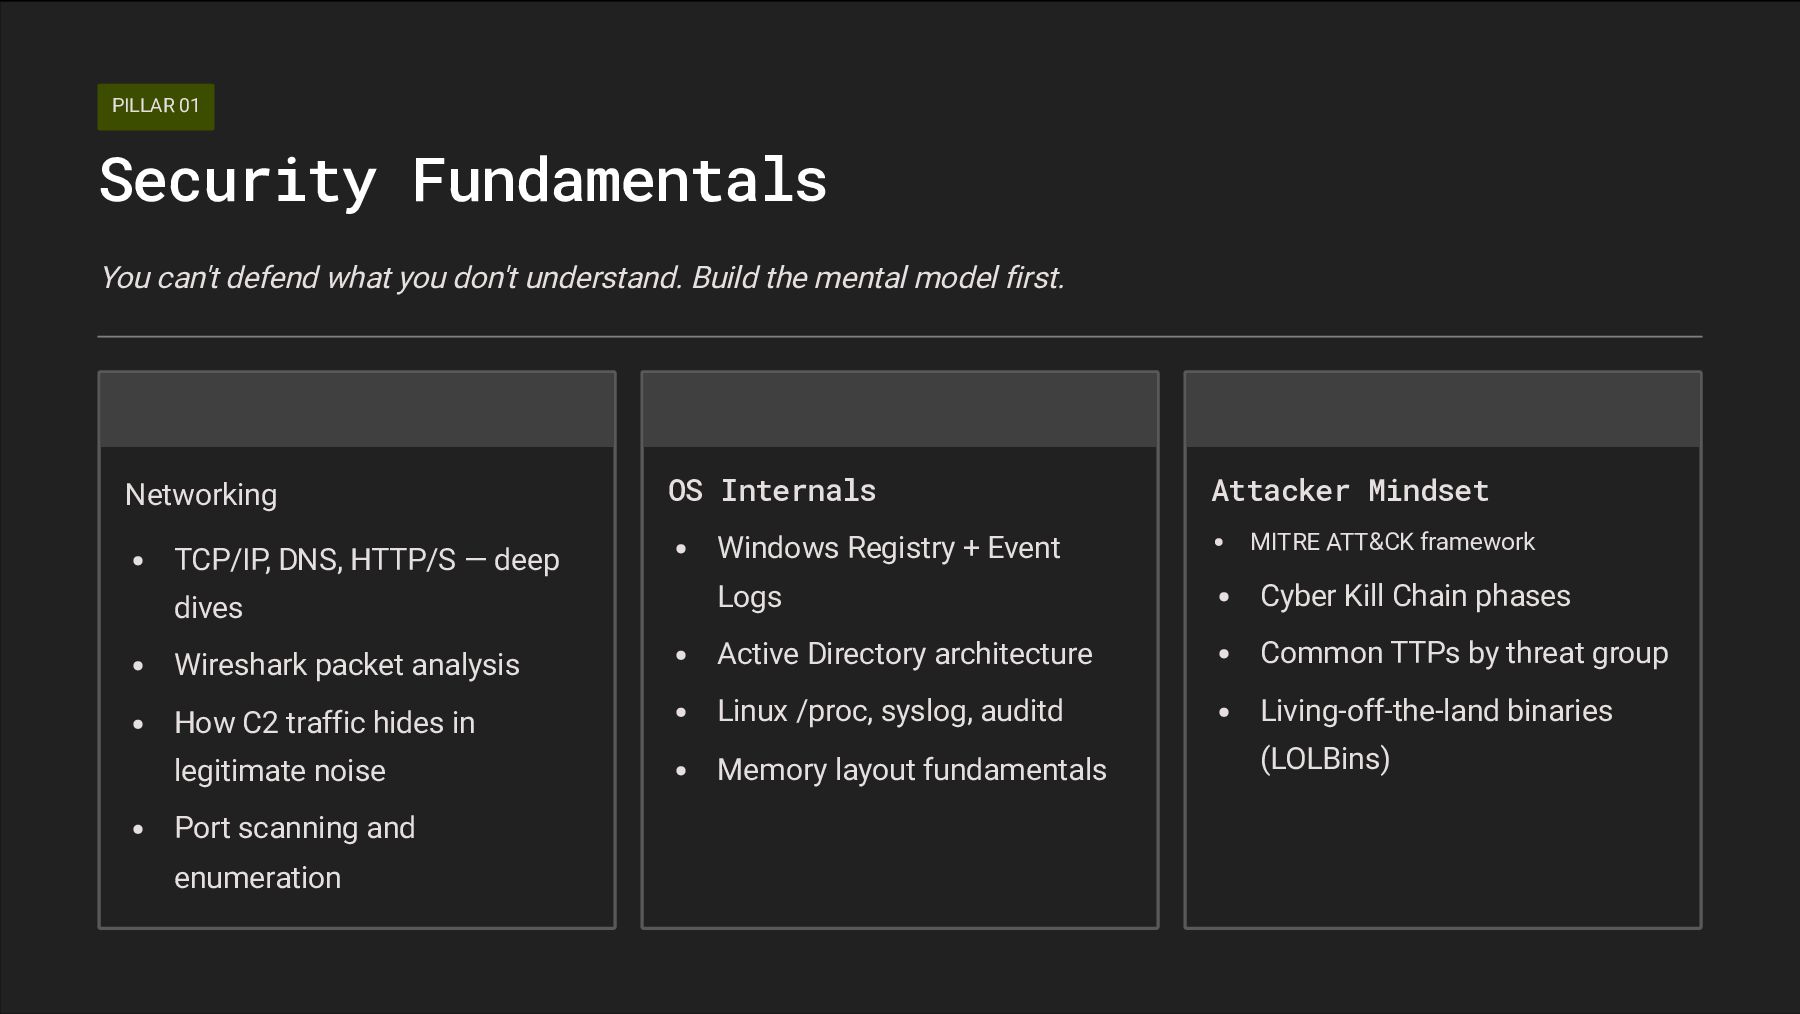
there. OK. you survived the scenario. Three pillars every future responder needs to build. 1 01 · Security Fundamentals Build the mental model. You can't defend what you don't understand. 2 02 · Automation & AI Learn to multiply yourself. The responders who scale are the ones who automate. 3 03 · Incident Commander Mindset Stopping the threat is the floor. What you do after separates good teams from great ones.
understand. Build the mental model first. Networking TCP/IP, DNS, HTTP/S — deep dives Wireshark packet analysis How C2 traffic hides in legitimate noise Port scanning and enumeration OS Internals Windows Registry + Event Logs Active Directory architecture Linux /proc, syslog, auditd Memory layout fundamentals Attacker Mindset MITRE ATT&CK framework Cyber Kill Chain phases Common TTPs by threat group Living-off-the-land binaries (LOLBins)
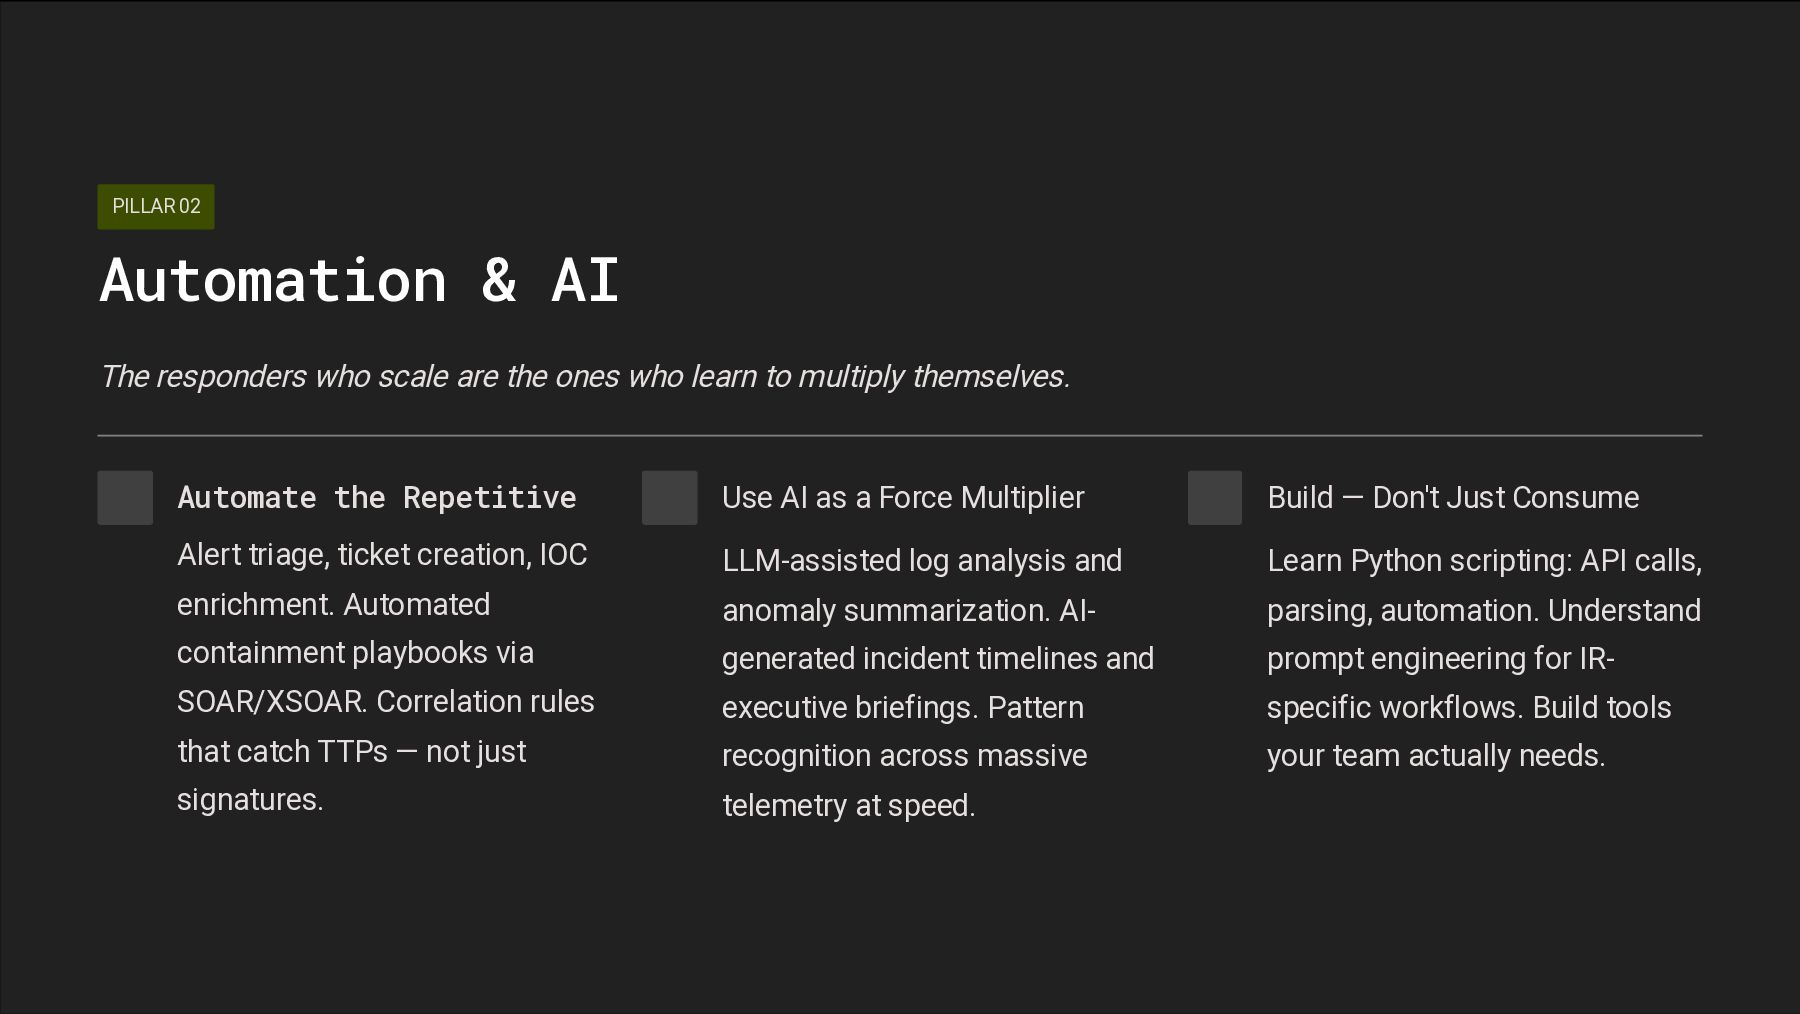
the ones who learn to multiply themselves. Automate the Repetitive Alert triage, ticket creation, IOC enrichment. Automated containment playbooks via SOAR/XSOAR. Correlation rules that catch TTPs — not just signatures. Use AI as a Force Multiplier LLM-assisted log analysis and anomaly summarization. AI- generated incident timelines and executive briefings. Pattern recognition across massive telemetry at speed. Build — Don't Just Consume Learn Python scripting: API calls, parsing, automation. Understand prompt engineering for IR- specific workflows. Build tools your team actually needs.
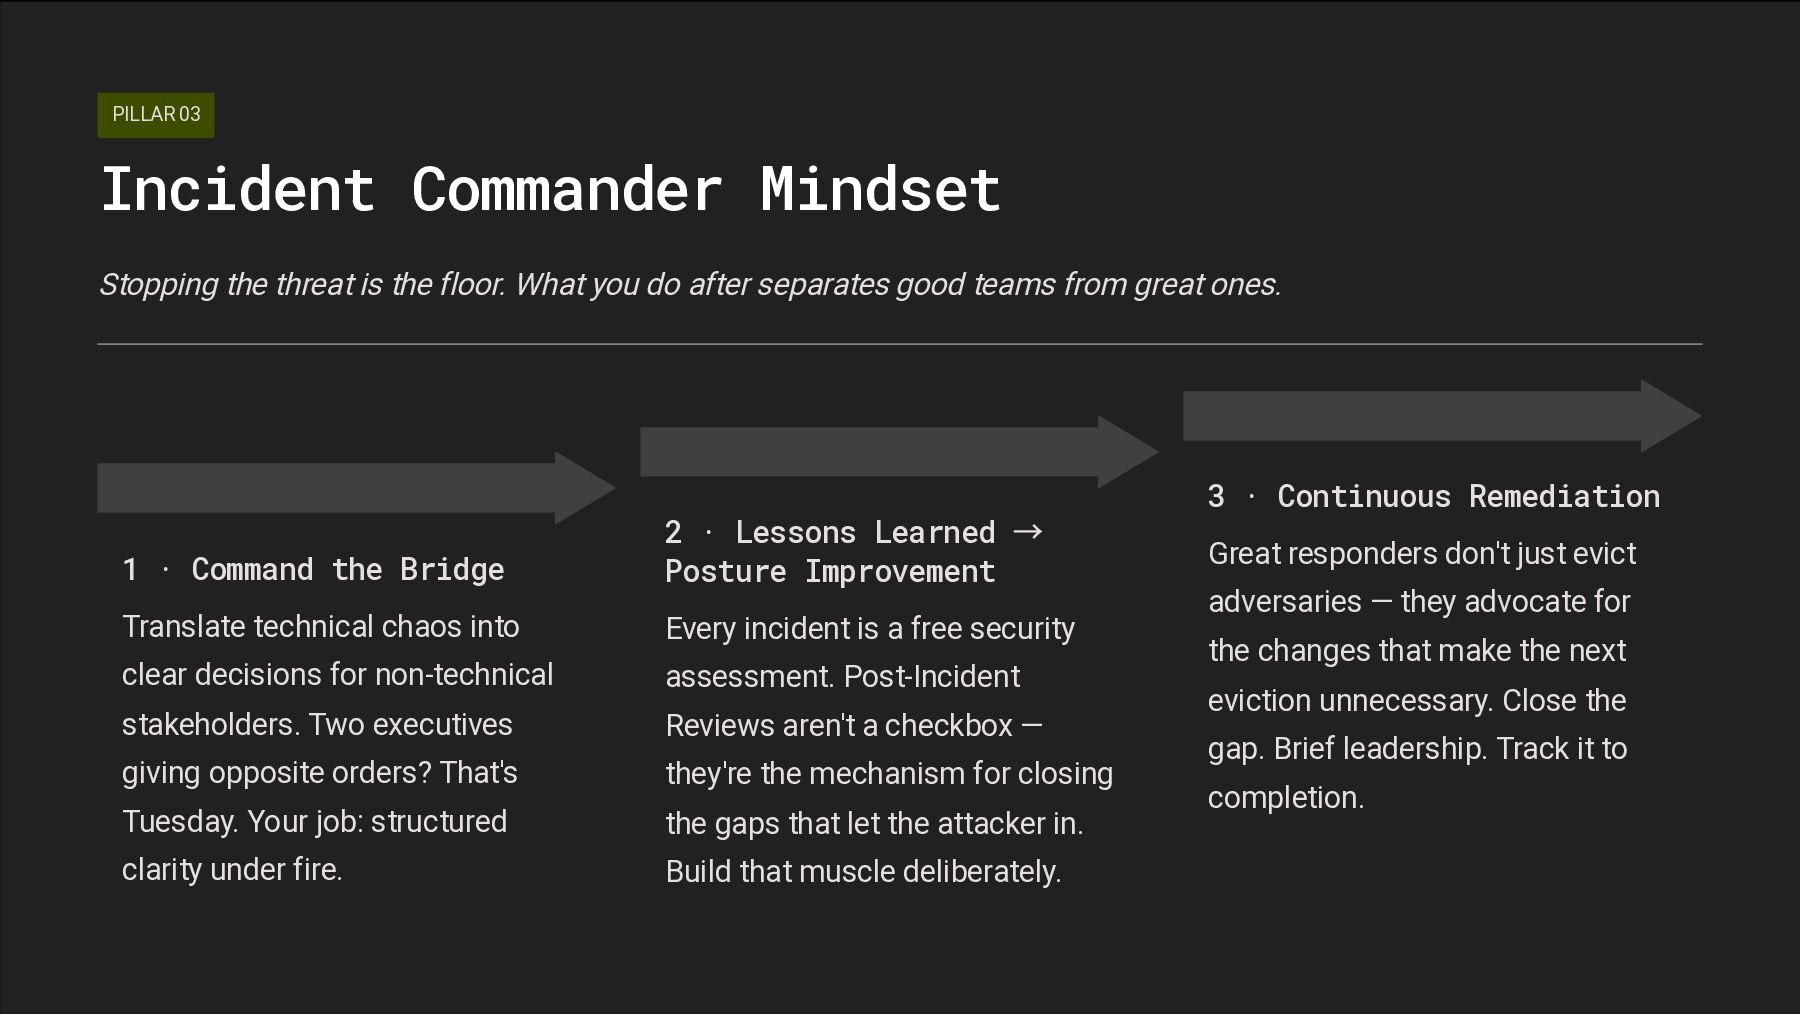
floor. What you do after separates good teams from great ones. 1 · Command the Bridge Translate technical chaos into clear decisions for non-technical stakeholders. Two executives giving opposite orders? That's Tuesday. Your job: structured clarity under fire. 2 · Lessons Learned → Posture Improvement Every incident is a free security assessment. Post-Incident Reviews aren't a checkbox — they're the mechanism for closing the gaps that let the attacker in. Build that muscle deliberately. 3 · Continuous Remediation Great responders don't just evict adversaries — they advocate for the changes that make the next eviction unnecessary. Close the gap. Brief leadership. Track it to completion.
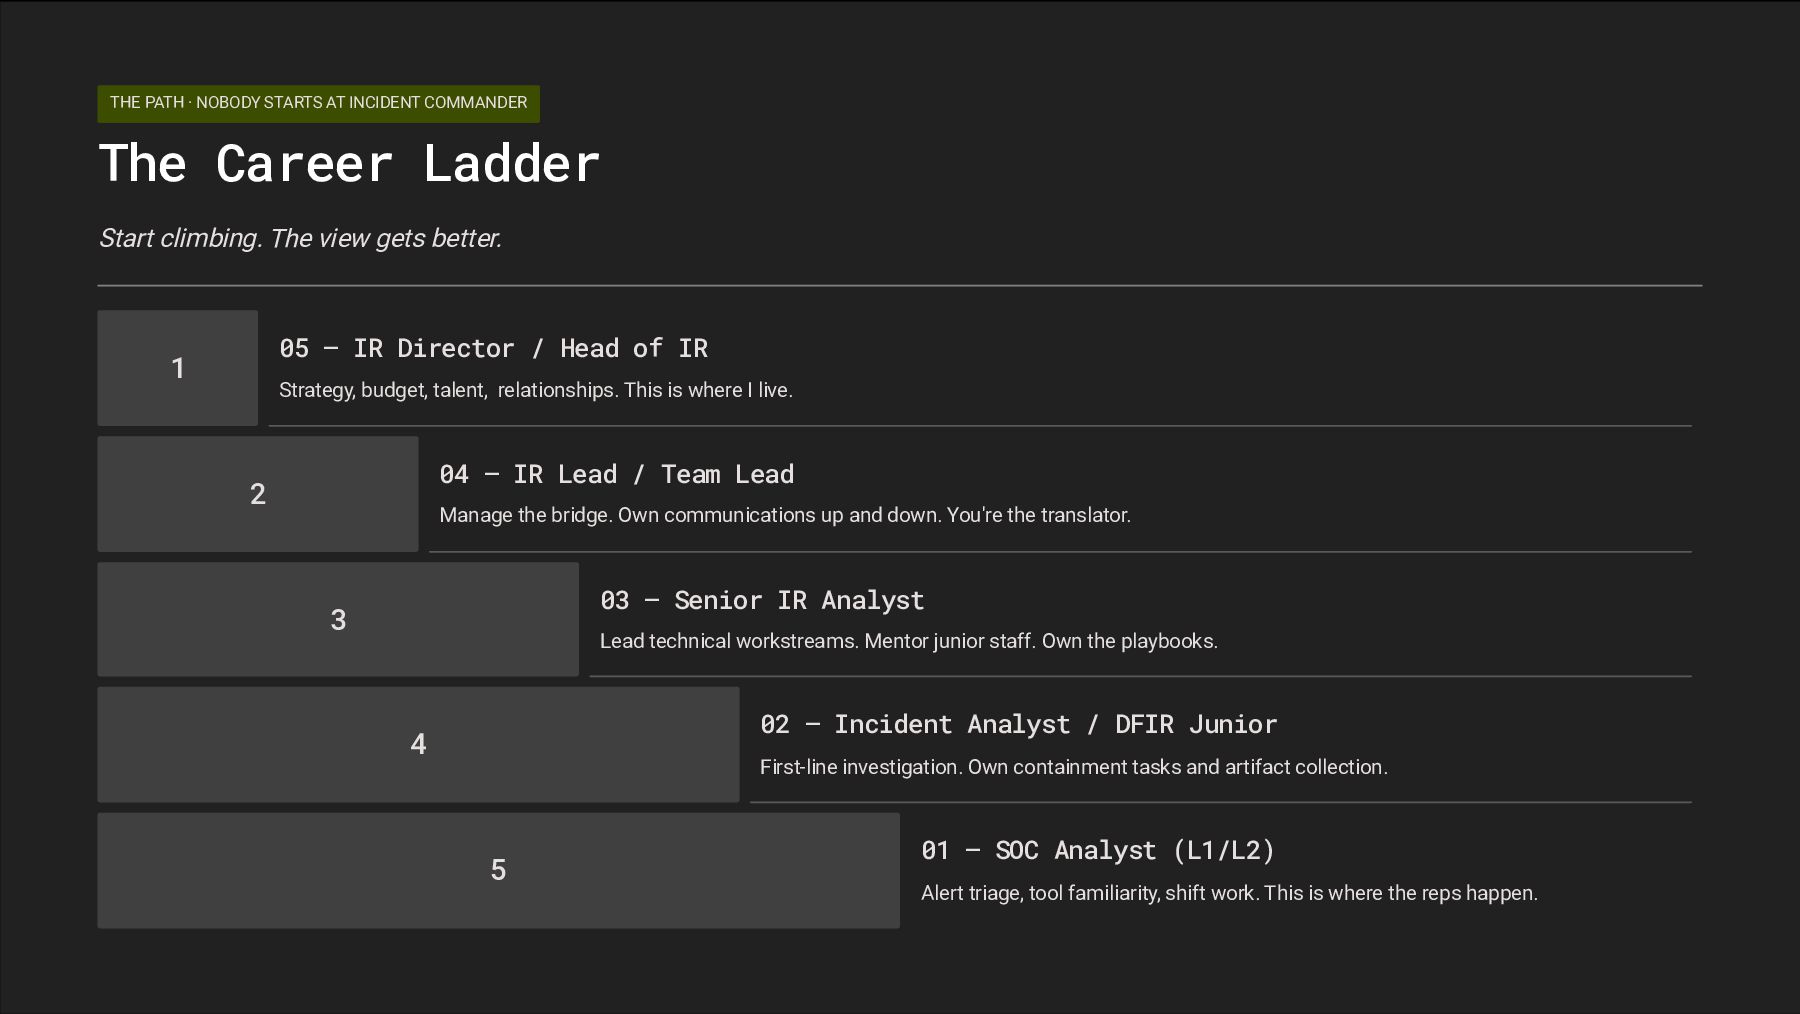
Ladder Start climbing. The view gets better. 1 05 — IR Director / Head of IR Strategy, budget, talent, relationships. This is where I live. 2 04 — IR Lead / Team Lead Manage the bridge. Own communications up and down. You're the translator. 3 03 — Senior IR Analyst Lead technical workstreams. Mentor junior staff. Own the playbooks. 4 02 — Incident Analyst / DFIR Junior First-line investigation. Own containment tasks and artifact collection. 5 01 — SOC Analyst (L1/L2) Alert triage, tool familiarity, shift work. This is where the reps happen.
toward the fire. It's not about titles or badges. It's about staring at a screen at 4AM, outsmarting a human being on the other side of the world who wants to destroy what you're protecting. If you're ready — welcome to the team. If not, see you when you get here. eric baldwin · director, incident response ·https://www.linkedin.com/in/ericbaldwinjr/ find me at the con — questions welcome


 bgpat
 takonda
 codmoninc
 teamlab
 endonanana
 shuta13
 camiha
 tetsuya28
 shumei_ito
 kizawa2020
 yahonda
 yu23ki14
 tmiket
 katiecoart
 chriscoyier
 baasie
 jonrohan
 nmsamuel
 portentint
 swwweet
 ammeep
 reverentgeek
 jlugia
 coloredviolet