Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Architecting Applications for HIPAA Compliance
Search
Frank Macreery
May 21, 2015
Technology
220
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Architecting Applications for HIPAA Compliance
Originally presented at "Cloud Computing & Healthcare with AWS."
Frank Macreery
May 21, 2015
More Decks by Frank Macreery
See All by Frank Macreery
Docker for Ruby Developers
fancyremarker
3
670
Aptible + TelePharm: HIPAA for Startups
fancyremarker
0
1.4k
Containerization and Compliance
fancyremarker
0
550
HIPAA Dev Ops: Architecting Layers of Responsibility
fancyremarker
0
84
Garner: Anatomy of a Ruby Gem
fancyremarker
0
350
Other Decks in Technology
See All in Technology
Optunaの最新リリースv5.0について
pfn
PRO
0
120
⾮構造化データを価値に変える AI エージェント基盤とその組織
ivry_presentationmaterials
0
190
SAENM ~Jupyterで残すPoCの試行錯誤、未来の自分と仲間を助ける記録!~
terapyon
0
110
go-sqletch
moznion
0
140
USB PDを使ってスマホを労わりたい
raspython3
0
180
M5Stackで作る BLEマウス GPSログの世界
tomokusaba
0
420
Running Kotlin + Quarkus with Lambda
nealle
1
3.7k
AI駆動で「他アプリの音を加工できる」アプリを作った
satomasahiro2005
0
150
"優秀な誰か"の下位互換にならないために
yut0naga1_fa
1
1.8k
パッチ更新でterraform initが落ちた日
grimoh
1
140
WasmをRustにする
sansantech
PRO
0
250
AI時代のPRレビューにどう向き合うか?
kairim0
1
240
Featured
See All Featured
So, you think you're a good person
axbom
PRO
2
2.2k
How To Stay Up To Date on Web Technology
chriscoyier
790
250k
Rails Girls Zürich Keynote
gr2m
96
14k
The Mindset for Success: Future Career Progression
greggifford
PRO
0
540
The MySQL Ecosystem @ GitHub 2015
samlambert
251
13k
Designing Dashboards & Data Visualisations in Web Apps
destraynor
232
55k
Paper Plane
katiecoart
PRO
5
54k
Lightning talk: Run Django tests with GitHub Actions
sabderemane
0
300
Intergalactic Javascript Robots from Outer Space
tanoku
273
28k
The Straight Up "How To Draw Better" Workshop
denniskardys
239
140k
What's in a price? How to price your products and services
michaelherold
247
13k
jQuery: Nuts, Bolts and Bling
dougneiner
66
8.6k
Transcript
Architecting Applications for HIPAA Compliance Frank Macreery CTO, Aptible @fancyremarker
None
HIPAA The Health Insurance Portability and Accountability Act of 1996
HIPAA: What?
Protected Health Information (PHI)
Protected Health Information (PHI) "is created or received by a
health care provider or health plan…"
Protected Health Information (PHI) "relates to the health or condition
of an individual; the provision of health care to an individual; or the payment for the provision of health care to an individual…"
Protected Health Information (PHI) "identifies the individual"
HIPAA: Who?
Covered Entities Health plans, health care clearinghouses, health care providers
Business Associates An entity which "creates, receives, maintains, or transmits
protected health information"
None
None
None
None
Omnibus Final Rule Published January 2013 Effective Date: March 2013
Compliance Date: September 2013
HIPAA: Why?
Office of Civil Rights (OCR) The enforcement agency for HIPAA
14,300 Enforcement Cases in 2014
14,300 Enforcement Cases in 2014 Up 300% since 2004
14,300 Enforcement Cases in 2014 24% of cases resulted in
corrective action
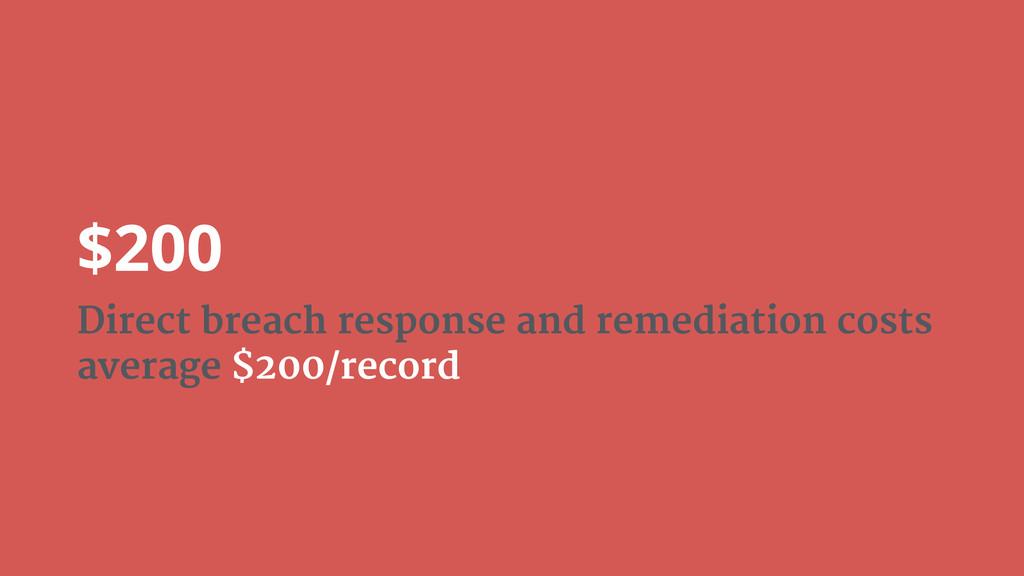
$200 Direct breach response and remediation costs average $200/record
$1000 Damages sought in class action suits average $1000/record
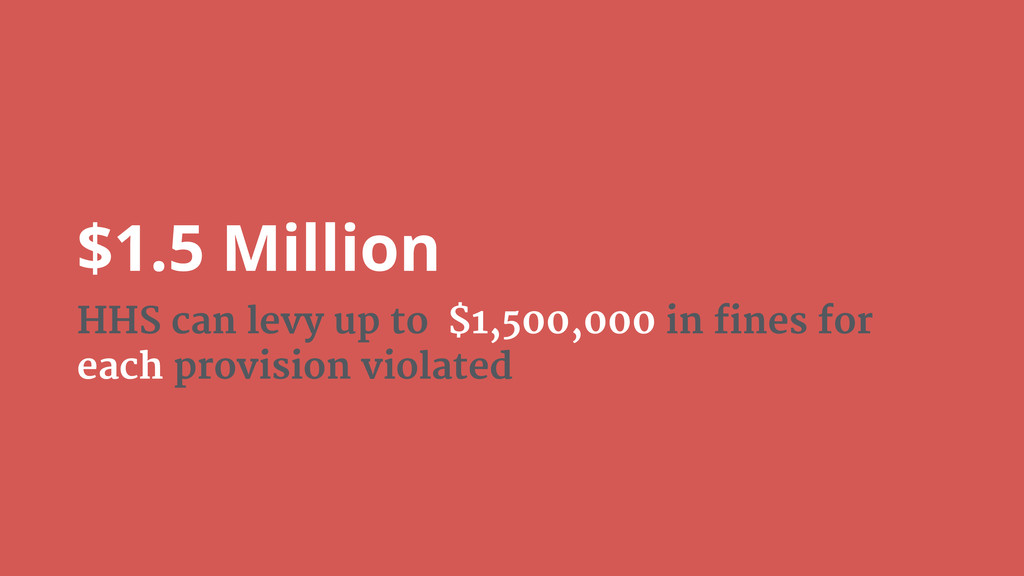
$1.5 Million HHS can levy up to $1,500,000 in fines
for each provision violated
Implementing Security Delegate, automate, standardize
What Does HIPAA Require?
Physical Safeguards
Physical Safeguards Facility Management
Physical Safeguards Physical Contingency Plans
Physical Safeguards
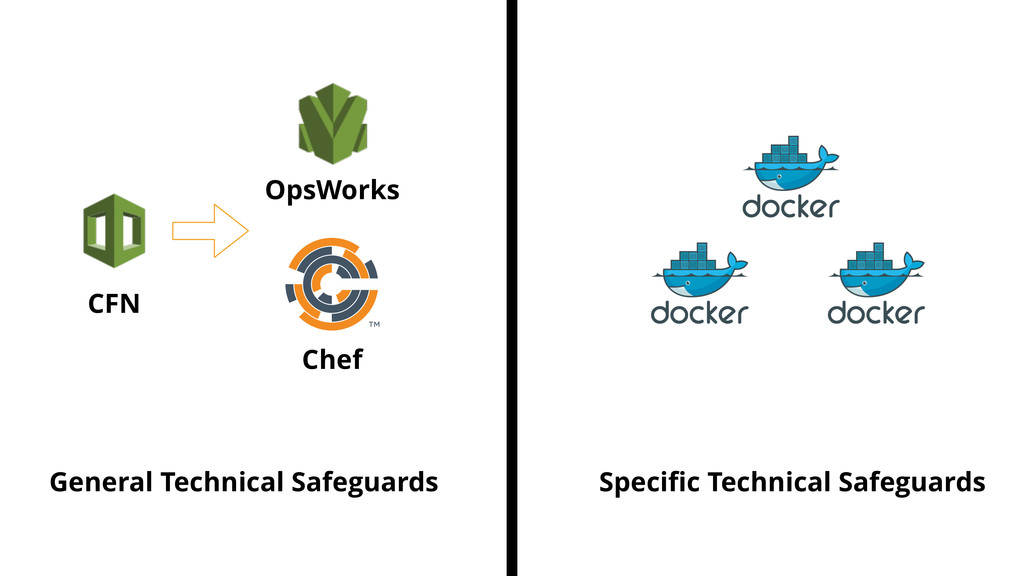
General Technical Safeguards
General Technical Safeguards Encryption
General Technical Safeguards Data Backups
General Technical Safeguards Instance Access (SSH) Controls
General Technical Safeguards
Specific Technical Safeguards
Specific Technical Safeguards Authentication
Specific Technical Safeguards PHI Record Access Controls (Authorization)
Specific Technical Safeguards
Administrative Safeguards
Administrative Safeguards Policies & Procedures
Administrative Safeguards Risk Assessments
Administrative Safeguards Workforce Training
Administrative Safeguards
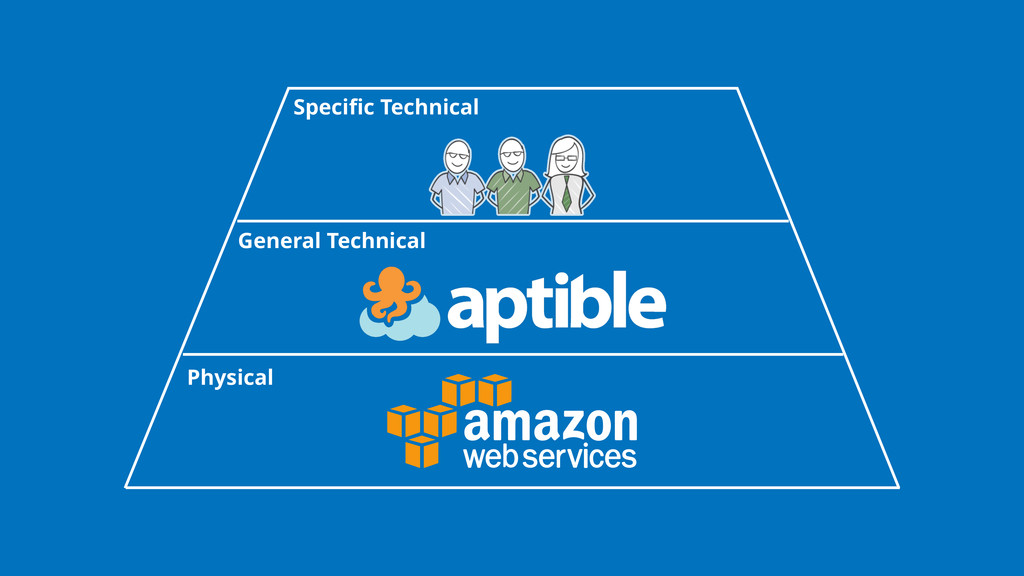
Physical General Technical Specific Technical
Delegation
Delegation Aptible delegates physical safeguards to AWS
Delegation Customers delegate administrative and (many) technical safeguards to Aptible
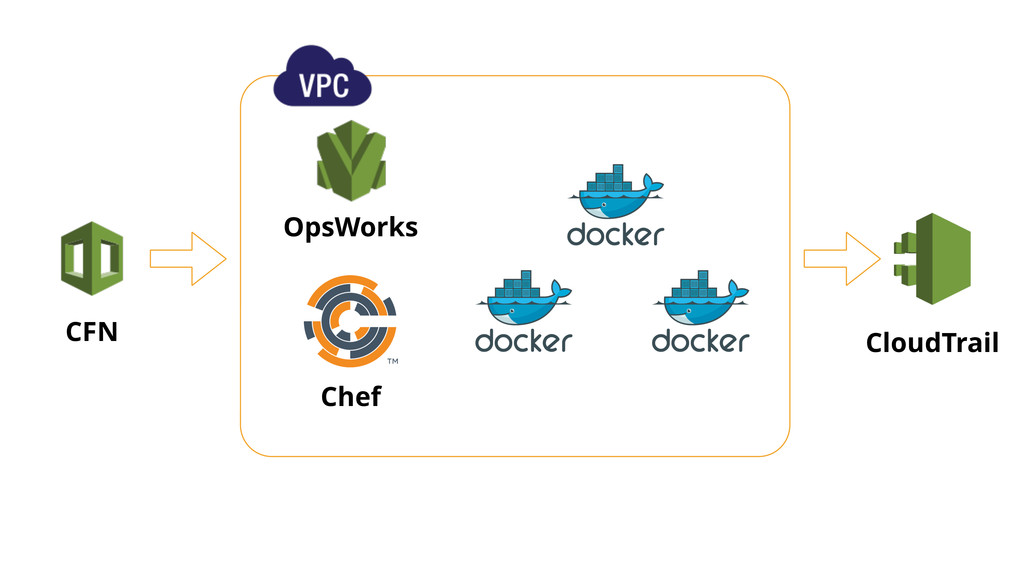
How does Aptible implement technical safeguards?
OpsWorks Chef CloudTrail CFN
OpsWorks Chef CFN General Technical Safeguards Specific Technical Safeguards
Unique SSH User Identification OpsWorks + IAM
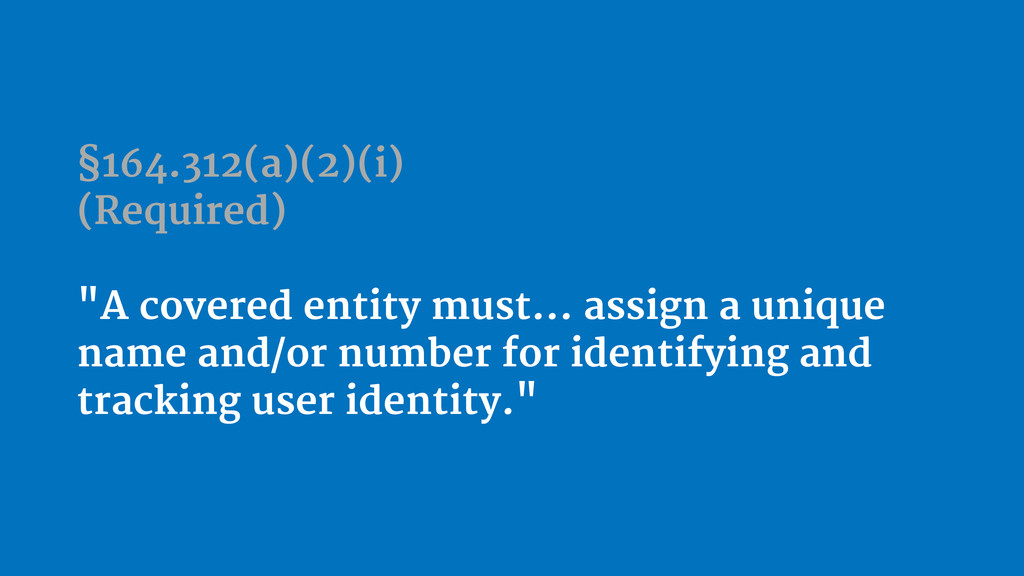
§164.312(a)(2)(i) (Required) "A covered entity must… assign a unique name
and/or number for identifying and tracking user identity."
Unique SSH User Identification OpsWorks + IAM
Unique SSH User Identification EC2 SSH key pair?
Unique SSH User Identification EC2 SSH key pair
Unique SSH User Identification Manual authorized_keys management?
Unique SSH User Identification Manual authorized_keys management
OpsWorks + IAM
IAM Identity and Access Management: Service for programmatically managing user
identities
None
OpsWorks Chef-based deployment platform
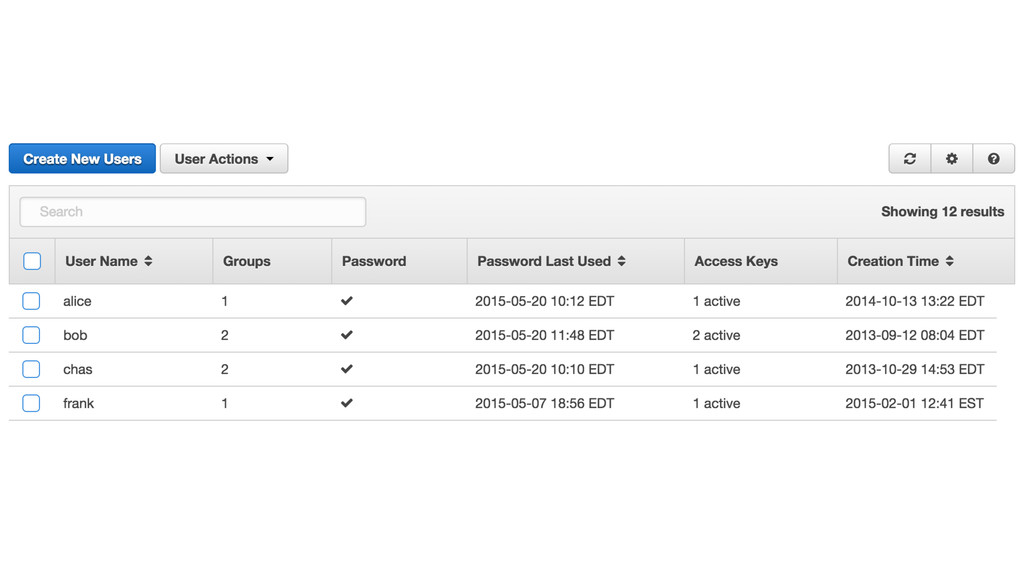
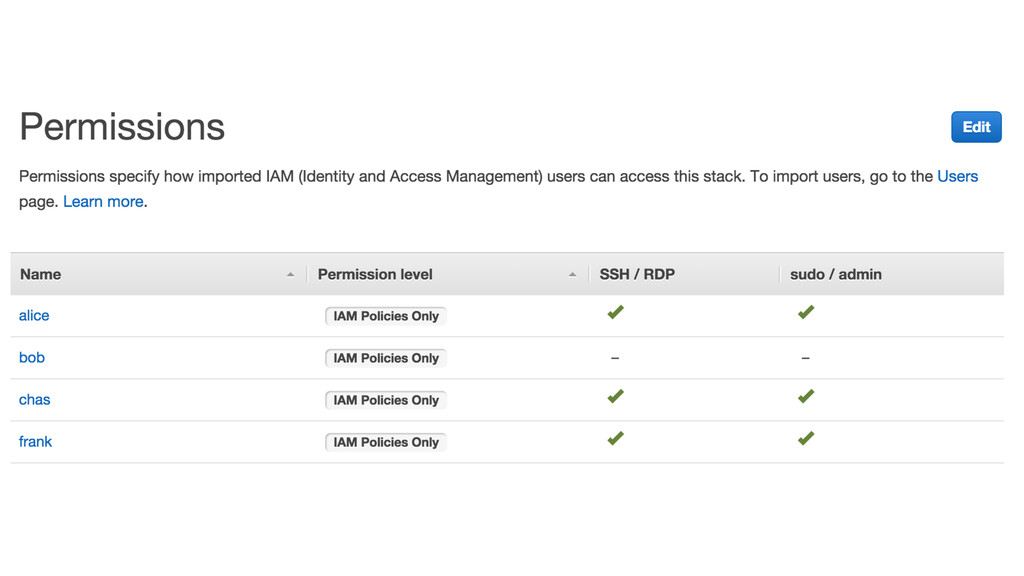
OpsWorks + IAM Gives visibility into current SSH permissions across
all EC2 instances
None
OpsWorks + IAM Makes it easy to rotate keys or
revoke access
OpsWorks + IAM Creates an audit log of all SSH
permission changes, through CloudTrail
End-to-end Encryption ELB—NGiNX—applications
§164.312(a)(2)(i) (Addressable) "A covered entity must… implement a mechanism to
encrypt electronic protected health information whenever deemed appropriate"
AWS "Approved" Services
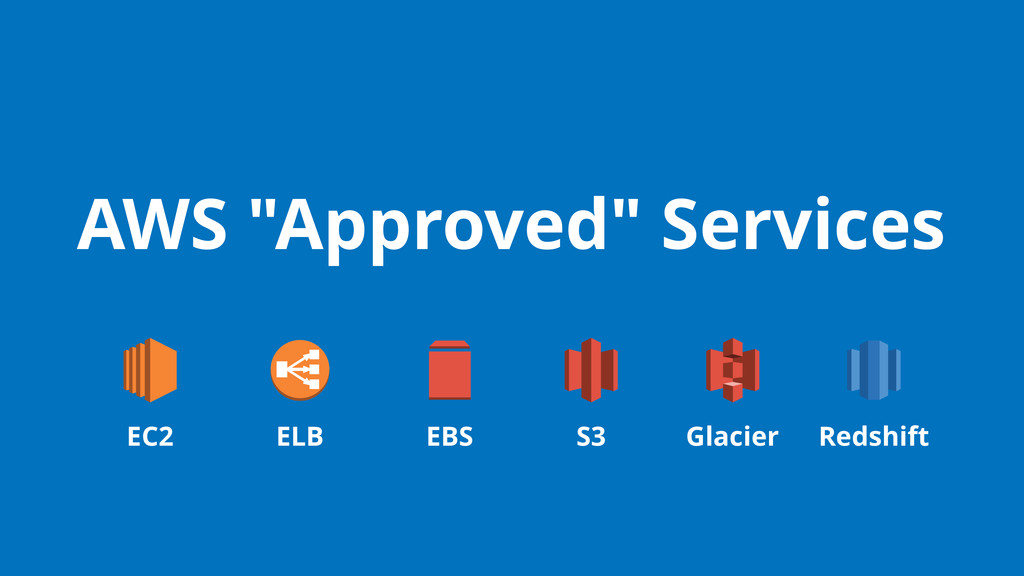
AWS "Approved" Services EC2 ELB EBS S3 Glacier Redshift
EC2 Must use dedicated instances for PHI
EBS All PHI volumes must be encrypted
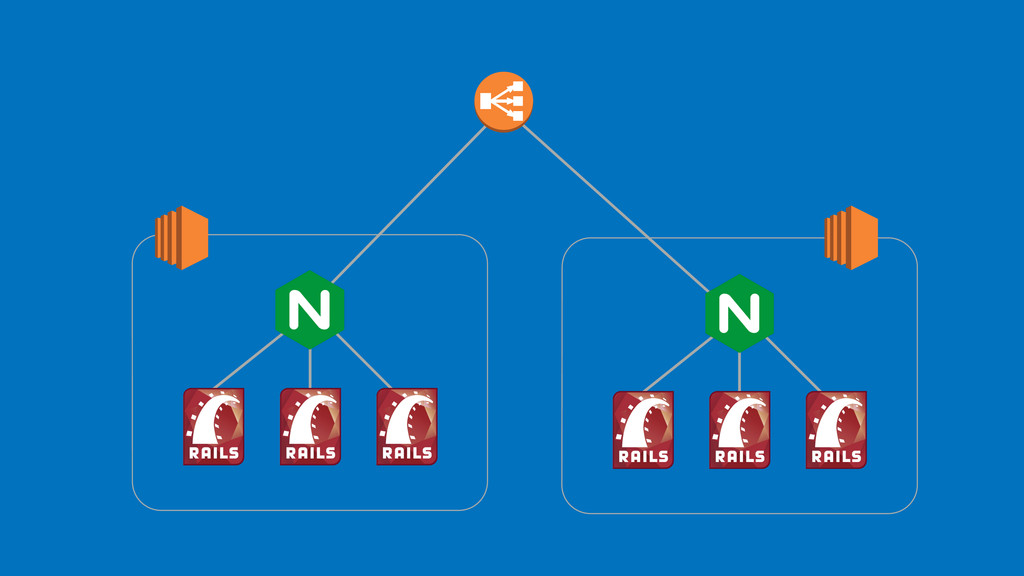
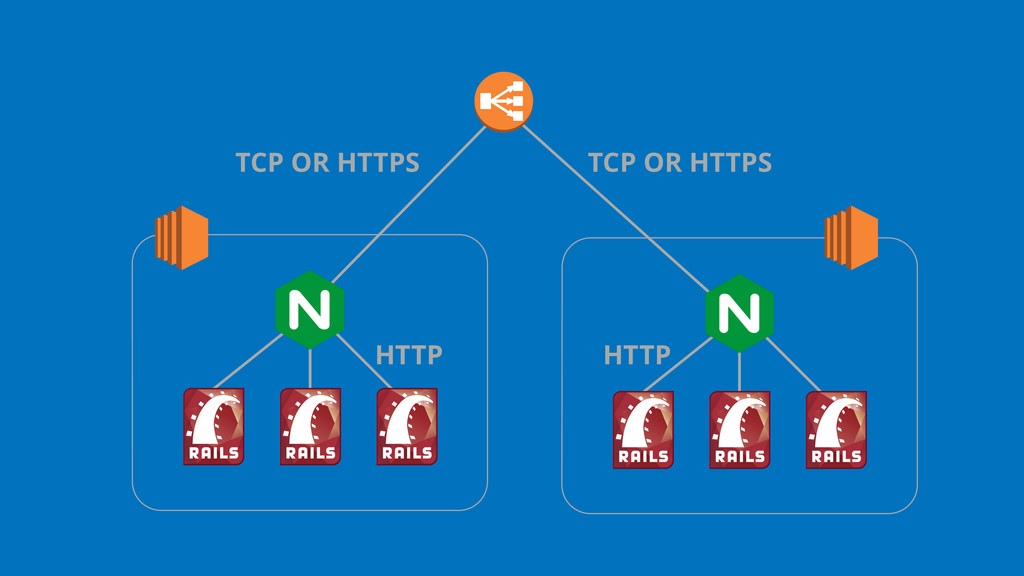
ELB End-to-end encryption in transit
None
TCP OR HTTPS HTTP HTTP TCP OR HTTPS
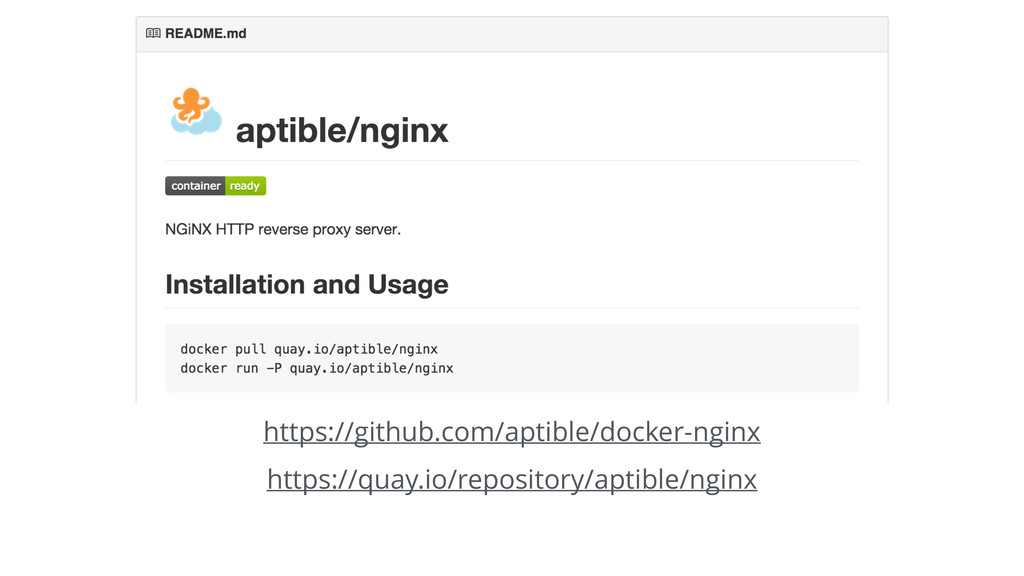
https://github.com/aptible/docker-nginx https://quay.io/repository/aptible/nginx
Standardized SSL Termination Container Deployed everywhere we require encryption in
transit
Configurable via ENV $UPSTREAM_SERVERS
Configurable via ENV $UPSTREAM_SERVERS $FORCE_SSL $HSTS_MAX_AGE (…)
Configurable via ENV Makes testing easier
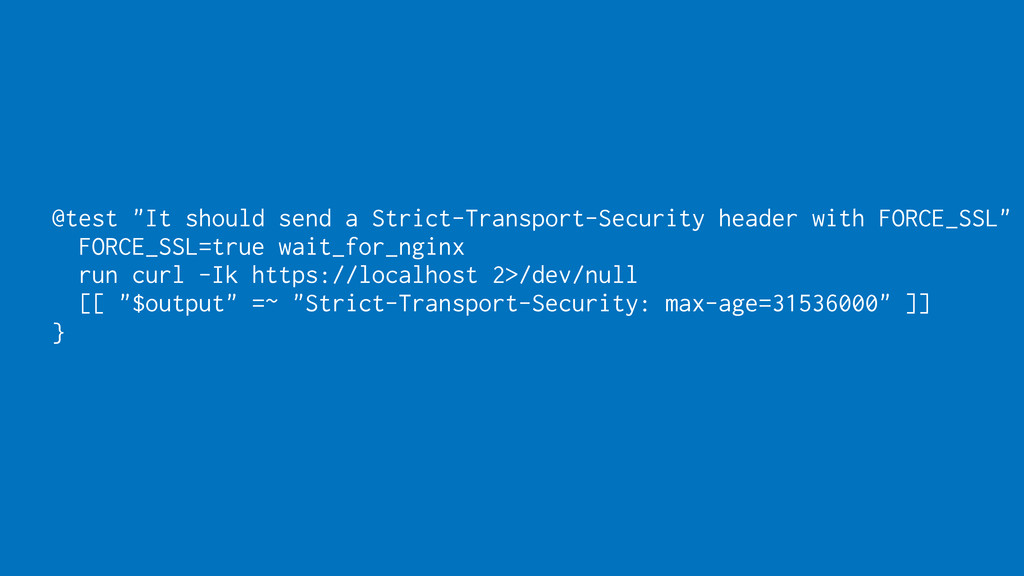
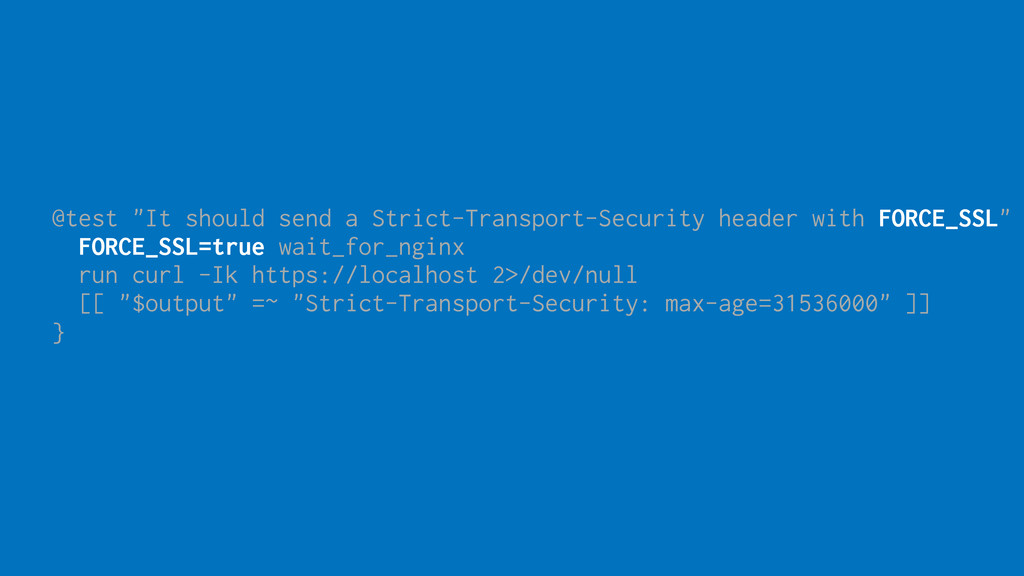
@test "It should send a Strict-Transport-Security header with FORCE_SSL" FORCE_SSL=true
wait_for_nginx run curl -Ik https://localhost 2>/dev/null [[ "$output" =~ "Strict-Transport-Security: max-age=31536000" ]] }
@test "It should send a Strict-Transport-Security header with FORCE_SSL" FORCE_SSL=true
wait_for_nginx run curl -Ik https://localhost 2>/dev/null [[ "$output" =~ "Strict-Transport-Security: max-age=31536000" ]] }
Configurable via ENV Abstracts implementation details: could be NGiNX, HAProxy,
…
ENV configuration Simplifies configuration management: central store doesn’t need to
know parameters in advance
Auditing Implementation is not enough
Auditing means… Logging SSH access to instances
OpsWorks + IAM
OpsWorks + IAM Creates an audit log of all SSH
permission changes, through CloudTrail
OpsWorks + IAM Works for new authorizations, but how can
we log individual SSH sessions?
Deny by Default
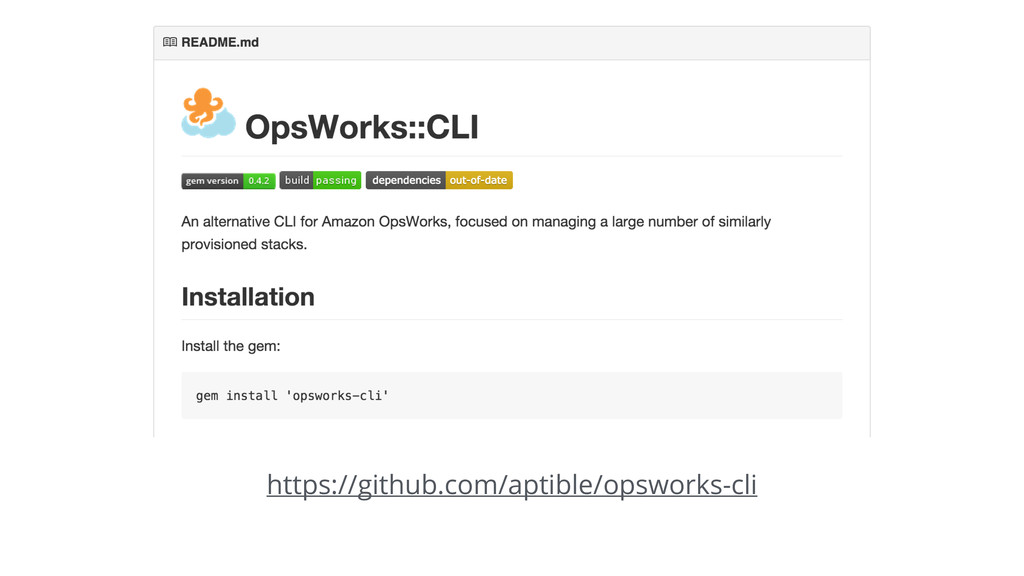
https://github.com/aptible/opsworks-cli
Deny by Default Periodically disable all SSH permissions: opsworks iam:lockdown
--stack foobar
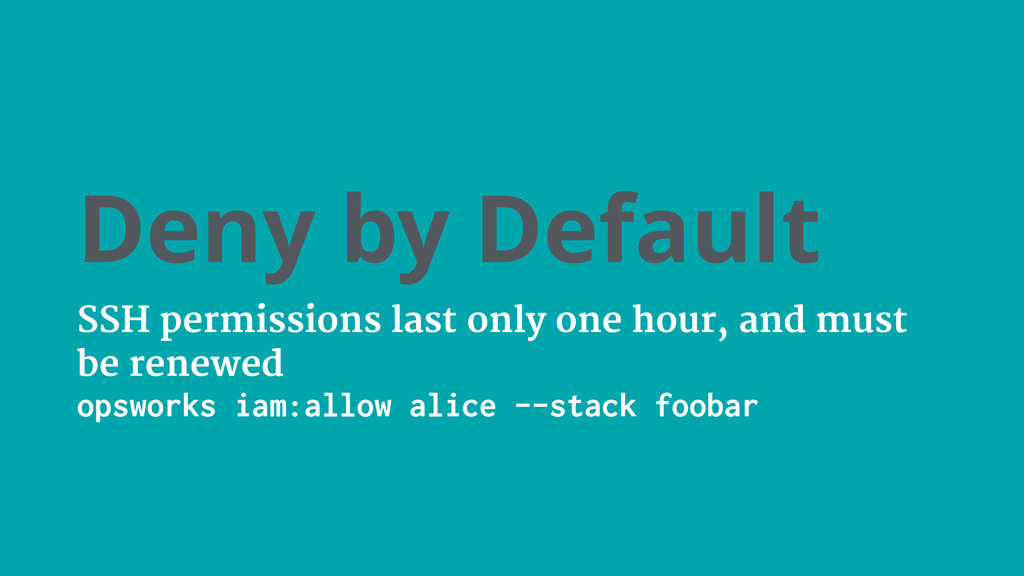
Deny by Default SSH permissions last only one hour, and
must be renewed opsworks iam:allow alice --stack foobar
Deny by Default Every SSH session gets logged to CloudTrail
(with 1 hour granularity)
Auditing means… Documenting a mitigation for every vulnerability
Heartbleed
Heartbleed POODLEbleed
Heartbleed POODLEbleed xBleed???
How do we prove that PHI was unaffected by xBleed?
Integration Tests Document every security response
https://github.com/sstephenson/bats
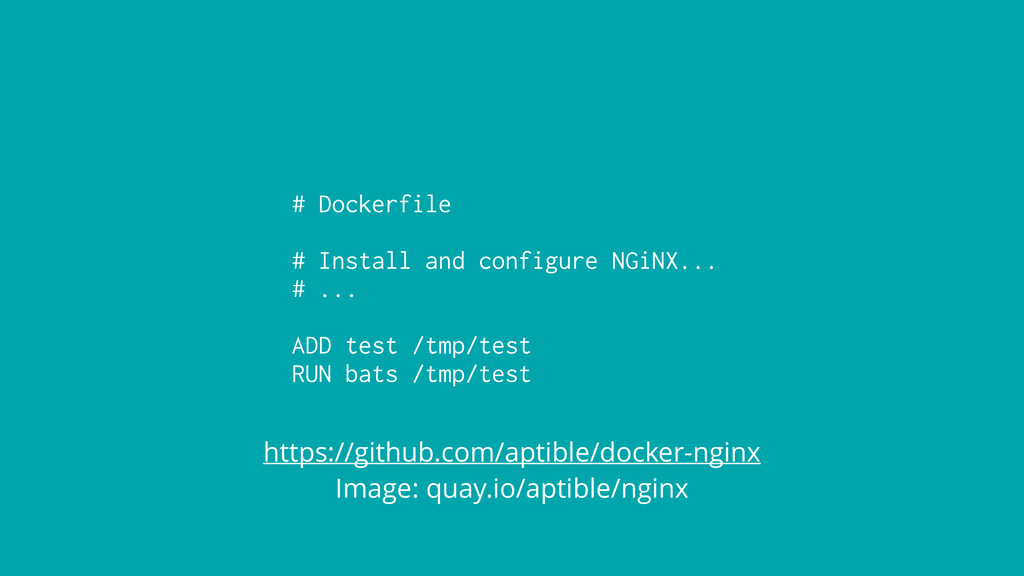
# Dockerfile # Install and configure NGiNX... # ... ADD
test /tmp/test RUN bats /tmp/test https://github.com/aptible/docker-nginx Image: quay.io/aptible/nginx
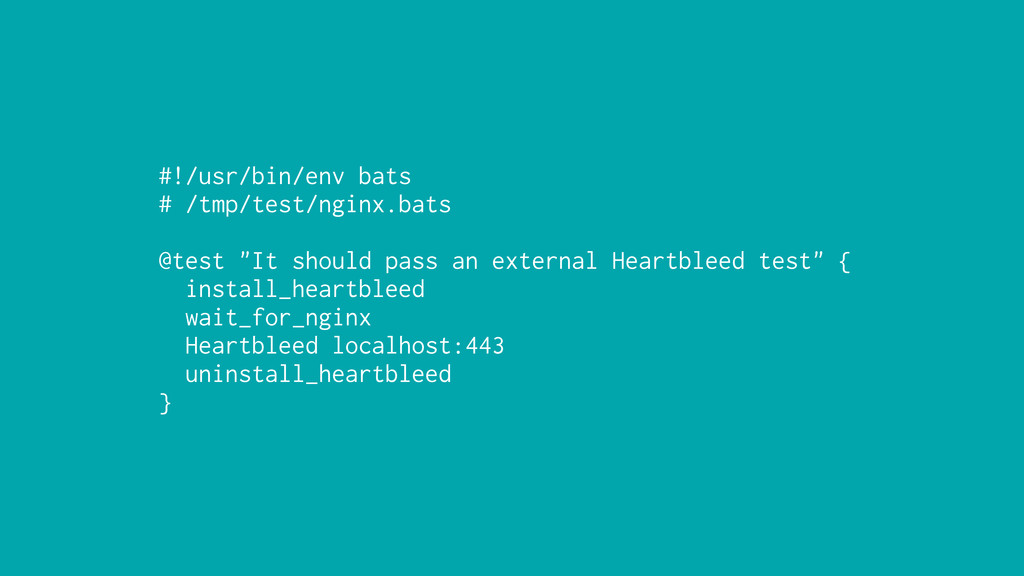
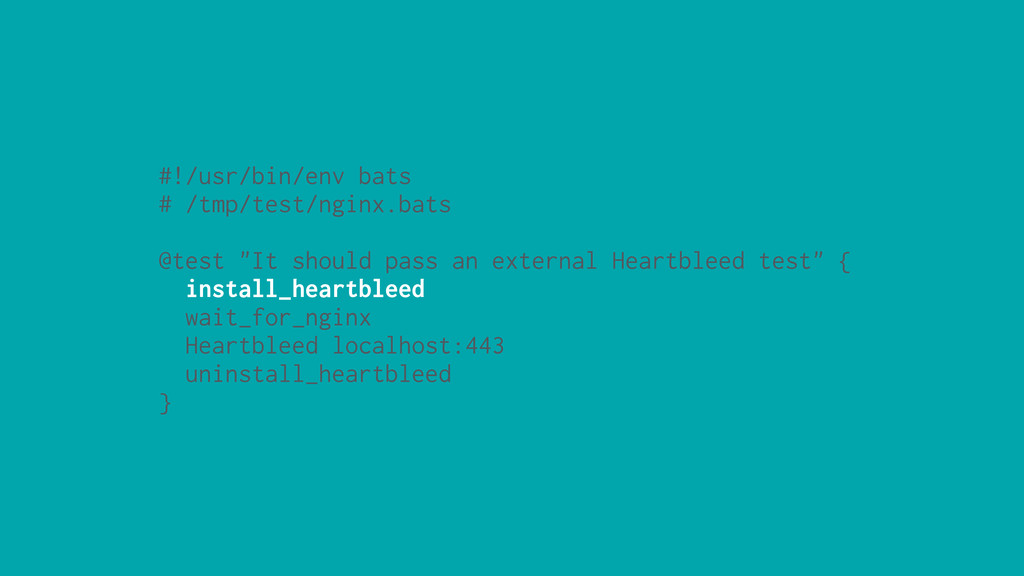
#!/usr/bin/env bats # /tmp/test/nginx.bats @test "It should pass an external
Heartbleed test" { install_heartbleed wait_for_nginx Heartbleed localhost:443 uninstall_heartbleed }
#!/usr/bin/env bats # /tmp/test/nginx.bats @test "It should pass an external
Heartbleed test" { install_heartbleed wait_for_nginx Heartbleed localhost:443 uninstall_heartbleed }
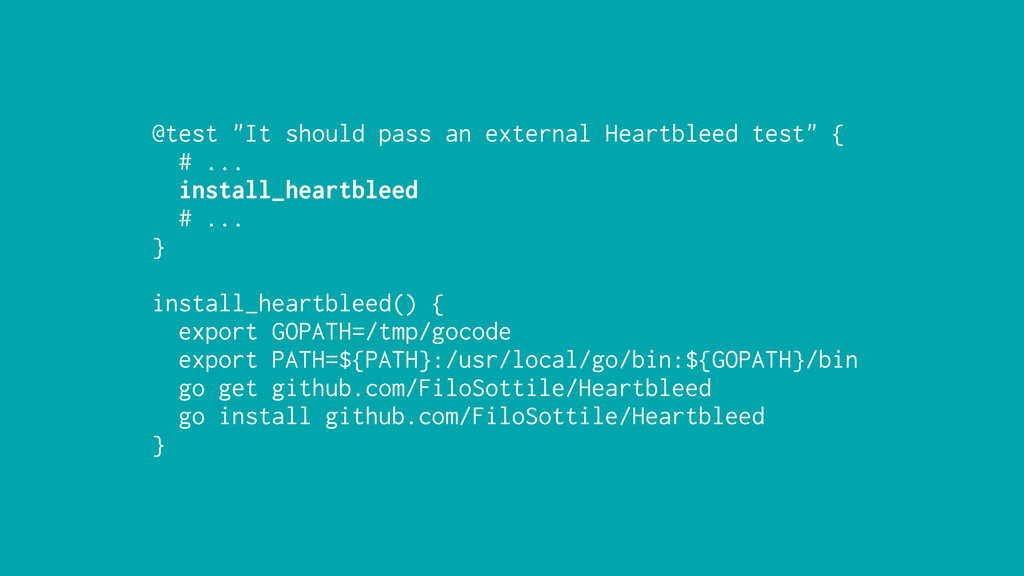
@test "It should pass an external Heartbleed test" { #
... install_heartbleed # ... } install_heartbleed() { export GOPATH=/tmp/gocode export PATH=${PATH}:/usr/local/go/bin:${GOPATH}/bin go get github.com/FiloSottile/Heartbleed go install github.com/FiloSottile/Heartbleed }
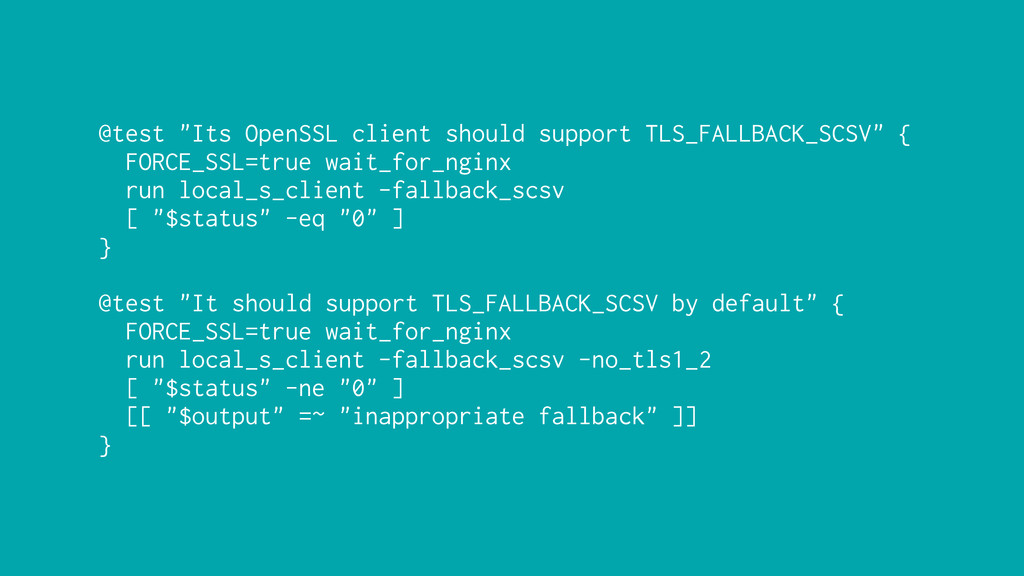
@test "Its OpenSSL client should support TLS_FALLBACK_SCSV" { FORCE_SSL=true wait_for_nginx
run local_s_client -fallback_scsv [ "$status" -eq "0" ] } @test "It should support TLS_FALLBACK_SCSV by default" { FORCE_SSL=true wait_for_nginx run local_s_client -fallback_scsv -no_tls1_2 [ "$status" -ne "0" ] [[ "$output" =~ "inappropriate fallback" ]] }
Integration tests happen during each image build
Integration tests happen during each image build Images are built
and tests run automatically
None
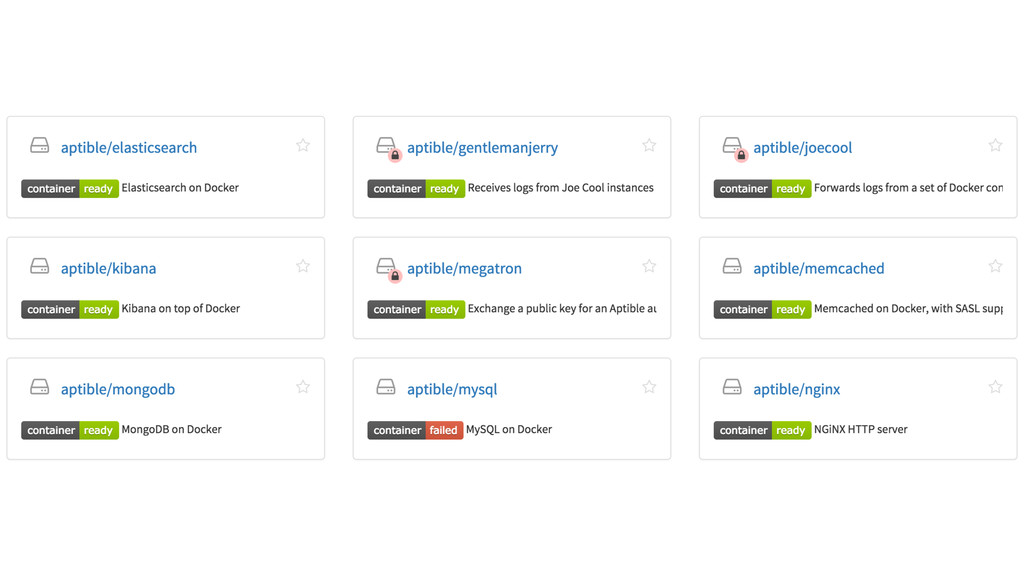
Integration tests happen during each image build Security test status
is easy to verify at a glance
None
HIPAA Regulates PHI, and any vendor handling PHI needs to
comply
Implementing Security Delegate low-level or general security details to providers
like AWS and Aptible
Implementing Security Automate management of technical safeguards (e.g., through OpsWorks
+ IAM for SSH access)
Implementing Security Standardize implementation and deployment of key security infrastructure
Auditing Use AWS services (OpsWorks, CloudTrail, etc.) to automate PHI
access logging
Auditing Audit all PHI access and document all responses to
security incidents
Thank you
@fancyremarker
[email protected]


 fancyremarker
 pfn
 ivry_presentationmaterials
 terapyon
 moznion
 raspython3
 tomokusaba
 nealle
 satomasahiro2005
 yut0naga1_fa
 grimoh
 sansantech
 kairim0
 axbom
 chriscoyier
 gr2m
 greggifford
 samlambert
 destraynor
 katiecoart
 sabderemane
 tanoku
 denniskardys
 michaelherold
 dougneiner