Defeating Cross-Site Scripting with Content Sec...

Defeating Cross-Site Scripting with Content Security Policy
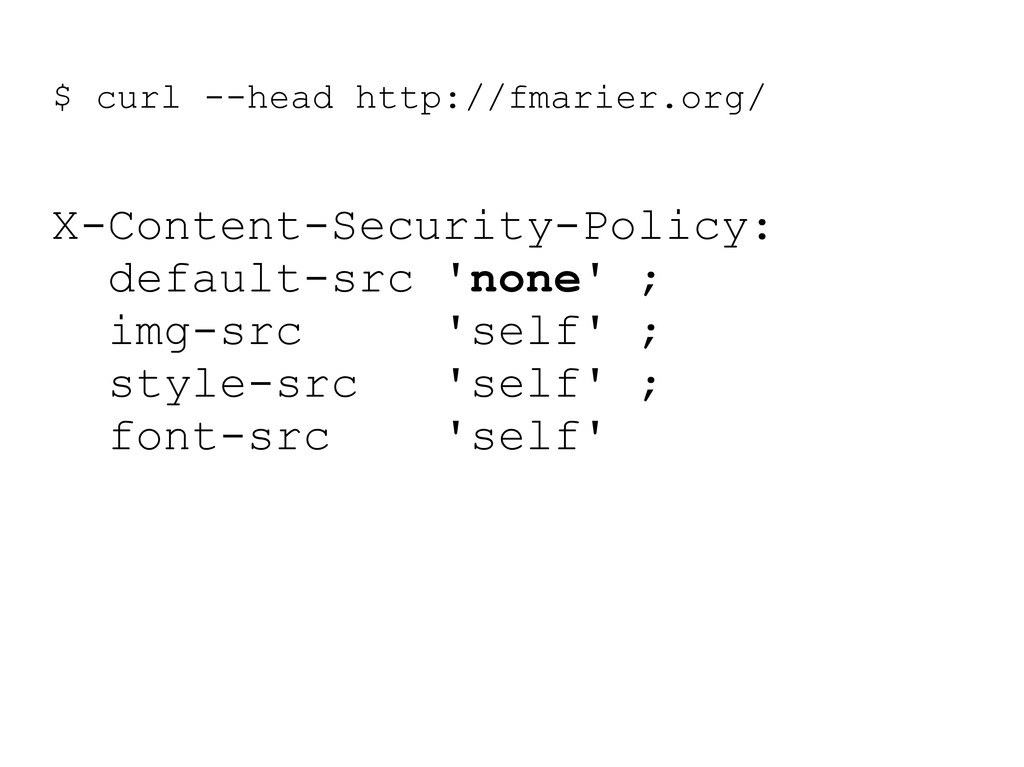
How a new proposed HTTP response header can help increase the depth of your web application defenses.

Francois Marier
March 07, 2012
 fmarier
 akihisaikeda
 koukimiura
 fornewid
 minodriven
 drumath2237
 kosukesaigusa
 takateeen_knj
 vivion
 quramy
 fuqda
 miccheng
 chigichan24
 takai
 jct
 rmw
 bluesmoon
 denniskardys
 cassininazir
 chrisshort
 brad_frost
 seathinner
 aleyda
 nwiizo
 samtorres