Share
Embed
【DroidKaigi 2026】「アクセシビリティを利用するとき、 アクセシビリティもまたこちらを利用している」 〜マルウェアによる攻撃と防衛について〜
DroidKaigi 2026登壇用資料です
Haruto K.
September 01, 2026
Transcript
93 slides
-
Haruto Kato Android Engineer @ BizReach モバイルセキュリティが好き @ HalunoYo ・情報処理安全確保支援士
・MASTG-OWASP ・CTF(rev/pwn) 本発表は所属企業とは関係ありません This presentation is unrelated to the business of my employer. Haruto Kato 2 -
本発表は教育・研究目的です。 示す技術の悪用は刑法・不正アクセス禁止法などに 抵触する可能性があります。 This talk is for education and research
purposes only. Misuse of any techniques shown may violate applicable laws. Haruto Kato 3 -
Part1. Part2. Part3. Part4. Haruto Kato AccessibilityService(A11yService)とは What is A11yService
A11yServiceを悪用したキルチェーン A kill chain abusing A11yService 悪用からアプリを守る Defend apps against A11yService abuse 倫理的なトレードオフ Ethical trade-offs 4 -
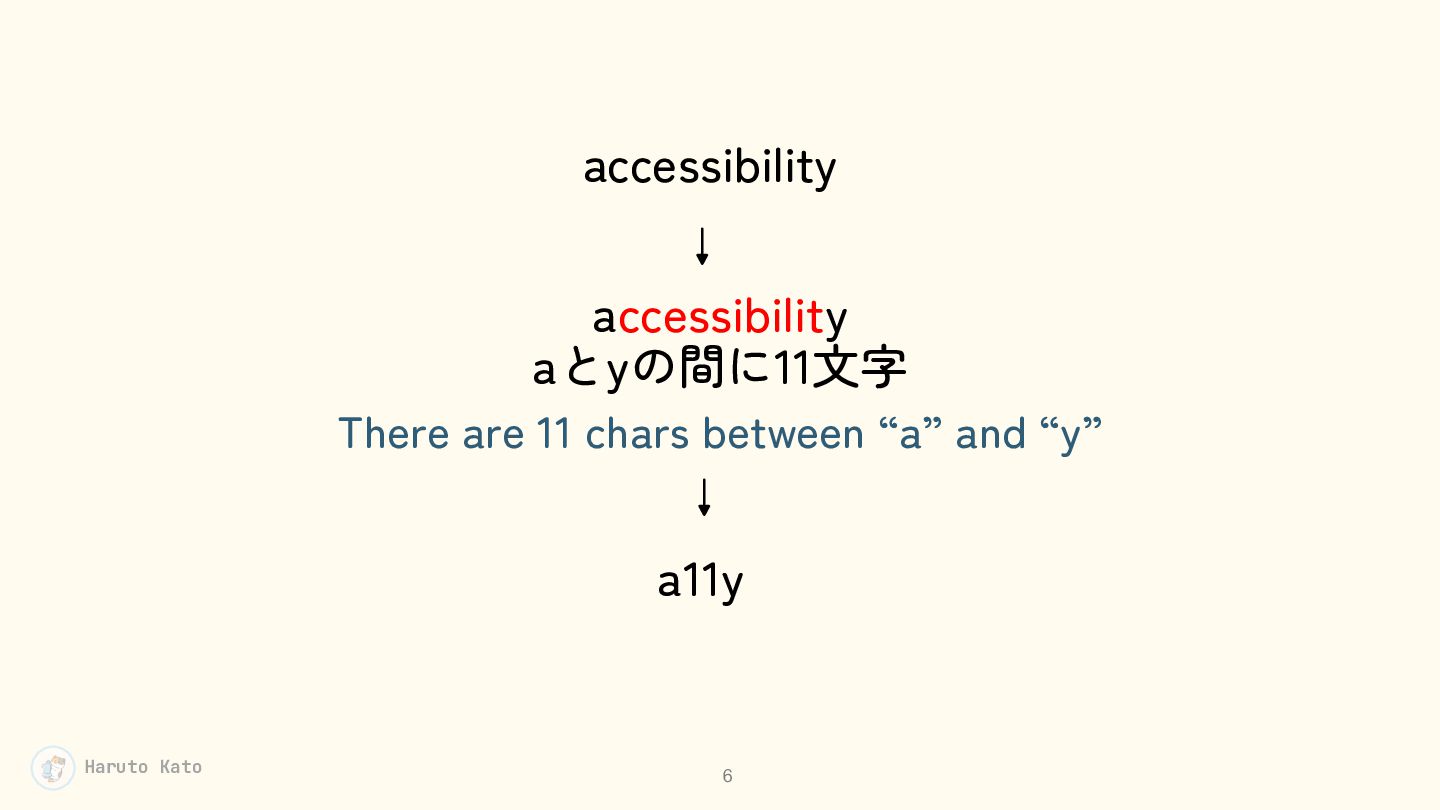
accessibility ↓ accessibility aとyの間に11文字 There are 11 chars between “a”
and “y” ↓ a11y Haruto Kato 6 -
a11y機能: 障がいの有無問わず、ユーザーがよりアプリを使い やすくするための機能 Accessibility features: The features enable users, regardless
of ability, to use apps easily. For example… Haruto Kato 7 -
TalkBack 音声ガイドによる画面情報の読み上げを可能とする It provides users with several features, such as
reading screen content aloud. Voice Access 音声を用いたアプリ操作を可能とする It allows users to use apps by voice – not by touch. Haruto Kato 8 -
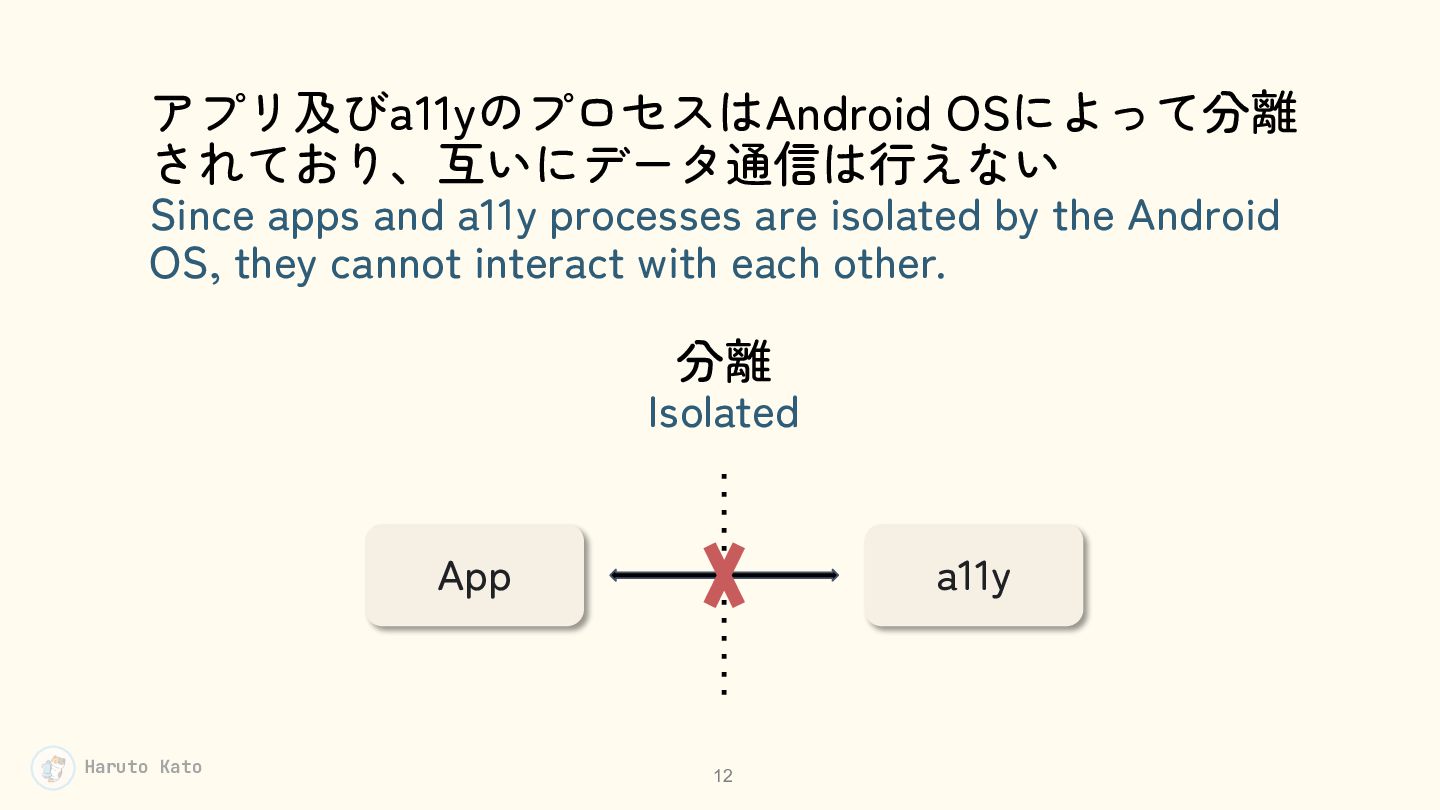
アプリ及びa11yのプロセスはAndroid OSによって分離 されており、互いにデータ通信は行えない Since apps and a11y processes are isolated
by the Android OS, they cannot interact with each other. 分離 Isolated App Haruto Kato a11y 12 -
しかし、画面上のデータ読み取りや音声による操作が 行えている However, these features can read screen content and
allow users to operate devices through their voices. Haruto Kato 14 -
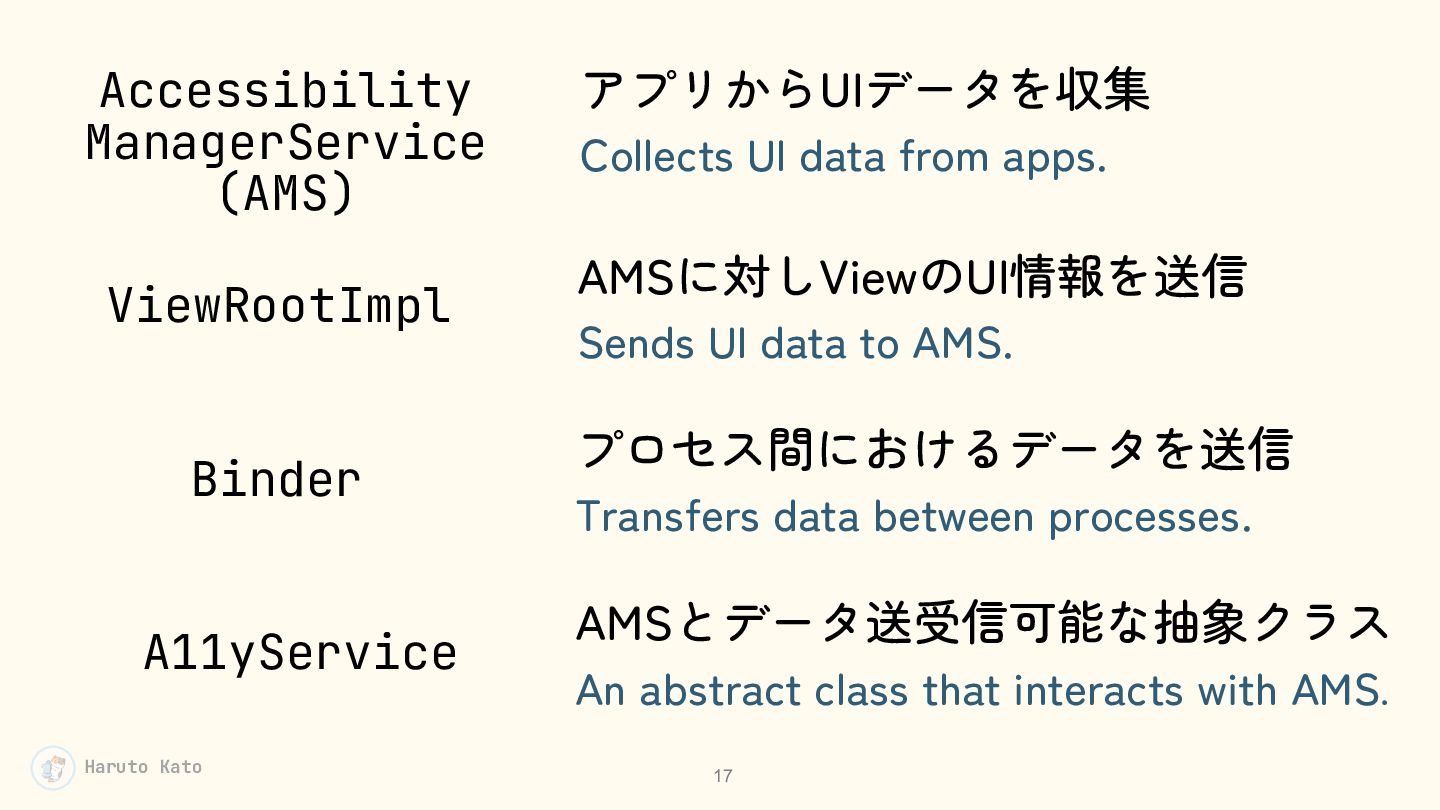
Accessibility ManagerService (AMS) アプリからUIデータを収集 ViewRootImpl AMSに対しViewのUI情報を送信 Binder プロセス間におけるデータを送信 A11yService Haruto
Kato Collects UI data from apps. Sends UI data to AMS. Transfers data between processes. AMSとデータ送受信可能な抽象クラス An abstract class that interacts with AMS. 17 -
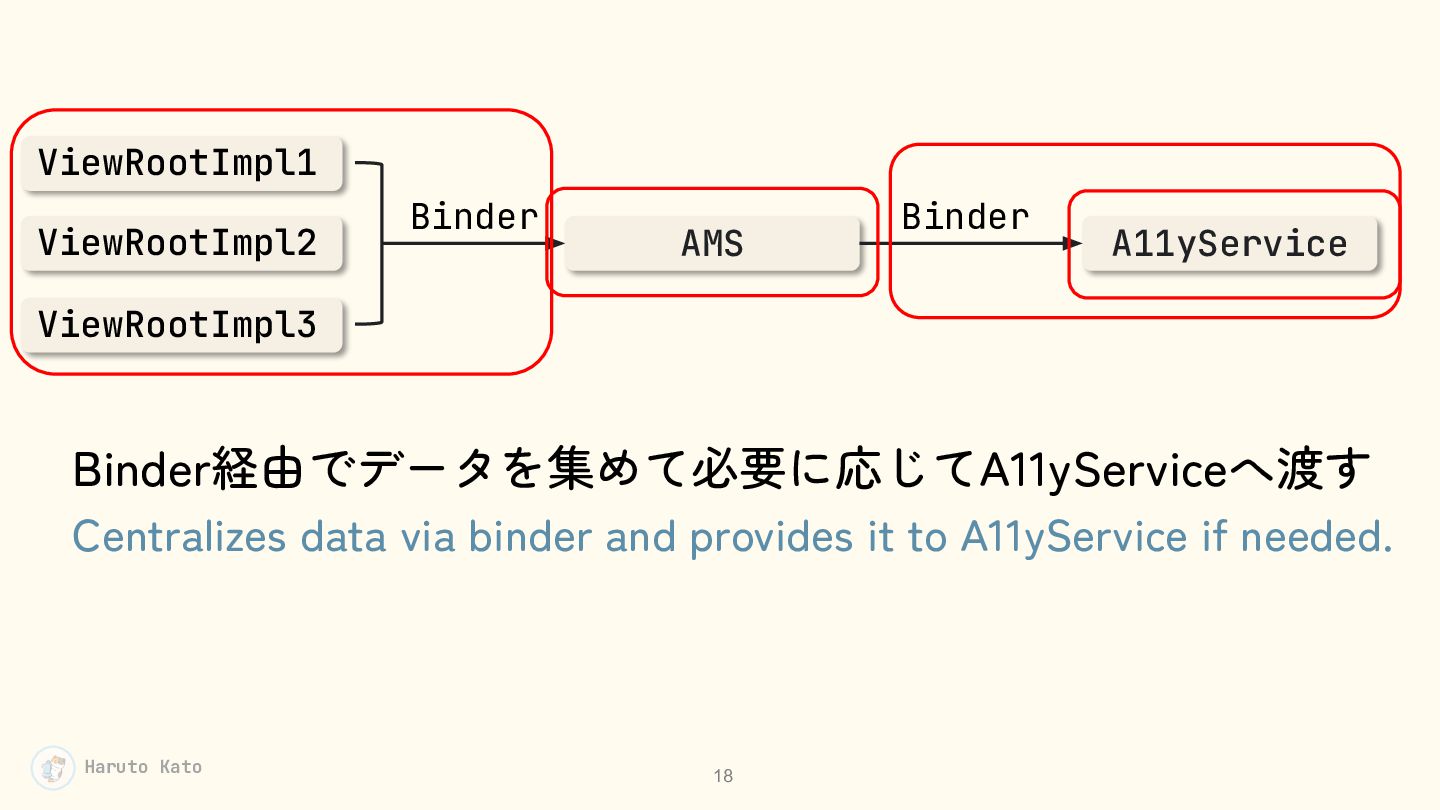
ViewRootImpl1 ViewRootImpl2 Binder AMS Binder A11yService ViewRootImpl3 Binder経由でデータを集めて必要に応じてA11yServiceへ渡す Centralizes data
via binder and provides it to A11yService if needed. Haruto Kato 18 -
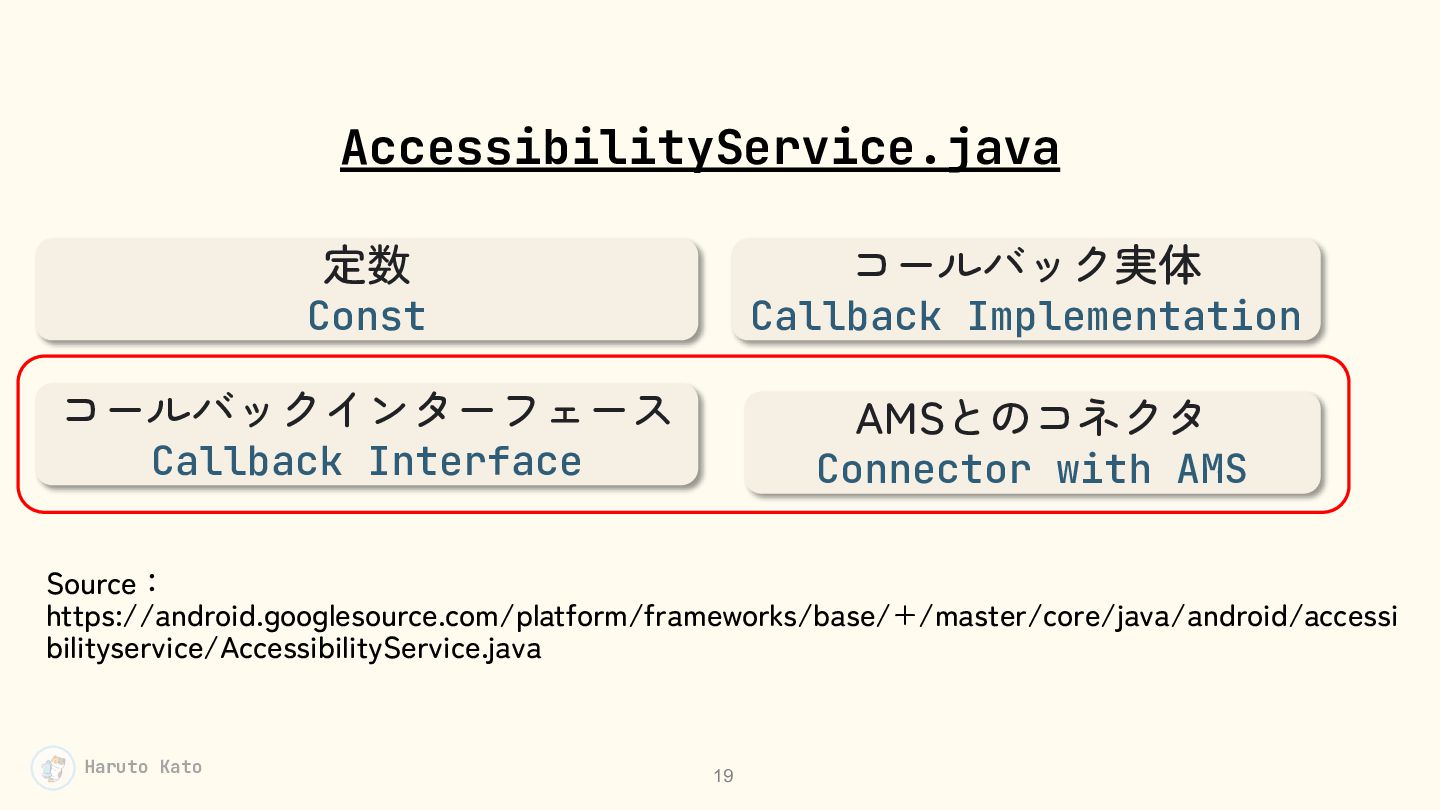
AccessibilityService.java 定数 コールバック実体 Const Callback Implementation コールバックインターフェース AMSとのコネクタ Callback Interface
Connector with AMS Source: https://android.googlesource.com/platform/frameworks/base/+/master/core/java/android/accessi bilityservice/AccessibilityService.java Haruto Kato 19 -
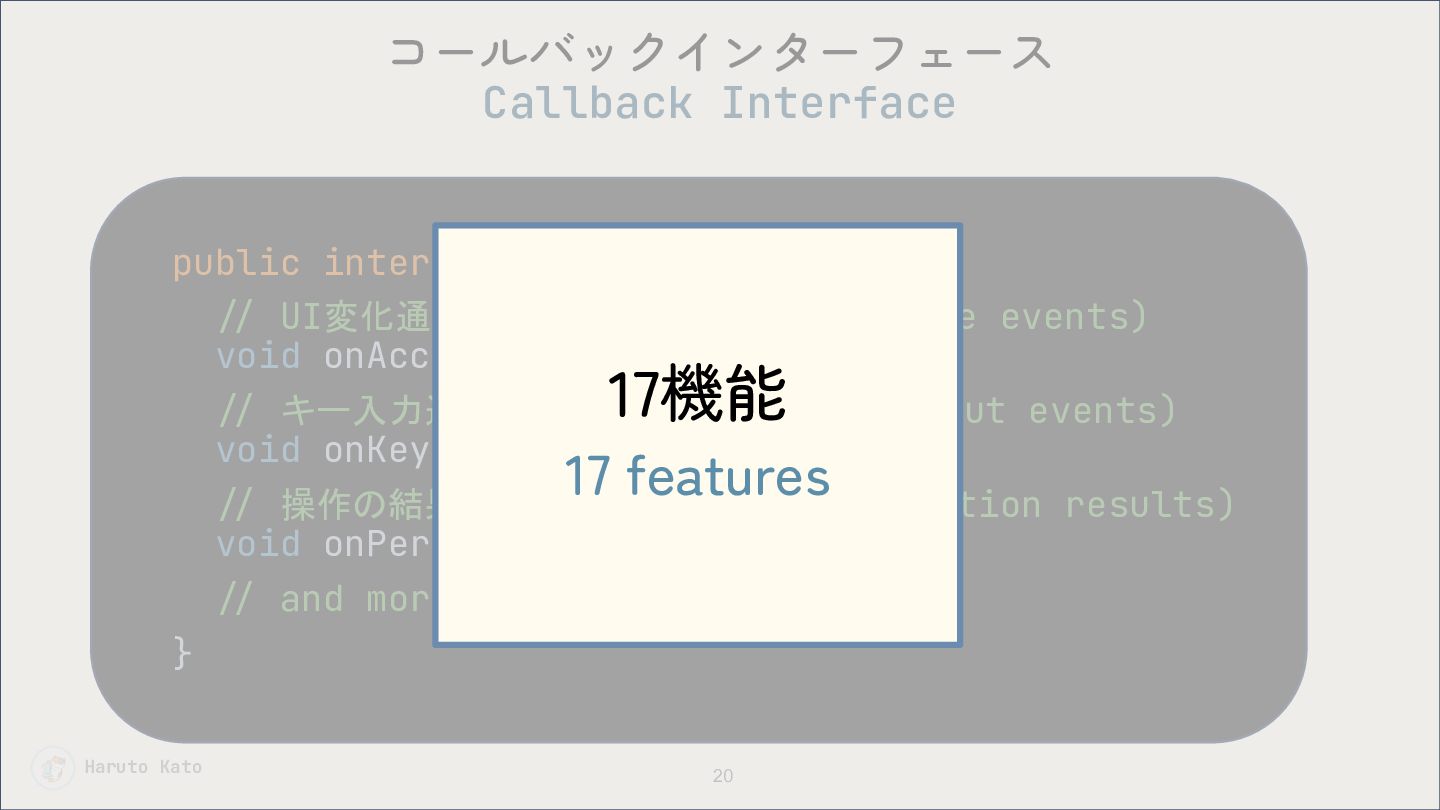
コールバックインターフェース Callback Interface public interface Callbacks { // UI変化通知イベント(notify UI
change events) void onAccessibilityEvent(…); 17機能 // キー入力通知イベント(notify key input events) void onKeyEvent(…); 17 features // 操作の結果通知イベント(notify operation results) void onPerformGestureResult(…); // and more } Haruto Kato 20 -
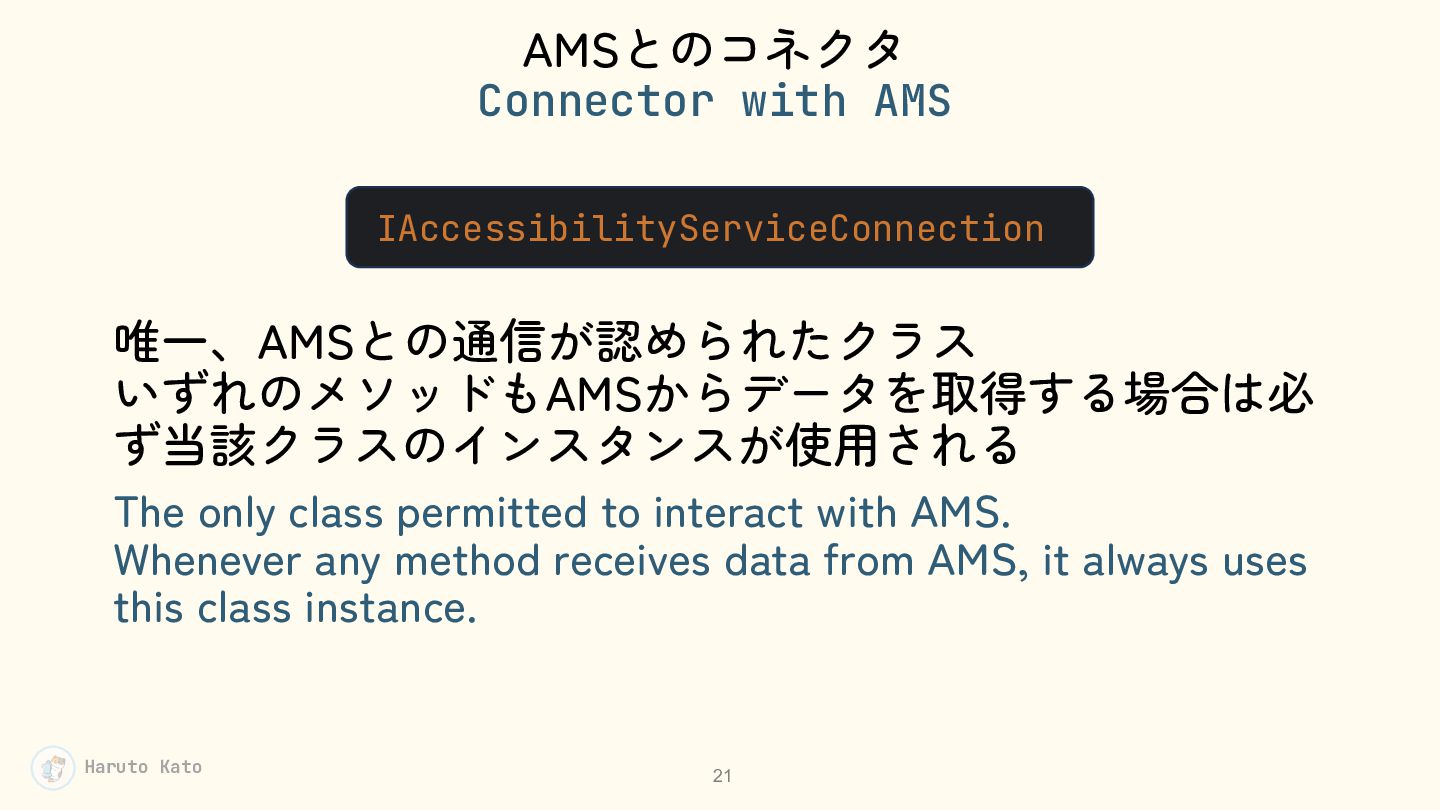
AMSとのコネクタ Connector with AMS IAccessibilityServiceConnection 唯一、AMSとの通信が認められたクラス いずれのメソッドもAMSからデータを取得する場合は必 ず当該クラスのインスタンスが使用される The only
class permitted to interact with AMS. Whenever any method receives data from AMS, it always uses this class instance. Haruto Kato 21 -
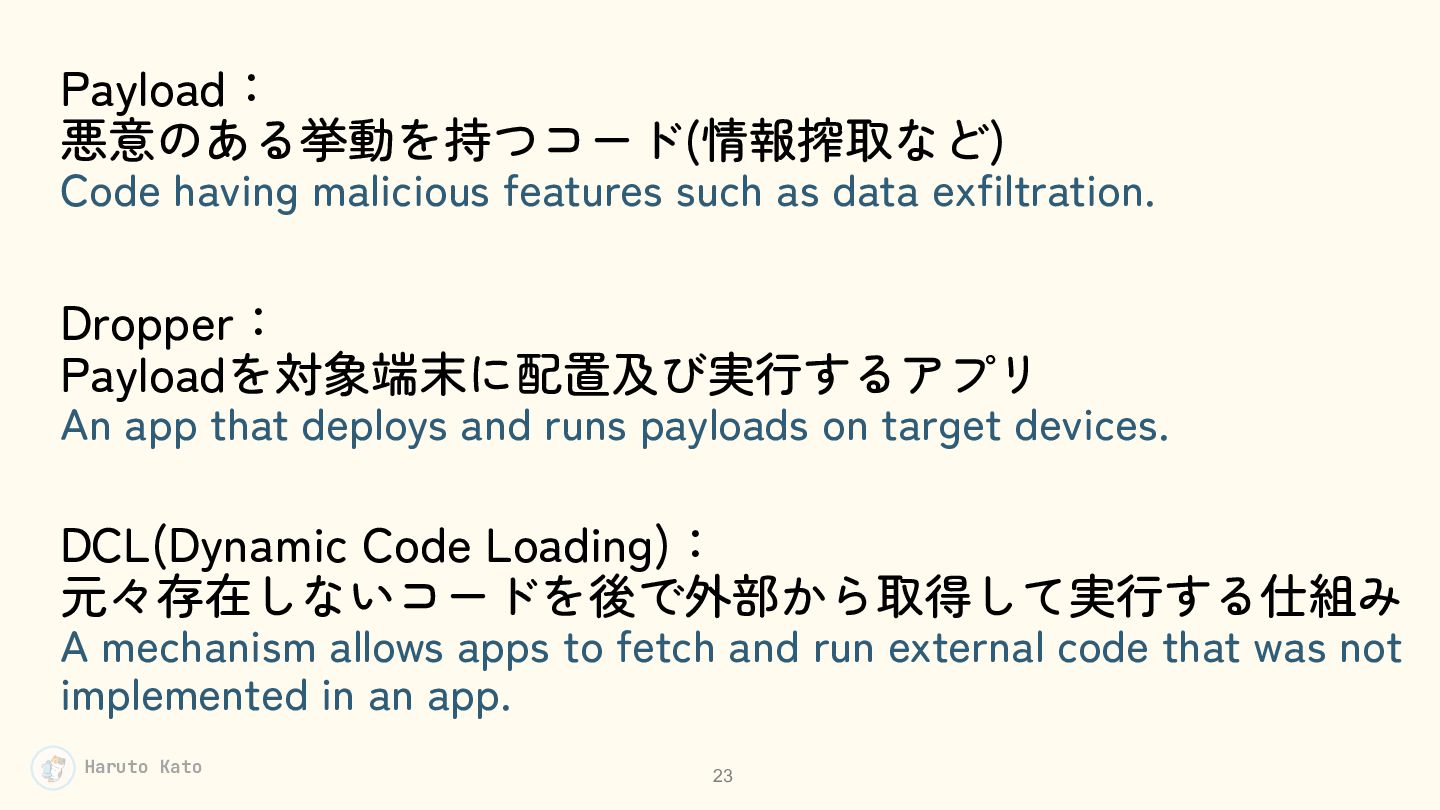
Payload: 悪意のある挙動を持つコード(情報搾取など) Code having malicious features such as data exfiltration.
Dropper: Payloadを対象端末に配置及び実行するアプリ An app that deploys and runs payloads on target devices. DCL(Dynamic Code Loading): 元々存在しないコードを後で外部から取得して実行する仕組み A mechanism allows apps to fetch and run external code that was not implemented in an app. Haruto Kato 23 -
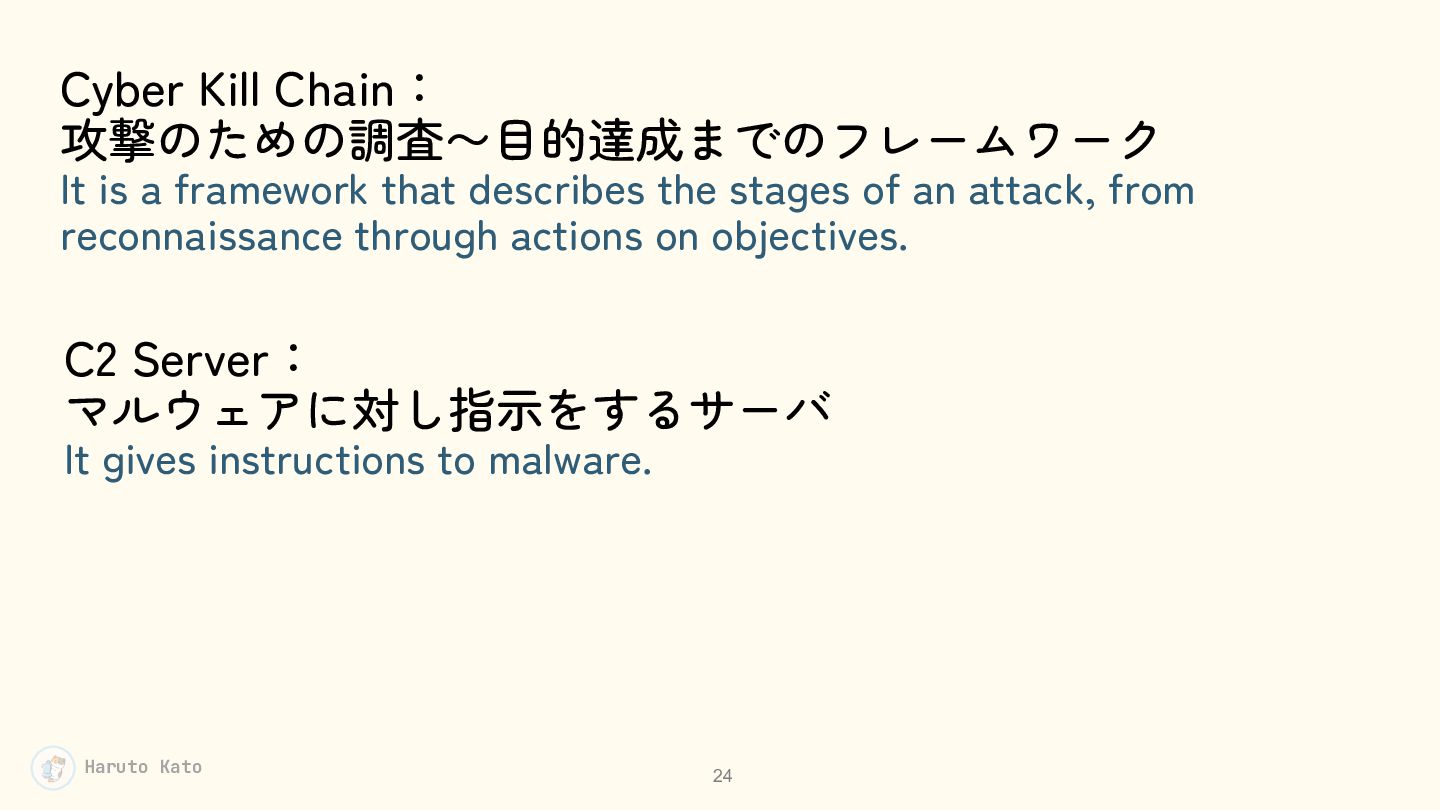
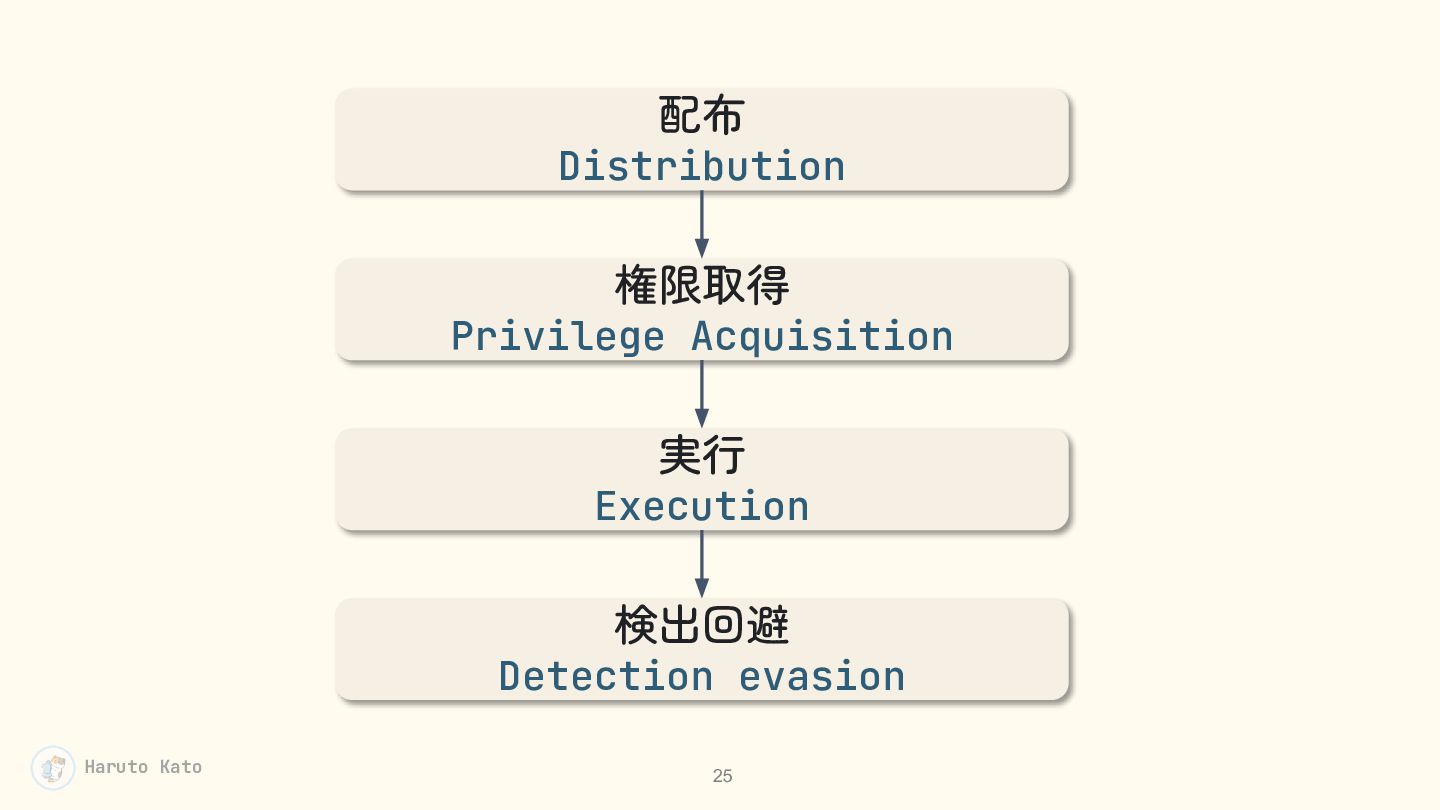
Cyber Kill Chain: 攻撃のための調査〜目的達成までのフレームワーク It is a framework that describes
the stages of an attack, from reconnaissance through actions on objectives. C2 Server: マルウェアに対し指示をするサーバ It gives instructions to malware. Haruto Kato 24 -
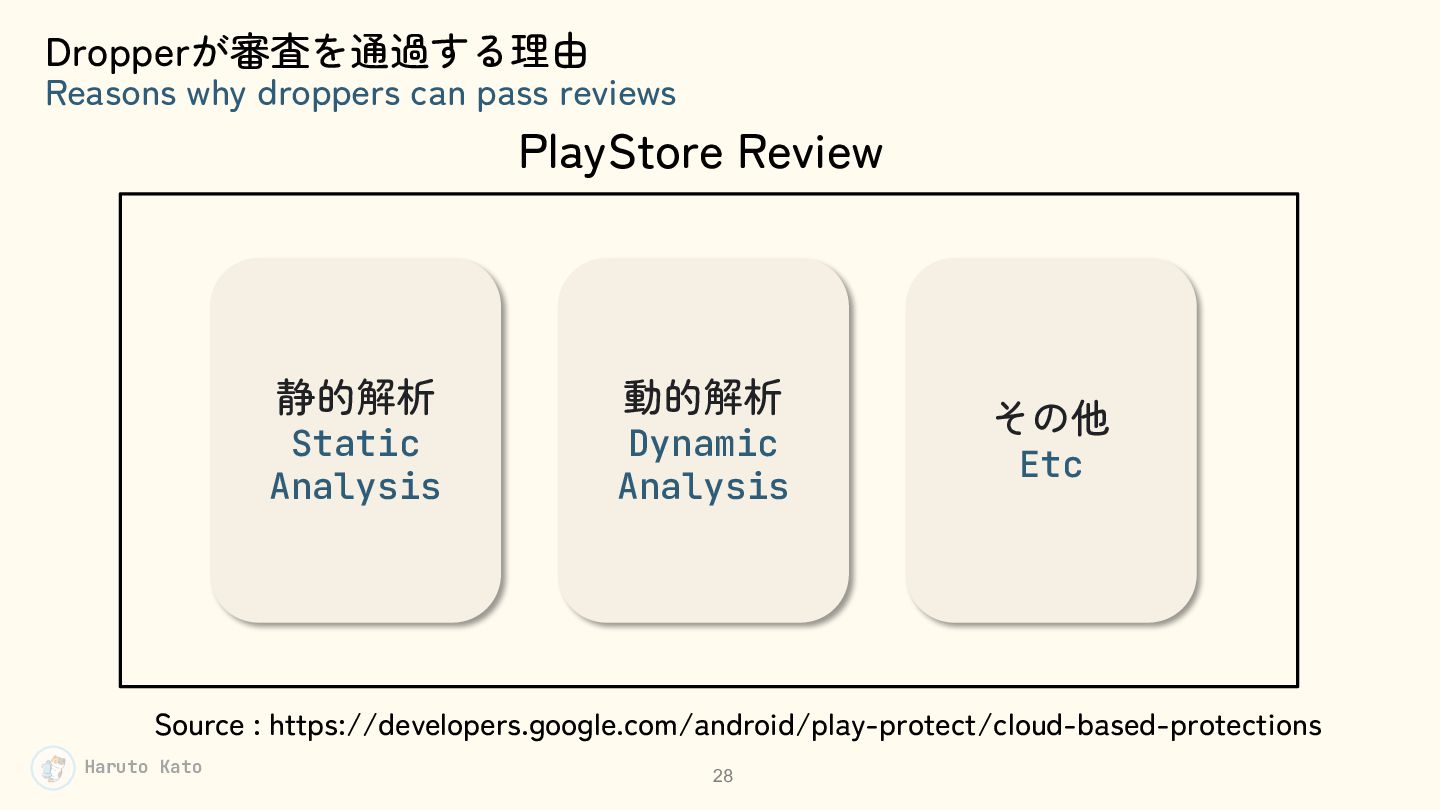
Dropperが審査を通過する理由 Reasons why droppers can pass reviews PlayStore Review 静的解析
動的解析 Static Analysis Dynamic Analysis その他 Etc Source : https://developers.google.com/android/play-protect/cloud-based-protections Haruto Kato 28 -
Dropperが審査を通過する理由 Reasons why droppers can pass reviews 静的解析: 一般的な解析ツールとARTの解析実装の挙動差を利用する ARTではアプリインストール時に解析実装が呼ばれる
Static analysis : Threat actors abuse the behavioral gap between general analysis tools and analysis implementations of ART. The analysis implementations of ART are called when users install an app. Haruto Kato 29 -
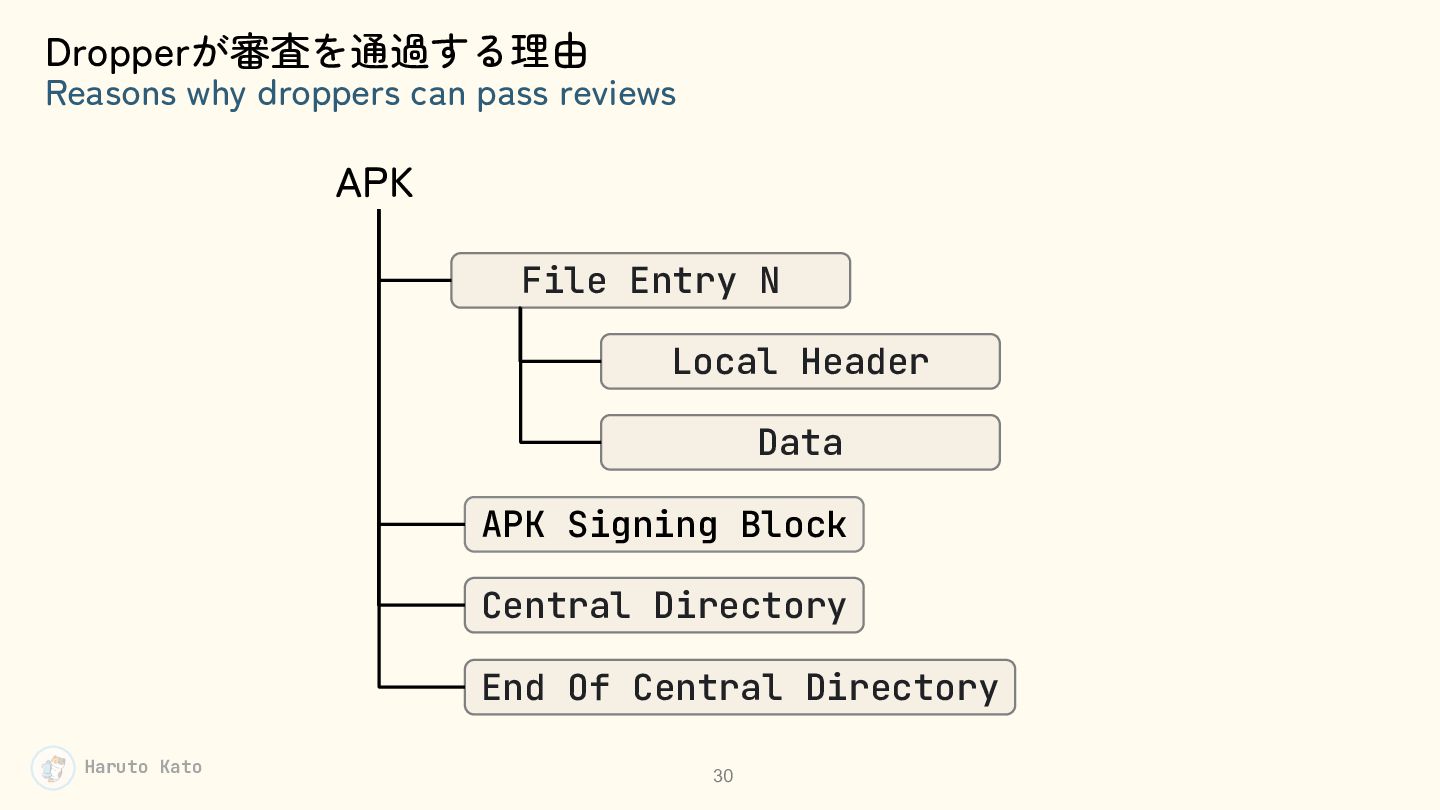
Dropperが審査を通過する理由 Reasons why droppers can pass reviews APK File Entry
N Local Header Data APK Signing Block Central Directory End Of Central Directory Haruto Kato 30 -
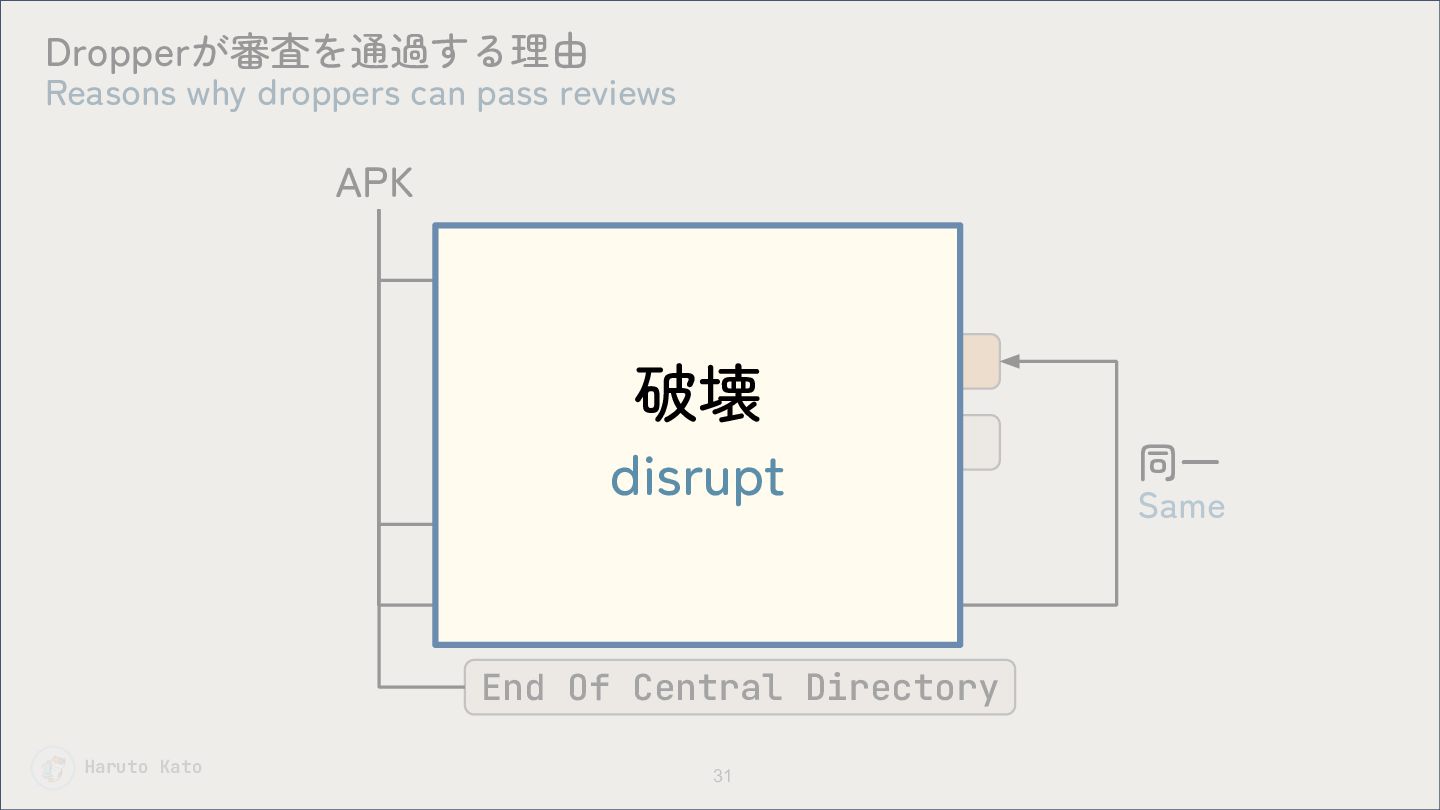
Dropperが審査を通過する理由 Reasons why droppers can pass reviews APK File Entry
N Local Header 破壊 Data disrupt APK Signing Block Central Directory End Of Central Directory Haruto Kato 31 同一 Same -
Dropperが審査を通過する理由 Reasons why droppers can pass reviews Local Headerだけ書き換え、 Central
Directoryの値はそのまま Threat actors modify only the Local Header’s value and keep the Central Directory’s value unchanged. Haruto Kato 32 -
Dropperが審査を通過する理由 Reasons why droppers can pass reviews 通常解析器: 不正な形式を検出した場合エラーを投げて終了 General
analysis tools : If they detect incorrect formats, they throw errors and exit. ART: 不正な形式を検出した場合Central Directoryを正として続行 If ART detects incorrect formats, it continues analysis processes and relies on the Central Directory. Source : https://unit42.paloaltonetworks.com/apk-badpack-malware-tampered-headers Haruto Kato 33 -
Dropperが審査を通過する理由 Reasons why droppers can pass reviews PlayStoreの静的解析では失敗 It would
fail in the Play Store's static analysis. ARTの静的解析では成功するためインストール可能 Since ART's static analysis succeeds, the app can still be installed on the device. Haruto Kato 34 -
Dropperが審査を通過する理由 Reasons why droppers can pass reviews GoogleはPlayStoreの静的解析が失敗した場合どうする かは公開していない しかし、この手法で実際にマルウェアがPlayStoreから
検出されたのは事実 Google has not disclosed how they handle static analysis failures. However, malware exploiting the gap was found in PlayStore. Source : https://www.malwarebytes.com/blog/news/2025/08/77-malicious-apps-removed-from-go ogle-play-store Haruto Kato 35 -
Dropperが審査を通過する理由 Reasons why droppers can pass reviews 動的解析: 審査中アプリはdropperのため、この時点では無害 通過後、しばらくしてからC2サーバなどと通信をする
そのため、Googleが動的解析で見つけるのは困難 Dynamic analysis : Since apps under review are just droppers, they are benign at this stage. After passing the review, they interact with C2 servers. Therefore, it is extremely difficult to detect malware via dynamic analysis. Haruto Kato 36 -
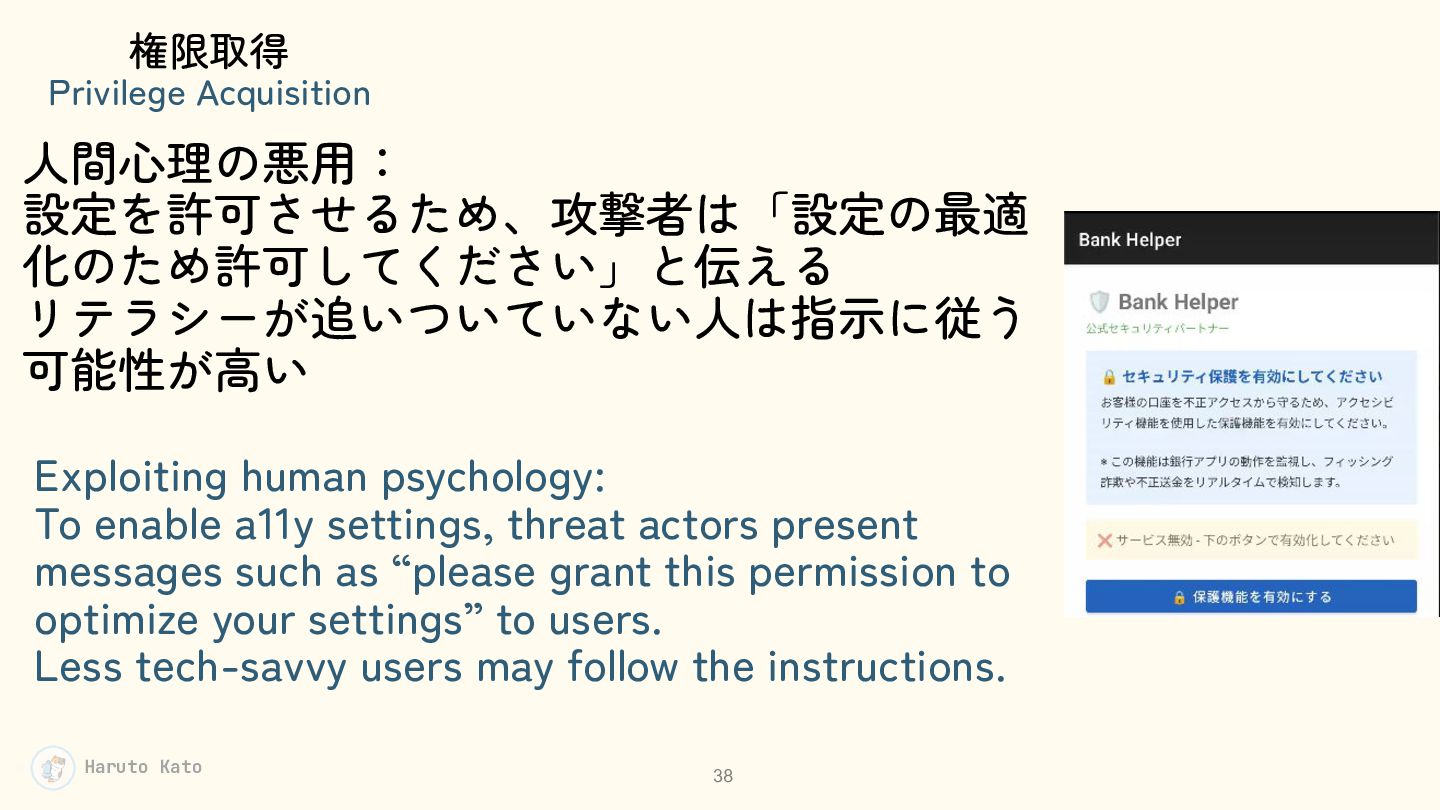
権限取得 Privilege Acquisition 人間心理の悪用: 設定を許可させるため、攻撃者は「設定の最適 化のため許可してください」と伝える リテラシーが追いついていない人は指示に従う 可能性が高い Exploiting human
psychology: To enable a11y settings, threat actors present messages such as “please grant this permission to optimize your settings” to users. Less tech-savvy users may follow the instructions. Haruto Kato 38 -
権限取得 Privilege Acquisition ハッカーらしくない This approach does not seem like
something hackers would do Haruto Kato 40 -
権限取得 Privilege Acquisition Android側のセキュリティが非常に厳しい。 a11yを悪用して自動的に権限を許可させる方法も 対策されている。 Android security is highly
restrictive. It also prevents apps from automatically granting permissions through a11y abuse. Haruto Kato 42 -
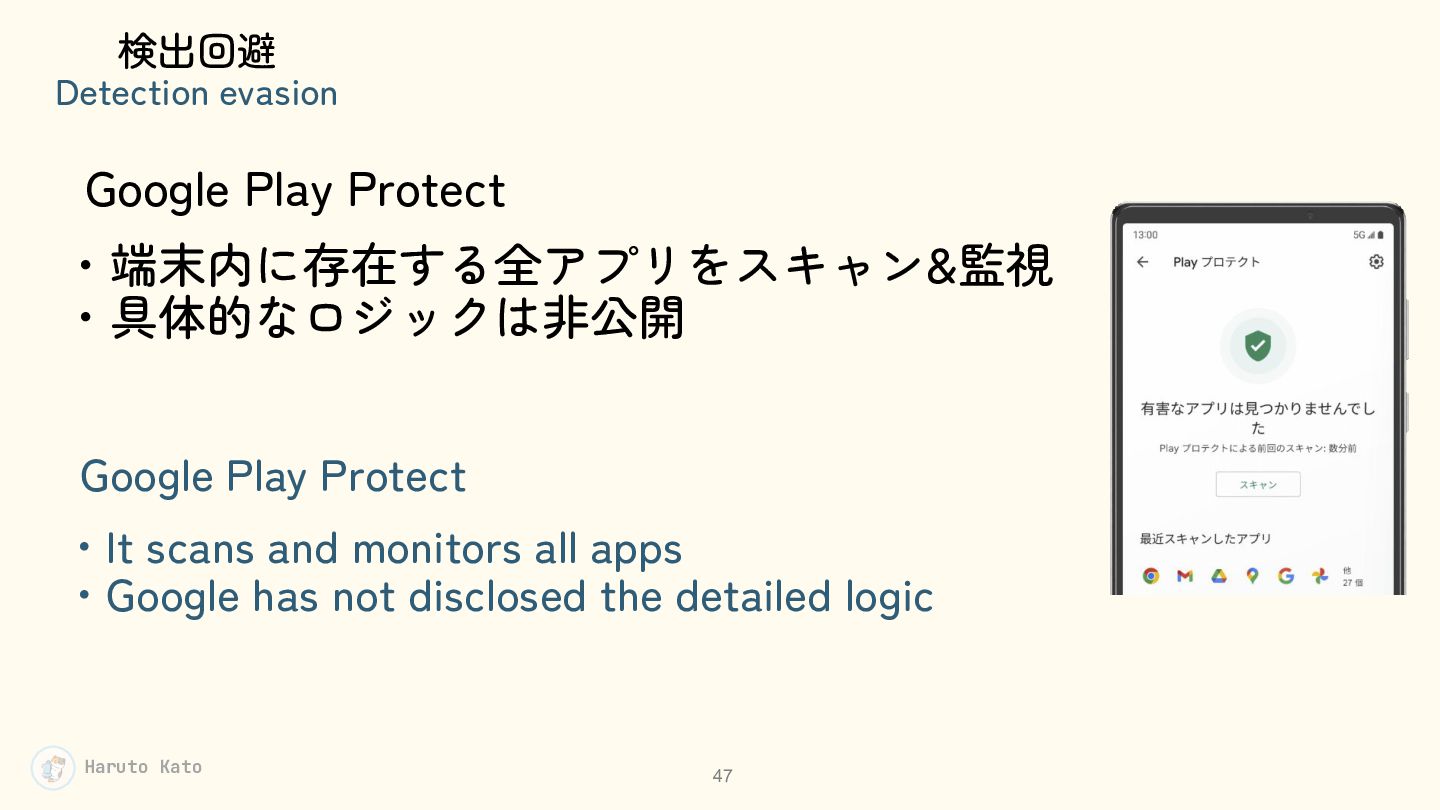
検出回避 Detection evasion Google Play Protect ・端末内に存在する全アプリをスキャン&監視 ・具体的なロジックは非公開 Google Play
Protect ・It scans and monitors all apps ・Google has not disclosed the detailed logic Haruto Kato 47 -
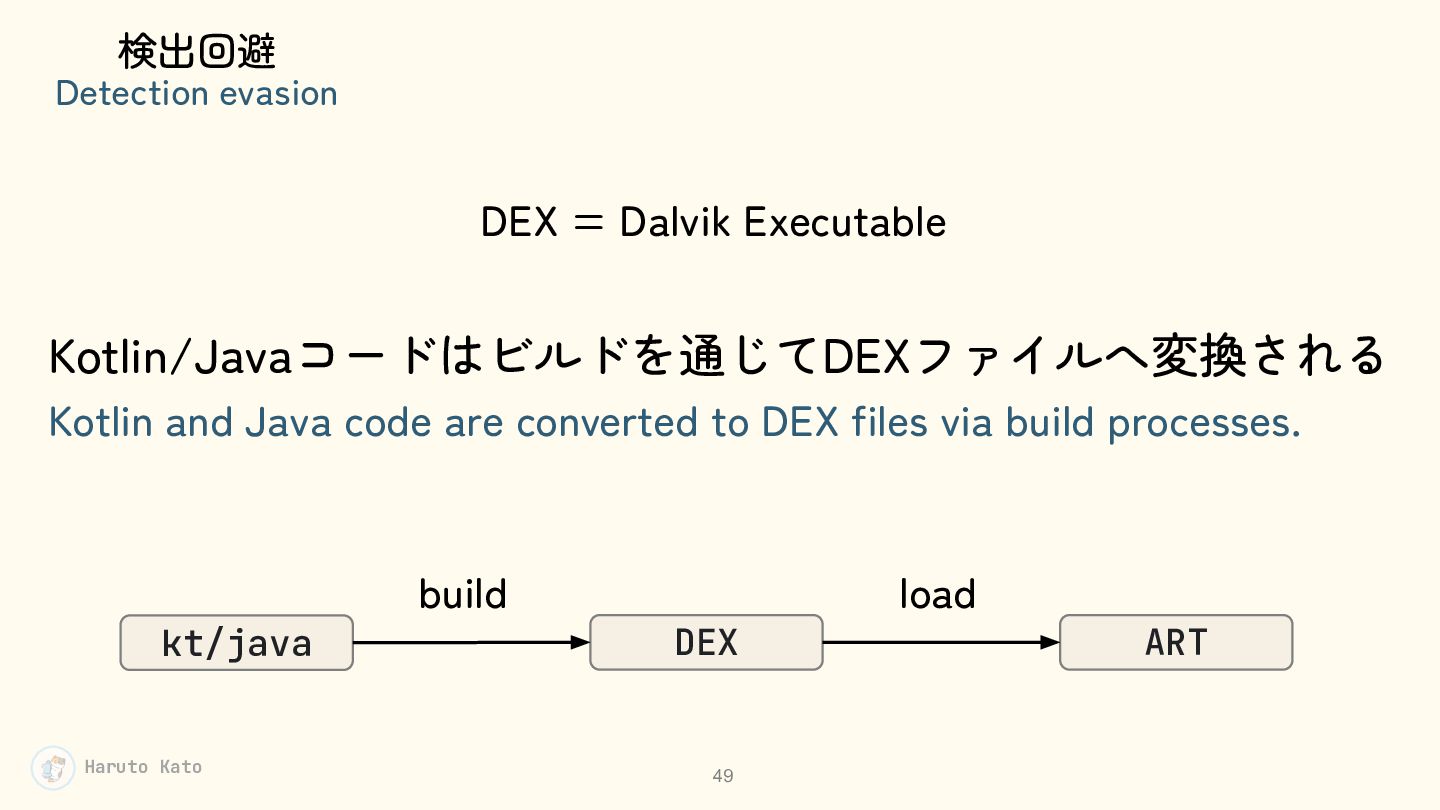
検出回避 Detection evasion DEX = Dalvik Executable Kotlin/Javaコードはビルドを通じてDEXファイルへ変換される Kotlin and
Java code are converted to DEX files via build processes. build kt/java Haruto Kato load DEX 49 ART -
検出回避 Detection evasion 直接実装せずともDEXデータがあれば任意処理が実行可能 With DEX data, arbitrary code can
be executed without implementing it in the app. 攻撃者はこの特性を利用してDEXデータでPayloadを注入 Threat actors abuse the feature and inject payloads through DEX data. Haruto Kato 51 -
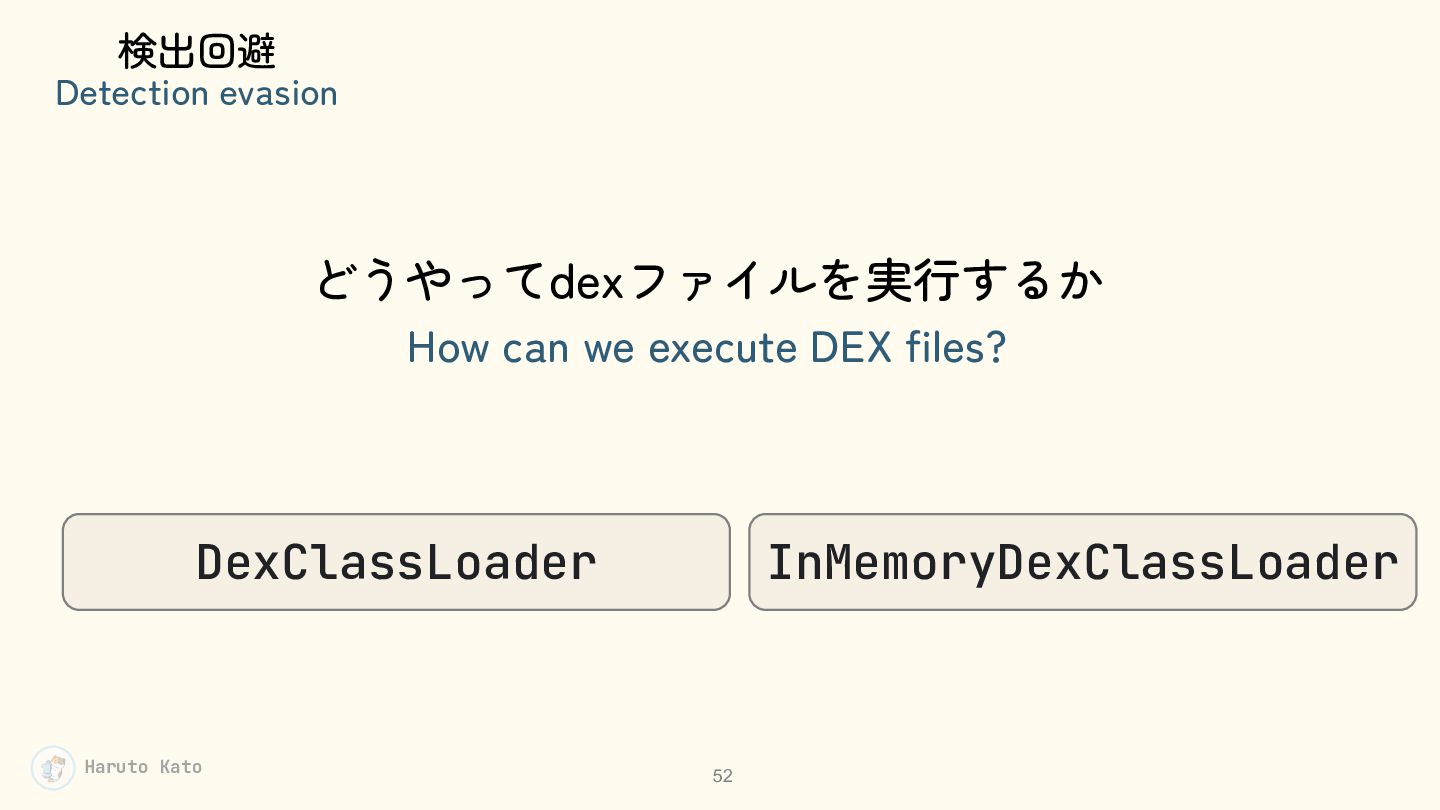
検出回避 Detection evasion どうやってdexファイルを実行するか How can we execute DEX files?
DexClassLoader Haruto Kato InMemoryDexClassLoader 52 -
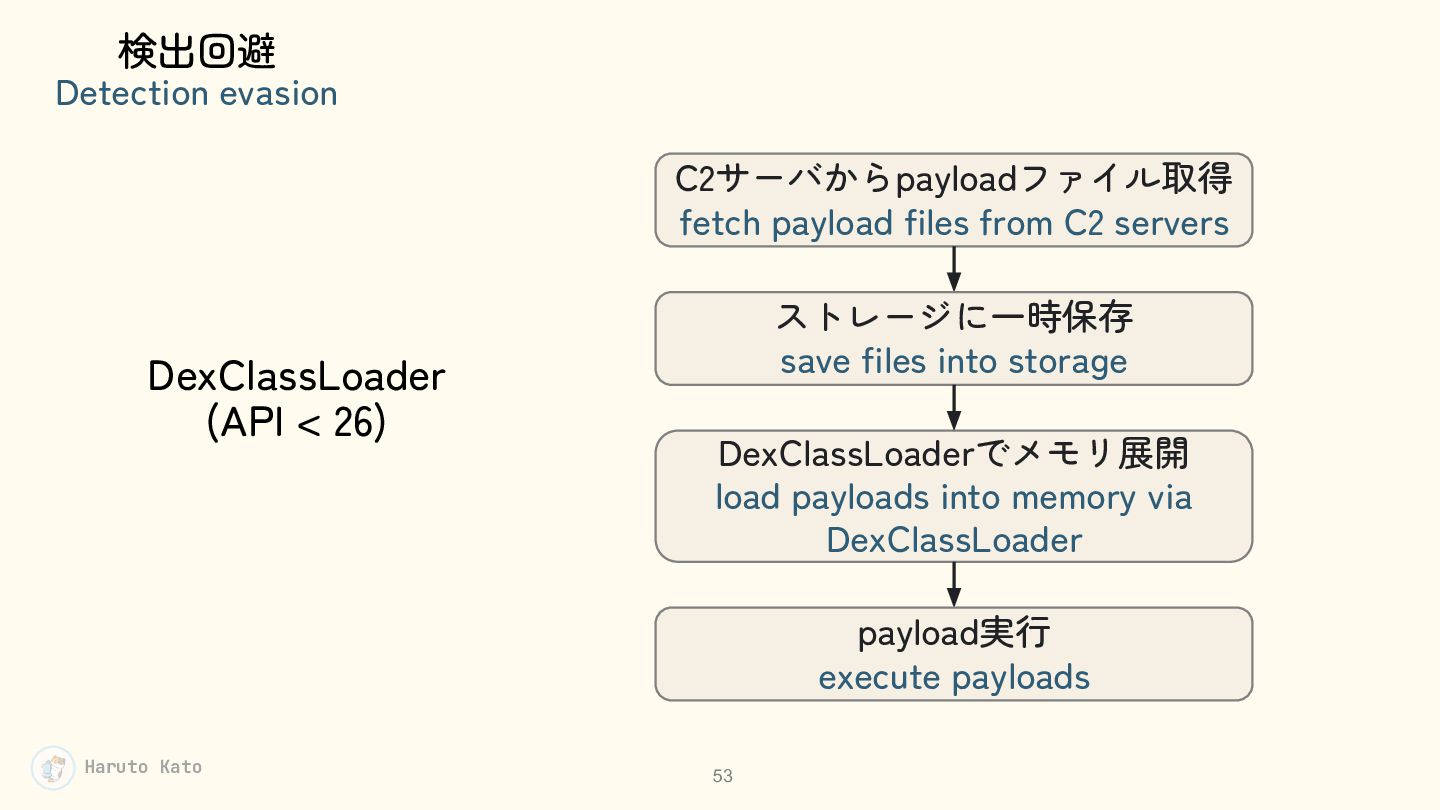
検出回避 Detection evasion C2サーバからpayloadファイル取得 fetch payload files from C2 servers
DexClassLoader (API < 26) ストレージに一時保存 save files into storage DexClassLoaderでメモリ展開 load payloads into memory via DexClassLoader payload実行 execute payloads Haruto Kato 53 -
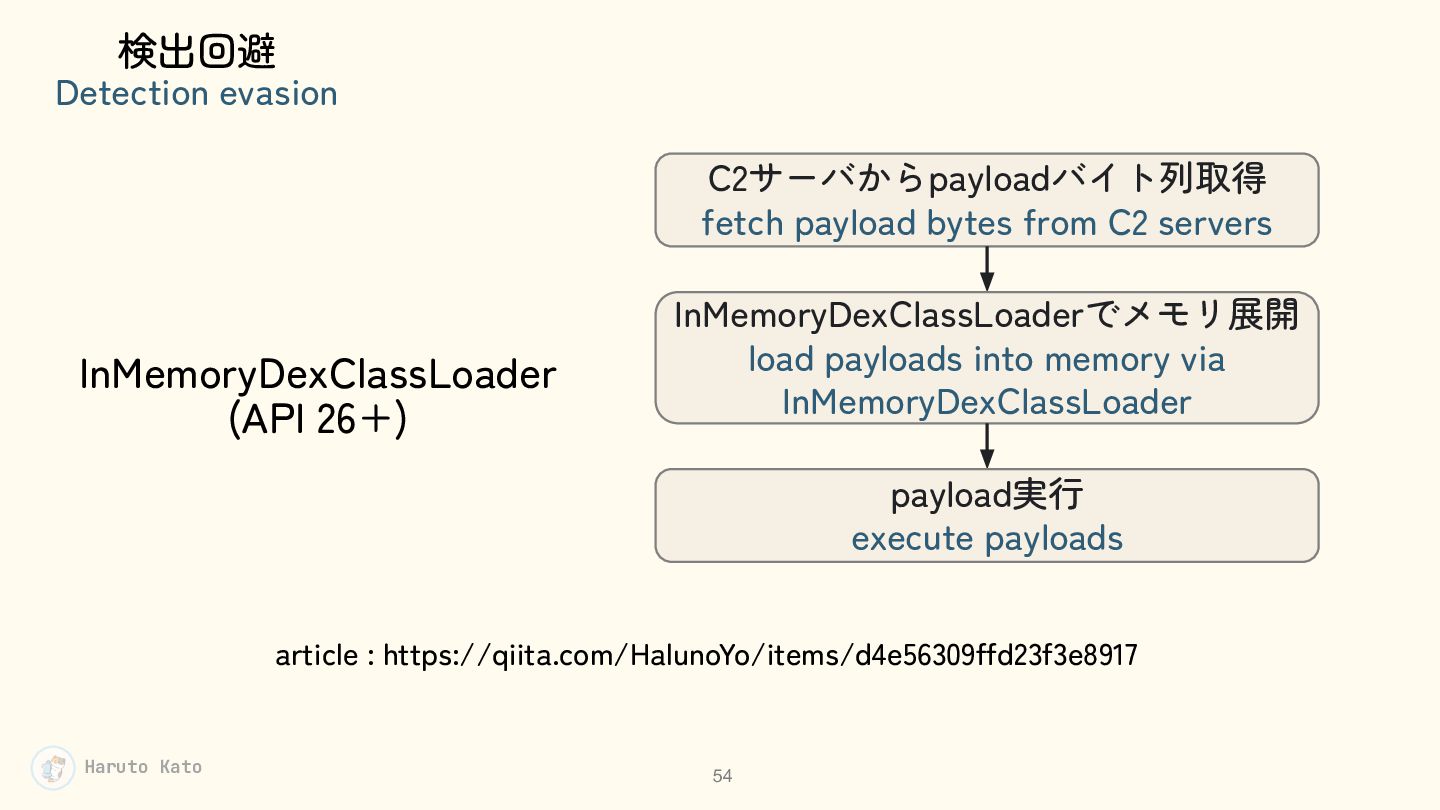
検出回避 Detection evasion C2サーバからpayloadバイト列取得 fetch payload bytes from C2 servers
InMemoryDexClassLoader (API 26+) InMemoryDexClassLoaderでメモリ展開 load payloads into memory via InMemoryDexClassLoader payload実行 execute payloads article : https://qiita.com/HalunoYo/items/d4e56309ffd23f3e8917 Haruto Kato 54 -
タップジャッキング対策 Tapjacking protection オーバーレイがボタンの上にある場合、タッ プしても反応しない If an overlay is placed
over the button, tapping it yields no response. Source : https://developer.android.com/privacy-and-security/risks/tapjacking Haruto Kato 57 -
実行パートで説明したような心理学を悪用して オーバーレイ経由で操作させるマルウェアに有効的 It is effective against malware that exploits human
psychology and tricks users into taking action through overlays. Haruto Kato 58 -
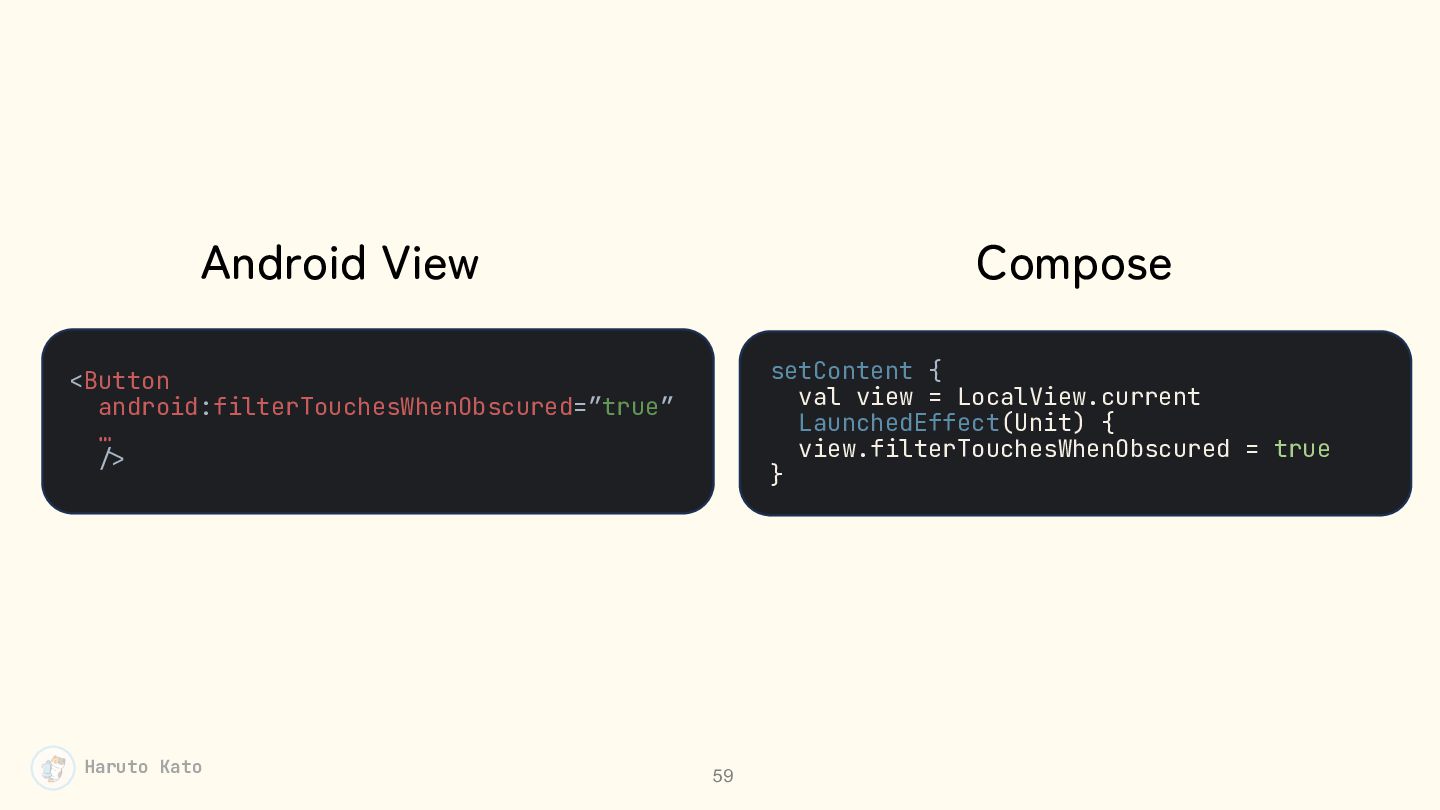
Android View Compose setContent { val view = LocalView.current LaunchedEffect(Unit)
{ view.filterTouchesWhenObscured = true } <Button android:filterTouchesWhenObscured=”true” … /> Haruto Kato 59 -
a11y悪用の本質: 画面に表示される情報を観測できること The essence of A11y abuse is the fact
that it can observe information displayed on the screen. Haruto Kato 61 -
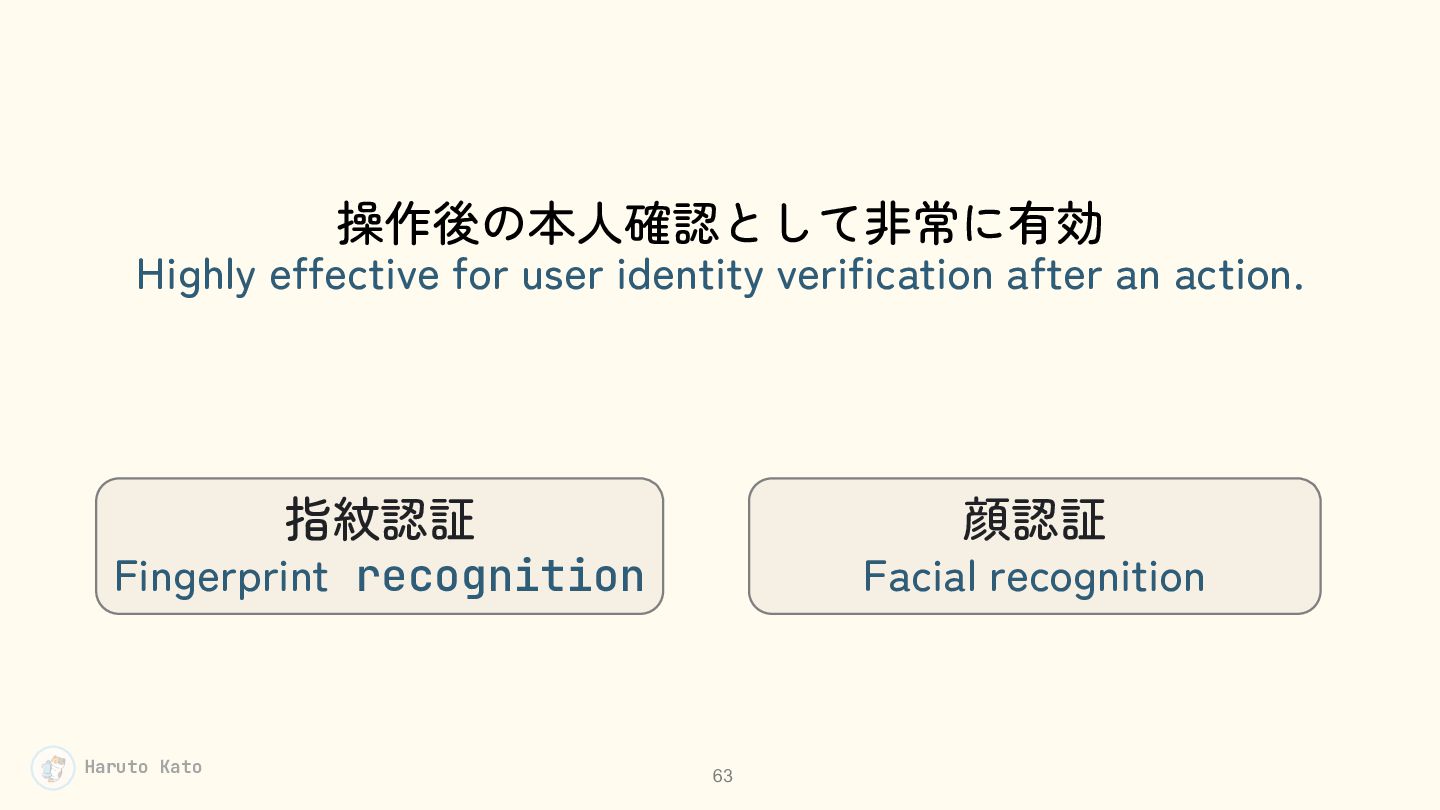
操作後の本人確認として非常に有効 Highly effective for user identity verification after an action.
指紋認証 顔認証 Fingerprint recognition Facial recognition Haruto Kato 63 -
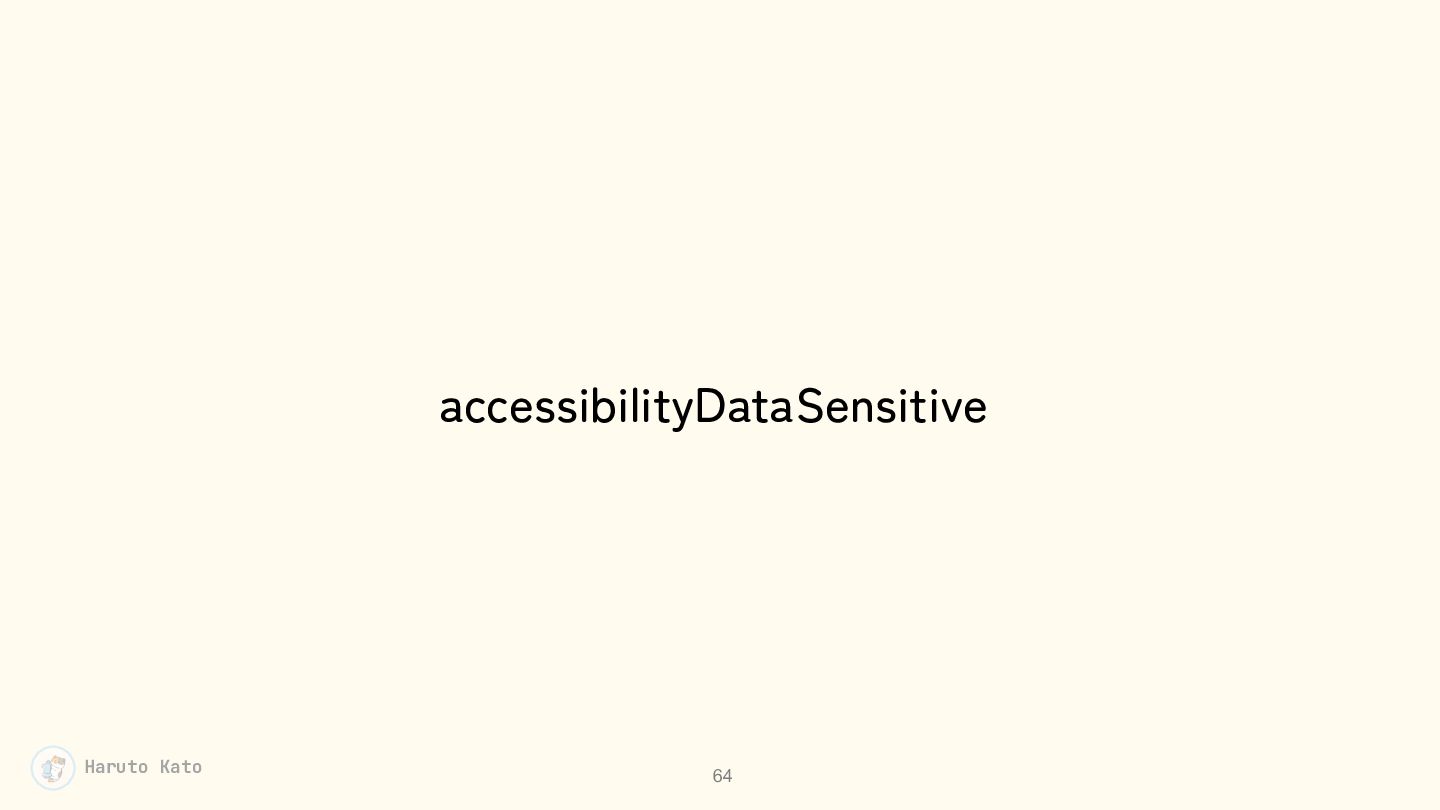
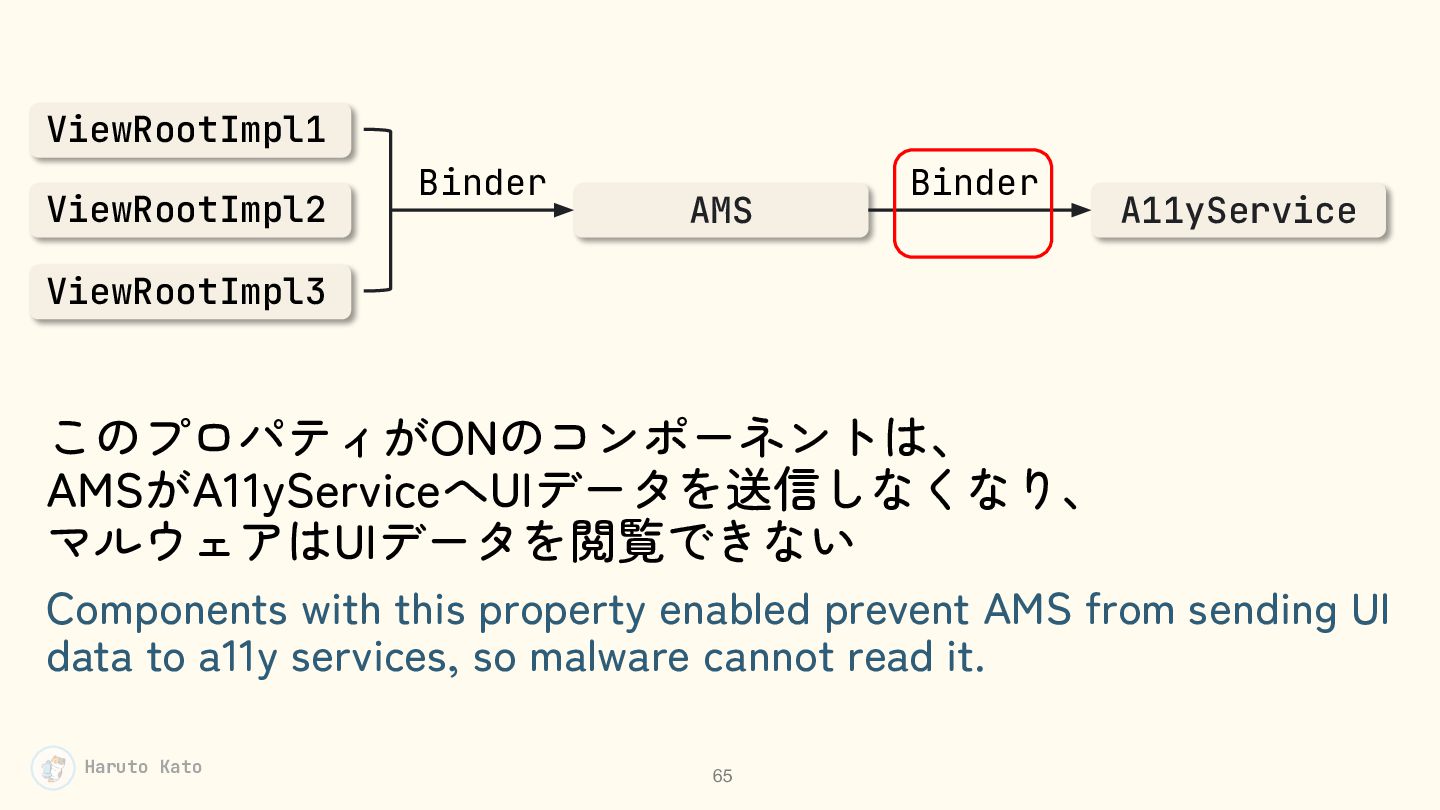
ViewRootImpl1 ViewRootImpl2 Binder AMS Binder A11yService ViewRootImpl3 このプロパティがONのコンポーネントは、 AMSがA11yServiceへUIデータを送信しなくなり、 マルウェアはUIデータを閲覧できない
Components with this property enabled prevent AMS from sending UI data to a11y services, so malware cannot read it. Haruto Kato 65 -
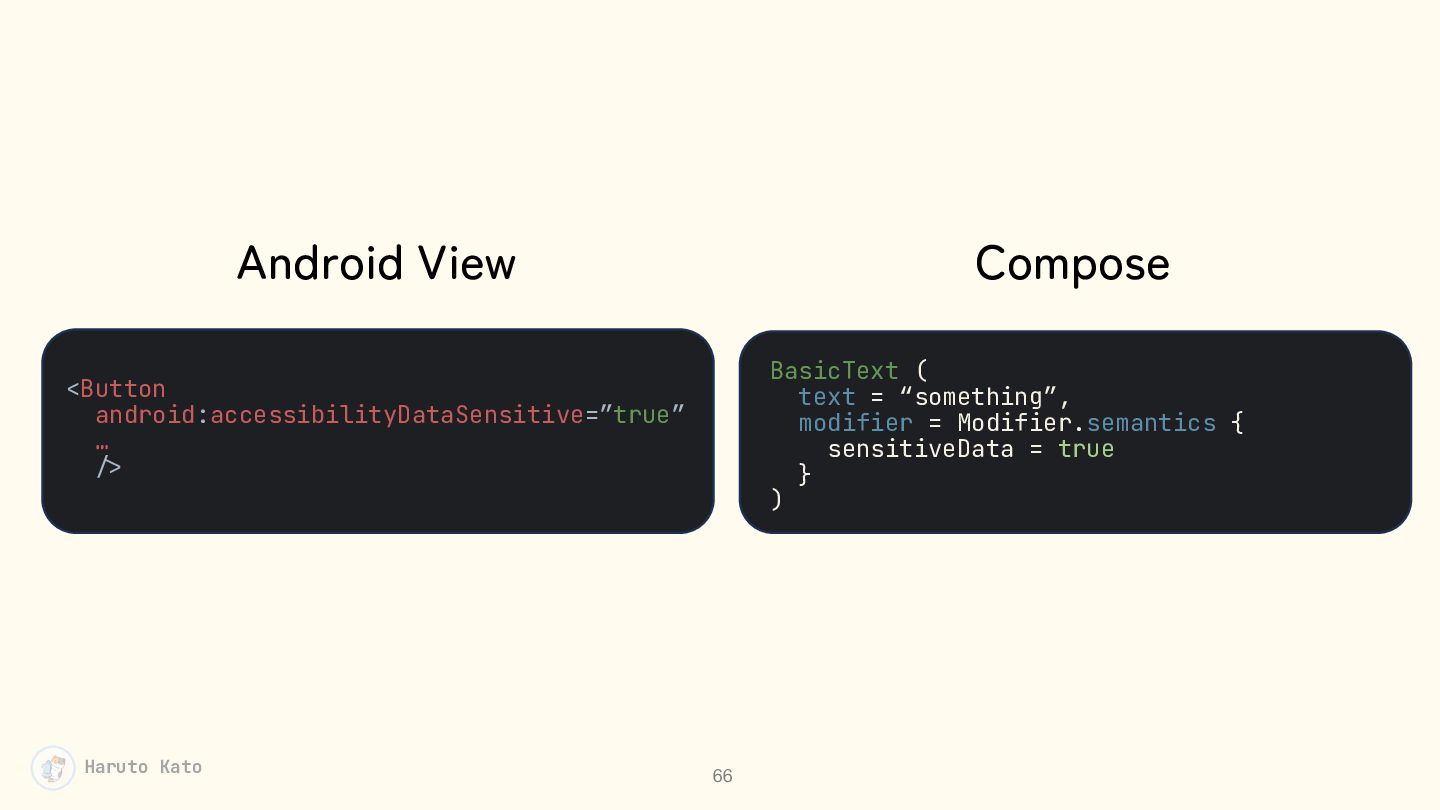
Android View Compose BasicText ( text = “something”, modifier =
Modifier.semantics { sensitiveData = true } ) <Button android:accessibilityDataSensitive=”true” … /> Haruto Kato 66 -
これは補助アプリ側が宣言するフラグ ただ、我々のアプリ側にも関係ある This flag is declared by the accessibility app,
but it also affects our apps. Haruto Kato 68 -
accessibilityDataSensitiveがONだと正規補助アプリも データが閲覧できない問題 If accessibilityDataSensitive is enabled, even legitimate accessibility apps
cannot view the data Haruto Kato 69 -
accessibilityDataSensitiveがONでもデータが読める しかし、ストア審査が厳密。 These apps can receive data even if other
apps have the accessibilityDataSensitive attribute. However, reviews of these apps are rigorous. Source : https://support.google.com/googleplay/android-developer/answer/10964491 Haruto Kato 71 -
これらの方法は確かにリスク低減できる しかし、考慮しないといけないポイントもある These approaches mitigate risks. However, there are several
factors we need to consider. Haruto Kato 76 -
a11y機能を必要としてるユーザーに対して MFAは適用しても大丈夫か? Can we apply MFA to people who need
a11y features? Haruto Kato 77 -
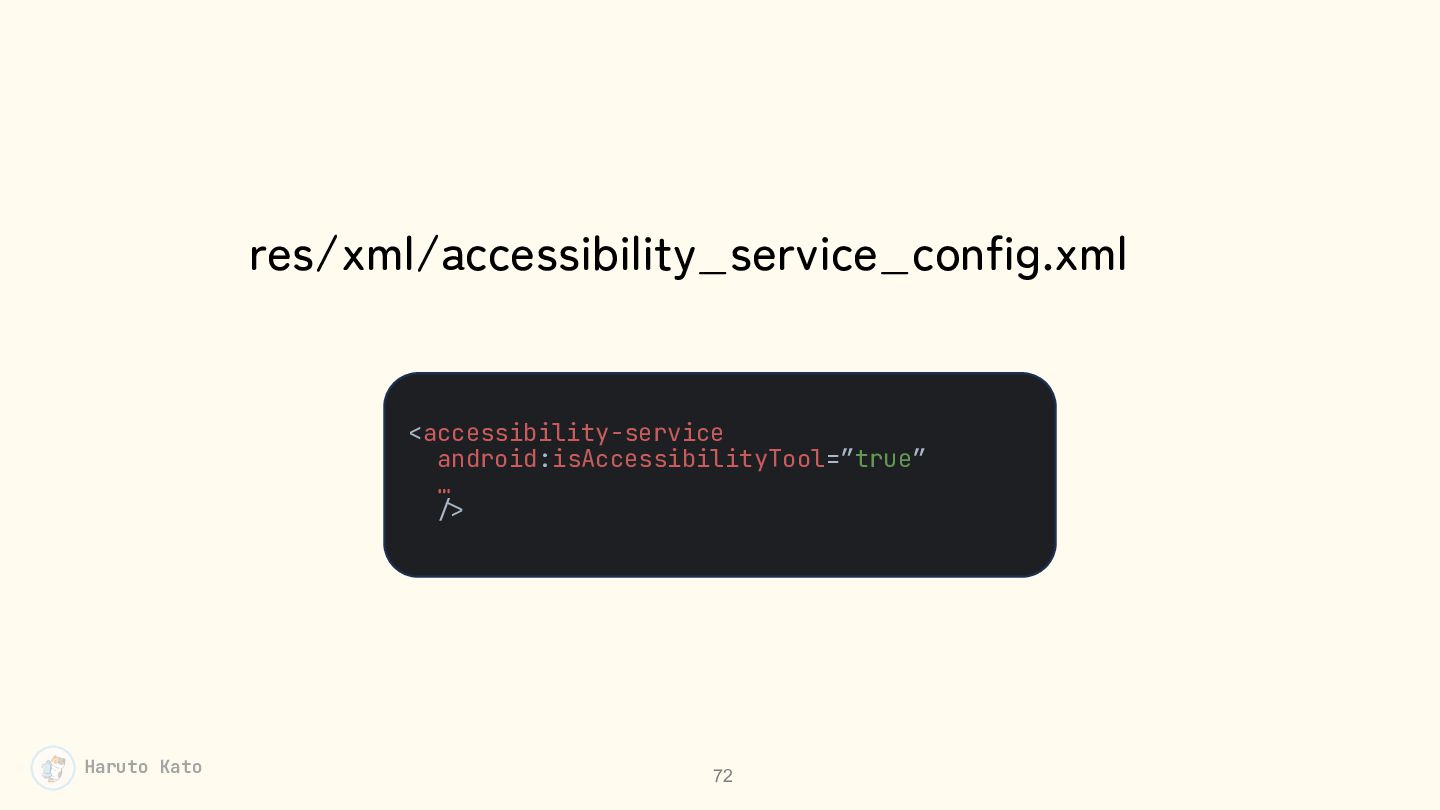
isAccessibilityTool 審査が厳しい? 無害なアプリとして審査提出を行い、期間 を置いてからpayloadを注入したら? Reviews are rigorous? Then what can
we do if threat actors submit a seemingly legitimate app and inject payloads after waiting for a long dormancy period? Haruto Kato 78 -
攻撃コストを高める 狙いは攻撃者に攻撃を諦めさせる Increase the cost of attacks. The intention is
to discourage threat actors from attacking. Haruto Kato 82 -
accessibilityDataSensitive / isAccessibilityTool 審査を通すのがコストかかる もし、後からpayloads流してバレたら待機した期間が水の泡 Passing reviews takes a lot
of time and effort. If threat actors inject payloads later and get caught, the months they spent waiting go to waste. MFA どうやってユーザーを騙し、そして認証させるか? How to deceive users and make them authenticate? Haruto Kato 83 -
被害軽減。 狙いは被害を被ることを前提とし、それらを最小限に収める こと Limit the blast radius. The intention is
to assume that damage will occur and minimize it. Haruto Kato 84 -
リスクベース認証 ユーザーの振る舞いが普段と異なる挙動をした場合 追加の本人確認を求める Risk-Based Authentication If a user's behavior differs
from their usual pattern, apps request additional identity verification. Haruto Kato 85 -
いくつか手法を紹介しました メリット&デメリットを考慮して対策を検討 してみましょう! I have explained several approaches. Let's weigh
the options against their advantages and disadvantages! Haruto Kato 86 -
ここまで、a11y機能は良い方向としても悪い方向としても使 われるとお伝えしてきました この双方向性をセッションを通じてお伝えしたかったです So far, I have explained that a11y
features can be utilized for both good and bad purposes. This double-edged nature is what I’d like you to know. Haruto Kato 88 -
セキュリティ対策はモバイル側でのみ行うのは困難。 よって、バックエンドやプロダクトセキュリティチー ムと協力する必要があります It is extremely difficult for mobile teams
to mitigate security risks on their own. Therefore, we need to collaborate with other teams such as back-end and product security teams. Haruto Kato 89 -
セキュリティ対策はコストが高く、何も発生しないと過 剰だったか?と考えるが、それはセキュリティが正しく 機能してる証 Mitigating security risks is costly and we
might think that it was excessive if no problems occurred. However, it means that the mitigation is working as intended. Haruto Kato 90 -
Ariadne AIエージェント向け自作MCP It’s an MCP tool for AI agents コミット前のテスト時、テスト実施関数を最小限にしてテスト
時間削減及びエージェントループを加速させます! Minimize the tests AI agents run before committing – faster feedback in the agent loop! Haruto Kato 92