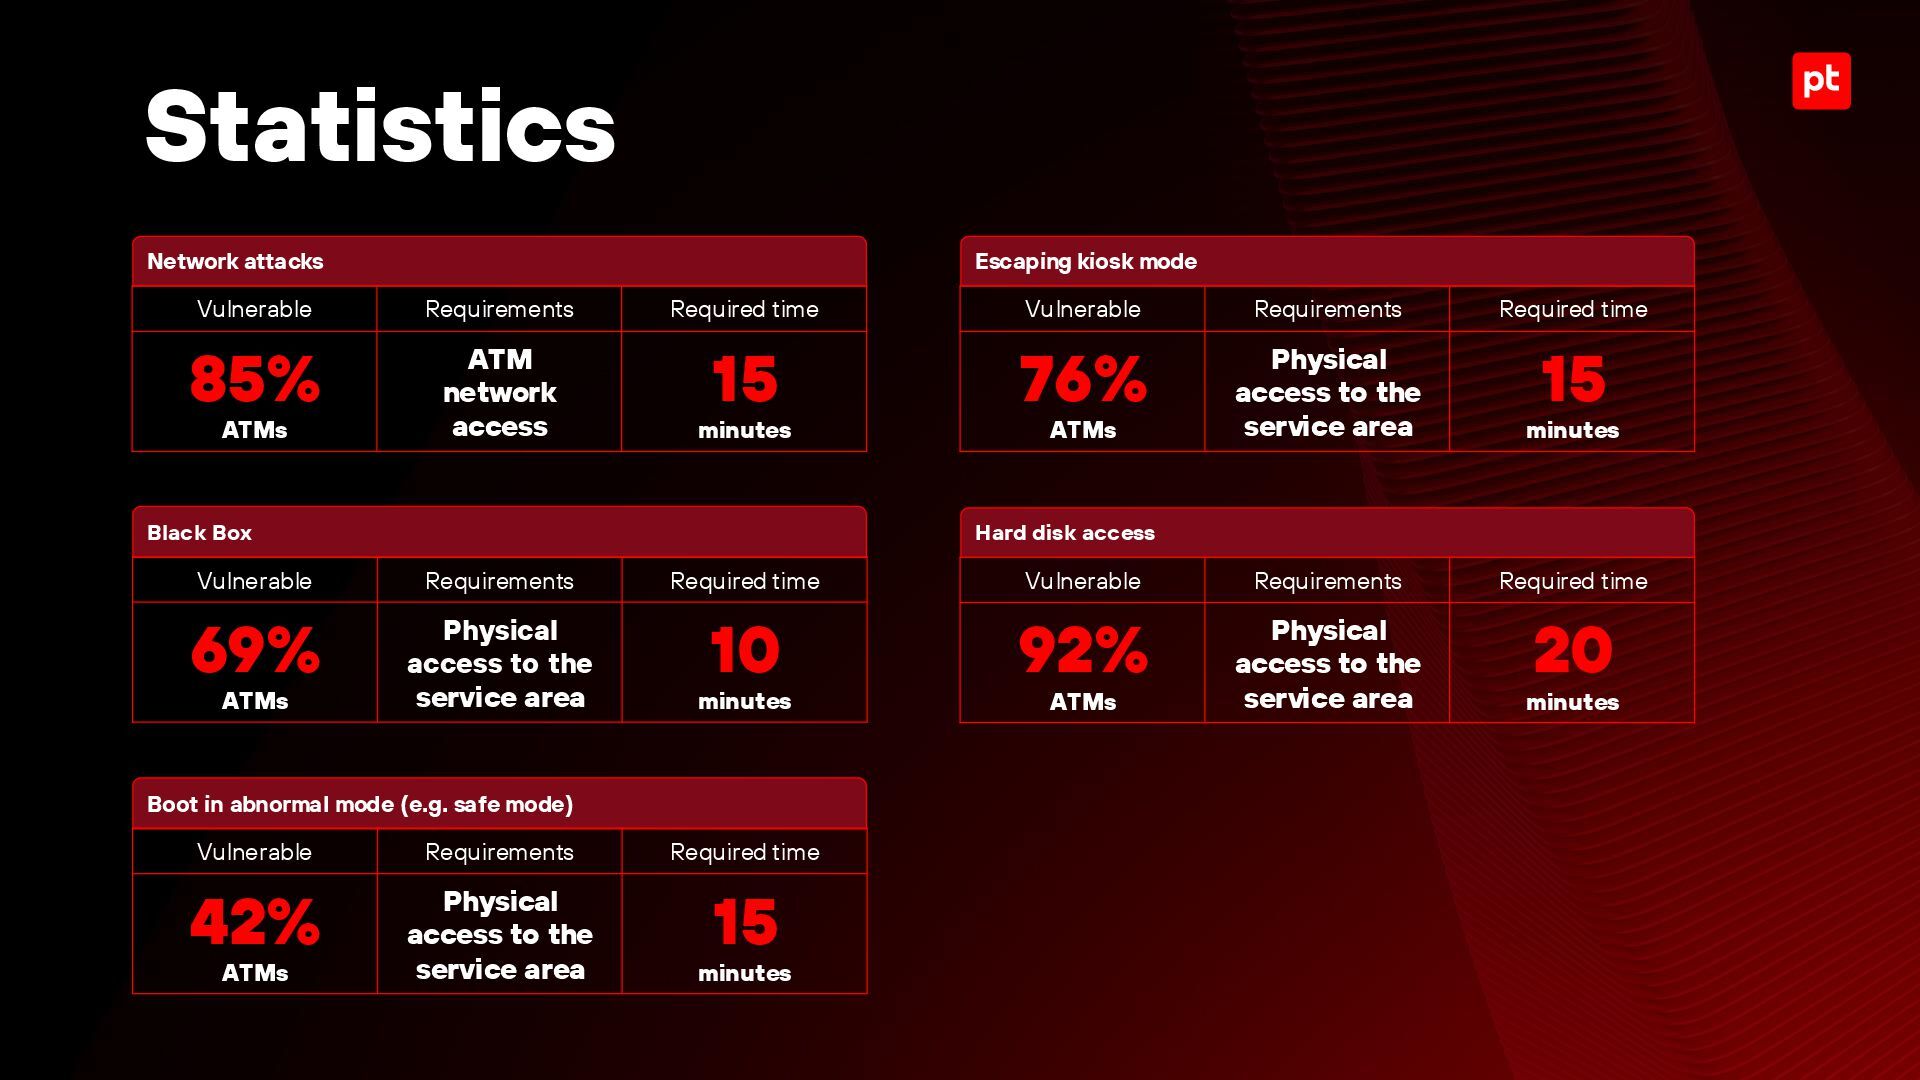
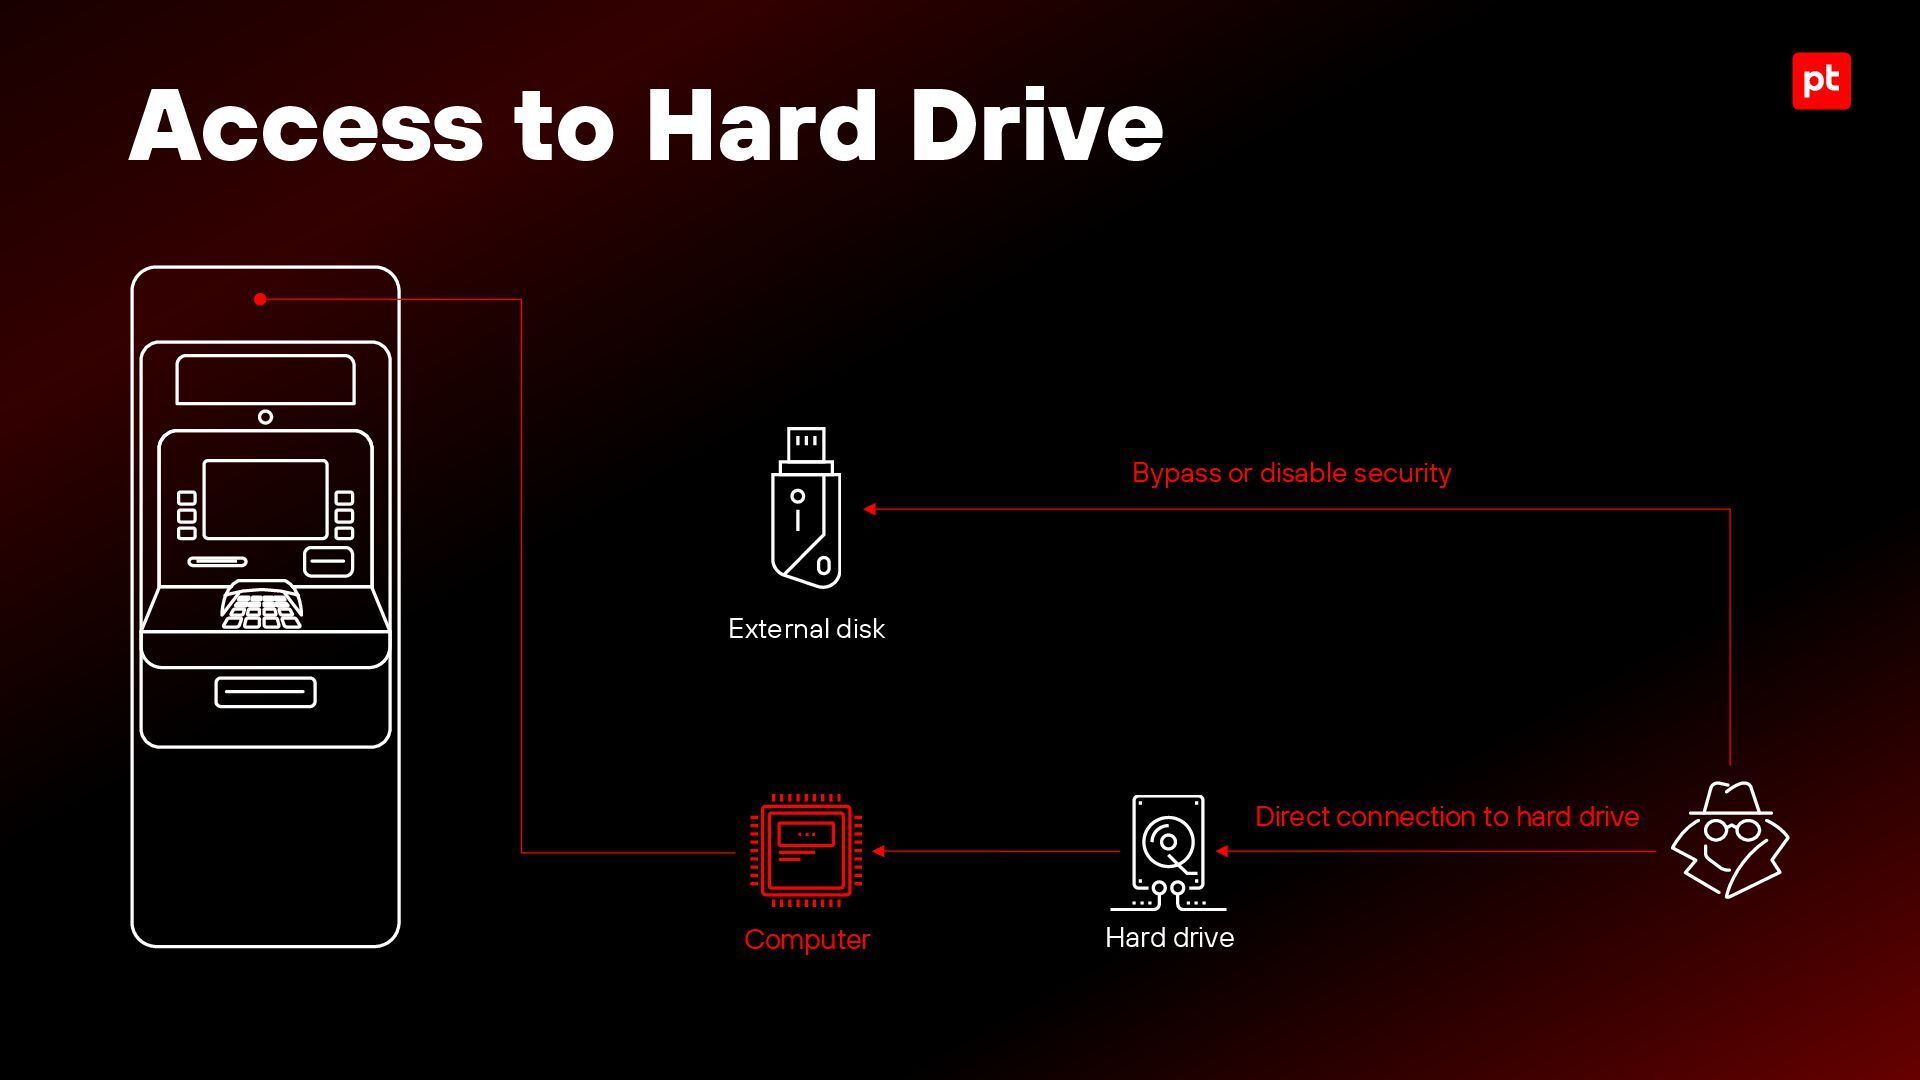
network access 15 minutes Black Box Vulnerable Requirements Required time 69% ATMs Physical access to the service area 10 minutes Boot in abnormal mode (e.g. safe mode) Vulnerable Requirements Required time 42% ATMs Physical access to the service area 15 minutes Escaping kiosk mode Vulnerable Requirements Required time 76% ATMs Physical access to the service area 15 minutes Hard disk access Vulnerable Requirements Required time 92% ATMs Physical access to the service area 20 minutes
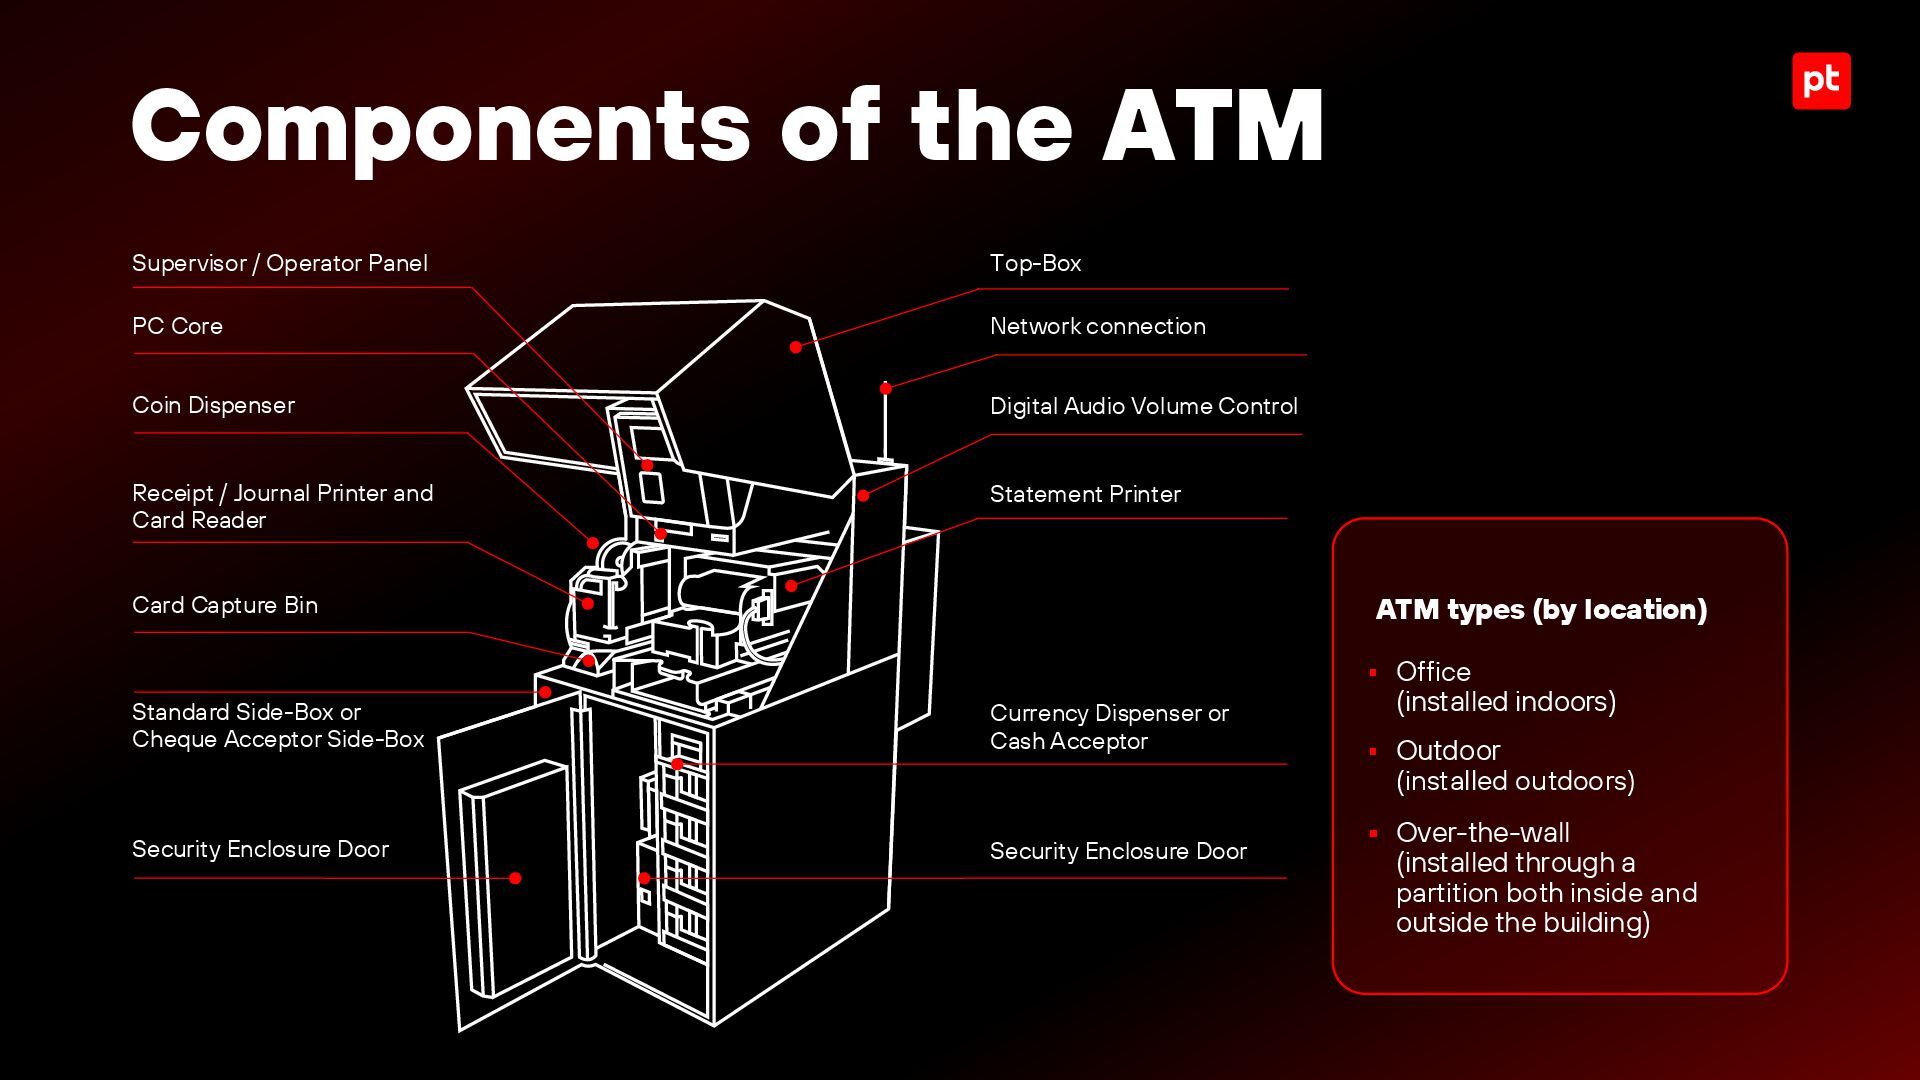
(installed indoors) ▪ Outdoor (installed outdoors) ▪ Over-the-wall (installed through a partition both inside and outside the building) Supervisor / Operator Panel PC Core Coin Dispenser Receipt / Journal Printer and Card Reader Card Capture Bin Standard Side-Box or Cheque Acceptor Side-Box Security Enclosure Door Top-Box Network connection Digital Audio Volume Control Statement Printer Currency Dispenser or Cash Acceptor Security Enclosure Door
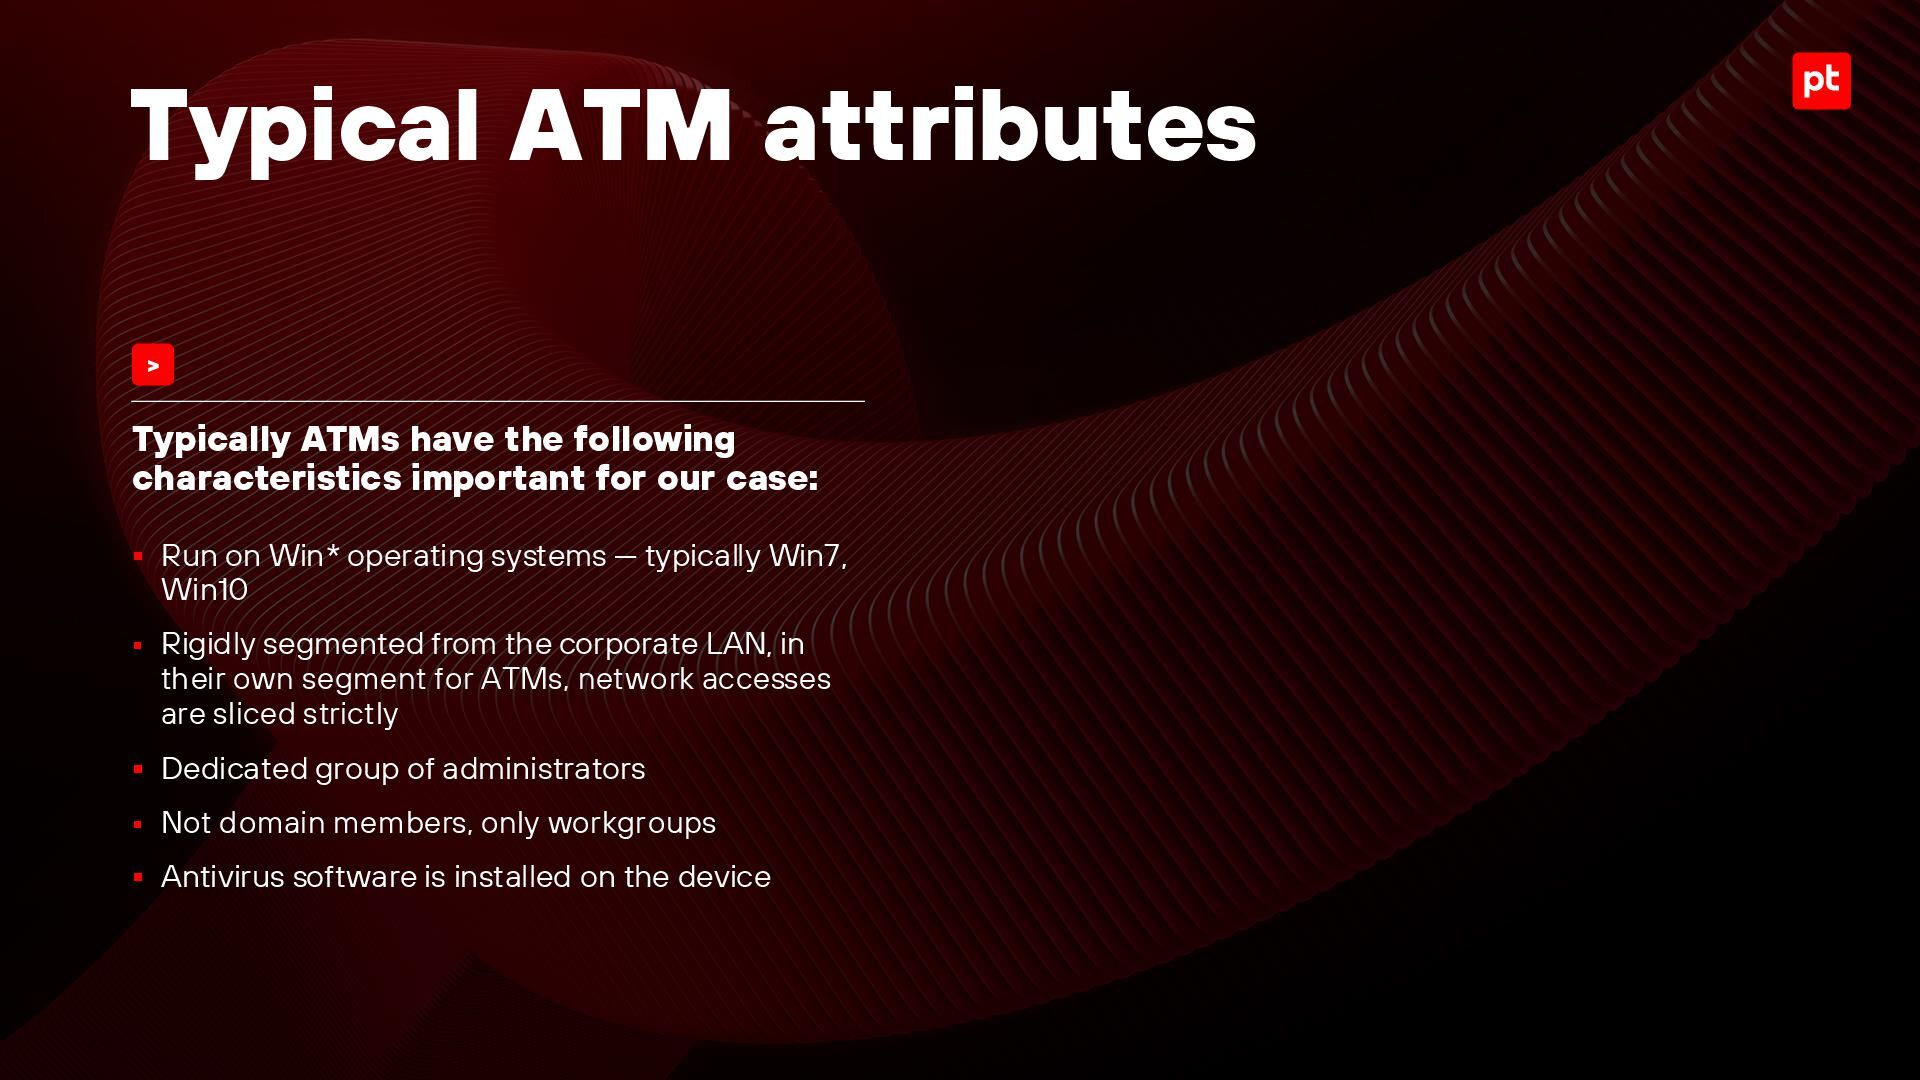
Typical ATM attributes ▪ Run on Win* operating systems — typically Win7, Win10 ▪ Rigidly segmented from the corporate LAN, in their own segment for ATMs, network accesses are sliced strictly ▪ Dedicated group of administrators ▪ Not domain members, only workgroups ▪ Antivirus software is installed on the device >
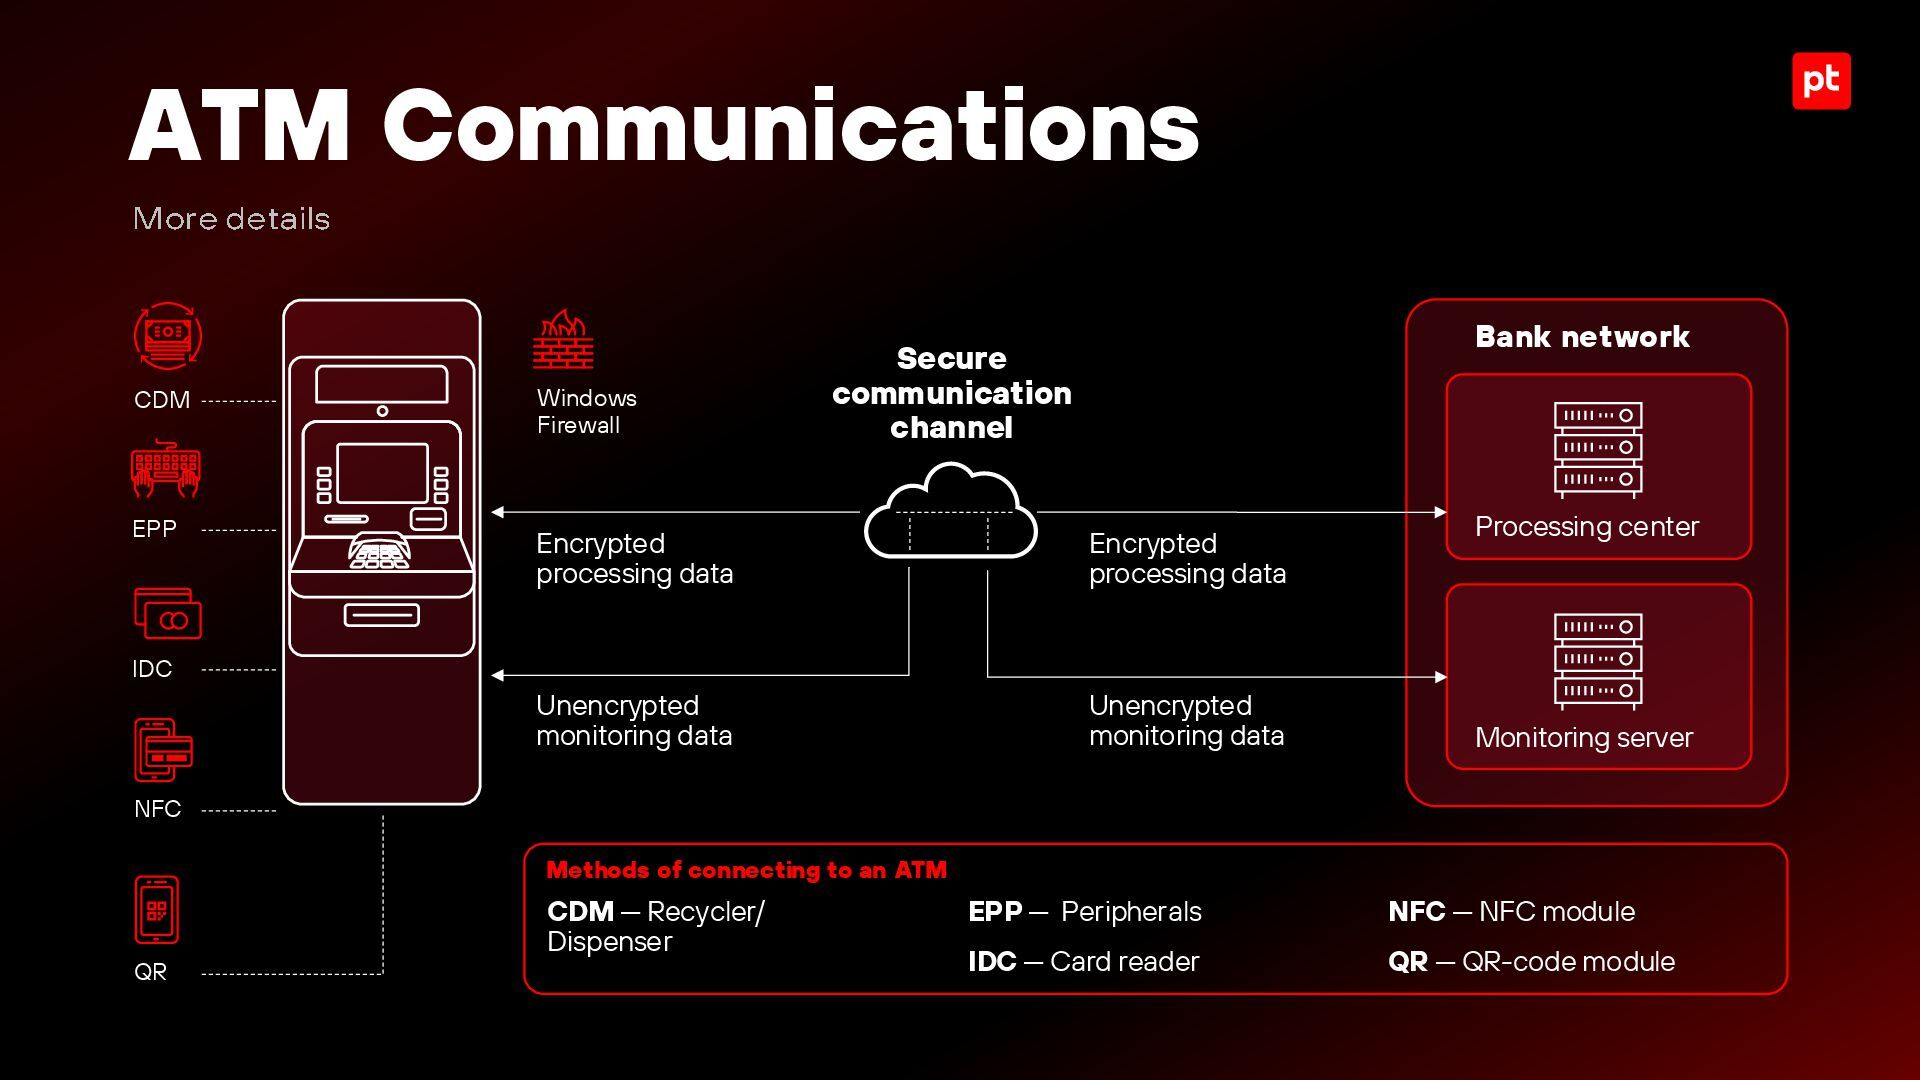
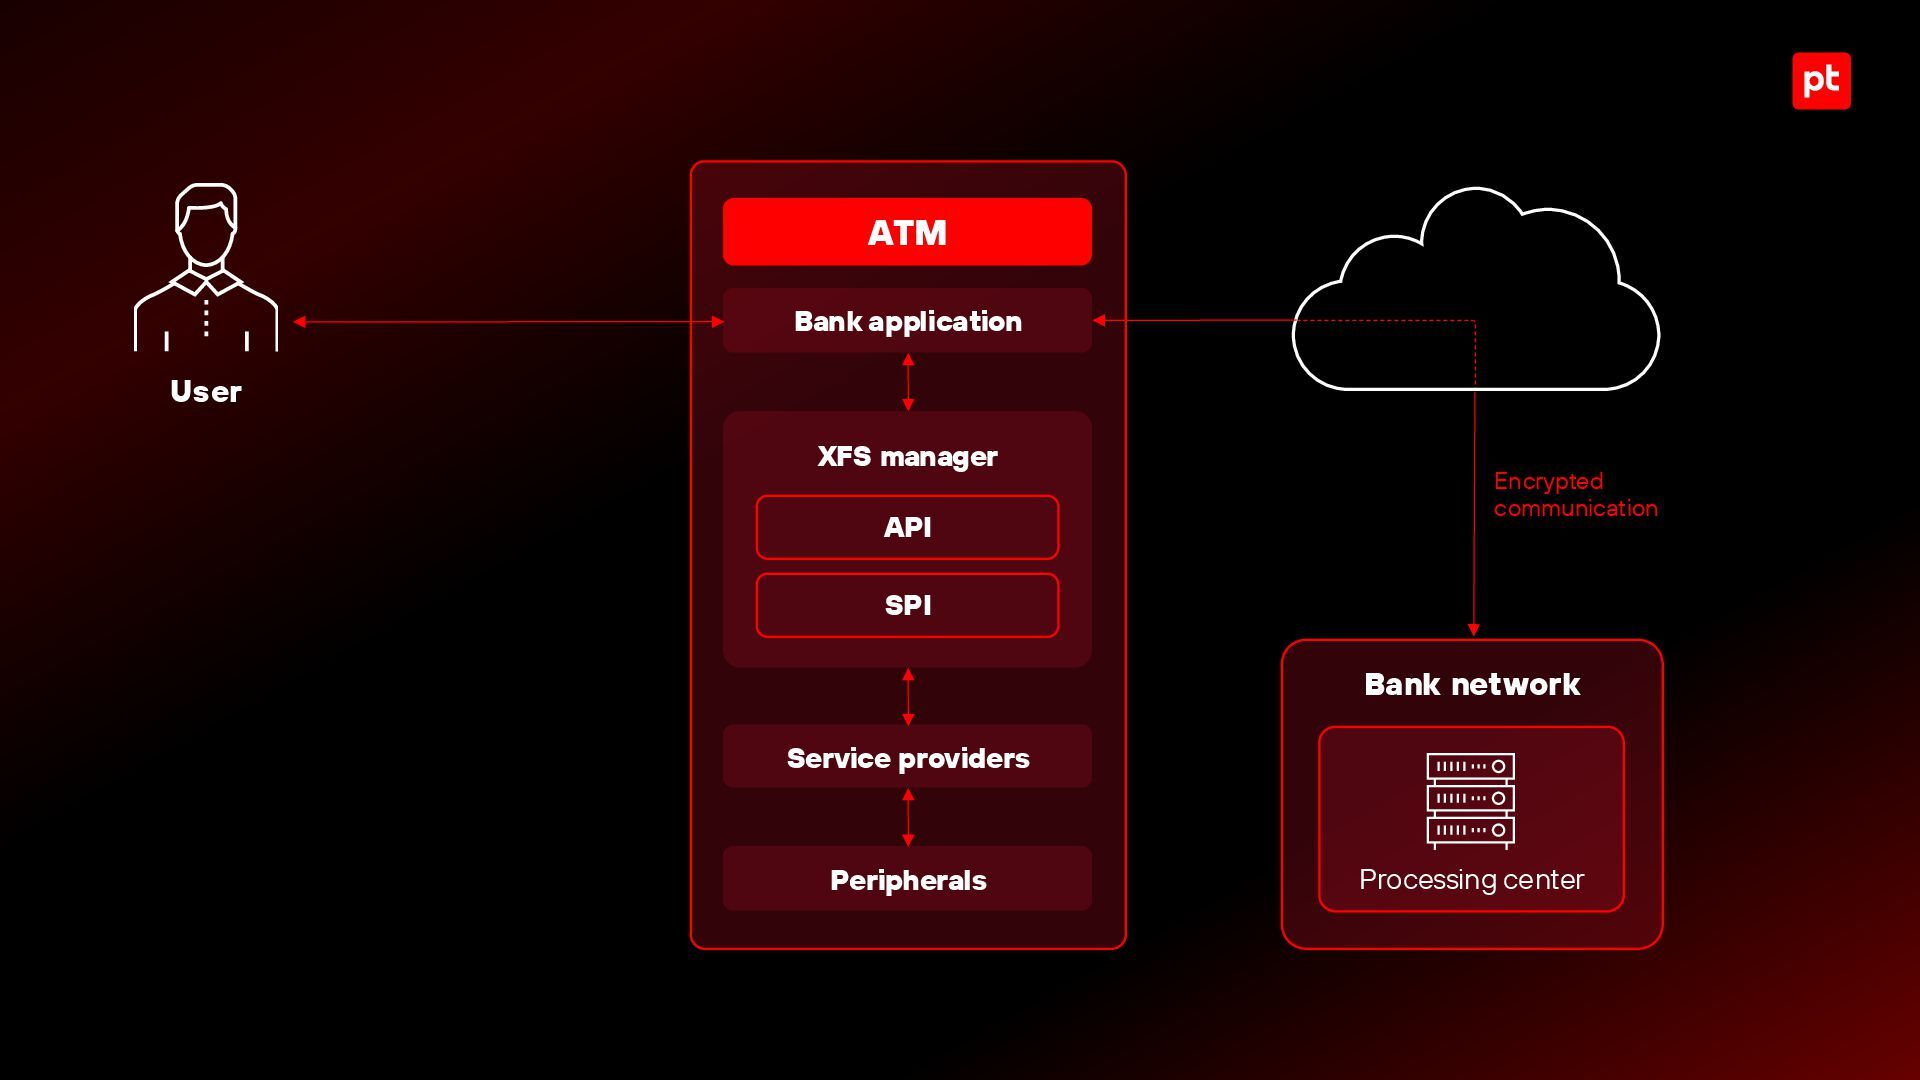
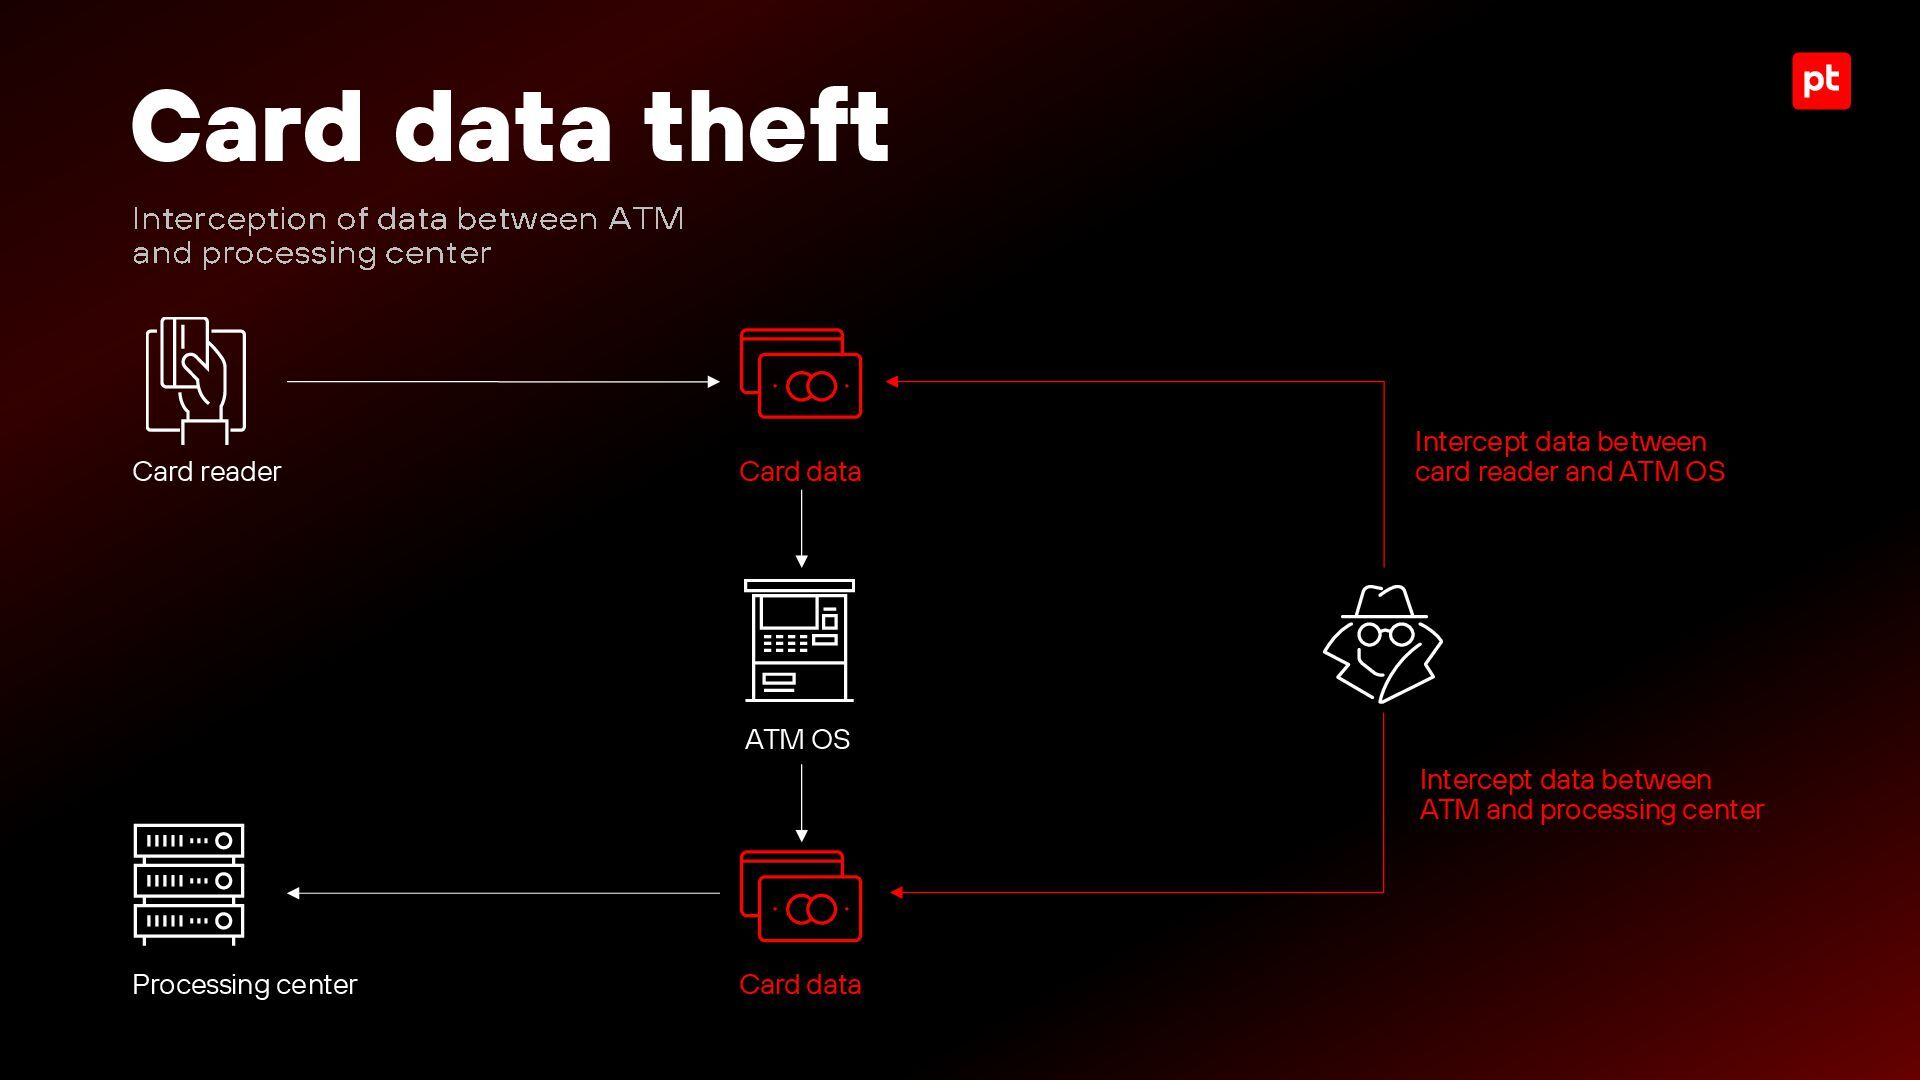
center Monitoring server Bank network Secure communication channel Methods of connecting to an ATM CDM — Recycler/ Dispenser EPP — Peripherals IDC — Card reader NFC — NFC module QR — QR-code module Encrypted processing data Unencrypted monitoring data Unencrypted monitoring data Encrypted processing data
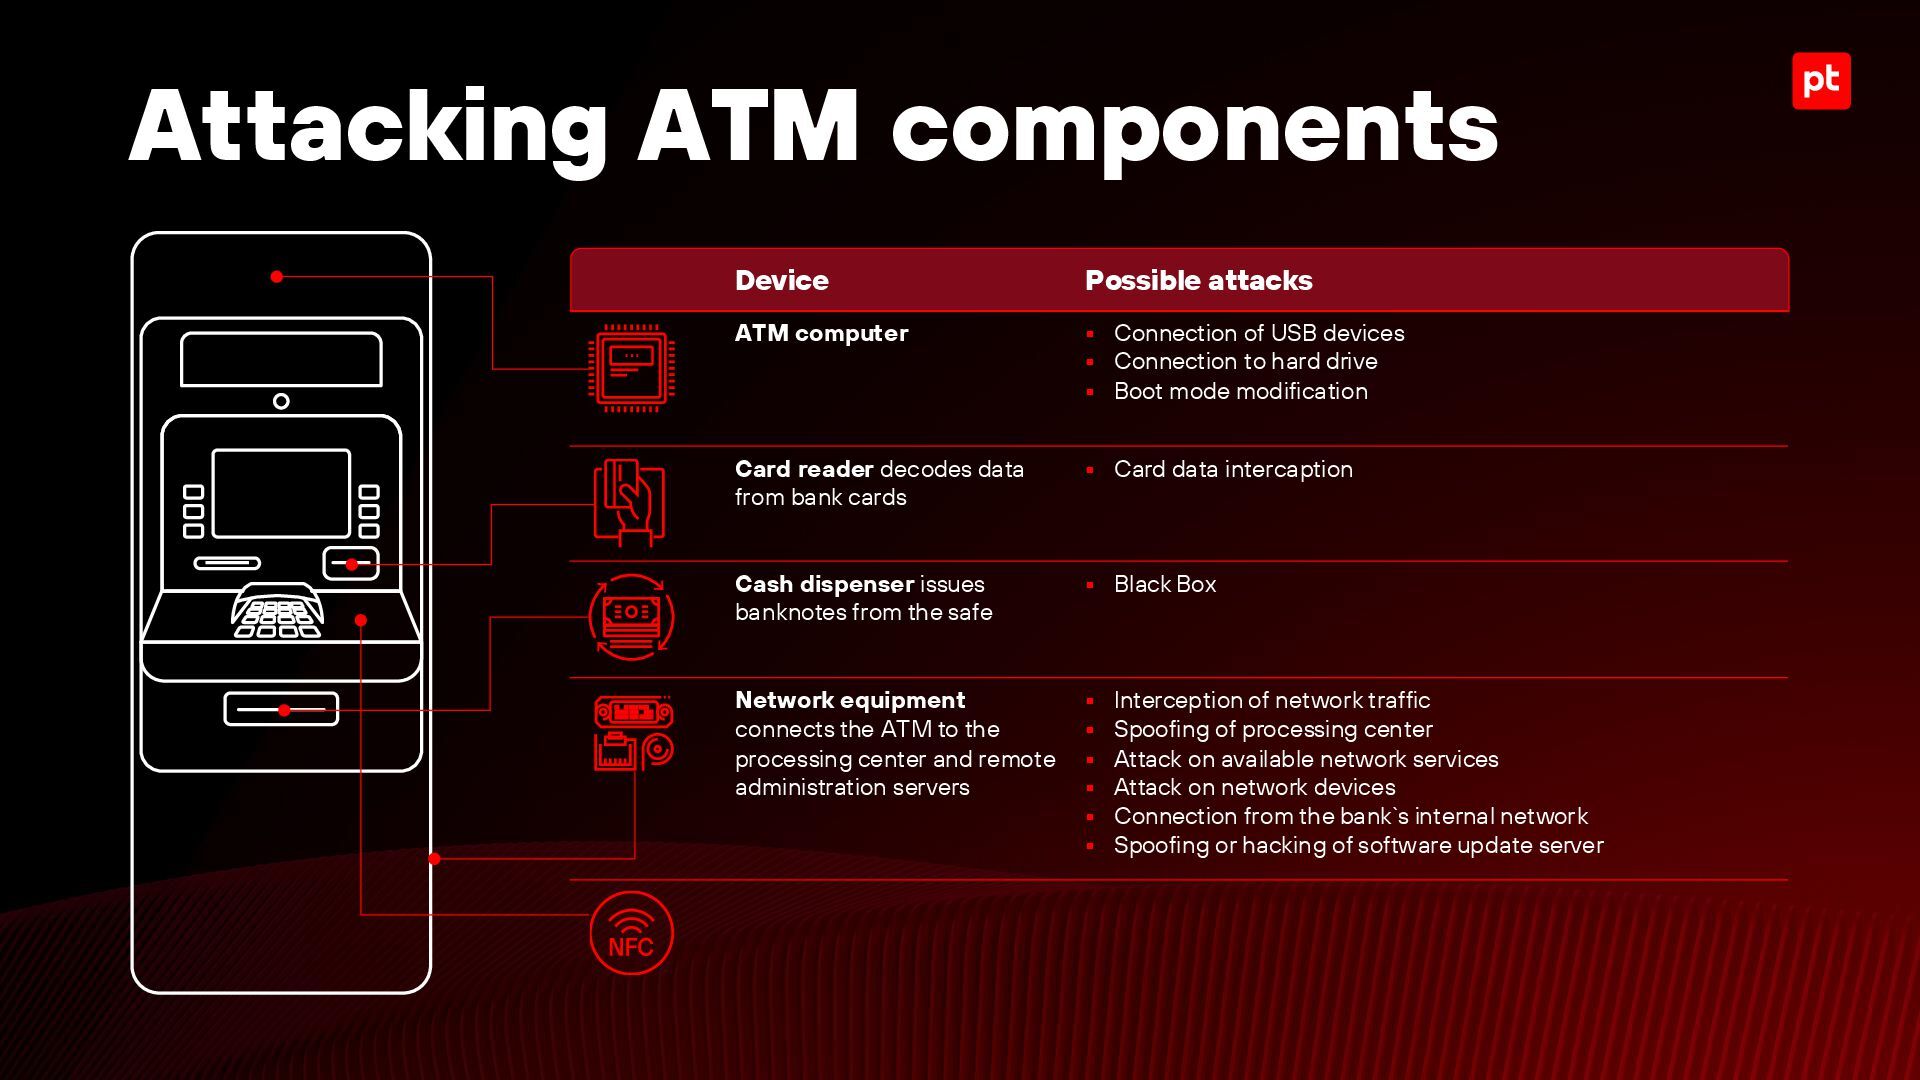
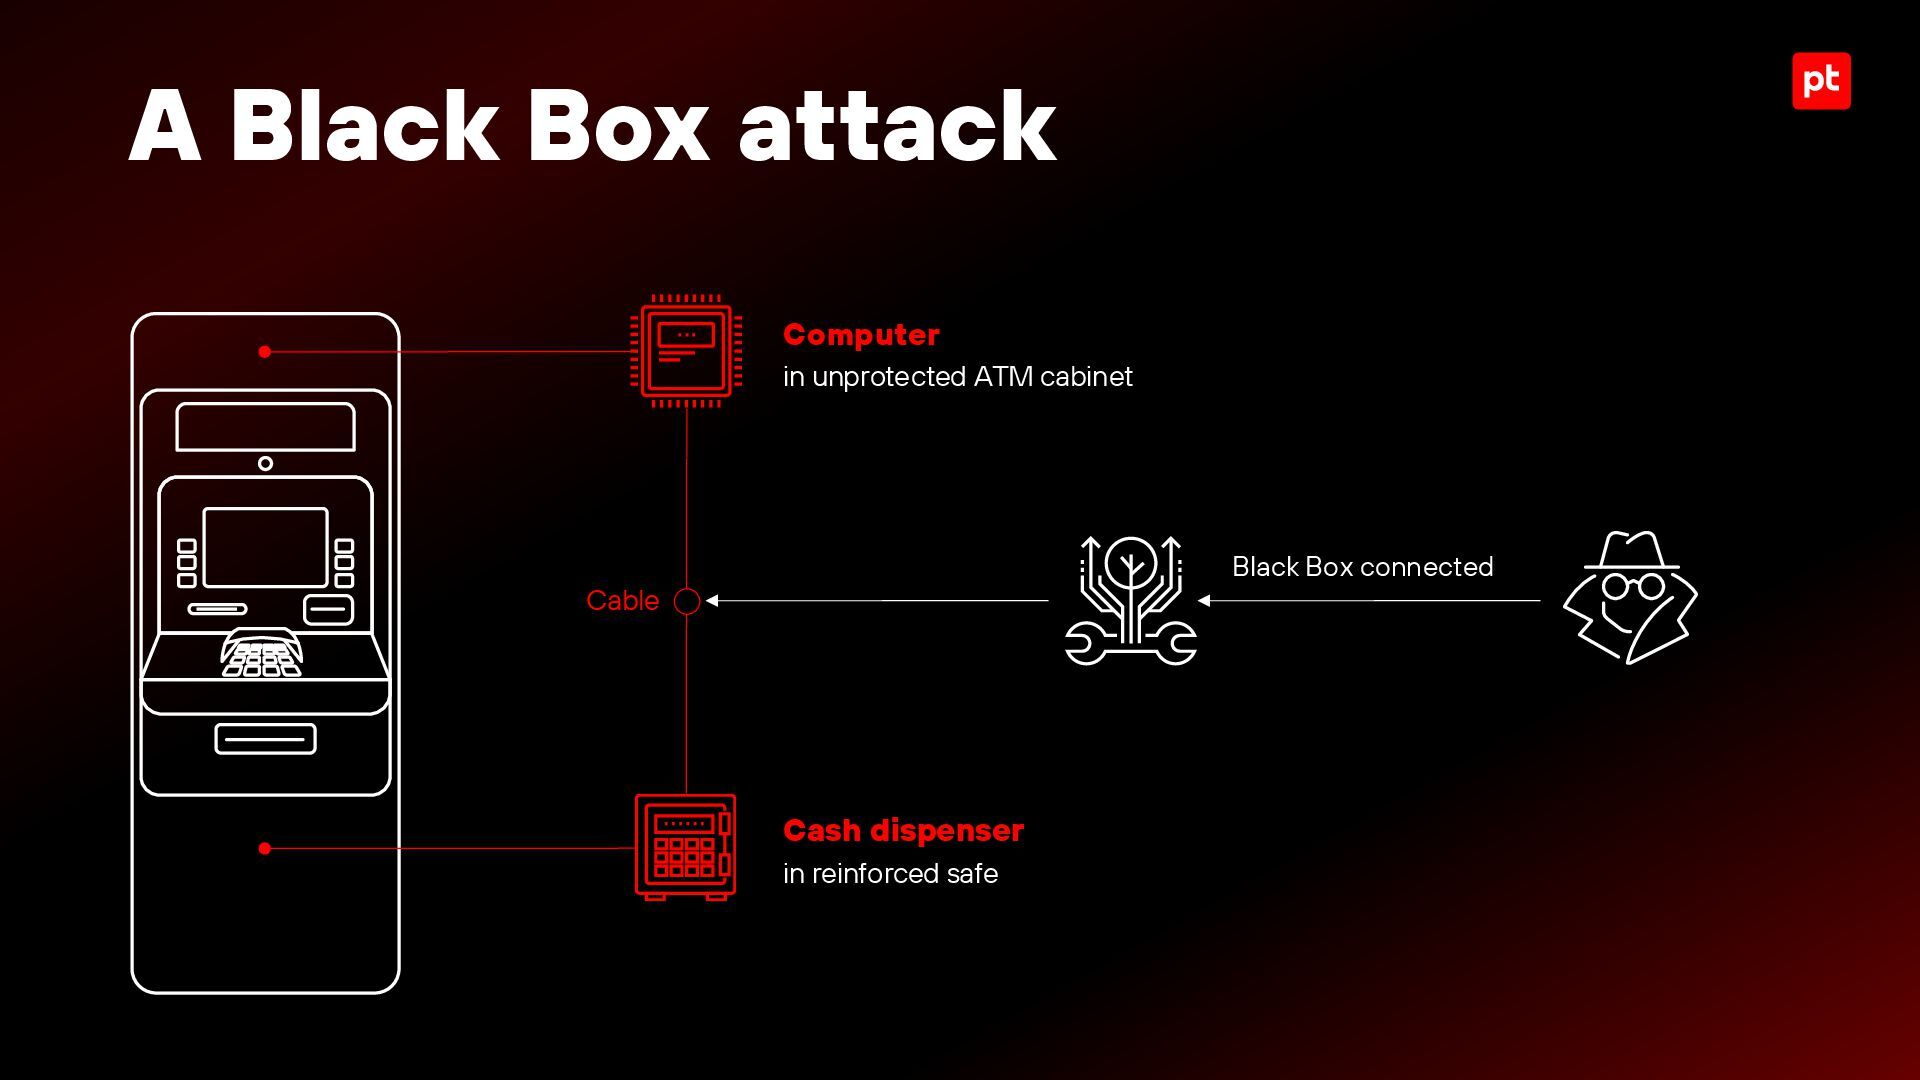
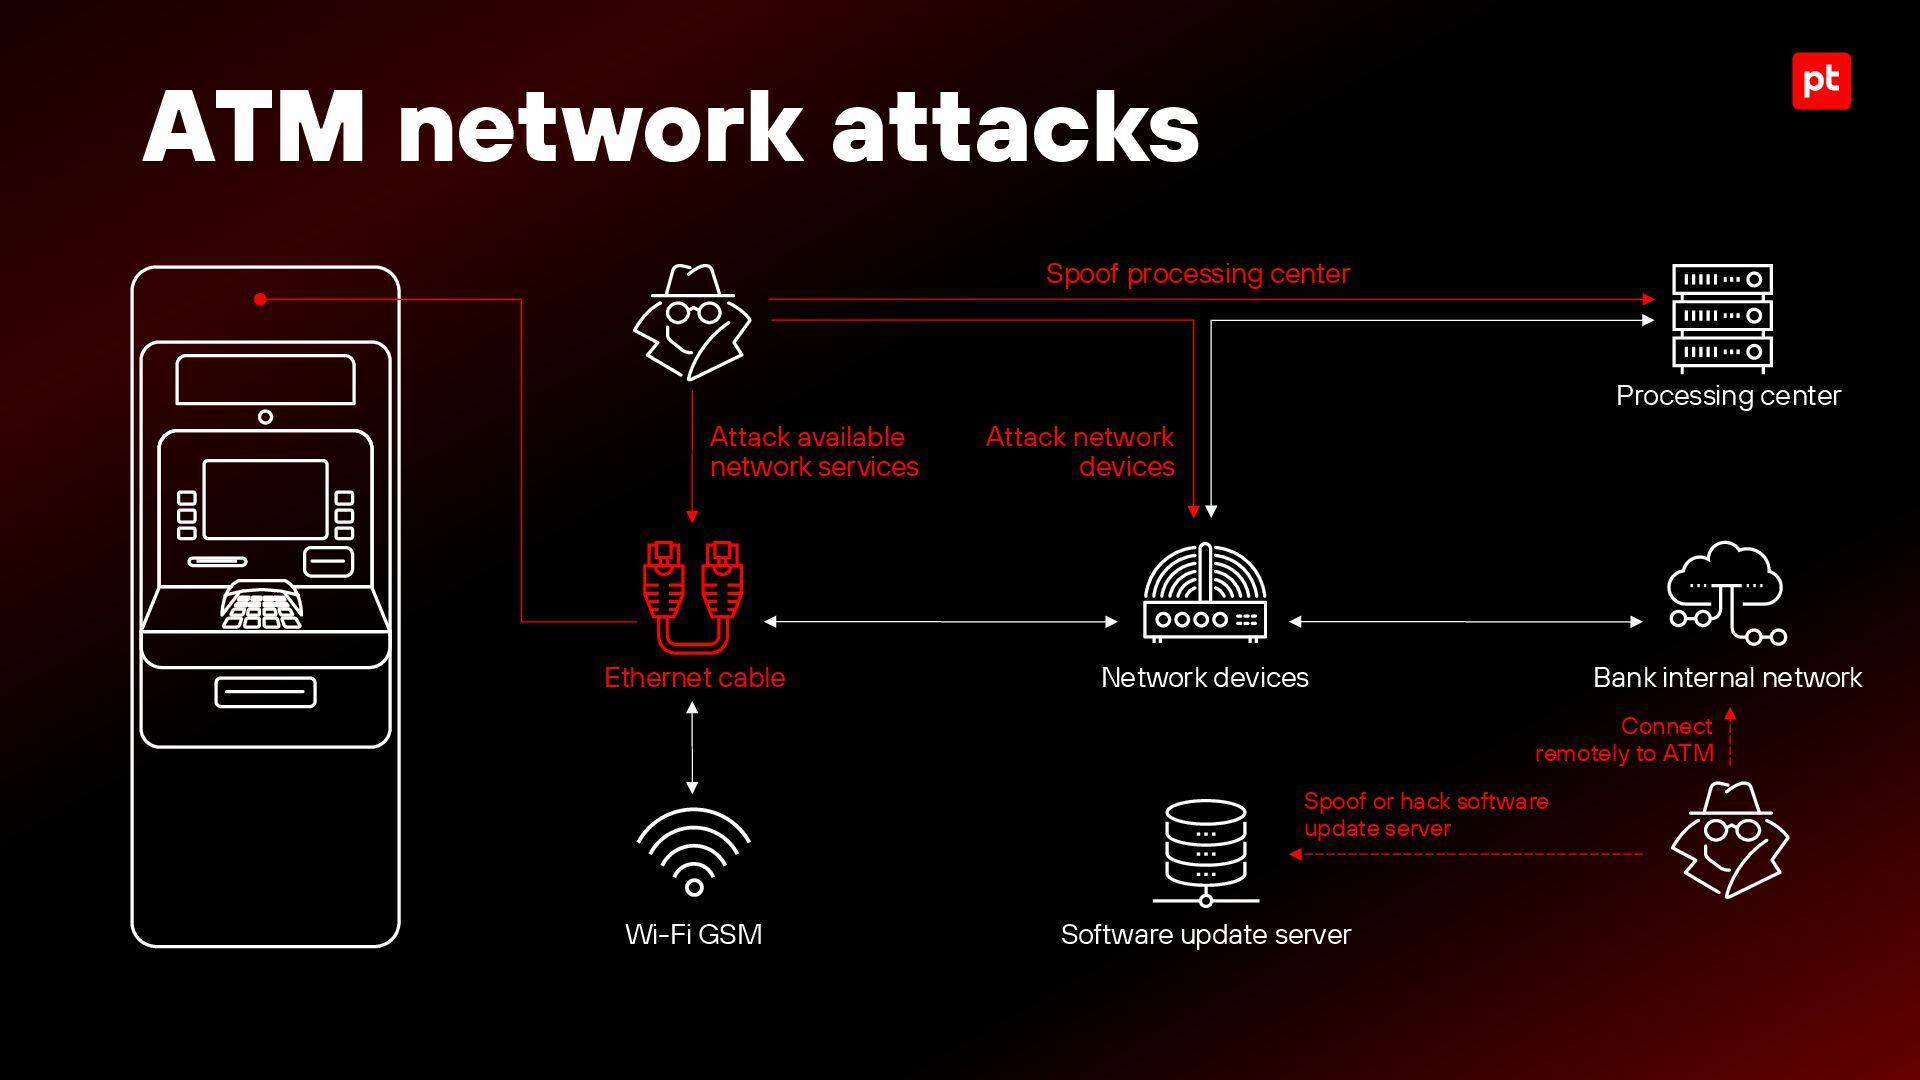
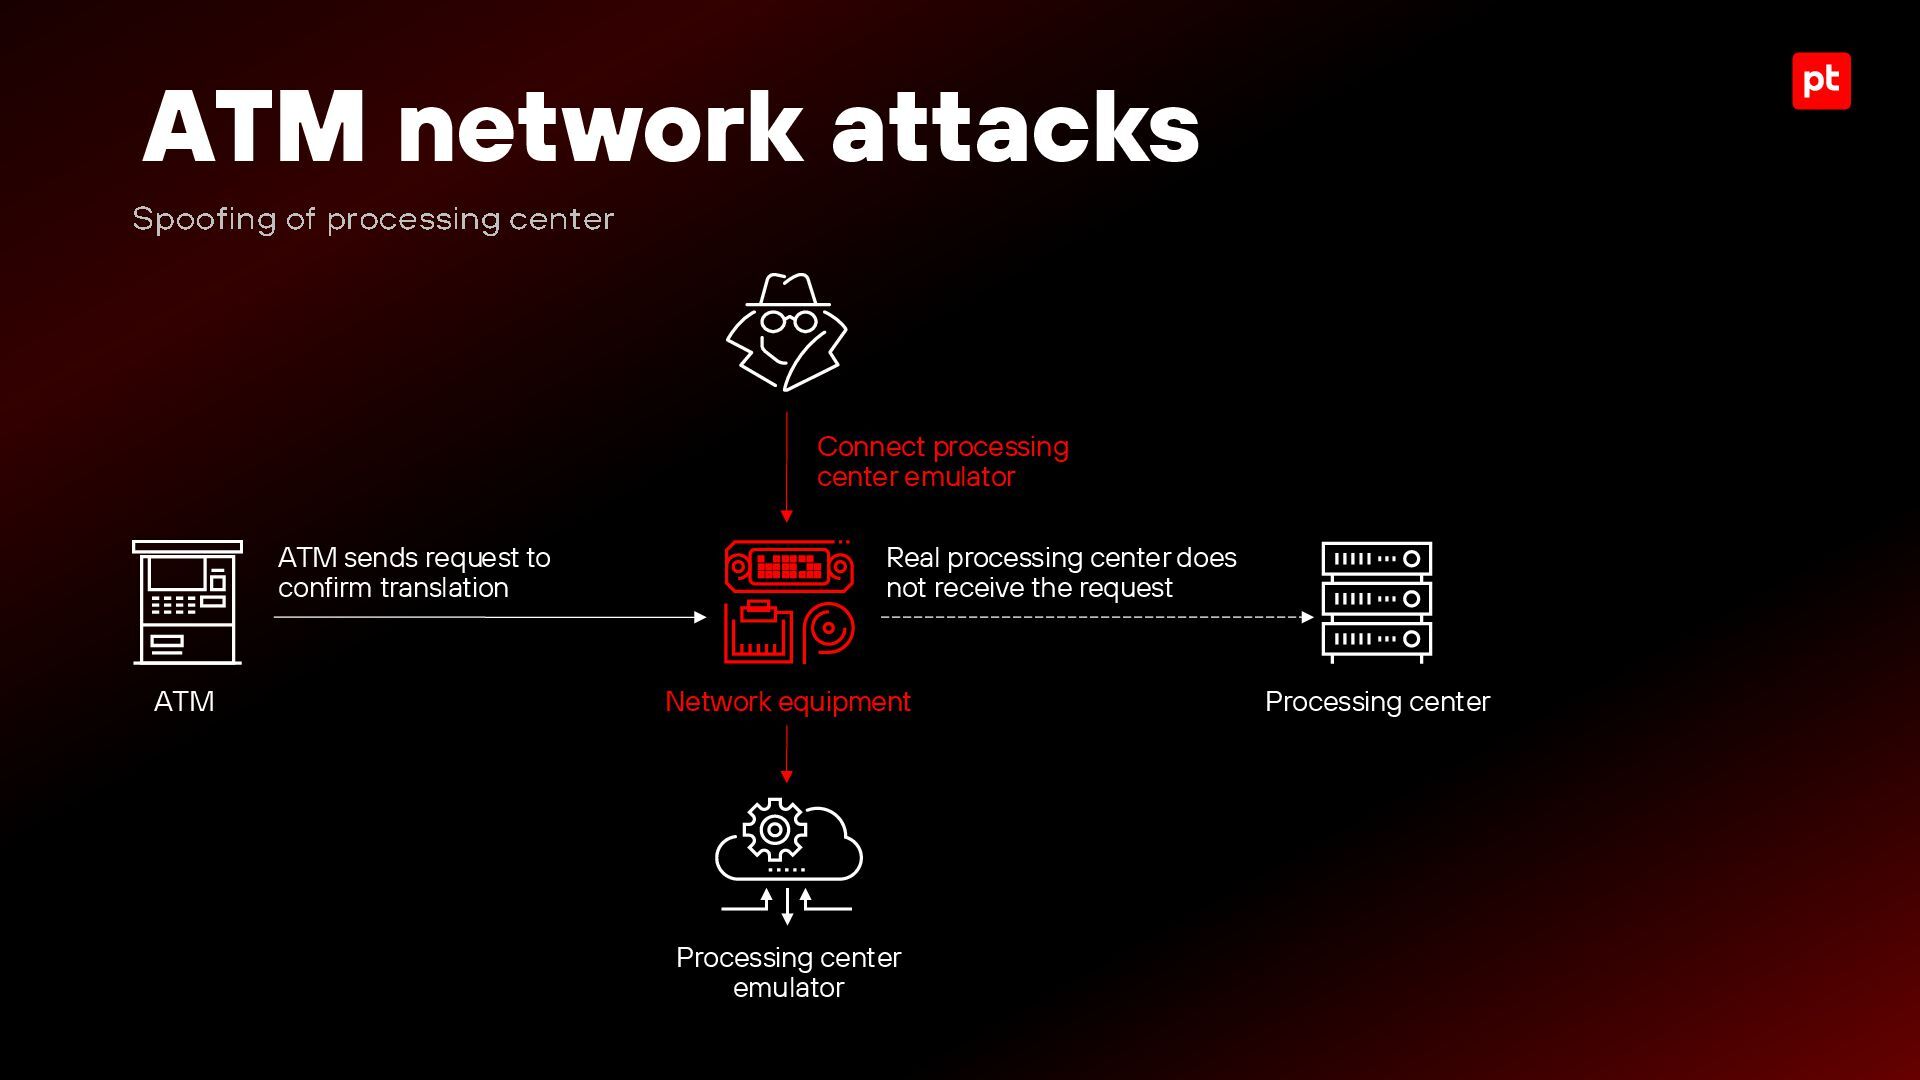
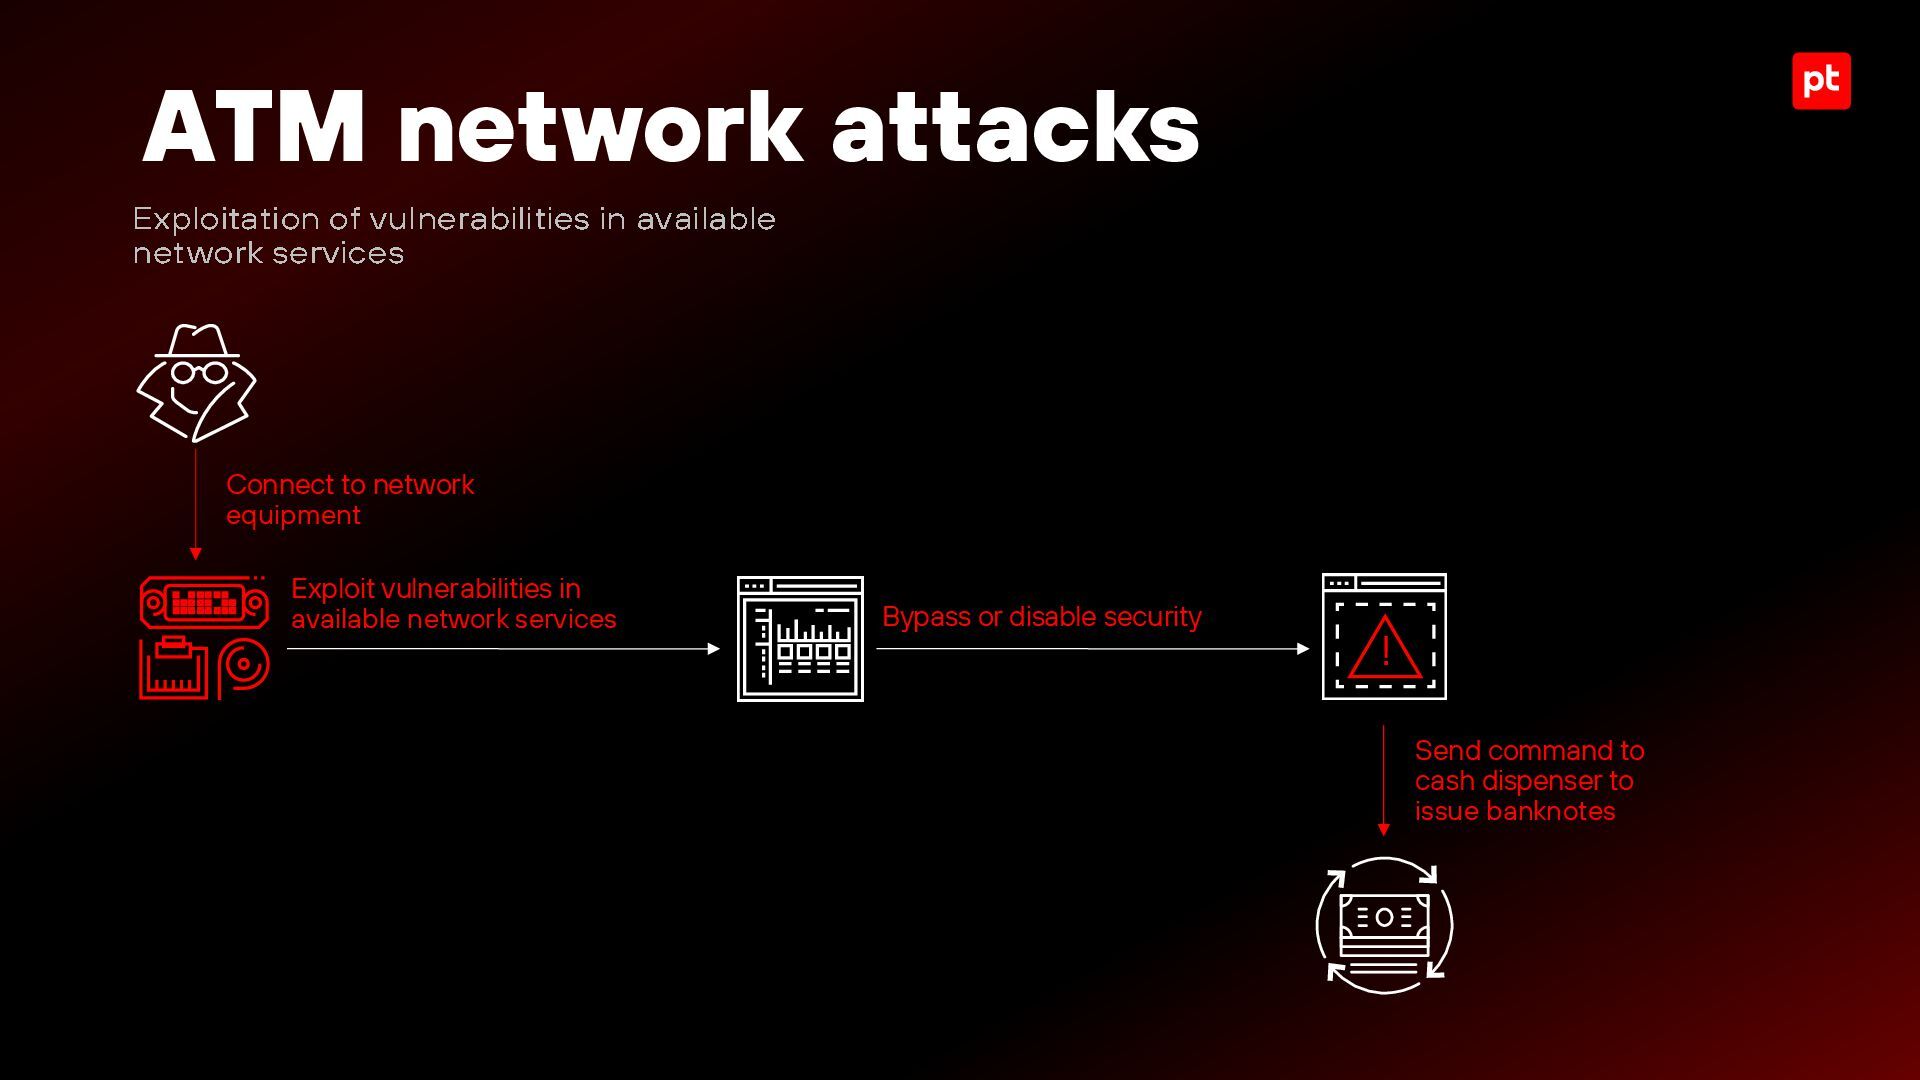
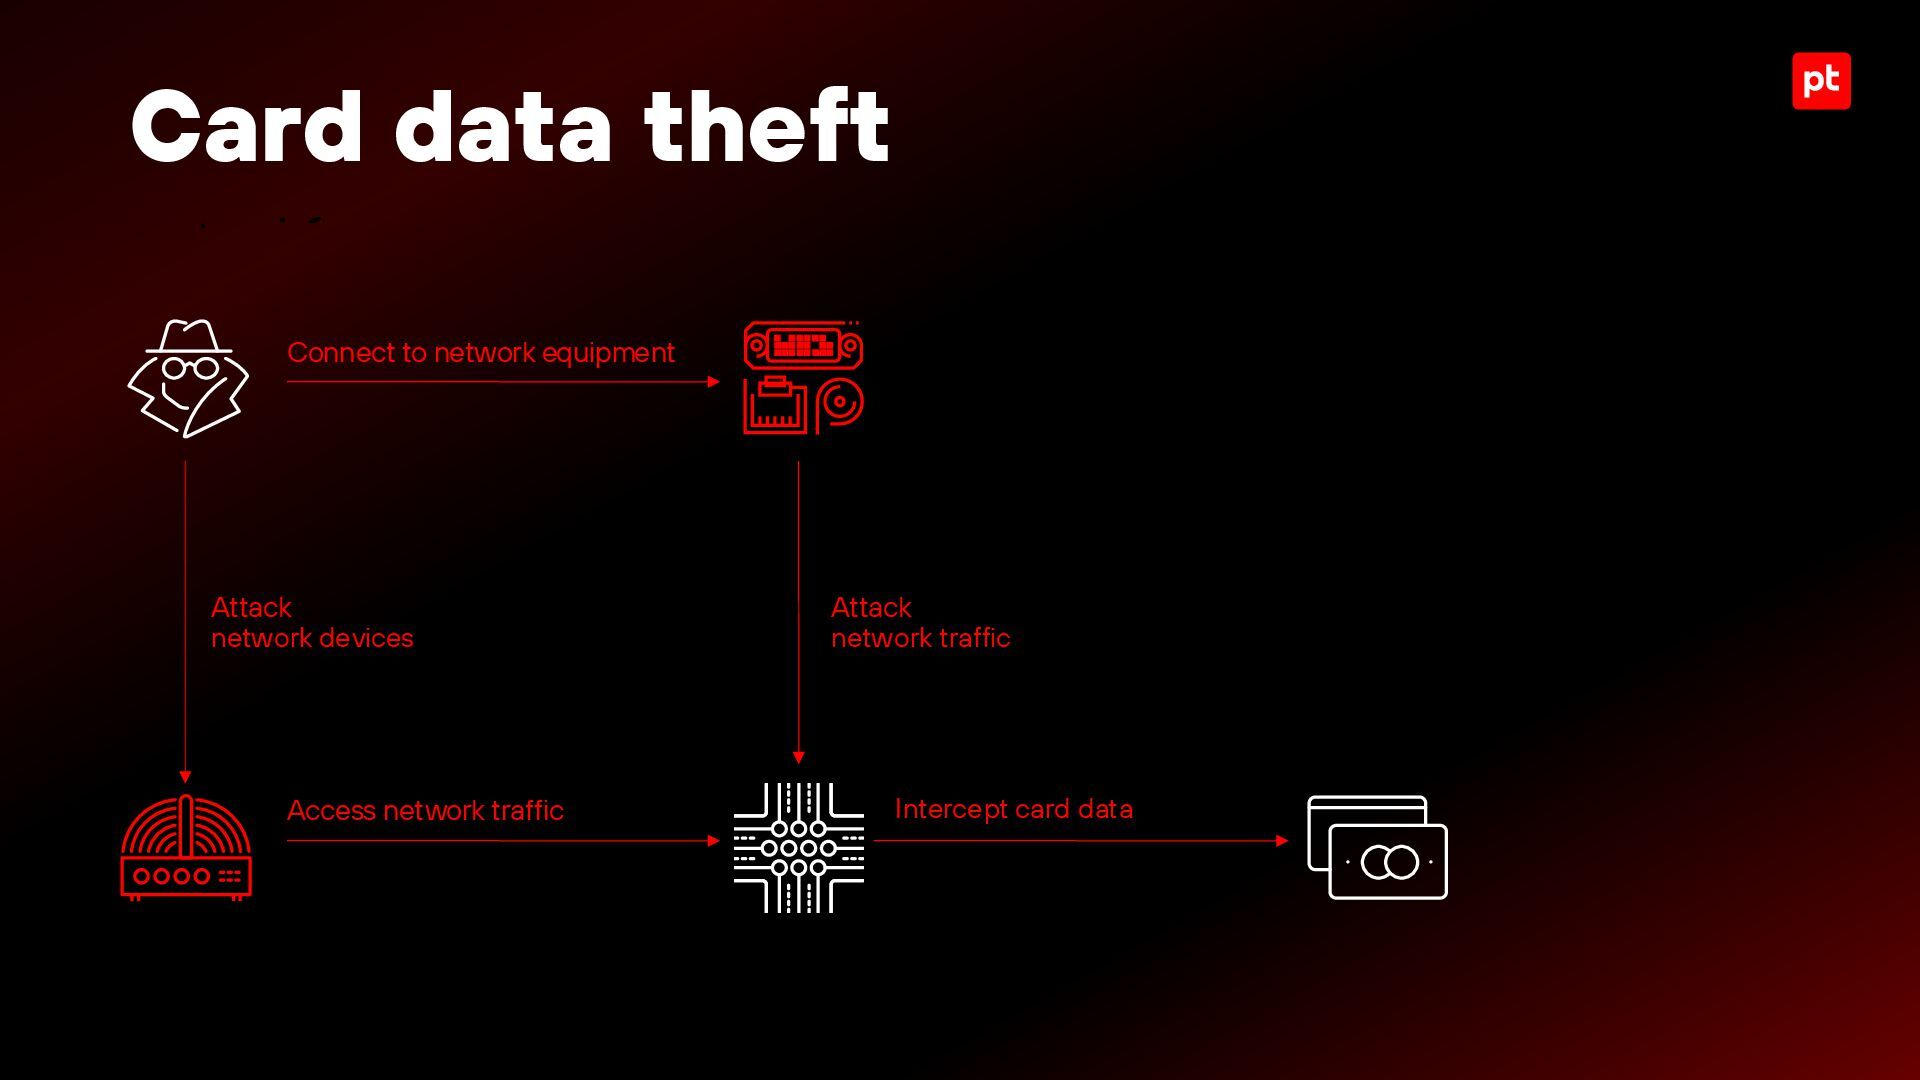
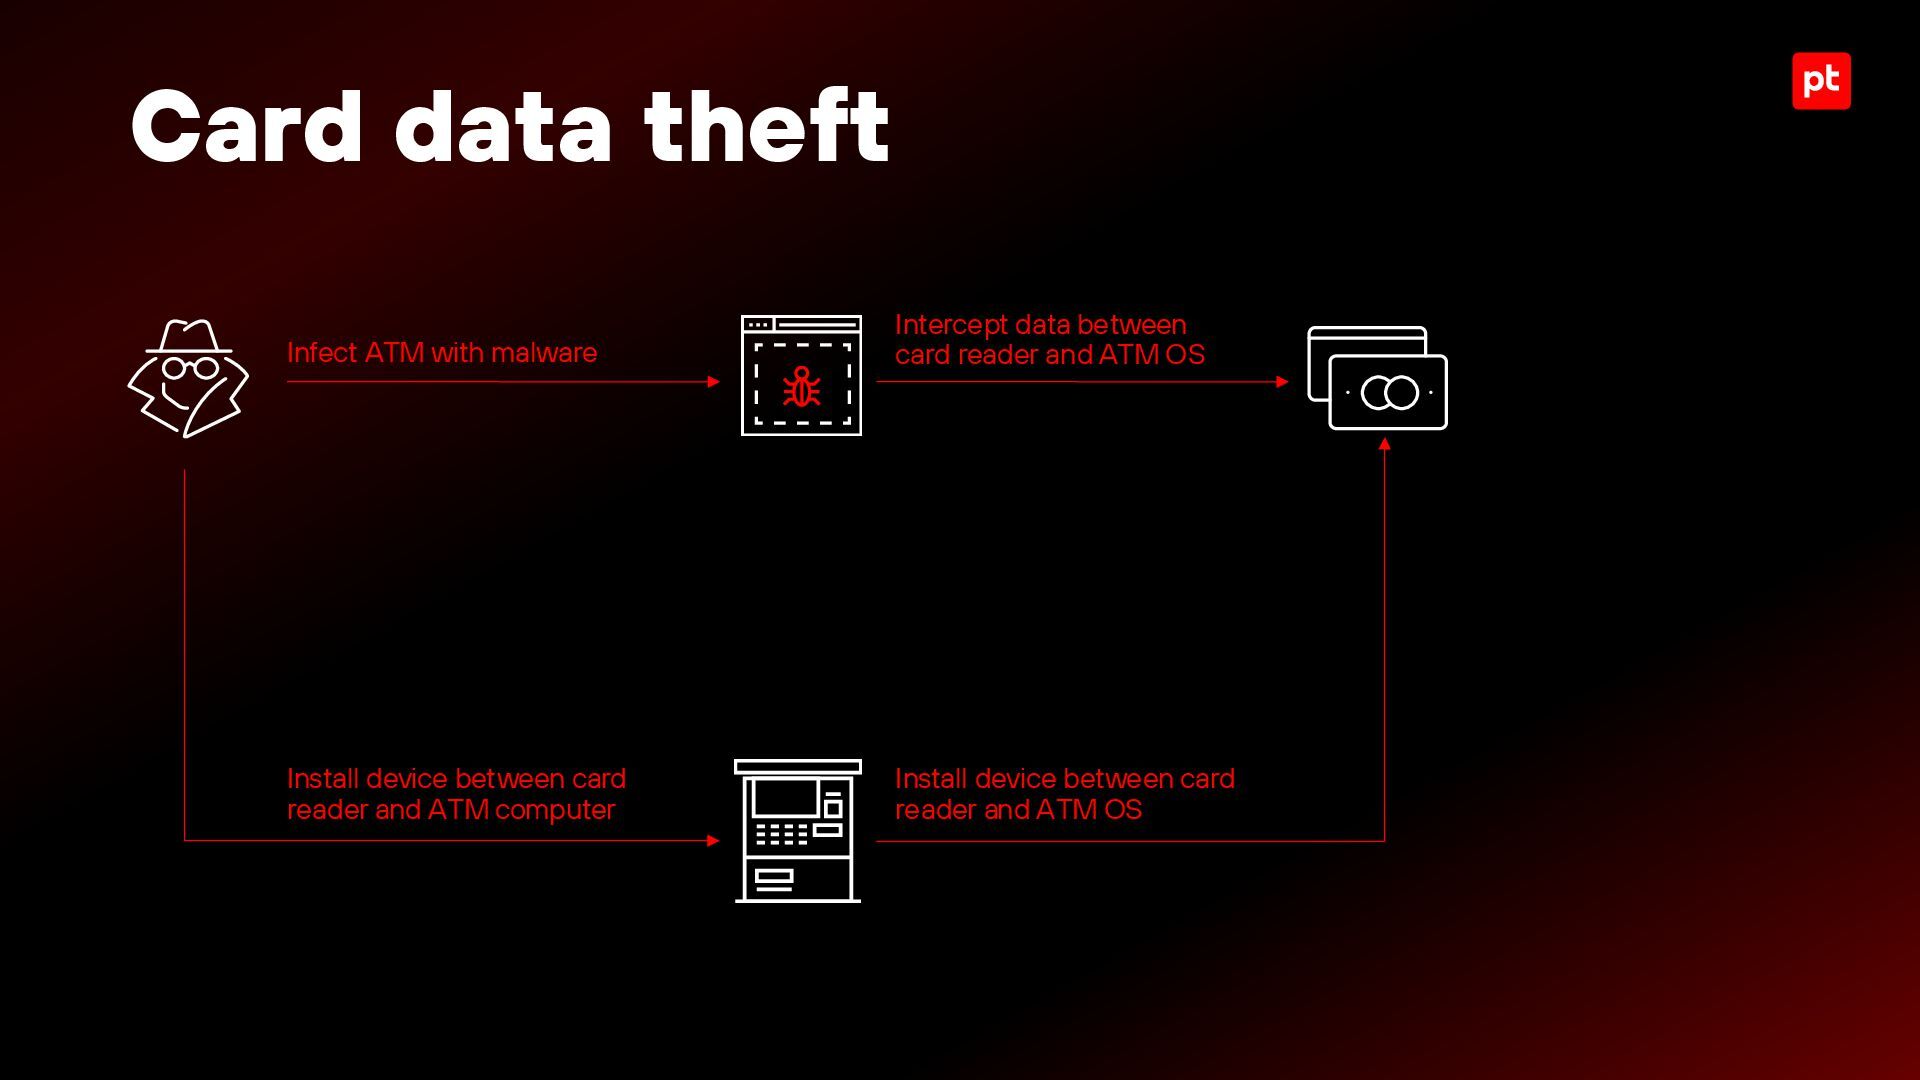
of USB devices ▪ Connection to hard drive ▪ Boot mode modification Card reader decodes data from bank cards ▪ Card data intercaption Cash dispenser issues banknotes from the safe ▪ Black Box Network equipment connects the ATM to the processing center and remote administration servers ▪ Interception of network traffic ▪ Spoofing of processing center ▪ Attack on available network services ▪ Attack on network devices ▪ Connection from the bank`s internal network ▪ Spoofing or hacking of software update server
or improper configuration of Application Control ▪ Improper configuration of systems or devices ▪ Insufficient network security ▪ Other things ATM vulnerabilities categories youtube.com/@bankomat3210
can install an outdated or modified firmware version (with malicious content) to bypass the encryption and withdraw cash.) Real life example CVE-2018-9099 CVE-2018-9100 CVE-2017-17668 CVE-2018-5717
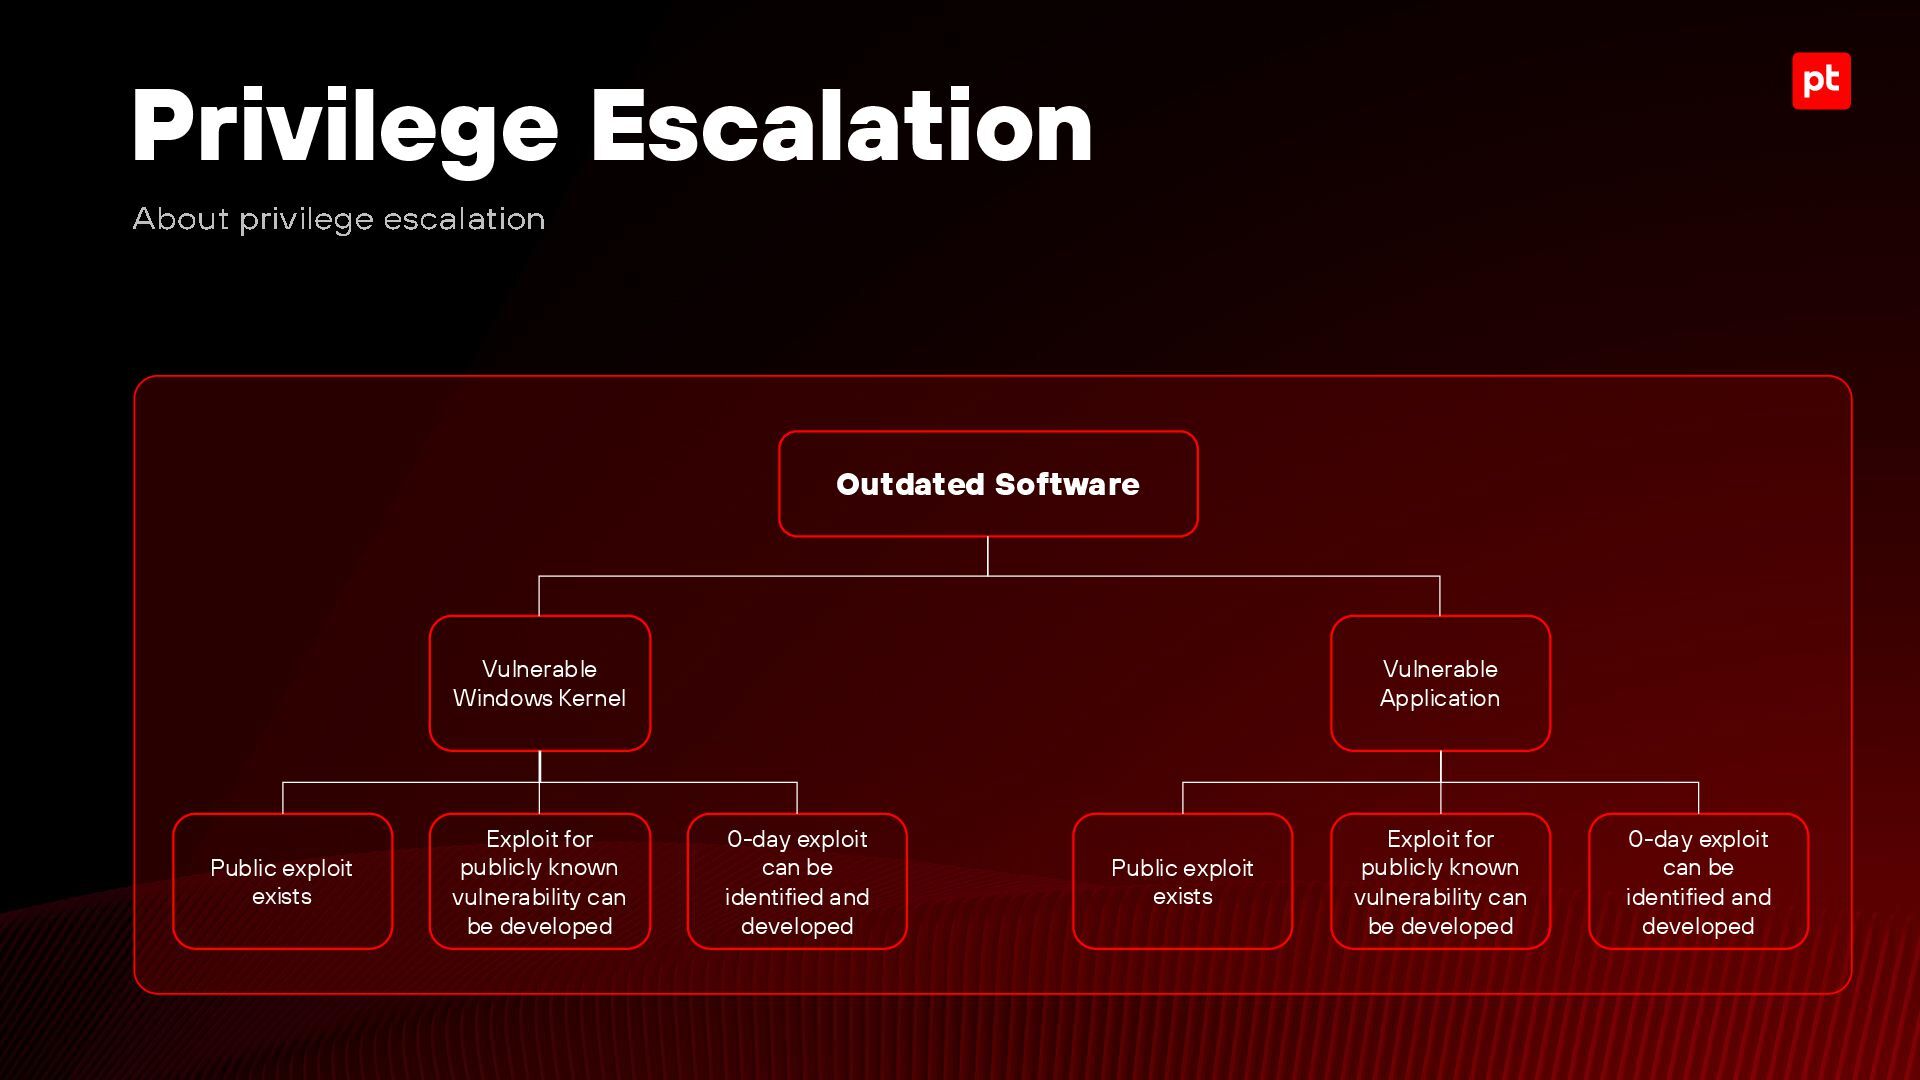
known vulnerability can be developed 0-day exploit can be identified and developed Public exploit exists Vulnerable Application Exploit for publicly known vulnerability can be developed 0-day exploit can be identified and developed Public exploit exists
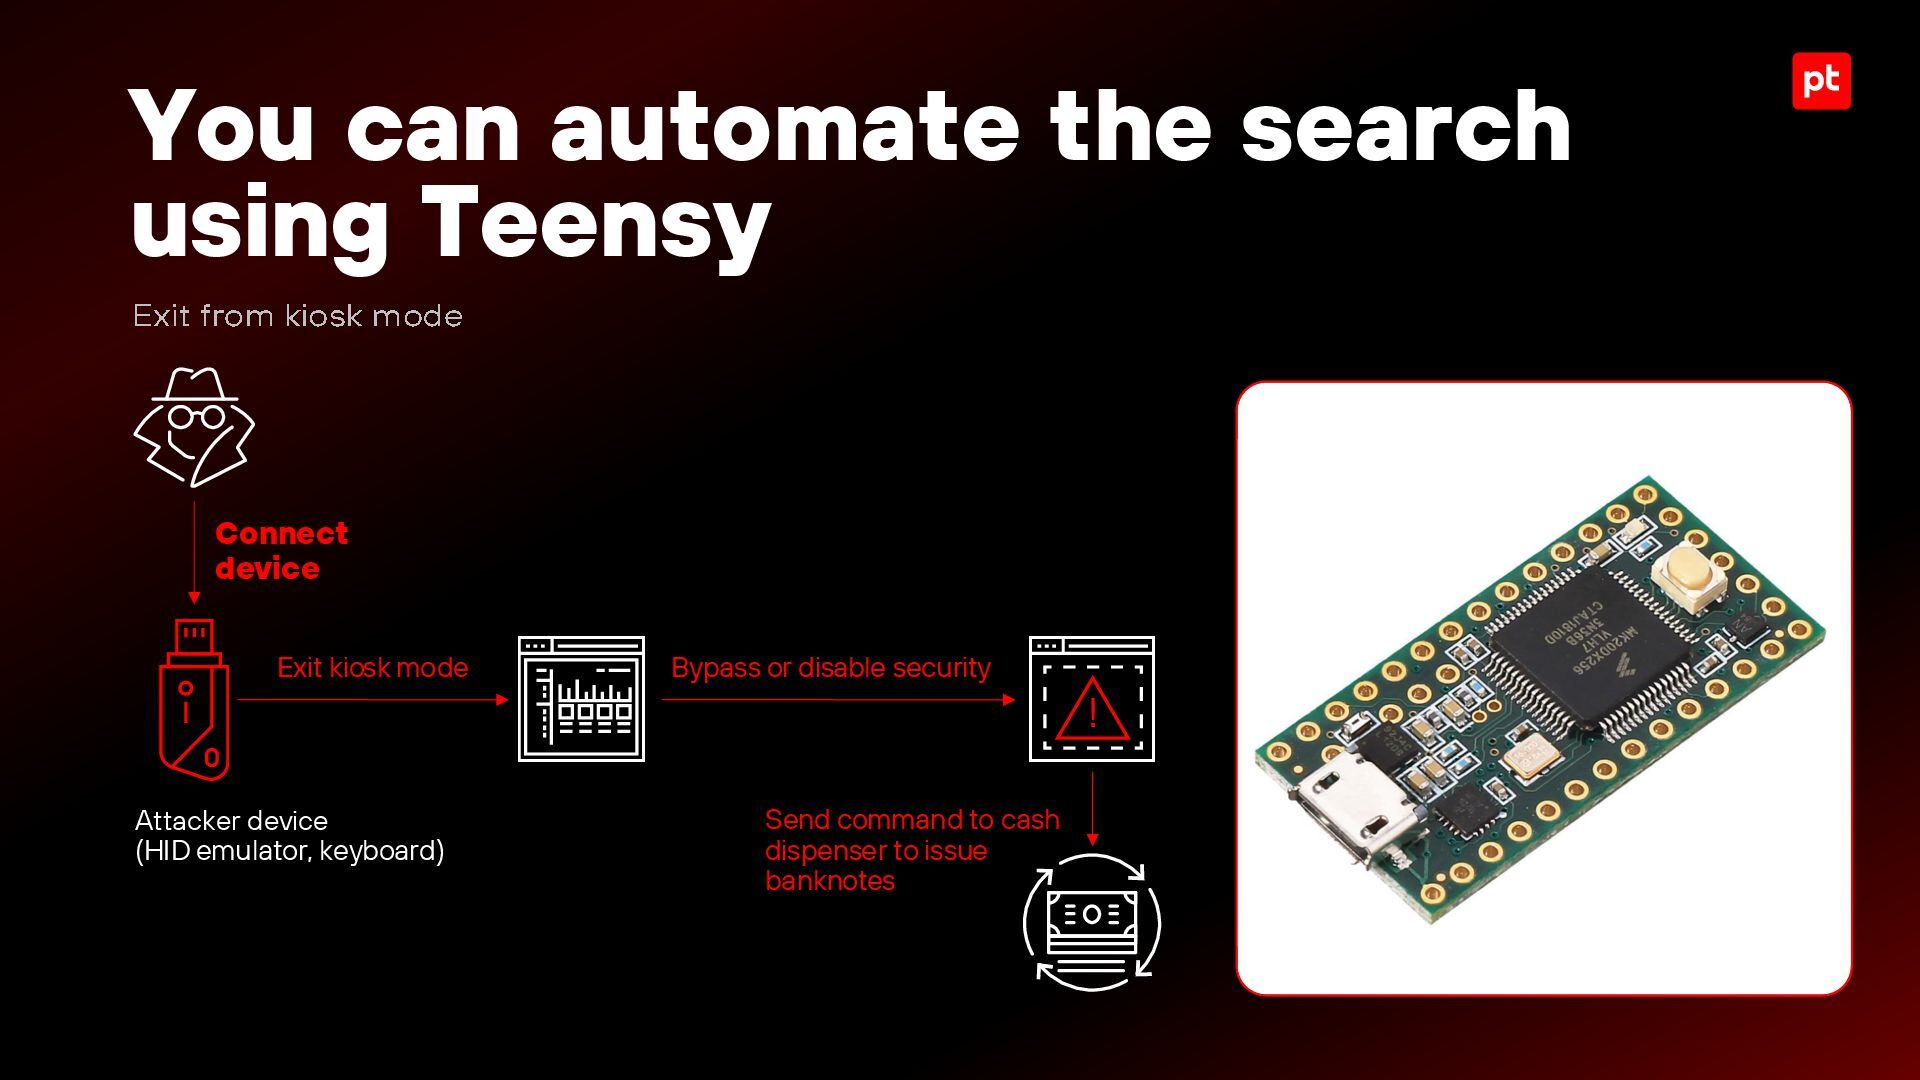
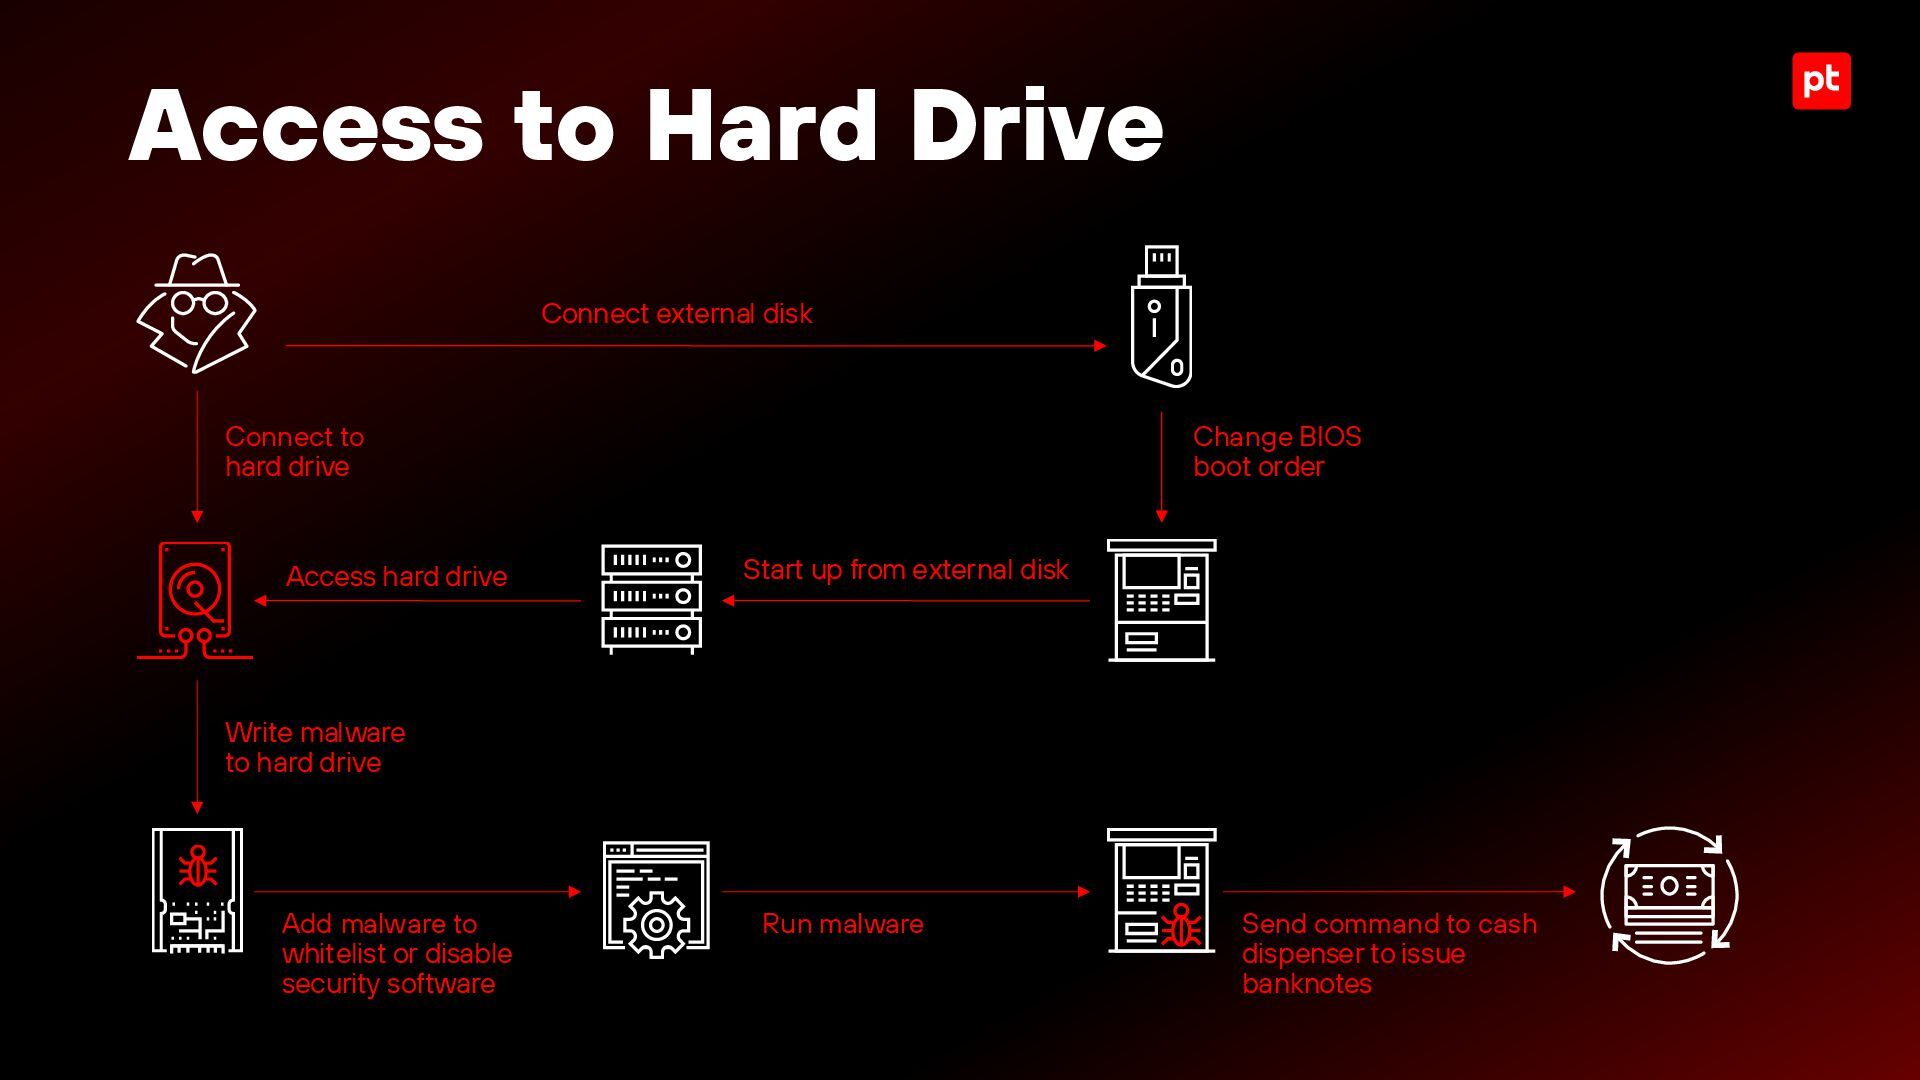
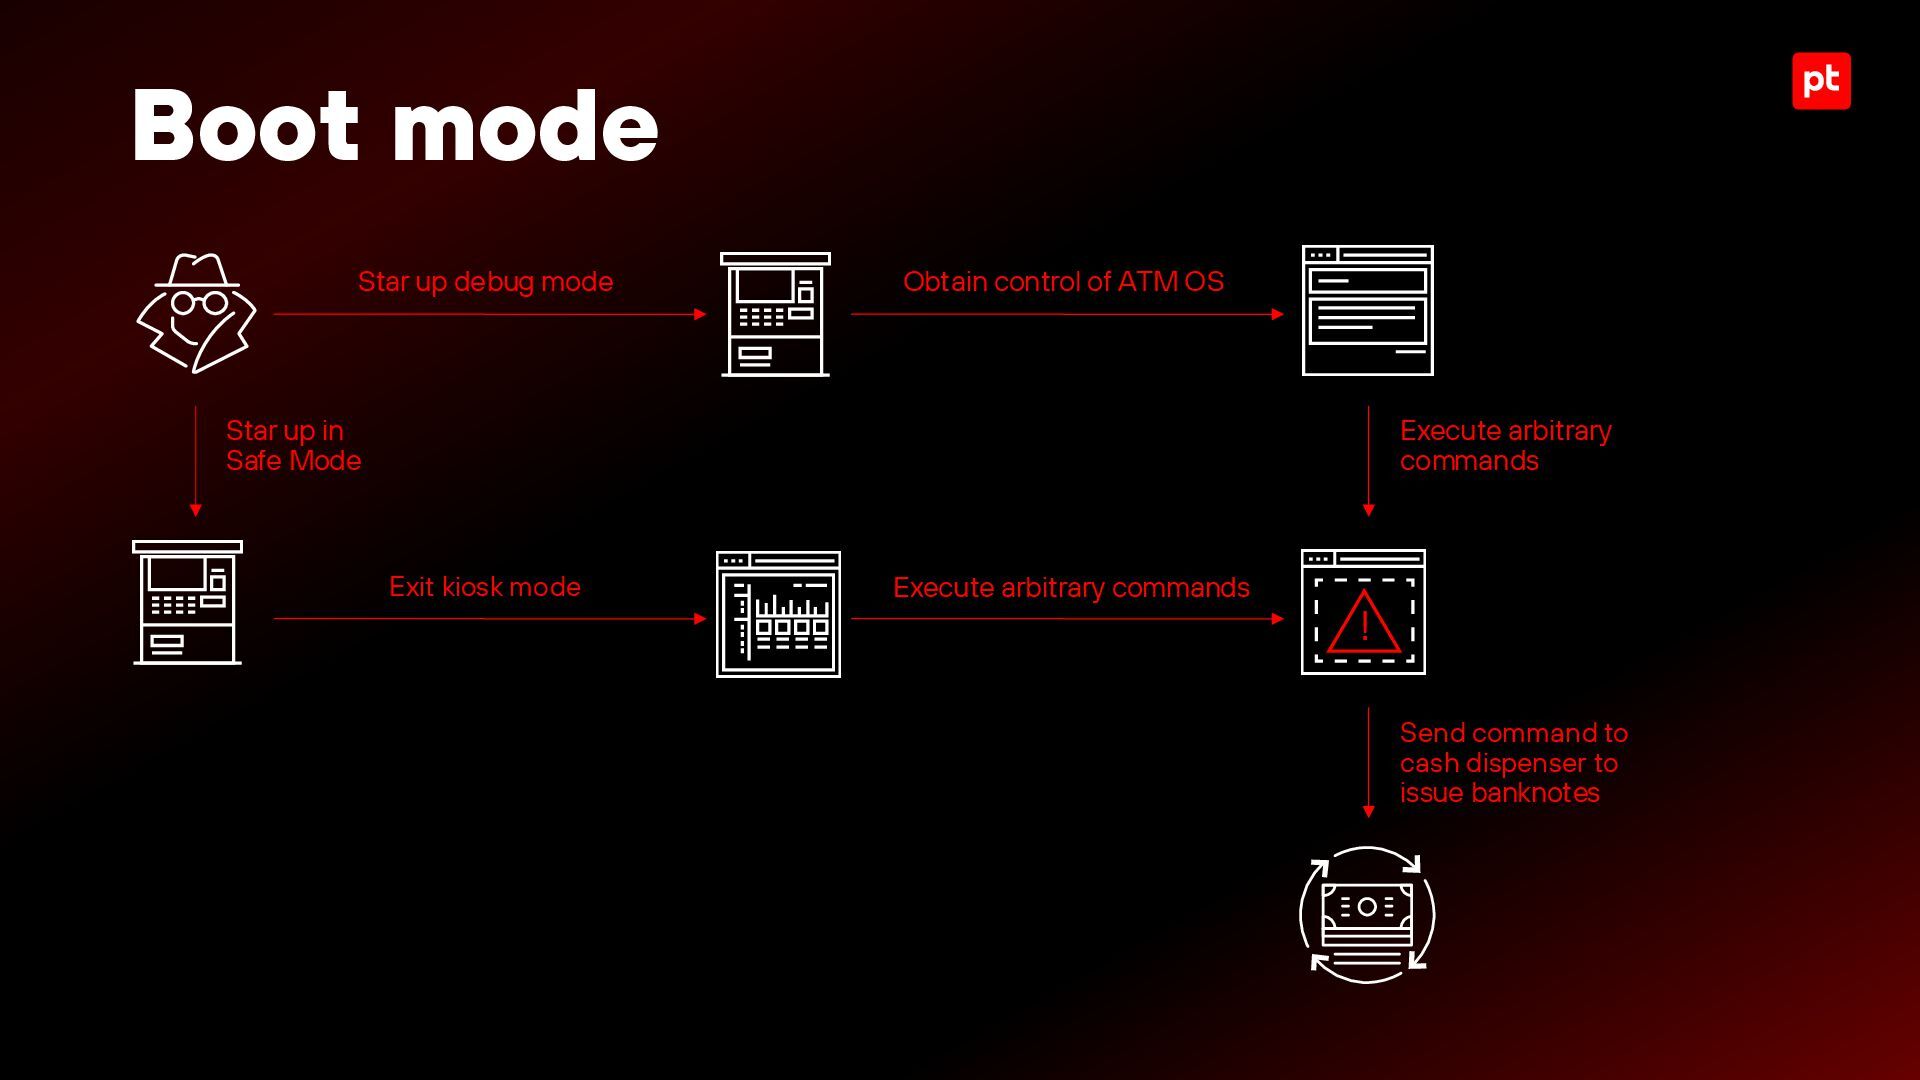
drive Access hard drive Start up from external disk Change BIOS boot order Write malware to hard drive Add malware to whitelist or disable security software Run malware Send command to cash dispenser to issue banknotes
services Bank internal network Processing center Software update server Wi-Fi GSM Spoof or hack software update server Connect remotely to ATM Spoof processing center Attack network devices
know how attackers will act if they want to hack into your ATM machine And you know who to turn to if you want to conduct such testing by white-hat hackers Let's sum it up


 odashi
 hiracky16
 codmoninc
 iktakahiro
 takonda
 greenmidori
 y0hgi
 camiha
 kaminashi
 teamlab
 ishikawa_satoru
 ymotongpoo
 rkendrick25
 gr2m
 reverentgeek
 trishagee
 denniskardys
 codingconduct
 portentint
 cassininazir
 csswizardry
 gurzu
 tammyeverts