Upgrade to Pro — share decks privately, control downloads, hide ads and more …

Web Exploitation II [Lect 8: Competitive Cybers...

Sponsored · Ship Features Fearlessly Turn features on and off without deploys. Used by thousands of Ruby developers. →

Web Exploitation II [Lect 8: Competitive Cybersecurity 101]

Transitioning from the browser to the backend, this lecture tackles severe server-side vulnerabilities where untrusted user input interacts directly with the operating system and databases. Students learn the mechanics and syntax of Command Injection and SQL Injection (SQLi), practicing classic login bypasses and arbitrary command execution. The session also introduces Burp Suite as the ultimate web proxy for intercepting and modifying HTTP requests.

Kannan Murugapandian

October 13, 2026

Transcript

12 slides
  1. Competitive Cybersecurity 101 Session 8: Web Exploitation II & Mini

    CTF Kannan Murugapandian August 28, 2026 Kannan Murugapandian Competitive Cybersecurity 101 August 28, 2026 1 / 12
  2. Disclaimer & Ethical Rules Strictly for Educational Purposes All knowledge

    and tools must only be applied in environments where you have explicit permission. Do not test on systems you do not personally own or lack authorization to assess. Unauthorized access constitutes a criminal offense under the Computer Misuse Act. Kannan Murugapandian Competitive Cybersecurity 101 August 28, 2026 2 / 12
  3. Today’s Agenda The Backend: Server-Side Execution Command Injection: Talking to

    the OS SQL Injection (SQLi): Talking to the Database Intercepting Traffic: Burp Suite Basics The Final Boss: Live Mini-CTF Competition Kannan Murugapandian Competitive Cybersecurity 101 August 28, 2026 3 / 12
  4. Client-Side vs. Server-Side Recap: Client-Side (Session 7) Happens in your

    browser (HTML, JS, Cookies). Bypassed by editing the DOM or changing cookies. The New Frontier: Server-Side Happens on the remote machine (PHP, Python, Databases). You cannot see the code. You can only interact with it by sending clever inputs. Kannan Murugapandian Competitive Cybersecurity 101 August 28, 2026 4 / 12
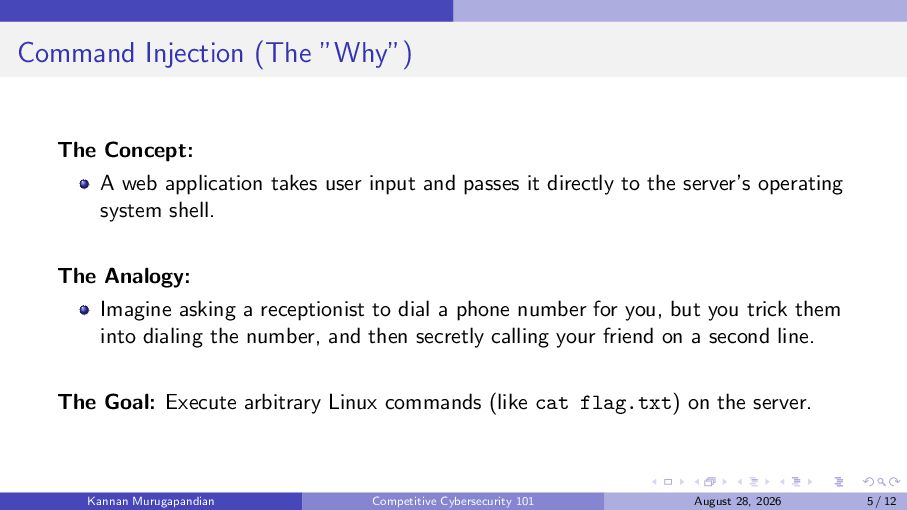
  5. Command Injection (The ”Why”) The Concept: A web application takes

    user input and passes it directly to the server’s operating system shell. The Analogy: Imagine asking a receptionist to dial a phone number for you, but you trick them into dialing the number, and then secretly calling your friend on a second line. The Goal: Execute arbitrary Linux commands (like cat flag.txt) on the server. Kannan Murugapandian Competitive Cybersecurity 101 August 28, 2026 5 / 12
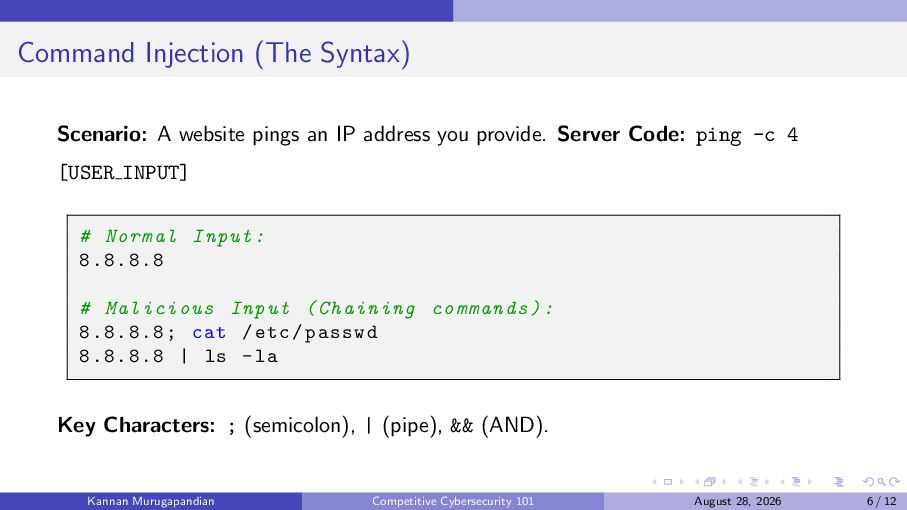
  6. Command Injection (The Syntax) Scenario: A website pings an IP

    address you provide. Server Code: ping -c 4 [USER INPUT] # Normal Input : 8.8.8.8 # Malicious Input ( Chaining commands ) : 8.8.8.8; cat / etc / passwd 8.8.8.8 | ls - la Key Characters: ; (semicolon), | (pipe), && (AND). Kannan Murugapandian Competitive Cybersecurity 101 August 28, 2026 6 / 12
  7. SQL Injection (The ”Why”) The Concept: Websites use SQL (Structured

    Query Language) to talk to databases. If user input is not sanitized, it breaks the SQL syntax and changes the query’s logic. The Result: Bypassing login screens. Dumping the entire database (usernames, passwords, flags). Kannan Murugapandian Competitive Cybersecurity 101 August 28, 2026 7 / 12
  8. SQLi: The Classic Login Bypass The Server’s SQL Query: SELECT

    * FROM users WHERE username = ’ admin ’ AND password = ’[ USER_INPUT ] ’; Your Malicious Input: ’ OR ’1 ’= ’1 The Resulting Query: ... AND password = ’’ OR ’1’=’1’; Since 1 always equals 1, the database returns True and logs you in as admin! Kannan Murugapandian Competitive Cybersecurity 101 August 28, 2026 8 / 12
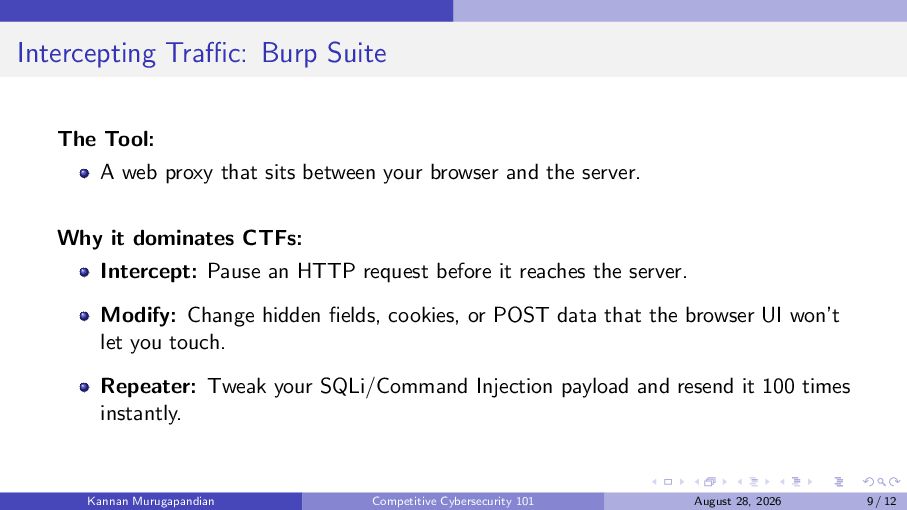
  9. Intercepting Traffic: Burp Suite The Tool: A web proxy that

    sits between your browser and the server. Why it dominates CTFs: Intercept: Pause an HTTP request before it reaches the server. Modify: Change hidden fields, cookies, or POST data that the browser UI won’t let you touch. Repeater: Tweak your SQLi/Command Injection payload and resend it 100 times instantly. Kannan Murugapandian Competitive Cybersecurity 101 August 28, 2026 9 / 12
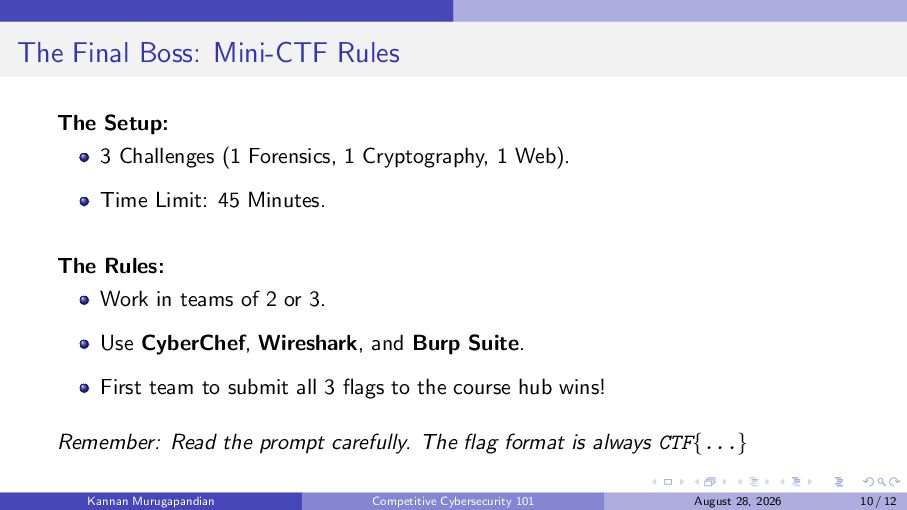
  10. The Final Boss: Mini-CTF Rules The Setup: 3 Challenges (1

    Forensics, 1 Cryptography, 1 Web). Time Limit: 45 Minutes. The Rules: Work in teams of 2 or 3. Use CyberChef, Wireshark, and Burp Suite. First team to submit all 3 flags to the course hub wins! Remember: Read the prompt carefully. The flag format is always CTF{...} Kannan Murugapandian Competitive Cybersecurity 101 August 28, 2026 10 / 12
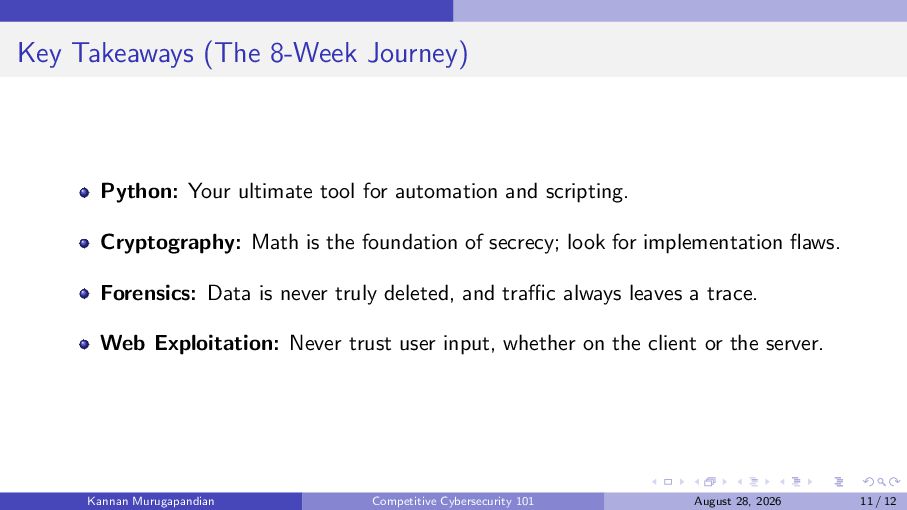
  11. Key Takeaways (The 8-Week Journey) Python: Your ultimate tool for

    automation and scripting. Cryptography: Math is the foundation of secrecy; look for implementation flaws. Forensics: Data is never truly deleted, and traffic always leaves a trace. Web Exploitation: Never trust user input, whether on the client or the server. Kannan Murugapandian Competitive Cybersecurity 101 August 28, 2026 11 / 12
  12. Thank You & Good Luck! Course Complete! Instructor: Kannan Murugapandian

    Email: [email protected] Course Hub: kannan.bearblog.dev/ctf-dps/ Next Stop: The National Cybersecurity Olympiad (NCO) Go make us proud! Kannan Murugapandian Competitive Cybersecurity 101 August 28, 2026 12 / 12

More Decks by Kannan Murugapandian

Other Decks in Technology