Upgrade to Pro — share decks privately, control downloads, hide ads and more …

gittufの紹介

 gittufの紹介

サイバートラスト株式会社 河原颯太氏
2026年10月26日開催 OSSセキュリティMeetup 講演資料

Avatar for Linux Foundation Japan

Linux Foundation Japan PRO

November 05, 2026

More Decks by Linux Foundation Japan

Other Decks in Technology

Transcript

  1. Index ▪ gittufの目的・できること ▪ gittufとTUF ▪ gittufの機能 • • •

    • gittufの前提 RSL(Reference State Log) gittufにおける署名と検証 gittufにおける検証とattestation reference ▪ demo
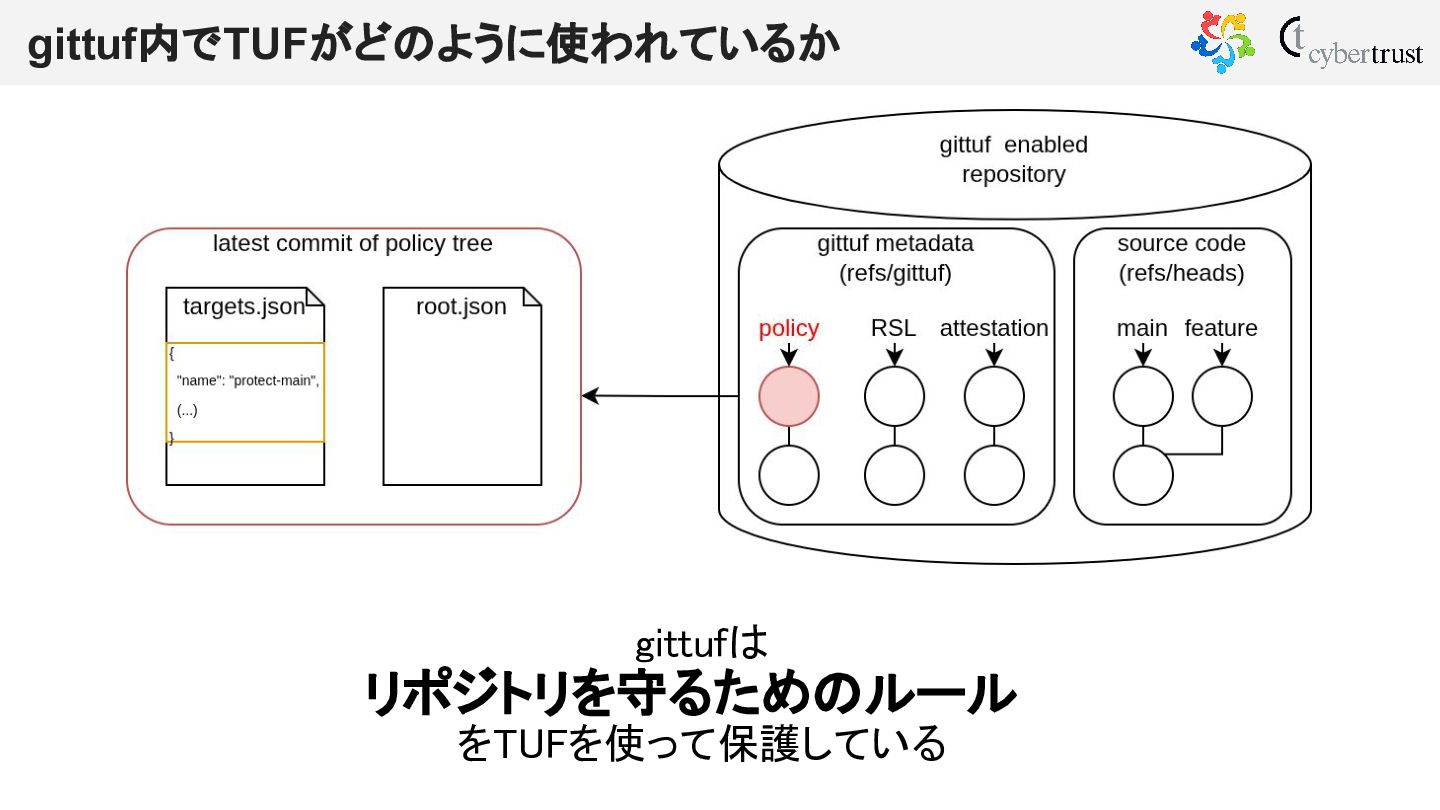
  2. gittufの目的 “gittuf is a platform-agnostic Git security system. can use

    gittuf to protect the contents of a Git repository from unauthorized or malicious changes.” gittufは「プラットフォームに依存しないGitセキュリティシステム」である. gittufを使用して,Gitリポジトリの内容を 不正な悪意ある変更から保護 することができる. “With gittuf, any developer who can pull from a Git repository can independently verify that the repository's security policies were followed.” ユーザーはリポジトリがセキュリティポリシーにしたがって 開発されていることを検証する ことができる
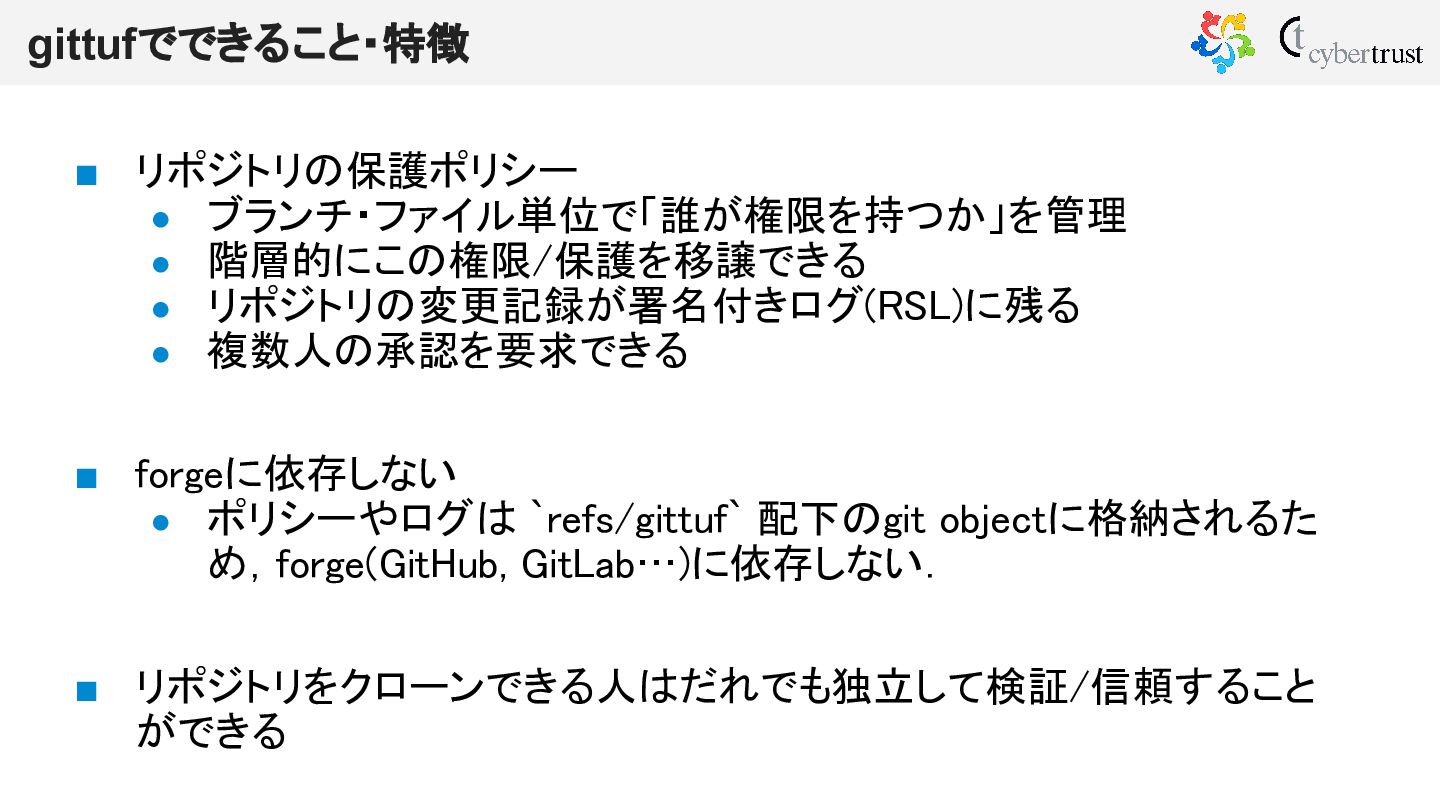
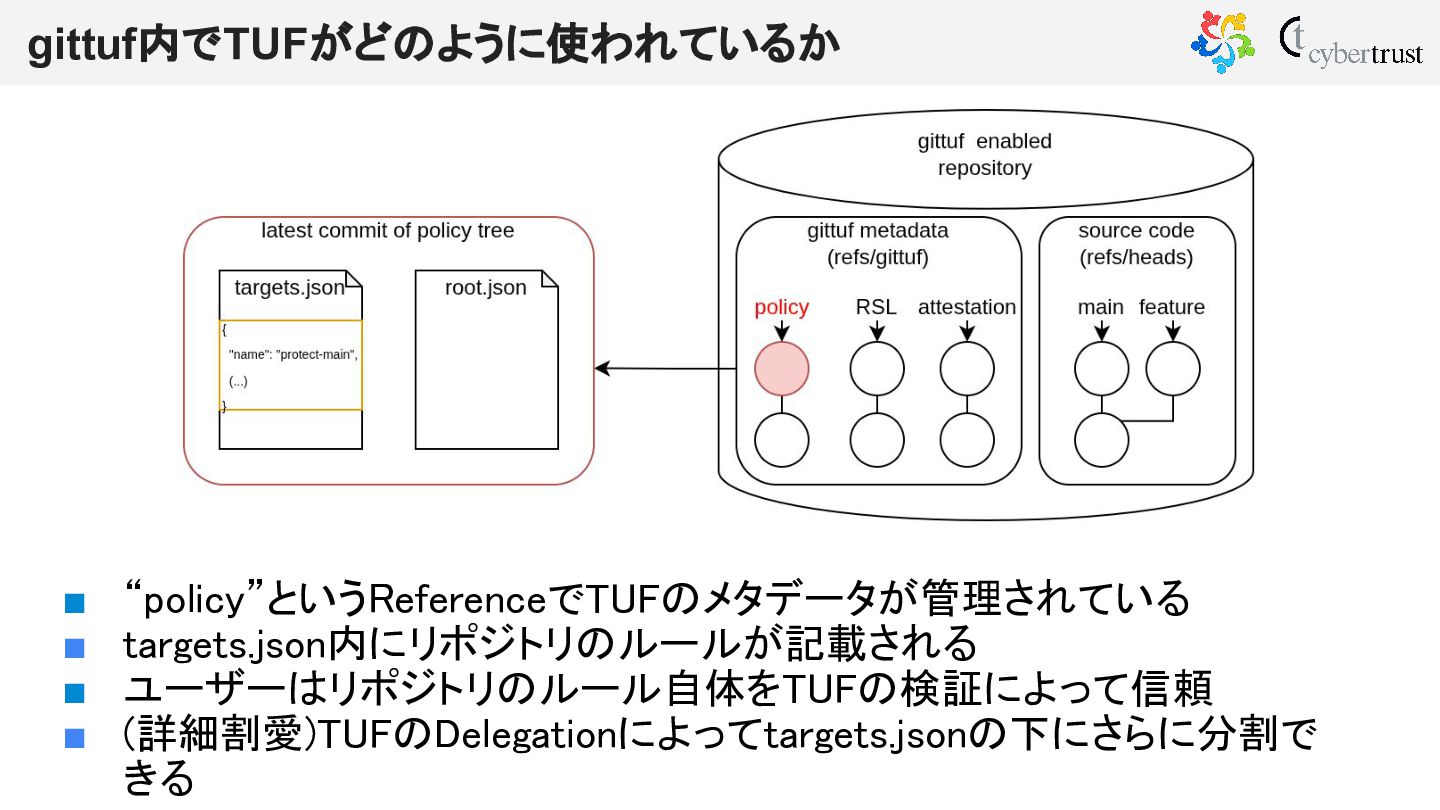
  3. gittufでできること・特徴 ▪ リポジトリの保護ポリシー • ブランチ・ファイル単位で「誰が権限を持つか」を管理 • 階層的にこの権限/保護を移譲できる • リポジトリの変更記録が署名付きログ(RSL)に残る •

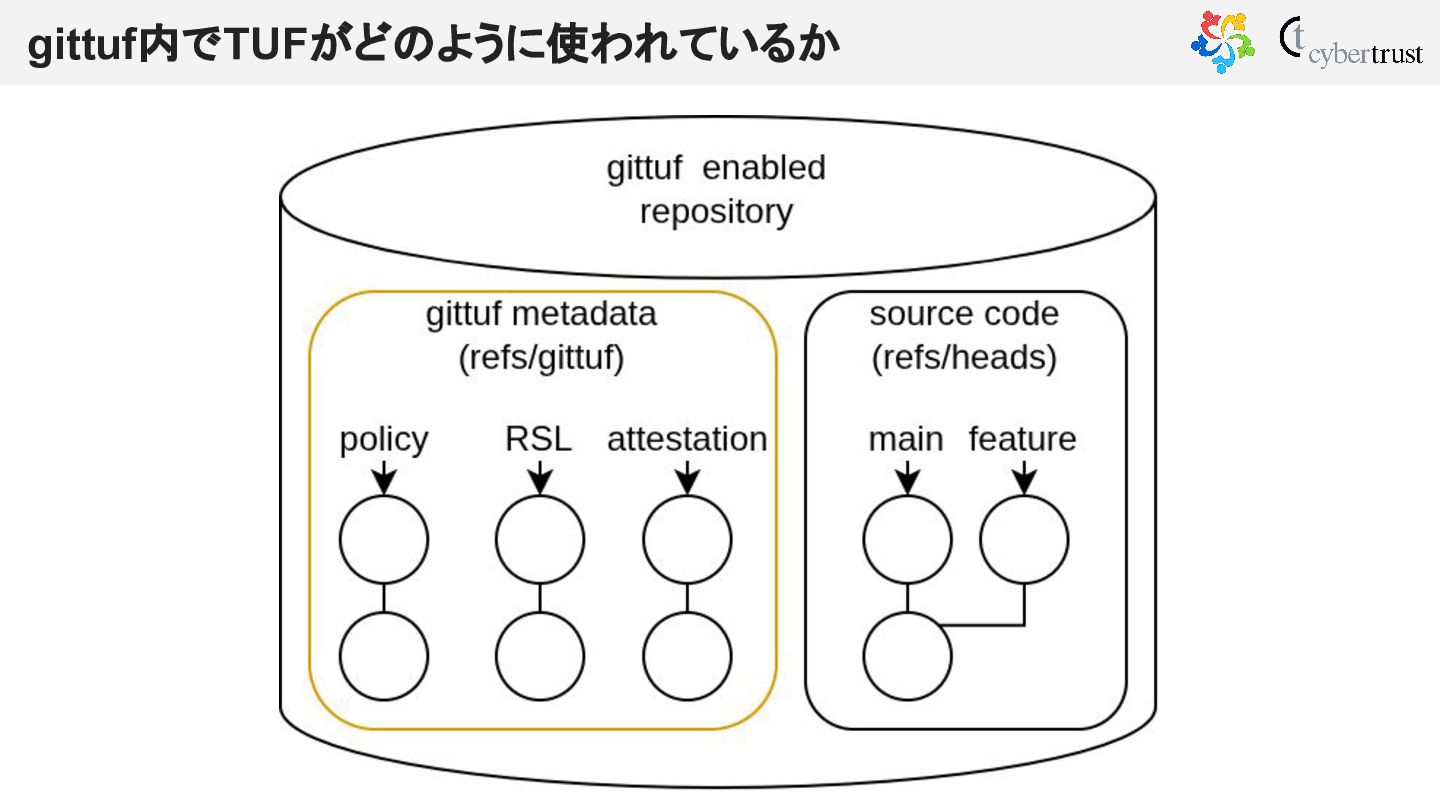
    複数人の承認を要求できる ▪ forgeに依存しない • ポリシーやログは `refs/gittuf` 配下のgit objectに格納されるた め,forge(GitHub, GitLab…)に依存しない. ▪ リポジトリをクローンできる人はだれでも独立して検証/信頼すること ができる
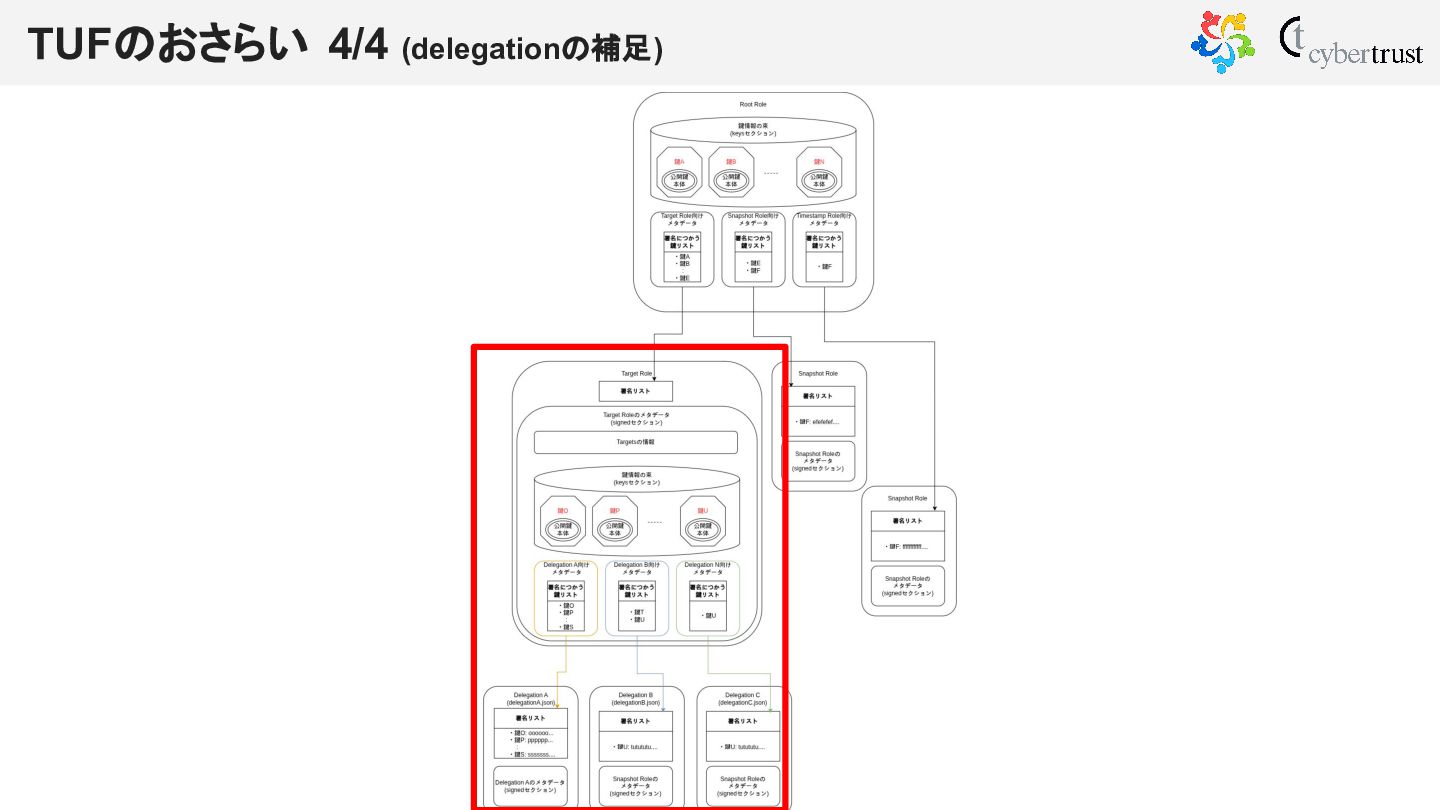
  4. TUFのおさらい 1/4 (TUFの目的) “a framework for securing software update systems”

    TUFは「ソフトウェアアップデートシステムを安全に するためのフレームワーク 」である “We are not creating a universal update system” “a simple and flexible way that applications can have high levels of security with their software update systems” TUFは既存のソフトウェアアップデートシステムを 塗り替えたり統合するものではない 既存のソフトウェアアップデートシステムが自身を, 攻撃から保護するために活用できるメカニズムを提供
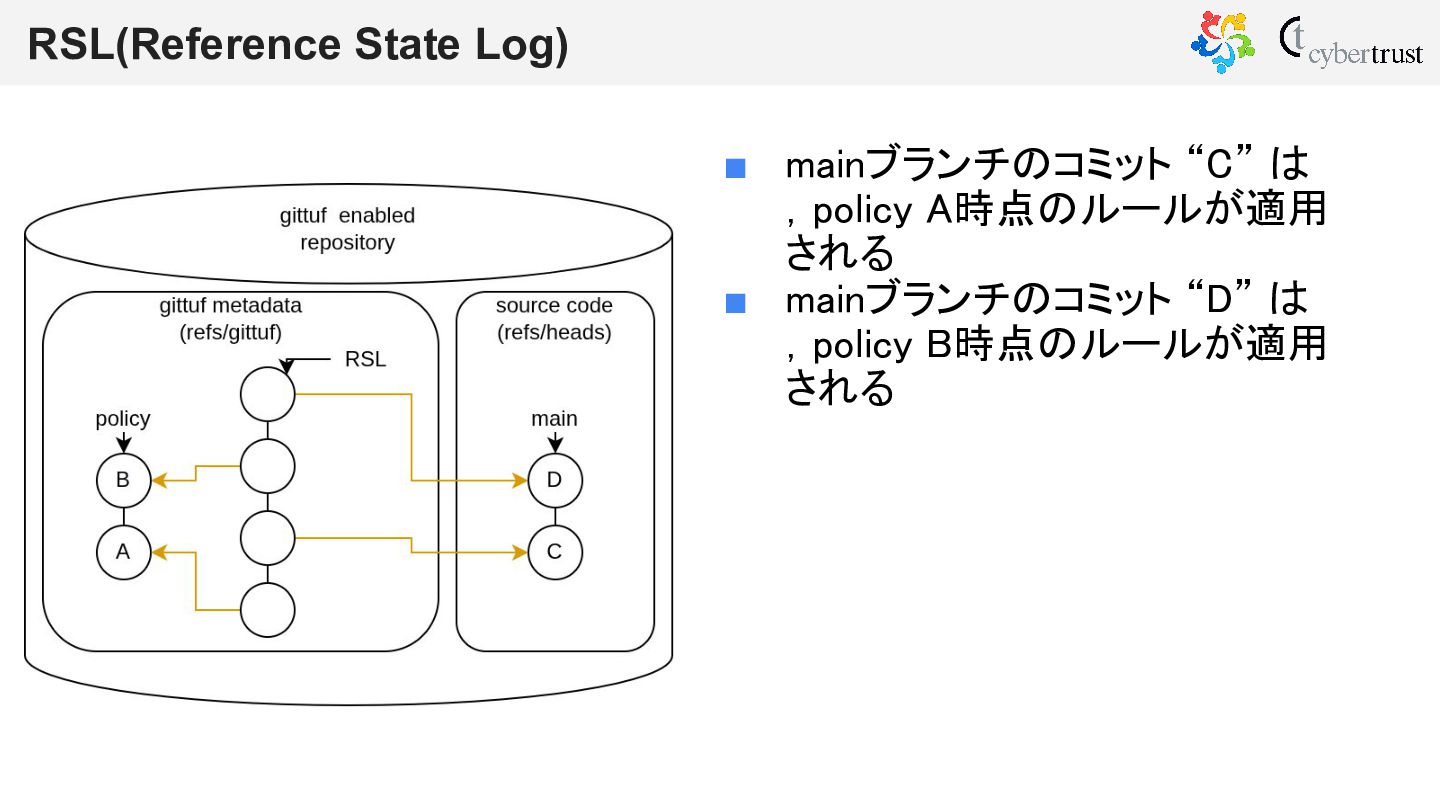
  5. RSL(Reference State Log) ▪ mainブランチのコミット “C” は ,policy A時点のルールが適用 される

    ▪ mainブランチのコミット “D” は ,policy B時点のルールが適用 される
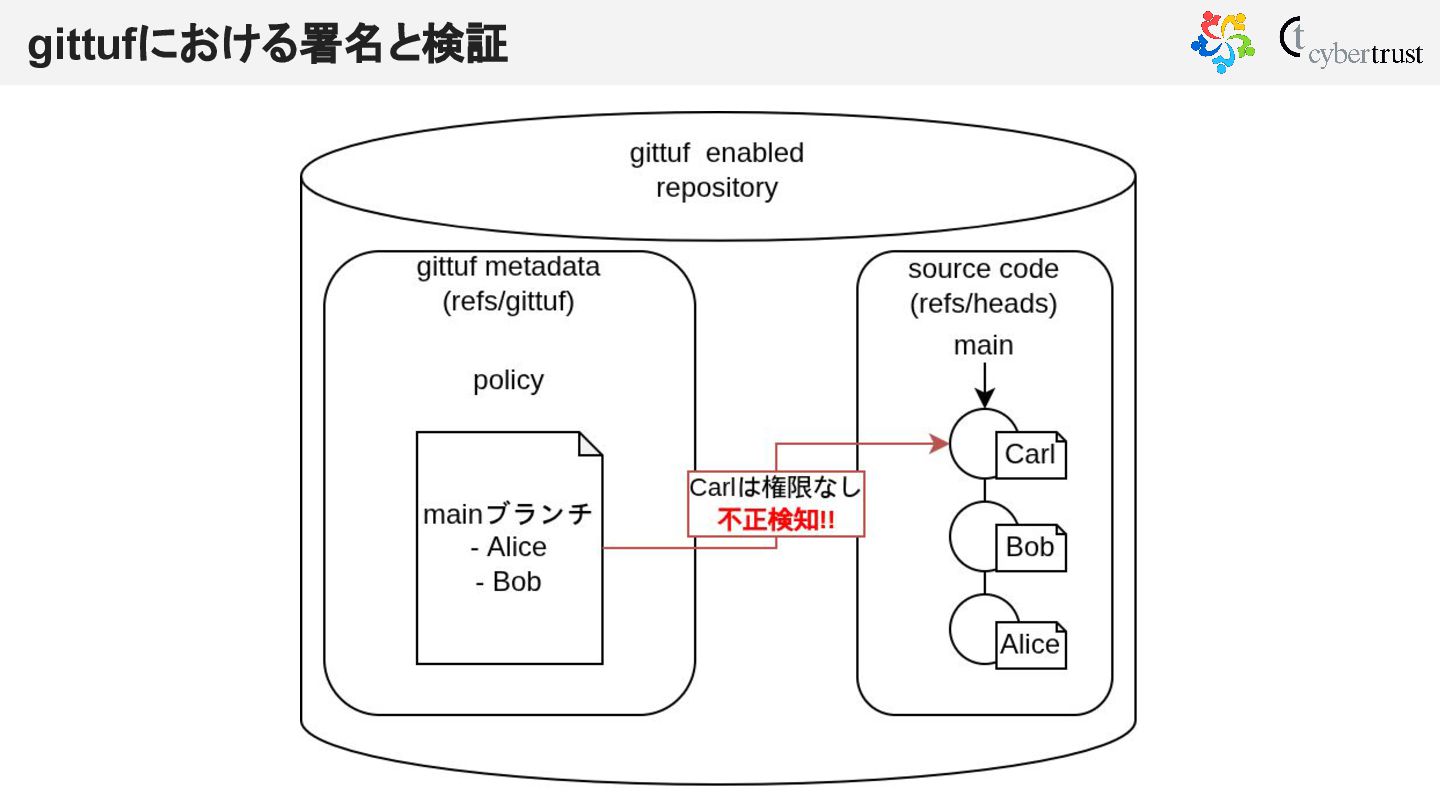
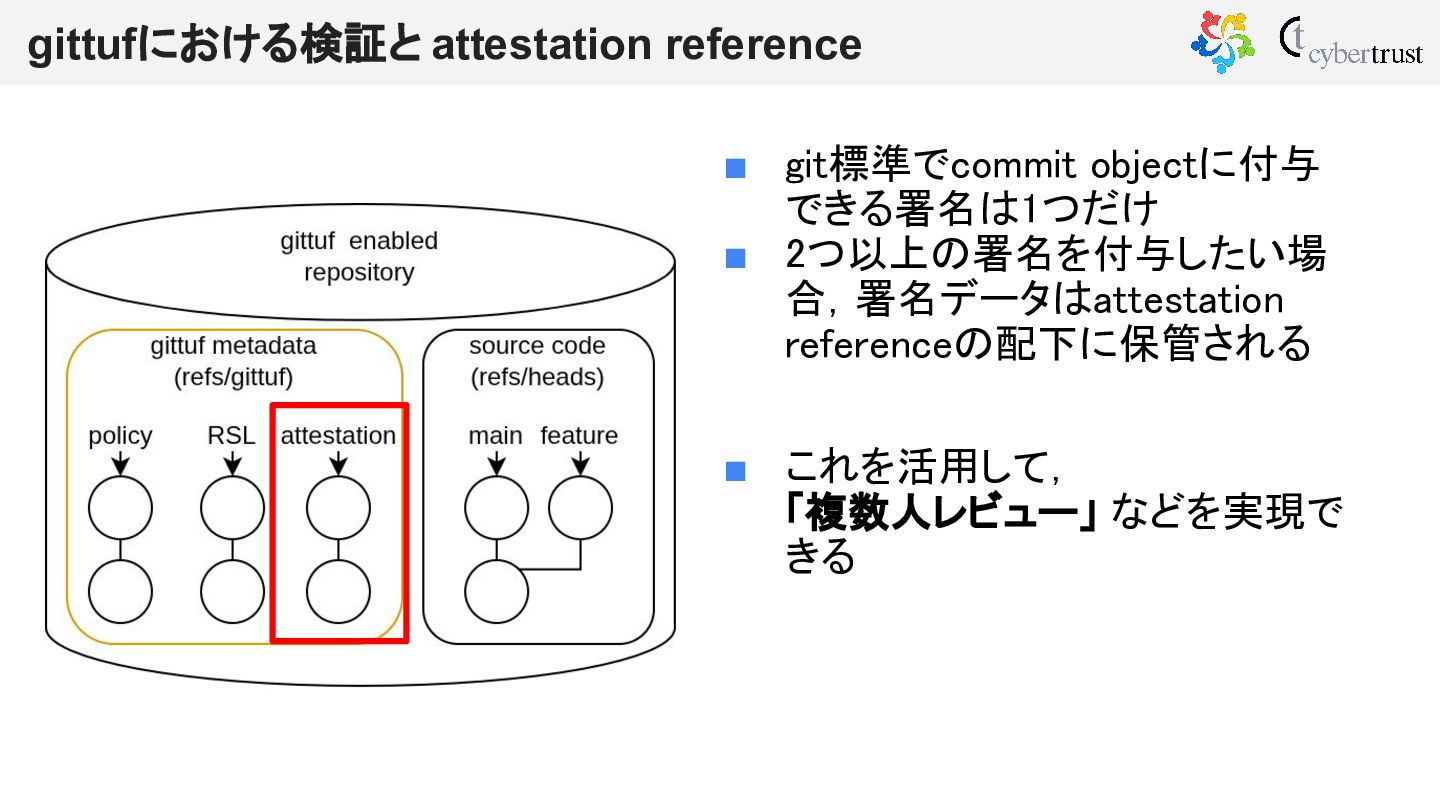
  6. gittufにおける署名と検証 ▪ gittufにおける署名 • git標準でgit objectにつけられる署名を活用 • すべてのcommit objectには署名がつけられる ▪

    gittufにおける検証 • 署名を検証することにより,「そのコミットを作成した人物」が特定 できる(principalと呼ぶ) • policyとprincipal,および変更内容を比較し,policyに則った変更 であるかを検証する