Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Rethinking Auth for SPAs and Micro Frontends: ...
Search
Sponsored
·
Your Podcast. Everywhere. Effortlessly.
Share. Educate. Inspire. Entertain. You do you. We'll handle the rest.
→
Manfred Steyer
PRO
September 26, 2022
Programming
290
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Rethinking Auth for SPAs and Micro Frontends: Easy and Secure With Gateways
Manfred Steyer
PRO
September 26, 2022
More Decks by Manfred Steyer
See All by Manfred Steyer
Human in the Loop Beyond Approval: Toward True Collaboration @FrontMania 2026 in Utrecht
manfredsteyer
PRO
0
67
Agentic UI: Where the Agent meets the User @FrontMania 2026 in Utrecht
manfredsteyer
PRO
0
69
A2UI as an Architecture Question: Agentic UI Between AI Freedom and Control
manfredsteyer
PRO
0
96
AI-Ready Angular Architectures Architecture as Executable Contract
manfredsteyer
PRO
0
260
Nostalgia Meets Technology: Super Mario with TypeScript @BASTA 2026 in Mainz, Germany
manfredsteyer
PRO
0
65
Beyond Chatbots: Agentic UI with Open Standards @AGNTcon 2026 in Amsterdam
manfredsteyer
PRO
0
150
Next-Level Frontends: Agentic Web UIs Under the Hood
manfredsteyer
PRO
0
110
Agentic UI with Open Standards @ngGraz Sep 2026
manfredsteyer
PRO
0
120
Agentic UI with Open Standards @GDG Salzburg, Bgl & Prishtina
manfredsteyer
PRO
0
100
Other Decks in Programming
See All in Programming
作って学ぶSpring BootのAuto Configuration / JJUG Night Seminar 2026-10-19
rshindo
0
170
KiroのSpecで「五目並べ」を作ってみる
satoshi256kbyte
1
380
パズルゲームの作り方 / how to make puzzle games
kaityo256
PRO
2
300
re:Inventに行く前に知っておきたい現地参加のノウハウ
nokomoro3
0
430
iOS 27でニュースアプリはどう変わる!? 〜日経電子版の新機能対応と、開発事例から〜
lynnswap
7
13k
機械に任せるテスト、人が見るテスト ⽣成AIで引き直した、運⽤保守フェーズの線引き
dske104
0
190
作れる、でも消せるか?──安全に「枯らして消す」機能削除術 / Drain, Then Delete
chobishiba
2
780
[JA] Domain Modeling with Vanilla Rails: 「操作」から再考するRailsの設計論
yasaichi
2
410
Kotlinの15年とServer-Side Kotlin
n_takehata
1
150
APNsからLive Activityを開始する話
yumnumm
0
170
Agents on Rails - Rails at Scale 2026
irinanazarova
0
570
Event is what happens
moro
2
850
Featured
See All Featured
State of Search Keynote: SEO is Dead Long Live SEO
ryanjones
0
320
Information Architects: The Missing Link in Design Systems
soysaucechin
1
1.2k
The Impact of AI in SEO - AI Overviews June 2024 Edition
aleyda
6
1.2k
Building Better People: How to give real-time feedback that sticks.
wjessup
371
20k
ラッコキーワード サービス紹介資料
rakko
1
5.4M
Have SEOs Ruined the Internet? - User Awareness of SEO in 2025
akashhashmi
0
520
Joys of Absence: A Defence of Solitary Play
codingconduct
1
550
How To Speak Unicorn (iThemes Webinar)
marktimemedia
1
600
Dominate Local Search Results - an insider guide to GBP, reviews, and Local SEO
greggifford
PRO
0
370
Building a Modern Day E-commerce SEO Strategy
aleyda
45
9.3k
Bootstrapping a Software Product
garrettdimon
PRO
306
120k
The Pragmatic Product Professional
lauravandoore
37
7.5k
Transcript
@ManfredSteyer ManfredSteyer Manfred Steyer, ANGULARarchitects.io
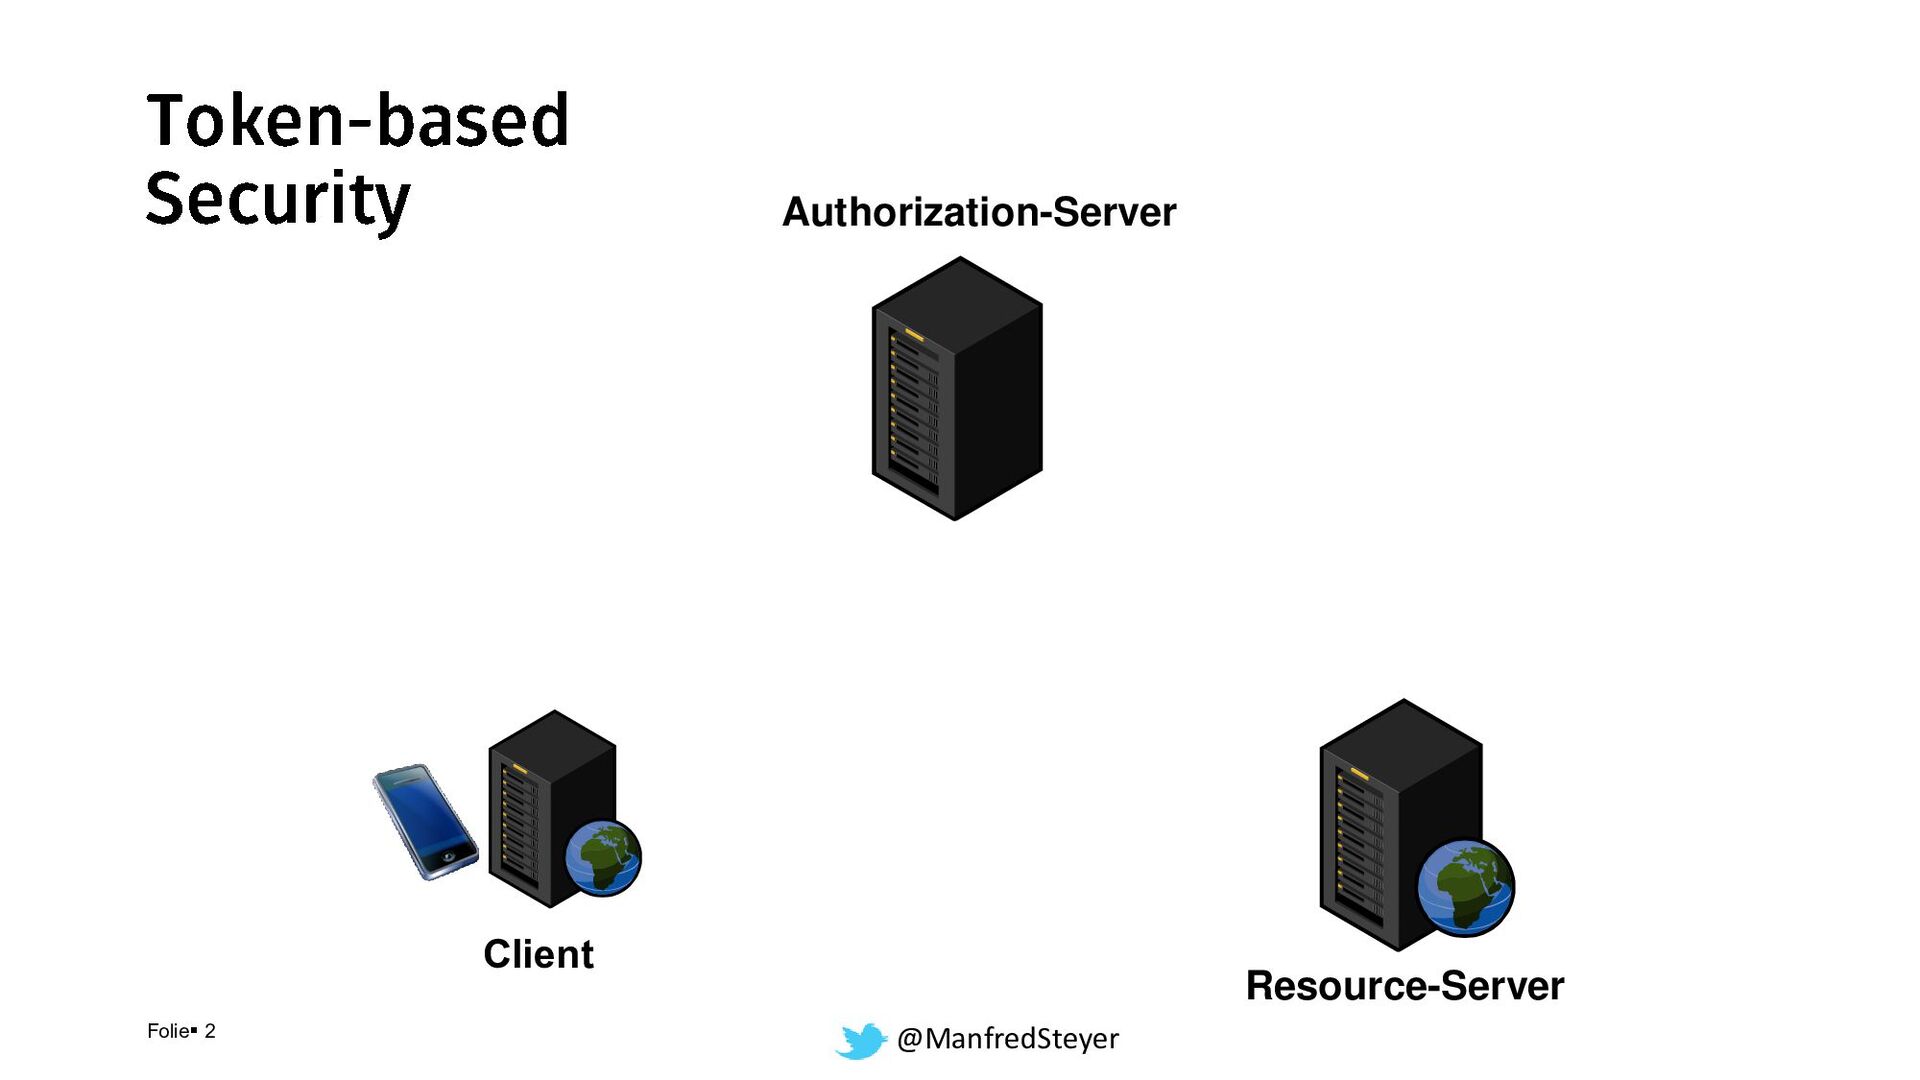
@ManfredSteyer Folie▪ 2 Client Authorization-Server Resource-Server
@ManfredSteyer Folie▪ 3 Client Authorization-Server Resource-Server 1. Redirection 2. Redirect
w/ (Code for) Access-Token in Query String 3. Access-Token
@ManfredSteyer Folie▪ 4 Client Authorization-Server Resource-Server 1. Redirection 2. Redirect
w/ (Code for) Access-Token and Id-Token 3. Access-Token User Info Endpoint (OIDC)
@ManfredSteyer
@ManfredSteyer
@ManfredSteyer Manfred Steyer
@ManfredSteyer
@ManfredSteyer
@ManfredSteyer
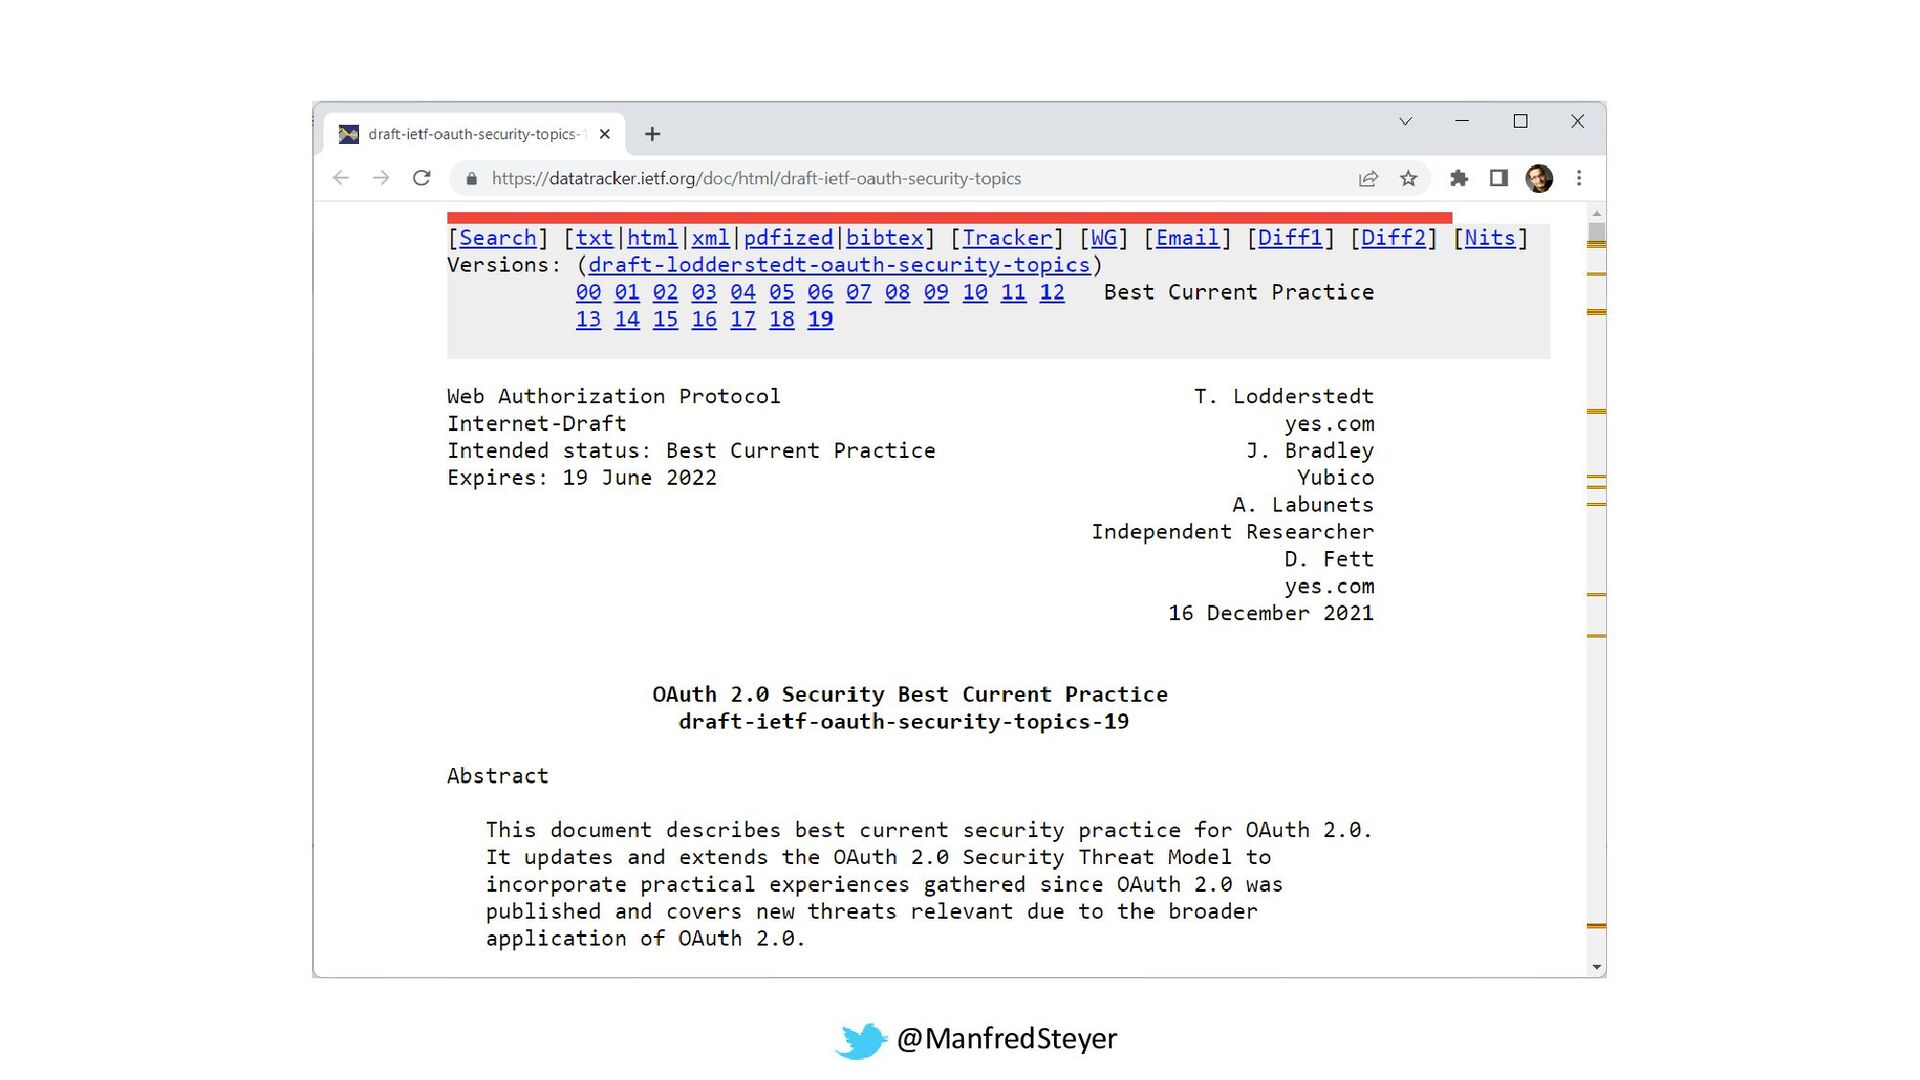
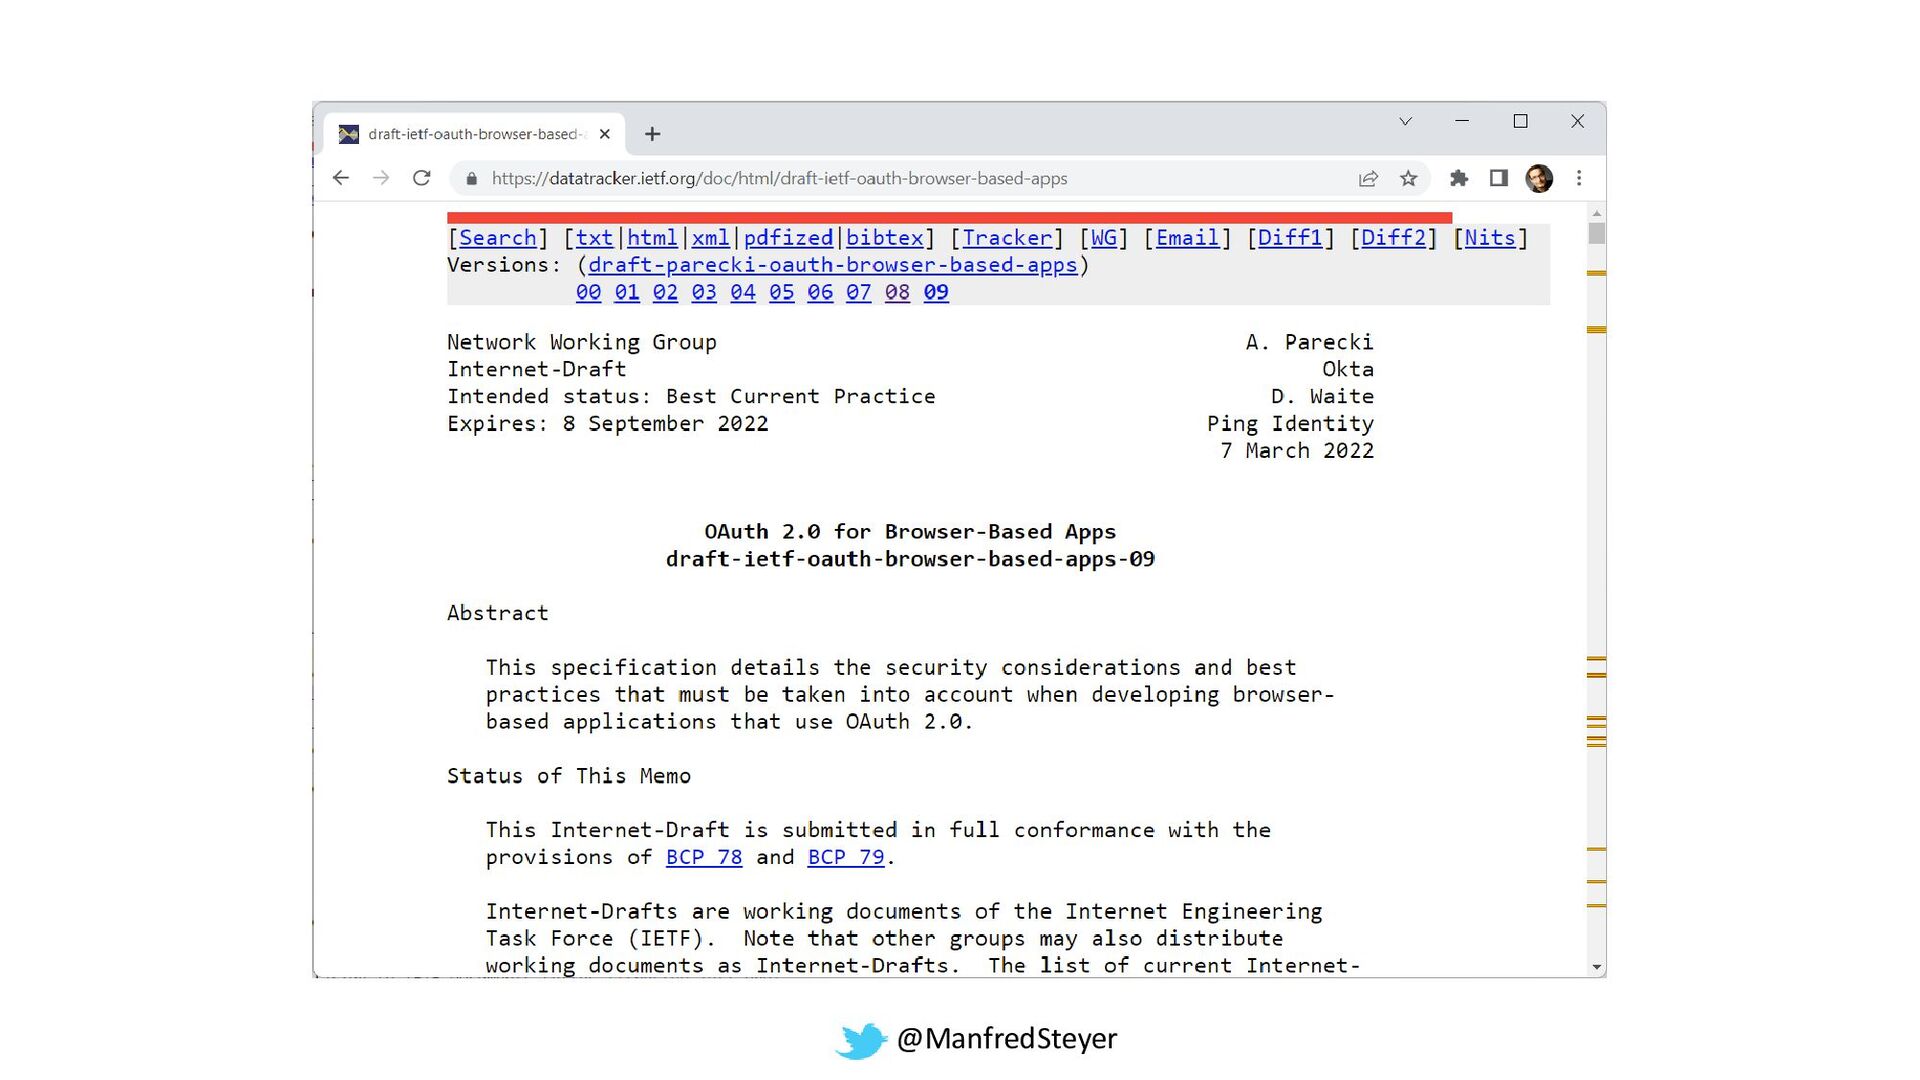
@ManfredSteyer Several suggestions for using OAuth 2 in a more
secure way
@ManfredSteyer Example: Using Code Flow + PKCE instead of Implicit
Flow
@ManfredSteyer Remaining Problem: XSS -> Stealing Tokens
@ManfredSteyer
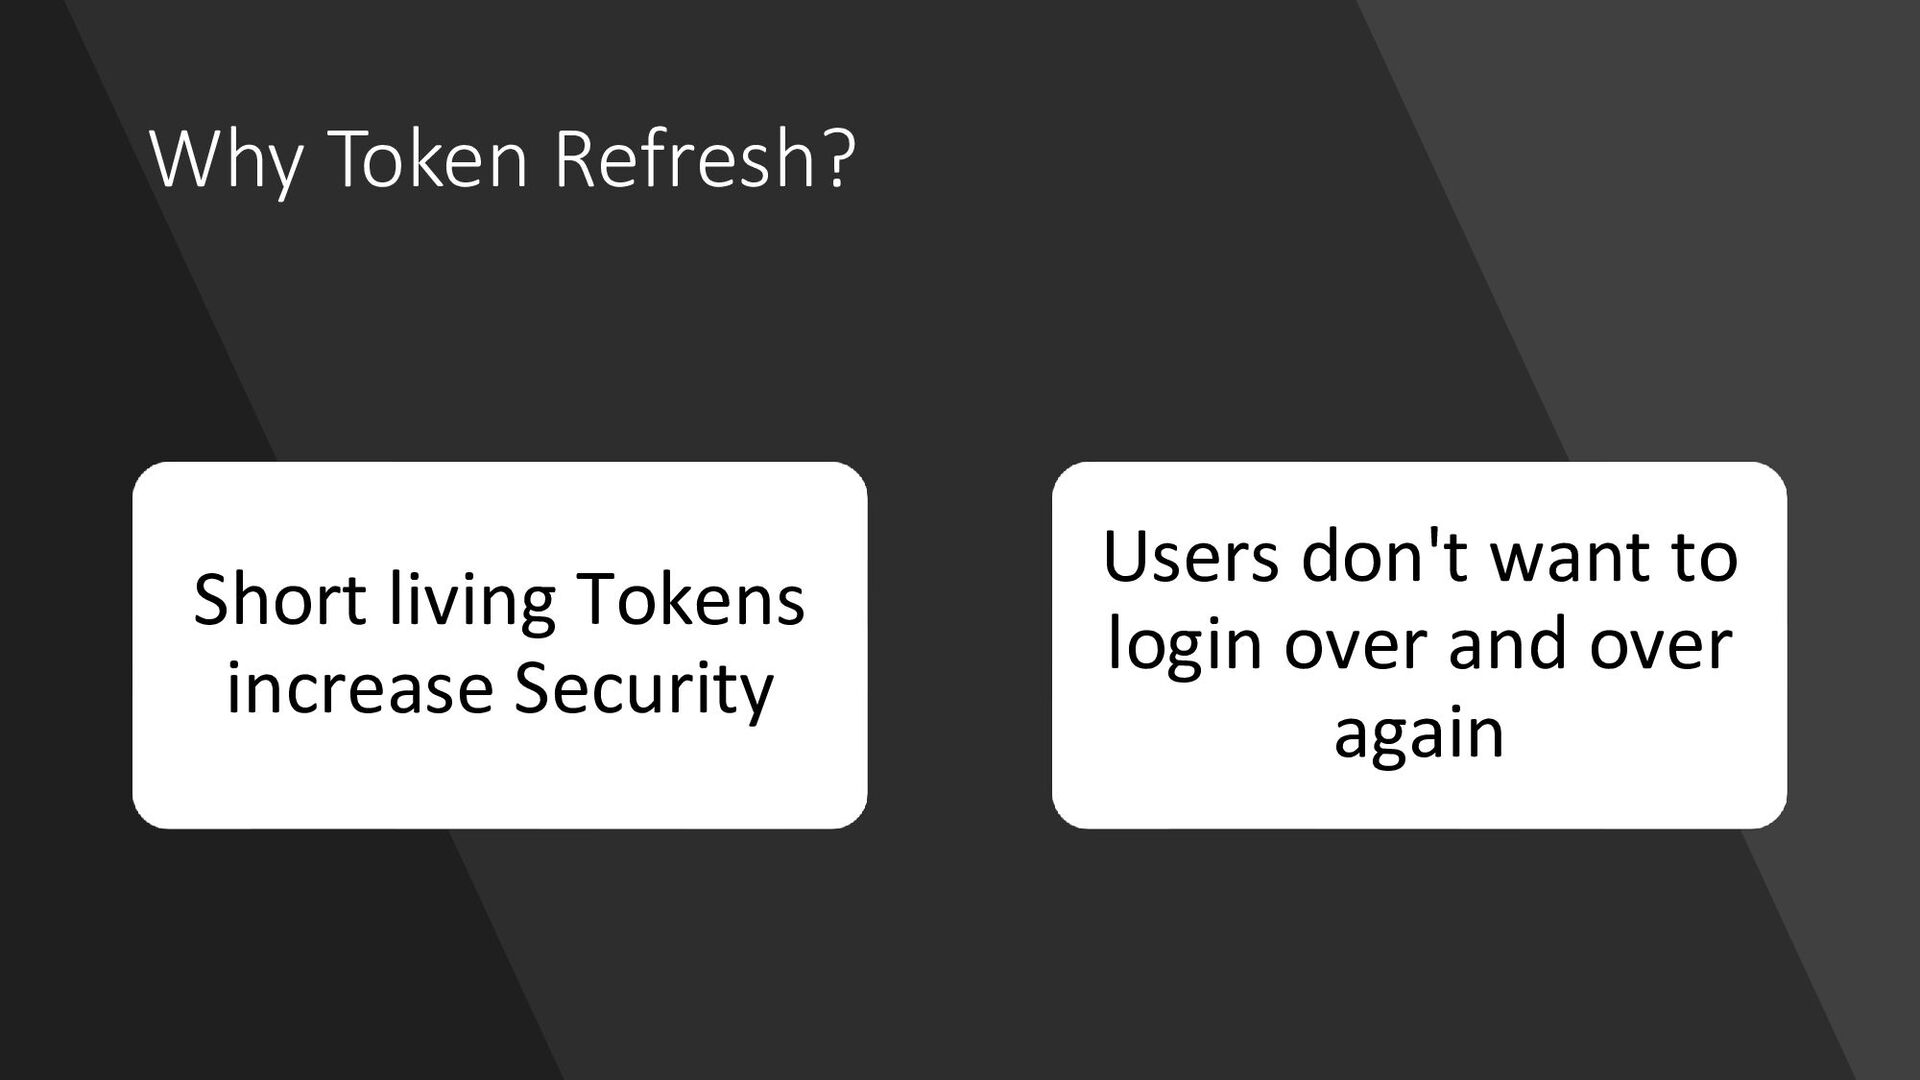
@ManfredSteyer Why Token Refresh? Short living Tokens increase Security Users
don't want to login over and over again
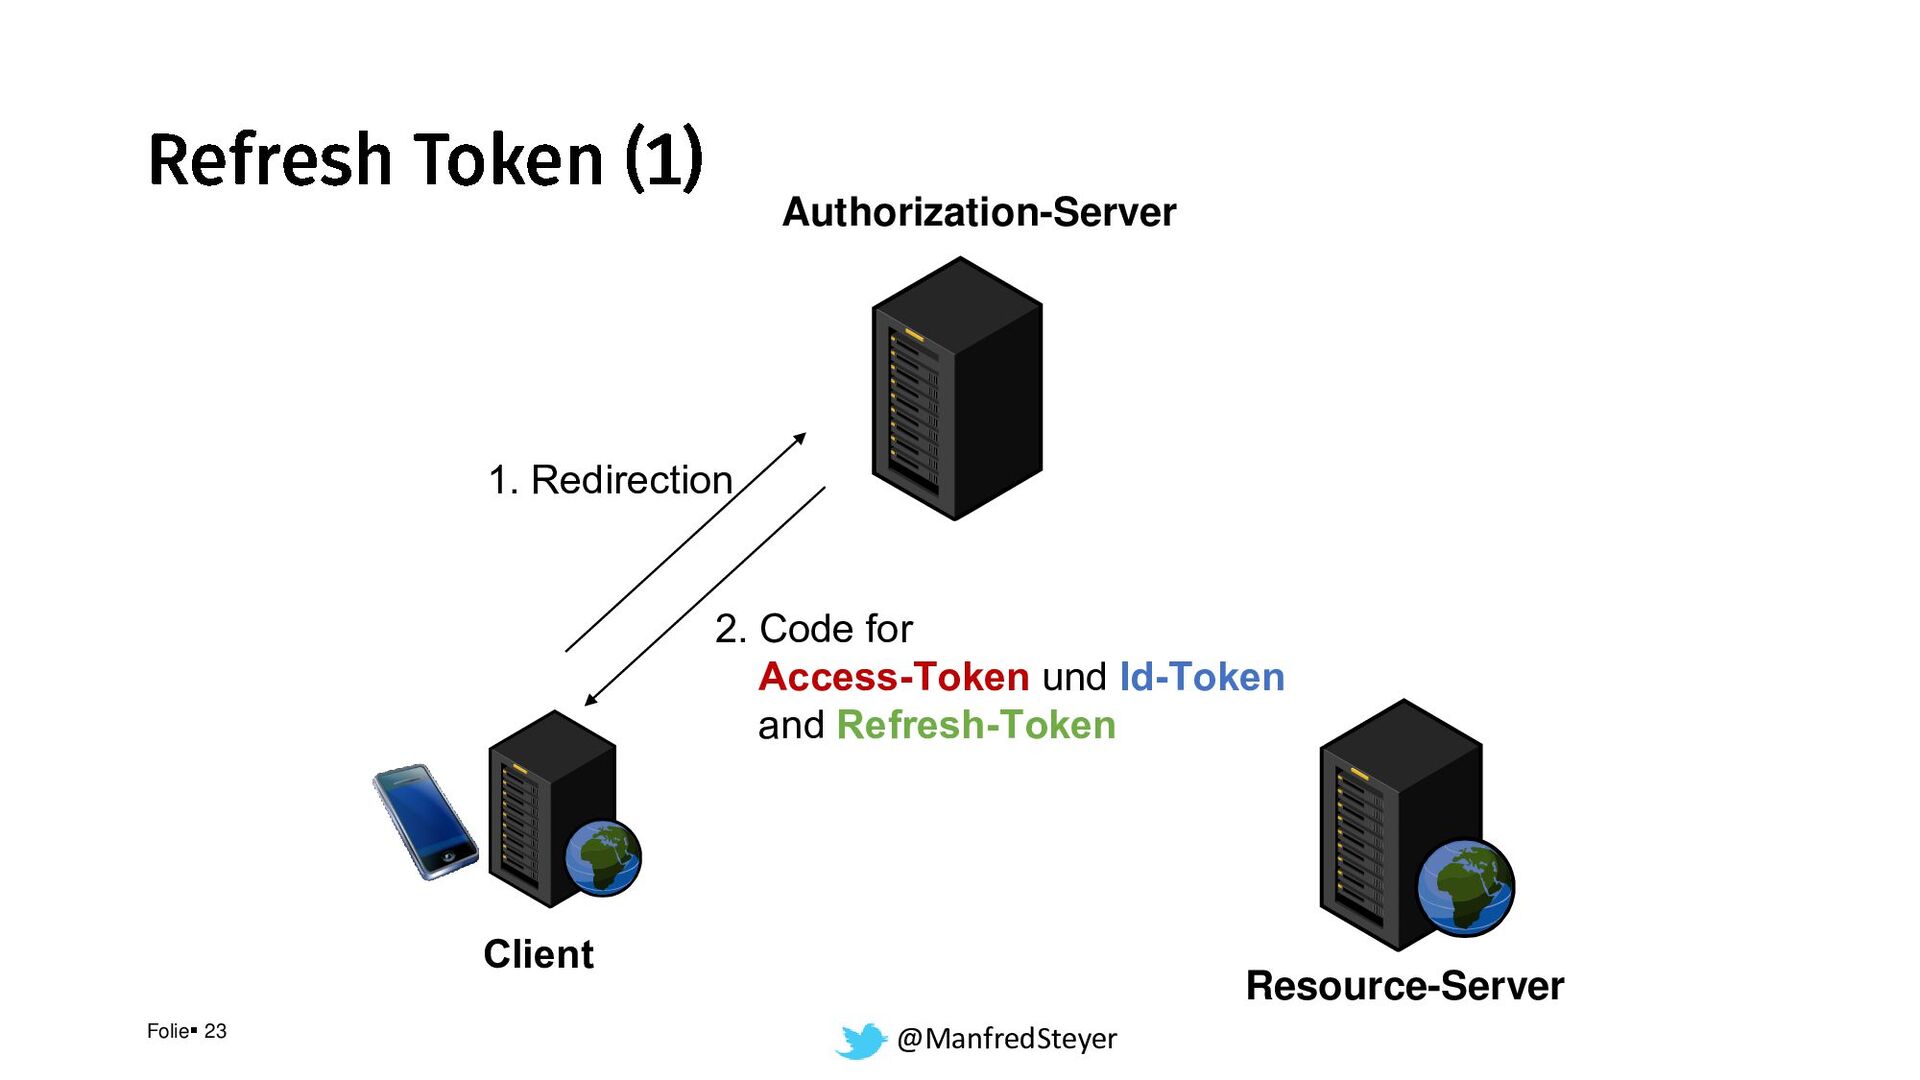
@ManfredSteyer Folie▪ 23 Client Authorization-Server Resource-Server 1. Redirection 2. Code
for Access-Token und Id-Token and Refresh-Token
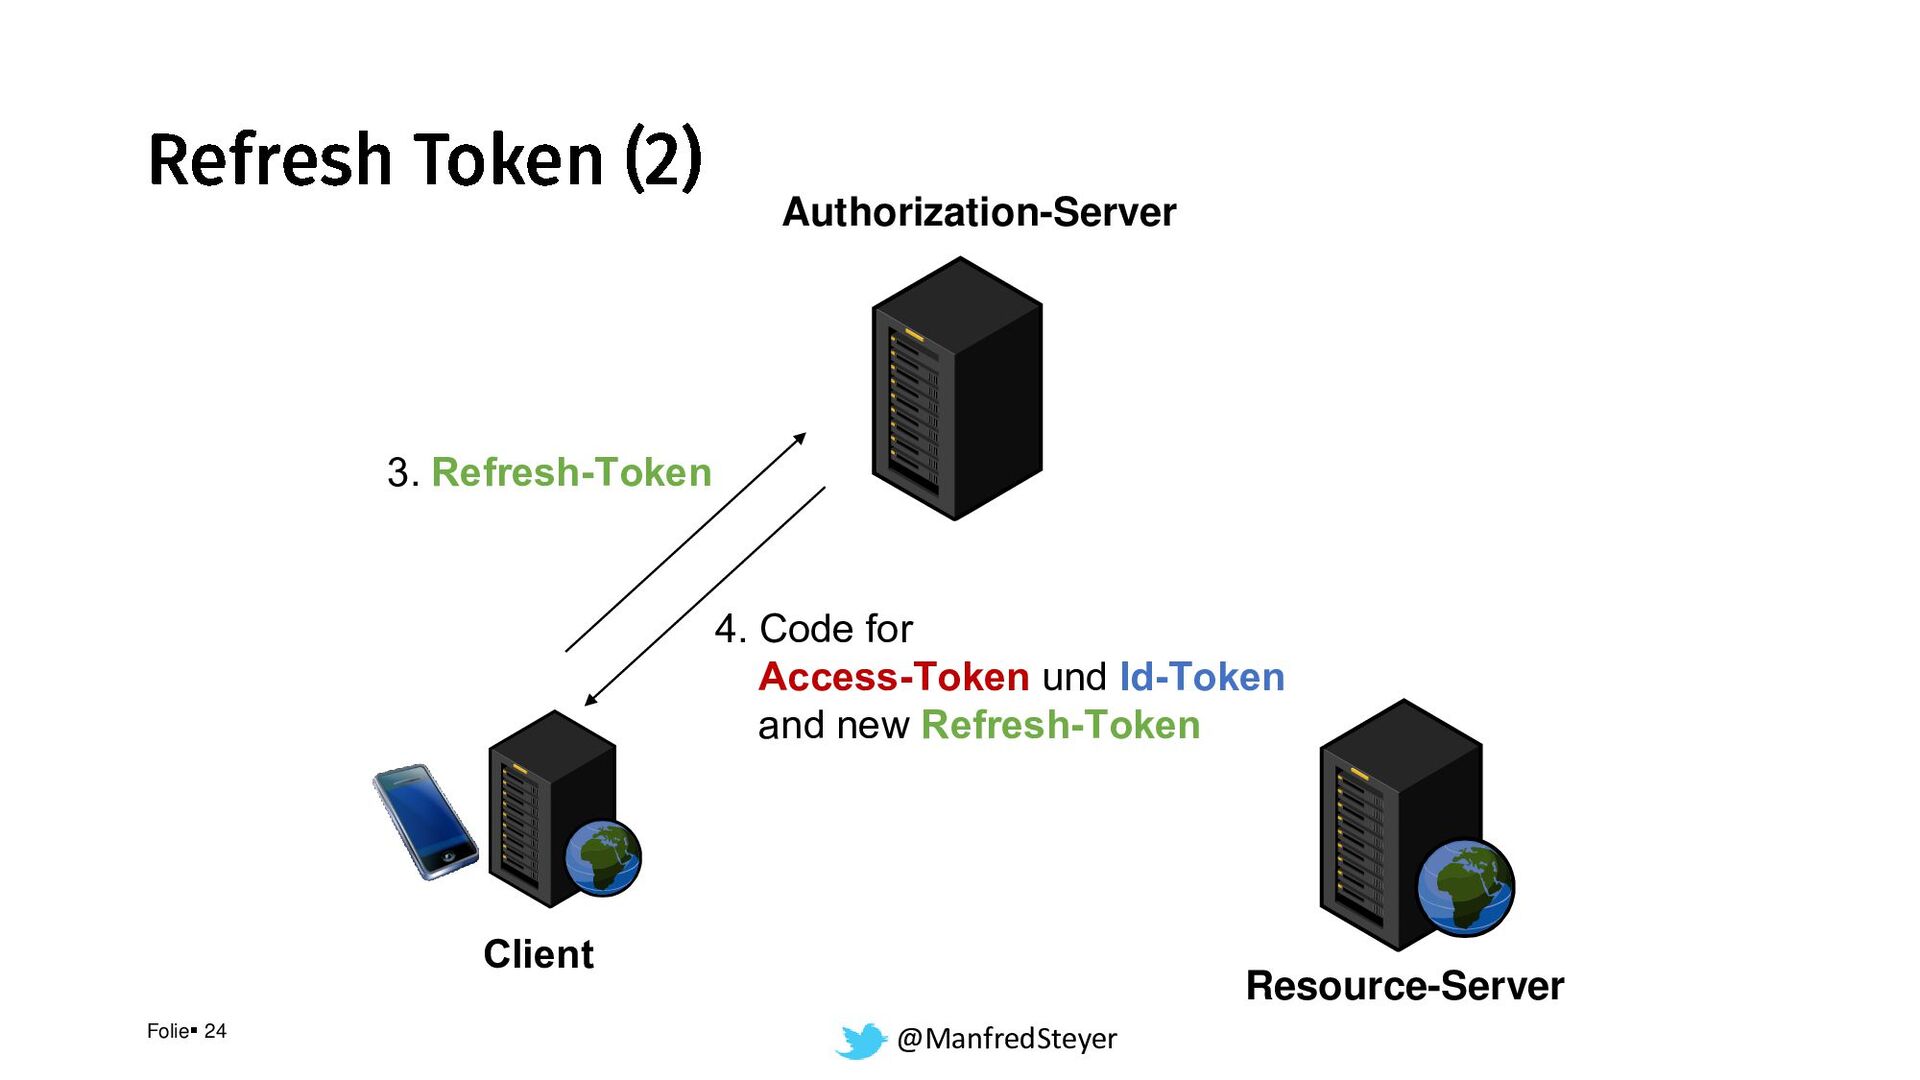
@ManfredSteyer Folie▪ 24 Client Authorization-Server Resource-Server 3. Refresh-Token 4. Code
for Access-Token und Id-Token and new Refresh-Token
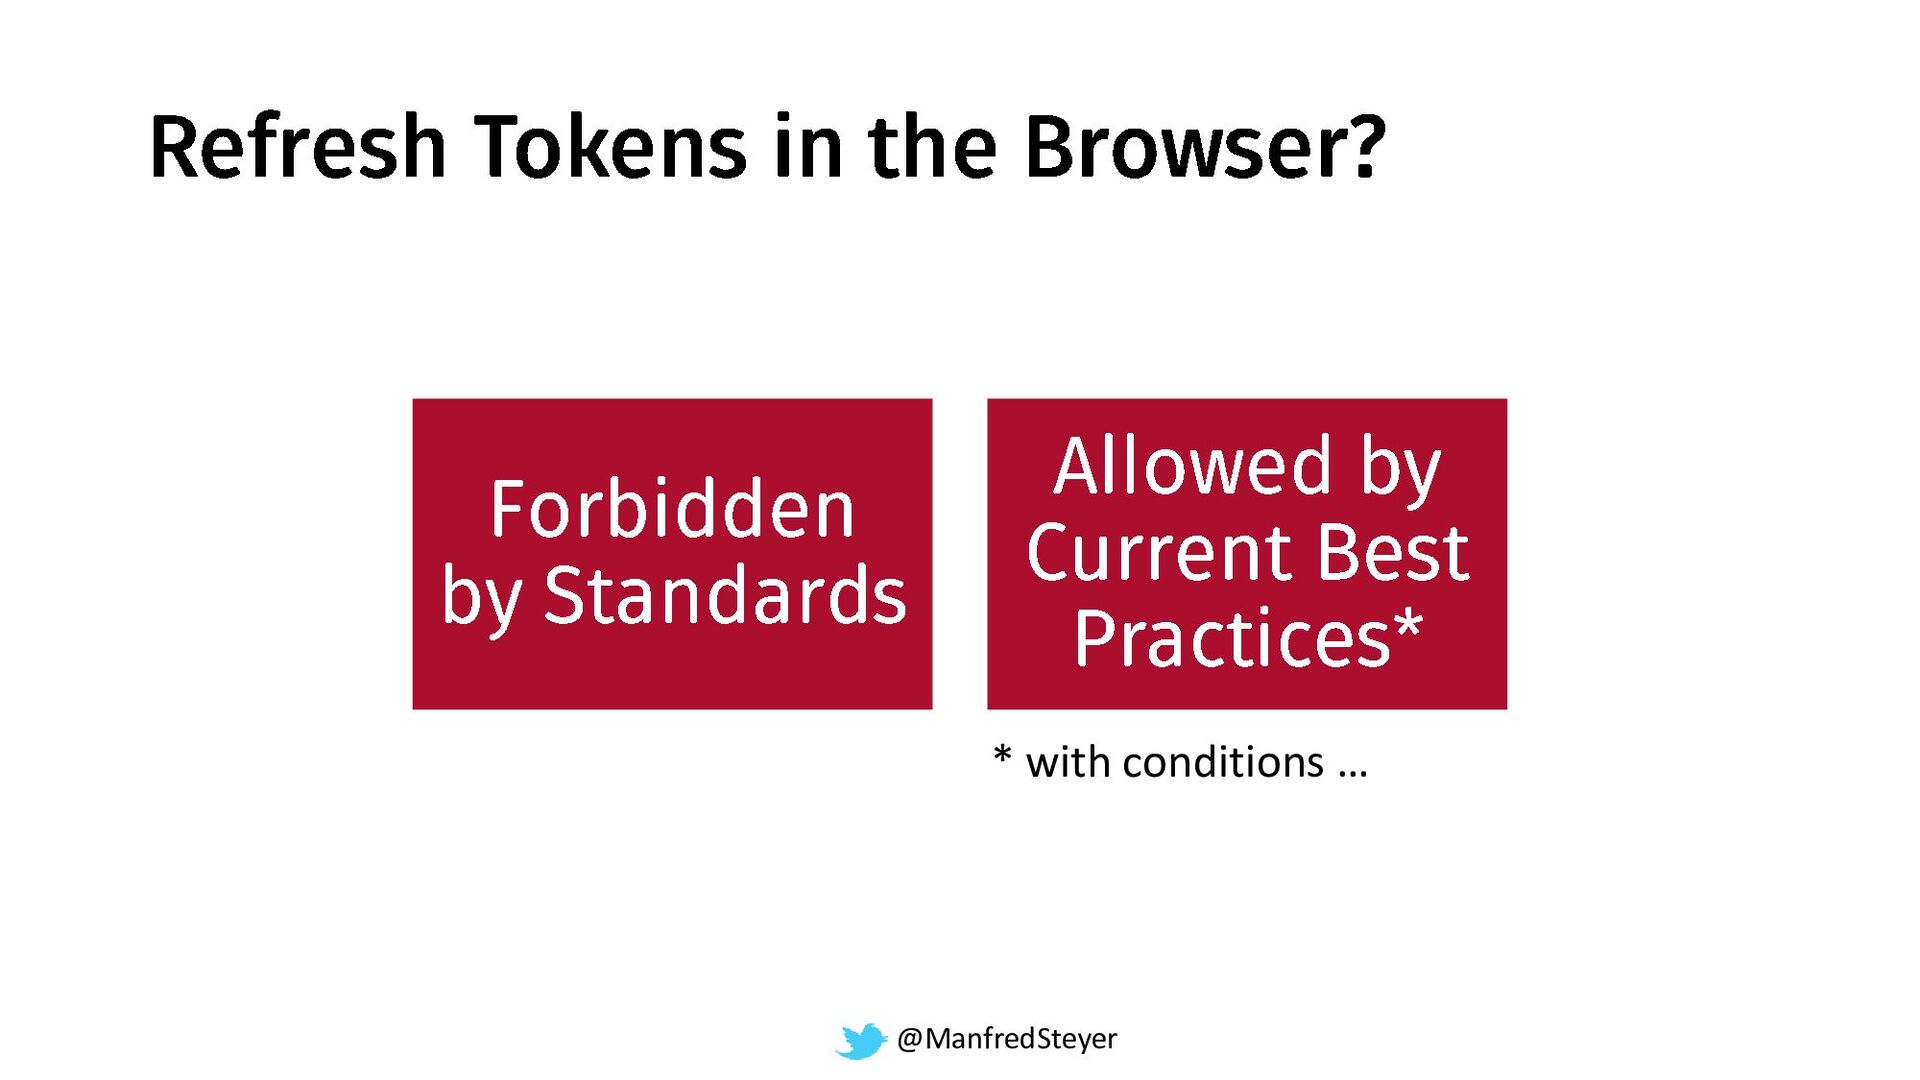
@ManfredSteyer * with conditions …
@ManfredSteyer
@ManfredSteyer
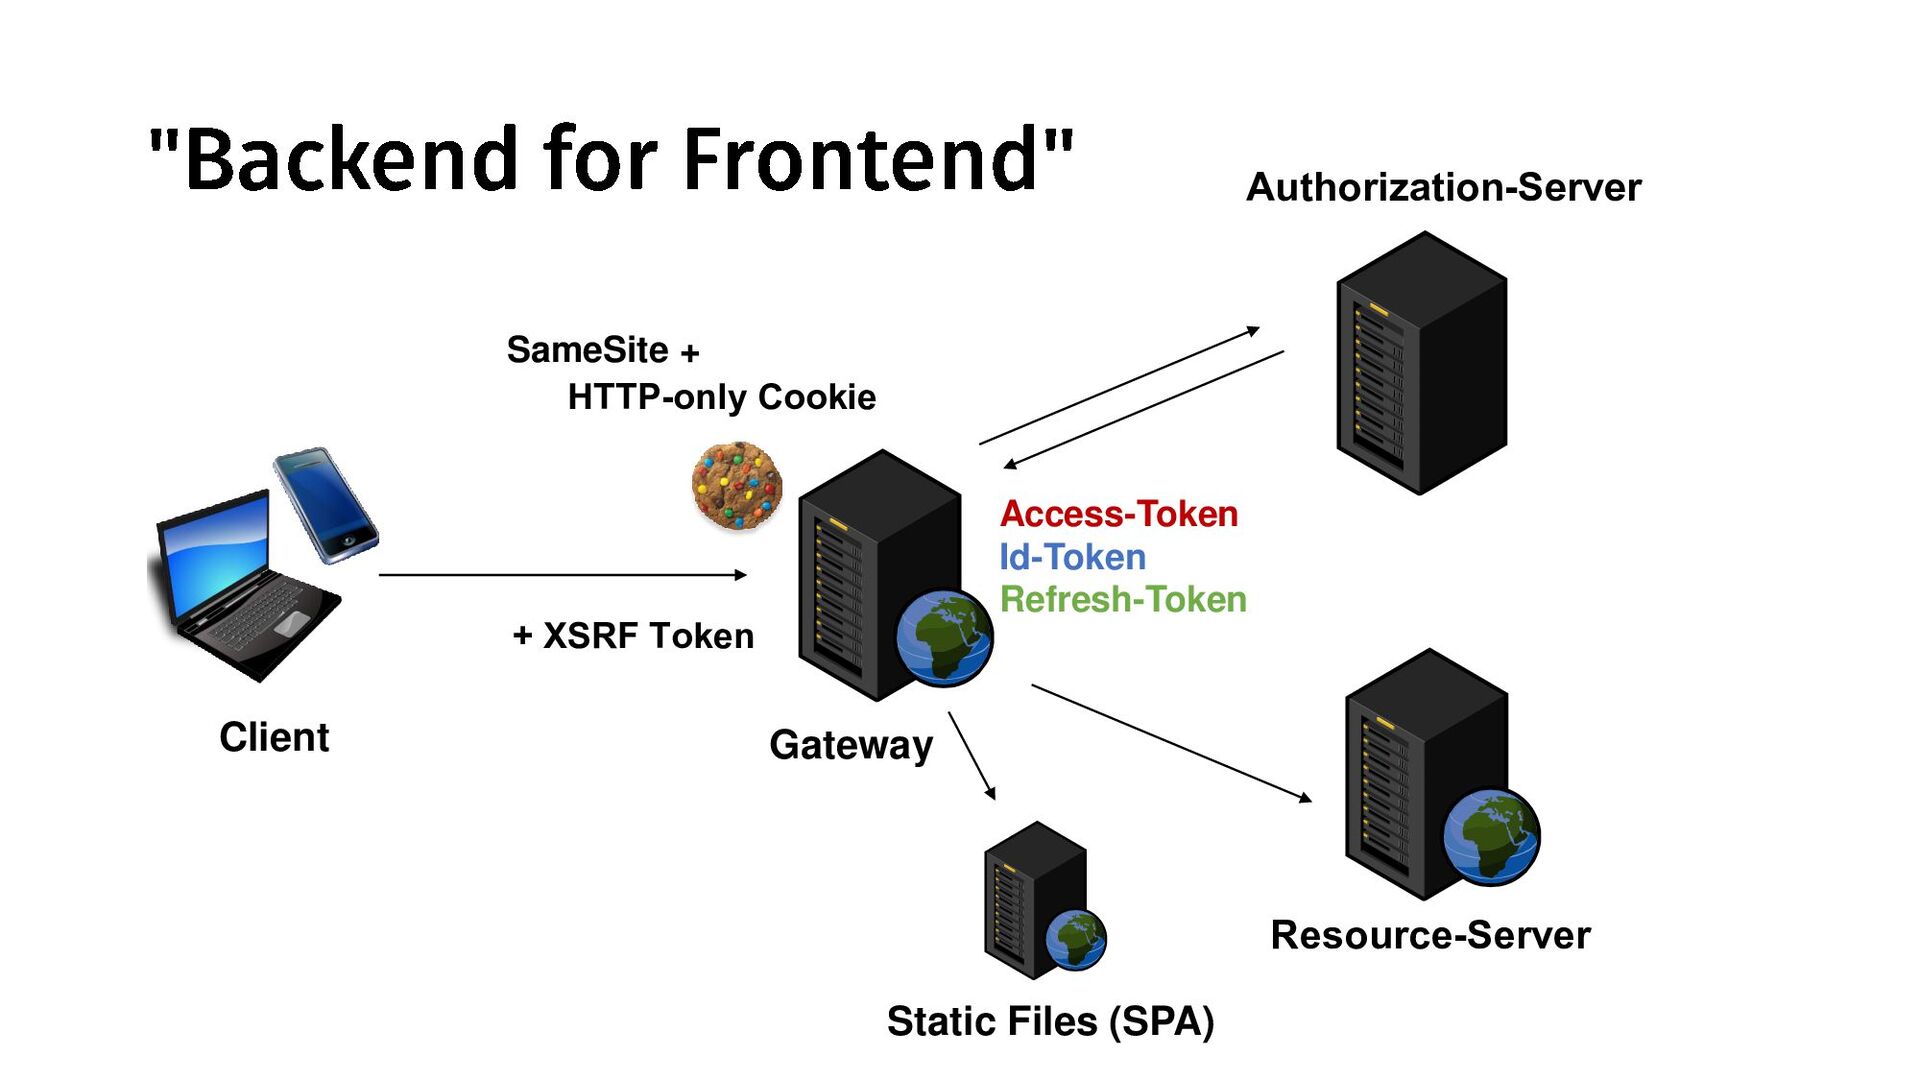
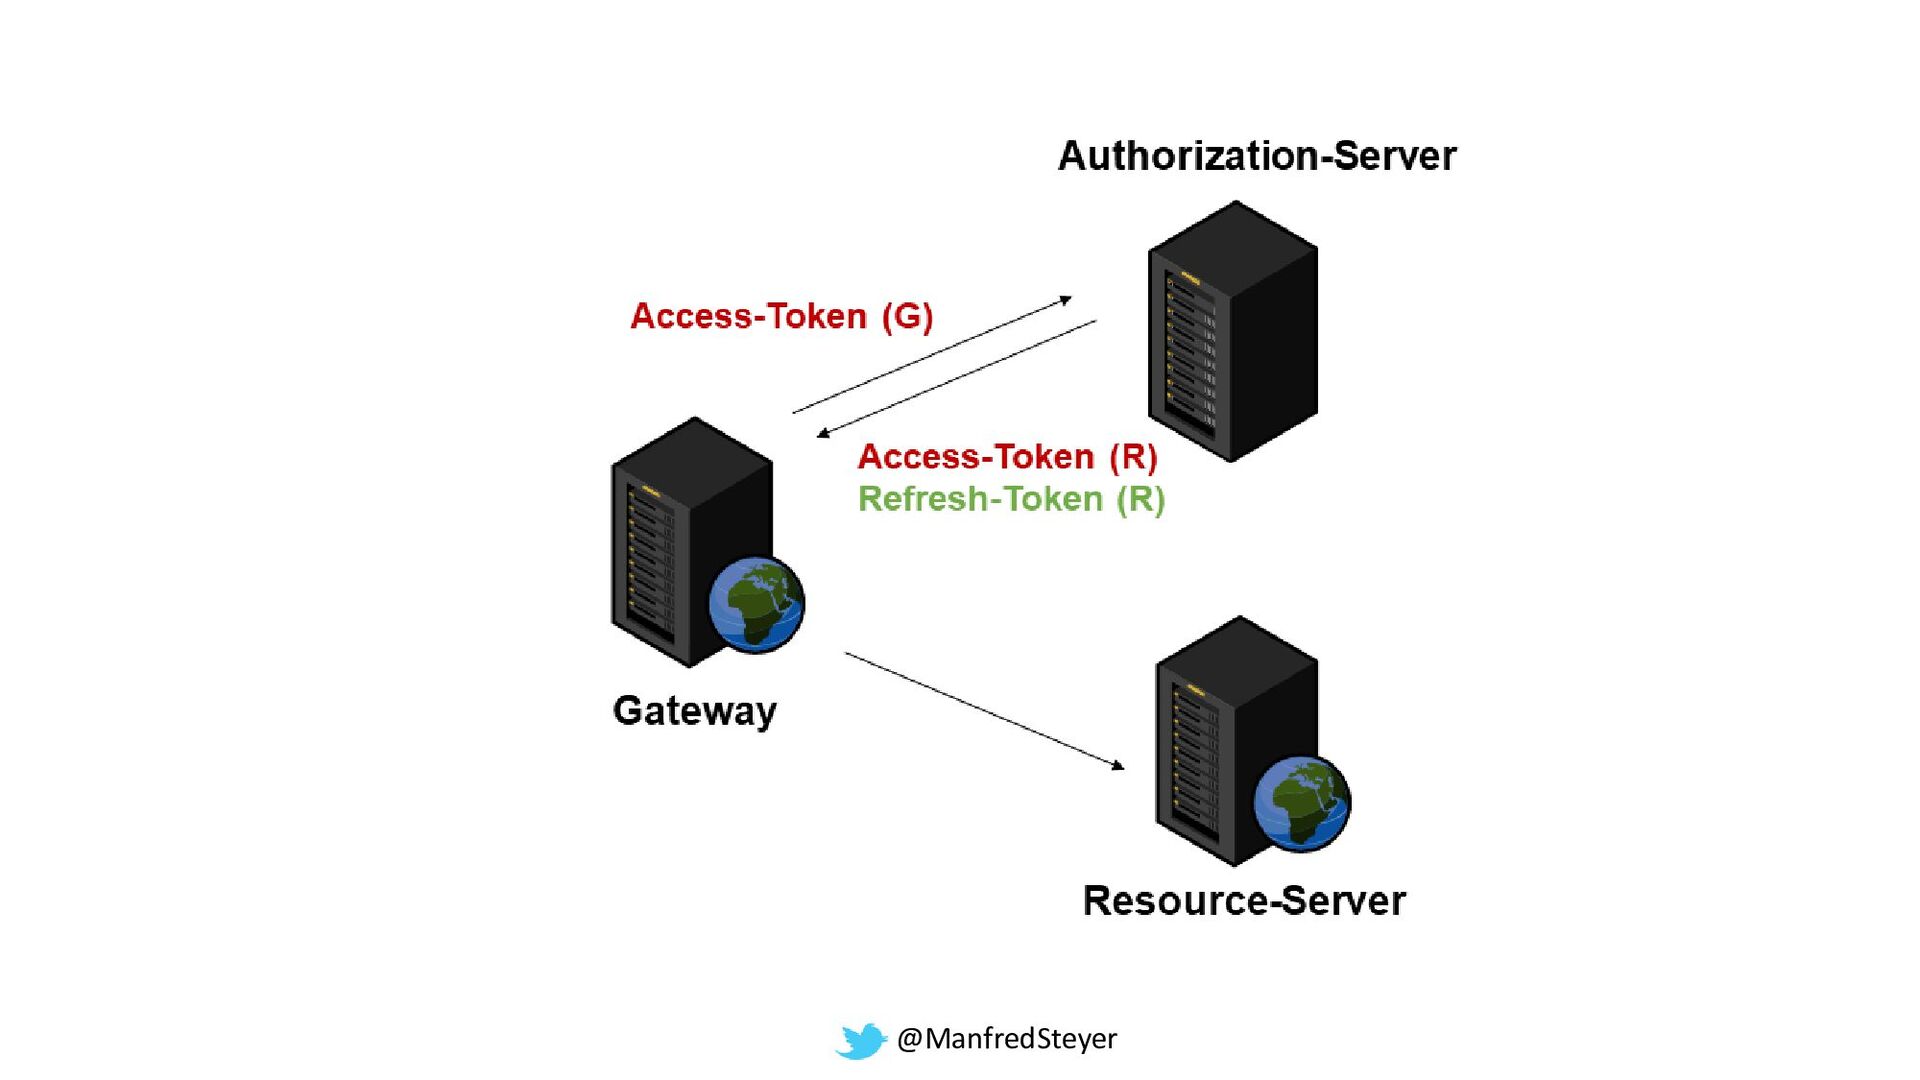
@ManfredSteyer Client Gateway Authorization-Server Resource-Server Access-Token Id-Token Refresh-Token HTTP-only Cookie
Static Files (SPA) + XSRF Token SameSite +
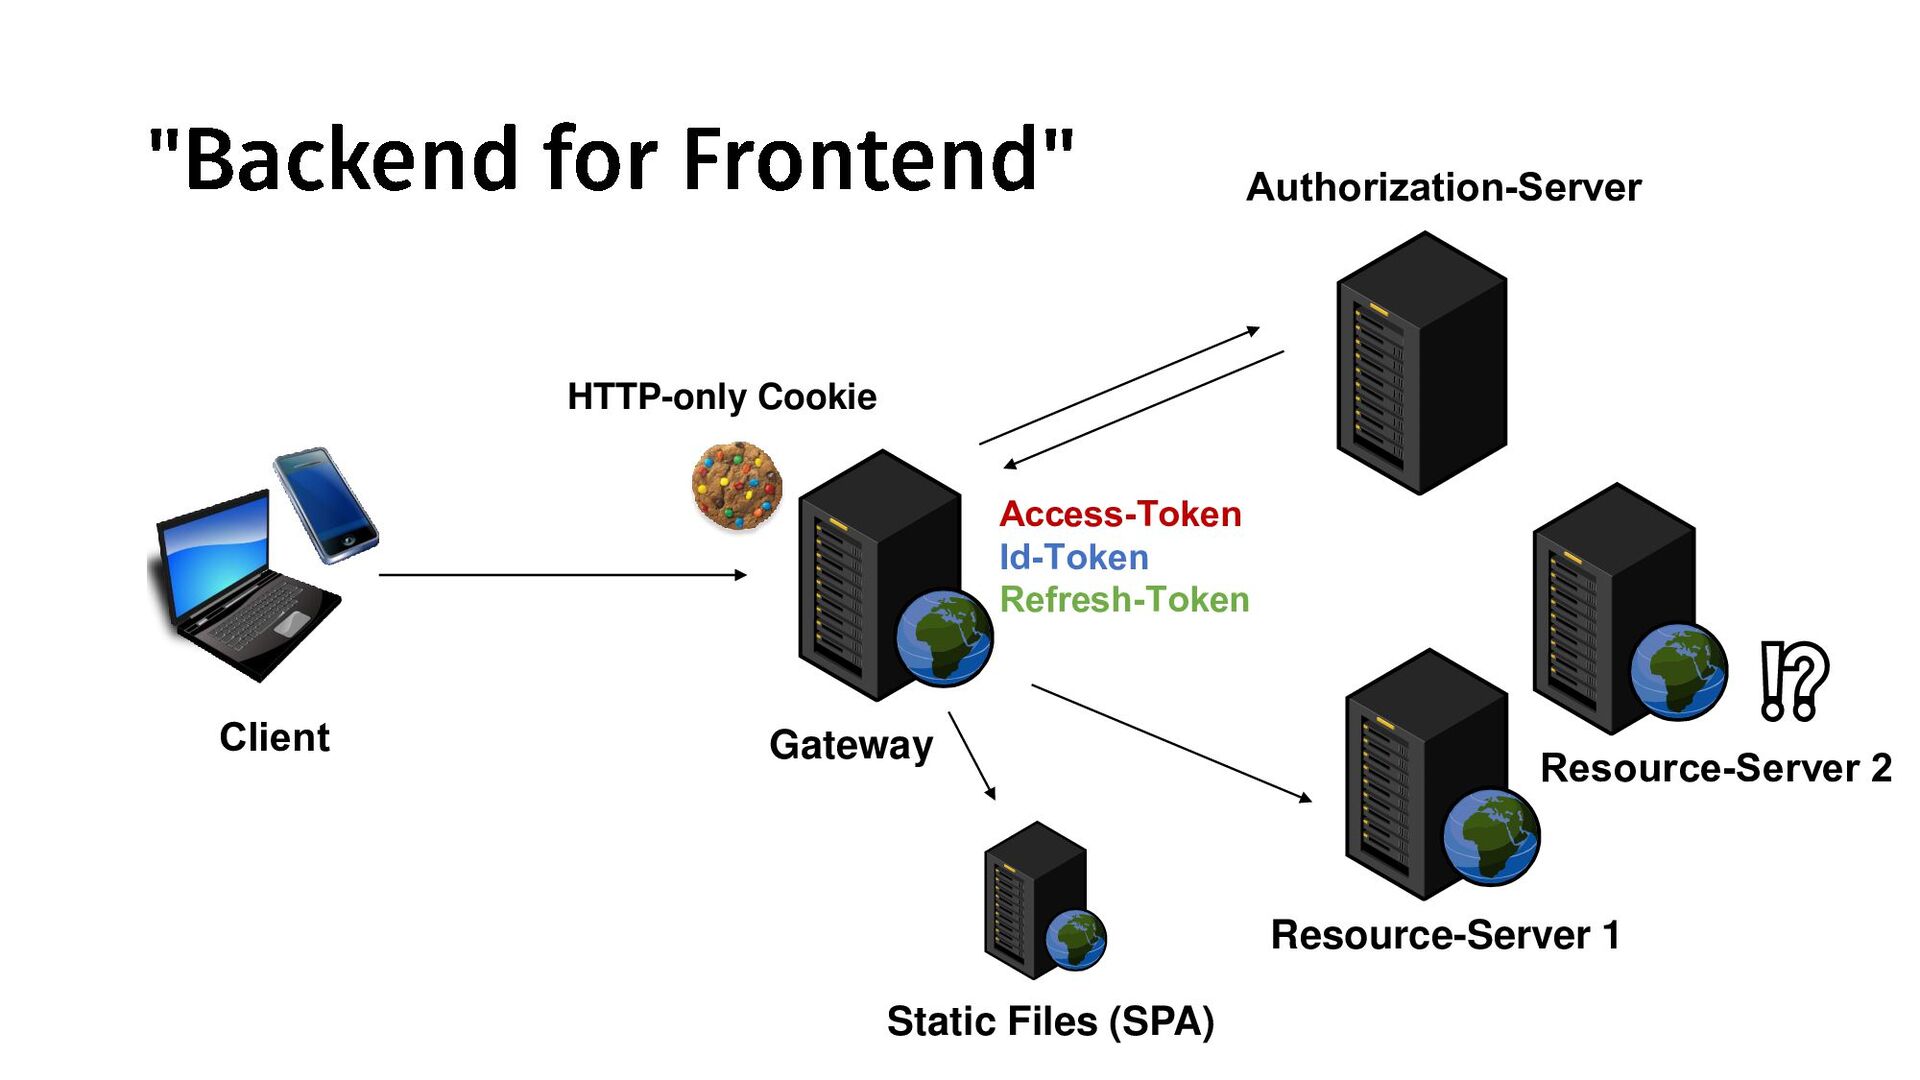
@ManfredSteyer Client Gateway Authorization-Server Resource-Server 1 Access-Token Id-Token Refresh-Token HTTP-only
Cookie Static Files (SPA) Resource-Server 2 ⁉️
@ManfredSteyer
@ManfredSteyer
@ManfredSteyer
@ManfredSteyer
@ManfredSteyer
@ManfredSteyer DEMO
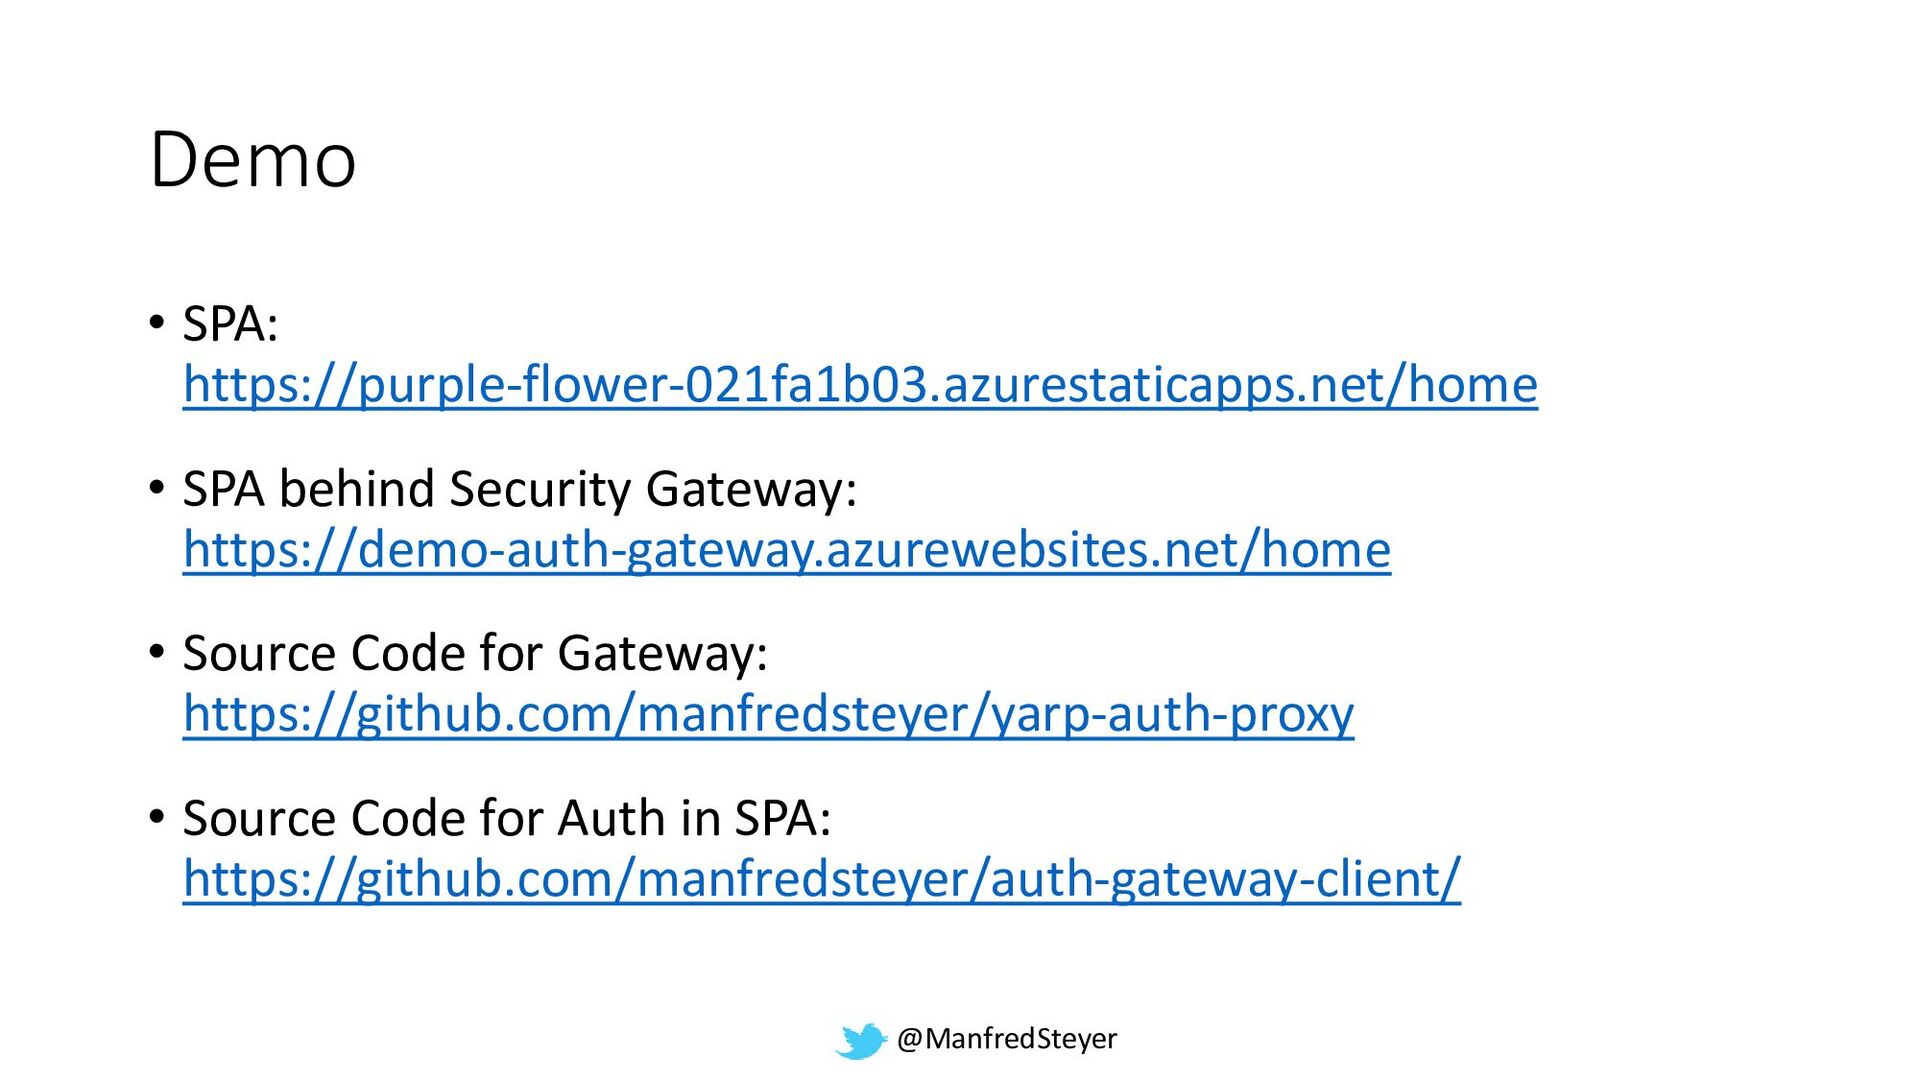
@ManfredSteyer Demo • SPA: https://purple-flower-021fa1b03.azurestaticapps.net/home • SPA behind Security Gateway:
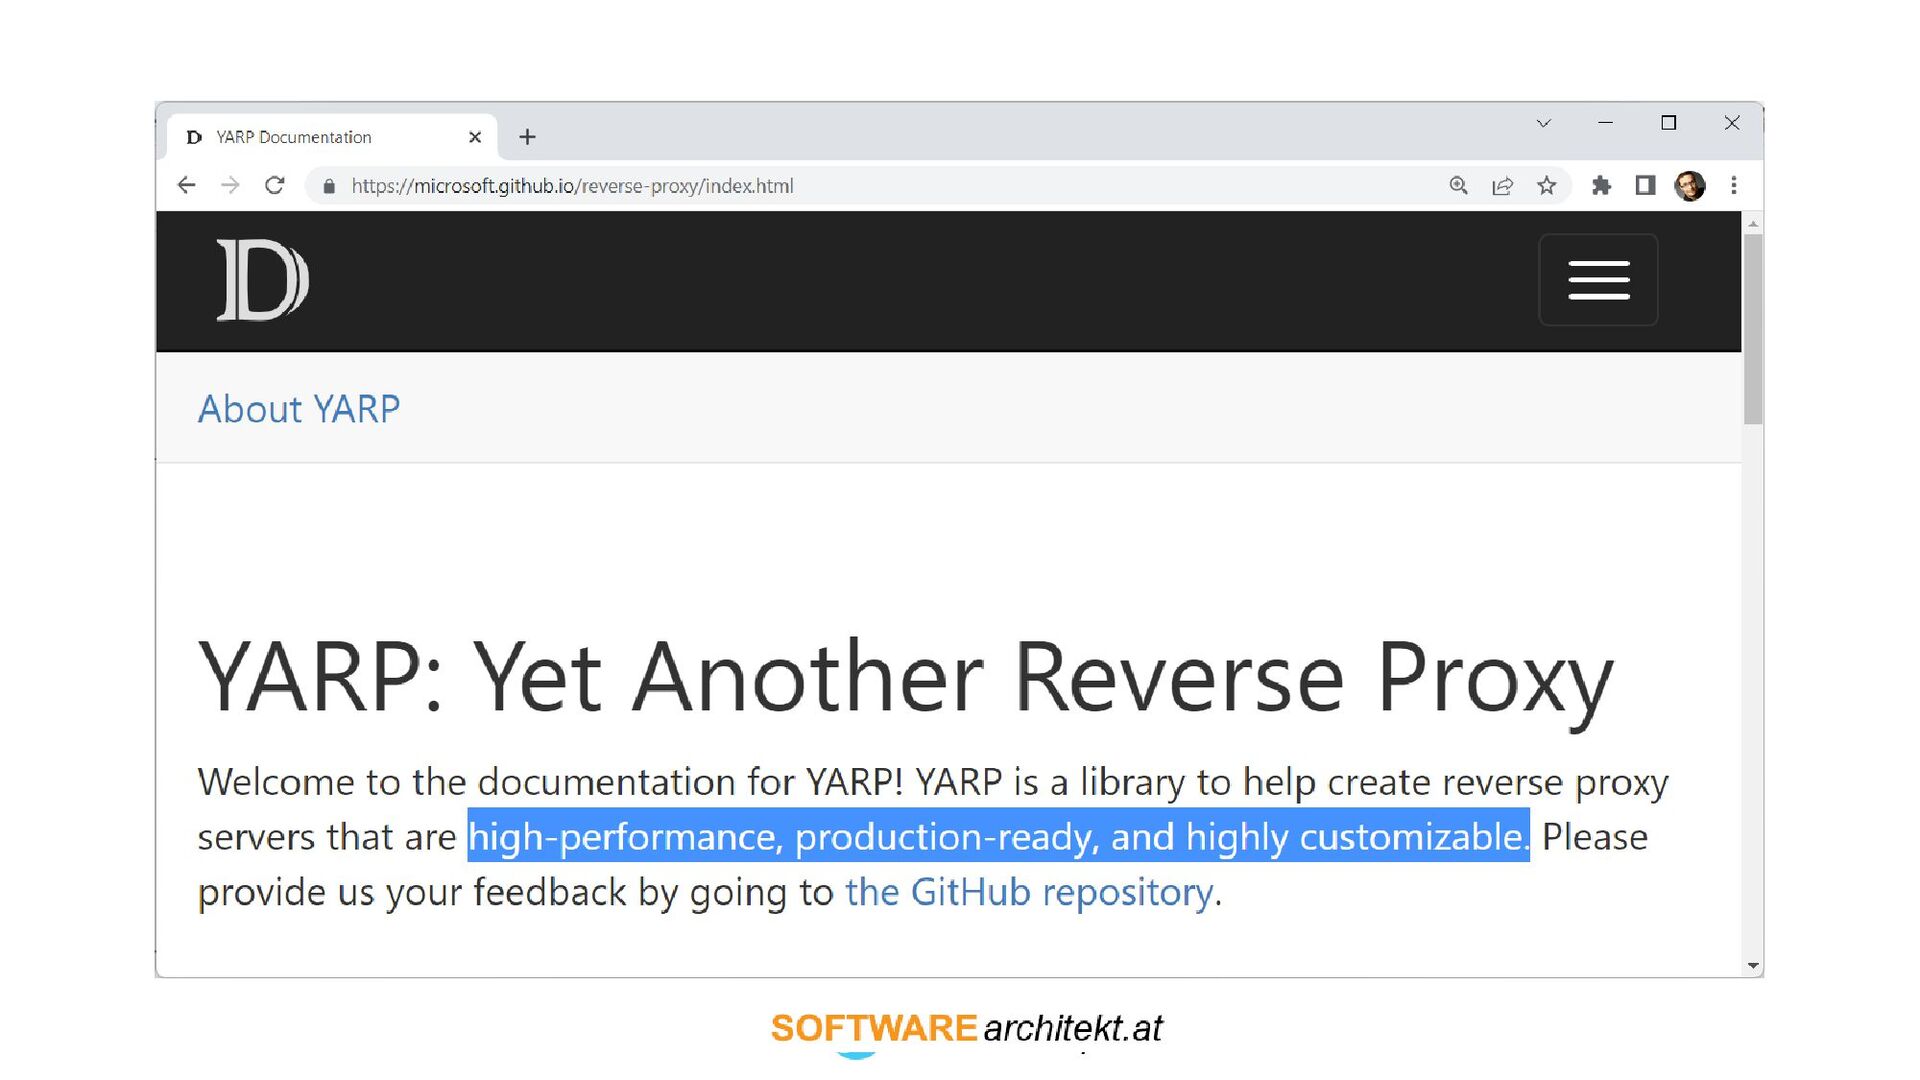
https://demo-auth-gateway.azurewebsites.net/home • Source Code for Gateway: https://github.com/manfredsteyer/yarp-auth-proxy • Source Code for Auth in SPA: https://github.com/manfredsteyer/auth-gateway-client/
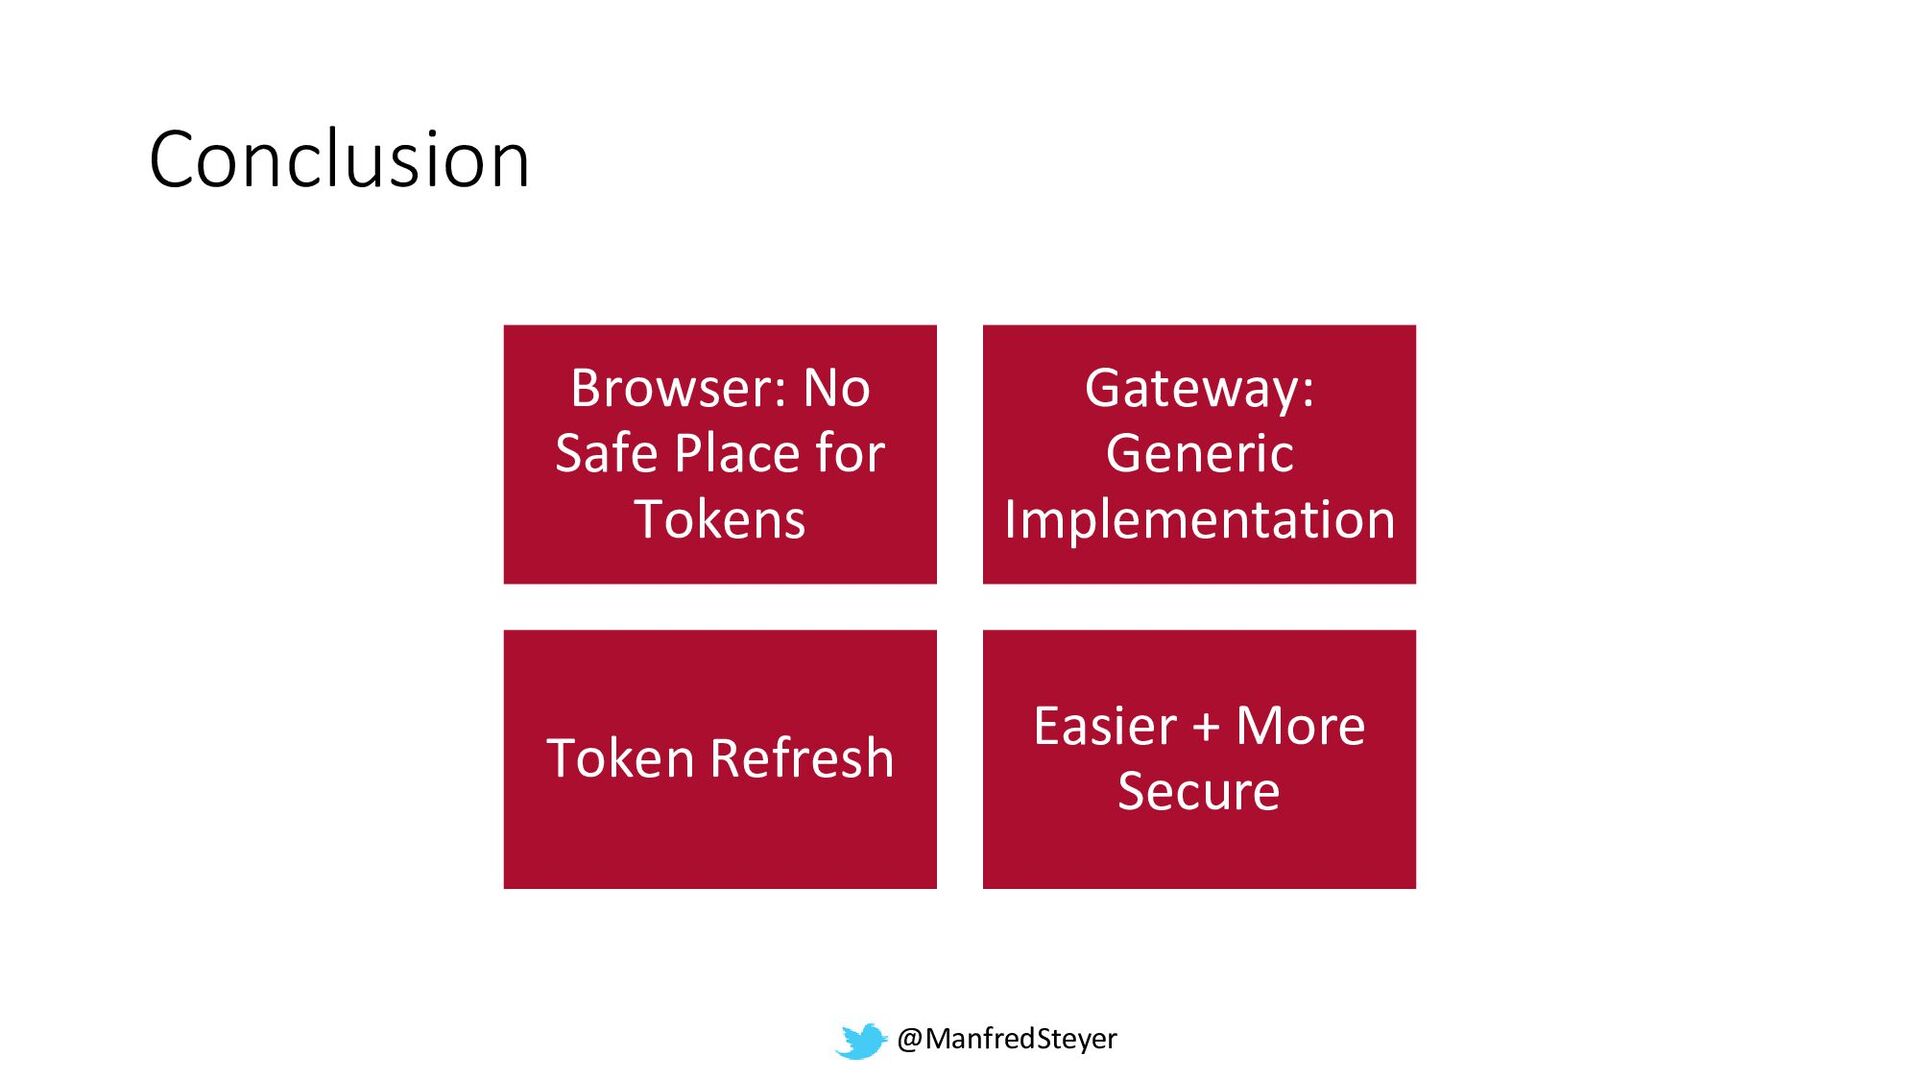
@ManfredSteyer Conclusion Browser: No Safe Place for Tokens Gateway: Generic
Implementation Token Refresh Easier + More Secure
@ManfredSteyer d Slides & Examples Remote and In-House http://softwarearchitekt.at/workshops


 manfredsteyer
 rshindo
 satoshi256kbyte
 kaityo256
 nokomoro3
 lynnswap
 dske104
 chobishiba
 yasaichi
 n_takehata
 yumnumm
 irinanazarova
 moro
 ryanjones
 soysaucechin
 aleyda
 wjessup
 rakko
 akashhashmi
 codingconduct
 marktimemedia
 greggifford
 garrettdimon
 lauravandoore