Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Rethinking Token-based Security: OAuth 2.0 Secu...
Search
Sponsored
·
Ship Features Fearlessly
Turn features on and off without deploys. Used by thousands of Ruby developers.
→
Manfred Steyer
PRO
November 22, 2019
Programming
580
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Rethinking Token-based Security: OAuth 2.0 Security Best Current Practice @jsPoland 2019 Warsaw
Manfred Steyer
PRO
November 22, 2019
More Decks by Manfred Steyer
See All by Manfred Steyer
Human in the Loop Beyond Approval: Toward True Collaboration @FrontMania 2026 in Utrecht
manfredsteyer
PRO
0
57
Agentic UI: Where the Agent meets the User @FrontMania 2026 in Utrecht
manfredsteyer
PRO
0
57
A2UI as an Architecture Question: Agentic UI Between AI Freedom and Control
manfredsteyer
PRO
0
92
AI-Ready Angular Architectures Architecture as Executable Contract
manfredsteyer
PRO
0
250
Nostalgia Meets Technology: Super Mario with TypeScript @BASTA 2026 in Mainz, Germany
manfredsteyer
PRO
0
49
Beyond Chatbots: Agentic UI with Open Standards @AGNTcon 2026 in Amsterdam
manfredsteyer
PRO
0
150
Next-Level Frontends: Agentic Web UIs Under the Hood
manfredsteyer
PRO
0
110
Agentic UI with Open Standards @ngGraz Sep 2026
manfredsteyer
PRO
0
120
Agentic UI with Open Standards @GDG Salzburg, Bgl & Prishtina
manfredsteyer
PRO
0
99
Other Decks in Programming
See All in Programming
複雑なUIコンポーネントとの ⻑い付き合い⽅:波及するバグからテスト戦略を経て、安全な再設計へ
mixplace
0
390
自サークルのIdPからログアウトできるようになるまで
taiseiue
1
140
AIに “答え“を書かせるのを やめてみた
___akari11
0
120
現場と育てるRailsモデリング 〜Spreadsheetから始めたモデル設計〜
siroemk
2
450
Rでドレミ/Do-Re-Mi_with_R
florets1
0
130
全ての永続トークンを、生まれる前に消し去りたい!
sylph01
2
480
When benchmarks go bad - what I learned from measuring performance wrong
hollycummins
0
210
外から家のPCの電源入れたい!をPHPで解決する
kawashimo0
1
130
AI時代のコードレビューは人に向けるな、仕組みに向けろ
texmeijin
5
3.6k
Findy - エンジニア向け会社紹介/Findy Company Deck
findyinc
6
400k
Agentic Software Factoryに、すごく賢いIF文を。 / super smart IF statement into the Agentic Software Factory.
rkaga
8
2.2k
sbt 2.0: takeoff
eed3si9n
0
150
Featured
See All Featured
How to build a perfect <img>
jonoalderson
1
6.1k
Collaborative Software Design: How to facilitate domain modelling decisions
baasie
1
340
Paper Plane (Part 1)
katiecoart
PRO
2
11k
Gemini Prompt Engineering: Practical Techniques for Tangible AI Outcomes
mfonobong
2
590
How to Get Subject Matter Experts Bought In and Actively Contributing to SEO & PR Initiatives.
livdayseo
0
220
Bootstrapping a Software Product
garrettdimon
PRO
306
120k
SERP Conf. Vienna - Web Accessibility: Optimizing for Inclusivity and SEO
sarafernandez
2
1.6k
The Impact of AI in SEO - AI Overviews June 2024 Edition
aleyda
6
1.2k
How to make the Groovebox
asonas
2
2.5k
B2B Lead Gen: Tactics, Traps & Triumph
marketingsoph
1
280
Unsuck your backbone
ammeep
672
58k
The Director’s Chair: Orchestrating AI for Truly Effective Learning
tmiket
1
330
Transcript
Rethinking Token-based Security: OAuth 2.0 Security Best Current Practice Manfred
Steyer SOFTWAREarchitekt.at ManfredSteyer
Contents State of the Art Issues leading to new Best
Practices Proposed Solution Token Refresh HTTP-only Cookies
About me… • Manfred Steyer SOFTWAREarchitekt.at • Angular Trainings and
Consultancy • Google Developer Expert (GDE) • Trusted Collaborator in the Angular Team Page ▪ 3 Manfred Steyer Public: Frankfurt, Munich, Vienna In-House: everywhere http://softwarearchitekt.at/workshops
State of the Art
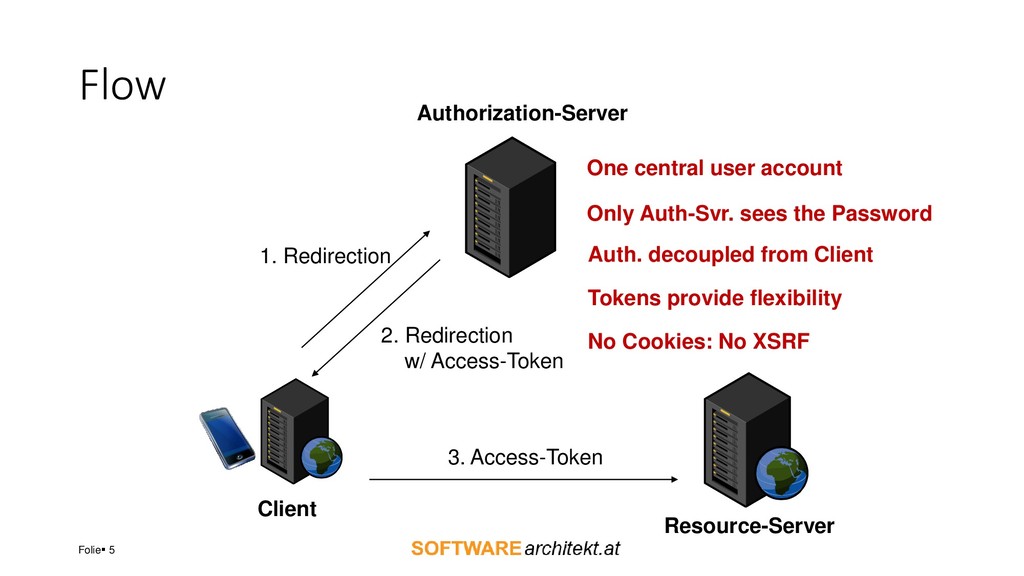
Flow Folie▪ 5 Client Authorization-Server Resource-Server 1. Redirection 2. Redirection
w/ Access-Token 3. Access-Token One central user account Only Auth-Svr. sees the Password Auth. decoupled from Client Tokens provide flexibility No Cookies: No XSRF
Most Popular Solution: OAuth 2 and OpenId Connect
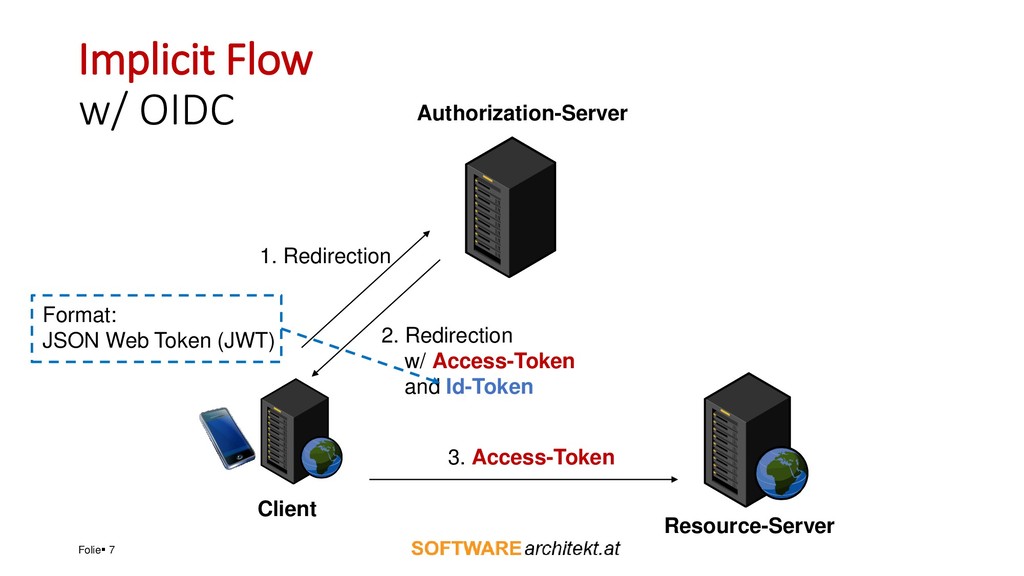
Implicit Flow w/ OIDC Folie▪ 7 Client Authorization-Server Resource-Server 1.
Redirection 2. Redirection w/ Access-Token and Id-Token 3. Access-Token Format: JSON Web Token (JWT)
Issues
None
Current Best Practices Document advices against Implicit Flow
There are possible attacks! However, this is not new for
us!
None
Have we been that naive in the last 6+ years?
No!
All serious implementations used Implicit Flow together with Best Practices
to prevent those attacks!
OpenId Connect enforces such Best Practices!
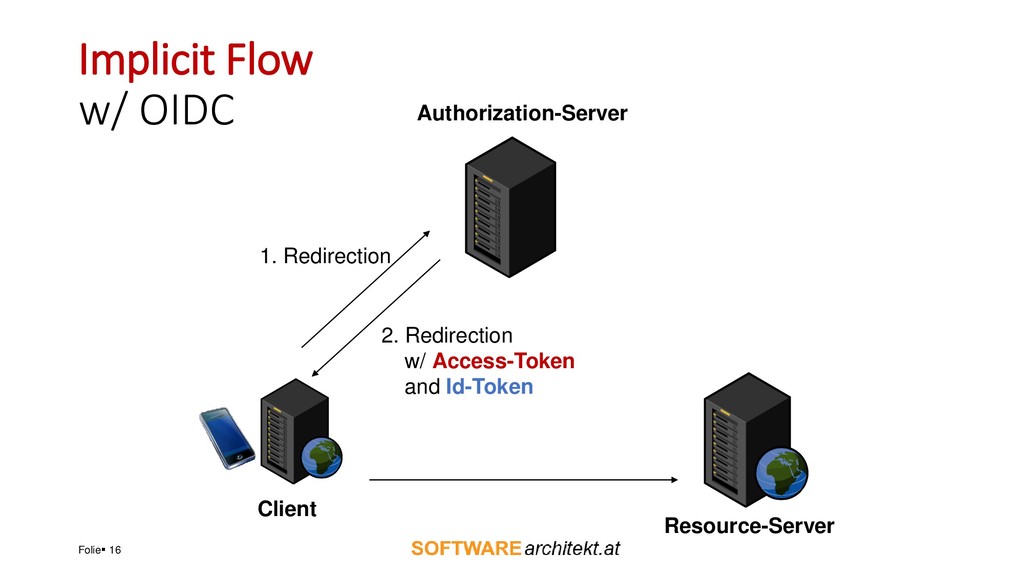
Implicit Flow w/ OIDC Folie▪ 16 Client Authorization-Server Resource-Server 1.
Redirection 2. Redirection w/ Access-Token and Id-Token
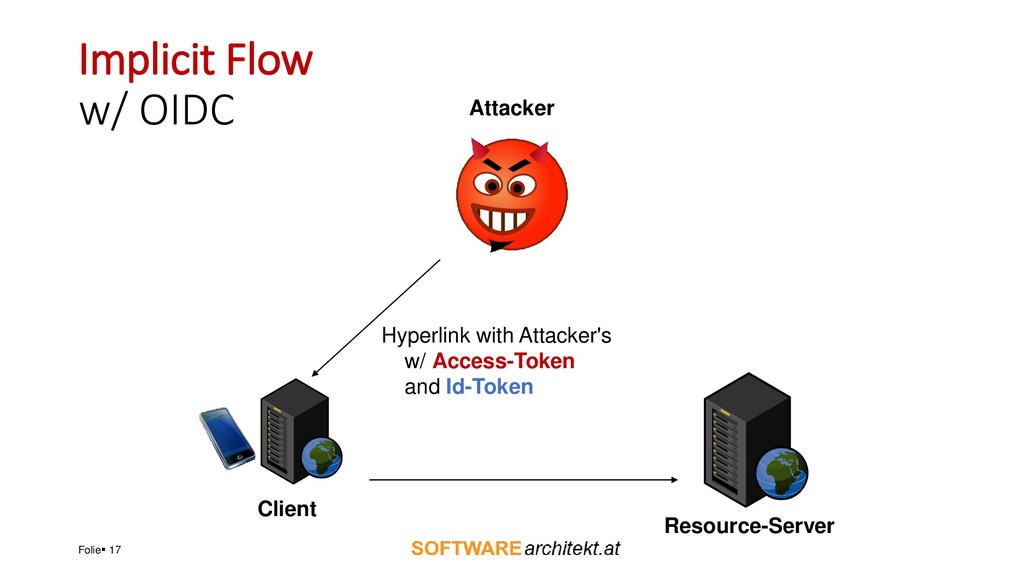
Implicit Flow w/ OIDC Folie▪ 17 Client Attacker Resource-Server Hyperlink
with Attacker's w/ Access-Token and Id-Token
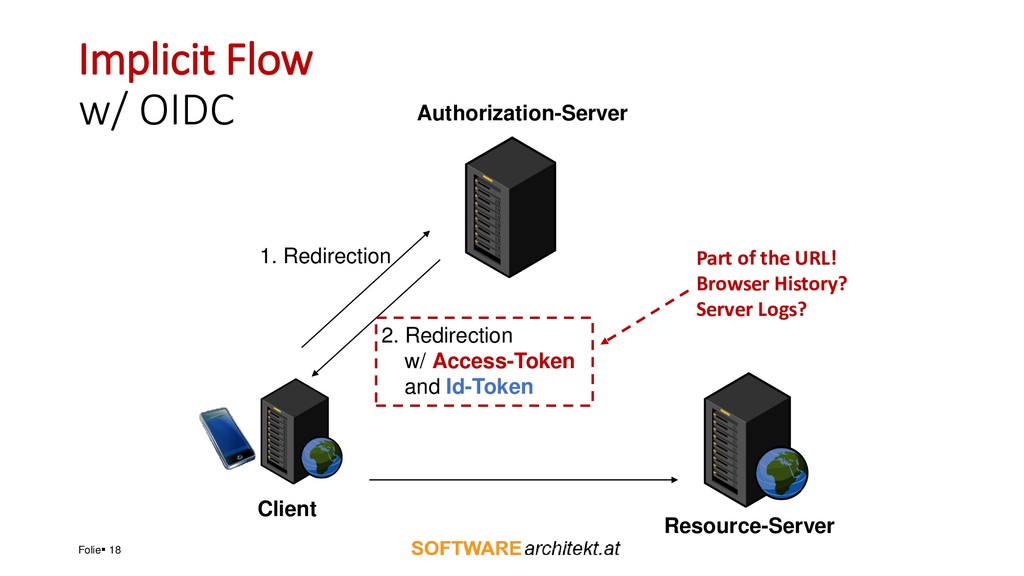
Implicit Flow w/ OIDC Folie▪ 18 Client Authorization-Server Resource-Server 1.
Redirection 2. Redirection w/ Access-Token and Id-Token Part of the URL! Browser History? Server Logs?
Proposed Solution
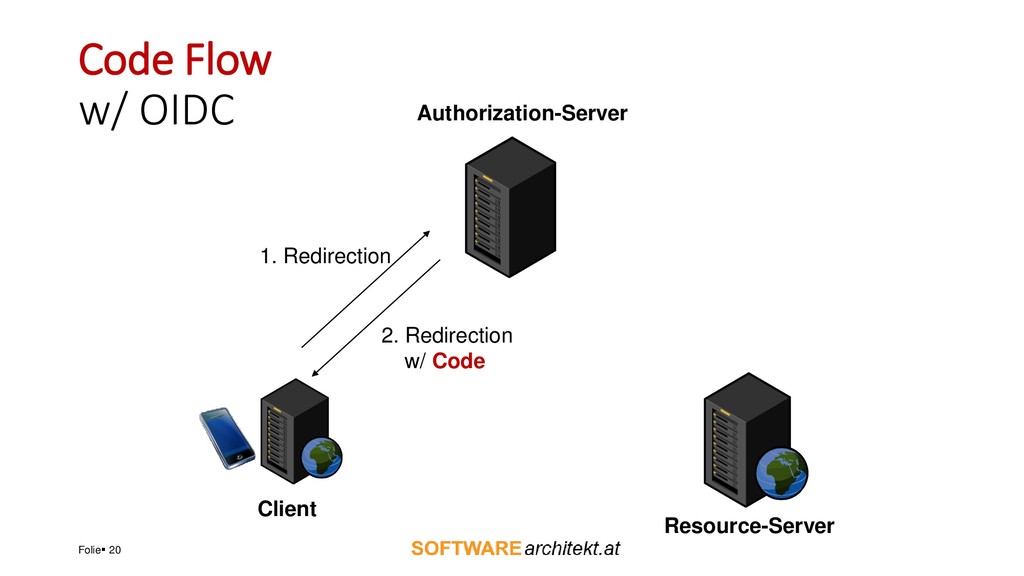
Code Flow w/ OIDC Folie▪ 20 Client Authorization-Server Resource-Server 1.
Redirection 2. Redirection w/ Code
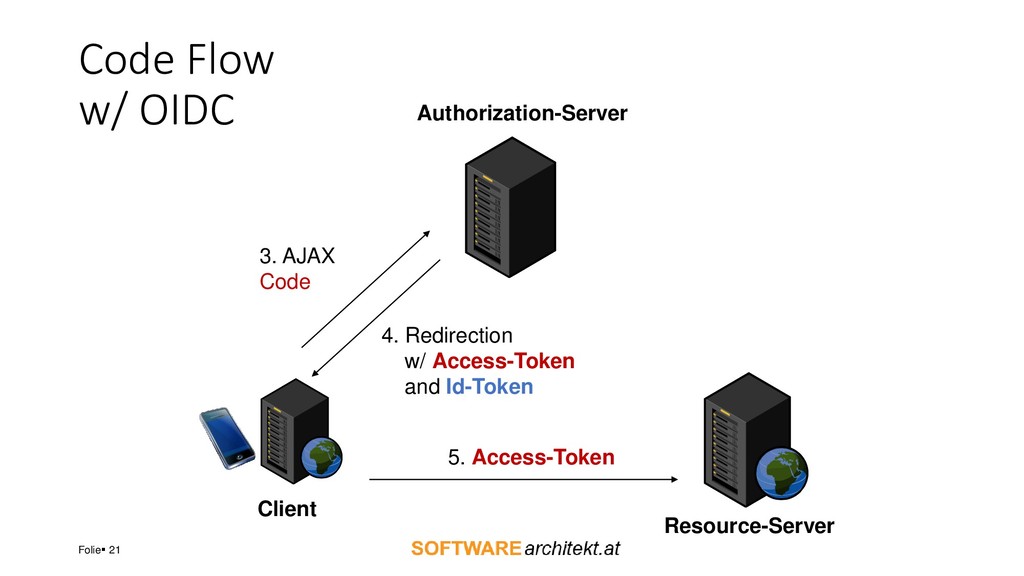
Code Flow w/ OIDC Folie▪ 21 Client Authorization-Server Resource-Server 3.
AJAX Code 4. Redirection w/ Access-Token and Id-Token 5. Access-Token
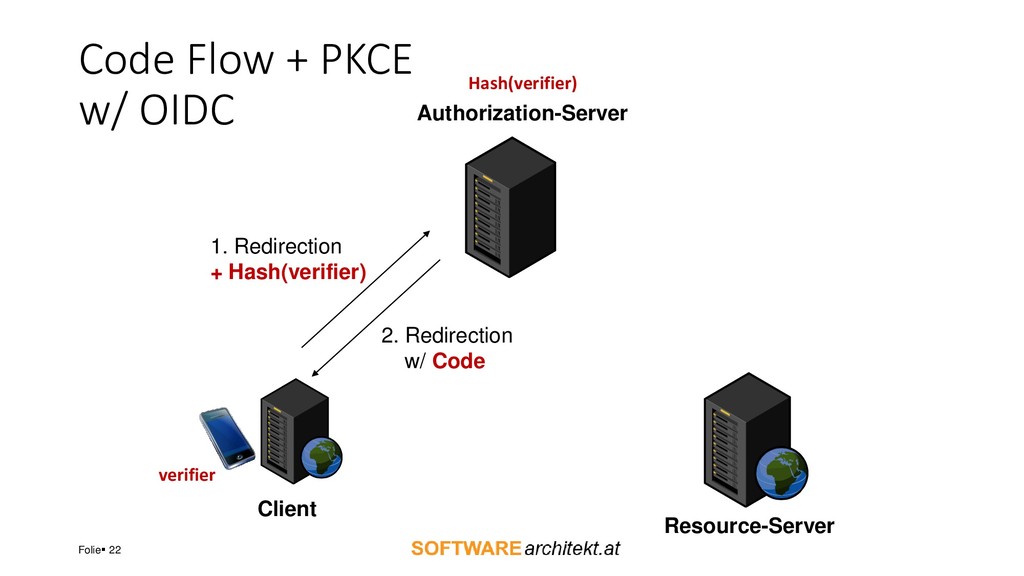
Code Flow + PKCE w/ OIDC Folie▪ 22 Client Authorization-Server
Resource-Server 1. Redirection + Hash(verifier) 2. Redirection w/ Code Hash(verifier) verifier
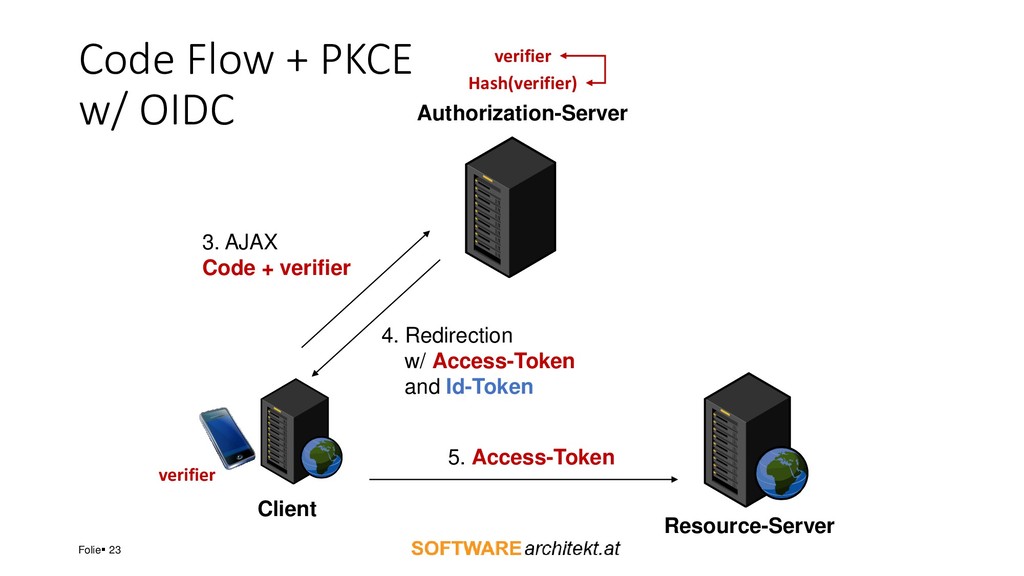
Code Flow + PKCE w/ OIDC Folie▪ 23 Client Authorization-Server
Resource-Server 3. AJAX Code + verifier 4. Redirection w/ Access-Token and Id-Token 5. Access-Token Hash(verifier) verifier verifier
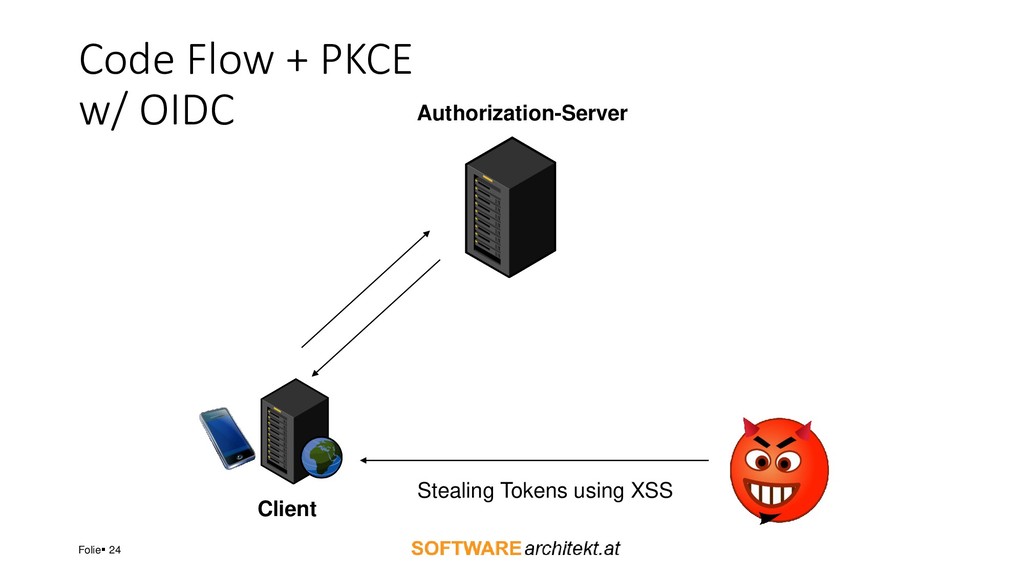
Code Flow + PKCE w/ OIDC Folie▪ 24 Client Authorization-Server
Stealing Tokens using XSS
Solutions Prevent XSS by using frameworks Look into CSP (Content
Security Policy) Short-living Tokens (~ 10 min)
Token Refresh Page ▪ 26
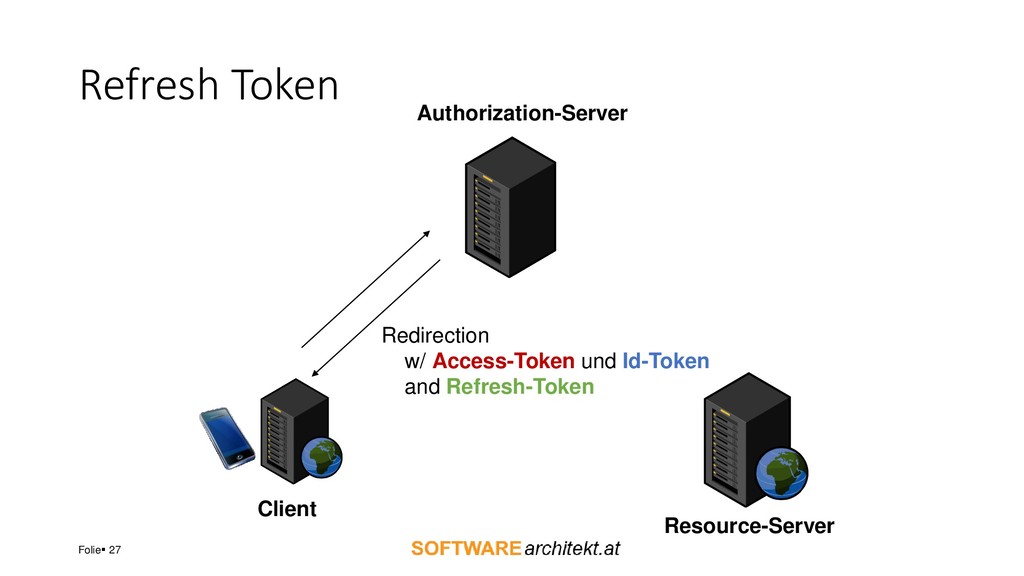
Refresh Token Folie▪ 27 Client Authorization-Server Resource-Server Redirection w/ Access-Token
und Id-Token and Refresh-Token
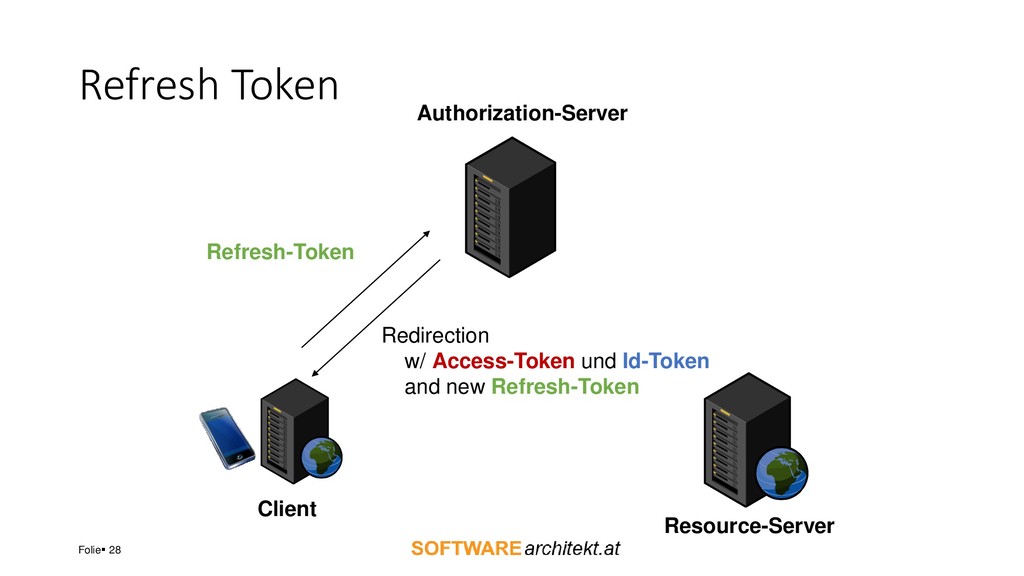
Refresh Token Folie▪ 28 Client Authorization-Server Resource-Server Refresh-Token Redirection w/
Access-Token und Id-Token and new Refresh-Token
Officially, Refresh Tokens are forbidden in the browser as they
can be stolen too (XSS).
Allowed by the Best Practices Document if … • Know
threats and take care of them (XSS!) • Refresh-Token is an one time token! • Log out users if used more than once!
None
Alternative: HTTP-Only Cookies
The savest way to store tokens in the browser are
HTTP Only Cookies!
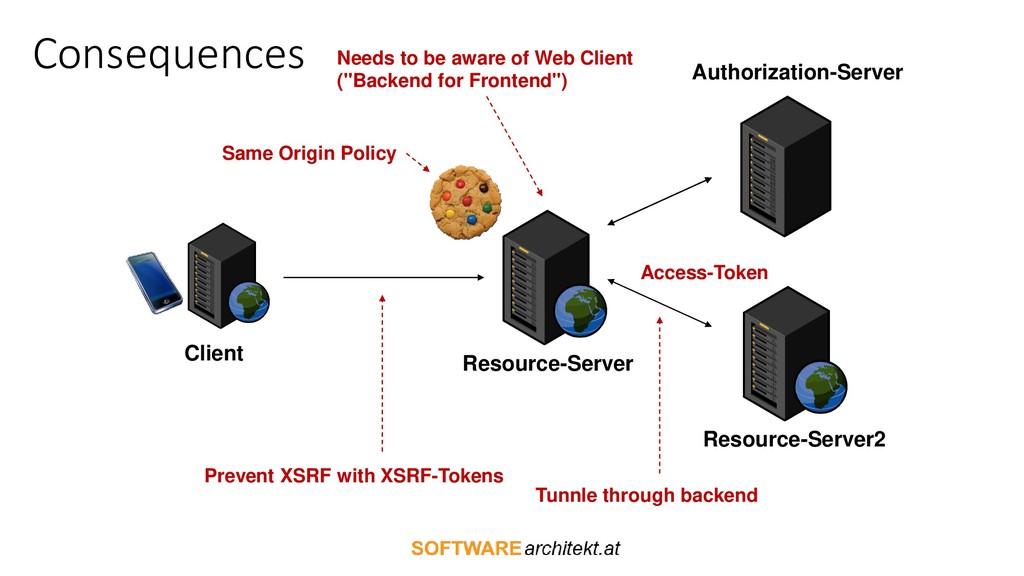
Client Resource-Server Authorization-Server Resource-Server2 Access-Token Tunnle through backend Prevent XSRF
with XSRF-Tokens Needs to be aware of Web Client ("Backend for Frontend") Consequences Same Origin Policy
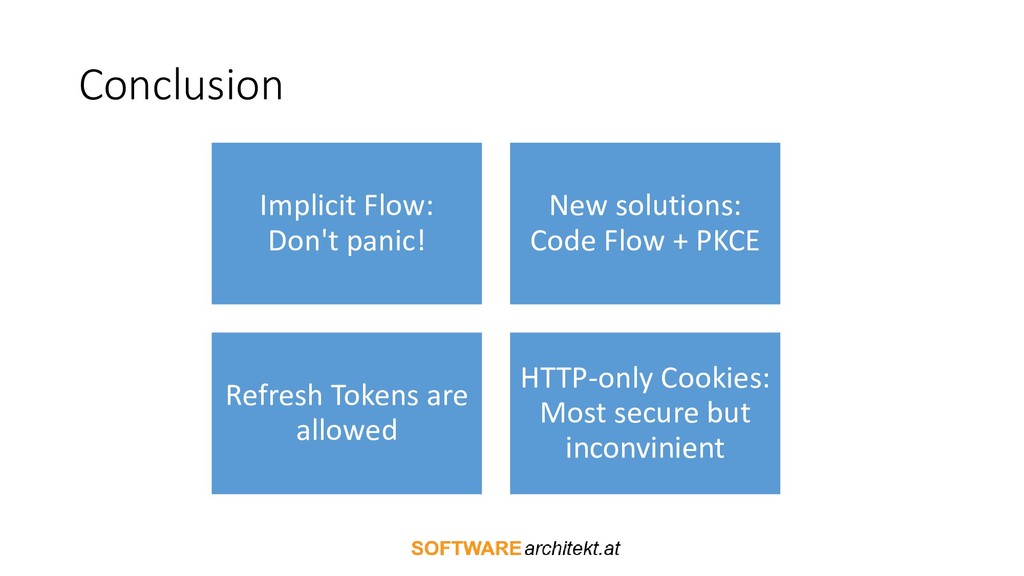
Conclusion Implicit Flow: Don't panic! New solutions: Code Flow +
PKCE Refresh Tokens are allowed HTTP-only Cookies: Most secure but inconvinient
Contact and Downloads [mail]
[email protected]
[web] SOFTWAREarchitekt.at [twitter] ManfredSteyer d
Slides & Examples Public: Frankfurt, Munich, Vienna In-House: everywhere http://softwarearchitekt.at/workshops


 manfredsteyer
 mixplace
 taiseiue
 ___akari11
 siroemk
 florets1
 sylph01
 hollycummins
 kawashimo0
 texmeijin
 findyinc
 rkaga
 eed3si9n
 jonoalderson
 baasie
 katiecoart
 mfonobong
 livdayseo
 garrettdimon
 sarafernandez
 aleyda
 asonas
 marketingsoph
 ammeep
 tmiket