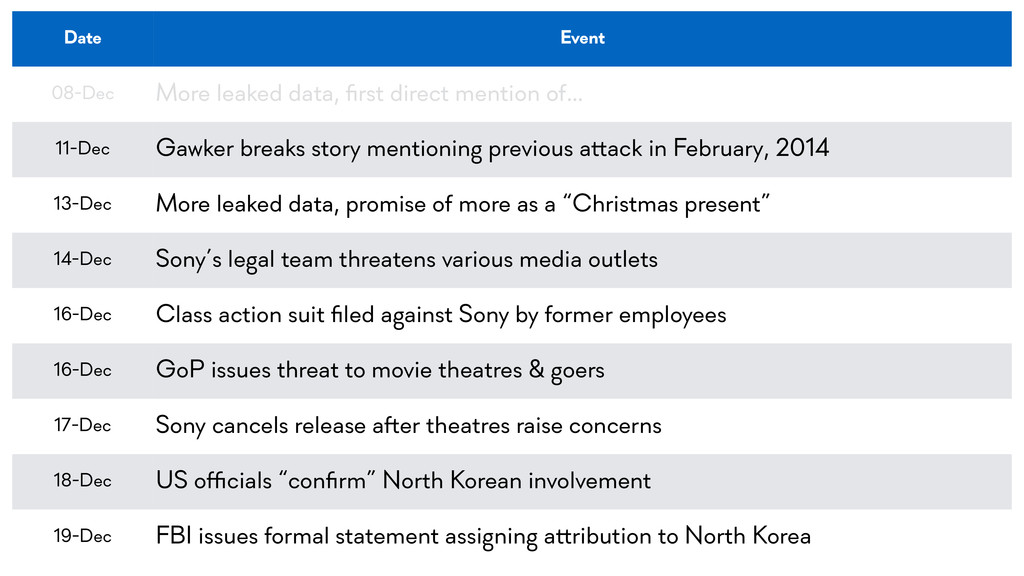
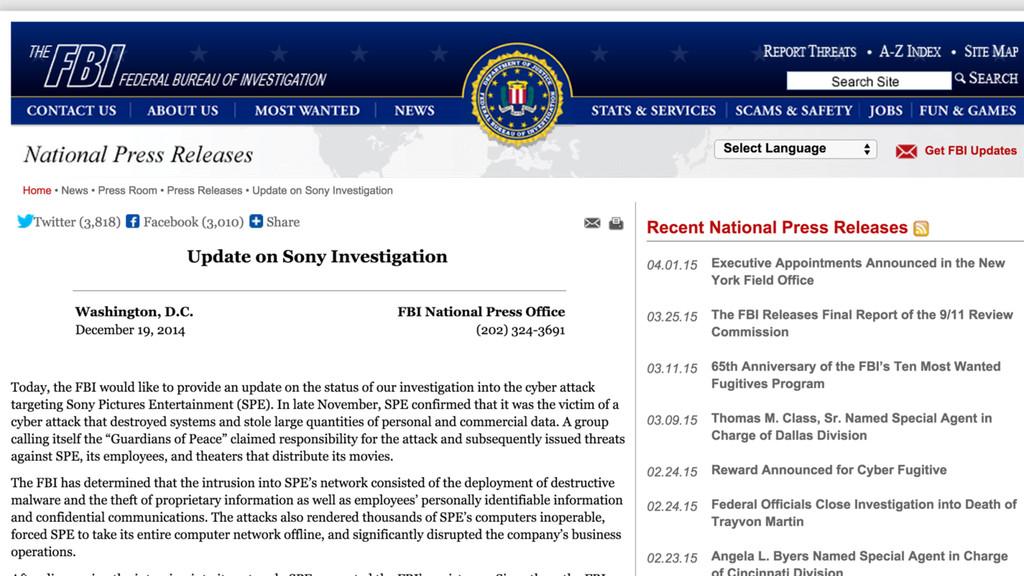
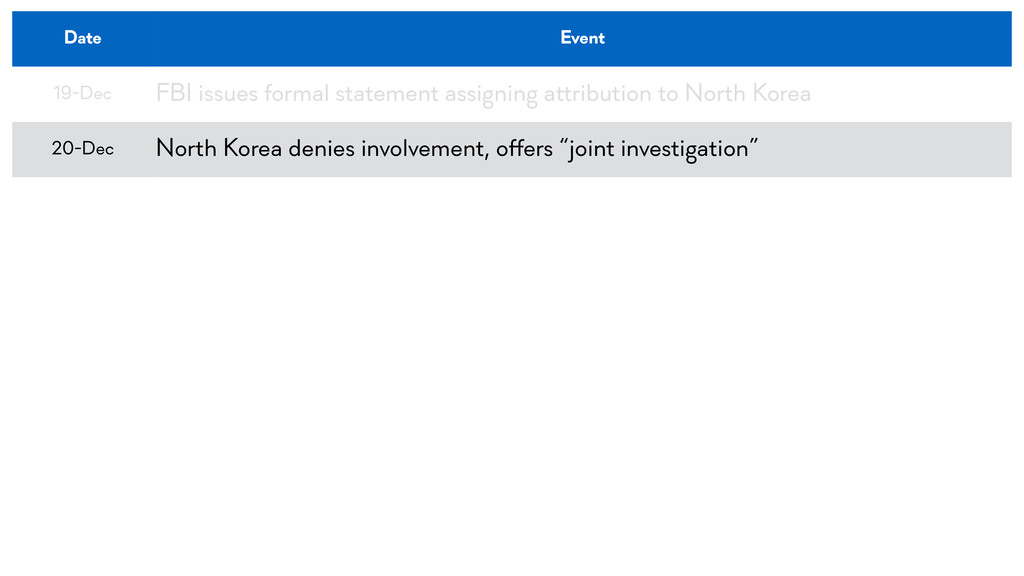
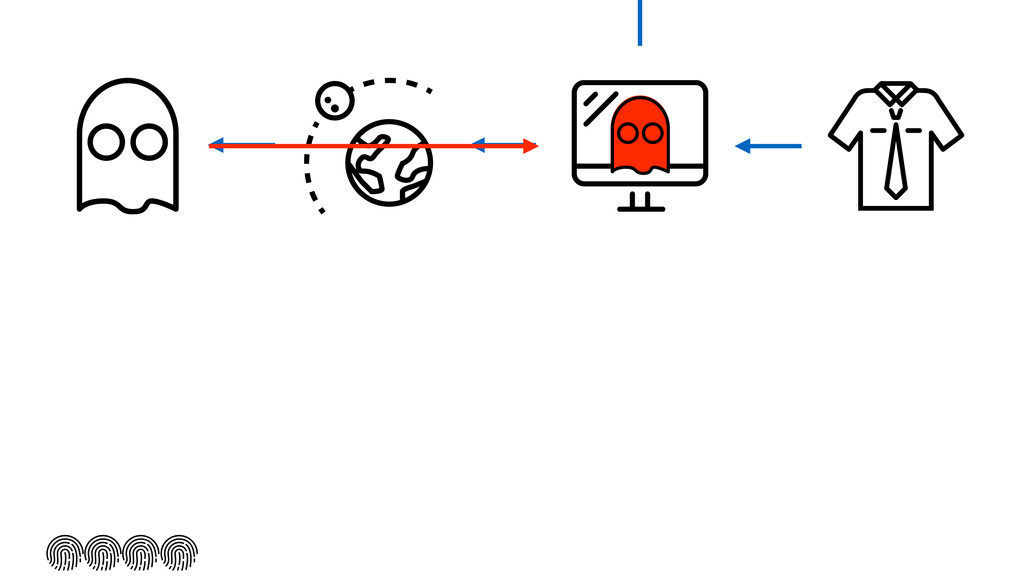
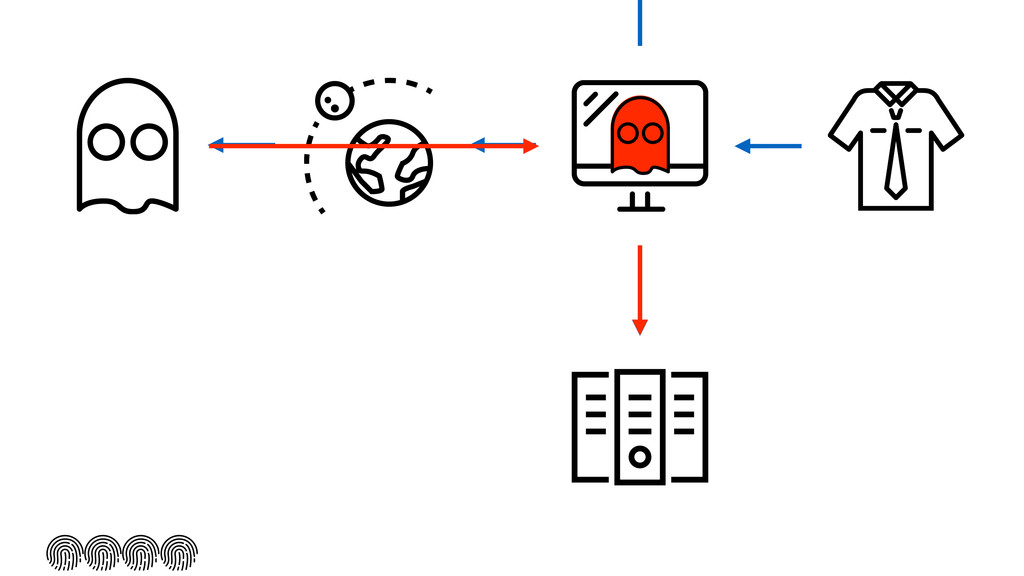
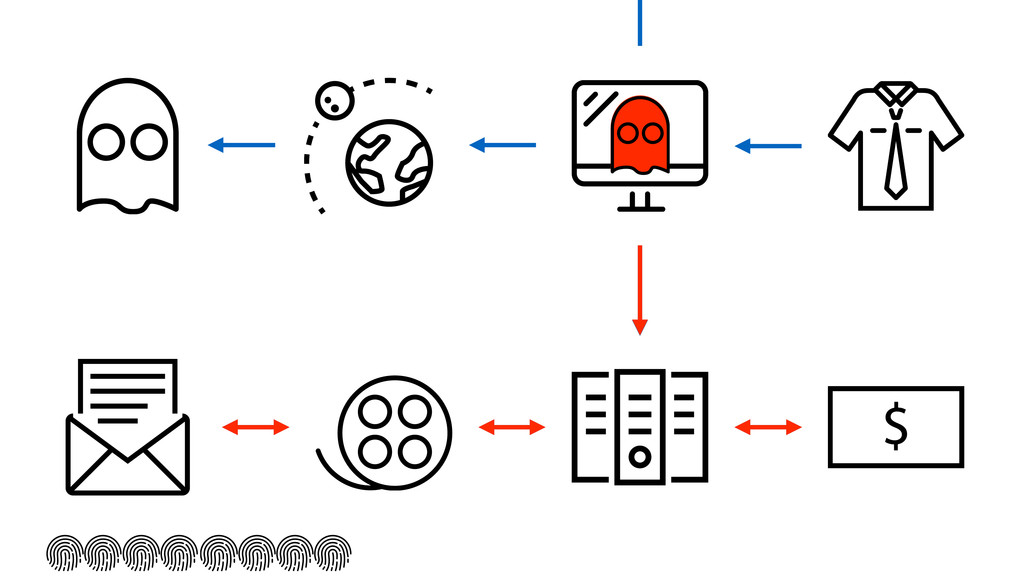
When it hits the fan, one of the first questions that you get asked is "Who did this?".
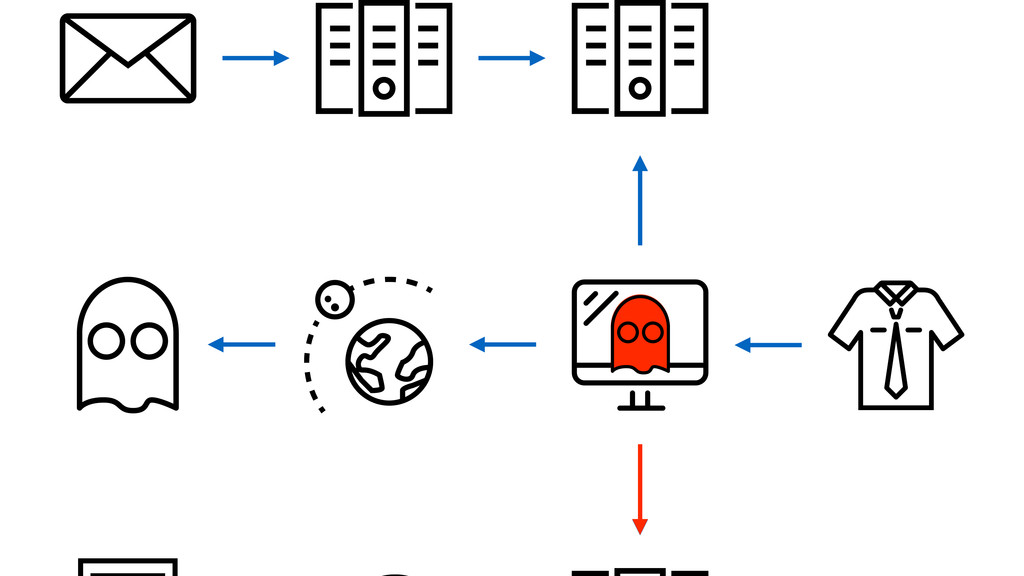
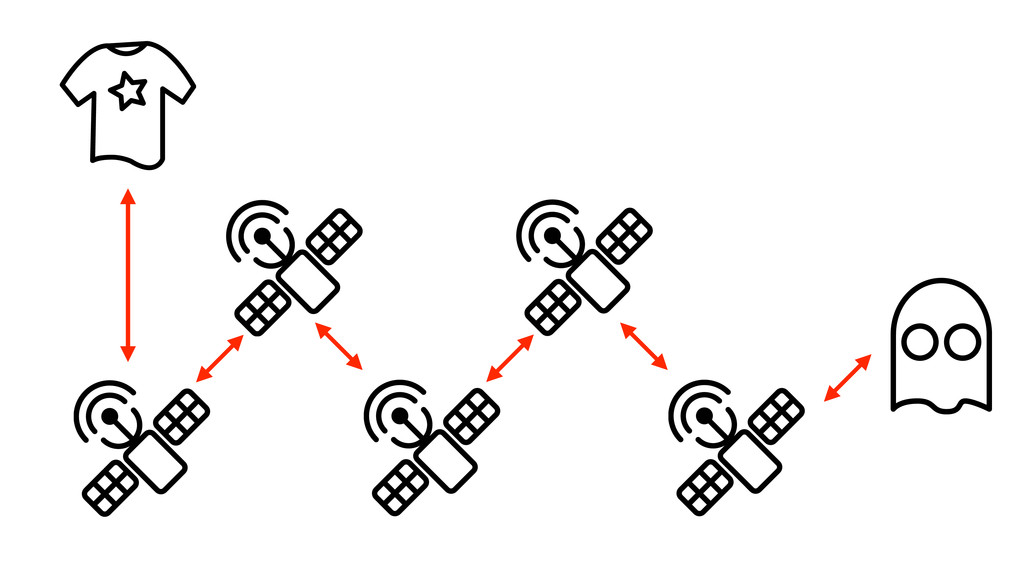
And like any good mystery, trying to find the attacker takes many twists and turns. There's a trail of evidence, a red herring or two, and the inevitable plot twist before the final reveal.
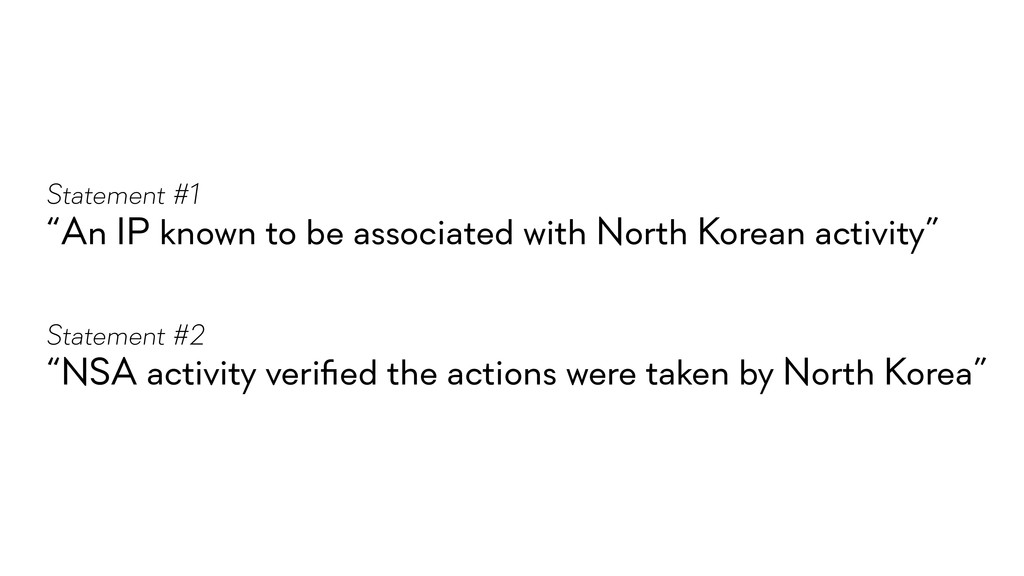
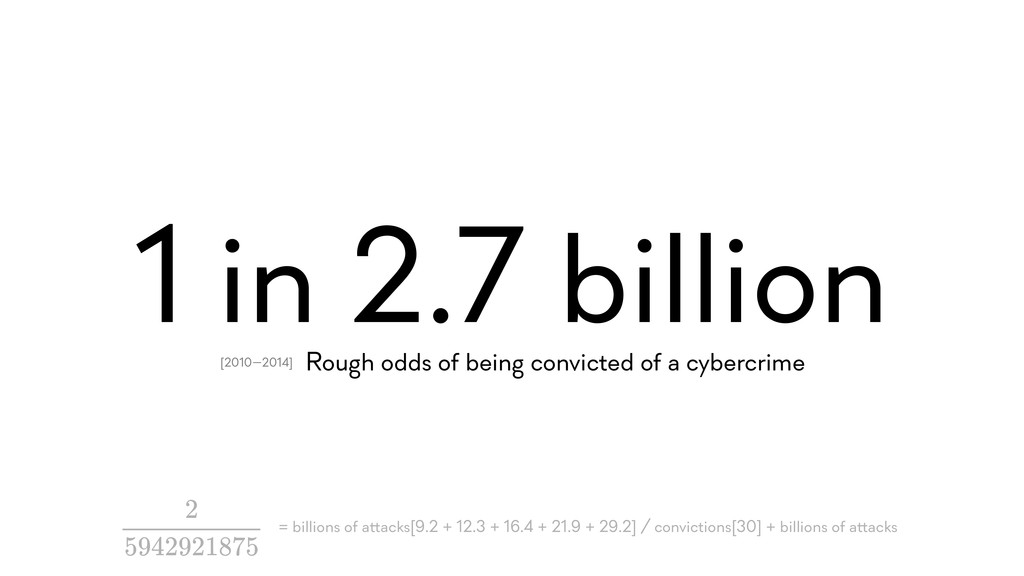
Unfortunately, despite what you see on TV, in the movies, or even in the press, attack attribution is hard. In face, it's one of the hardest problems in information security today.
In this talk, we use real world examples to work through what it takes to properly make the connection between attack and attacker.
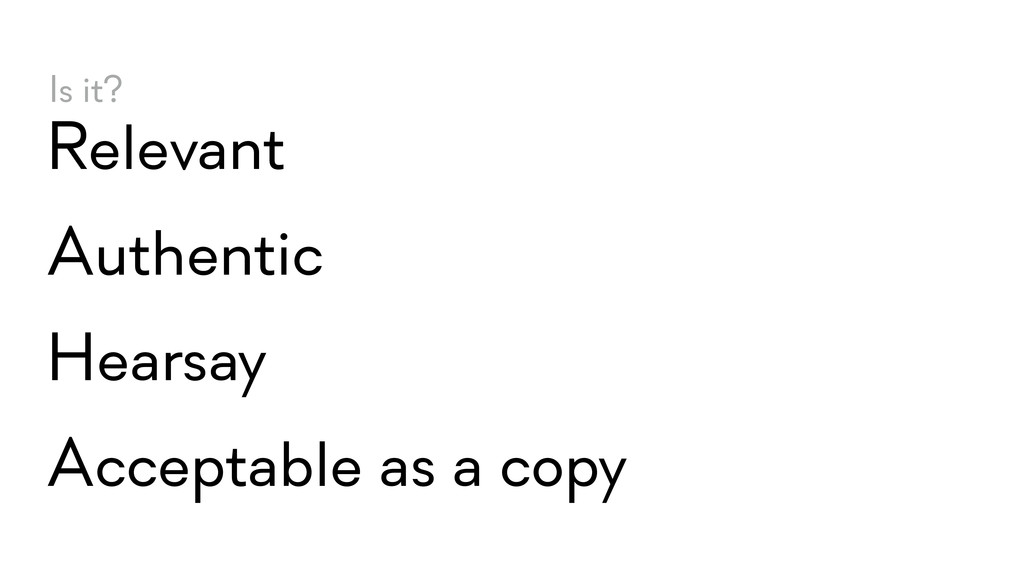
Looking at real world techniques used to gather and validate evidence, we'll examine what it takes for that evidence to hold up to cross examination. We'll look at the role each of your security controls play in the attribution process and the steps you can take to immediately make attribution easier.
Come learn what it takes to actually prove who the attacker is and where attribution fits into your daily security practice.


 terapyon
 ludicmind
 recruitengineers
 shogo4131
 kworkdev
 riyaamemiya
 kash1064
 glaforge
 teamlab
 kairim0
 kentarofujii
 bgpat
 akademiya2063
 szymonslowik
 chriscoyier
 kneath
 katarinadahlin
 greggifford
 cassininazir
 erikaheidi
 hatefulcrawdad
 marktimemedia
 pwiseman
 samtorres