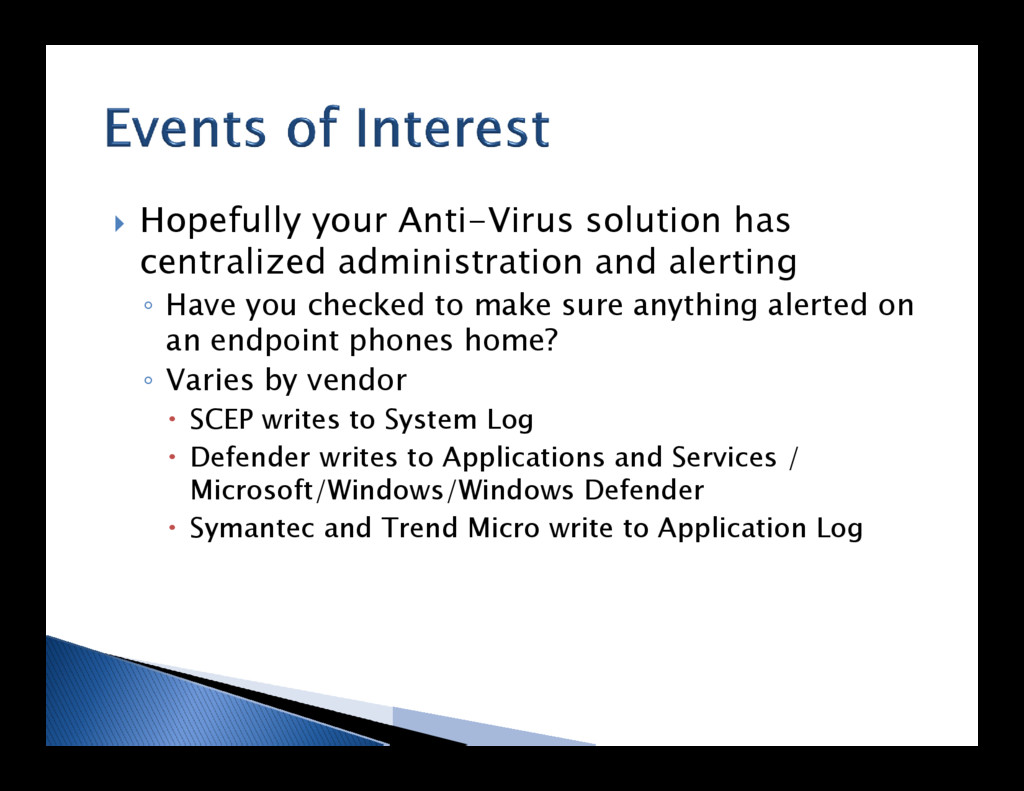
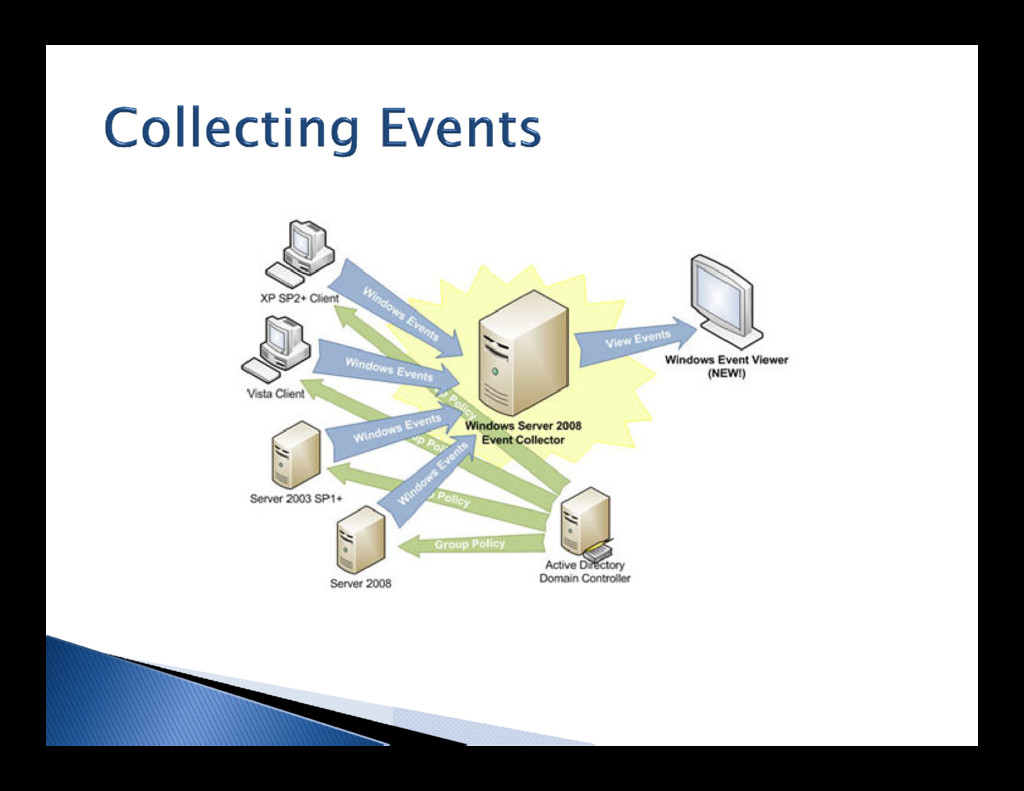
Have you checked to make sure anything alerted on an endpoint phones home? ◦ Varies by vendor SCEP writes to System Log Defender writes to Applications and Services / Microsoft/Windows/Windows Defender Symantec and Trend Micro write to Application Log
enable 4688 – Process created 4689 – Process terminated ◦ Microsoft is slowly adding more details to the captured data Server 2012R2 added command line info Server 2016 Preview includes SHA1/2 hashes
of SysInternals suite Writes to Applications and Services Logs/Microsoft/Windows/Sysmon/Operational Process name, ID, parent process, command line, etc. Also terminations, TCP/UDP connections, file modification times, raw disk access Event IDs 1-9 depending on configuration Change default log size!
on .NET 4.5 and WMF 5.0 Can generate 1MB/min during activity (legit or otherwise) Expand default log size if you want any value ◦ Records blocks of code passing through Powershell -EncodedCommand de-obfuscation Invoke-Mimikatz, anyone?
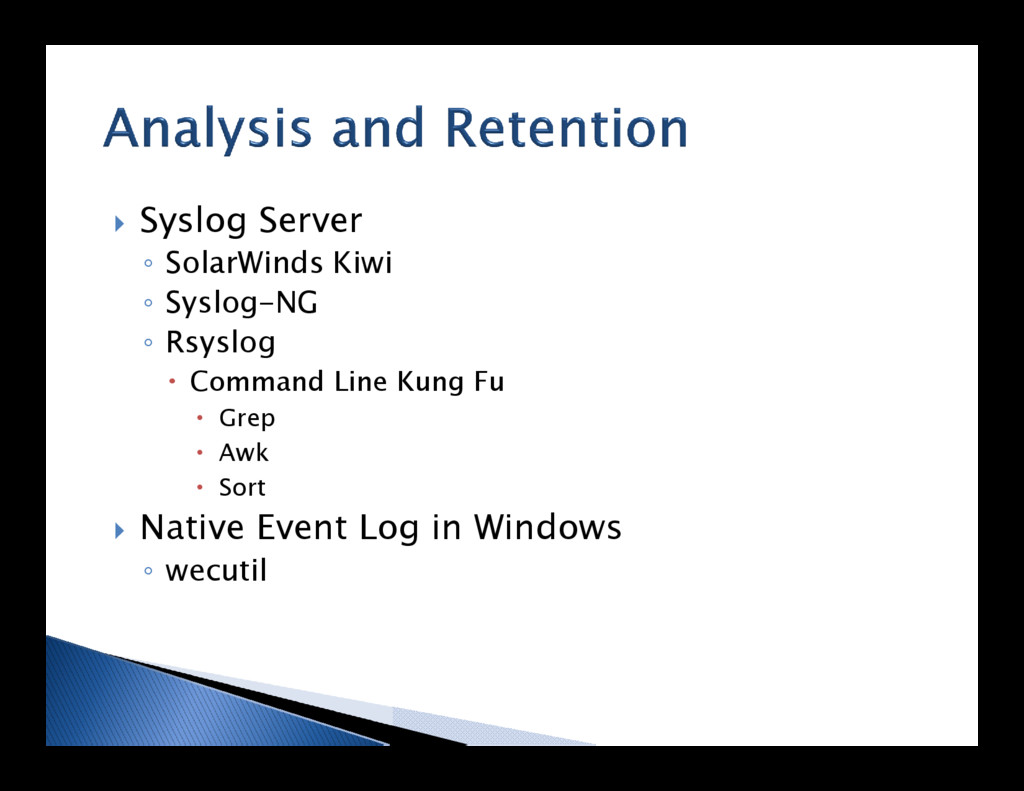
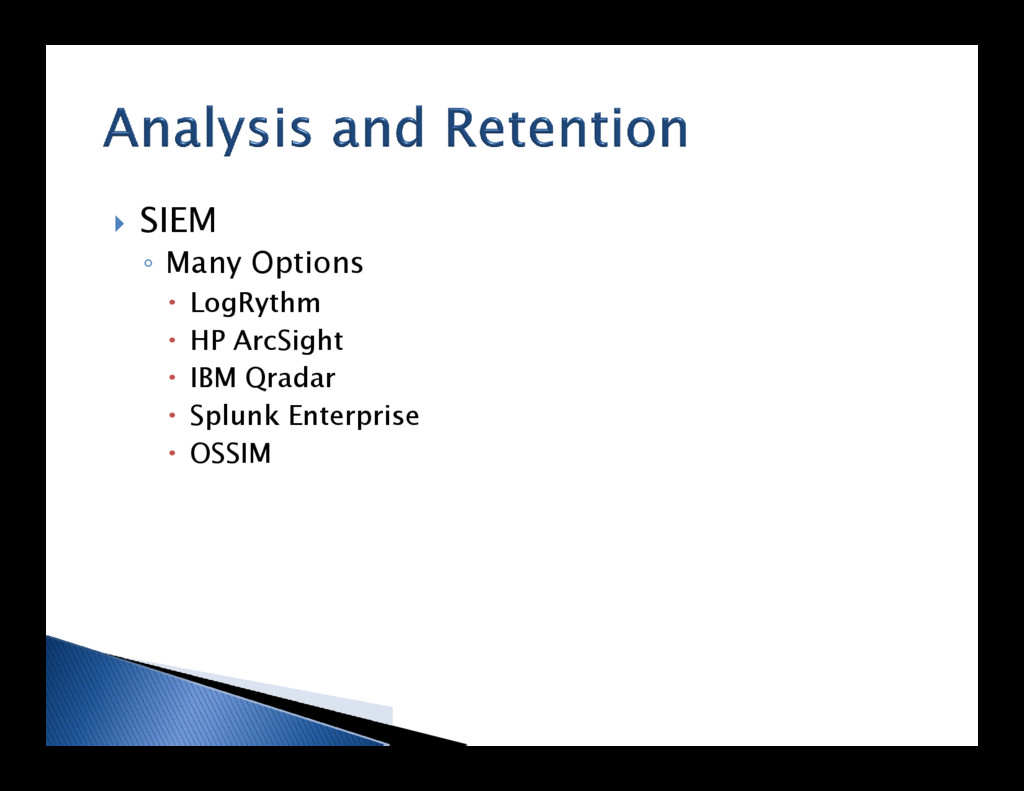
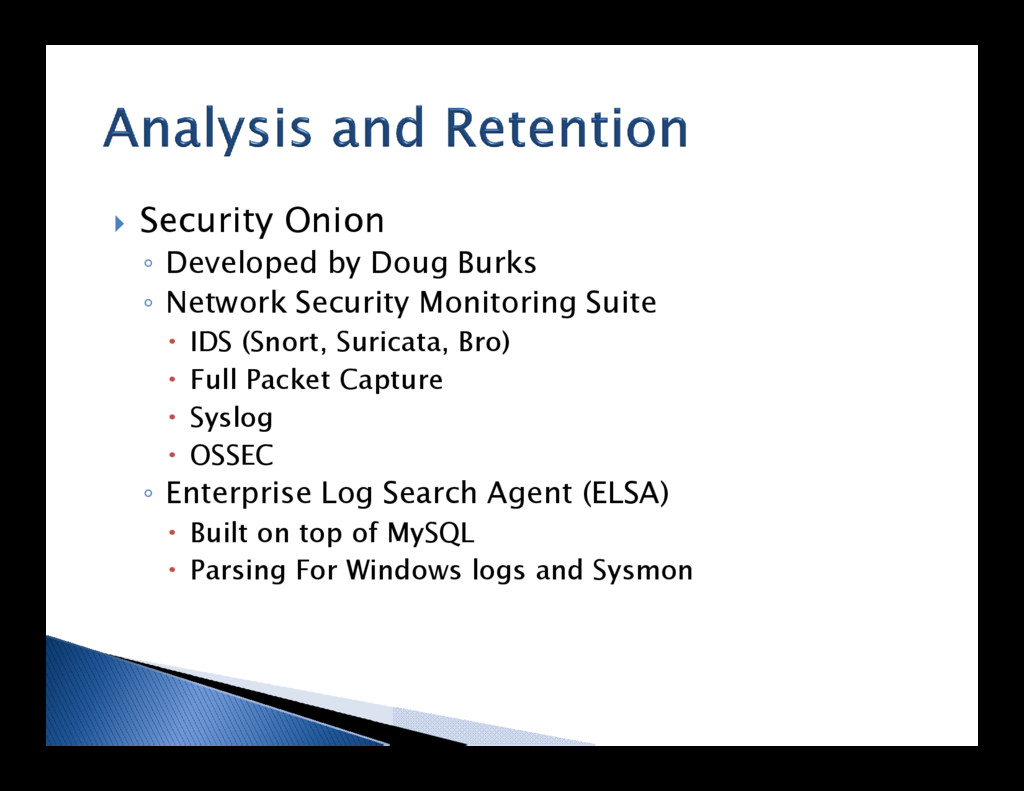
Monitoring Suite IDS (Snort, Suricata, Bro) Full Packet Capture Syslog OSSEC ◦ Enterprise Log Search Agent (ELSA) Built on top of MySQL Parsing For Windows logs and Sysmon


 nd_issa
 hiracky16
 jozono
 pfn
 terurou
 gionn
 sudoakiy
 maimyyym
 techtekt
 masakiokuda
 jtakeda
 recruitengineers
 glaforge
 gurzu
 palkan
 dougneiner
 marketingsoph
 chrislema
 konakalab
 keithpitt
 eileencodes
 mza
 hatefulcrawdad
 maltzj
 baasie