Share
Embed
Transcript
36 slides
-
the best way to build and ship software Me 2
! • Github Security Engineer • Twitter: @ndm • Github: @oreoshake -
the best way to build and ship software The story
of a line of code 4 ! • Before the code is written • While the code is being written • After the code has been written • After the code has shipped -
the best way to build and ship software Before the
code is written 5 ! • Framework / Architecture Security • Secure by default • Education • Culture -
the best way to build and ship software Framework /
Architecture security 6 ! • Provide the necessary controls • Don’t provide anything else • Disable unused framework features • Deprecate and remove/replace unsafe API -
the best way to build and ship software Secure by
default 7 An extension of “opting out” of security ! • Apply security headers by default • The framework is configured in the most restrictive way possible -
the best way to build and ship software Education (nho)
8 ! • Separate code and data • Understand the context boundaries • Learn how to safely cross contexts • If you do, we’ll leave you alone -
the best way to build and ship software Culture 9
! • Don’t be a jerk • Security is not a blocker, it’s a passive guide • Secure code is correct code • Understand your code will be scrutinized -
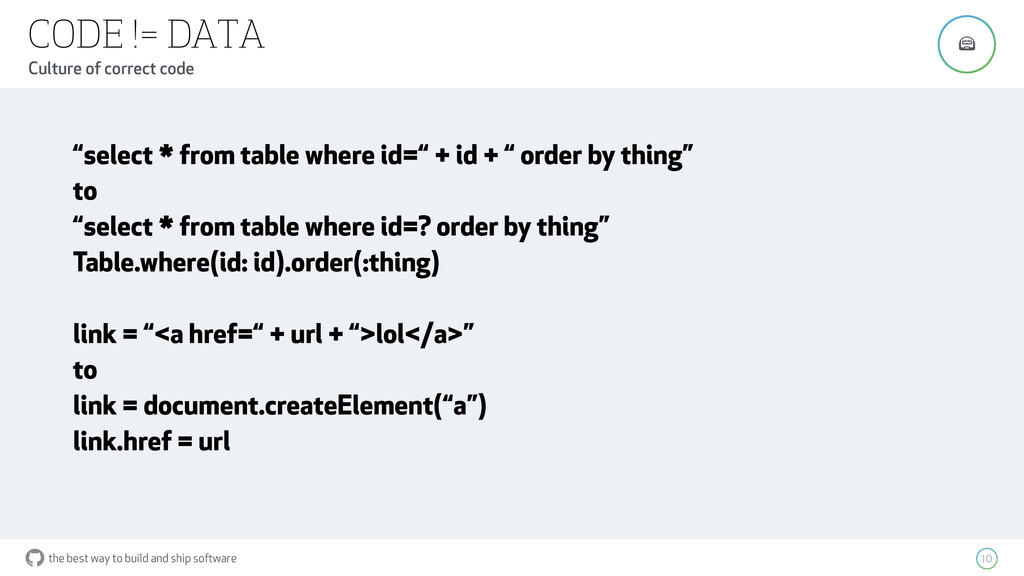
the best way to build and ship software CODE !=
DATA 10 Culture of correct code ! “select * from table where id=“ + id + “ order by thing” to “select * from table where id=? order by thing” Table.where(id: id).order(:thing) link = “<a href=“ + url + “>lol</a>” to link = document.createElement(“a”) link.href = url -
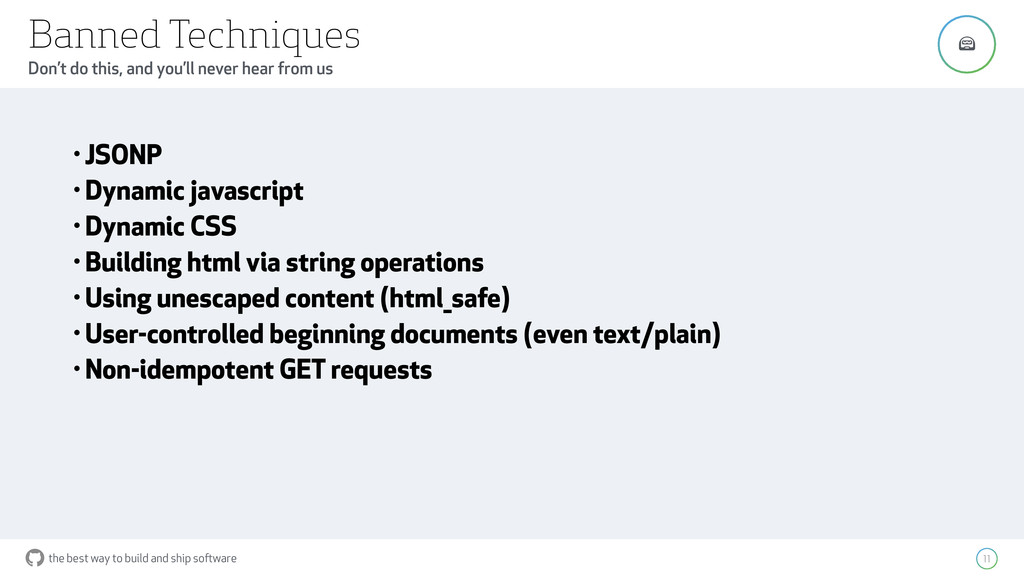
the best way to build and ship software Banned Techniques
11 Don’t do this, and you’ll never hear from us ! • JSONP • Dynamic javascript • Dynamic CSS • Building html via string operations • Using unescaped content (html_safe) • User-controlled beginning documents (even text/plain) • Non-idempotent GET requests -
the best way to build and ship software Tests are
your friend 12 ! • Encourage “negative” test cases -
the best way to build and ship software While the
code is being written 13 ! • provide what is needed • tooling • libraries • process integration -
the best way to build and ship software secure_headers 15
! • It’s just a (set of) header(s) • Ported to Node*, Go, .Net, Java, PHP, Python, dancer, drupal, etc. • Think of the benefits of the headers as config values, rather than the textual value -
the best way to build and ship software Provide what
is needed: CSP 16 ! • Nonce / Hash support -
the best way to build and ship software It’s a
bug, not a feature 17 ! • XSS? • Mixed content? • Site defacement? • All solved* by csp -
the best way to build and ship software Nonce 18
! • Generate a random value per request • Populate a “nonce” attribute for any script tag you want to be whitelisted -
the best way to build and ship software Railsgoat +
nonce 19 ! • Pull request to add nonce support[1] • 46 files changed, 72 additions, -46 deletions • global find and replace took care of 90% of the job [1] https://github.com/OWASP/railsgoat/pull/174 -
the best way to build and ship software Hashes 20
! • Find and compute hash values for <script> tags • Associate each hash with the file it lives in • Every time a file is rendered, include the corresponding hashes in the header • Requires less changes than the nonce approach -
the best way to build and ship software Railsgoat +
hash 21 ! • Pull request[1] to add hashes when possible, nonces when not • 12 files change, 33 additions, 13 deletions (> 50% reduction in changes over nonce) • Hardest part was dealing with dynamic js (which requires the use of nonce) [1] https://github.com/oreoshake/railsgoat/pull/1 -
the best way to build and ship software IRL 22
! • Coming to a twitter near you… • Only 5 inline scripts -
the best way to build and ship software After the
code has been written 23 ! • Go all out • Stay out of the way -
the best way to build and ship software Scan on
arrival 24 ! • Every time new code is pushed, run tools and diff the results from master -
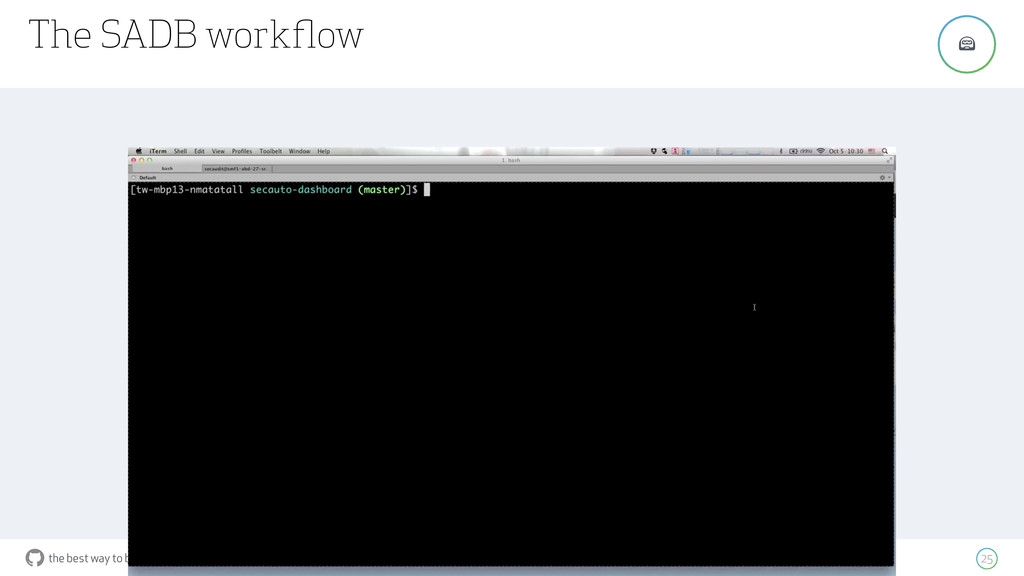
the best way to build and ship software The SADB
workflow 25 ! -
the best way to build and ship software Laundry list
of tools 26 ! • Static analysis • Brakeman • scan js • Dependency Management • bundler-audit • retire js • owasp dependency check • Other • Charlie Miller’s fuzzer thing -
the best way to build and ship software Review upon
review 27 ! • Code review is a great integration point -
the best way to build and ship software Again, it’s
just a regex 28 ! • When your threat model is tiny, the tools required to support it are pretty simple -
the best way to build and ship software Notify the
relavent authorities 29 ! • OWNERS -
the best way to build and ship software Did we
catch it all? 30 ! • Probably not -
the best way to build and ship software After the
code has been shipped 31 ! • It’s out of our hands, right? -
the best way to build and ship software Decider 32
! • All features, and any new code is often behind a Feature Flag • Graudual rollouts • “dark shipping” • Beta/targeted testing • “oh shit” button -
the best way to build and ship software Bug Bounty
33 ! • Penetration testing on the cheap -
the best way to build and ship software Stats 34
! • They aren’t just for proving a feature was a success -
the best way to build and ship software You can
do it 35 ! • These tools and integrations came out of a direct need. • “The best indicator of the next bug is the last bug” • Look at your previous bugs, and focus there -
the best way to build and ship software Time to
Chill 36 ! • Your threat model is small • Code is always under scrutiny • People know what the “right thing” is • You have sensors to detect issues at all phases of the pipeline • You have social and technical controls in place