Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
How CSP Will (maybe) Solve the XSS Problem
Search
Sponsored
·
Your Podcast. Everywhere. Effortlessly.
Share. Educate. Inspire. Entertain. You do you. We'll handle the rest.
→
Neil Matatall
September 12, 2014
Programming
180
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
How CSP Will (maybe) Solve the XSS Problem
More ramblings about how awesome csp and how it solves all of your problems.
Neil Matatall
September 12, 2014
More Decks by Neil Matatall
See All by Neil Matatall
Twubhubbook - It's like appsec, but for startups (with notes)
oreoshake
0
150
Twubhubbook - it's like appsec, but for startups (without notes)
oreoshake
0
130
Automatic Application Security v2
oreoshake
0
170
JRubyFX For Web Developers
oreoshake
0
270
Automatic Application Security
oreoshake
0
170
Putting your robots to work: Security Automation @Twitter
oreoshake
2
190
BSidesLA Managing Content Security Policy
oreoshake
3
1.2k
Other Decks in Programming
See All in Programming
golang-bob.pdf
iwatsukayura
0
150
Spec-driven Development with AI
simas
PRO
0
2.2k
Next.js: The final boss of Web Performance
guaca
0
360
No More NoSuchMethodError
exoego
1
120
複雑なUIコンポーネントとの ⻑い付き合い⽅:波及するバグからテスト戦略を経て、安全な再設計へ
mixplace
0
490
[2026-10-09]一枚の布で作らなくてもいい。 信頼性は「パッチワーク」で紡がれる~既存の運用と新しい可能性をつなぎ合わせてきたCREの話~
tosite
0
120
TS 7.0 で baseUrl が使えなくなった今、パスエイリアスをどうするか
bicstone
1
270
Long Living Tokens, Die, Die, Die! (or: The One Ring is Banned in Modern)
sylph01
0
390
PyConTW 2026 - AI Coding 不只是工具升級, 區域醫院醫療資訊系統協作開發與資訊團隊轉型實踐
cclai999
0
210
當我們開始不讀 Code - AI Agent 時代,Code Review 與 Clean Code 還剩下什麼?
jame2408
1
340
社内AIエージェント「Askワンバン」における コストチューニングの取り組み
t0yohei
0
110
ActionController meets Protocol Buffers
sorah
1
750
Featured
See All Featured
Scaling GitHub
holman
464
140k
Sharpening the Axe: The Primacy of Toolmaking
bcantrill
46
3k
Groundhog Day: Seeking Process in Gaming for Health
codingconduct
0
450
Producing Creativity
orderedlist
PRO
348
41k
Google's AI Overviews - The New Search
badams
0
1.6k
Gemini Prompt Engineering: Practical Techniques for Tangible AI Outcomes
mfonobong
2
600
Agile Actions for Facilitating Distributed Teams - ADO2019
mkilby
0
320
Data-driven link building: lessons from a $708K investment (BrightonSEO talk)
szymonslowik
1
1.4k
Highjacked: Video Game Concept Design
rkendrick25
PRO
1
500
ラッコキーワード サービス紹介資料
rakko
5
5.6M
Claude Code のすすめ
schroneko
67
230k
Done Done
chrislema
187
17k
Transcript
How CSP Will (maybe) Solve the XSS Problem Neil Matatall
OWASP SD 4/17/2014
Me • Twitter appsec engineer • I’m actually just a
developer • In the business of going out of business • Sick and tired of fixing XSS
XSS is so 1998
So is XSS prevention
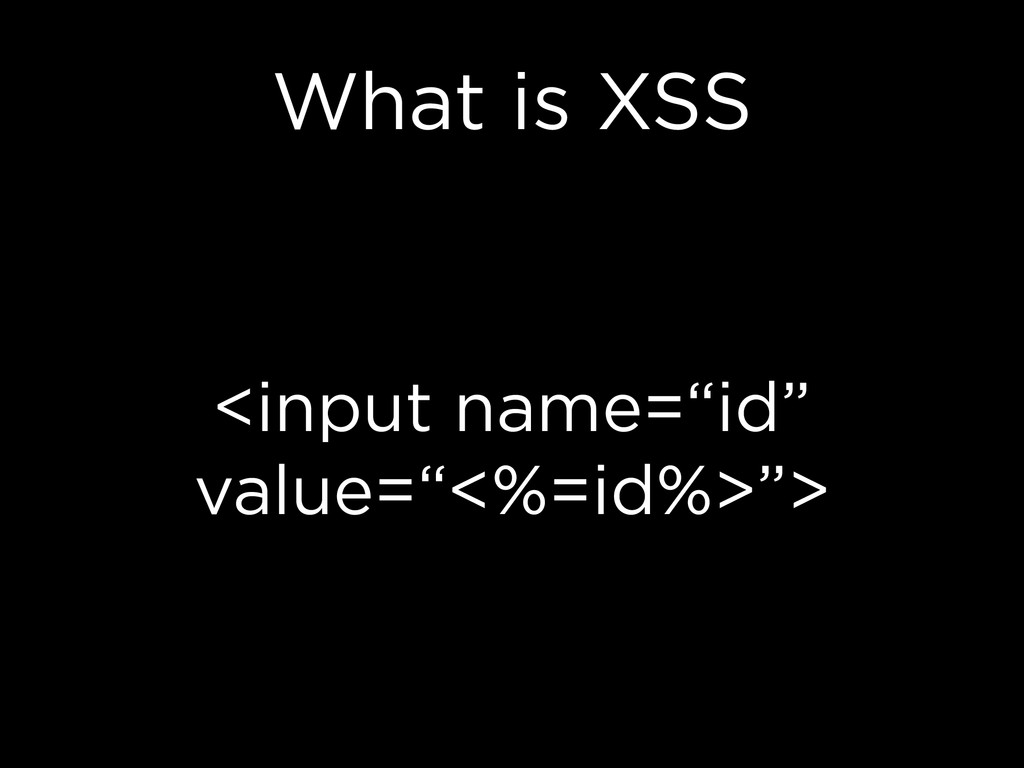
What is XSS <input name=“id” value=“<%=id%>”>
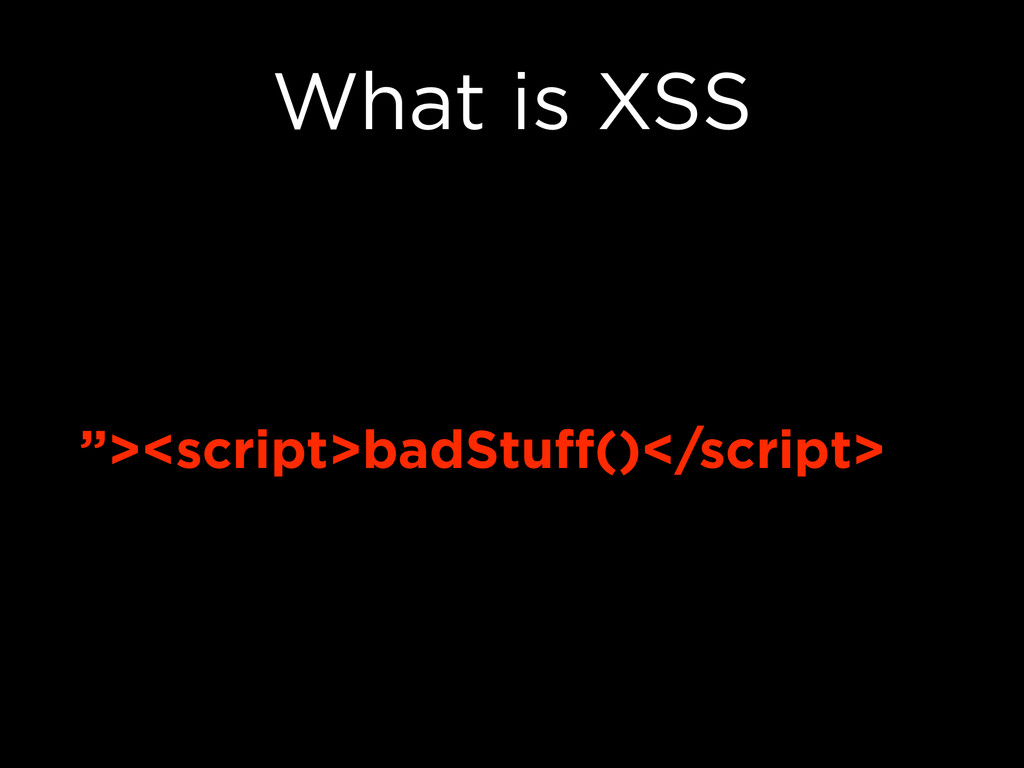
What is XSS ”><script>badStuff()</script>
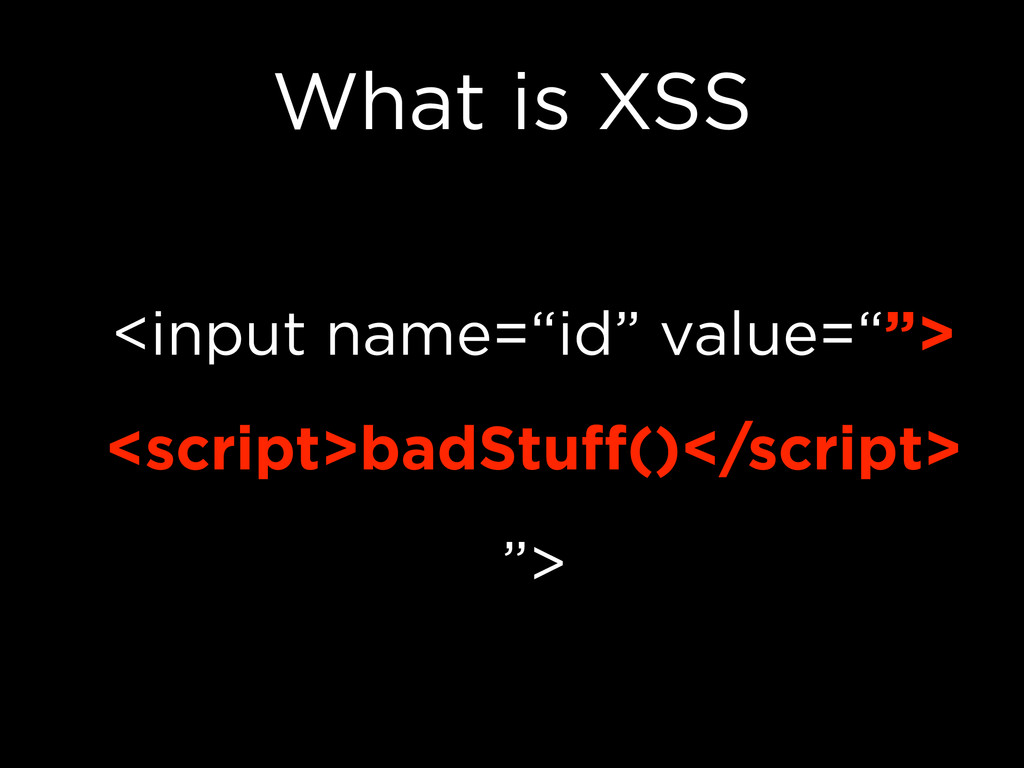
What is XSS <input name=“id” value=“”> <script>badStuff()</script> ”>
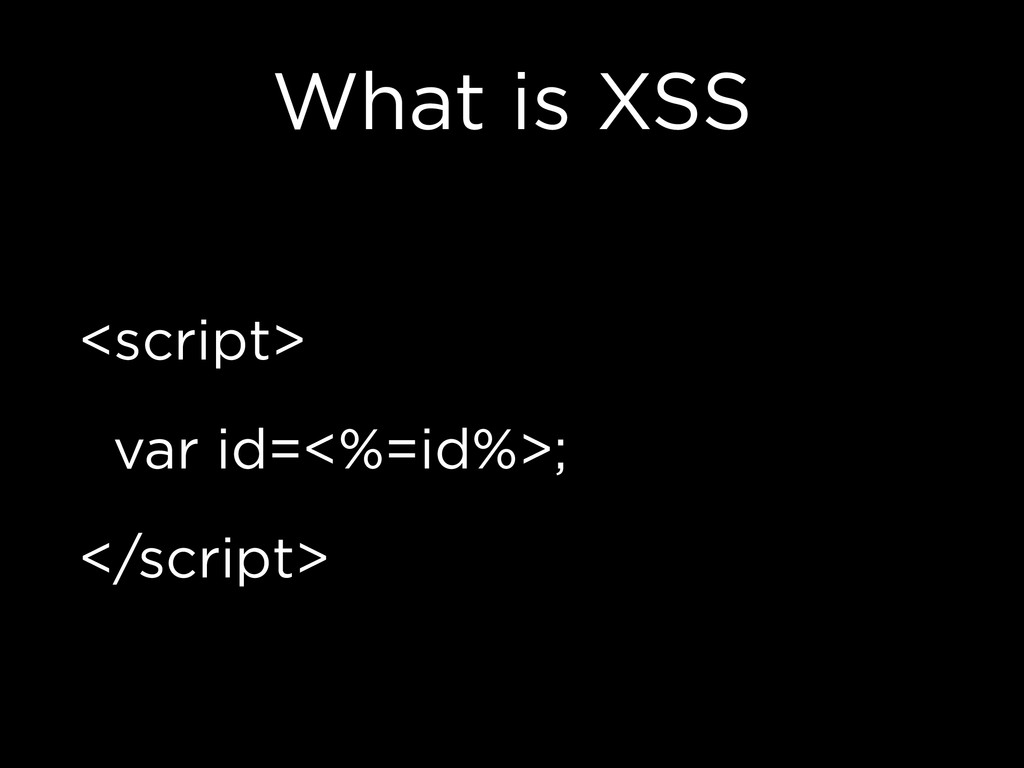
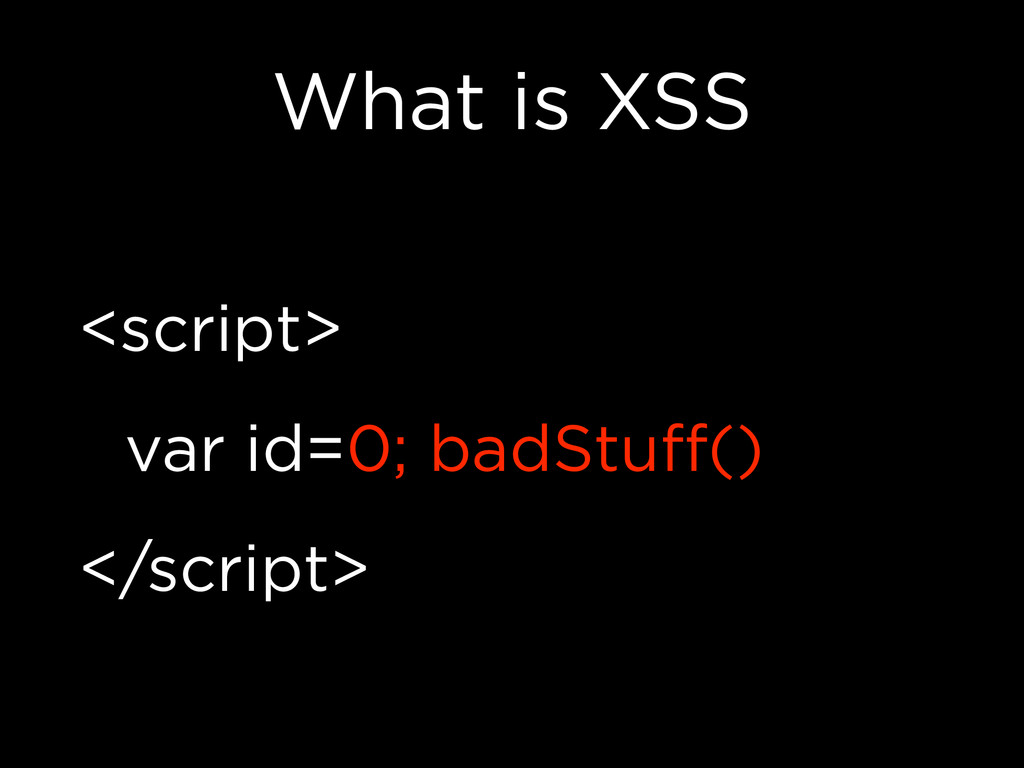
What is XSS <script> var id=<%=id%>; </script>
What is XSS 0;badStuff();
What is XSS <script> var id=0; badStuff() </script>
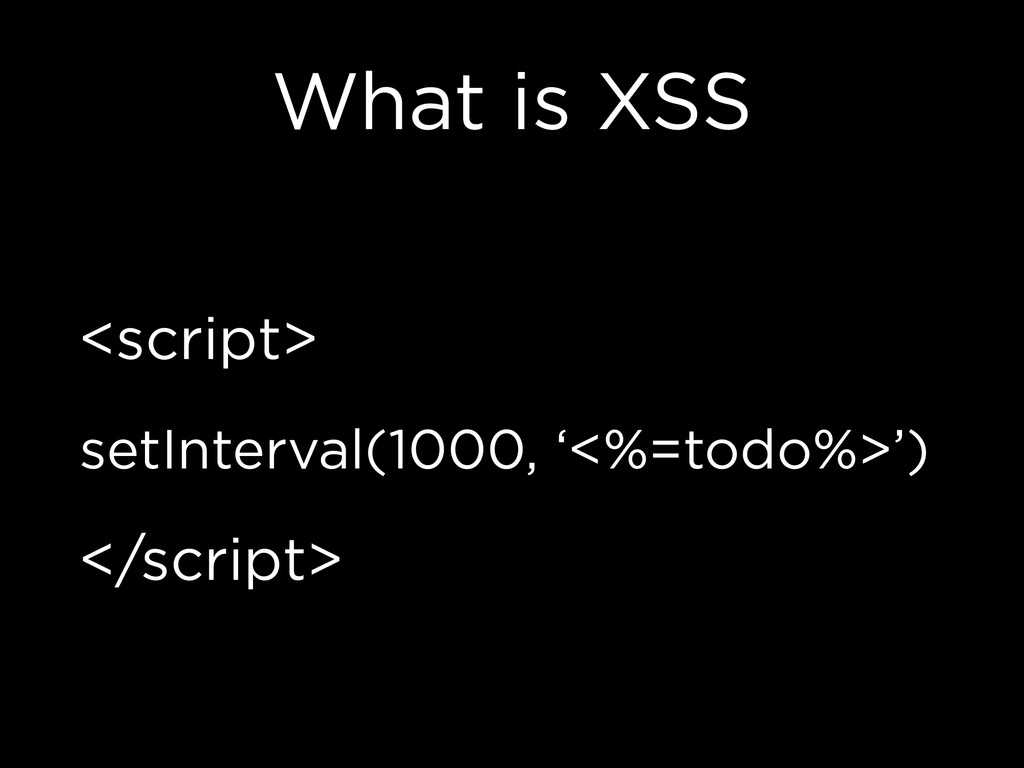
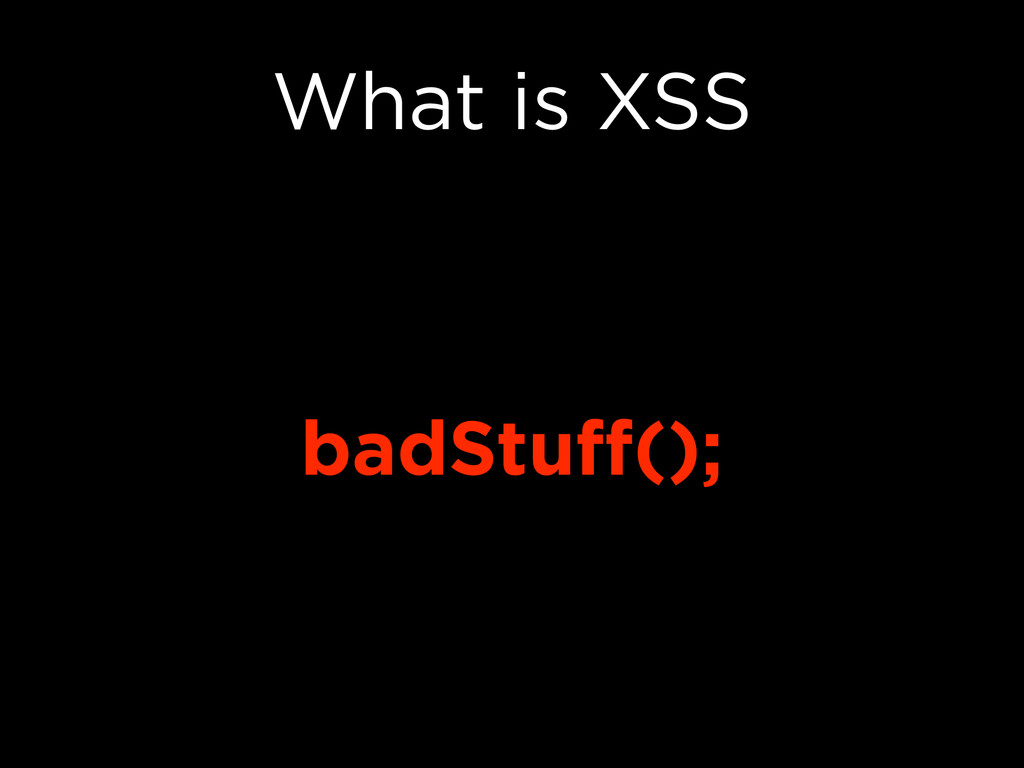
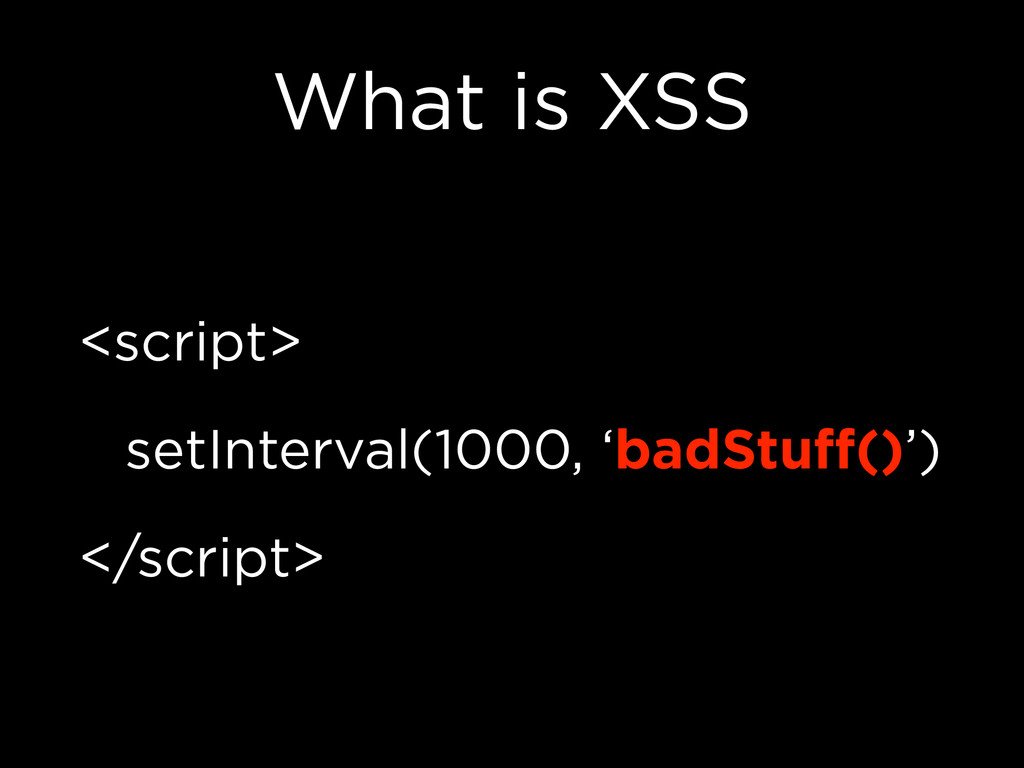
What is XSS <script> setInterval(1000, ‘<%=todo%>’) </script>
What is XSS badStuff();
What is XSS <script> setInterval(1000, ‘badStuff()’) </script>
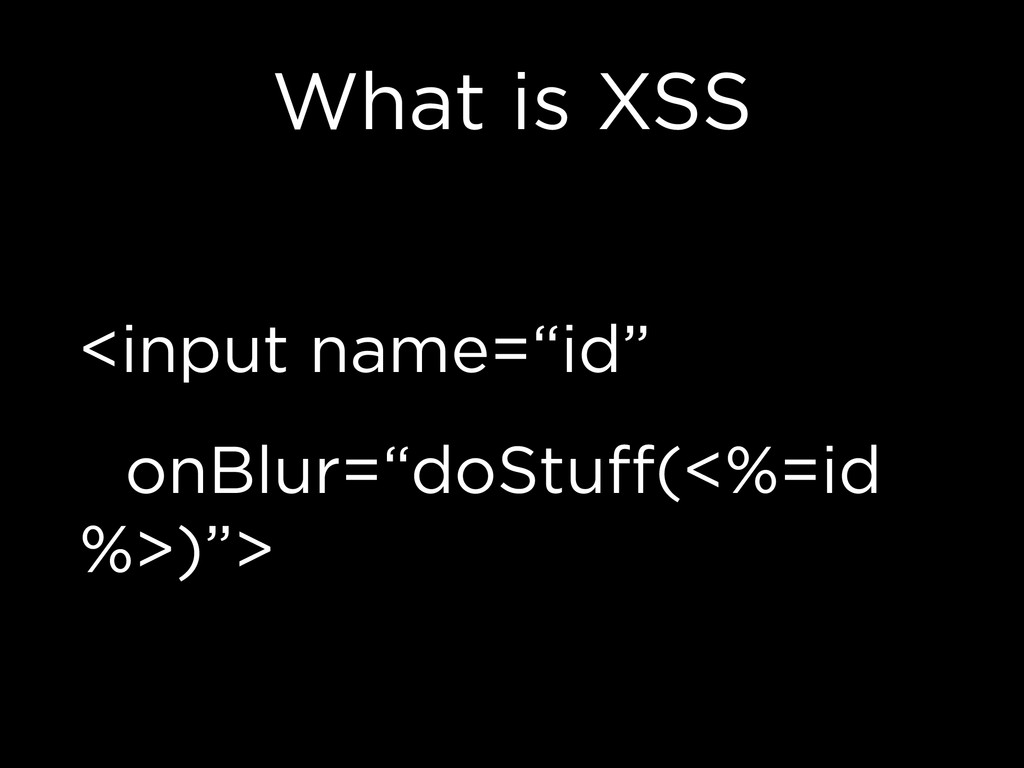
What is XSS <input name=“id” onBlur=“doStuff(<%=id %>)”>
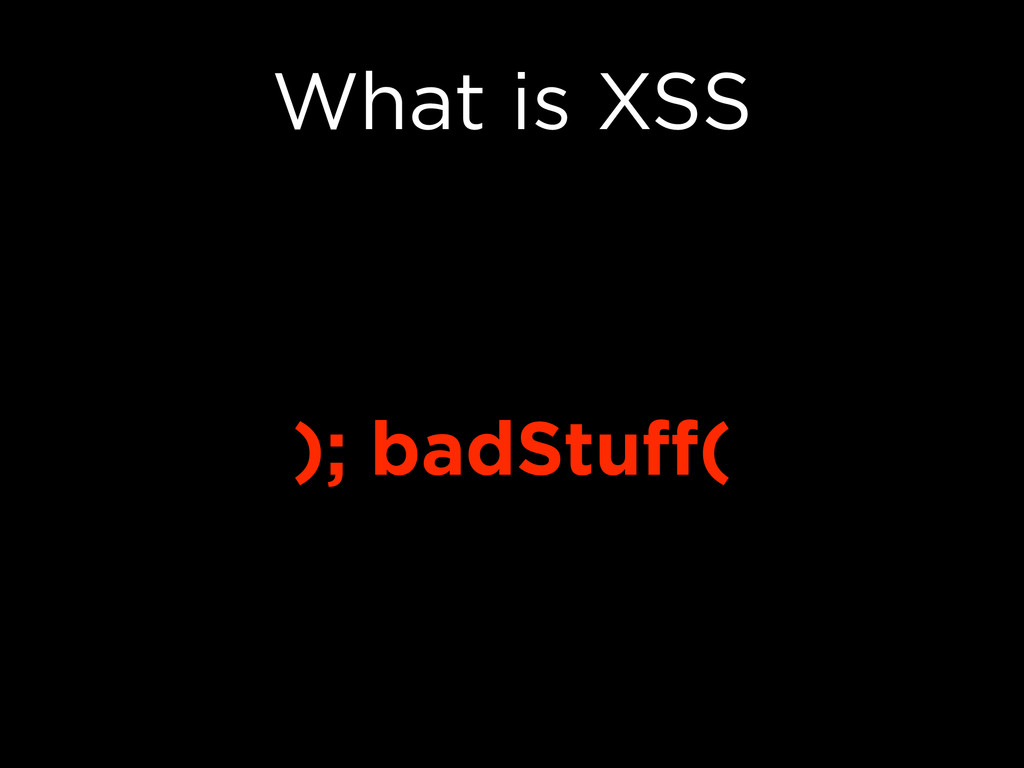
What is XSS ); badStuff(
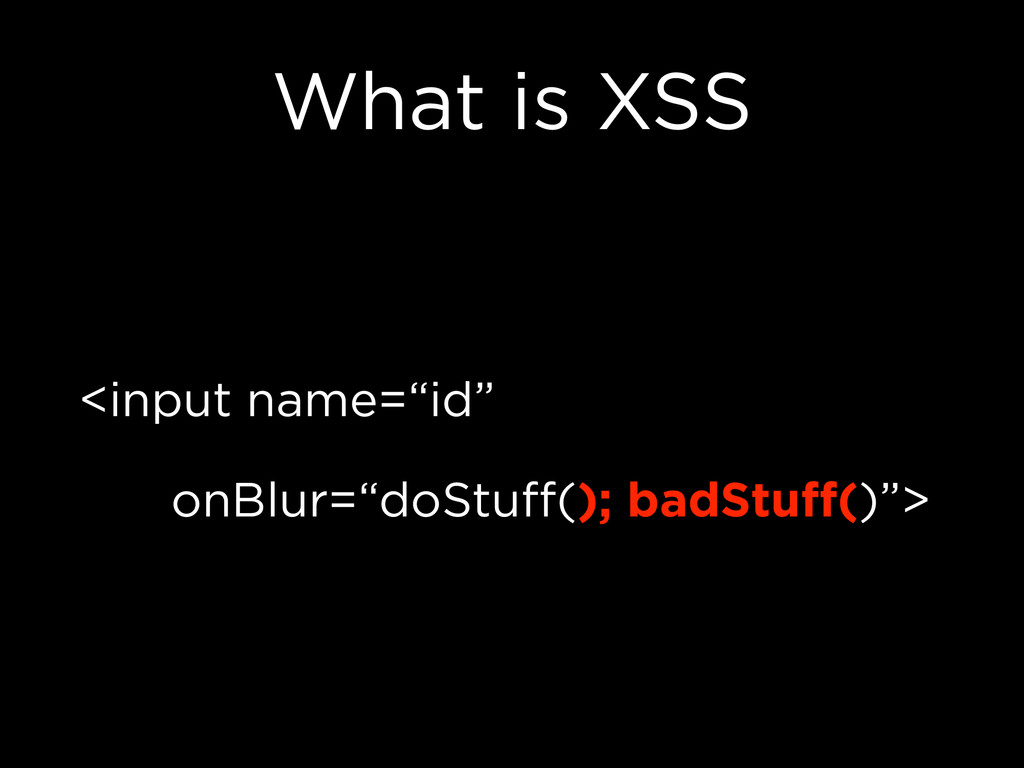
What is XSS <input name=“id” onBlur=“doStuff(); badStuff()”>
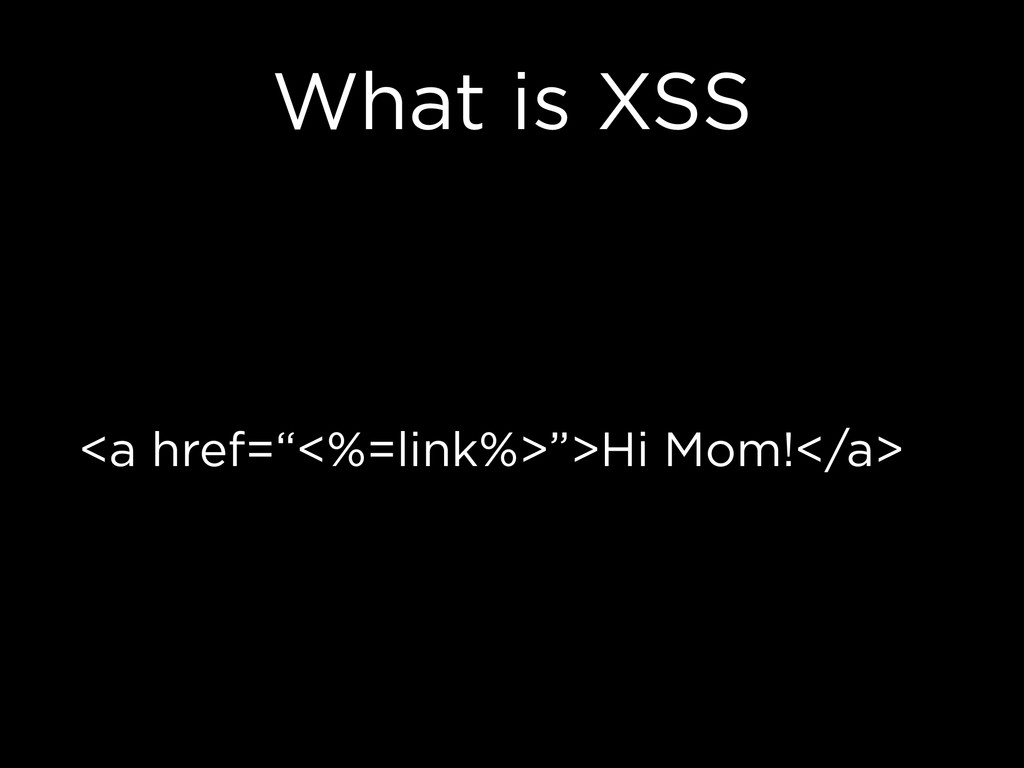
What is XSS <a href=“<%=link%>”>Hi Mom!</a>
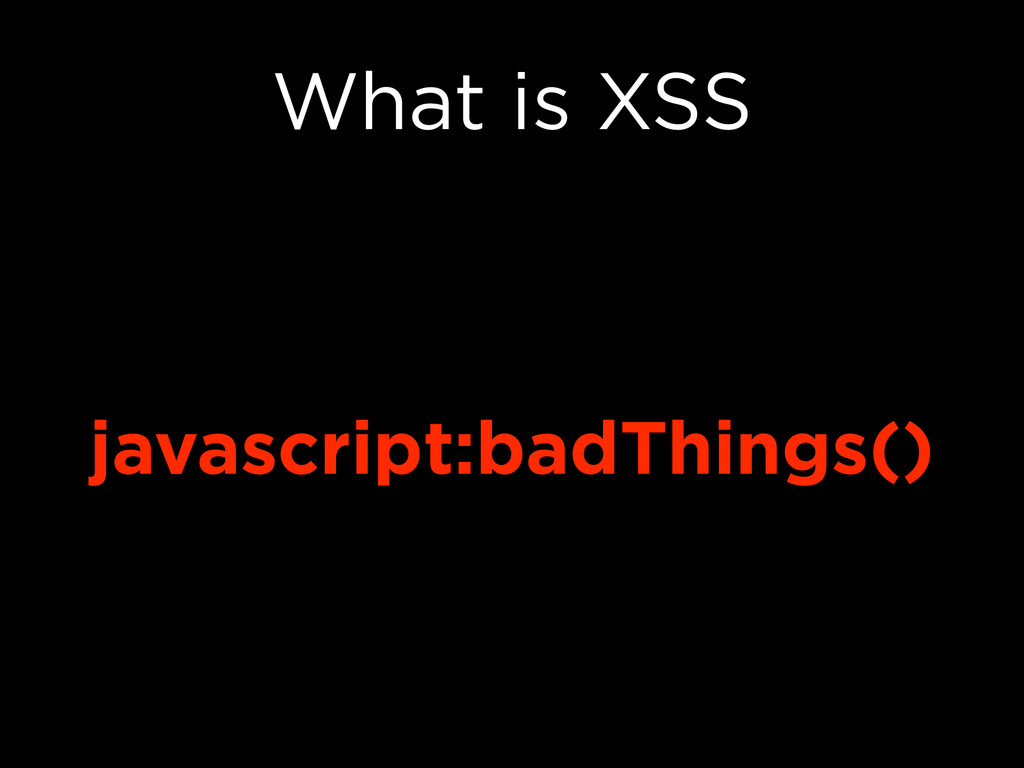
What is XSS javascript:badThings()
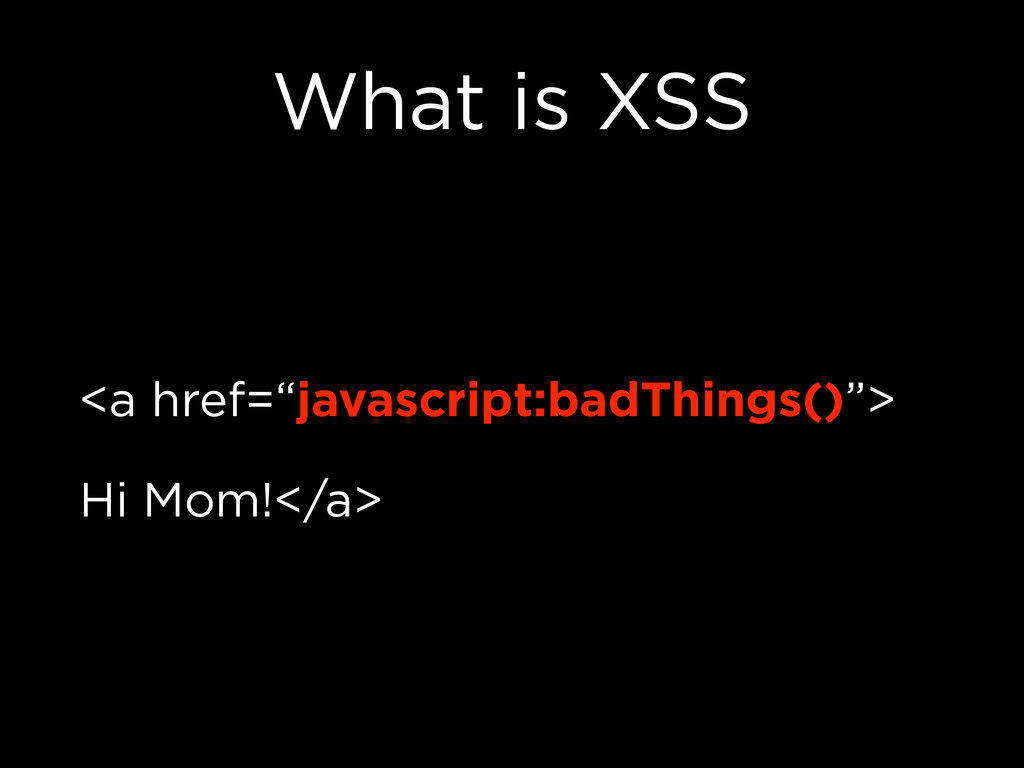
What is XSS <a href=“javascript:badThings()”> Hi Mom!</a>
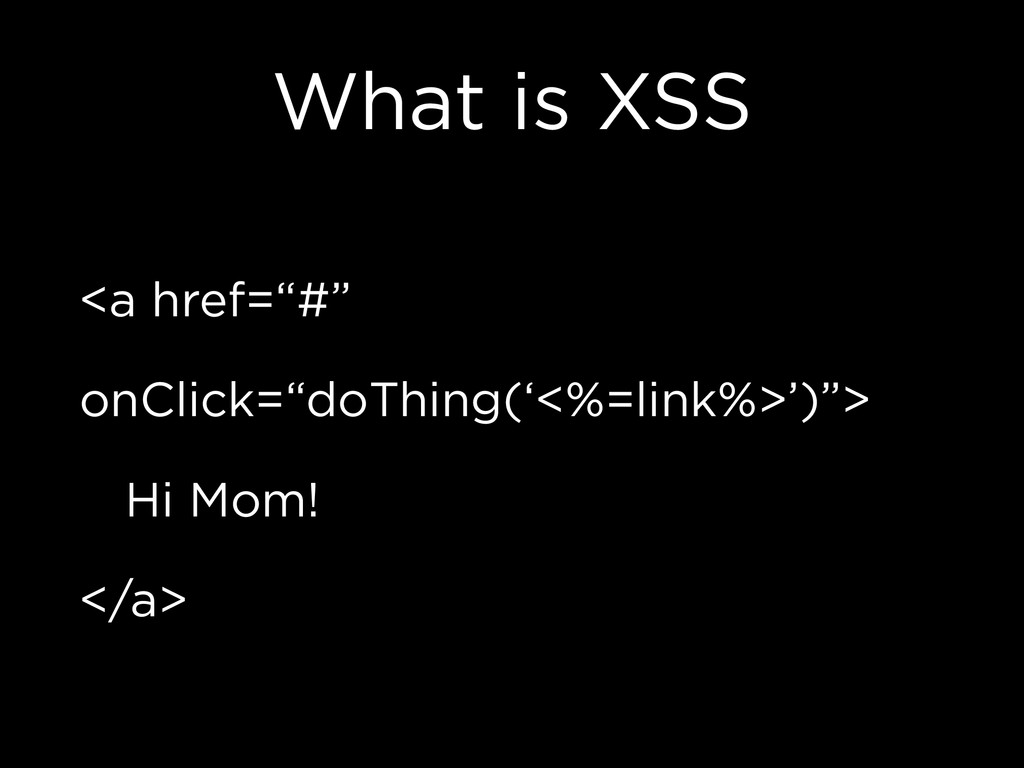
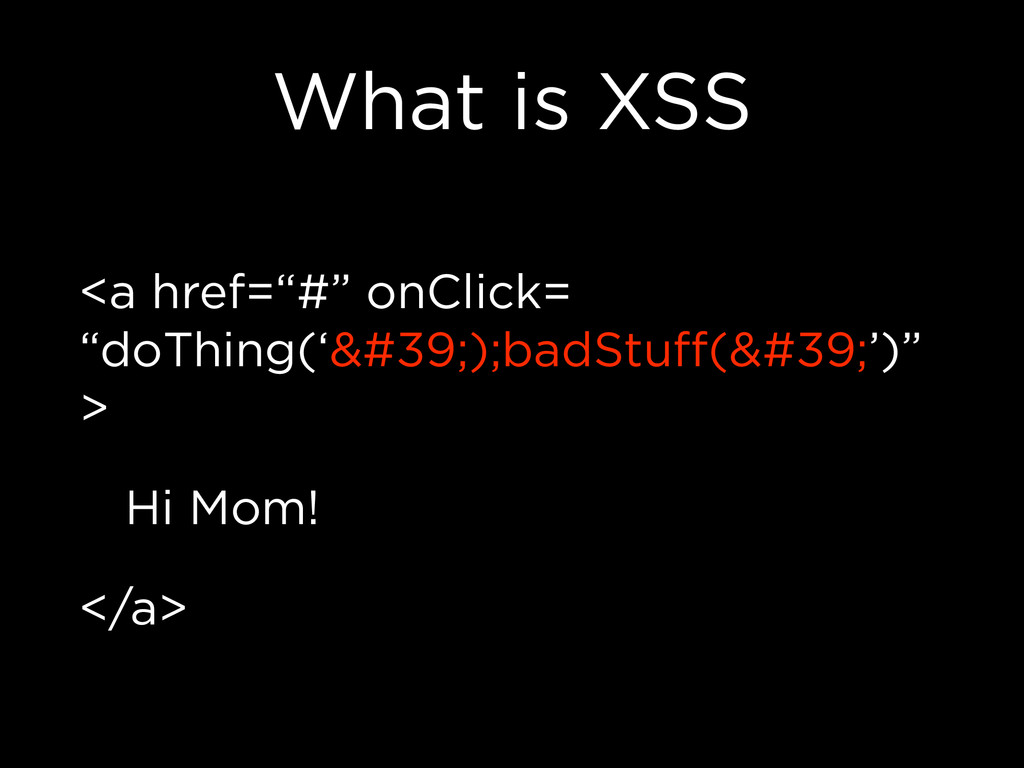
What is XSS <a href=“#” onClick=“doThing(‘<%=link%>’)”> Hi Mom! </a>
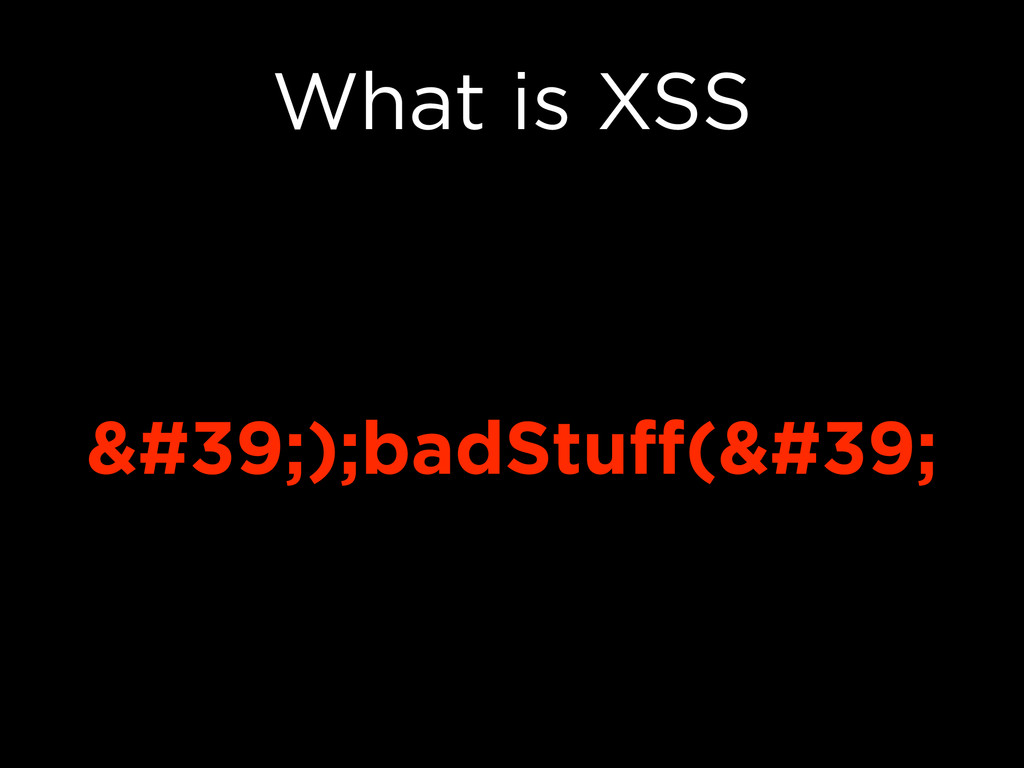
What is XSS ');badStuff('
What is XSS <a href=“#” onClick= “doThing(‘');badStuff('’)” > Hi Mom!
</a>
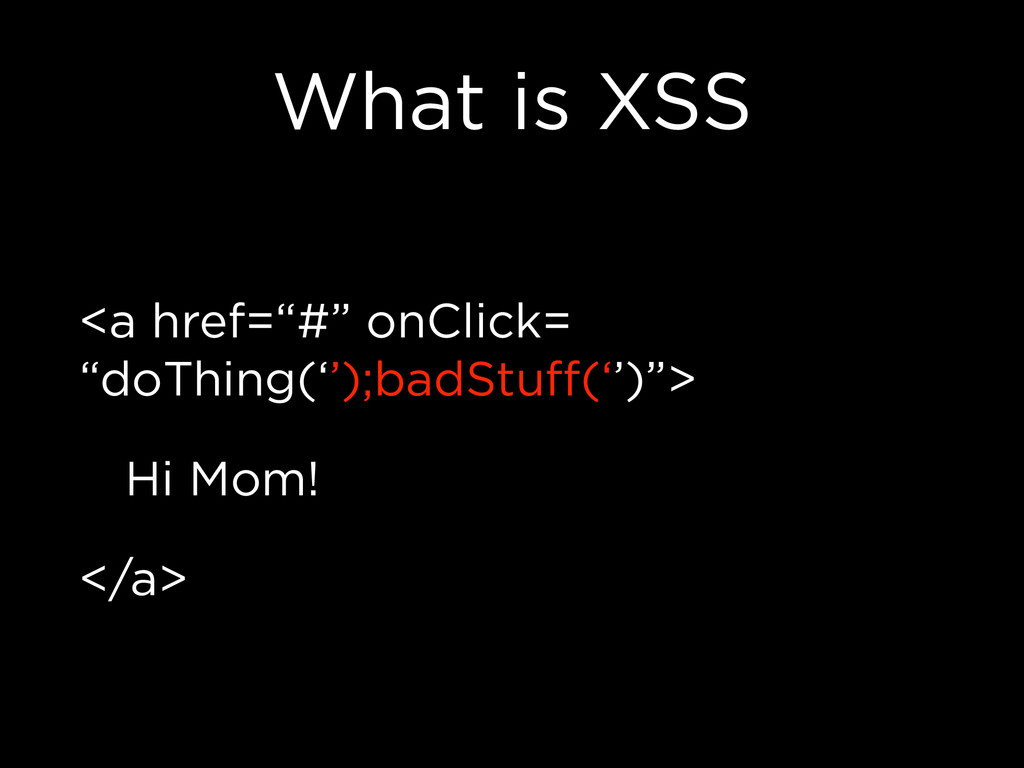
What is XSS <a href=“#” onClick= “doThing(‘’);badStuff(‘’)”> Hi Mom! </a>
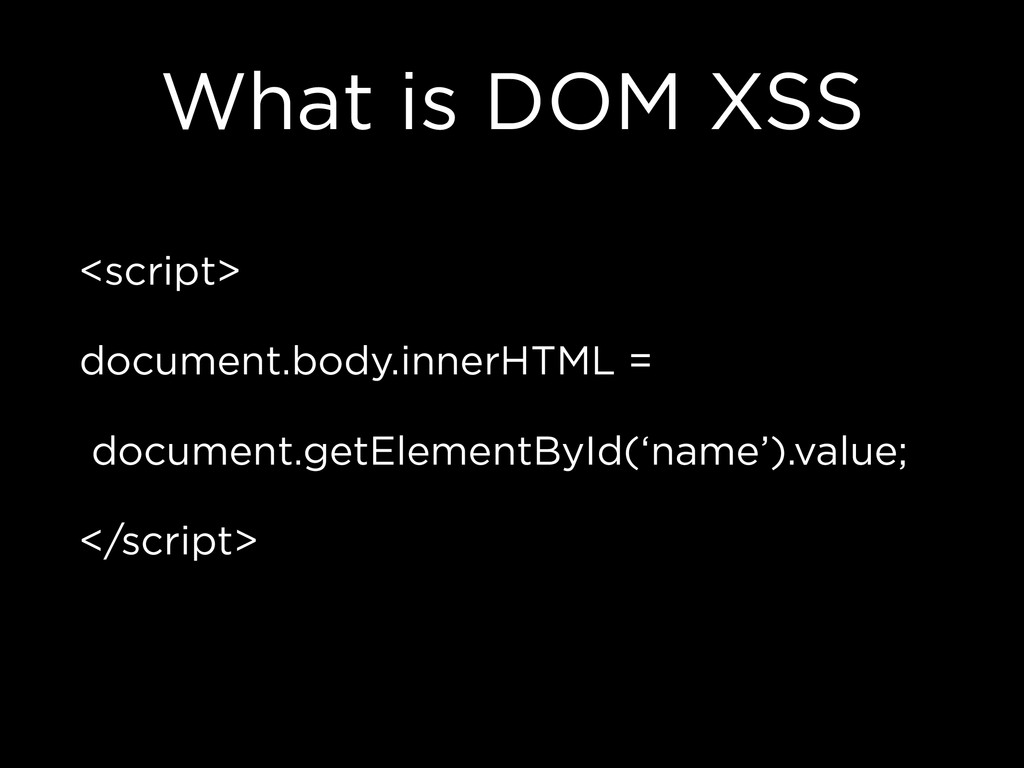
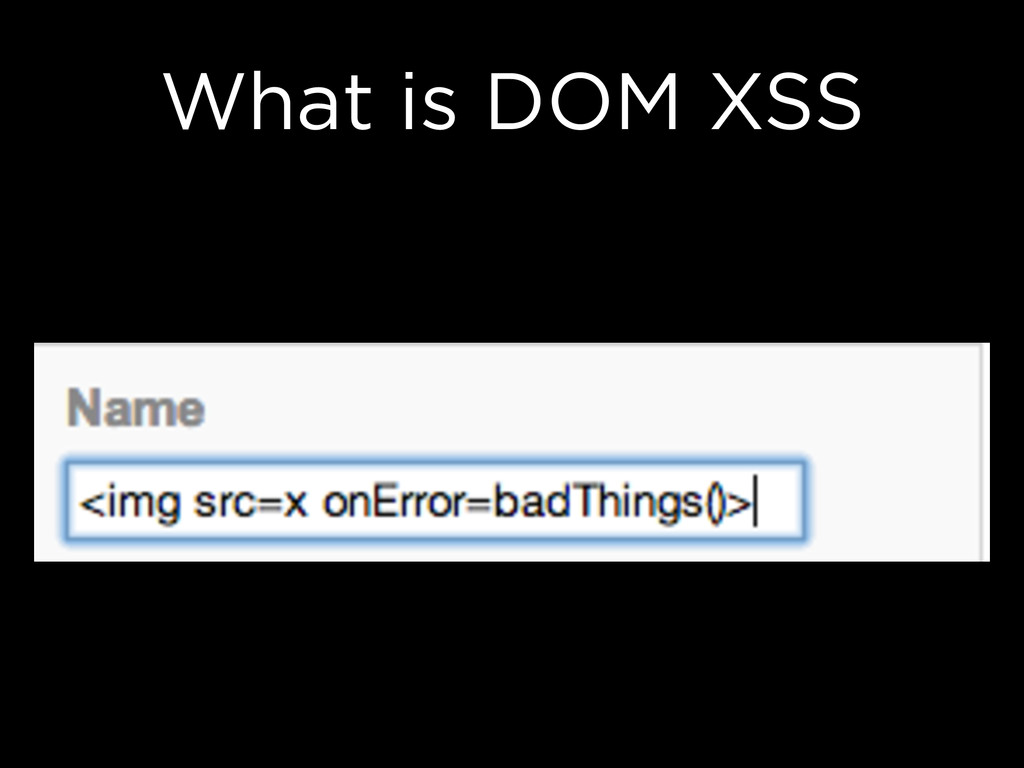
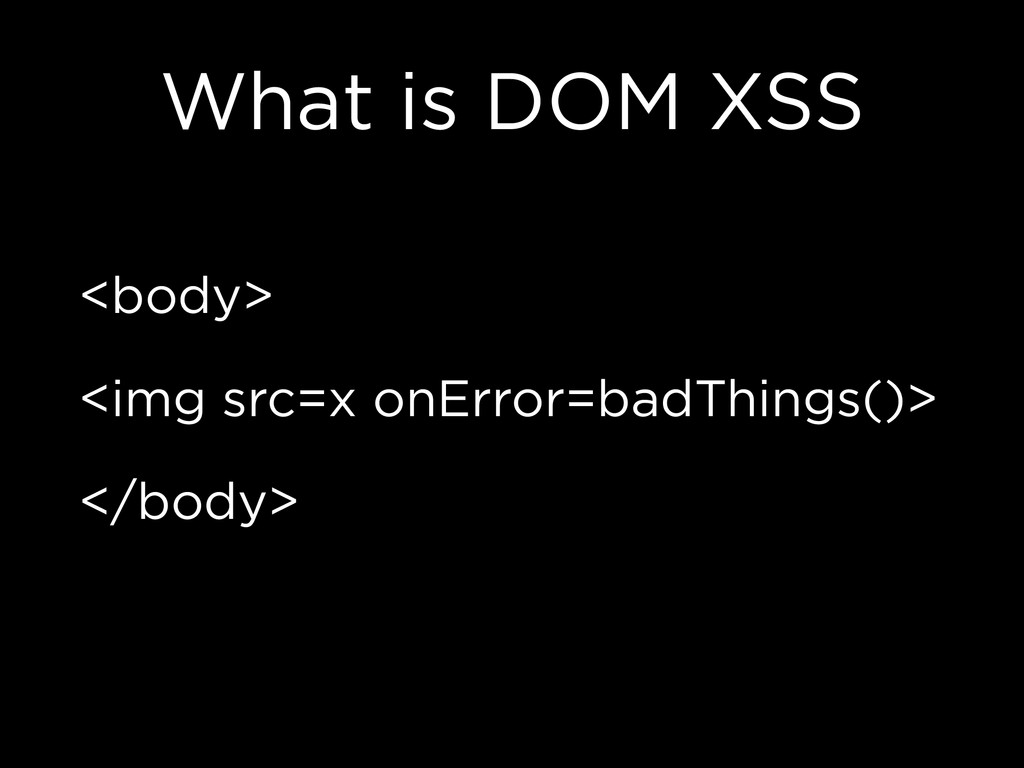
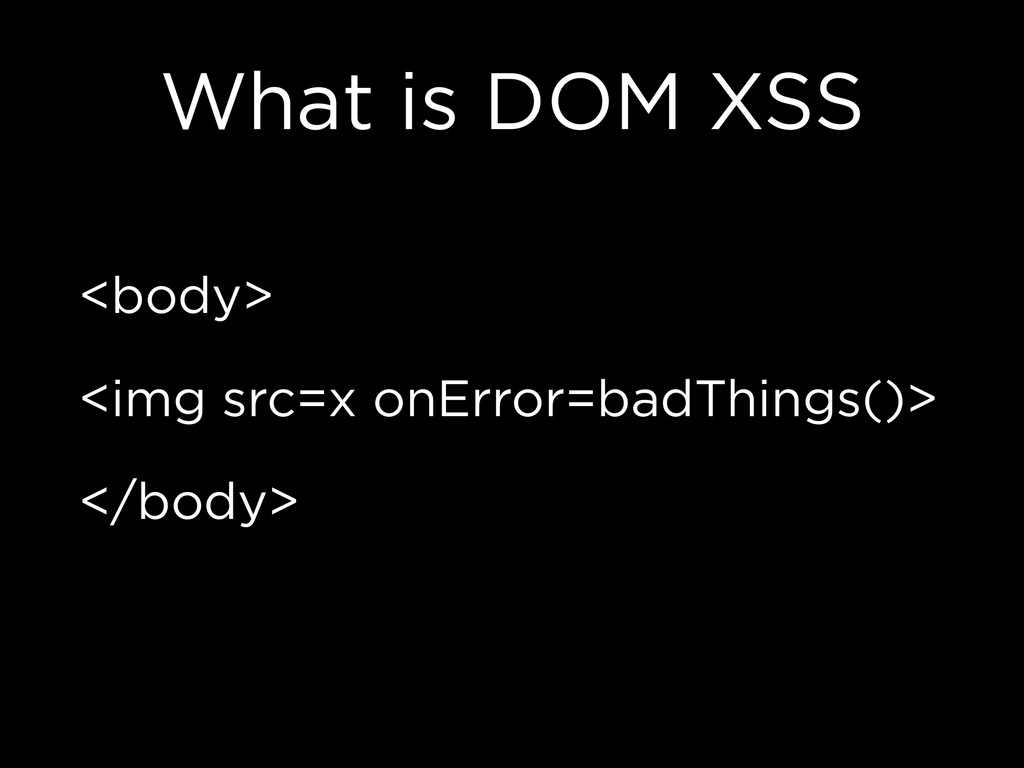
What is DOM XSS <script> document.body.innerHTML = document.getElementById(‘name’).value; </script>
What is DOM XSS
What is DOM XSS <body> <img src=x onError=badThings()> </body>
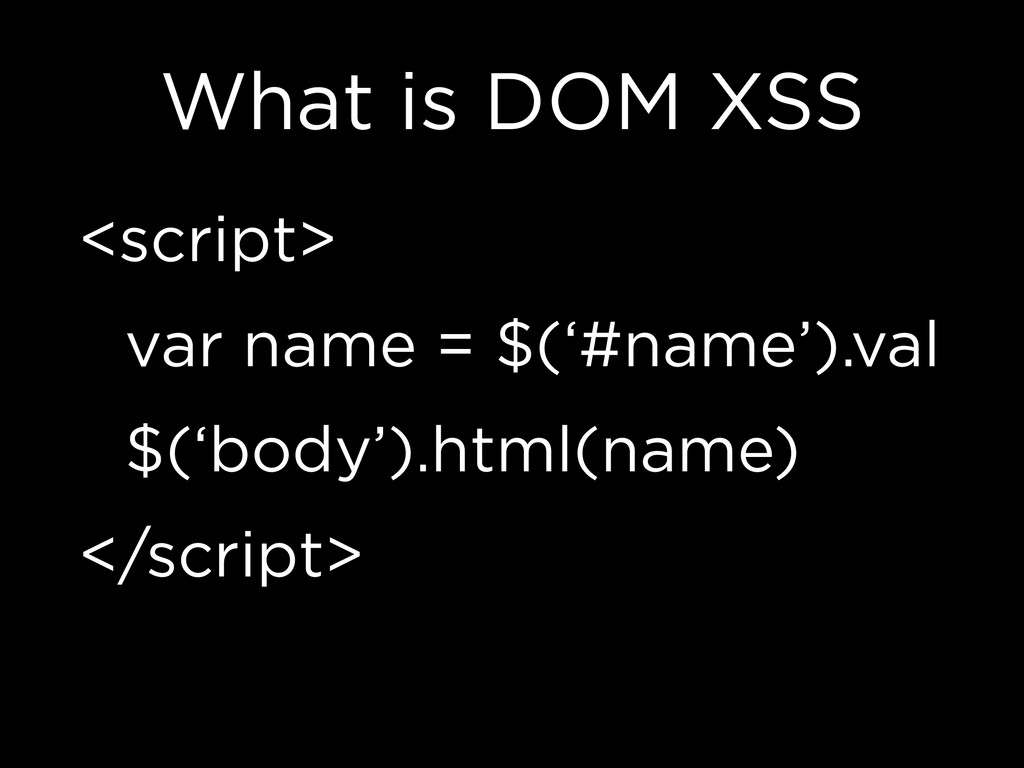
What is DOM XSS <script> var name = $(‘#name’).val $(‘body’).html(name)
</script>
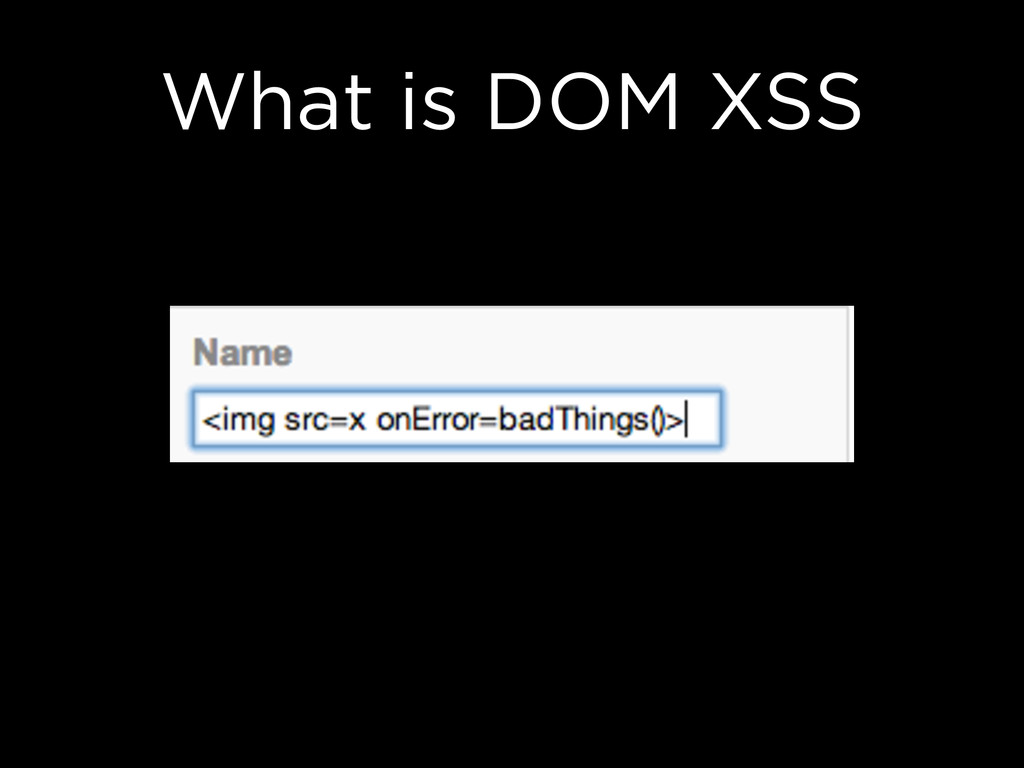
What is DOM XSS
What is DOM XSS <body> <img src=x onError=badThings()> </body>
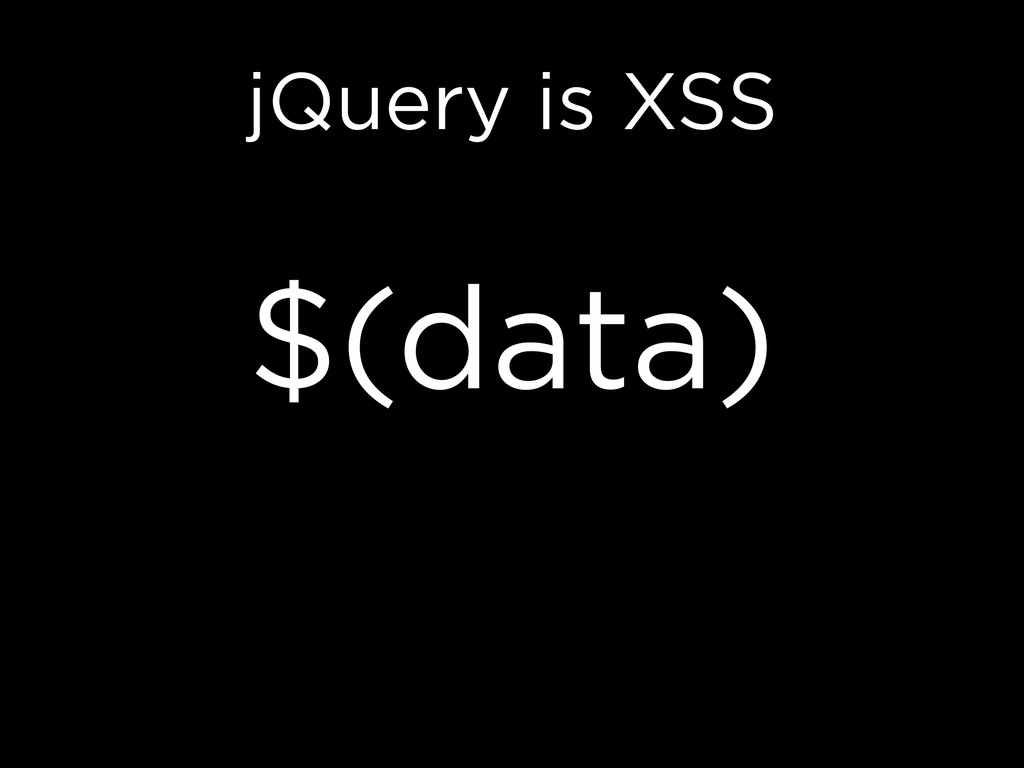
jQuery is XSS $(data)
What is XSS <style> a { color: <%=usersFavoriteColor%>; } </style>
What is XSS I dunno, something with SVG, CSS Expressions,
etc. The list grows.
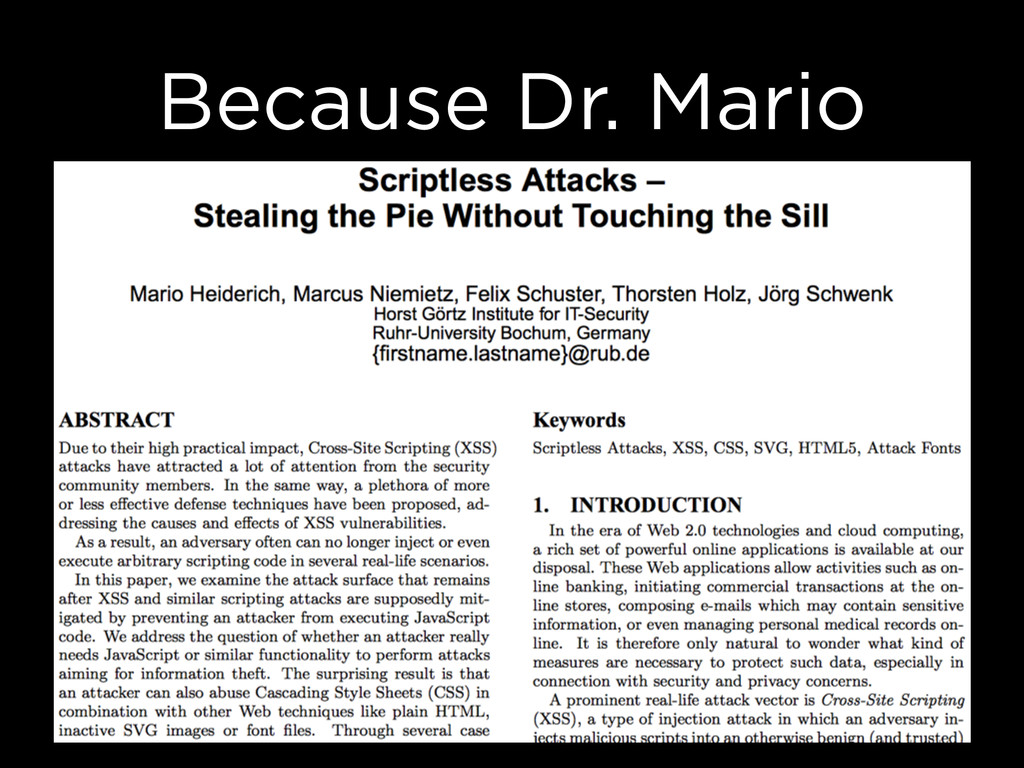
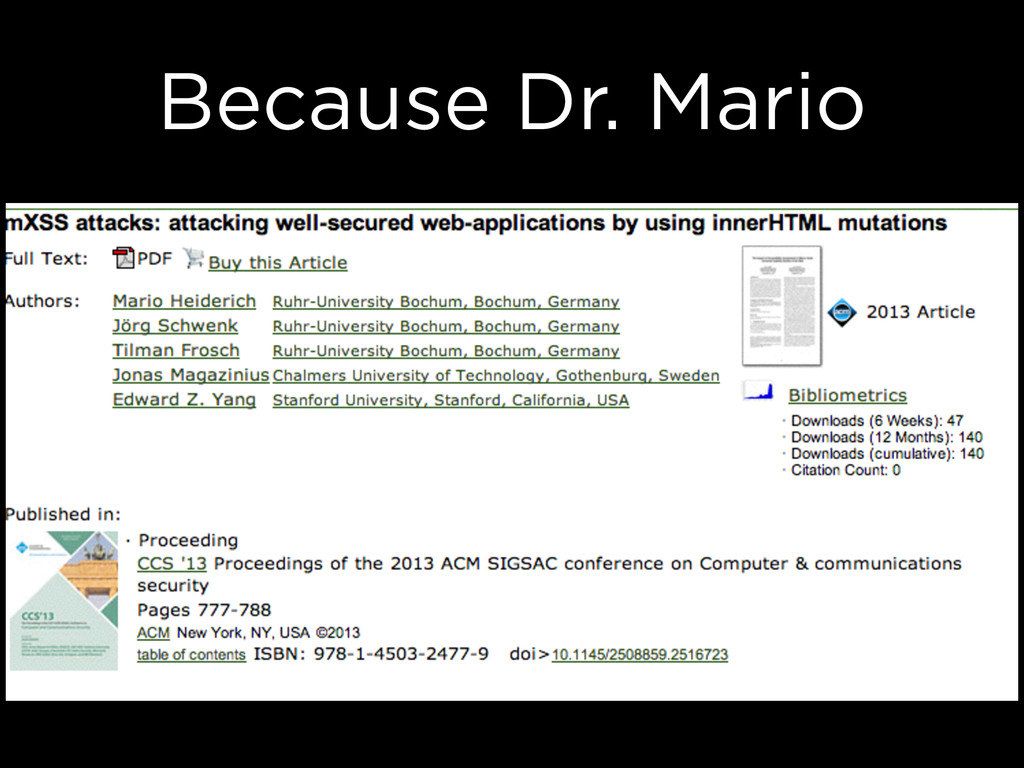
Because Dr. Mario
Because Dr. Mario
Why do those crazy things?
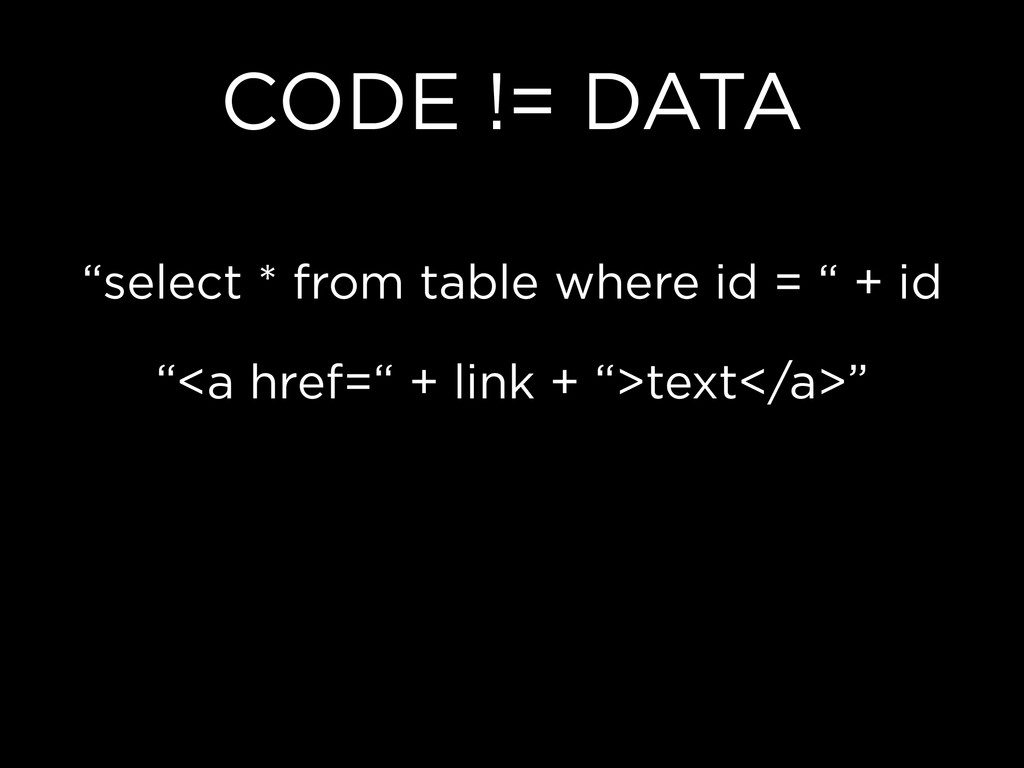
CODE != DATA “select * from table where id =
“ + id “<a href=“ + link + “>text</a>”
But we don’t do stupid things
I will religiously escape content
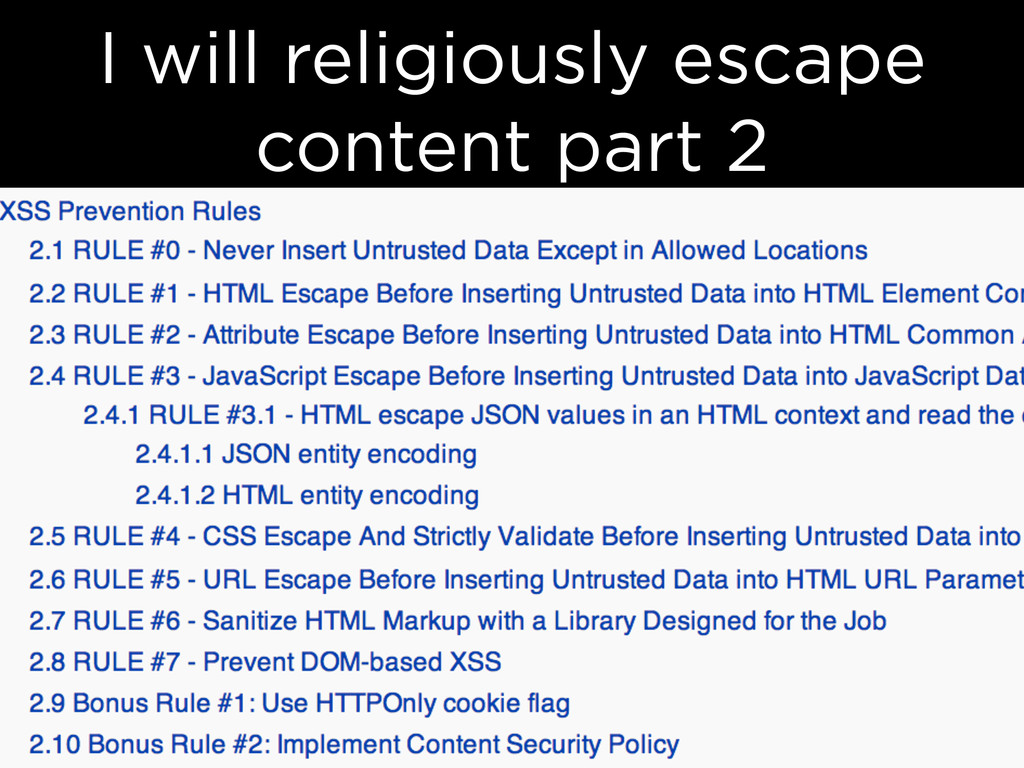
I will religiously escape content part 2
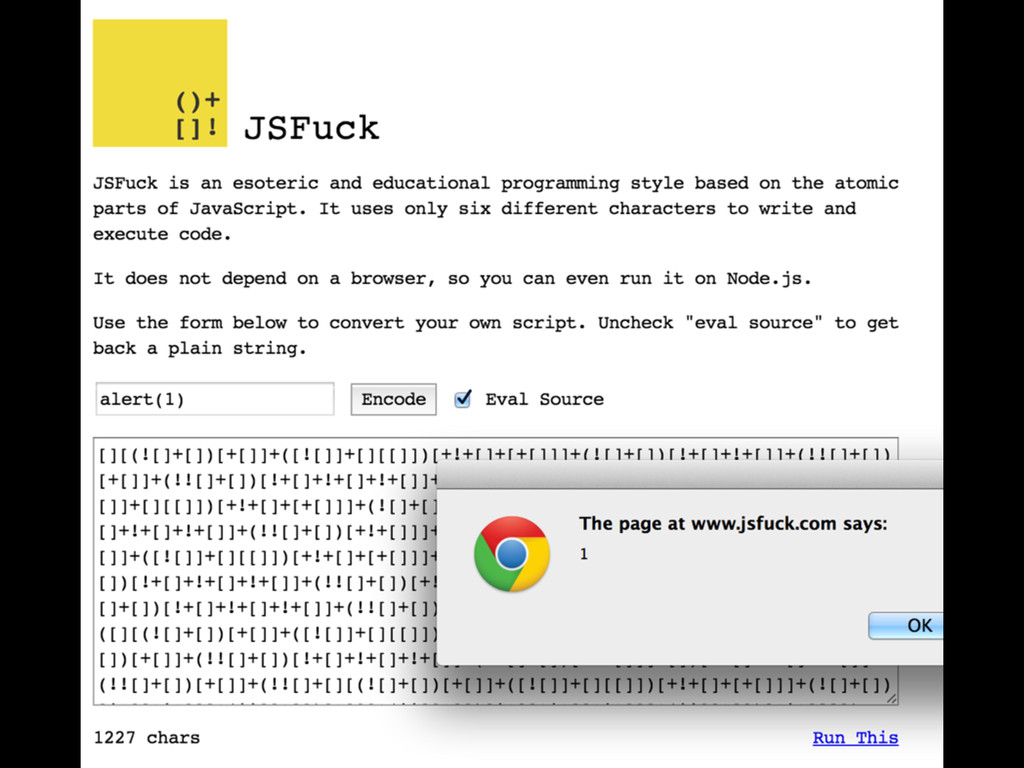
JSFuck - Write any JavaScript with 6 Characters: []()!+ I
will religiously escape content part 3
None
I’ll sanitize / validate input
I’ll use a scanner
I’ll perform periodic assessments
Security is about layers
None
Thermos? Koozie?
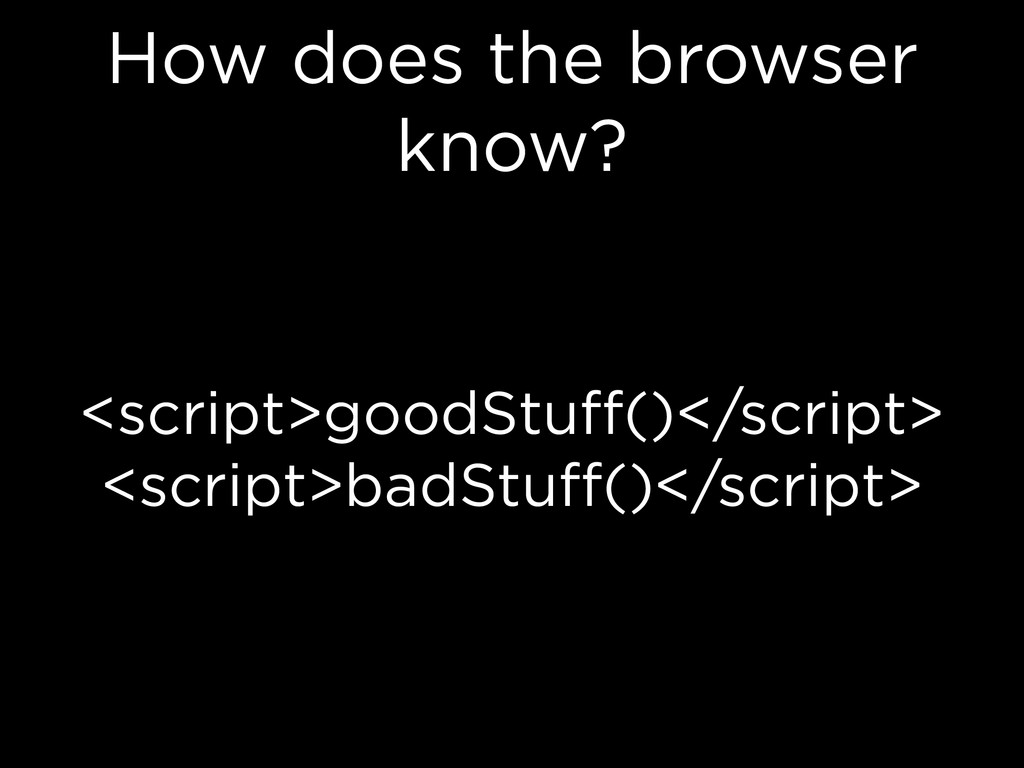
<script>goodStuff()</script> <script>badStuff()</script> How does the browser know?
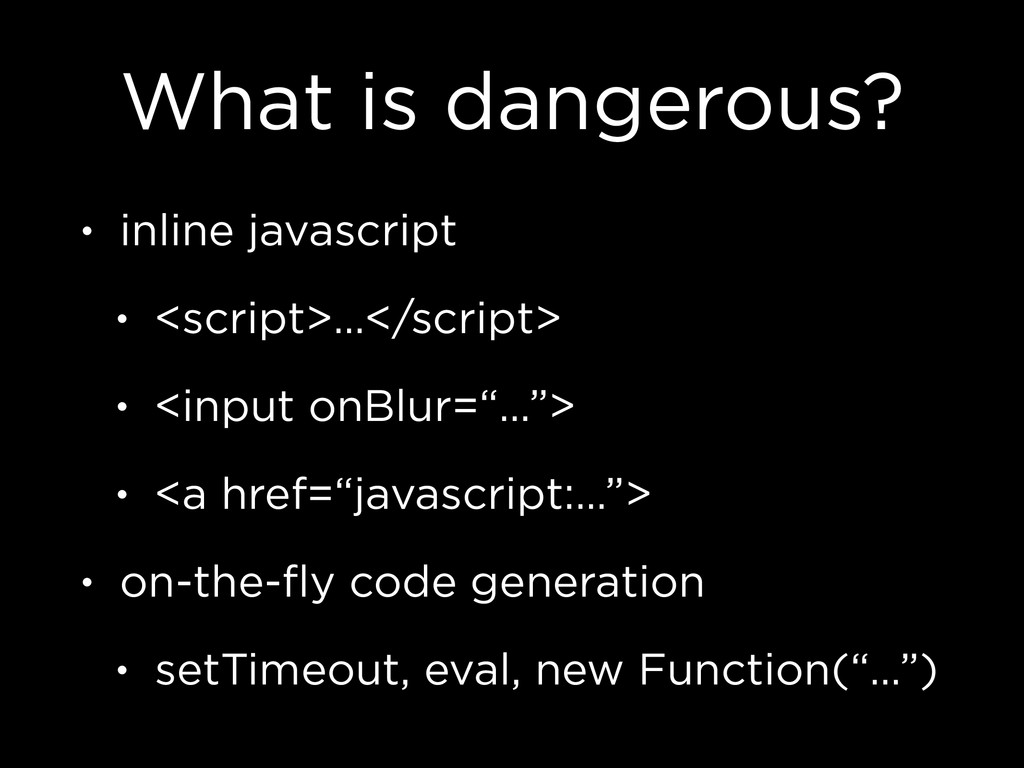
What is dangerous? • inline javascript • <script>…</script> • <input
onBlur=“…”> • <a href=“javascript:…”> • on-the-fly code generation • setTimeout, eval, new Function(“…”)
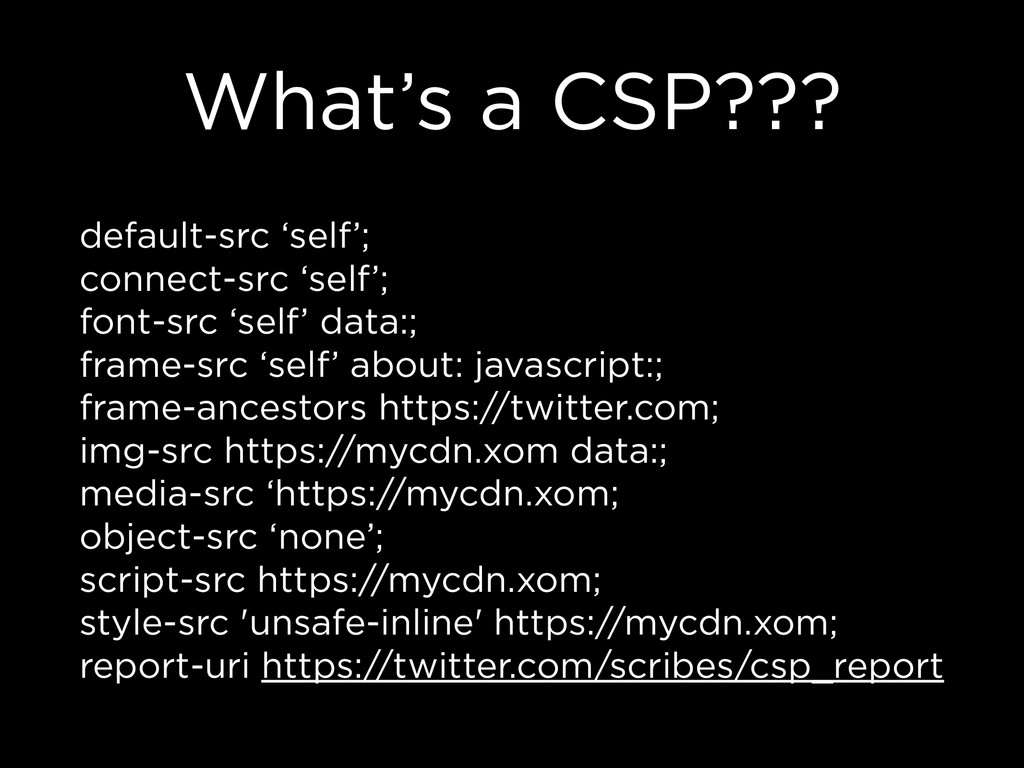
What’s a CSP??? default-src ‘self’; connect-src ‘self’; font-src ‘self’ data:;
frame-src ‘self’ about: javascript:; frame-ancestors https://twitter.com; img-src https://mycdn.xom data:; media-src ‘https://mycdn.xom; object-src ‘none’; script-src https://mycdn.xom; style-src 'unsafe-inline' https://mycdn.xom; report-uri https://twitter.com/scribes/csp_report
CSP is more than XSS protection
Nothing is free
Report-Only mode
Techniques for removing inline javascript
Removing the dangerous stuff
CSP 1.1 • Whitelisting inline <script> in a safe way
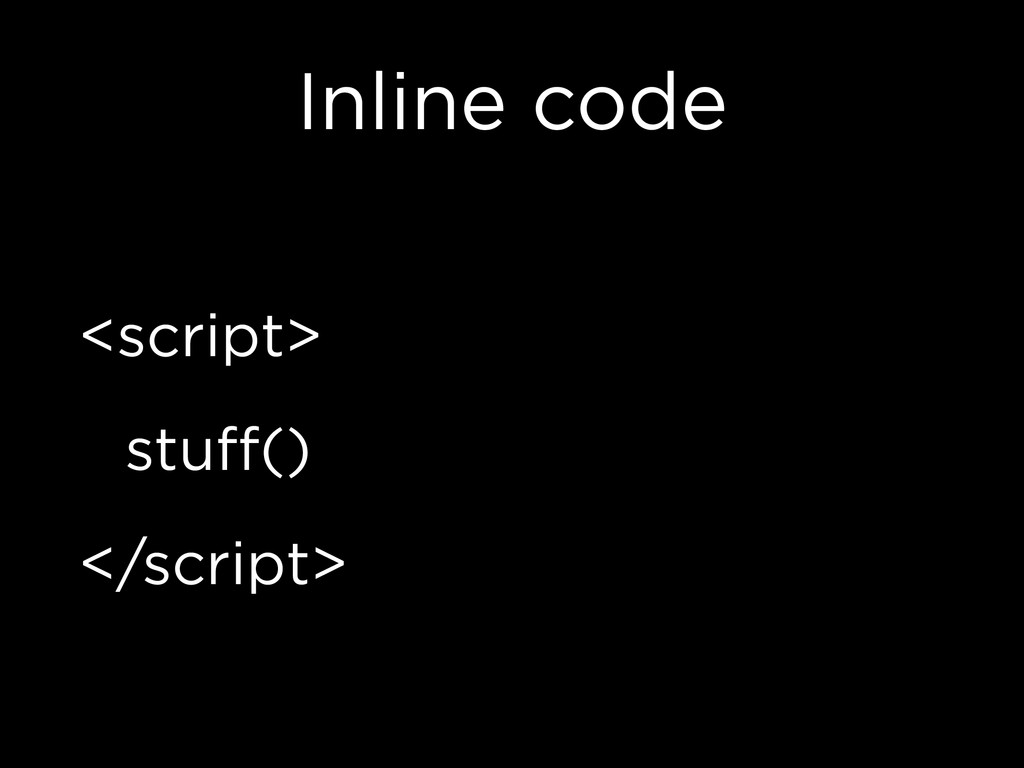
Inline code <script> stuff() </script>
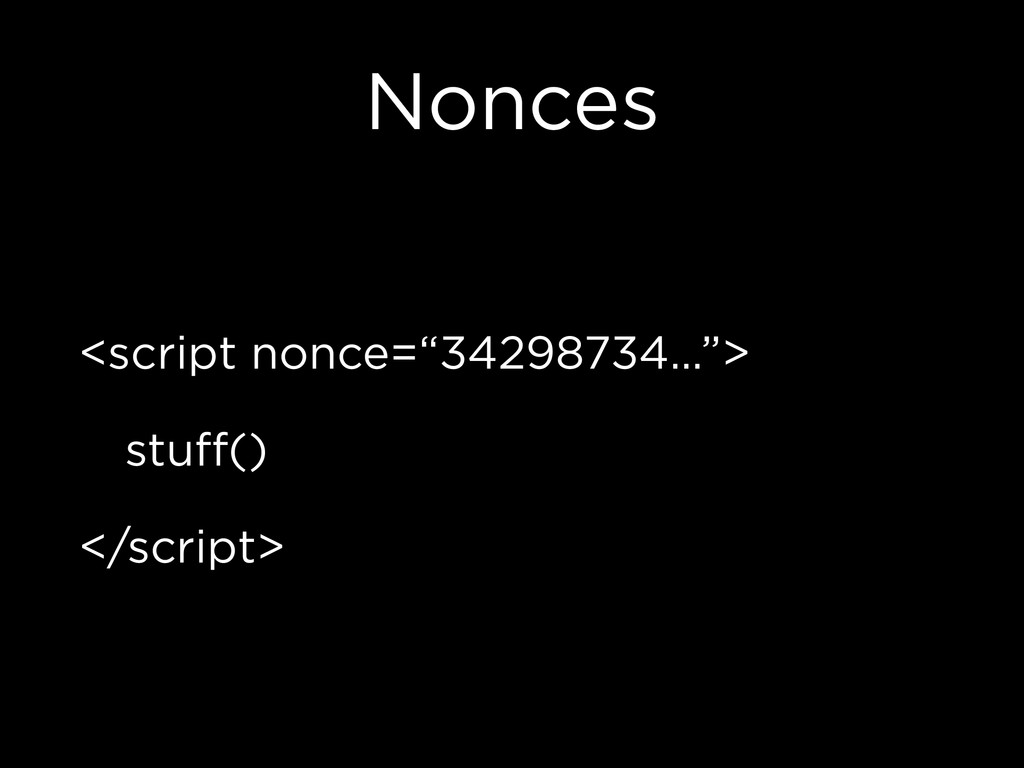
Nonces <script nonce=“34298734…”> stuff() </script>
Hashes <script> stuff() </script>
Hashes are more secure, and more limited than nonces
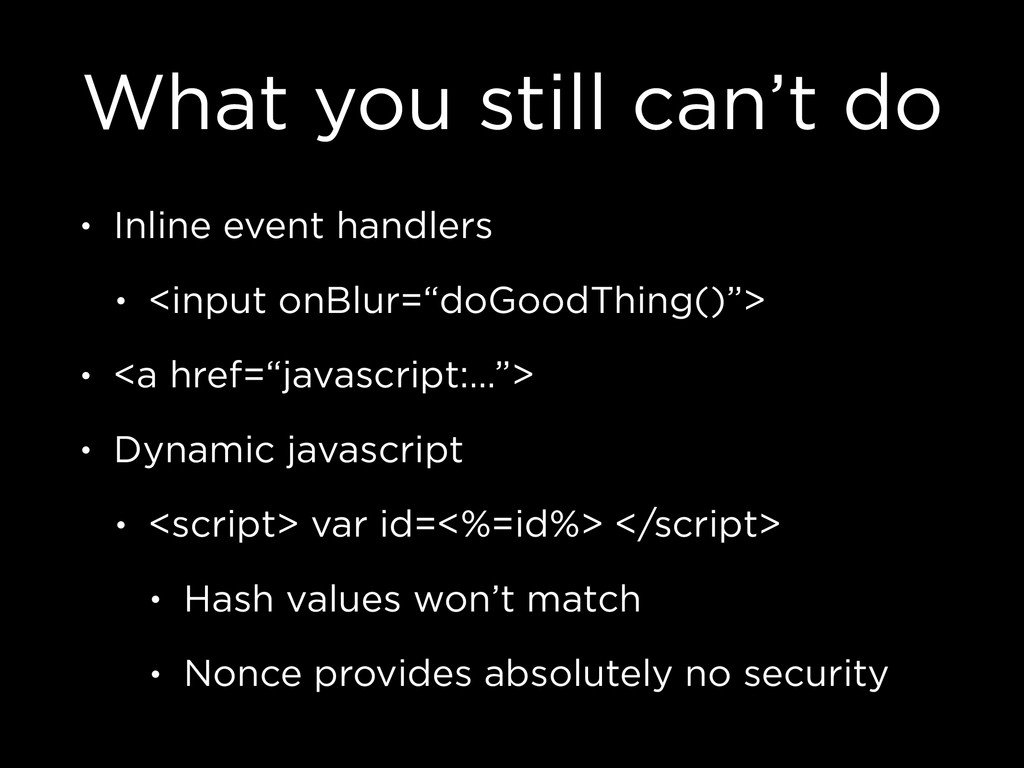
What you still can’t do • Inline event handlers •
<input onBlur=“doGoodThing()”> • <a href=“javascript:…”> • Dynamic javascript • <script> var id=<%=id%> </script> • Hash values won’t match • Nonce provides absolutely no security
Automatic CSP Protection (Silverish bullet)
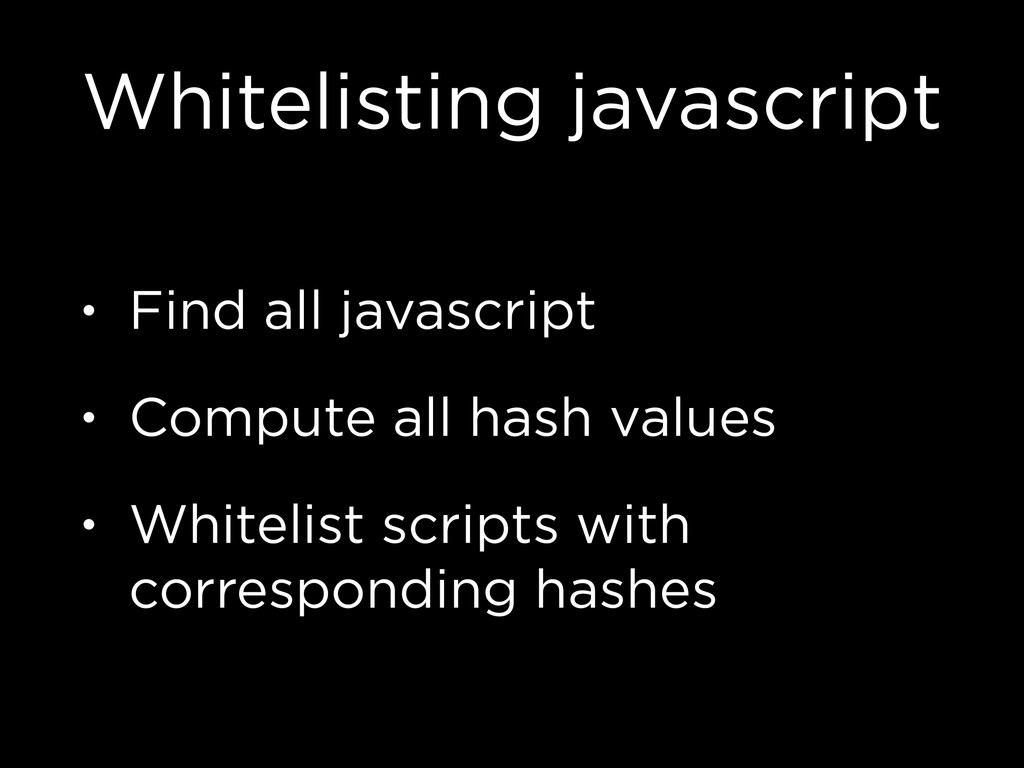
Whitelisting javascript • Find all javascript • Compute all hash
values • Whitelist scripts with corresponding hashes
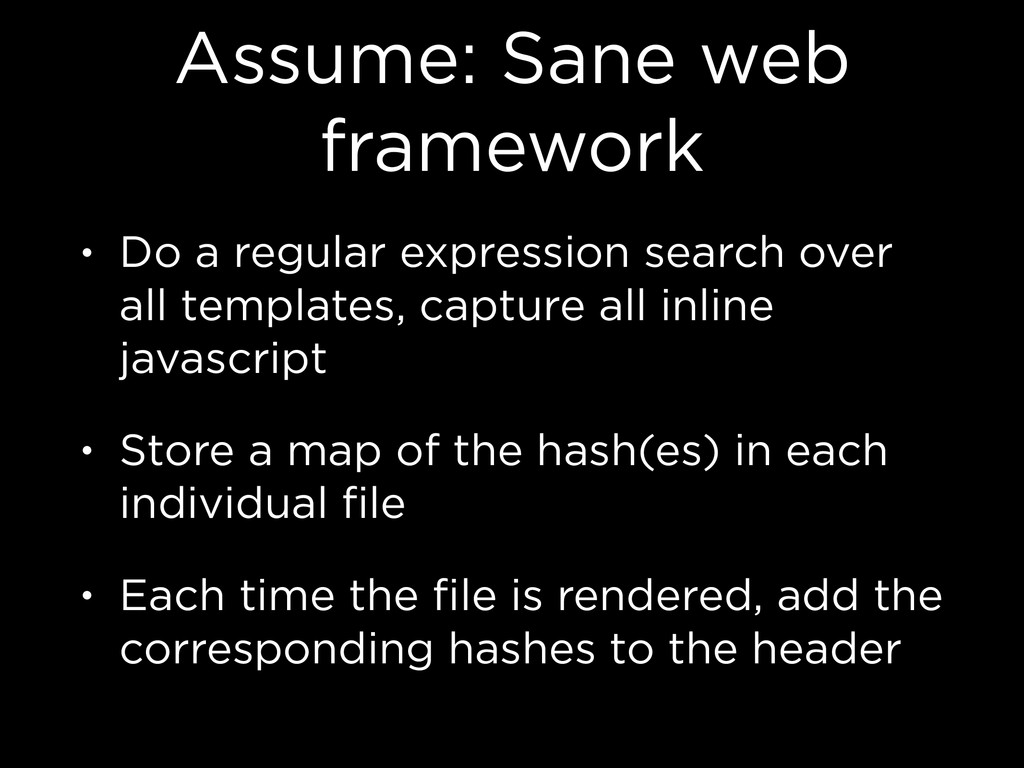
Assume: Sane web framework • Do a regular expression search
over all templates, capture all inline javascript • Store a map of the hash(es) in each individual file • Each time the file is rendered, add the corresponding hashes to the header
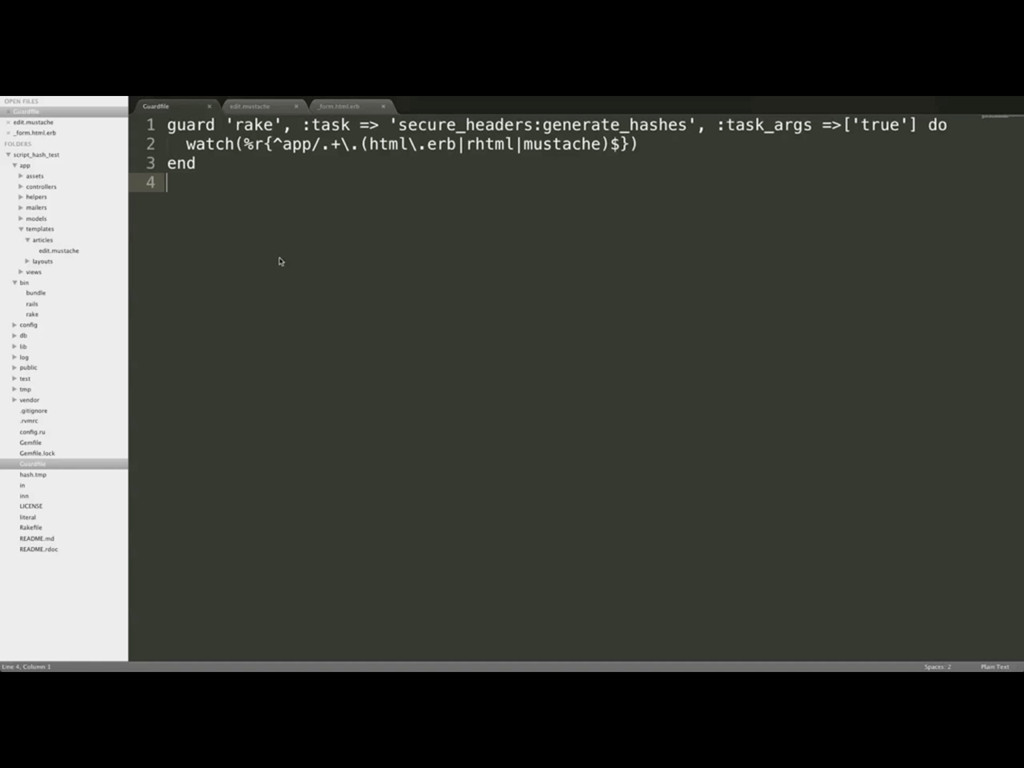
Developer productivity • Serve dynamic hash values in (!production), serve
hardcoded hash values in production
None


 oreoshake
 iwatsukayura
 simas
 guaca
 exoego
 mixplace
 tosite
 bicstone
 sylph01
 cclai999
 jame2408
 t0yohei
 sorah
 holman
 bcantrill
 codingconduct
 orderedlist
 badams
 mfonobong
 mkilby
 szymonslowik
 rkendrick25
 rakko
 schroneko
 chrislema
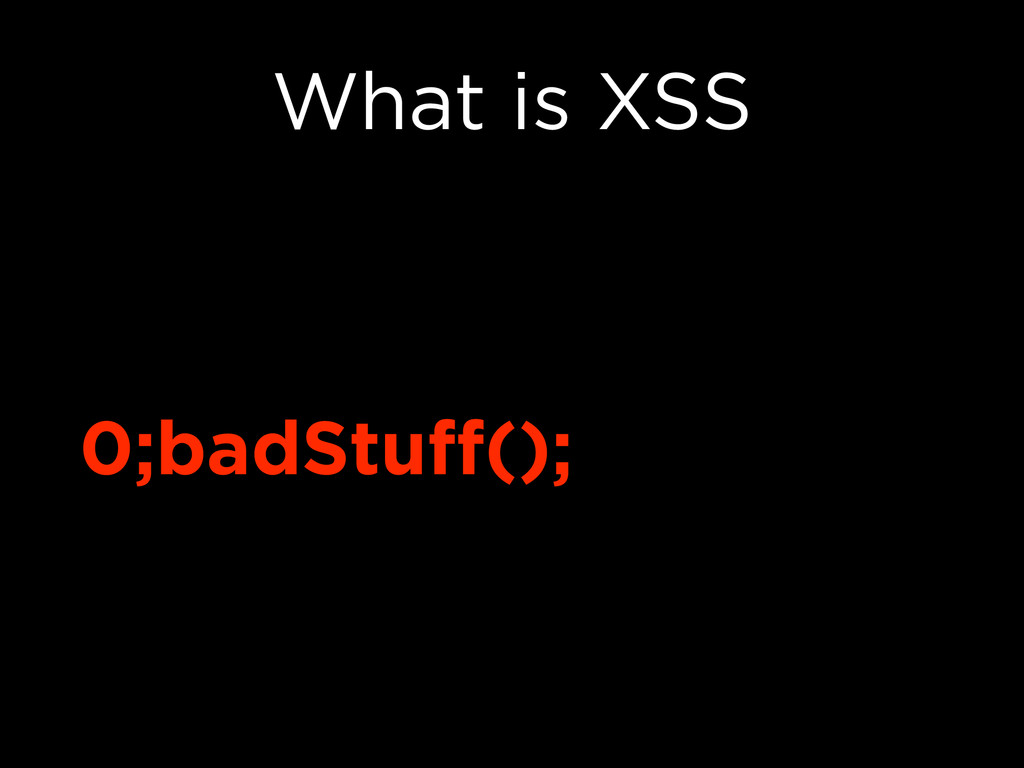

![JSFuck - Write any JavaScript with 6 Characters: []()!+ I](https://files.speakerdeck.com/presentations/7e4273001cff0132ff4412198c64cd5d/slide_39.jpg)