Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Frog and Toad Learn Django Security
Search
Philip James
July 20, 2016
Technology
180
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Frog and Toad Learn Django Security
Talk given at DjangoCon US 2016
Philip James
July 20, 2016
More Decks by Philip James
See All by Philip James
3 (or whatever) ways to put something on the internet
phildini
0
20
Frog and Toad Learn about Django Security - NBT6
phildini
0
41
The Elephant and the Serpent (PyLatam 2019)
phildini
0
83
Account Security for the Fashionable App Developer
phildini
1
80
All in the Timing: Side-Channel Attacks
phildini
0
94
Giving Thanks
phildini
0
58
All in the Timing: Side-Channel Attacks in Python
phildini
0
440
API-Driven Django
phildini
1
460
Type uWSGI; Press Enter; What Happens?
phildini
0
120
Other Decks in Technology
See All in Technology
AIで選択肢が広がった組織設計の理想と現実
konifar
16
7.5k
慶應義塾大学 AI実践05 論文執筆の仕組み化
keio_smilab
PRO
6
3.5k
Copilot Coworkで「みのるん式」やってみた
minorun365
PRO
2
1.3k
AX時代の自治体支援リソース再配分と役割分担の再構成:戦略とロードマップ(概要)
sishi2026
0
180
FinOpsを導入してマルチプロダクトのコスト最適化を実現する
kworkdev
PRO
0
110
20261031_IoTLT_vol140_kitazaki_v1.pdf
kitazaki
0
160
SLOを阻む不安
sraku2159
0
210
Don't write the architecture only in the prompt.
neohsu
0
300
E2Eってつらくないですか?E2Eの管理コストを下げる手段とその実践
akaboshinit
6
2.9k
You Have Agency(サンキュー、Ruby)
snoozer05
PRO
5
660
cdk deployとcdkd deploy、実際にデプロイして5倍速近くの差を実測した
yama3133
1
160
AIエージェント統制はAPIから——押さえるべき5つの要素
nagix
0
120
Featured
See All Featured
Mozcon NYC 2025: Stop Losing SEO Traffic
samtorres
1
600
The Myth of the Modular Monolith - Day 2 Keynote - Rails World 2024
eileencodes
28
3.7k
My Coaching Mixtape
mlcsv
0
380
Taking LLMs out of the black box: A practical guide to human-in-the-loop distillation
inesmontani
PRO
3
2.5k
Bootstrapping a Software Product
garrettdimon
PRO
306
120k
技術選定の審美眼(2025年版) / Understanding the Spiral of Technologies 2025 edition
twada
PRO
120
120k
The MySQL Ecosystem @ GitHub 2015
samlambert
251
13k
The Director’s Chair: Orchestrating AI for Truly Effective Learning
tmiket
1
350
BBQ
matthewcrist
90
10k
Stop Working from a Prison Cell
hatefulcrawdad
274
21k
Side Projects
sachag
456
43k
Writing Fast Ruby
sferik
630
63k
Transcript
@phildini #djangotoad Frog and Toad Learn Django Security
@phildini #djangotoad I have this great idea for a startup!
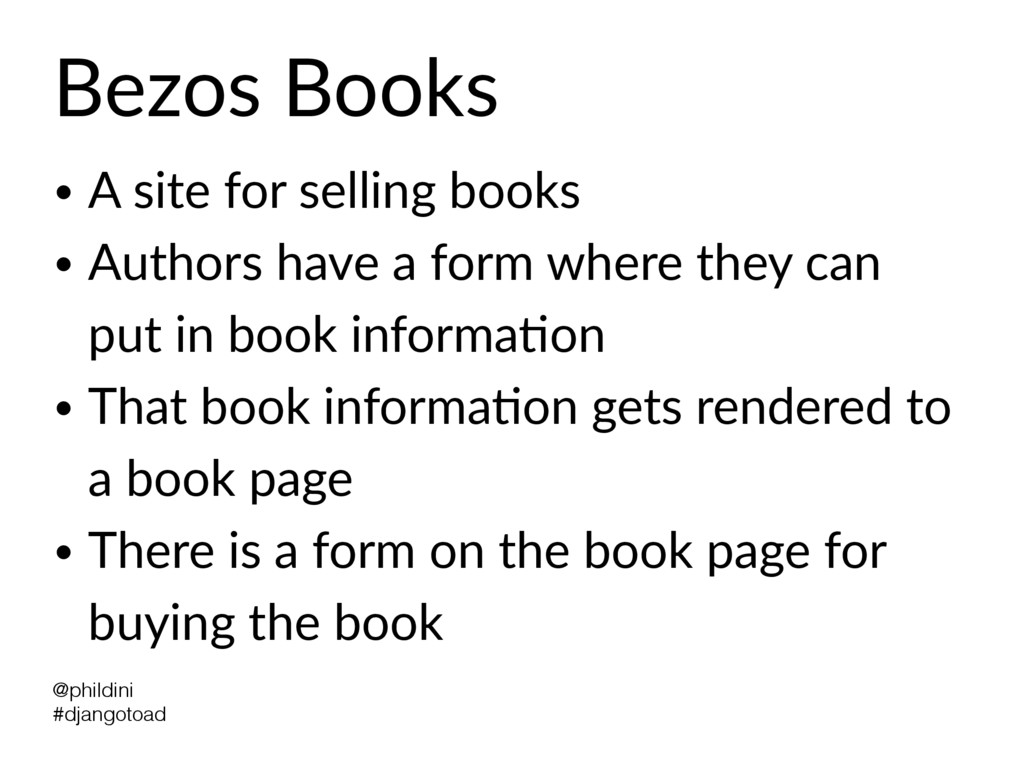
@phildini #djangotoad Bezos Books • A site for selling books
• Authors have a form where they can put in book informaDon • That book informaDon gets rendered to a book page • There is a form on the book page for buying the book
@phildini #djangotoad Django!
@phildini #djangotoad SECURITY?!?
@phildini #djangotoad XSS Cross-Site ScripDng
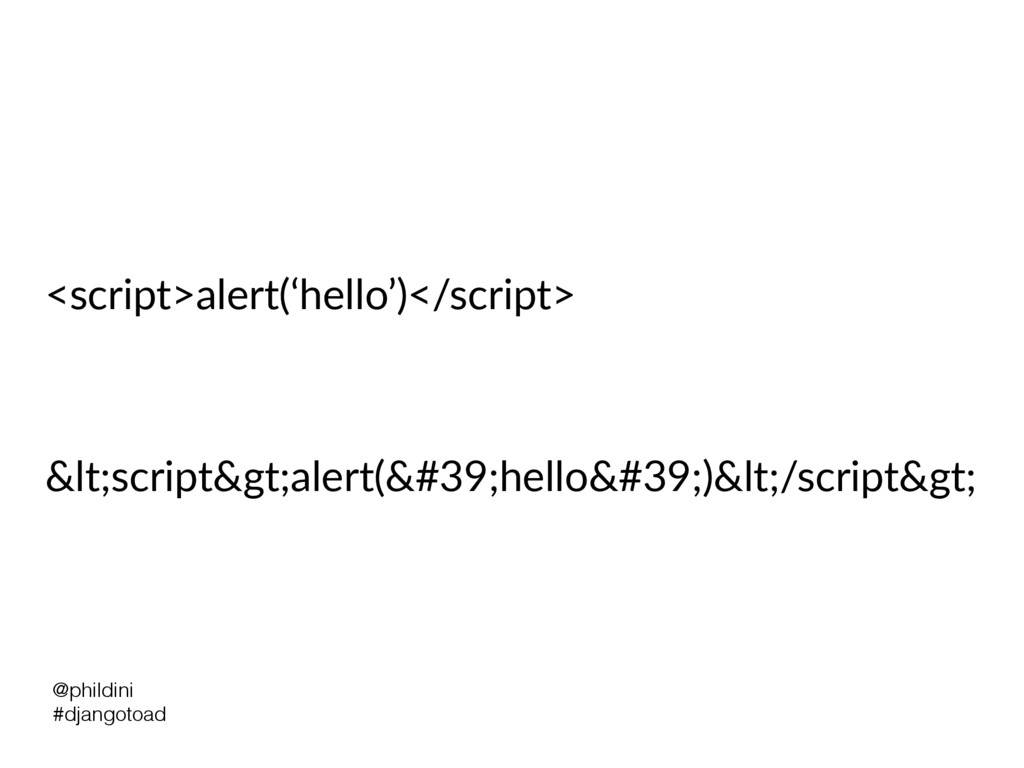
@phildini #djangotoad <script>alert(‘hello’)</script> <script>alert('hello')</script>
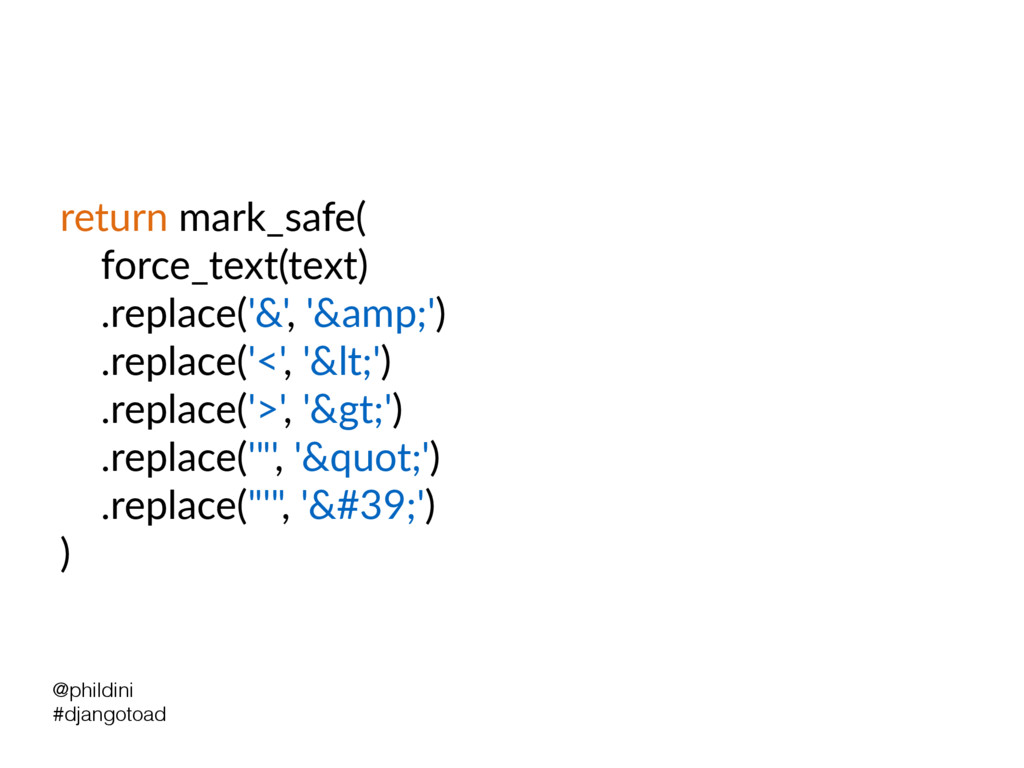
@phildini #djangotoad return mark_safe( force_text(text) .replace('&', '&') .replace('<', '<') .replace('>',
'>') .replace('"', '"') .replace("'", ''') )
@phildini #djangotoad django.uDls.html https://github.com/django/django/blob/master/django/utils/html.py#L47
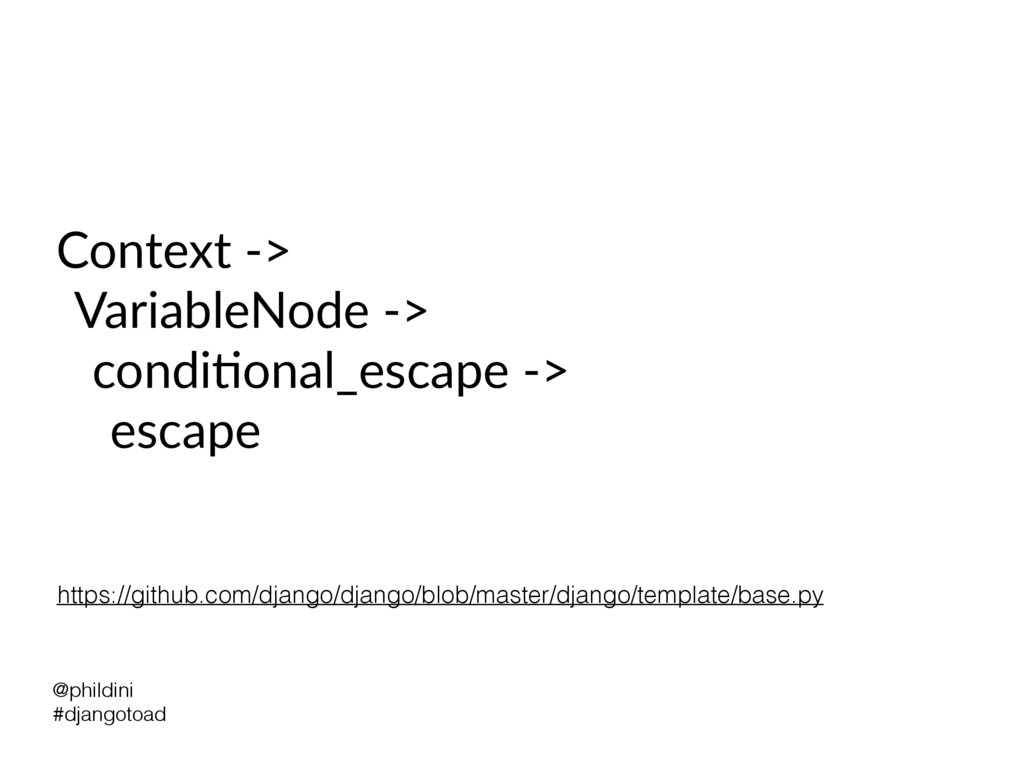
@phildini #djangotoad Context -> VariableNode -> condiDonal_escape -> escape https://github.com/django/django/blob/master/django/template/base.py
@phildini #djangotoad mark_safe(), | n, | safe
@phildini #djangotoad CSRF Cross-Site Request Forgery
@phildini #djangotoad CsrfViewMiddleware https://github.com/django/django/blob/master/django/middleware/csrf.py
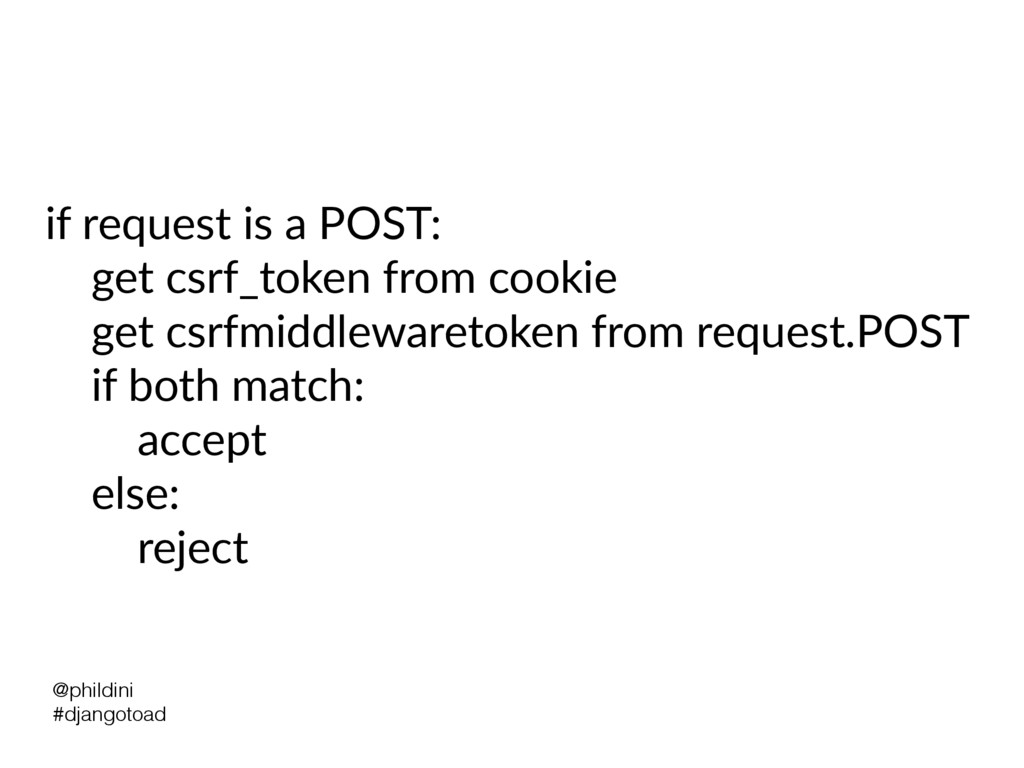
@phildini #djangotoad if request is a POST: get csrf_token from
cookie get csrfmiddlewaretoken from request.POST if both match: accept else: reject
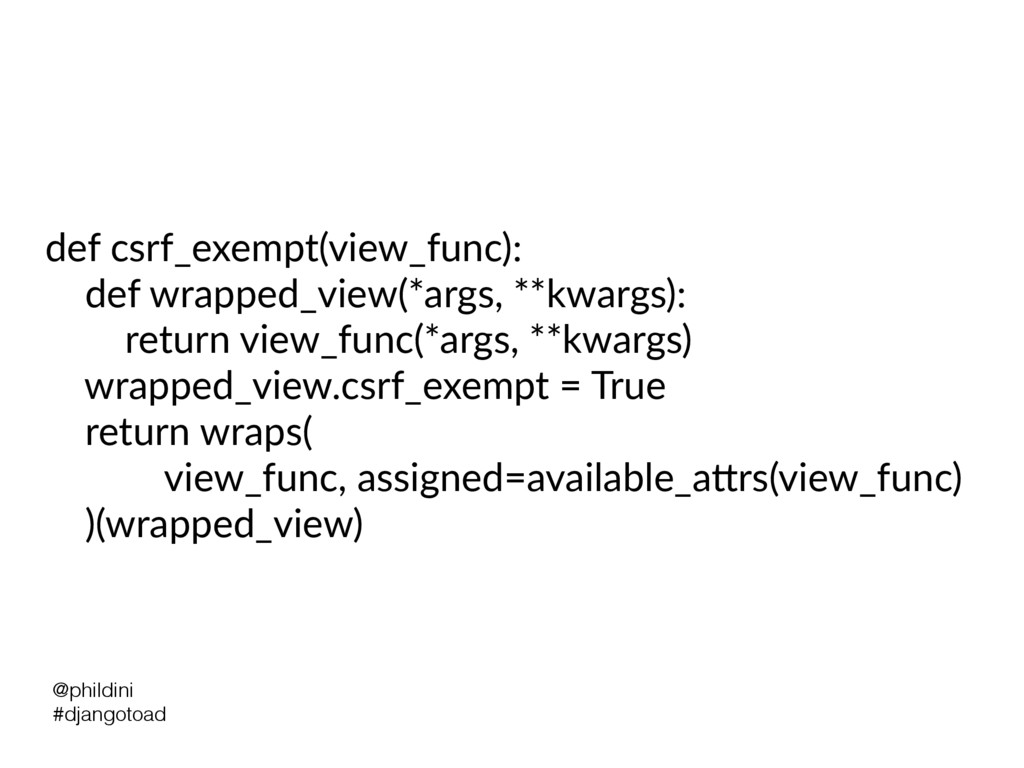
@phildini #djangotoad def csrf_exempt(view_func): def wrapped_view(*args, **kwargs): return view_func(*args, **kwargs)
wrapped_view.csrf_exempt = True return wraps( view_func, assigned=available_airs(view_func) )(wrapped_view)
@phildini #djangotoad django.views.decorators.csrf.csrf_exempt
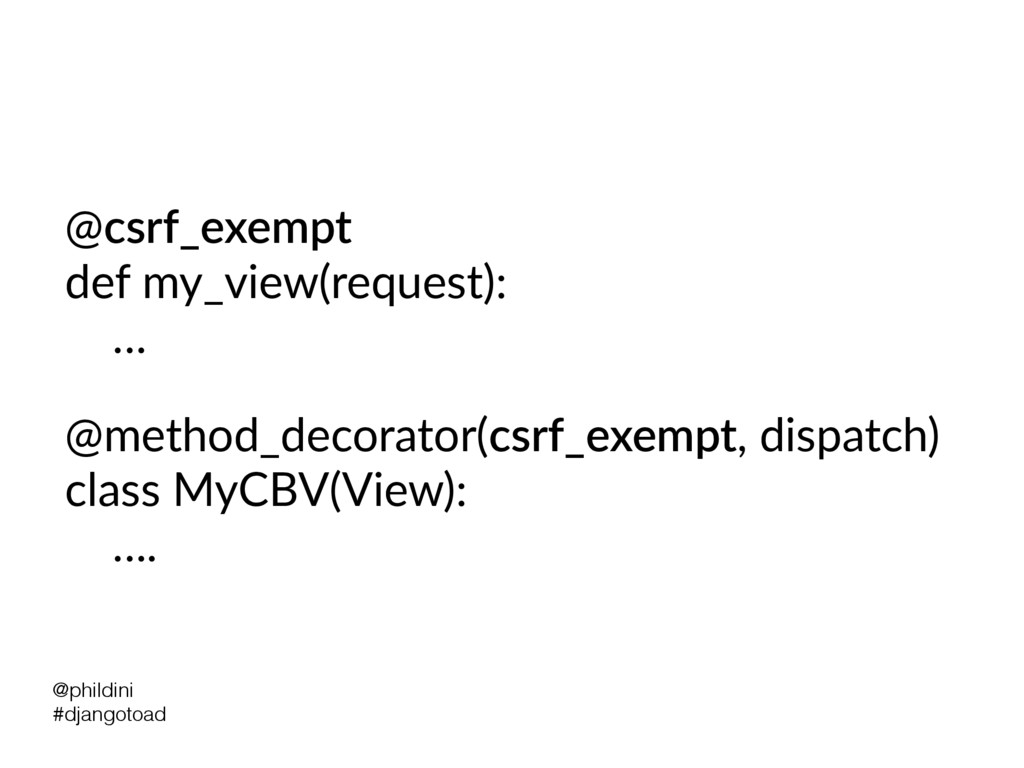
@phildini #djangotoad @csrf_exempt def my_view(request): … @method_decorator(csrf_exempt, dispatch) class MyCBV(View):
….
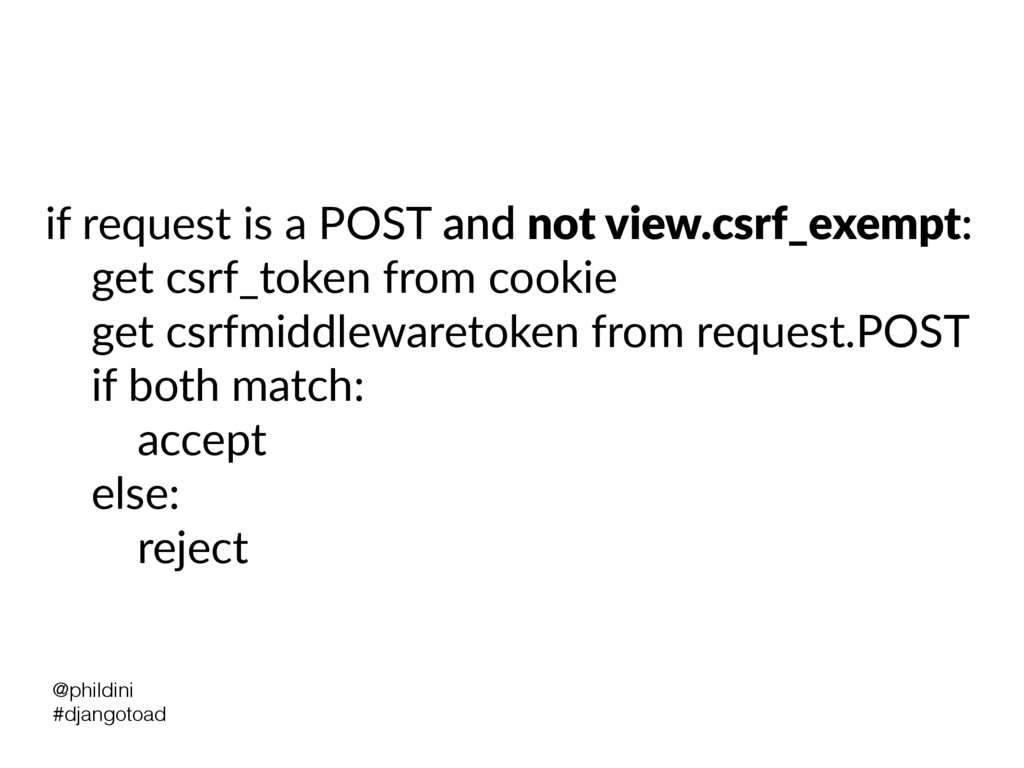
@phildini #djangotoad if request is a POST and not view.csrf_exempt:
get csrf_token from cookie get csrfmiddlewaretoken from request.POST if both match: accept else: reject
@phildini #djangotoad Cookies
@phildini #djangotoad SQLi SQL InjecDon
@phildini #djangotoad [This Slide IntenDonally Len Blank]
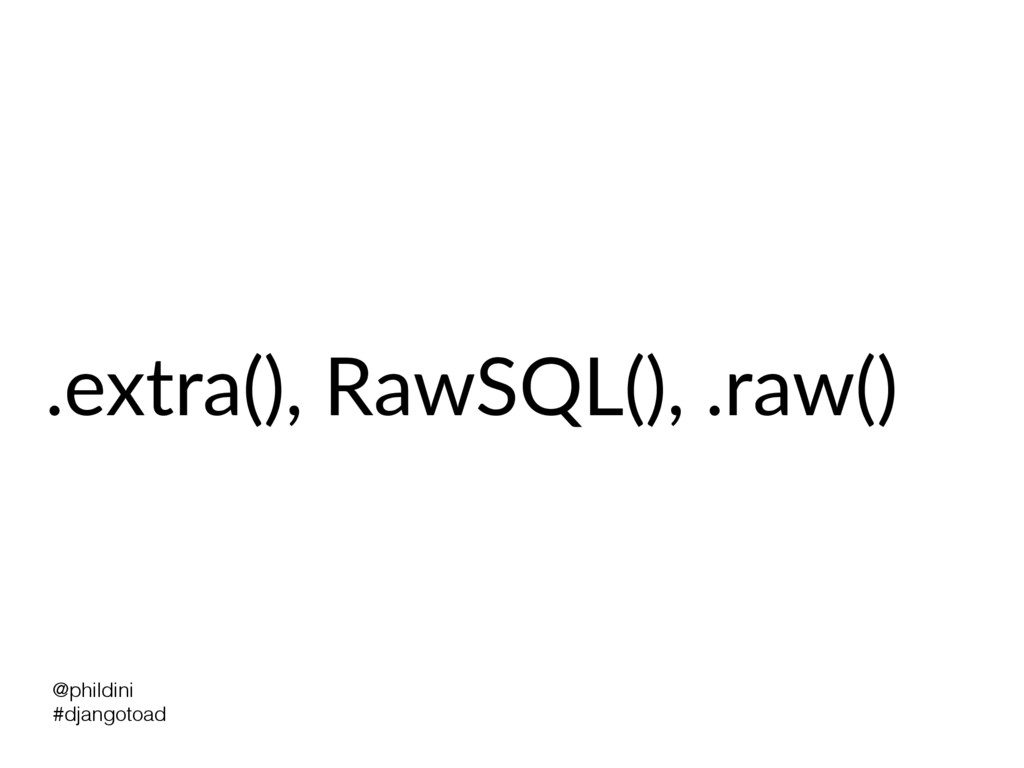
@phildini #djangotoad .extra(), RawSQL(), .raw()
@phildini #djangotoad Clickjacking
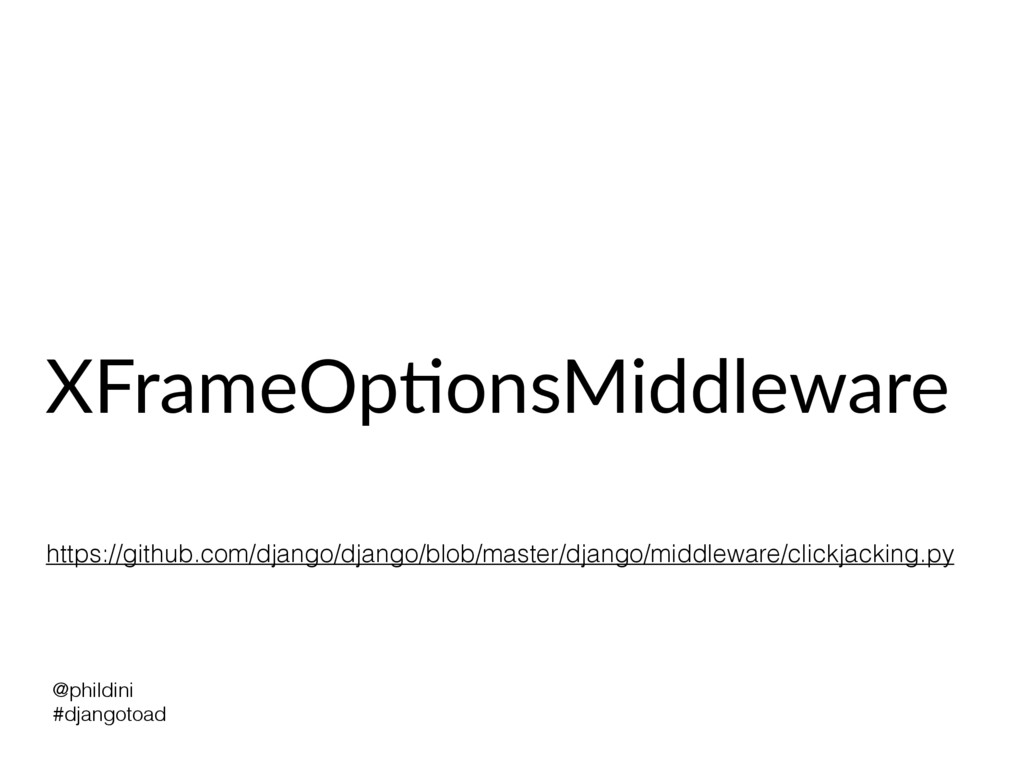
@phildini #djangotoad XFrameOpDonsMiddleware https://github.com/django/django/blob/master/django/middleware/clickjacking.py
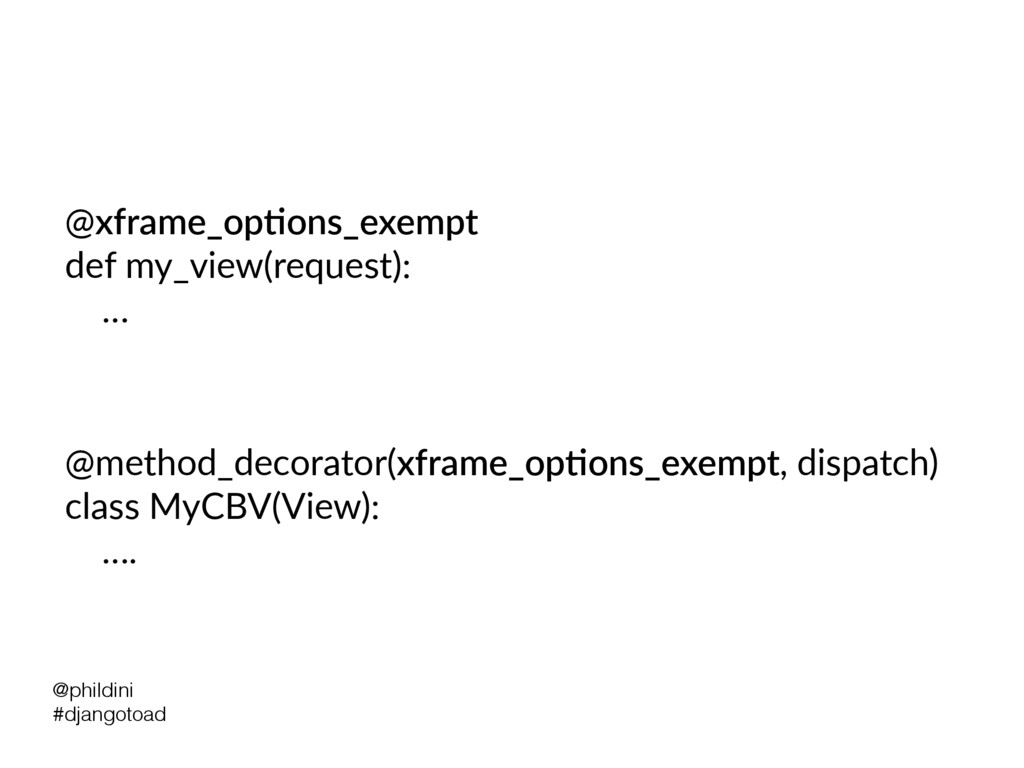
@phildini #djangotoad @xframe_op1ons_exempt def my_view(request): … @method_decorator(xframe_op1ons_exempt, dispatch) class MyCBV(View):
….
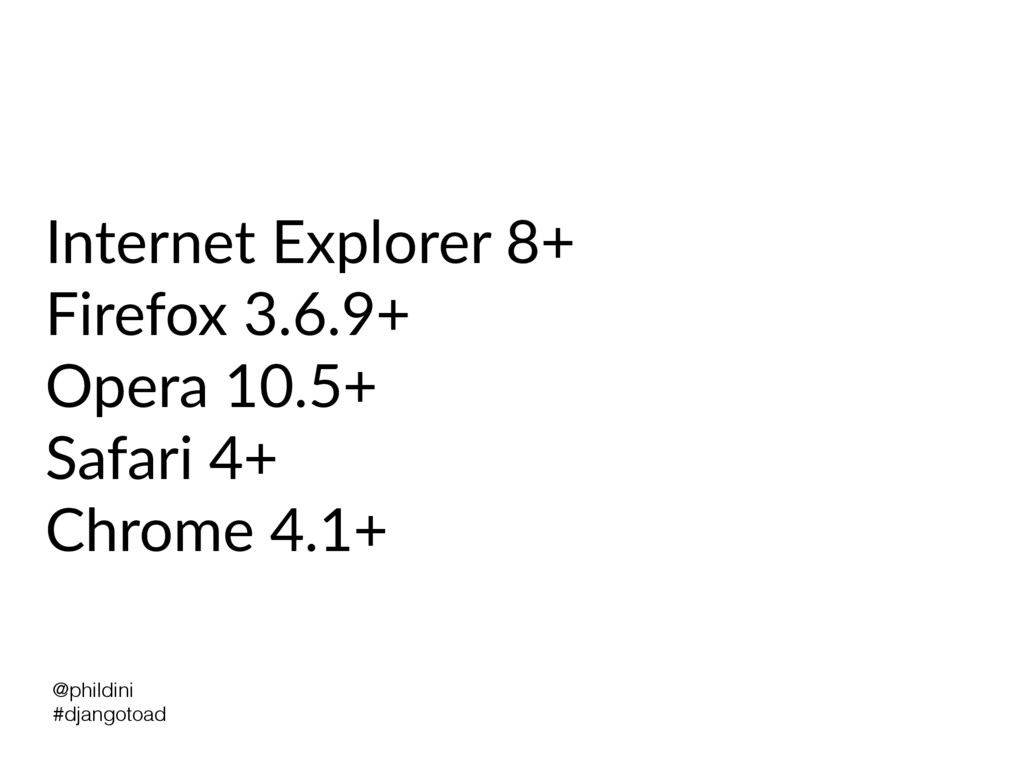
@phildini #djangotoad Internet Explorer 8+ Firefox 3.6.9+ Opera 10.5+ Safari
4+ Chrome 4.1+
@phildini #djangotoad Host Header ValidaDon
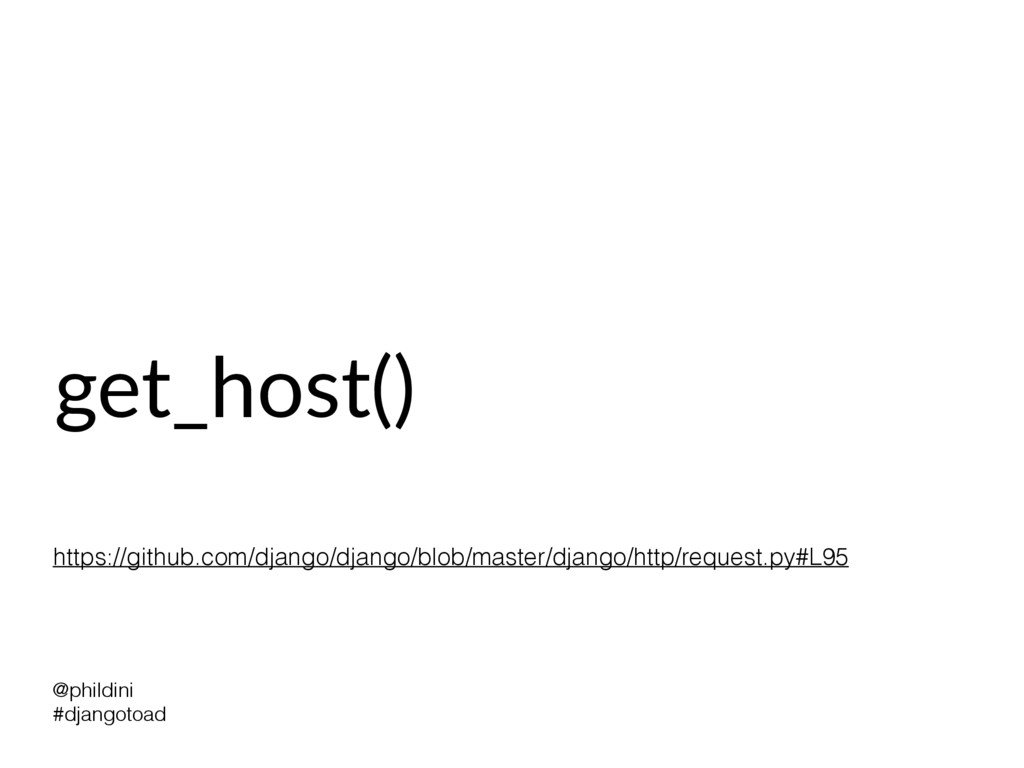
@phildini #djangotoad get_host() https://github.com/django/django/blob/master/django/http/request.py#L95
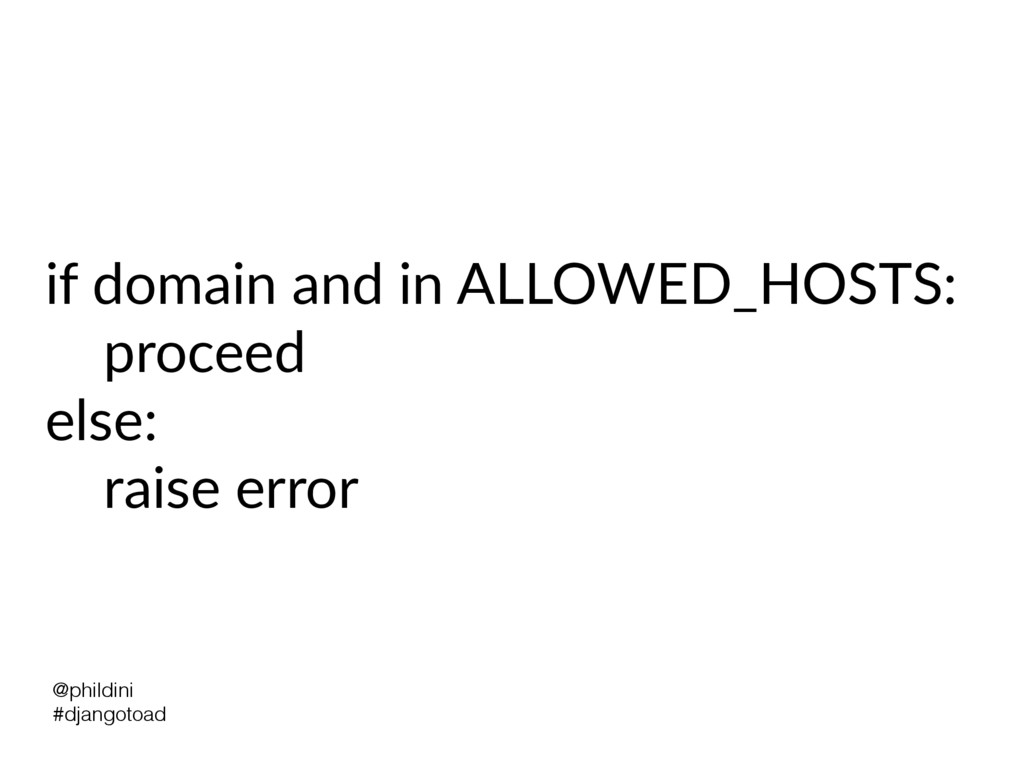
@phildini #djangotoad if domain and in ALLOWED_HOSTS: proceed else: raise
error
@phildini #djangotoad Passwords
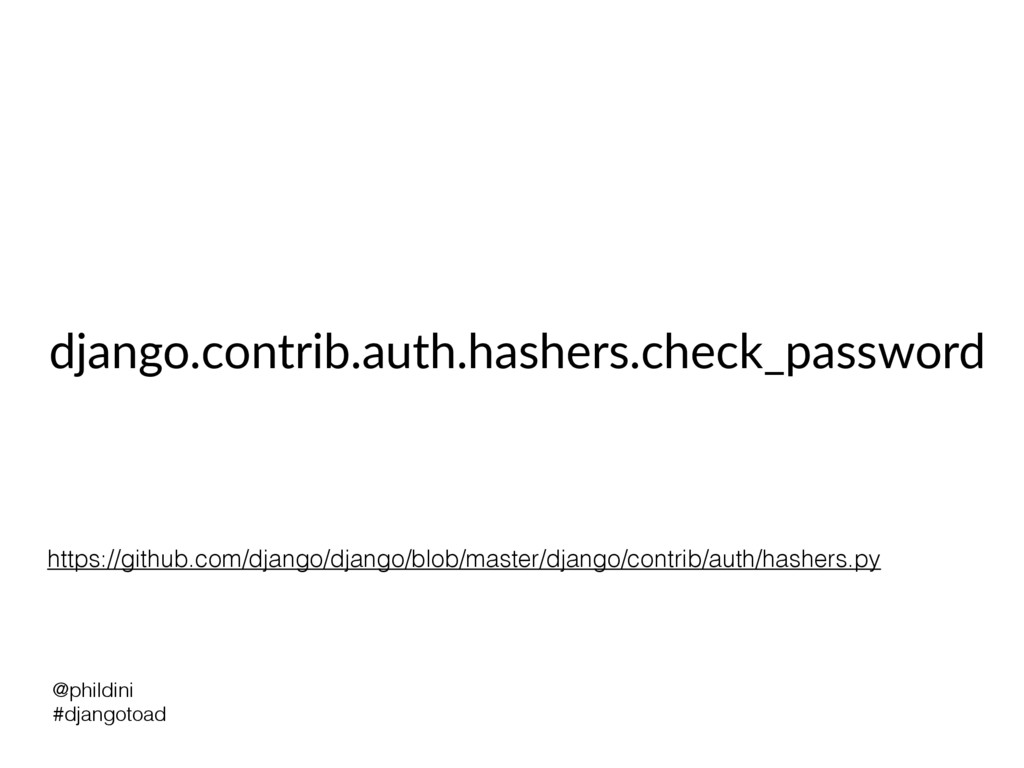
@phildini #djangotoad django.contrib.auth.hashers.check_password https://github.com/django/django/blob/master/django/contrib/auth/hashers.py
@phildini #djangotoad How do we make this beier?
@phildini #djangotoad Constant Vigilance!
@phildini #djangotoad HTTPS
@phildini #djangotoad CSP ReporDng Content Security Policy
@phildini #djangotoad django_encrypted_fields hips:/ /github.com/defrex/django-encrypted-fields
@phildini #djangotoad django-secure hip:/ /django-secure.readthedocs.org/en/v0.1.2/
@phildini #djangotoad Pony Checkup hips:/ /www.ponycheckup.com/
@phildini #djangotoad Making Django Ridiculously Secure hip:/ /nerd.kelseyinnis.com/blog/2015/09/08/making-django-really-really-ridiculously-secure/
@phildini #djangotoad
@phildini #djangotoad The End. Philip James @phildini hip:/ /bit.ly/djangotoad


 phildini
 konifar
 keio_smilab
 minorun365
 sishi2026
 kworkdev
 kitazaki
 sraku2159
 neohsu
 akaboshinit
 snoozer05
 yama3133
 nagix
 samtorres
 eileencodes
 mlcsv
 inesmontani
 garrettdimon
 twada
 samlambert
 tmiket
 matthewcrist
 hatefulcrawdad
 sachag
 sferik