Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Frog and Toad Learn about Django Security - NBT6
Search
Philip James
December 17, 2021
Technology
41
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Frog and Toad Learn about Django Security - NBT6
Philip James
December 17, 2021
More Decks by Philip James
See All by Philip James
3 (or whatever) ways to put something on the internet
phildini
0
24
The Elephant and the Serpent (PyLatam 2019)
phildini
0
83
Account Security for the Fashionable App Developer
phildini
1
83
All in the Timing: Side-Channel Attacks
phildini
0
94
Giving Thanks
phildini
0
58
All in the Timing: Side-Channel Attacks in Python
phildini
0
440
API-Driven Django
phildini
1
460
Type uWSGI; Press Enter; What Happens?
phildini
0
120
Type uWSGI; Press Enter; What Happens?
phildini
1
110
Other Decks in Technology
See All in Technology
BALLAS Technology Deck
ballas_inc
0
260
[General] 개발자로 해외 기업에서 일하기
skydoves
1
310
HQ駆動開発で最高のAI-Contextを作ろう
sansantech
PRO
1
110
コードレビューをなくして見えたもの
henteko
0
140
AI Agent 時代のデータ基盤: ClickHouse で実現する 超高速分析とコスト削減の両立
jozono
0
210
ゼロから作るWebアプリの新定番!?Amplify Gen 2 × AWS Blocksで実現する「開発速度とRDBの柔軟性のいいとこ取り」
amixedcolor
1
180
AX時代の自治体支援リソース再配分と役割分担の再構成:戦略とロードマップ(概要)
sishi2026
0
200
サボる子はいねぇがー!AgentCoreハーネスの脆弱性に学ぶ、エージェントの入力バリデーション
iwamot
PRO
5
310
PostgreSQL オプティマイザ統計の秘密
nori_shinoda
0
420
Content Mapper APIの応用例~CSS Modules、言語ファイル~
uhyo
2
620
自律的なチームを作るためにTechPMがやらないこと
ny7760
1
530
Lint の層を組み直した話
bengo4com
3
330
Featured
See All Featured
The Success of Rails: Ensuring Growth for the Next 100 Years
eileencodes
47
8.4k
Bootstrapping a Software Product
garrettdimon
PRO
306
120k
The Cult of Friendly URLs
andyhume
79
7.1k
Amusing Abliteration
ianozsvald
1
380
Information Architects: The Missing Link in Design Systems
soysaucechin
1
1.3k
How to optimise 3,500 product descriptions for ecommerce in one day using ChatGPT
katarinadahlin
PRO
3
3.9k
The Curse of the Amulet
leimatthew05
3
17k
ReactJS: Keep Simple. Everything can be a component!
pedronauck
666
130k
The AI Search Optimization Roadmap by Aleyda Solis
aleyda
2
6.4k
Are puppies a ranking factor?
jonoalderson
2
4.2k
The Organizational Zoo: Understanding Human Behavior Agility Through Metaphoric Constructive Conversations (based on the works of Arthur Shelley, Ph.D)
kimpetersen
PRO
0
530
The AI Revolution Will Not Be Monopolized: How open-source beats economies of scale, even for LLMs
inesmontani
PRO
3
3.8k
Transcript
@phildini #nbt6 Frog and Toad Learn Django Security
@phildini #nbt6 I have this great idea for a startup!
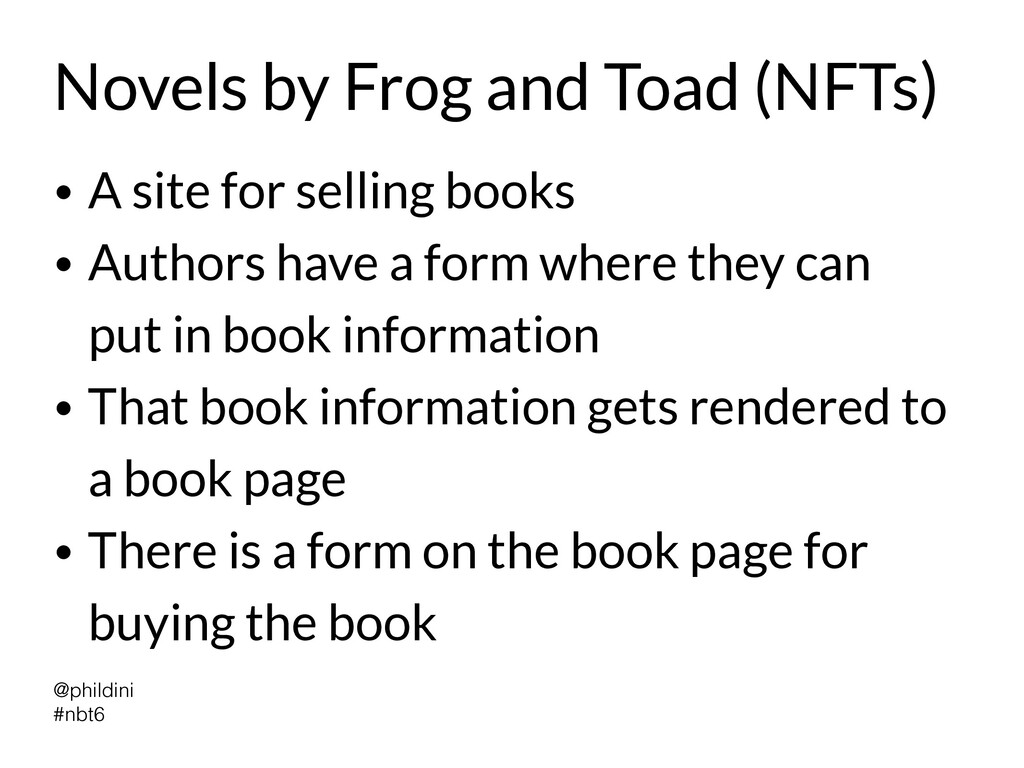
@phildini #nbt6 Novels by Frog and Toad (NFTs) • A
site for selling books • Authors have a form where they can put in book information • That book information gets rendered to a book page • There is a form on the book page for buying the book
@phildini #nbt6 Django!
@phildini #nbt6 SECURITY?!?
@phildini #nbt6 XSS Cross-Site Scripting
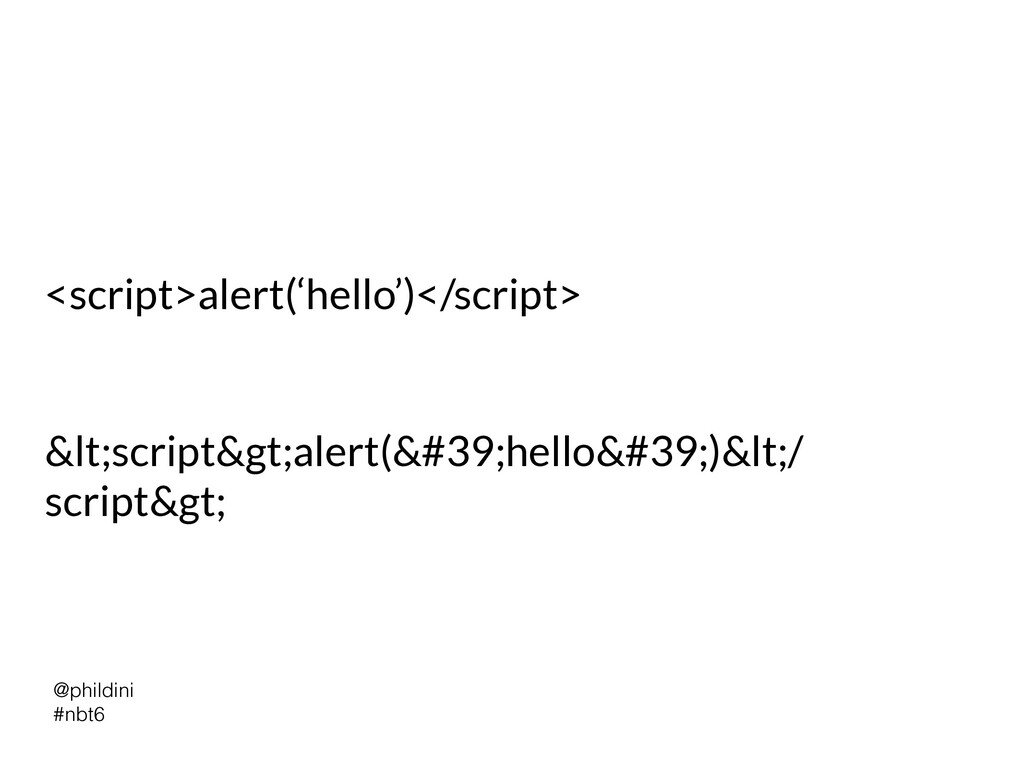
@phildini #nbt6 <script>alert(‘hello’)</script> <script>alert('hello')</ script>
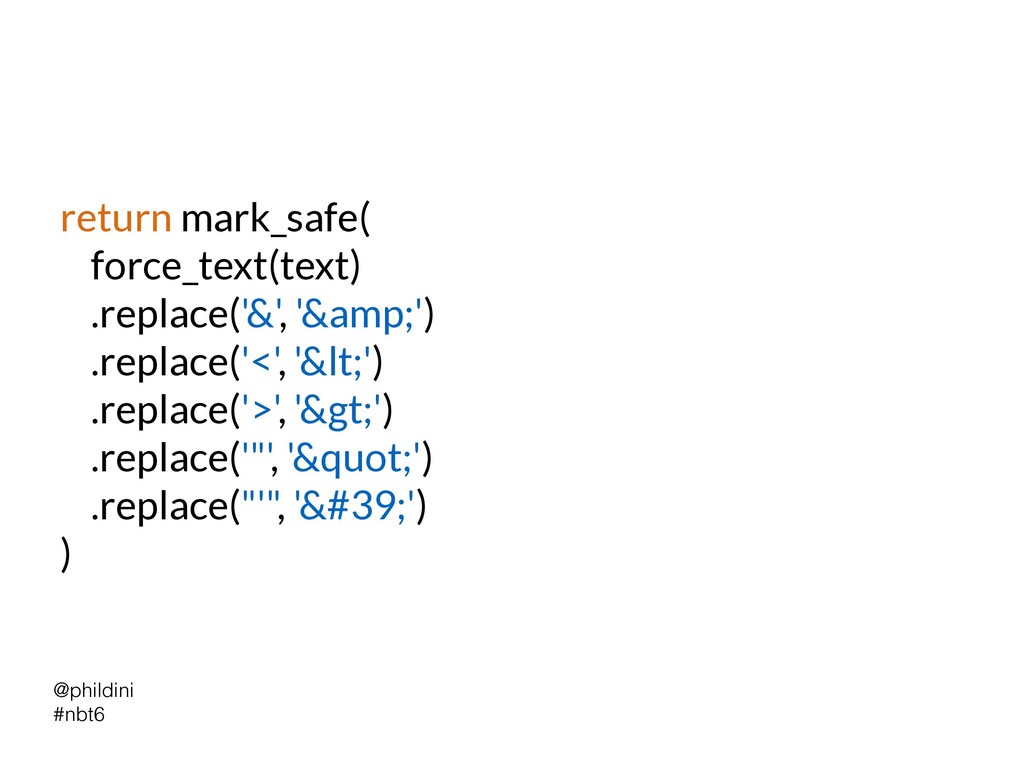
@phildini #nbt6 return mark_safe( force_text(text) .replace('&', '&') .replace('<', '<') .replace('>',
'>') .replace('"', '"') .replace("'", ''') )
@phildini #nbt6 django.utils.html https://github.com/django/django/blob/master/django/utils/html.py#L47
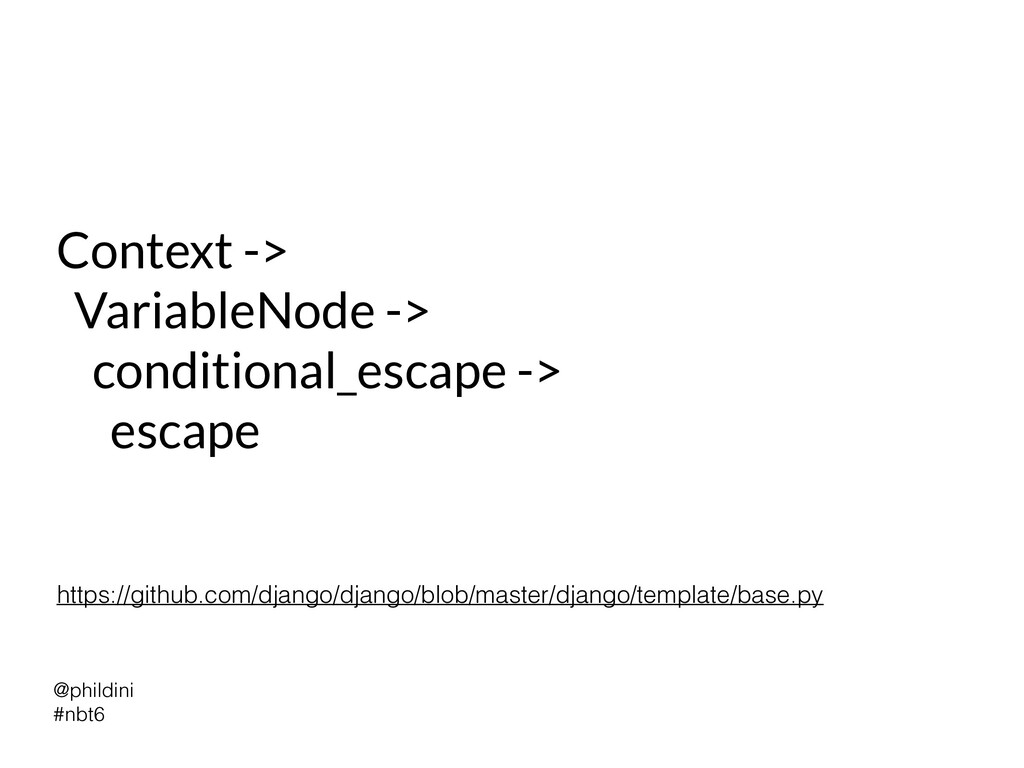
@phildini #nbt6 Context -> VariableNode -> conditional_escape -> escape https://github.com/django/django/blob/master/django/template/base.py
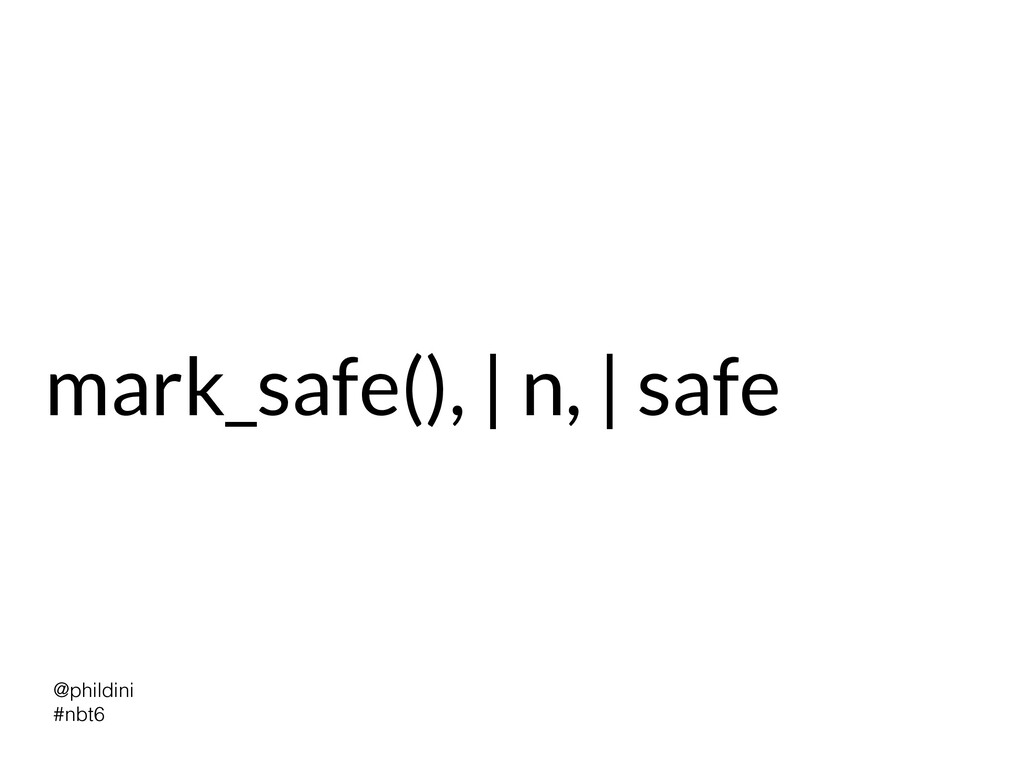
@phildini #nbt6 mark_safe(), | n, | safe
@phildini #nbt6 CSRF Cross-Site Request Forgery
@phildini #nbt6 CsrfViewMiddleware https://github.com/django/django/blob/master/django/middleware/csrf.py
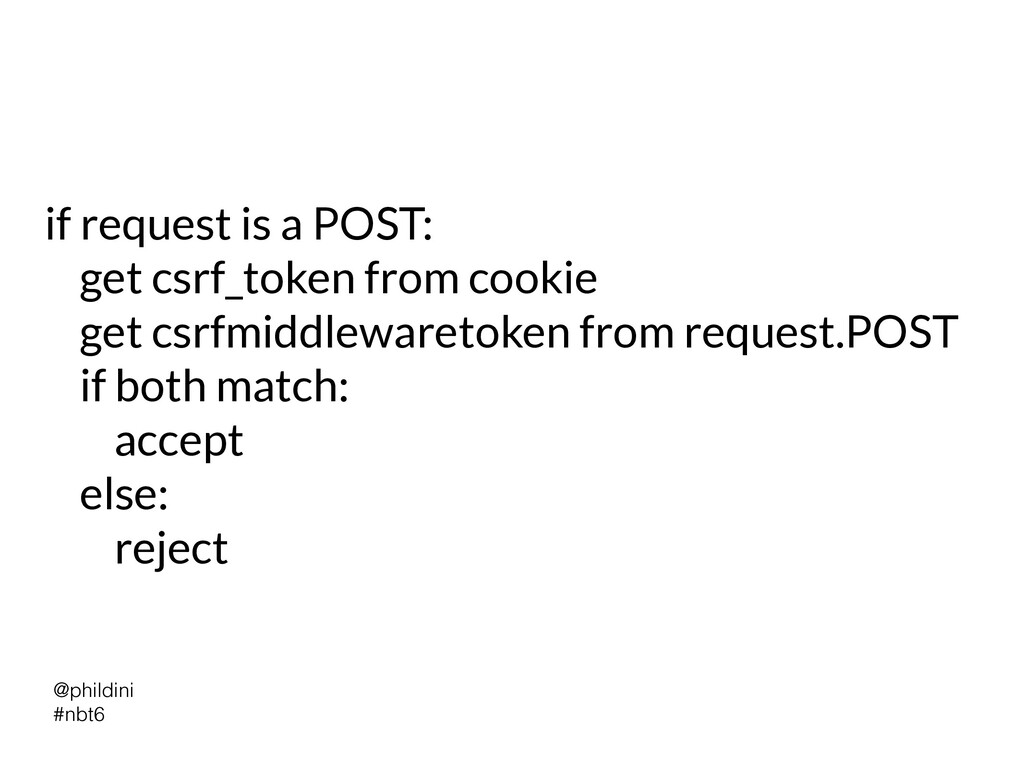
@phildini #nbt6 if request is a POST: get csrf_token from
cookie get csrfmiddlewaretoken from request.POST if both match: accept else: reject
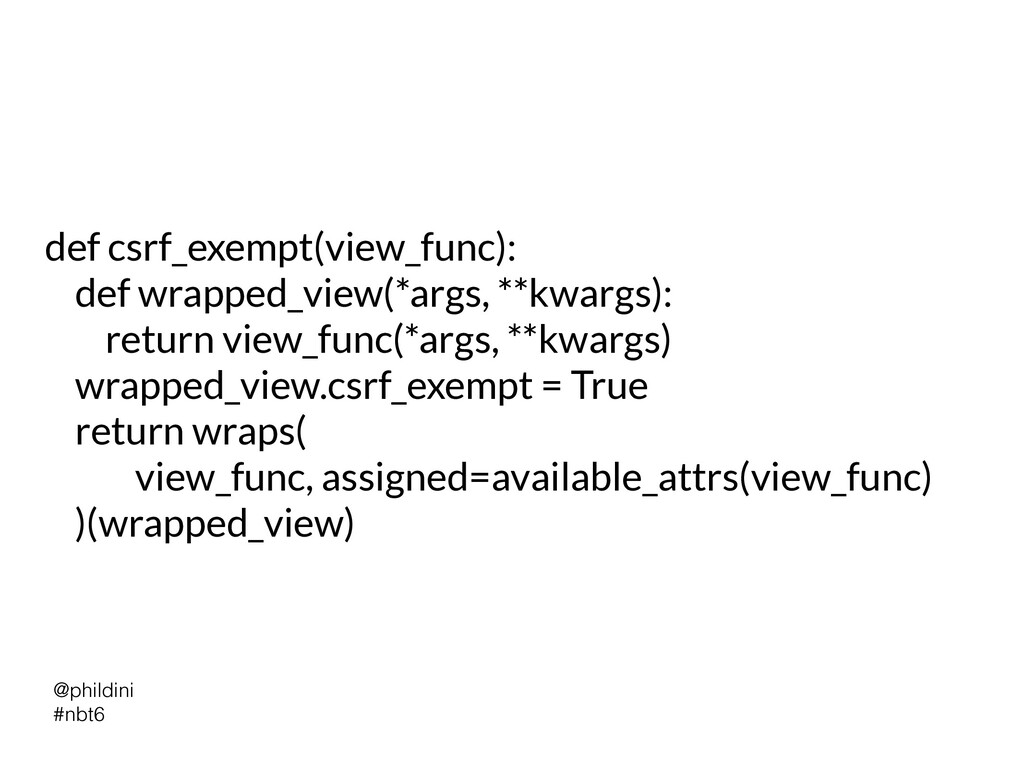
@phildini #nbt6 def csrf_exempt(view_func): def wrapped_view(*args, **kwargs): return view_func(*args, **kwargs)
wrapped_view.csrf_exempt = True return wraps( view_func, assigned=available_attrs(view_func) )(wrapped_view)
@phildini #nbt6 django.views.decorators.csrf.csrf_exempt
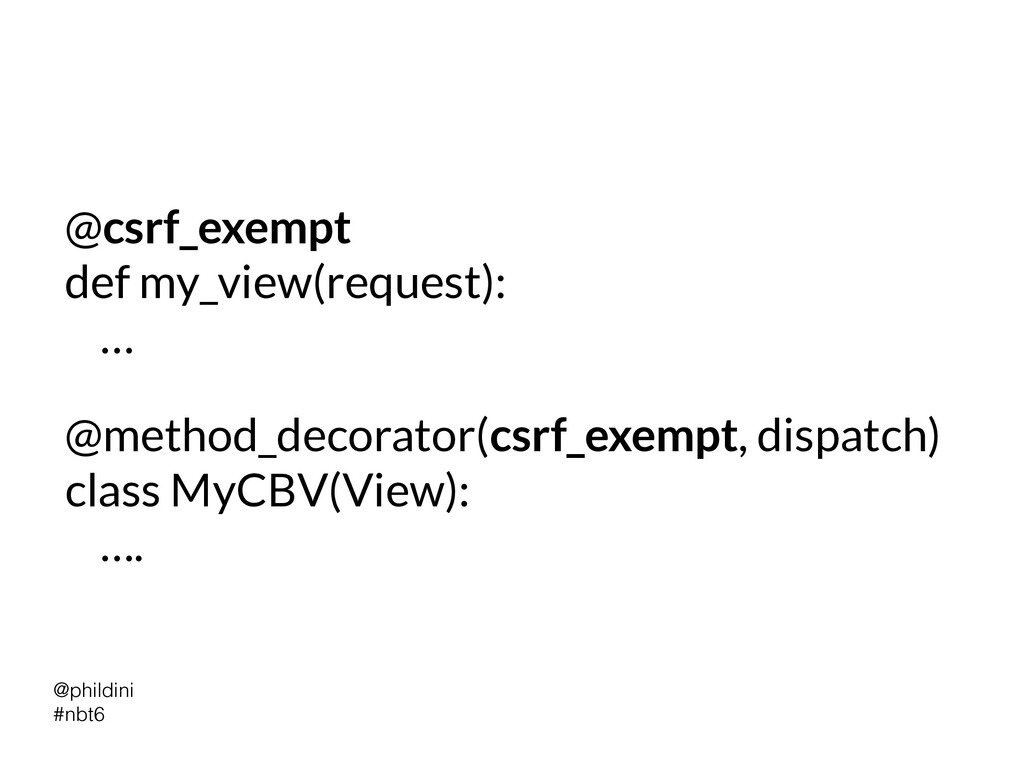
@phildini #nbt6 @csrf_exempt def my_view(request): … @method_decorator(csrf_exempt, dispatch) class MyCBV(View):
….
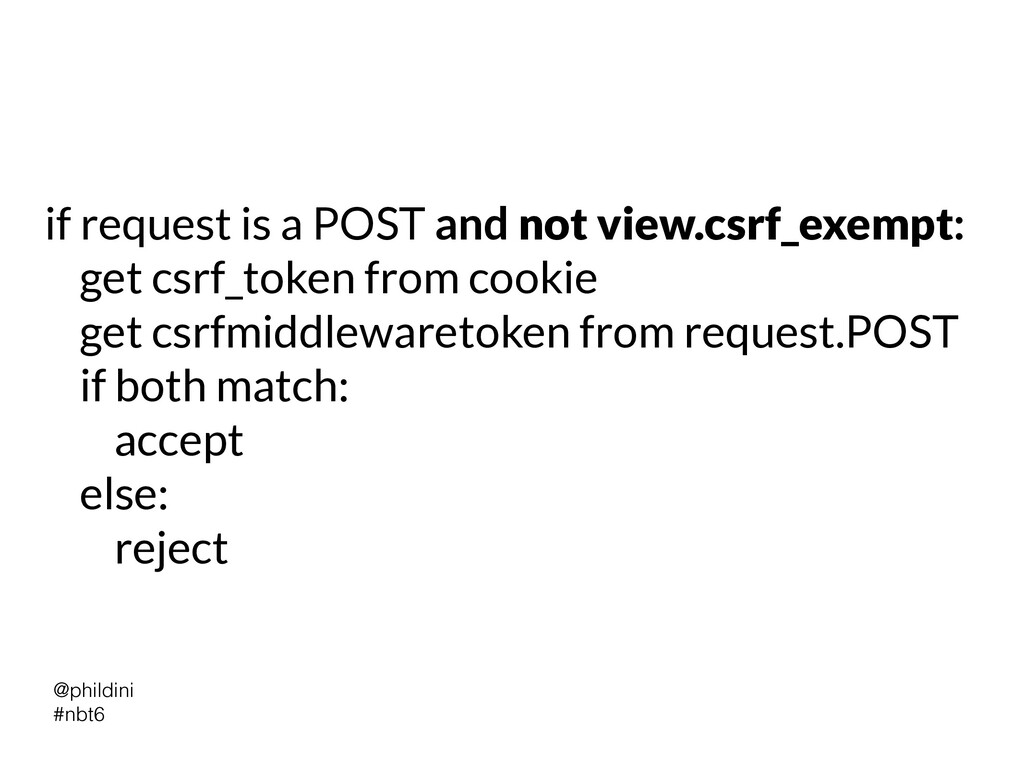
@phildini #nbt6 if request is a POST and not view.csrf_exempt:
get csrf_token from cookie get csrfmiddlewaretoken from request.POST if both match: accept else: reject
@phildini #nbt6 Cookies
@phildini #nbt6 SQLi SQL Injection
@phildini #nbt6 [This Slide Intentionally Left Blank]
@phildini #nbt6 .extra(), RawSQL(), .raw()
@phildini #nbt6 Clickjacking
@phildini #nbt6 XFrameOptionsMiddleware https://github.com/django/django/blob/master/django/middleware/clickjacking.py
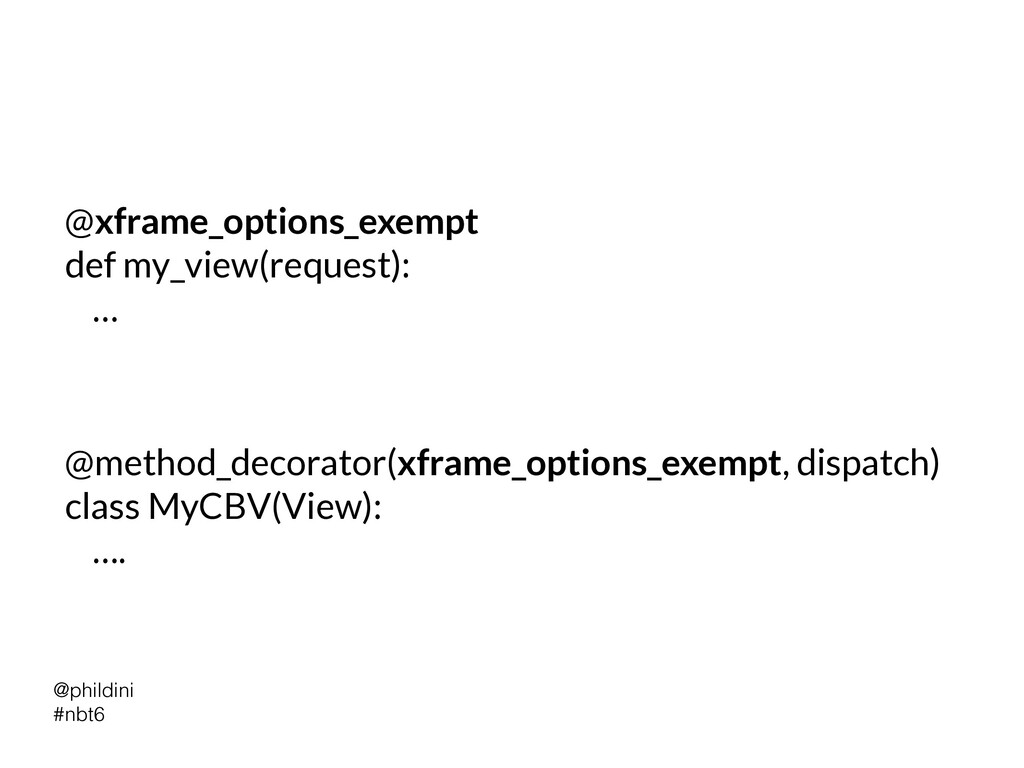
@phildini #nbt6 @xframe_options_exempt def my_view(request): … @method_decorator(xframe_options_exempt, dispatch) class MyCBV(View):
….
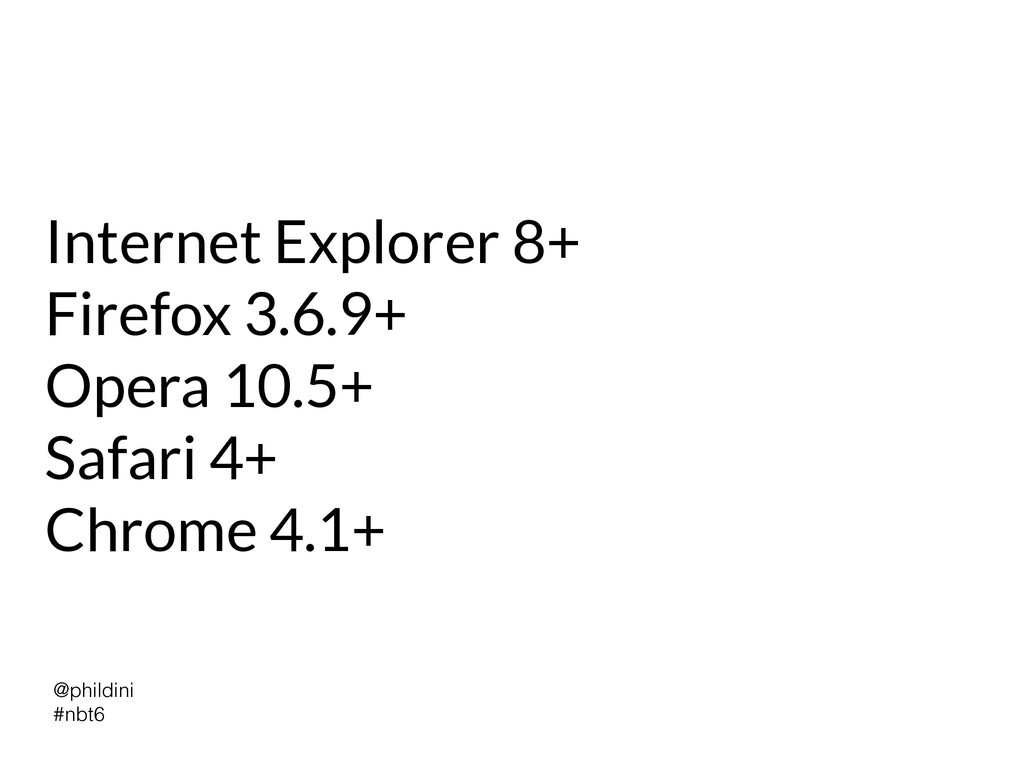
@phildini #nbt6 Internet Explorer 8+ Firefox 3.6.9+ Opera 10.5+ Safari
4+ Chrome 4.1+
@phildini #nbt6 Host Header Validation
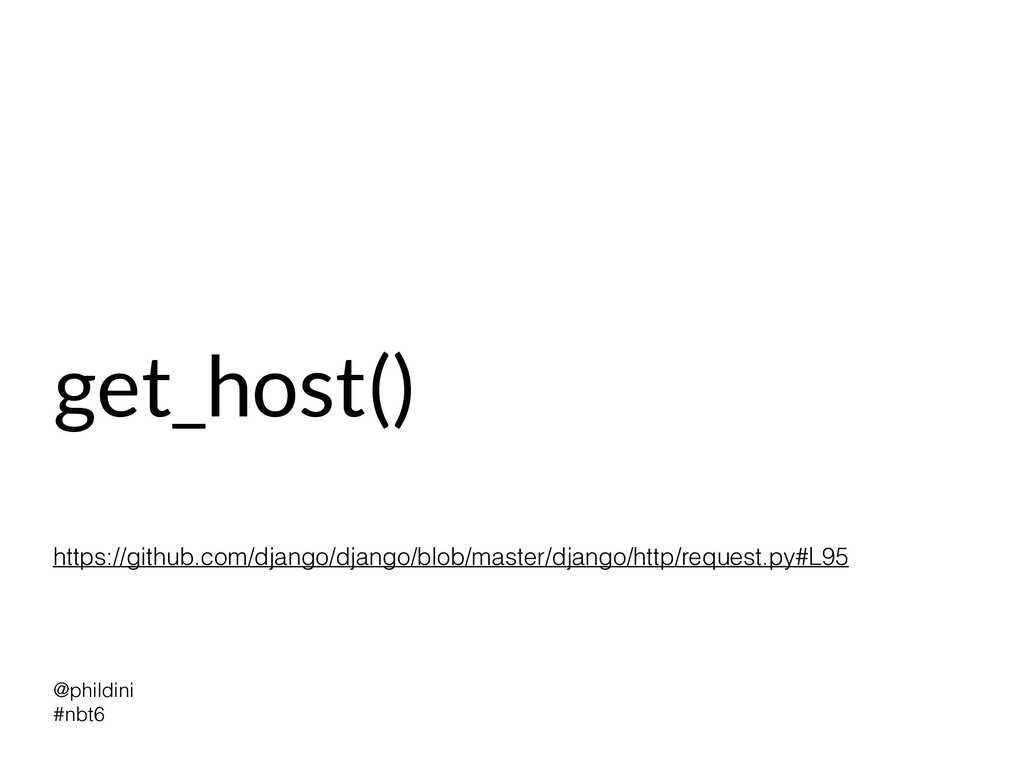
@phildini #nbt6 get_host() https://github.com/django/django/blob/master/django/http/request.py#L95
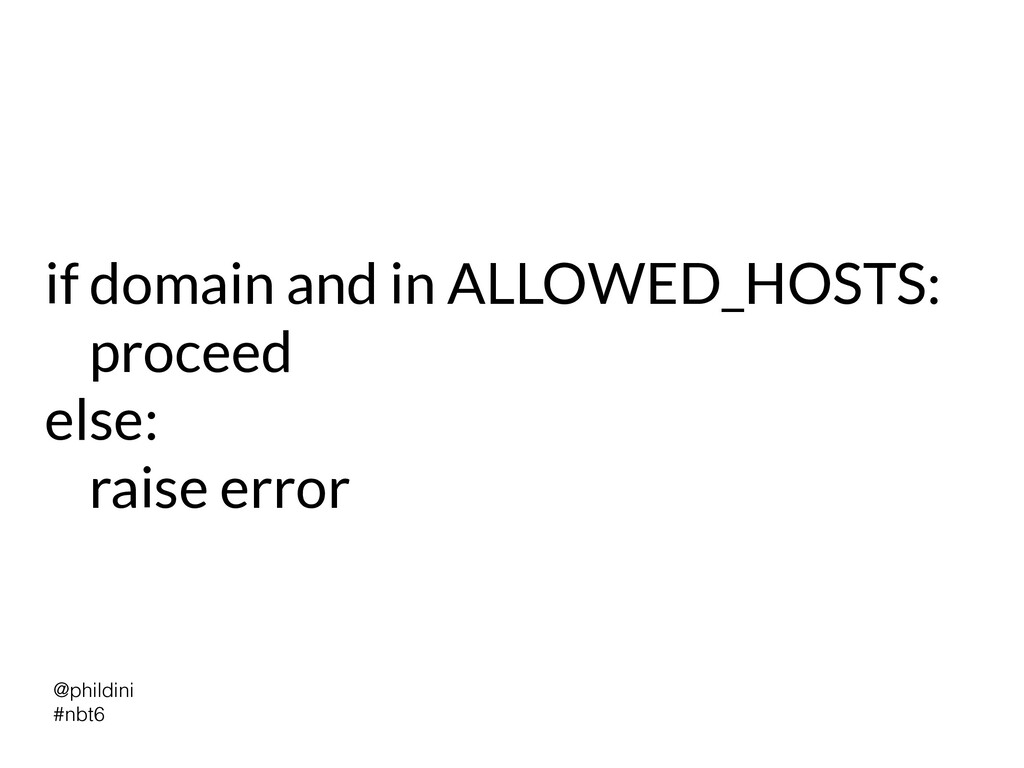
@phildini #nbt6 if domain and in ALLOWED_HOSTS: proceed else: raise
error
@phildini #nbt6 Passwords
@phildini #nbt6 django.contrib.auth.hashers.check_password https://github.com/django/django/blob/master/django/contrib/auth/hashers.py
@phildini #nbt6 How do we make this better?
@phildini #nbt6 Constant Vigilance!
@phildini #nbt6 Package updates!
@phildini #nbt6 Package Updates https://pyup.io/safety/, GitHub dependabot
@phildini #nbt6 HTTPS https://letsencrypt.org/
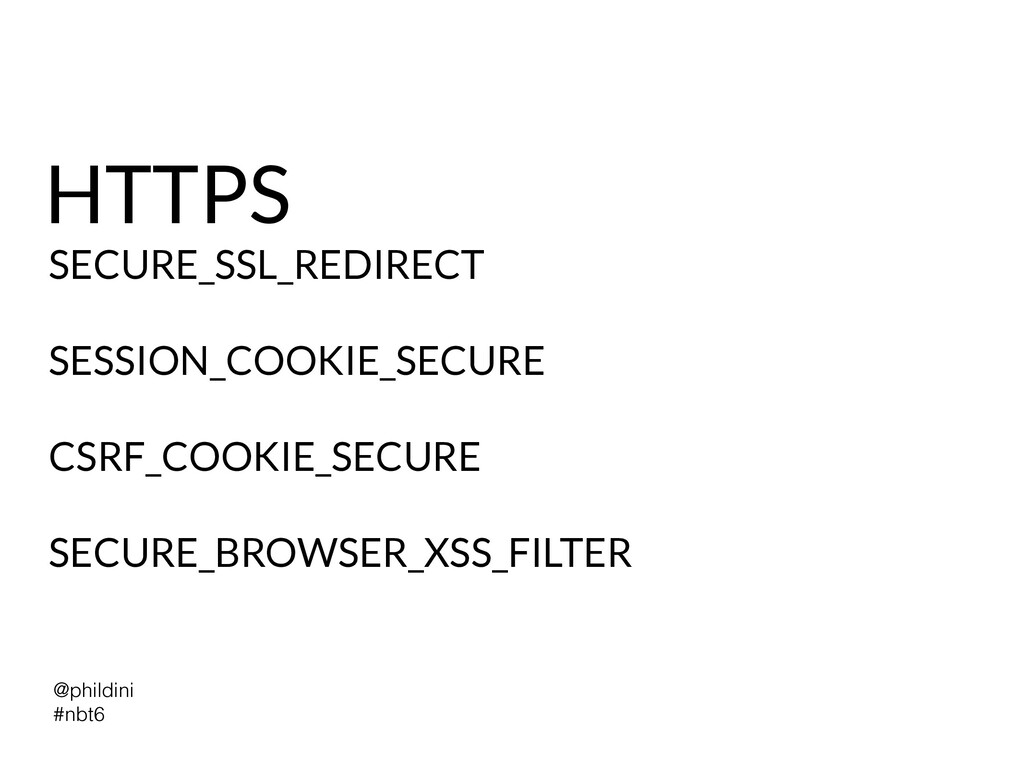
@phildini #nbt6 HTTPS SECURE_SSL_REDIRECT SESSION_COOKIE_SECURE CSRF_COOKIE_SECURE SECURE_BROWSER_XSS_FILTER
@phildini #nbt6 HTTPS SECURE_HSTS_SECONDS SECURE_HSTS_PRELOAD SECURE_HSTS_INCLUDE_SUBDOMAINS
@phildini #nbt6 CSP Reporting Content Security Policy
@phildini #nbt6 django_encrypted_ fi elds https://github.com/defrex/django-encrypted- fi elds
@phildini #nbt6 Django Defender https://github.com/jazzband/django-defender
@phildini #nbt6 Token Vaulting https://www.verygoodsecurity.com/
@phildini #nbt6 Making Django Ridiculously Secure http://nerd.kelseyinnis.com/blog/2015/09/08/making-django-really-really-ridiculously-secure/ Account Security Best
Practices https://pyvideo.org/pycon-us-2019/account-security-patterns-how-logged-in-are-you.html
@phildini #nbt6
@phildini #nbt6 The End. Philip James @phildini


 phildini
 ballas_inc
 skydoves
 sansantech
 henteko
 jozono
 amixedcolor
 sishi2026
 iwamot
 nori_shinoda
 uhyo
 ny7760
 bengo4com
 eileencodes
 garrettdimon
 andyhume
 ianozsvald
 soysaucechin
 katarinadahlin
 leimatthew05
 pedronauck
 aleyda
 jonoalderson
 kimpetersen
 inesmontani