Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Safe-ish By Default
Search
Philip James
December 10, 2015
Technology
92
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Safe-ish By Default
The Django Security Model and How to Make it Better
Philip James
December 10, 2015
More Decks by Philip James
See All by Philip James
3 (or whatever) ways to put something on the internet
phildini
0
20
Frog and Toad Learn about Django Security - NBT6
phildini
0
41
The Elephant and the Serpent (PyLatam 2019)
phildini
0
83
Account Security for the Fashionable App Developer
phildini
1
80
All in the Timing: Side-Channel Attacks
phildini
0
94
Giving Thanks
phildini
0
58
All in the Timing: Side-Channel Attacks in Python
phildini
0
440
API-Driven Django
phildini
1
460
Type uWSGI; Press Enter; What Happens?
phildini
0
120
Other Decks in Technology
See All in Technology
AX時代の自治体支援リソース再配分と役割分担の再構成:戦略とロードマップ(概要)
sishi2026
0
180
外国人エンジニアがVueプロトタイプで仕様を合わせている話 / Vue Fes Japan 2026 LT
eluwing
0
390
re:Invent の去年のスケジュールを公開します!
miu_crescent
PRO
0
200
コードレビューをなくして見えたもの
henteko
0
130
"AWSはちょっと苦手"でも大丈夫。AWS Blocks で手軽に作る Flutter のバックエンド #FlutterKaigi
tacck
PRO
0
130
書き手が人でもAIでも正しくなる道、 SREを埋め込んだDeveloper Platform / tech drivers day8
chmikata
4
900
キヨさん、67歳。AIコーディングエージェントに挑む
happysamurai294
0
140
kintoneで在庫管理システムを作るときの要件定義・設計ポイント
kai0707
0
220
AIコーディングはじめました
miso
0
140
Agent Loopを組み込んだ アンビエントなAI機能を実現する / Ambient AI fetures with Agent Loop
nekorush14
0
140
バックオフィスに染み出すTypeScript ── clasp で安全に仕組みを作る
nealle
1
170
渡米前の準備を制す!re:Invent 2026徹底準備術 / The Ultimate Preparation Guide for re:Invent 2026
yuj1osm
1
510
Featured
See All Featured
Making Projects Easy
brettharned
120
6.8k
Rails Girls Zürich Keynote
gr2m
96
14k
Prompt Engineering for Job Search
mfonobong
0
570
The innovator’s Mindset - Leading Through an Era of Exponential Change - McGill University 2025
jdejongh
PRO
1
390
Designing for Timeless Needs
cassininazir
1
540
Test your architecture with Archunit
thirion
2
2.5k
Cheating the UX When There Is Nothing More to Optimize - PixelPioneers
stephaniewalter
287
14k
The agentic SEO stack - context over prompts
schlessera
0
990
Collaborative Software Design: How to facilitate domain modelling decisions
baasie
1
360
Getting science done with accelerated Python computing platforms
jacobtomlinson
2
560
Embracing the Ebb and Flow
colly
88
5.2k
Are puppies a ranking factor?
jonoalderson
2
4.1k
Transcript
#safedjango @phildini Safe-ish by Default The Django Security Model and
How to Make it Better Philip James
#safedjango @phildini Who’s this guy?
#safedjango @phildini How We Use Django at Eventbrite
#safedjango @phildini Safe-ish? #safedjango @phildini
#safedjango @phildini XSS
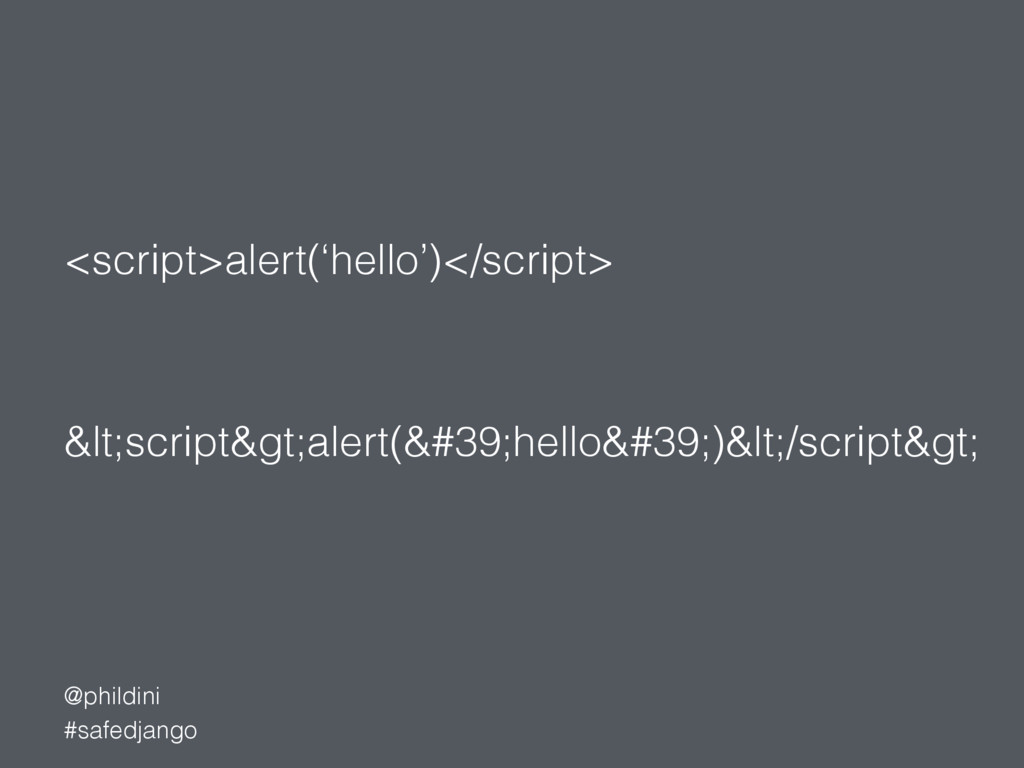
#safedjango @phildini <script>alert(‘hello’)</script> <script>alert('hello')</script>
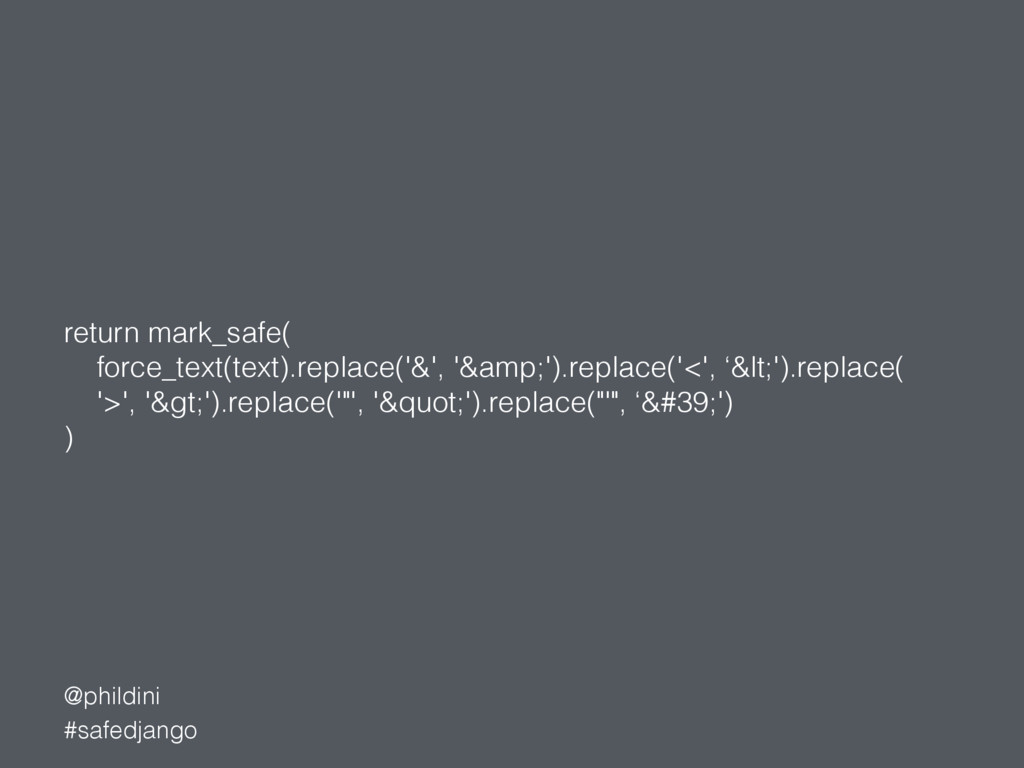
#safedjango @phildini return mark_safe( force_text(text).replace('&', '&').replace('<', ‘<').replace( '>', '>').replace('"', '"').replace("'",
‘'') )
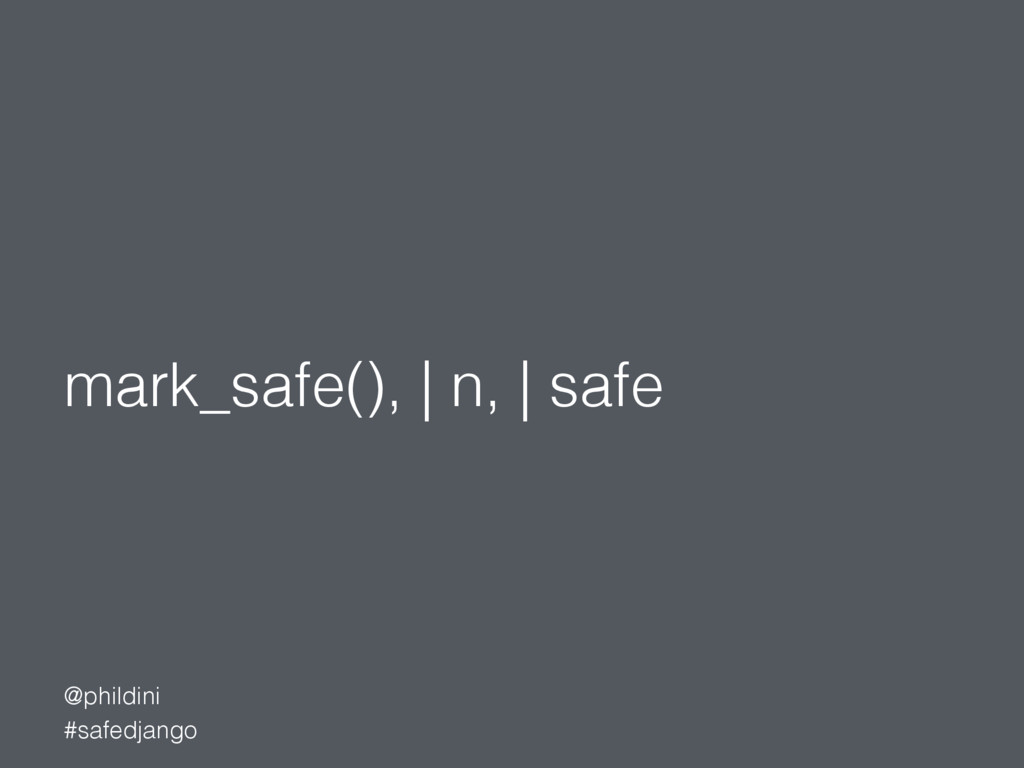
#safedjango @phildini mark_safe(), | n, | safe
#safedjango @phildini CSRF
#safedjango @phildini CsrfViewMiddleware
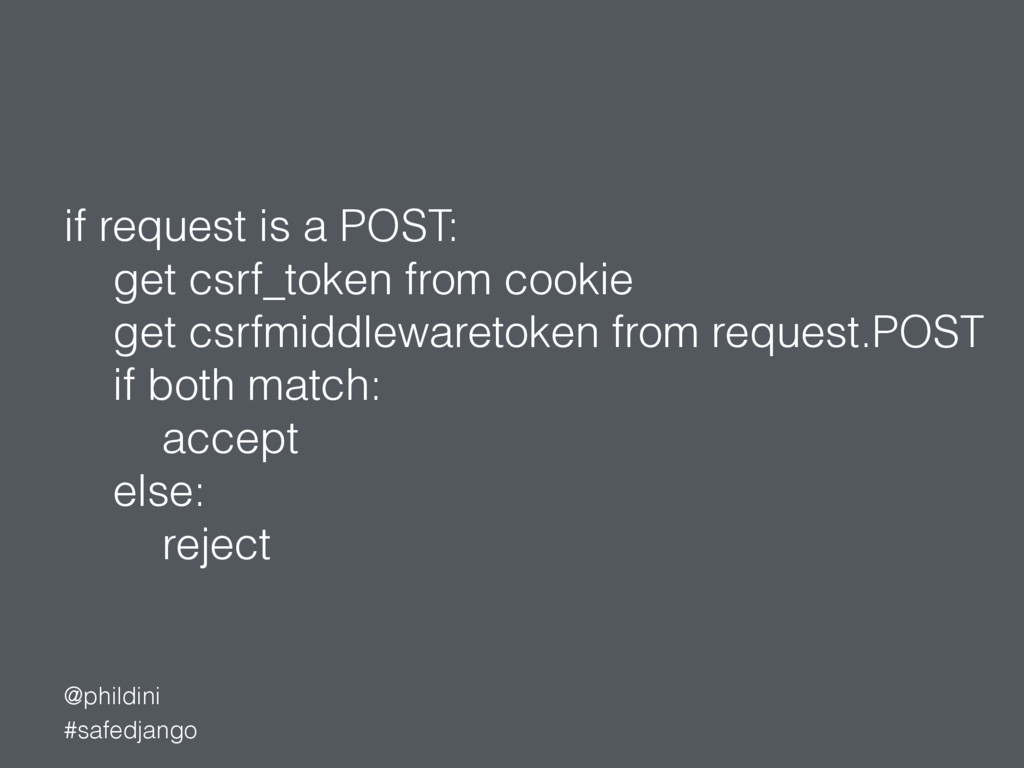
#safedjango @phildini if request is a POST: get csrf_token from
cookie get csrfmiddlewaretoken from request.POST if both match: accept else: reject
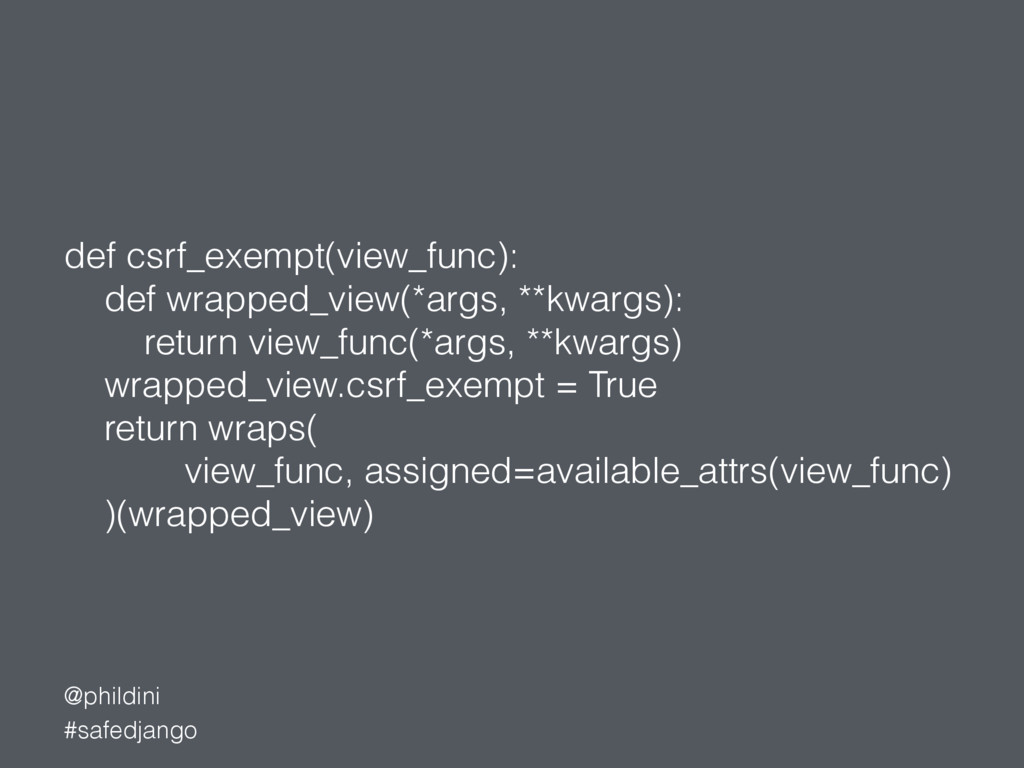
#safedjango @phildini def csrf_exempt(view_func): def wrapped_view(*args, **kwargs): return view_func(*args, **kwargs)
wrapped_view.csrf_exempt = True return wraps( view_func, assigned=available_attrs(view_func) )(wrapped_view)
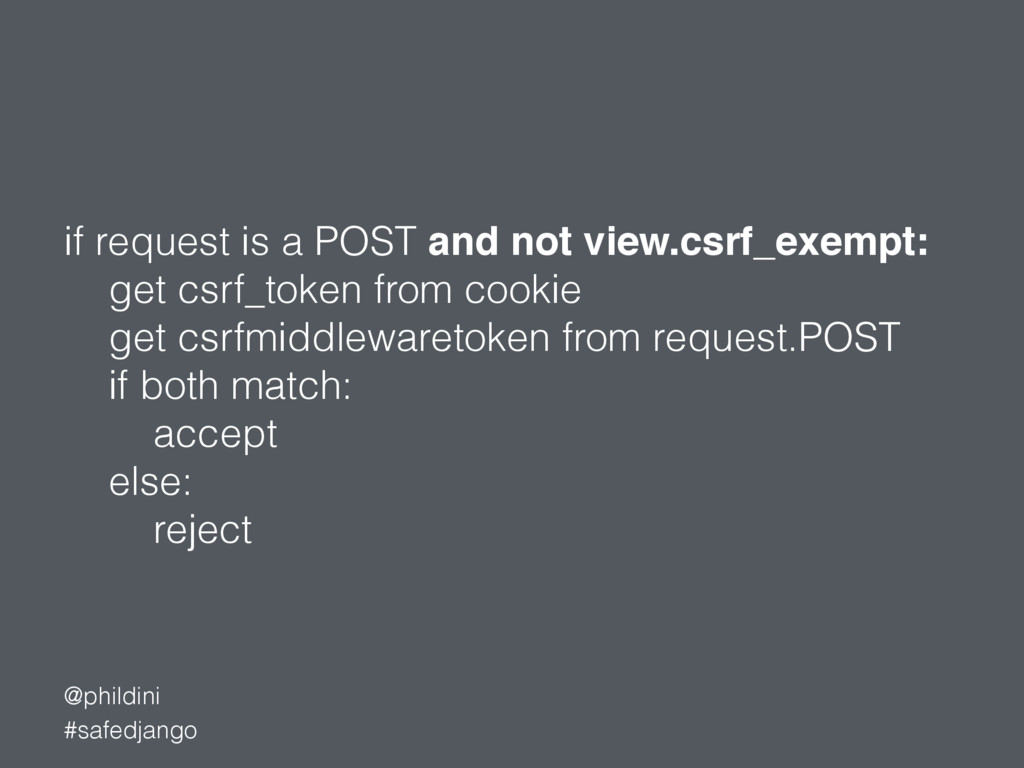
#safedjango @phildini if request is a POST and not view.csrf_exempt:
get csrf_token from cookie get csrfmiddlewaretoken from request.POST if both match: accept else: reject
#safedjango @phildini Sidenote: Cookies
#safedjango @phildini SQLi
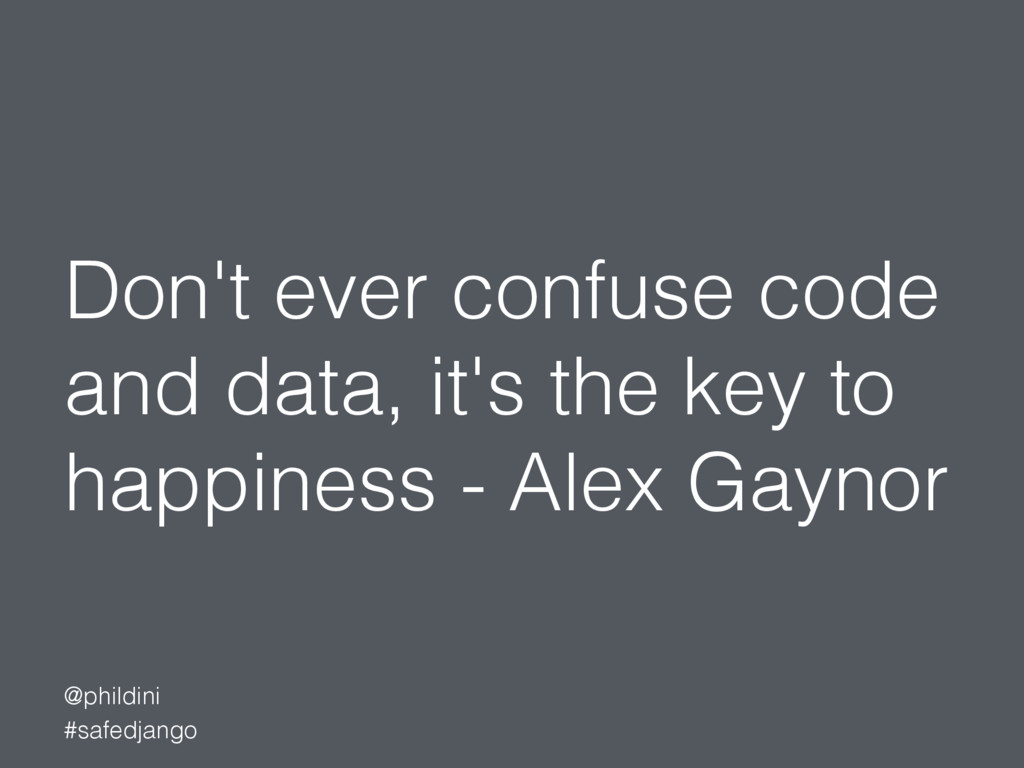
#safedjango @phildini Don't ever confuse code and data, it's the
key to happiness - Alex Gaynor
#safedjango @phildini .extra(), RawSQL()
#safedjango @phildini Clickjacking
#safedjango @phildini XFrameOptionsMiddleware
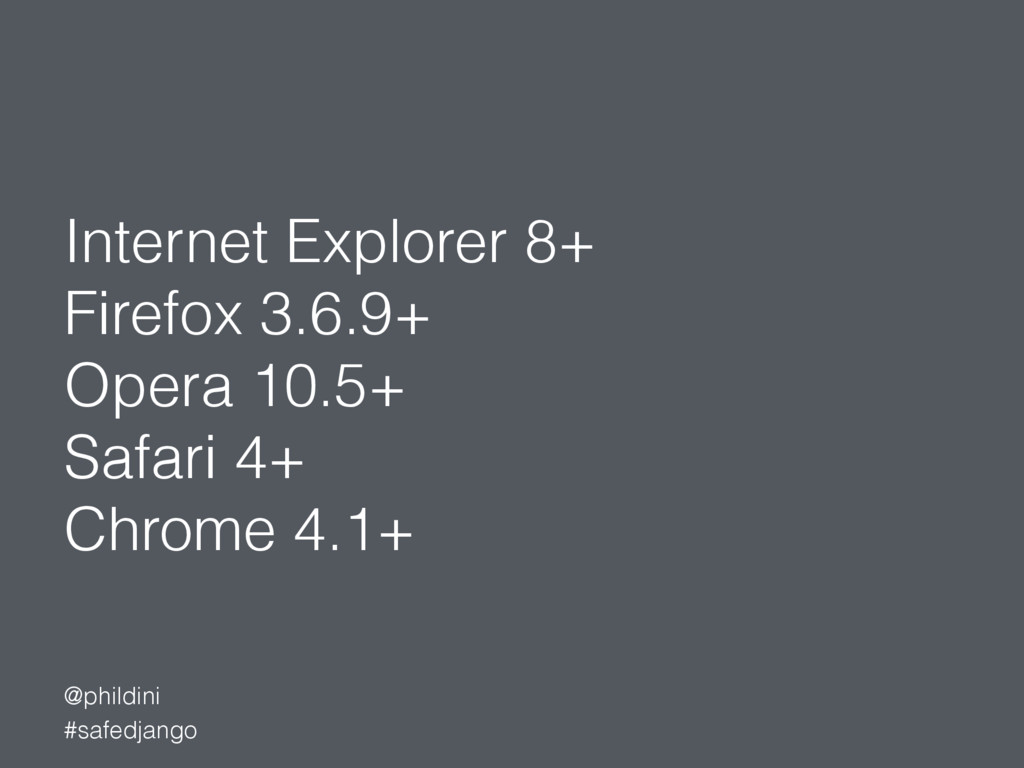
#safedjango @phildini Internet Explorer 8+ Firefox 3.6.9+ Opera 10.5+ Safari
4+ Chrome 4.1+
#safedjango @phildini Host Header Validation
#safedjango @phildini get_host()
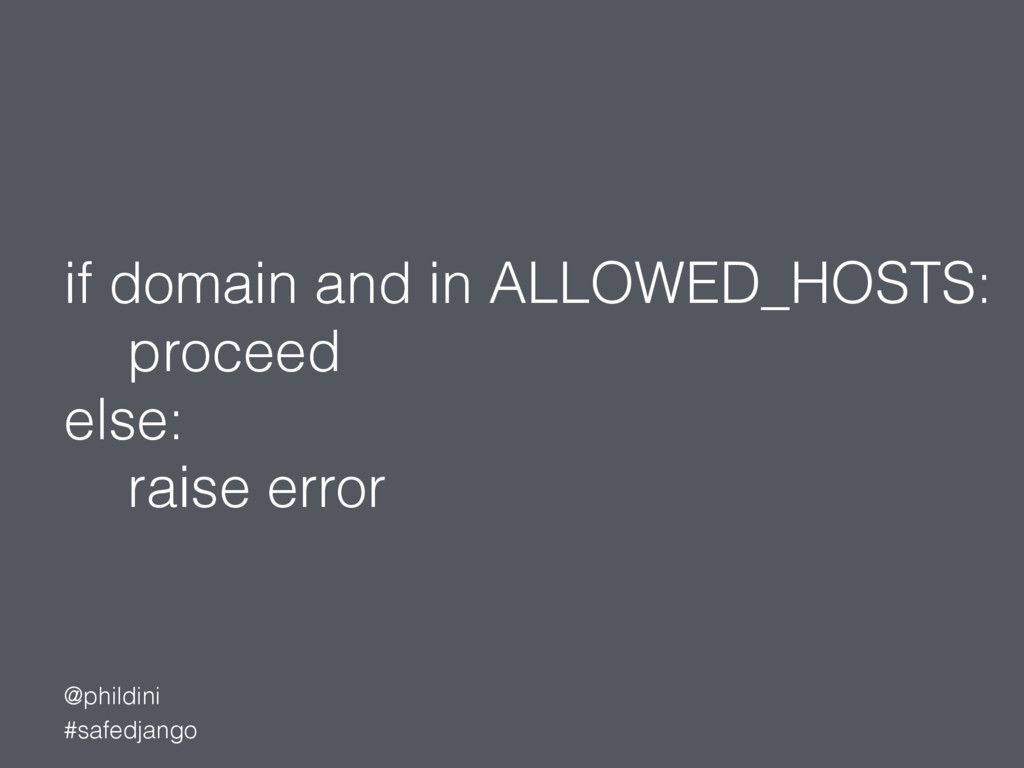
#safedjango @phildini if domain and in ALLOWED_HOSTS: proceed else: raise
error
#safedjango @phildini Sessions
#safedjango @phildini Passwords
#safedjango @phildini How Can We Make This Safer?
#safedjango @phildini Constant Vigilance!
#safedjango @phildini HTTPS
#safedjango @phildini What Does EB Do?
#safedjango @phildini CSP Reporting
#safedjango @phildini EBSecure
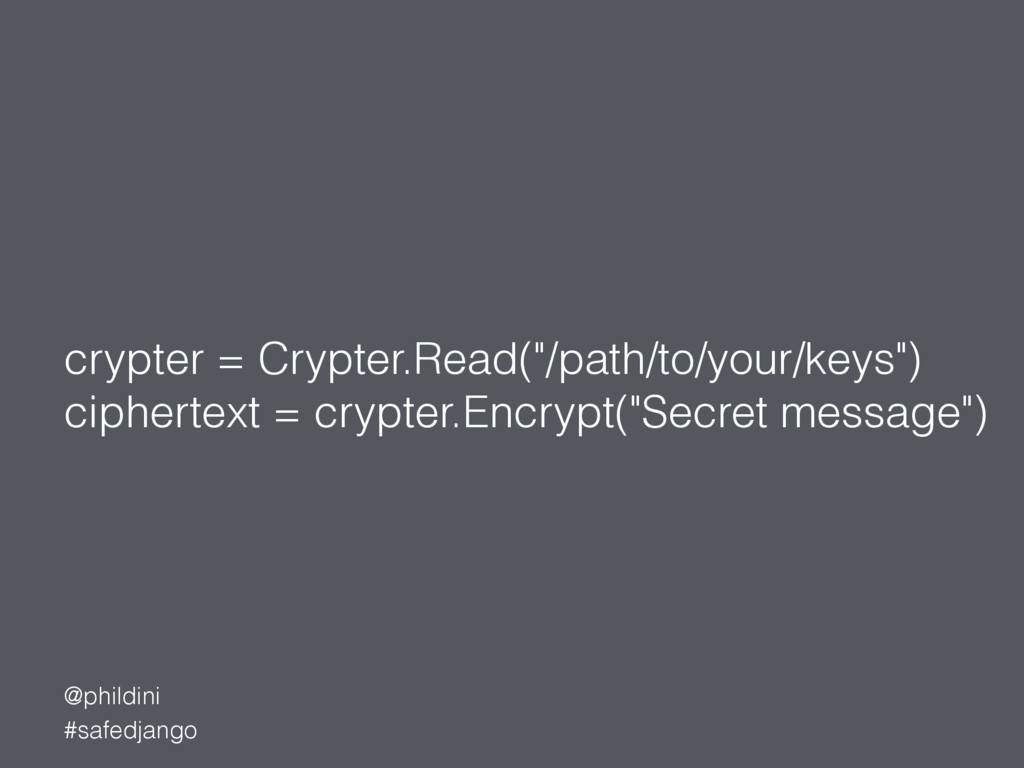
#safedjango @phildini crypter = Crypter.Read("/path/to/your/keys") ciphertext = crypter.Encrypt("Secret message")
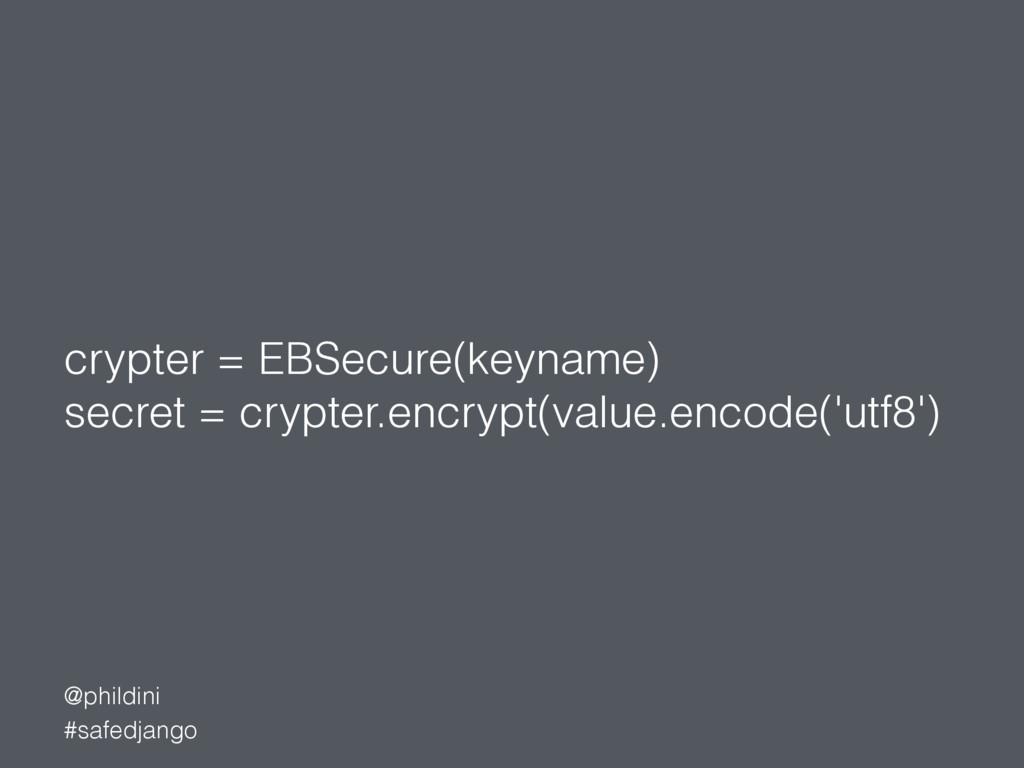
#safedjango @phildini crypter = EBSecure(keyname) secret = crypter.encrypt(value.encode('utf8')
#safedjango @phildini django_encrypted_fields https://github.com/defrex/django-encrypted-fields
#safedjango @phildini Other Resources
#safedjango @phildini django-secure http://django-secure.readthedocs.org/en/v0.1.2/
#safedjango @phildini Pony Checkup https://www.ponycheckup.com/
#safedjango @phildini Making Django Ridiculously Secure http://nerd.kelseyinnis.com/blog/2015/09/08/making-django-really-really-ridiculously-secure/
#safedjango @phildini Thanks! Questions?


 phildini
 sishi2026
 eluwing
 miu_crescent
 henteko
 tacck
 chmikata
 happysamurai294
 kai0707
 miso
 nekorush14
 nealle
 yuj1osm
 brettharned
 gr2m
 mfonobong
 jdejongh
 cassininazir
 thirion
 stephaniewalter
 schlessera
 baasie
 jacobtomlinson
 colly
 jonoalderson