Upgrade to Pro — share decks privately, control downloads, hide ads and more …

Security Driven Development

Security Driven Development

In an increasingly connected world, security is the chief concern. As developers, we are one of the earliest lines of defense. In this talk, we will look at the current state of application security. We will then look at some tools that can be implemented in current test environments that will test for security vulnerabilities. From there, we look at the work that is left to be done by security professionals and developers.

Avatar for Ricky Rickard

Ricky Rickard

May 01, 2015

Other Decks in Technology

Transcript

  1. Who Am I? • Husband and Father. • Comic Books,

    Video Games, and Board Games. • 20 years around technology • Predominantly focused on software development and testing. • Becoming more interested in information security and how it intersects with software development and testing • @rrickardjr on Twitter
  2. What’s This All About? • Security is a top concern

    for most people that use the Internet. • As developers, we have a great power. • “With great power comes great responsibility.” – Uncle Ben • The early a vulnerability can be detected, the less impact it will have. • Insecure code can create significant damage, both to your company and the users of your application • In this talk we are going to cover 3 major areas: • Where we are now in terms of security • Tools for developers to use to test their applications for security • The work we still have left to do
  3. Rugged Software Manifesto I am rugged and, more importantly, my

    code is rugged. I recognize that software has become a foundation of our modern world. I recognize the awesome responsibility that comes with this foundational role. I recognize that my code will be used in ways I cannot anticipate, in ways it was not designed, and for longer than it was ever intended. I recognize that my code will be attacked by talented and persistent adversaries who threaten our physical, economic and national security. I recognize these things – and I choose to be rugged. I am rugged because I refuse to be a source of vulnerability or weakness. I am rugged because I assure my code will support its mission. I am rugged because my code can face these challenges and persist in spite of them. I am rugged, not because it is easy, but because it is necessary and I am up for the challenge.
  4. Rails Goat • http://railsgoat.cktricky.com/ • Intentionally vulnerable version of the

    Ruby on Rails framework • Used as a training and demonstration resource for developers and security people.
  5. Brakeman Scanner • http://brakemanscanner.org/ • Looks at your source code

    for vulnerabilities • Used by GitHub, New Relic, and Twitter. • Rails Security Scanner • Works with Jenkins or Hudson Continuous Integration tools • Tests for a wide range of vulnerabilities, including the OWASP Top 10. • A pro version is launching this year, currently in beta, https://www.brakemanpro.com/
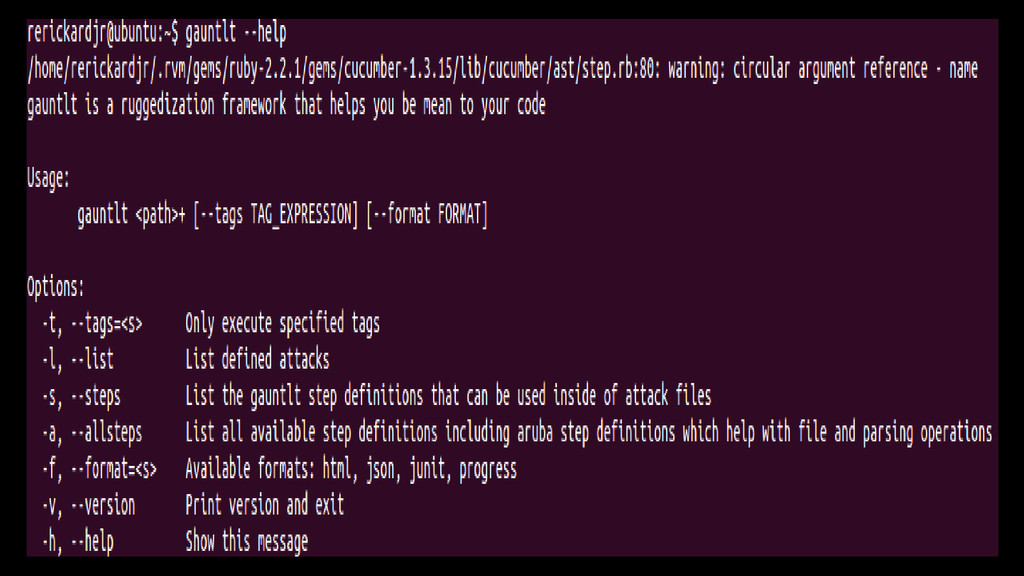
  6. Gauntlt • http://gauntlt.org • Be Mean To Your Code •

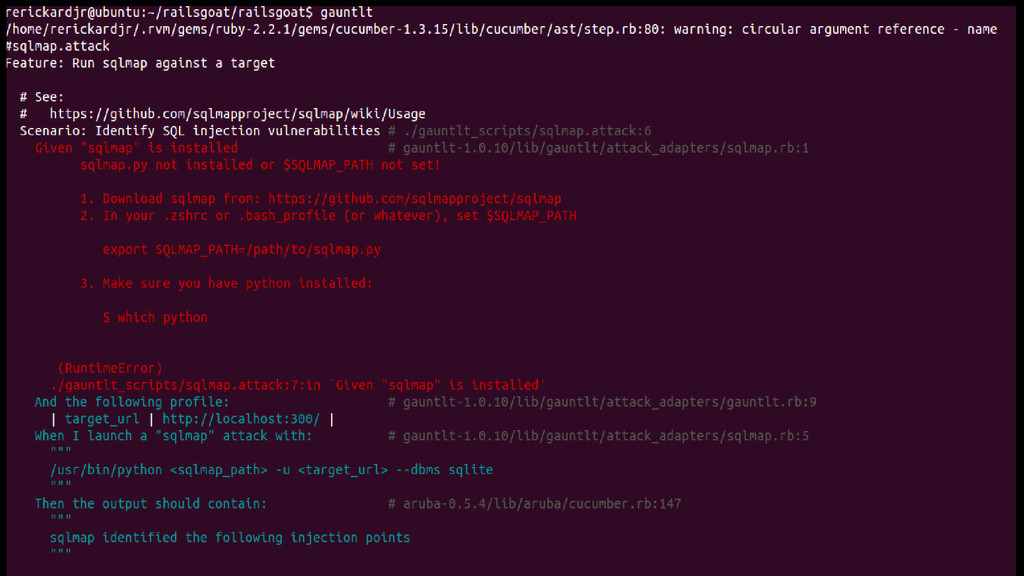
    Runs tests based on these tools: • curl • nmap • sslyze • sqlmap • Garmr • Heartbleed • Arachni • Built on top of Cucumber • Tests written in Gherkin Format
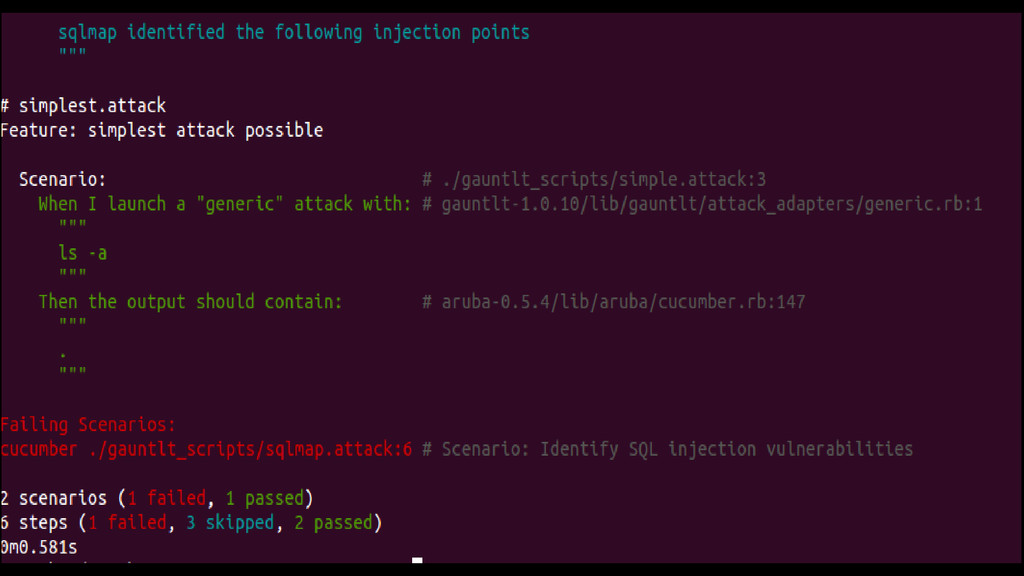
  7. Gauntlt Features • Because of Gherkin, Gauntlt attacks are written

    in a easy-to-read language • Because it is built on Cucumber, it can easily hook into your organization's testing tools and processes. • Security tool adapters come with the gauntlt quick start kit (you will need to install the adapters manually if you just gem install) • Uses unix standard error and standard out to pass status
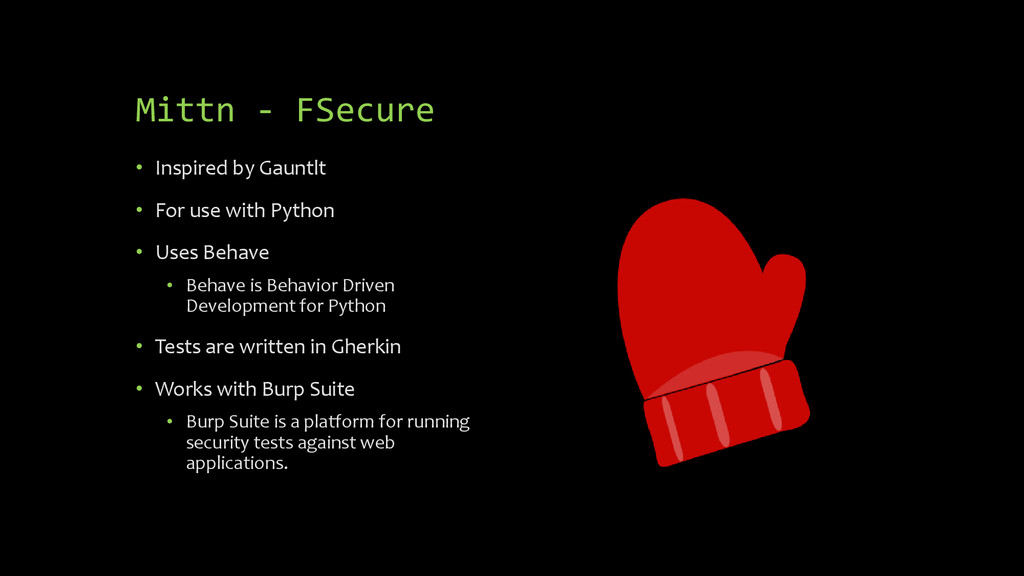
  8. Mittn - FSecure • Inspired by Gauntlt • For use

    with Python • Uses Behave • Behave is Behavior Driven Development for Python • Tests are written in Gherkin • Works with Burp Suite • Burp Suite is a platform for running security tests against web applications.
  9. BDD-Security – Continuum Security • http://www.continuumsecurity.net/ bdd-intro.html • Uses Java

    and Apache Ant to run • Uses the Given, When, Then model for user stories. • Focus on the “evil user” • Tests are exposed to all levels and can be run at a moments notice.
  10. OWASP • Open Web Application Security Project • No commercial

    products • Everything is free and open source. • Driven to make software security visible and accessible.
  11. OWASP Zed Attack Proxy (ZAP) • ZAP is an integrated

    penetration testing tool to find vulnerabilities in web applications. • It can be run as a stand alone tool or integrated using the API to be ran as part of a testing setup. • This is one of the flagship projects for OWASP is very well maintained and documented.
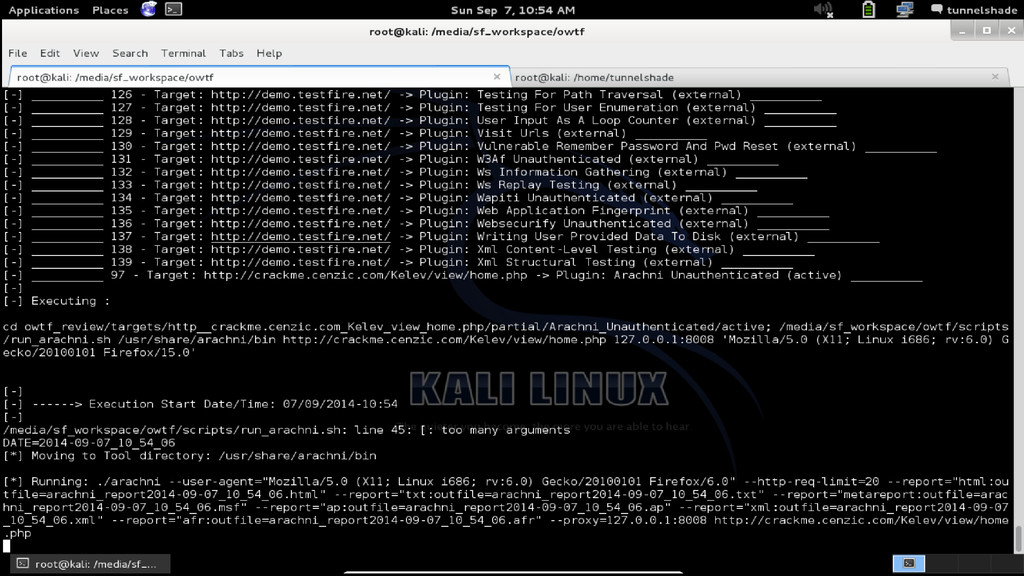
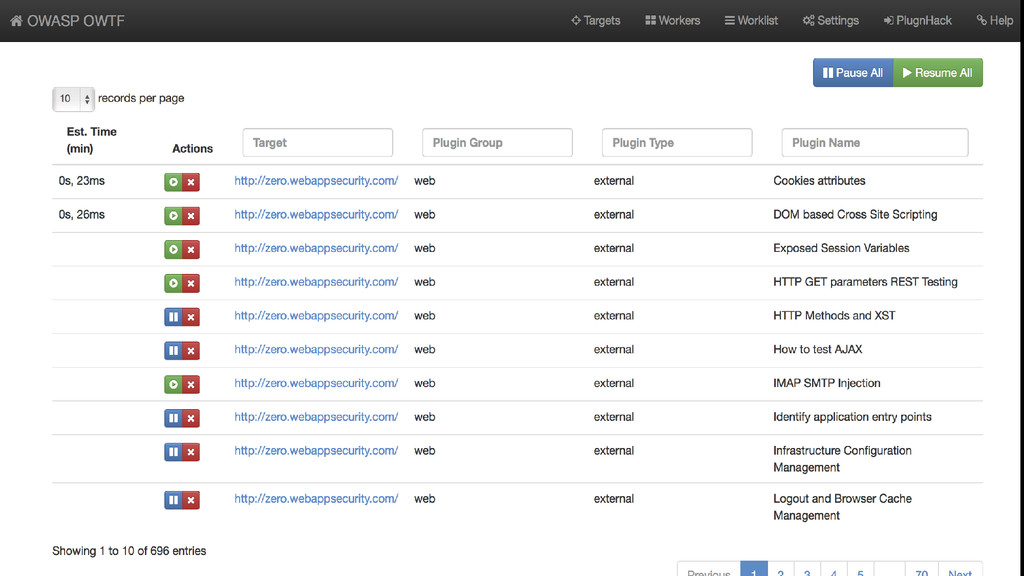
  12. OWASP Offensive Web Testing Framework • Aligned with OWASP Testing

    Guide + PTES + NIST • More efficient • More comprehensive • More creative and fun (minimise un- creative work)
  13. What’s Next? • Education / Awareness • Implementation • Encourage

    Creativity • Think outside the narrow scope of the application • Think of creative ways to break your application • Put yourself in the shoes of an attacker • Don’t let speed cause you to sacrifice security • Contribute to Open Source Security projects like Brakeman, Gauntlt and OWASP • Be active in your local developer community and your local information security community.
  14. Local Security and Developer Groups • Security MBA – www.securitymba.org

    • Central Ohio ISSA -www.centralohioissa.org/ • OWASP Columbus - http://www.meetup.com/Columbus-OWASP/ • Columbus Ruby Brigade - http://columbusrb.com/ • Central Ohio Python User Group - http://www.meetup.com/Central-Ohio-Python-Users- Group/ • Windows Developer User Group - http://thewindowsdeveloperusergroup.com/ • Central Ohio .NET Developers Group - http://www.condg.org/