Share
Introducing the OWASP Nettacker Project
OWASP Nettacker project was created to automate the information gathering, vulnerability scanning and in general to aid the penetration testing engagements. Nettacker is able to run various scans using a variety of methods and generate scan reports for applications and networks, including services, bugs, vulnerabilities, misconfigurations, default credentials and many other cool features - for example an ability to chain different scan methods. This relatively new (Summer 2017) and a lesser-known OWASP project has generated a huge amount of interest at BlackHat Europe 2018 Arsenal live demo gathering massive crowds of seasoned hackers and penetration testers eager to see this new tool in practice. This talk will showcase the OWASP Nettacker project giving an overview of its features including the live demo of the tool.
Sam Stepanyan
Transcript
58 slides
-
Introducing OWASP Nettacker Sam Stepanyan OWASP London Chapter Leader
Twitter: @securestep9 SAM STEPANYAN @securestep9 -
$ whoami - Sam Stepanyan Software development background OWASP London
Chapter Leader Application Security Consultant, Financial Services I am a Defender Why am I presenting a talk about a tool which consists of words “Network” and “Attacker”??? @securestep9 -
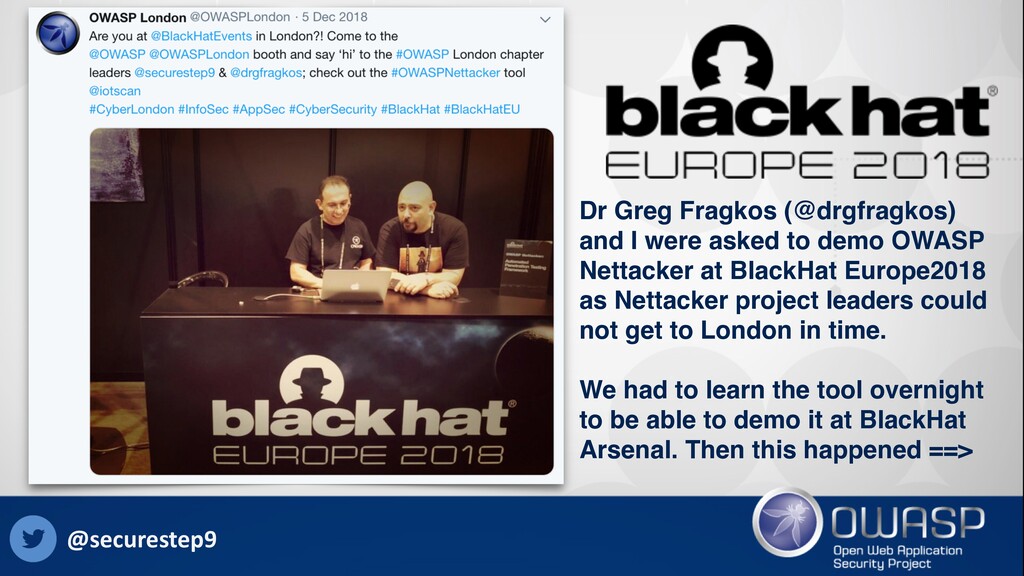
Dr Greg Fragkos (@drgfragkos) and I were asked to demo
OWASP Nettacker at BlackHat Europe2018 as Nettacker project leaders could not get to London in time. We had to learn the tool overnight to be able to demo it at BlackHat Arsenal. Then this happened ==> @securestep9 -
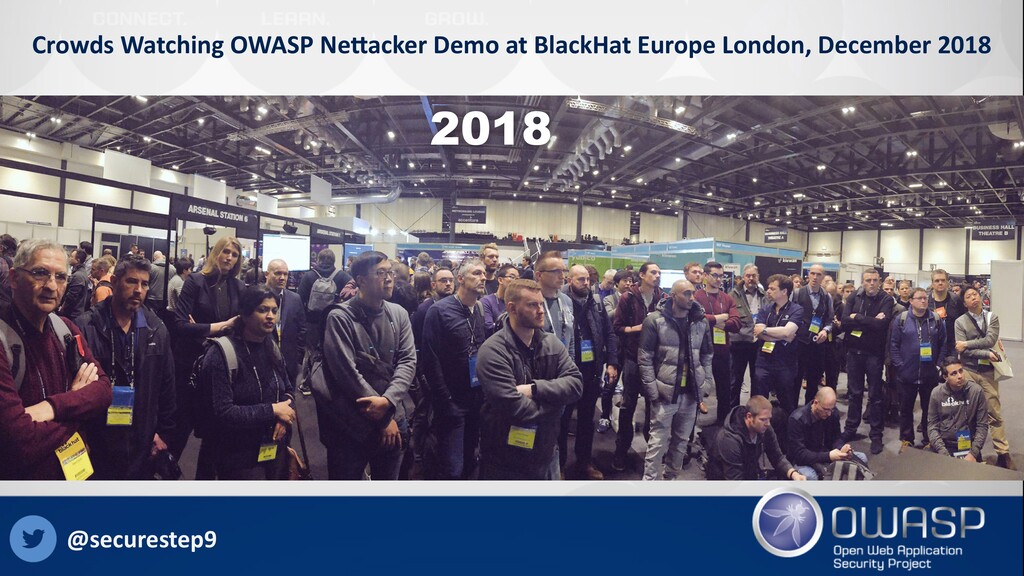
Crowds Watching OWASP NeEacker Demo at BlackHat Europe London, December
2018 @securestep9 2018 -
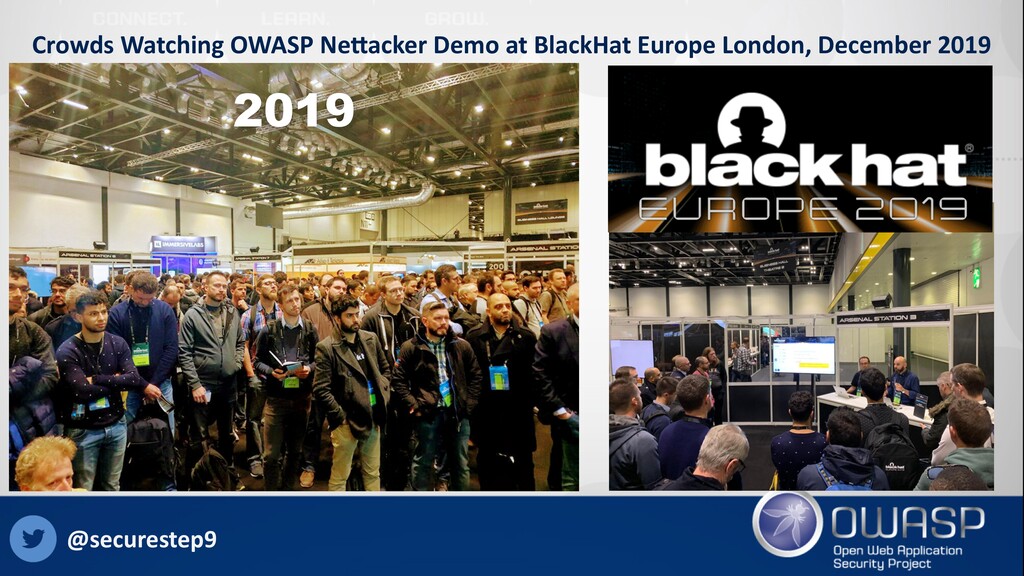
Crowds Watching OWASP NeEacker Demo at BlackHat Europe London, December
2019 @securestep9 2019 -
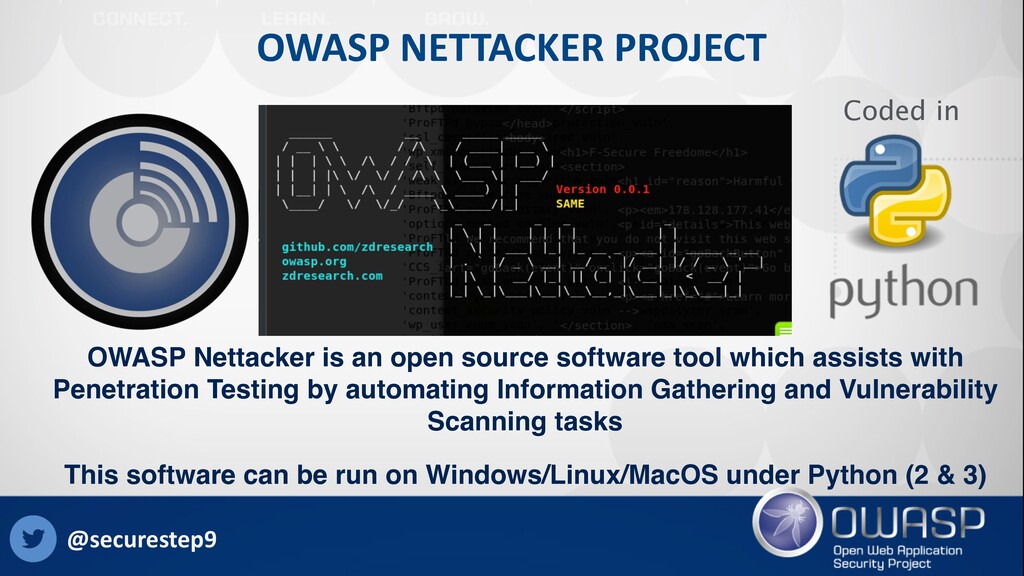
OWASP NETTACKER PROJECT OWASP Nettacker is an open source software
tool which assists with Penetration Testing by automating Information Gathering and Vulnerability Scanning tasks This software can be run on Windows/Linux/MacOS under Python (2 & 3) Coded in @securestep9 -
A BIT OF OWASP NETTACKER HISTORY April 2017 - Nettacker
created by: Ali Razmjoo (@razielowfsky) Mohammed Reza Espargham (@rezesp) originally named “iotscan” for IoT Scanning Donated to OWASP by ZDResearch CORE DEVELOPERS Ali Razmjoo-Qalaei Mohammad Reza Espargham Vahid Behzadan Abbas Naderi-Afooshteh Johanna Curiel Sri Harsha Gajavalli @securestep9 -
A BIT OF OWASP NETTACKER HISTORY Accepted as a Google
Summer Of Code (GSoC) Project in 2018 Enhanced by GSoC Students: Shaddy Garg Pradeep Jairamani Hannah Brand Watch visualisation: https://www.youtube.com/watch?v=bW_KDNzc36g @securestep9 -
a tool consisting of many tools not necessarily compatible with
each other can they be all used together??? “SWISS ARMY KNIFE”? @securestep9 -
•a collection of tools •modular structure •create own modules •fast
perfomance / multi-threading •customisable profiles (bundle of modules focused on specific task) •automate and run from command line WHY OWASP NETTACKER @securestep9 -
it is not “officially released” yet not even in “beta”
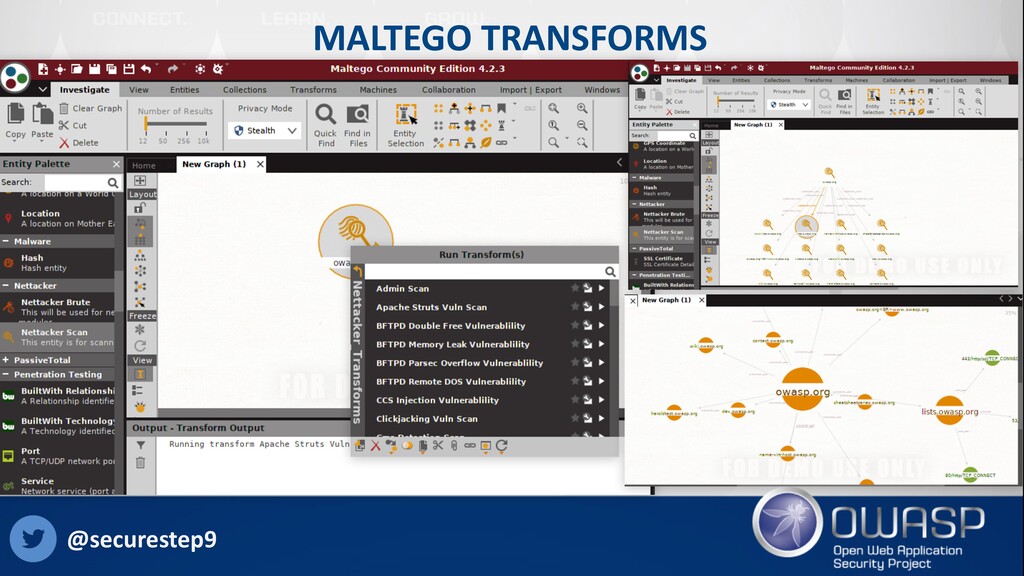
- v0.0.1 looking for more contributors …however it already has: command line interface Web UI API Report generator Maltego transforms 62 modules (+1) @securestep9 OWASP NETTACKER -
RESPONSIBLE USE WARNING You shall not misuse this tool nor
any other security tool for unauthorized access Performing security scans without permission from the owner of the computer system is illegal. @securestep9 -
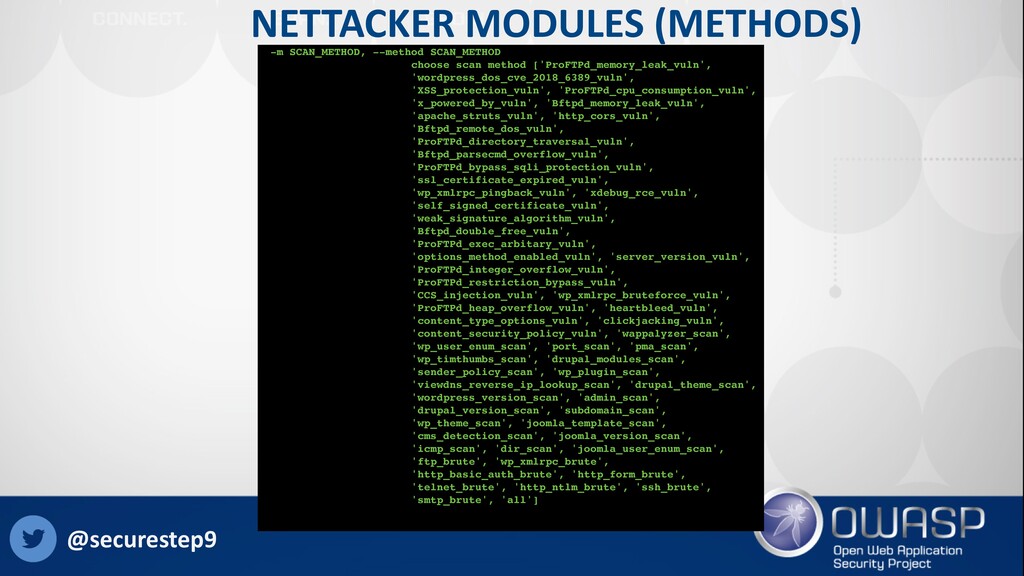
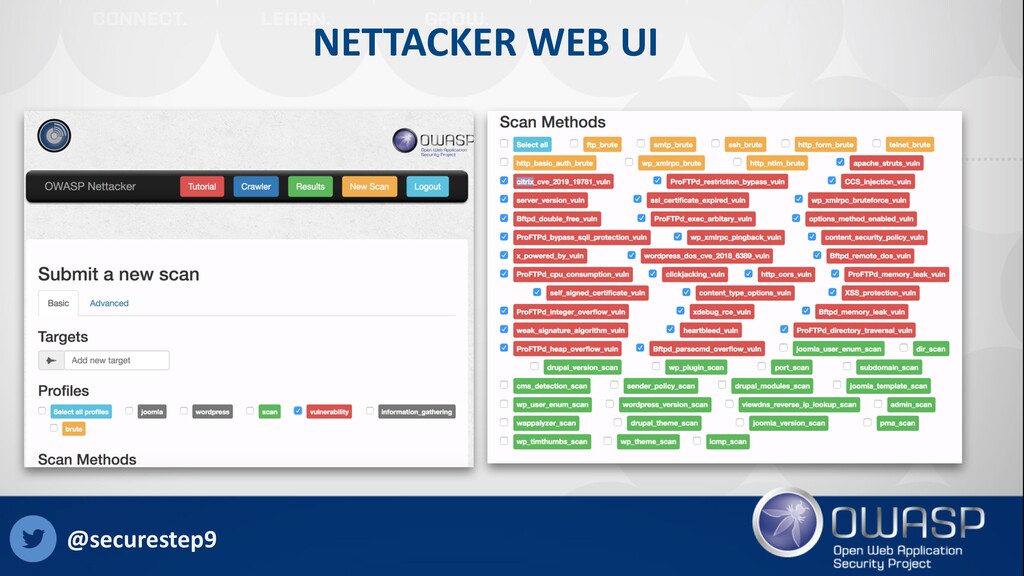
NETTACKER MODULES (METHODS) -m SCAN_METHOD, --method SCAN_METHOD choose scan method
['ProFTPd_memory_leak_vuln', 'wordpress_dos_cve_2018_6389_vuln', 'XSS_protection_vuln', 'ProFTPd_cpu_consumption_vuln', 'x_powered_by_vuln', 'Bftpd_memory_leak_vuln', 'apache_struts_vuln', 'http_cors_vuln', 'Bftpd_remote_dos_vuln', 'ProFTPd_directory_traversal_vuln', 'Bftpd_parsecmd_overflow_vuln', 'ProFTPd_bypass_sqli_protection_vuln', 'ssl_certificate_expired_vuln', 'wp_xmlrpc_pingback_vuln', 'xdebug_rce_vuln', 'self_signed_certificate_vuln', 'weak_signature_algorithm_vuln', 'Bftpd_double_free_vuln', 'ProFTPd_exec_arbitary_vuln', 'options_method_enabled_vuln', 'server_version_vuln', 'ProFTPd_integer_overflow_vuln', 'ProFTPd_restriction_bypass_vuln', 'CCS_injection_vuln', 'wp_xmlrpc_bruteforce_vuln', 'ProFTPd_heap_overflow_vuln', 'heartbleed_vuln', 'content_type_options_vuln', 'clickjacking_vuln', 'content_security_policy_vuln', 'wappalyzer_scan', 'wp_user_enum_scan', 'port_scan', 'pma_scan', 'wp_timthumbs_scan', 'drupal_modules_scan', 'sender_policy_scan', 'wp_plugin_scan', 'viewdns_reverse_ip_lookup_scan', 'drupal_theme_scan', 'wordpress_version_scan', 'admin_scan', 'drupal_version_scan', 'subdomain_scan', 'wp_theme_scan', 'joomla_template_scan', 'cms_detection_scan', 'joomla_version_scan', 'icmp_scan', 'dir_scan', 'joomla_user_enum_scan', 'ftp_brute', 'wp_xmlrpc_brute', 'http_basic_auth_brute', 'http_form_brute', 'telnet_brute', 'http_ntlm_brute', 'ssh_brute', 'smtp_brute', 'all'] @securestep9 -
‘scan’ - e.g. port_scan ‘vuln’ - e.g. apache_struts_vuln ‘brute’- e.g.
ssh_brute @securestep9 NETTACKER MODULE TYPES -
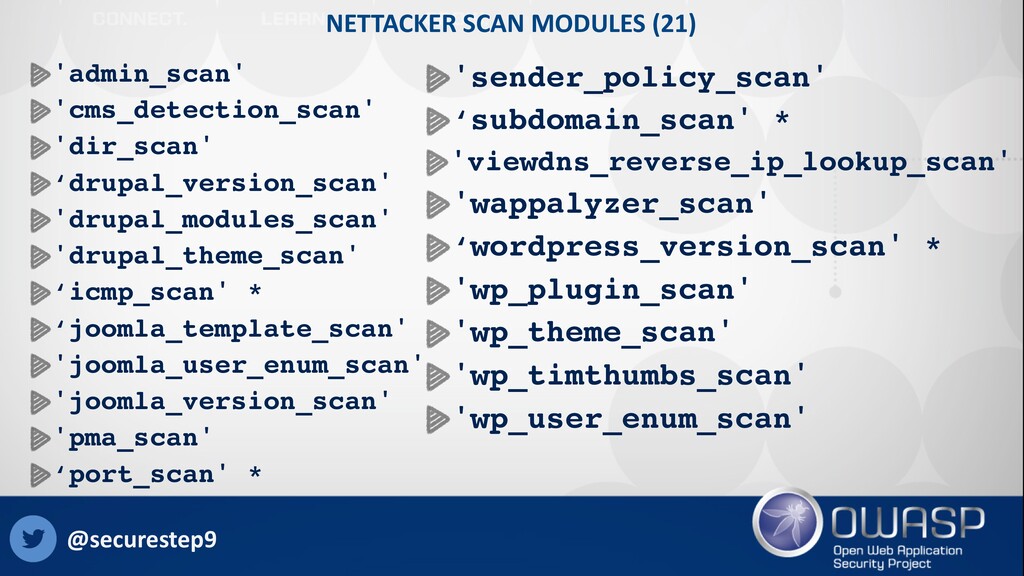
NETTACKER SCAN MODULES (21) 'admin_scan' 'cms_detection_scan' 'dir_scan' ‘drupal_version_scan' 'drupal_modules_scan' 'drupal_theme_scan'
‘icmp_scan' * ‘joomla_template_scan' 'joomla_user_enum_scan' 'joomla_version_scan' 'pma_scan' ‘port_scan' * 'sender_policy_scan' ‘subdomain_scan' * 'viewdns_reverse_ip_lookup_scan' 'wappalyzer_scan' ‘wordpress_version_scan' * 'wp_plugin_scan' 'wp_theme_scan' 'wp_timthumbs_scan' 'wp_user_enum_scan' @securestep9 -
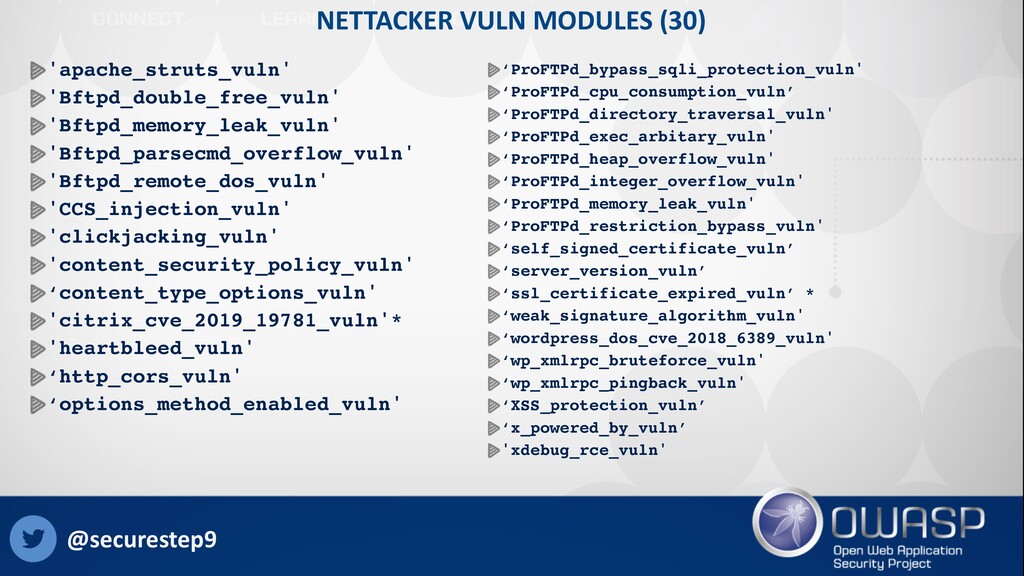
NETTACKER VULN MODULES (30) 'apache_struts_vuln' 'Bftpd_double_free_vuln' 'Bftpd_memory_leak_vuln' 'Bftpd_parsecmd_overflow_vuln' 'Bftpd_remote_dos_vuln' 'CCS_injection_vuln'
'clickjacking_vuln' 'content_security_policy_vuln' ‘content_type_options_vuln' 'citrix_cve_2019_19781_vuln'* 'heartbleed_vuln' ‘http_cors_vuln' ‘options_method_enabled_vuln' ‘ProFTPd_bypass_sqli_protection_vuln' ‘ProFTPd_cpu_consumption_vuln’ ‘ProFTPd_directory_traversal_vuln' ‘ProFTPd_exec_arbitary_vuln' ‘ProFTPd_heap_overflow_vuln' ‘ProFTPd_integer_overflow_vuln' ‘ProFTPd_memory_leak_vuln' ‘ProFTPd_restriction_bypass_vuln' ‘self_signed_certificate_vuln’ ‘server_version_vuln’ ‘ssl_certificate_expired_vuln’ * ‘weak_signature_algorithm_vuln' ‘wordpress_dos_cve_2018_6389_vuln' ‘wp_xmlrpc_bruteforce_vuln' ‘wp_xmlrpc_pingback_vuln' ‘XSS_protection_vuln’ ‘x_powered_by_vuln’ 'xdebug_rce_vuln' @securestep9 -
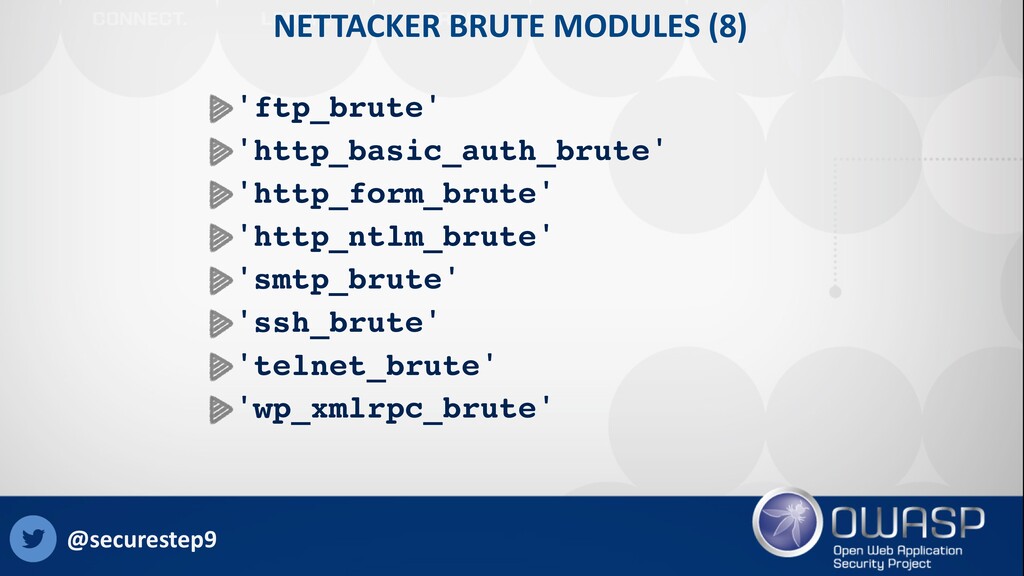
NETTACKER BRUTE MODULES (8) 'ftp_brute' 'http_basic_auth_brute' 'http_form_brute' 'http_ntlm_brute' 'smtp_brute' 'ssh_brute'
'telnet_brute' 'wp_xmlrpc_brute' @securestep9 -
OWASP Nettacker runs on: Windows, Linux, and macOS operating systems.
It is compatible with both Python2 and Python3. I will demonstrate how to install it on Kali Linux INSTALLING NETTACKER @securestep9 -
GitHub To install directly from GitHub using git, execute this
command: git clone https://github.com/zdresearch/OWASP- Nettacker.git && cd OWASP-Nettacker && pip install -r requirements.txt && python setup.py install INSTALLING NETTACKER @securestep9 -
scan your network for IOT devices scan IOT device for
open ports default credentials (admin/admin) IOT SCAN @securestep9 -
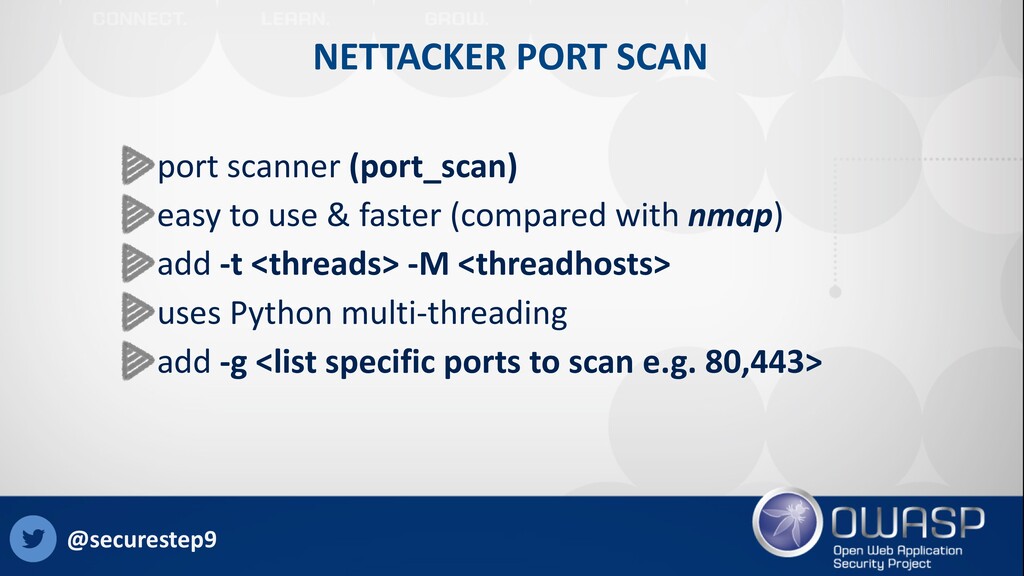
NETTACKER PORT SCAN port scanner (port_scan) easy to use &
faster (compared with nmap) add -t <threads> -M <threadhosts> uses Python multi-threading add -g <list specific ports to scan e.g. 80,443> @securestep9 -
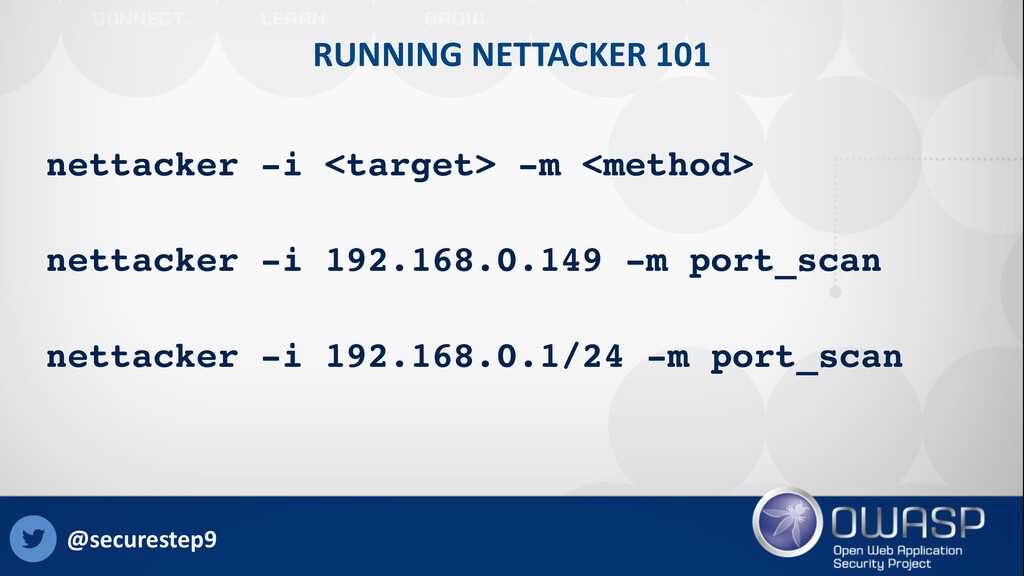
RUNNING NETTACKER 101 nettacker -i <target> -m <method> nettacker -i
192.168.0.149 -m port_scan nettacker -i 192.168.0.1/24 -m port_scan @securestep9 -
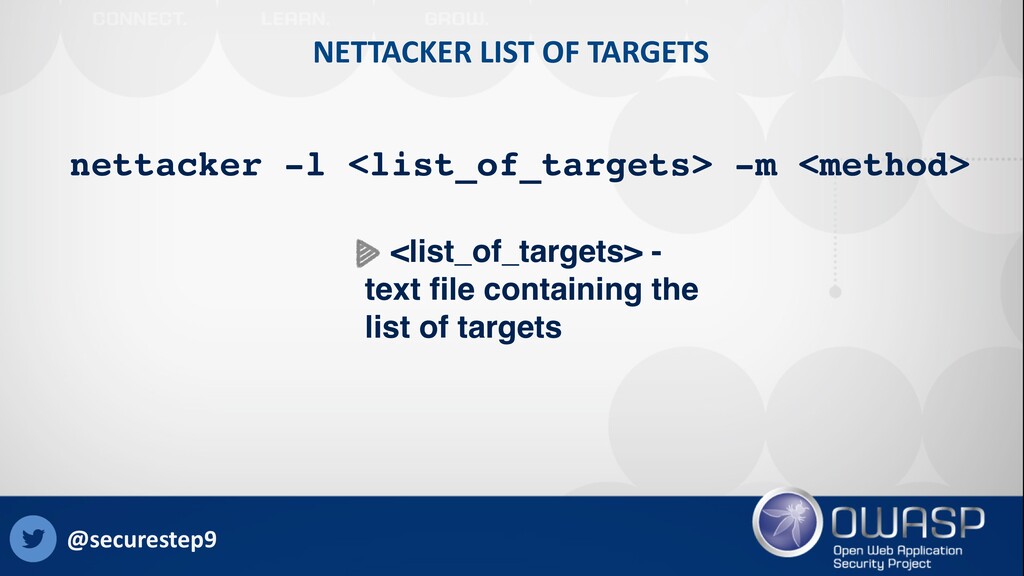
NETTACKER LIST OF TARGETS nettacker -l <list_of_targets> -m <method> <list_of_targets>
- text file containing the list of targets @securestep9 -
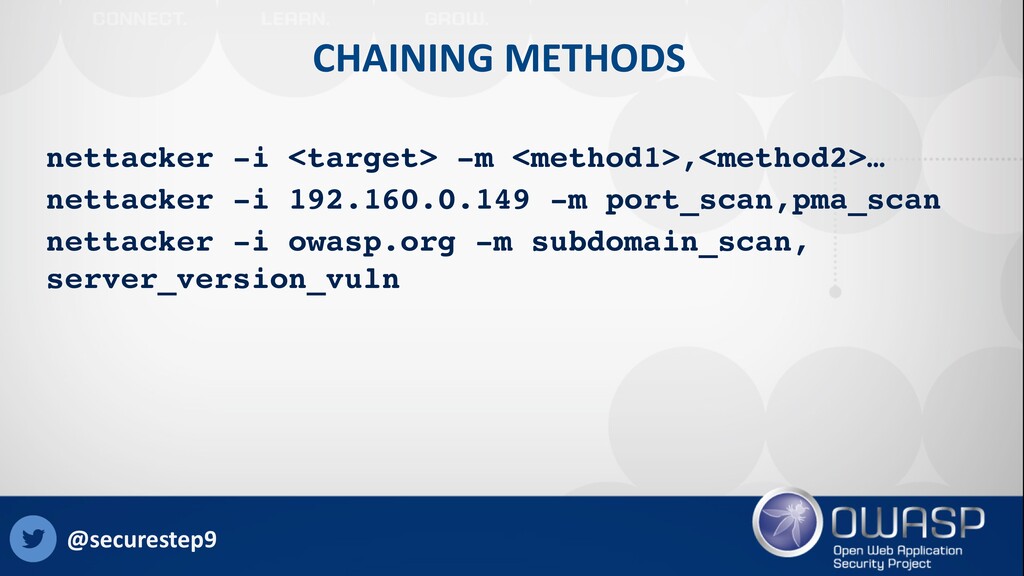
CHAINING METHODS nettacker -i <target> -m <method1>,<method2>… nettacker -i 192.160.0.149
-m port_scan,pma_scan nettacker -i owasp.org -m subdomain_scan, server_version_vuln @securestep9 -
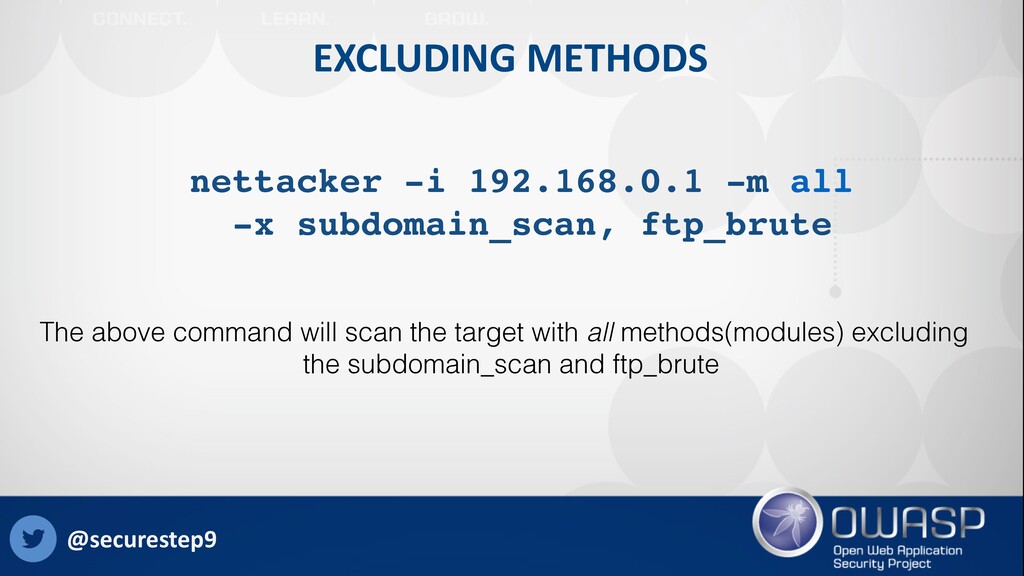
EXCLUDING METHODS nettacker -i 192.168.0.1 -m all -x subdomain_scan, ftp_brute
The above command will scan the target with all methods(modules) excluding the subdomain_scan and ftp_brute @securestep9 -
NETTACKER PROFILES nettacker -i <target> —-profile info ‘info’ ‘scan’ ‘brute’
‘vuln’ ‘wp’ ‘joomla’ 'all' Bundles of methods to be used on a target @securestep9 -
NETTACKER COMMAND LINE Usage: Nettacker [-L LANGUAGE] [-v VERBOSE_LEVEL] [-V]
[-c] [-o LOG_IN_FILE] [--graph GRAPH_FLAG] [-h] [-W] [--profile PROFILE] [-i TARGETS] [-l TARGETS_LIST] [-m SCAN_METHOD] [-x EXCLUDE_METHOD] [-u USERS] [-U USERS_LIST] [-p PASSWDS] [-P PASSWDS_LIST] [-g PORTS] [-T TIMEOUT_SEC] [-w TIME_SLEEP] [-r] [-s] [-t THREAD_NUMBER] [-M THREAD_NUMBER_HOST] [-R SOCKS_PROXY] [--retries RETRIES] [--ping-before-scan] [--method-args METHODS_ARGS] [--method-args-list] [--start-api] [--api-host API_HOST] [--api-port API_PORT] [--api-debug-mode] [--api-access-key API_ACCESS_KEY] [--api-client-white-list] [--api-client-white-list-ips API_CLIENT_WHITE_LIST_IPS] [--api-access-log] [--api-access-log-filename API_ACCESS_LOG_FILENAME] @securestep9 -
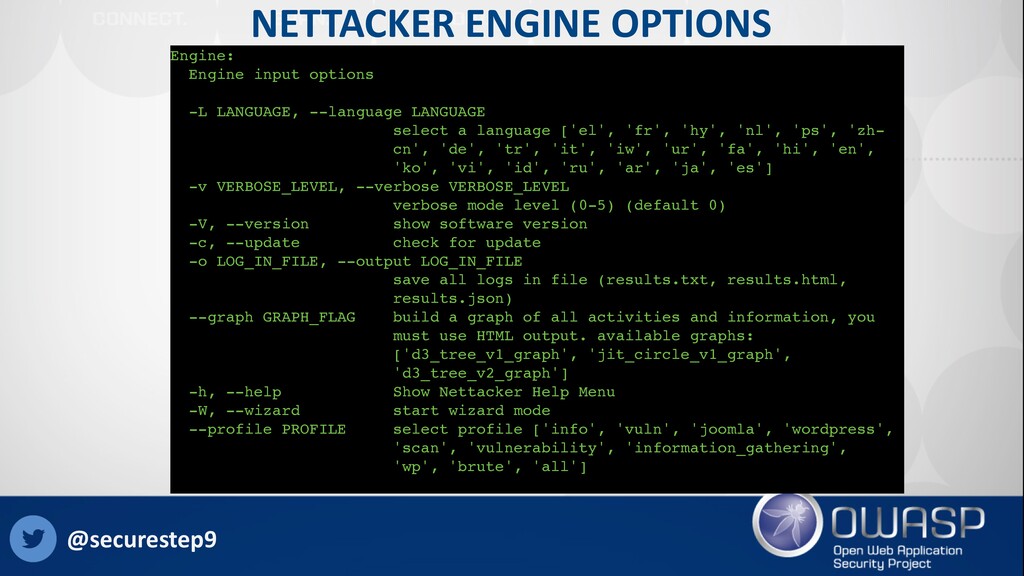
NETTACKER ENGINE OPTIONS Engine: Engine input options -L LANGUAGE, --language
LANGUAGE select a language ['el', 'fr', 'hy', 'nl', 'ps', 'zh- cn', 'de', 'tr', 'it', 'iw', 'ur', 'fa', 'hi', 'en', 'ko', 'vi', 'id', 'ru', 'ar', 'ja', 'es'] -v VERBOSE_LEVEL, --verbose VERBOSE_LEVEL verbose mode level (0-5) (default 0) -V, --version show software version -c, --update check for update -o LOG_IN_FILE, --output LOG_IN_FILE save all logs in file (results.txt, results.html, results.json) --graph GRAPH_FLAG build a graph of all activities and information, you must use HTML output. available graphs: ['d3_tree_v1_graph', 'jit_circle_v1_graph', 'd3_tree_v2_graph'] -h, --help Show Nettacker Help Menu -W, --wizard start wizard mode --profile PROFILE select profile ['info', 'vuln', 'joomla', 'wordpress', 'scan', 'vulnerability', 'information_gathering', 'wp', 'brute', 'all'] @securestep9 -
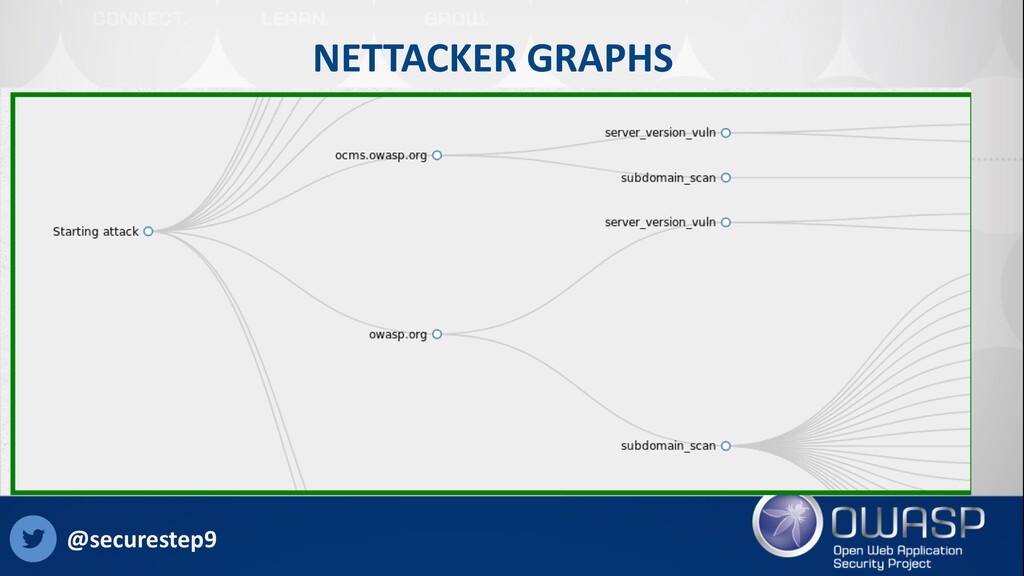
NETTACKER GRAPHS - HTML REPORT [+] report saved in /root/.owasp-nettacker/results/
results_<timestamp>.html each Nettacker run output is saved in HTML results file with a graph in it you can change the graph type using ‘--graph’ : d3_tree_v1_graph d3_tree_v2_graph jit_circle_v1_graph @securestep9 -
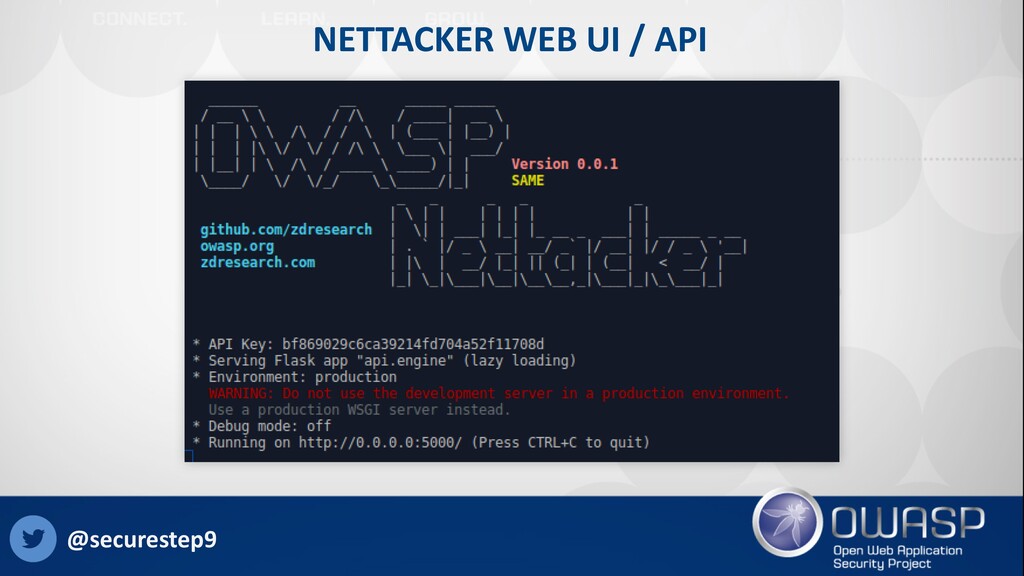
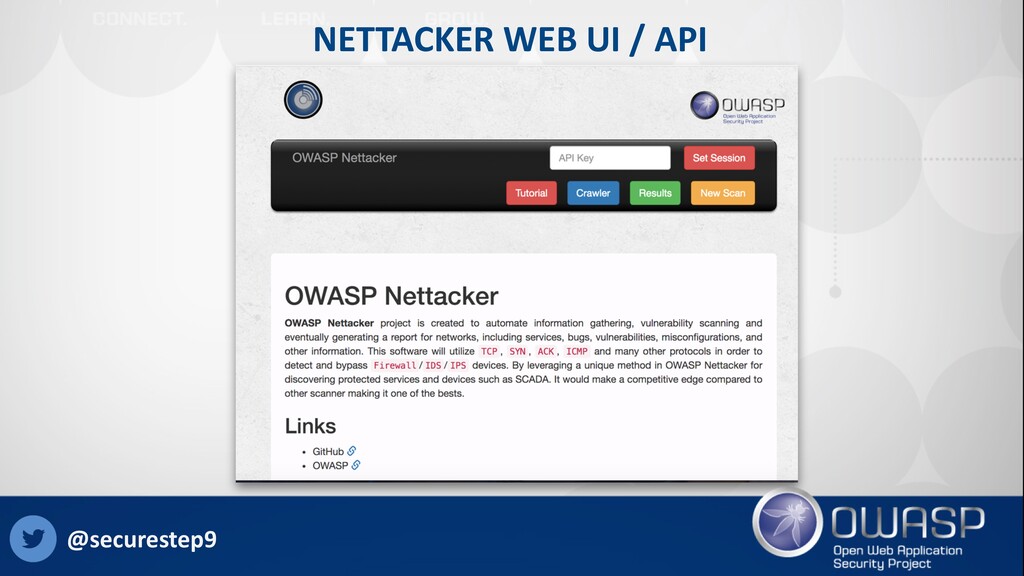
NETTACKER API API options --start-api start the API service --api-host
API_HOST API host address --api-port API_PORT API port number --api-debug-mode API debug mode --api-access-key API_ACCESS_KEY --api-client-white-list just allow white list hosts to connect to the API --api-client-white-list-ips API_CLIENT_WHITE_LIST_IPS define white list hosts, separate with , (examples: 127.0.0.1, 192.168.0.1/24, 10.0.0.1-10.0.0.255) --api-access-log generate API access log --api-access-log-filename API_ACCESS_LOG_FILENAME API access log filename @securestep9 -
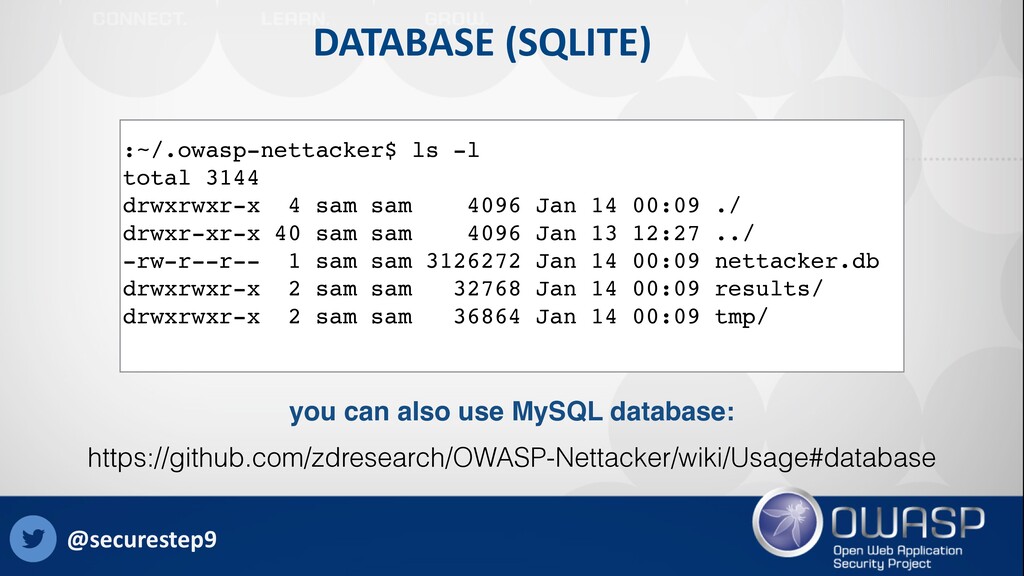
DATABASE (SQLITE) :~/.owasp-nettacker$ ls -l total 3144 drwxrwxr-x 4 sam
sam 4096 Jan 14 00:09 ./ drwxr-xr-x 40 sam sam 4096 Jan 13 12:27 ../ -rw-r--r-- 1 sam sam 3126272 Jan 14 00:09 nettacker.db drwxrwxr-x 2 sam sam 32768 Jan 14 00:09 results/ drwxrwxr-x 2 sam sam 36864 Jan 14 00:09 tmp/ @securestep9 you can also use MySQL database: https://github.com/zdresearch/OWASP-Nettacker/wiki/Usage#database -
NETTACKER REPORTS - JSON nettacker -i <target> -m <method> -o
file.json @securestep9 -
NETTACKER METHODS ARGS LIST PART 1 [+] Bftpd_remote_dos_vuln --> bftpd_vuln_ports
[+] content_security_policy_vuln --> csp_vuln_ports [+] port_scan --> port_scan_ports, port_scan_stealth, udp_scan [+] smtp_brute --> smtp_brute_ports, smtp_brute_split_user_set_pass, smtp_brute_users, smtp_brute_split_user_set_pass_prefix, smtp_brute_passwds [+] icmp_scan --> [+] xdebug_rce_vuln --> xdebug_vuln_ports [+] wp_user_enum_scan --> wp_user_enum_ports [+] ProFTPd_cpu_consumption_vuln --> Proftpd_vuln_ports [+] wp_xmlrpc_brute --> wp_users, wp_xmlrpc_brute_ports, wp_passwds [+] x_powered_by_vuln --> xpb_vuln_port [+] ProFTPd_heap_overflow_vuln --> Proftpd_vuln_ports [+] ProFTPd_integer_overflow_vuln --> Proftpd_vuln_ports [+] admin_scan --> admin_scan_http_method, admin_scan_list, admin_scan_random_agent @securestep9 -
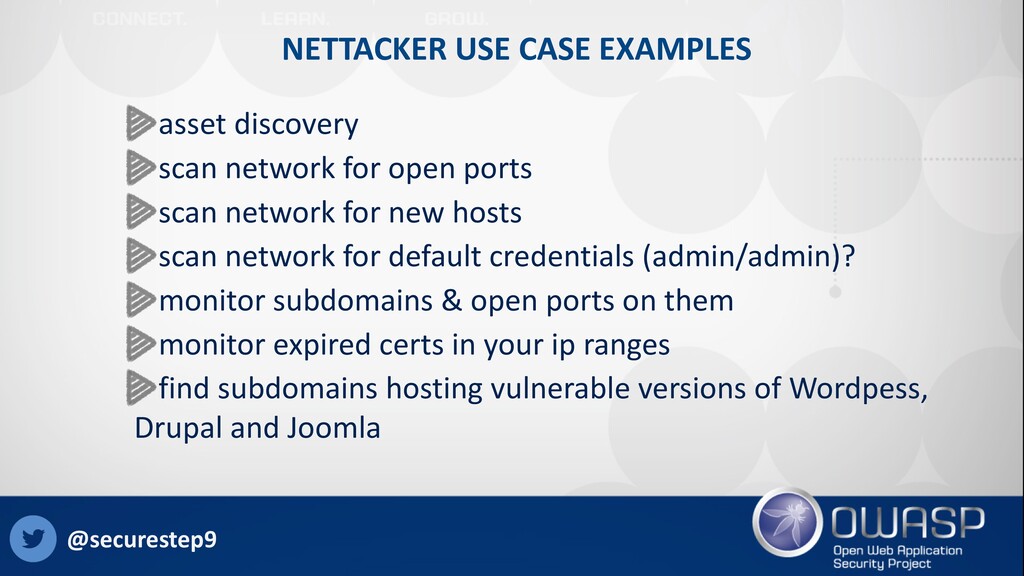
NETTACKER USE CASE EXAMPLES asset discovery scan network for open
ports scan network for new hosts scan network for default credentials (admin/admin)? monitor subdomains & open ports on them monitor expired certs in your ip ranges find subdomains hosting vulnerable versions of Wordpess, Drupal and Joomla @securestep9 -
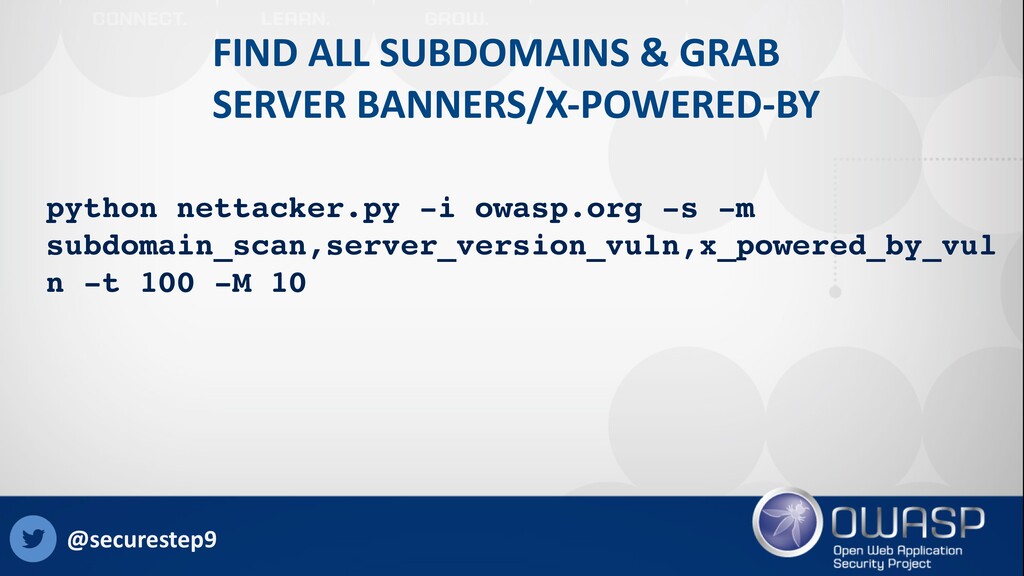
@securestep9 python nettacker.py -i owasp.org -s -m subdomain_scan,server_version_vuln,x_powered_by_vul n -t
100 -M 10 FIND ALL SUBDOMAINS & GRAB SERVER BANNERS/X-POWERED-BY -
@securestep9 python nettacker.py -i 192.168.0.1/24 -m port_scan,server_version_vuln,x_powered_by_vuln -g 80,443 -t
100 -M 10 FIND WEB SERVICES ON YOUR NETWORK & GRAB SERVER BANNERS / X-POWERED-BY -
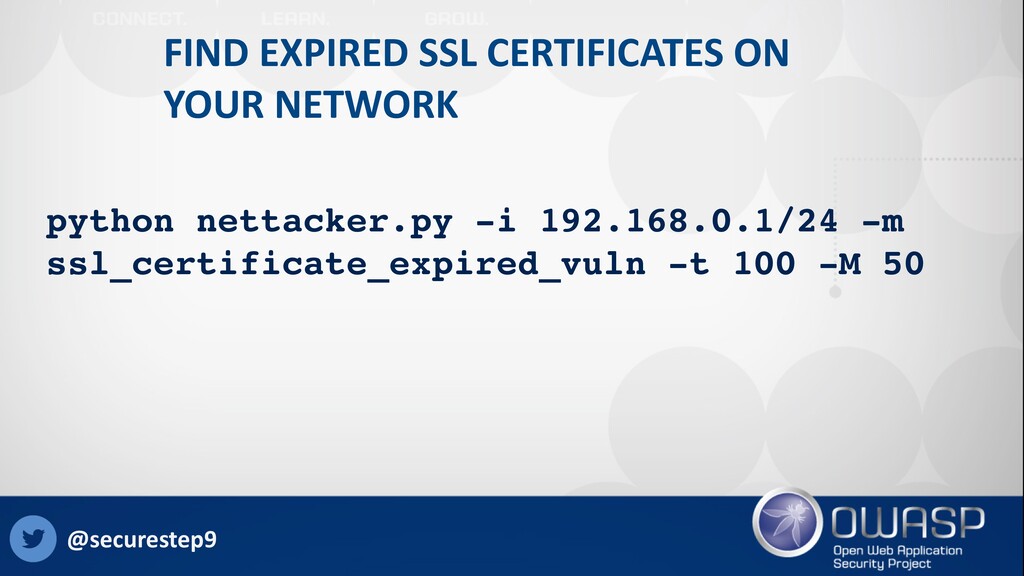
@securestep9 python nettacker.py -i 192.168.0.1/24 -m ssl_certificate_expired_vuln -t 100 -M
50 FIND EXPIRED SSL CERTIFICATES ON YOUR NETWORK -
@securestep9 python nettacker.py -i yourcompany.com -s -m subdomain_scan,wordpress_version_scan -t 100
-M 10 DETECT WORDPRESS VERSION ON YOUR SUBDOMAINS -
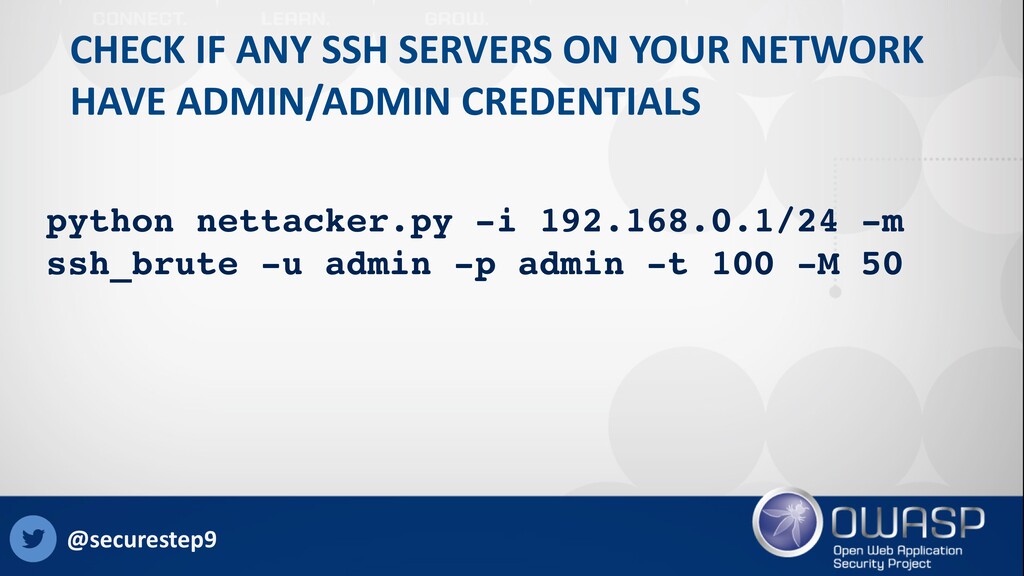
@securestep9 python nettacker.py -i 192.168.0.1/24 -m ssh_brute -u admin -p
admin -t 100 -M 50 CHECK IF ANY SSH SERVERS ON YOUR NETWORK HAVE ADMIN/ADMIN CREDENTIALS -
NETTACKER - PLEASE CONTRIBUTE! Developer Wiki: https://github.com/zdresearch/ OWASP-Nettacker/wiki/Developers Read &
follow the Contributor guidelines @securestep9 -
Thank You! Questions? sam.stepanyan @ owasp . org
@securestep9 SAM STEPANYAN @securestep9