This presentation, originally held at BruCON 2011, was voted to be held again at the 10 year anniversary of BruCON in 2018.
Let's assume you need heart sugery. I hope you don't, but let's just stick with it for a minute. How much would you be willing for someone to fix it and who would you hire to do it? If you are a suicidal emo kid, please do not answer, you are ruining the point here. Here's the thing: People want someone suitable and knowledgeable to cut them open and sew them up again and they are willing to pay good money for it. Here are two things you don't want to do:
1) You don't want to hire some old drunk with a pocket knife and a sewing kit from the dollar shop which claims to fix your heart for 100 bucks.
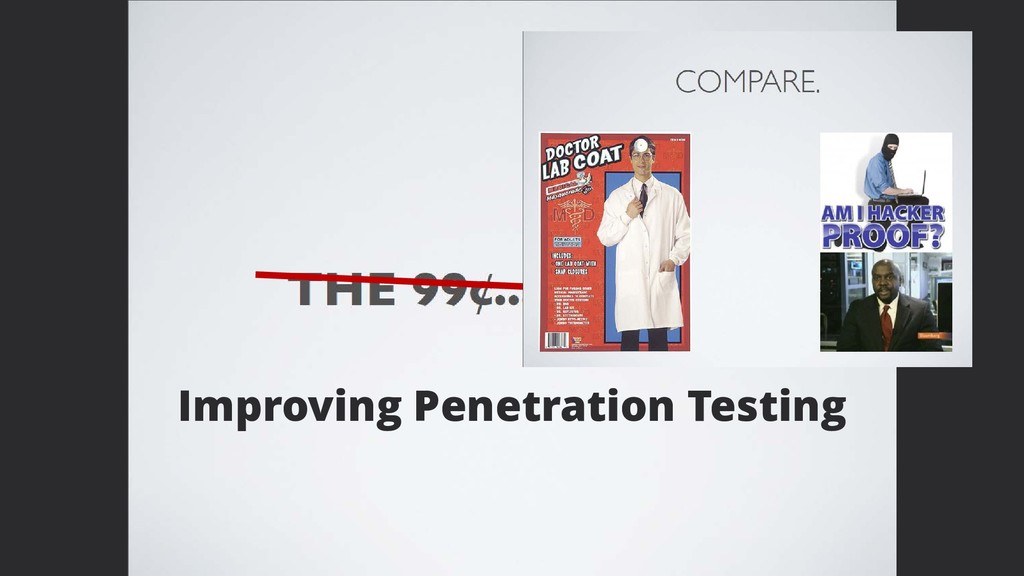
2) You don't want to hire the same guy for 100'000 bucks when he's wearing a white coat and got shiny high tech tools because the last guy paid in advance...
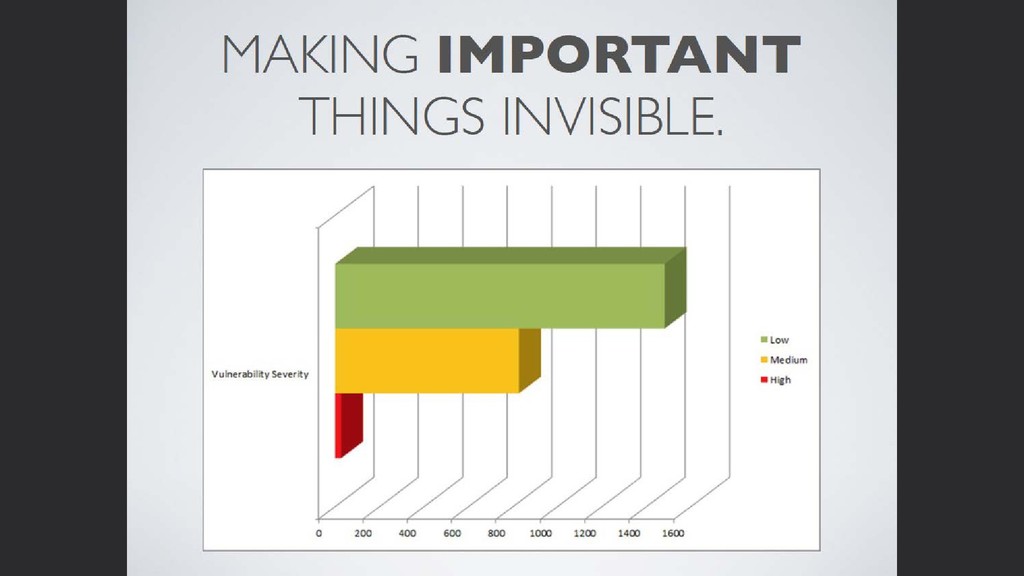
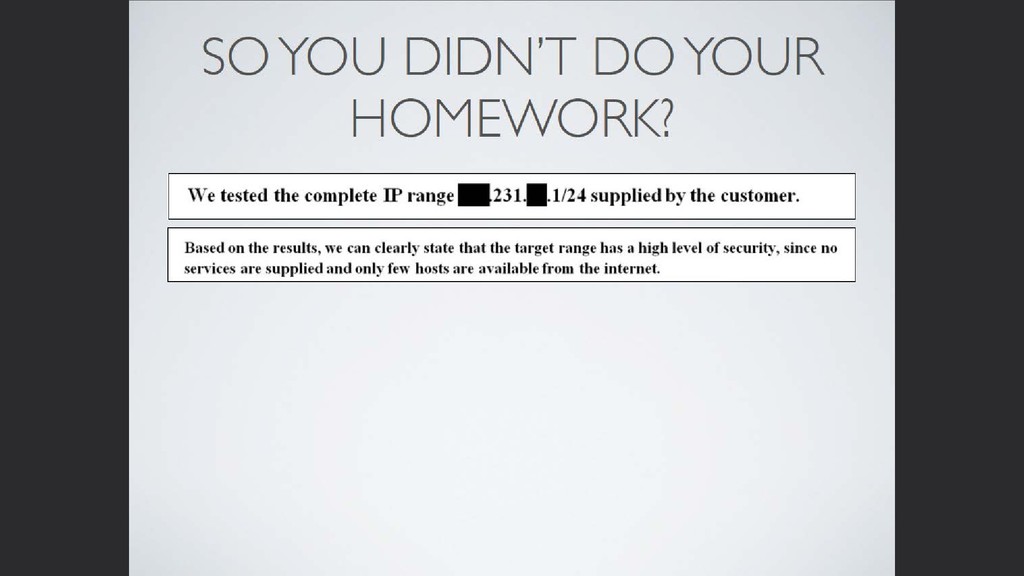
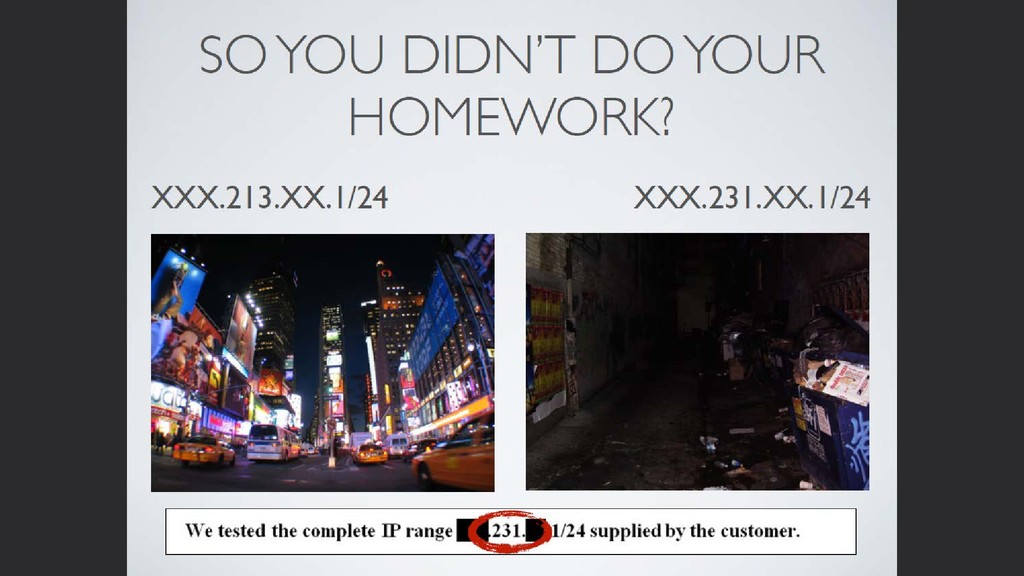
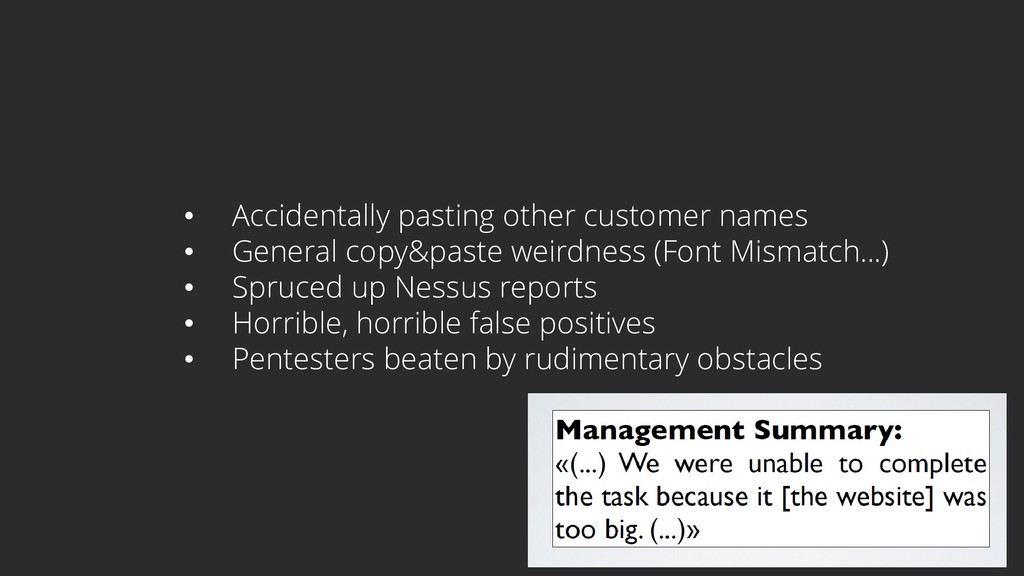
What does this have to do with penetration testing? More than we like, unfortunately. I have met companies that invested thousands of dollars, expecting a pentest and getting a spiced up Nessus report as a result. More subtle nuances of "crappy pentest" might overlook essential threats and leave customers at risk with a false sense of security.
This talk will explore the common mistakes made when performing pentests, which includes the test itself, as well as pre- and post-engagement matters. Also, it applies for testers and customers alike. Also, it might help saving the rainforests.
While revisiting this talk from 2011, we will look into the question: Have things changed for the better and do we still face the same issues?


 stfn42
 genda
 techtekt
 sh_fk2
 riyaamemiya
 pfn
 nttcom
 akitoshiga
 shogo4131
 ykanoh
 sansantech
 namiki64
 occhi
 cassininazir
 malarkey
 bkeepers
 denniskardys
 mfonobong
 chriscoyier
 techseoconnect
 axbom
 akademiya2063
 szymonslowik
 aarron
 sergeychernyshev