Upgrade to Pro — share decks privately, control downloads, hide ads and more …

DevSecOps and Defence in Depth for the Cloud

Avatar for Matt Tyler Matt Tyler
November 21, 2019

DevSecOps and Defence in Depth for the Cloud

While the adoption of DevOps and Cloud have thrown open the gates of productivity for many teams, challenges in governance remain. How do you enable developer innovation while protecting your business and customers? We build “Cloud Native Factories” on AWS, which enable teams to deliver compliant products and innovate rapidly within safe guardrails.

Avatar for Matt Tyler

Matt Tyler

November 21, 2019

More Decks by Matt Tyler

Other Decks in Programming

Transcript

  1. ! Application is delivered via the web, on-demand.
 
 !

    Application - User interaction is driven via client side javascript.
 
 ! Application may communicate with many external resources (API’s, CDN etc) Building a Better SPA “Enterprise JAM Stack”
 
 Javascript
 APIs Markup
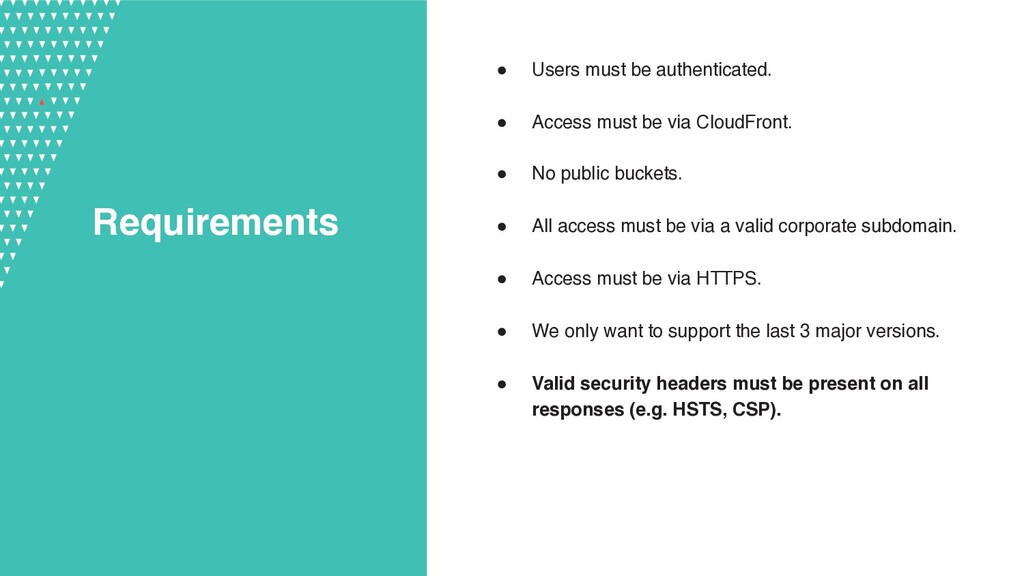
  2. Requirements ! Users must be authenticated.
 ! Access must be

    via CloudFront.
 ! No public buckets.
 ! All access must be via a valid corporate subdomain.
 ! Access must be via HTTPS.
 ! We only want to support the last 3 major versions.
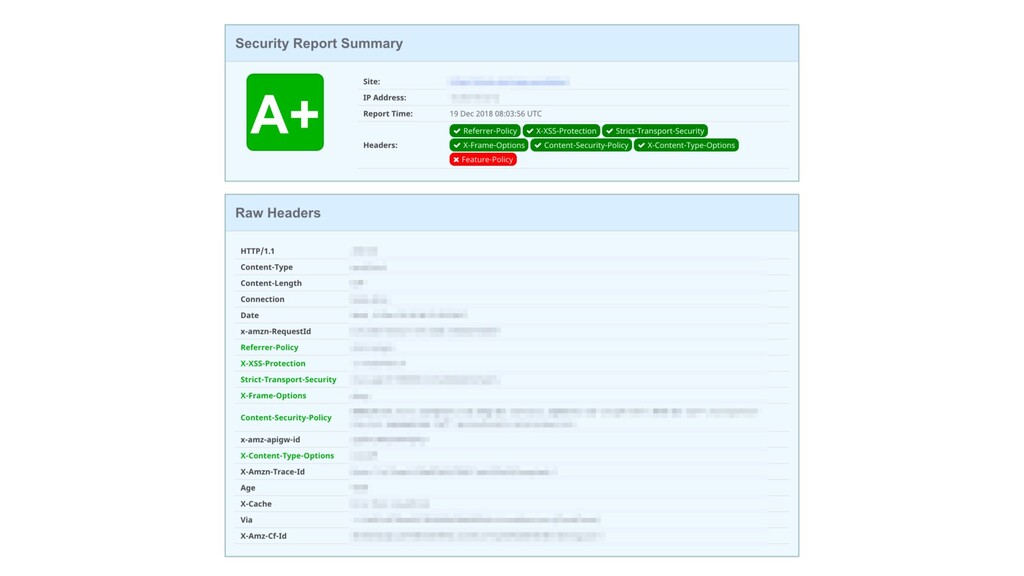
 ! Valid security headers must be present on all responses (e.g. HSTS, CSP).
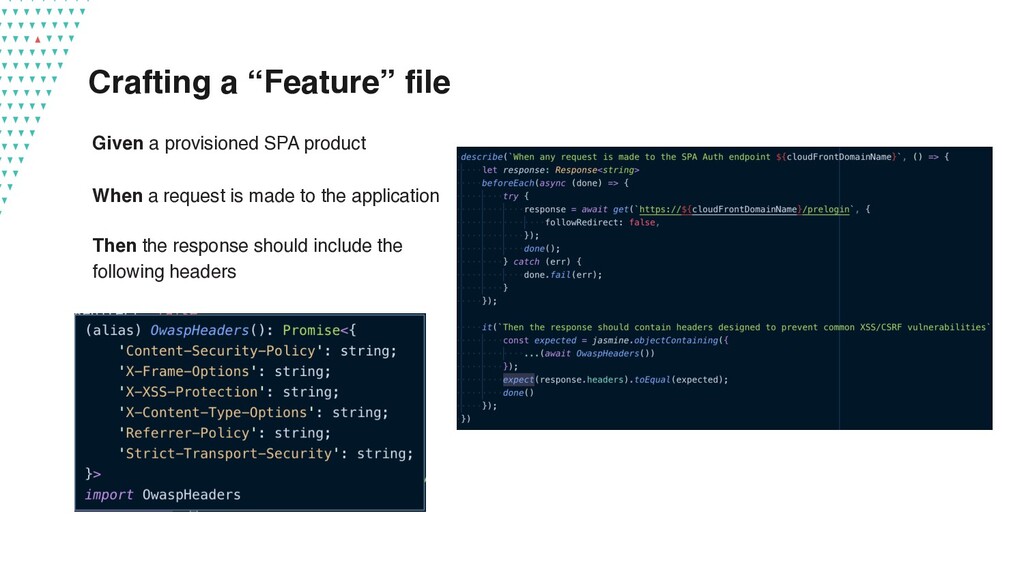
  3. Crafting a “Feature” file Given a provisioned SPA product


    When a request is made to the application Then the response should include the following headers
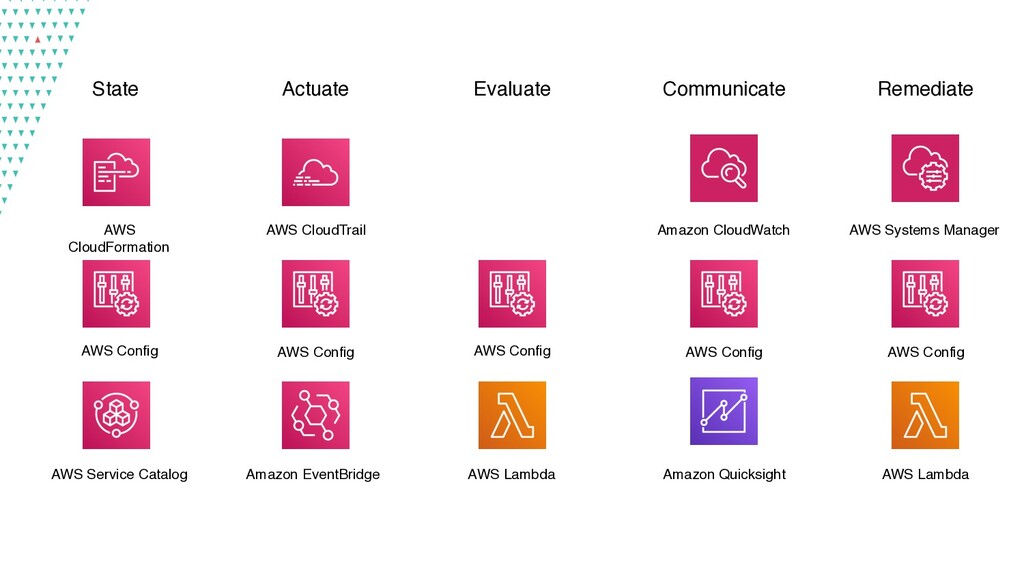
  4. State Actuate Evaluate Communicate Remediate AWS Lambda AWS Lambda AWS

    Config AWS Config AWS Config AWS Config AWS Config AWS CloudFormation AWS CloudTrail AWS Service Catalog Amazon EventBridge Amazon CloudWatch Amazon Quicksight AWS Systems Manager