Upgrade to Pro — share decks privately, control downloads, hide ads and more …

Hunting Vulnerabilities in PHP with LLMs

Sponsored · Your Podcast. Everywhere. Effortlessly. Share. Educate. Inspire. Entertain. You do you. We'll handle the rest. →

Hunting Vulnerabilities in PHP with LLMs

Talk given at the
IPC Munich September 2027

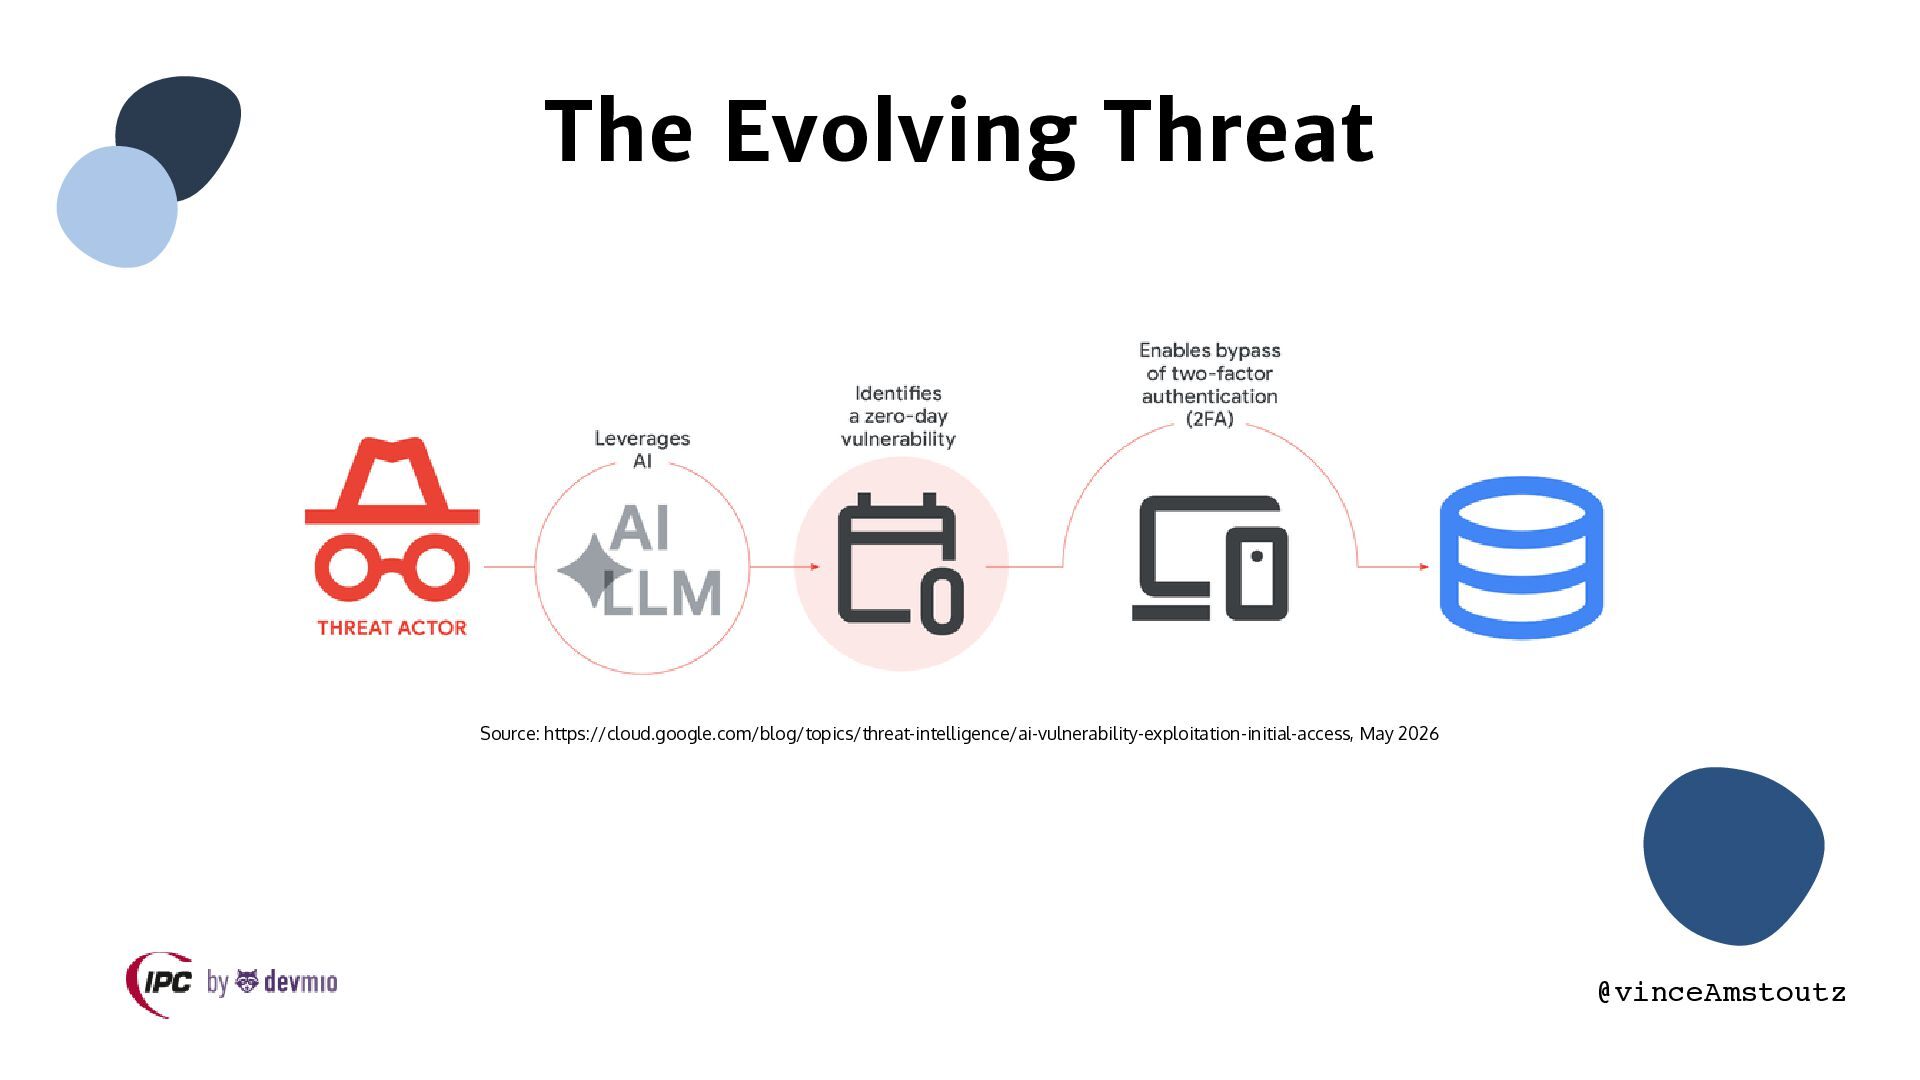
Hackers are already using Large Language Models to map your attack surface, it’s time you used them to defend it.

While we’ve spent years trying to write the perfect regex or rule-set to catch bugs, LLMs have unlocked a terrifyingly effective ability to understand the intent and context of our Symfony and PHP code.

This session dives into the practical reality of using AI as an autonomous security researcher to uncover deep-seated vulnerabilities in Symfony applications that traditional tools simply cannot see.

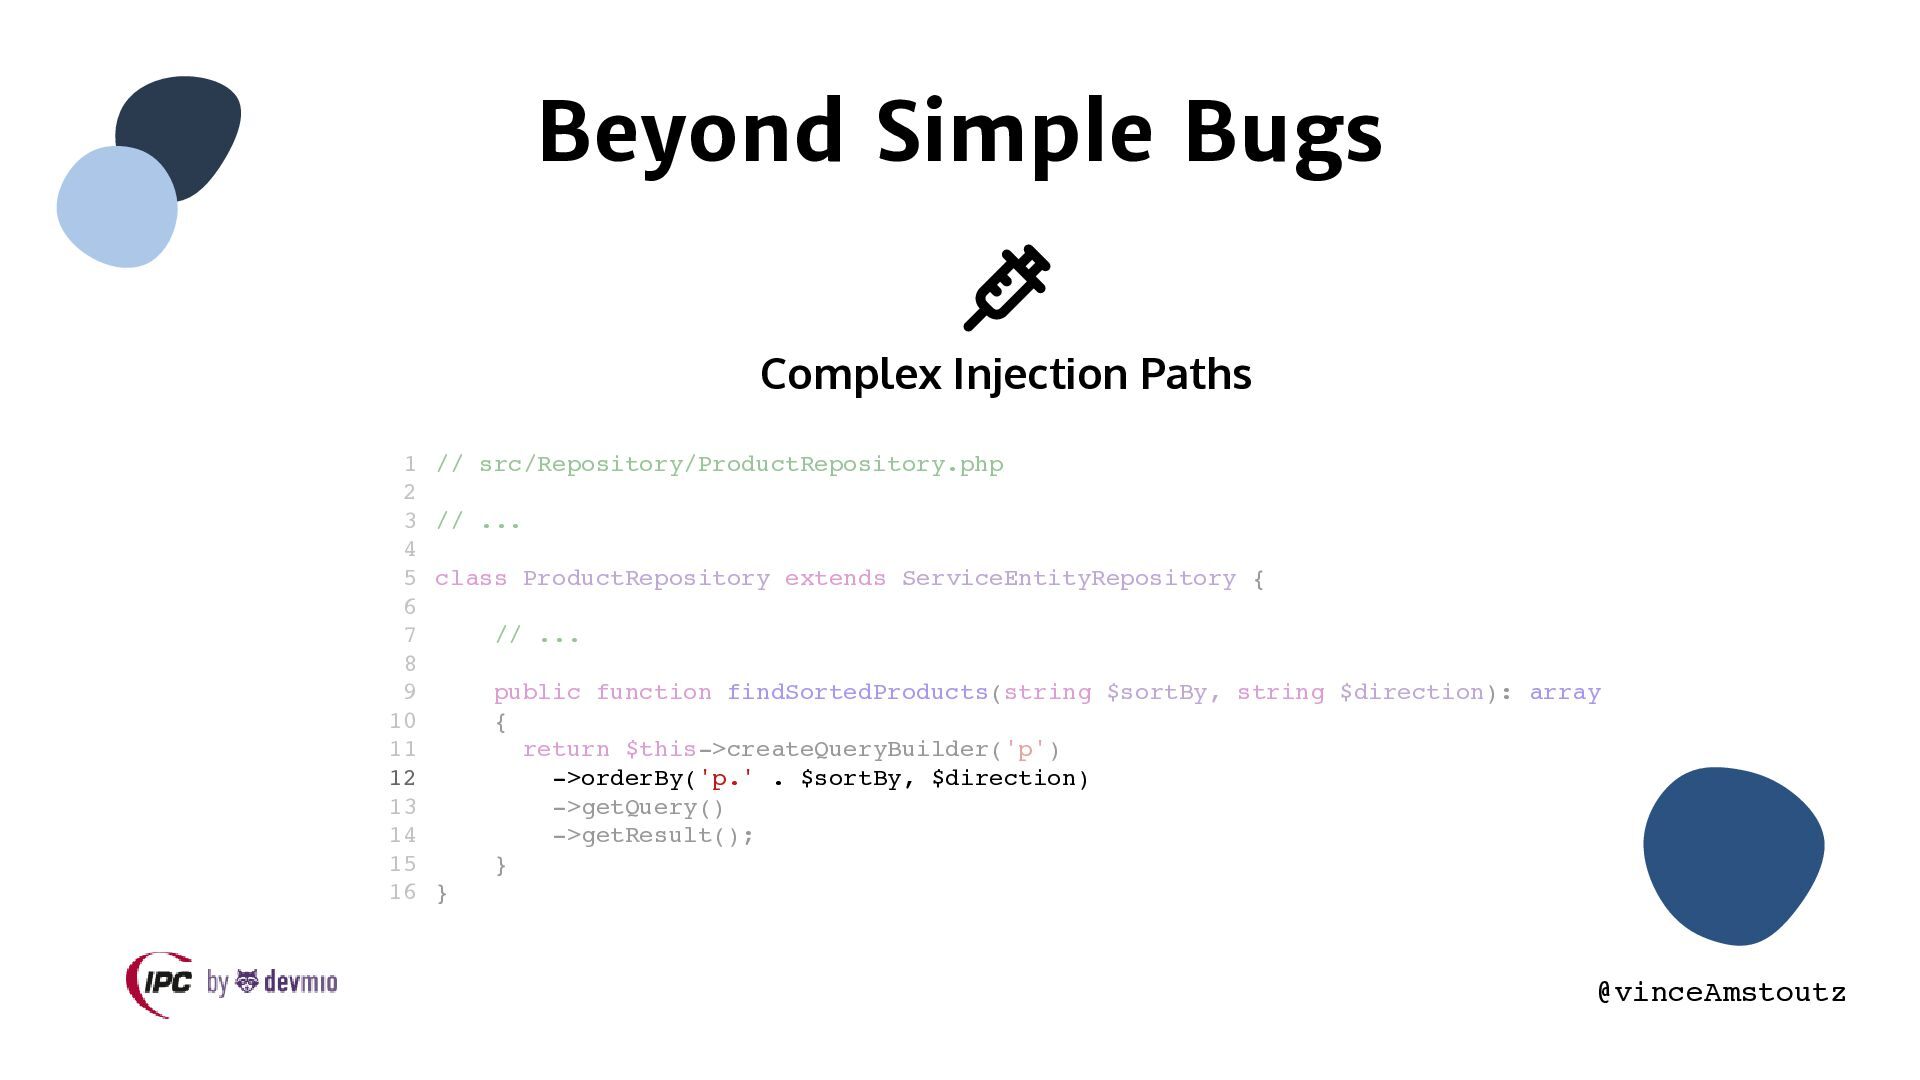
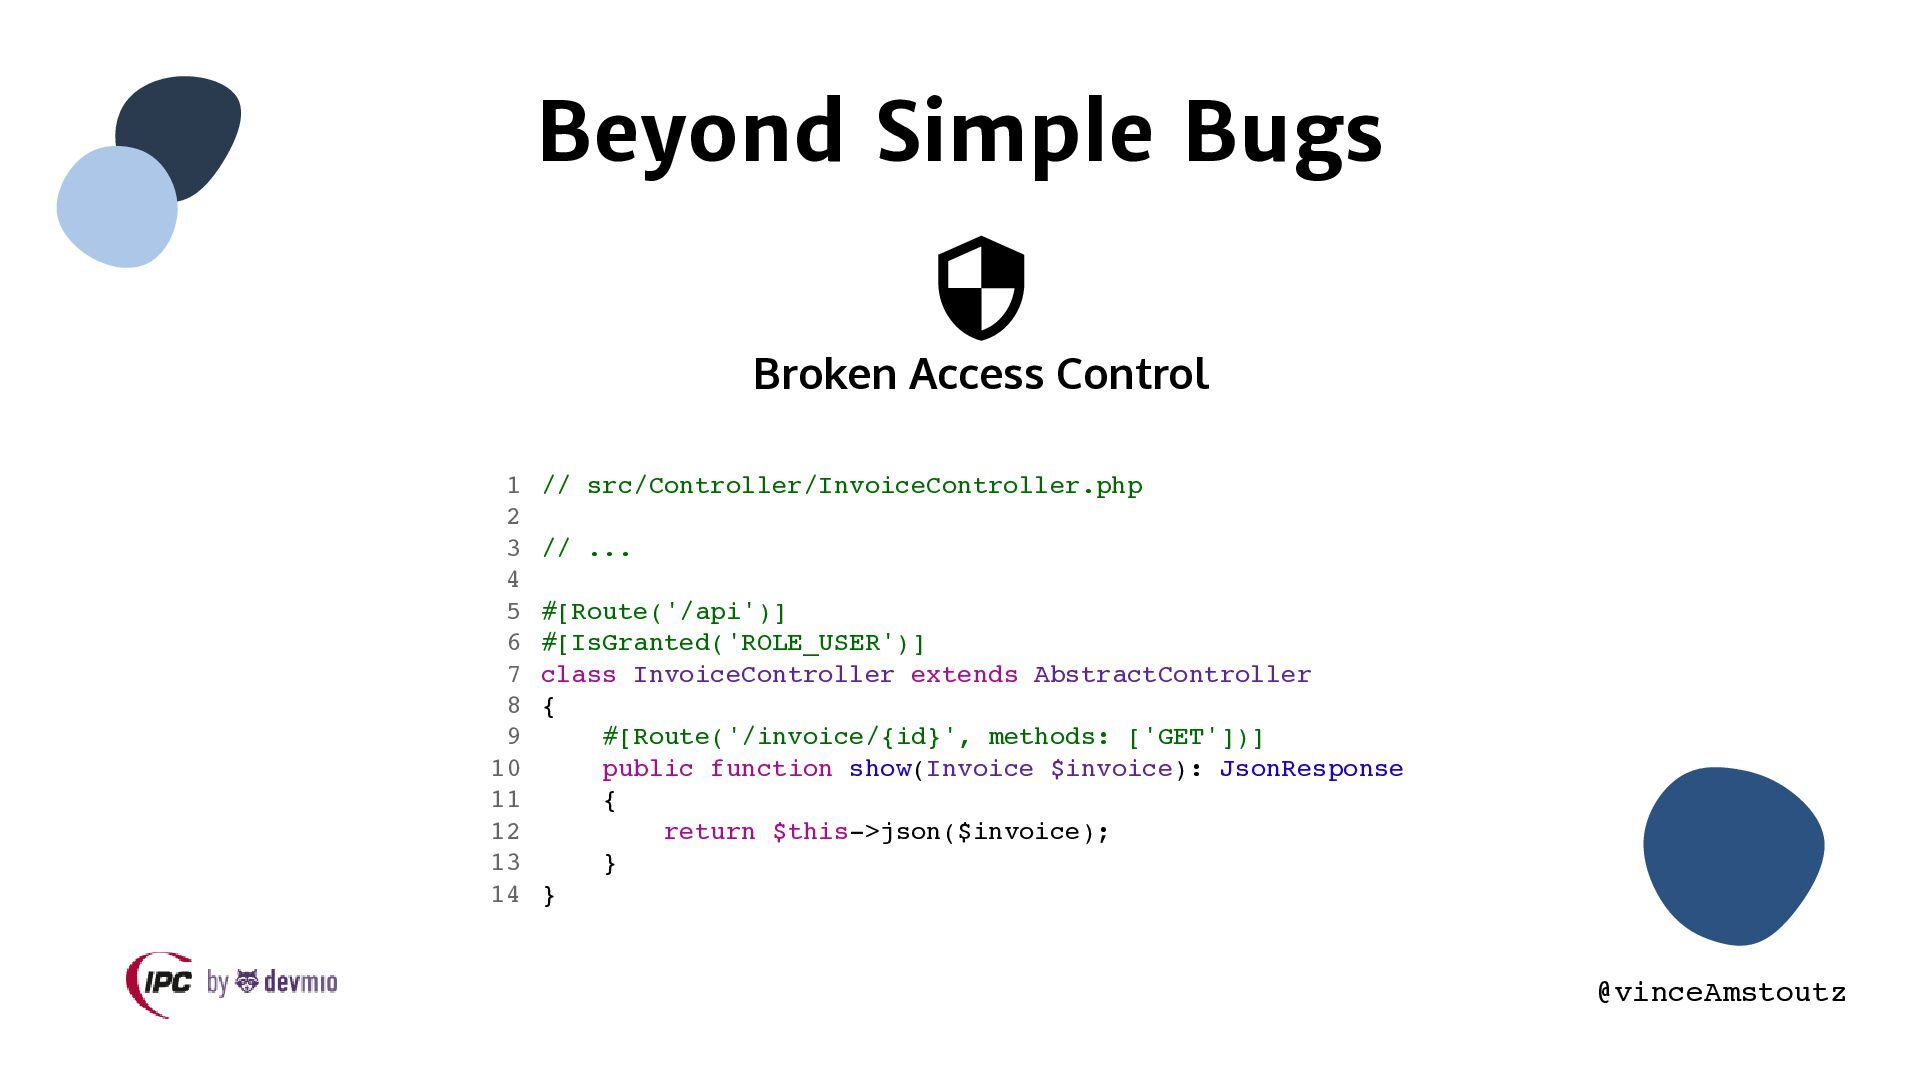
We will explore how to architect a high-speed security pipeline that feeds your codebase to an LLM to detect broken access control, complex injection paths, and logic flaws in real-time.

You’ll walk away with a battle-tested strategy to weaponize AI against your own technical debt, turning the most unpredictable technology of our time into your most meticulous security auditor.

Avatar for Vincent Amstoutz

Vincent Amstoutz

November 05, 2026

More Decks by Vincent Amstoutz

Other Decks in Programming
Transcript

  1. Vincent Amstoutz EXPERT BACKEND DEVELOPER @Swikly | Also freelance (Part-time)

    MAIN OSS CONTRIBUTIONS Creator of Symfony Security Auditor API Platform Core Team FrankenPHP Symfony
  2. Vincent Amstoutz EXPERT BACKEND DEVELOPER @Swikly | Also freelance (Part-time)

    MAIN OSS CONTRIBUTIONS Creator of Symfony Security Auditor FrankenPHP API Platform Core Team @vinceAmstoutz https://vince-amstoutz.tech Symfony
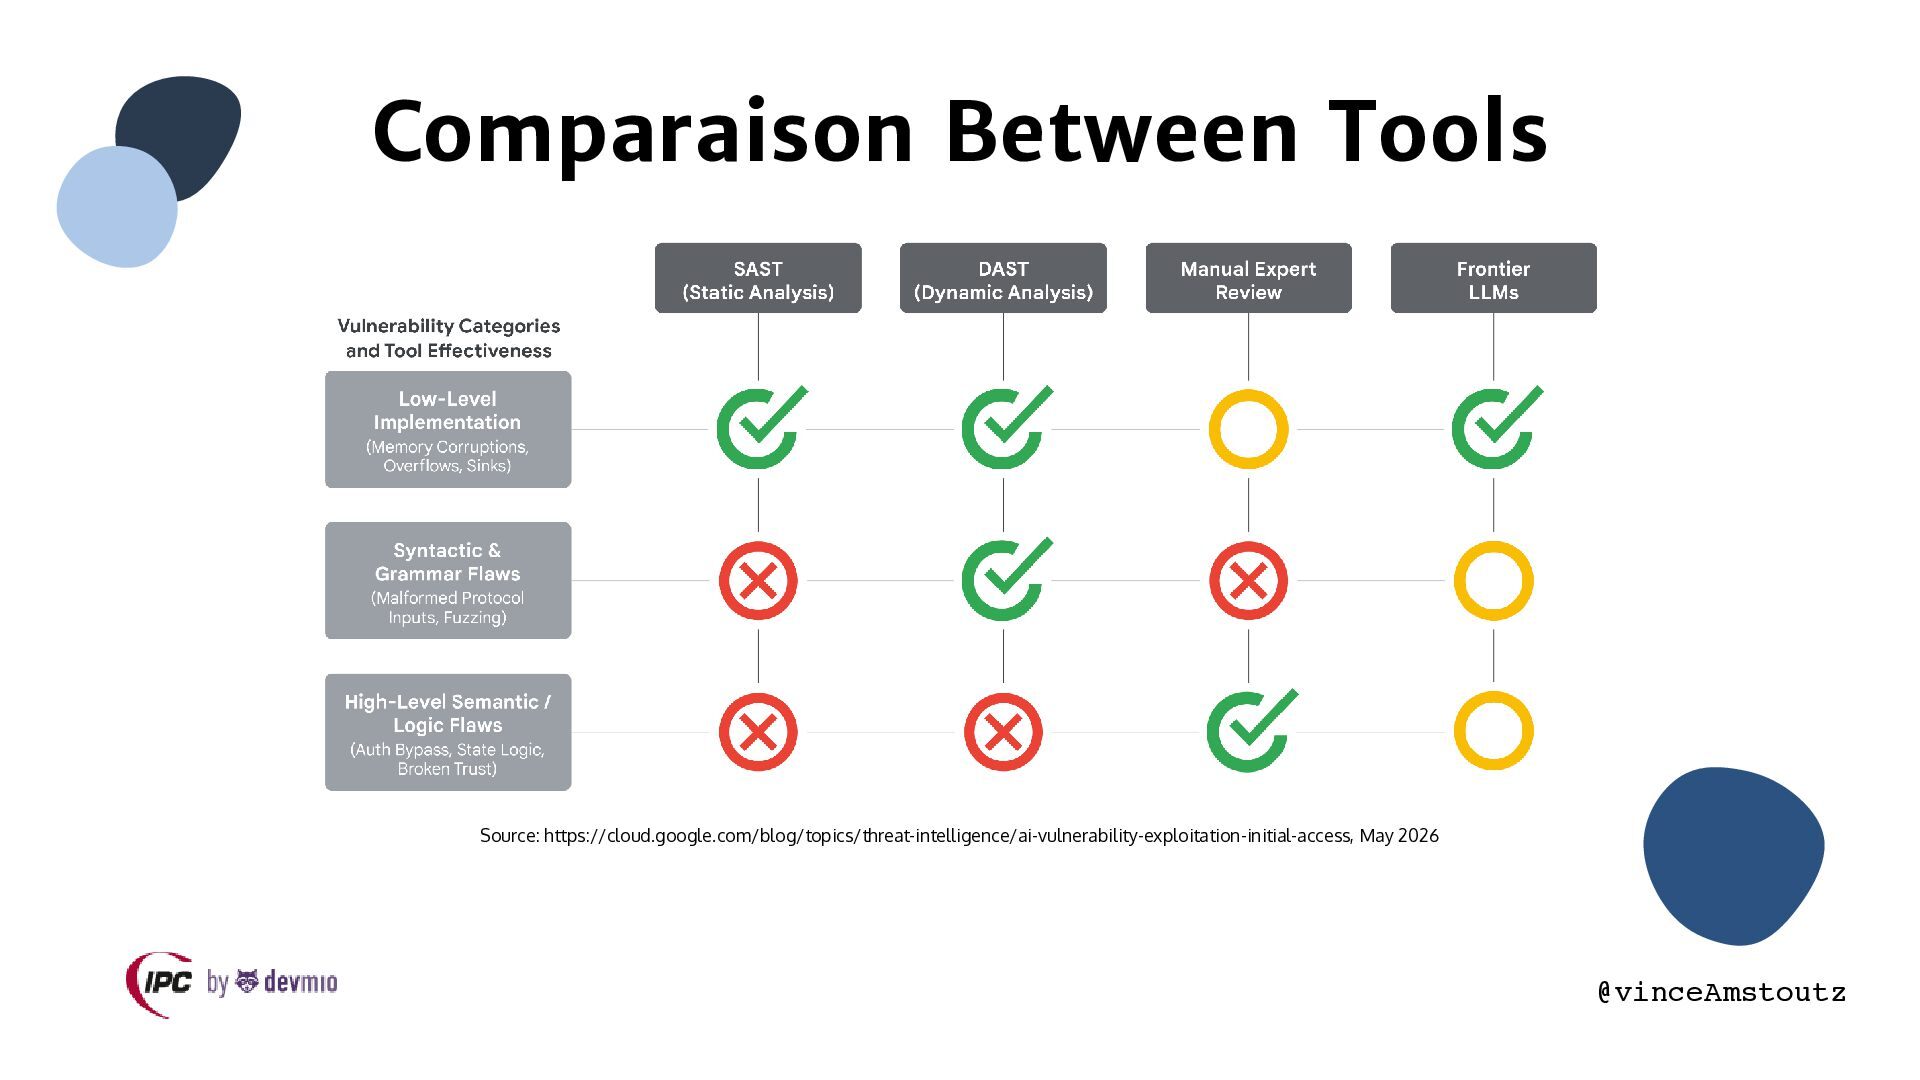
  3. Why Traditional Tools Fail? Syntax vs. Intent Legacy SAST tools

    rely on "Regex patterns". @vinceAmstoutz
  4. Why Traditional Tools Fail? Syntax vs. Intent Context is King

    Legacy SAST tools rely on "Regex patterns". LLMs understand the deep relationship between a Controller, a Voter, and the Database. @vinceAmstoutz
  5. Problems caused 1 2 Hyper-Accelerated Discovery Instant Weaponization Fast zero-day

    discovery. Fast zero-day implementation. @vinceAmstoutz
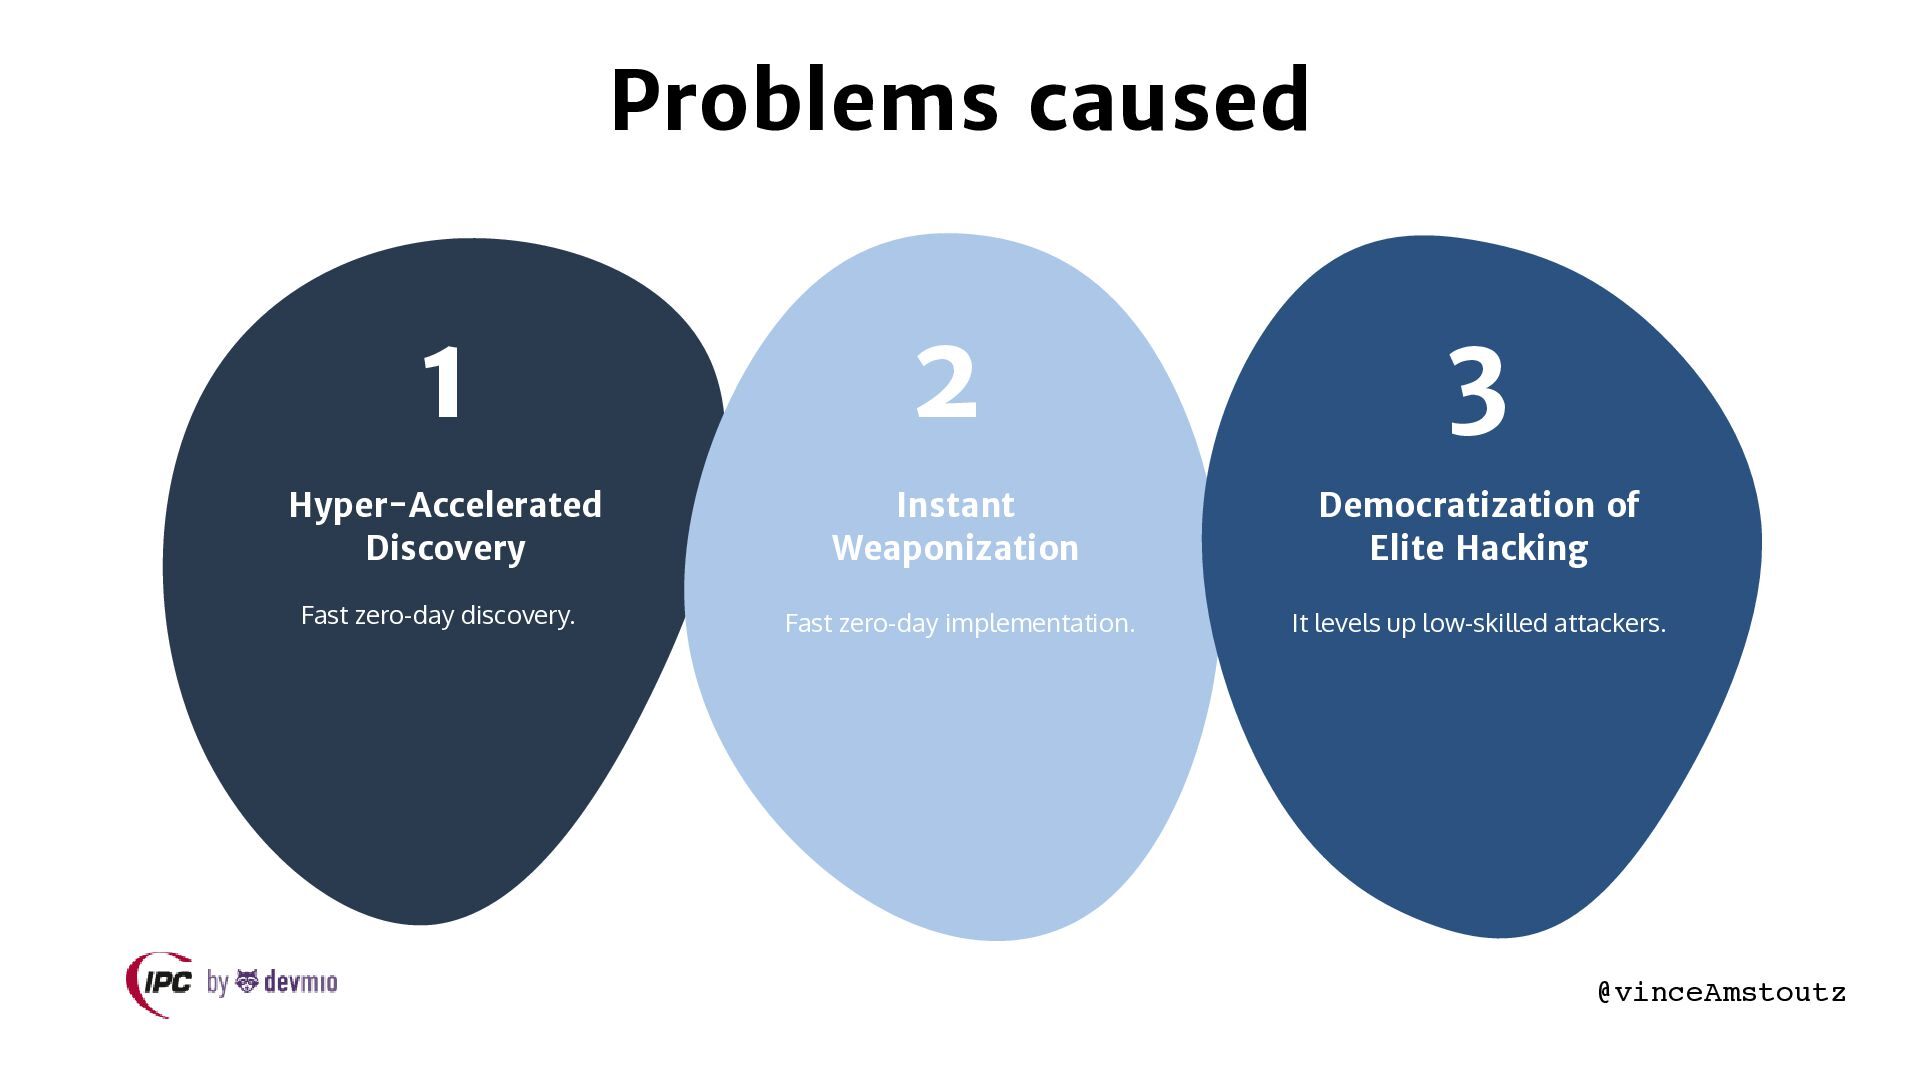
  6. Problems caused 1 2 3 Hyper-Accelerated Discovery Instant Weaponization Democratization

    of Elite Hacking Fast zero-day discovery. Fast zero-day implementation. It levels up low-skilled attackers. @vinceAmstoutz
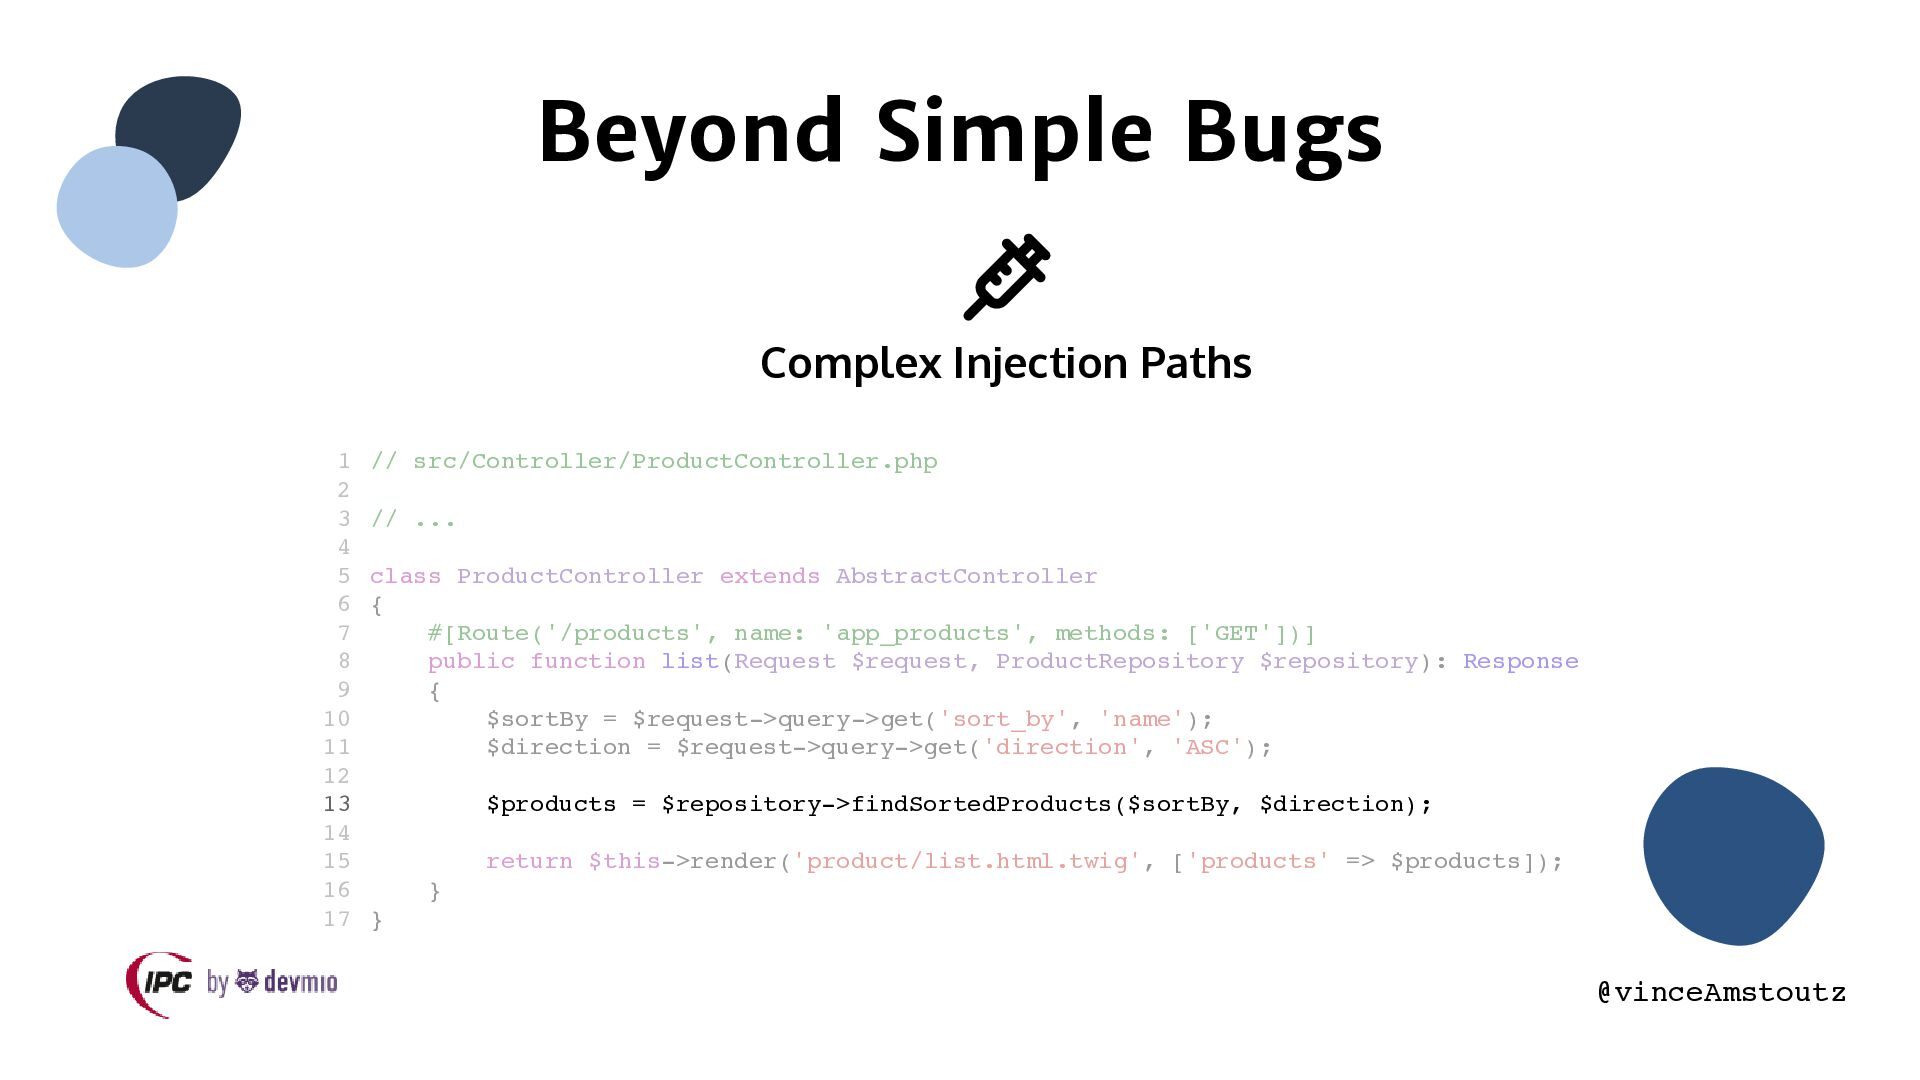
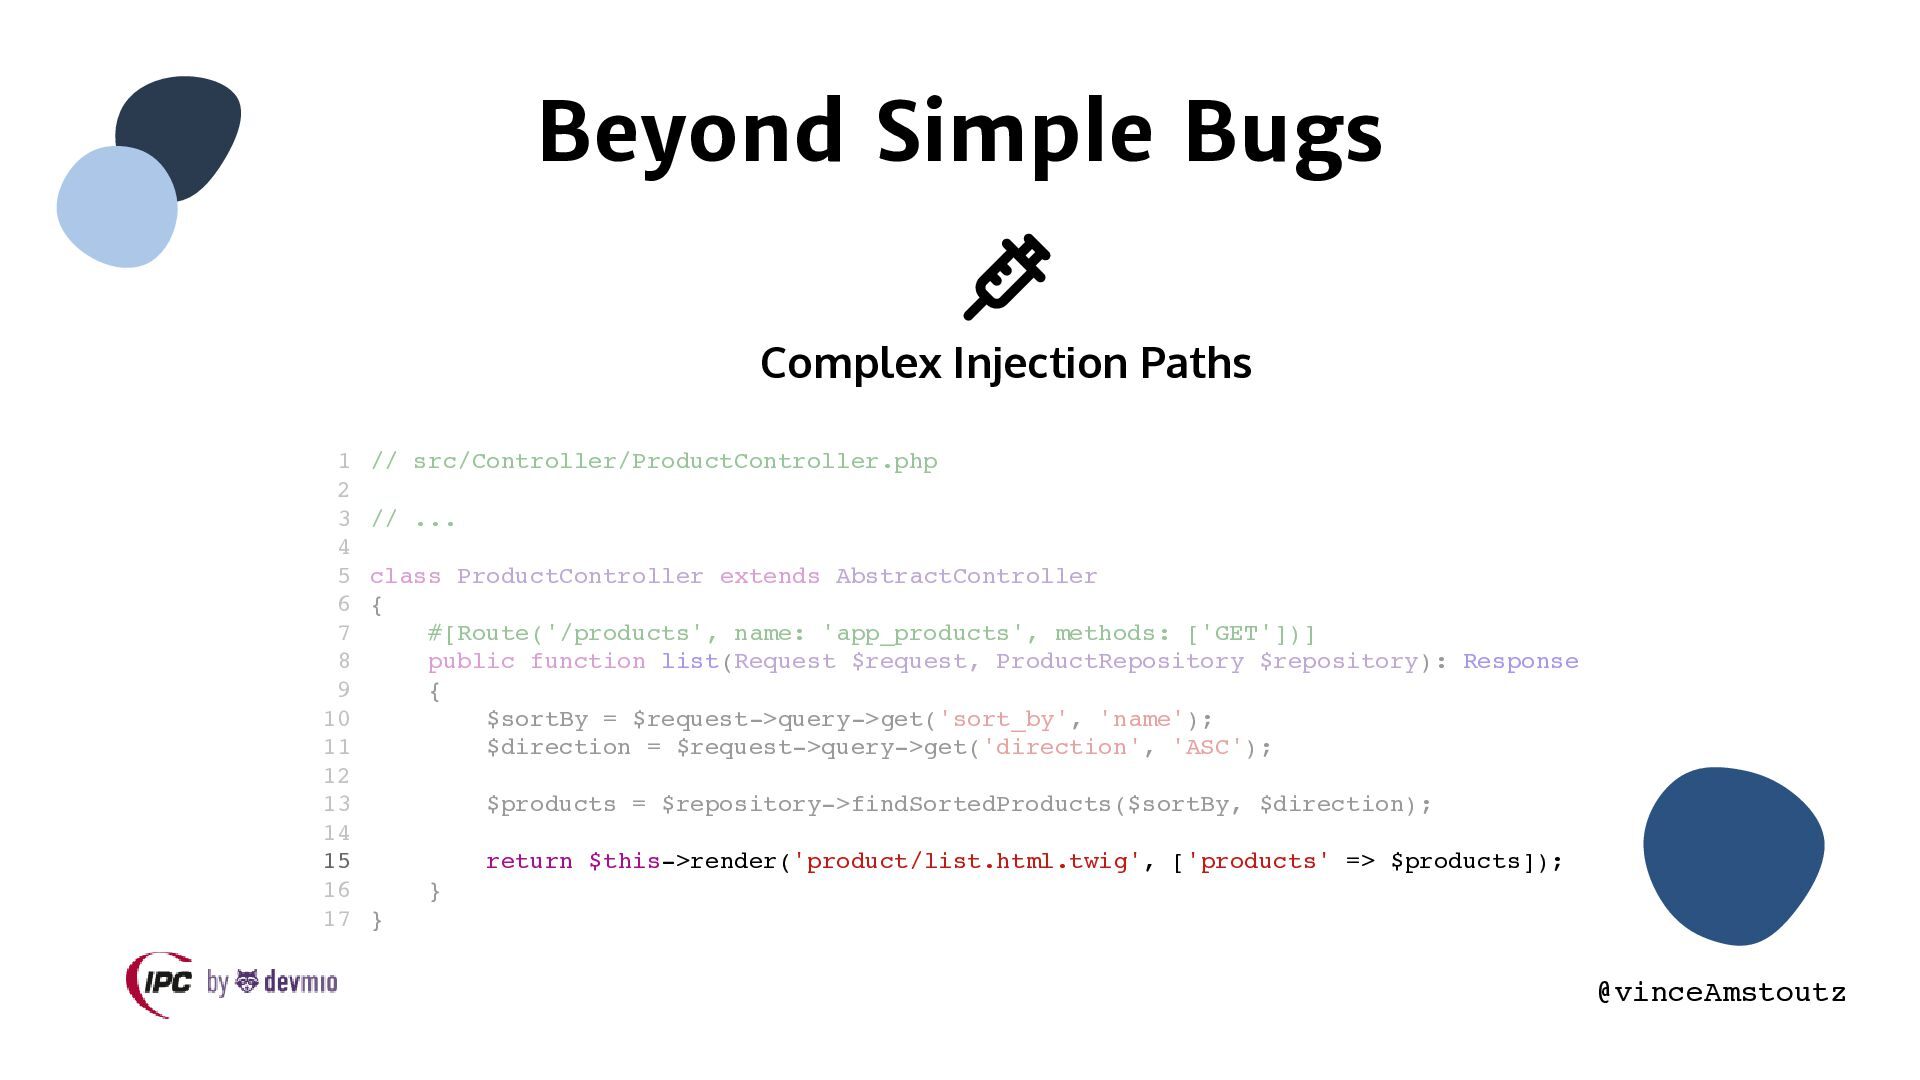
  7. Beyond Simple Bugs Complex Injection Paths 1 2 3 4

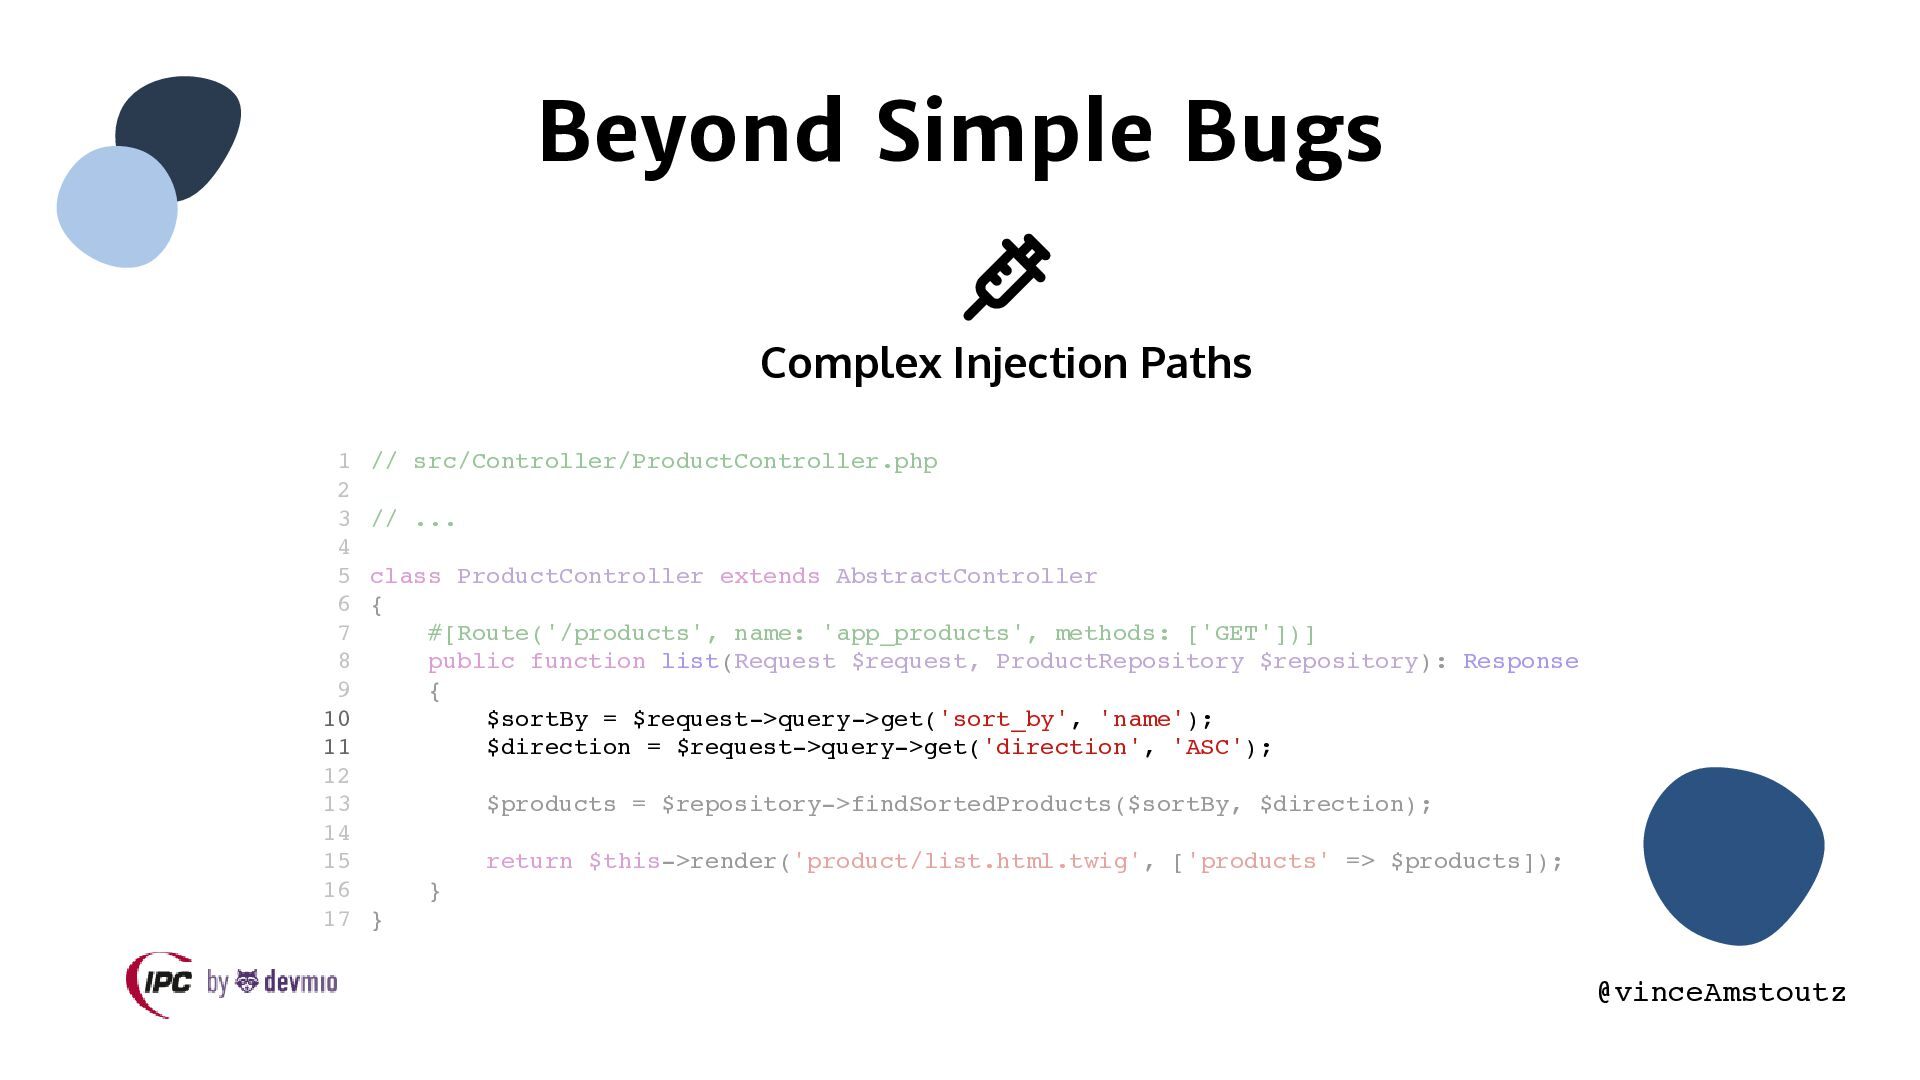
    5 6 7 8 9 10 11 12 13 14 15 16 17 // src/Controller/ProductController.php // ... class ProductController extends AbstractController { #[Route('/products', name: 'app_products', methods: ['GET'])] public function list(Request $request, ProductRepository $repository): Response { $sortBy = $request->query->get('sort_by', 'name'); $direction = $request->query->get('direction', 'ASC'); $products = $repository->findSortedProducts($sortBy, $direction); return $this->render('product/list.html.twig', ['products' => $products]); } } @vinceAmstoutz
  8. Beyond Simple Bugs Complex Injection Paths 1 2 3 4

    5 6 7 8 9 10 11 12 13 14 15 16 17 // src/Controller/ProductController.php // ... class ProductController extends AbstractController { #[Route('/products', name: 'app_products', methods: ['GET'])] public function list(Request $request, ProductRepository $repository): Response { $sortBy = $request->query->get('sort_by', 'name'); $direction = $request->query->get('direction', 'ASC'); $products = $repository->findSortedProducts($sortBy, $direction); return $this->render('product/list.html.twig', ['products' => $products]); } } @vinceAmstoutz
  9. Beyond Simple Bugs Complex Injection Paths 1 2 3 4

    5 6 7 8 9 10 11 12 13 14 15 16 17 // src/Controller/ProductController.php // ... class ProductController extends AbstractController { #[Route('/products', name: 'app_products', methods: ['GET'])] public function list(Request $request, ProductRepository $repository): Response { $sortBy = $request->query->get('sort_by', 'name'); $direction = $request->query->get('direction', 'ASC'); $products = $repository->findSortedProducts($sortBy, $direction); return $this->render('product/list.html.twig', ['products' => $products]); } } @vinceAmstoutz
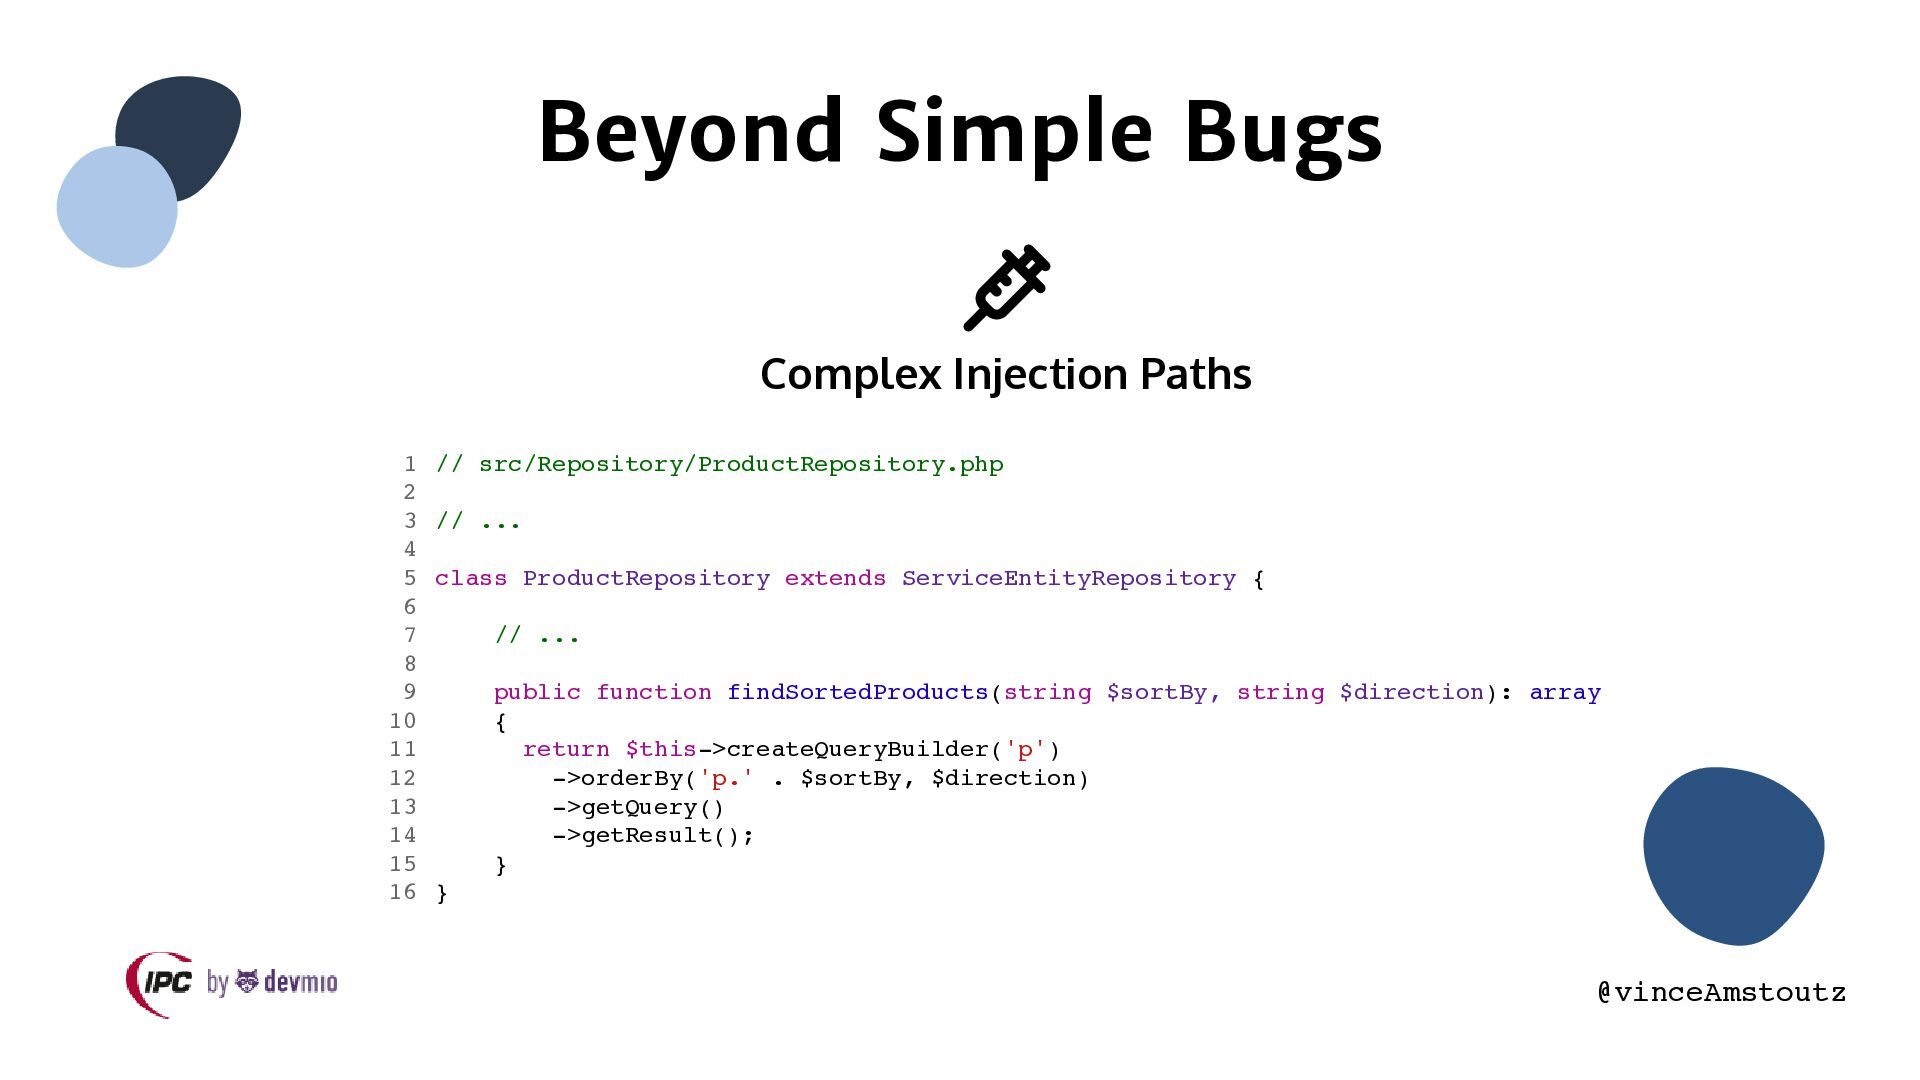
  10. Beyond Simple Bugs Complex Injection Paths 1 2 3 4

    5 6 7 8 9 10 11 12 13 14 15 16 // src/Repository/ProductRepository.php // ... class ProductRepository extends ServiceEntityRepository { // ... public function findSortedProducts(string $sortBy, string $direction): array { return $this->createQueryBuilder('p') ->orderBy('p.' . $sortBy, $direction) ->getQuery() ->getResult(); } } @vinceAmstoutz
  11. Beyond Simple Bugs Complex Injection Paths 1 2 3 4

    5 6 7 8 9 10 11 12 13 14 15 16 // src/Repository/ProductRepository.php // ... class ProductRepository extends ServiceEntityRepository { // ... public function findSortedProducts(string $sortBy, string $direction): array { return $this->createQueryBuilder('p') ->orderBy('p.' . $sortBy, $direction) ->getQuery() ->getResult(); } } @vinceAmstoutz
  12. Beyond Simple Bugs Broken Access Control 1 2 3 4

    5 6 7 8 9 10 11 12 13 14 // src/Controller/InvoiceController.php // ... #[Route('/api')] #[IsGranted('ROLE_USER')] class InvoiceController extends AbstractController { #[Route('/invoice/{id}', methods: ['GET'])] public function show(Invoice $invoice): JsonResponse { return $this->json($invoice); } } @vinceAmstoutz
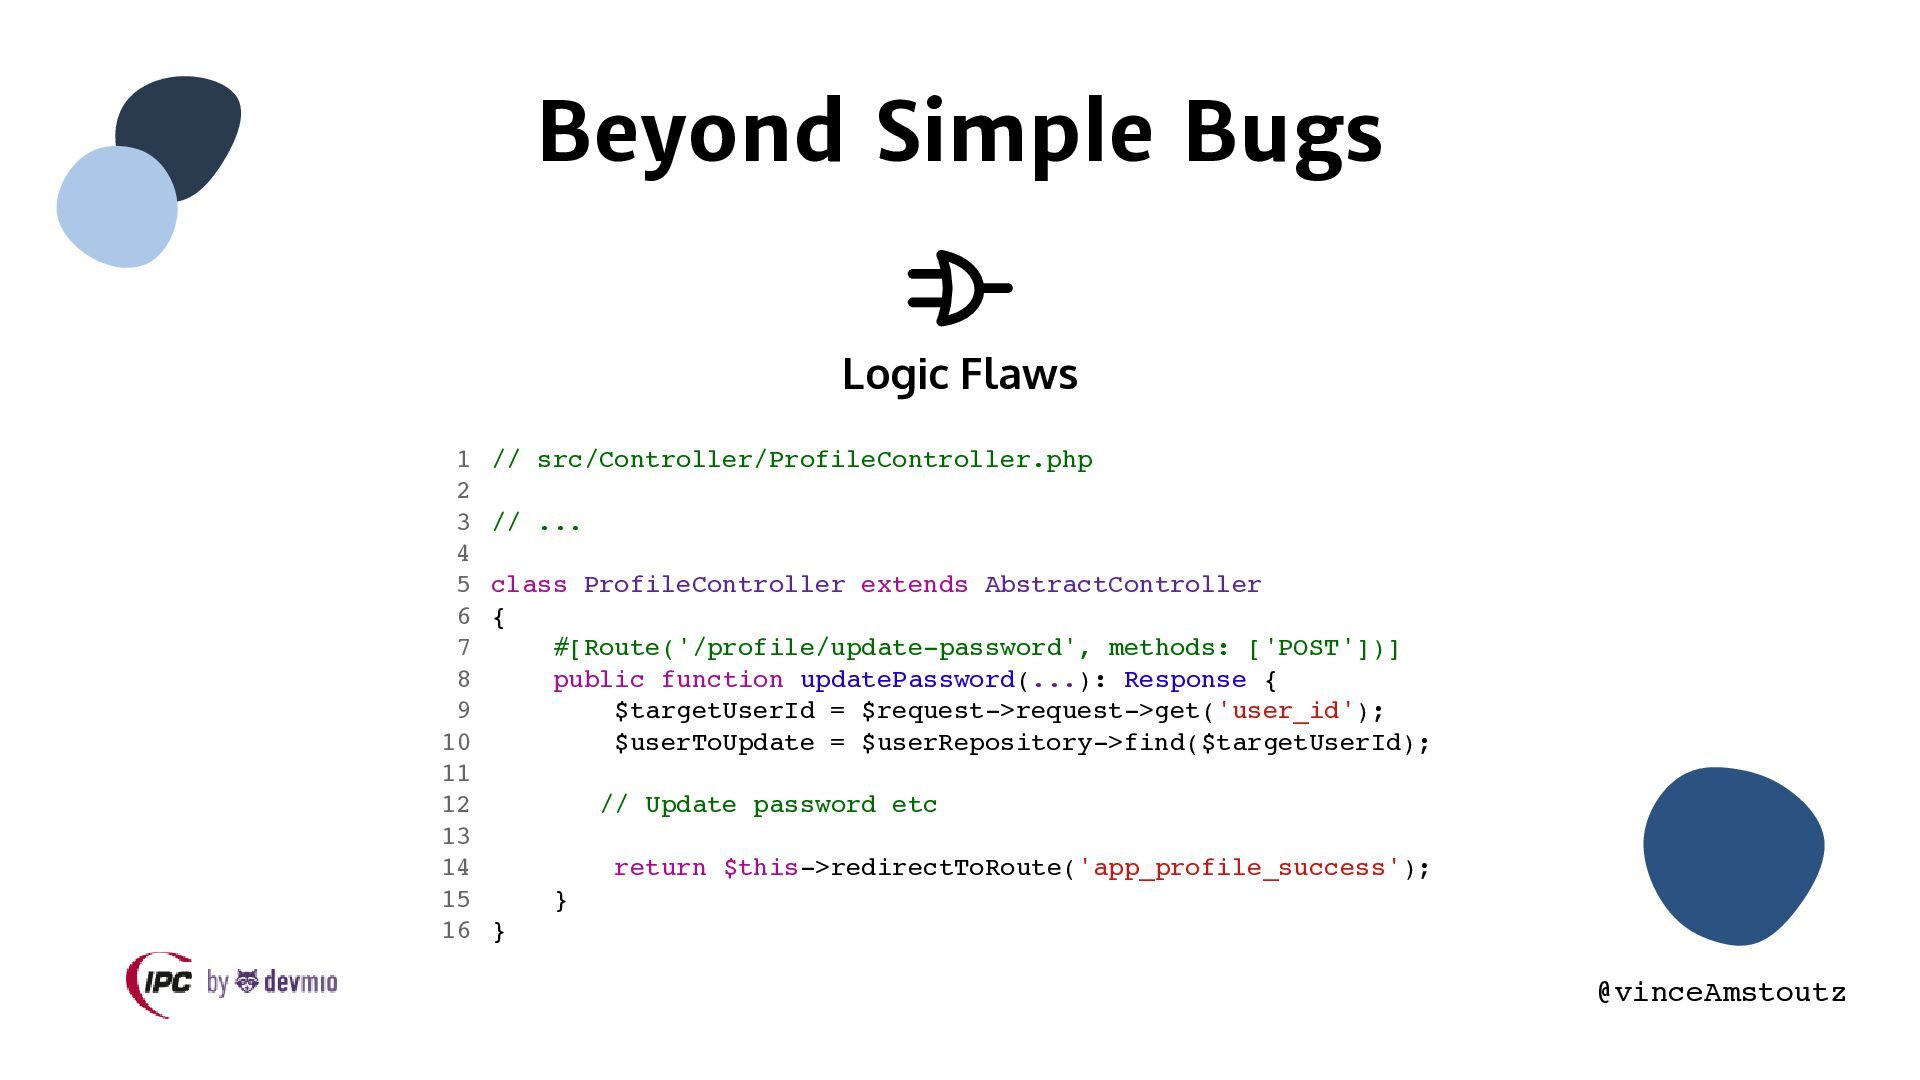
  13. Beyond Simple Bugs Logic Flaws 1 2 3 4 5

    6 7 8 9 10 11 12 13 14 15 16 // src/Controller/ProfileController.php // ... class ProfileController extends AbstractController { #[Route('/profile/update-password', methods: ['POST'])] public function updatePassword(...): Response { $targetUserId = $request->request->get('user_id'); $userToUpdate = $userRepository->find($targetUserId); // Update password etc return $this->redirectToRoute('app_profile_success'); } } @vinceAmstoutz
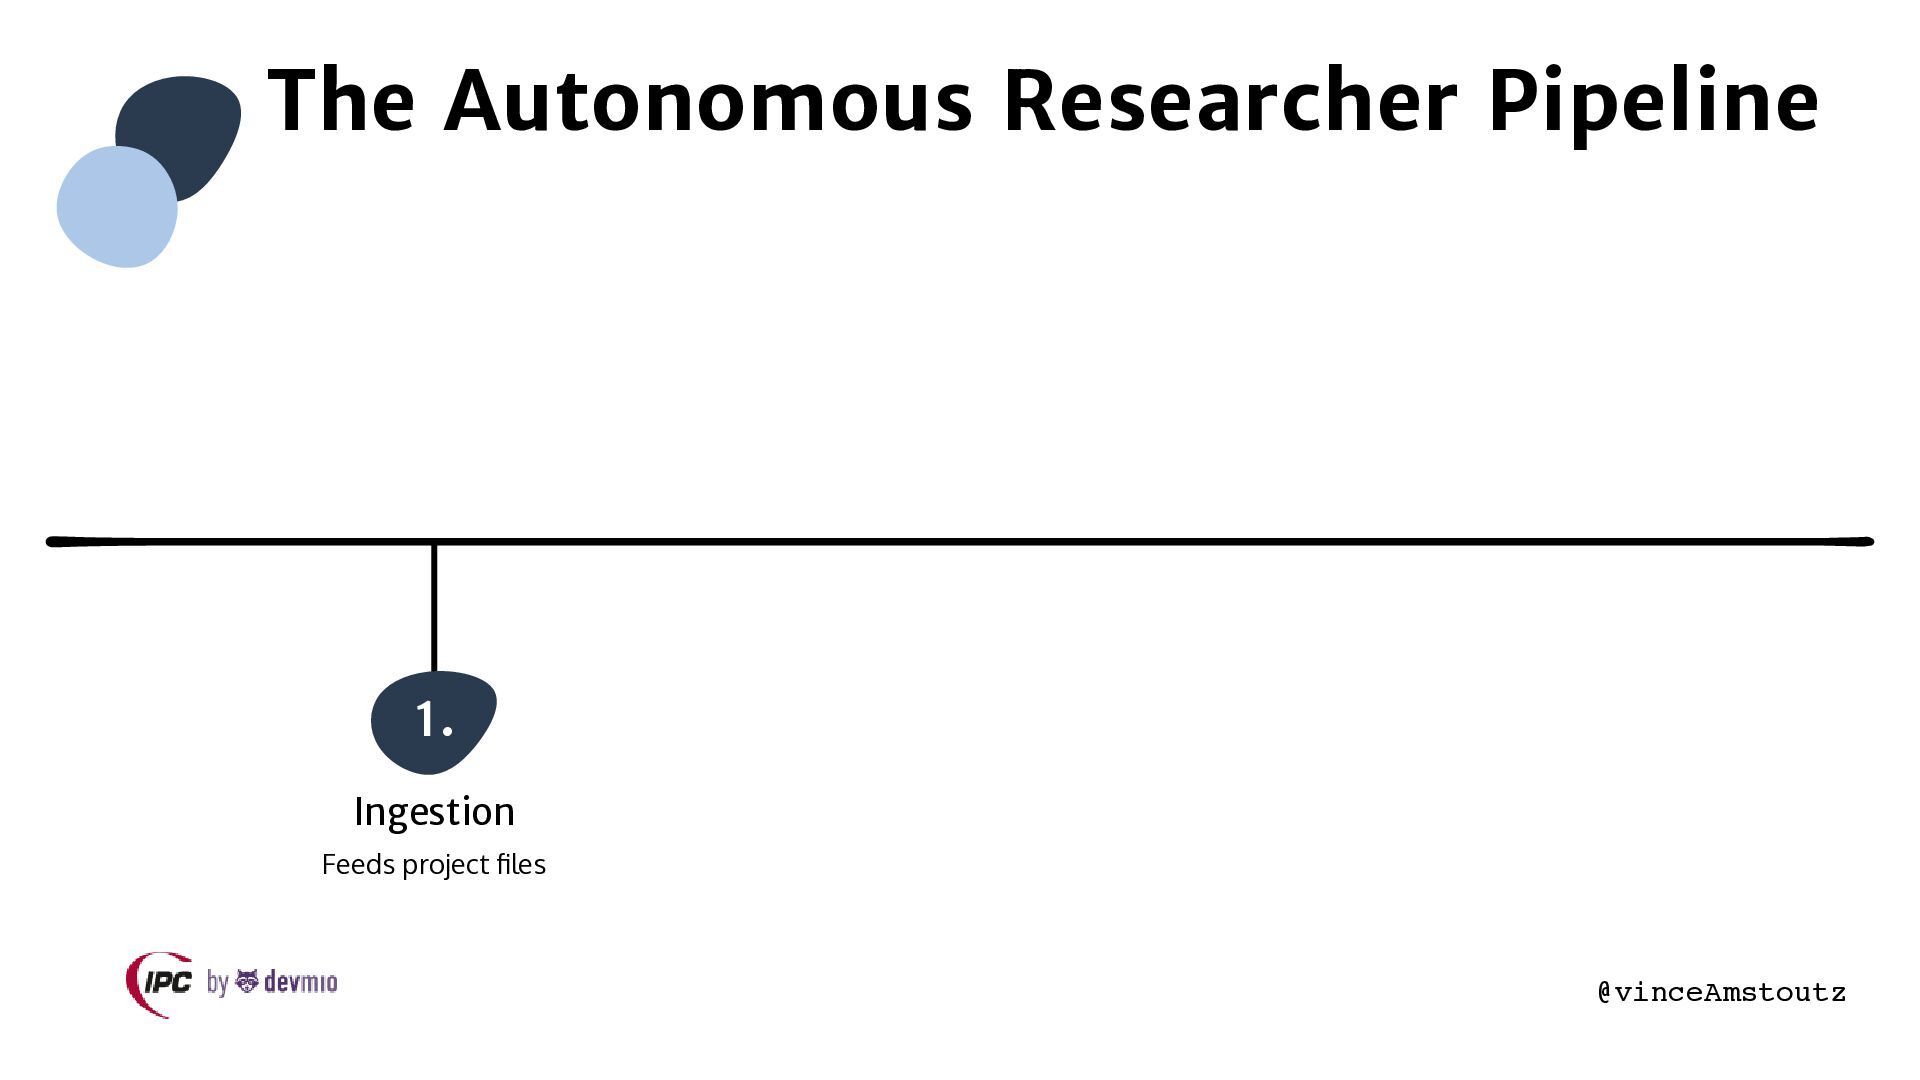
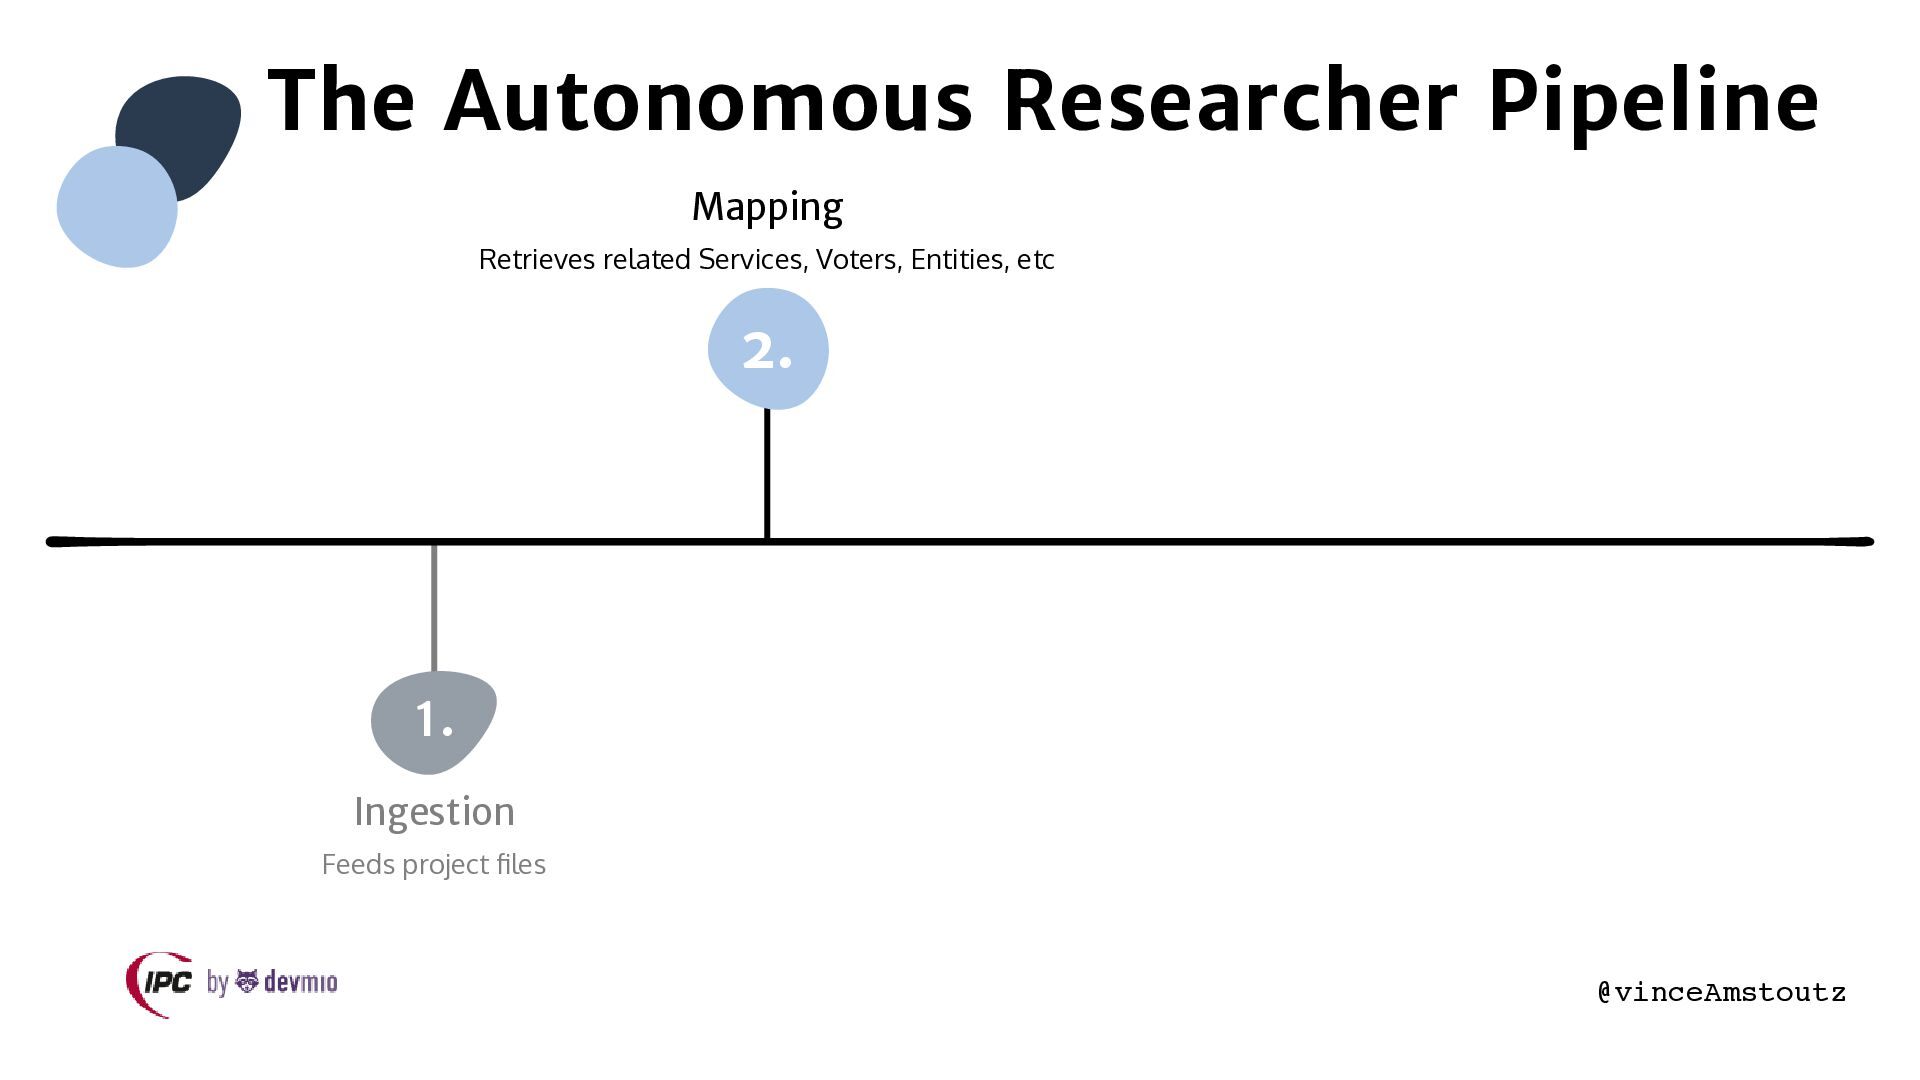
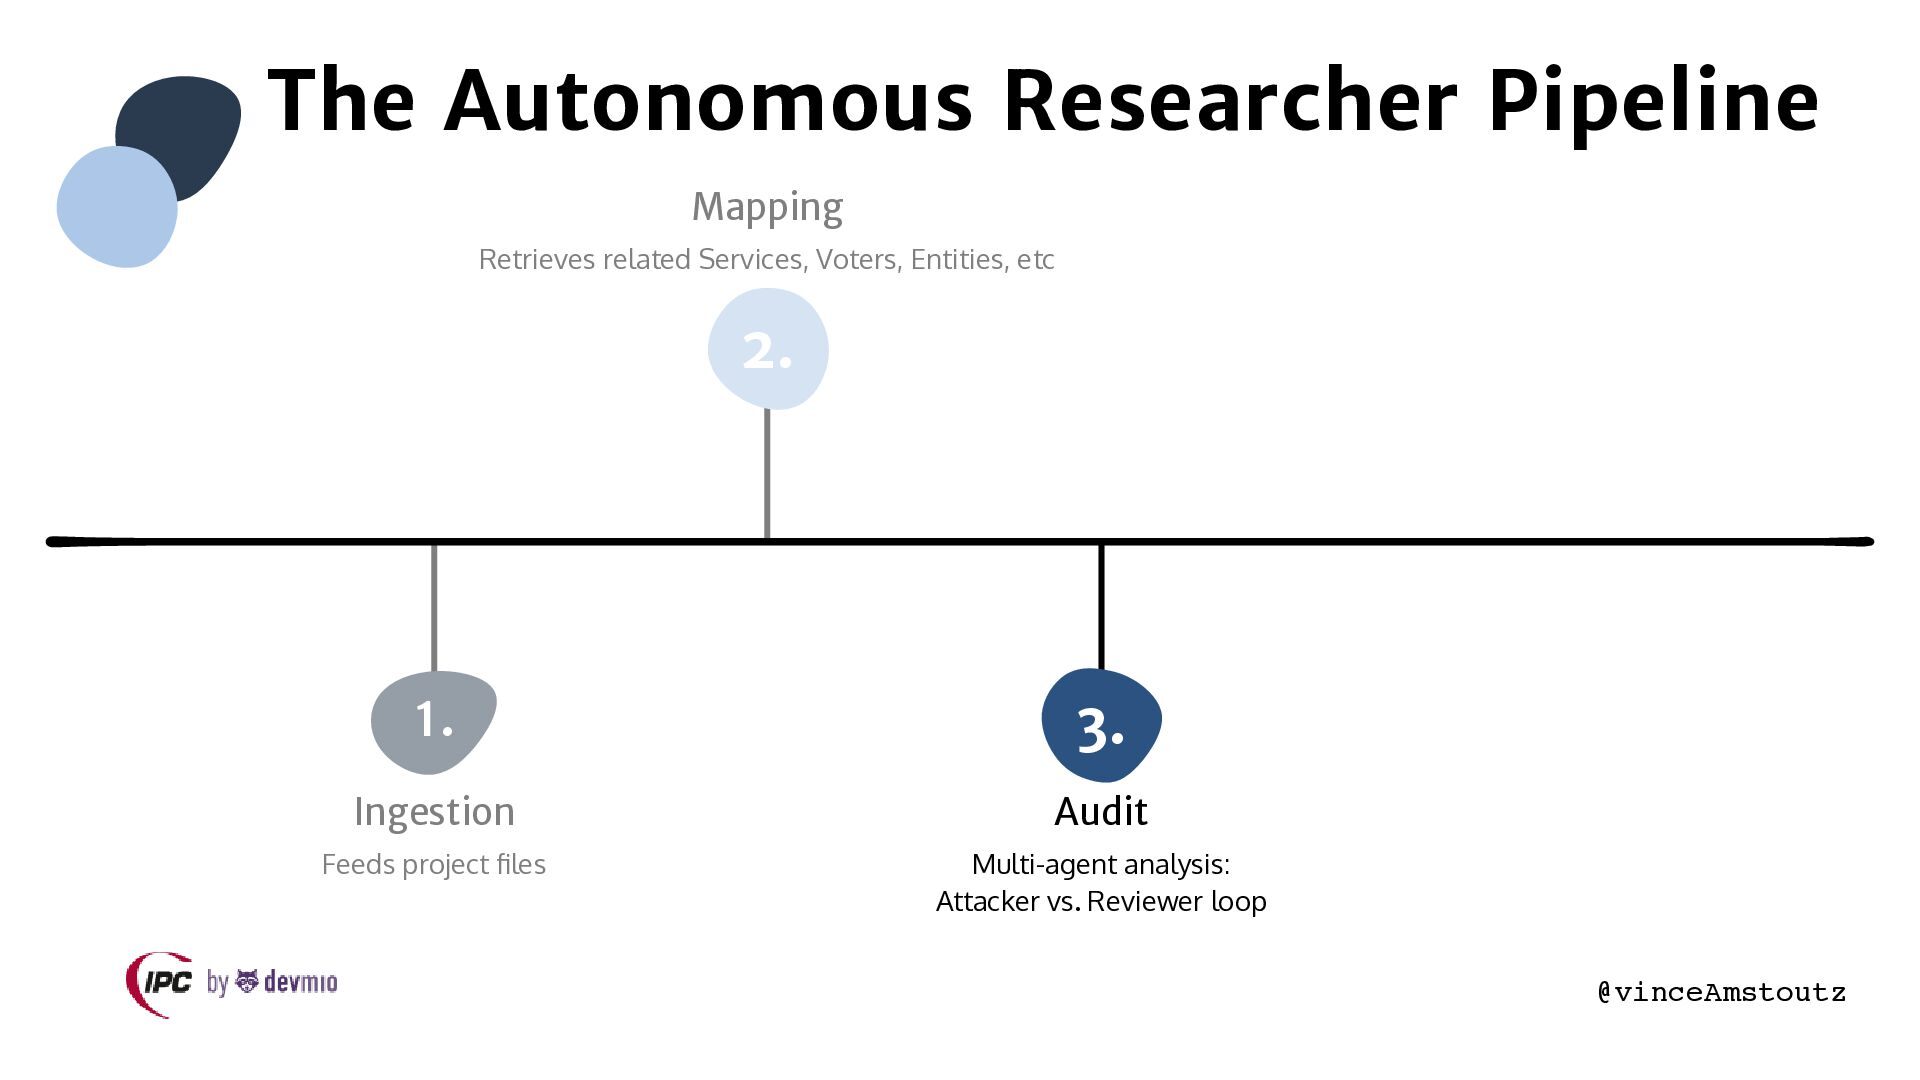
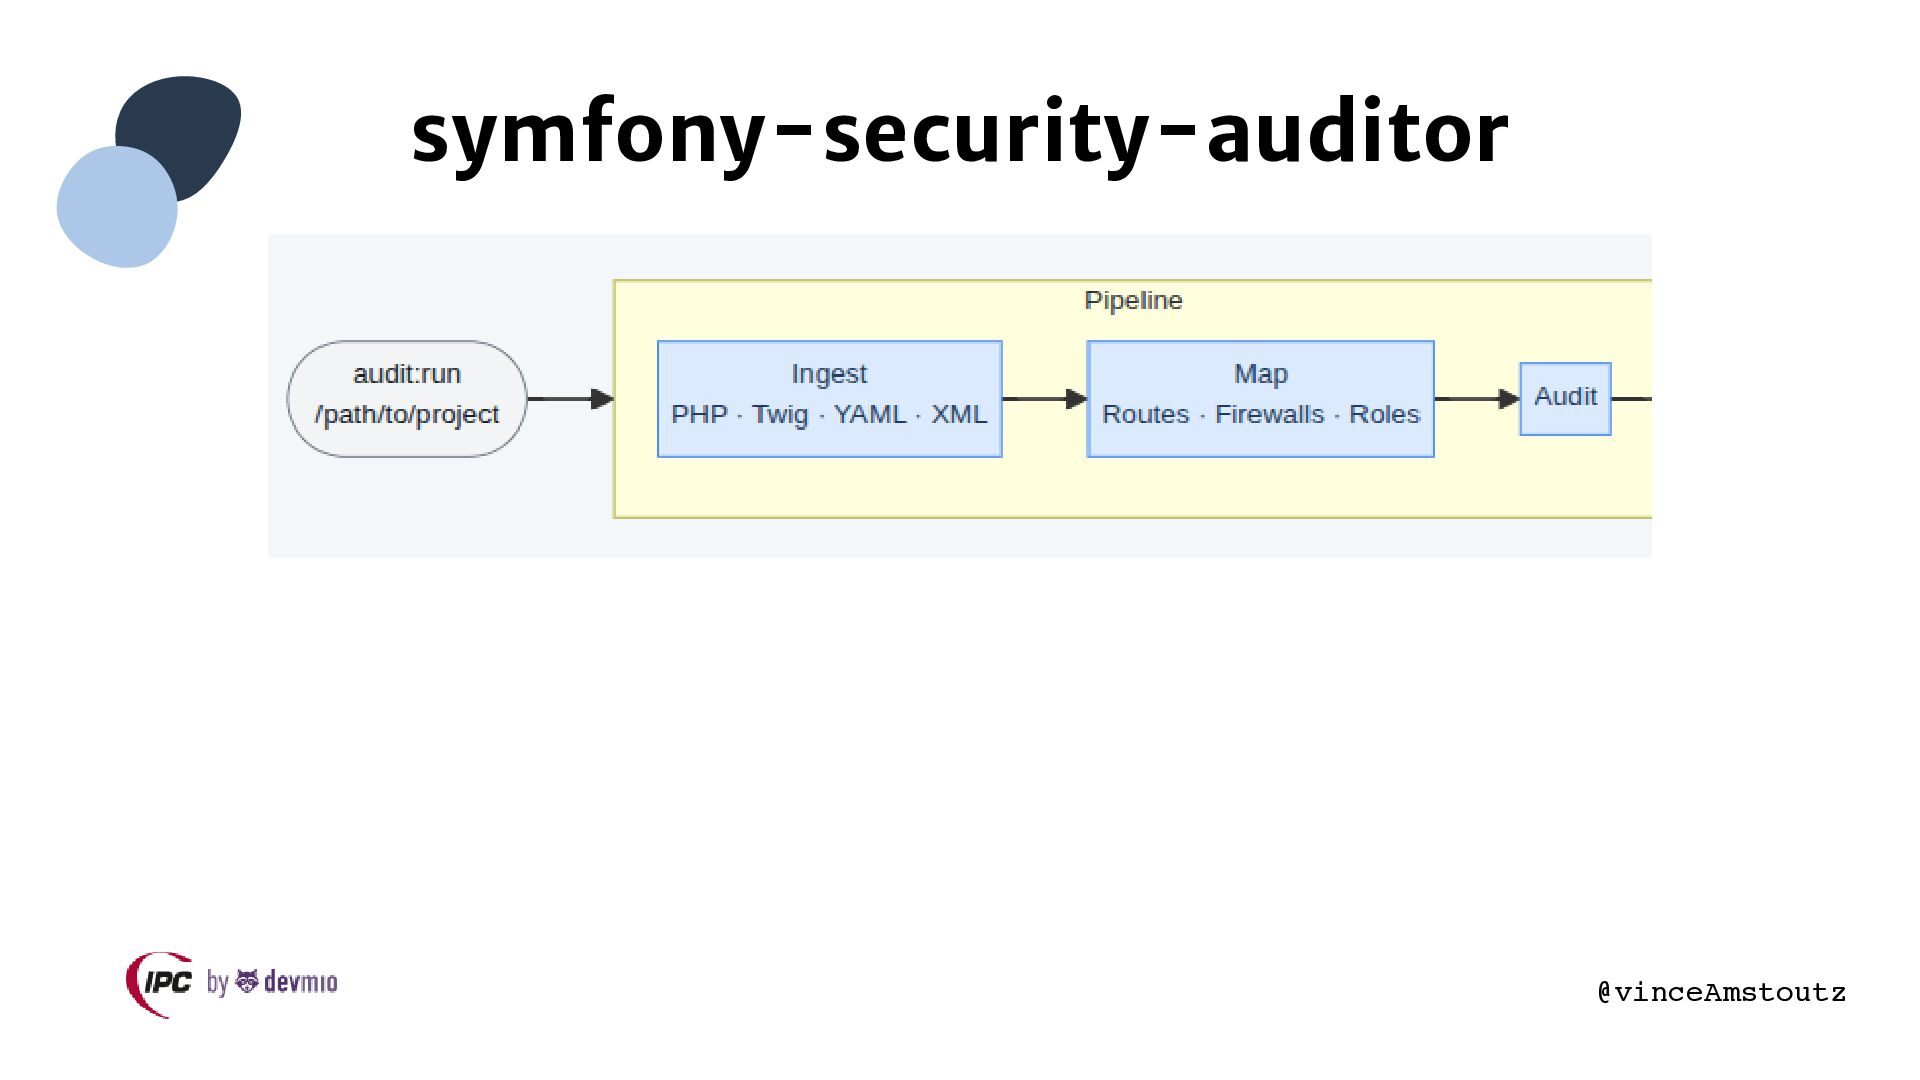
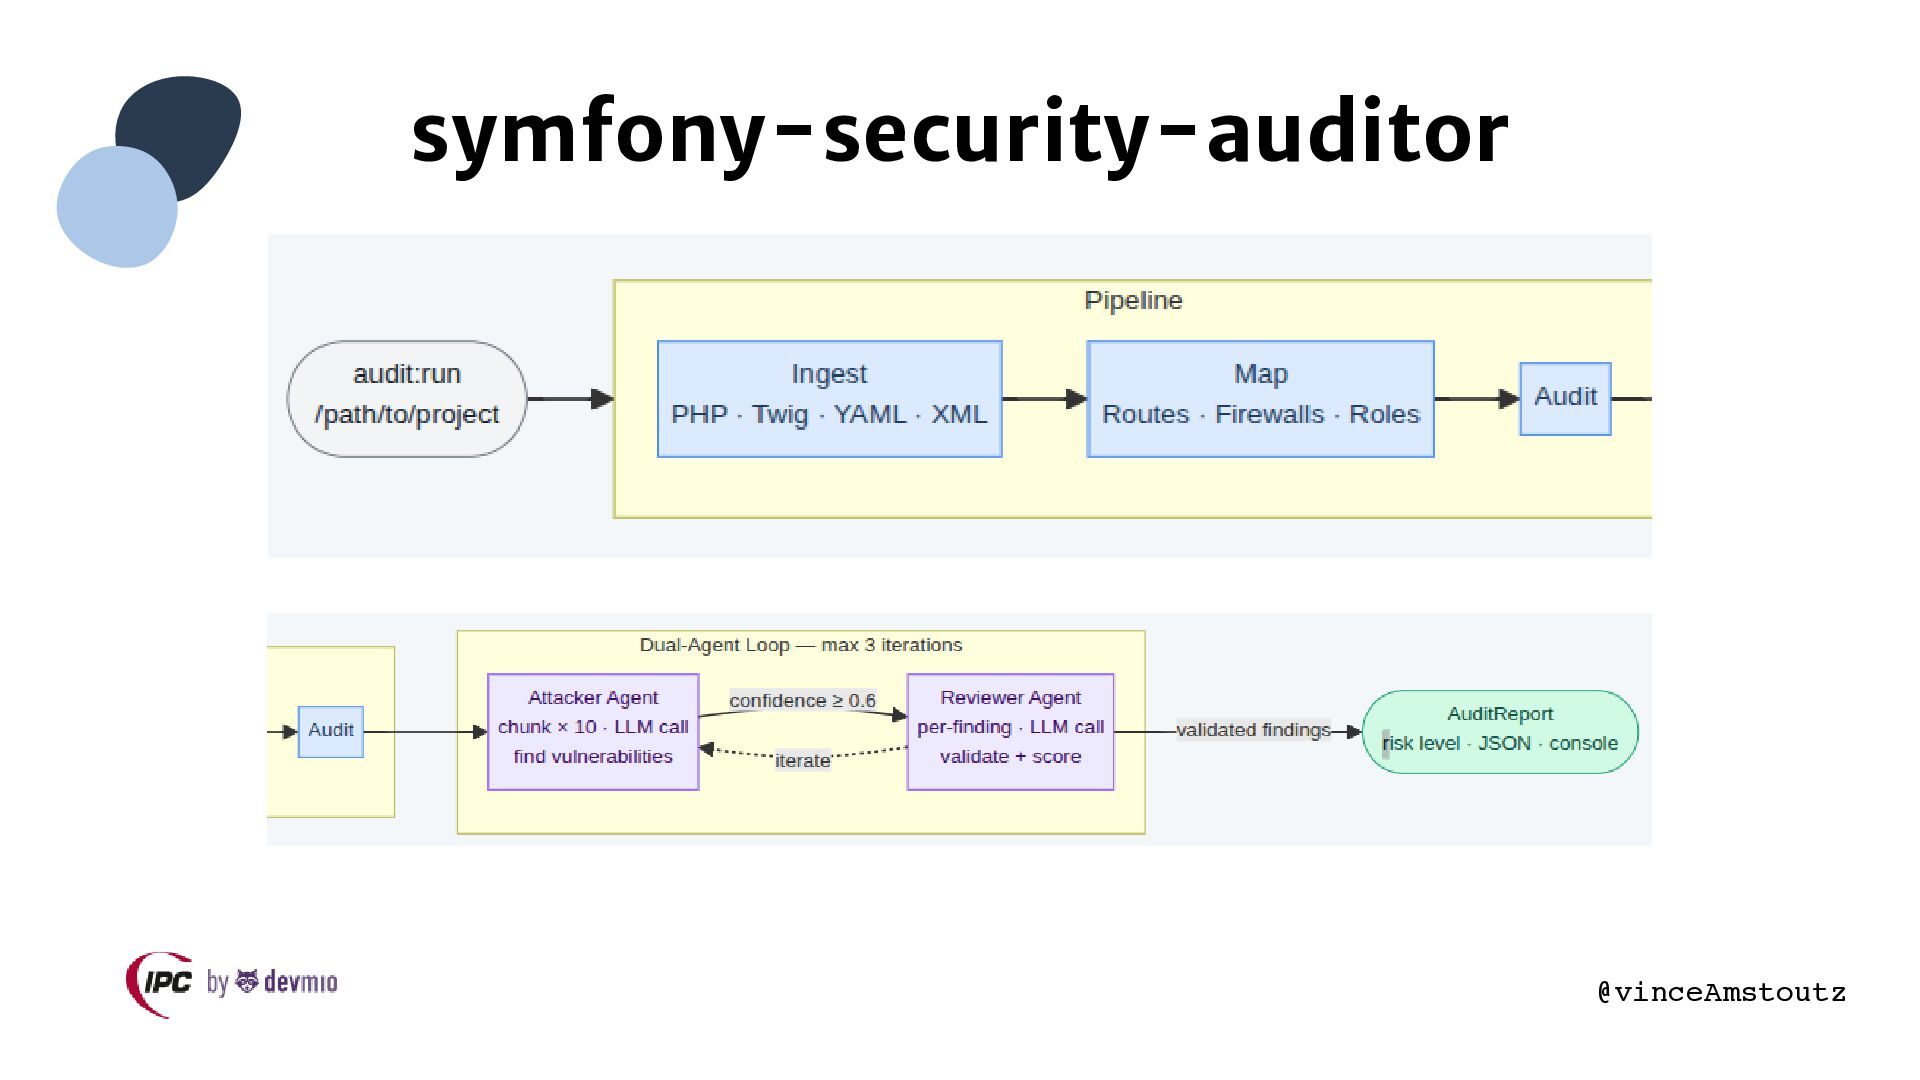
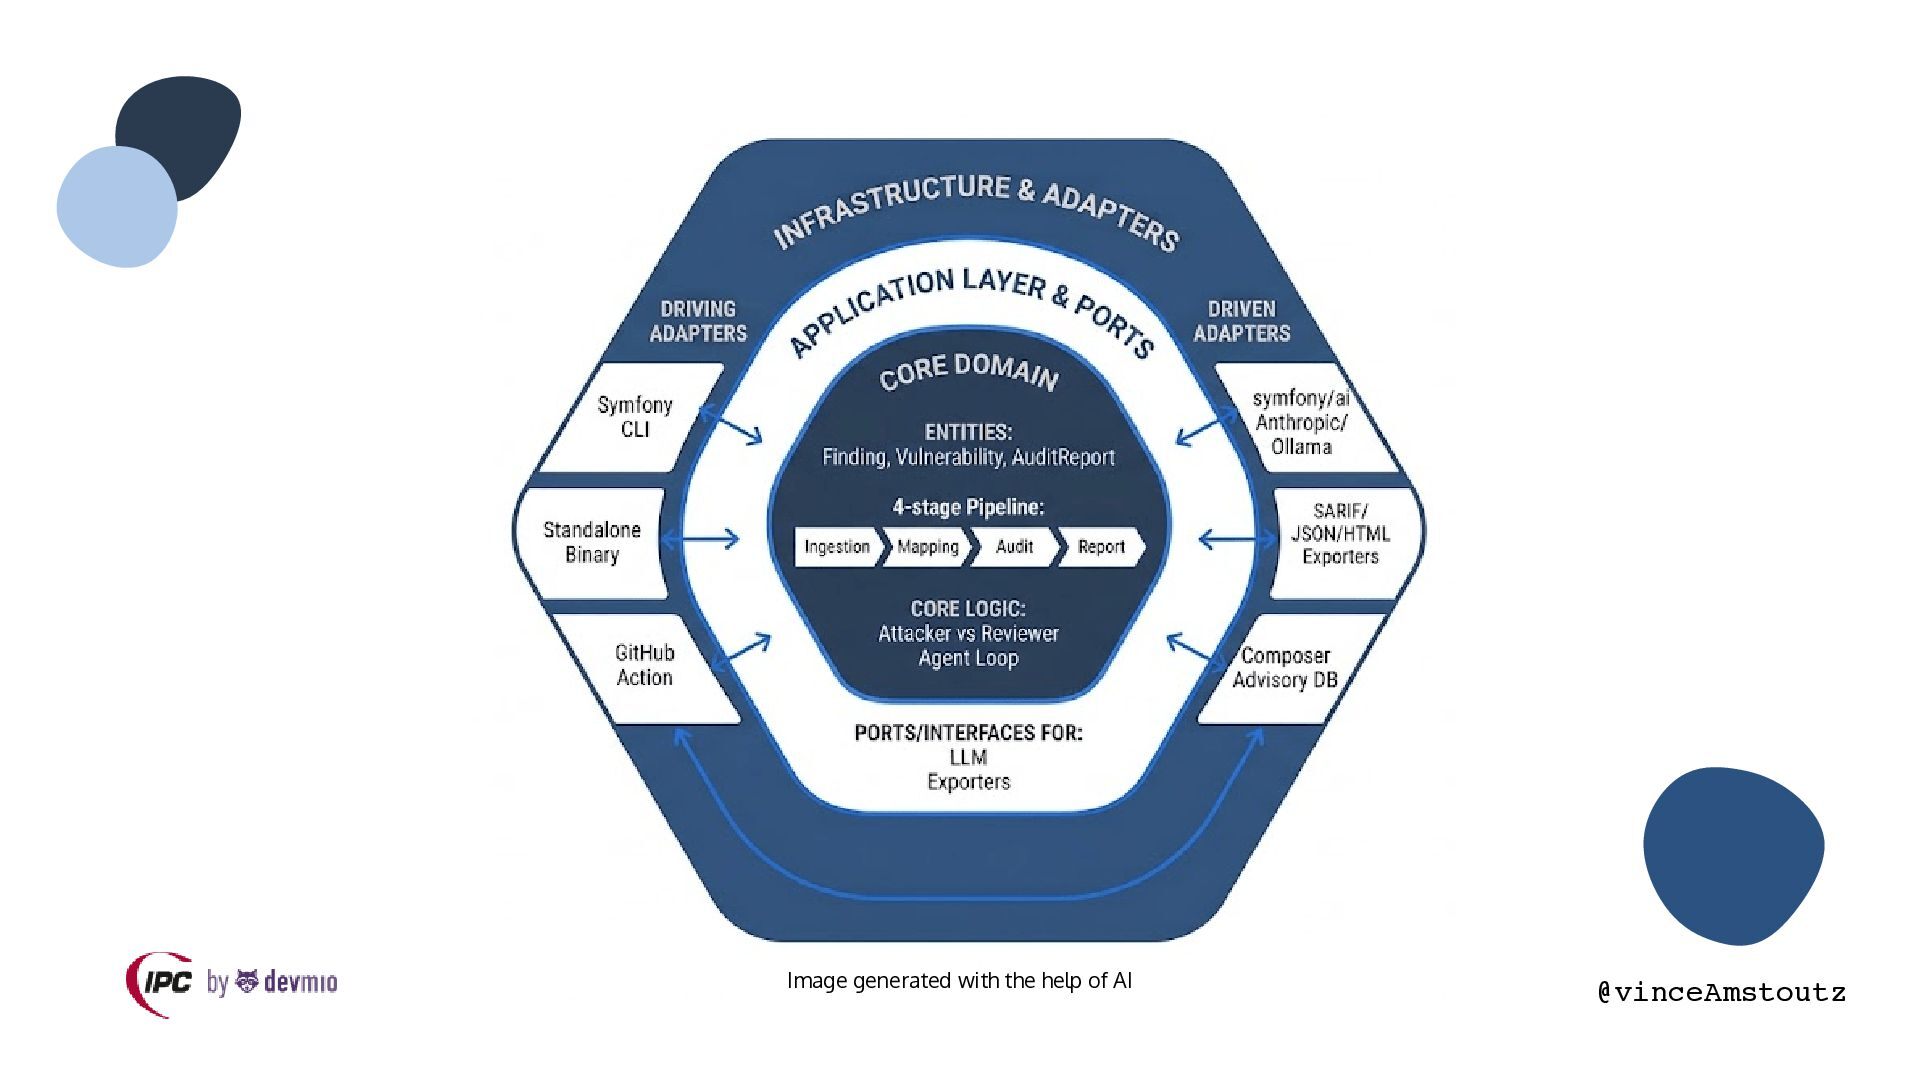
  14. The Autonomous Researcher Pipeline Mapping Retrieves related Services, Voters, Entities,

    etc 2. 1. 3. Ingestion Audit Feeds project files Multi-agent analysis: Attacker vs. Reviewer loop @vinceAmstoutz
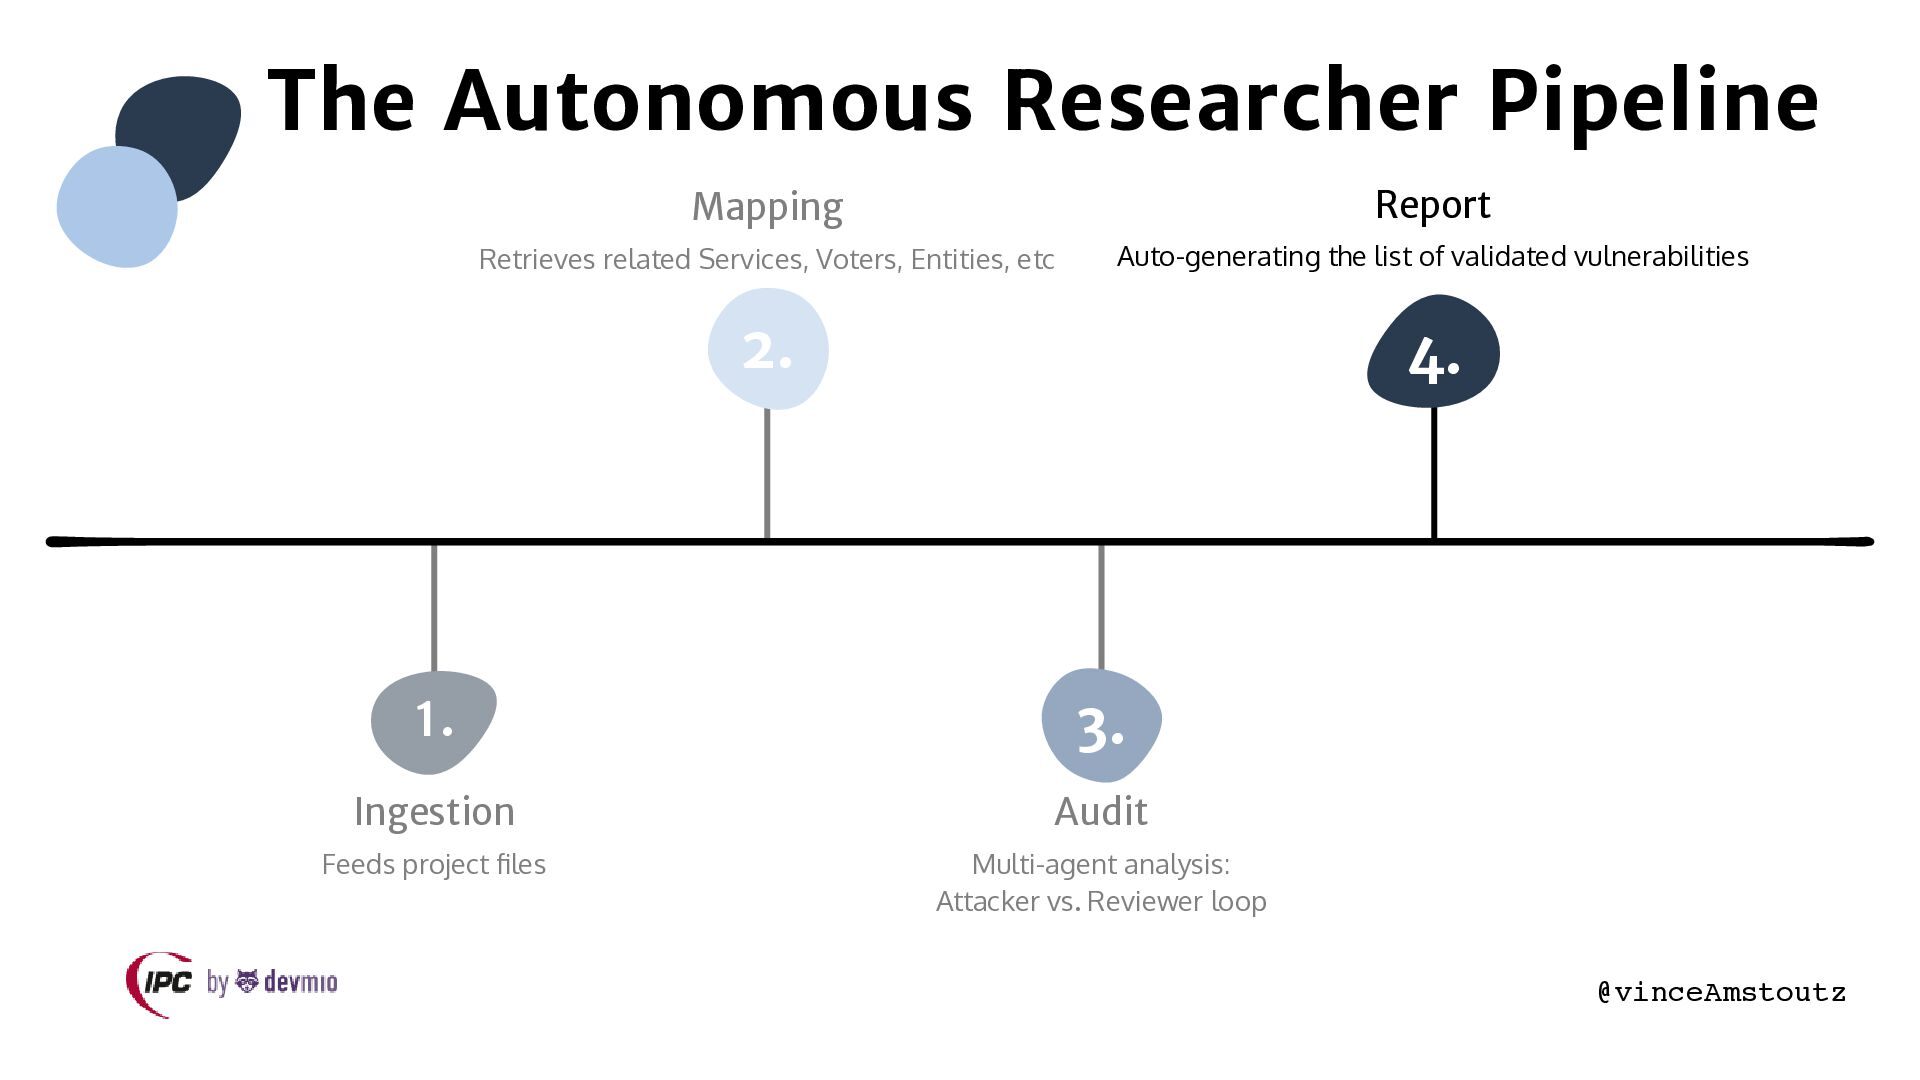
  15. The Autonomous Researcher Pipeline Mapping Report Retrieves related Services, Voters,

    Entities, etc Auto-generating the list of validated vulnerabilities 2. 4. 1. 3. Ingestion Audit Feeds project files Multi-agent analysis: Attacker vs. Reviewer loop @vinceAmstoutz
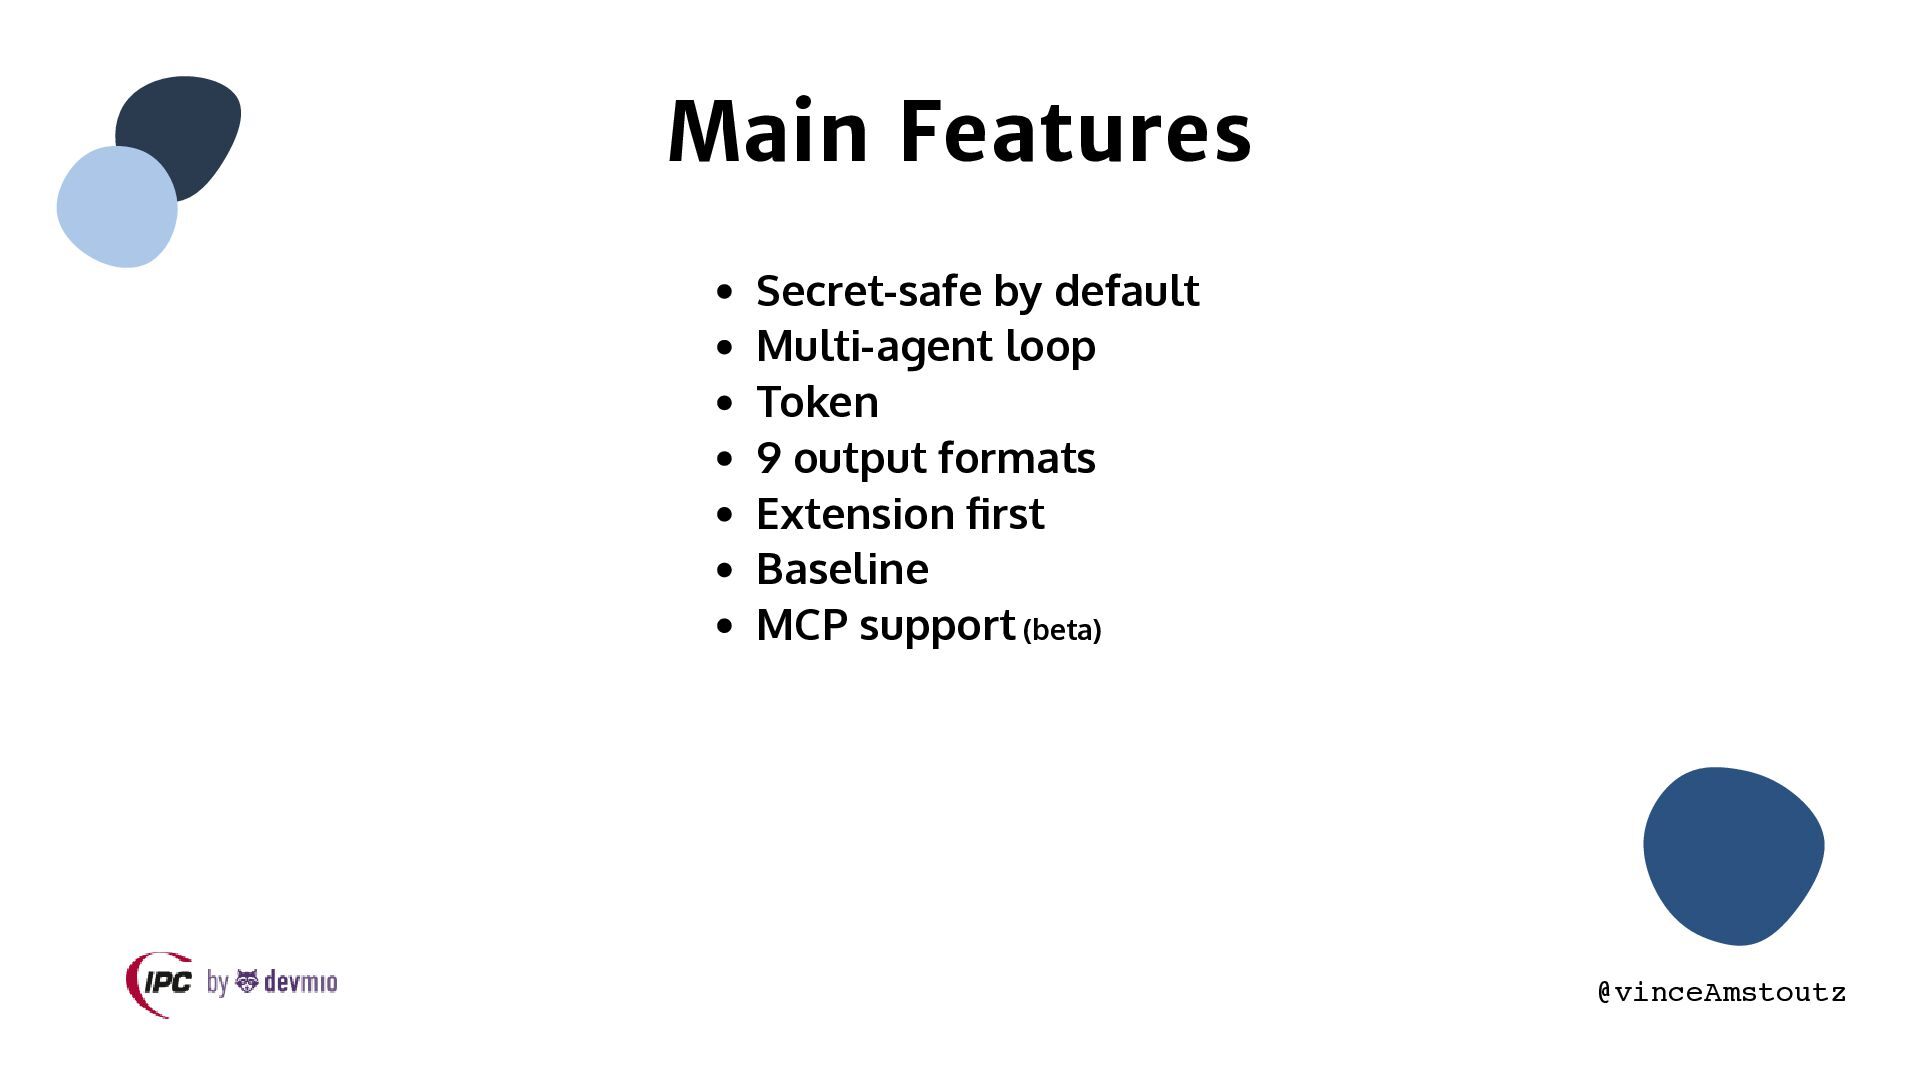
  16. Main Features Secret-safe by default Multi-agent loop Token 9 output

    formats Extension first Baseline @vinceAmstoutz
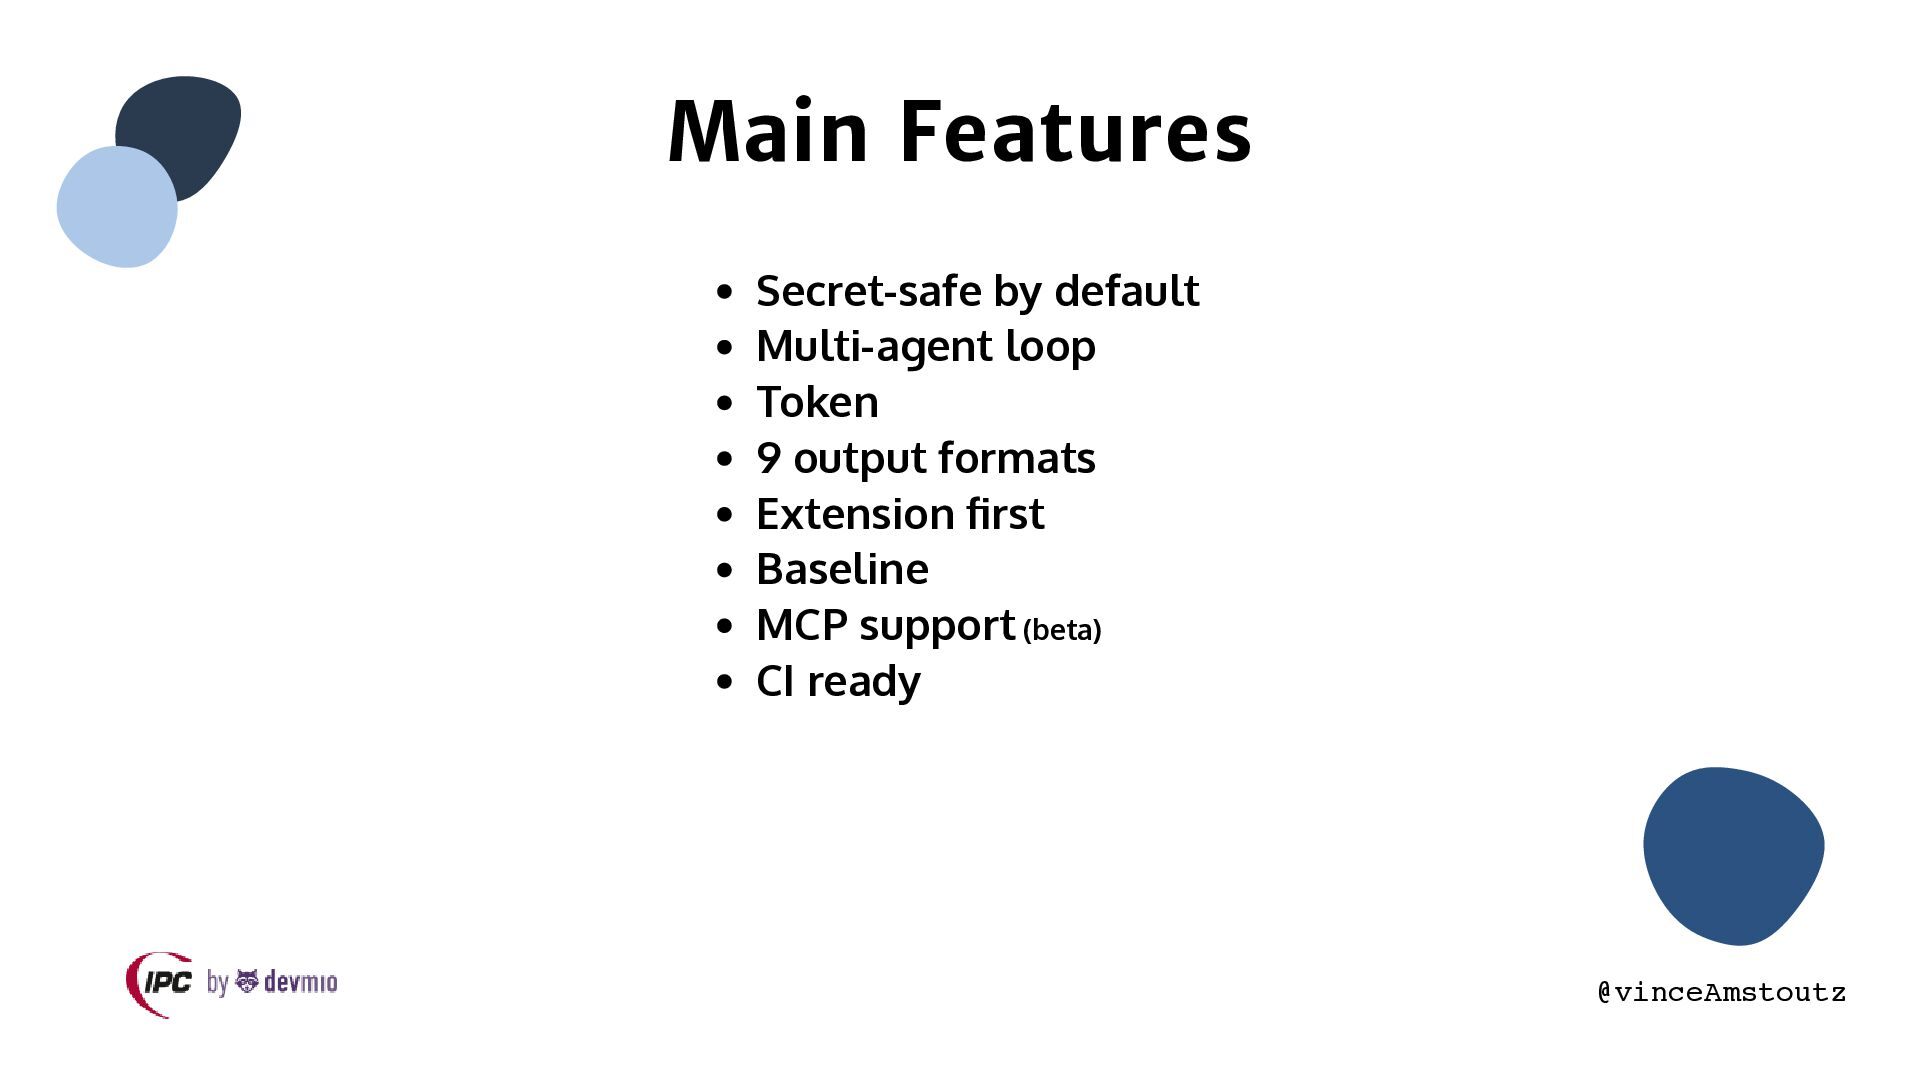
  17. Main Features Secret-safe by default Multi-agent loop Token 9 output

    formats Extension first Baseline MCP support (beta) @vinceAmstoutz
  18. Main Features Secret-safe by default Multi-agent loop Token 9 output

    formats Extension first Baseline MCP support (beta) CI ready @vinceAmstoutz
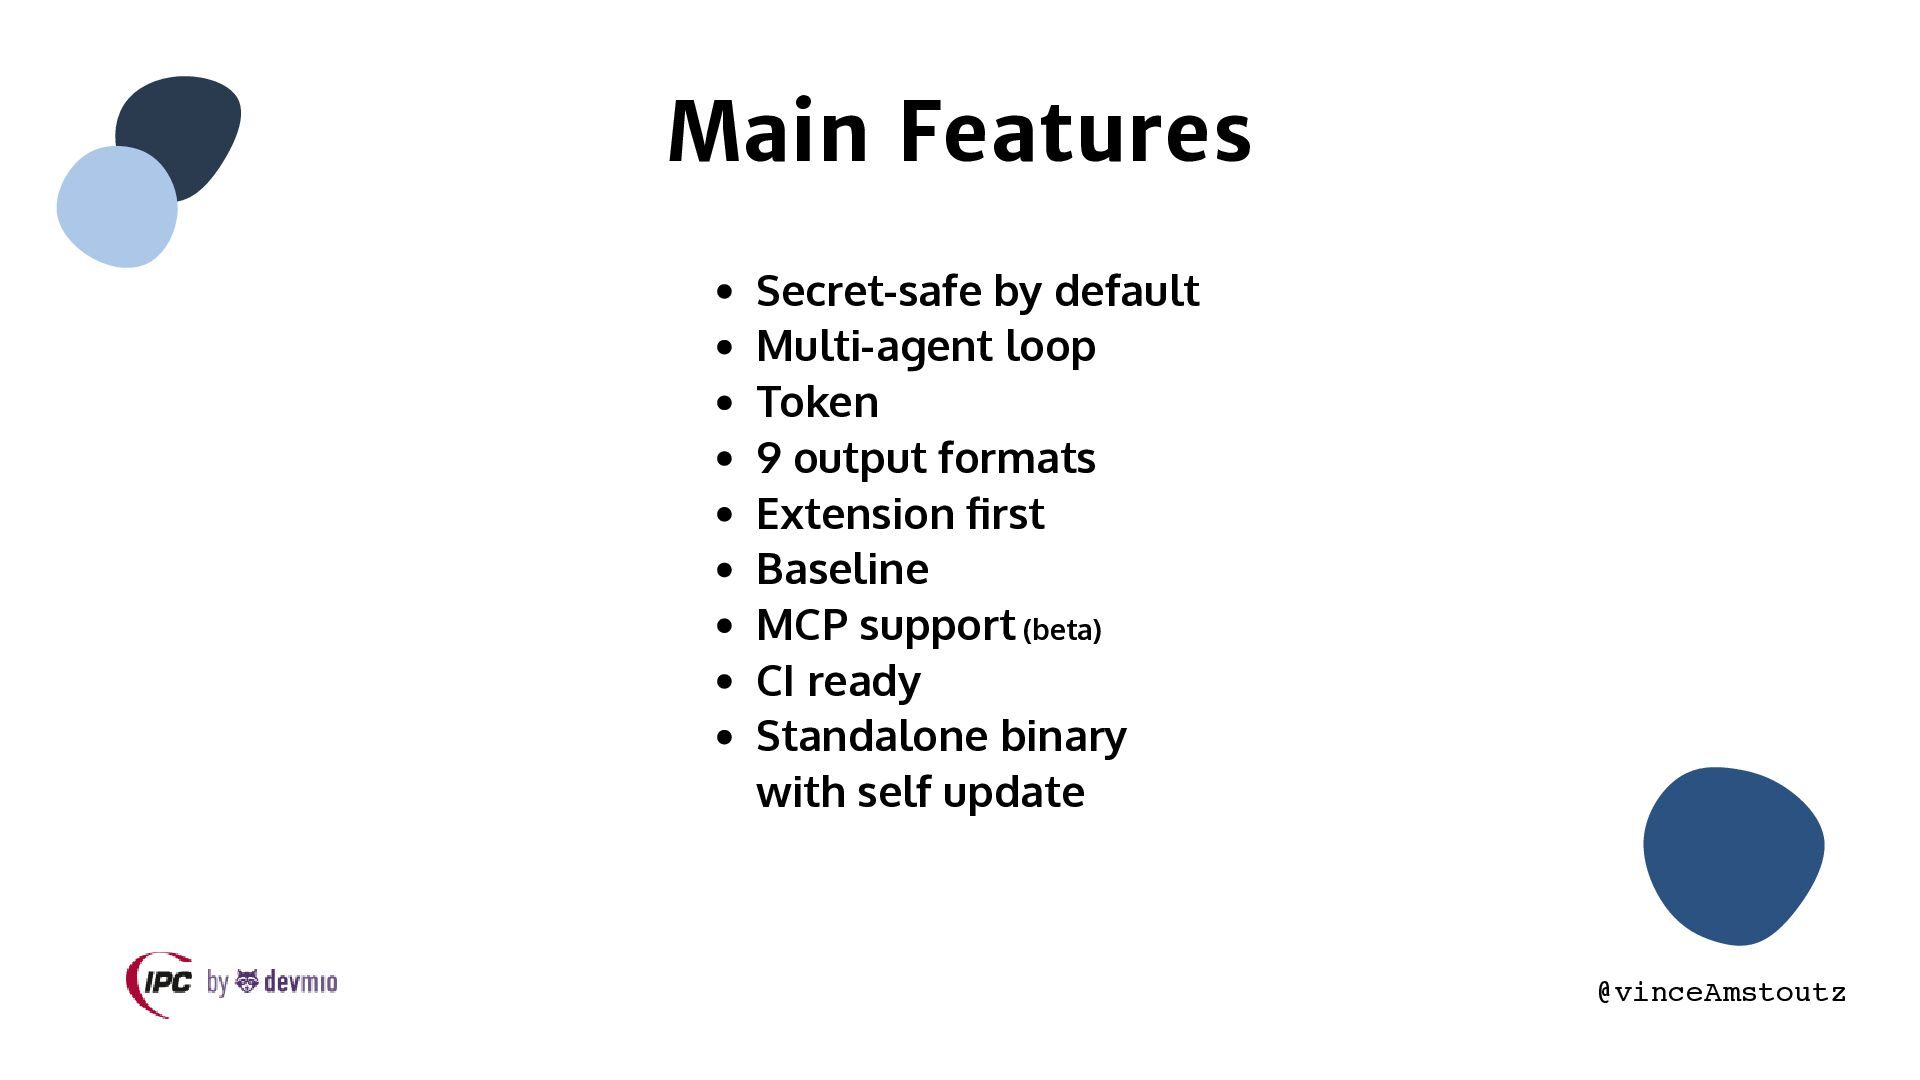
  19. Main Features Secret-safe by default Multi-agent loop Token 9 output

    formats Extension first Baseline MCP support (beta) CI ready Standalone binary with self update @vinceAmstoutz
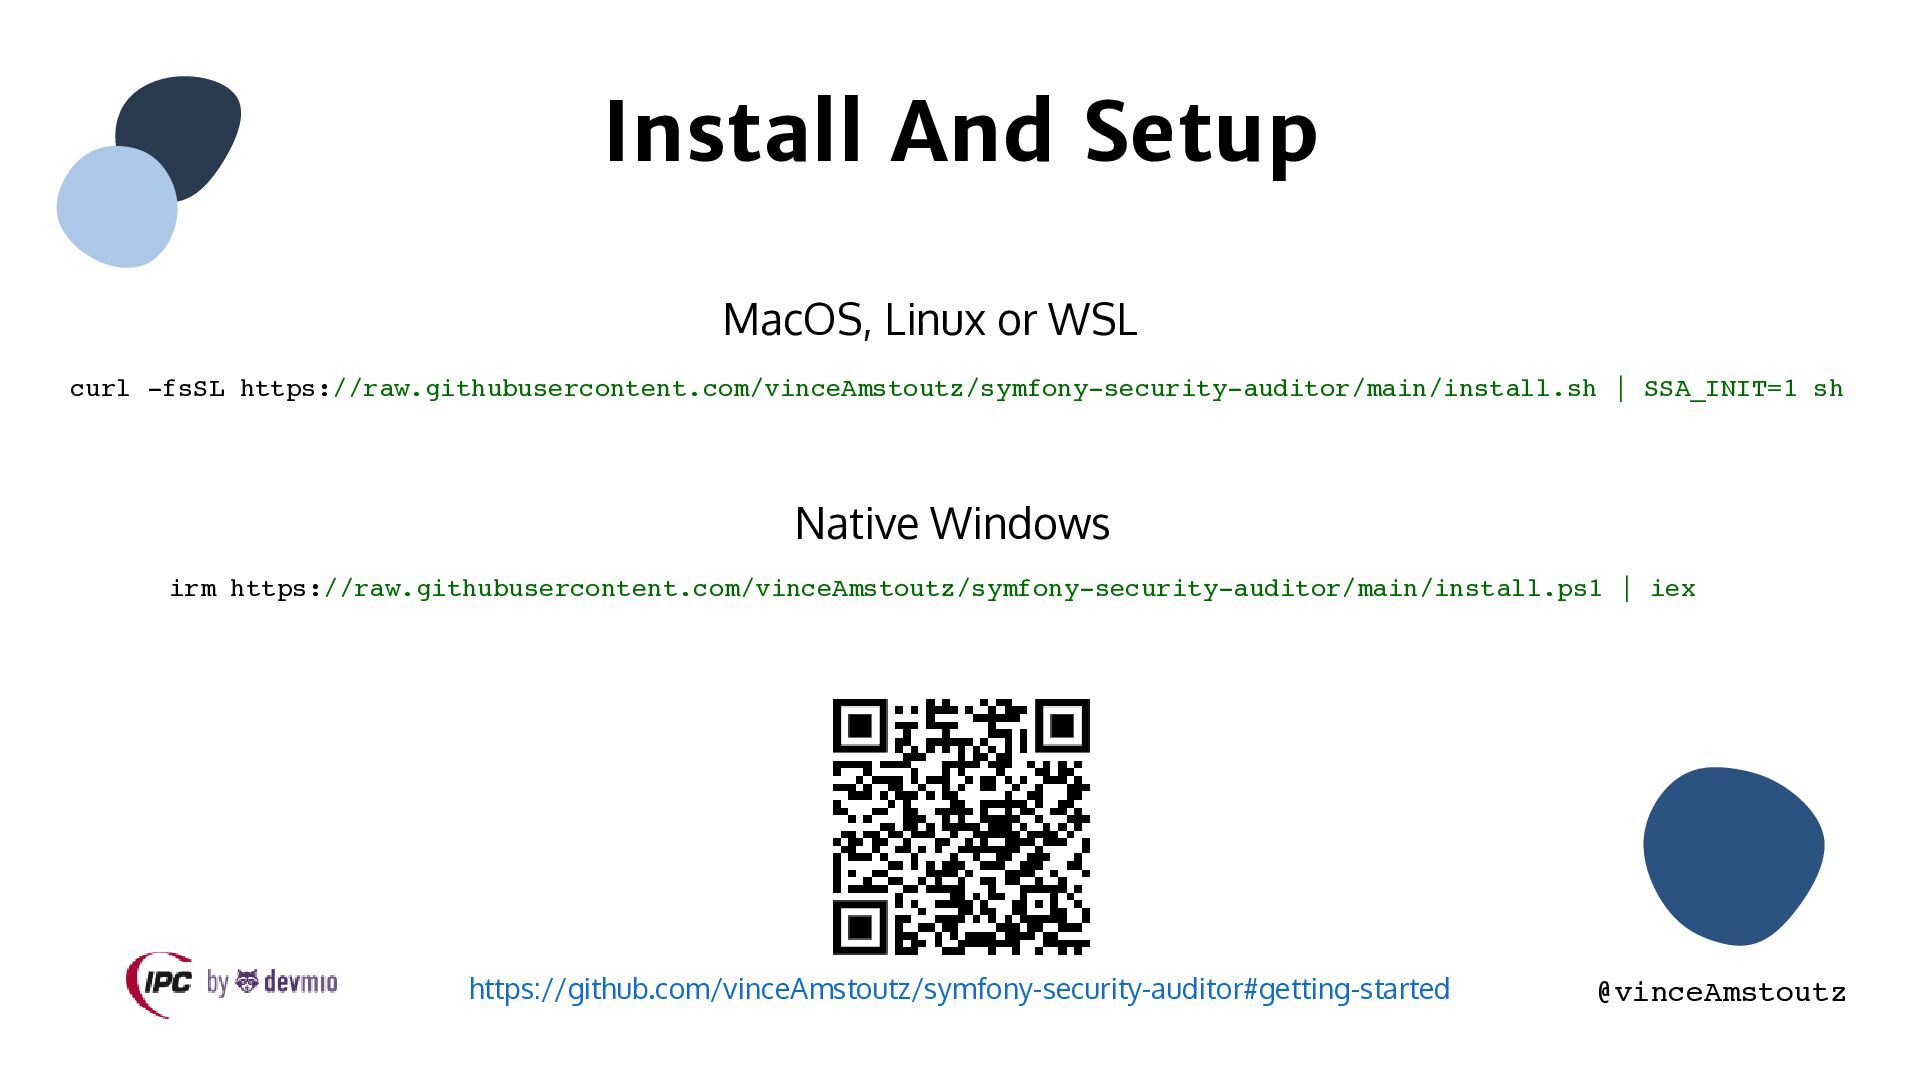
  20. Install And Setup MacOS, Linux or WSL curl -fsSL https://raw.githubusercontent.com/vinceAmstoutz/symfony-security-auditor/main/install.sh

    | SSA_INIT=1 sh Native Windows irm https://raw.githubusercontent.com/vinceAmstoutz/symfony-security-auditor/main/install.ps1 | iex https://github.com/vinceAmstoutz/symfony-security-auditor#getting-started @vinceAmstoutz
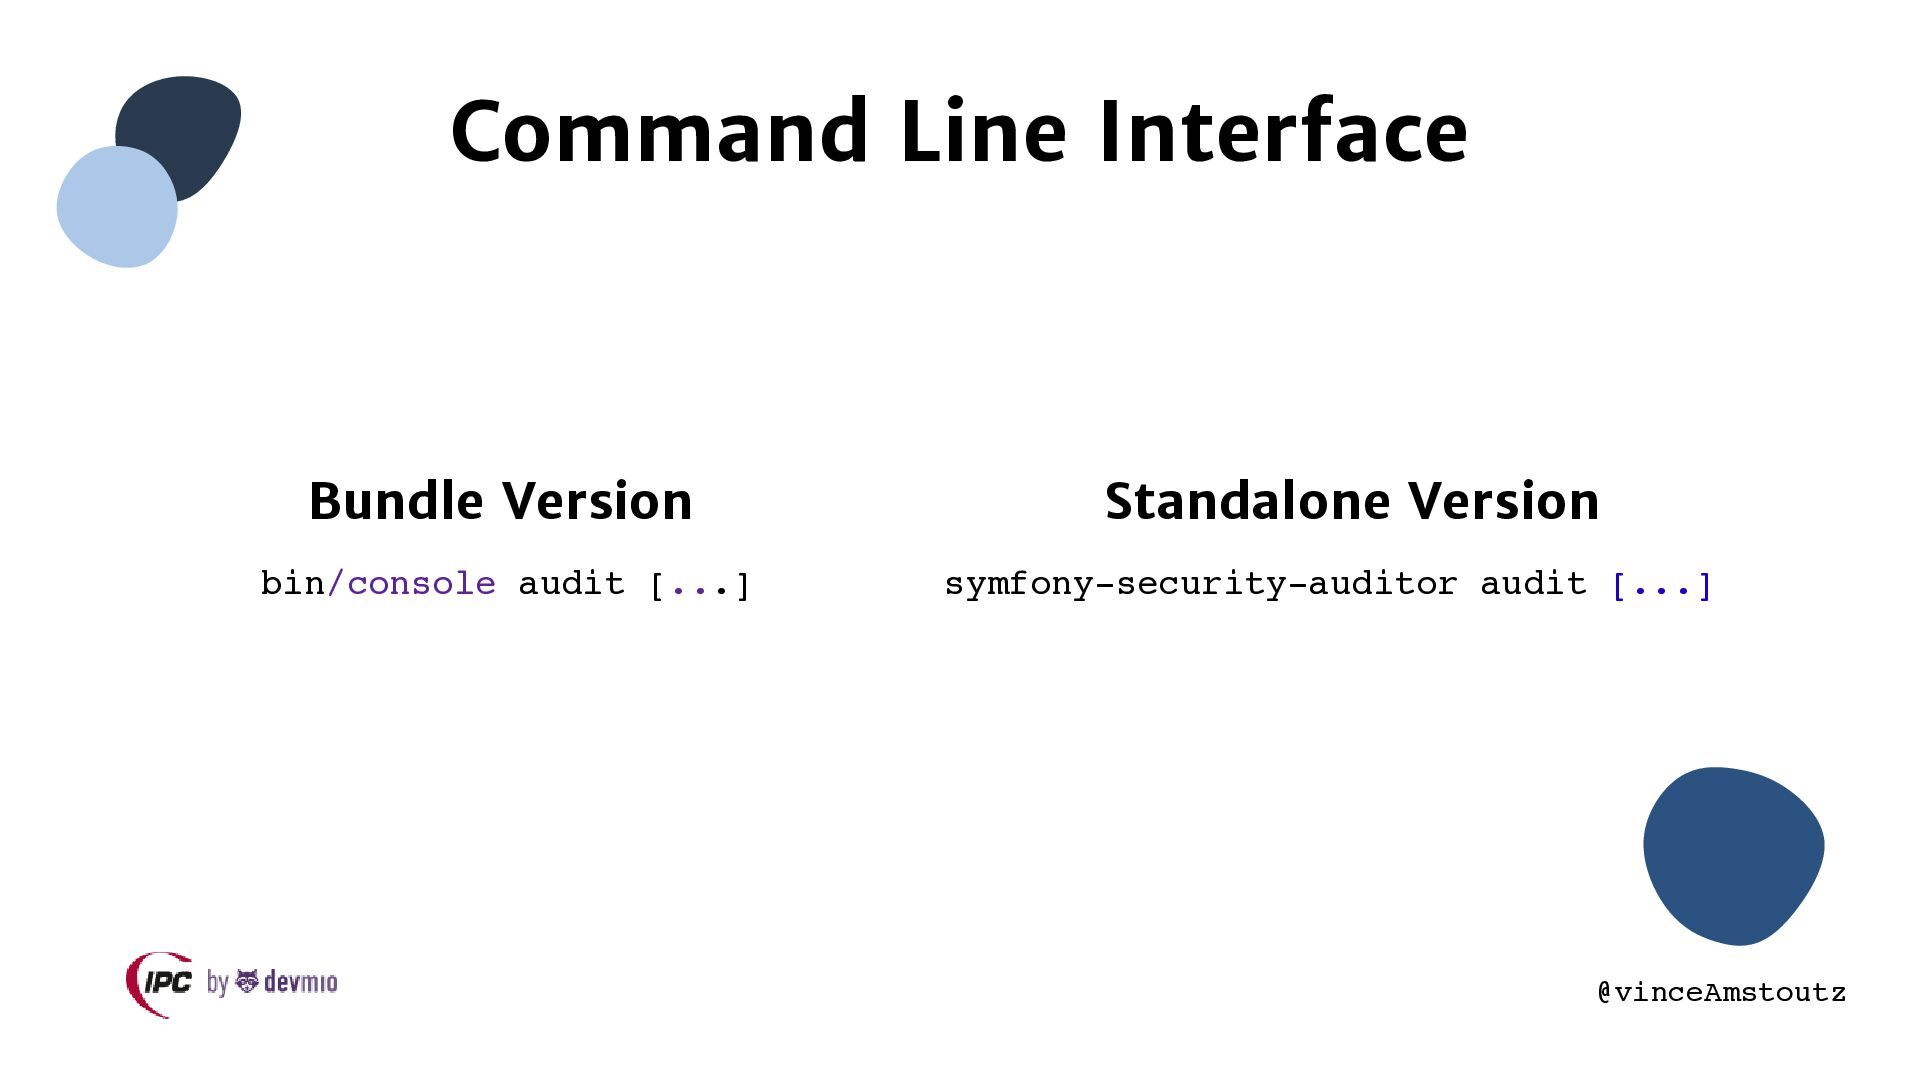
  21. Command Line Interface Bundle Version Standalone Version bin/console audit [...]

    symfony-security-auditor audit [...] @vinceAmstoutz
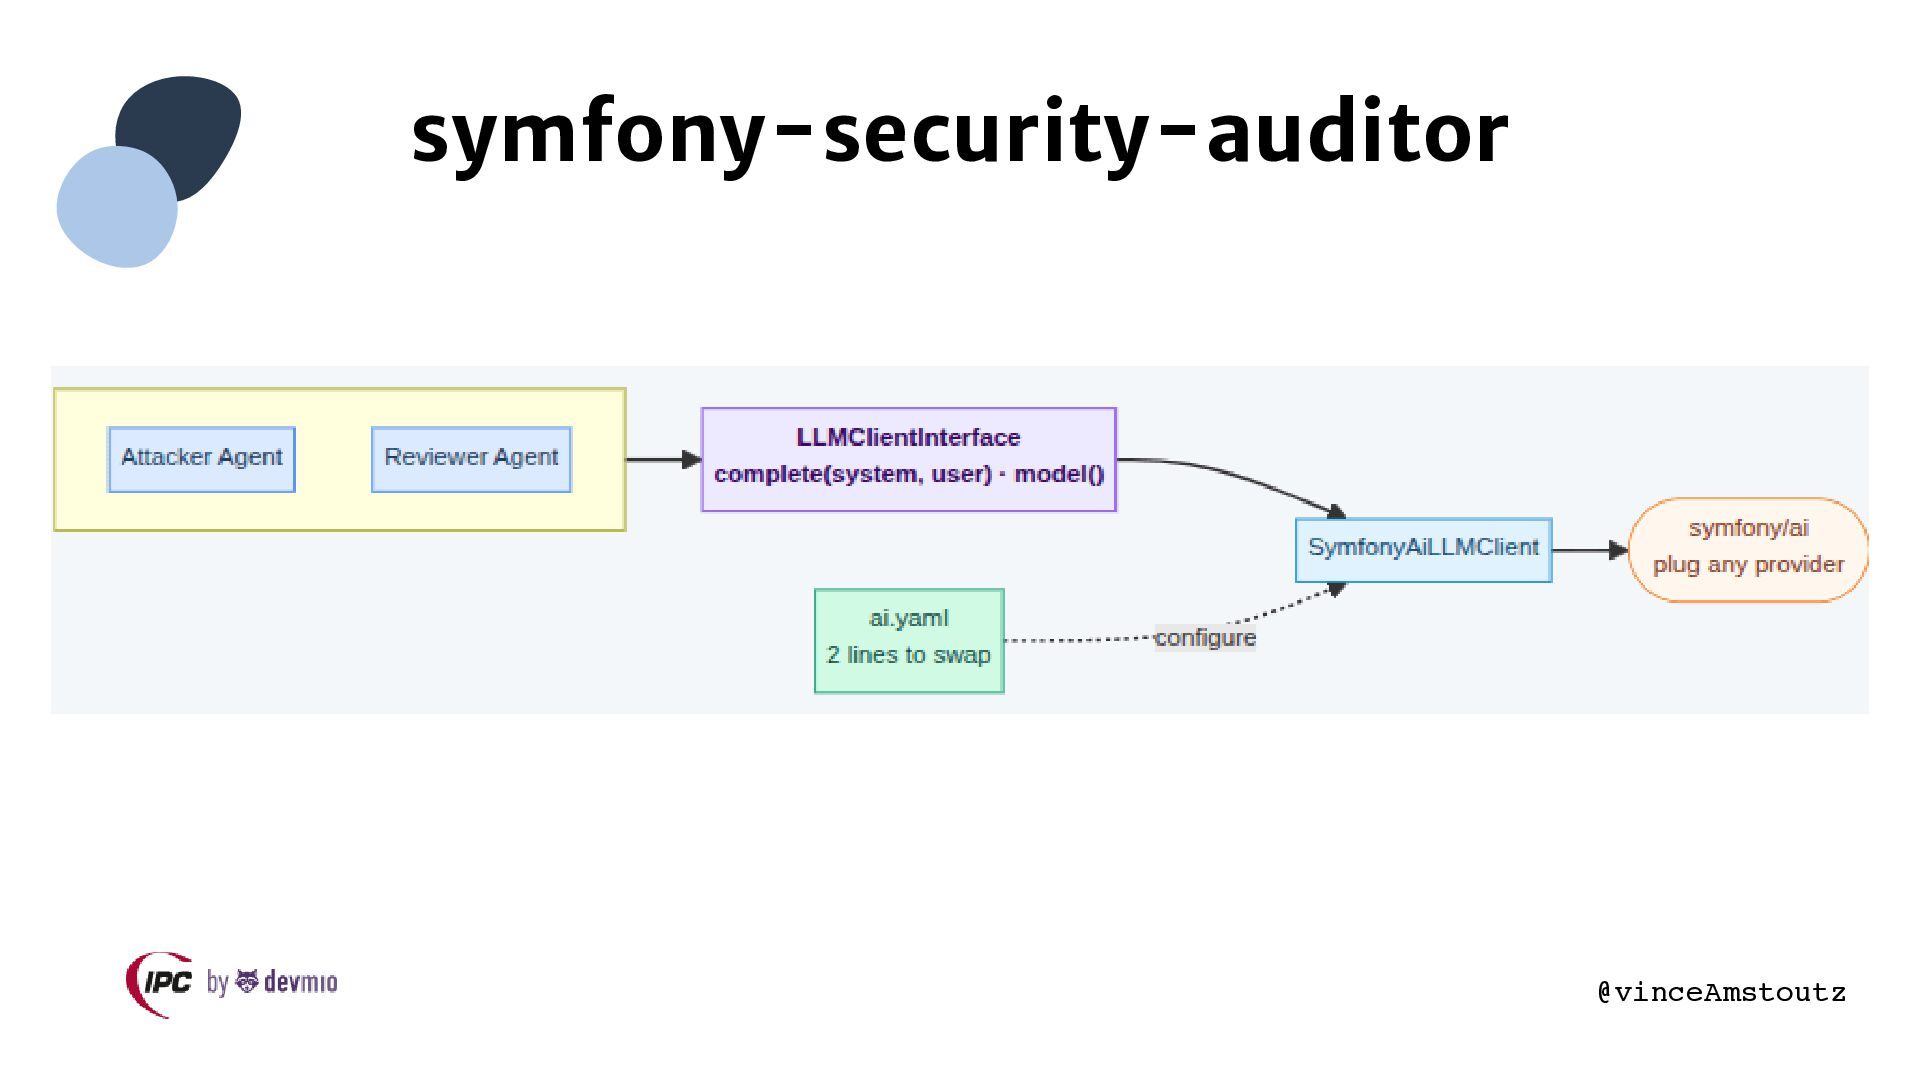
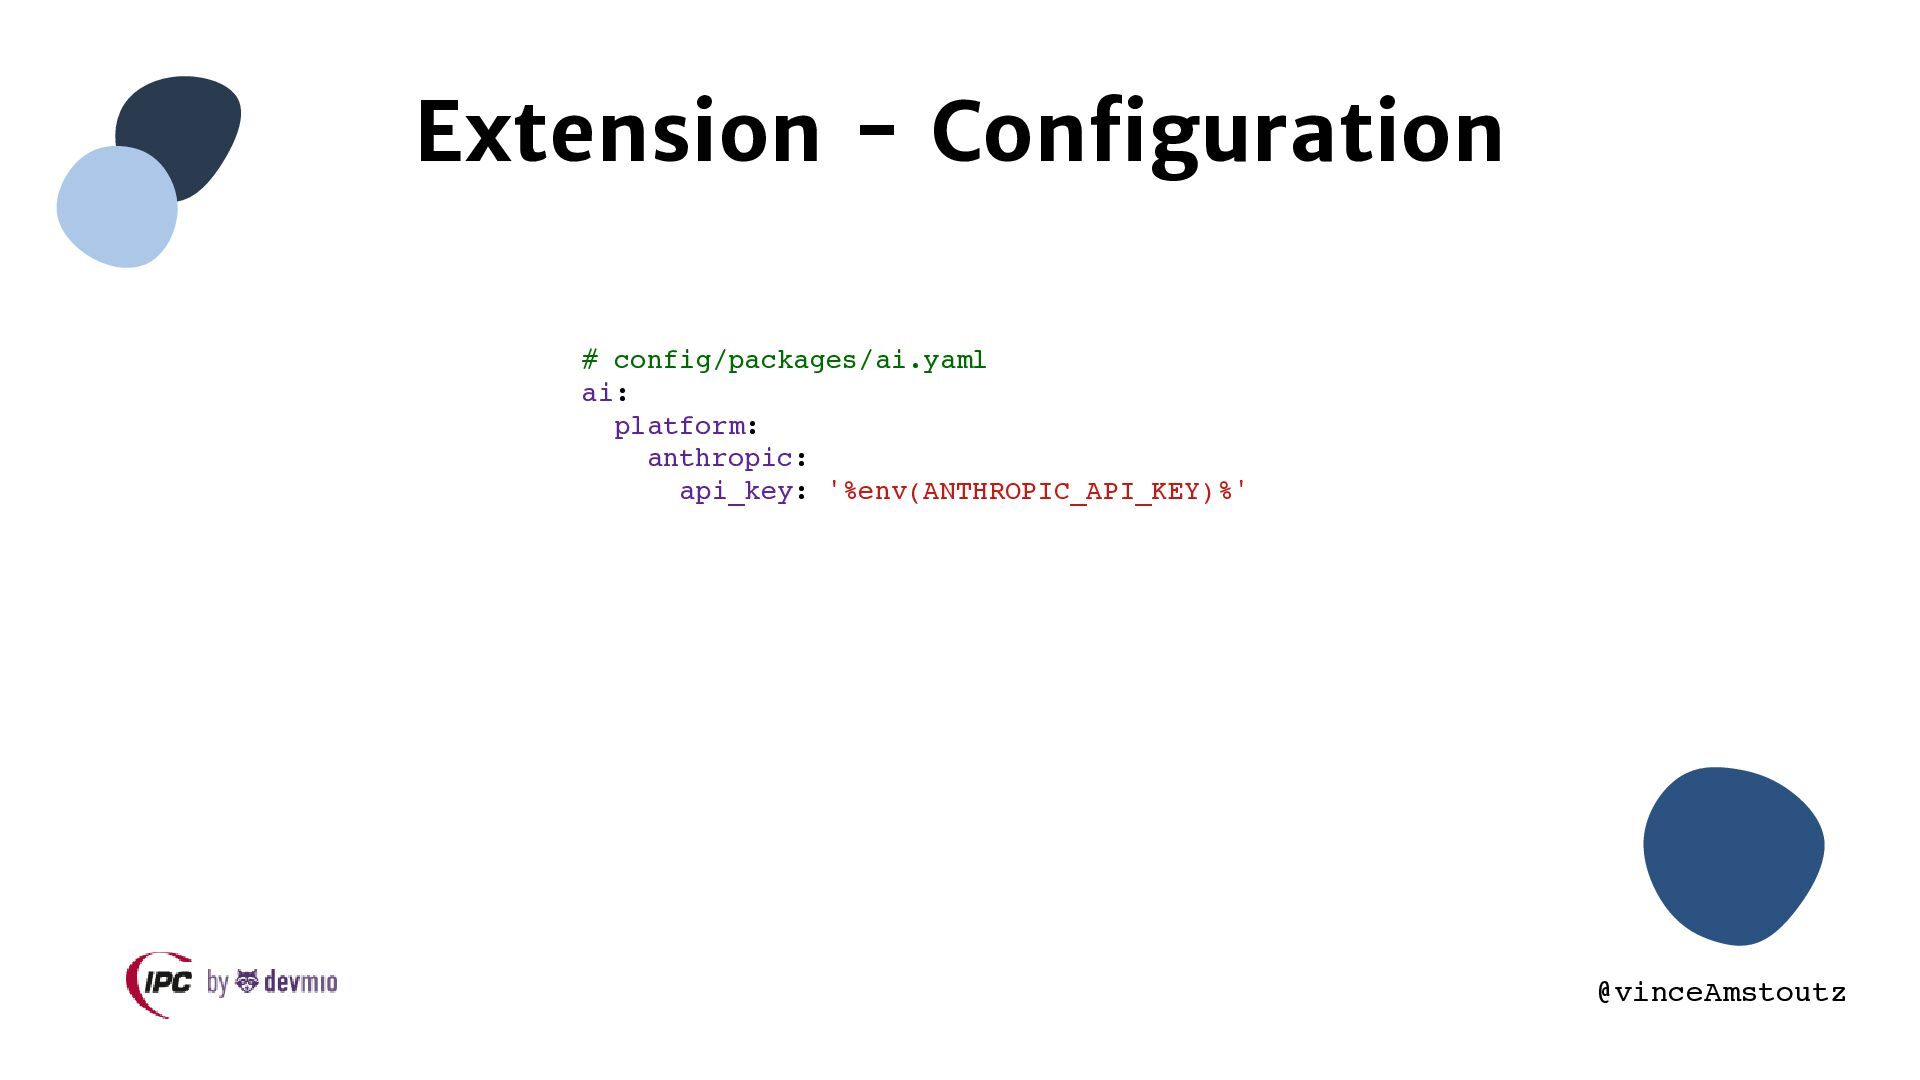
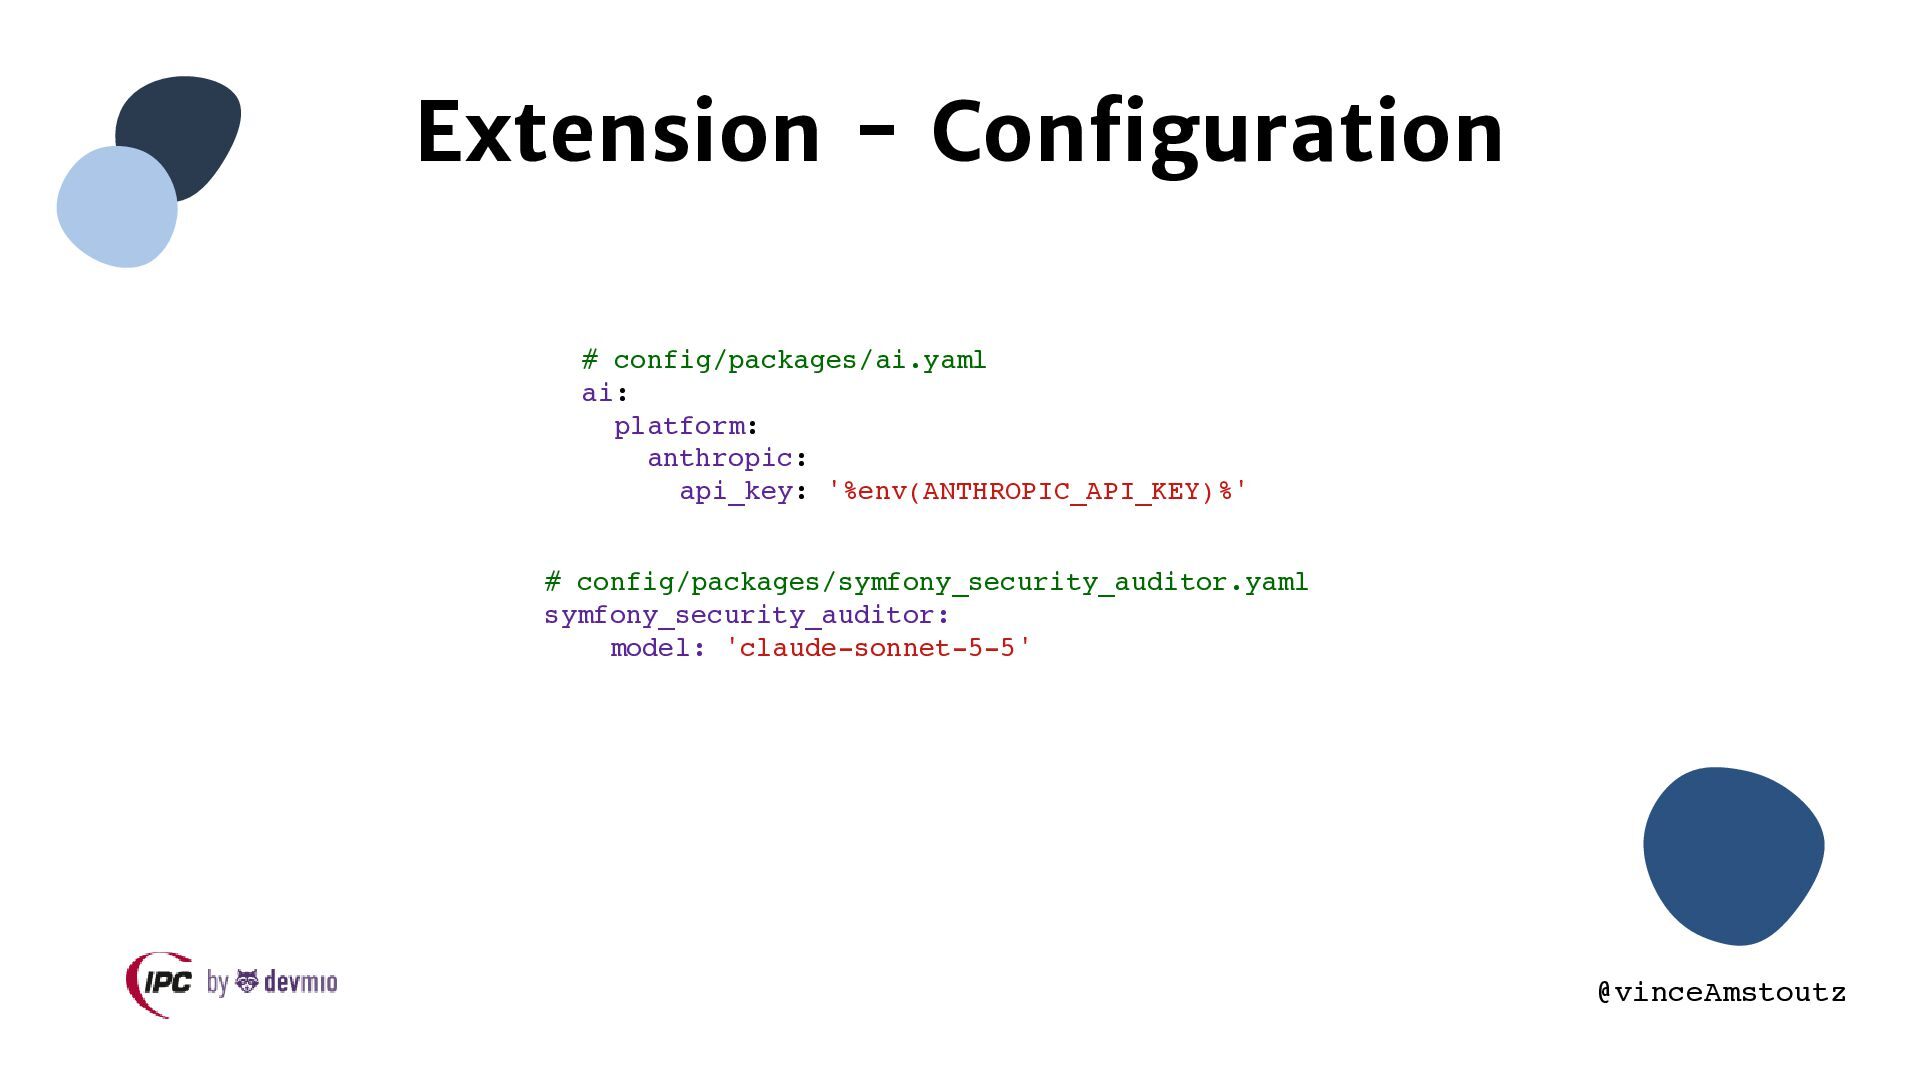
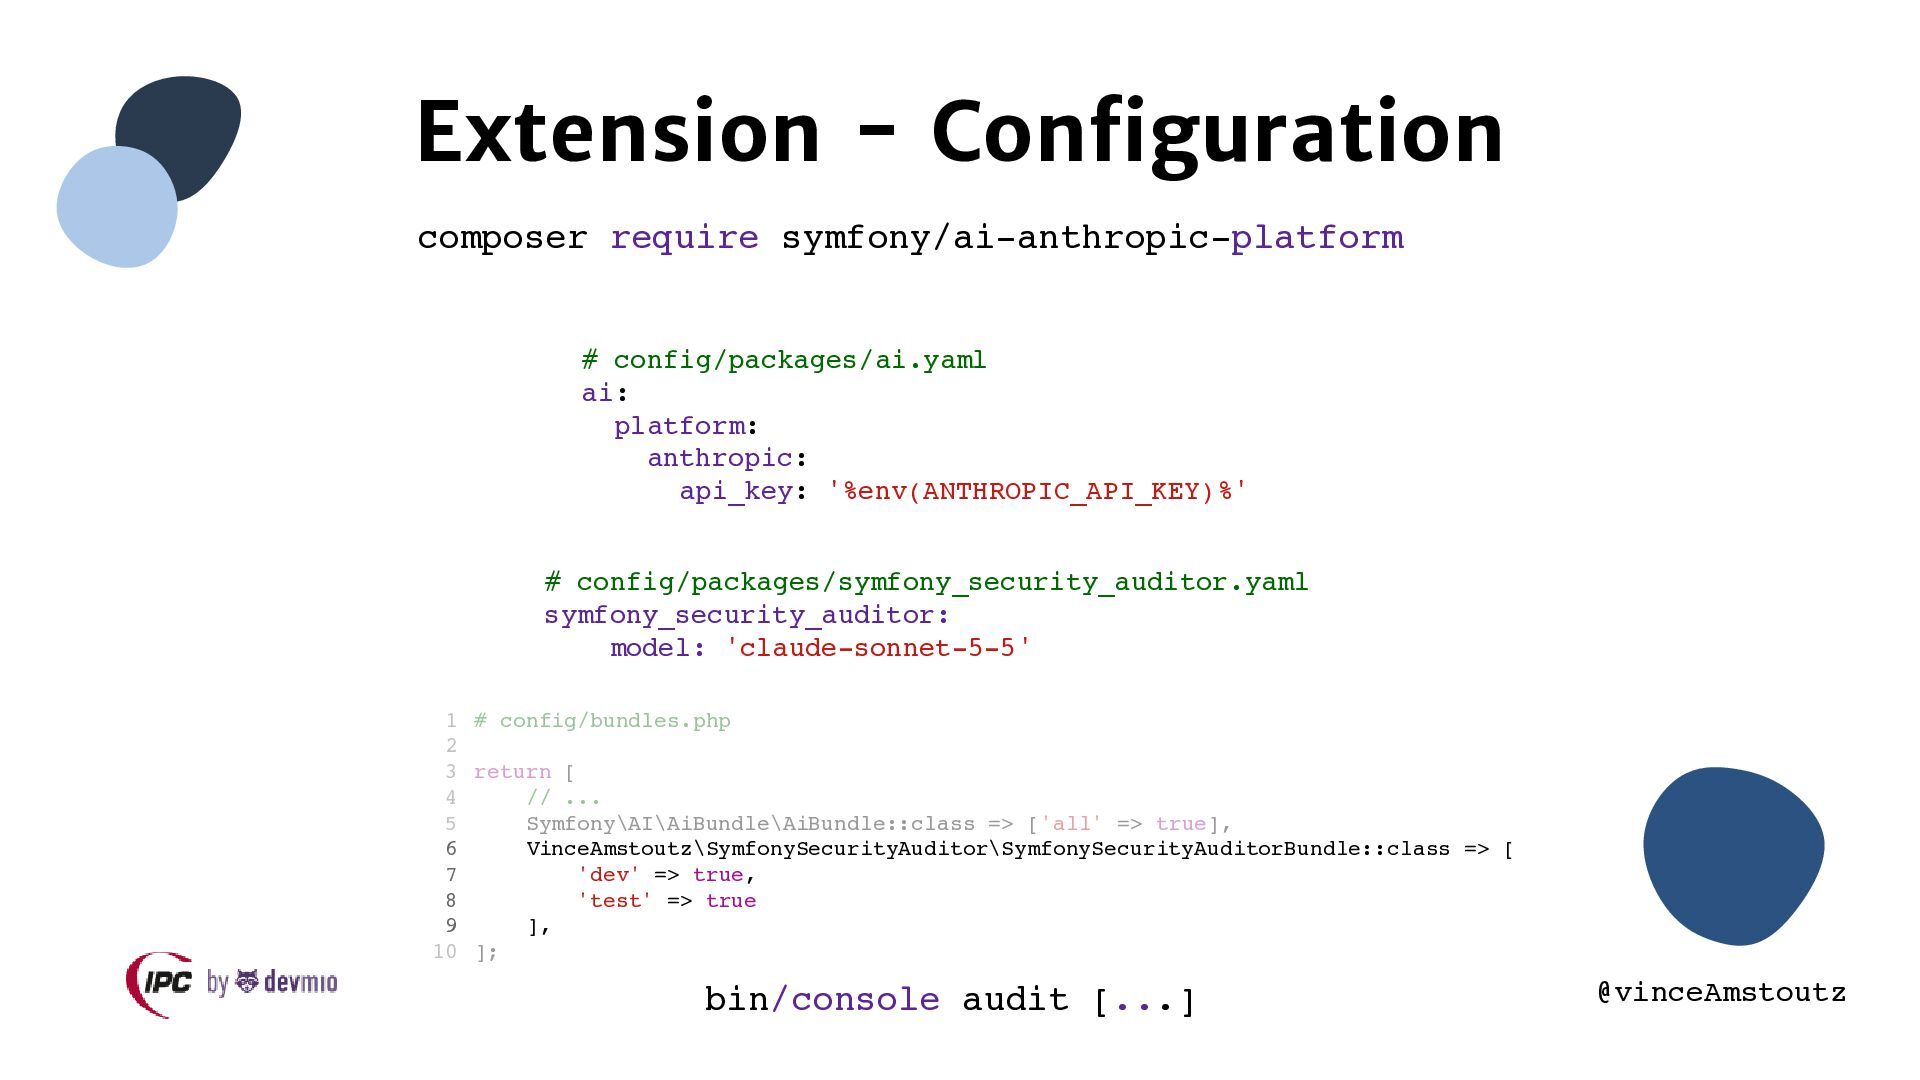
  22. Extension - Configuration # config/packages/ai.yaml ai: platform: anthropic: api_key: '%env(ANTHROPIC_API_KEY)%'

    # config/packages/symfony_security_auditor.yaml symfony_security_auditor: model: 'claude-sonnet-5-5' @vinceAmstoutz
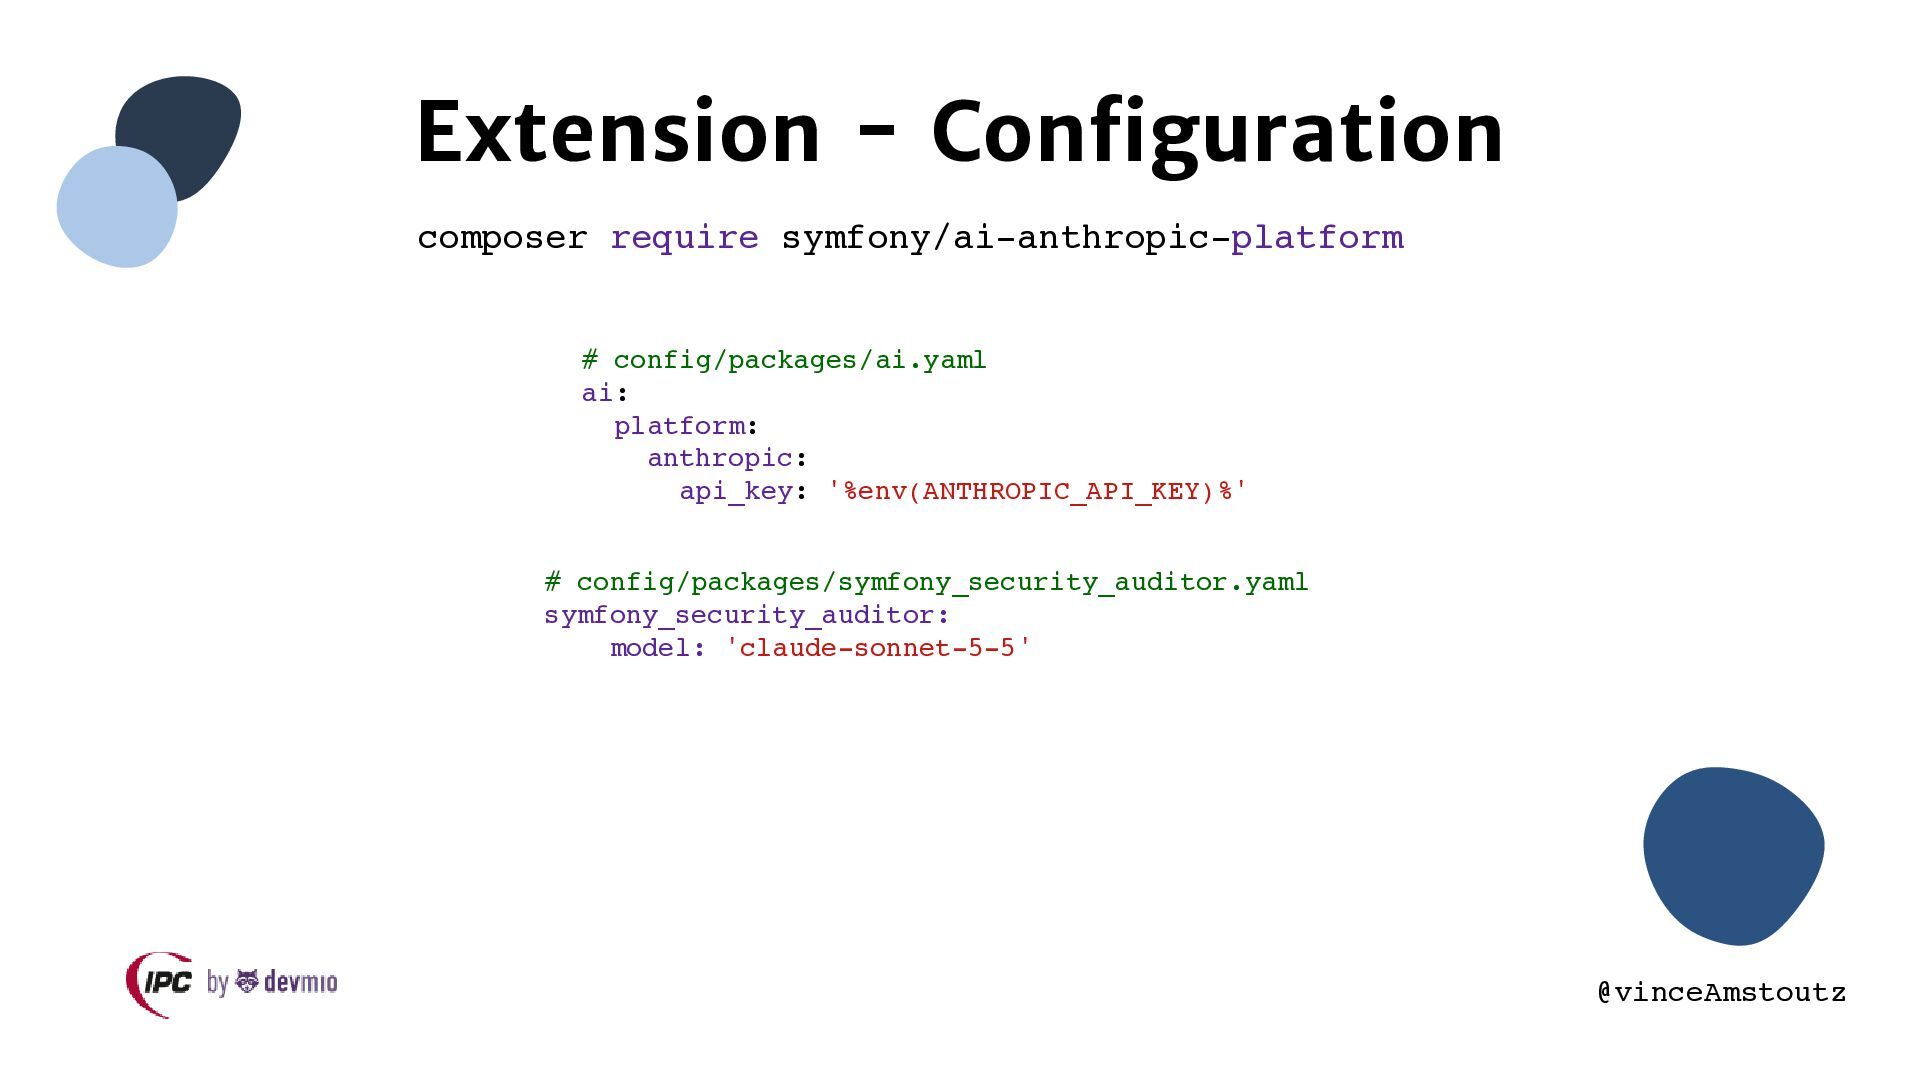
  23. Extension - Configuration composer require symfony/ai-anthropic-platform # config/packages/ai.yaml ai: platform:

    anthropic: api_key: '%env(ANTHROPIC_API_KEY)%' # config/packages/symfony_security_auditor.yaml symfony_security_auditor: model: 'claude-sonnet-5-5' @vinceAmstoutz
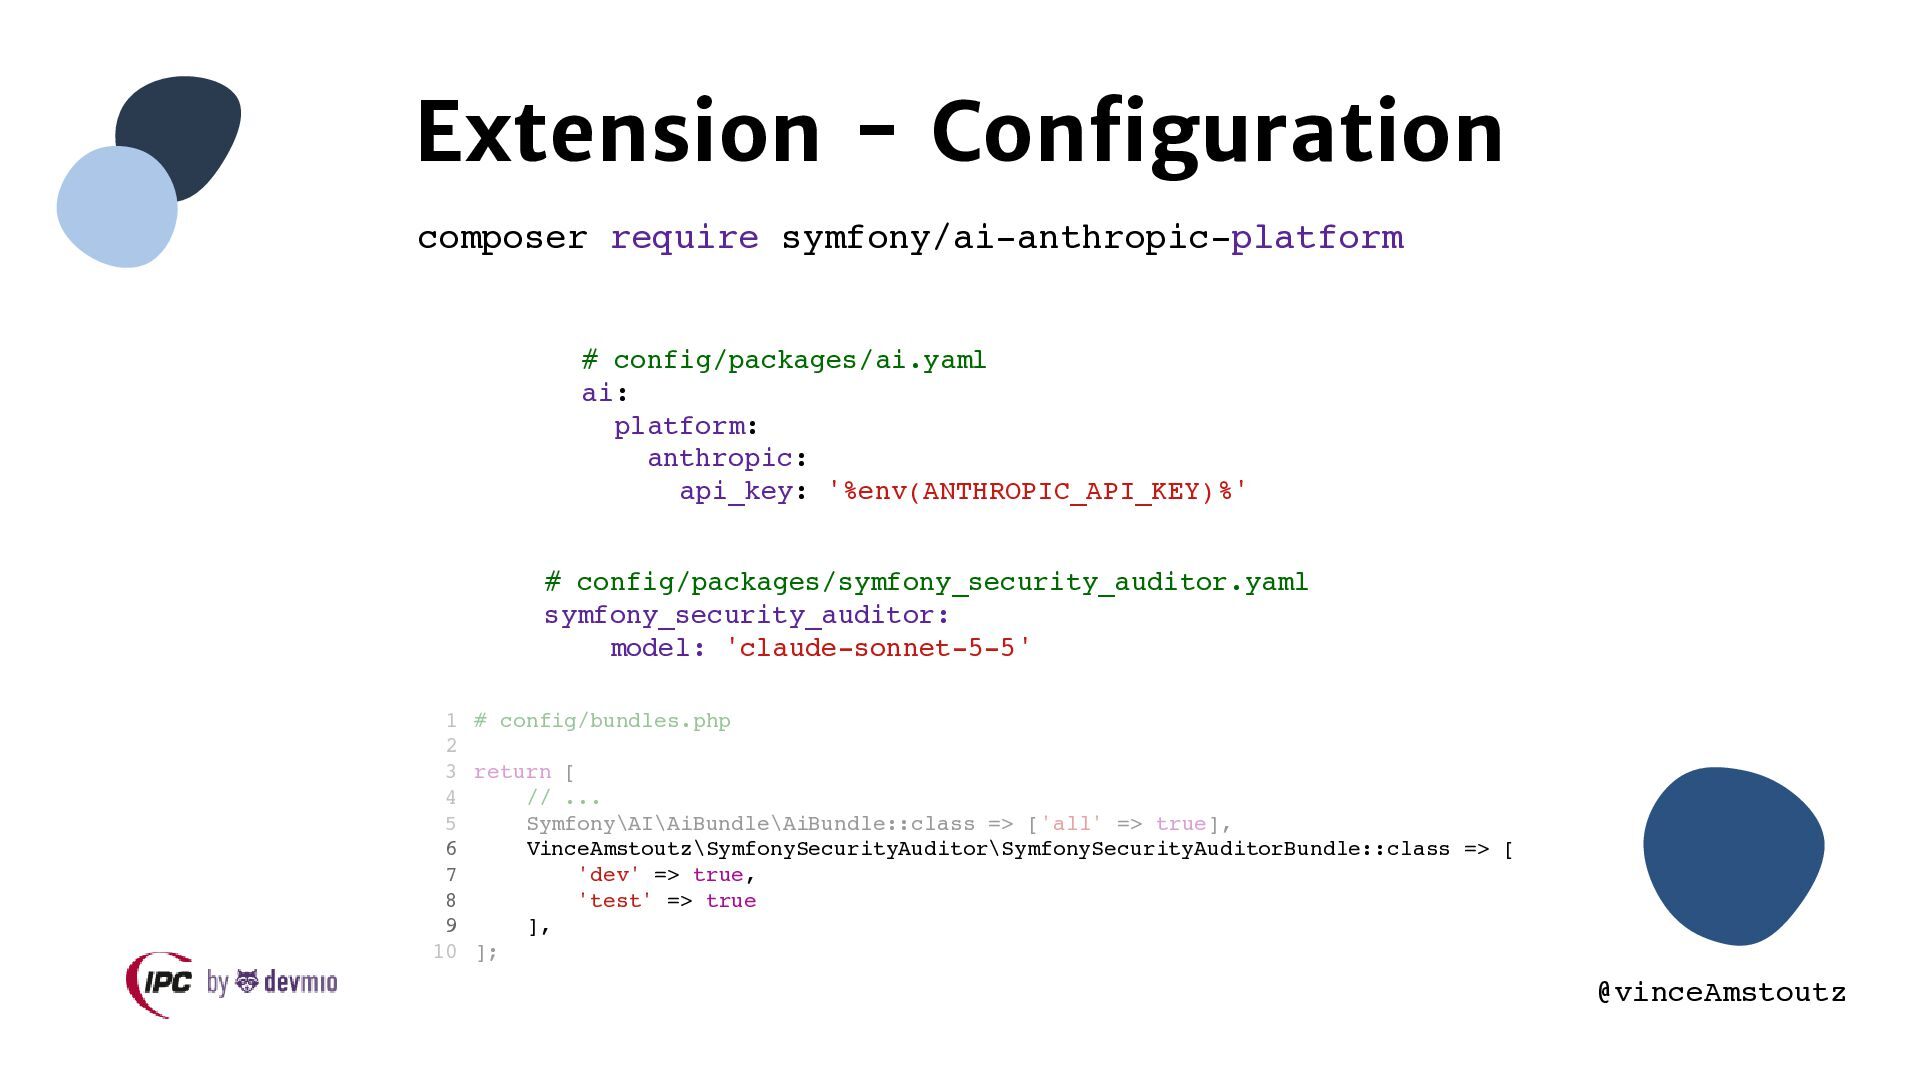
  24. Extension - Configuration composer require symfony/ai-anthropic-platform # config/packages/ai.yaml ai: platform:

    anthropic: api_key: '%env(ANTHROPIC_API_KEY)%' # config/packages/symfony_security_auditor.yaml symfony_security_auditor: model: 'claude-sonnet-5-5' 1 # config/bundles.php 2 3 return [ 4 // ... 5 Symfony\AI\AiBundle\AiBundle::class => ['all' => true], 6 VinceAmstoutz\SymfonySecurityAuditor\SymfonySecurityAuditorBundle::class => [ 7 'dev' => true, 8 'test' => true 9 ], 10 ]; @vinceAmstoutz
  25. Extension - Configuration composer require symfony/ai-anthropic-platform # config/packages/ai.yaml ai: platform:

    anthropic: api_key: '%env(ANTHROPIC_API_KEY)%' # config/packages/symfony_security_auditor.yaml symfony_security_auditor: model: 'claude-sonnet-5-5' 1 # config/bundles.php 2 3 return [ 4 // ... 5 Symfony\AI\AiBundle\AiBundle::class => ['all' => true], 6 VinceAmstoutz\SymfonySecurityAuditor\SymfonySecurityAuditorBundle::class => [ 7 'dev' => true, 8 'test' => true 9 ], 10 ]; bin/console audit [...] @vinceAmstoutz
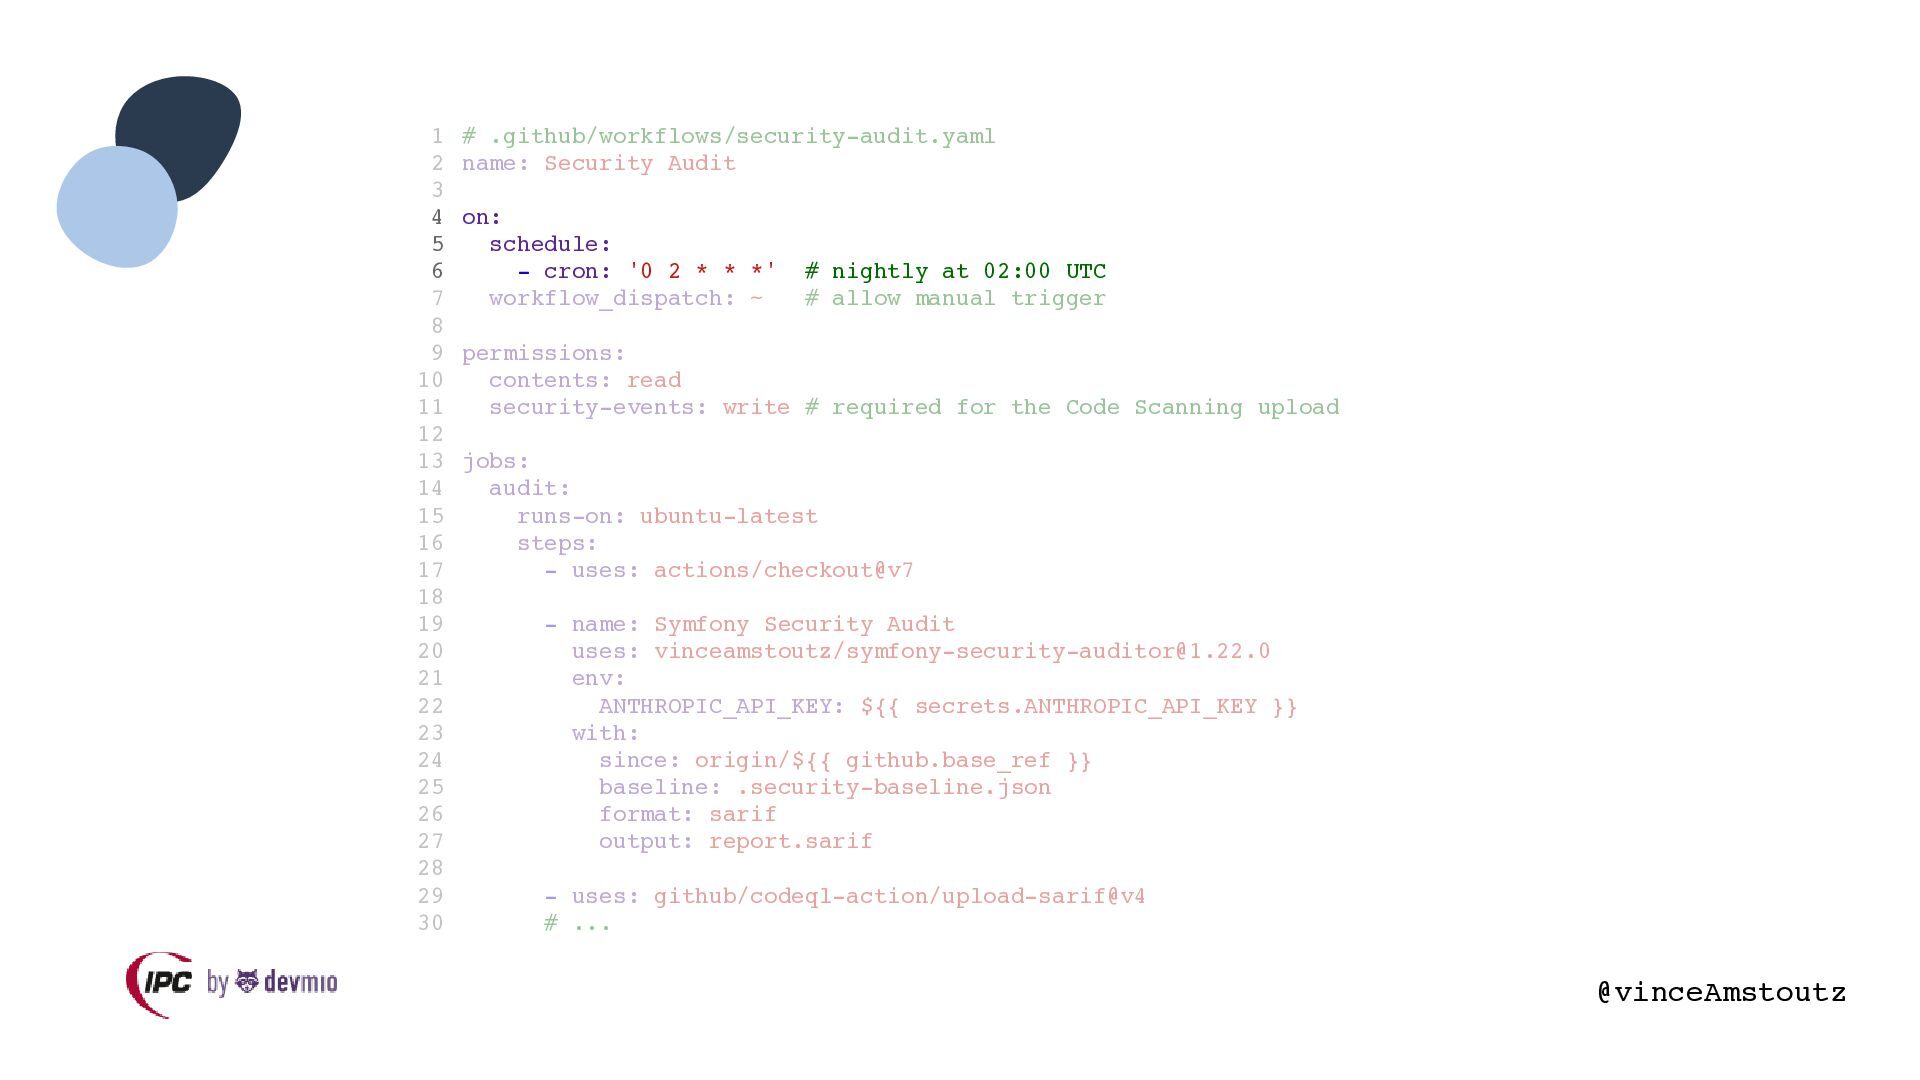
  26. 1 2 3 4 5 6 7 8 9 10

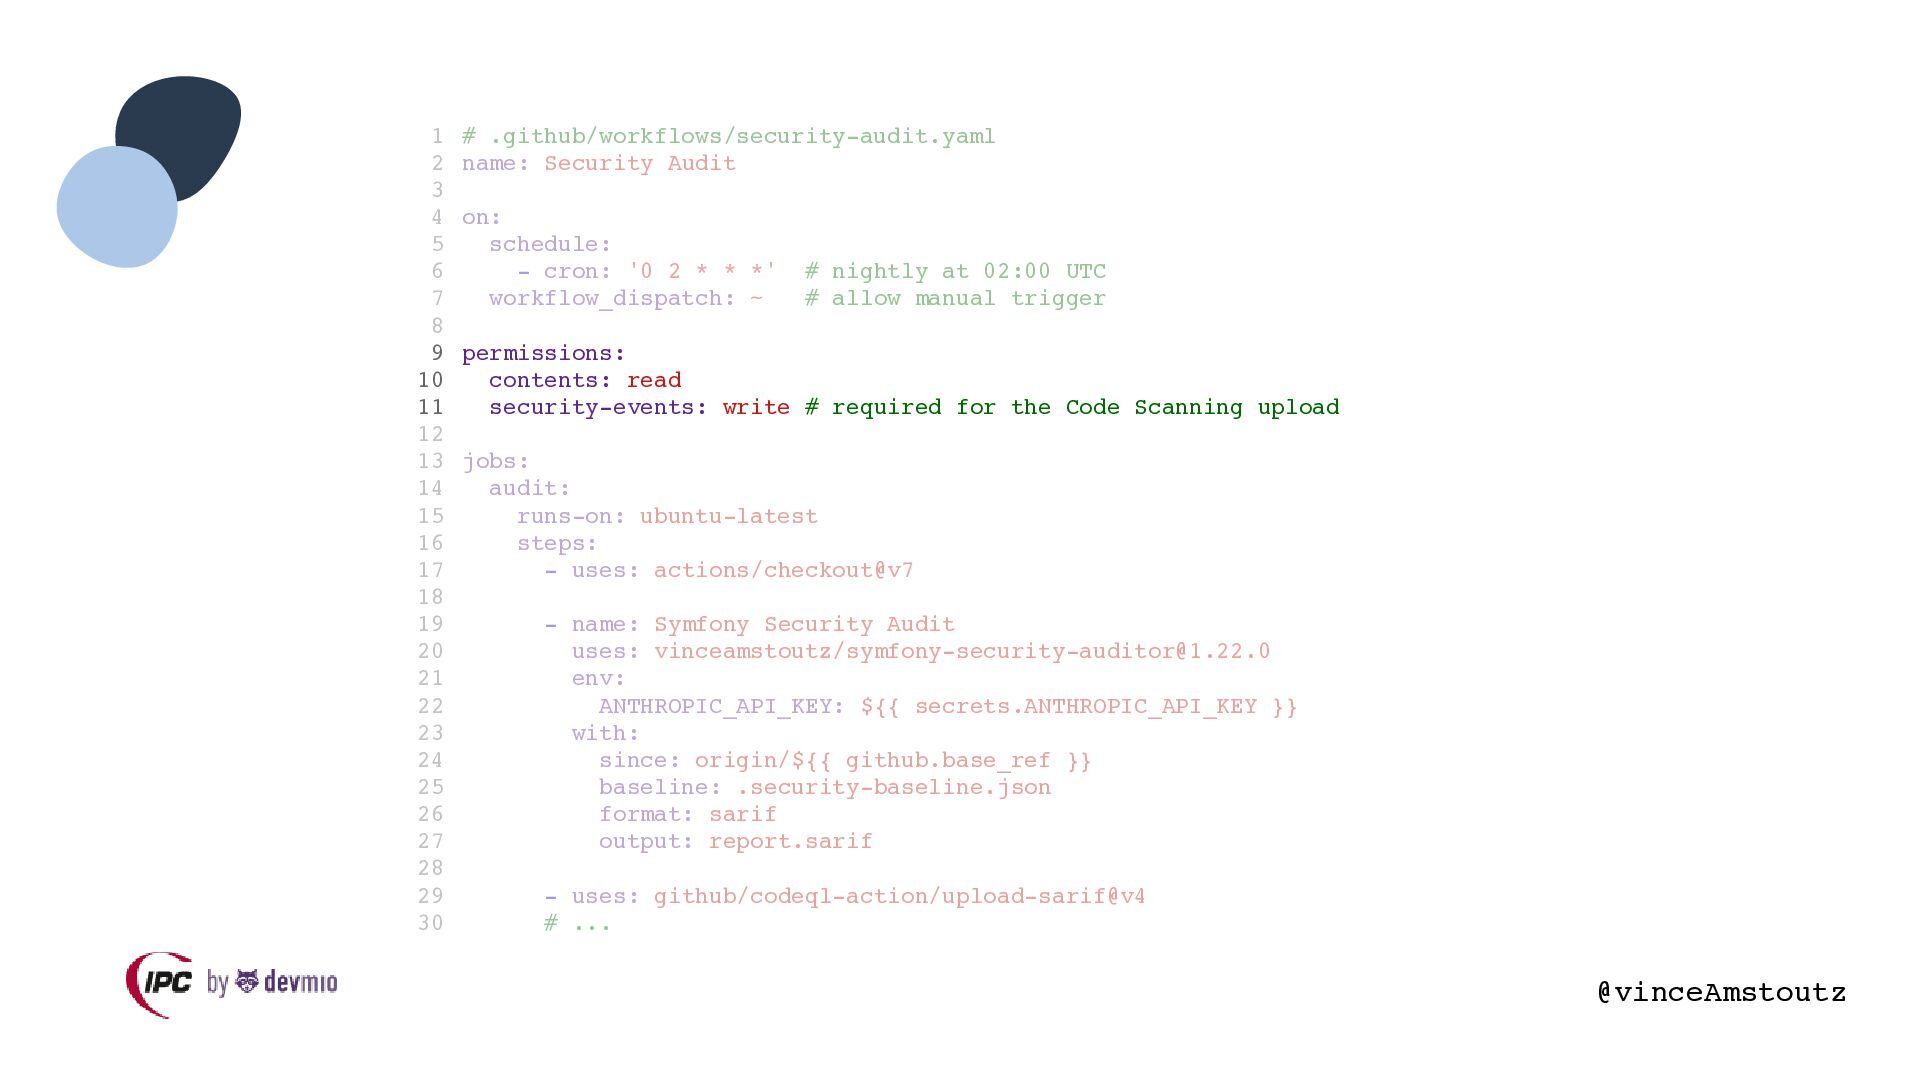
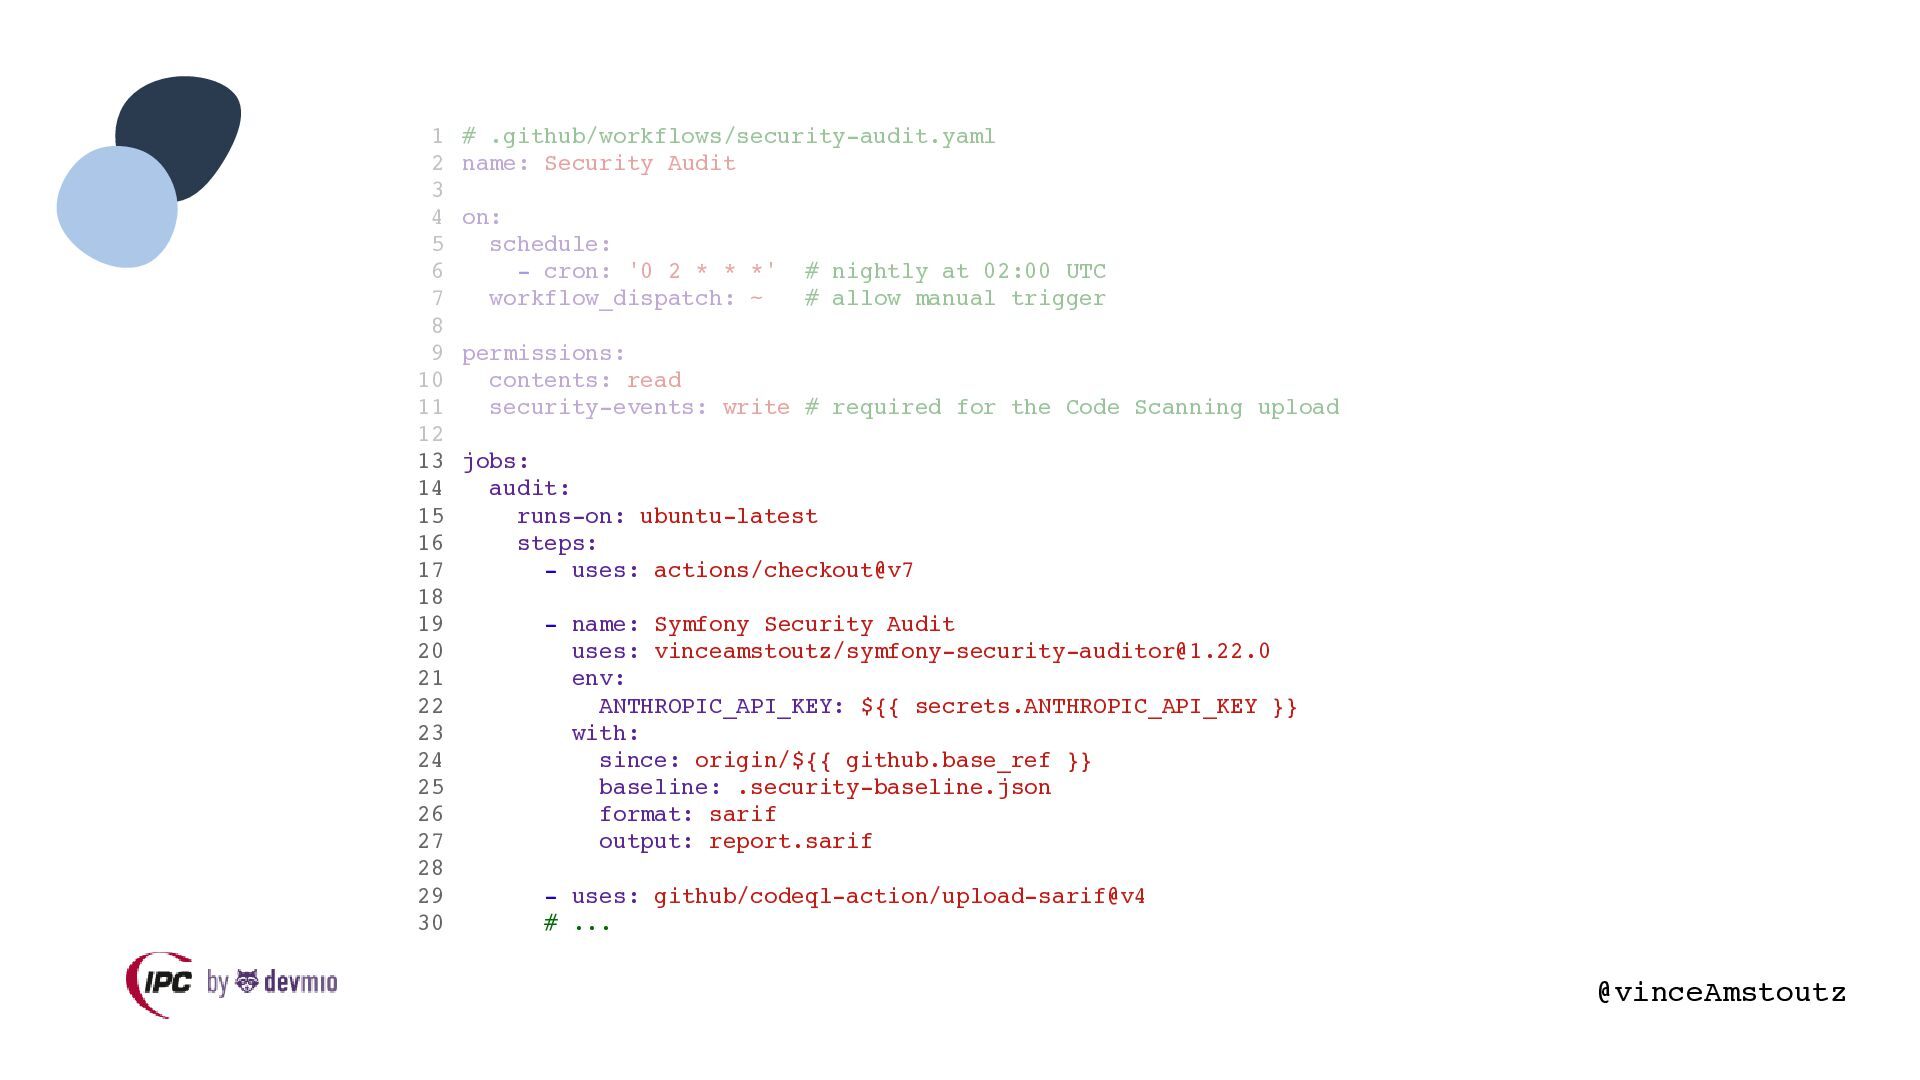
    11 12 13 14 15 16 17 18 19 20 21 22 23 24 25 26 27 28 29 30 # .github/workflows/security-audit.yaml name: Security Audit on: schedule: - cron: '0 2 * * *' workflow_dispatch: ~ # nightly at 02:00 UTC # allow manual trigger permissions: contents: read security-events: write # required for the Code Scanning upload jobs: audit: runs-on: ubuntu-latest steps: - uses: actions/checkout@v7 - name: Symfony Security Audit uses: vinceamstoutz/[email protected] env: ANTHROPIC_API_KEY: ${{ secrets.ANTHROPIC_API_KEY }} with: since: origin/${{ github.base_ref }} baseline: .security-baseline.json format: sarif output: report.sarif - uses: github/codeql-action/upload-sarif@v4 # ... @vinceAmstoutz
  27. 1 2 3 4 5 6 7 8 9 10

    11 12 13 14 15 16 17 18 19 20 21 22 23 24 25 26 27 28 29 30 # .github/workflows/security-audit.yaml name: Security Audit on: schedule: - cron: '0 2 * * *' workflow_dispatch: ~ # nightly at 02:00 UTC # allow manual trigger permissions: contents: read security-events: write # required for the Code Scanning upload jobs: audit: runs-on: ubuntu-latest steps: - uses: actions/checkout@v7 - name: Symfony Security Audit uses: vinceamstoutz/[email protected] env: ANTHROPIC_API_KEY: ${{ secrets.ANTHROPIC_API_KEY }} with: since: origin/${{ github.base_ref }} baseline: .security-baseline.json format: sarif output: report.sarif - uses: github/codeql-action/upload-sarif@v4 # ... @vinceAmstoutz
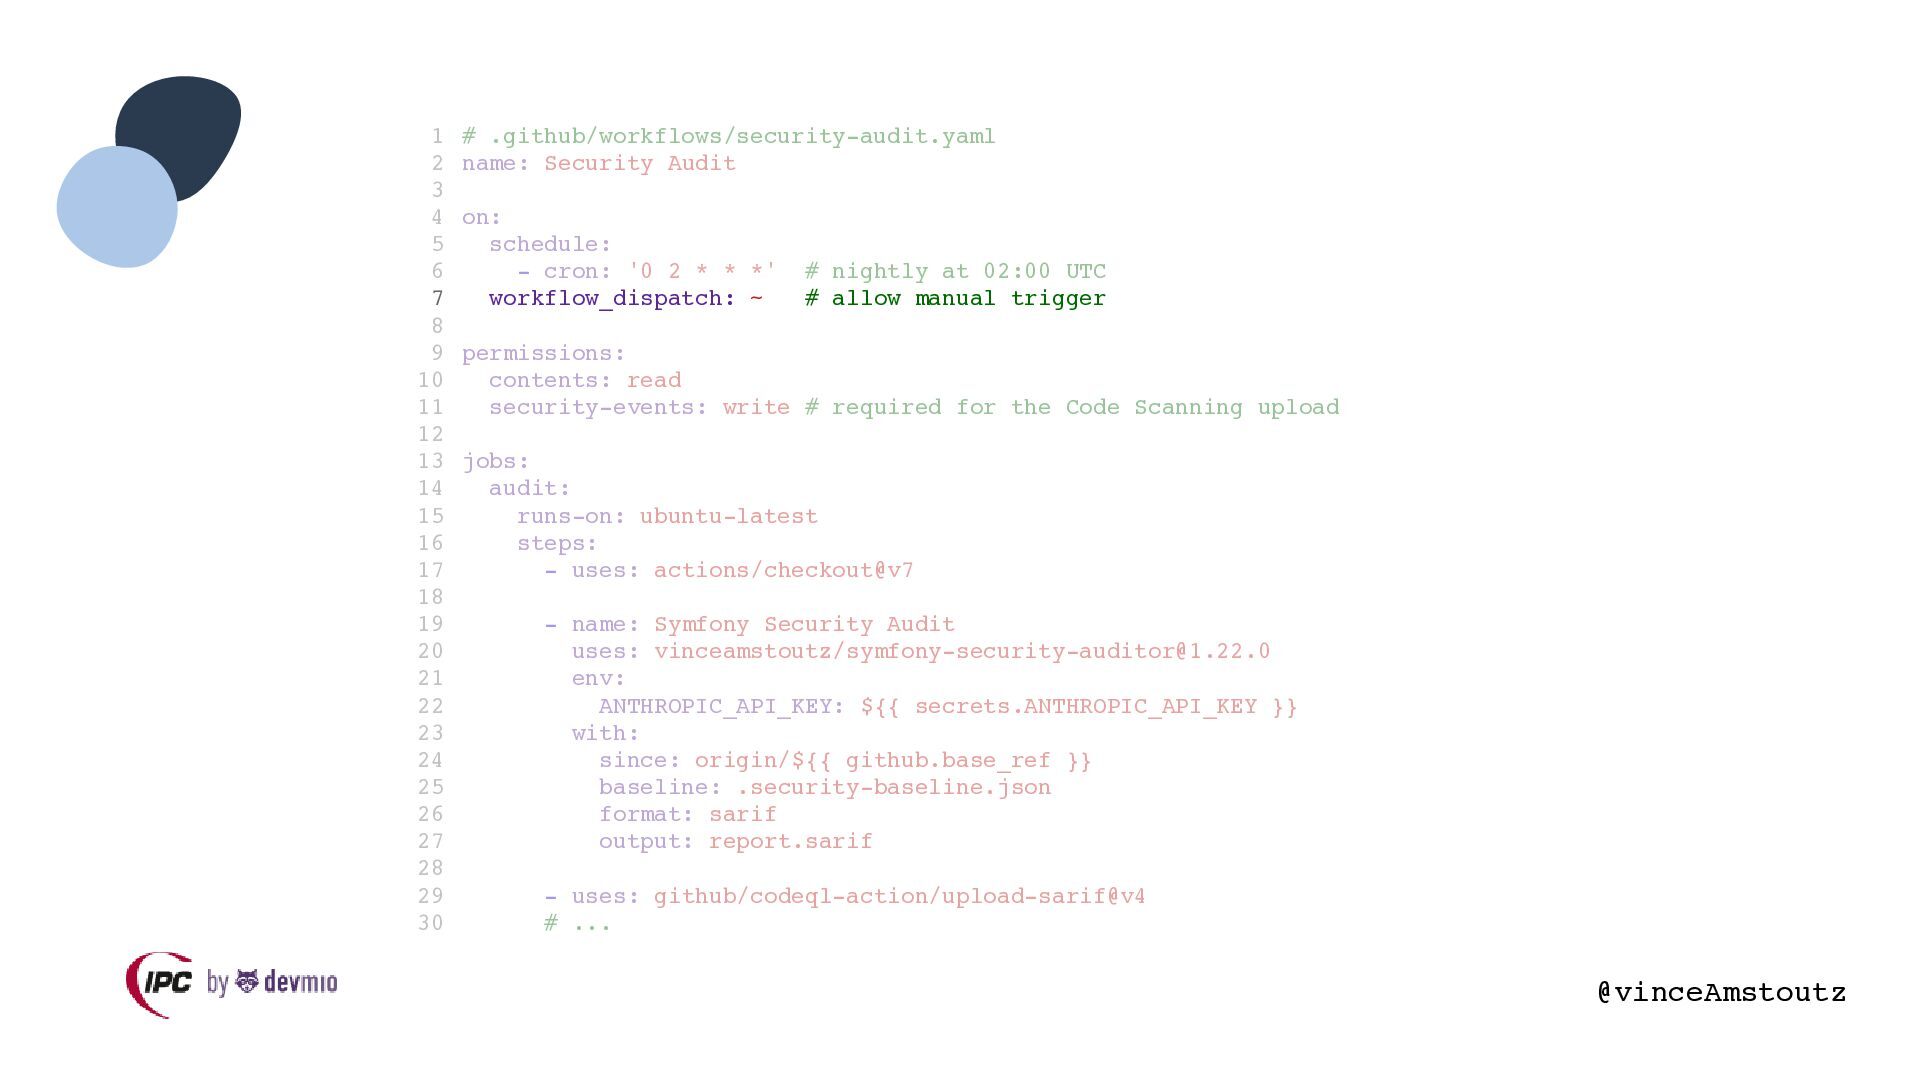
  28. 1 2 3 4 5 6 7 8 9 10

    11 12 13 14 15 16 17 18 19 20 21 22 23 24 25 26 27 28 29 30 # .github/workflows/security-audit.yaml name: Security Audit on: schedule: - cron: '0 2 * * *' workflow_dispatch: ~ # nightly at 02:00 UTC # allow manual trigger permissions: contents: read security-events: write # required for the Code Scanning upload jobs: audit: runs-on: ubuntu-latest steps: - uses: actions/checkout@v7 - name: Symfony Security Audit uses: vinceamstoutz/[email protected] env: ANTHROPIC_API_KEY: ${{ secrets.ANTHROPIC_API_KEY }} with: since: origin/${{ github.base_ref }} baseline: .security-baseline.json format: sarif output: report.sarif - uses: github/codeql-action/upload-sarif@v4 # ... @vinceAmstoutz
  29. 1 2 3 4 5 6 7 8 9 10

    11 12 13 14 15 16 17 18 19 20 21 22 23 24 25 26 27 28 29 30 # .github/workflows/security-audit.yaml name: Security Audit on: schedule: - cron: '0 2 * * *' workflow_dispatch: ~ # nightly at 02:00 UTC # allow manual trigger permissions: contents: read security-events: write # required for the Code Scanning upload jobs: audit: runs-on: ubuntu-latest steps: - uses: actions/checkout@v7 - name: Symfony Security Audit uses: vinceamstoutz/[email protected] env: ANTHROPIC_API_KEY: ${{ secrets.ANTHROPIC_API_KEY }} with: since: origin/${{ github.base_ref }} baseline: .security-baseline.json format: sarif output: report.sarif - uses: github/codeql-action/upload-sarif@v4 # ... @vinceAmstoutz
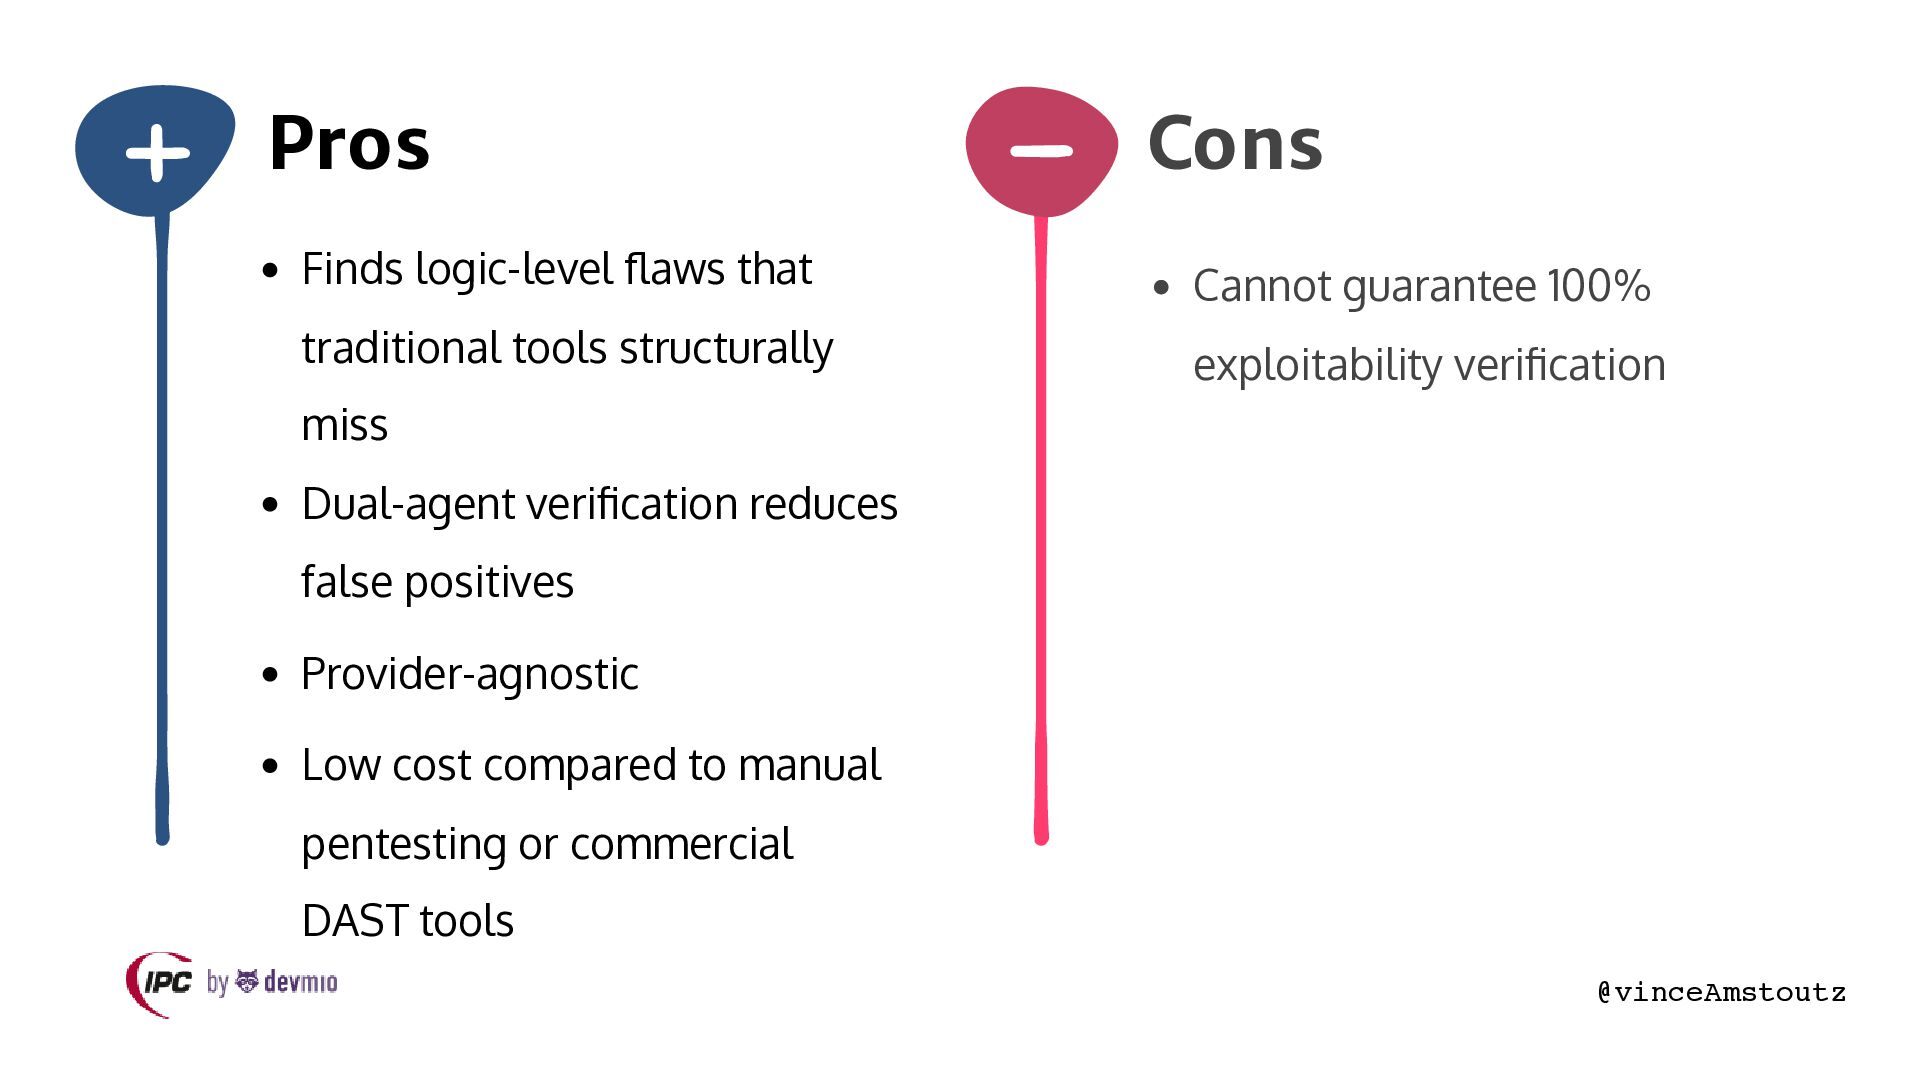
  30. Pros Finds logic-level flaws that traditional tools structurally miss Dual-agent

    verification reduces false positives @vinceAmstoutz
  31. Pros Finds logic-level flaws that traditional tools structurally miss Dual-agent

    verification reduces false positives Provider-agnostic @vinceAmstoutz
  32. Pros Finds logic-level flaws that traditional tools structurally miss Dual-agent

    verification reduces false positives Provider-agnostic Low cost compared to manual pentesting or commercial DAST tools @vinceAmstoutz
  33. Pros Cons Finds logic-level flaws that traditional tools structurally miss

    Dual-agent verification reduces false positives Provider-agnostic Low cost compared to manual pentesting or commercial DAST tools @vinceAmstoutz
  34. Pros Cons Finds logic-level flaws that Cannot guarantee 100% traditional

    tools structurally exploitability verification miss Dual-agent verification reduces false positives Provider-agnostic Low cost compared to manual pentesting or commercial DAST tools @vinceAmstoutz
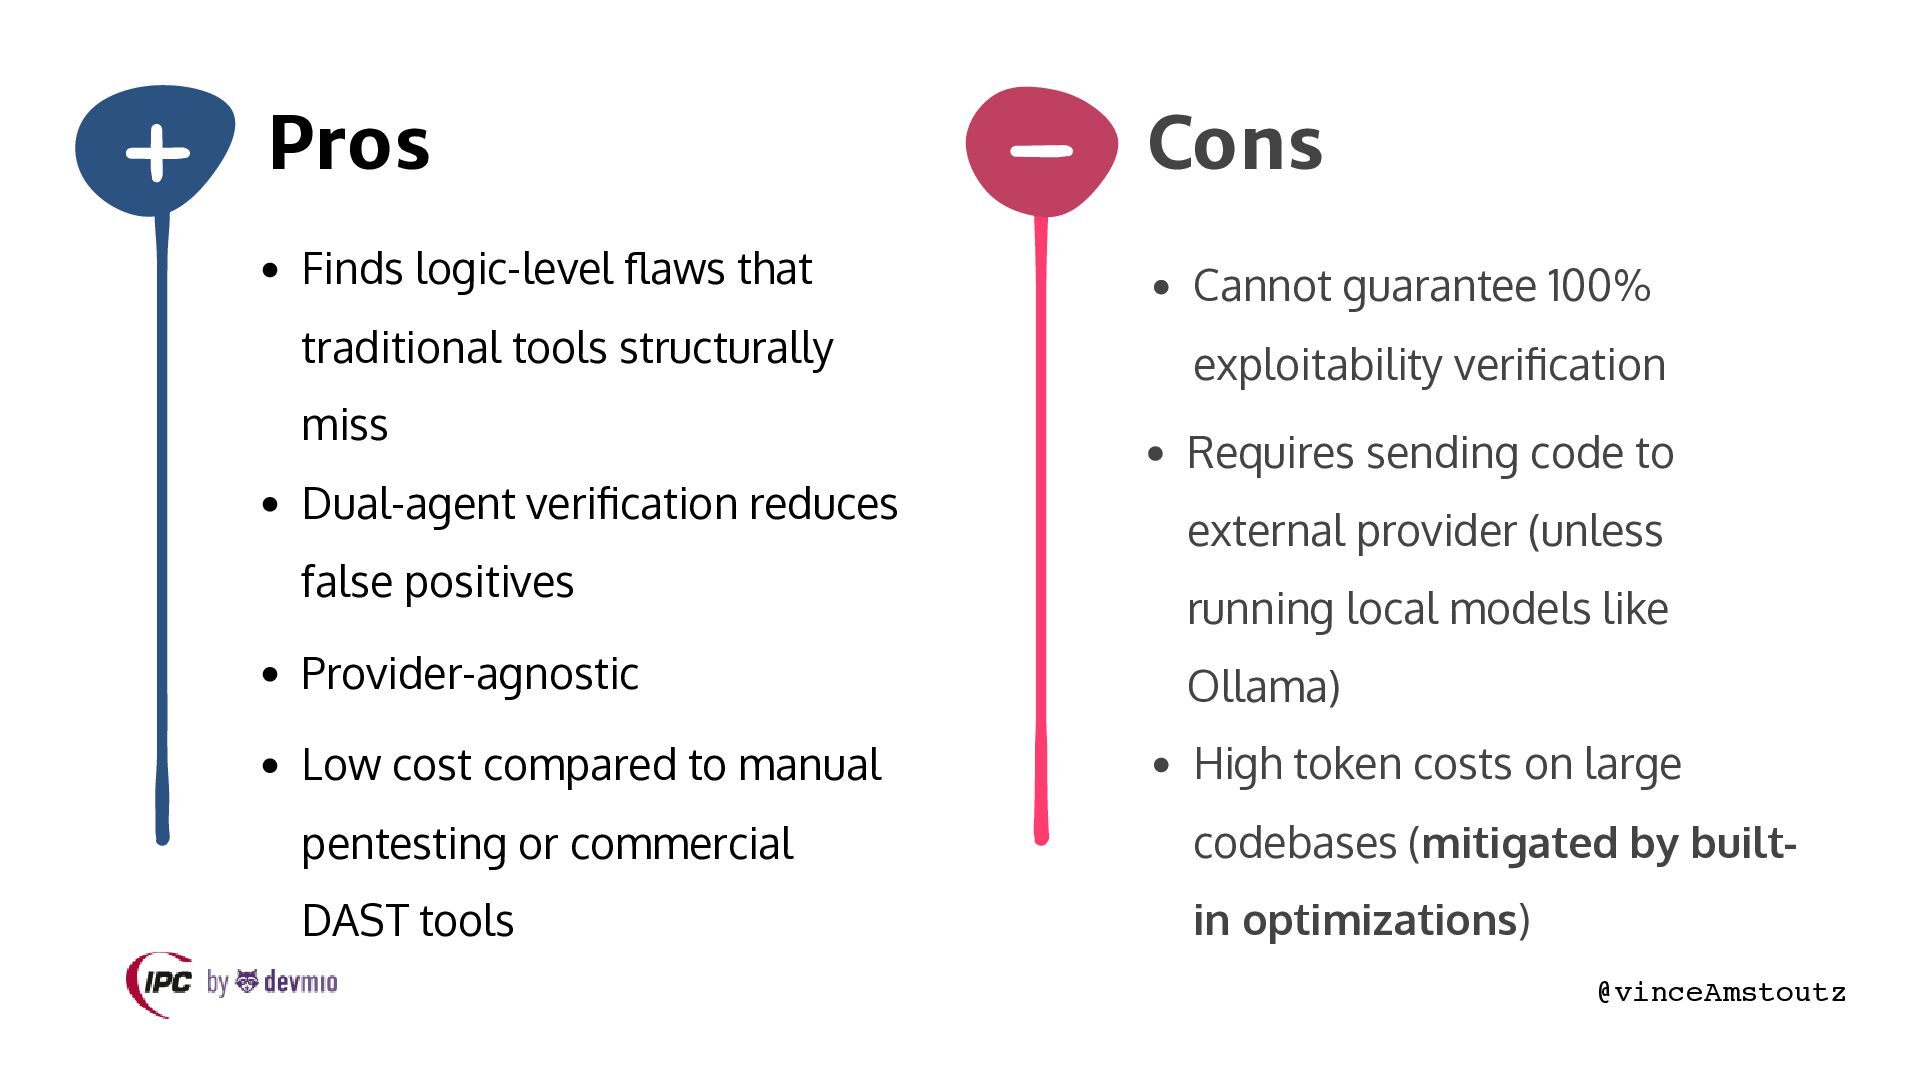
  35. Pros Cons Finds logic-level flaws that Cannot guarantee 100% traditional

    tools structurally exploitability verification miss Dual-agent verification reduces false positives Provider-agnostic Requires sending code to external provider (unless running local models like Ollama) Low cost compared to manual pentesting or commercial DAST tools @vinceAmstoutz
  36. Pros Cons Finds logic-level flaws that Cannot guarantee 100% traditional

    tools structurally exploitability verification miss Dual-agent verification reduces false positives Requires sending code to external provider (unless running local models like Provider-agnostic Ollama) Low cost compared to manual High token costs on large pentesting or commercial codebases (mitigated by built- DAST tools in optimizations) @vinceAmstoutz