Share
Embed
BtleJuice: The Bluetooth Smart MitM Framework
Tool presented and released at DEF CON 24.
Damien Cauquil
August 06, 2016
Transcript
51 slides
-
/ME Senior researcher at CERT-UBIK (ECONOCOM) Head of Research and
Development Focus on Bluetooth Smart since 2014 Twitter (me): @virtualabs Twitter CERT-UBIK: @iotcert -
AGENDA Bluetooth Smart (or Low Energy) 101 Bluetooth Smart vs.
Bluetooth Classic Why sniffing sucks Man-in-the-Middle attacks on BTLE BtleJuice MitM framework Live demos ! -
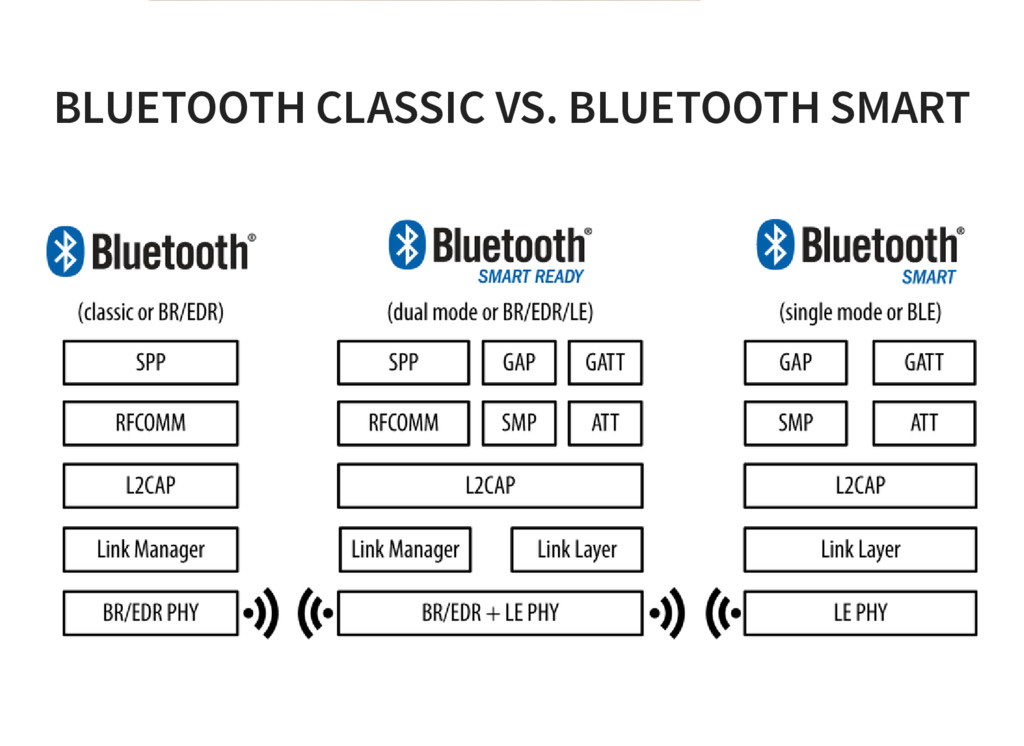
BLUETOOTH CLASSIC VS. BLUETOOTH SMART Both defined in the Bluetooth
4.0+ Specs Bluetooth Smart was designed for low power devices (Low Energy) Bluetooth Smart is lighter than Bluetooth Classic Bluetooth Smart is widely used in tiny embedded devices -
BLUETOOTH SMART MAIN FEATURES Frequency Hopping Spread Spectrum to avoid
interferences (FHSS) Encrypted communications (Security Manager Protocol) Simple communications through Services and characteristics (GAP/GATT) One connection at a time -
FREQUENCY HOPPING SPREAD SPECTRUM Devices synchronize first ... ... then
both of them hop from channel to channel Difficult to sniff an existing connection between two devices ! -
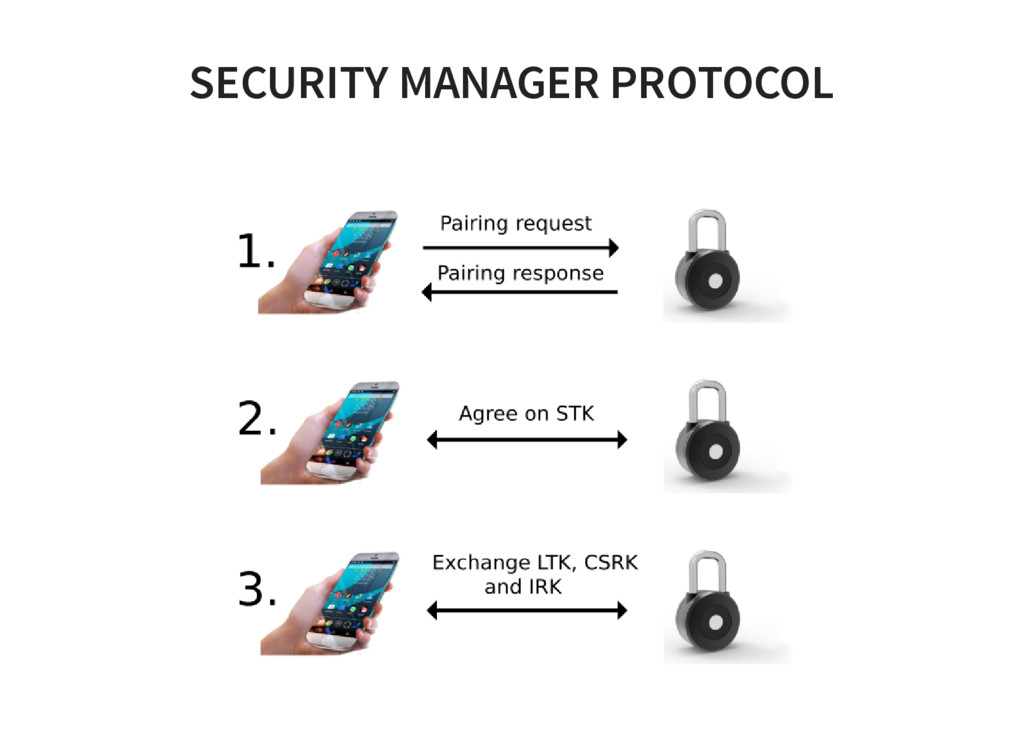
SECURITY MANAGER PROTOCOL Devices exchange pairing information (JustWorks, PIN, OOB)
Devices authenticate the link Keys are distributed and long-term keys stored One must sniff this exchange to break the encryption keys (CrackLE) -
THE HARD TRUTH IS: Few devices use encryption but do
not require it (failed pairing is OK) Almost all devices are not strongly authenticated by mobile applications or other devices BD address is o en the only check performed to ensure authenticity Sniffing-based attacks are difficult to perform in the wild -
WHY BTLE SNIFFING SUCKS Ubertooth: $120 Adafruit Bluefruit sniffer: $30
(non-standard PCAP) btproxy: only works for Bluetooth Classic, not BTLE Encryption: sniff first then decrypt -
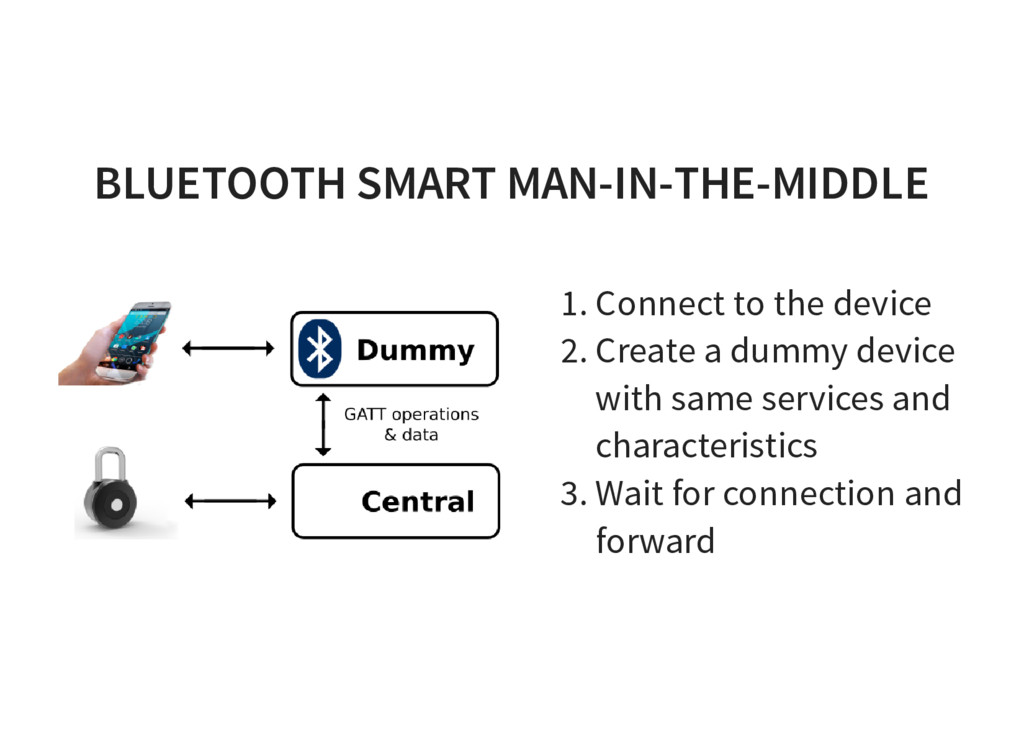
BLUETOOTH SMART MAN-IN-THE-MIDDLE 1. Connect to the device 2. Create
a dummy device with same services and characteristics 3. Wait for connection and forward -
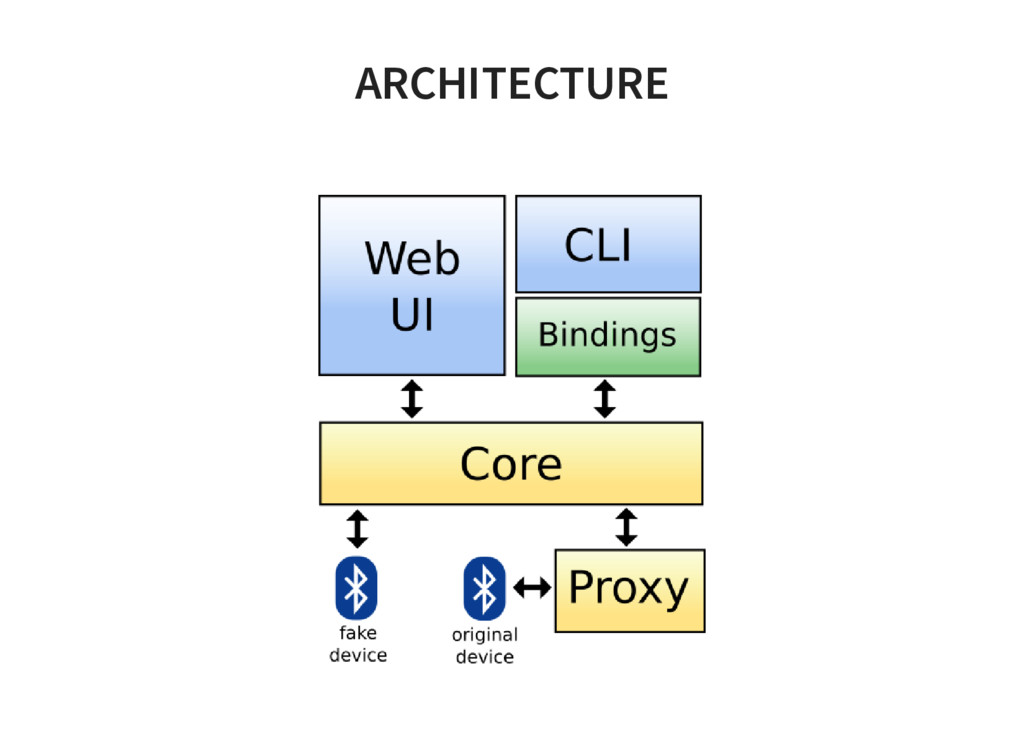
INTRODUCING BTLEJUICE FRAMEWORK Noble for central and Bleno for dummy
Standard BT 4.0+ adapters for both central and dummy Websocket to forward GATT operations (and more) Supports bonding (JustWorks) for Bluez 5.x and Linux kernel 4.x -
HOLD ON, A SIMILAR TOOL EXISTS ! Presented @ BHUSA
2016 by Slawomir Jasek I just discovered it yesterday (thanks to its author) Same libs, same requirements I just discovered it yesterday (thanks to its author) Same goal, different tools More tricks with Bleno and Noble http://www.gattack.io/ https://en.wikipedia.org/wiki/Multiple_discovery -
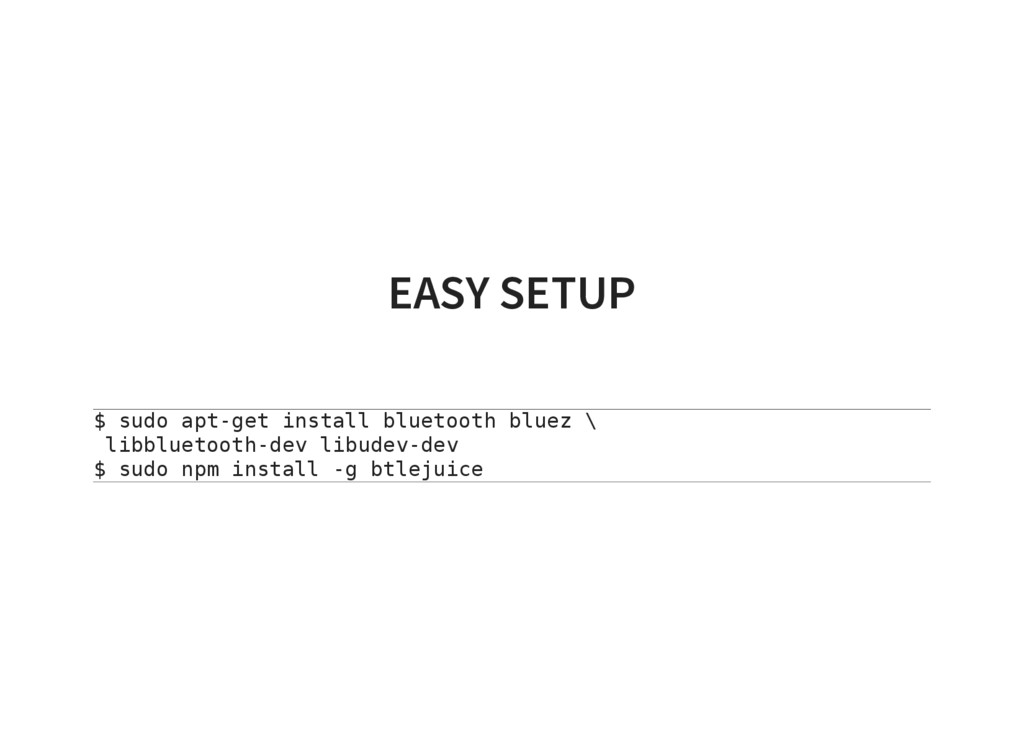
EASY SETUP $ s u d o a p t
- g e t i n s t a l l b l u e t o o t h b l u e z \ l i b b l u e t o o t h - d e v l i b u d e v - d e v $ s u d o n p m i n s t a l l - g b t l e j u i c e -
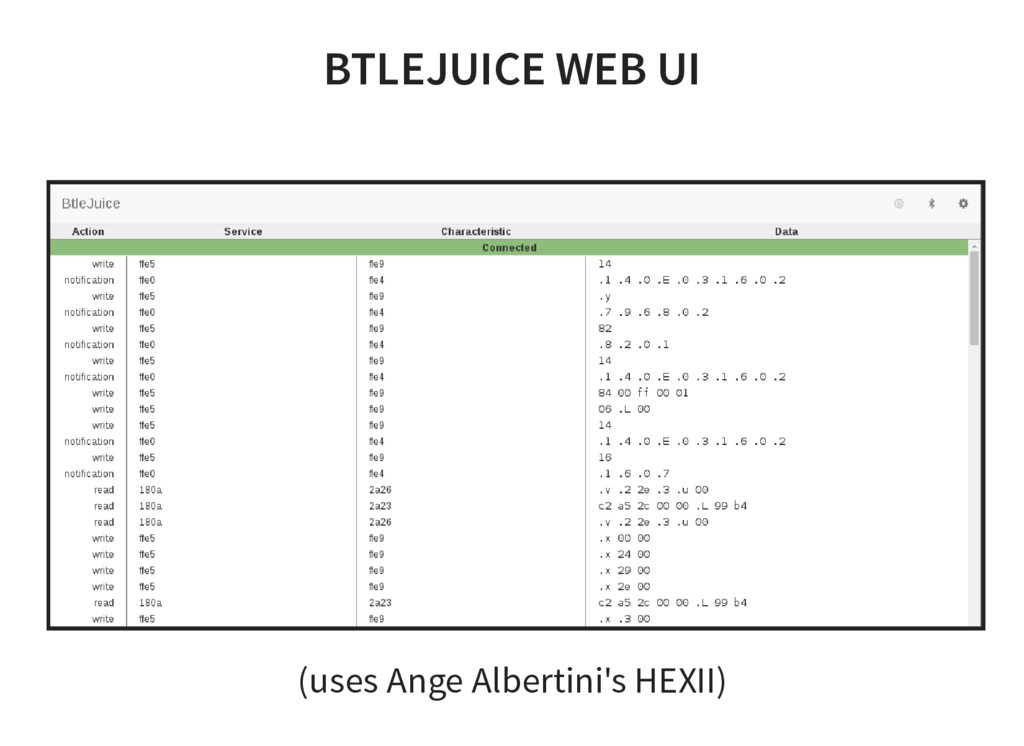
BTLEJUICE FEATURES Live GATT operations and data sniffing Burp-like interception
mode allows data manipulation Web user interface Python bindings (2.x & 3.x) Node.js bindings (ES6) -
REQUIREMENTS Two-machine setup (we can use a VM too) Two
Bluetooth 4.0+ adapters (CSR 4.0+ ideally) Node >= v4.3.0 -
MAN-IN-THE-MIDDLE BENEFITS Works with any Bluetooth 4.0+ adapters Intercepting GATT
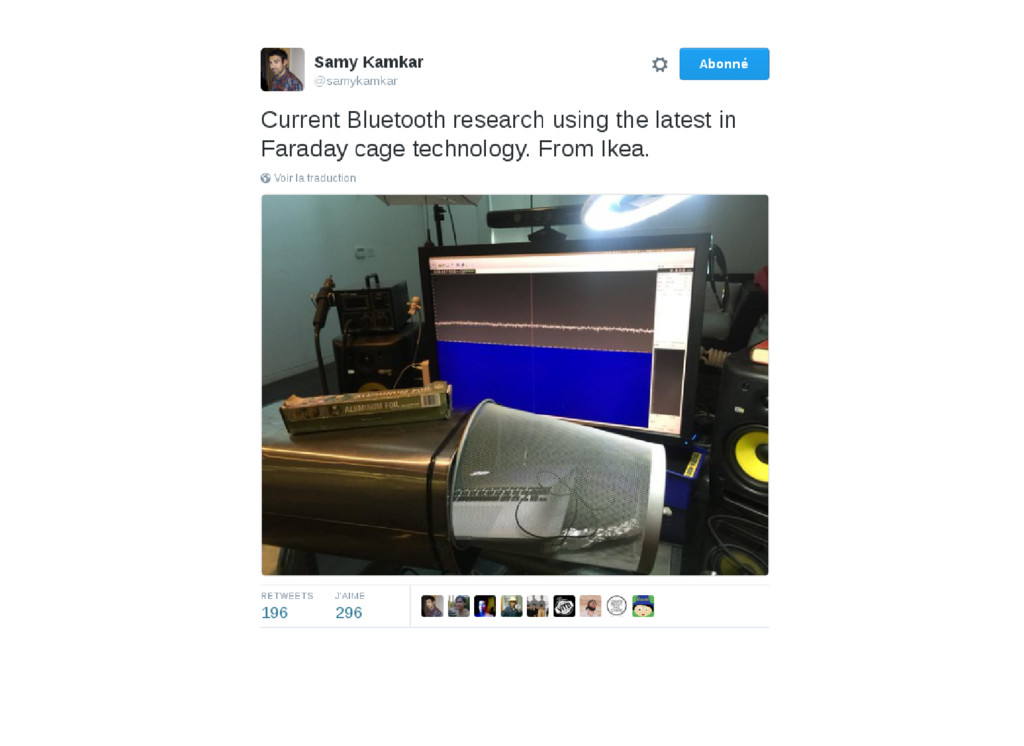
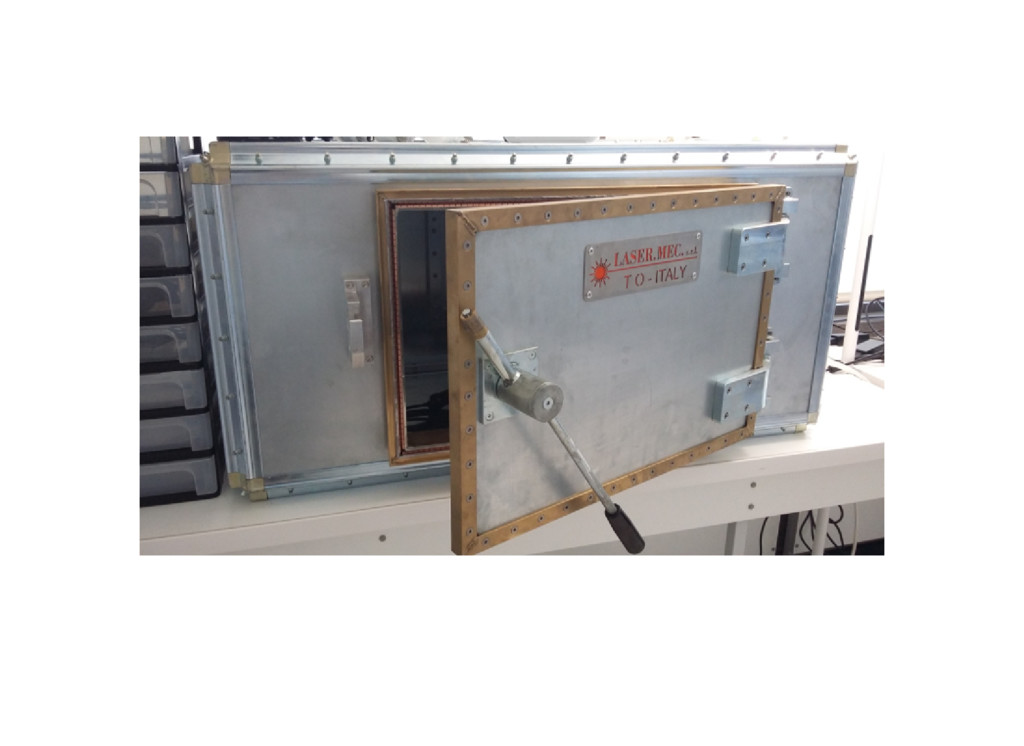
reads and writes are way easier Supports bonding/encryption ! Compatible with tests using a Faraday cage BD address spoofing is possible =) -
CREATING THE PERFECT DUMMY (OR HOW TO CLONE A DEVICE)
Connect BtleJuice Proxy to target device ... No more advertisement, frequency hopping active ! BD address can be spoofed using CSR adapters We can advertise a new device with same address while connected to the original one ὠ -
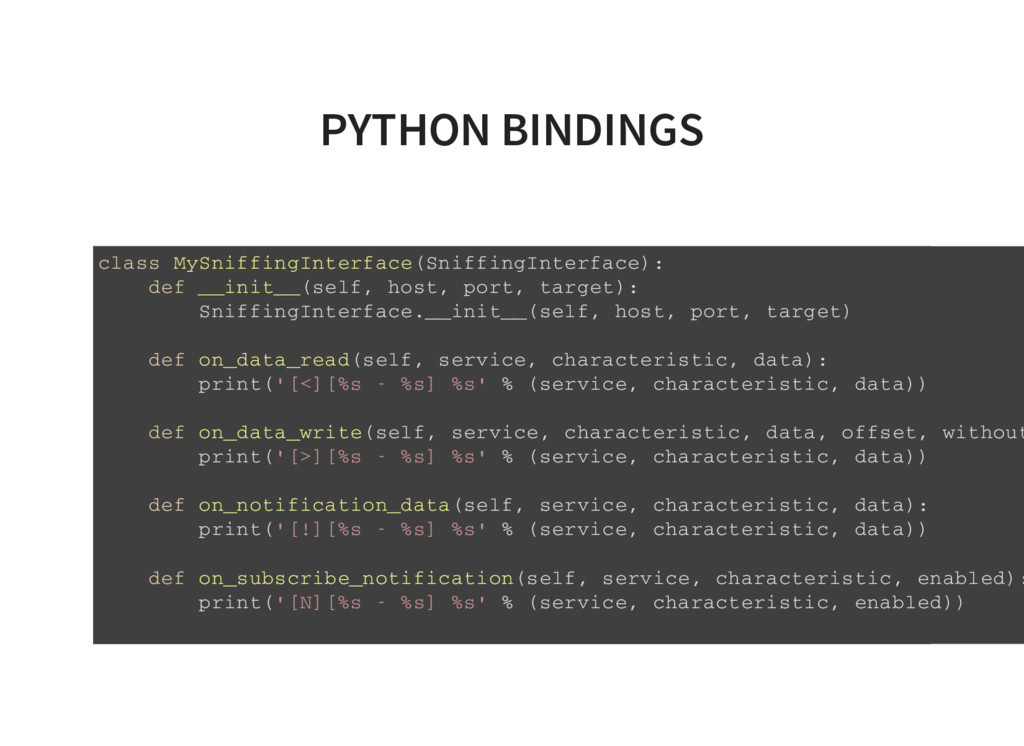
PYTHON BINDINGS class MySniffingInterface(SniffingInterface): def __init__(self, host, port, target): SniffingInterface.__init__(self,
host, port, target) def on_data_read(self, service, characteristic, data): print('[<][%s - %s] %s' % (service, characteristic, data)) def on_data_write(self, service, characteristic, data, offset, without print('[>][%s - %s] %s' % (service, characteristic, data)) def on_notification_data(self, service, characteristic, data): print('[!][%s - %s] %s' % (service, characteristic, data)) def on_subscribe_notification(self, service, characteristic, enabled): print('[N][%s - %s] %s' % (service, characteristic, enabled)) -
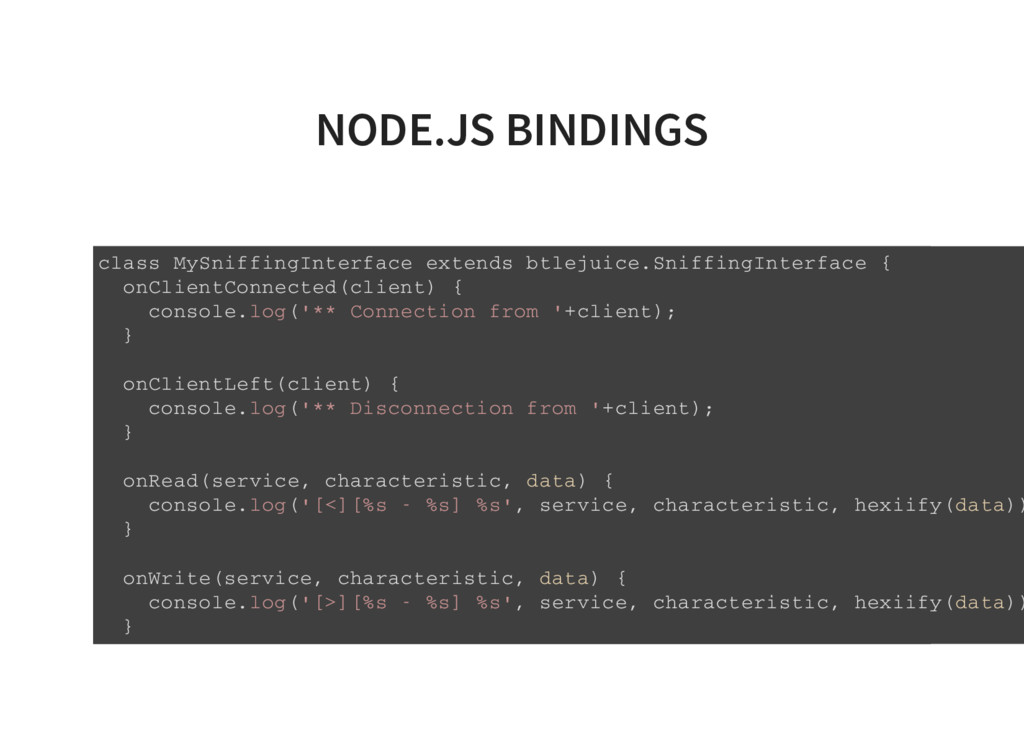
NODE.JS BINDINGS class MySniffingInterface extends btlejuice.SniffingInterface { onClientConnected(client) { console.log('**
Connection from '+client); } onClientLeft(client) { console.log('** Disconnection from '+client); } onRead(service, characteristic, data) { console.log('[<][%s - %s] %s', service, characteristic, hexiify(data)) } onWrite(service, characteristic, data) { console.log('[>][%s - %s] %s', service, characteristic, hexiify(data)) } -
ON-THE-FLY DATA MODIFICATION def on_before_read(self, service, characteristic, offset): if service.lower()
== '180f' and \ characteristic.lower()=='2a19': self.batt_level -= 1 if self.batt_level < 0: self.batt_level = 100 raise HookForceResponse(chr(self.batt_level)) def on_before_subscribe(self, service, characteristic, enabled): # dismiss raise HookForceResponse() -
KNOWN LIMITATIONS Noble does not support long writes (>22 bytes)
Induced latency (BTLE to websocket then back to BTLE) May be tricky to use when devices keep connections or advertise during a short delay -
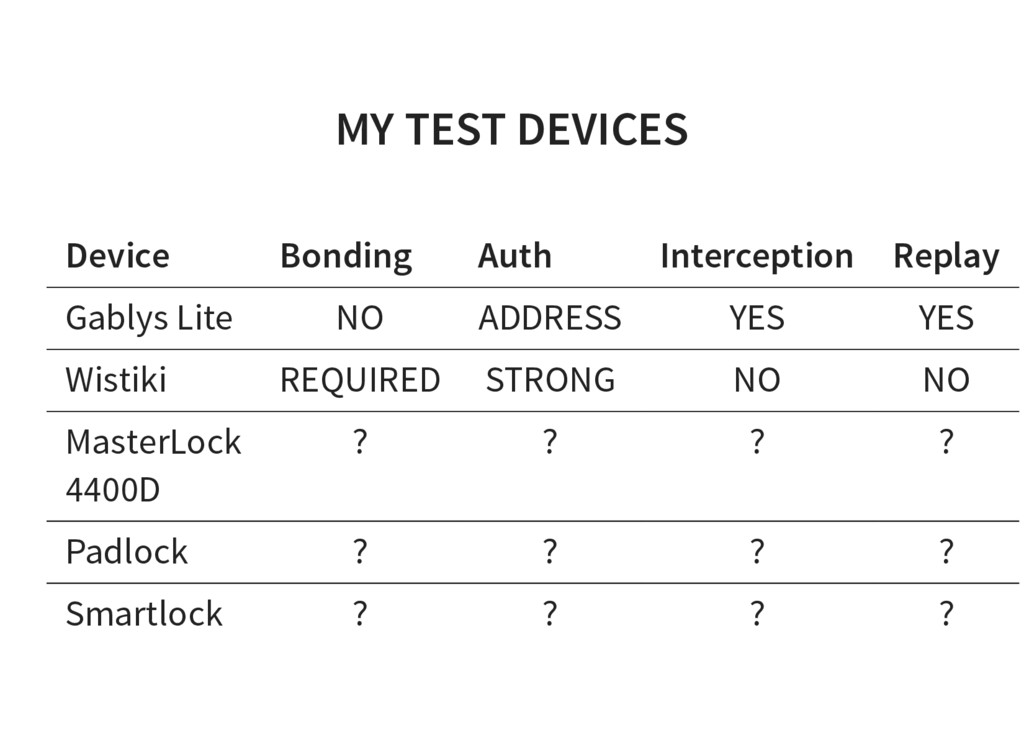
MY TEST DEVICES Device Bonding Auth Interception Replay Gablys Lite
? ? ? ? Wistiki ? ? ? ? MasterLock 4400D ? ? ? ? Padlock ? ? ? ? Smartlock ? ? ? ? -
GABLYS LITE Bonding supported, but not required No strong authentication
Anyone may make this tag beep Denial of service attack found through replay -
WISTIKI Bonding required Bonding provides strong authentication Tag is declared
lost when connection is lost -
MY TEST DEVICES Device Bonding Auth Interception Replay Gablys Lite
NO ADDRESS YES YES Wistiki REQUIRED STRONG NO NO MasterLock 4400D ? ? ? ? Padlock ? ? ? ? Smartlock ? ? ? ? -
MASTERLOCK 4400D Encrypted communications (AES-CCM) No bonding required Authentication through
challenge/response Long writes through characteristics Available a short amount of time -
PADLOCK Everything sent in plaintext Authentication based on BD address
No bonding required Stays active once a client connected -
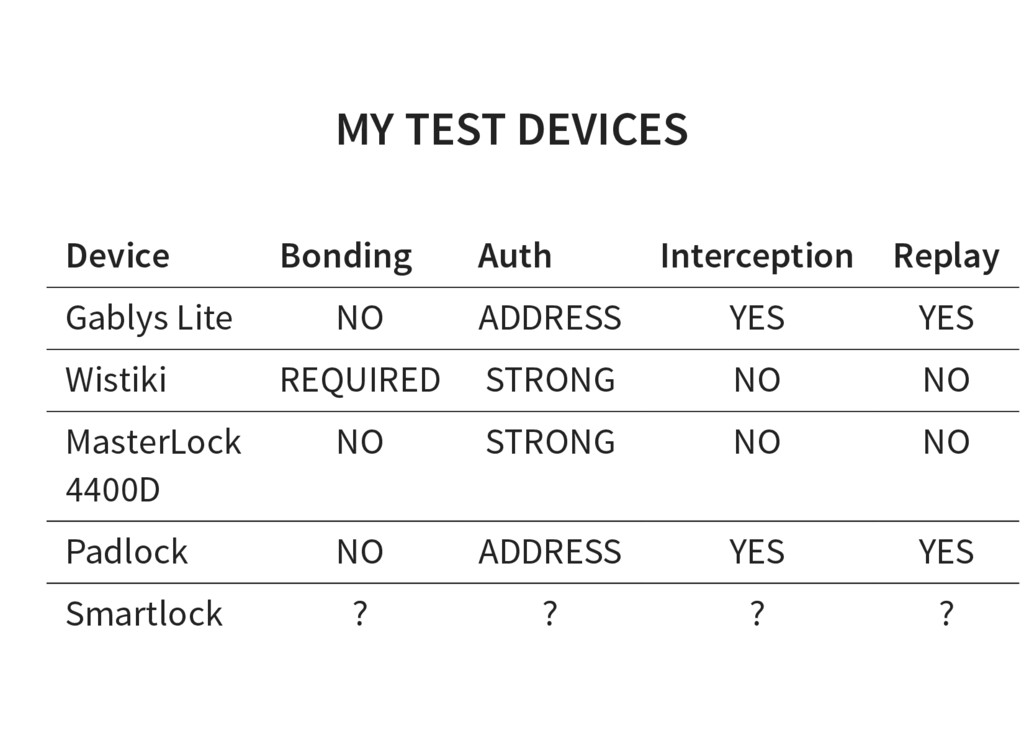
MY TEST DEVICES Device Bonding Auth Interception Replay Gablys Lite
NO ADDRESS YES YES Wistiki REQUIRED STRONG NO NO MasterLock 4400D NO STRONG NO NO Padlock NO ADDRESS YES YES Smartlock ? ? ? ? -
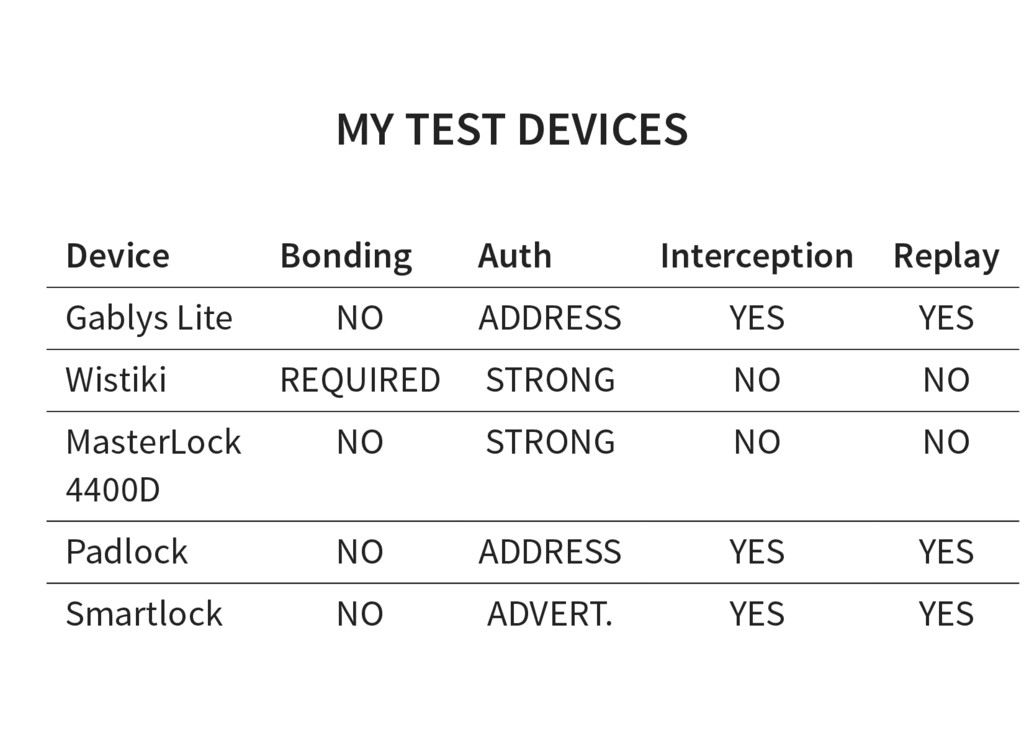
MY TEST DEVICES Device Bonding Auth Interception Replay Gablys Lite
NO ADDRESS YES YES Wistiki REQUIRED STRONG NO NO MasterLock 4400D NO STRONG NO NO Padlock NO ADDRESS YES YES Smartlock NO ADVERT. YES YES -
BTLEJUICE AS A SECURITY TOOL Useful to determine a device's
behavior Allows data sniffing and manipulation Allows replay attacks Supports bonding -
BTLEJUICE AS AN ATTACK TOOL Can bypass BD address authentication
Can be instrumented to automate attacks Requires generic hardware but at least two machines Known limitations due to Noble and Bleno limitations -
FUTURE WORK Improve BtleJuice's proxy reliability Solve the two-machine problem
Improve user interfaces and bindings Moar testing (need feedback !)