Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Authentication and Permissions with Django REST...
Search
Sponsored
·
Ship Features Fearlessly
Turn features on and off without deploys. Used by thousands of Ruby developers.
→
Ordoquy Xavier - Linovia
October 16, 2016
Programming
200
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Authentication and Permissions with Django REST framework
An overview of the authentication and permissions management with Django REST framework.
Ordoquy Xavier - Linovia
October 16, 2016
More Decks by Ordoquy Xavier - Linovia
See All by Ordoquy Xavier - Linovia
SQLAlchemy - un ami qui vous veut du bien
xordoquy
0
30
pycon.fr 2018 - Django REST framework workshop
xordoquy
0
360
mauvaises bonnes idées pour REST
xordoquy
1
420
Buildbot 0.9
xordoquy
0
110
Performances Django REST framework - DjangoCong 2016
xordoquy
0
130
Présentation de l'architecture REST - meetup Django Paris
xordoquy
0
110
Django REST framework workshop @Djangocon Europe 2015
xordoquy
0
130
Django REST framework - DjangoConG 2015
xordoquy
3
160
Django REST framework workshop - DjangoCong 2015
xordoquy
1
140
Other Decks in Programming
See All in Programming
當我們開始不讀 Code - AI Agent 時代,Code Review 與 Clean Code 還剩下什麼?
jame2408
1
210
外から家のPCの電源入れたい!をPHPで解決する
kawashimo0
1
130
Railsバージョンを4倍にした話
optim
0
350
すこし踏み込む CancellationToken
htkym
2
1.7k
HTML-in-Canvasで作る未来のWeb UI表現
clockmaker
5
5.1k
自サークルのIdPからログアウトできるようになるまで
taiseiue
1
140
re:Inventに行く前に知っておきたい現地参加のノウハウ
nokomoro3
0
430
機械に任せるテスト、人が見るテスト ⽣成AIで引き直した、運⽤保守フェーズの線引き
dske104
0
190
Compiling a real-world CLI tool to native with Static Hermes
tmikov2023
0
120
AI主導のプログラミング学習アプリを作ってみた
econanringo
0
180
ジョジョの世界をXRで再現する
mofurune
0
160
月間100万人のサービス刷新で、 技術選定をHonoに振り切った話
yutobara
8
6.6k
Featured
See All Featured
Art, The Web, and Tiny UX
lynnandtonic
304
22k
The Myth of the Modular Monolith - Day 2 Keynote - Rails World 2024
eileencodes
28
3.7k
Producing Creativity
orderedlist
PRO
348
41k
Collaborative Software Design: How to facilitate domain modelling decisions
baasie
1
340
Breaking role norms: Why Content Design is so much more than writing copy - Taylor Woolridge
uxyall
1
450
Everyday Curiosity
cassininazir
0
350
Pawsitive SEO: Lessons from My Dog (and Many Mistakes) on Thriving as a Consultant in the Age of AI
davidcarrasco
0
260
Side Projects
sachag
456
43k
Amusing Abliteration
ianozsvald
1
350
Ruling the World: When Life Gets Gamed
codingconduct
0
400
Making the Leap to Tech Lead
cromwellryan
135
10k
"I'm Feeling Lucky" - Building Great Search Experiences for Today's Users (#IAC19)
danielanewman
230
23k
Transcript
Django REST framework Authentification Permissions Xavier Ordoquy
Mainteneur Django REST framework Freelance irc: linovia twitter: linovia_net
Django
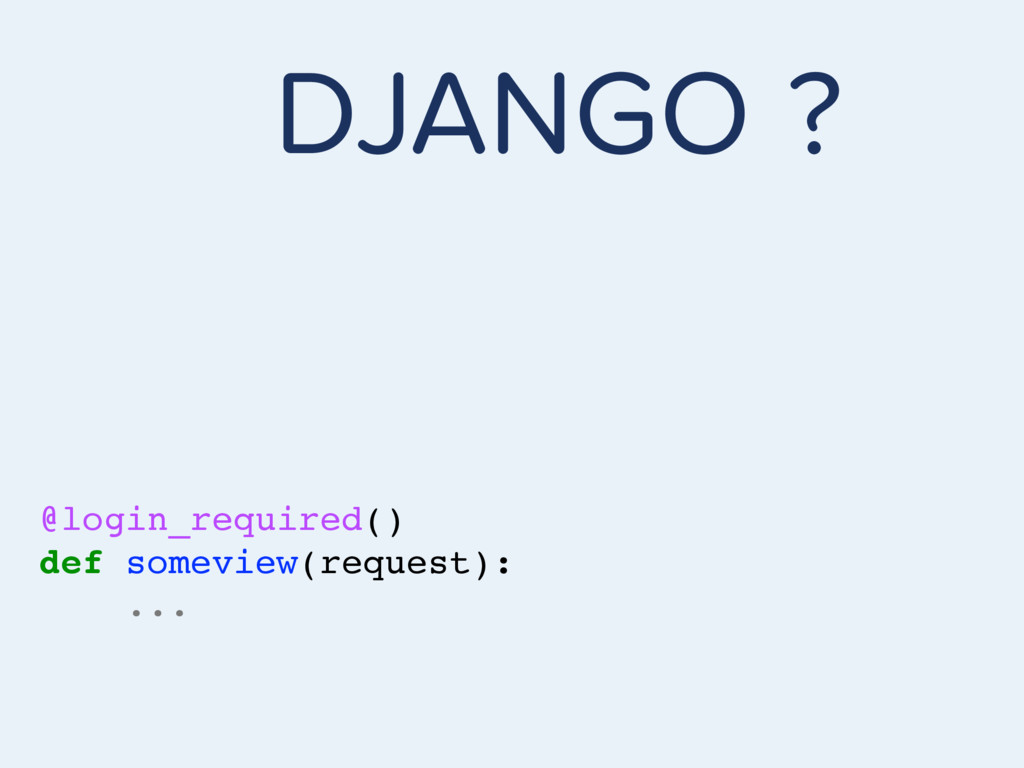
DJANGO @login_required() def someview(request): ... ?
DJANGO MIDDLEWARE = [ "django...SessionMiddleware", "django...AuthenticationMiddleware", ] @login_required() def someview(request):
... !
Auth =/= Perm
Django REST framework
CLASSE VUE class ExampleView(APIView): authentication_classes = [SessionAuthentication] permission_classes = [IsAuthenticated]
FONCTION @api_view(['GET']) @authentication_classes([SessionAuthentication]) @permission_classes([IsAuthenticated]) def example_view(request, format=None): return Response({})
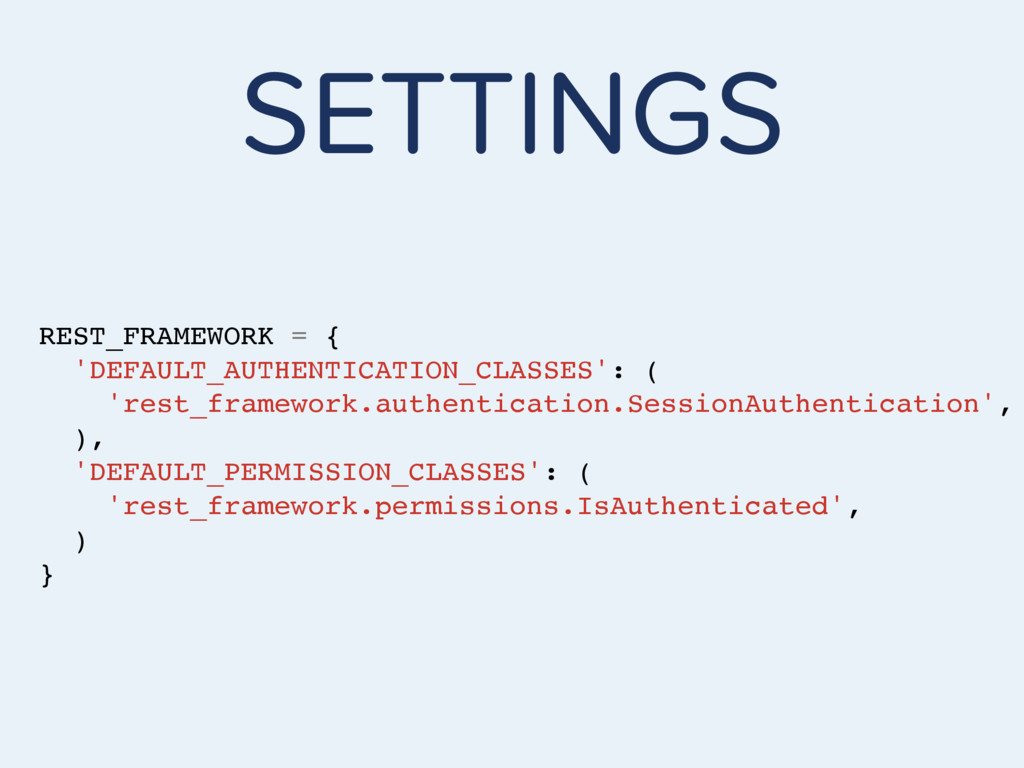
SETTINGS REST_FRAMEWORK = { 'DEFAULT_AUTHENTICATION_CLASSES': ( 'rest_framework.authentication.SessionAuthentication', ), 'DEFAULT_PERMISSION_CLASSES': (
'rest_framework.permissions.IsAuthenticated', ) }
vue >> settings
Pourquoi ne pas réutiliser Django ?
DJANGO MIDDLEWARE = [ "django...SessionMiddleware", "django...AuthenticationMiddleware", ] @login_required() def someview(request):
...
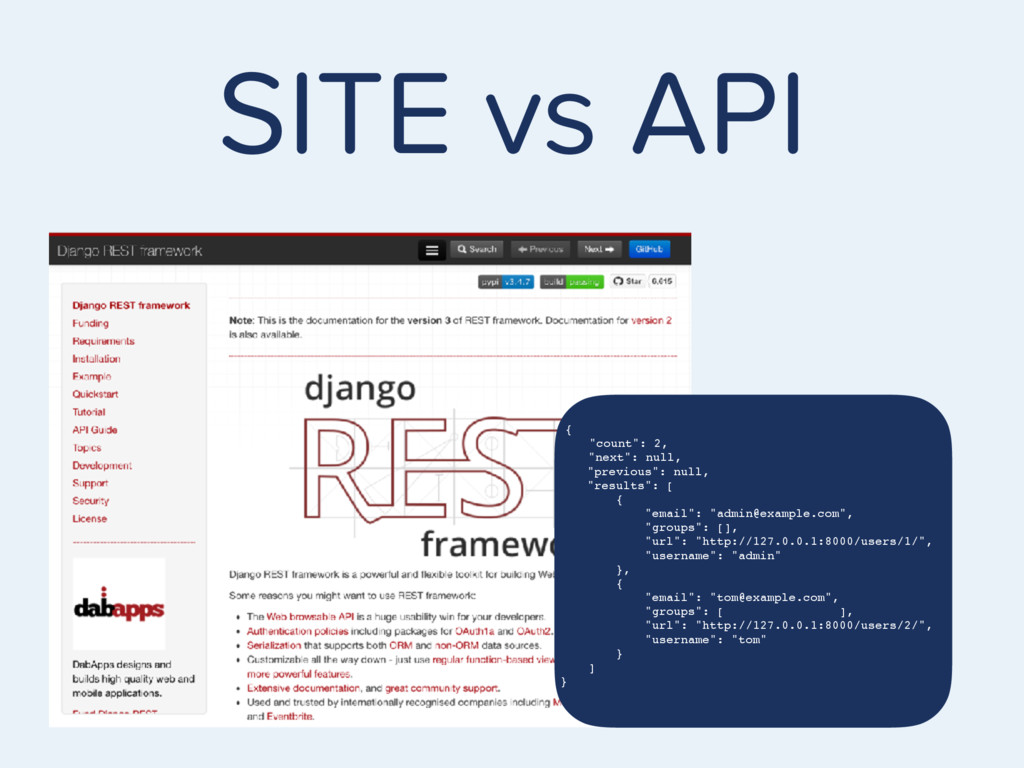
Problème: authentifications différentes
Problème: trop lié à l’utilisateur
Problème: Middleware pour tout le site
SITE vs API { "count": 2, "next": null, "previous": null,
"results": [ { "email": "
[email protected]
", "groups": [], "url": "http://127.0.0.1:8000/users/1/", "username": "admin" }, { "email": "
[email protected]
", "groups": [ ], "url": "http://127.0.0.1:8000/users/2/", "username": "tom" } ] }
Inclus: Basic
Inclus: Session
Inclus: Token
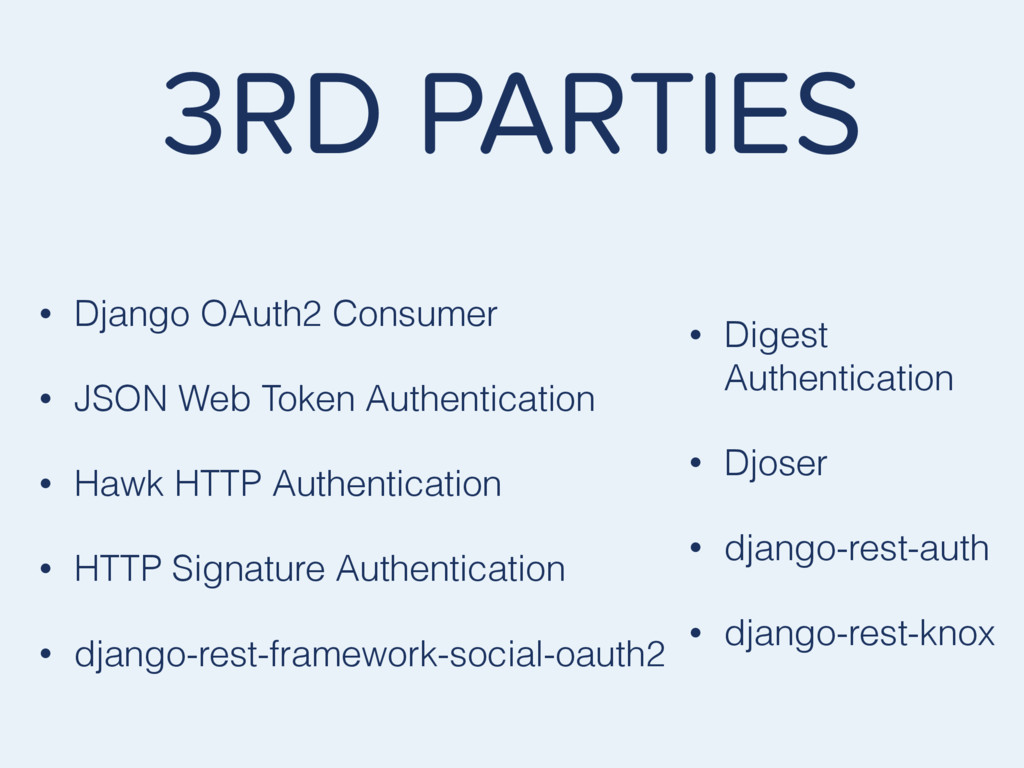
3RD PARTIES • Django OAuth2 Consumer • JSON Web Token
Authentication • Hawk HTTP Authentication • HTTP Signature Authentication • django-rest-framework-social-oauth2 • Digest Authentication • Djoser • django-rest-auth • django-rest-knox
401 / 403
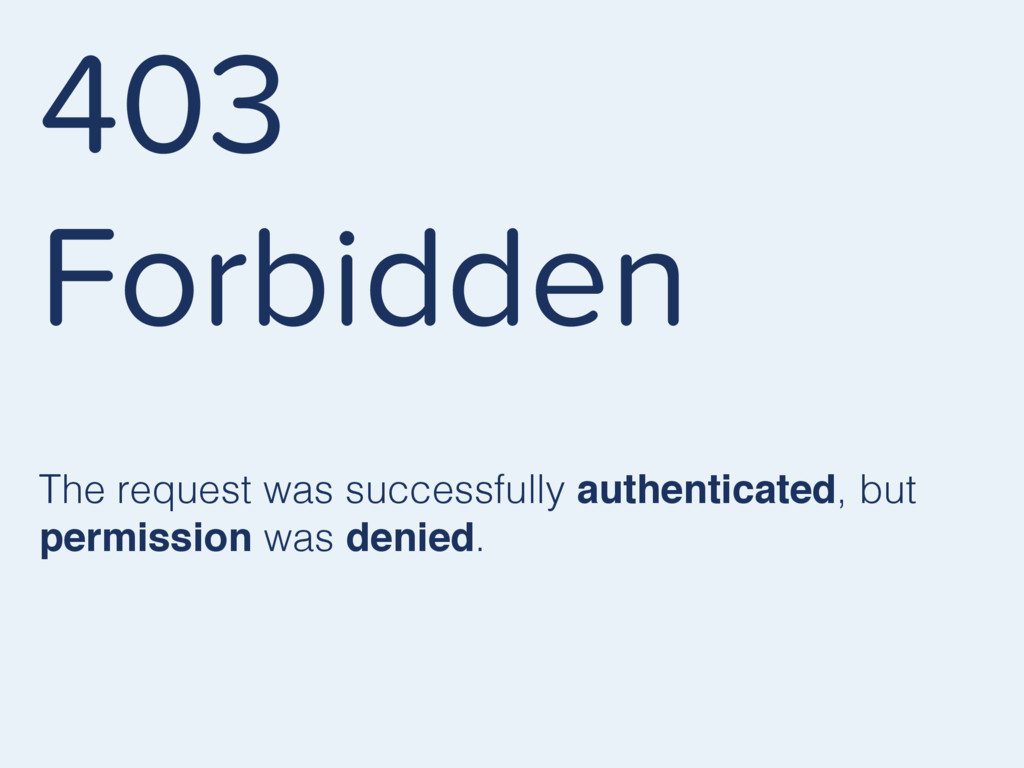
403 Forbidden The request was successfully authenticated, but permission was
denied.
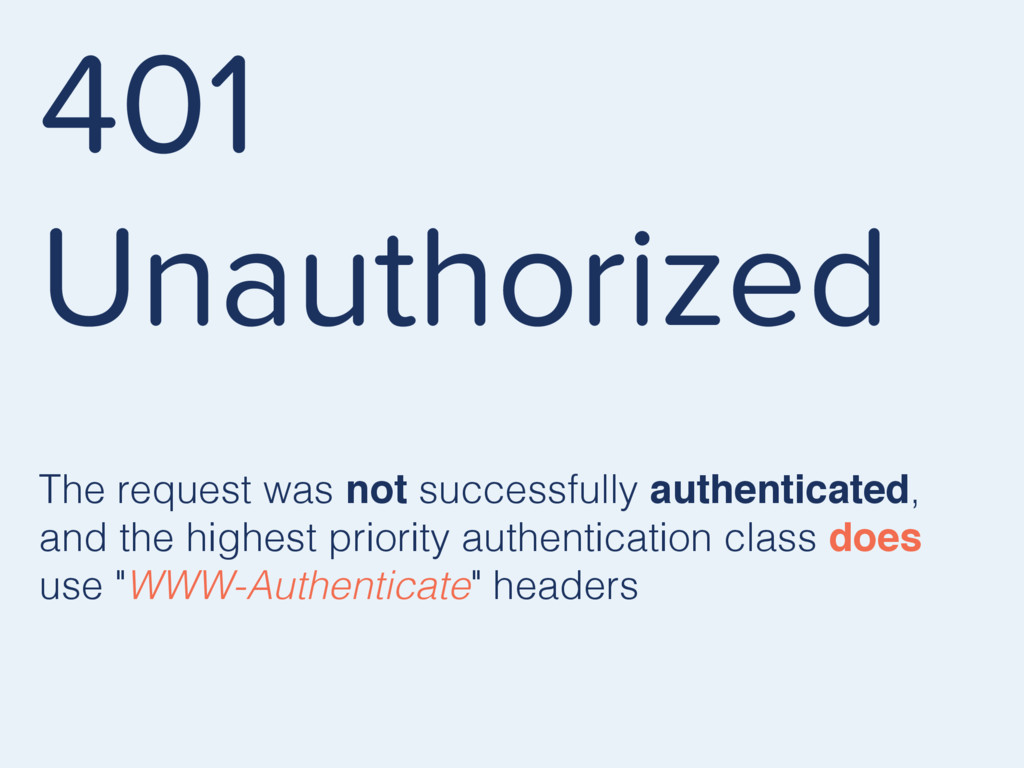
401 Unauthorized The request was not successfully authenticated, and the
highest priority authentication class does use "WWW-Authenticate" headers
403 Forbidden The request was not successfully authenticated, and the
highest priority authentication class does not use "WWW-Authenticate" headers. > SessionAuthentication <
pas de header pas de 401 401 Unauthorized
CSRF
CSRF @csrf_exempt
CSRF Géré par SessionAuth…
PERMISSIONS
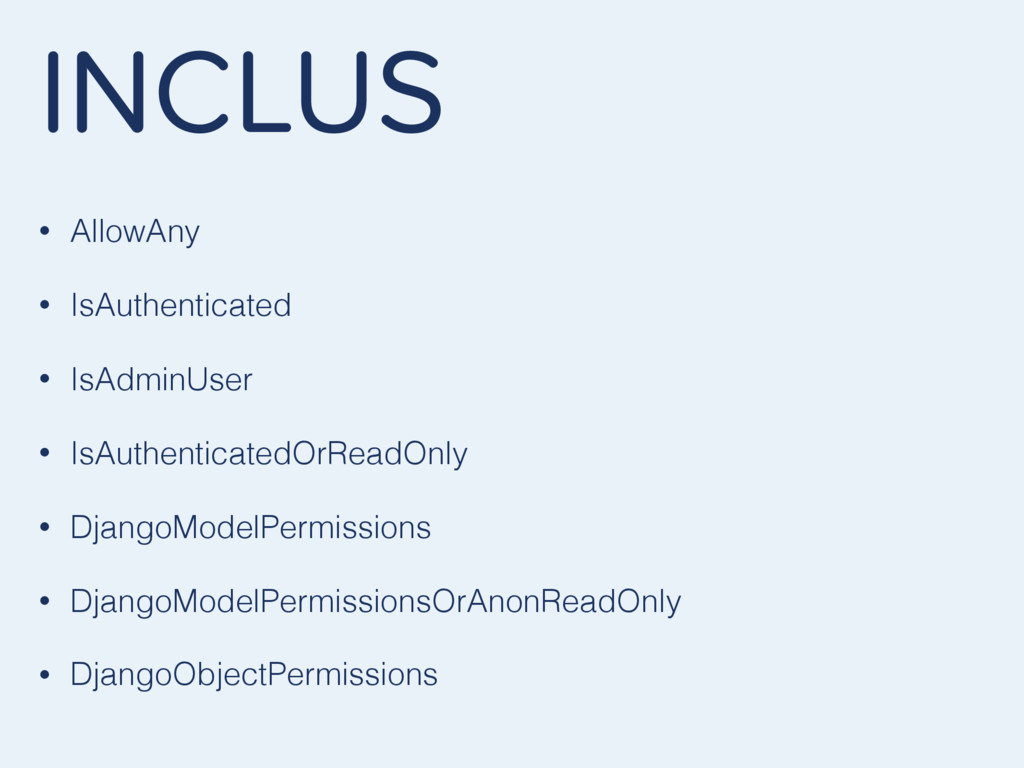
• AllowAny • IsAuthenticated • IsAdminUser • IsAuthenticatedOrReadOnly • DjangoModelPermissions
• DjangoModelPermissionsOrAnonReadOnly • DjangoObjectPermissions INCLUS
DjangoModel Permissions Permissions par Model de django.contrib.auth
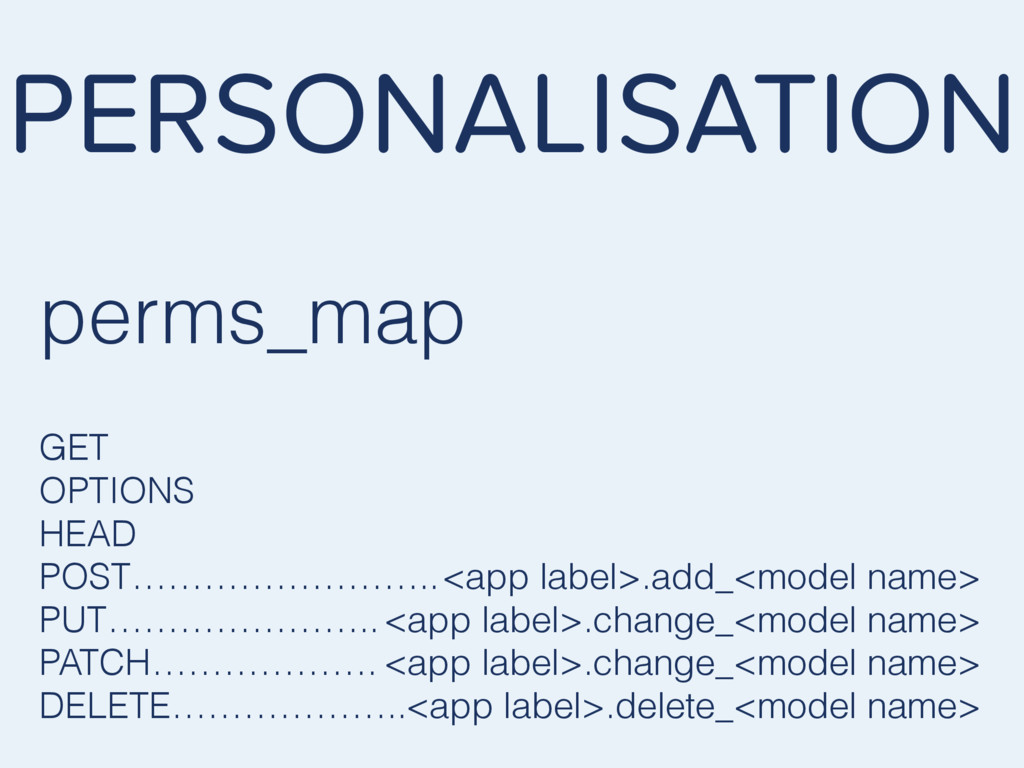
PERSONALISATION GET OPTIONS HEAD POST…………………….. PUT………………….. PATCH………………. DELETE……………….. <app label>.add_<model
name> <app label>.change_<model name> <app label>.change_<model name> <app label>.delete_<model name> perms_map
DjangoObject Permissions Permissions par objet de django.contrib.auth (django-guardian ou autre)
PERMISSIONS PAR OBJET SUR LISTE ?
class CustomObjectPermissions(DjangoObjectPermissions): perms_map = { 'GET': ['%(app_label)s.view_%(model_name)s'], 'OPTIONS': ['%(app_label)s.view_%(model_name)s'], 'HEAD':
['%(app_label)s.view_%(model_name)s'], 'POST': ['%(app_label)s.add_%(model_name)s'], 'PUT': ['%(app_label)s.change_%(model_name)s'], 'PATCH': ['%(app_label)s.change_%(model_name)s'], 'DELETE': ['%(app_label)s.delete_%(model_name)s'], } class EventViewSet(viewsets.ModelViewSet): queryset = Event.objects.all() serializer_class = EventSerializer filter_backends = [filters.DjangoObjectPermissionsFilter] permission_classes = [CustomObjectPermissions]
WTF ?!? mes permissions sont appelées 6 x ?
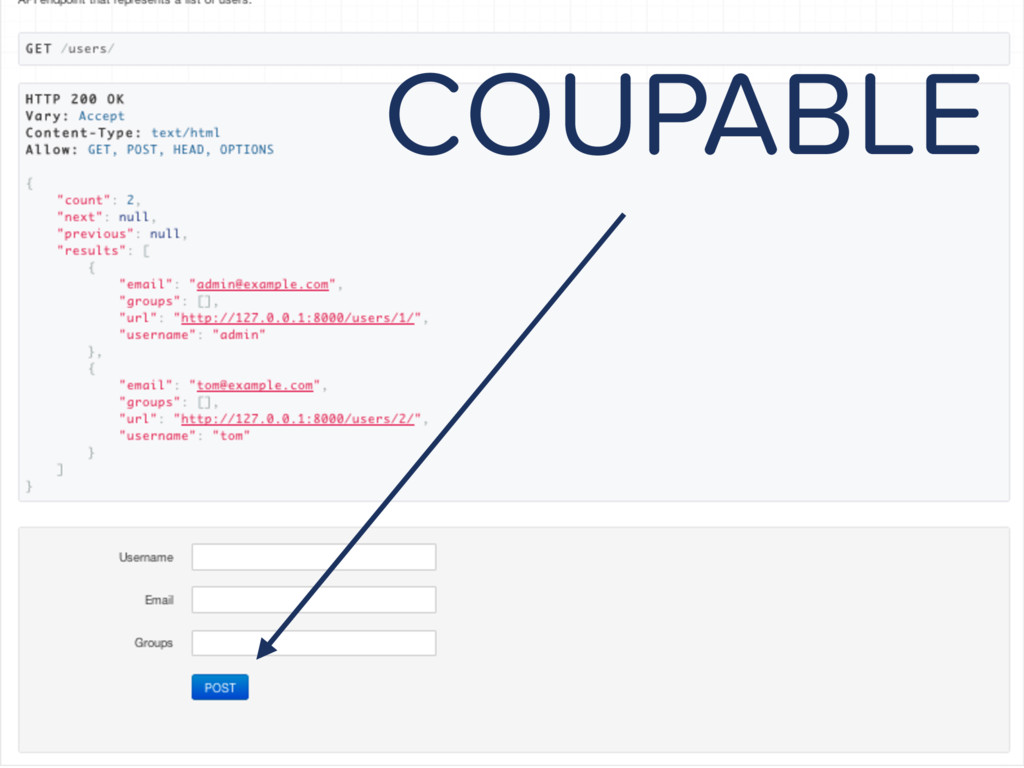
COUPABLE
Pas de permissions sur mon get_object !!
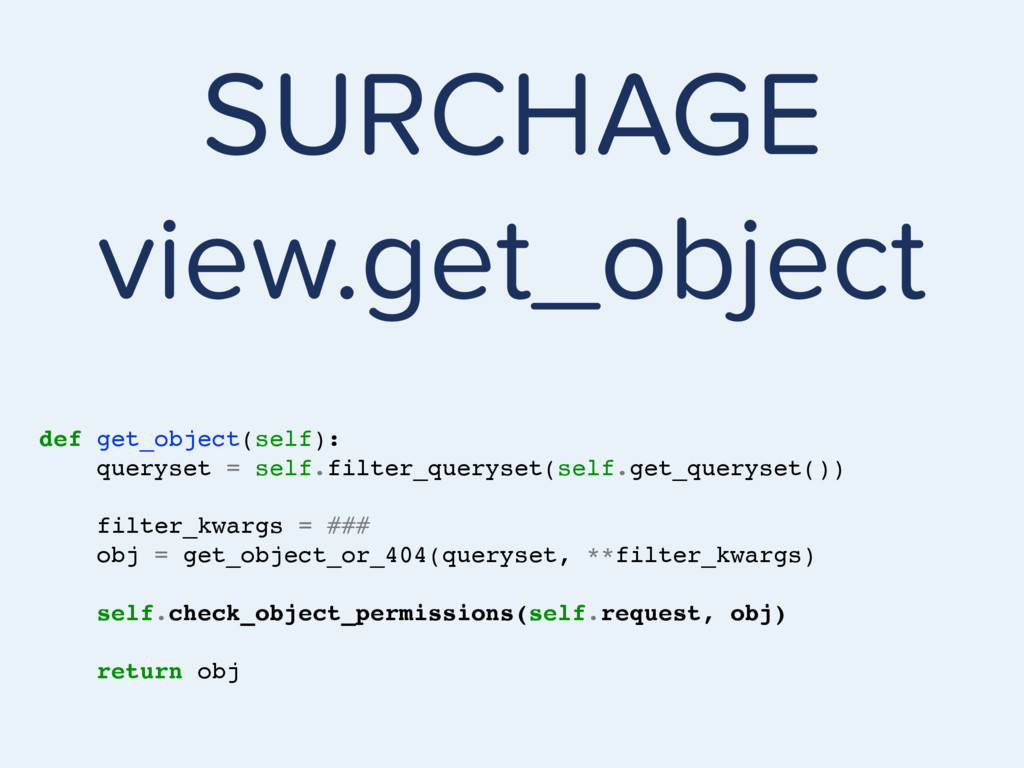
SURCHAGE view.get_object def get_object(self): queryset = self.filter_queryset(self.get_queryset()) filter_kwargs = ###
obj = get_object_or_404(queryset, **filter_kwargs) self.check_object_permissions(self.request, obj) return obj
CACHE GLOBAL (MIDDLEWARE) Pas de gestion de permissions
Permissions complexes ?
Et si j’avais besoin de lire la requête ?
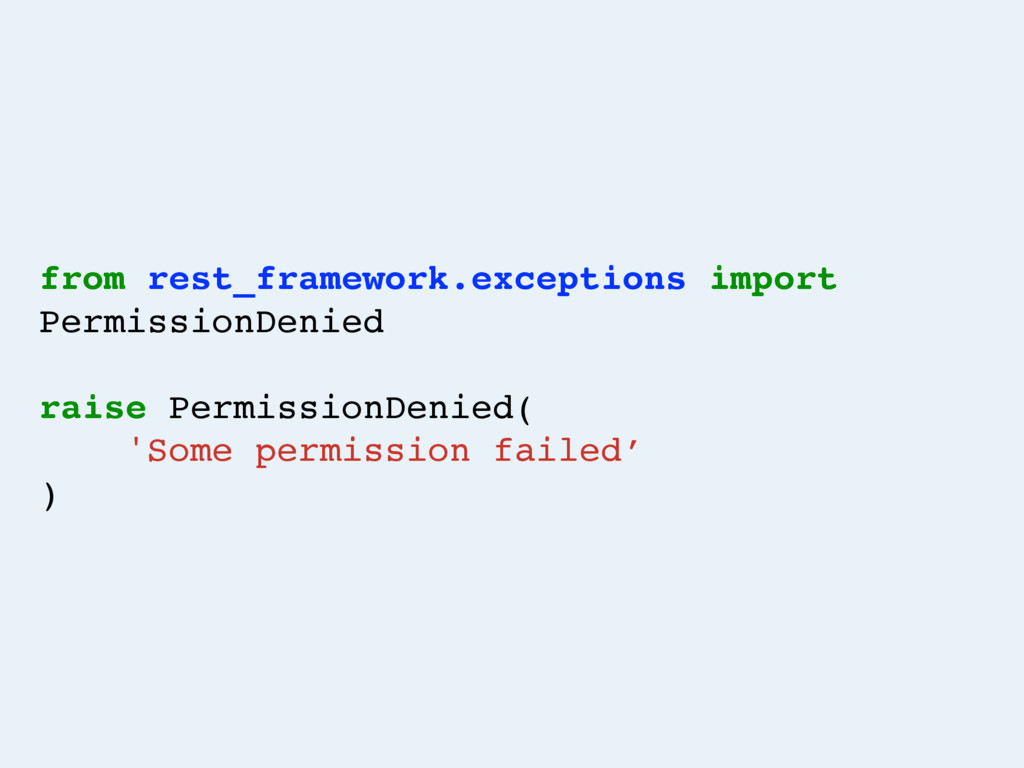
from rest_framework.exceptions import PermissionDenied raise PermissionDenied( 'Some permission failed’ )
Ecrire son auth
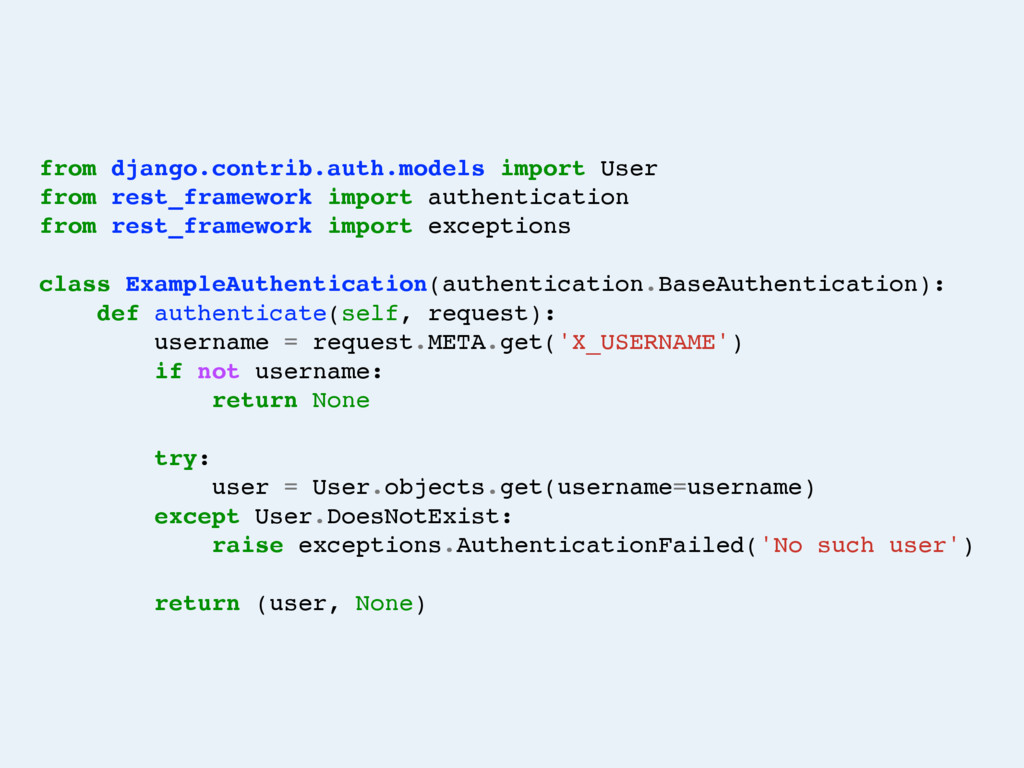
from django.contrib.auth.models import User from rest_framework import authentication from rest_framework
import exceptions class ExampleAuthentication(authentication.BaseAuthentication): def authenticate(self, request): username = request.META.get('X_USERNAME') if not username: return None try: user = User.objects.get(username=username) except User.DoesNotExist: raise exceptions.AuthenticationFailed('No such user') return (user, None)
Ecrire ses perms
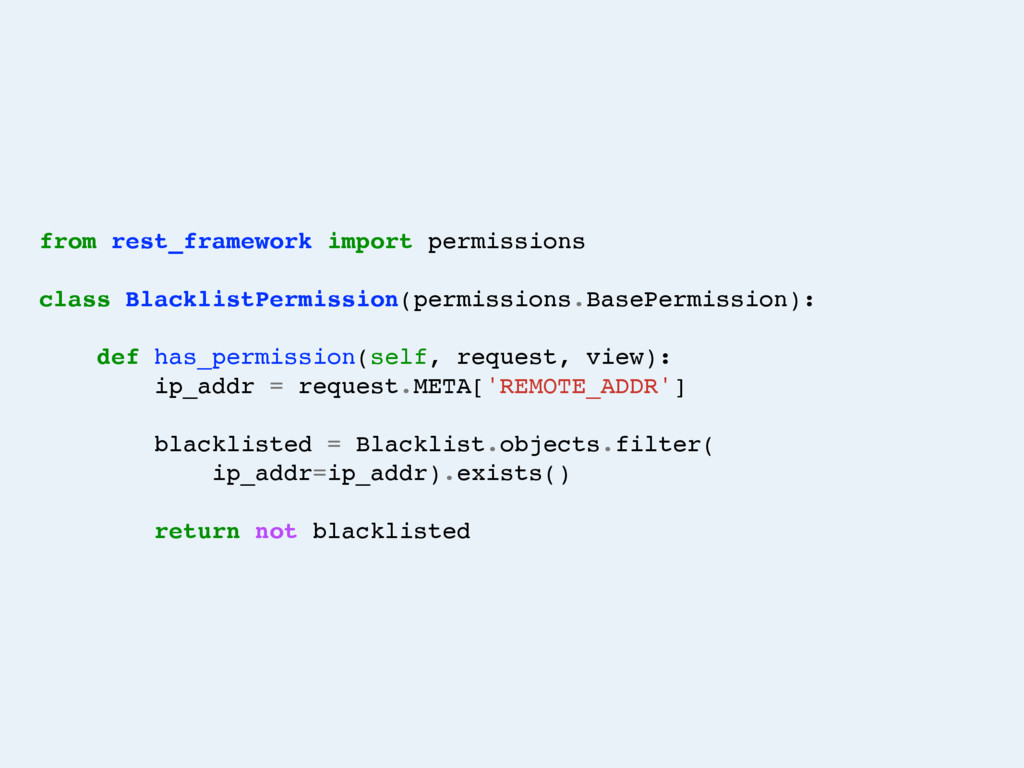
from rest_framework import permissions class BlacklistPermission(permissions.BasePermission): def has_permission(self, request, view):
ip_addr = request.META['REMOTE_ADDR'] blacklisted = Blacklist.objects.filter( ip_addr=ip_addr).exists() return not blacklisted
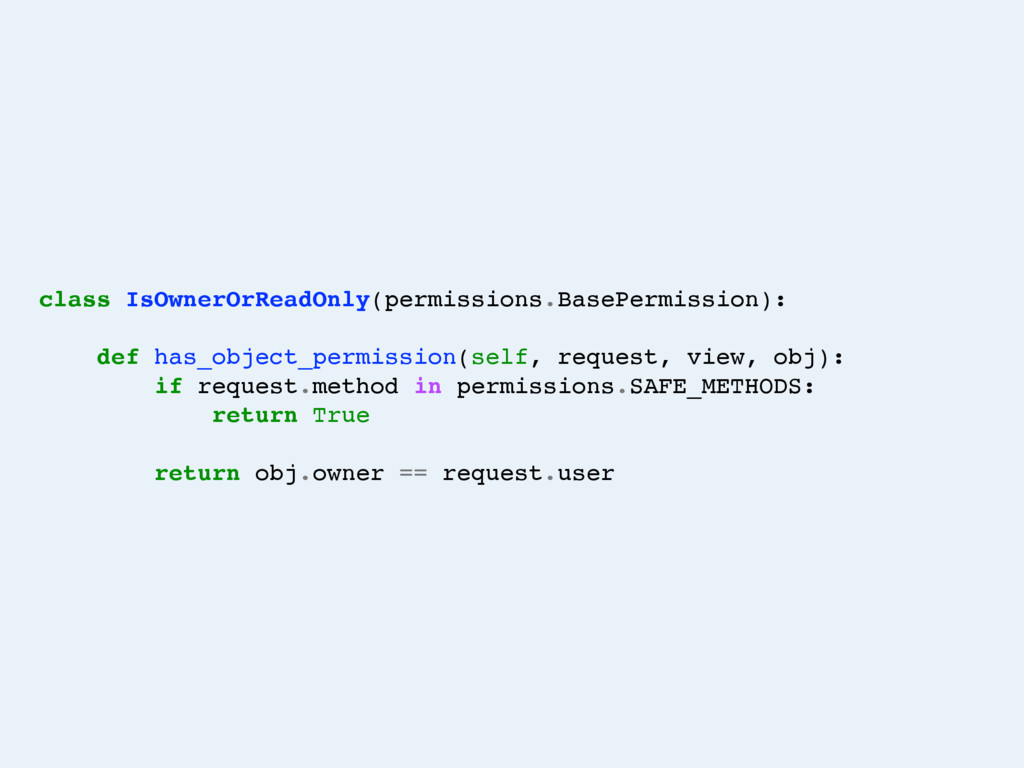
class IsOwnerOrReadOnly(permissions.BasePermission): def has_object_permission(self, request, view, obj): if request.method in
permissions.SAFE_METHODS: return True return obj.owner == request.user
One more thing
Pérennité http://www.django-rest- framework.org/topics/funding/
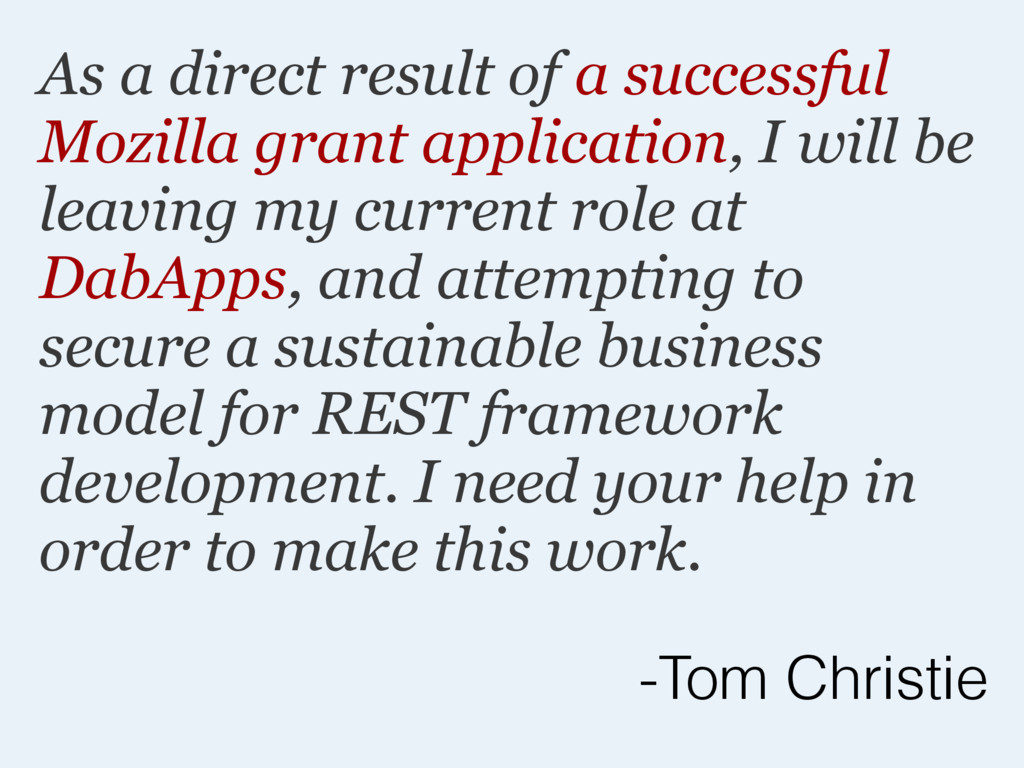
As a direct result of a successful Mozilla grant application,
I will be leaving my current role at DabApps, and attempting to secure a sustainable business model for REST framework development. I need your help in order to make this work. -Tom Christie
MERCI @linovia_net


 xordoquy
 jame2408
 kawashimo0
 optim
 htkym
 clockmaker
 taiseiue
 nokomoro3
 dske104
 tmikov2023
 econanringo
 mofurune
 yutobara
 lynnandtonic
 eileencodes
 orderedlist
 baasie
 uxyall
 cassininazir
 davidcarrasco
 sachag
 ianozsvald
 codingconduct
 cromwellryan
 danielanewman