Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Introduction to Fuzzing with AFL
Search
Sponsored
·
Ship Features Fearlessly
Turn features on and off without deploys. Used by thousands of Ruby developers.
→
Ayush Priya
November 16, 2021
Technology
81
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Introduction to Fuzzing with AFL
This talk is an introduction to using AFL or American Fuzzy Lop to fuzz binaries.
Ayush Priya
November 16, 2021
More Decks by Ayush Priya
See All by Ayush Priya
Scrubbing PII from Logs in LogStash
ayushpriya10
0
900
Introduction to Deserialization Attacks
ayushpriya10
2
710
Web Assembly for Hackers
ayushpriya10
0
110
Other Decks in Technology
See All in Technology
Deep Data Security 機能解説
oracle4engineer
PRO
3
970
SLOを阻む不安
sraku2159
0
160
LLMの知識とAIエージェント
happysamurai294
0
130
「作れる」と「リリースできる」の間にあったもの── PdMを外して見えた、PdMがやるべき仕事/Buildable ≠ Shippable: What Removing the PM Taught Me About the PM’s Job
yappli_developers
0
390
ドメインエキスパートは いかにして AI を使って プロダクト開発をするか
tatsuyashiraishi
1
240
あなたのDartコードは丸見えかもしれない ~reFlutterで暴くFlutterアプリの中身と多層防御~
zozotech
PRO
0
710
AX時代の自治体支援リソース再配分と役割分担の再構成:戦略とロードマップ(概要)
sishi2026
0
140
(swiftc) NonCopyableとライフタイム修飾子
teamhimeh
0
160
[General] 개발자로 해외 기업에서 일하기
skydoves
1
130
Claude Codeから見る、エンジニアの世界の変容とその先
oikon48
7
4.9k
基本から分かる!AWSセキュリティ運用の考え方と任せ方
cmusudakeisuke
1
270
新米を「売り越さない」、Aurora DSQLで作る在庫ゼロ死守の限定ドロップEC
yama3133
0
110
Featured
See All Featured
Being A Developer After 40
akosma
PRO
92
590k
Designing Powerful Visuals for Engaging Learning
tmiket
1
620
How to audit for AI Accessibility on your Front & Back End
davetheseo
0
620
Discover your Explorer Soul
emna__ayadi
2
1.3k
Max Prin - Stacking Signals: How International SEO Comes Together (And Falls Apart)
techseoconnect
PRO
0
510
Design of three-dimensional binary manipulators for pick-and-place task avoiding obstacles (IECON2024)
konakalab
0
640
Mind Mapping
helmedeiros
1
420
Redefining SEO in the New Era of Traffic Generation
szymonslowik
1
500
Unlocking the hidden potential of vector embeddings in international SEO
frankvandijk
0
1k
How Fast Is Fast Enough? [PerfNow 2025]
tammyeverts
3
960
[RailsConf 2023] Rails as a piece of cake
palkan
59
7.1k
Building Applications with DynamoDB
mza
96
7.3k
Transcript
Introduction to fuzzing with AFL
Ayush Priya VIT, Vellore @ayushpriya10 https://ayushpriya.com https://www.linkedin.com/in/ayushpriya10
What am I learning? • What is fuzzing and fuzzers?
• What is AFL? • How to use AFL?
Why am I learning this? • Discover undiscovered bugs •
Build a robust approach to development • (Maybe make some money)
What is Fuzzing? • A form of testing • Random
invalid input • Behaviour analysis
"You can find bugs in your sleep." - Craig Young
Why fuzz at all? • Unique test cases • Eliminates
methodology bias • Metrics - Code Coverage, Path Coverage
Types of fuzzers • Mutational • Grammar • Feedback-based
Introduction to AFL • Open-source • Smart fuzzer: PoC -
“Hello JPG”
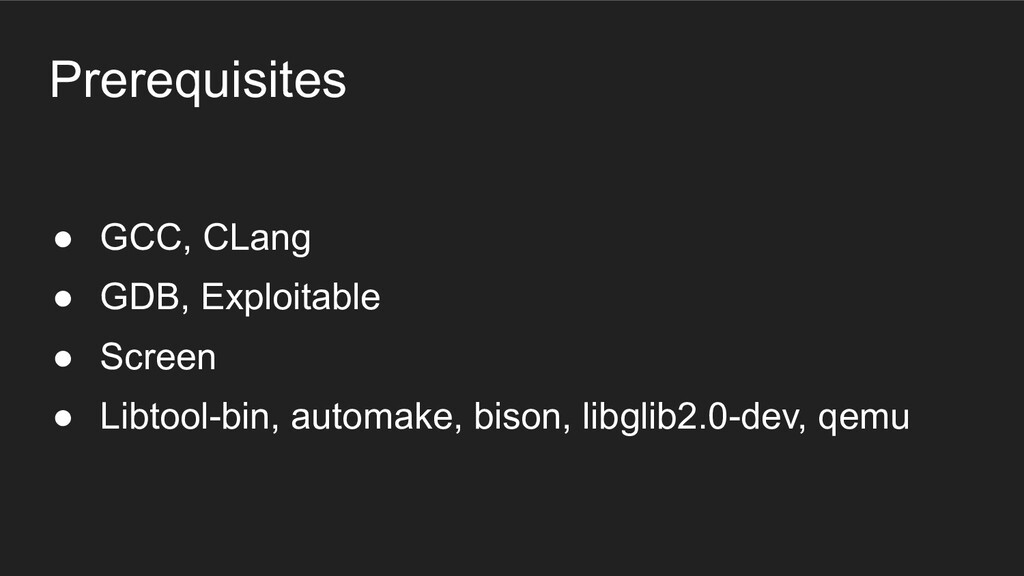
Prerequisites • GCC, CLang • GDB, Exploitable • Screen •
Libtool-bin, automake, bison, libglib2.0-dev, qemu
Installation • Install AFL • Enable LLVM mode • Enable
QEMU mode
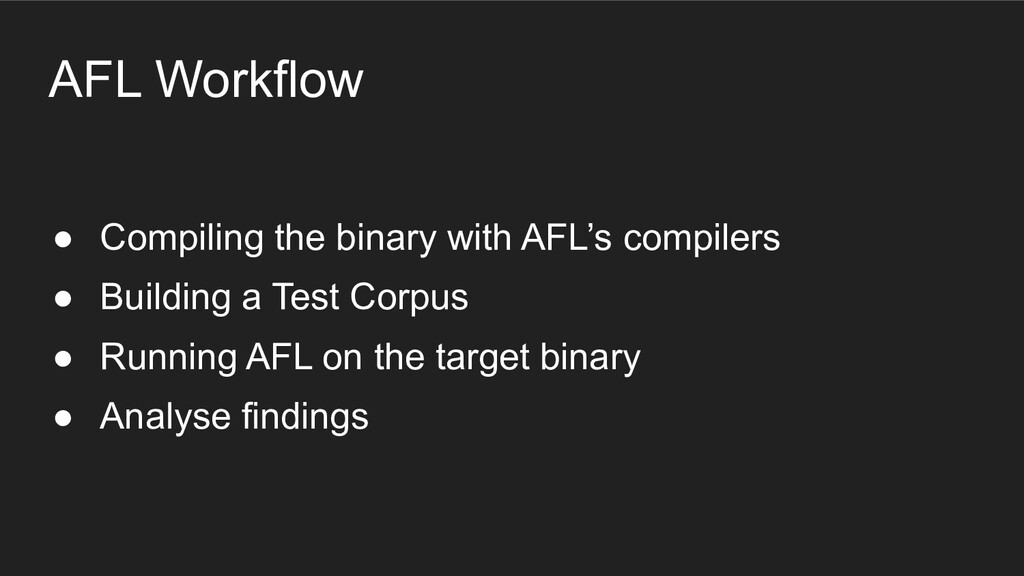
AFL Workflow • Compiling the binary with AFL’s compilers •
Building a Test Corpus • Running AFL on the target binary • Analyse findings
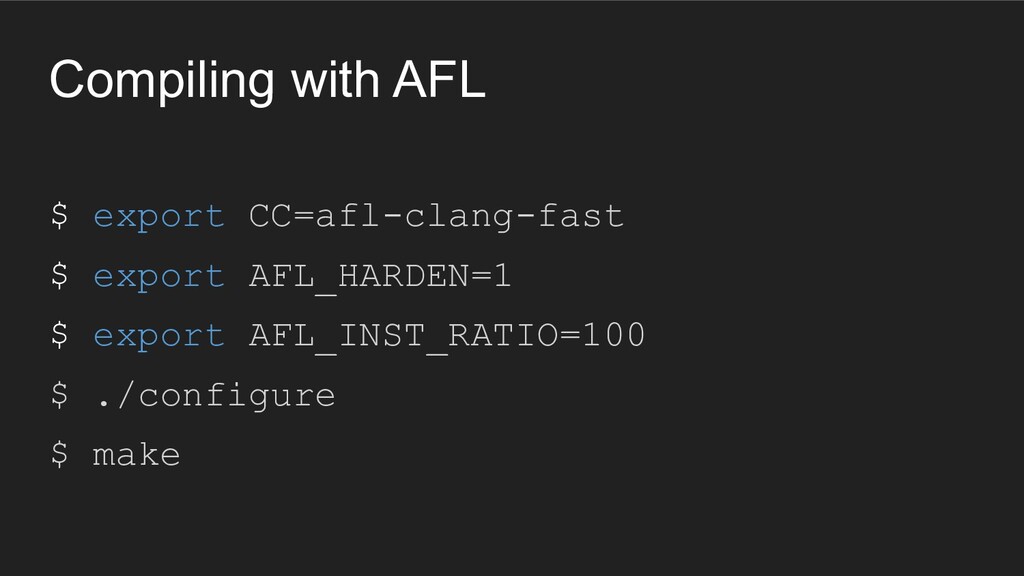
Compiling with AFL $ export CC=afl-clang-fast $ export AFL_HARDEN=1 $
export AFL_INST_RATIO=100 $ ./configure $ make
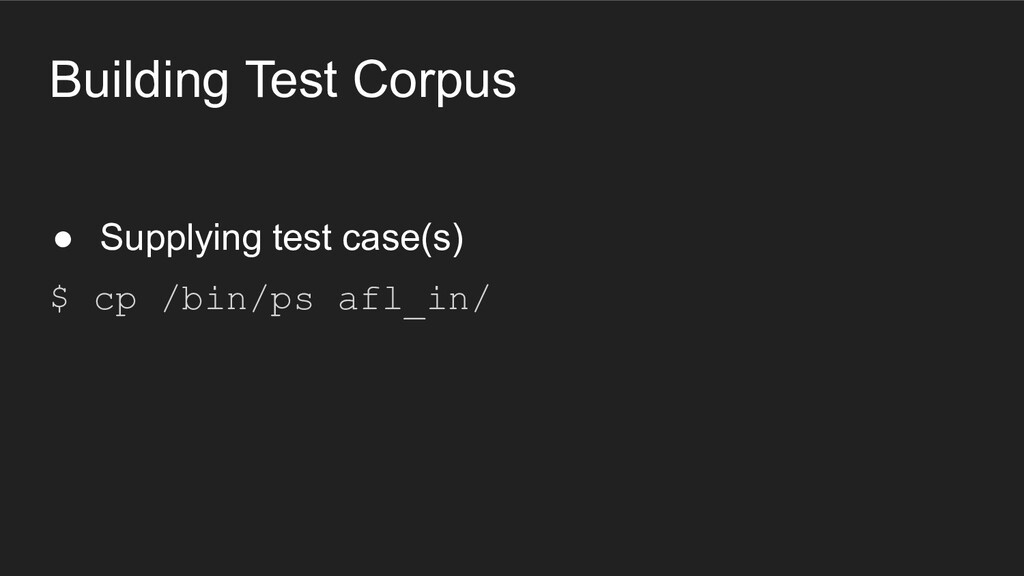
Building Test Corpus • Supplying test case(s) $ cp /bin/ps
afl_in/
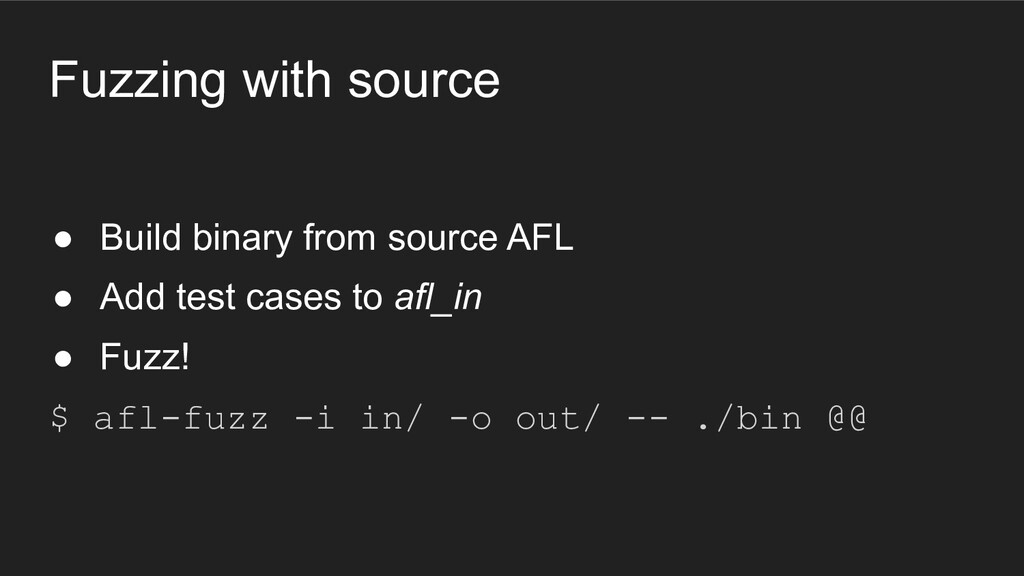
Fuzzing with source • Build binary from source AFL •
Add test cases to afl_in • Fuzz! $ afl-fuzz -i in/ -o out/ -- ./bin @@
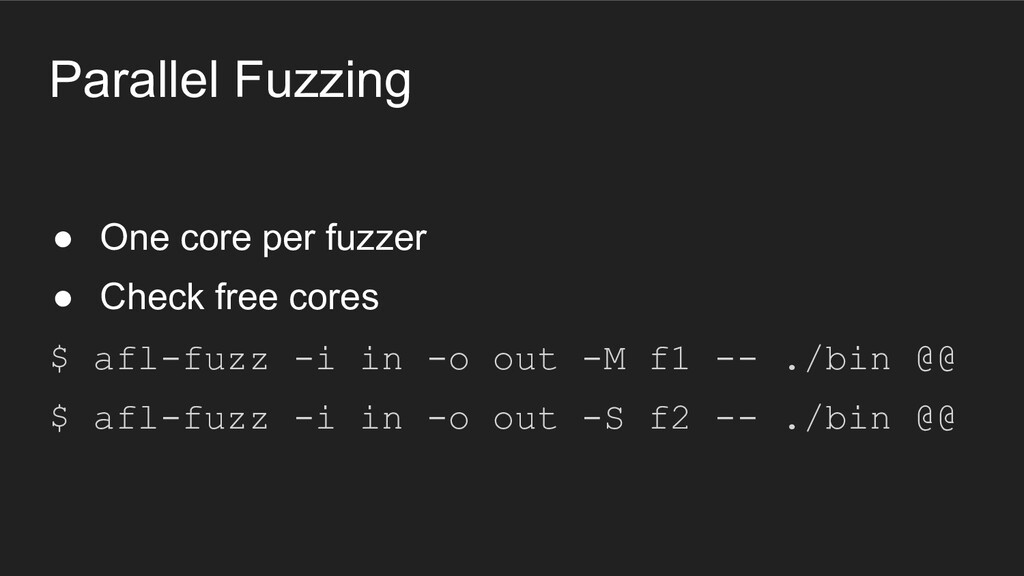
Parallel Fuzzing • One core per fuzzer • Check free
cores $ afl-fuzz -i in -o out -M f1 -- ./bin @@ $ afl-fuzz -i in -o out -S f2 -- ./bin @@
Output Structure • One folder per fuzzer • /crashes, /hangs,
/queue
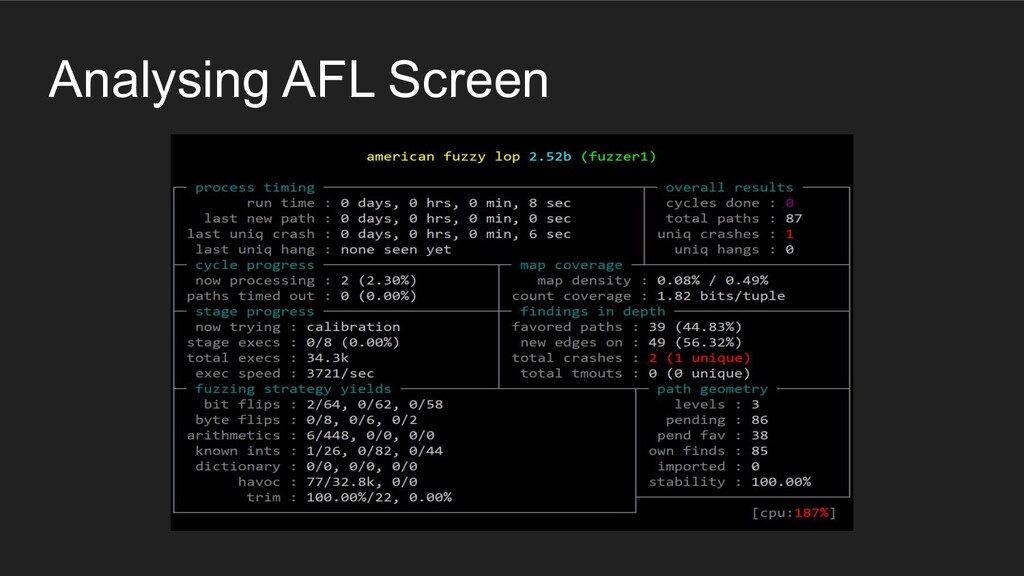
Analysing AFL Screen
Hands-on • Clone fuzzgoat • Compile with AFL • Fuzz
in parallel • Check status
GDB and Exploitable • Open binary with GDB • Choose
a crash case • Run test case • Classify with Exploitable
Optimising Fuzzing • Execution Speed, Fail Fast • Isolate test
code • Minimise test cases • Minimise test files
Fuzzing a binary without source • Linux binaries • AFL’s
QEMU Mode
Limitations of AFL • Supports file/STDIN input • Supports selective
binaries • Supports selective OSs
Thanks!


 ayushpriya10
 oracle4engineer
 sraku2159
 happysamurai294
 yappli_developers
 tatsuyashiraishi
 zozotech
 sishi2026
 teamhimeh
 skydoves
 oikon48
 cmusudakeisuke
 yama3133
 akosma
 tmiket
 davetheseo
 emna__ayadi
 techseoconnect
 konakalab
 helmedeiros
 szymonslowik
 frankvandijk
 tammyeverts
 palkan
 mza