Upgrade to Pro — share decks privately, control downloads, hide ads and more …

Web Assembly for Hackers

Ayush Priya
November 16, 2021

Web Assembly for Hackers

This talk provides a primer on Web Assembly and some basic scenarios on how to exploit web assembly in applications.

Ayush Priya

November 16, 2021

Transcript

36 slides
  1. A Hacker’s Introduction to Web Assembly A brief overview of

    Web Assembly and its impact on security.
  2. Overview • Why this session? • What is WASM and

    why it exists? • Can python run on browsers? • Similar Attempts • WASM vs. JS • Is WASM secure? • WASM for exploitation • Exploiting WASM
  3. Why this session? To answer: • What is Web Assembly?

    • Why should you care? • Is Web Assembly secure? • How to use Web Assembly for exploitation? • How to exploit Web Assembly?
  4. Why does WASM exist? • Performance Upgrade ◦ Load Time

    ◦ Run-time • Reusability • Portability
  5. Is WASM the first of its kind? • Native Client

    (NaCl) • Portable Native Client (PNaCl) • asm.js
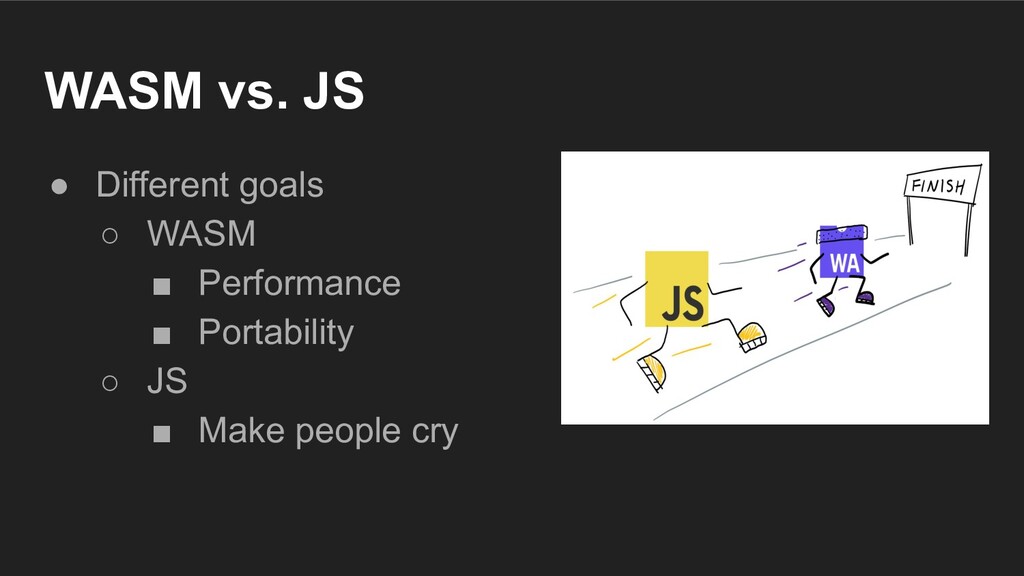
  6. WASM vs. JS • Different goals ◦ WASM ▪ Performance

    ▪ Portability ◦ JS ▪ Make people cry
  7. But why should I care? • Wide-spread support • New

    vulnerabilities • New ways to hack
  8. Is WASM secure? • Control Flow Integrity • Signature Checks

    • Data Execution Prevention Security Web Assembly
  9. How to write Web Assembly? • Write C/C++ Code •

    Compile to target • Load with JS
  10. How do I exploit Web Assembly? • Formatted Strings •

    Buffer Overflows • Indirect Function Calls • Type Confusion Is this hacking?
  11. Conclusions • What is Web Assembly? ◦ Low-Level Portable Binary

    • Why should you care? ◦ Upcoming technology
  12. Conclusions • Is Web Assembly secure? ◦ From primitive cases

    • How to use Web Assembly for exploitation? ◦ Control Take-over, Obfuscation • How to exploit Web Assembly? ◦ BoF, Format Strings, Indirect Function Calls, etc.

More Decks by Ayush Priya

Other Decks in Technology