Share
Embed

Transcript
42 slides
-
/whoami Alexander Antukh Security Consultant Offensive Security Certified
Expert Interests: kittens and stuff -
/whoami Yury Chemerkin Experienced in : Mobile Security
and MDM Cyber Security & Cloud Security Compliance & Transparency and Security Writing -
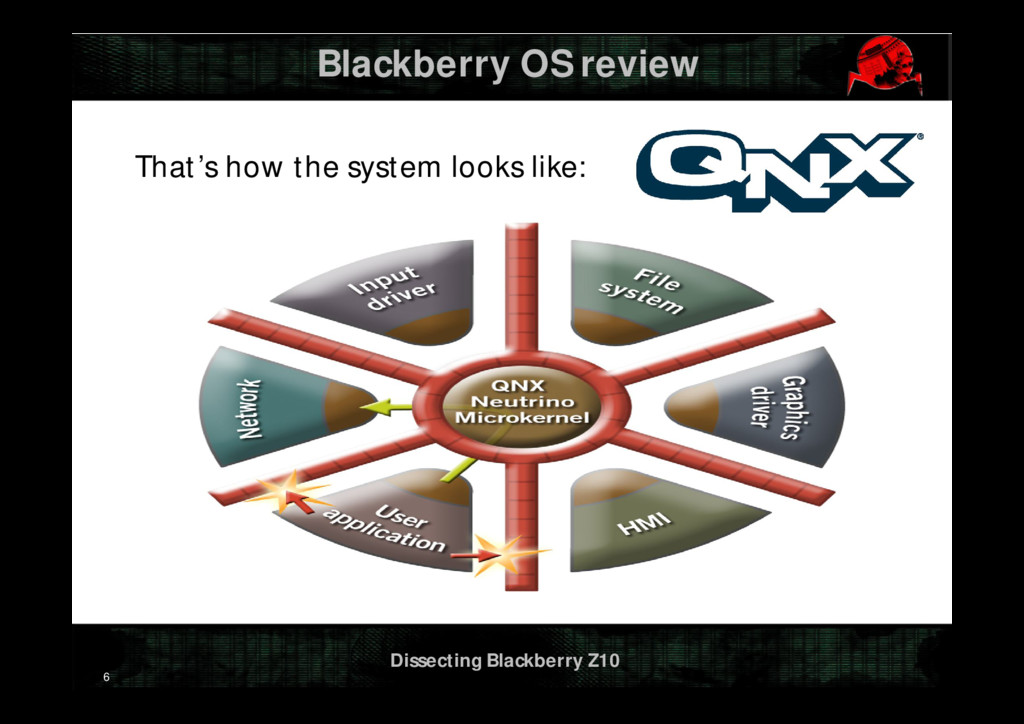
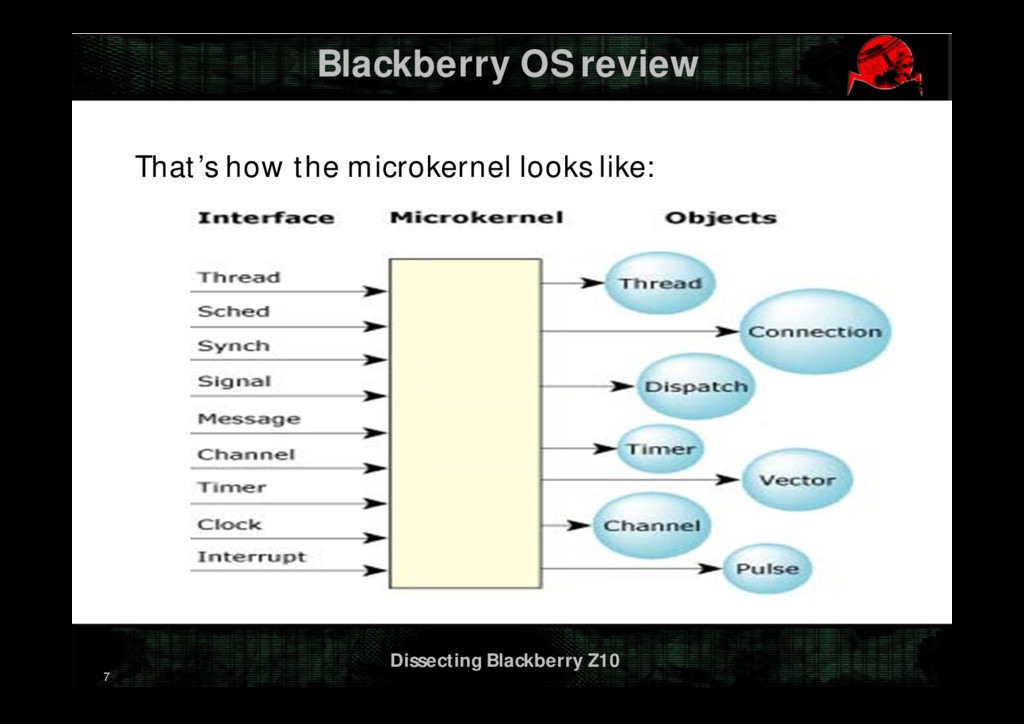
Dissecting Blackberry Z10 Agenda Blackberry OS review Shell Access The
Approaches Firmware from the inside Playing with the browser Security on the application level Funny with APIs MDM capabilities Efficiency of security features Future research 4 -
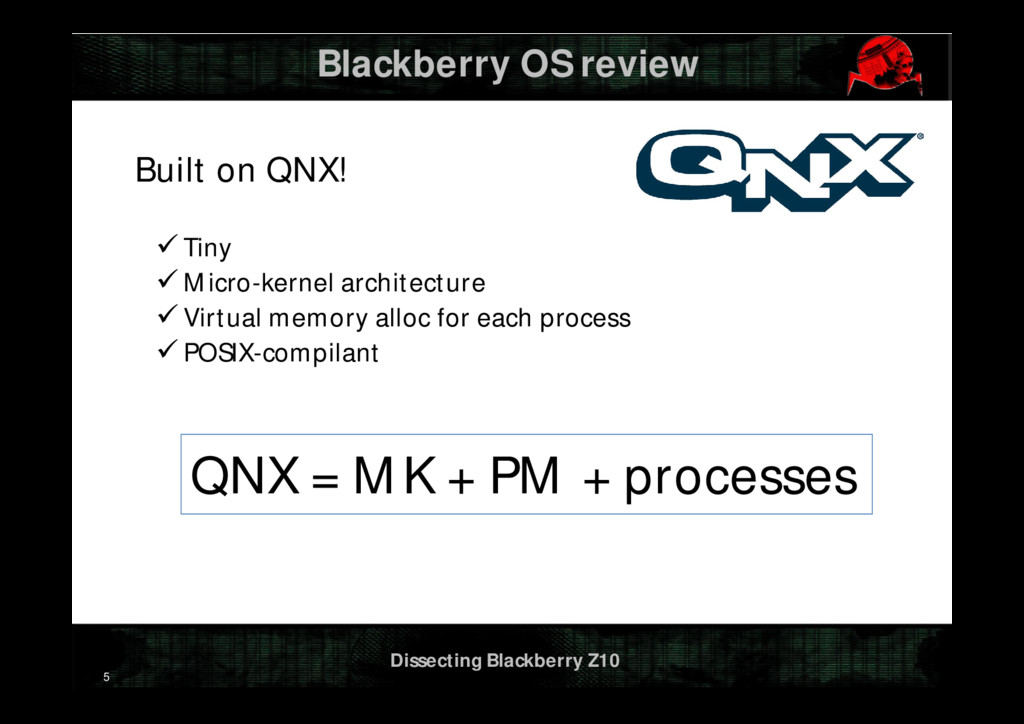
Dissecting Blackberry Z10 Blackberry OS review Built on QNX! 5
Tiny Micro-kernel architecture Virtual memory alloc for each process POSIX-compilant QNX = MK + PM + processes -
Dissecting Blackberry Z10 Agenda Blackberry OS review Shell Access The
Approaches Firmware from the inside Playing with the browser Security on the application level Funny with APIs MDM capabilities Efficiency of security features Future research 8 -
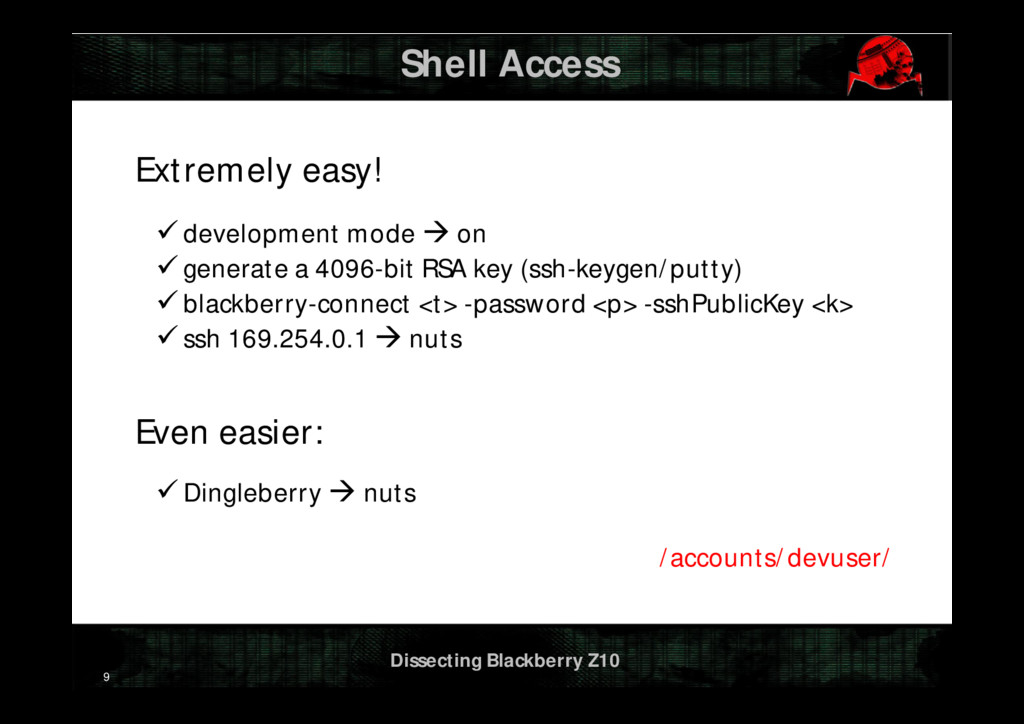
Dissecting Blackberry Z10 Shell Access Extremely easy! 9 development
mode on generate a 4096-bit RSA key (ssh-keygen/putty) blackberry-connect <t> -password <p> -sshPublicKey <k> ssh 169.254.0.1 nuts Even easier: Dingleberry nuts /accounts/devuser/ -
Dissecting Blackberry Z10 Agenda Blackberry OS review Shell Access The
Approaches Firmware from the inside Playing with the browser Security on the application level Funny with APIs MDM capabilities Efficiency of security features Future research 10 -
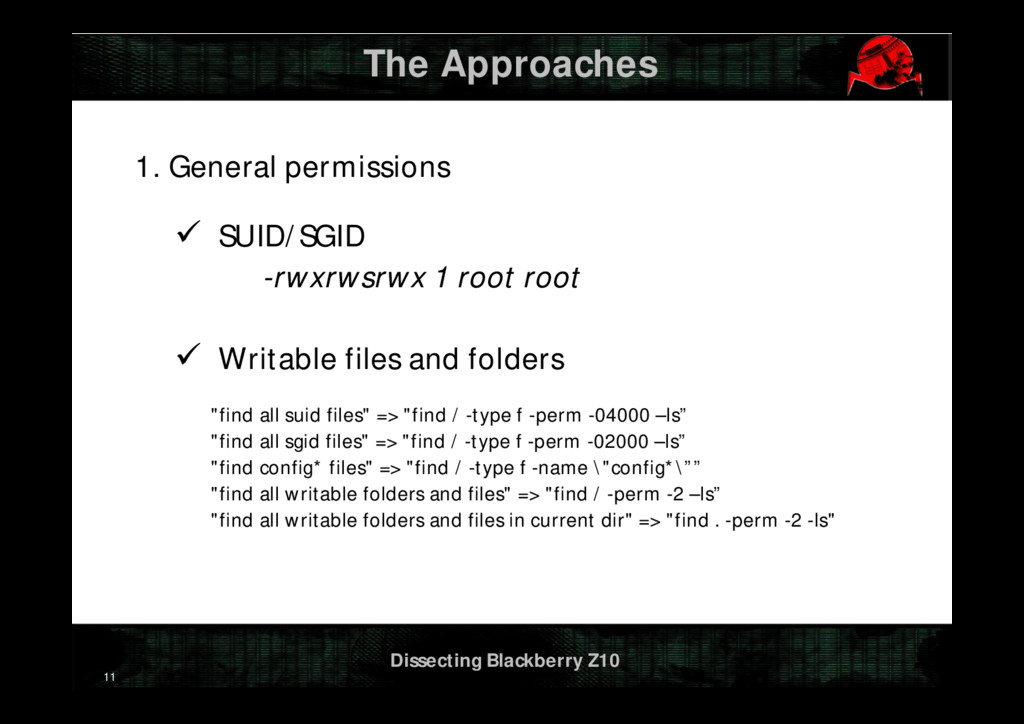
Dissecting Blackberry Z10 The Approaches 1. General permissions 11
SUID/SGID -rwxrwsrwx 1 root root Writable files and folders "find all suid files" => "find / -type f -perm -04000 –ls” "find all sgid files" => "find / -type f -perm -02000 –ls” "find config* files" => "find / -type f -name \"config*\”” "find all writable folders and files" => "find / -perm -2 –ls” "find all writable folders and files in current dir" => "find . -perm -2 -ls" -
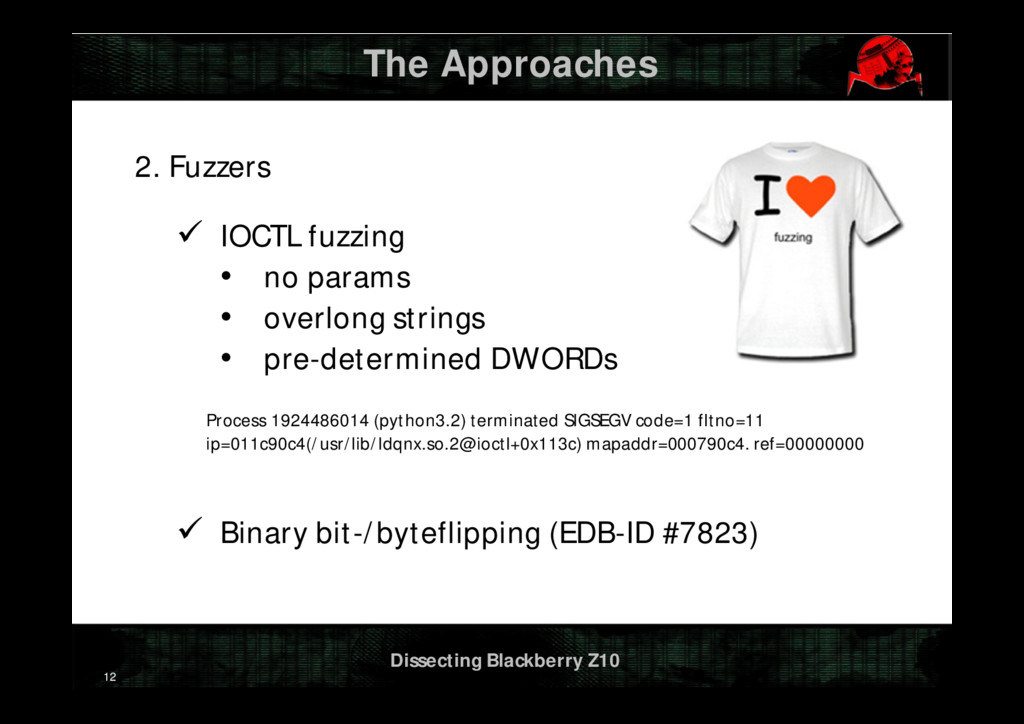
Dissecting Blackberry Z10 The Approaches 2. Fuzzers 12 IOCTL
fuzzing • no params • overlong strings • pre-determined DWORDs Process 1924486014 (python3.2) terminated SIGSEGV code=1 fltno=11 ip=011c90c4(/usr/lib/ldqnx.so.2@ioctl+0x113c) mapaddr=000790c4. ref=00000000 Binary bit-/byteflipping (EDB-ID #7823) -
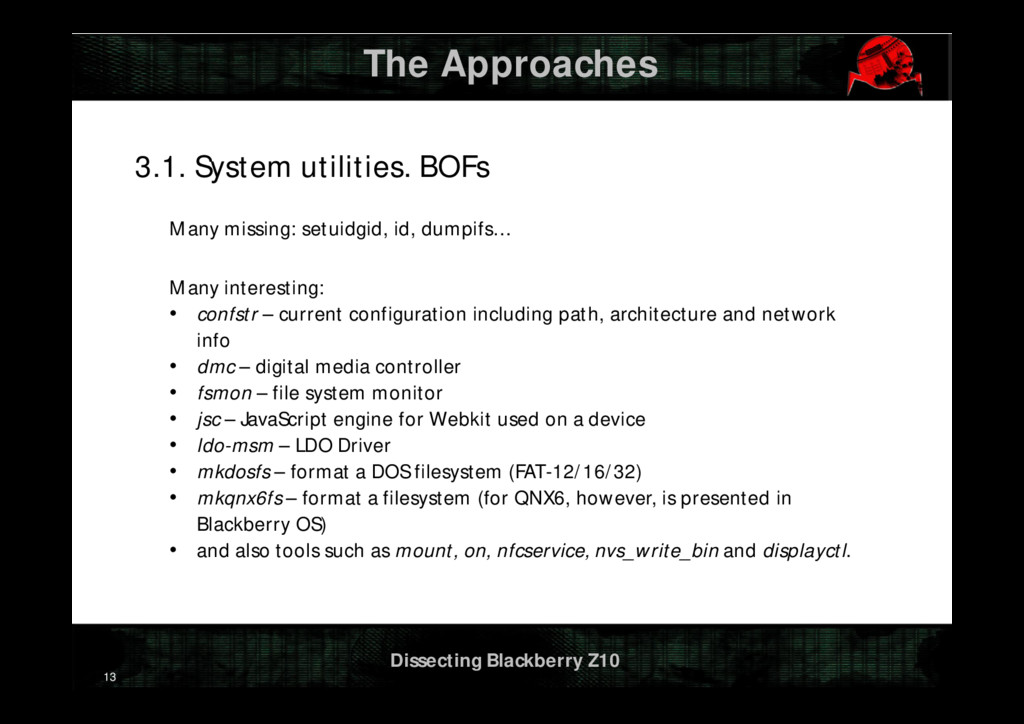
Dissecting Blackberry Z10 The Approaches 3.1. System utilities. BOFs 13
Many missing: setuidgid, id, dumpifs… Many interesting: • confstr – current configuration including path, architecture and network info • dmc – digital media controller • fsmon – file system monitor • jsc – JavaScript engine for Webkit used on a device • ldo-msm – LDO Driver • mkdosfs – format a DOS filesystem (FAT-12/16/32) • mkqnx6fs – format a filesystem (for QNX6, however, is presented in Blackberry OS) • and also tools such as mount, on, nfcservice, nvs_write_bin and displayctl. -
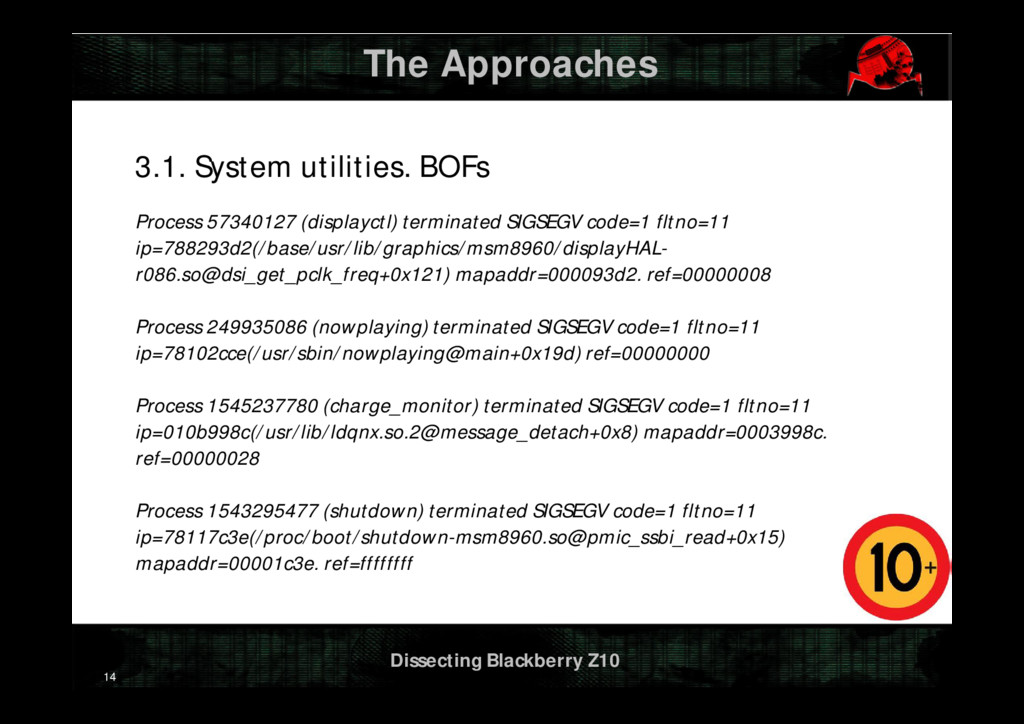
Dissecting Blackberry Z10 The Approaches 3.1. System utilities. BOFs 14
Process 57340127 (displayctl) terminated SIGSEGV code=1 fltno=11 ip=788293d2(/base/usr/lib/graphics/msm8960/displayHAL- r086.so@dsi_get_pclk_freq+0x121) mapaddr=000093d2. ref=00000008 Process 249935086 (nowplaying) terminated SIGSEGV code=1 fltno=11 ip=78102cce(/usr/sbin/nowplaying@main+0x19d) ref=00000000 Process 1545237780 (charge_monitor) terminated SIGSEGV code=1 fltno=11 ip=010b998c(/usr/lib/ldqnx.so.2@message_detach+0x8) mapaddr=0003998c. ref=00000028 Process 1543295477 (shutdown) terminated SIGSEGV code=1 fltno=11 ip=78117c3e(/proc/boot/shutdown-msm8960.so@pmic_ssbi_read+0x15) mapaddr=00001c3e. ref=ffffffff -
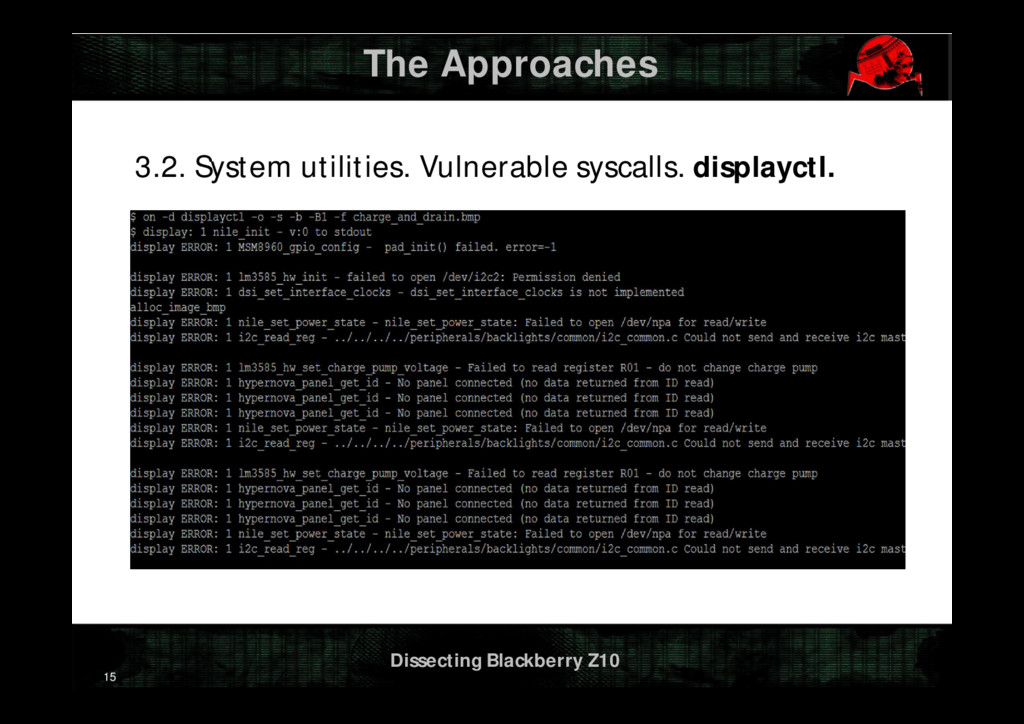
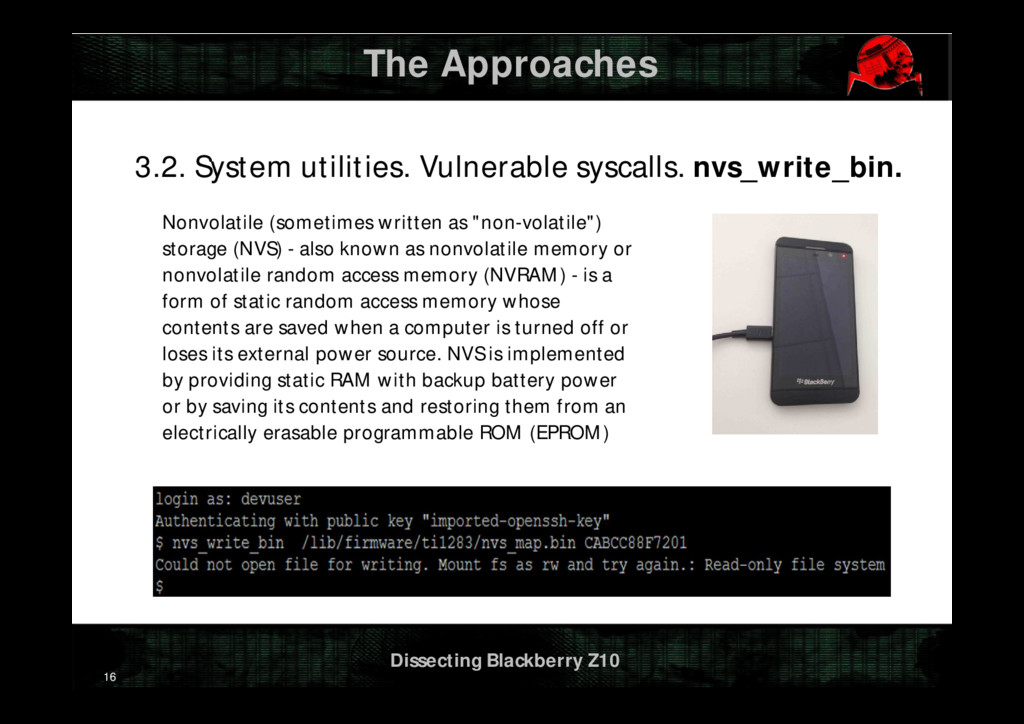
Dissecting Blackberry Z10 The Approaches 3.2. System utilities. Vulnerable syscalls.
nvs_write_bin. 16 Nonvolatile (sometimes written as "non-volatile") storage (NVS) - also known as nonvolatile memory or nonvolatile random access memory (NVRAM) - is a form of static random access memory whose contents are saved when a computer is turned off or loses its external power source. NVS is implemented by providing static RAM with backup battery power or by saving its contents and restoring them from an electrically erasable programmable ROM (EPROM) -
Dissecting Blackberry Z10 Agenda Blackberry OS review Shell Access The
Approaches Firmware from the inside Playing with the browser Security on the application level Funny with APIs MDM capabilities Efficiency of security features Future research 17 -
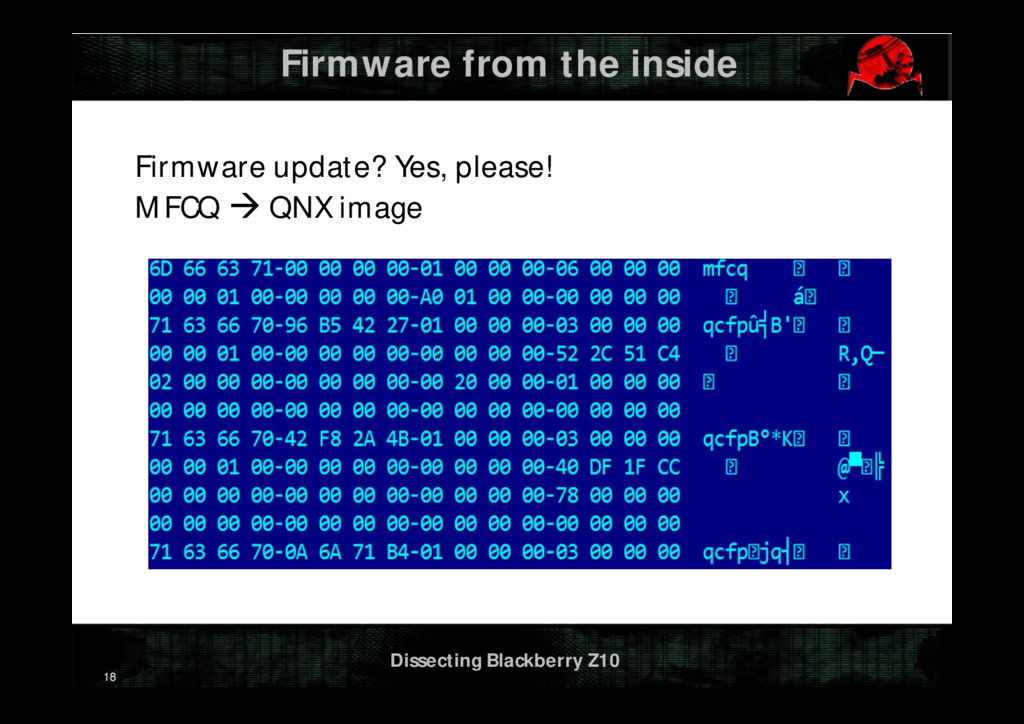
Dissecting Blackberry Z10 Firmware from the inside Firmware update? Yes,
please! MFCQ QNX image 18 -
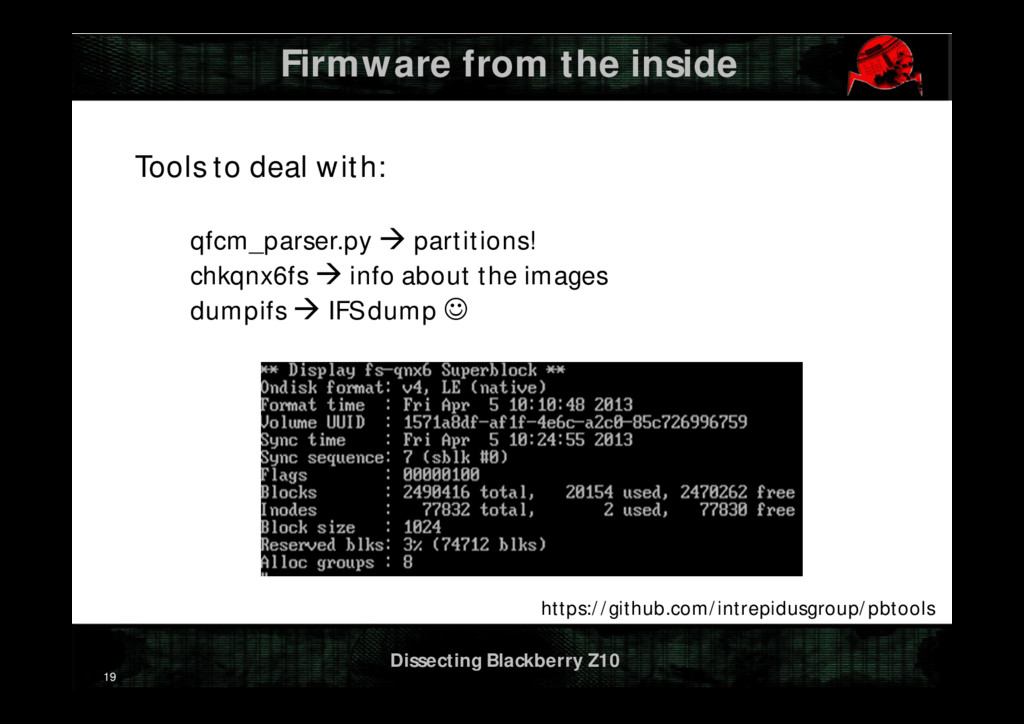
Dissecting Blackberry Z10 Firmware from the inside Tools to deal
with: 19 qfcm_parser.py partitions! chkqnx6fs info about the images dumpifs IFS dump https://github.com/intrepidusgroup/pbtools -
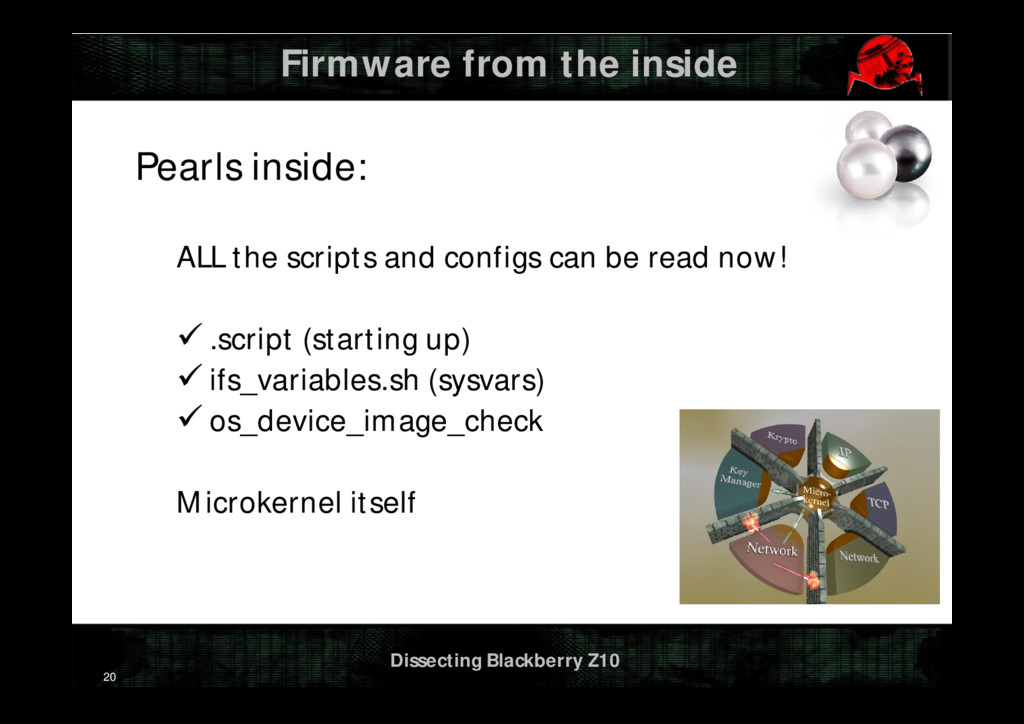
Dissecting Blackberry Z10 Firmware from the inside Pearls inside: 20
ALL the scripts and configs can be read now! .script (starting up) ifs_variables.sh (sysvars) os_device_image_check Microkernel itself -
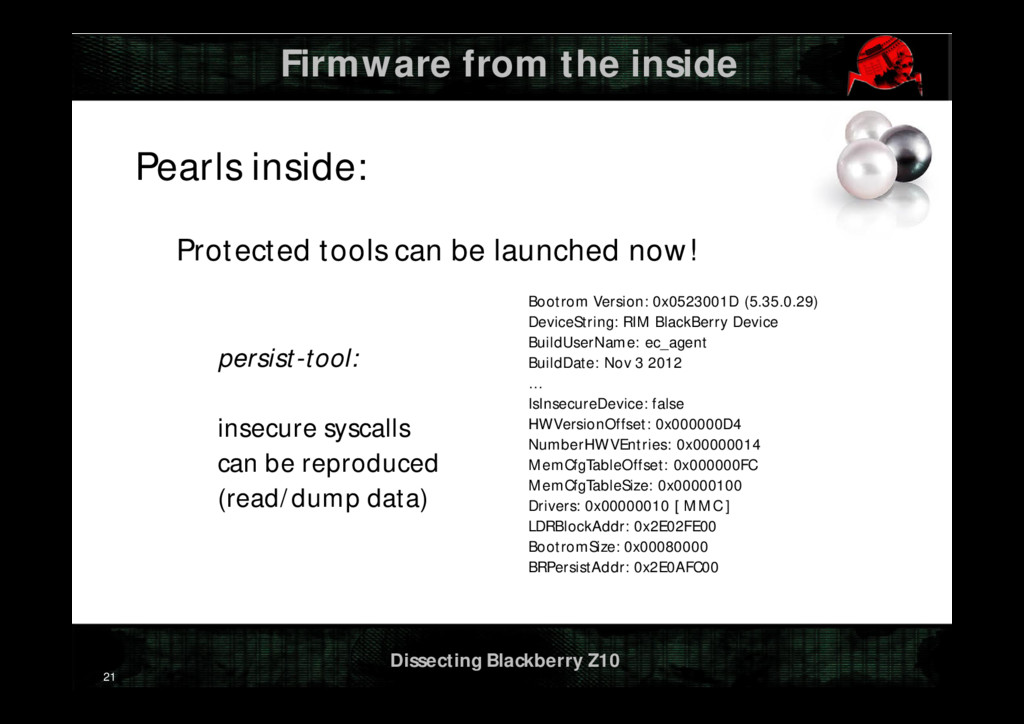
Dissecting Blackberry Z10 Firmware from the inside 21 Pearls inside:
Protected tools can be launched now! Bootrom Version: 0x0523001D (5.35.0.29) DeviceString: RIM BlackBerry Device BuildUserName: ec_agent BuildDate: Nov 3 2012 … IsInsecureDevice: false HWVersionOffset: 0x000000D4 NumberHWVEntries: 0x00000014 MemCfgTableOffset: 0x000000FC MemCfgTableSize: 0x00000100 Drivers: 0x00000010 [ MMC ] LDRBlockAddr: 0x2E02FE00 BootromSize: 0x00080000 BRPersistAddr: 0x2E0AFC00 persist-tool: insecure syscalls can be reproduced (read/dump data) -
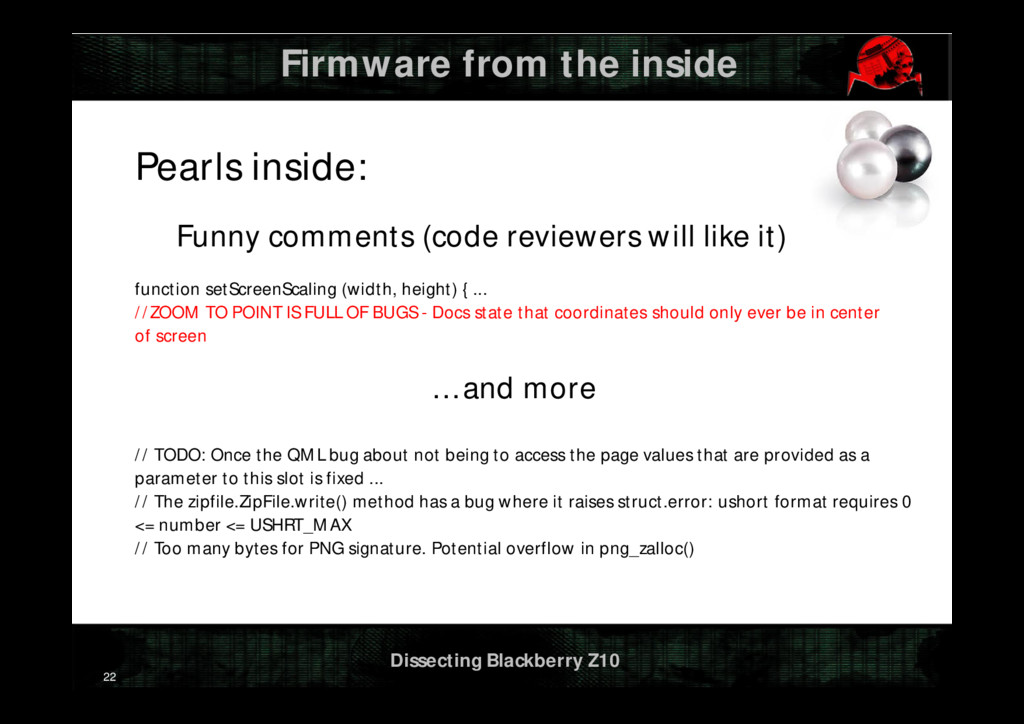
Dissecting Blackberry Z10 Firmware from the inside 22 Pearls inside:
Funny comments (code reviewers will like it) function setScreenScaling (width, height) { ... //ZOOM TO POINT IS FULL OF BUGS - Docs state that coordinates should only ever be in center of screen // TODO: Once the QML bug about not being to access the page values that are provided as a parameter to this slot is fixed ... // The zipfile.ZipFile.write() method has a bug where it raises struct.error: ushort format requires 0 <= number <= USHRT_MAX // Too many bytes for PNG signature. Potential overflow in png_zalloc() … and more -
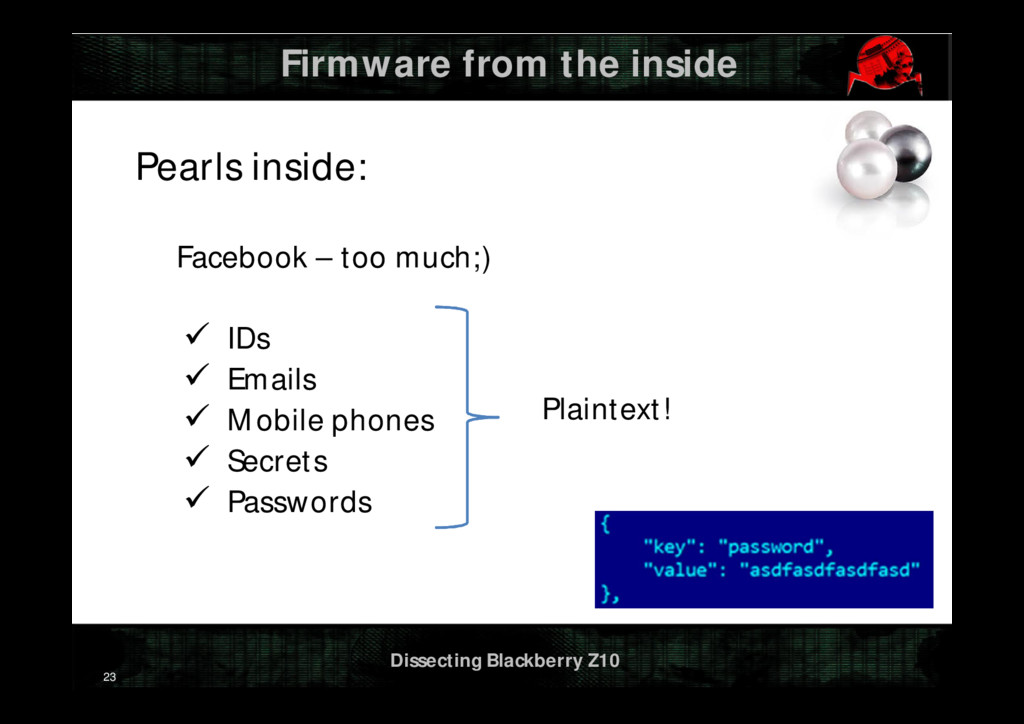
Dissecting Blackberry Z10 Firmware from the inside 23 Pearls inside:
Facebook – too much;) IDs Emails Mobile phones Secrets Passwords Plaintext! -
Dissecting Blackberry Z10 Agenda Blackberry OS review Shell Access The
Approaches Firmware from the inside Playing with the browser Security on the application level Funny with APIs MDM capabilities Efficiency of security features Future research 24 -
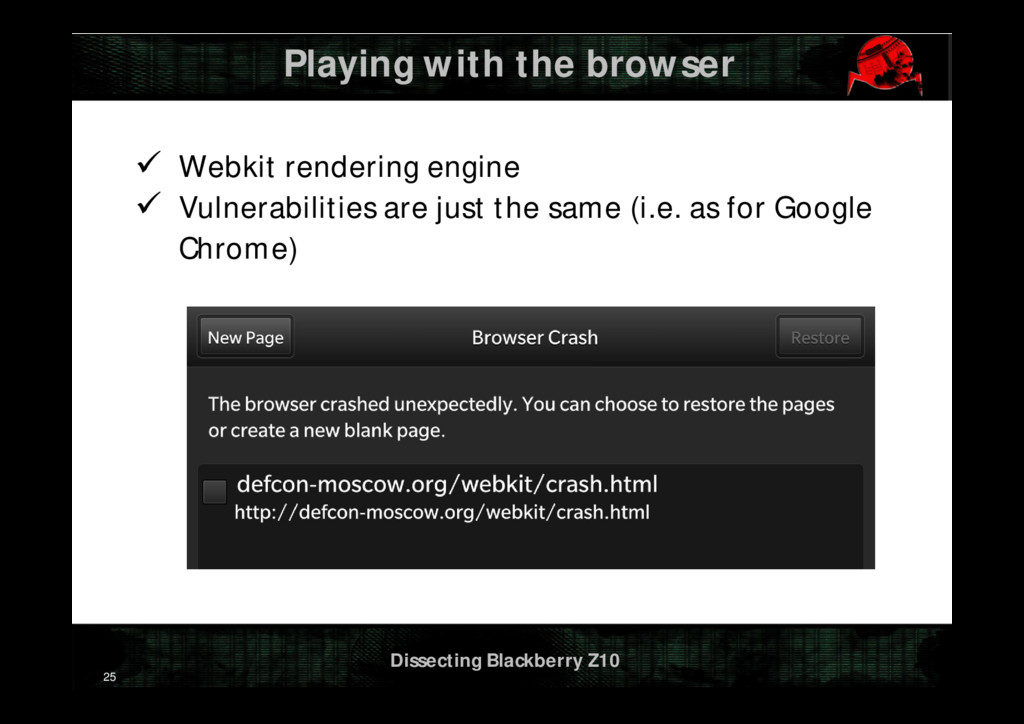
Dissecting Blackberry Z10 Playing with the browser Webkit rendering
engine Vulnerabilities are just the same (i.e. as for Google Chrome) 25 -
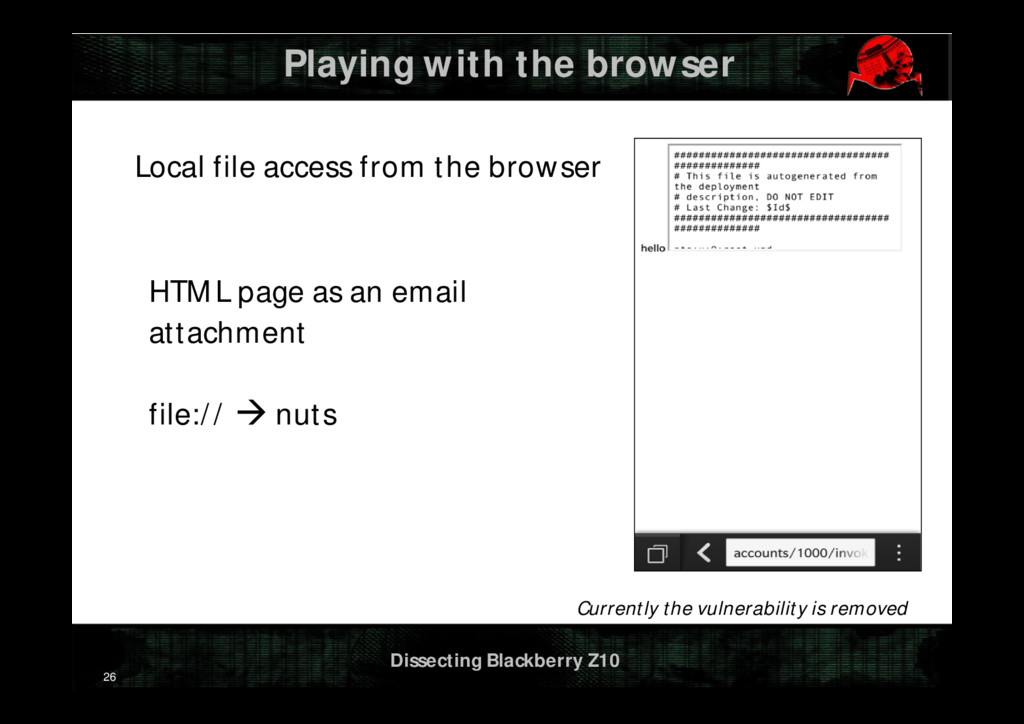
Dissecting Blackberry Z10 Playing with the browser Local file access
from the browser 26 HTML page as an email attachment file:// nuts Currently the vulnerability is removed -
Dissecting Blackberry Z10 Agenda Blackberry OS review Shell Access The
Approaches Firmware from the inside Playing with the browser Security on the application level Funny with APIs MDM capabilities Efficiency of security features Future research 27 -
Dissecting Blackberry Z10 Security on the Application Level BlackBerry Z10
– Vulnerability in BlackBerry Protect Limited: by the inability of a potential attacker to force exploitation of the vulnerability without significant customer interaction and physical access to the device Affected Software BlackBerry 10 OS version 10.0.10.261 and earlier, except version 10.0.9.2743 BlackBerry Z10 smartphone only 28 Currently the vulnerability is removed -
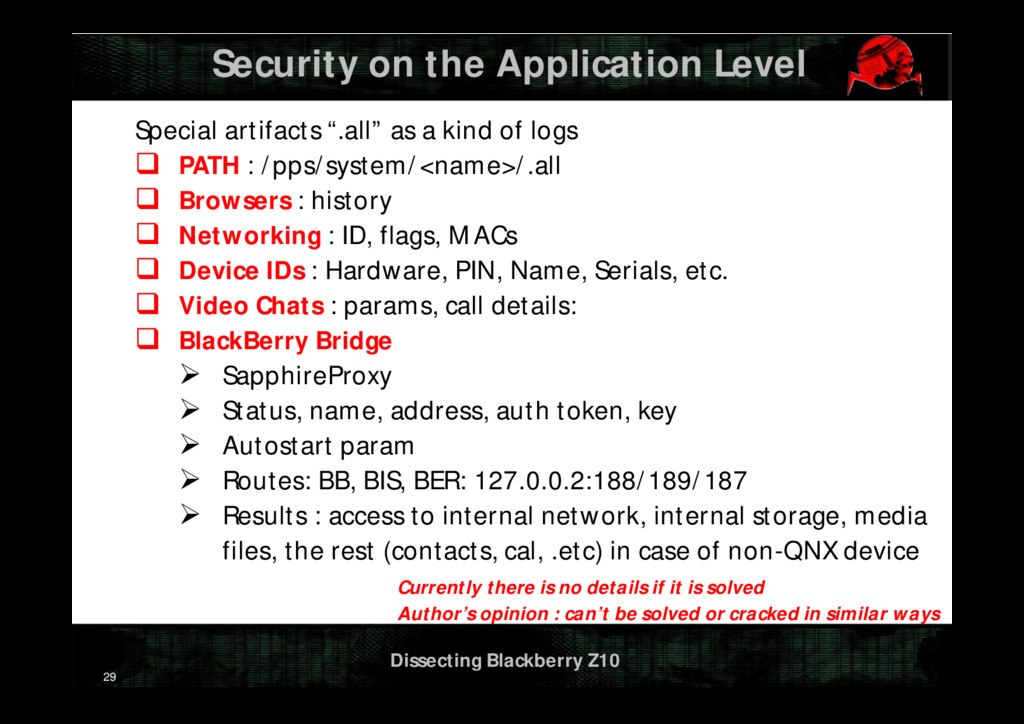
Dissecting Blackberry Z10 Security on the Application Level Special artifacts
“.all” as a kind of logs PATH : /pps/system/<name>/.all Browsers : history Networking : ID, flags, MACs Device IDs : Hardware, PIN, Name, Serials, etc. Video Chats : params, call details: BlackBerry Bridge SapphireProxy Status, name, address, auth token, key Autostart param Routes: BB, BIS, BER: 127.0.0.2:188/189/187 Results : access to internal network, internal storage, media files, the rest (contacts, cal, .etc) in case of non-QNX device 29 Currently there is no details if it is solved Author’s opinion : can’t be solved or cracked in similar ways -
Dissecting Blackberry Z10 Agenda 30 Blackberry OS review Shell Access
The Approaches Firmware from the inside Playing with the browser Security on the application level Funny with APIs MDM capabilities Efficiency of security features Future research -
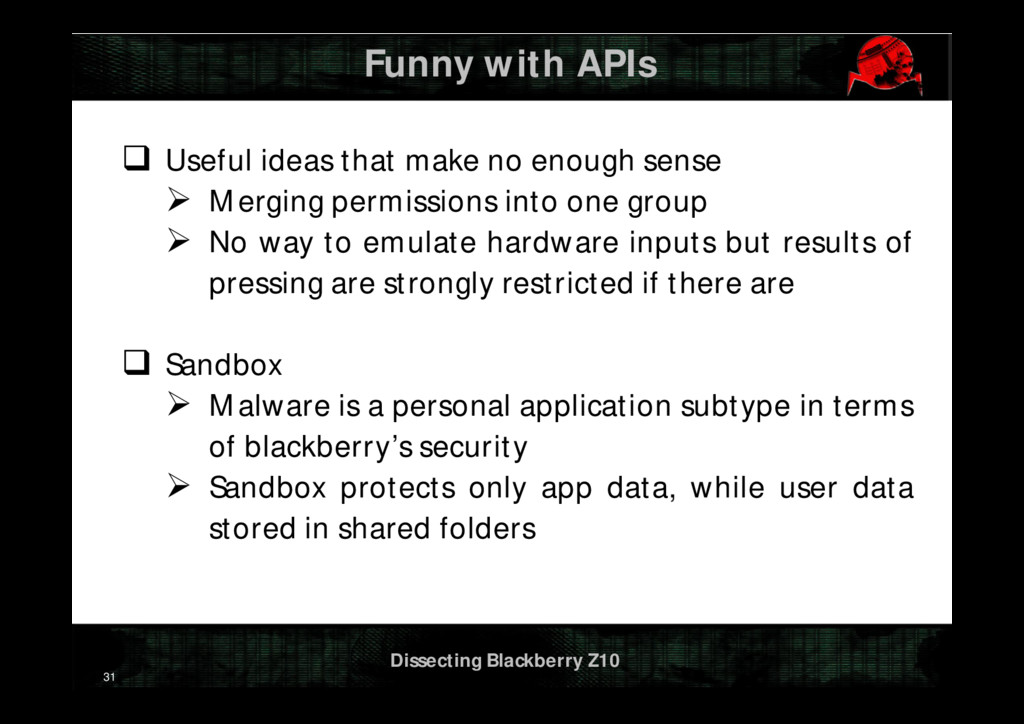
Dissecting Blackberry Z10 Funny with APIs Useful ideas that
make no enough sense Merging permissions into one group No way to emulate hardware inputs but results of pressing are strongly restricted if there are Sandbox Malware is a personal application subtype in terms of blackberry’s security Sandbox protects only app data, while user data stored in shared folders 31 -
Dissecting Blackberry Z10 Funny with APIs Non-controlled activity by
any permission Accessing to data passed through the clipboard Access to ‘Accounts’ leads to a ‘read’ access to contacts,messages, notebooks, calendar by default MediaPlayer is a great way to access to the FS Access to file system in many ways and most cases managing device’s resources Camera activity, Contact photos Calendar event attachments Message attachments (Email, BBM) Saving records (camera photos, video, audios) 32 -
Dissecting Blackberry Z10 Agenda 33 Blackberry OS review Shell Access
The Approaches Firmware from the inside Playing with the browser Security on the application level Funny with APIs MDM capabilities Efficiency of security features Future research -
Dissecting Blackberry Z10 Agenda 34 BlackBerry Old iOS BlackBerry QNX
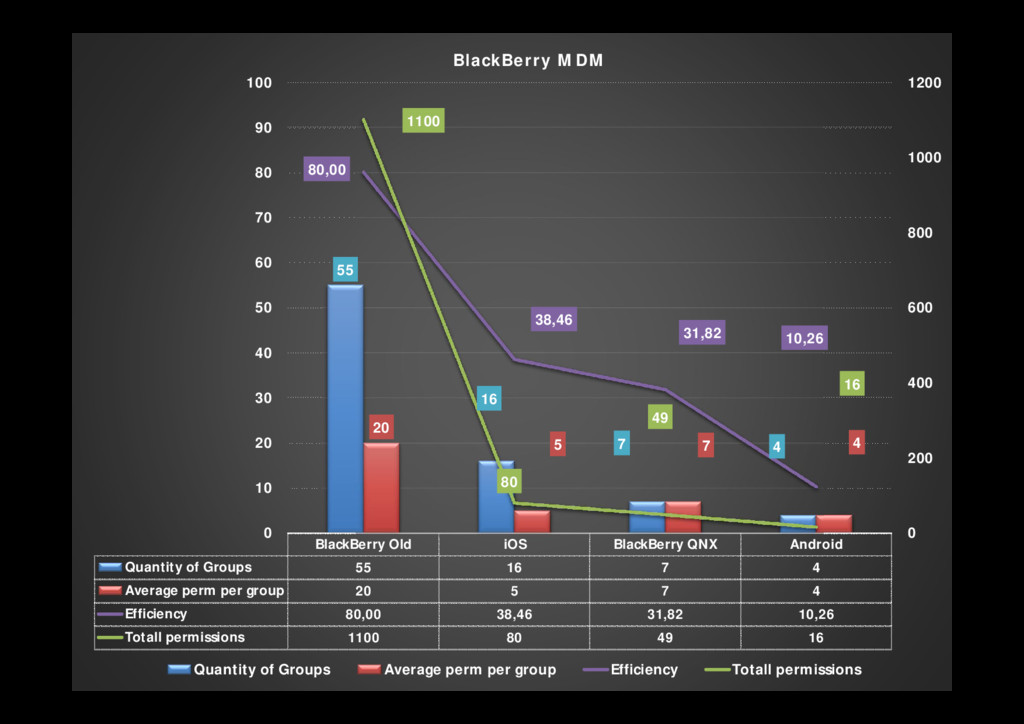
Android Quantity of Groups 55 16 7 4 Average perm per group 20 5 7 4 Efficiency 80,00 38,46 31,82 10,26 Totall permissions 1100 80 49 16 55 16 7 4 20 5 7 4 80,00 38,46 31,82 10,26 1100 80 49 16 0 200 400 600 800 1000 1200 0 10 20 30 40 50 60 70 80 90 100 BlackBerry MDM Quantity of Groups Average perm per group Efficiency Totall permissions -
Dissecting Blackberry Z10 Agenda 35 Blackberry OS review Shell Access
The Approaches Firmware from the inside Playing with the browser Security on the application level Funny with APIs MDM capabilities Efficiency of security features Future research -
Dissecting Blackberry Z10 Efficiency of security features Activity
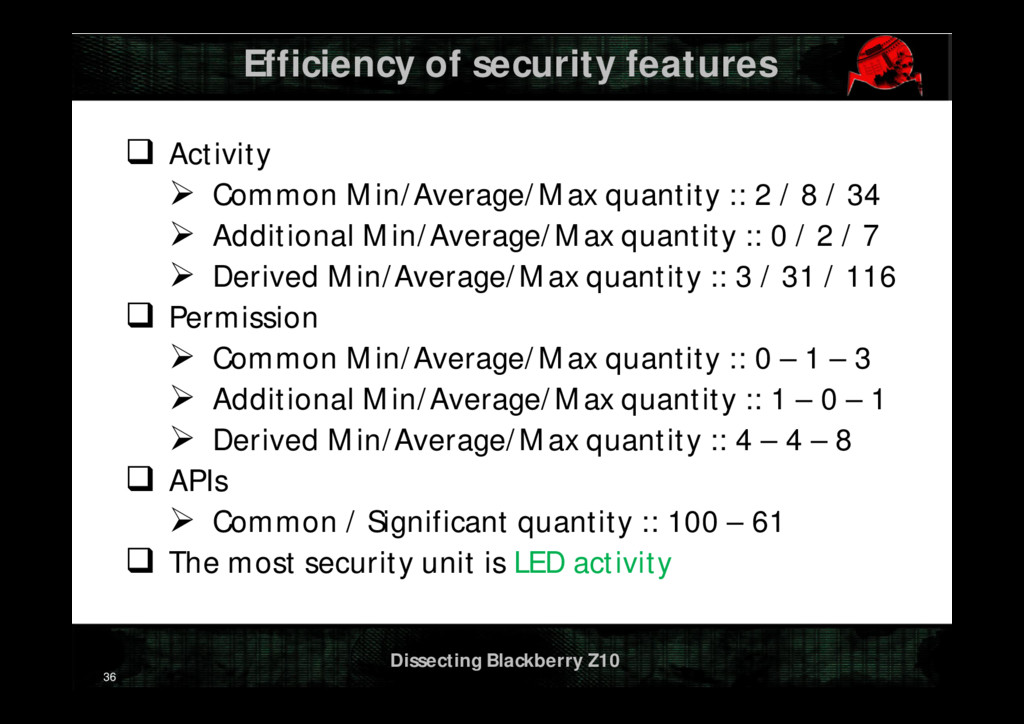
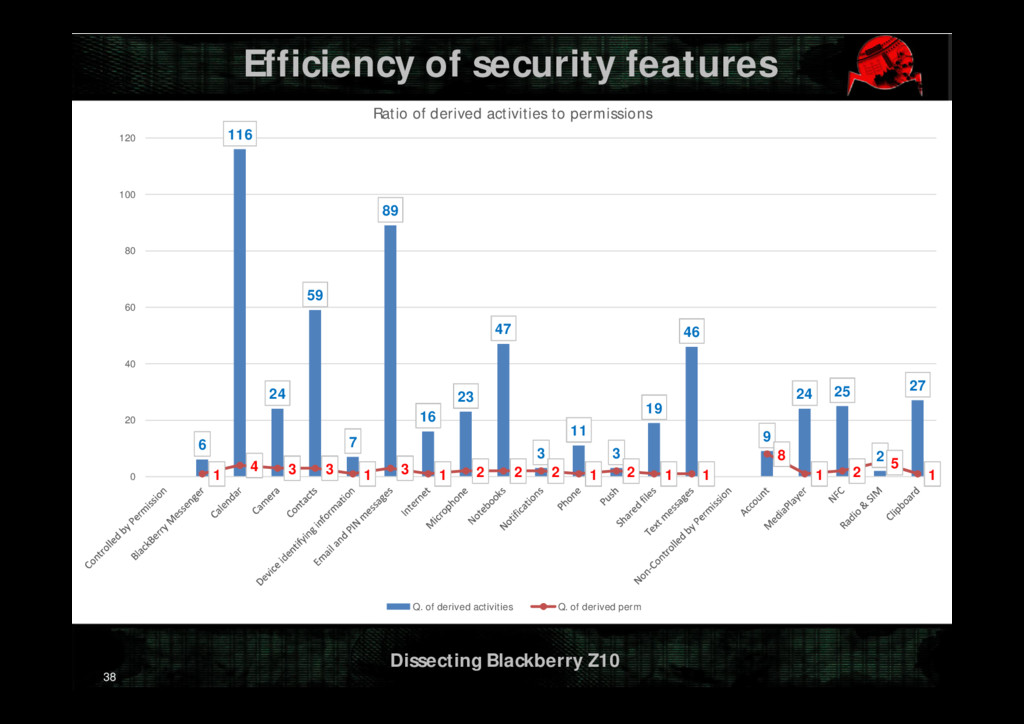
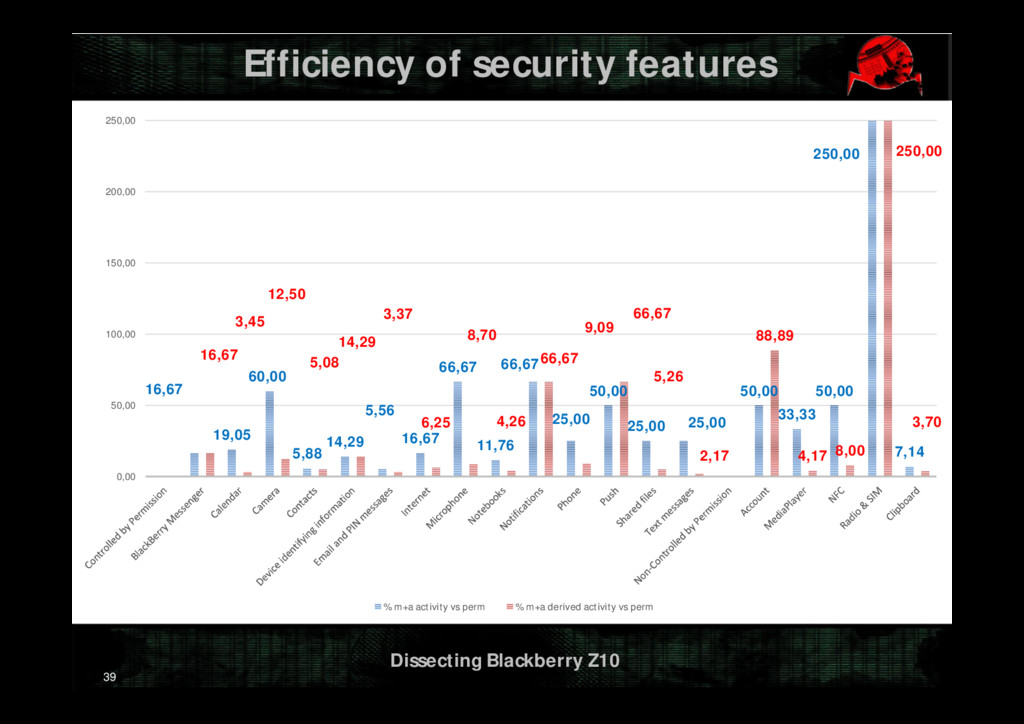
Common Min/Average/Max quantity :: 2 / 8 / 34 Additional Min/Average/Max quantity :: 0 / 2 / 7 Derived Min/Average/Max quantity :: 3 / 31 / 116 Permission Common Min/Average/Max quantity :: 0 – 1 – 3 Additional Min/Average/Max quantity :: 1 – 0 – 1 Derived Min/Average/Max quantity :: 4 – 4 – 8 APIs Common / Significant quantity :: 100 – 61 The most security unit is LED activity 36 -
Dissecting Blackberry Z10 Efficiency of security features 37 6 21
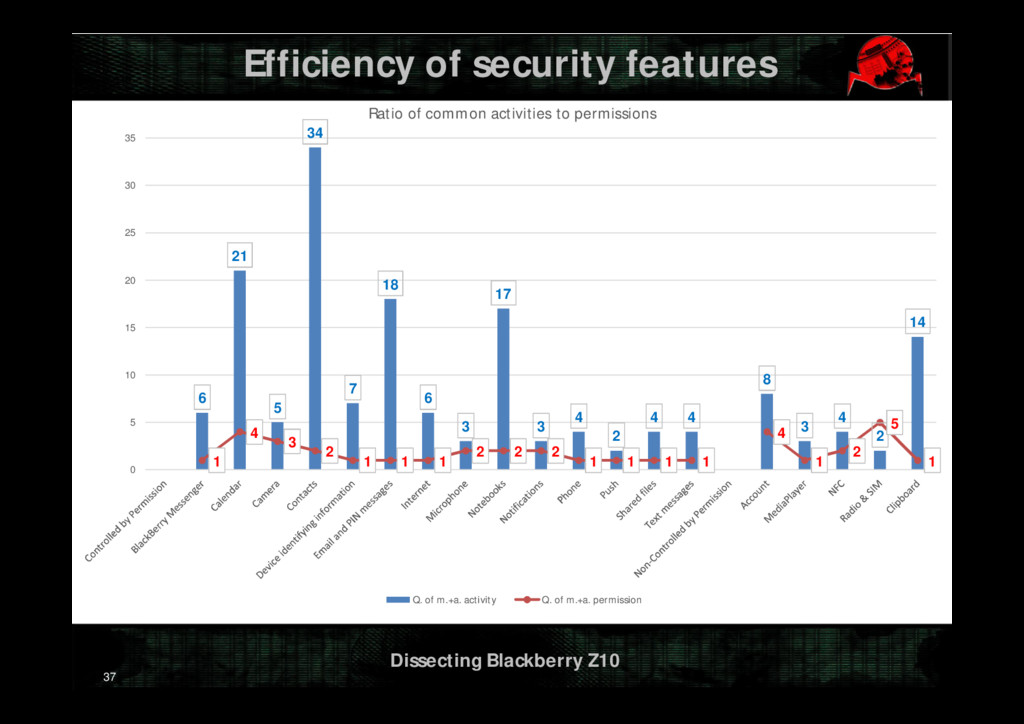
5 34 7 18 6 3 17 3 4 2 4 4 8 3 4 2 14 1 4 3 2 1 1 1 2 2 2 1 1 1 1 4 1 2 5 1 0 5 10 15 20 25 30 35 Ratio of common activities to permissions Q. of m.+a. activity Q. of m.+a. permission -
Dissecting Blackberry Z10 Efficiency of security features 38 6 116
24 59 7 89 16 23 47 3 11 3 19 46 9 24 25 2 27 1 4 3 3 1 3 1 2 2 2 1 2 1 1 8 1 2 5 1 0 20 40 60 80 100 120 Ratio of derived activities to permissions Q. of derived activities Q. of derived perm -
Dissecting Blackberry Z10 Efficiency of security features 39 16,67 19,05
60,00 5,88 14,29 5,56 16,67 66,67 11,76 66,67 25,00 50,00 25,00 25,00 50,00 33,33 50,00 250,00 7,14 16,67 3,45 12,50 5,08 14,29 3,37 6,25 8,70 4,26 66,67 9,09 66,67 5,26 2,17 88,89 4,17 8,00 250,00 3,70 0,00 50,00 100,00 150,00 200,00 250,00 % m+a activity vs perm % m+a derived activity vs perm -
Dissecting Blackberry Z10 Agenda 40 Blackberry OS review Shell Access
The Approaches Firmware from the inside Playing with the browser Security on the application level Funny with APIs MDM capabilities Efficiency of security features Future research -
Dissecting Blackberry Z10 Future research 41 Image parser fuzzing Jailbreak
IOCTL / syscalls further research Play more with SSH Blackberry Balance is not available yet Permission collision Overpemissioning by system applications and services Bypassing MDM features by both of previous -
Dissecting Blackberry Z10 Full articles … are available here (no
SMS to send is required! Free for a very limited time!) 42 http://goo.gl/dP9iR Blackberry Z10 research http://goo.gl/PpXxg Blackberry and more
 c0rdis
 rfujii
 hisaokatsumi
 institutdelelevage
 masao
 shunk031
 satai
 shibuiwilliam
 analokmaus
 tmiket
 letsgokoyo
 gurzu
 chikuwait
 tamaranovitovic
 denniskardys
 addyosmani
 lara
 codingconduct
 samtorres
 thirion