Share
Embed

Transcript
131 slides
-
About us • Alexander Antukh • OWASP Poland Board Member
• Head of Product Security at • @c0rdis -
About us • Marek Puchalski • OWASP Poland member •
Developer and Security Consultant at Capgemini • https://marek.puchal.ski -
About us • Pawel Rzepa • Security Engineer in Intive
• Contributor in OWASP MSTG (Mobile Security Testing Guide) -
About us • Andrii Sygida • OWASP Poland almost member
• Application security specialist at -
About us • Daniel Ramirez • OWASP Member • Security
Specialist in EY • Hands-on VA experience in the different kinds of apps. -
Motivation • Top 10 is a de-facto standard in Webappsec
world • OWASP is mostly associated with it … • but there are many more! As of 2016, there are 133 different projects, which can help you whether you are on attacker’s or defender’s parts of the barricades! -
Agenda • Problem 1: efficient security training • Solution: WebGoat
• Problem 2: efficient management of multiple penetration testing tasks • Solution: Offensive Web Testing Framework -
Problem of efficient security training …and XSS allows you injecting
such horrifying pop up windows!!! Security awareness trainings for developers are quite common, but reality shows they are still ineffective :( -
What about… Finally a security training which isn’t an online
course to fly through and forget! Internal course that is free and isn’t a corpo- bullshit?! Cannot believe that… …arranging internal hands- on labs for developers and testers, where they can deeply understand vulnerabilities by finding and fixing them? -
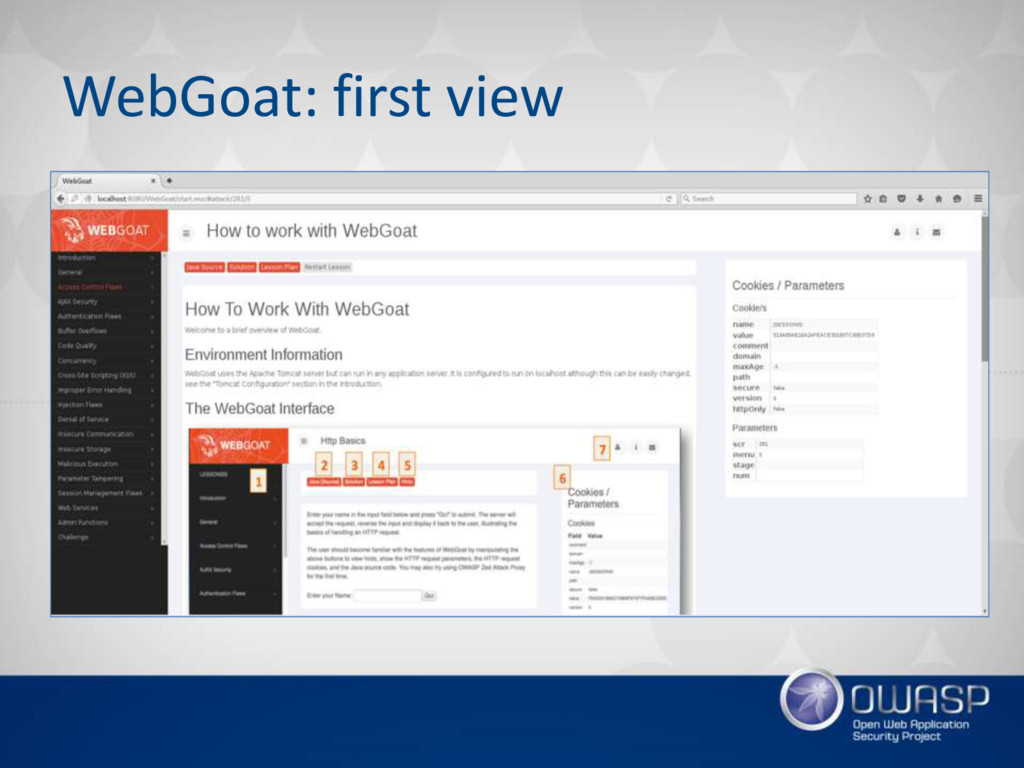
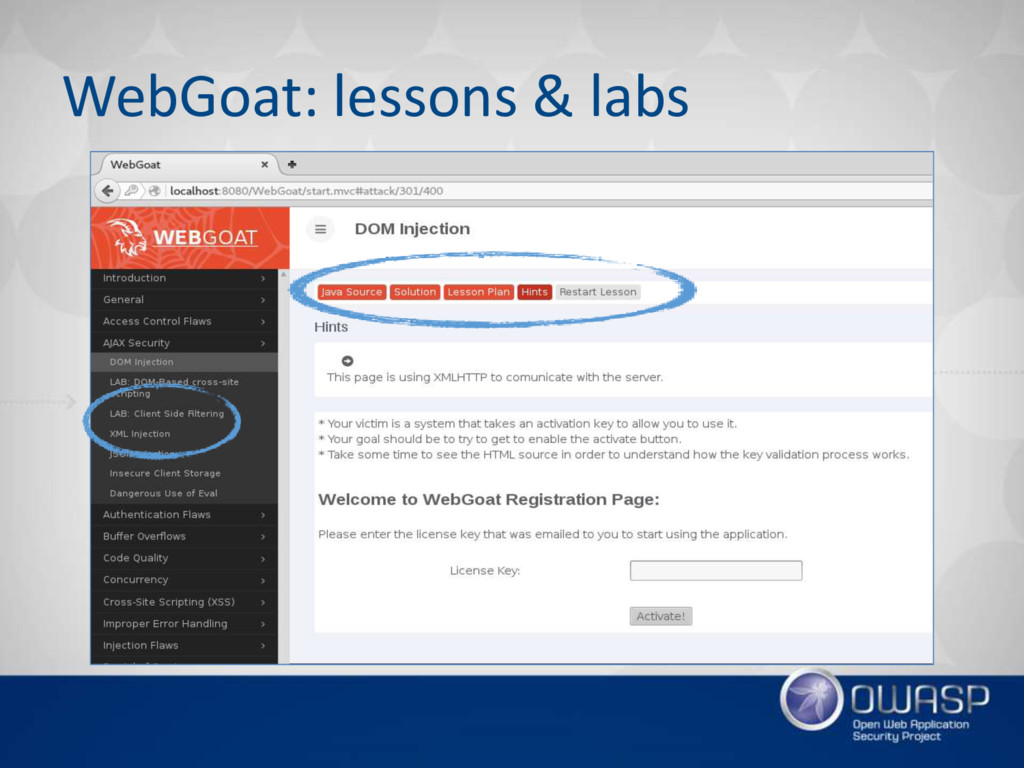
WebGoat: few words about • A deliberately insecure Java-based application,
which allows you to test common vulnerabilities • 50+ lessons • After finding a vulnerability, learn to fix it! • Easy manageable lessons via plugins • You can create your own lessons and easily customize a content and language …or .Net-based: https://www.owasp.org/index.php/ WebGoatFor.Net WebGoat: few words about • A deliberately insecure Java-based (or .Net based: https://www.owasp.org/index.php/WebGoatFor.Net) application, which allows you to test common vulnerabilities • 50+ lessons • After finding a vulnerability, learn to fix it! • Easy manageable lessons via plugins • You can create your own lessons and easily customize a content and language -
Not only web apps… • Ruby on Rails: OWASP Rails
Goat Project • PHP: OWASP WebGoatPHP • Node.js: OWASP Node_js Goat Project • Android: OWASP GoatDroid Project • iOS: OWASP iGoat Project -
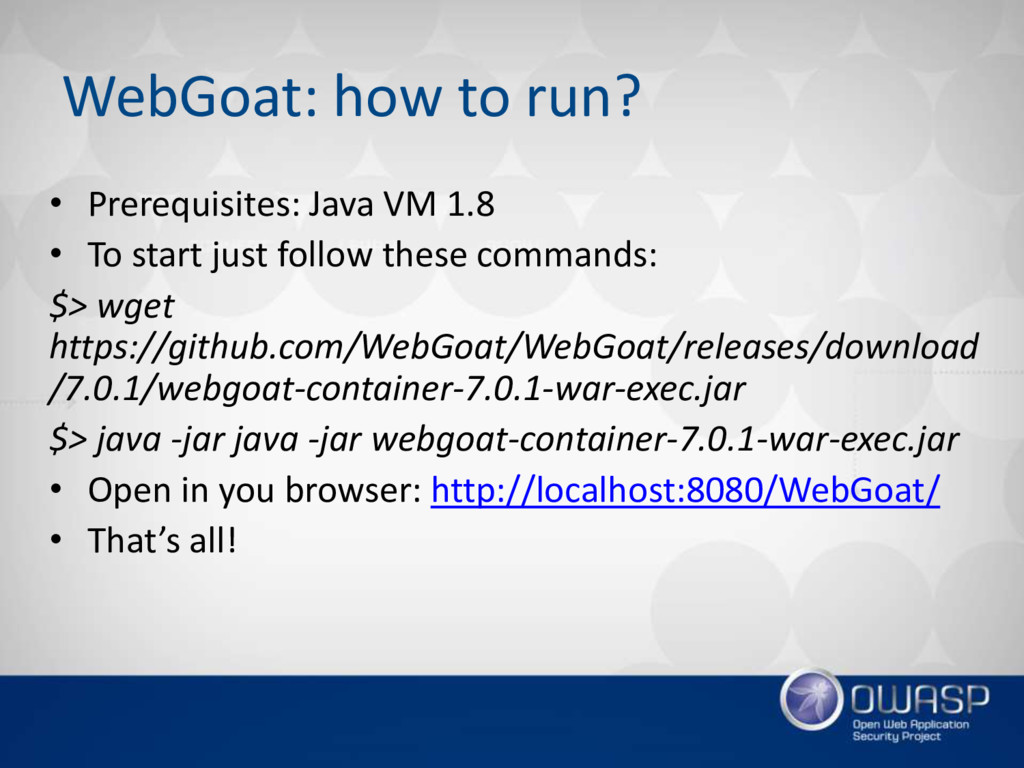
WebGoat: how to run? • Prerequisites: Java VM 1.8 •
To start just follow these commands: $> wget https://github.com/WebGoat/WebGoat/releases/download /7.0.1/webgoat-container-7.0.1-war-exec.jar $> java -jar java -jar webgoat-container-7.0.1-war-exec.jar • Open in you browser: http://localhost:8080/WebGoat/ • That’s all! -
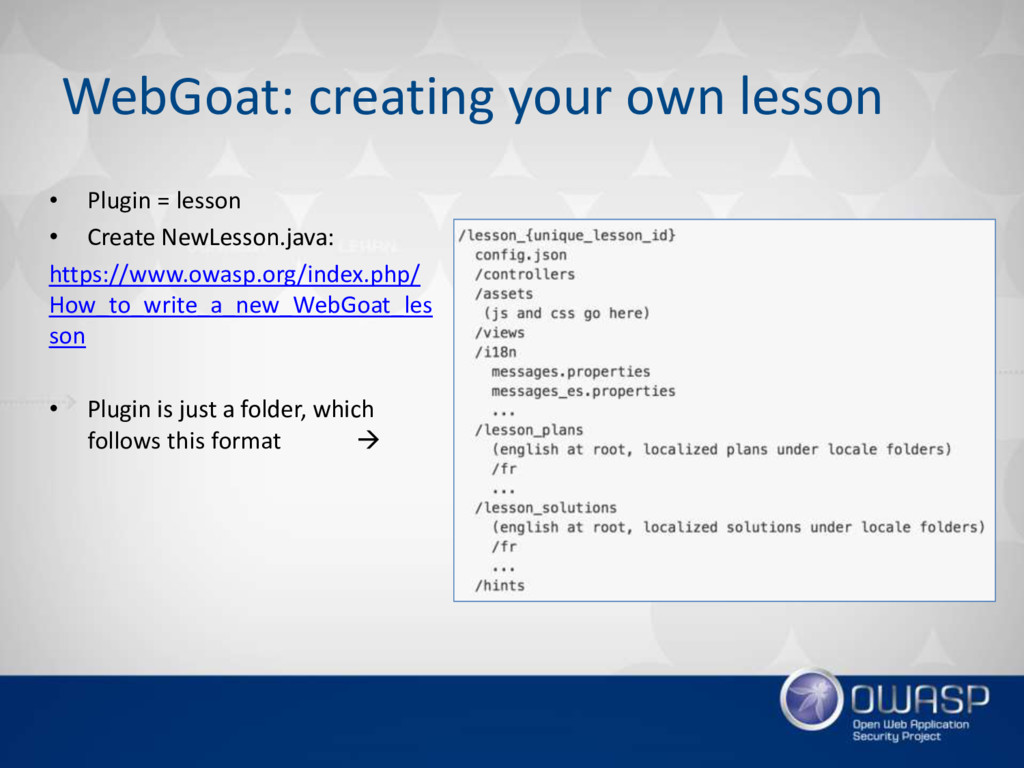
WebGoat: creating your own lesson • Plugin = lesson •
Create NewLesson.java: https://www.owasp.org/index.php/ How_to_write_a_new_WebGoat_les son • Plugin is just a folder, which follows this format -
Problem: how to efficiently manage outputs from many different applications?
• Each pentester uses many different applications (vuln scanner, web crawler, SSL/TLS tests, session management tests) • Running each of those tests consumes time, right? • It’s easy to automate those tasks, but analysing a consolidated output is much more difficult :( • And finally you have to form a readable report from all those tests… • …oooh… :( -
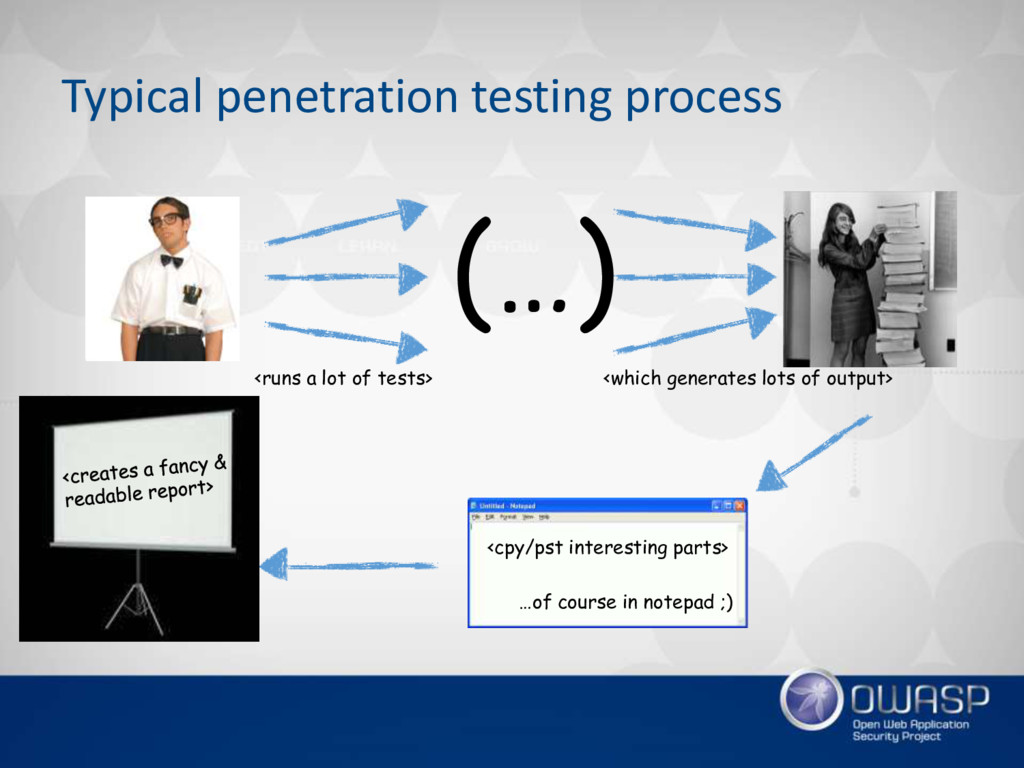
Typical penetration testing process <which generates lots of output> <cpy/pst
interesting parts> …of course in notepad ;) (…) <runs a lot of tests> -
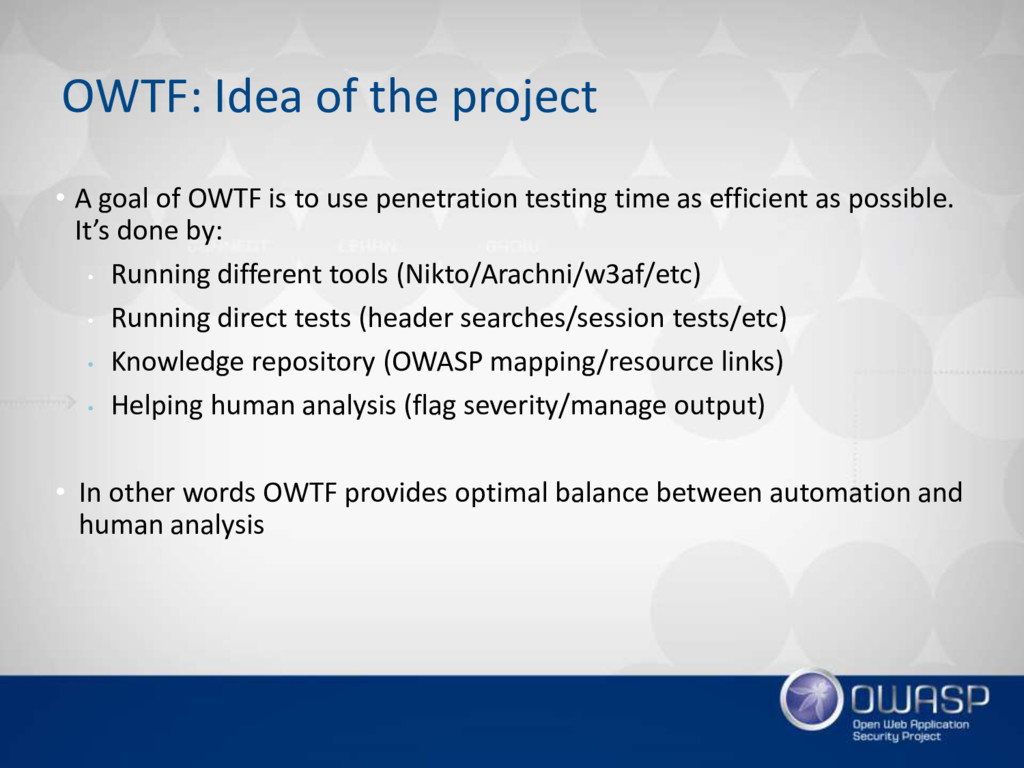
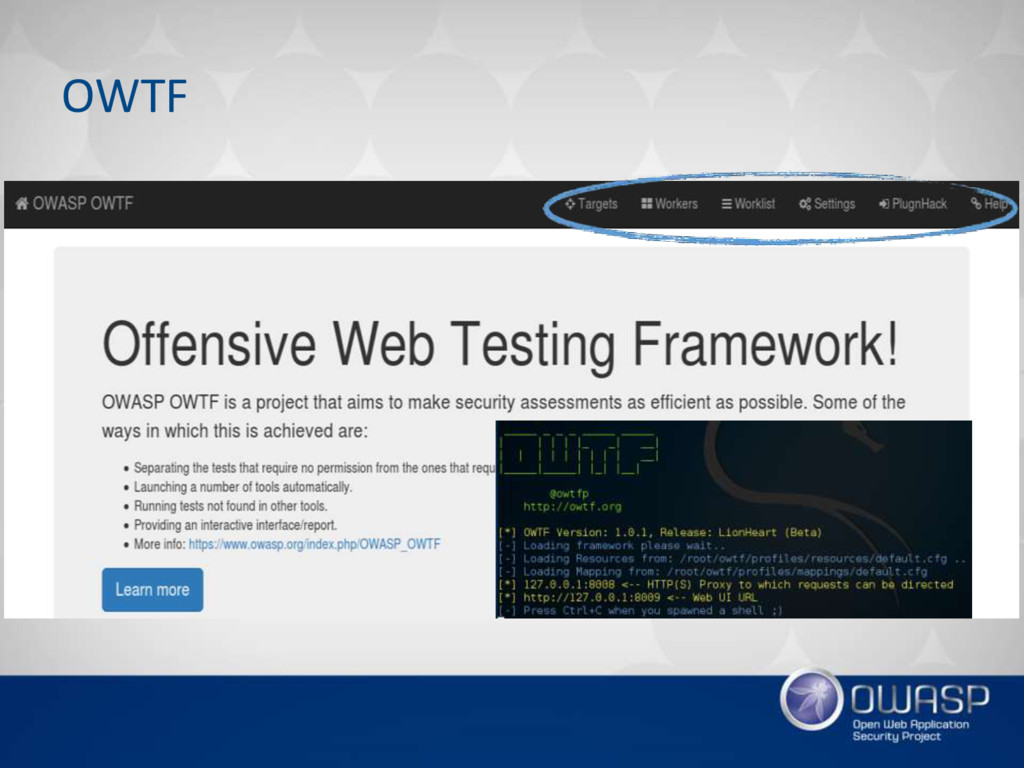
• A goal of OWTF is to use penetration testing
time as efficient as possible. It’s done by: • Running different tools (Nikto/Arachni/w3af/etc) • Running direct tests (header searches/session tests/etc) • Knowledge repository (OWASP mapping/resource links) • Helping human analysis (flag severity/manage output) • In other words OWTF provides optimal balance between automation and human analysis OWTF: Idea of the project -
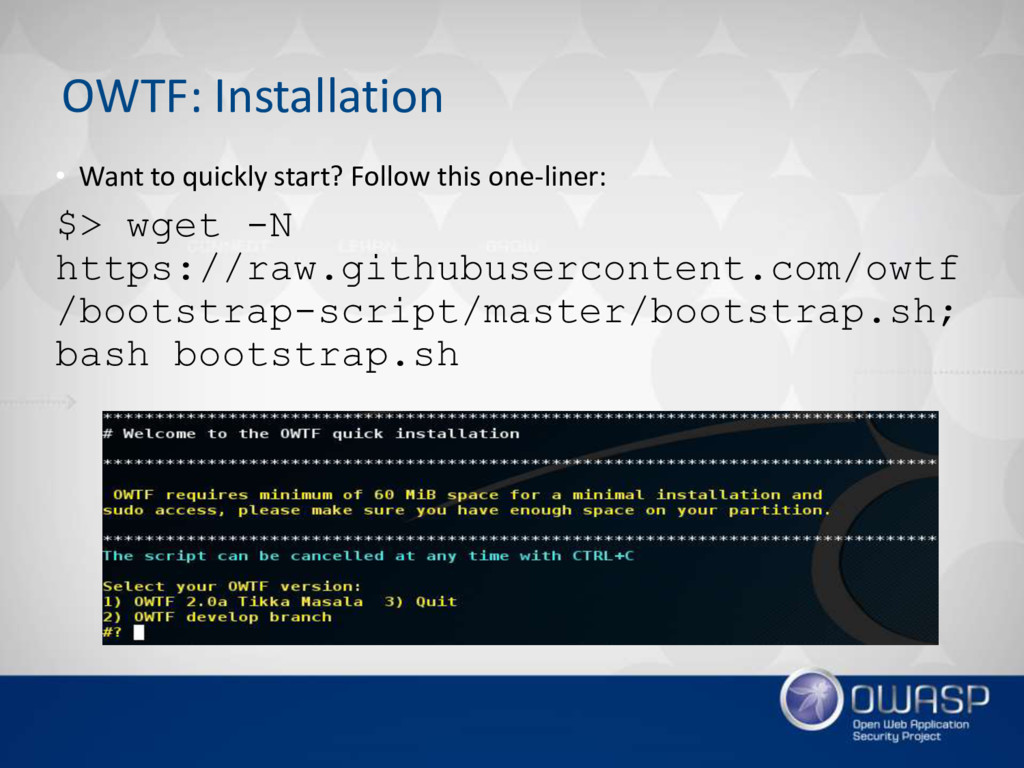
• Want to quickly start? Follow this one-liner: $> wget
-N https://raw.githubusercontent.com/owtf /bootstrap-script/master/bootstrap.sh; bash bootstrap.sh OWTF: Installation -
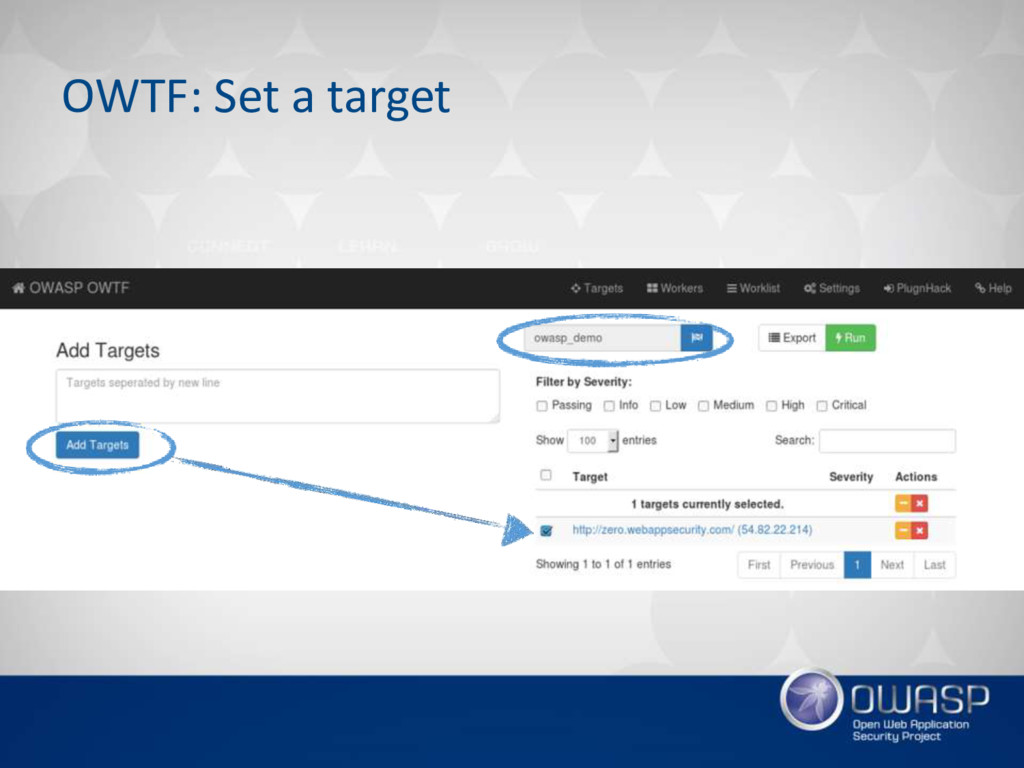
sends normal traffic to target active vulnerability probing probing services
(e.g. FTP/SMB ) assist manual testing searches on HTTP transactions test via 3rd parties (no traffic to target) Testing web apps Testing network services OWTF: Choose plugins and run! -
OWTF: Useful links • Project: https://www.owasp.org/index.php/OWASP_OWTF • Documentation: http://docs.owtf.org/en/latest/ •
Online passive scanner: https://owtf.github.io/online-passive-scanner -
• Use OWASP WebGoat to provide efficient security trainings in
your company. • Use OWASP OWTF to automate your penetration testing tasks. It allows you for easy test’s output analyse and create reports in a fast way. Summary -
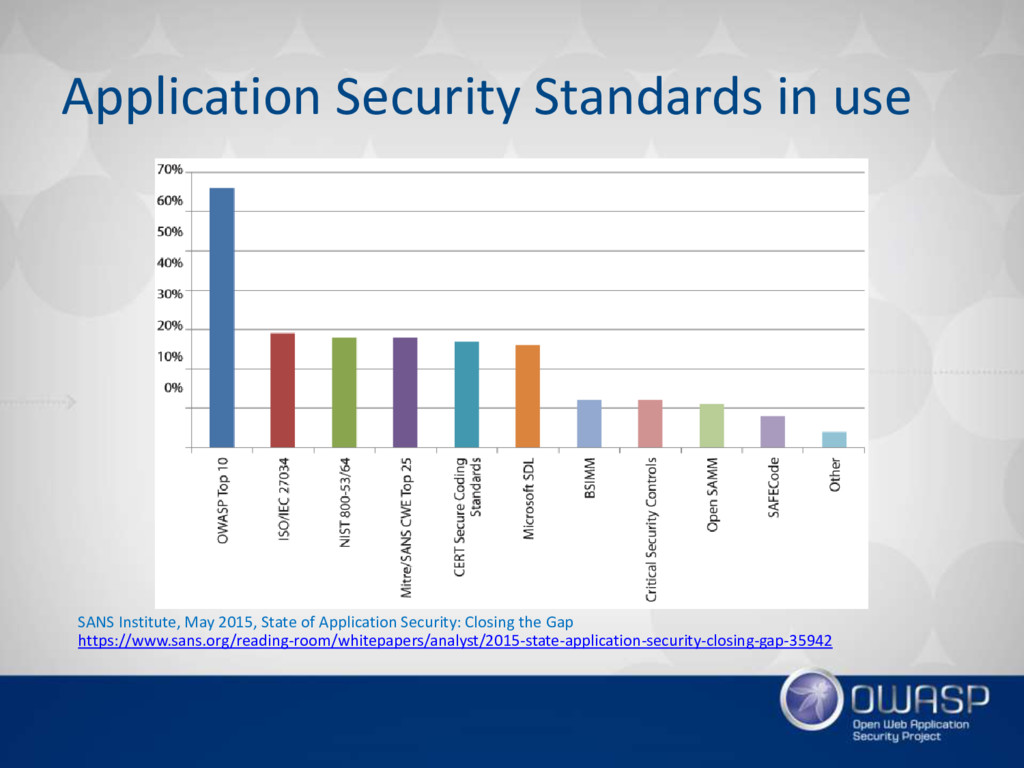
SANS Institute, May 2015, State of Application Security: Closing the
Gap https://www.sans.org/reading-room/whitepapers/analyst/2015-state-application-security-closing-gap-35942 Application Security Standards in use -
OWASP Application Security Verification Standard (ASVS) is a list of
application security requirements or tests that can be used by architects, developers, testers, security professionals, and even consumers to define what a secure application is. In short -
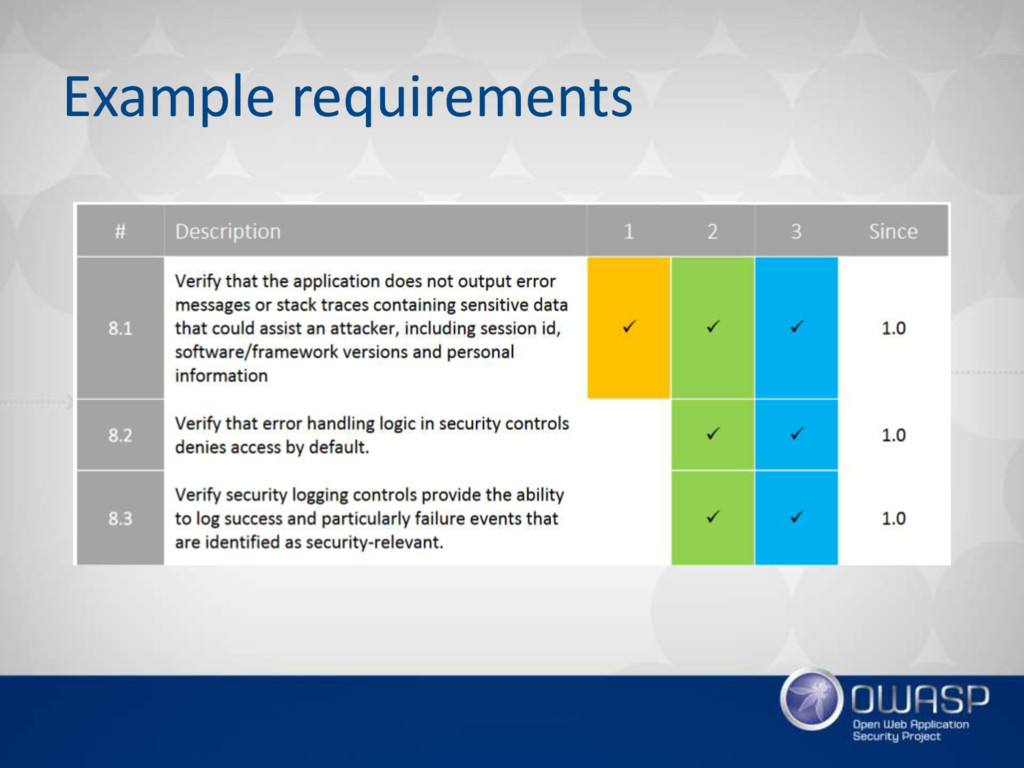
Example requirements • Architecture and design • Input handling •
Data protection • Session management • Error handling • Business logic • Configuration • Web services • 19 sections in total • Every chapter has control objective, reqs and references -
First introduced: June 2008 ASVS v1.0: 2009 ASVS v2.0: 2014
ASVS v3.0: 2015 Current version: v3.0.1 (July 2016) History -
Idea behind • Use as a metric - provide application
developers and application owners with a yardstick with which to assess the degree of trust that can be placed in their Web applications • Use as guidance - provide guidance to security control developers as to what to build into security controls in order to satisfy application security requirements • Use during procurement - provide a basis for specifying application security verification requirements in contracts -
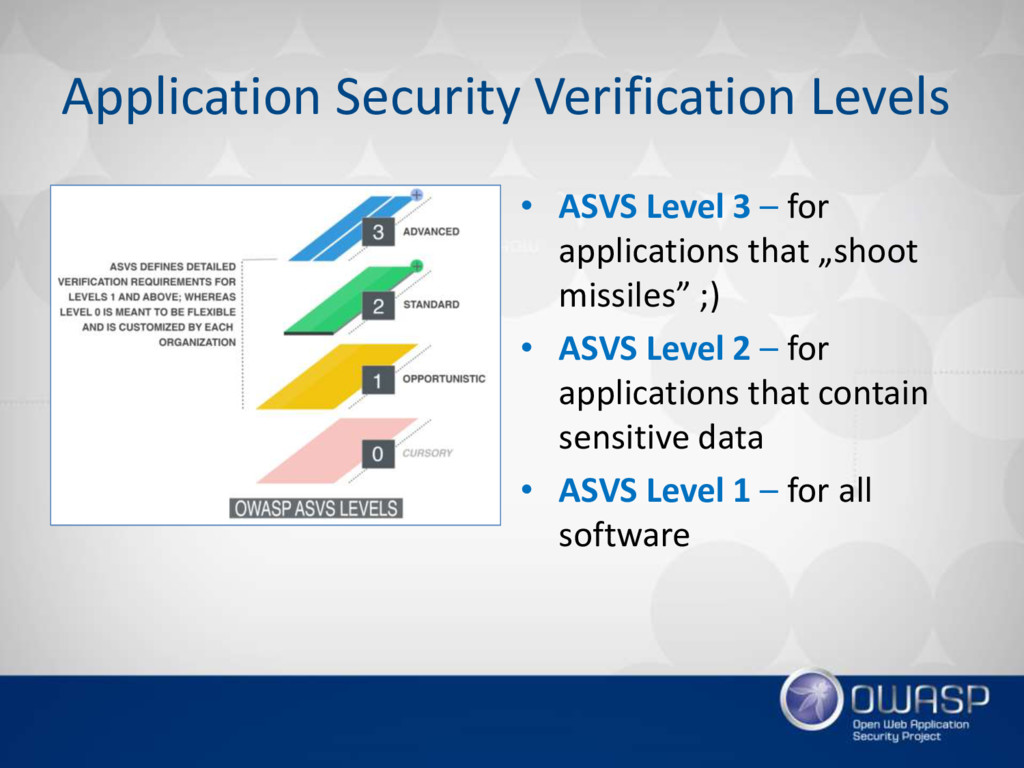
Application Security Verification Levels • ASVS Level 3 – for
applications that „shoot missiles” ;) • ASVS Level 2 – for applications that contain sensitive data • ASVS Level 1 – for all software -
Benefits for you • Helps you to develop and maintain
secure applications • Contains clear and ready-to-use high level checklists and use cases • Allows you as well as security services, vendors, and consumers to align requirements and offerings -
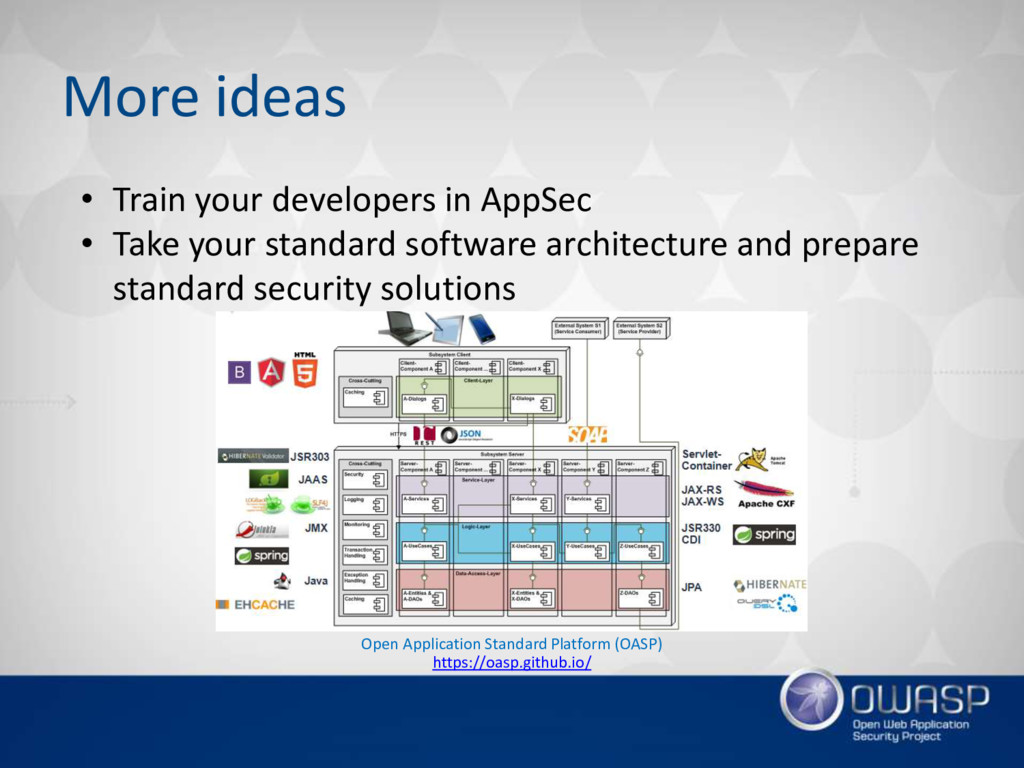
More ideas • Train your developers in AppSec • Take
your standard software architecture and prepare standard security solutions Open Application Standard Platform (OASP) https://oasp.github.io/ -
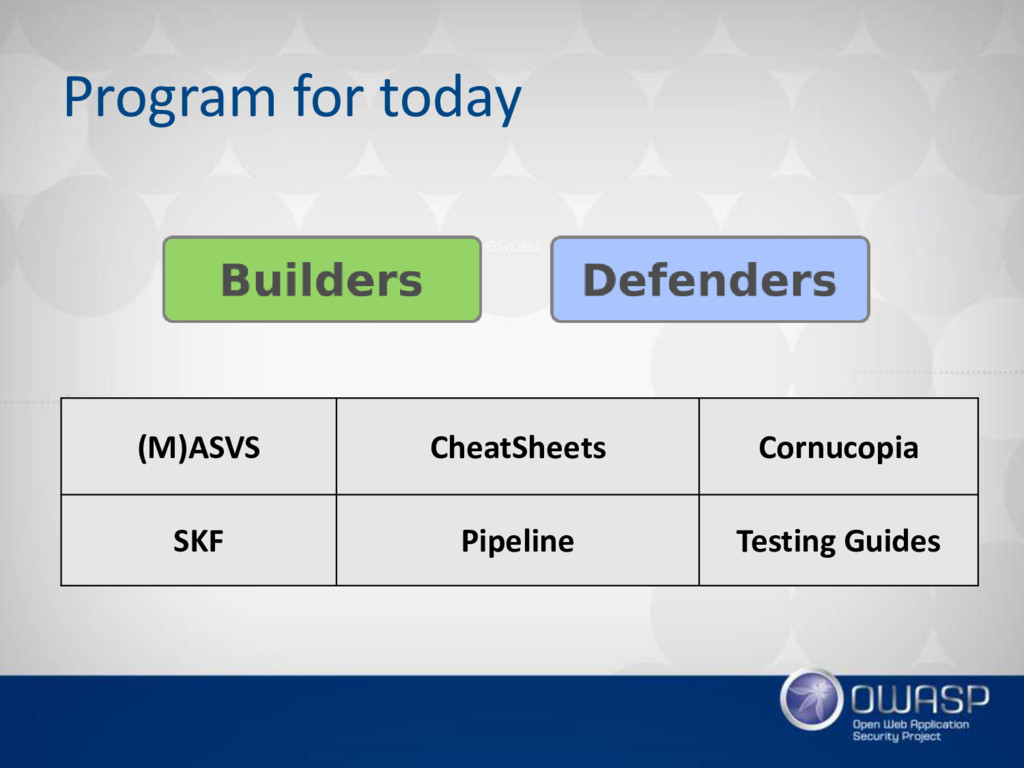
Projects based on ASVS • Secure Knowledge Framework - training
developers in writing secure code and providing a knowledge base of secure design patterns • Zed Attack Proxy - easy to use integrated penetration testing tool for finding vulnerabilities in web applications, both automatically and manually • Cornucopia - mechanism in the form of a card game to assist software development teams identify security requirements in Agile, conventional and formal development processes. It is language, platform and technology agnostic. -
Useful links • Project: https://www.owasp.org/index.php/Category:OWASP_Application_Sec urity_Verification_Standard_Project • Excel checklist: https://github.com/OWASP/ASVS/blob/master/ASVS-excel-v3.0.1.xlsx
• OWASP ASVS mailing list https://lists.owasp.org/mailman/listinfo/owasp-application-security- verification-standard -
In short • There is a significant difference between security
assurance of web and mobile applications • MASVS is to mobiles, what ASVS is to web • The project is work in progress (v0.9.2 is currently available) -
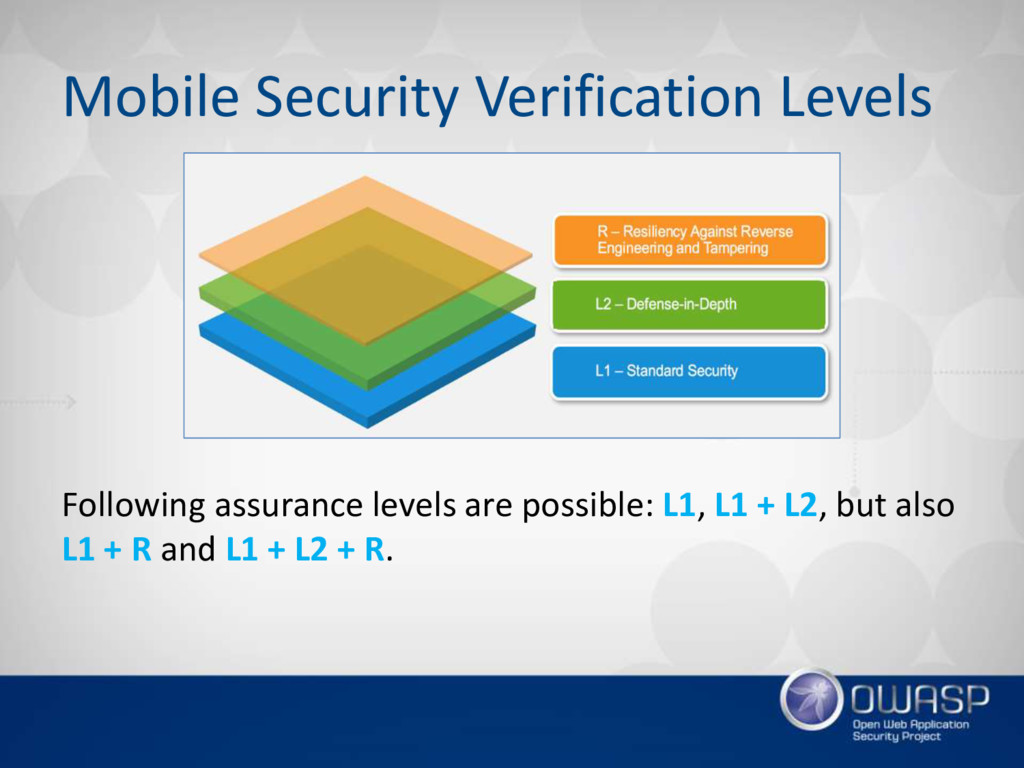
Mobile Security Verification Levels Following assurance levels are possible: L1,
L1 + L2, but also L1 + R and L1 + L2 + R. -
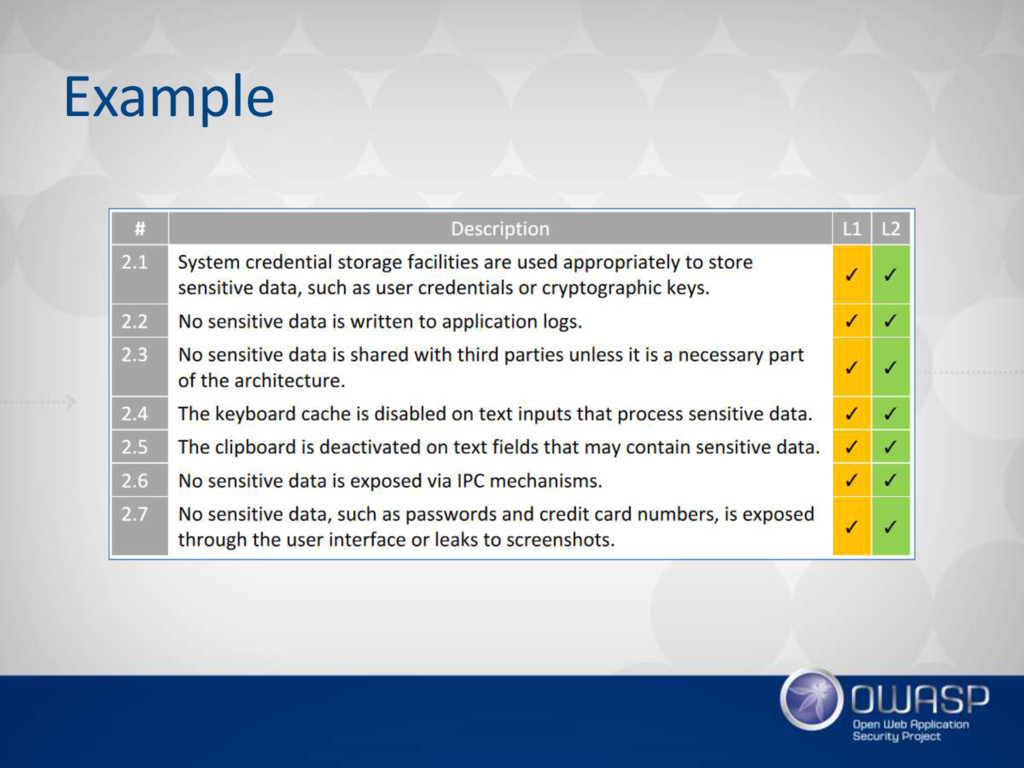
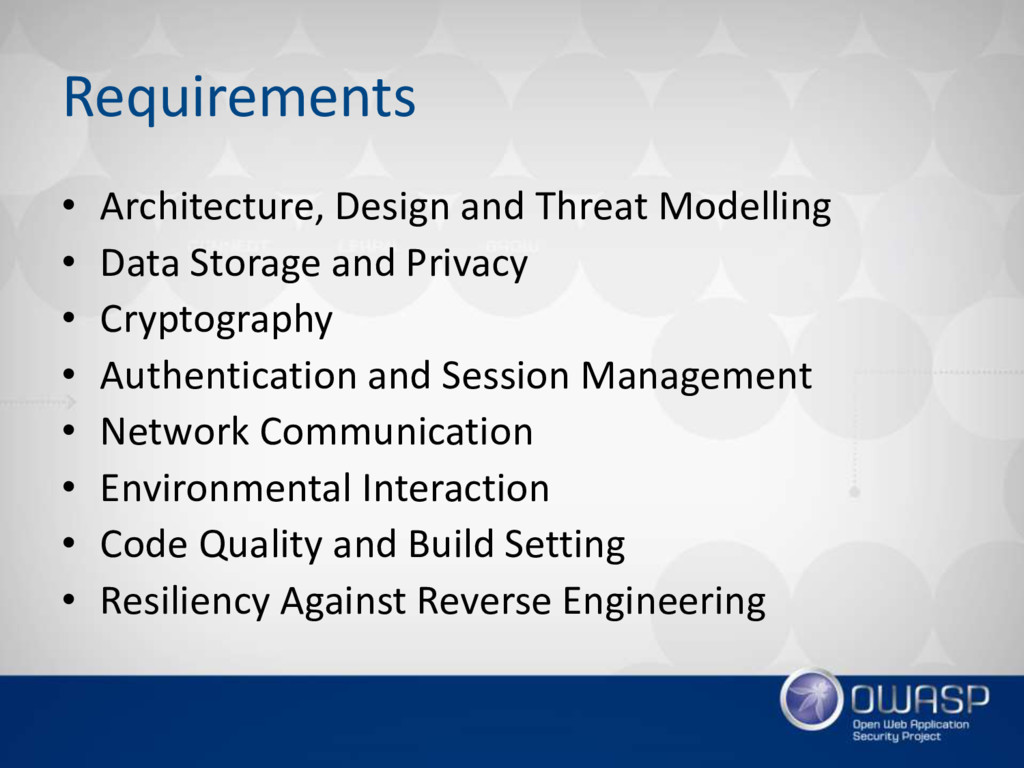
Requirements • Architecture, Design and Threat Modelling • Data Storage
and Privacy • Cryptography • Authentication and Session Management • Network Communication • Environmental Interaction • Code Quality and Build Setting • Resiliency Against Reverse Engineering -
OWASP Cornucopia is a mechanism in the form of a
card game to assist software development teams identify security requirements in Agile, conventional and formal development processes. It is language, platform and technology agnostic. Cornucopia is based on the concepts and game ideas from Microsoft SDL EoP game and OWASP Secure Coding Practices Guide. OWASP Cornucopia Ecommerce Website Edition is in the current Payment Card Industry Security Standards Council information supplement PCI DSS E-commerce Guidelines v2, January 2013 In short -
Idea behind • Help development teams to identify application security
requirements and develop security-based user stories • Aimed at first place at Agile-based methodologies • Gamification approach to threat modeling -
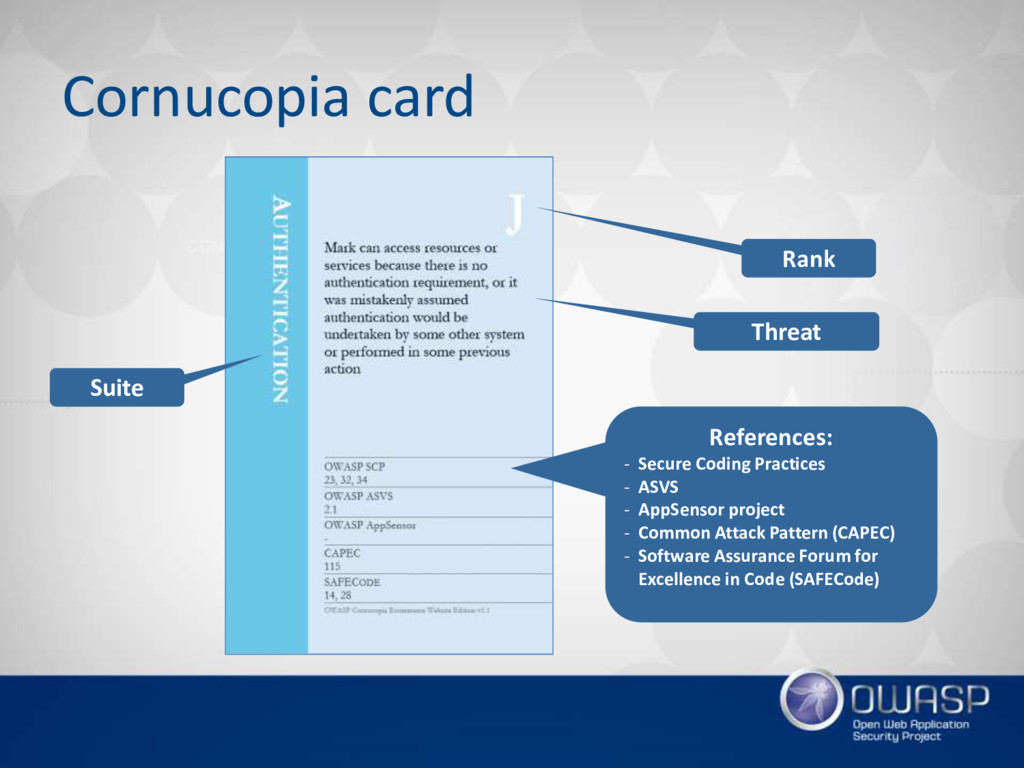
Suite Rank Threat References: - Secure Coding Practices - ASVS
- AppSensor project - Common Attack Pattern (CAPEC) - Software Assurance Forum for Excellence in Code (SAFECode) Cornucopia card -
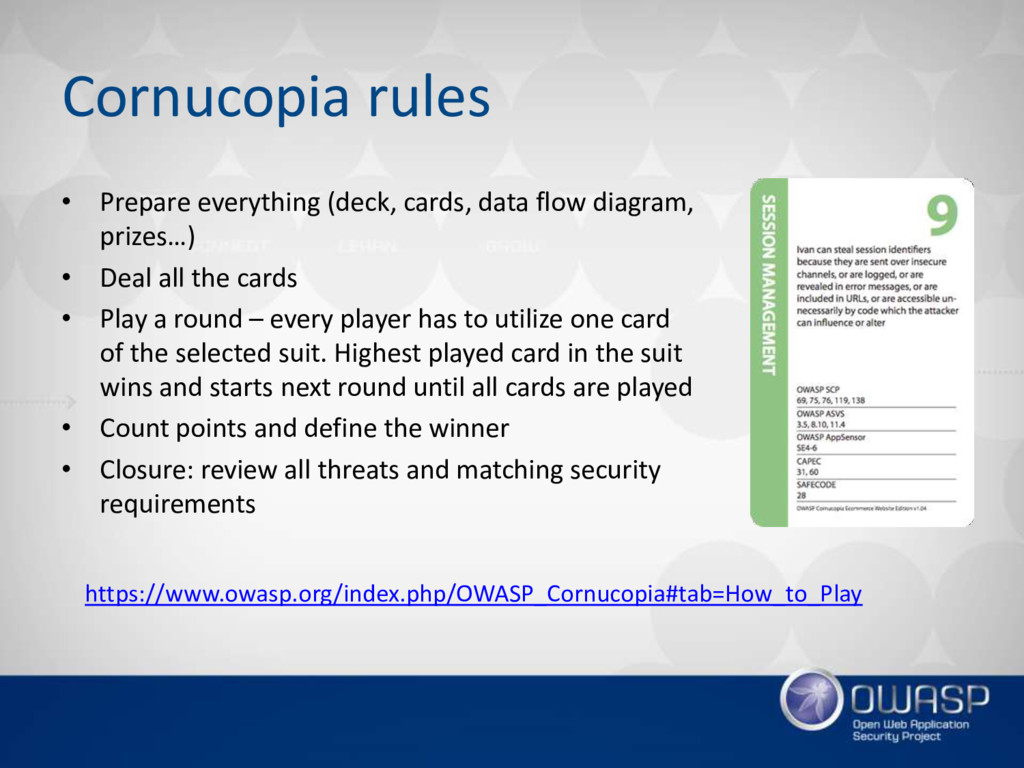
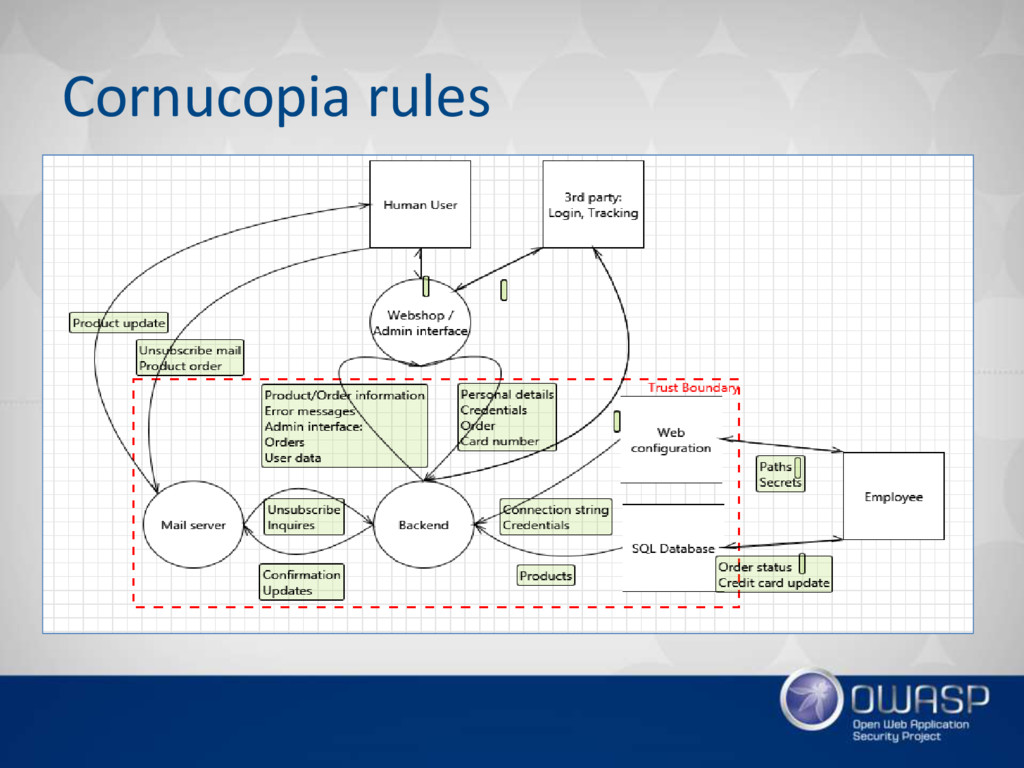
Cornucopia rules • Prepare everything (deck, cards, data flow diagram,
prizes…) • Deal all the cards • Play a round – every player has to utilize one card of the selected suit. Highest played card in the suit wins and starts next round until all cards are played • Count points and define the winner • Closure: review all threats and matching security requirements https://www.owasp.org/index.php/OWASP_Cornucopia#tab=How_to_Play -
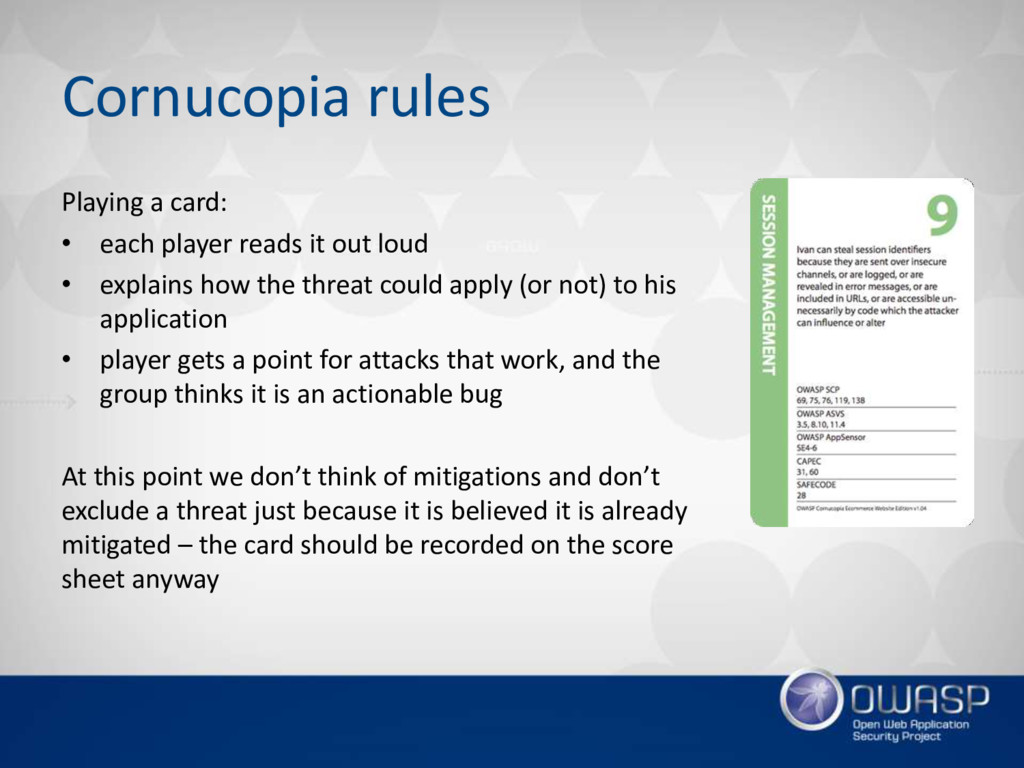
Cornucopia rules Playing a card: • each player reads it
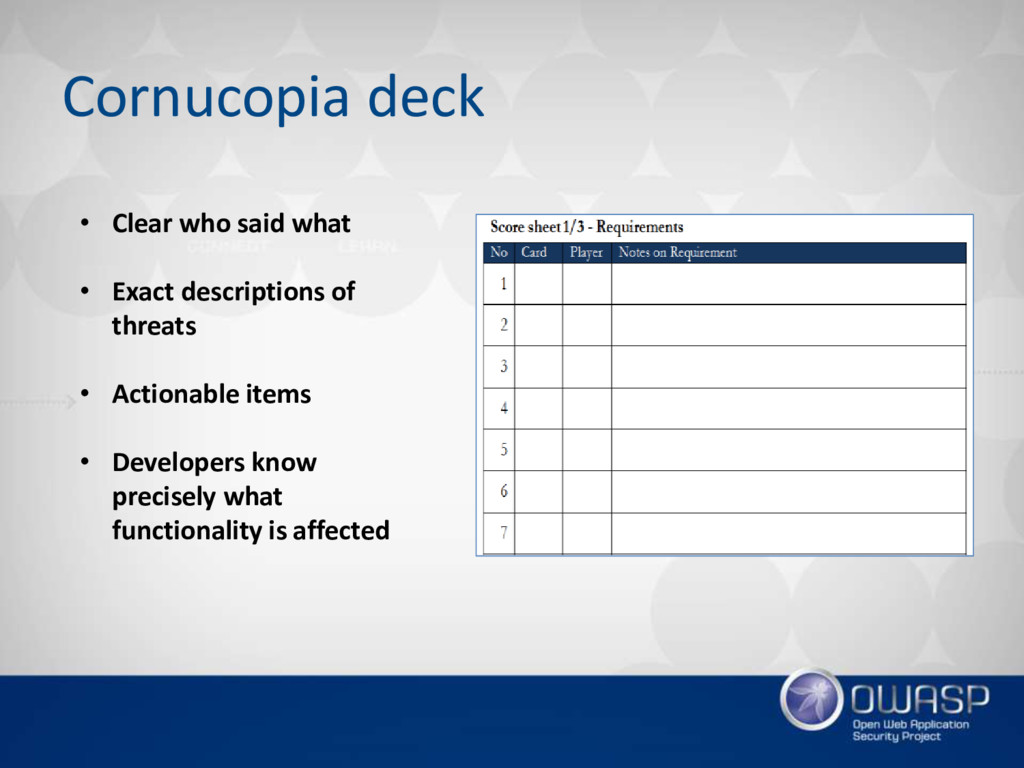
out loud • explains how the threat could apply (or not) to his application • player gets a point for attacks that work, and the group thinks it is an actionable bug At this point we don’t think of mitigations and don’t exclude a threat just because it is believed it is already mitigated – the card should be recorded on the score sheet anyway -
Cornucopia deck • Clear who said what • Exact descriptions
of threats • Actionable items • Developers know precisely what functionality is affected -
Benefits for you • Teaching developers on how to identify
and assess vulnerabilities on every sprint • Training sessions for developers • Raising awareness in application security field in your organization -
Useful links • Project: https://www.owasp.org/index.php/OWASP_Cornucopia • Rules explained on Youtube:
https://www.youtube.com/watch?v=i5Y0akWj31k • Presentation from OWASP EEE (Hungary): http://www.slideshare.net/OWASPEEE/hungary-i-play-jack- of-information-disclosure -
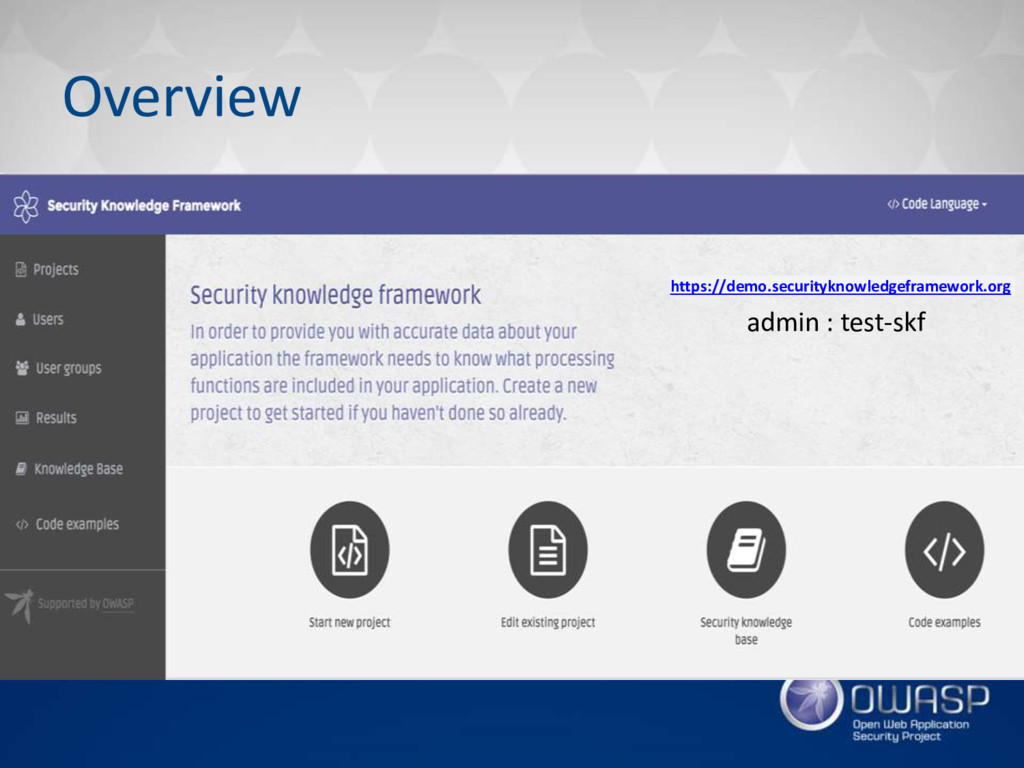
OWASP SKF is a fully open-source Python-Flask expert system web-application
that uses the OWASP Application Security Verification Standard and code examples and can be used to support developers in pre-development (security by design) as well as after code is released (OWASP ASVS Level 1-3) „we decided to develop a proof of concept framework in order to create a guide system available for all developers so they can develop applications secure by design” In short http://secureby.design -
Idea behind The 4 Core usage of SKF: • Security
Requirements ASVS for development and third party vendor applications • Security knowledge reference (code examples/ knowledge base items) • Security is part of design with the pre-development functionality in SKF • Security post-development functionality in SKF for verification with the ASVS -
Installation Super-easy! Supported ways to install it: • Automated installation
with Chef • AWS by using CloudFormation • … or manually as you would do with any other Python project: sudo pip install owasp-skf https://github.com/blabla1337/skf-flask#installing -
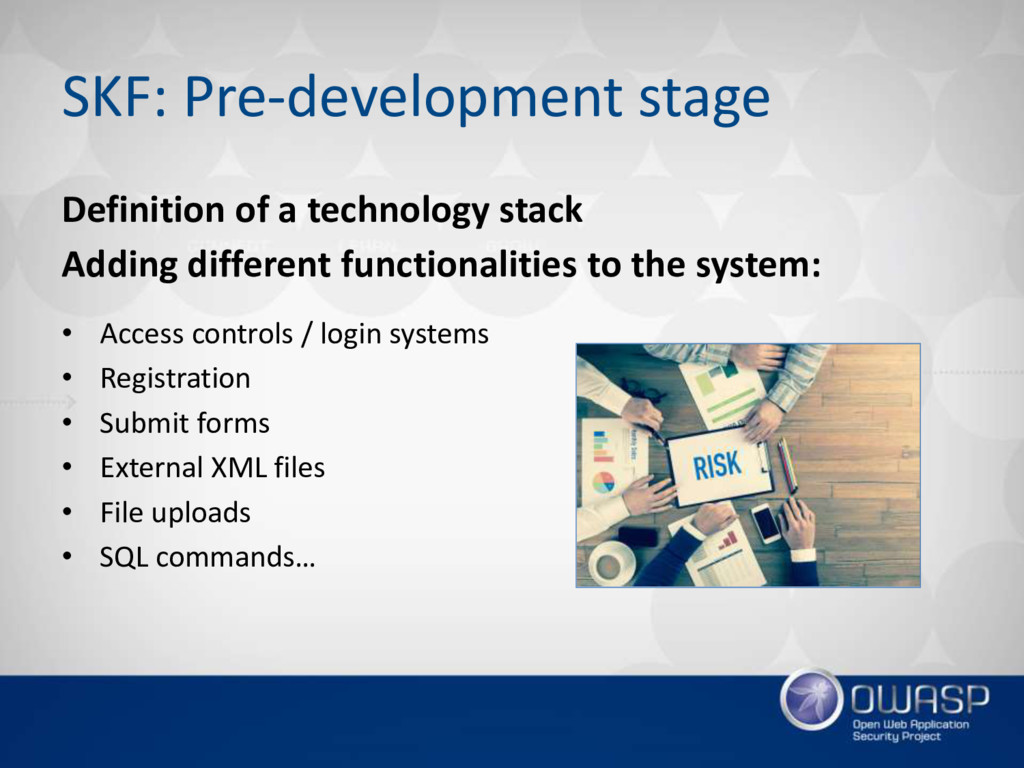
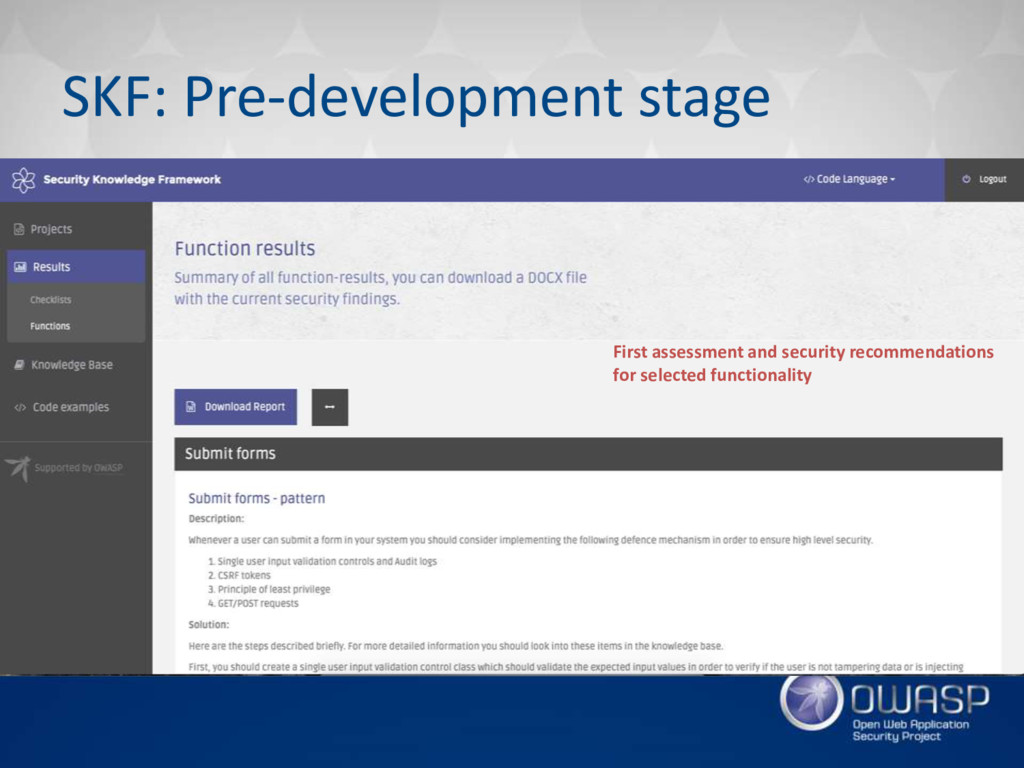
SKF: Pre-development stage Definition of a technology stack Adding different
functionalities to the system: • Access controls / login systems • Registration • Submit forms • External XML files • File uploads • SQL commands… -
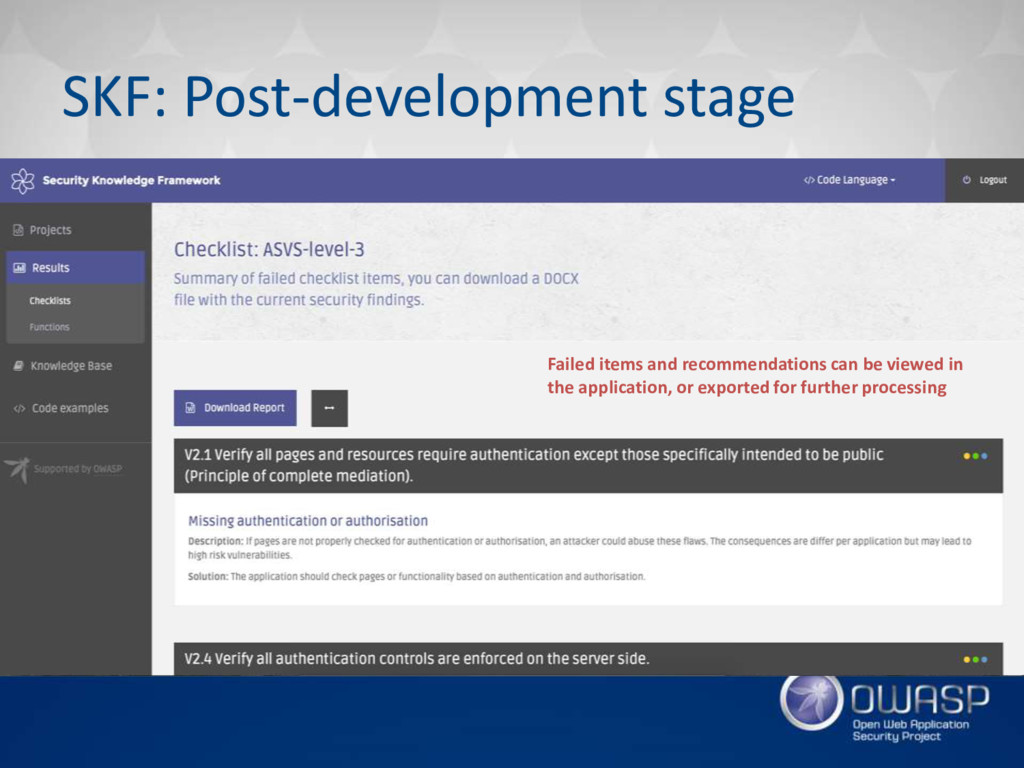
SKF: Post-development stage • Double-check your app by means of
pre-defined or custom checklists • ASVS-based checklists for different levels of criticality of the application are auto-generated after pre- development stage! • After providing answers to clear and simple questions, reports with failed items are ready to be downloaded and prioritized -
SKF: Post-development stage Failed items and recommendations can be viewed
in the application, or exported for further processing -
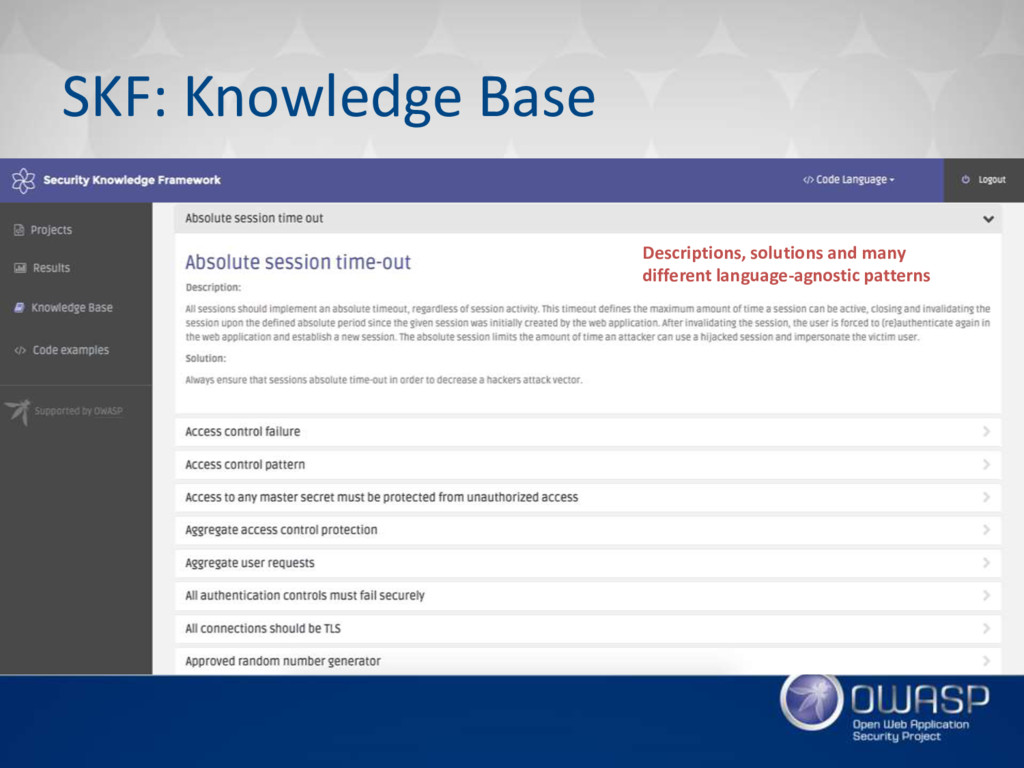
SKF: Knowledge Base • „Use info, do not get hacked,
profit!” • Multiple options of secure design patterns with examples • Gives a good understanding for developers not only about what to fix but also why to do so -
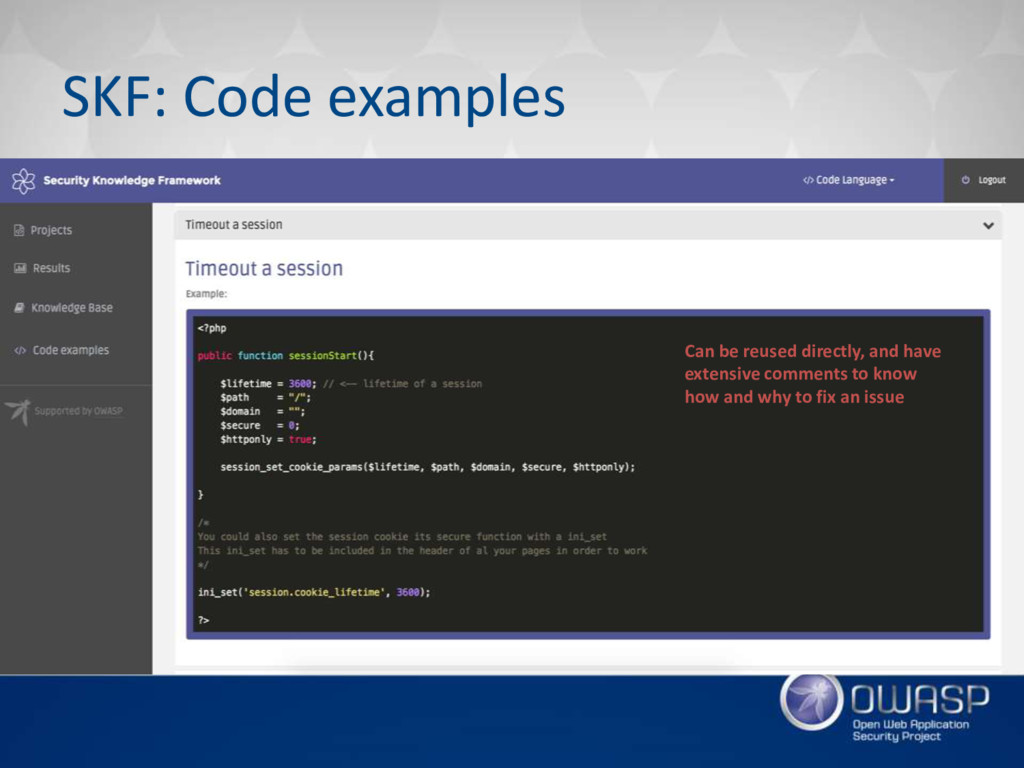
SKF: Code examples • We were talking about generic secure
patterns so far • Code examples with extensive comments provide ready-to-use solutions on how to do things right! • Currently supported languages: PHP, .NET and Java (soon ☺) -
SKF: Code examples Can be reused directly, and have extensive
comments to know how and why to fix an issue -
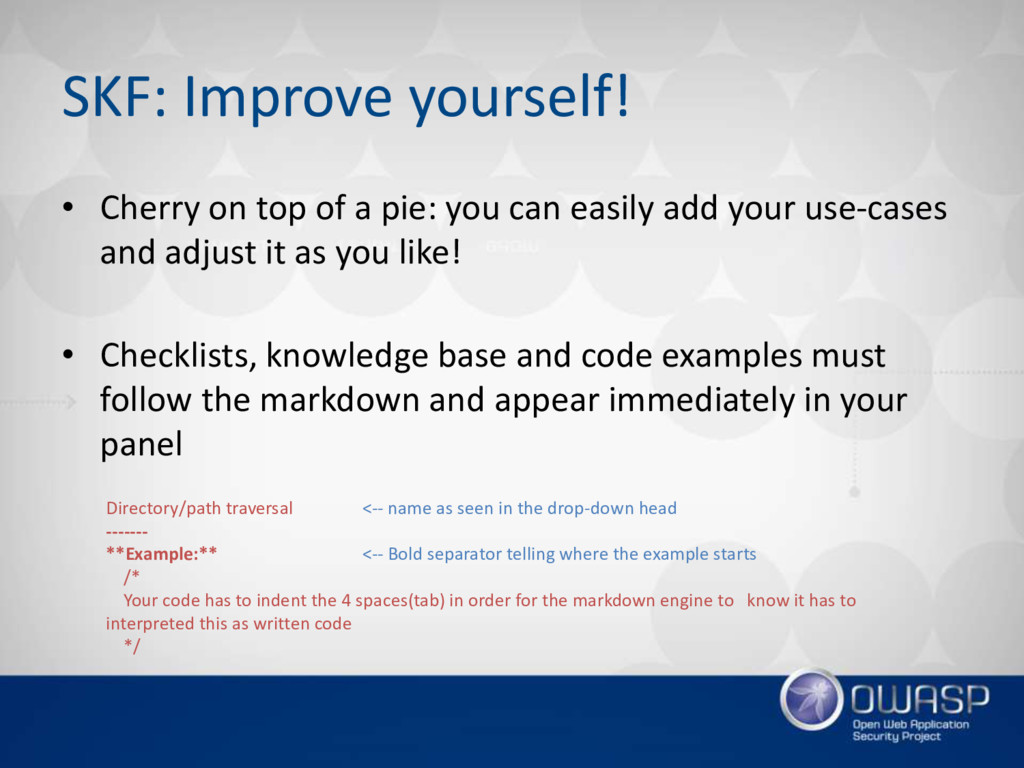
SKF: Improve yourself! • Cherry on top of a pie:
you can easily add your use-cases and adjust it as you like! • Checklists, knowledge base and code examples must follow the markdown and appear immediately in your panel Directory/path traversal <-- name as seen in the drop-down head ------- **Example:** <-- Bold separator telling where the example starts /* Your code has to indent the 4 spaces(tab) in order for the markdown engine to know it has to interpreted this as written code */ -
Benefits for you • Guide to secure programming • Secuity
by design, not implementing afterwards • Security awareness • Will inform about threats even before one wrote a single line of code • Central place for security reference • Provides information applicable for specific needs on the spot -
Useful links • Project: http://secureby.design • Source code: https://github.com/blabla1337/skf-flask •
SKF workshop (DevOpsDays 2015): https://www.owasp.org/images/5/54/Skf-design- workshop.pptx.pdf -
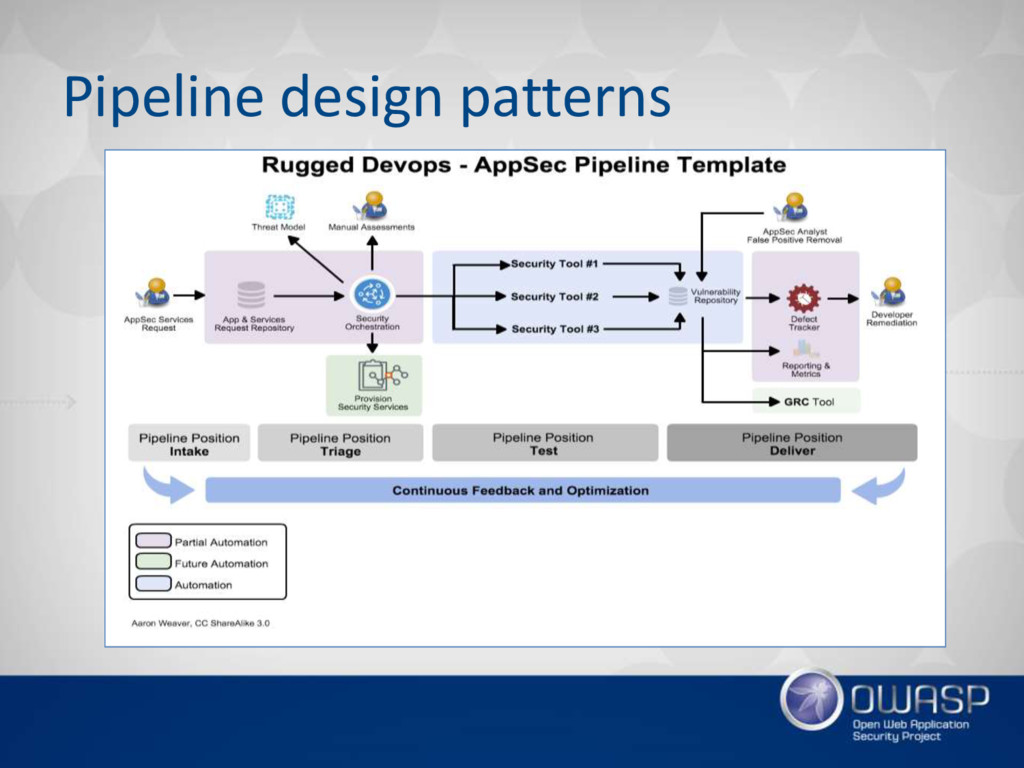
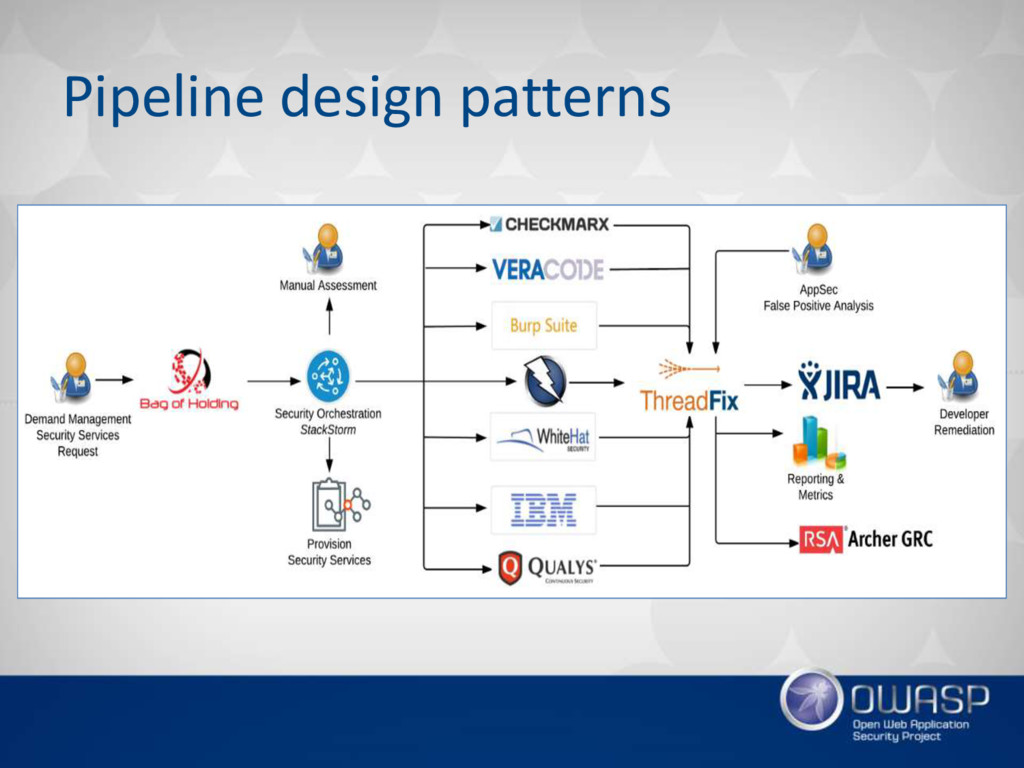
The AppSec pipeline project • Place to gather together information,
techniques and tools to create your own AppSec pipeline • Right now: AppSec pipeline patterns and tools https://www.owasp.org/index.php/OWASP_AppSec_Pipeline -
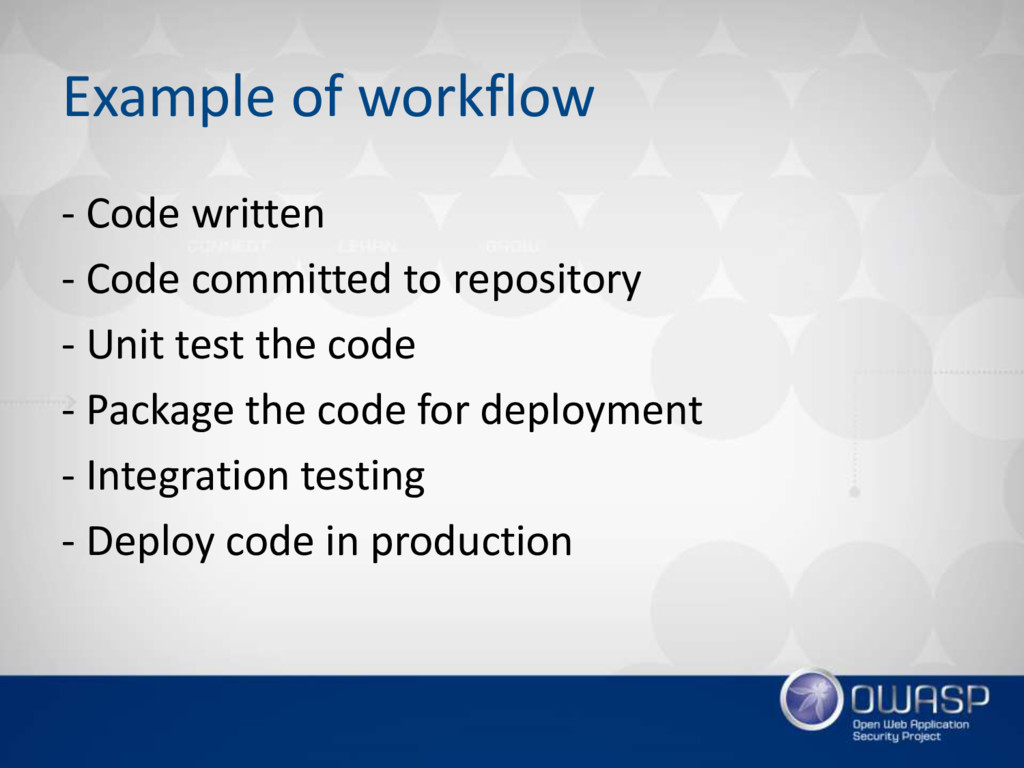
Example of workflow - Code written - Code committed to
repository - Unit test the code - Package the code for deployment - Integration testing - Deploy code in production -
Security tools evaluation criteria • API is the first •
Pipeline position • Cloud scalable • Runs as a service • Client libraries • CI/CD plugins -
What is OWASP ZAP? • Webapp security testing tool •
Free and open source • Written in Java → cross platform https://www.owasp.org/index.php/ZAP -
OWASP ZAP Features • GUI, headless and REST API •
Intercepting proxy • Classic and AJAX spiders • Passive and active scanning • … and of course can be extended via addons! -
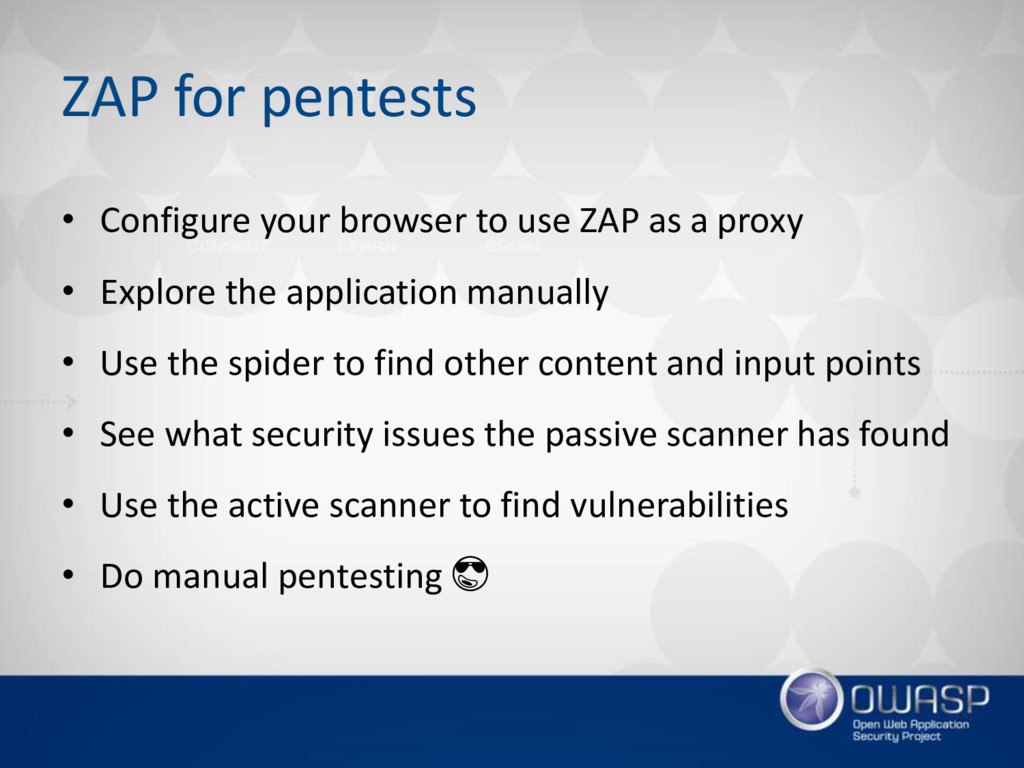
ZAP for pentests • Configure your browser to use ZAP
as a proxy • Explore the application manually • Use the spider to find other content and input points • See what security issues the passive scanner has found • Use the active scanner to find vulnerabilities • Do manual pentesting -
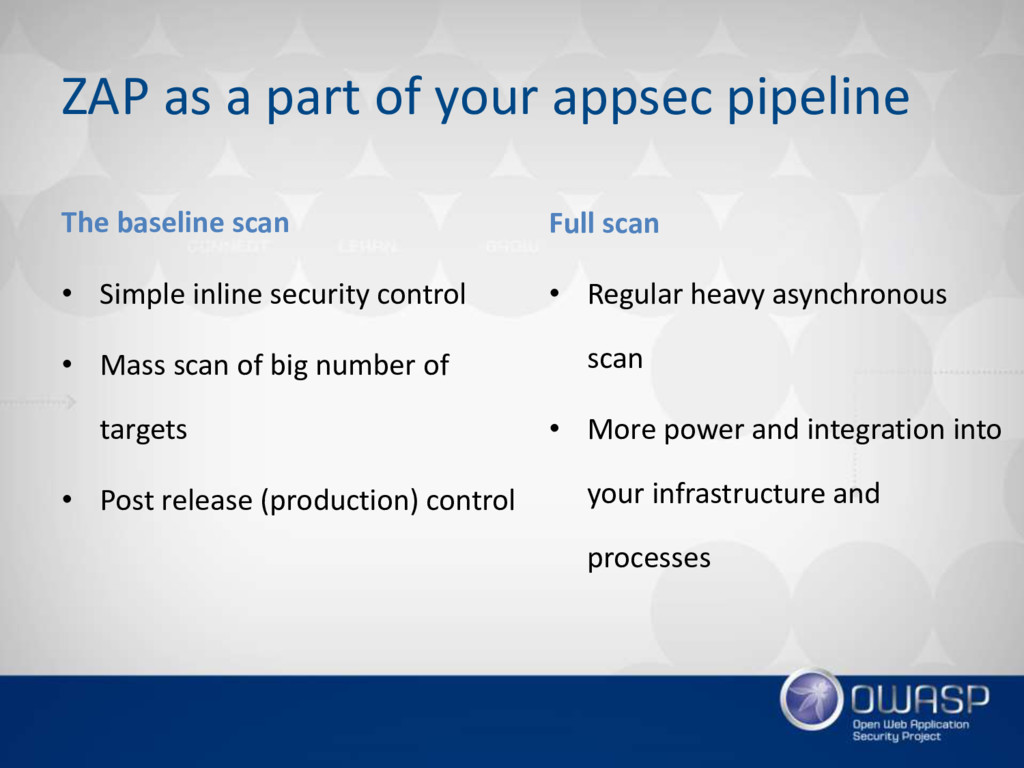
ZAP as a part of your appsec pipeline The baseline
scan • Simple inline security control • Mass scan of big number of targets • Post release (production) control Full scan • Regular heavy asynchronous scan • More power and integration into your infrastructure and processes -
The baseline scan • Uses Docker • Only passive scanning
• Time limited spider of target • By default warns on all issues: – Missing / incorrect security headers like CSP – Cookie problems – Information / error disclosure – Missing CSRF tokens etc. -
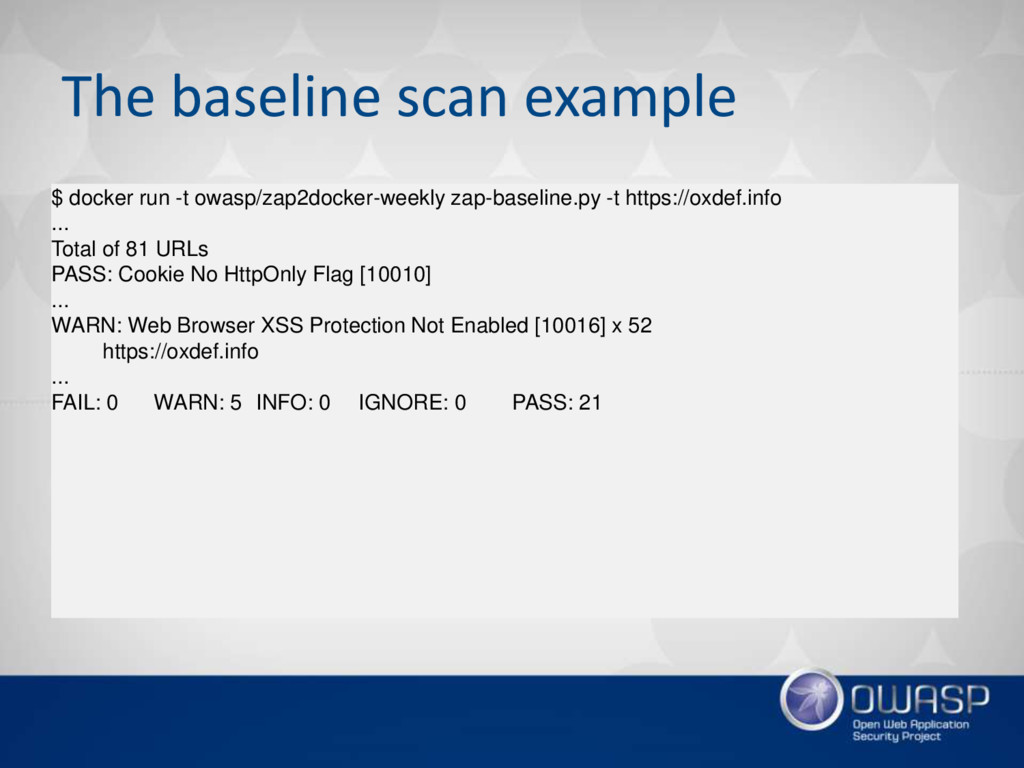
The baseline scan example $ docker run -t owasp/zap2docker-weekly zap-baseline.py
-t https://oxdef.info ... Total of 81 URLs PASS: Cookie No HttpOnly Flag [10010] ... WARN: Web Browser XSS Protection Not Enabled [10016] x 52 https://oxdef.info ... FAIL: 0 WARN: 5 INFO: 0 IGNORE: 0 PASS: 21 -
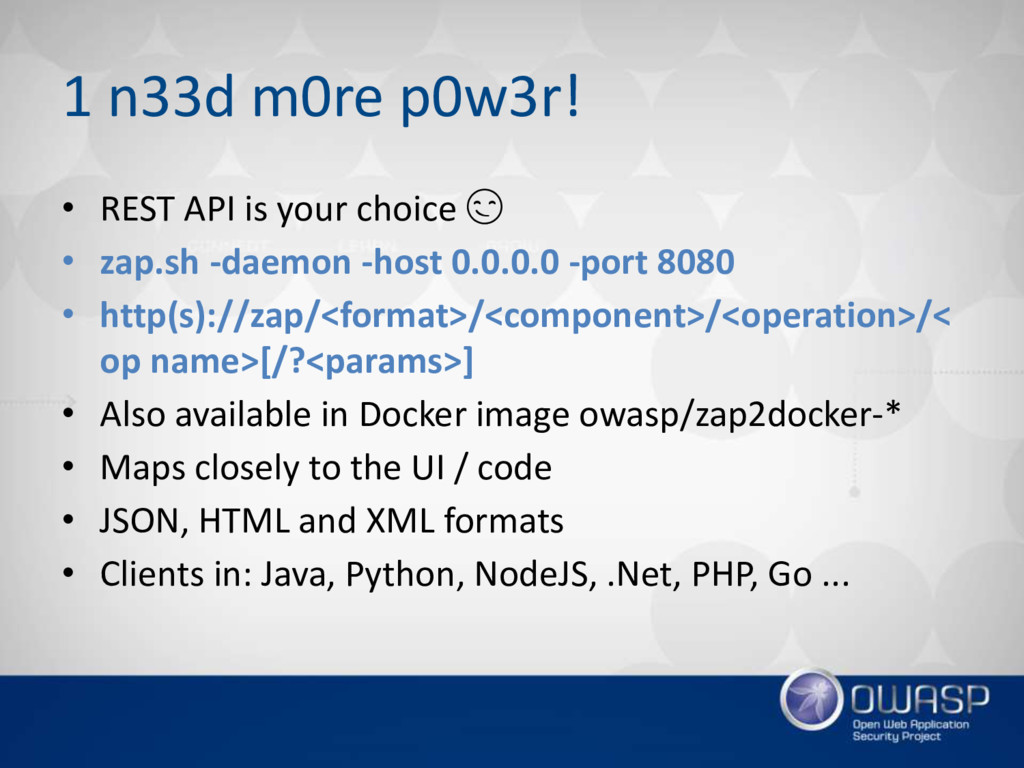
1 n33d m0re p0w3r! • REST API is your choice
• zap.sh -daemon -host 0.0.0.0 -port 8080 • http(s)://zap/<format>/<component>/<operation>/< op name>[/?<params>] • Also available in Docker image owasp/zap2docker-* • Maps closely to the UI / code • JSON, HTML and XML formats • Clients in: Java, Python, NodeJS, .Net, PHP, Go ... -
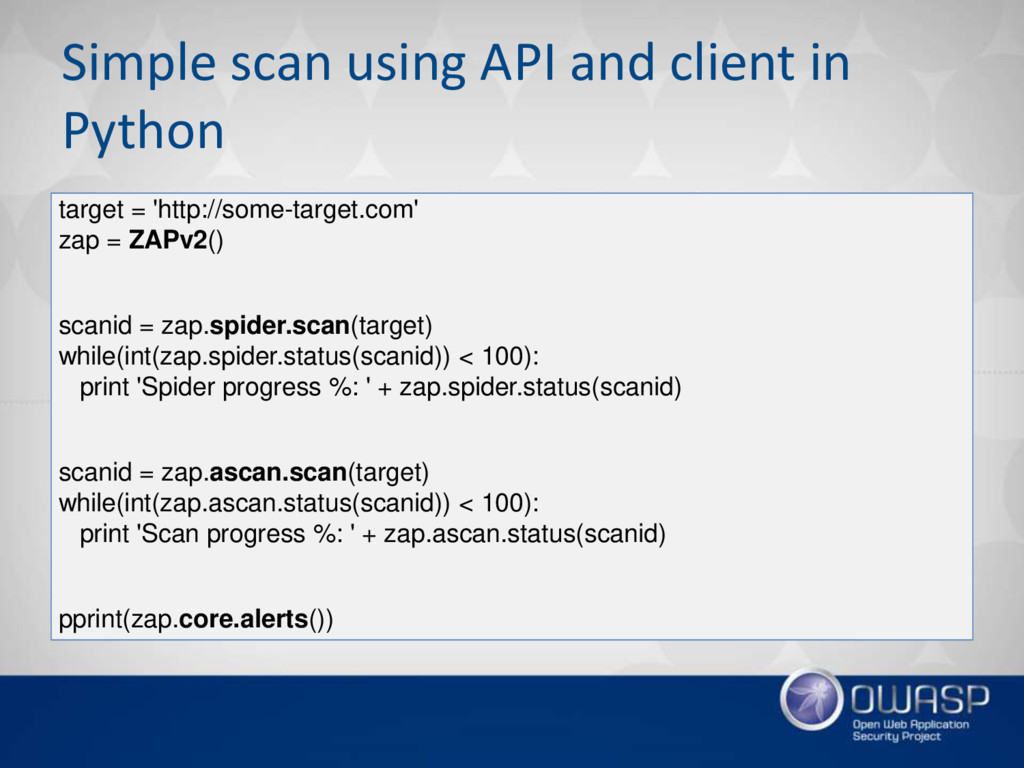
Simple scan using API and client in Python target =
'http://some-target.com' zap = ZAPv2() scanid = zap.spider.scan(target) while(int(zap.spider.status(scanid)) < 100): print 'Spider progress %: ' + zap.spider.status(scanid) scanid = zap.ascan.scan(target) while(int(zap.ascan.status(scanid)) < 100): print 'Scan progress %: ' + zap.ascan.status(scanid) pprint(zap.core.alerts()) -
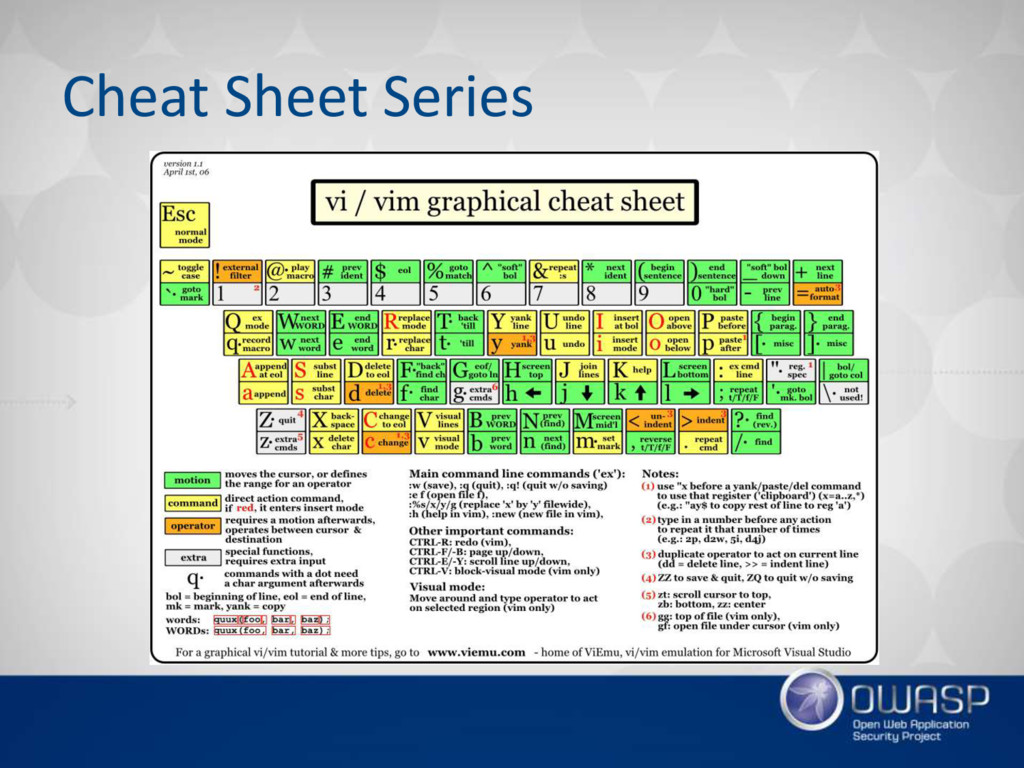
Cheat Sheet Series • «The OWASP Cheat Sheet Series was
created to provide a concise collection of high value information on specific web application security topics» • You can browse it online or get as PDF book • Mostly fresh and actual topics https://www.owasp.org/index.php/Cheat_Sheets -
3rd party JavaScript management The invocation of 3rd party JS
code in a web application requires consideration for 3 risks in particular: • The loss of control over changes to the client application • The execution of arbitrary code on client systems • The disclosure or leakage of sensitive information to 3rd parties https://www.owasp.org/index.php/3rd_Party_Javascript_ Management_Cheat_Sheet -
XSS Prevention RULE #3 - JavaScript Escape Before Inserting Untrusted
Data into JavaScript Data Values Except for alphanumeric characters, escape all characters less than 256 with the \xHH format to prevent switching out of the data value into the script context or into another attribute. https://www.owasp.org/index.php/XSS_(Cross_Site_Scrip ting)_Prevention_Cheat_Sheet -
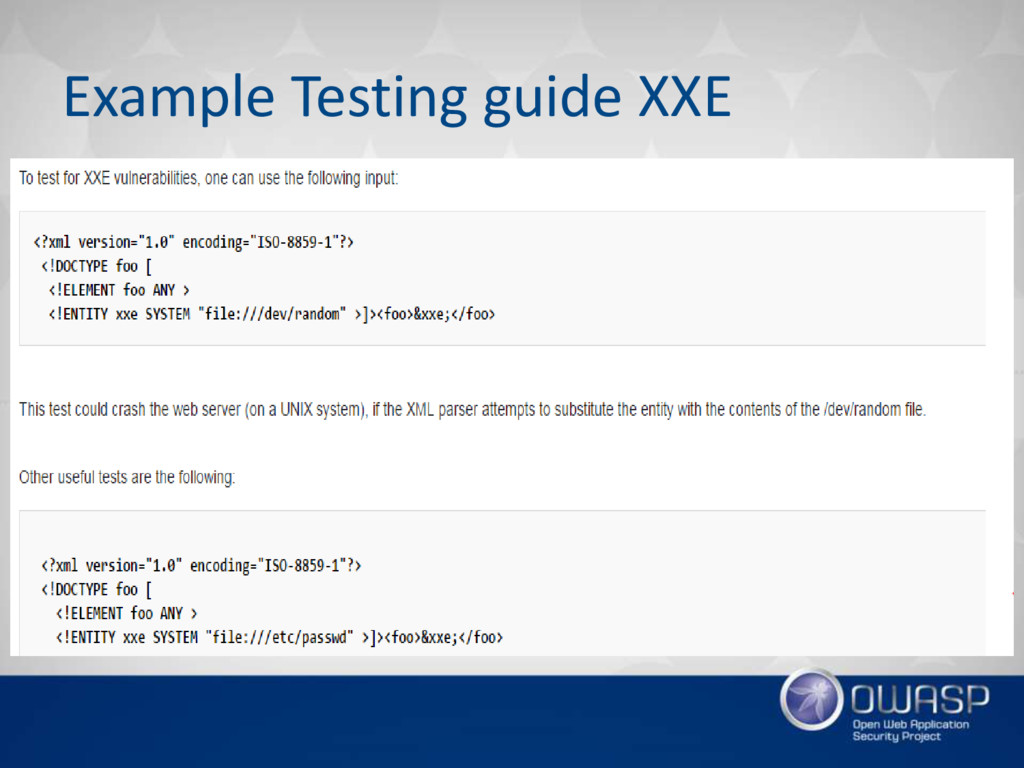
XXE Prevention Libxml2: the Enum xmlParserOption should not have the
following options defined: • XML_PARSE_NOENT: Expands entities and substitutes them with replacement text • XML_PARSE_DTDLOAD: Load the external DT https://www.owasp.org/index.php/XML_External_Entity_ (XXE)_Prevention_Cheat_Sheet -
Featured cheat sheets • Clickjacking Defense • Cross-Site Request Forgery
(CSRF) Prevention • Deserialization • DOM based XSS Prevention • REST Security • Virtual Patching -
Summary • OWASP AppSec Pipeline helps you with choosing suitable
tools and building your own AppSec pipeline • OWASP ZAP is one of such tools. Using it you can make manual pentest of web app or automate web app security testing in SDL • OWASP Cheat Sheets helps you in specific areas of application security -
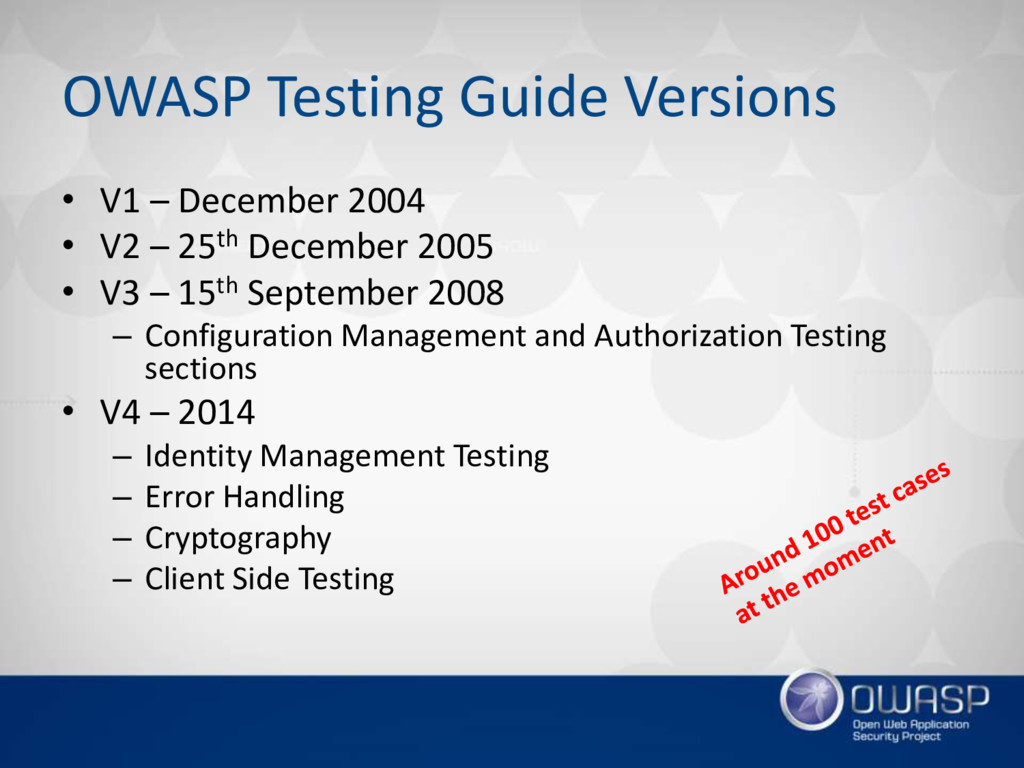
OWASP Testing Guide Versions • V1 – December 2004 •
V2 – 25th December 2005 • V3 – 15th September 2008 – Configuration Management and Authorization Testing sections • V4 – 2014 – Identity Management Testing – Error Handling – Cryptography – Client Side Testing -
Purpose • The OWASP Testing Guide includes a "best practice"
penetration testing framework which users can implement in their own organizations and • a "low level" penetration testing guide that describes techniques for testing most common web application and services security issues. -
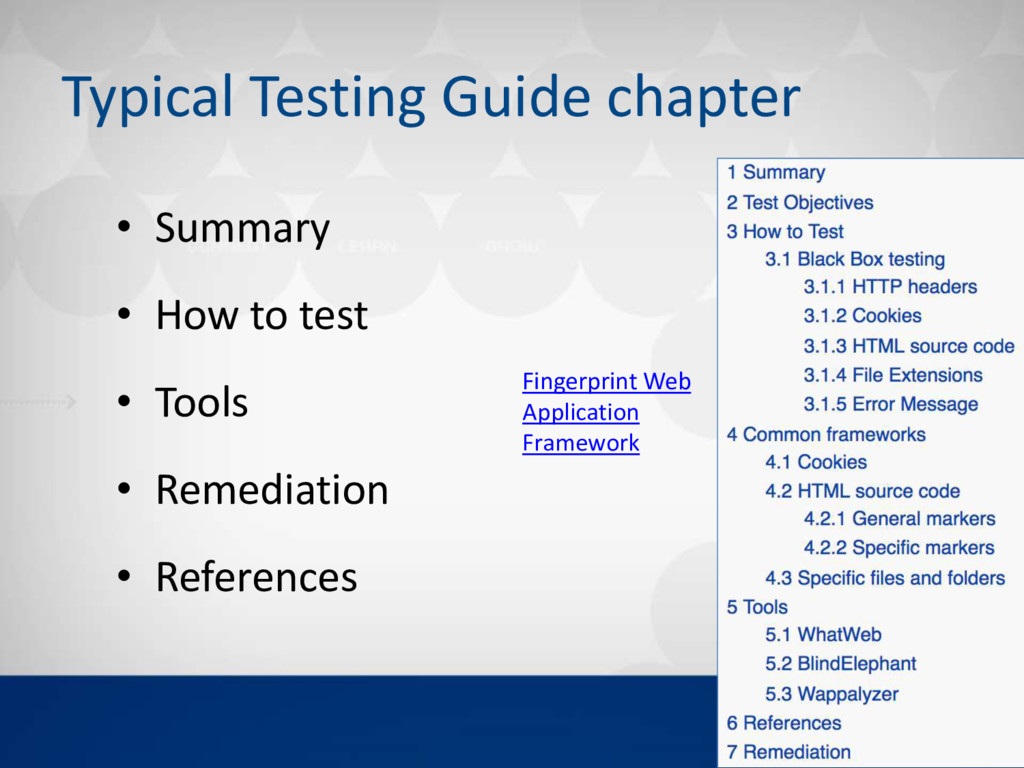
Typical Testing Guide chapter • Summary • How to test
• Tools • Remediation • References Fingerprint Web Application Framework -
Why to test • The steps that need to be
undertaken to build and operate a testing program on web apps. • Effective testing program: – People – Process – Technology • Testing just the technical implementation of an application will not uncover management or operational vulnerabilities that could be present -
When to test • Don’t test software until it has
already been created and is in the deployment phase of its life cycle ineffective and cost-prohibitive practice • One of the best methods to prevent security bugs from appearing in production applications is to improve the SDLC by including security in each of its phases -
Summary • Constant work in progress • Anybody is welcome
to collaborate • Best practice for web penetration tests -
OWASP MSTG Leaders • MSTG was initiated by Milan Singh
Thakur in 2015. The original document was hosted on Google Drive Github • Bernhard Mueller (2016) • Sven Schleier (2016) -
OWASP MSTG • MSTG is a manual for testing the
security of mobile apps. It describes technical processes for verifying the controls listed in the MASVS • MSTG is meant to provide a baseline set of test cases for black-box and white-box security tests, and to help ensure completeness and consistency of the tests -
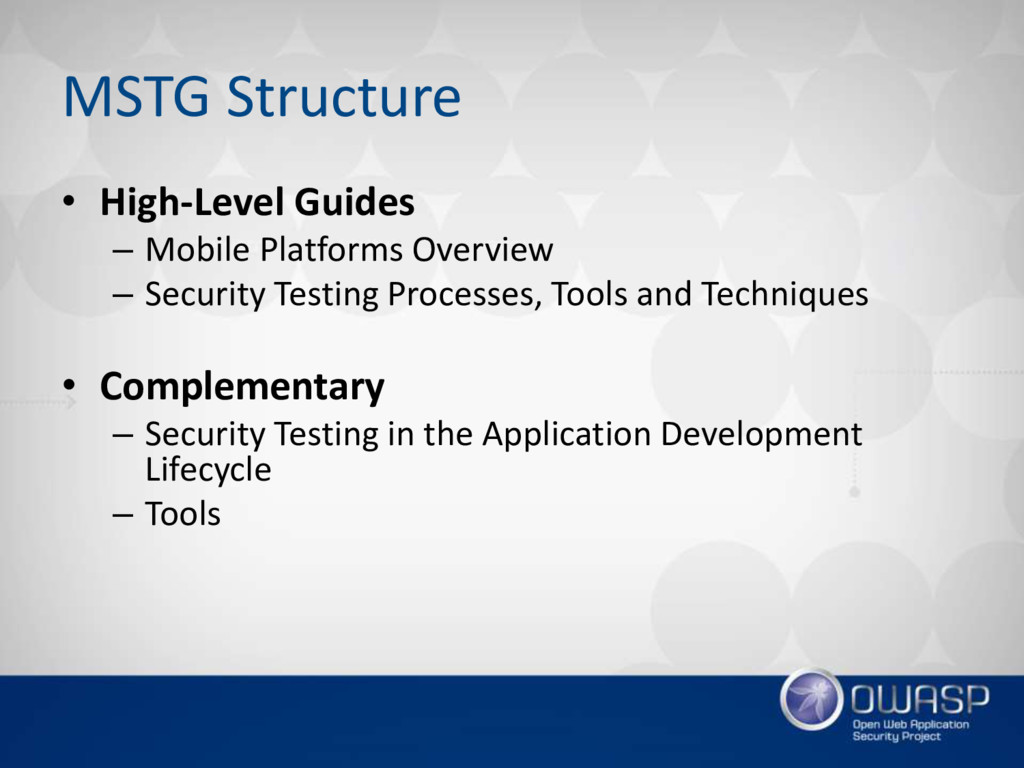
MSTG Structure • High-Level Guides – Mobile Platforms Overview –
Security Testing Processes, Tools and Techniques • Complementary – Security Testing in the Application Development Lifecycle – Tools -
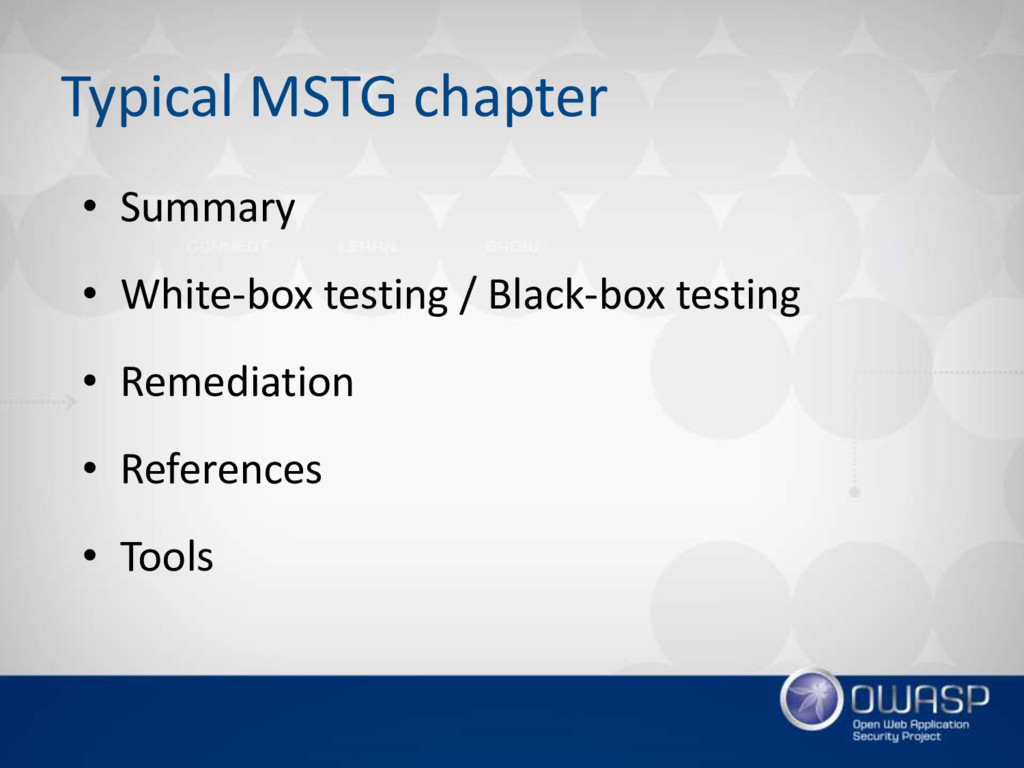
Typical MSTG chapter • Summary • White-box testing / Black-box
testing • Remediation • References • Tools -
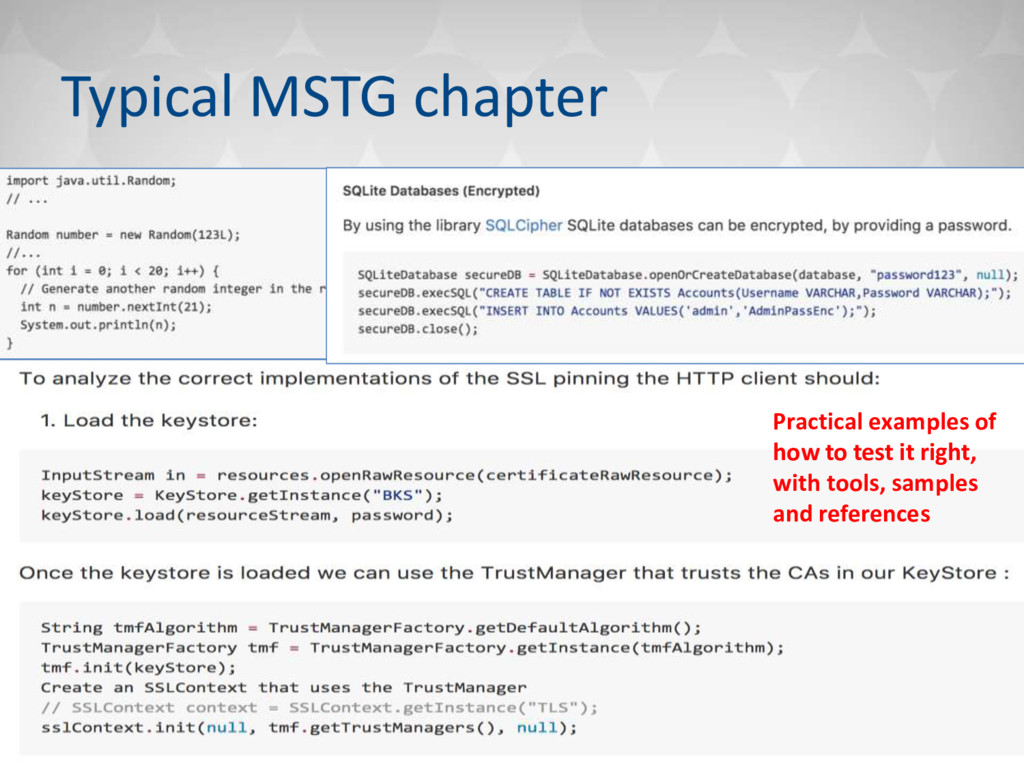
Typical MSTG chapter Practical examples of how to test it
right, with tools, samples and references -
Summary • Constant work in progress • Anybody is
welcome to collaborate • Best practice for mobile penetration tests -
Foreword • There are many projects happening right now (very
good examples are MASVS and MSTG) • Due to a huge front of work every small help is valuable • Do something good today – contribute to OWASP Projects
 c0rdis
 sansantech
 kworkdev
 oracle4engineer
 jcabot
 tnir
 kota2and3kan
 kazzpapa3
 oidfj
 jirtosterone
 comi190327
 trallard
 tammyeverts
 helenjbeal
 bermonpainter
 aleyda
 eileencodes
 techseoconnect
 akashhashmi
 rmw
 orderedlist
 tonyrice
 rabernat