are vulnerable to OWASP top 10 attacks • Hackers reverse engineer apps to access private APIs • Data thefts • User account compromise • Coding flaws • Badly Implemented clients may leave your system vulnerable
System should service only legitimate users • Authorization System should allow users to perform only legitimate operations • Confidentiality Confidential data should be protected • Integrity Integrity of transactions should be protected
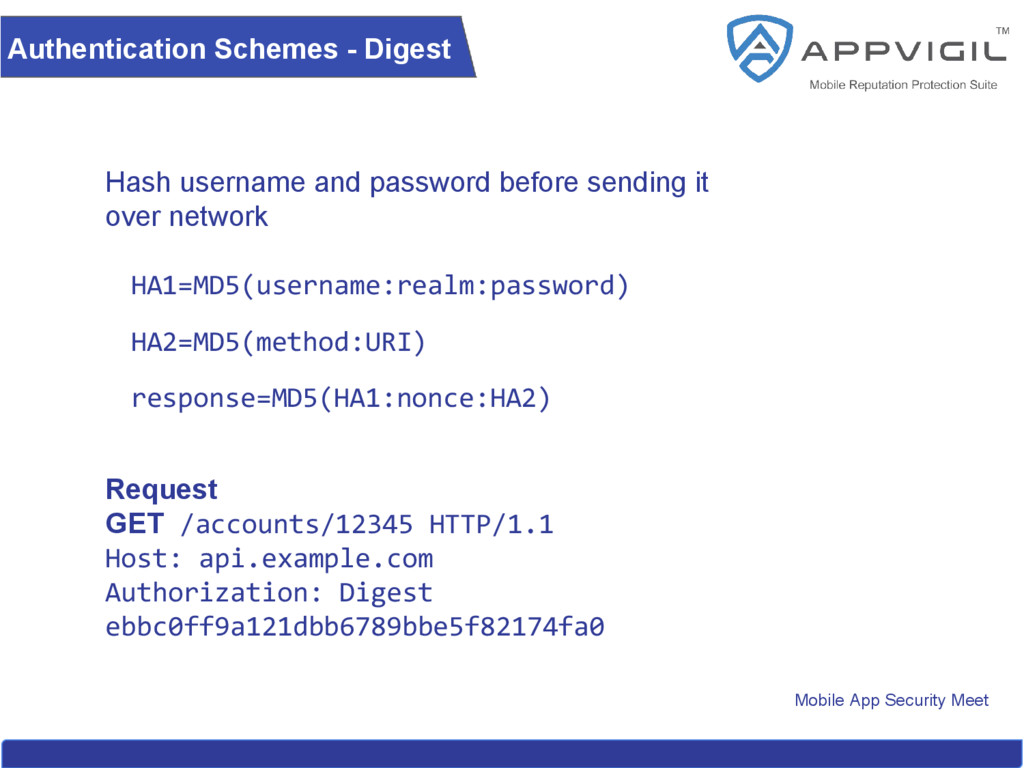
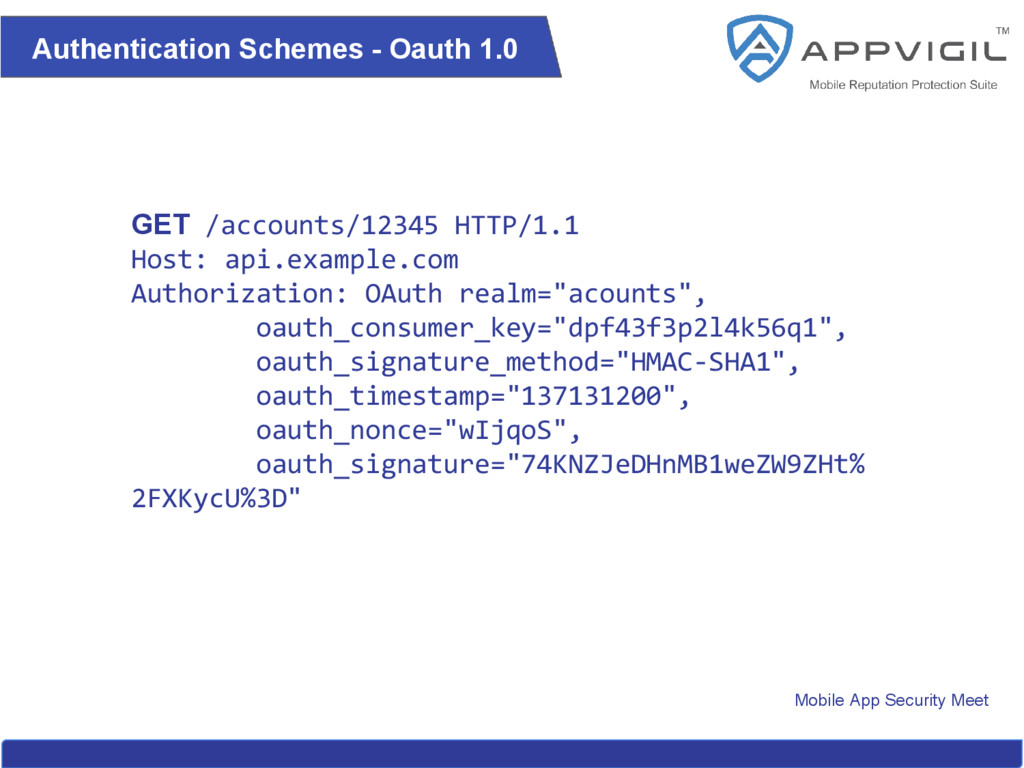
and password before sending it over network HA1=MD5(username:realm:password) HA2=MD5(method:URI) response=MD5(HA1:nonce:HA2) Request GET /accounts/12345 HTTP/1.1 Host: api.example.com Authorization: Digest ebbc0ff9a121dbb6789bbe5f82174fa0
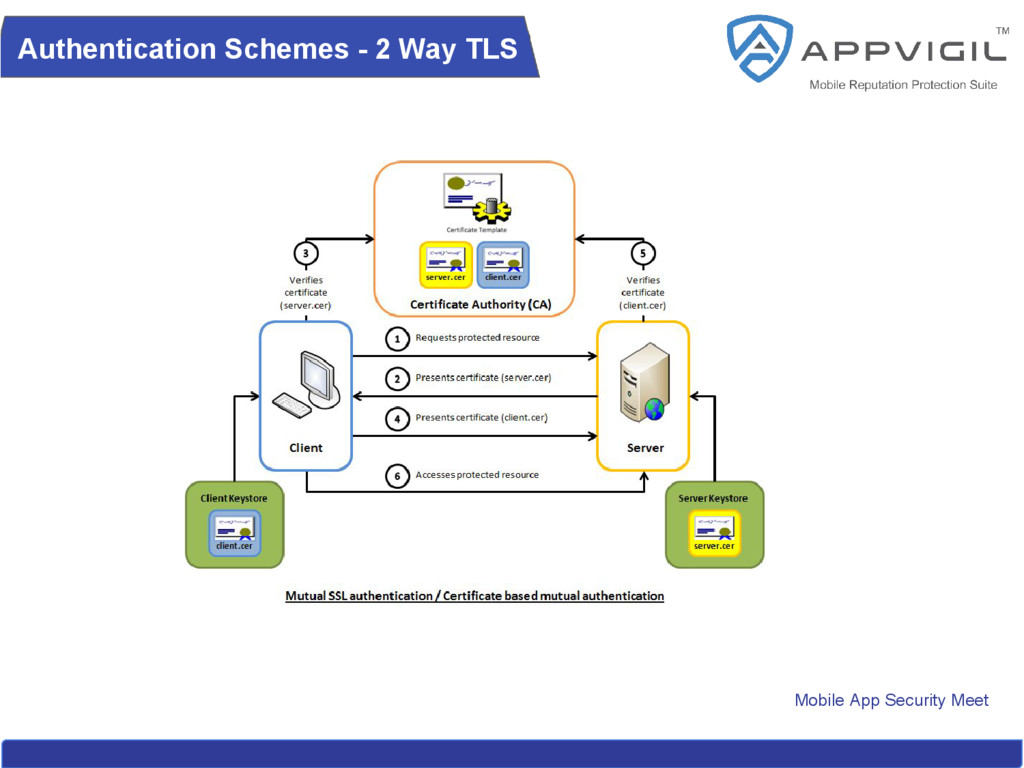
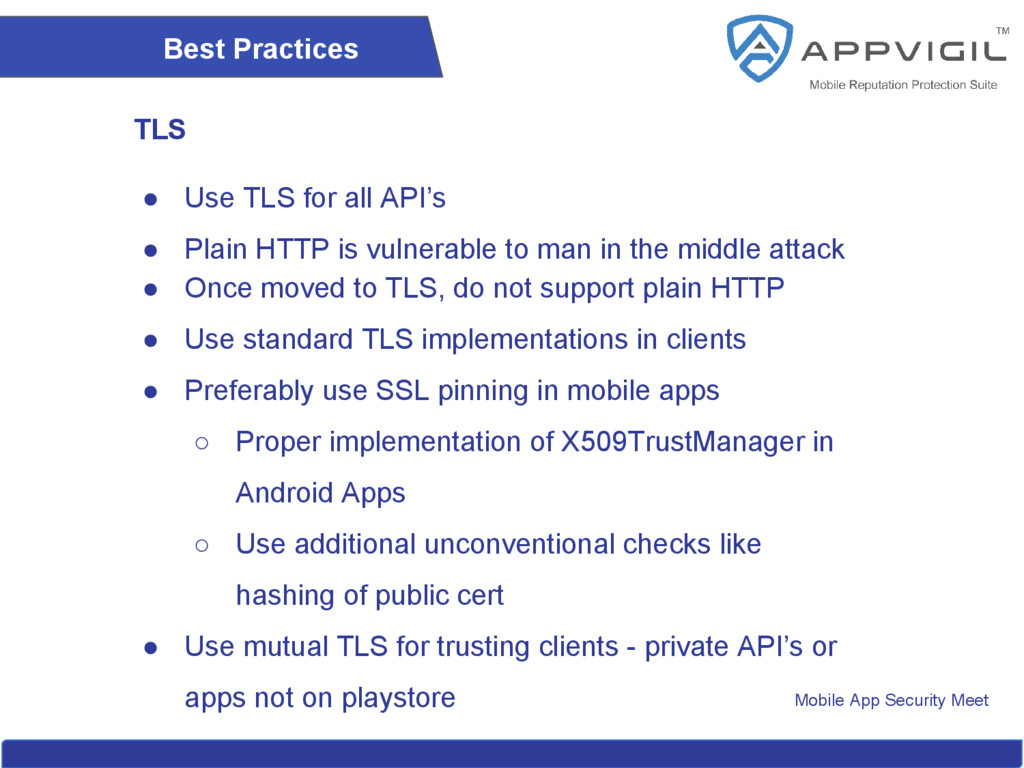
for all API’s • Plain HTTP is vulnerable to man in the middle attack • Once moved to TLS, do not support plain HTTP • Use standard TLS implementations in clients • Preferably use SSL pinning in mobile apps ◦ Proper implementation of X509TrustManager in Android Apps ◦ Use additional unconventional checks like hashing of public cert • Use mutual TLS for trusting clients - private API’s or apps not on playstore
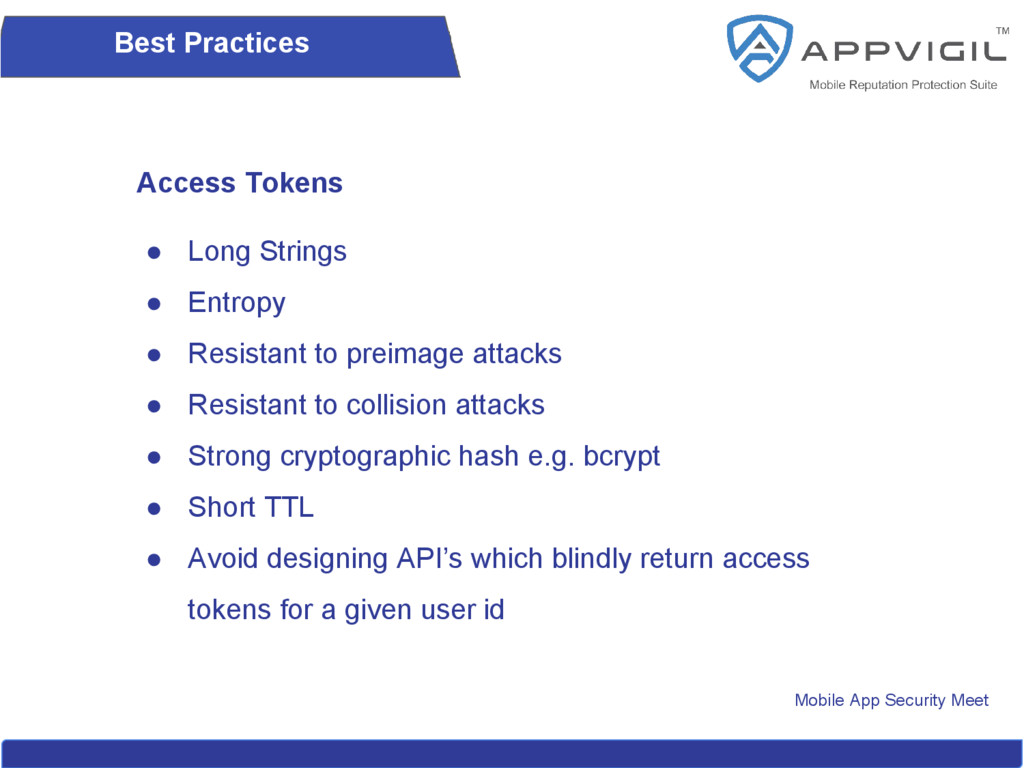
Strings • Entropy • Resistant to preimage attacks • Resistant to collision attacks • Strong cryptographic hash e.g. bcrypt • Short TTL • Avoid designing API’s which blindly return access tokens for a given user id
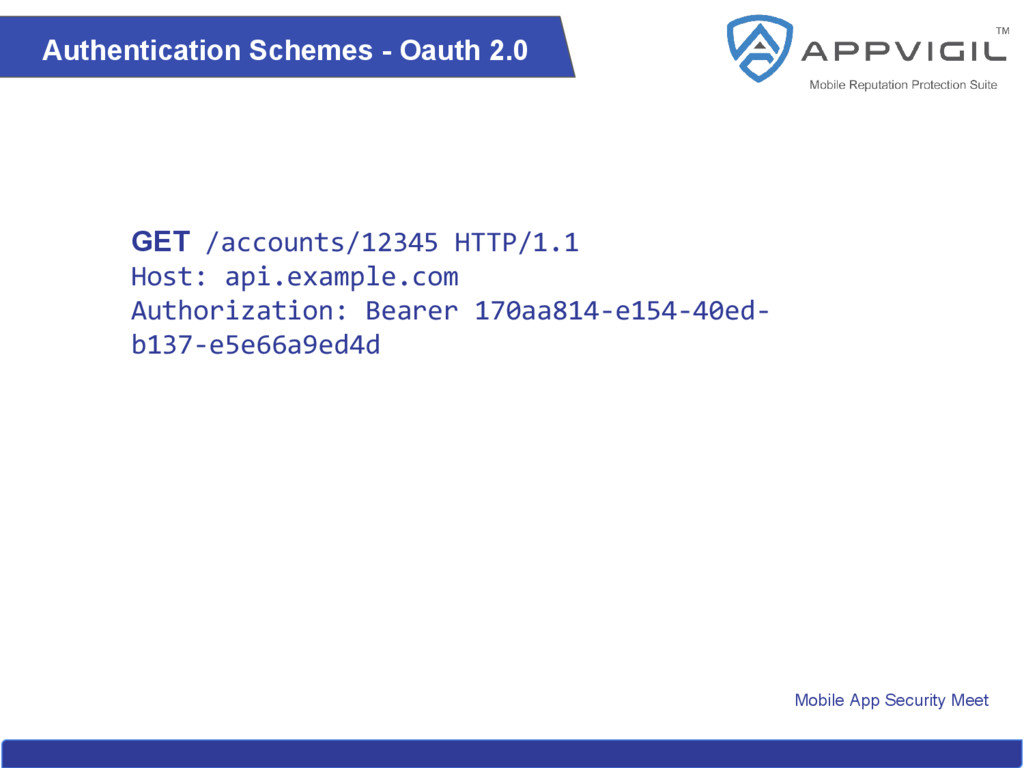
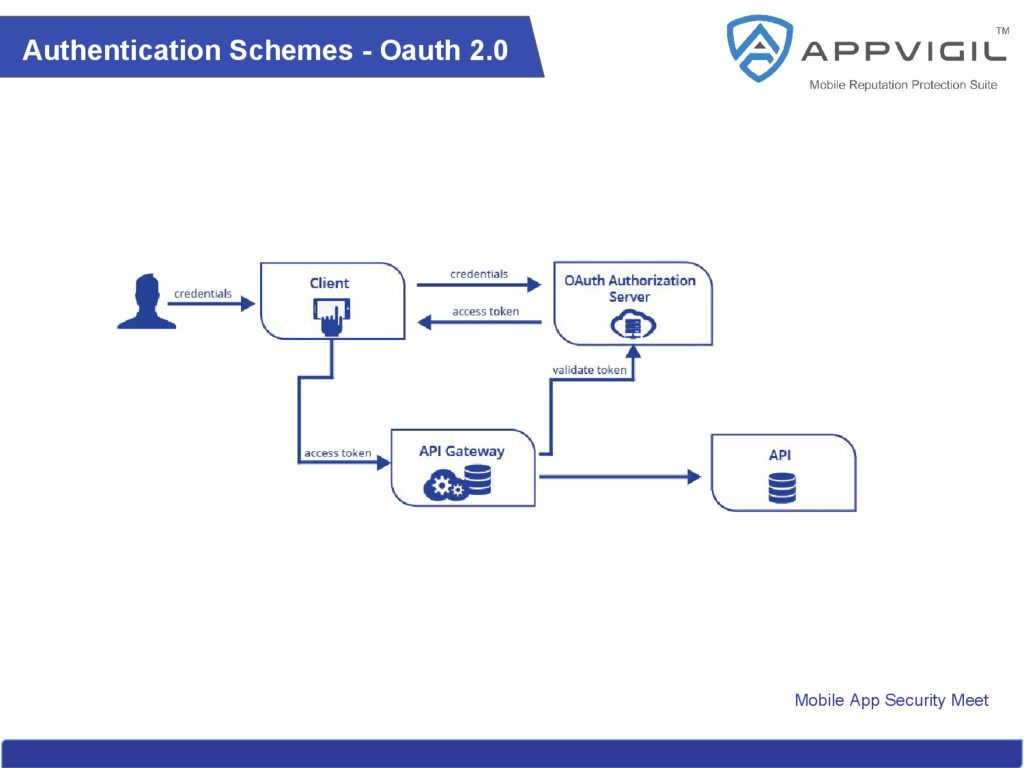
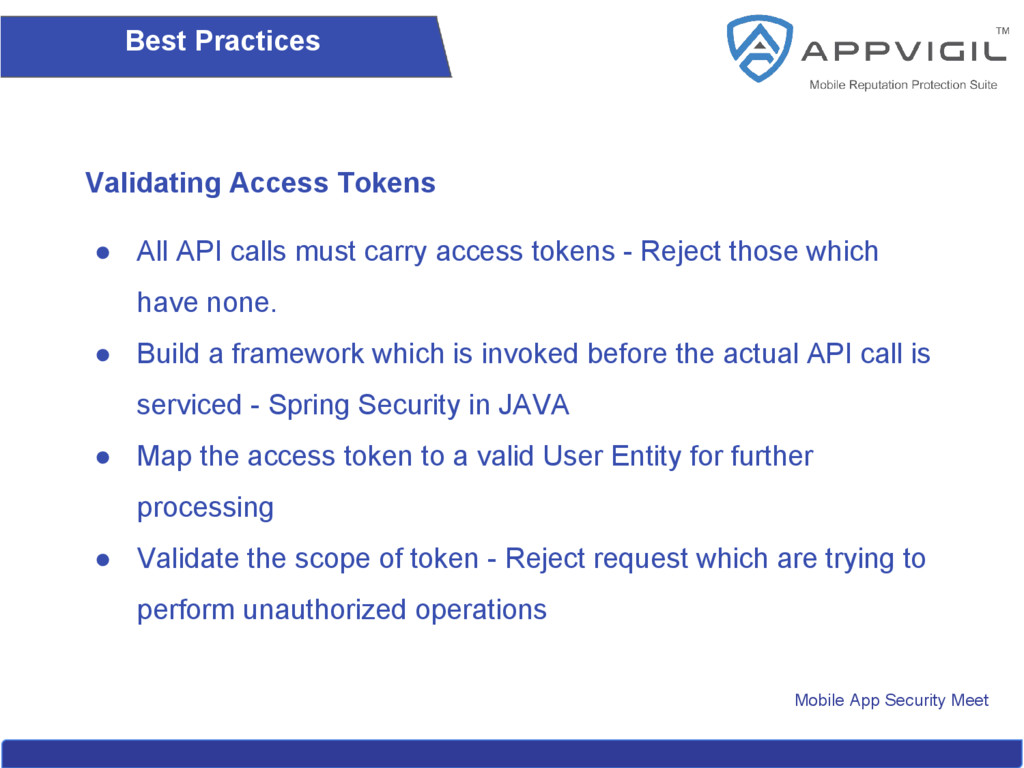
All API calls must carry access tokens - Reject those which have none. • Build a framework which is invoked before the actual API call is serviced - Spring Security in JAVA • Map the access token to a valid User Entity for further processing • Validate the scope of token - Reject request which are trying to perform unauthorized operations
defined password rules • Mix of alphanumeric and special characters • Avoid dictionary words - Dictionary Attack • Extra care while designing API’s which reset password like ◦ Forgot Password ◦ Profile Edit • Use additional security measures like OTP via email or text • Badly implemented API’s will create a backdoor to your system
using session cookies - Consider Access Tokens • Stateless API’s are more easy to manage than stateful • Access Tokens + Stateless API = No CSRF attacks • Set Cookie: JSESSIONID=xyz124kjf9; Secure; HttpOnly;
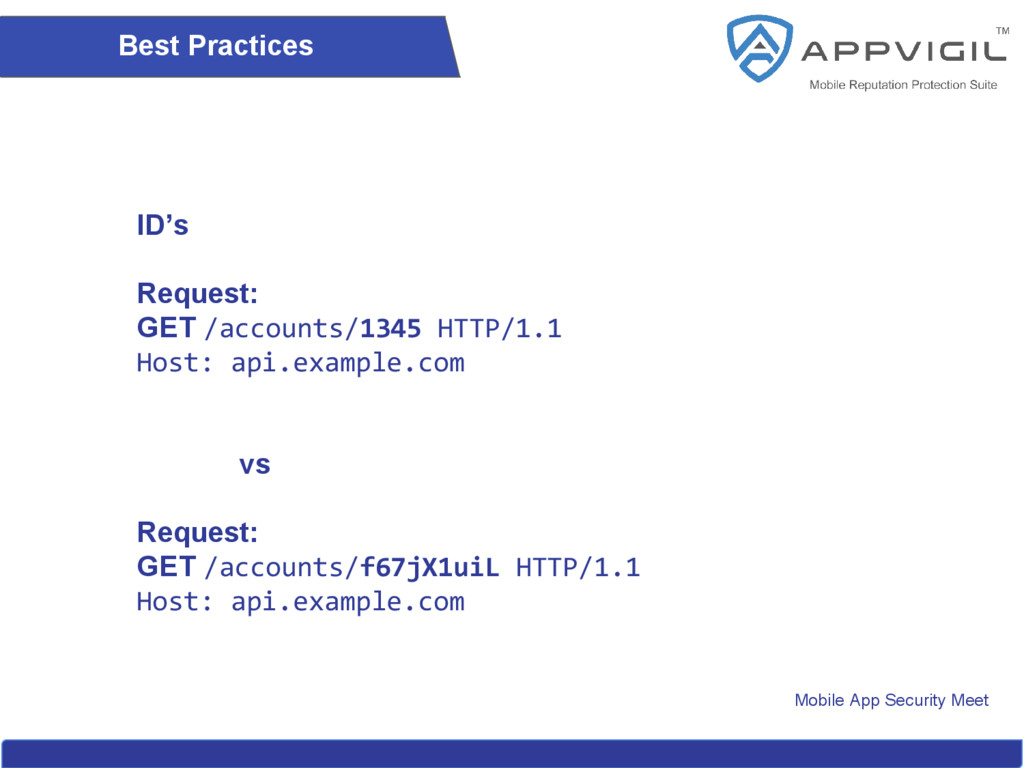
serial numbers as primary identifiers of your resources like accounts, transactions - Brute Force Attack • Use hashes instead • Preferably use unique identifiers like UUID’s as transaction id’s ◦ universally unique ◦ avoids contention ◦ performance boost


 suneo3476
 colorful12
 akihisaikeda
 palkan
 ryu1013
 morizo_1984
 yub0n
 oniak3ibm
 lynnswap
 deka_morita
 a_matsuda
 gonta
 mfonobong
 tammielis
 madoxten
 ryanjones
 addyosmani
 techseoconnect
 skipperchong
 watany
 marcduiker
 sarafernandez