Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
.NET Day 19 - Authentication and Authorization ...
Search
.NET Day
May 28, 2019
Technology
370
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
.NET Day 19 - Authentication and Authorization in ASP.NET Core by Damien Bowden
.NET Day
May 28, 2019
More Decks by .NET Day
See All by .NET Day
.NET Day 2026 What I learned from modernizing a microservices architecture
dotnetday
0
40
.NET Day 2026 The impact and relevance of code reviews on software quality
dotnetday
0
46
.NET Day 2026 From Co-Pilot to Co-Worker: Mastering GitHub Copilot Agent Mode
dotnetday
0
51
.NET Day 2026 Are you sure your access tokens are really secure?
dotnetday
0
38
.NET Day 2026 The death of Passwords, Implementing Passkeys in .NET 10
dotnetday
0
49
.NET Day 2026 How Banks Protect Their Applications with FAPI
dotnetday
0
33
.NET Day 2026 AI Your Way: MCPs vs Skills vs SubAgents 🤖🚀
dotnetday
0
45
.NET Day 2026 The Past, Present and Future of Programming Languages
dotnetday
0
59
.NET Day 2026 Mis-Estimating – why estimating effort does not work
dotnetday
0
47
Other Decks in Technology
See All in Technology
SAENM ~Jupyterで残すPoCの試行錯誤、未来の自分と仲間を助ける記録!~
terapyon
0
110
会社説明資料
persolserverworks
0
9.8k
フロントエンドカンファレンス関西2026 - 速すぎるUIに、待ち時間を
teamlab
PRO
0
130
Rustuna: Rustによる高速なOptuna実装
pfn
PRO
0
190
サブエージェントと Claude Mods で作る独自 Advisor ツールの話
kenichiodo
2
160
DWH の限界突破! AI エージェント向け爆速リアルタイムデータ基盤 ClickHouse
jozono
1
470
自作バイナリを動かす「入口」8選
puhitaku
2
1.3k
LambdaWebFunctionsを試してみた / exploring-lambda-web-functions
koukihosaka
1
340
AI駆動で「他アプリの音を加工できる」アプリを作った
satomasahiro2005
0
150
Code for Security プロジェクト紹介 2026年10月
yu23ki14
0
110
DGX Spark でどこまでハッキングができるのか?
kash1064
3
1.3k
AI駆動開発の時代になったのでトヨタ生産方式から見直す
terurou
7
6k
Featured
See All Featured
The browser strikes back
jonoalderson
0
1.8k
From π to Pie charts
rasagy
1
400
YesSQL, Process and Tooling at Scale
rocio
174
15k
Hiding What from Whom? A Critical Review of the History of Programming languages for Music
tomoyanonymous
3
1.3k
How to build an LLM SEO readiness audit: a practical framework
nmsamuel
2
950
Measuring Dark Social's Impact On Conversion and Attribution
stephenakadiri
2
310
Leveraging Curiosity to Care for An Aging Population
cassininazir
1
540
Highjacked: Video Game Concept Design
rkendrick25
PRO
1
480
Everyday Curiosity
cassininazir
0
350
職位にかかわらず全員がリーダーシップを発揮するチーム作り / Building a team where everyone can demonstrate leadership regardless of position
madoxten
69
67k
JAMstack: Web Apps at Ludicrous Speed - All Things Open 2022
reverentgeek
1
640
How to Align SEO within the Product Triangle To Get Buy-In & Support - #RIMC
aleyda
2
1.8k
Transcript
ASP.NET Core Security • Damien Bowden Microsoft MVP • https://damienbod.com
• @damien_bod
https://github.com/damienbod ASP.NET Core, OpenID Connect, OAuth, Identity, Azure Angular, angular-auth-oidc-client
npm
Security & Applications today OpenID Connect, OAuth2 Authorization: ASP.NET Core
Policies
Security & Applications today
Application
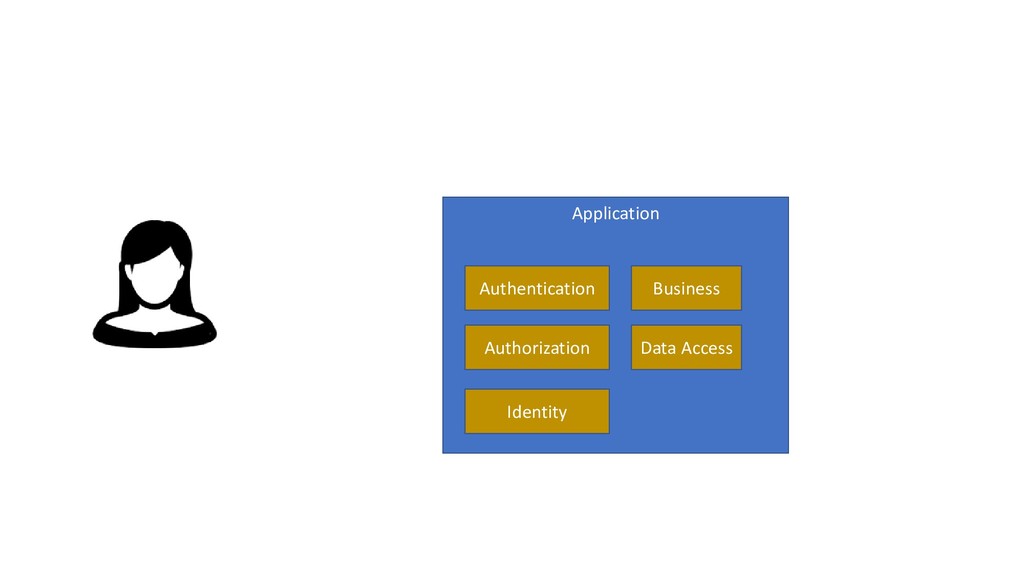
Application Authentication Business Data Access Authorization Identity
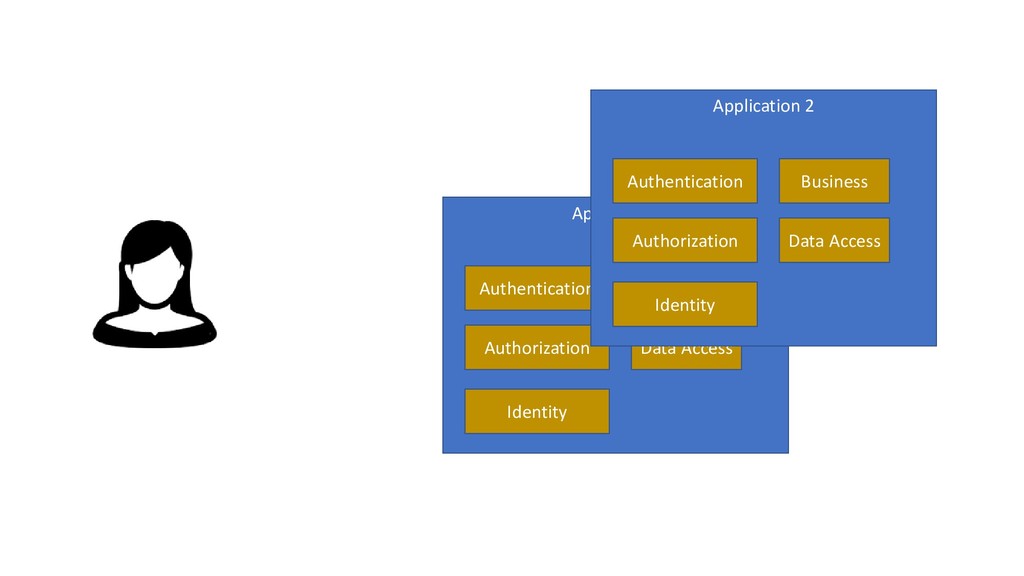
Application Authentication Business Data Access Authorization Identity Application 2 Authentication
Business Data Access Authorization Identity
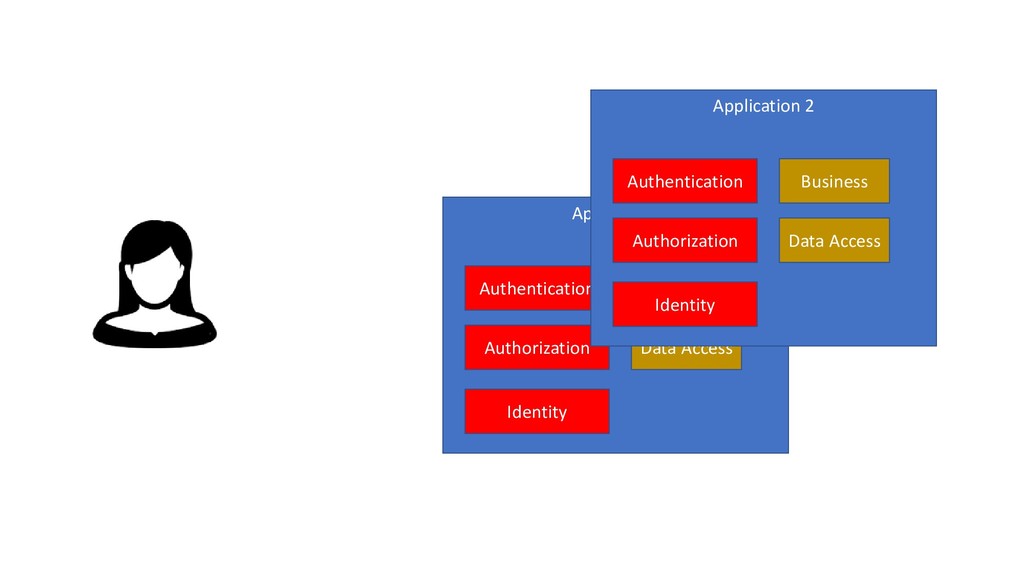
Application Authentication Business Data Access Authorization Identity Application 2 Authentication
Business Data Access Authorization Identity
None
None
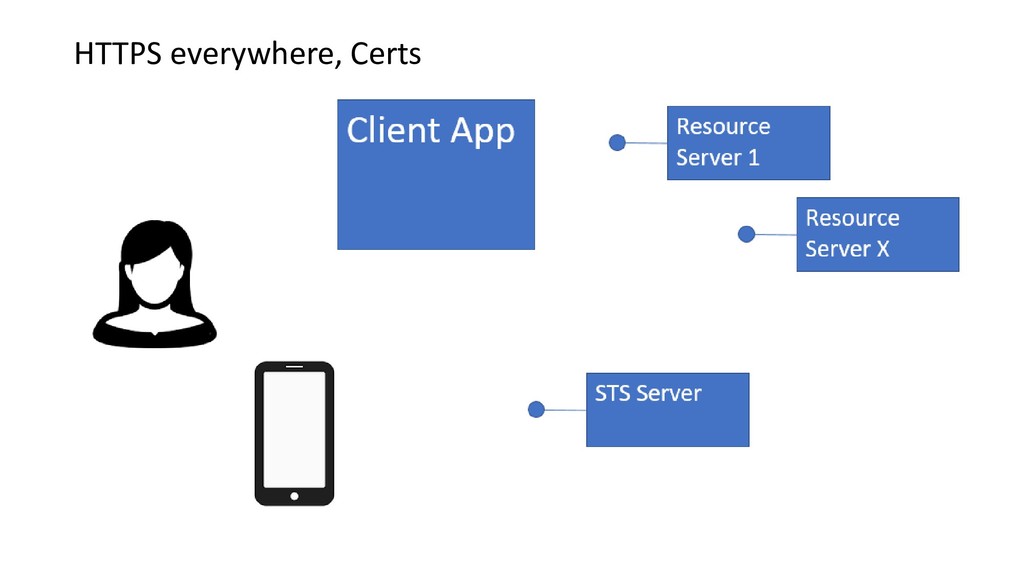
HTTPS everywhere, Certs
WAF HTTPS everywhere, Certs Protected Zone
WAF HTTPS everywhere, Certs Protected Zone
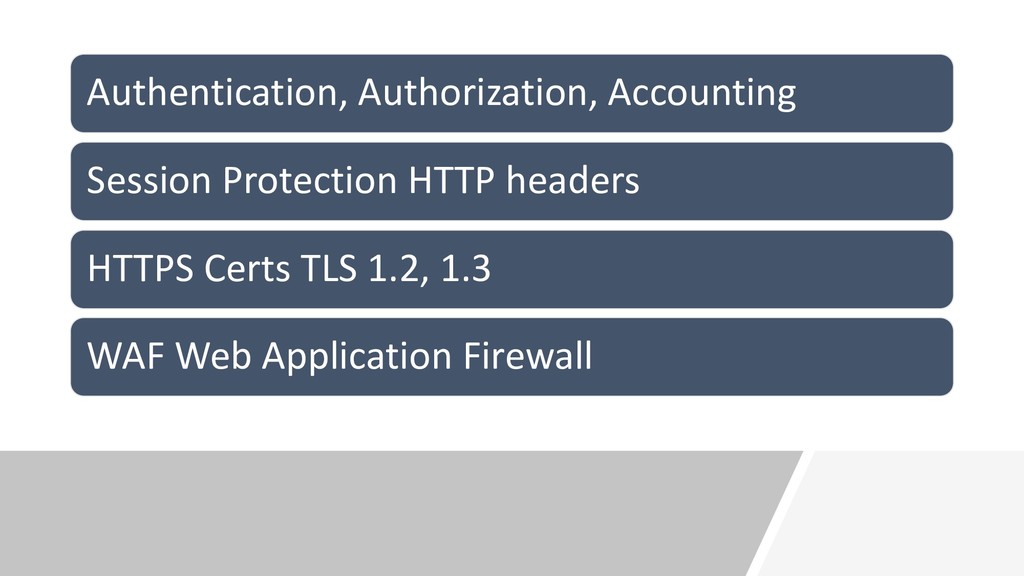
Authentication, Authorization, Accounting Session Protection HTTP headers HTTPS Certs TLS
1.2, 1.3 WAF Web Application Firewall
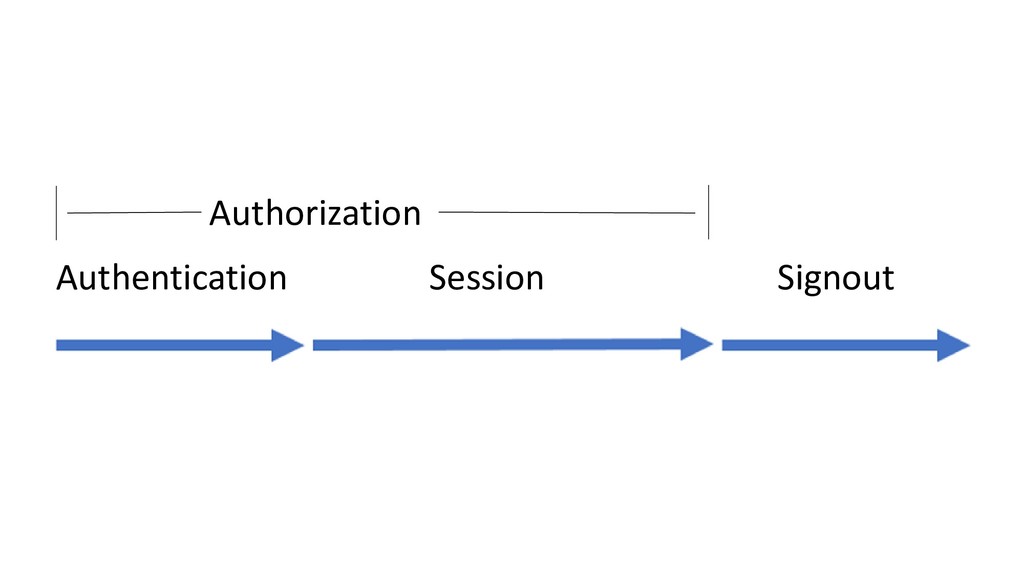
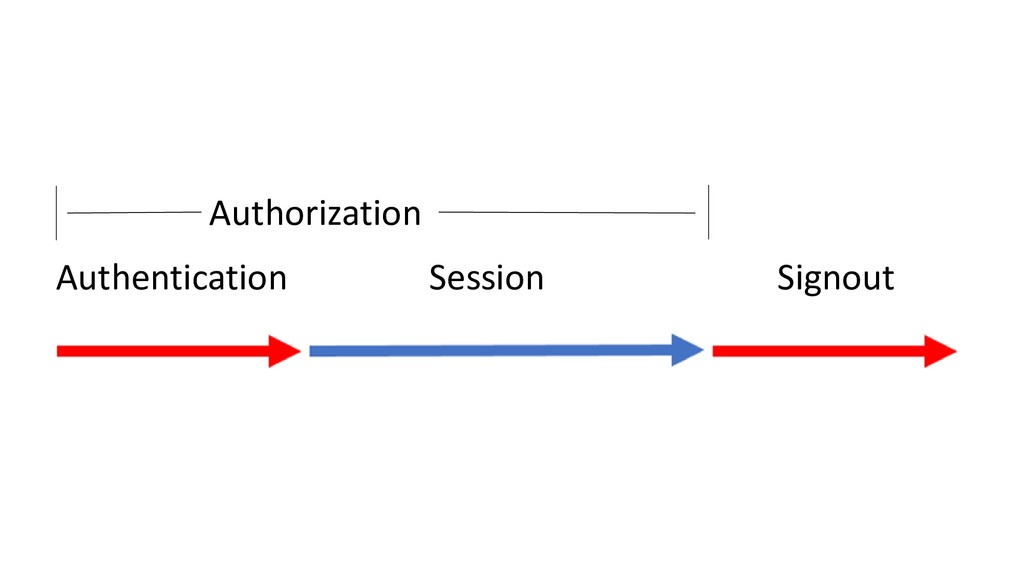
Authentication Authorization Signout Session
USE Standards Don’t implement this yourself, use certified libs, packages,
tested
None
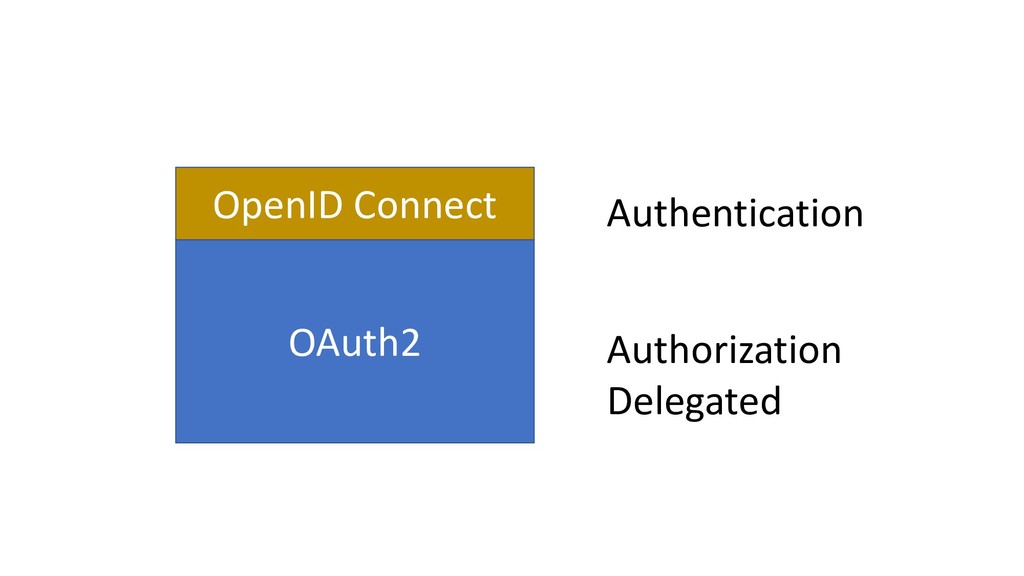
OAuth2 OpenID Connect Authentication Authorization Delegated
OpenID Connect http://openid.net/connect/ • Standard, Specification • Authentication and Authorization
• built on top of OAuth2 (access control) • Identity (Person can have n Identities) • UserInfo Endpoint
Open ID Connect (OIDC) is supported by almost all systems
. Azure AD, Azure B2C, OKTA, IdentityServer4, google accounts, Openiddict, node-oidc-provider
Authentication Authorization Signout Session
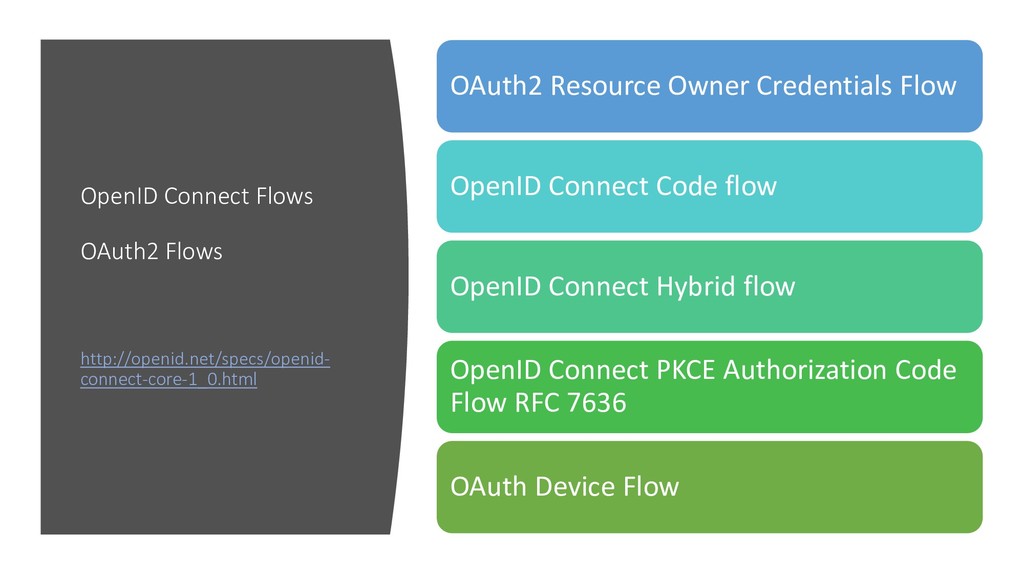
OpenID Connect Flows OAuth2 Flows http://openid.net/specs/openid- connect-core-1_0.html OAuth2 Resource Owner
Credentials Flow OpenID Connect Code flow OpenID Connect Hybrid flow OpenID Connect PKCE Authorization Code Flow RFC 7636 OAuth Device Flow
id token token (access token) reference / self contained token
refresh token scope Back-Channel Front-Channel User Agent
OAuth2 Resource Owner Credentials Flow • MC to MC applications
• trusted client • grant_type=client_cred ential&client_id=xxxxx xxxxx&client_secret=xx xxxxxxxx • Limited user cases
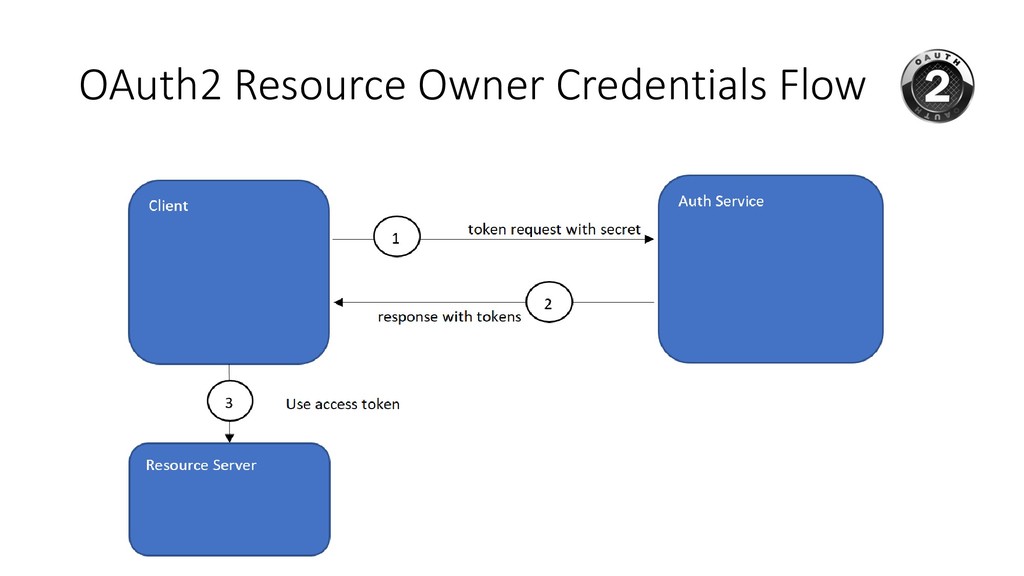
OAuth2 Resource Owner Credentials Flow
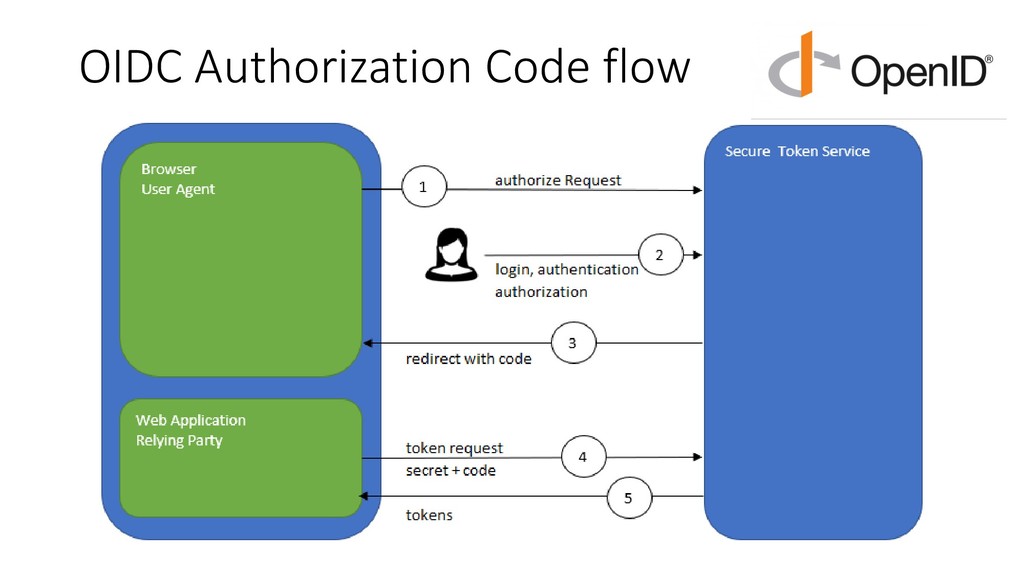
OpenID Connect Authorization Code flow • Server to server applications
with User • Can keep secrets, is trusted • Client is authenticated • response_type = code
OIDC Authorization Code flow
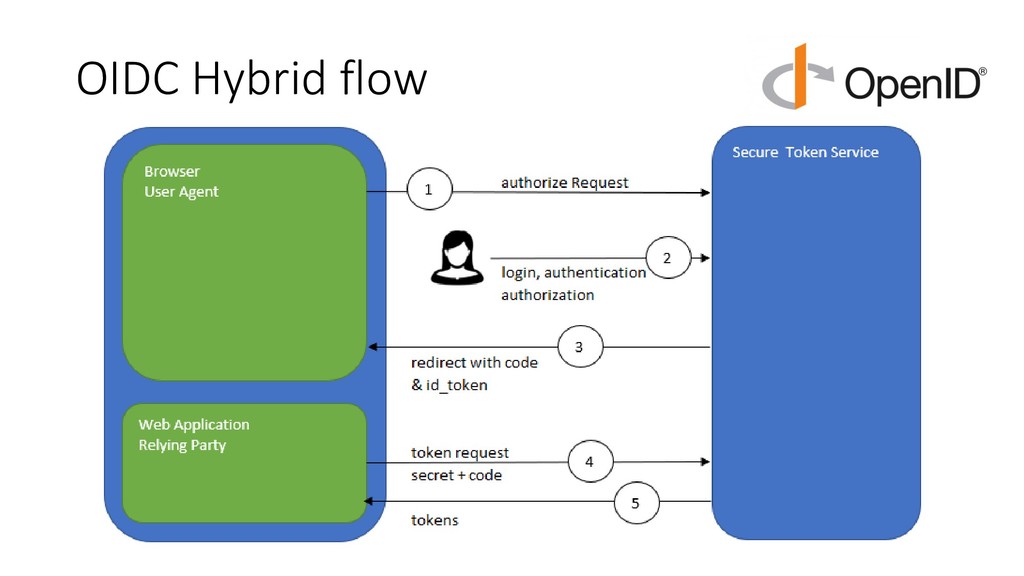
OIDC Hybrid flow • Mix of the Code and Implicit
Flow • Can be used for Web applications with server side rendering. • response_type = code id_token | code id_token token | code token
OIDC Hybrid flow
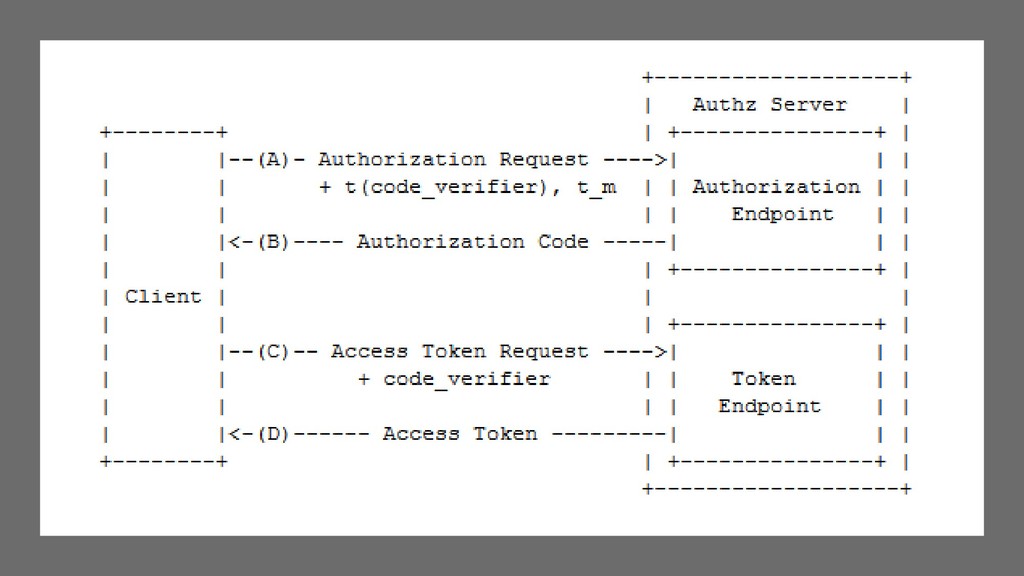
Native App PKCE Authorization Code Flow RFC 7636 https://tools.ietf.org/html/rfc 7636
None
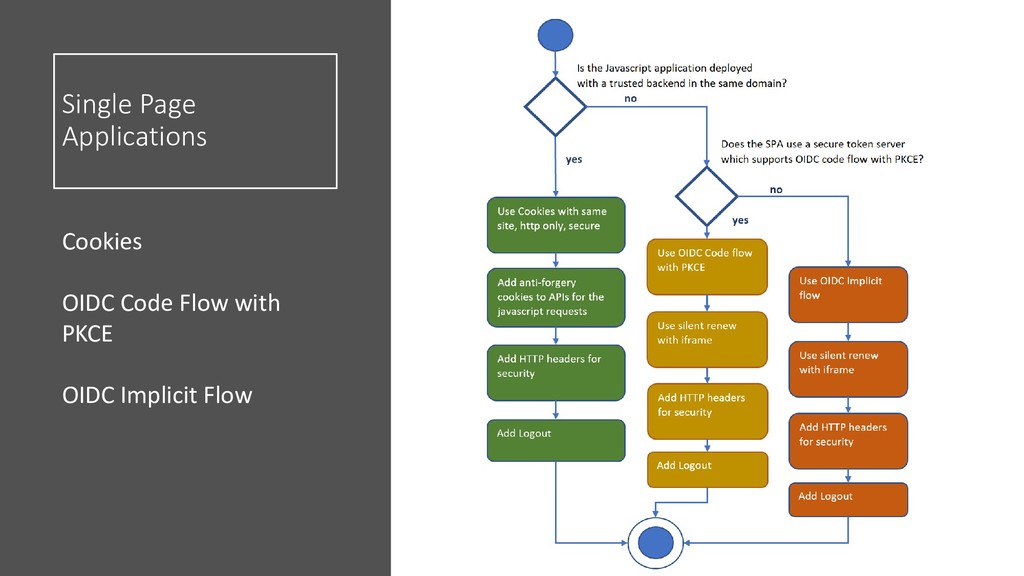
Single Page Applications Cookies OIDC Code Flow with PKCE OIDC
Implicit Flow
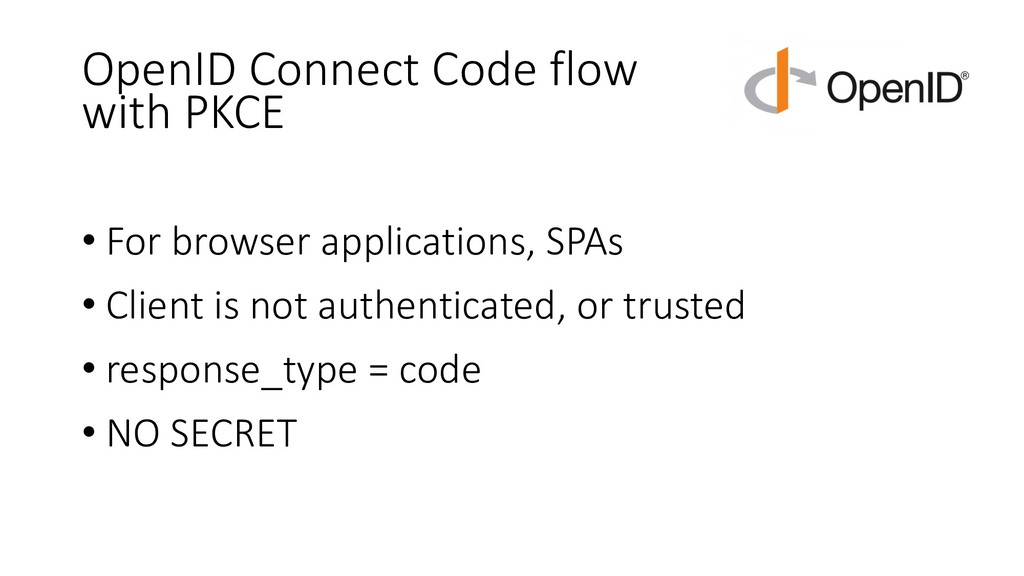
OpenID Connect Code flow with PKCE • For browser applications,
SPAs • Client is not authenticated, or trusted • response_type = code • NO SECRET
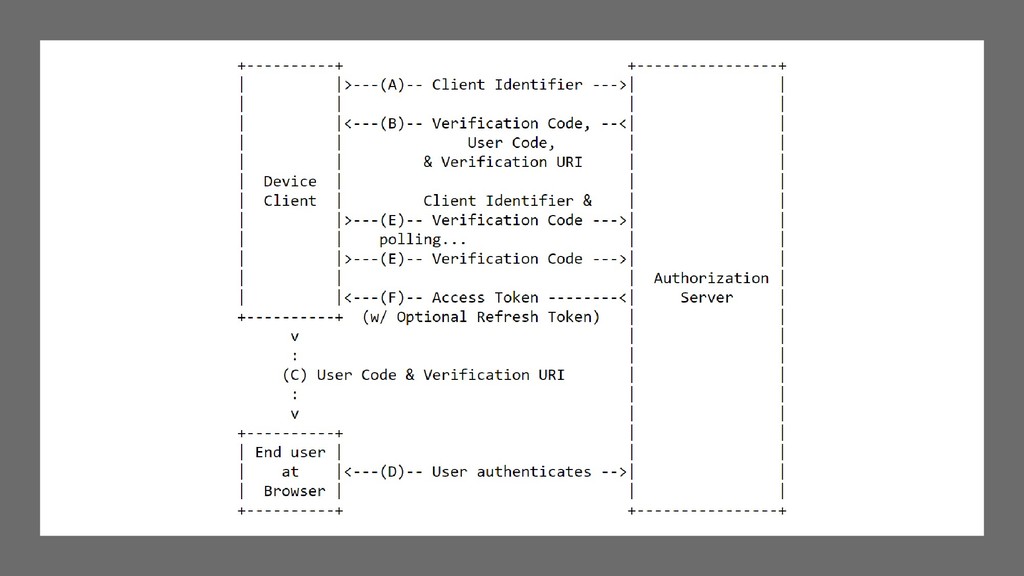
OAuth Device Flow RFC 7636 https://tools.ietf.org/html/dra ft-ietf-oauth-device-flow-12
None
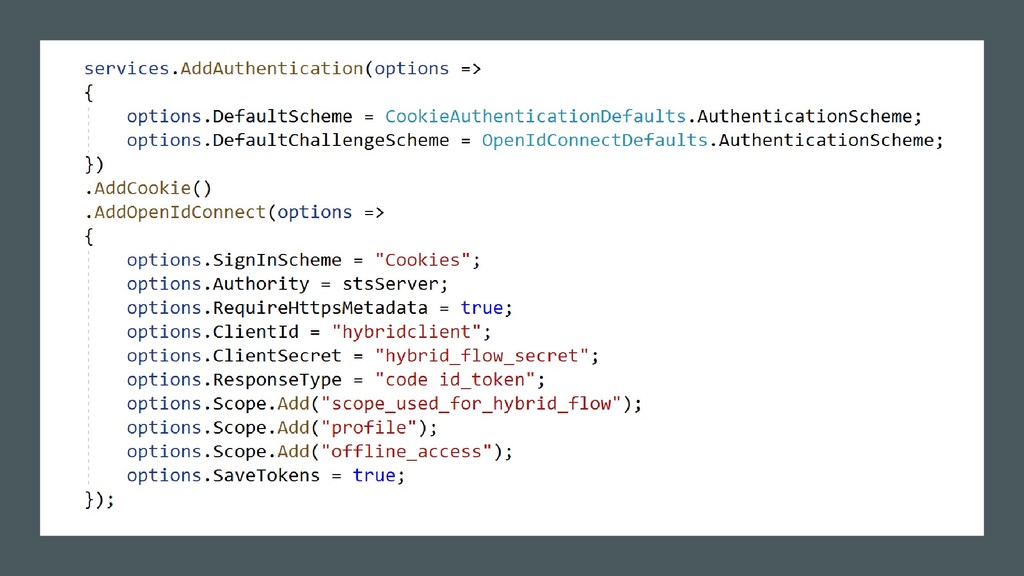
https://github.com/damienbod/AspNetCoreHybridFlowWithApi https://github.com/damienbod/AspNetCoreWindowsAuth OpenID Connect Hybrid Flow / Code Flow Code
examples
None
None
None
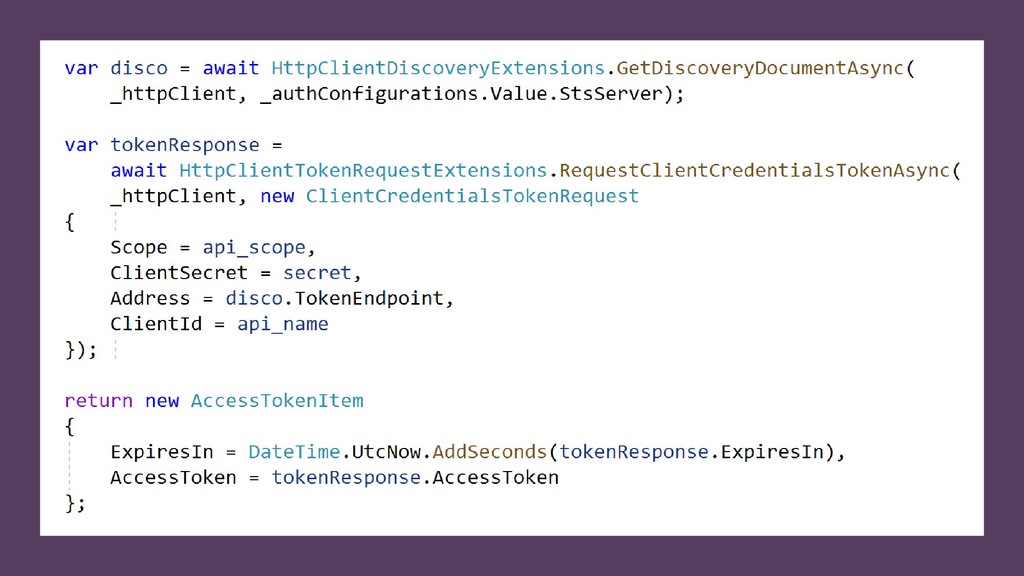
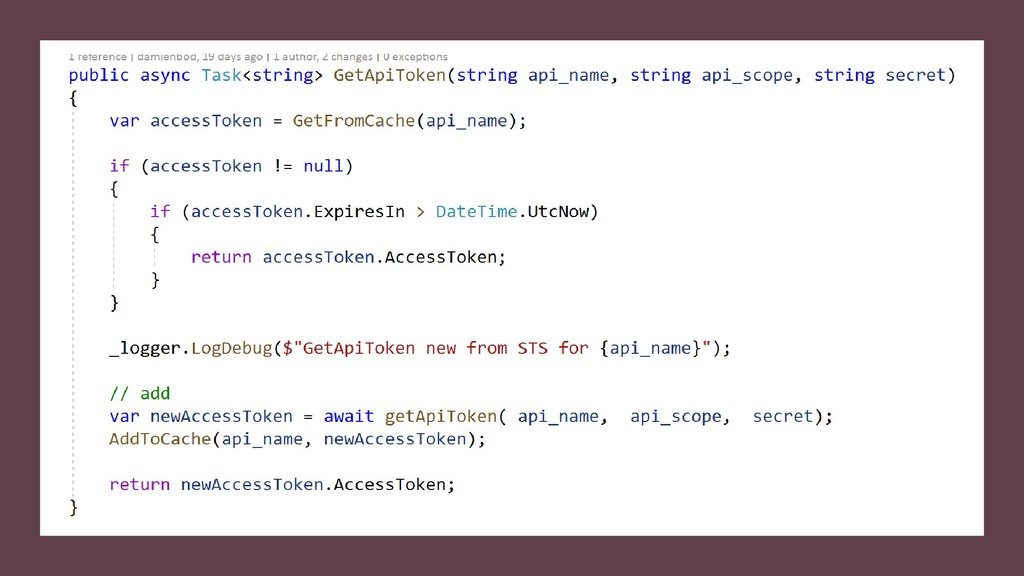
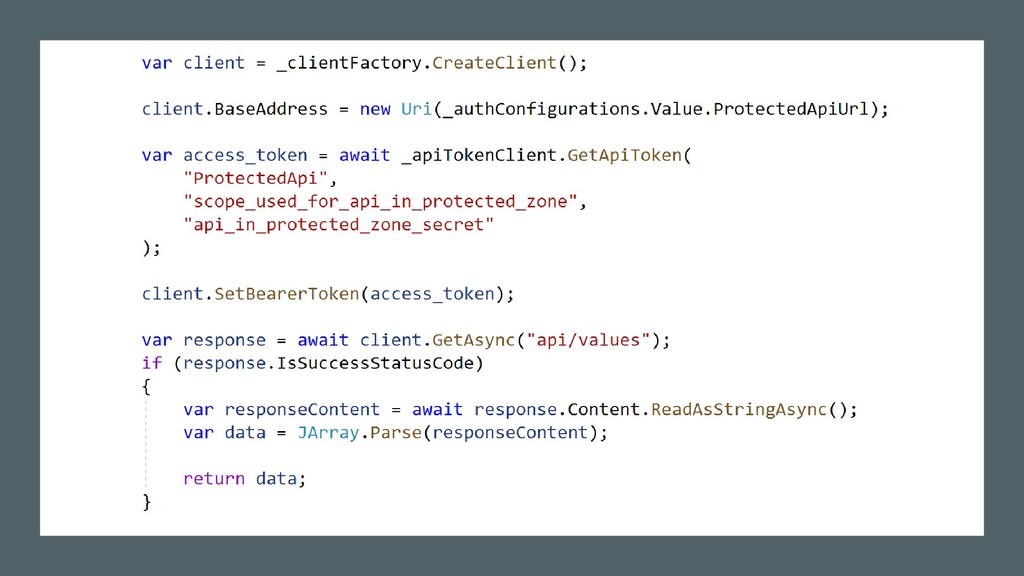
https://github.com/damienbod/AspNetCoreHybridFlowWithApi https://github.com/damienbod/AspNetCoreWindowsAuth OAuth2 Resource Owner Credentials Flow Code examples
None
None
None
None
Authorization: ASP.NET Core Policies
Authorization is the responsibility of the Application / API, not
the STS. This can be implemented in an separate library.
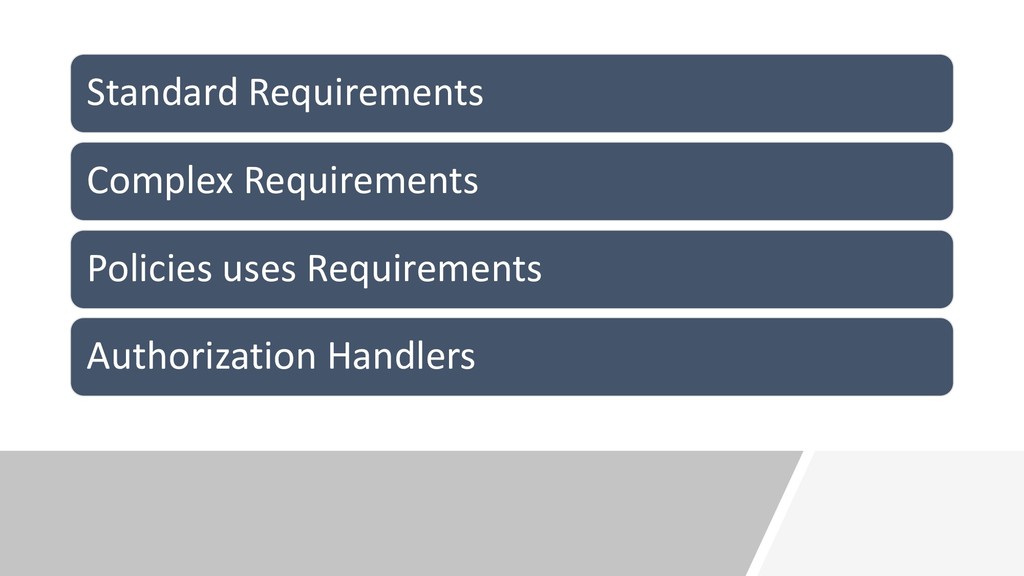
Standard Requirements Complex Requirements Policies uses Requirements Authorization Handlers
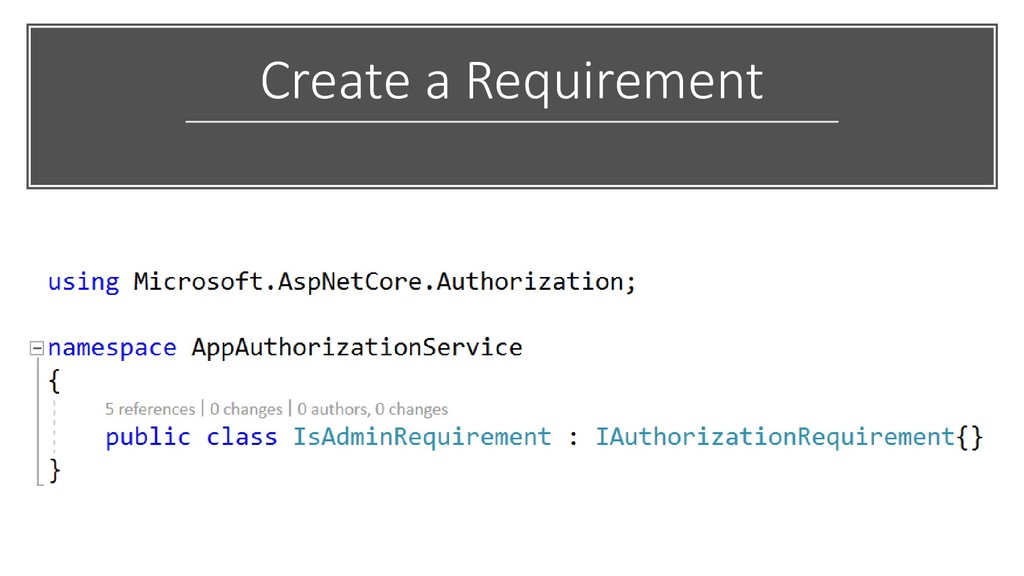
Create a Requirement
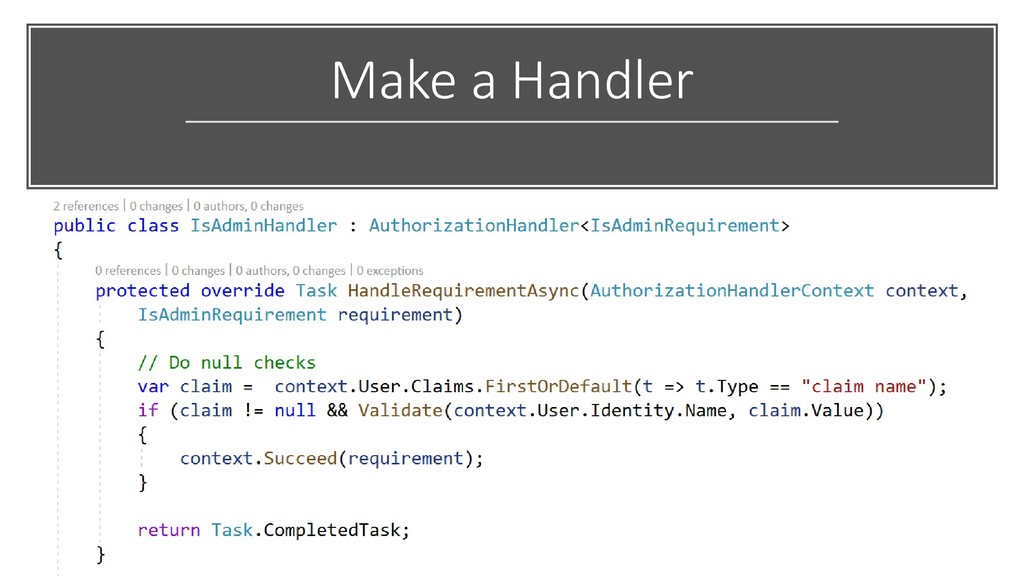
Make a Handler
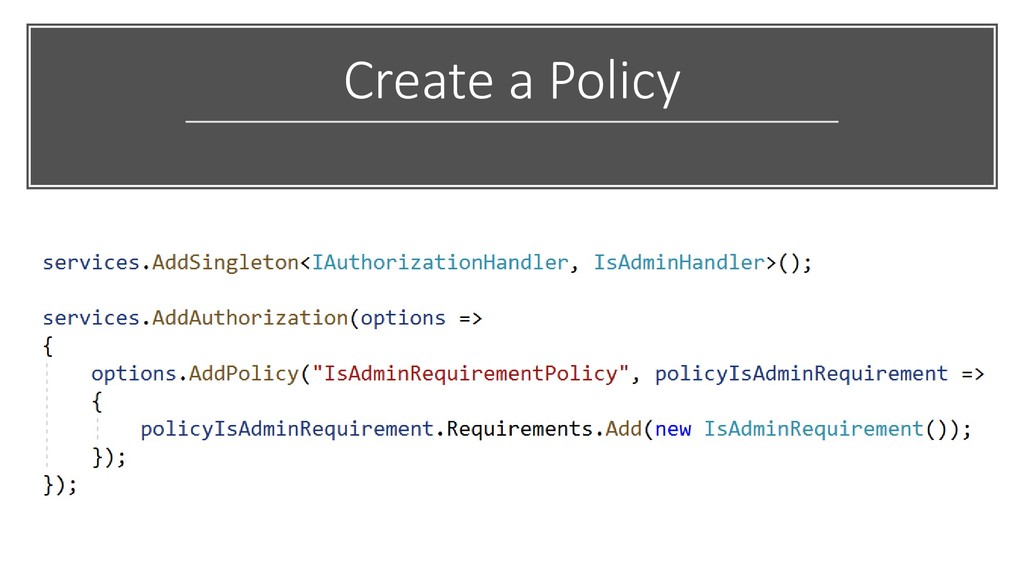
Create a Policy
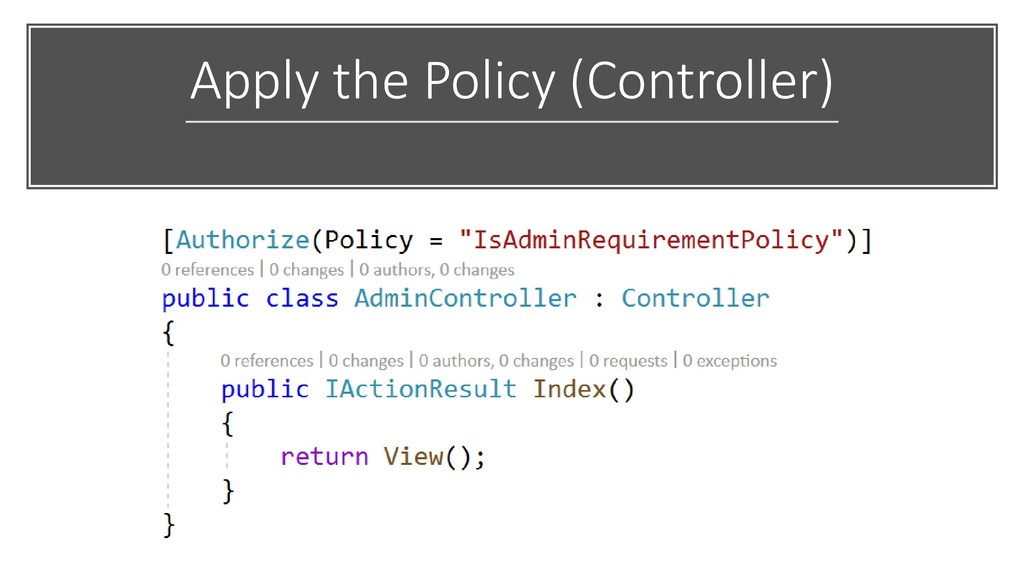
Apply the Policy (Controller)
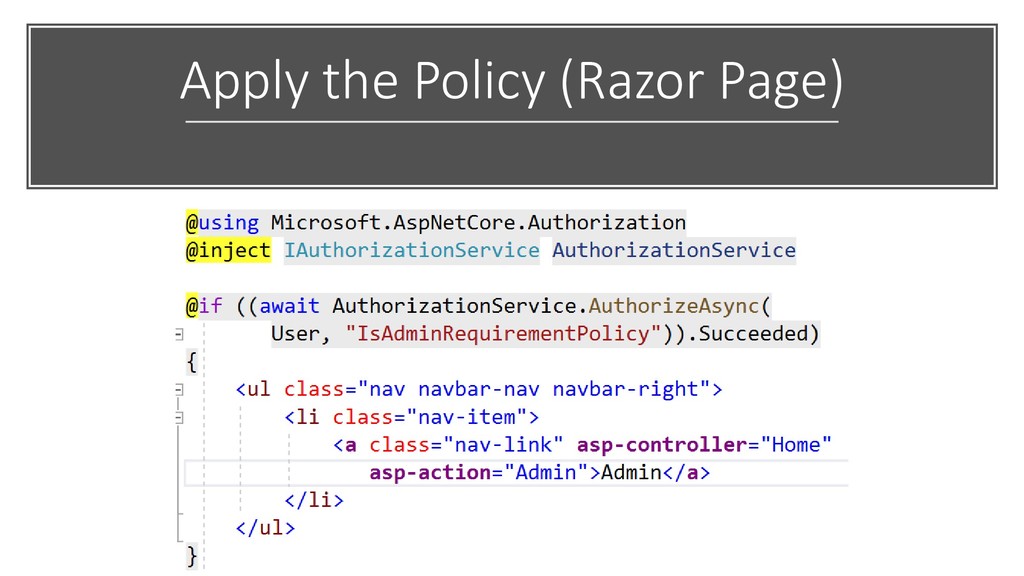
Apply the Policy (Razor Page)
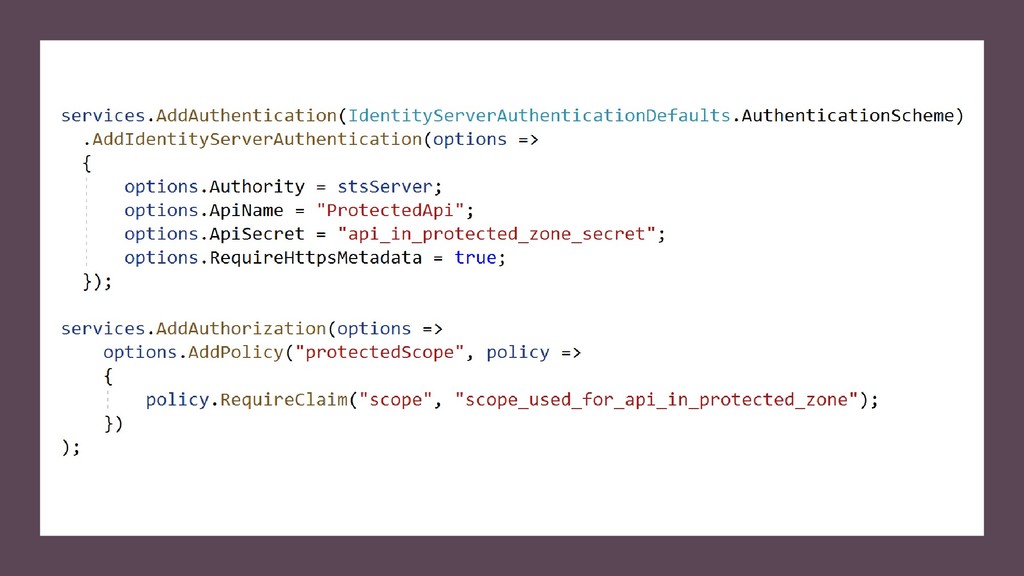
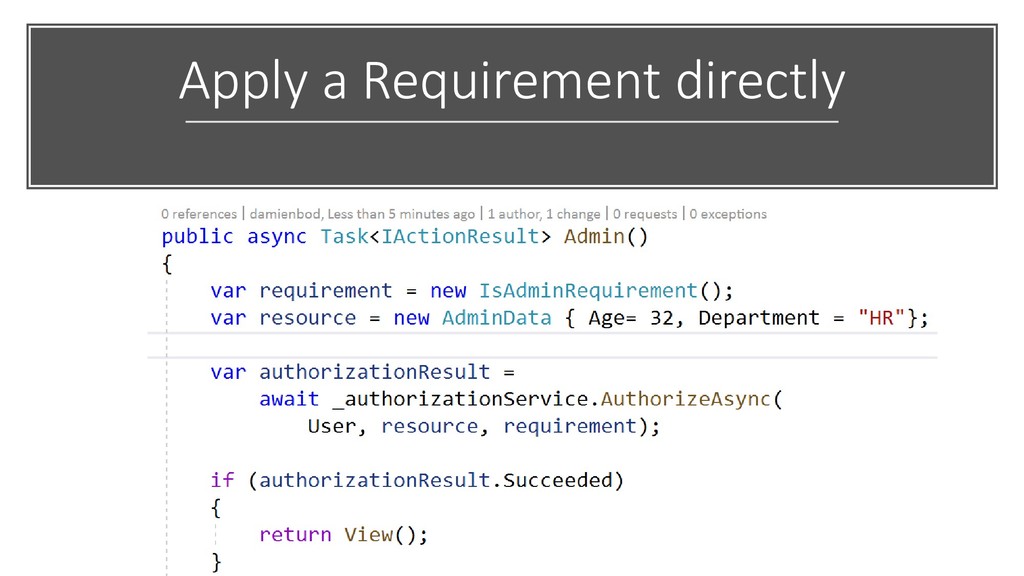
Apply a Requirement directly
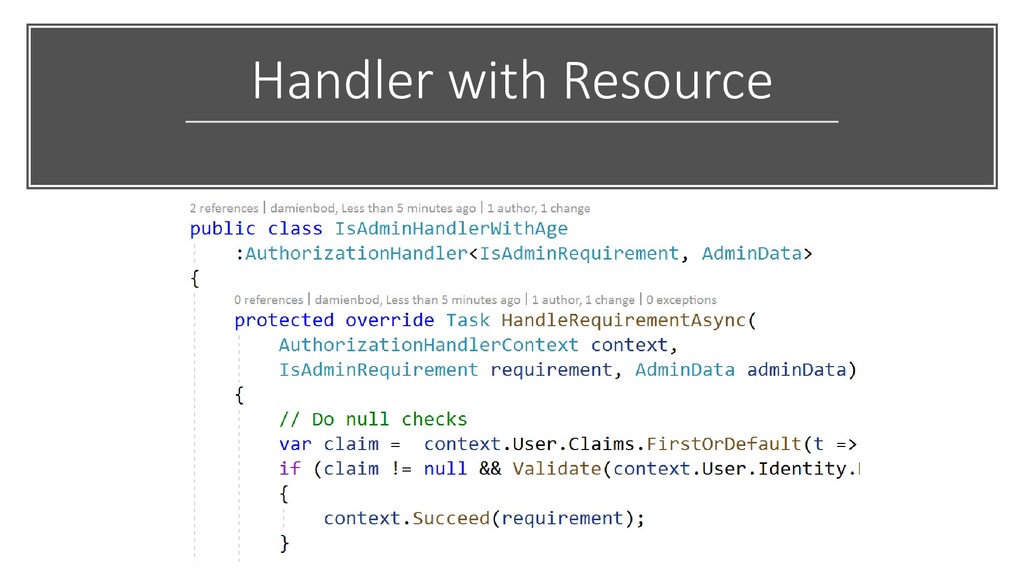
Handler with Resource
ASP.NET Core Policies, Handlers and Requirements makes it easy to
focus on Authorization
Thank you @damienbod
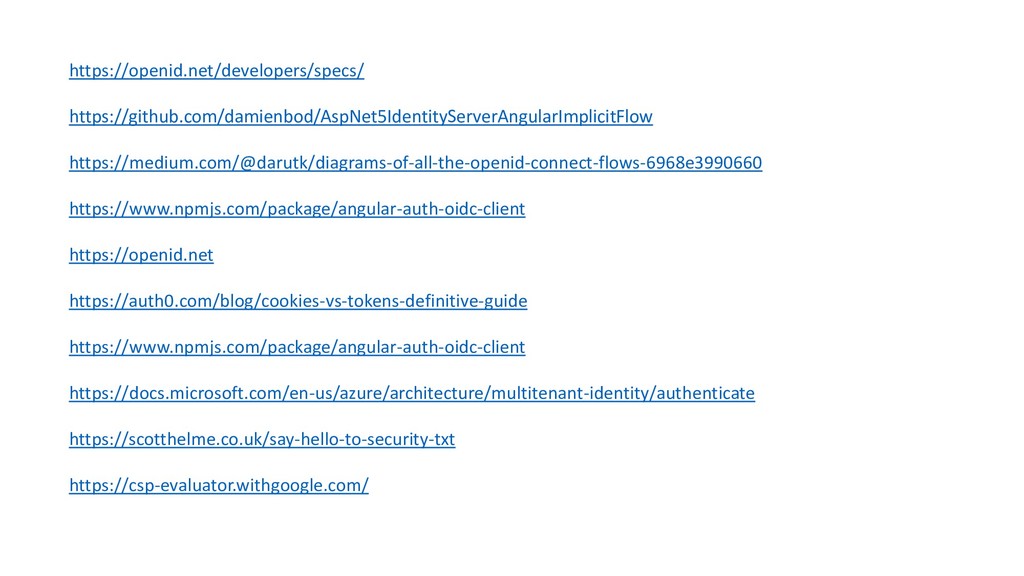
https://openid.net/developers/specs/ https://github.com/damienbod/AspNet5IdentityServerAngularImplicitFlow https://medium.com/@darutk/diagrams-of-all-the-openid-connect-flows-6968e3990660 https://www.npmjs.com/package/angular-auth-oidc-client https://openid.net https://auth0.com/blog/cookies-vs-tokens-definitive-guide https://www.npmjs.com/package/angular-auth-oidc-client https://docs.microsoft.com/en-us/azure/architecture/multitenant-identity/authenticate https://scotthelme.co.uk/say-hello-to-security-txt https://csp-evaluator.withgoogle.com/


 dotnetday
 terapyon
 persolserverworks
 teamlab
 pfn
 kenichiodo
 jozono
 puhitaku
 koukihosaka
 satomasahiro2005
 yu23ki14
 kash1064
 terurou
 jonoalderson
 rasagy
 rocio
 tomoyanonymous
 nmsamuel
 stephenakadiri
 cassininazir
 rkendrick25
 madoxten
 reverentgeek
 aleyda