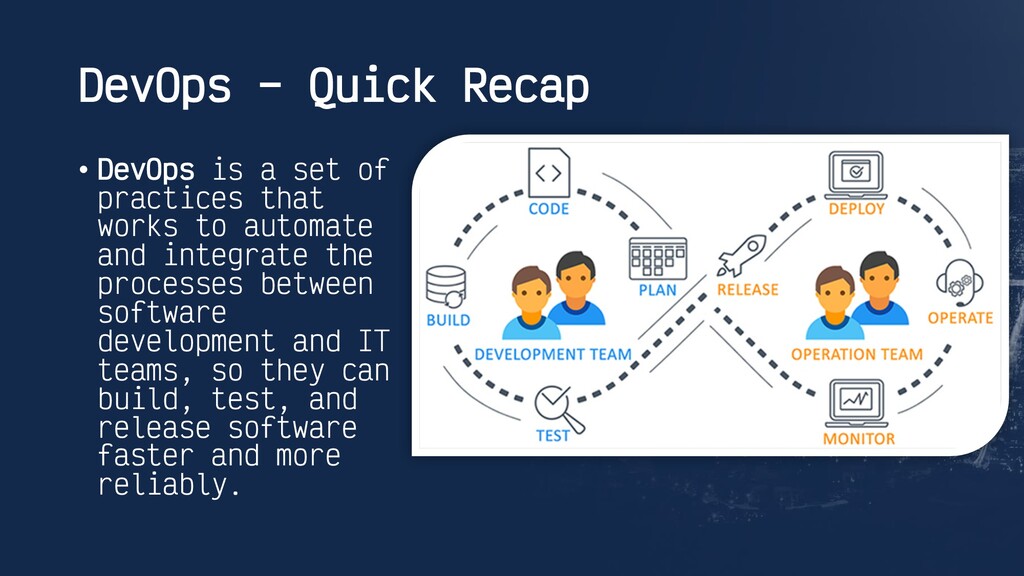
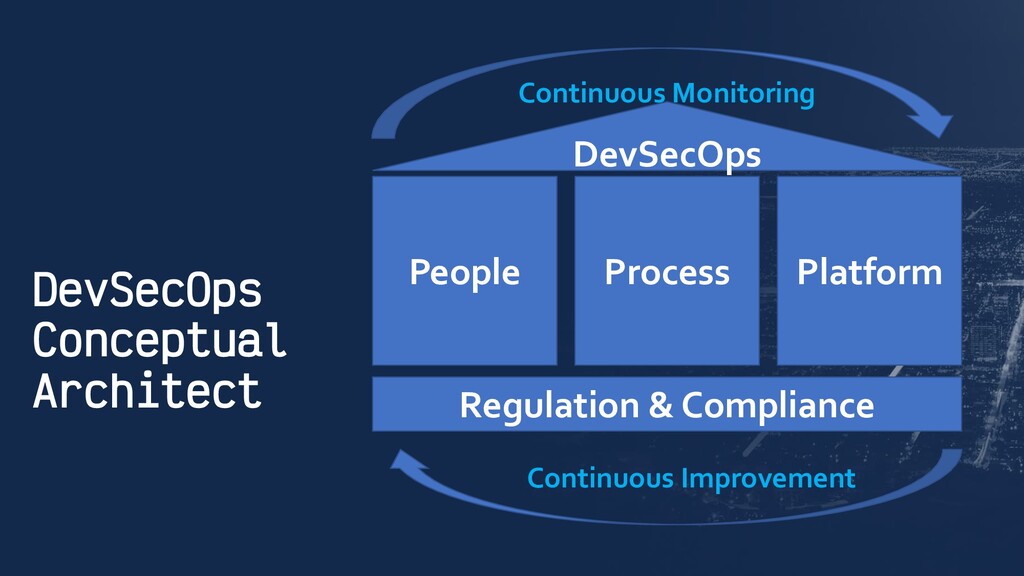
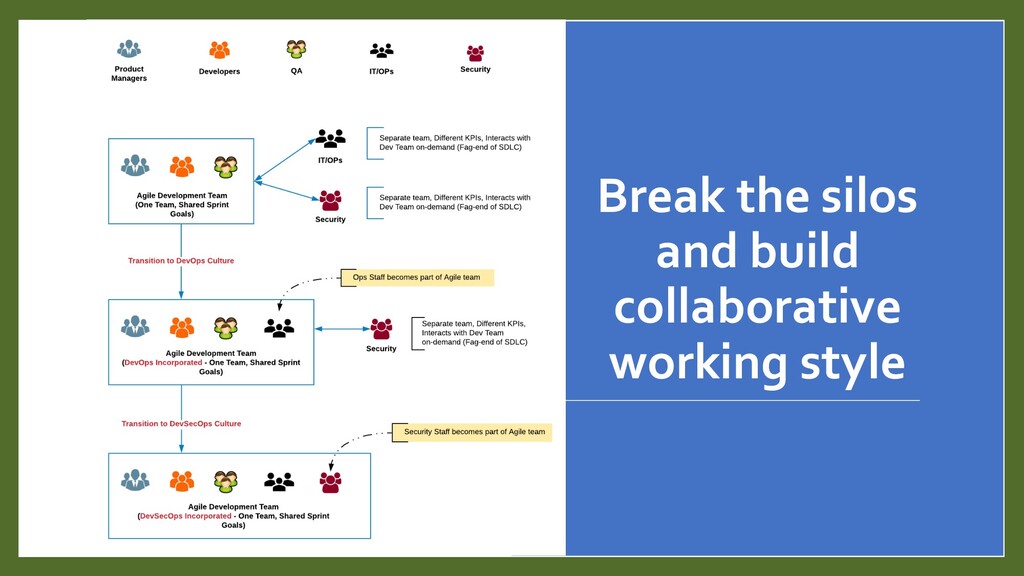
practices that works to automate and integrate the processes between software development and IT teams, so they can build, test, and release software faster and more reliably.
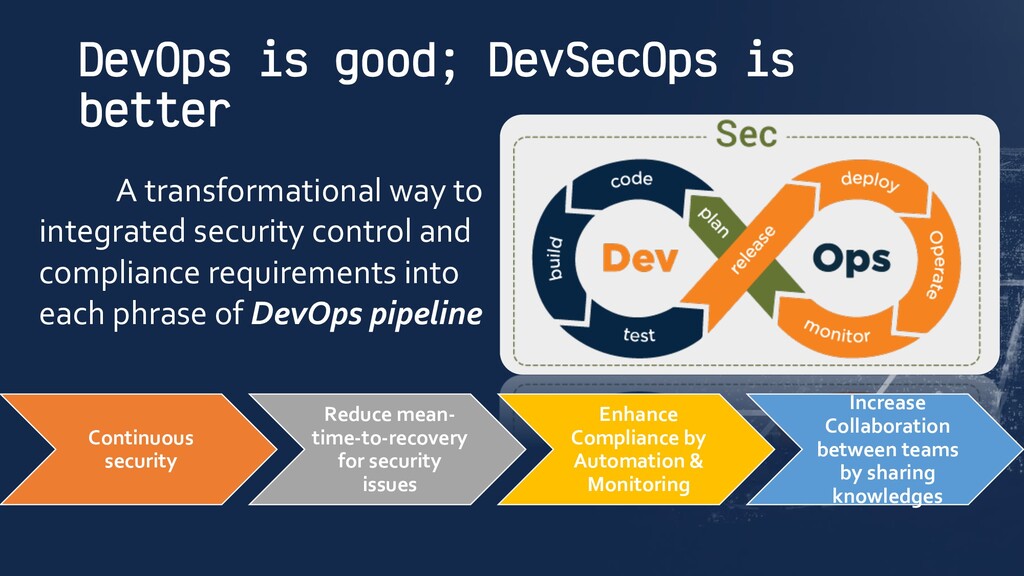
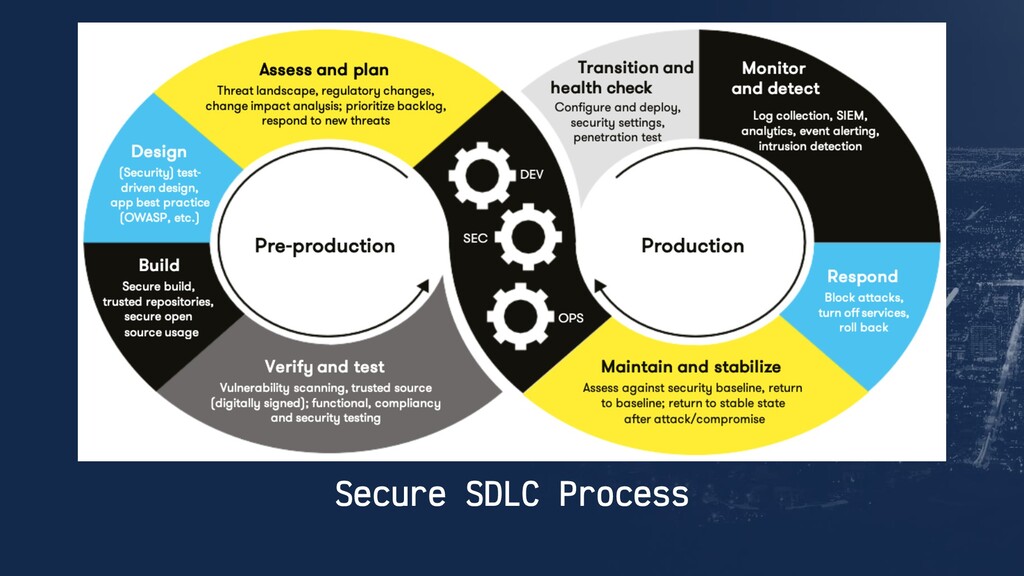
integrated security control and compliance requirements into each phrase of DevOps pipeline Continuous security Reduce mean- time-to-recovery for security issues Enhance Compliance by Automation & Monitoring Increase Collaboration between teams by sharing knowledges
services to help monitoring & measure DevOps • Empower DevOps engineers to take personal responsibility for security • Adopt version control and tight management of infrastructure automation tools Security • Incorporated application security testing for custom code • Adapt to “continuous security” • Involve to Development cycle
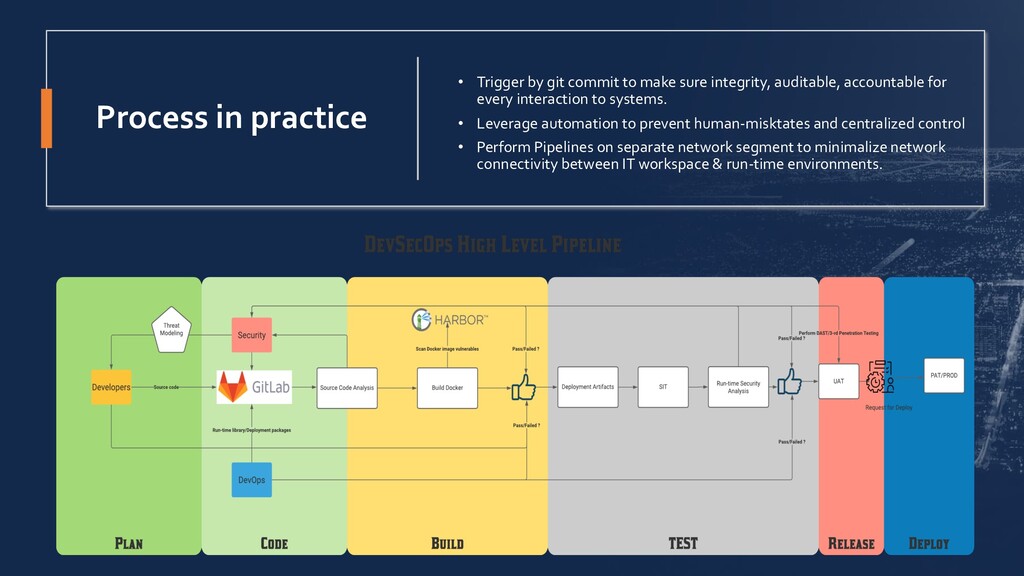
sure integrity, auditable, accountable for every interaction to systems. • Leverage automation to prevent human-misktates and centralized control • Perform Pipelines on separate network segment to minimalize network connectivity between IT workspace & run-time environments.
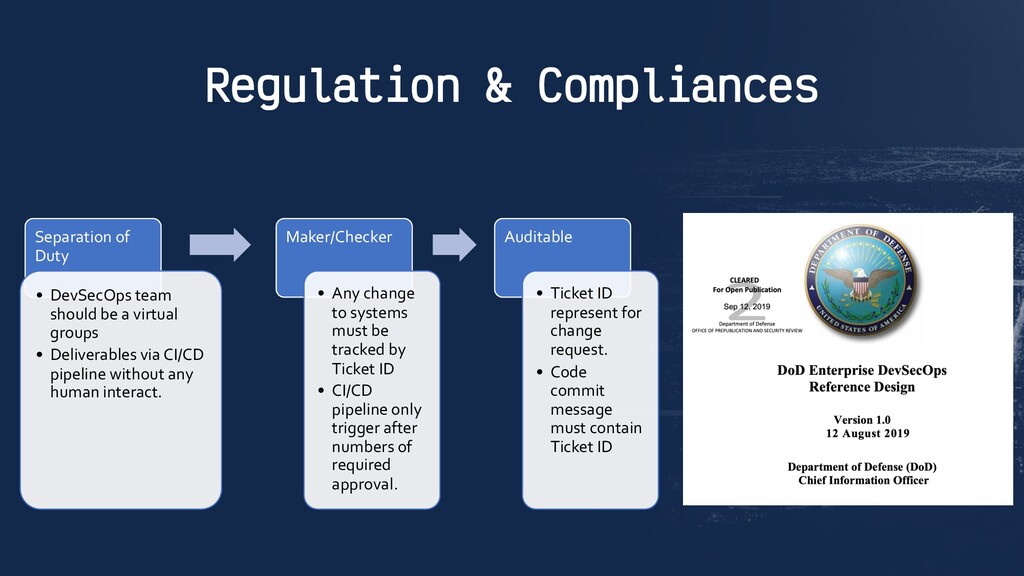
be a virtual groups • Deliverables via CI/CD pipeline without any human interact. Maker/Checker • Any change to systems must be tracked by Ticket ID • CI/CD pipeline only trigger after numbers of required approval. Auditable • Ticket ID represent for change request. • Code commit message must contain Ticket ID
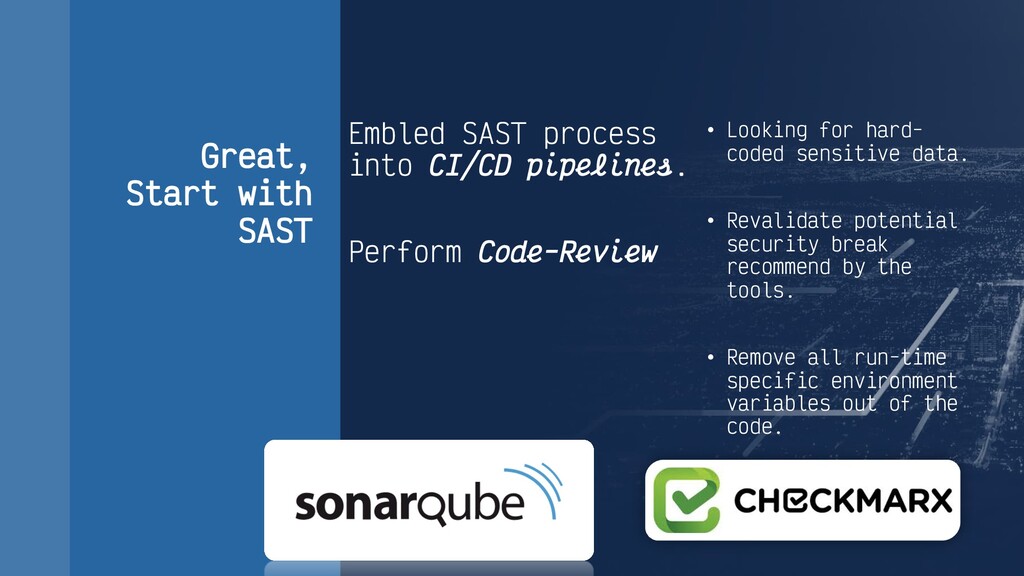
Perform Code-Review • Looking for hard- coded sensitive data. • Revalidate potential security break recommend by the tools. • Remove all run-time specific environment variables out of the code.
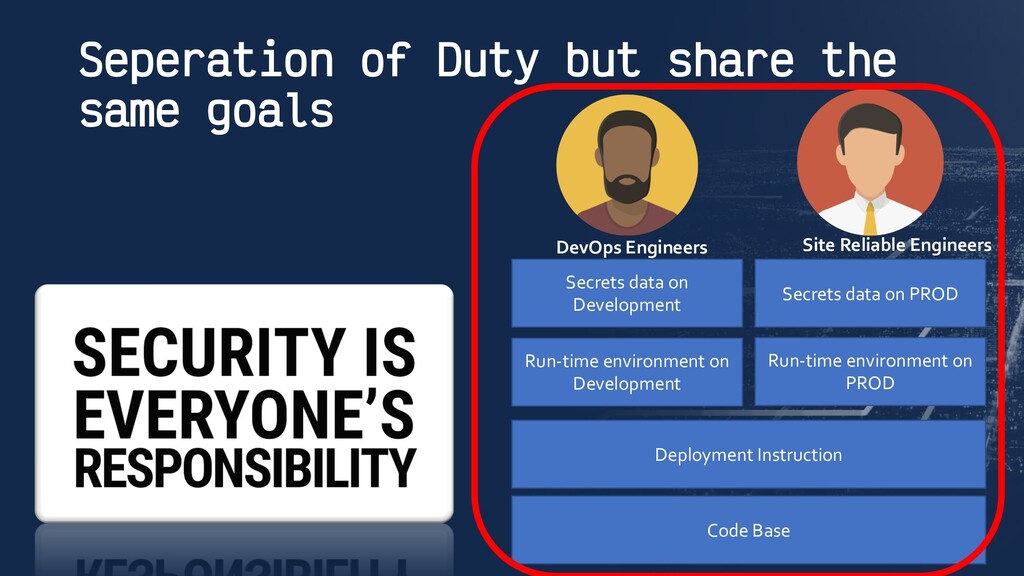
Deployment Instruction Run-time environment on Development Run-time environment on PROD Secrets data on Development Secrets data on PROD DevOps Engineers Site Reliable Engineers
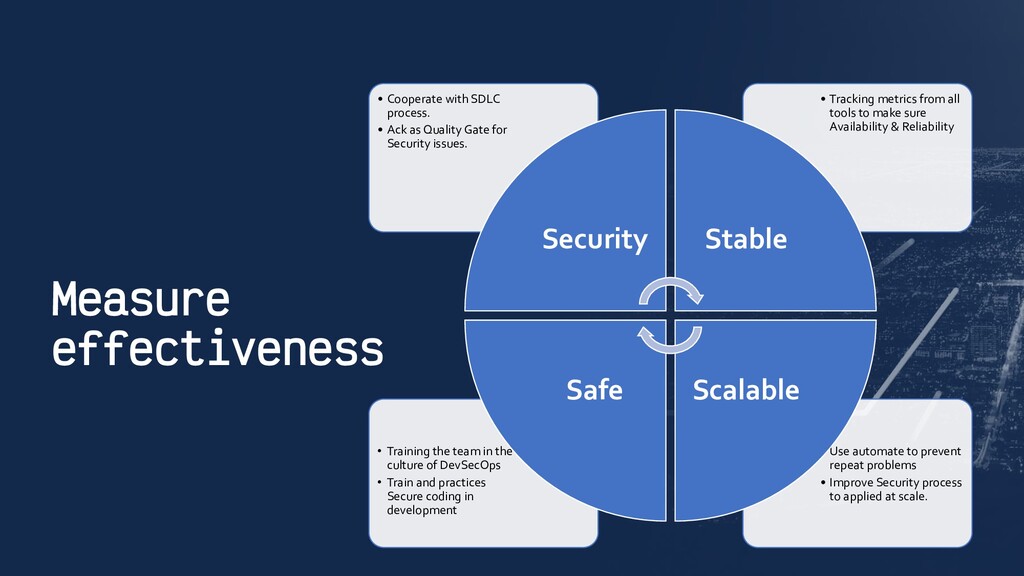
Improve Security process to applied at scale. • Training the team in the culture of DevSecOps • Train and practices Secure coding in development • Tracking metrics from all tools to make sure Availability & Reliability • Cooperate with SDLC process. • Ack as Quality Gate for Security issues. Security Stable Scalable Safe
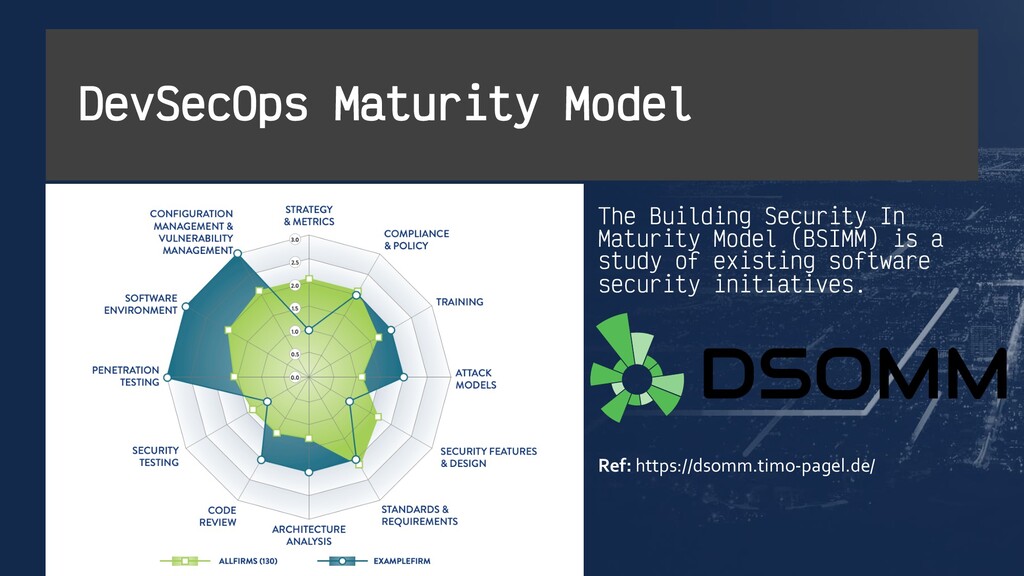
https://dsomm.timo-pagel.de/ • Mitigating the Risk of Software 1 Vulnerabilities by Adopting a Secure 2 3 Software Development Framework (SSDF) https://csrc.nist.gov/CSRC/media/Publications/white-paper/2019/06/07/mitigating-risk-of-software-vulnerabilities-with- ssdf/draft/documents/ssdf-for-mitigating-risk-of-software-vulns-draft.pdf


 kash1064
 recruitengineers
 codmoninc
 camiha
 endonanana
 koukihosaka
 shuta13
 persolserverworks
 ludicmind
 yazm
 yuuuuuuu168
 eileencodes
 marcduiker
 shpigford
 marketingsoph
 retrage
 skipperchong
 addyosmani
 aemeredith
 axbom
 trallard
 jakevdp
 varn