Share
Embed
PAR: Securing the OAuth and OpenID Connect Front Channel
Duende Software
January 09, 2024
Transcript
20 slides
-
Securing the OAuth and OpenID Connect Front Channel Dominick Baier
@leastprivilege https://duendesoftware.com Pushed Authorization Requests (PAR) RFC 9126 -
2 @duendeidentity Me • Dominick – 20+ years consulting and
project work in the identity space – co-creator of IdentityServer & IdentityModel OSS projects – co-Founder of Duende Software slides https://speakerdeck.com/duendesoftware email [email protected] -
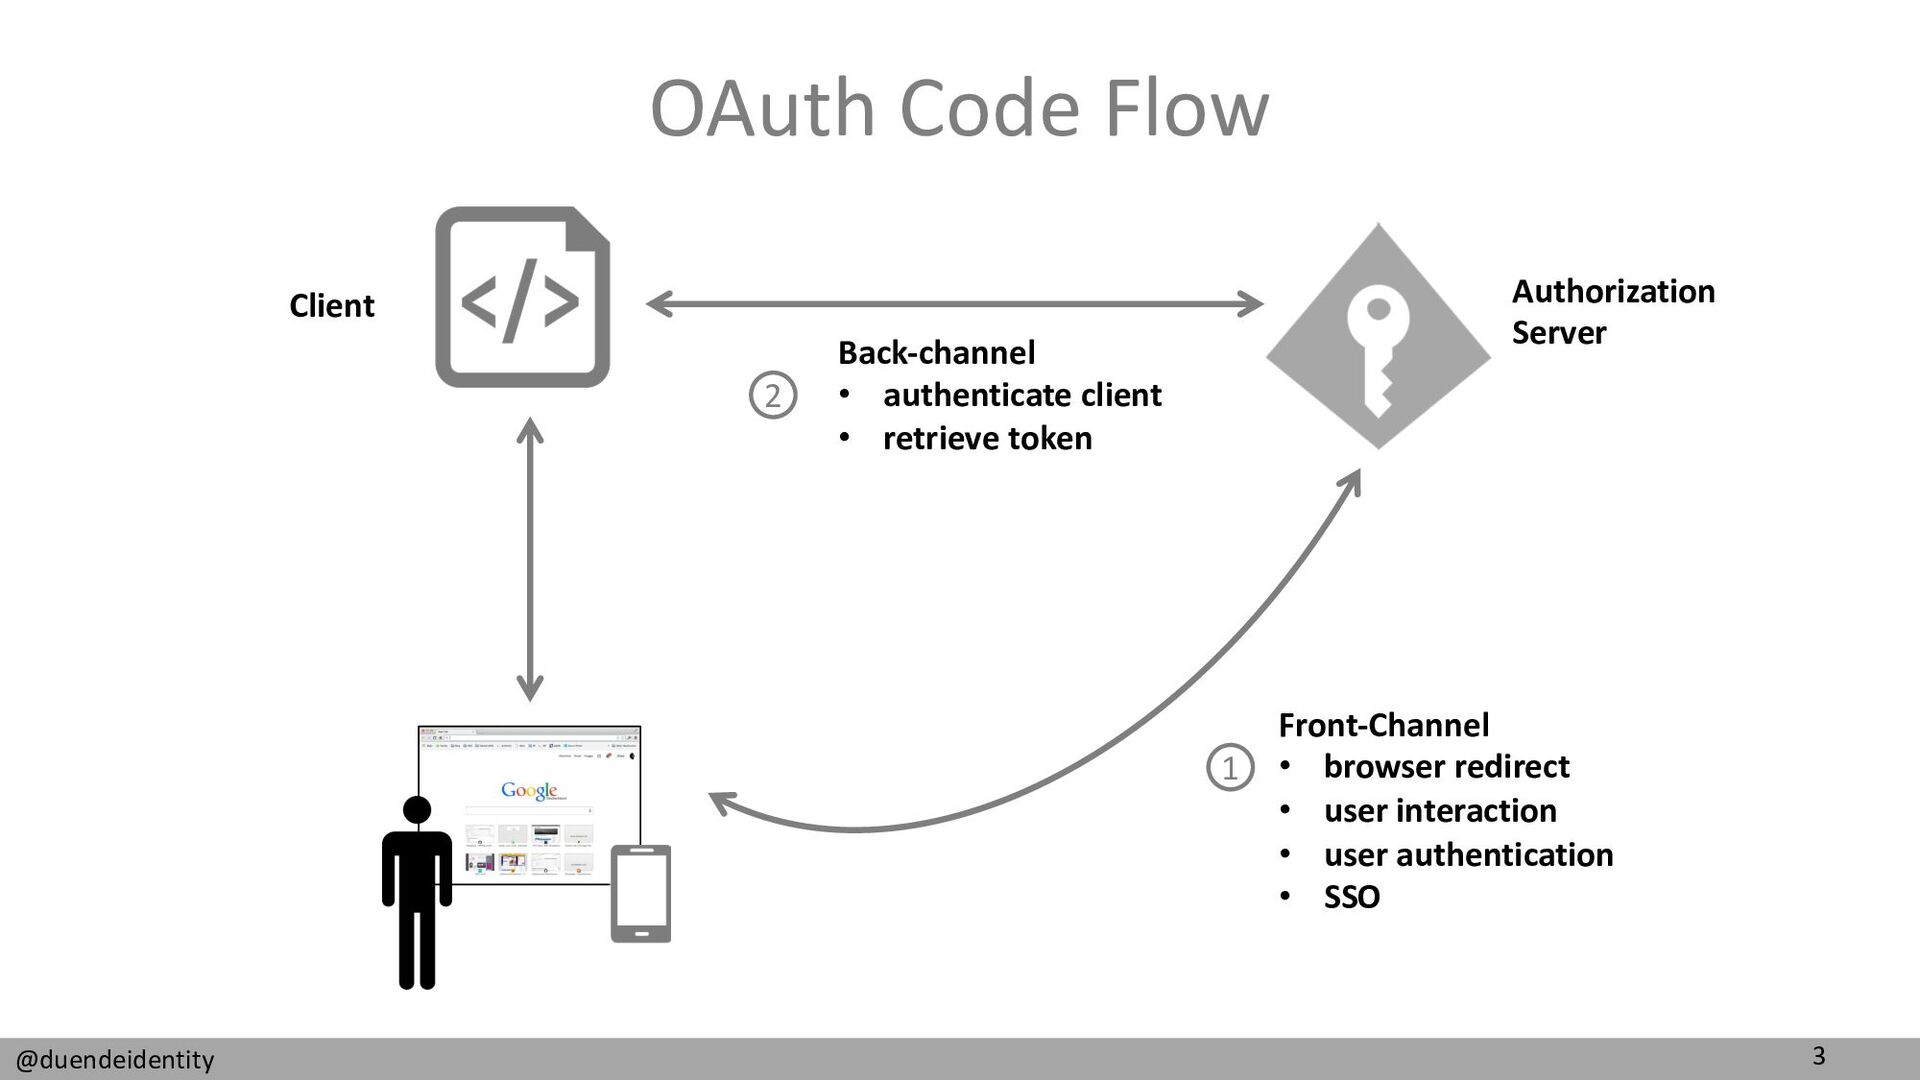
3 @duendeidentity OAuth Code Flow Front-Channel • browser redirect •
user interaction • user authentication • SSO Back-channel • authenticate client • retrieve token 2 1 Client Authorization Server -
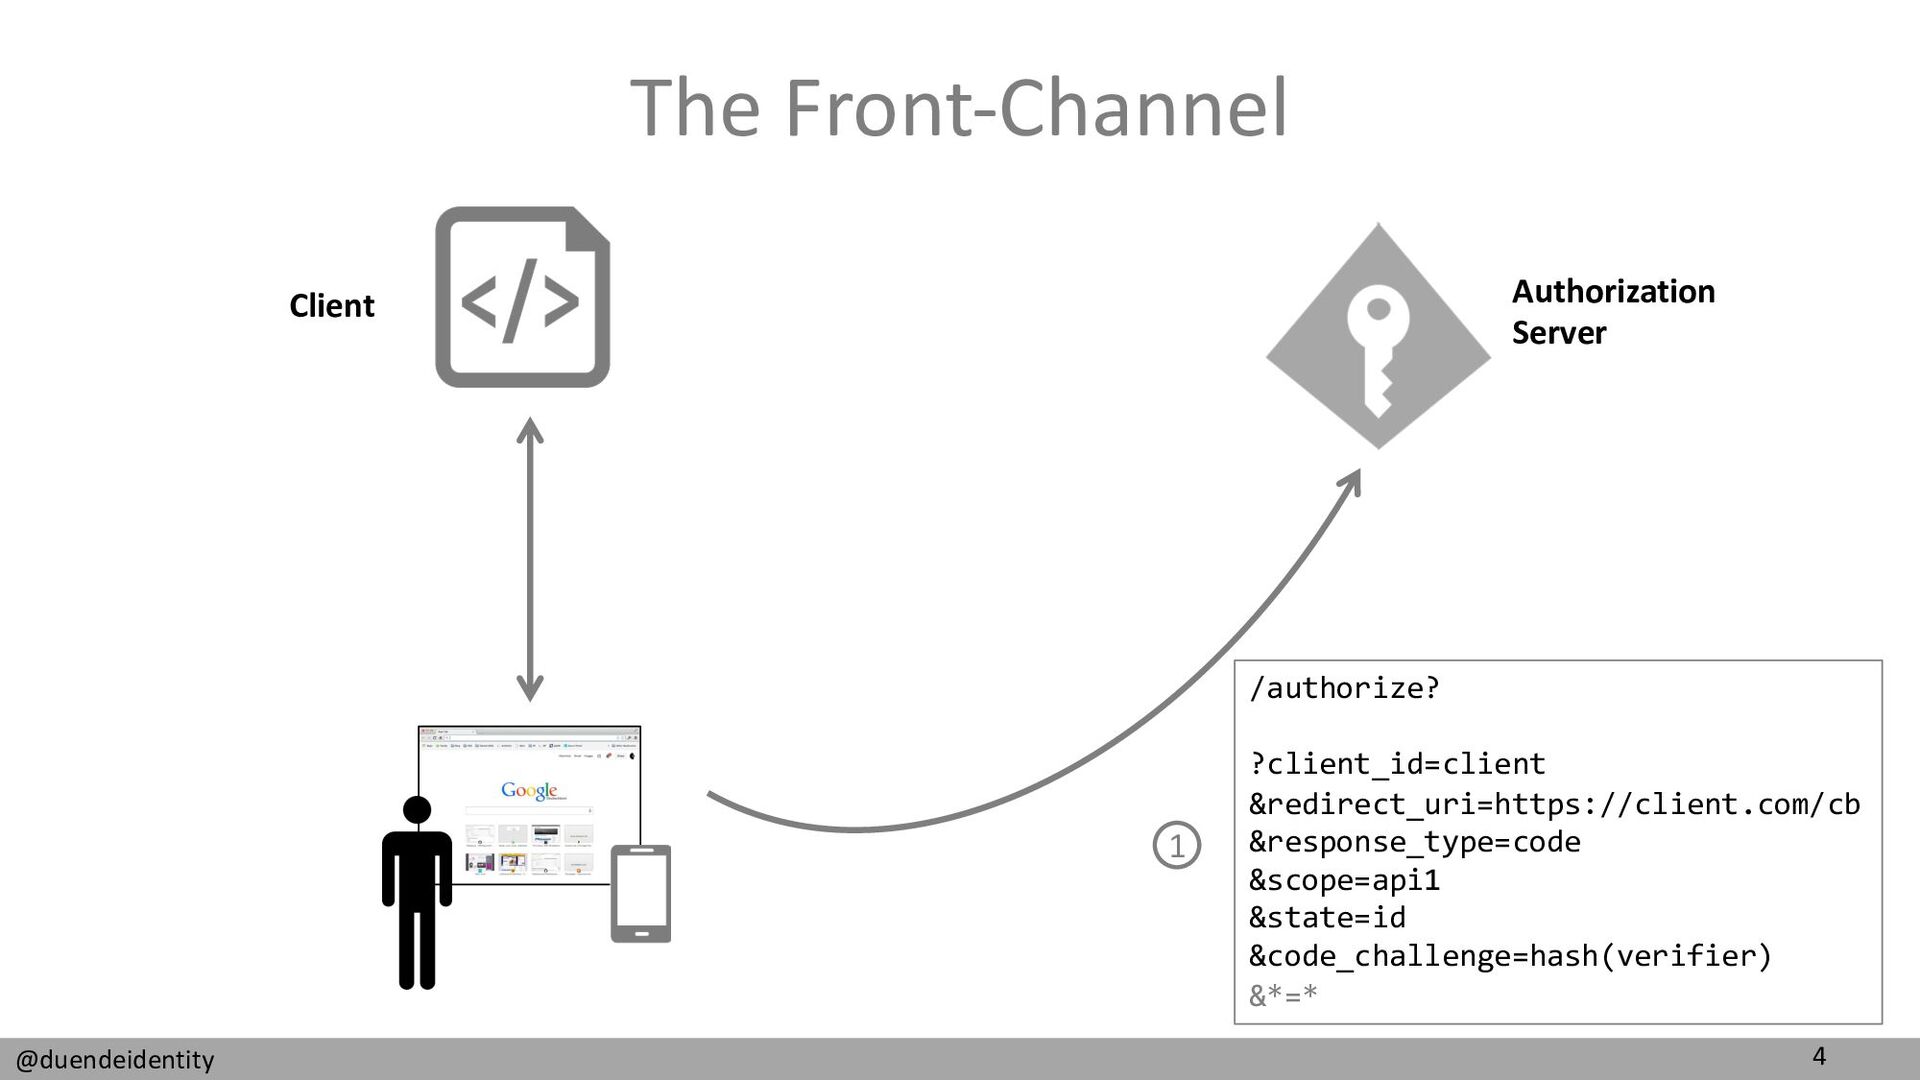
4 @duendeidentity The Front-Channel /authorize? ?client_id=client &redirect_uri=https://client.com/cb &response_type=code &scope=api1 &state=id
&code_challenge=hash(verifier) &*=* 1 Client Authorization Server -
6 @duendeidentity In Summary • There is no cryptographic integrity
and authenticity protection – an attacker could, for example, modify the scope of access requested or swap the context of a payment transaction by changing scope values • There is no mechanism to ensure confidentiality of the request parameters – although HTTPS is required, request data passes through the user agent in the clear, and query string data can inadvertently leak to web server logs and to other sites via the referrer. • Authorization request URLs can become quite large, especially in scenarios requiring fine-grained authorization data/scopes • Allowing to package the whole authorize request into a URL opens the door for all kinds of click/phishing attacks -
7 @duendeidentity Better solutions 1. remove parameters from the authorize
request 2. make the parameters tamper proof 3. authenticate the client at the authorize endpoint to help validation -
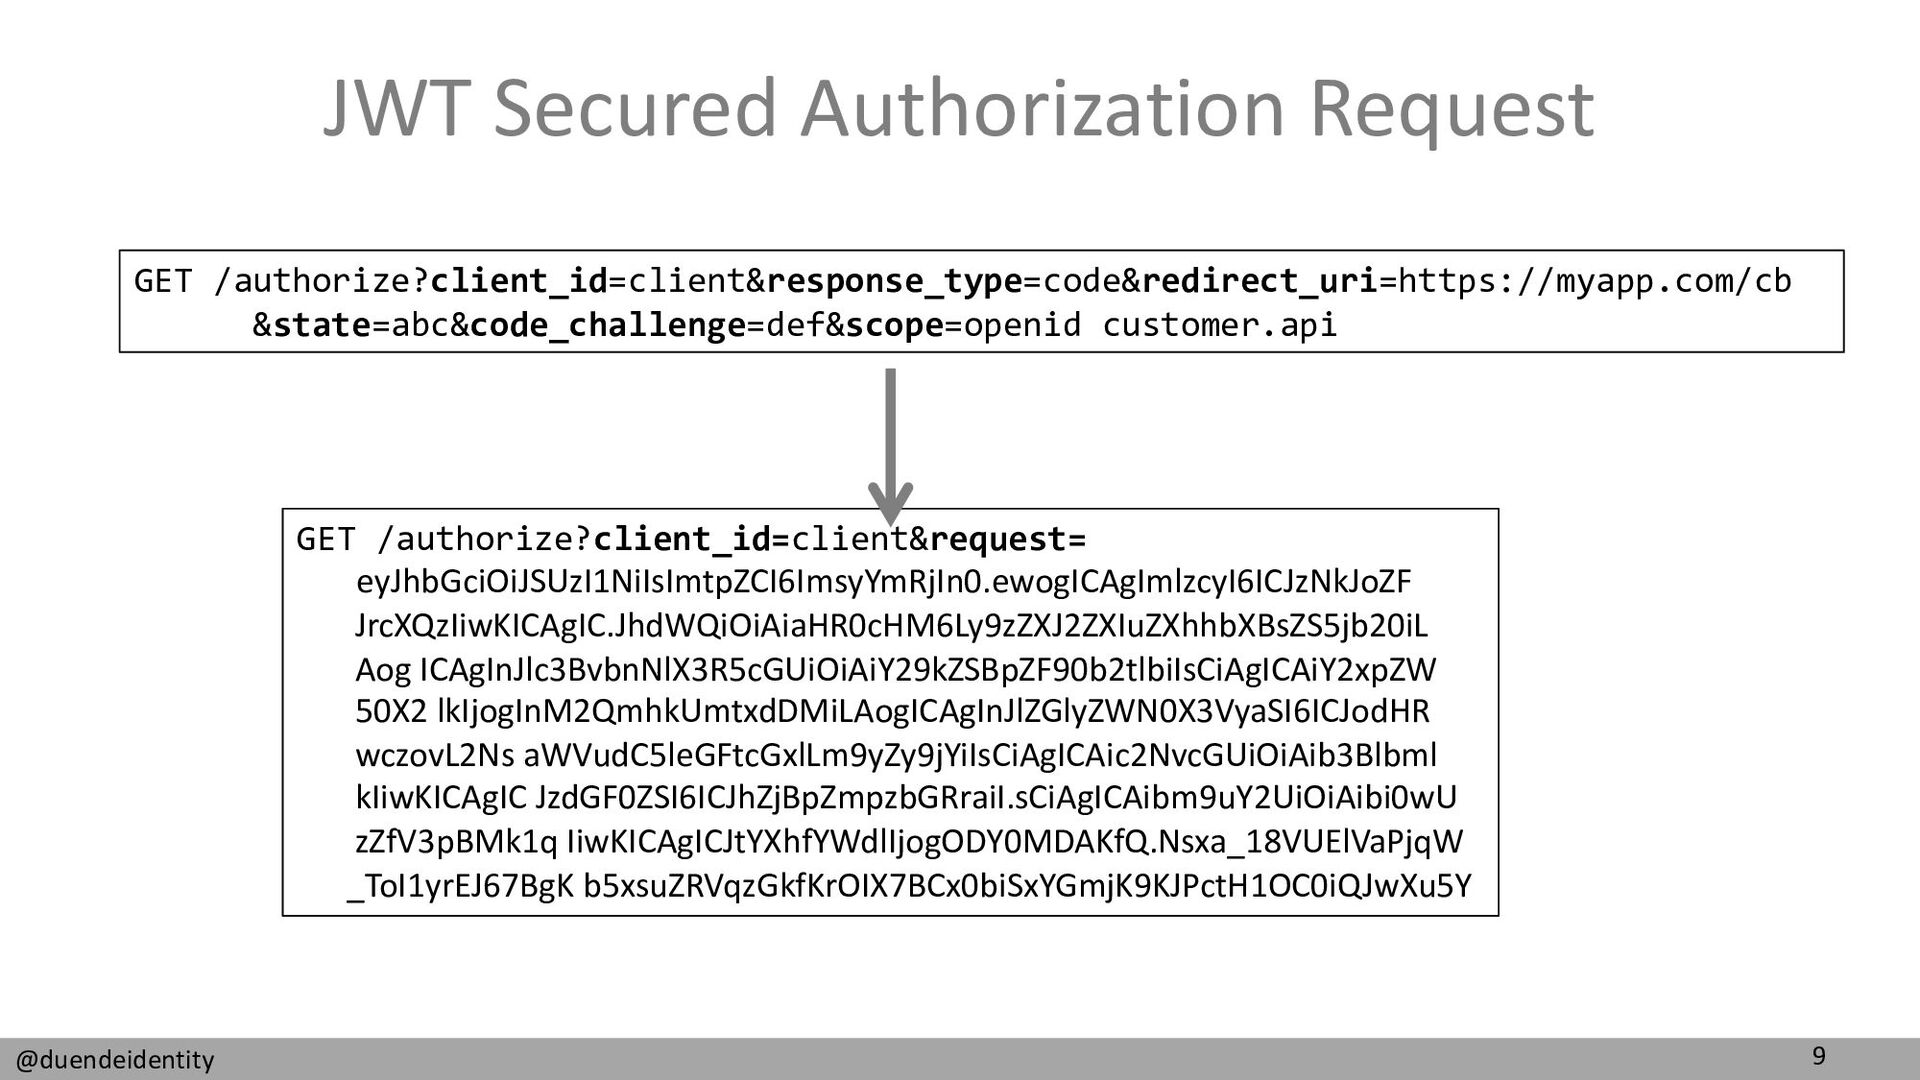
9 @duendeidentity JWT Secured Authorization Request GET /authorize?client_id=client&response_type=code&redirect_uri=https://myapp.com/cb &state=abc&code_challenge=def&scope=openid customer.api
GET /authorize?client_id=client&request= eyJhbGciOiJSUzI1NiIsImtpZCI6ImsyYmRjIn0.ewogICAgImlzcyI6ICJzNkJoZF JrcXQzIiwKICAgIC.JhdWQiOiAiaHR0cHM6Ly9zZXJ2ZXIuZXhhbXBsZS5jb20iL Aog ICAgInJlc3BvbnNlX3R5cGUiOiAiY29kZSBpZF90b2tlbiIsCiAgICAiY2xpZW 50X2 lkIjogInM2QmhkUmtxdDMiLAogICAgInJlZGlyZWN0X3VyaSI6ICJodHR wczovL2Ns aWVudC5leGFtcGxlLm9yZy9jYiIsCiAgICAic2NvcGUiOiAib3Blbml kIiwKICAgIC JzdGF0ZSI6ICJhZjBpZmpzbGRraiI.sCiAgICAibm9uY2UiOiAibi0wU zZfV3pBMk1q IiwKICAgICJtYXhfYWdlIjogODY0MDAKfQ.Nsxa_18VUElVaPjqW _ToI1yrEJ67BgK b5xsuZRVqzGkfKrOIX7BCx0biSxYGmjK9KJPctH1OC0iQJwXu5Y -
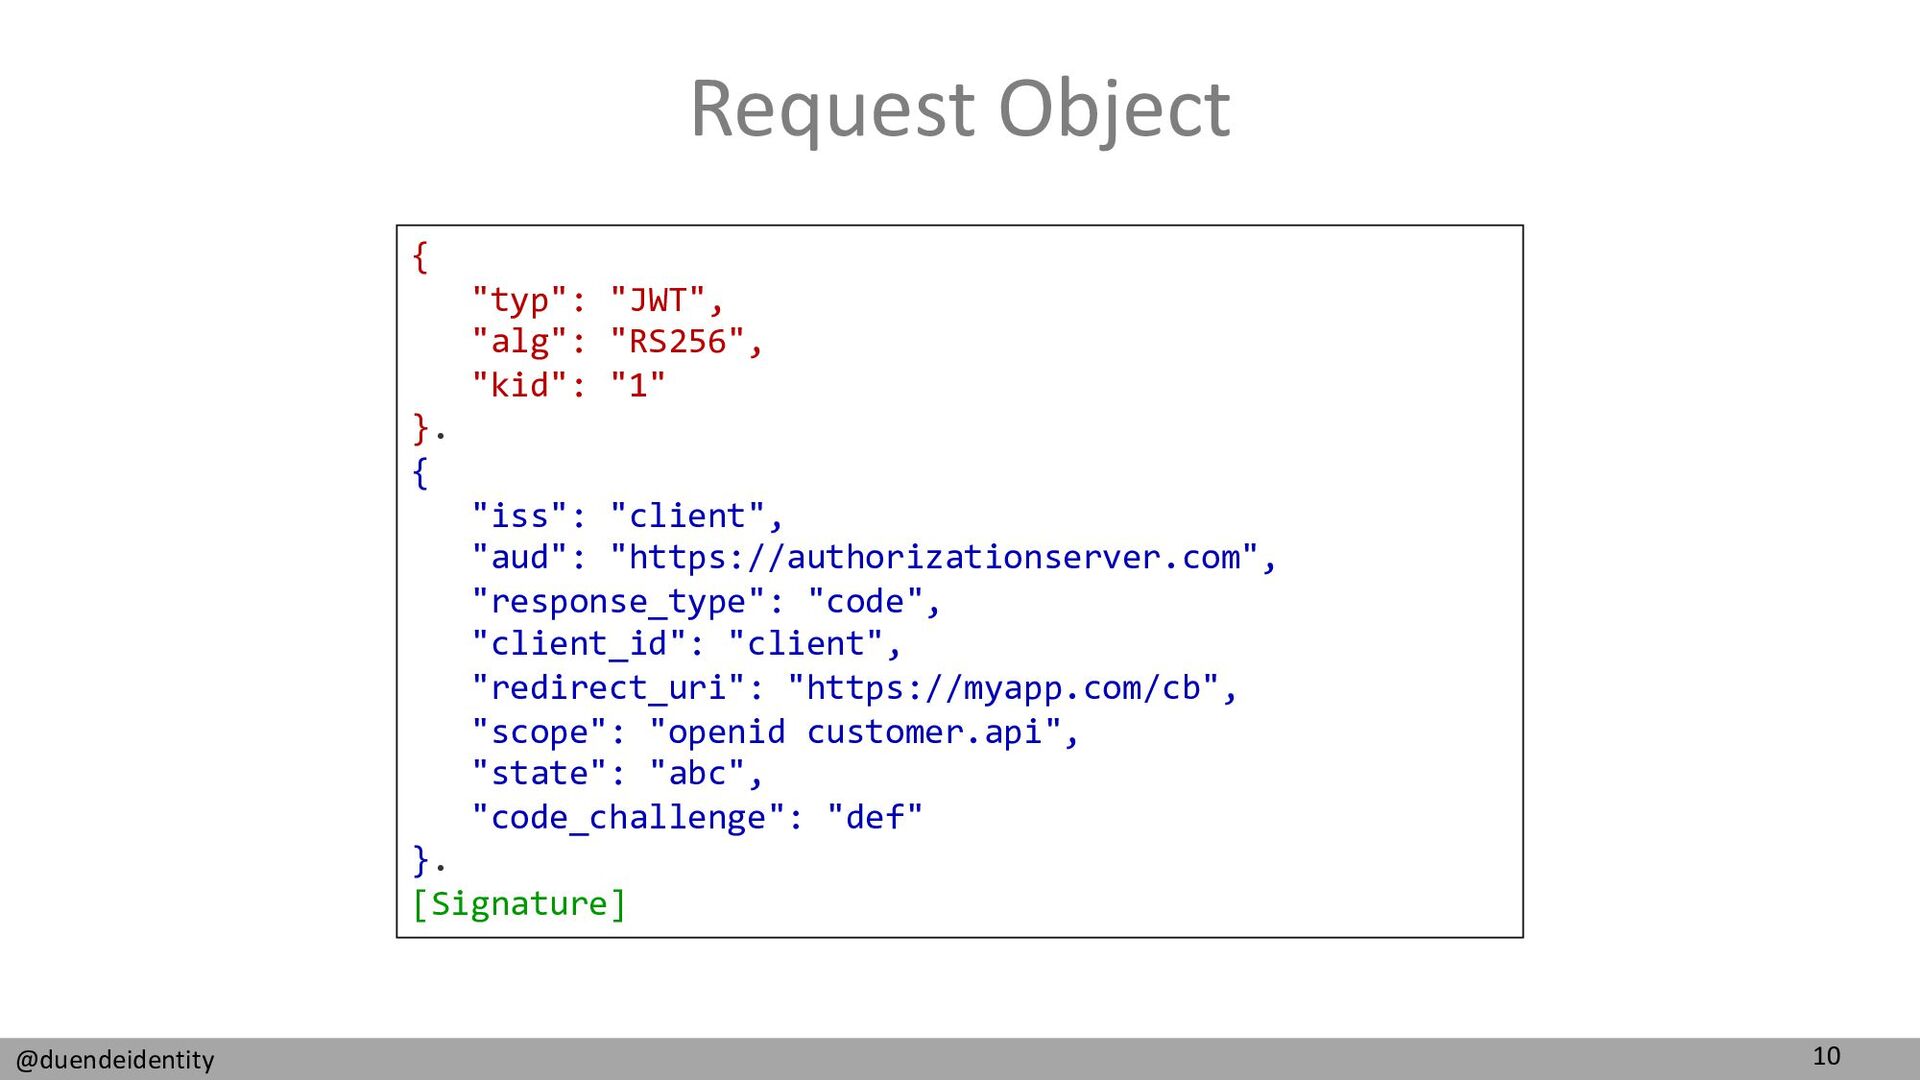
10 @duendeidentity Request Object { "typ": "JWT", "alg": "RS256", "kid":
"1" }. { "iss": "client", "aud": "https://authorizationserver.com", "response_type": "code", "client_id": "client", "redirect_uri": "https://myapp.com/cb", "scope": "openid customer.api", "state": "abc", "code_challenge": "def" }. [Signature] -
11 @duendeidentity Issues with JAR • Increased complexity – key
management (maybe in addition to existing client secret) – crypto and JWT creation in client application • lack of client library support – increased size of URLs -
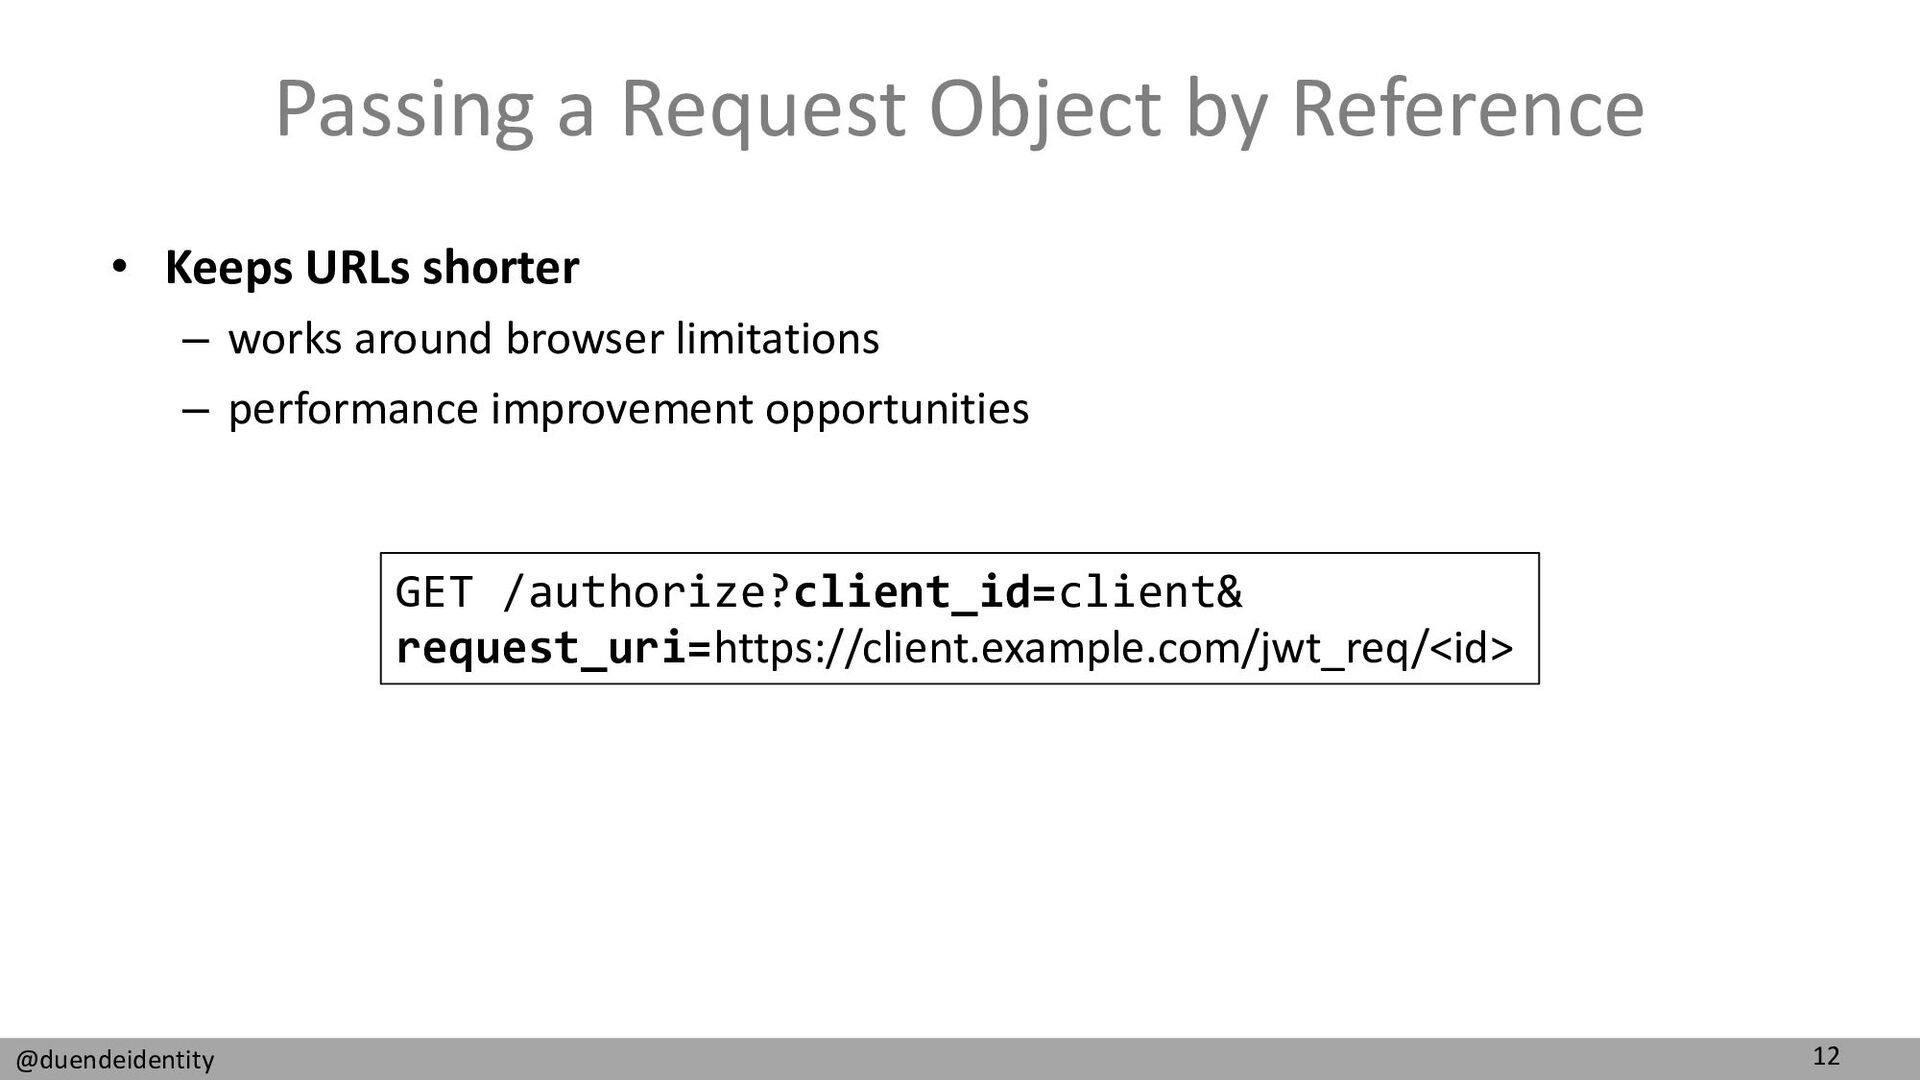
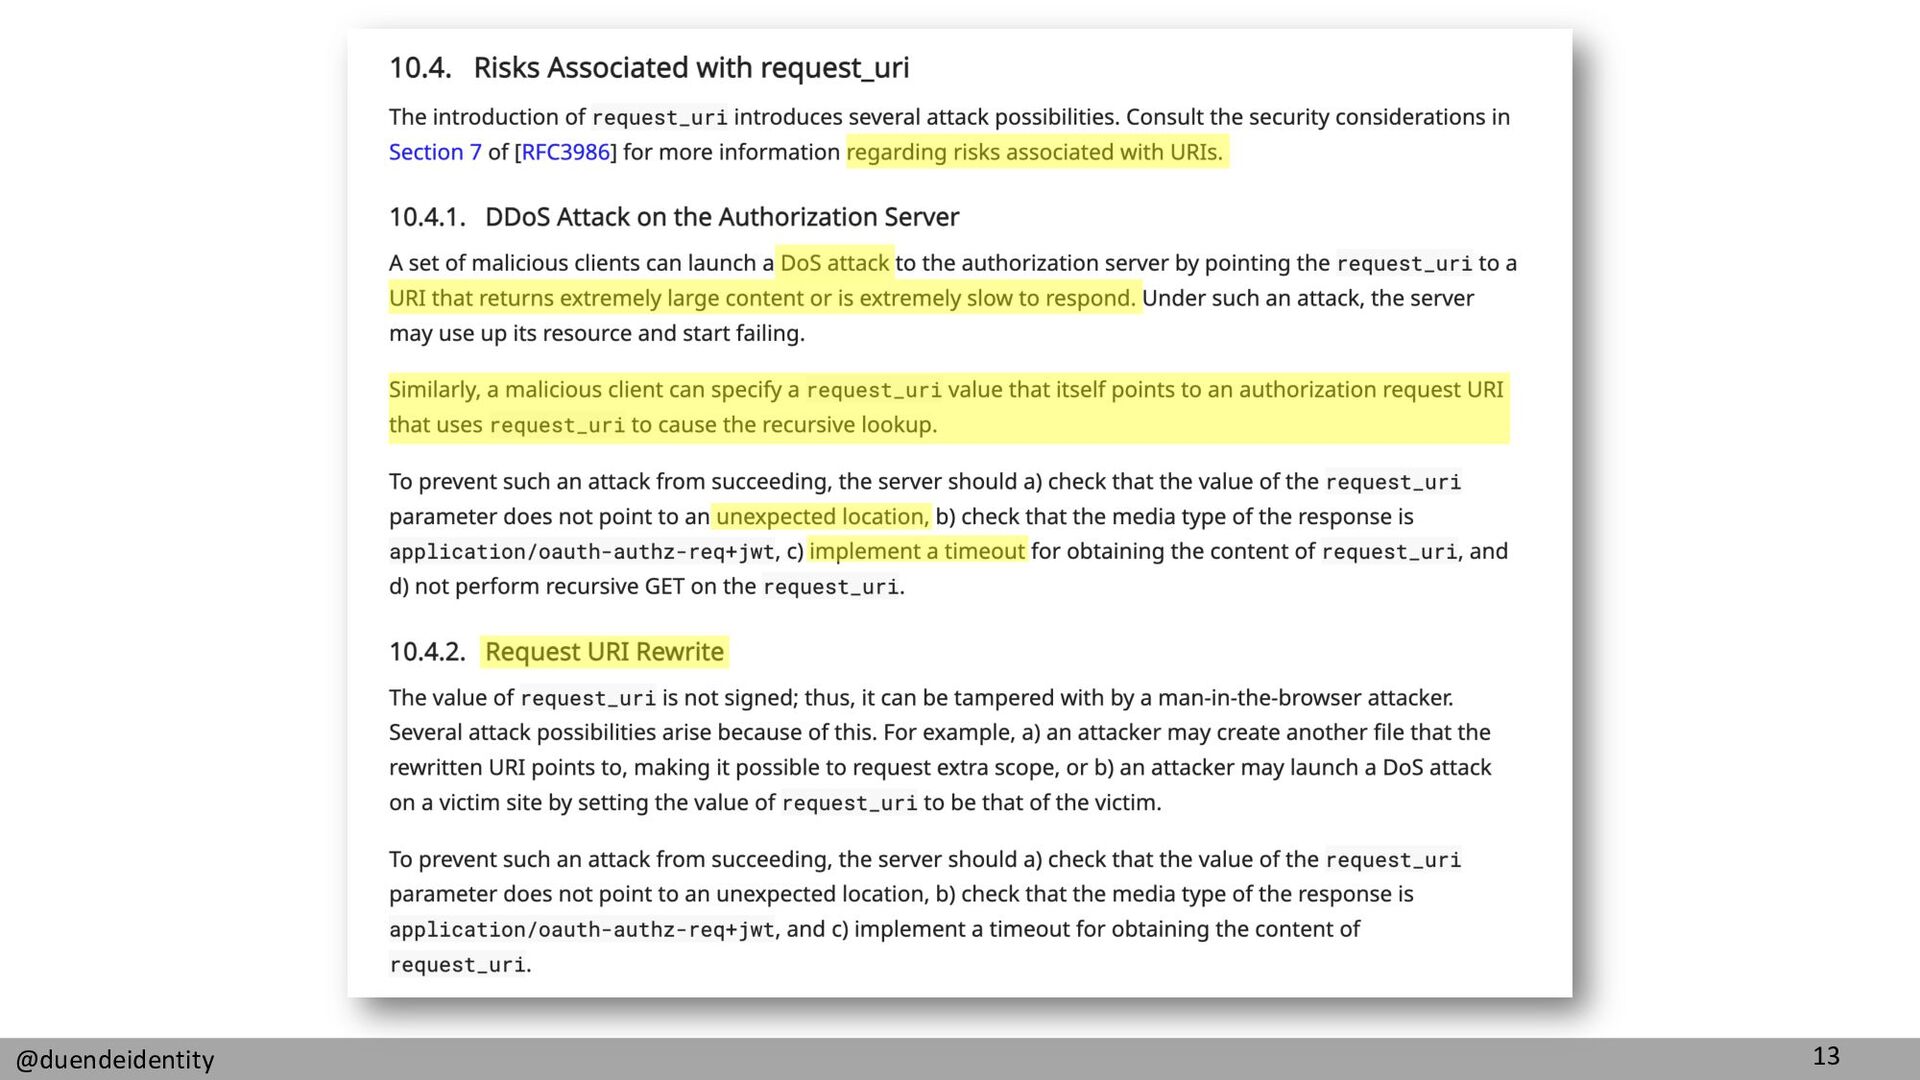
12 @duendeidentity Passing a Request Object by Reference • Keeps
URLs shorter – works around browser limitations – performance improvement opportunities GET /authorize?client_id=client& request_uri=https://client.example.com/jwt_req/<id> -
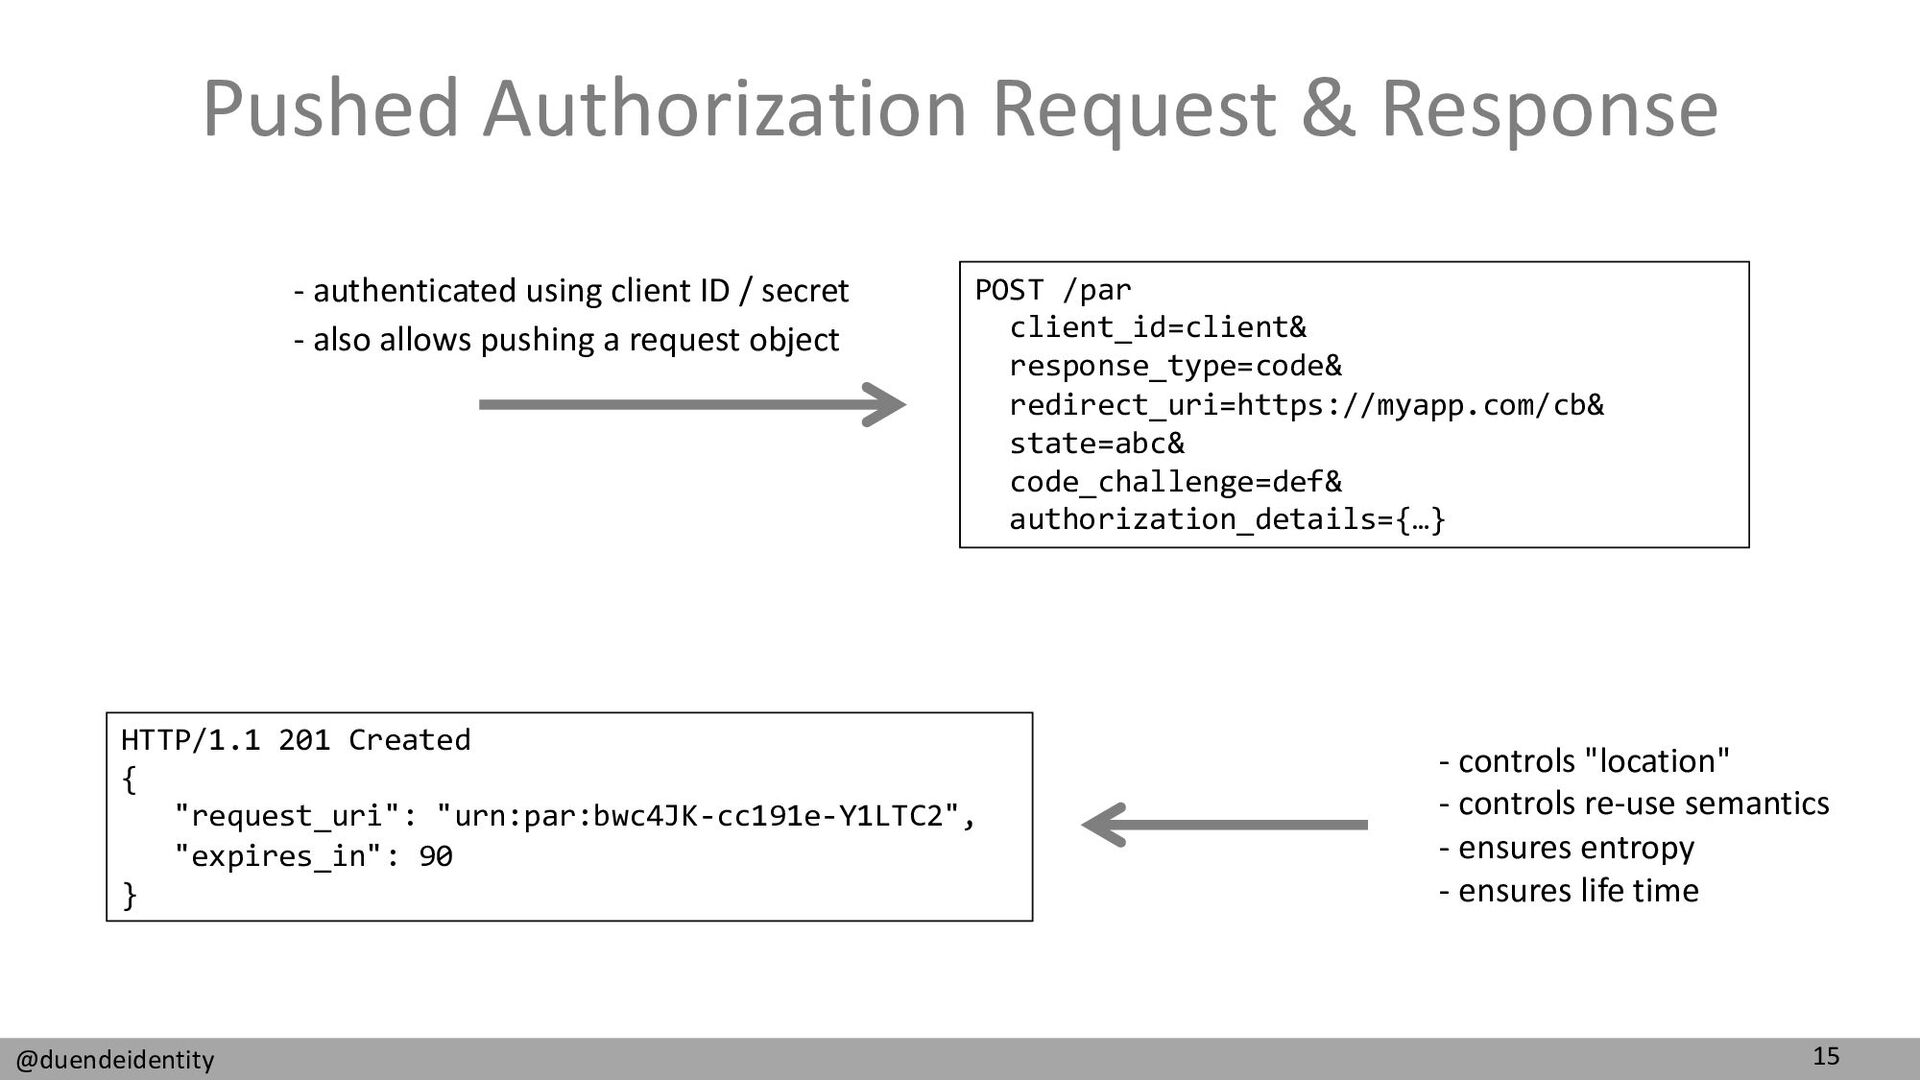
15 @duendeidentity Pushed Authorization Request & Response POST /par client_id=client&
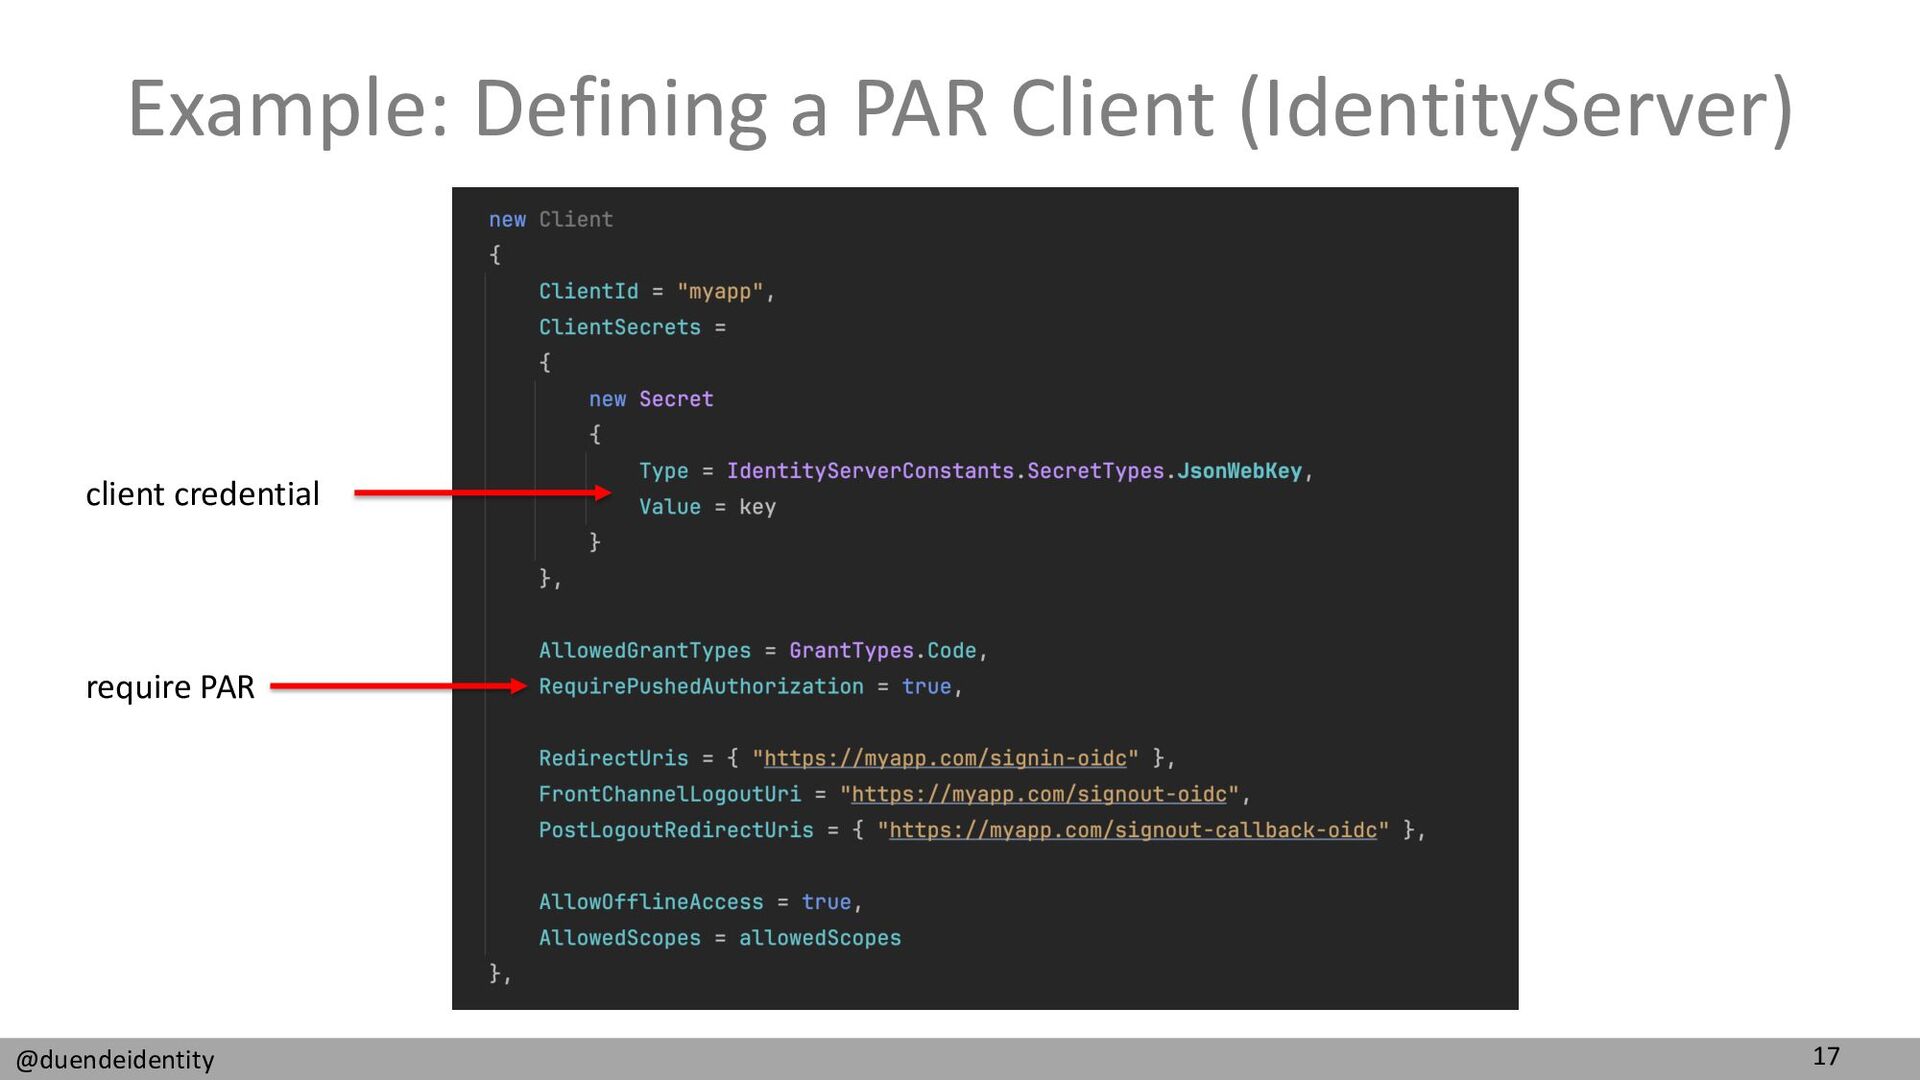
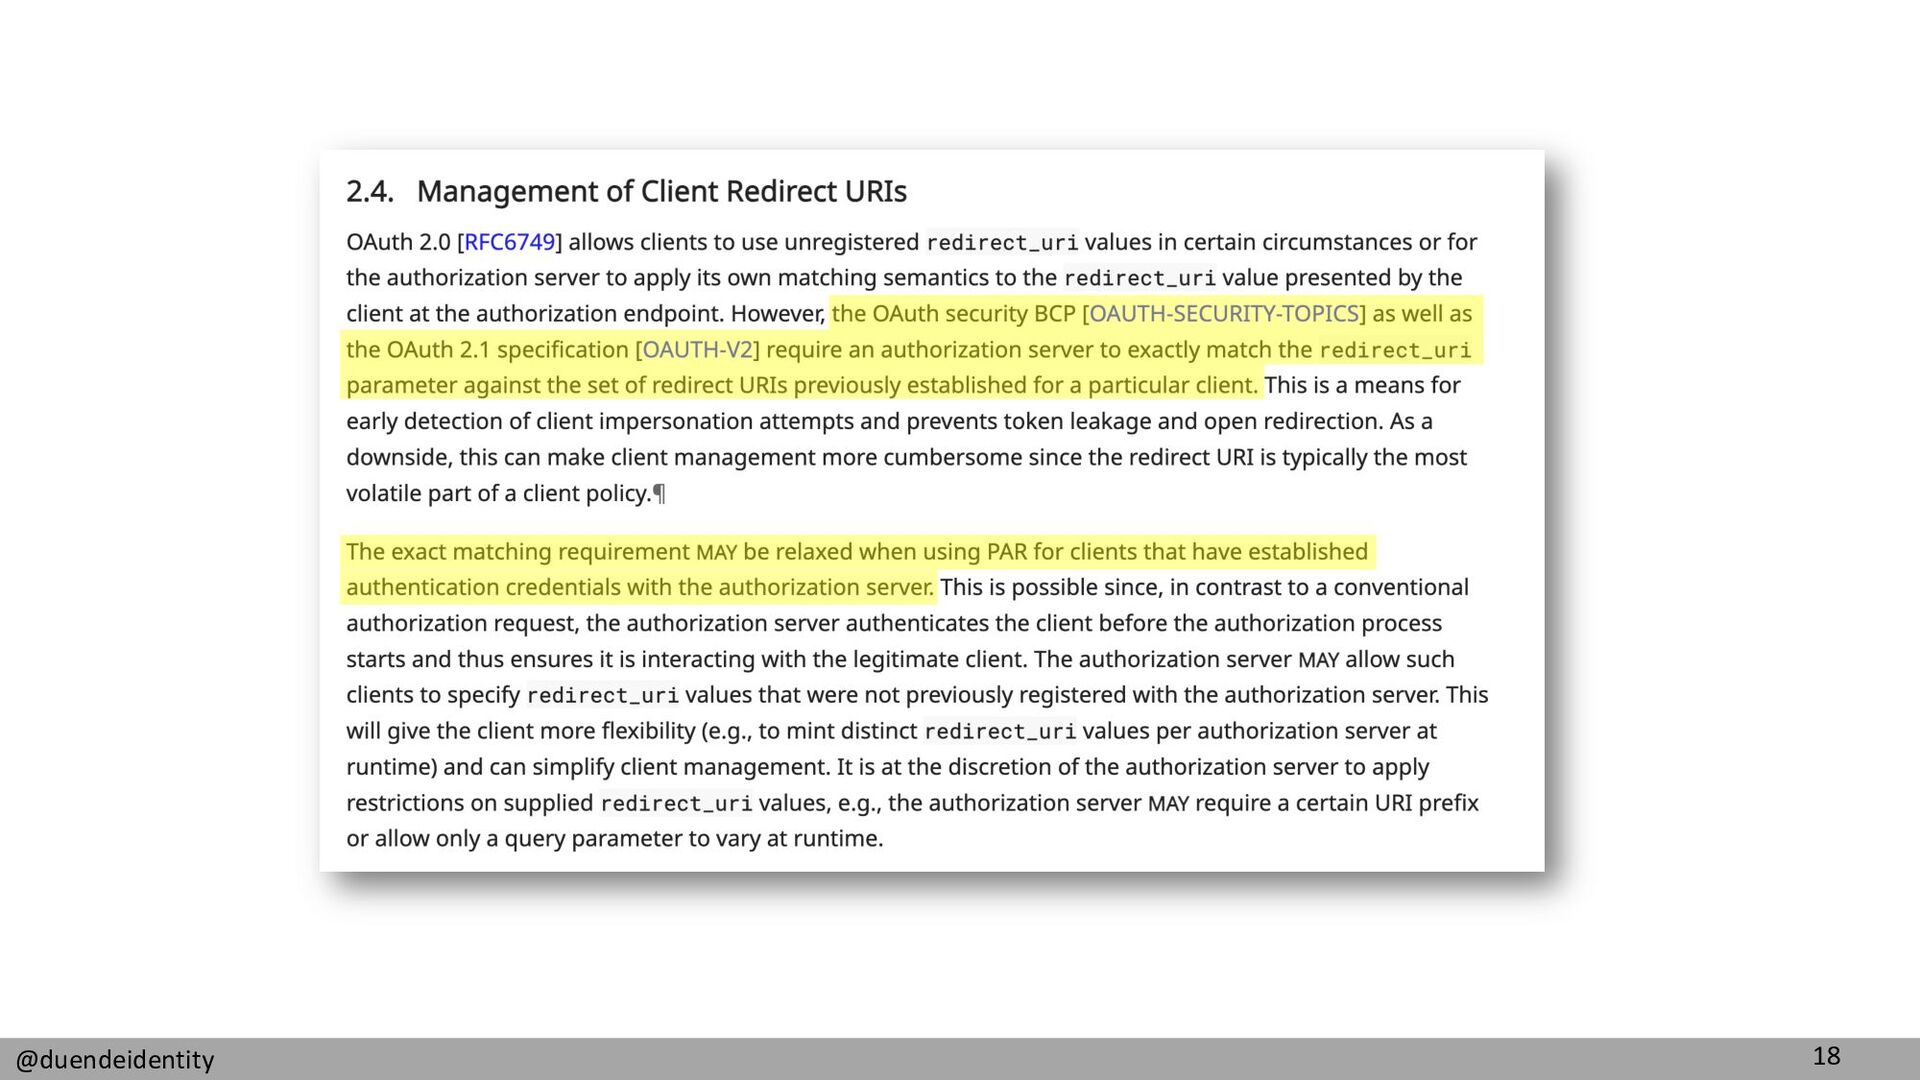
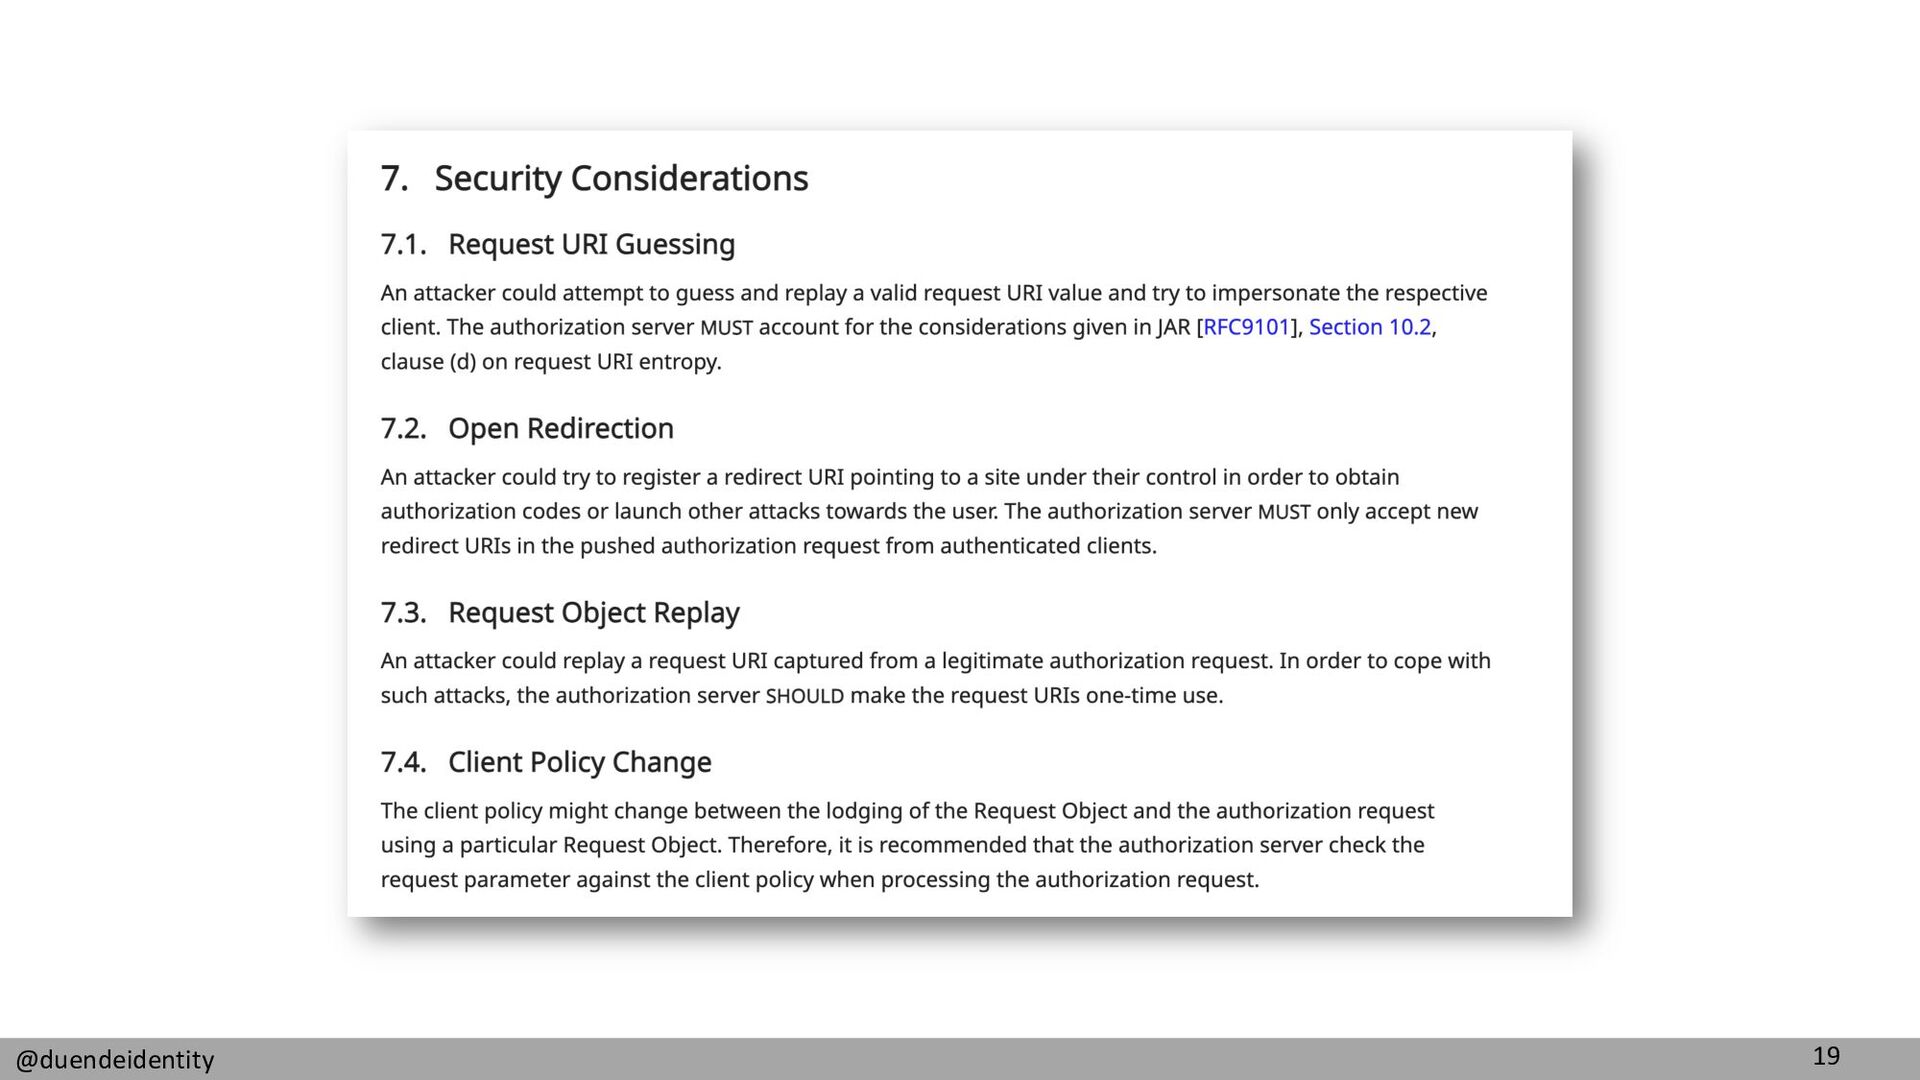
response_type=code& redirect_uri=https://myapp.com/cb& state=abc& code_challenge=def& authorization_details={…} HTTP/1.1 201 Created { "request_uri": "urn:par:bwc4JK-cc191e-Y1LTC2", "expires_in": 90 } - authenticated using client ID / secret - also allows pushing a request object - controls "location" - controls re-use semantics - ensures entropy - ensures life time -
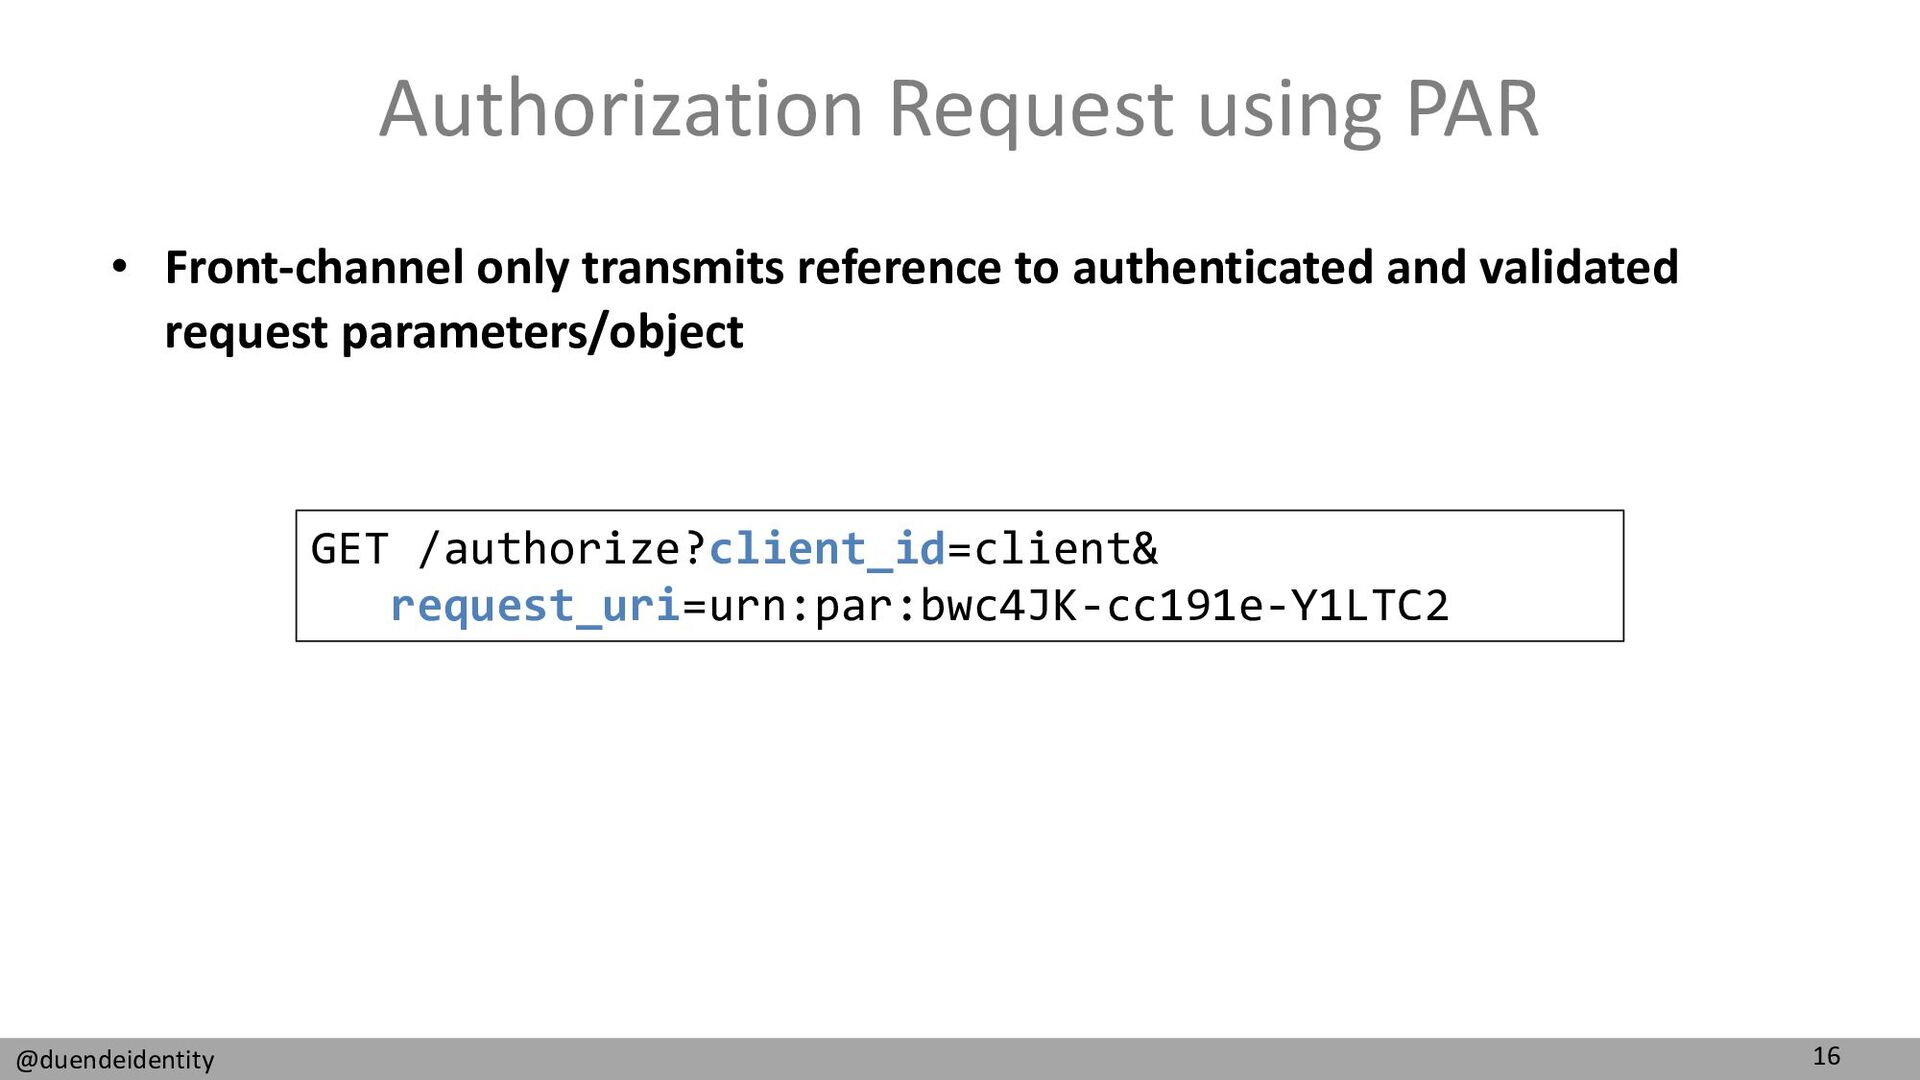
16 @duendeidentity Authorization Request using PAR • Front-channel only transmits
reference to authenticated and validated request parameters/object GET /authorize?client_id=client& request_uri=urn:par:bwc4JK-cc191e-Y1LTC2 -
20 @duendeidentity Summary • PAR eliminates a whole class of
attacks against OAuth/OpenID Connect • Simple to implement • Should be the default going forward • Client libraries need to catch up