Share
Embed
DDD17 - Web Applications Automated Security Testing in a Continuous Delivery Pipeline
Slides from "Web Applications Automated Security Testing in a Continuous Delivery Pipeline" workshop, made during Drupal Developers Days 2017 at Seville, Spain
Fedir RYKHTIK
March 21, 2017
Transcript
41 slides
-
Web Applications Automated Security Testing in a Continuous Delivery Pipeline
At #DrupalDevDaysSeville by @FedirFr -
About this workshop • Duration 2 hours • 100% open
source powered • Intermediate technical level required • Oriented Developers / QA / Operations / CTO / ... • Interactive, study-oriented ... -
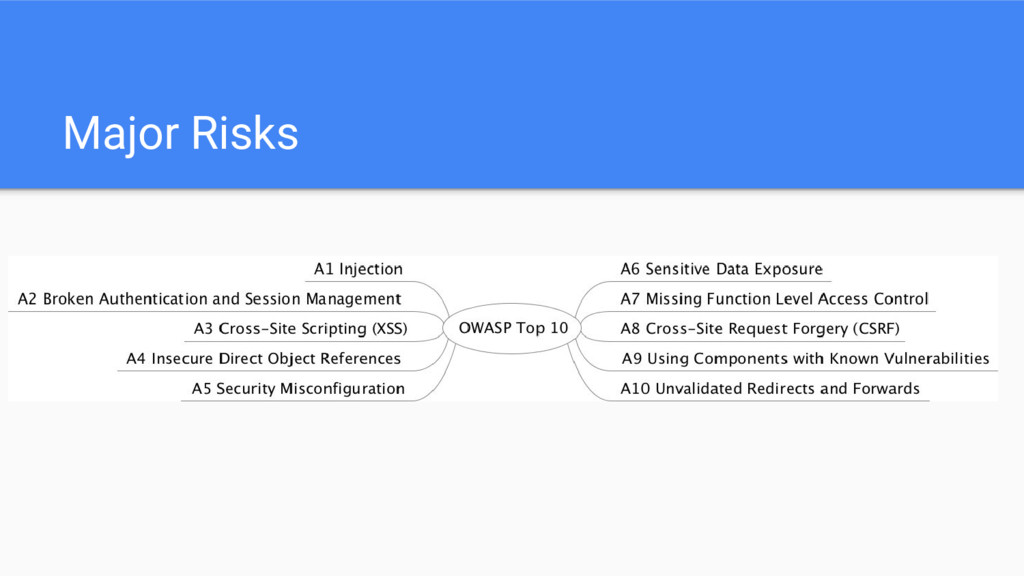
Workshop content • Theoretical part • Introduction to Web security
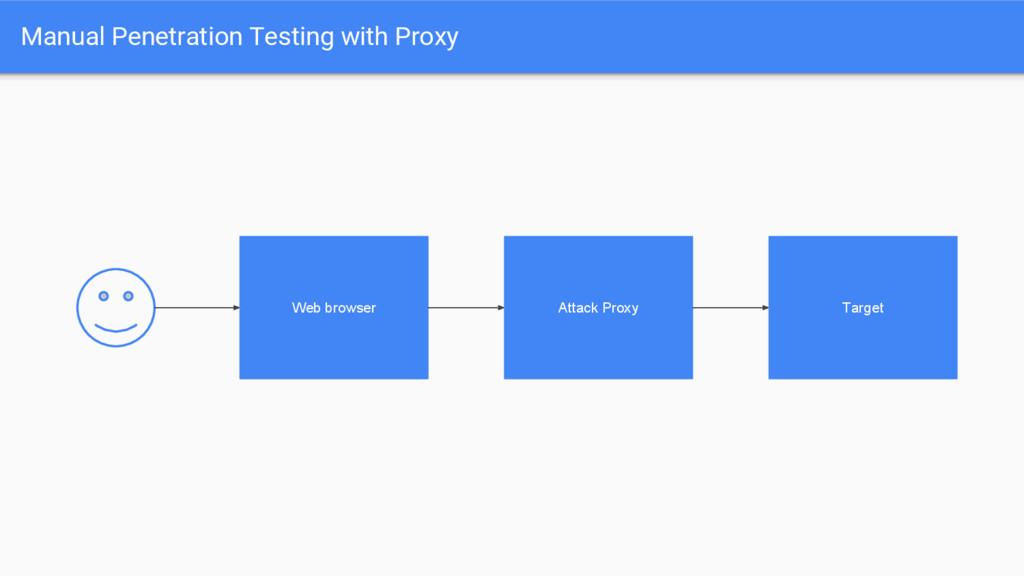
◦ Major security risks ◦ Pentesting types • Insecure code • Drupalxploitable project • Practical part • Vulnerable site create / study • Manual security testing with scanners • Manual security testing using Zed Attack Proxy GUI • Automated security testing -
Pentesting methods - Black-box • We don't know what is
inside • Testing as an external user -
Pentesting methods - White-box • We know all about the
project • We have the access to the project code -
Current situation for Drupal 8 • https://www.drupal.org/docs/8/security/writing-secure-code-for-drupal-8 a. Sanitizing on
output to avoid Cross Site Scripting (XSS) attacks : t(), Html::escape Xss::filter() or Xss::filterAdmin() b. Checking URLs UrlHelper::stripDangerousProtocols(), UrlHelper::filterBadProtocol(), SafeMarkup::format(). c. Use the database abstraction layer to avoid SQL injection attacks -
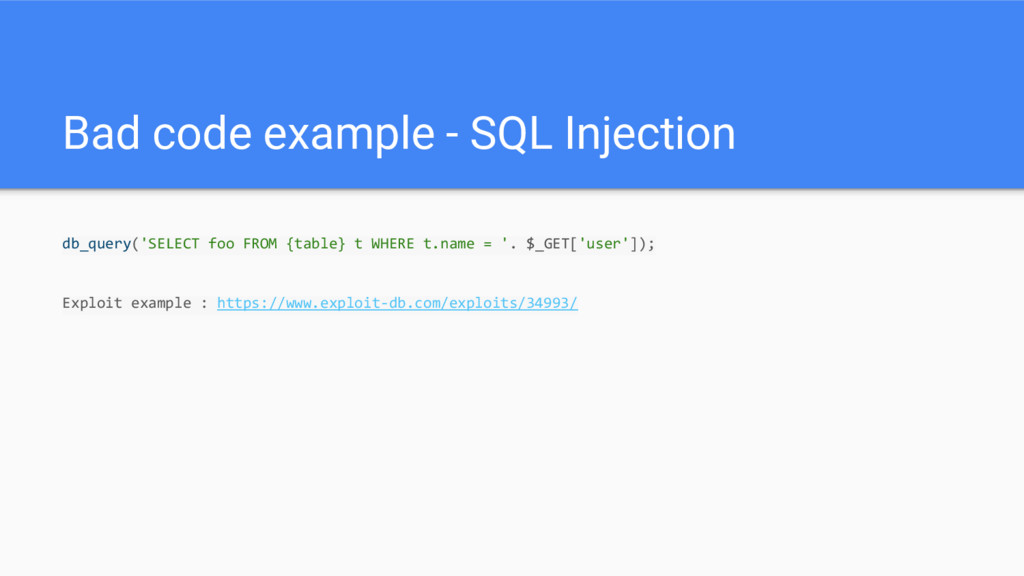
Bad code example - SQL Injection db_query('SELECT foo FROM {table}
t WHERE t.name = '. $_GET['user']); Exploit example : https://www.exploit-db.com/exploits/34993/ -
Bad code example - XSS exploits - --- modules/system/system.admin.inc 2013-04-03
17:29:52.000000000 -0400 +++ modules/system/system.admin.inc 2013-08-07 10:47:29.277279676 -0400 @@ -979,10 +979,10 @@ function _system_modules_build_row($info ); // Set the basic properties. $form['name'] = array( - - '#markup' => $info['name'], + '#markup' => check_plain($info['name']), ); $form['description'] = array( - - '#markup' => t($info['description']), + '#markup' => t("@desc", array('@desc' => $info['description'])), ); $form['version'] = array( '#markup' => $info['version'], http://seclists.org/fulldisclosure/2013/Aug/158 -
There are much more risks ... SQL, HTML, iFrame, SSI,
OS Command, PHP, XML, XPath, LDAP, Host Header and SMTP injections Cross-Site Scripting (XSS), Cross-Site Tracing (XST) and Cross-Site Request Forgery (CSRF) AJAX and Web Services issues (jQuery/JSON/XML/SOAP/WSDL) Authentication, authorization and session issues, file upload flaws and backdoor files Arbitrary file access, directory traversals, local and remote file inclusions (LFI/RFI) Configuration issues: Man-in-the-Middle, cross-domain policy files, information disclosures,... HTTP parameter pollution, HTTP response splitting and HTTP verb tampering Insecure DistCC, FTP, NTP, Samba, SNMP, VNC and WebDAV configurations HTML5 ClickJacking, Cross-Origin Resource Sharing (CORS) and web storage issues XML External Entity attacks (XXE) and Server Side Request Forgery (SSRF) Heartbleed and Shellshock vulnerability (OpenSSL), Denial-of-Service (DoS) attacks Parameter tampering, cookie and password reset poisoning ... -
About Drupalxploitable • Purposefully vulnerables Drupal installation • Basically :
“a very crappy Drupal site” • Open source (github) -
Existing projects in PHP world Damn Vulnerable Web Application (DVWA)
http://www.dvwa.co.uk/ Mutillidae http://www.irongeek.com/i.php?page=mutillidae/mutillidae-deliberately-vulnerable-php-owasp-top-10 WebGoatPHP https://github.com/shivamdixit/WebGoatPHP buggy web application http://www.itsecgames.com/ -
Used infrastructure • Virtualbox VM ◦ Ubuntu 16.04 LTS server
64 bit ◦ Jenkins CI ◦ OWASP ZAP, sqlmap, CMSMap ... ◦ Drupal 8 vulnerable site for manual and automatic testing -
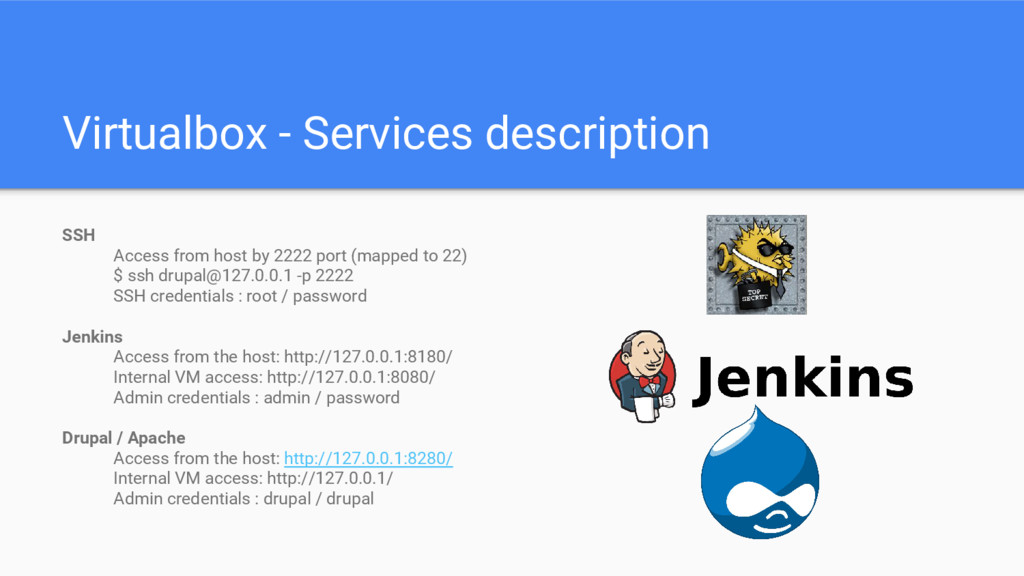
SSH Access from host by 2222 port (mapped to 22)
$ ssh [email protected] -p 2222 SSH credentials : root / password Jenkins Access from the host: http://127.0.0.1:8180/ Internal VM access: http://127.0.0.1:8080/ Admin credentials : admin / password Drupal / Apache Access from the host: http://127.0.0.1:8280/ Internal VM access: http://127.0.0.1/ Admin credentials : drupal / drupal Virtualbox - Services description -
sqlmap python sqlmap.py -v 2 --url=http://127.0.0.1/user/ --user-agent=SQLMAP --delay=1 --retries=2 --keep-alive
--threads=5 --batch --dbms=MySQL --os=Linux --level=5 --risk=2 --banner --is-dba --dbs --tables --technique=BEUST -s /tmp/scan_report.txt --flush-session -t /tmp/scan_trace.txt --fresh-queries -
gauntlt https://github.com/gauntlt/gauntlt https://github.com/gauntlt/gauntlt-demo/tree/master/examples Uses natural language in a Given, When,
Then Gherkin syntax to describe security requirements as features. -
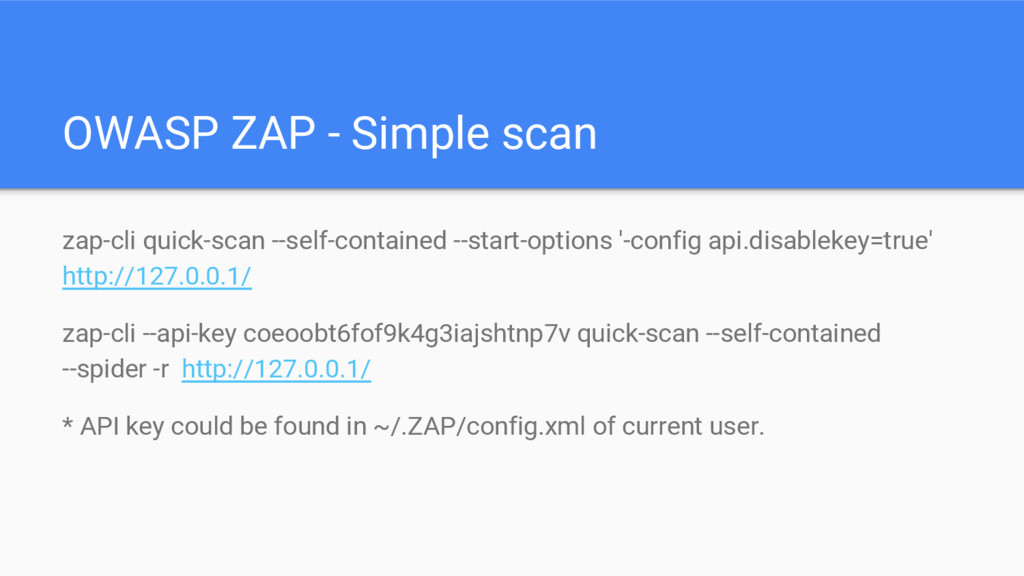
OWASP ZAP - Simple scan zap-cli quick-scan --self-contained --start-options '-config
api.disablekey=true' http://127.0.0.1/ zap-cli --api-key coeoobt6fof9k4g3iajshtnp7v quick-scan --self-contained --spider -r http://127.0.0.1/ * API key could be found in ~/.ZAP/config.xml of current user. -
OWASP ZAP - Simple scan with ZAPR zapr --debug --summary
http://127.0.0.1 -
OWASP ZAP - Running as a daemon /opt/zaproxy/zap.sh -daemon -host
0.0.0.0 -port 8480 Also, Docker usage possible : https://github.com/zaproxy/zaproxy/wiki/Docker -
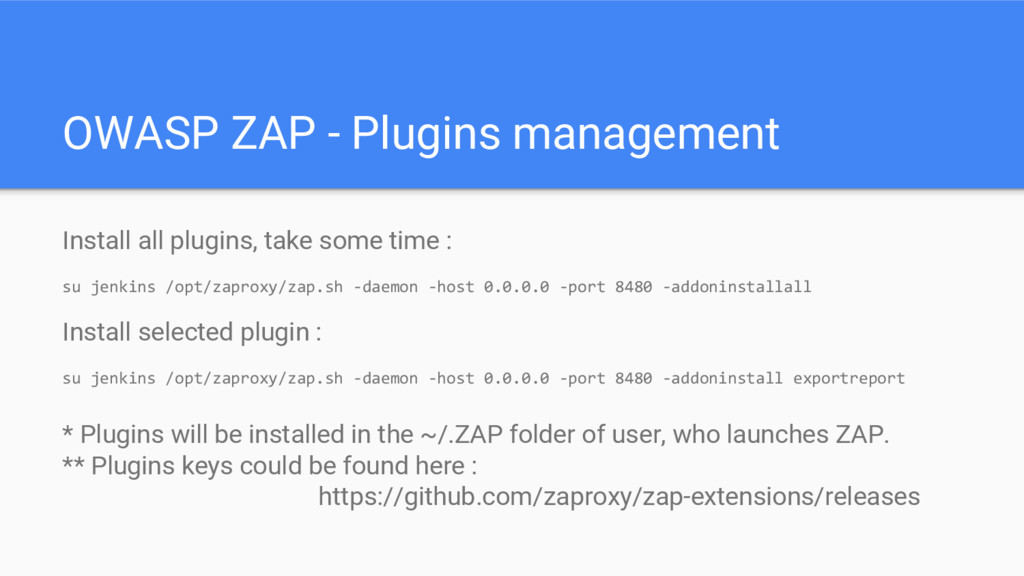
OWASP ZAP - Plugins management Install all plugins, take some
time : su jenkins /opt/zaproxy/zap.sh -daemon -host 0.0.0.0 -port 8480 -addoninstallall Install selected plugin : su jenkins /opt/zaproxy/zap.sh -daemon -host 0.0.0.0 -port 8480 -addoninstall exportreport * Plugins will be installed in the ~/.ZAP folder of user, who launches ZAP. ** Plugins keys could be found here : https://github.com/zaproxy/zap-extensions/releases -
OWASP ZAP https://github.com/zaproxy/zaproxy/wiki/Docker zap.sh -daemon -host 0.0.0.0 -port 8480 zap-x.sh
-daemon -host 0.0.0.0 -port 8080 zap-cli quick-scan --self-contained \ --start-options '-config api.disablekey=true' http://target -
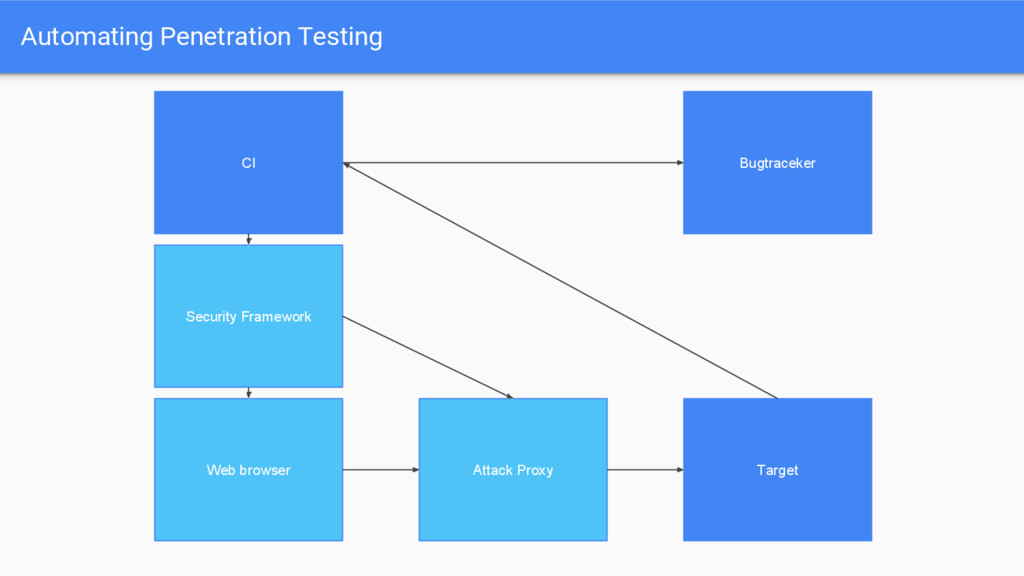
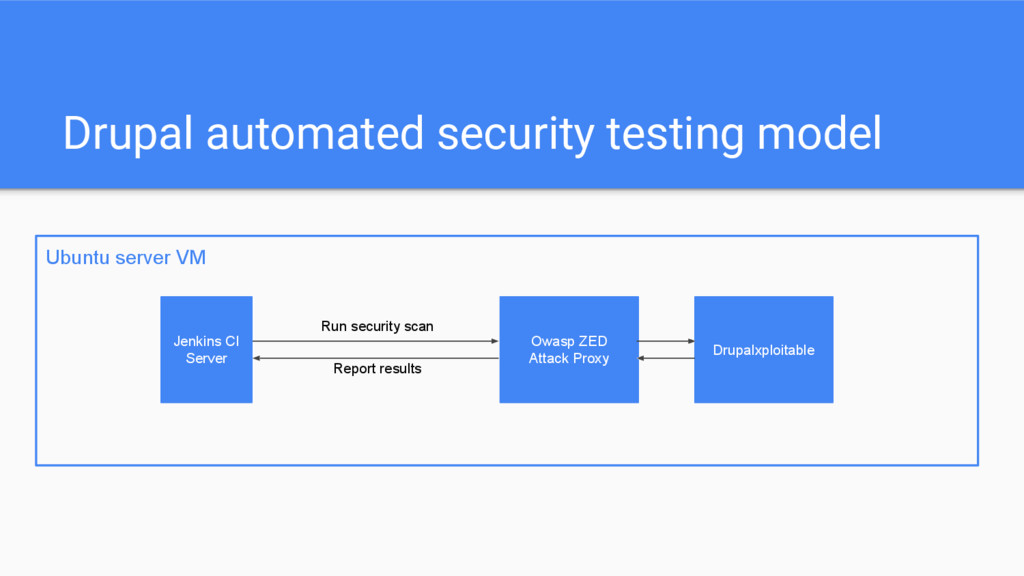
Ubuntu server VM Jenkins CI Server Drupalxploitable Owasp ZED Attack
Proxy Report results Run security scan Drupal automated security testing model -
Jenkins CI - Plugins used • Official OWASP ZAP Jenkins
Plugin • Environment Injector Plugin -
Ressources • https://martijnvanlambalgen.wordpress.com/2015/10/18/automating-your-vulnerability-scan-with-owasp-zap/ • https://www.securify.nl/blog/SFY20150303/automating_security_tests_using_owasp_zap_and_jenkins.html • https://tools.pentestbox.org/ • https://www.owasp.org/index.php/OWASP_Vulnerable_Web_Applications_Directory_Project •
http://connect.ed-diamond.com/MISC/MISC-087/Pourquoi-inclure-la-securite-dans-votre-pipeline-DevOps • https://www.owasp.org/index.php/Automated_Audit_using_SQLMap • https://myexploit.wordpress.com/information-gathering-sqlmap/ • https://insights.sei.cmu.edu/devops/2016/01/adding-security-to-your-devops-pipeline.html • https://www.slideshare.net/wickett/pragmatic-security-and-rugged-devops-sxsw-2015 • https://es.slideshare.net/StephendeVries2/automating-security-tests-for-continuous-integration • https://www.drupal.org/docs/8/security/writing-secure-code-for-drupal-8 • https://www.drupal.org/node/101496 • https://www.drupal.org/taxonomy/term/127 • https://www.owasp.org/index.php/How_to_write_insecure_code • https://es.slideshare.net/StephendeVries2/continuous-and-visible-security-testing-with-bddsecurity • https://theagileadmin.com/2015/12/03/security-tooling-delivered-by-docker/ -
Special thanks • To my company @AgenceStratis, which understands the
importance of open source culture and supports it • To Mikke Schirén (@mikkdroid) from wunderkraut, who really helped us with Jenkins 2 configuration during the workshop day • To Drupal Developer Days Sevilla team for great organization of the event.