Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Single Sign-On und User Self Service für den Ha...
Search
Sponsored
·
Ship Features Fearlessly
Turn features on and off without deploys. Used by thousands of Ruby developers.
→
fraosug
November 19, 2019
Technology
210
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Single Sign-On und User Self Service für den Hausgebrauch
Single Sign-On und User Self Service für den Hausgebrauch, Vortrag von Christopher J. Ruwe
fraosug
November 19, 2019
More Decks by fraosug
See All by fraosug
SAMFS-Vortrag von Carsten Grzemba
fraosug
0
420
DKIM Vortrag Dr. Erwin Hoffmann
fraosug
0
320
SmartOS Homerouter
fraosug
0
330
Zeit, Schaltsekunden, Neujahr und ntp, Vortrag von Erwin Hoffmann
fraosug
0
260
Virtual Datacenter Cloud Framework
fraosug
0
270
pkgsrc bulk-builds für illumos SmartOS
fraosug
0
180
Login mit signierten ssh-Schlüsseln
fraosug
0
150
cloud-init mit SmartOS
fraosug
0
310
(Private) Cloud auf SmartOS
fraosug
0
280
Other Decks in Technology
See All in Technology
慶應義塾大学 AI実践05 論文執筆の仕組み化
keio_smilab
PRO
3
2.8k
You Have Agency(サンキュー、Ruby)
snoozer05
PRO
5
640
書き手が人でもAIでも正しくなる道、 SREを埋め込んだDeveloper Platform / tech drivers day8
chmikata
4
870
Agent Loopを組み込んだ アンビエントなAI機能を実現する / Ambient AI fetures with Agent Loop
nekorush14
0
120
【Oracle AI SPOTLIGHT ウェビナー】事例から見る!なぜOCIが選ばれたのか ― AI時代のクラウド戦略を紐解く ―
oracle4engineer
PRO
1
140
GitHub、使う?使わない?
happysamurai294
0
130
Claude for Google Workspaces ポン出し/claude-for-google-workspace-slide-conversion
emiki
0
13k
[FECONF-2026] 신대륙을 향한 카카오페이증권 프론트엔드 항해기 (이주승)
l1ghthouse
0
340
Flutter Widget Previewerで始めるUIプレビューとVRTの自動化
sakusaku3939
0
190
Copilot Coworkで「みのるん式」やってみた
minorun365
PRO
1
110
Autonomous AI Lakehouse - Live AI Hubから始めるセキュアなAIデータ活用 -
oracle4engineer
PRO
2
180
推論基盤と Scale-Up Interconnect の現状と制約から俯瞰する技術動向
markunet
2
710
Featured
See All Featured
Bash Introduction
62gerente
615
220k
Impact Scores and Hybrid Strategies: The future of link building
tamaranovitovic
0
470
Unlocking the hidden potential of vector embeddings in international SEO
frankvandijk
0
1k
Making Projects Easy
brettharned
120
6.8k
Save Time (by Creating Custom Rails Generators)
garrettdimon
PRO
33
5.5k
Speed Design
sergeychernyshev
33
2.2k
"I'm Feeling Lucky" - Building Great Search Experiences for Today's Users (#IAC19)
danielanewman
230
23k
Java REST API Framework Comparison - PWX 2021
mraible
34
9.8k
実際に使うSQLの書き方 徹底解説 / pgcon21j-tutorial
soudai
PRO
203
77k
From Legacy to Launchpad: Building Startup-Ready Communities
dugsong
0
370
Tips & Tricks on How to Get Your First Job In Tech
honzajavorek
1
820
How to optimise 3,500 product descriptions for ecommerce in one day using ChatGPT
katarinadahlin
PRO
3
3.9k
Transcript
SSO für den Hausgebrauch Christopher J. Ruwe <
[email protected]
> selbstständiger IT-Consultant
Problem • mehrere Services sollen dem gleichen Nutzerkreis zur Verfügung
gestellt werden • die Services sollen nicht öffentlich sein • Berechtigungen sollen nicht separat gepflegt werden (müssen)
Lösungsskizze • auf einer zentralen Instanz werden Nutzer und Berechtigungen
gepflegt • es existiert ein Vertrauensverhältnis von allen Services zu dieser zentralen Instanz • es existiert ein Mechanismus, Identitäten und/oder Berechtigungen zu transportieren
Protokolle (Auswahl) • SAML v2.0 (Security Assertion Markup Languange): authn
/ authz • OAuth v2.0 (Open Authorization): authz • OIDC (OpenIF Connect): authn
Lingo • Resource Owner • Client • Authorization Server •
Resource Server • Realm • Relying Party • OpenID Provider • End-User • User Agent • Resource Server
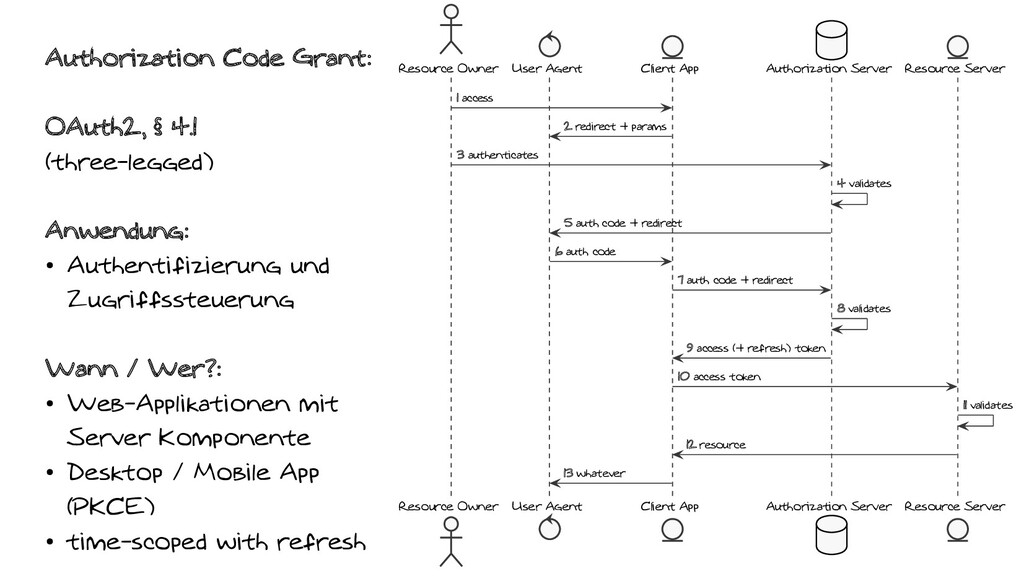
Authorization Code Grant: OAuth2, § 4.1 (three-legged) Anwendung: • Authentifizierung
und Zugriffssteuerung Wann / Wer?: • Web-Applikationen mit Server Komponente • Desktop / Mobile App (PKCE) • time-scoped with refresh Resource Owner Resource Owner User Agent User Agent Client App Client App Authorization Server Authorization Server Resource Server Resource Server 1 access 2 redirect + params 3 authenticates 4 validates 5 auth code + redirect 6 auth code 7 auth code + redirect 8 validates 9 access (+ refresh) token 10 access token 11 validates 12 resource 13 whatever
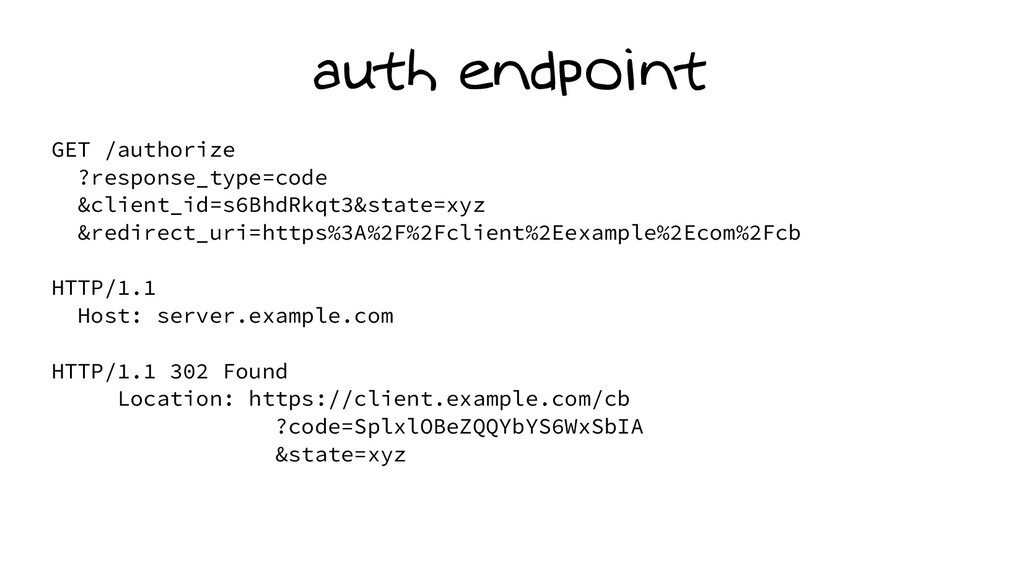
auth endpoint GET /authorize ?response_type=code &client_id=s6BhdRkqt3&state=xyz &redirect_uri=https%3A%2F%2Fclient%2Eexample%2Ecom%2Fcb HTTP/1.1 Host: server.example.com
HTTP/1.1 302 Found Location: https://client.example.com/cb ?code=SplxlOBeZQQYbYS6WxSbIA &state=xyz
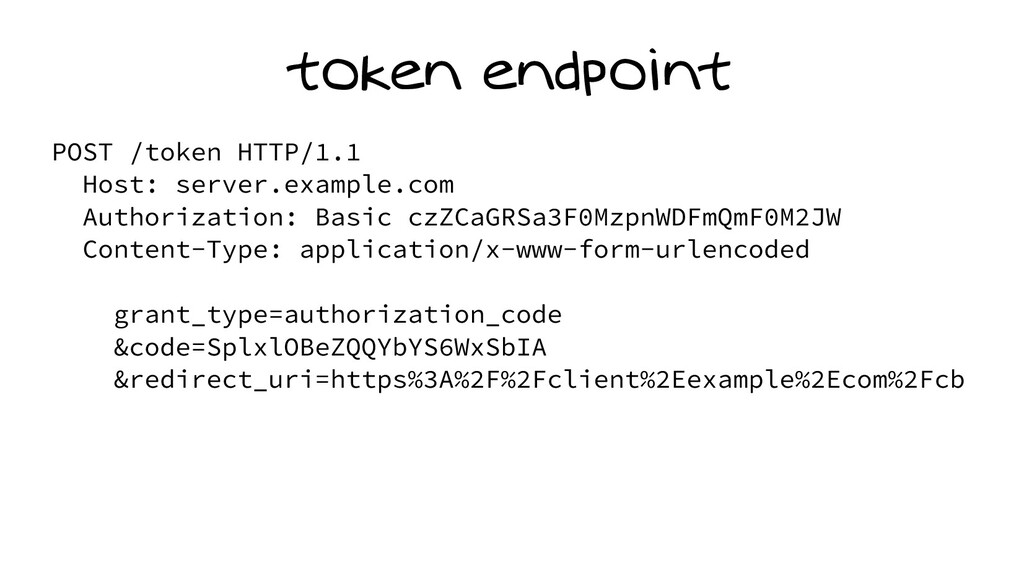
token endpoint POST /token HTTP/1.1 Host: server.example.com Authorization: Basic czZCaGRSa3F0MzpnWDFmQmF0M2JW
Content-Type: application/x-www-form-urlencoded grant_type=authorization_code &code=SplxlOBeZQQYbYS6WxSbIA &redirect_uri=https%3A%2F%2Fclient%2Eexample%2Ecom%2Fcb
token endpoint HTTP/1.1 200 OK Content-Type: application/json;charset=UTF-8 Cache-Control: no-store Pragma:
no-cache { "access_token":"2YotnFZFEjr1zCsicMWpAA", "token_type":"example", "expires_in":3600, "refresh_token":"tGzv3JOkF0XG5Qx2TlKWIA", "example_parameter":"example_value" }
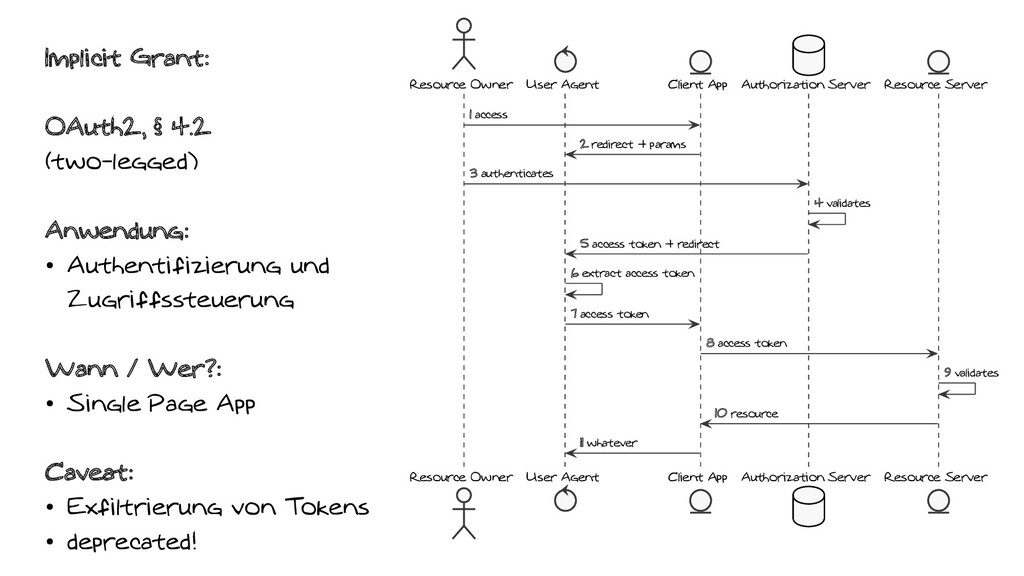
Resource Owner Resource Owner User Agent User Agent Client App
Client App Authorization Server Authorization Server Resource Server Resource Server 1 access 2 redirect + params 3 authenticates 4 validates 5 access token + redirect 6 extract access token 7 access token 8 access token 9 validates 10 resource 11 whatever Implicit Grant: OAuth2, § 4.2 (two-legged) Anwendung: • Authentifizierung und Zugriffssteuerung Wann / Wer?: • Single Page App Caveat: • Exfiltrierung von Tokens • deprecated!
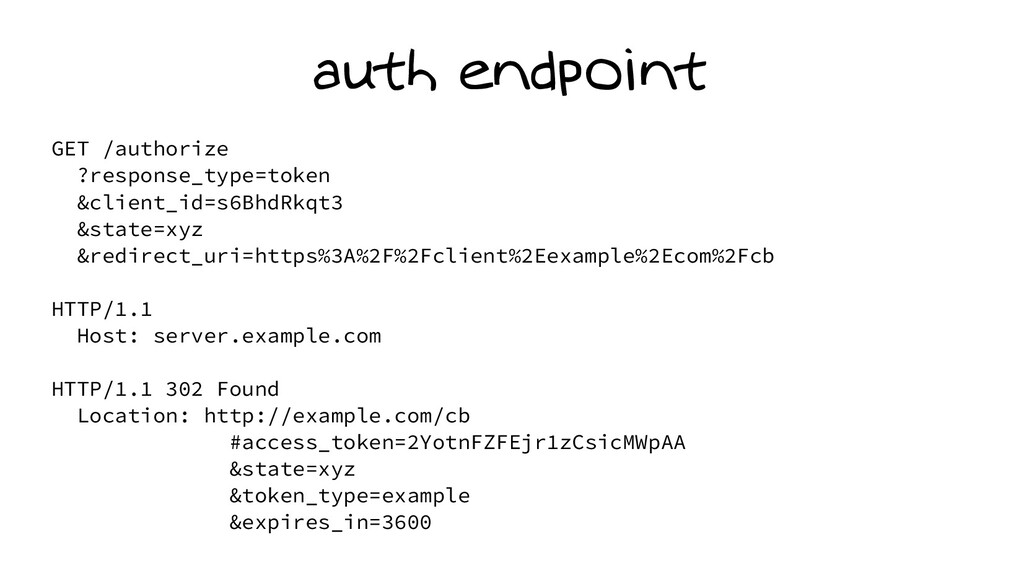
auth endpoint GET /authorize ?response_type=token &client_id=s6BhdRkqt3 &state=xyz &redirect_uri=https%3A%2F%2Fclient%2Eexample%2Ecom%2Fcb HTTP/1.1 Host:
server.example.com HTTP/1.1 302 Found Location: http://example.com/cb #access_token=2YotnFZFEjr1zCsicMWpAA &state=xyz &token_type=example &expires_in=3600
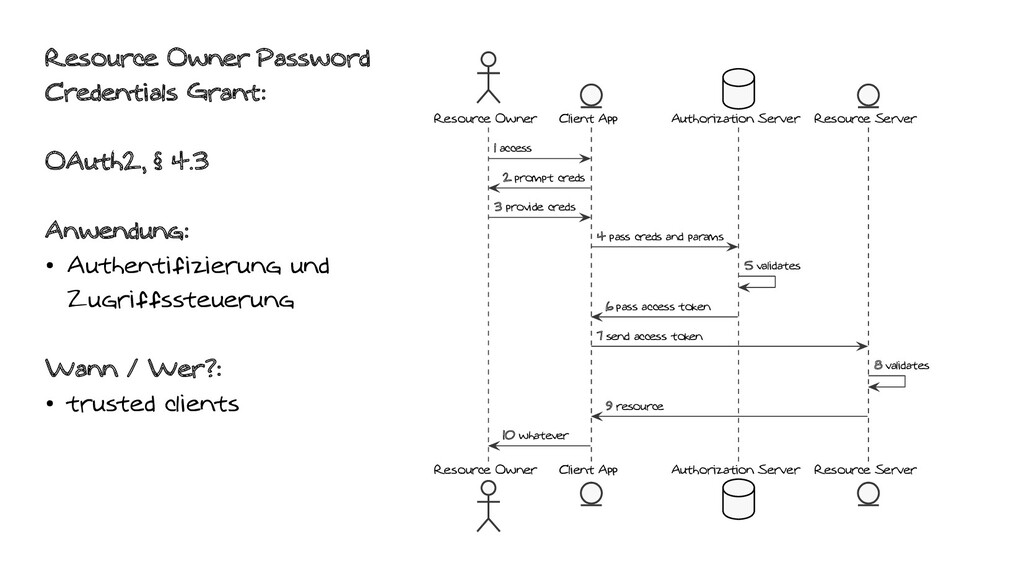
Resource Owner Password Credentials Grant: OAuth2, § 4.3 Anwendung: •
Authentifizierung und Zugriffssteuerung Wann / Wer?: • trusted clients Resource Owner Resource Owner Client App Client App Authorization Server Authorization Server Resource Server Resource Server 1 access 2 prompt creds 3 provide creds 4 pass creds and params 5 validates 6 pass access token 7 send access token 8 validates 9 resource 10 whatever
Client Credentials Grant: OAuth2, § 4.4 Anwendung: • Authentifizierung und
Zugriffssteuerung von autnomen Apps Wann / Wer?: • trusted clients non interactive Client App Client App Authorization Server Authorization Server Resource Server Resource Server 1 pass creds and params 2 validates 3 pass access token 4 send access token 5 validates 6 whatever
OIDC Authorization Code Flow OIDC v1.0, § 3.1 Anwendung: •
User-Authentifizierung • RP Authentifizierung • SSO auf RP • Authorisierung • verschiedene Scopes Resource Owner User Agent Client App (Relying Party) OpenID Provider Resource Server 1 access 2 redirect + params 3 authenticate at authorization endpoint 4 validate 5 auth code + redirect 6 auth code 7 auth code to token endpoint 8 validate 9 ID, access, (opt. refresh) token 10 validate ID 11 validate access 12 opt. request from userinfo endpoint) 13 validate access 14 additional claims
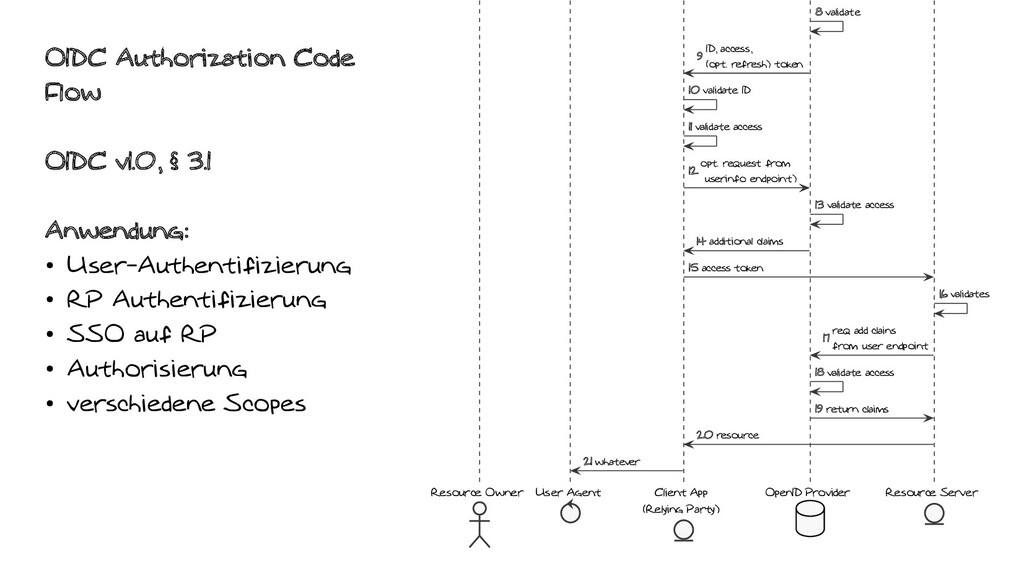
OIDC Authorization Code Flow OIDC v1.0, § 3.1 Anwendung: •
User-Authentifizierung • RP Authentifizierung • SSO auf RP • Authorisierung • verschiedene Scopes Resource Owner User Agent Client App (Relying Party) OpenID Provider Resource Server 8 validate 9 ID, access, (opt. refresh) token 10 validate ID 11 validate access 12 opt. request from userinfo endpoint) 13 validate access 14 additional claims 15 access token 16 validates 17 req add clains from user endpoint 18 validate access 19 return claims 20 resource 21 whatever
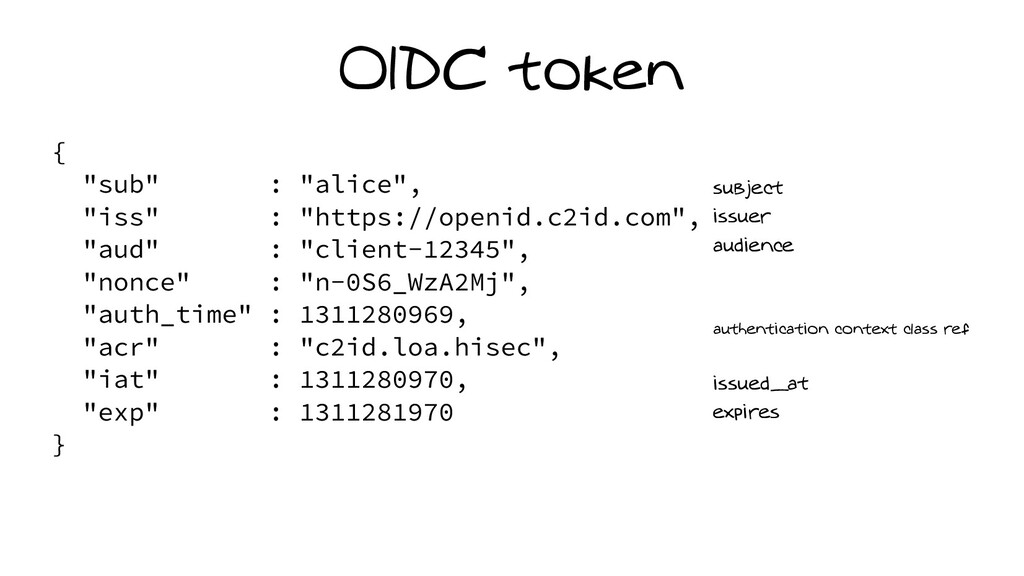
OIDC token { "sub" : "alice", "iss" : "https://openid.c2id.com", "aud"
: "client-12345", "nonce" : "n-0S6_WzA2Mj", "auth_time" : 1311280969, "acr" : "c2id.loa.hisec", "iat" : 1311280970, "exp" : 1311281970 } subject issuer audience authentication context class ref issued_at expires
Token eyJhbGciOiJSUzI1NiIsImtpZCI6IjFlOWdkazcifQ.ewogImlzcyI6ICJodHRw Oi8vc2VydmVyLmV4YW1wbGUuY29tIiwKICJzdWIiOiAiMjQ4Mjg5NzYxMDAxIiw KICJhdWQiOiAiczZCaGRSa3F0MyIsCiAibm9uY2UiOiAibi0wUzZfV3pBMk1qIi wKICJleHAiOiAxMzExMjgxOTcwLAogImlhdCI6IDEzMTEyODA5NzAKfQ.ggW8hZ 1EuVLuxNuuIJKX_V8a_OMXzR0EHR9R6jgdqrOOF4daGU96Sr_P6qJp6IcmD3HP9 9Obi1PRs-cwh3LO-p146waJ8IhehcwL7F09JdijmBqkvPeB2T9CJNqeGpe-gccM g4vfKjkM8FcGvnzZUN4_KSP0aAp1tOJ1zZwgjxqGByKHiOtX7TpdQyHE5lcMiKP XfEIQILVq0pc_E2DzL7emopWoaoZTF_m0_N0YzFC6g6EJbOEoRoSK5hoDalrcvR YLSrQAZZKflyuVCyixEoV9GfNQC3_osjzw2PAithfubEEBLuVVk4XUVrWOLrLl0
nx7RkKU8NXNHq-rvKMzqg
Auslassungen • OIDC Implicit Flow (§ 3.2) • OIDC Hybrid
Flow (§ 3.3)
Anwendung • Vertrauensverhältnis von Ressourcen- Konsument zu Authorization Server /
Identity Provider • sichere Kommunikation zwischen den Komponenten
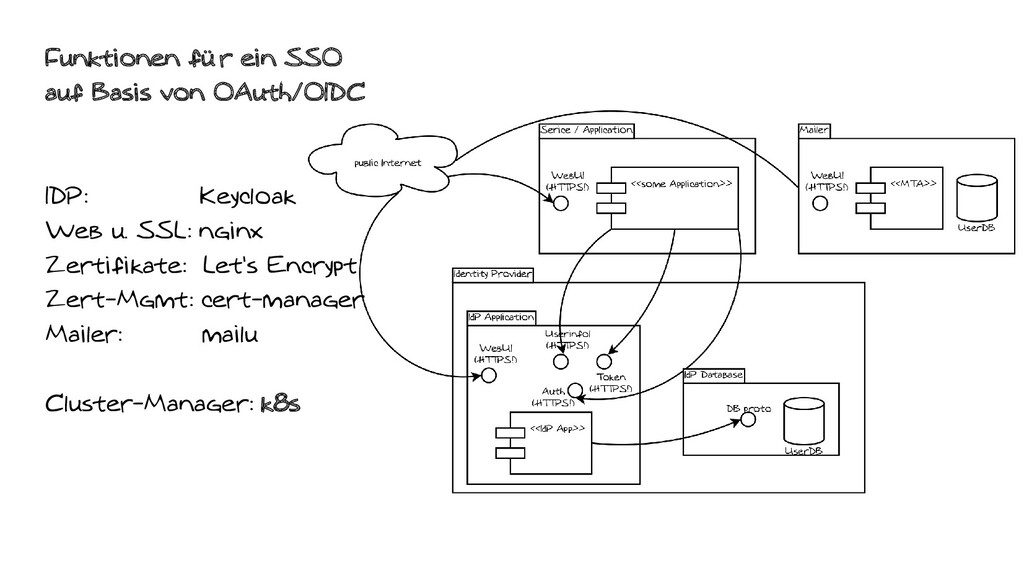
Funktionen für ein SSO auf Basis von OAuth/OIDC IDP: Keycloak
Web u. SSL: nginx Zertifikate: Let‘s Encrypt Zert-Mgmt: cert-manager Mailer: mailu Cluster-Manager: k8s
cert-manager $ kubectl get clusterissuers.certmanager.k8s.io cruwe-le-prod --output=yaml apiVersion: certmanager.k8s.io/v1alpha1 kind:
ClusterIssuer metadata: name: cruwe-le-prod spec: acme: email:
[email protected]
http01: {} privateKeySecretRef: name: issuer-cruwe-le-prod server: https://acme-v02.api.letsencrypt.org/directory
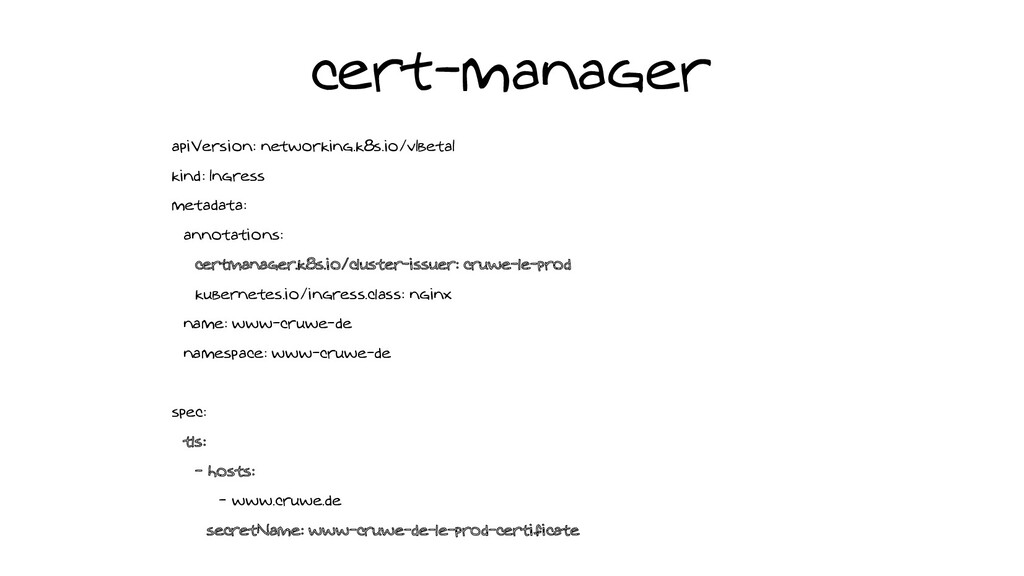
cert-manager apiVersion: networking.k8s.io/v1beta1 kind: Ingress metadata: annotations: certmanager.k8s.io/cluster-issuer: cruwe-le-prod kubernetes.io/ingress.class:
nginx name: www-cruwe-de namespace: www-cruwe-de spec: tls: - hosts: - www.cruwe.de secretName: www-cruwe-de-le-prod-certificate
keycloak
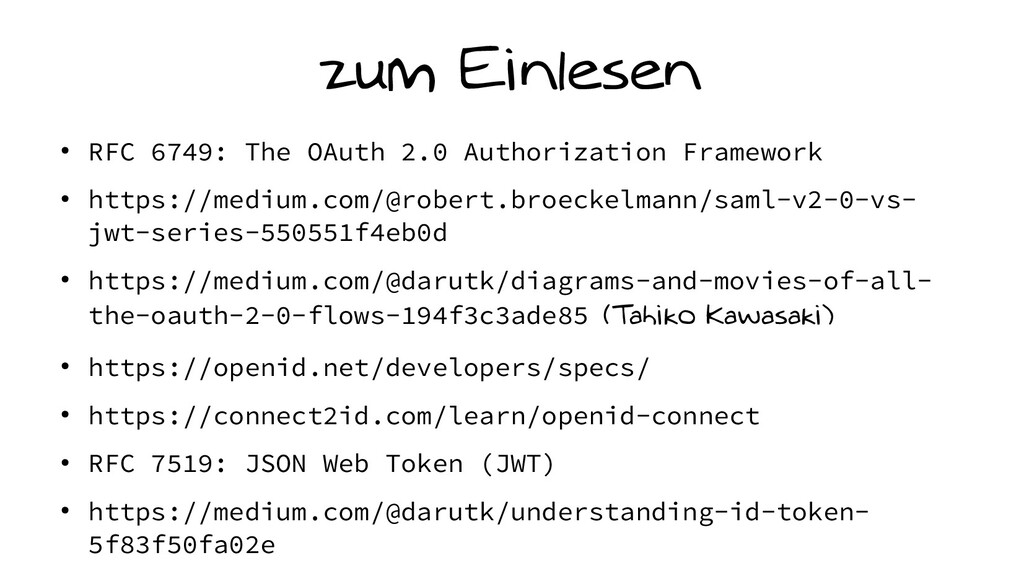
zum Einlesen • RFC 6749: The OAuth 2.0 Authorization Framework
• https://medium.com/@robert.broeckelmann/saml-v2-0-vs- jwt-series-550551f4eb0d • https://medium.com/@darutk/diagrams-and-movies-of-all- the-oauth-2-0-flows-194f3c3ade85 (Tahiko Kawasaki) • https://openid.net/developers/specs/ • https://connect2id.com/learn/openid-connect • RFC 7519: JSON Web Token (JWT) • https://medium.com/@darutk/understanding-id-token- 5f83f50fa02e


 fraosug
 keio_smilab
 snoozer05
 chmikata
 nekorush14
 oracle4engineer
 happysamurai294
 emiki
 l1ghthouse
 sakusaku3939
 minorun365
 markunet
 62gerente
 tamaranovitovic
 frankvandijk
 brettharned
 garrettdimon
 sergeychernyshev
 danielanewman
 mraible
 soudai
 dugsong
 honzajavorek
 katarinadahlin