Share
Embed
Dissecting Logons
Tools and techniques for examining what happens/happened during a Windows user logon to aid troubleshooting slowness and other problems.
Given, with demos, at the Romanian Citrix User Group meeting, November 2020
Guy Leech
November 18, 2020
Transcript
8 slides
-
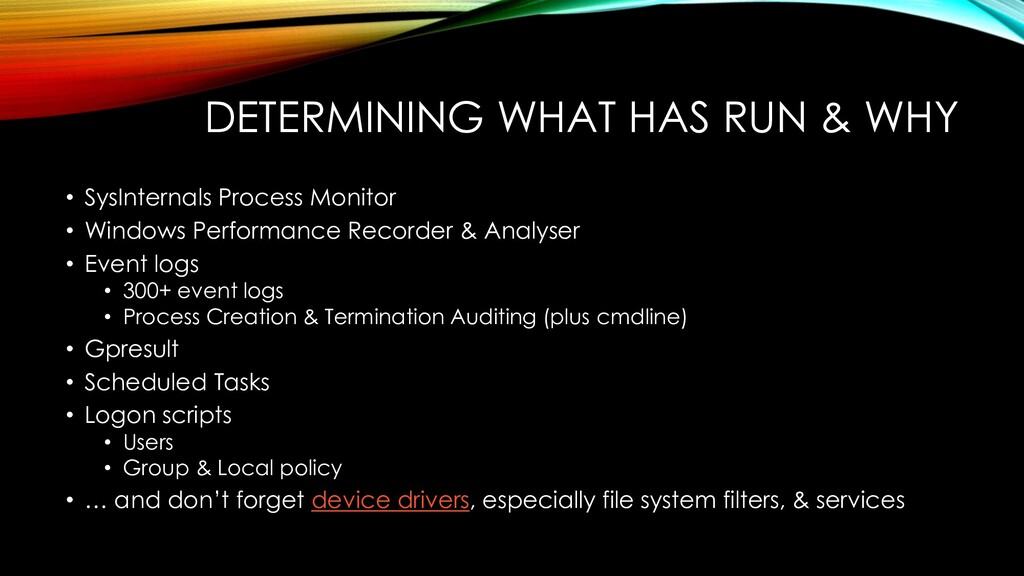
DETERMINING WHAT HAS RUN & WHY • SysInternals Process Monitor
• Windows Performance Recorder & Analyser • Event logs • 300+ event logs • Process Creation & Termination Auditing (plus cmdline) • Gpresult • Scheduled Tasks • Logon scripts • Users • Group & Local policy • … and don’t forget device drivers, especially file system filters, & services -
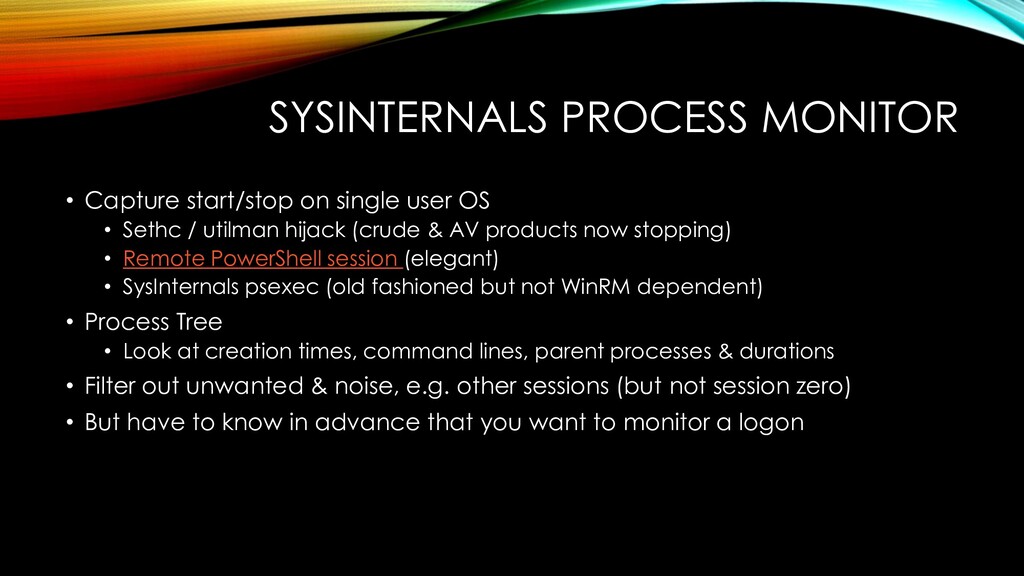
SYSINTERNALS PROCESS MONITOR • Capture start/stop on single user OS
• Sethc / utilman hijack (crude & AV products now stopping) • Remote PowerShell session (elegant) • SysInternals psexec (old fashioned but not WinRM dependent) • Process Tree • Look at creation times, command lines, parent processes & durations • Filter out unwanted & noise, e.g. other sessions (but not session zero) • But have to know in advance that you want to monitor a logon -
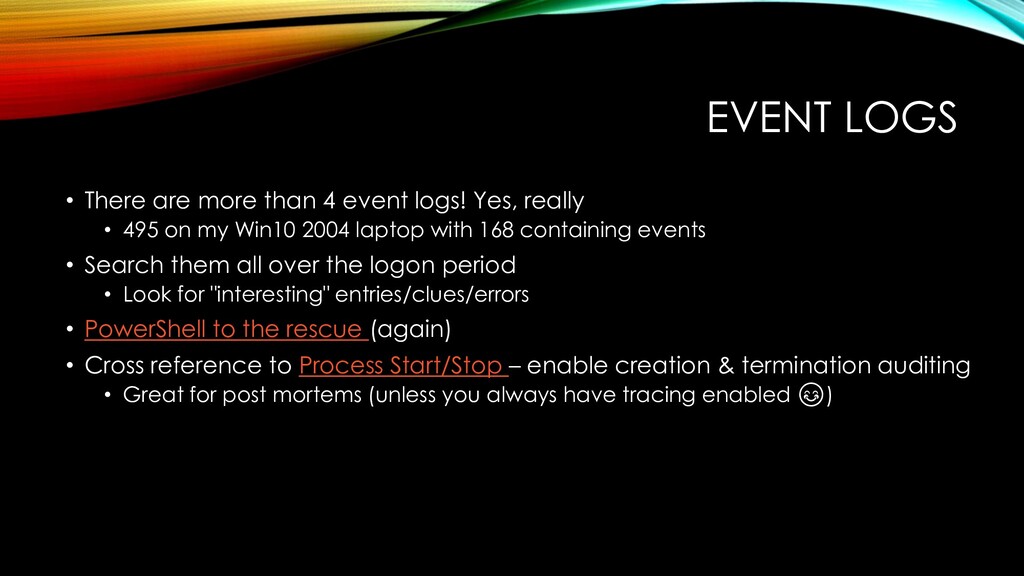
EVENT LOGS • There are more than 4 event logs!
Yes, really • 495 on my Win10 2004 laptop with 168 containing events • Search them all over the logon period • Look for "interesting" entries/clues/errors • PowerShell to the rescue (again) • Cross reference to Process Start/Stop – enable creation & termination auditing • Great for post mortems (unless you always have tracing enabled ) -
CONTROLUP LOGON ANALYSIS SCRIPT • Doesn’t need ControlUp to run
• Download from script library • Needs logon and process creation/termination auditing in place + cmdline • Script can do this for you locally or set via GPO • Just need to pass domain\user parameter for simplest use • Outputs phases including group policy, logon script & printer mappings • Also now shows Fslogix, Ivanti Environment Manager & VMware AppVolumes & DEM stages -
WINDOWS PERFORMANCE RECORDER & ANALYSER • Standard in Windows 10
• But need Windows 10 SDK/ADK full version for on/off traces • Although can copy folder once installed for recording & analysis • wpr.exe -start CPU -start DiskIO -start FileIO -start Registry -start Network -start Minifilter -onoffscenario boot -onoffresultspath c:\temp - onoffproblemdescription SlowBootSlowLogon -numiterations 1 • Or use the GUI • Stops on logon or use "wpr –stop <trace.etl>" via PowerShell Enter-PSSession, etc • Can be slow to create trace afterwards which can be GB in size • Analyser is a beast – data overload – expert users only 6 -
OTHER USEFUL THINGS TO LOOK AT • GPSvcDebugLevel • SysInternals
AutoRuns – what runs at logon that we don't need including ActiveSetup • Base/Default Profile • 3rd party log files e.g. FSlogix , VMware Cloud Volumes, Citrix WEM, Ivanti • Security software/Anti Virus – especially exclusions • User profile persistence (e.g. “Roman” profiles, UPM, Ivanti EM, etc.) • AppSetup value in Winlogon reg key (e.g. usrlogon.cmd) • Appinit_dlls • Local & hypervisor performance counters & network/storage load • Persistent image bloat – e.g. GPO cache, temp folders • Driver installation files in %systemroot%\inf\setupapi.dev.log & setupapi.app.log • The internet – many articles about logon optimisation e.g. @james______________rankin 7 -
PARTING THOUGHTS …. • Is it already fast enough? •
Is it worth the effort/cost to try & make it any faster? • Is it consistent? • Do you really need to do everything at logon for every user every time? • Maintainability • Documentation • Future Proofing • Logon analysis is available as a bespoke consultancy service from @guyrleech