Share
Embed
高橋メソッドでCVE解説シリーズ 〜CVE-2026-123633/CVE-2026-123007〜
fable5.2で作らせた、nginxの脆弱性解説 (高橋メソッド調)
Hakkadaikon
November 18, 2026
Transcript
93 slides
-
CVE-2026-123633 / CVE-2026-123007 nginx HTTP/2 の脆弱性 2 件を読む ネットワークと C
がわかる人向け。nginx の中身は知らなくてよい 2026-11-19 時点の公開情報にもとづく 1 / 93 -
は イベントループ worker 1 つのプロセスが epoll_wait() などで I/O を待ち、多数の接続を順に処理する Development
guide: Event loop 11 / 93 -
接続 1 本 = ngx_connection_t ソケットを包む構造体。read / write のイベントとメモリプールを持つ Development
guide: Connection 13 / 93 -
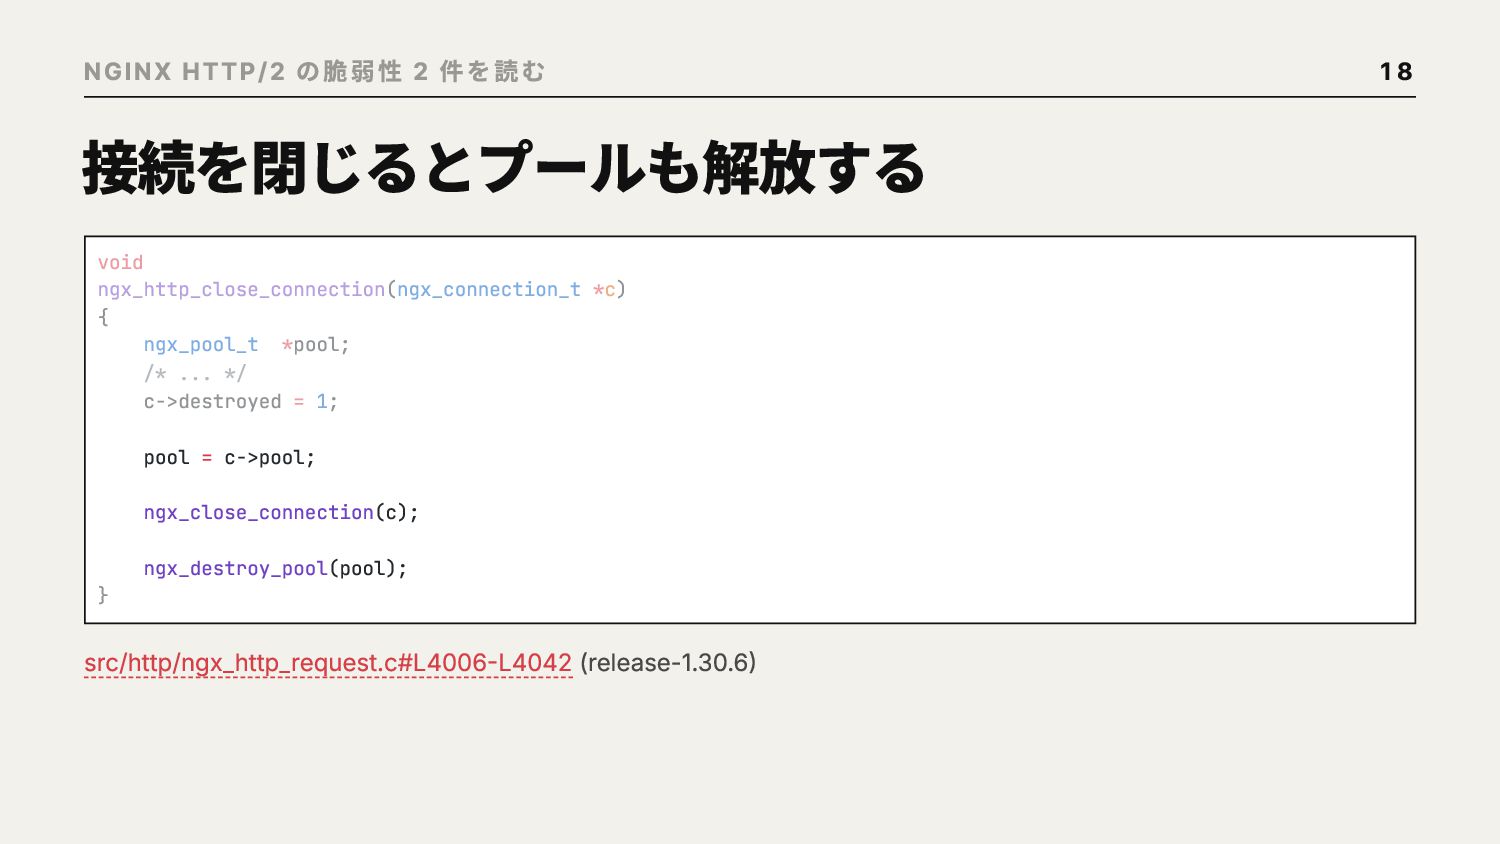
NGINX HTTP/2 の脆弱性 2 件を読む 接続を閉じるとプールも解放する void ngx_http_close_connection(ngx_connection_t *c) {
ngx_pool_t *pool; /* ... */ c->destroyed = 1; pool = c->pool; ngx_close_connection(c); } ngx_destroy_pool(pool); src/http/ngx_http_request.c#L4006-L4042 (release-1.30.6) 18 -
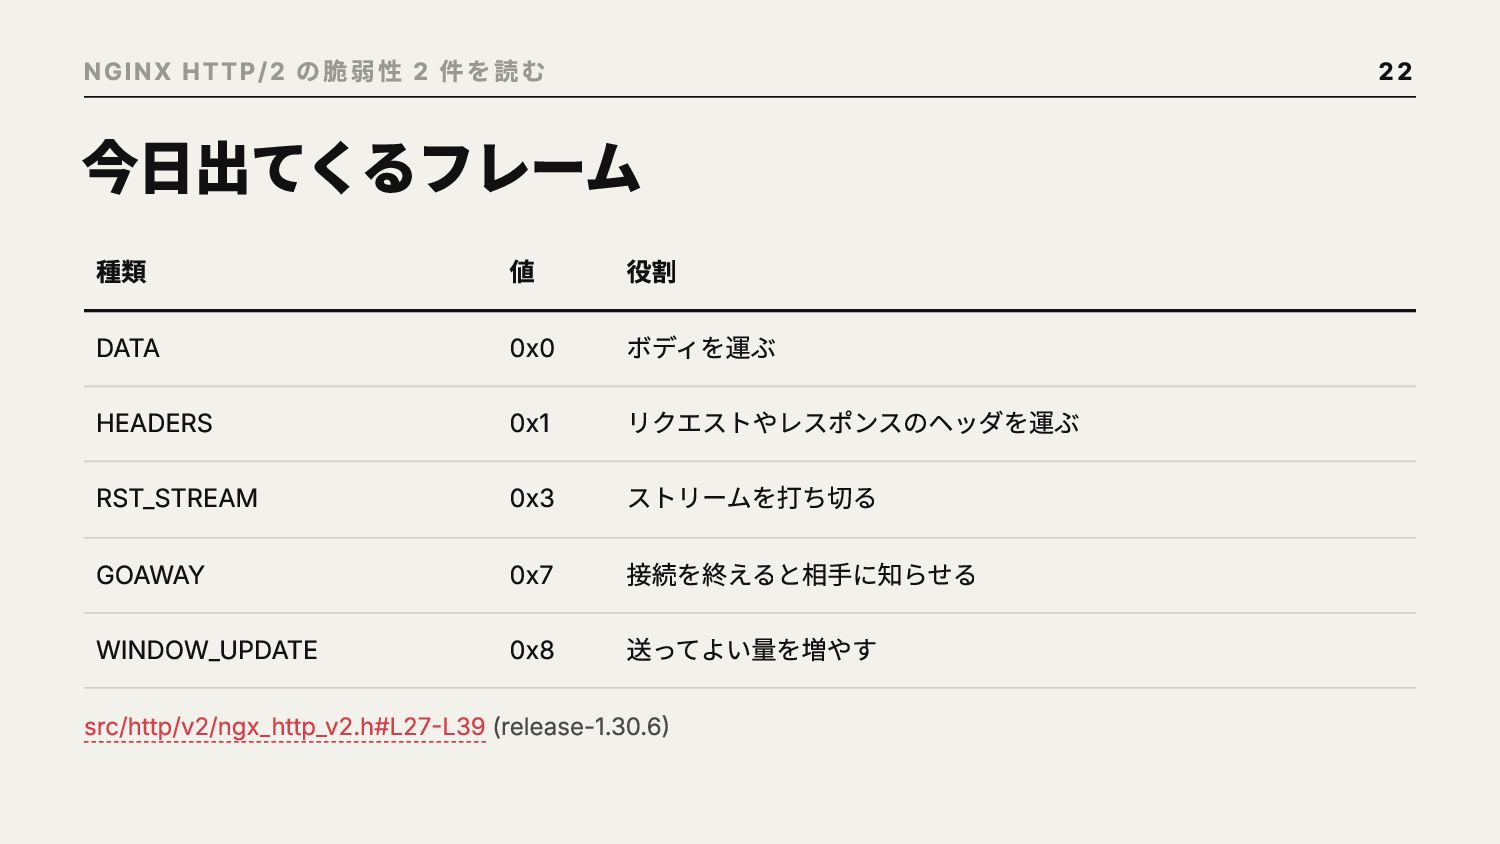
NGINX HTTP/2 の脆弱性 2 件を読む 今日出てくるフレーム 種類 値 役割 DATA
0x0 HEADERS 0x1 RST_STREAM 0x3 ボディを運ぶ リクエストやレスポンスのヘッダを運ぶ ストリームを打ち切る GOAWAY 0x7 WINDOW_UPDATE 0x8 接続を終えると相手に知らせる 送ってよい量を増やす src/http/v2/ngx_http_v2.h#L27-L39 (release-1.30.6) 22 -
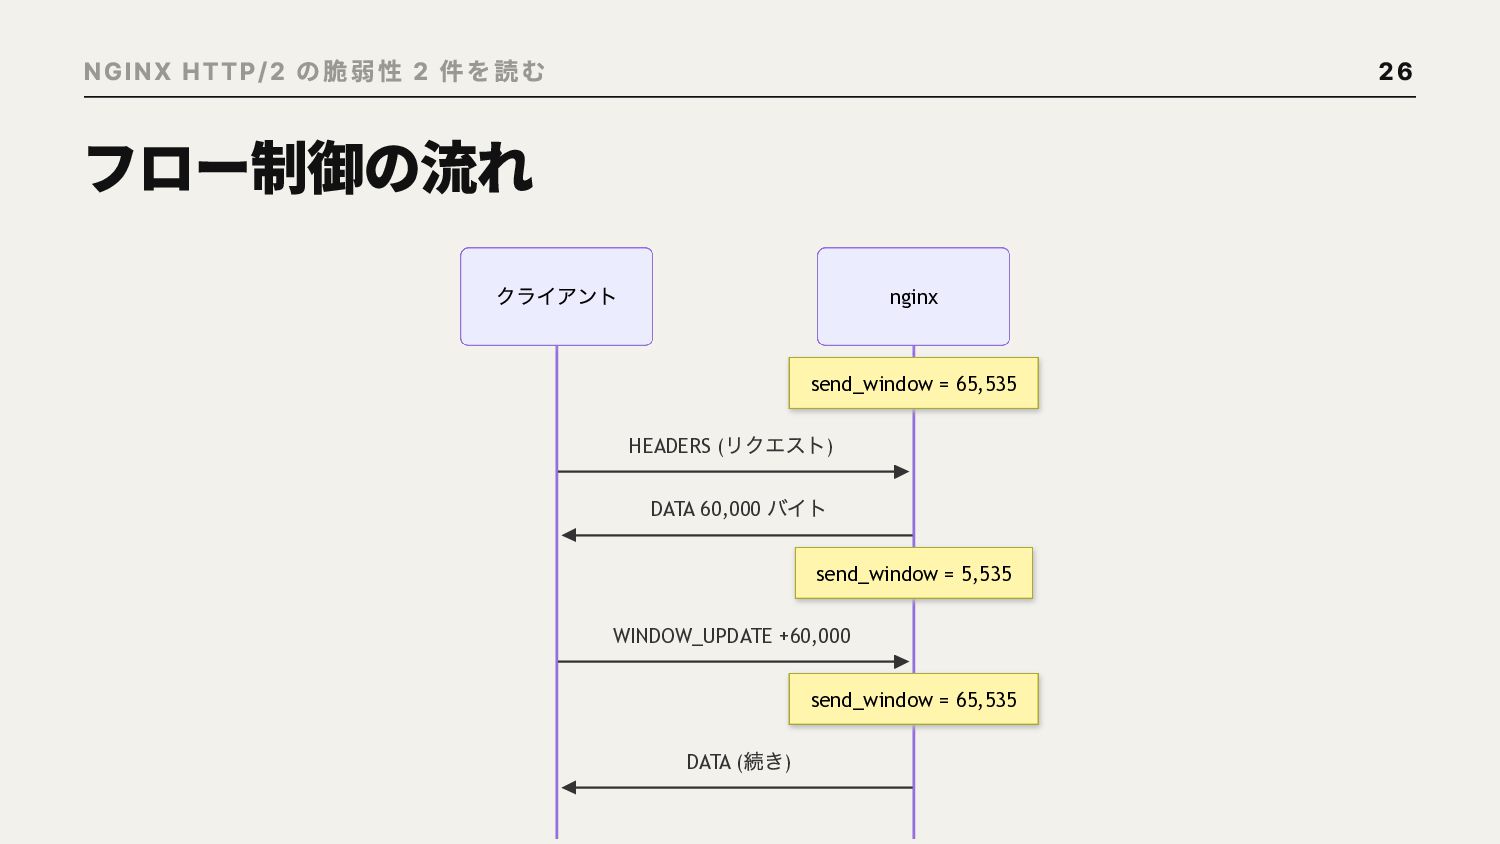
NGINX HTTP/2 の脆弱性 2 件を読む 26 フロー制御の流れ クライアント nginx send_window
= 65,535 リクエスト) HEADERS ( DATA 60,000 バイト send_window = 5,535 WINDOW_UPDATE +60,000 send_window = 65,535 続き) DATA ( -
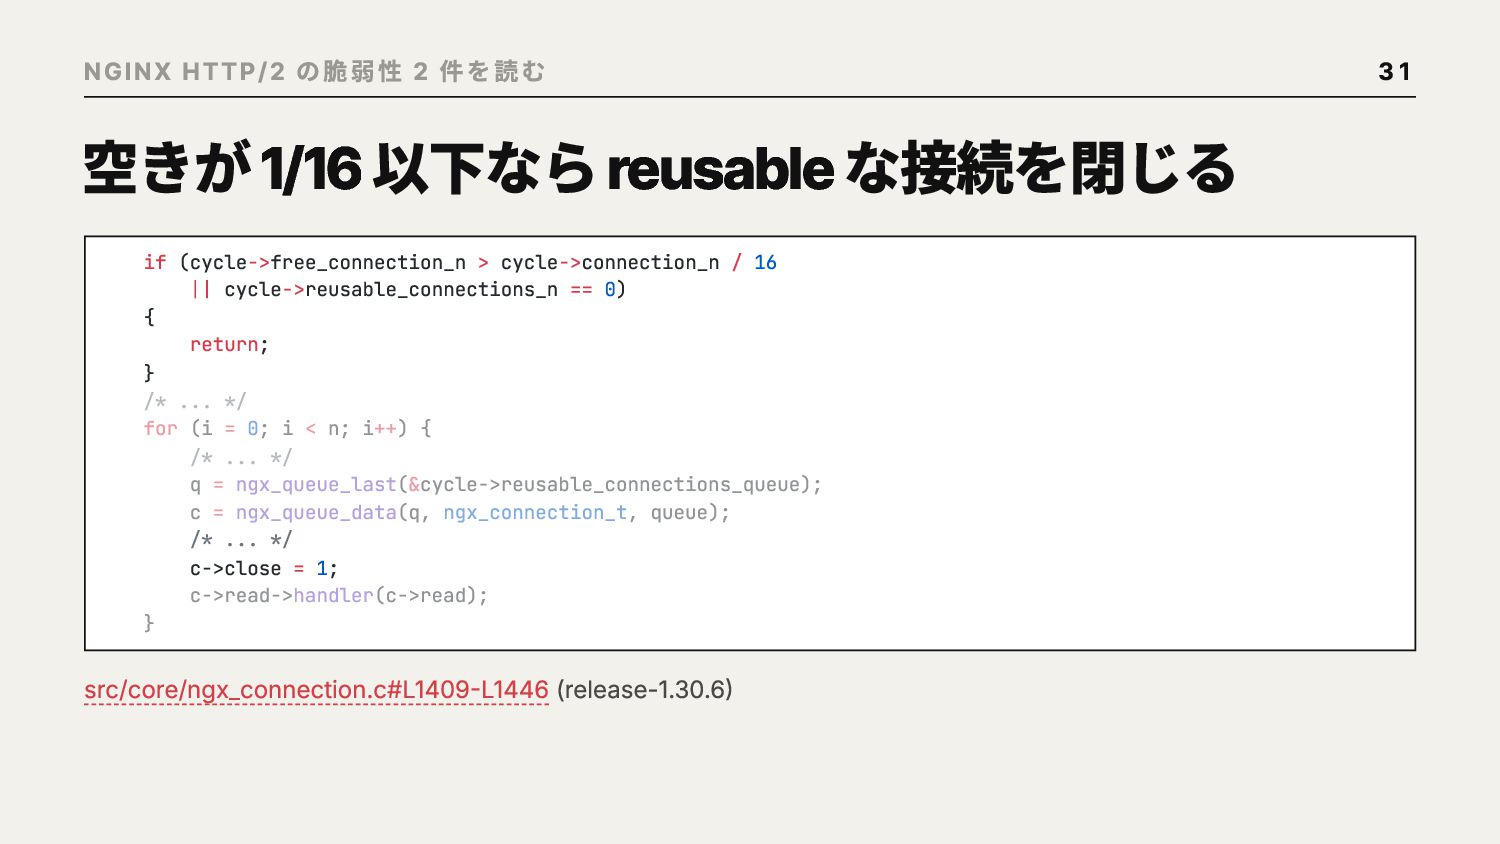
NGINX HTTP/2 の脆弱性 2 件を読む 空きが 1/16 以下なら reusable な接続を閉じる
if (cycle->free_connection_n > cycle->connection_n / 16 || cycle->reusable_connections_n == 0) { return; } /* ... */ for (i = 0; i < n; i++) { /* ... */ q = ngx_queue_last(&cycle->reusable_connections_queue); c = ngx_queue_data(q, ngx_connection_t, queue); /* ... */ c->close = 1; c->read->handler(c->read); } src/core/ngx_connection.c#L1409-L1446 (release-1.30.6) 31 -
NGINX HTTP/2 の脆弱性 2 件を読む ストリームが 0 本なら reusable にする
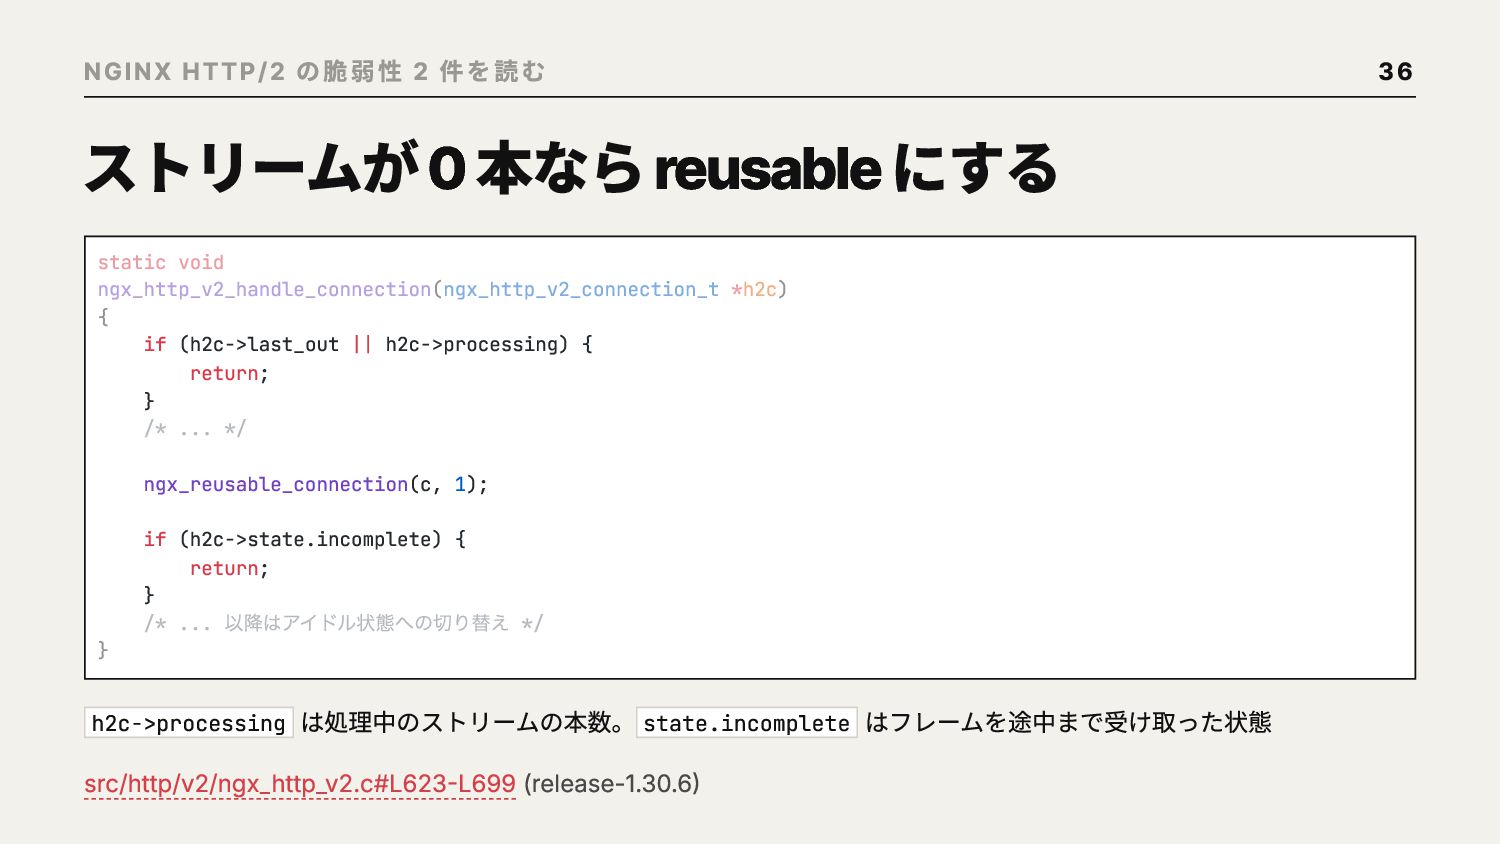
static void ngx_http_v2_handle_connection(ngx_http_v2_connection_t *h2c) { if (h2c->last_out || h2c->processing) { return; } /* ... */ ngx_reusable_connection(c, 1); } if (h2c->state.incomplete) { return; } /* ... 以降はアイドル状態への切り替え */ h2c->processing は処理中のストリームの本数。 state.incomplete はフレームを途中まで受け取った状態 src/http/v2/ngx_http_v2.c#L623-L699 (release-1.30.6) 36 -
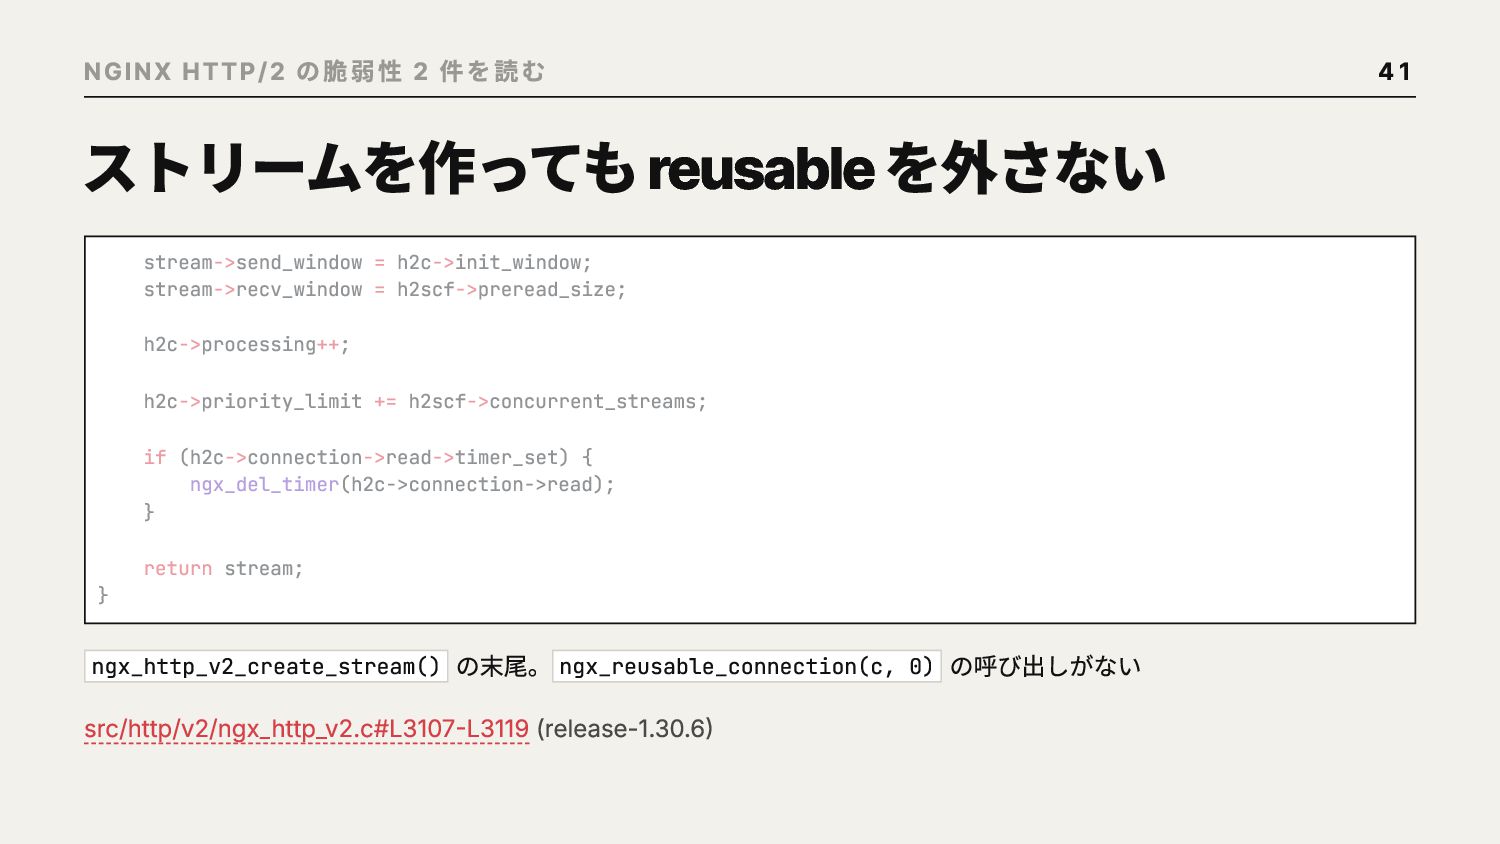
NGINX HTTP/2 の脆弱性 2 件を読む ストリームを作っても reusable を外さない stream->send_window =
h2c->init_window; stream->recv_window = h2scf->preread_size; h2c->processing++; h2c->priority_limit += h2scf->concurrent_streams; if (h2c->connection->read->timer_set) { ngx_del_timer(h2c->connection->read); } } return stream; ngx_http_v2_create_stream() の末尾。 ngx_reusable_connection(c, 0) の呼び出しがない src/http/v2/ngx_http_v2.c#L3107-L3119 (release-1.30.6) 41 -
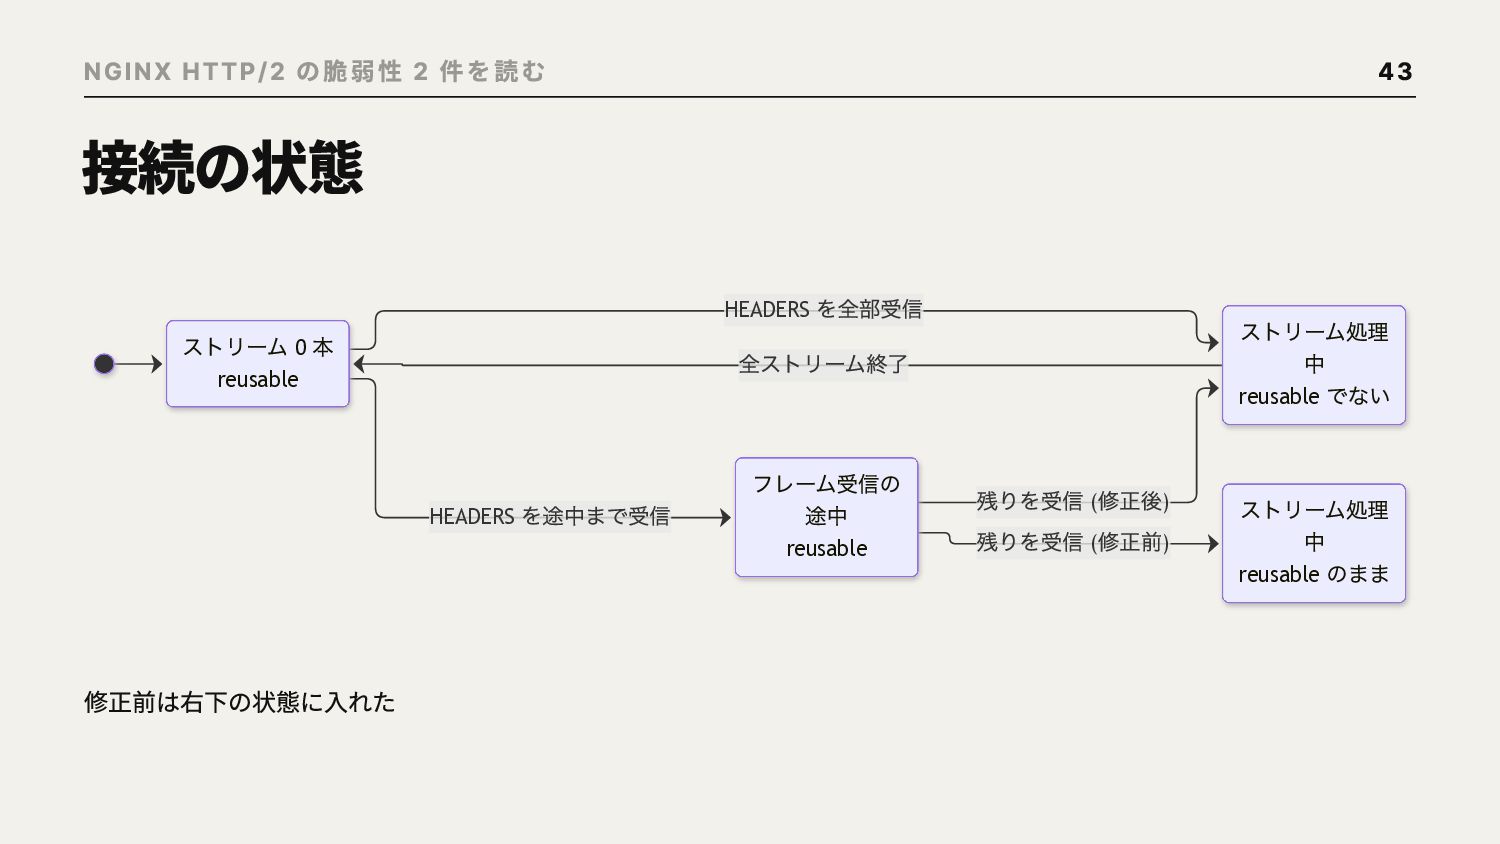
NGINX HTTP/2 の脆弱性 2 件を読む 43 接続の状態 を全部受信 全ストリーム終了 HEADERS
ストリーム 0 本 reusable HEADERS 修正前は右下の状態に入れた を途中まで受信 フレーム受信の 途中 reusable ストリーム処理 中 reusable でない 残りを受信 (修正後) 残りを受信 (修正前) ストリーム処理 中 reusable のまま -
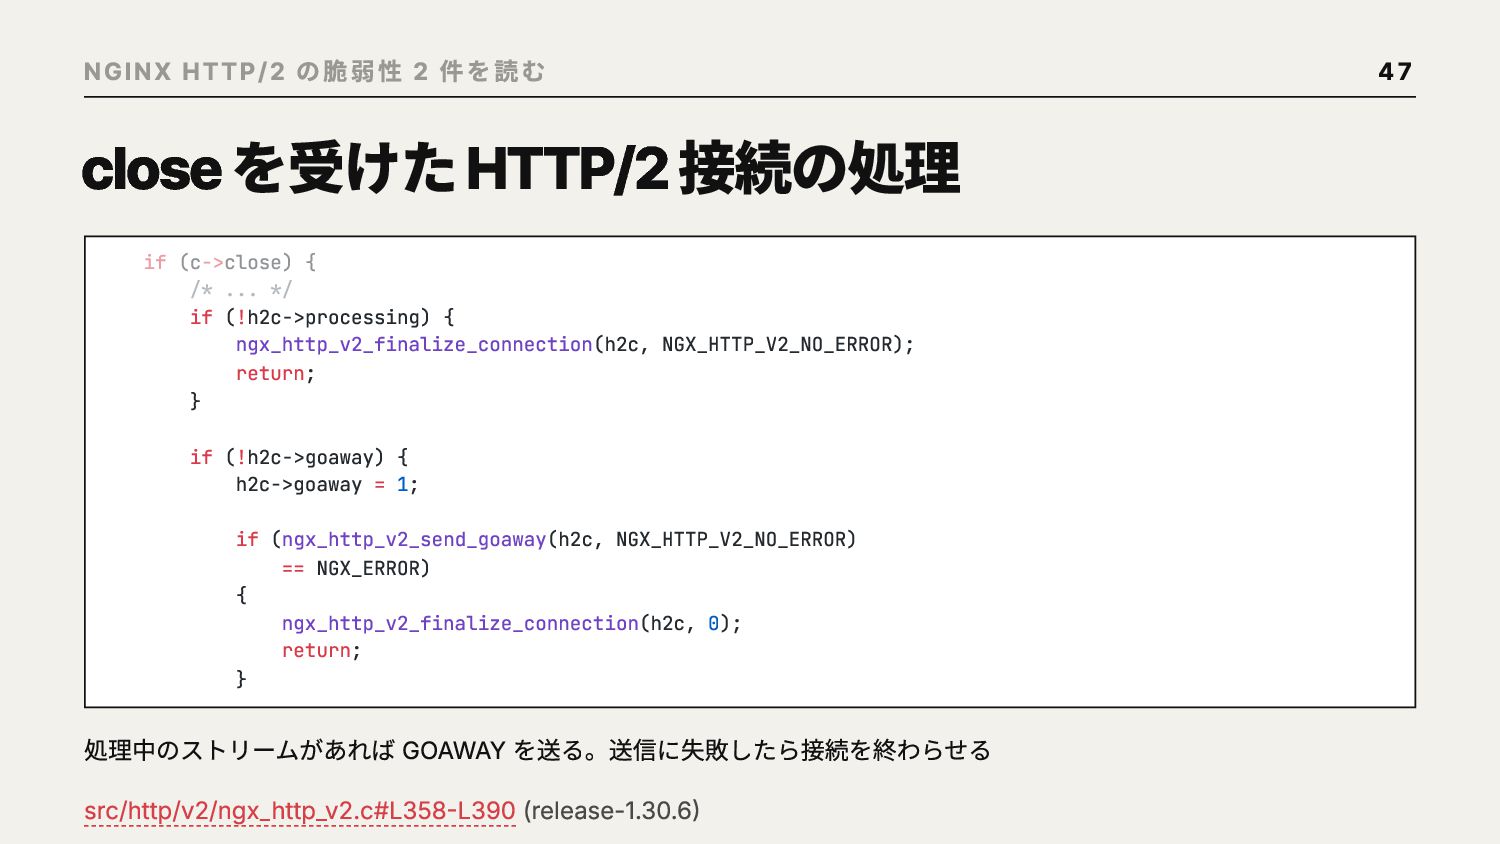
NGINX HTTP/2 close の脆弱性 2 件を読む を受けた HTTP/2 接続の処理 if
(c->close) { /* ... */ if (!h2c->processing) { ngx_http_v2_finalize_connection(h2c, NGX_HTTP_V2_NO_ERROR); return; } if (!h2c->goaway) { h2c->goaway = 1; if (ngx_http_v2_send_goaway(h2c, NGX_HTTP_V2_NO_ERROR) == NGX_ERROR) { ngx_http_v2_finalize_connection(h2c, 0); return; } 処理中のストリームがあれば GOAWAY を送る。送信に失敗したら接続を終わらせる src/http/v2/ngx_http_v2.c#L358-L390 (release-1.30.6) 47 -
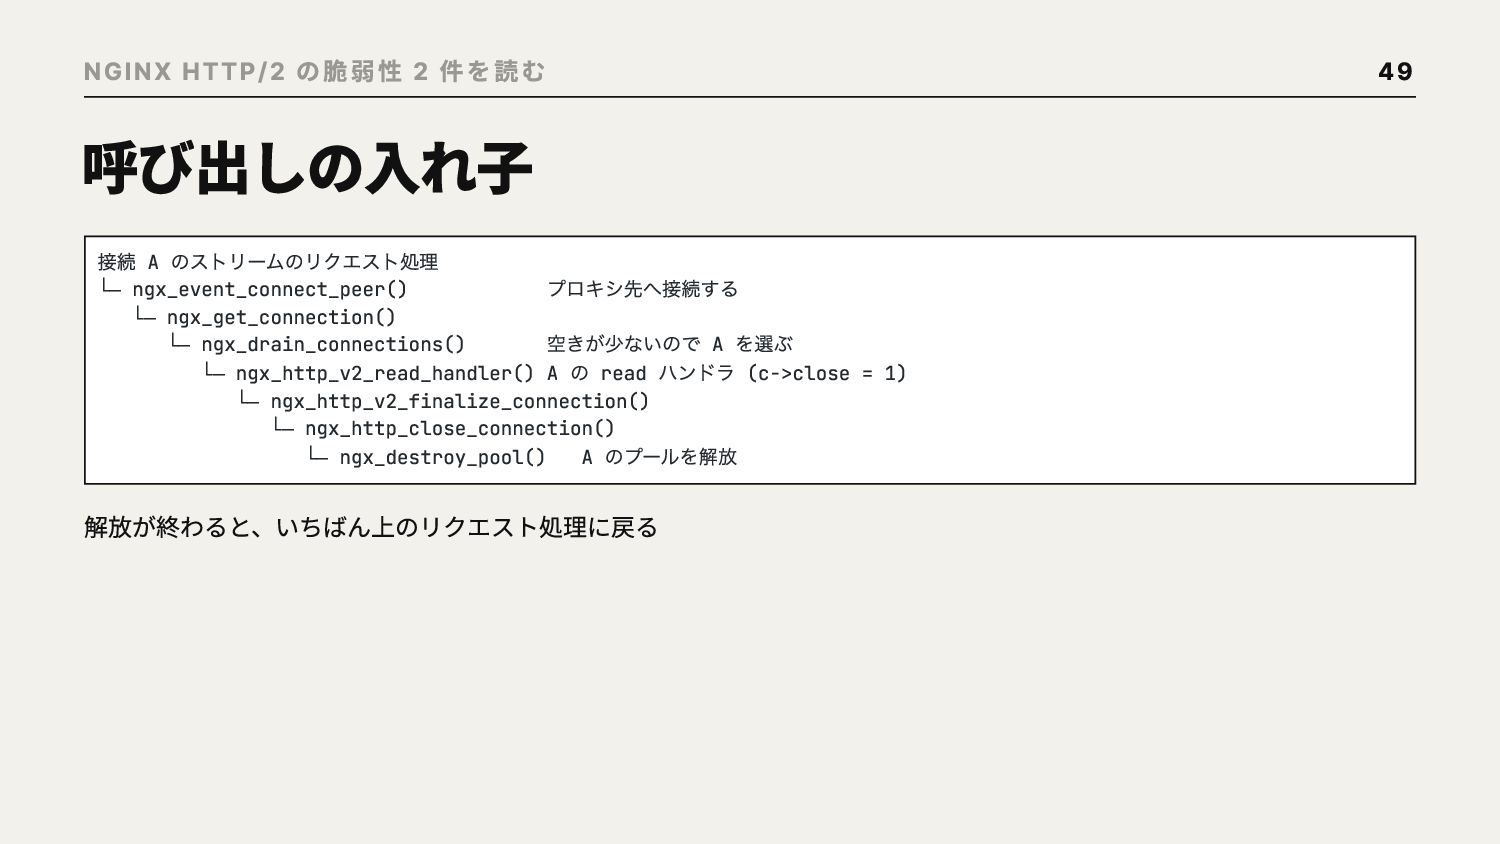
NGINX HTTP/2 の脆弱性 2 件を読む 49 呼び出しの入れ子 接続 A のストリームのリクエスト処理
プロキシ先へ接続する 空きが少ないので A を選ぶ の ハンドラ (c->close = 1) └─ ngx_event_connect_peer() └─ ngx_get_connection() └─ ngx_drain_connections() └─ ngx_http_v2_read_handler() A read └─ ngx_http_v2_finalize_connection() └─ ngx_http_close_connection() └─ ngx_destroy_pool() A のプールを解放 解放が終わると、いちばん上のリクエスト処理に戻る -
攻撃者 接続 A) nginx ( HEADERS プロキシ先 の先頭だけ 戻った先は 解放済みメモリ
A HEADERS を reusable に登録 の残り ストリーム作成 (reusable のまま) 接続を確保しようとする 空きが少ない → A に close = 1 GOAWAY の送信に失敗 A を閉じてプールを解放 リクエスト処理に戻る → 解放済みメモリを使う リクエスト処理は解放された接続のメモリを使い続ける 51 / 93 -
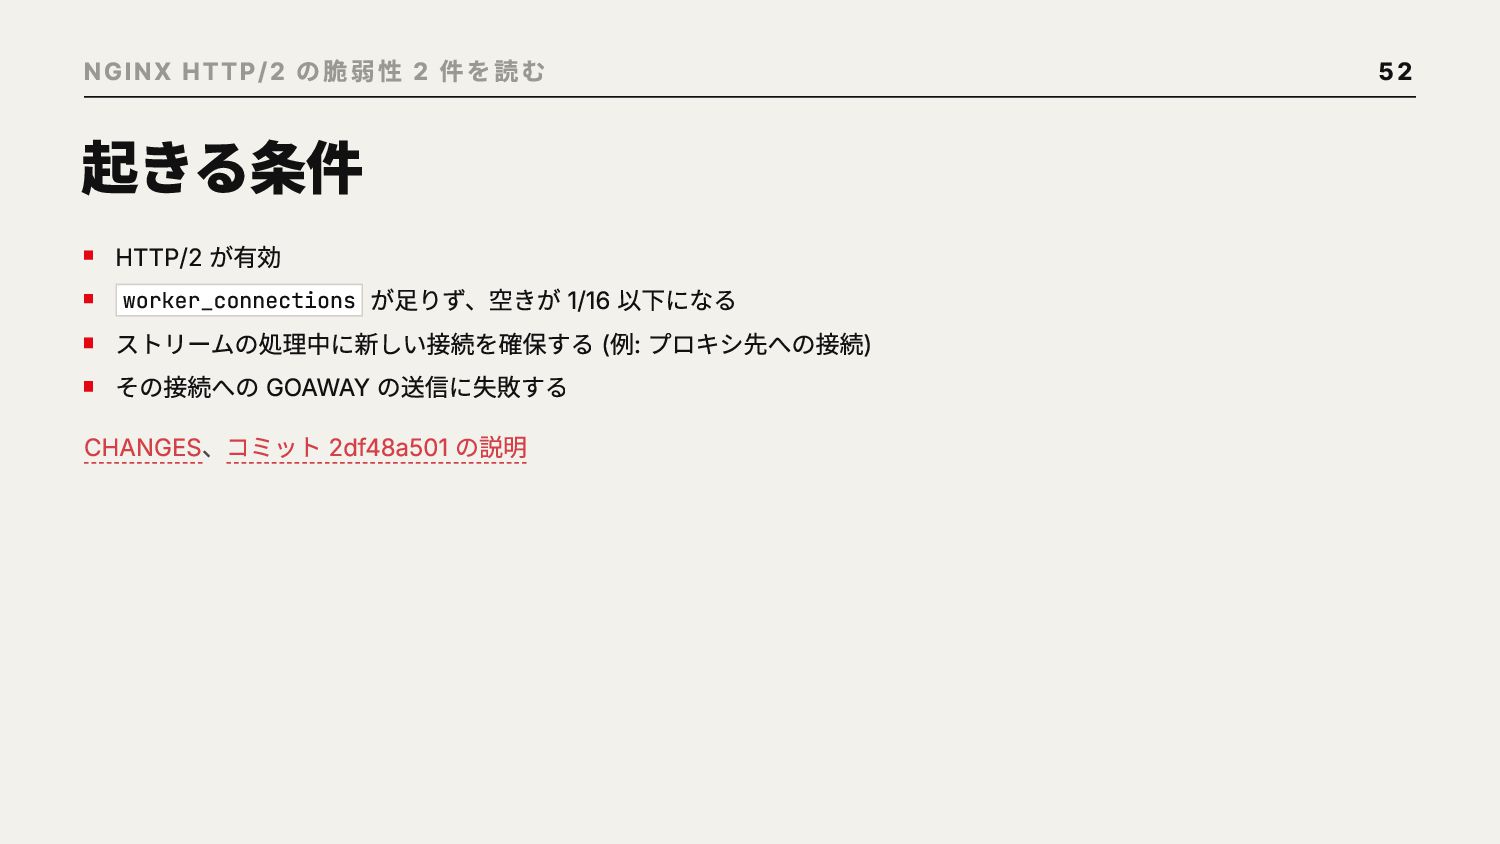
NGINX HTTP/2 の脆弱性 2 件を読む 起きる条件 HTTP/2 が有効 が足りず、空きが 1/16
以下になる ストリームの処理中に新しい接続を確保する (例: プロキシ先への接続) その接続への GOAWAY の送信に失敗する CHANGES、コミット 2df48a501 の説明 worker_connections 52 -
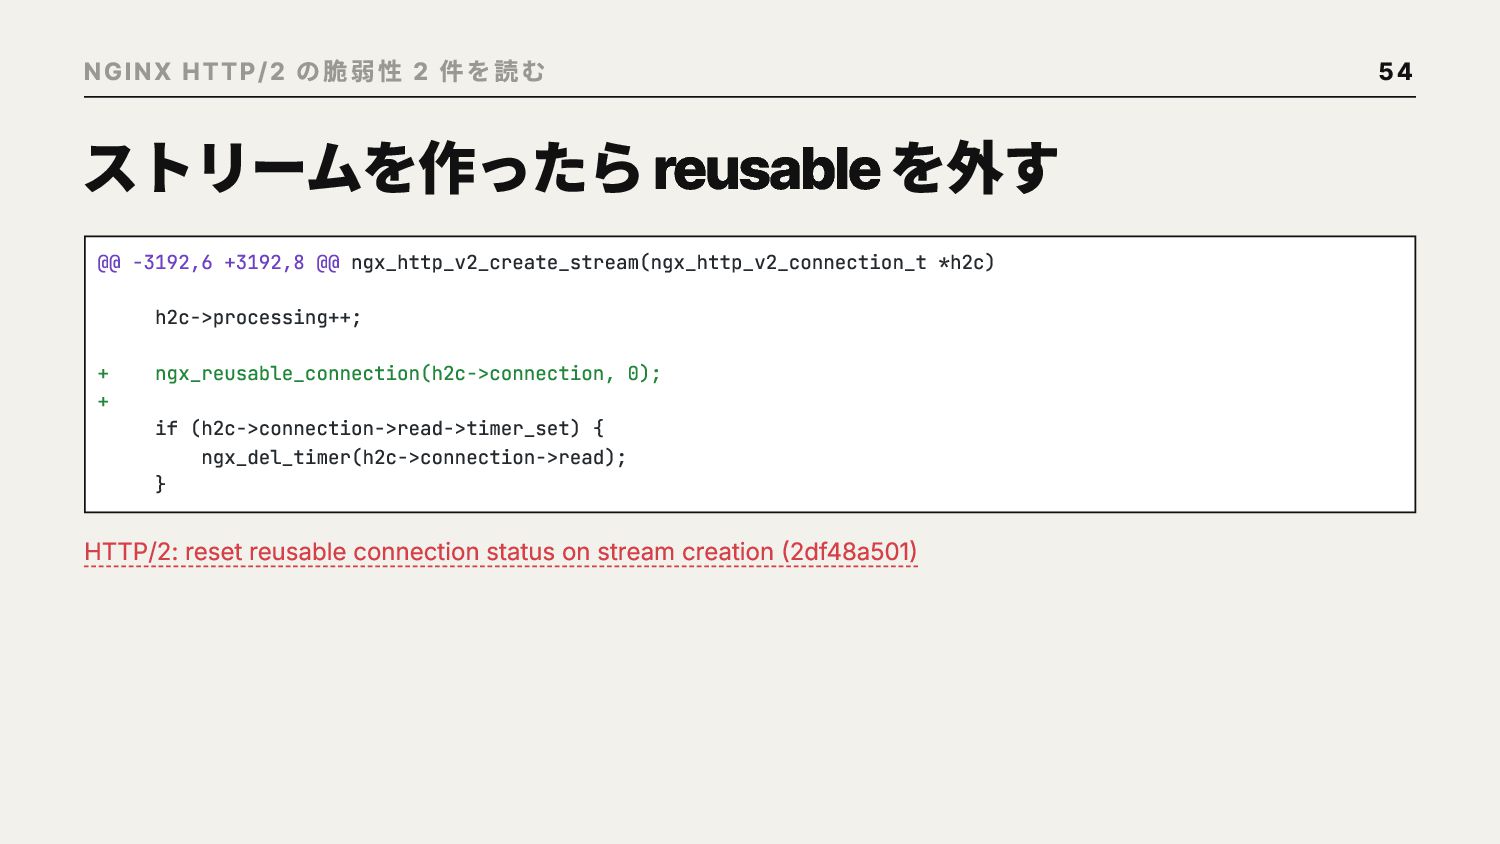
NGINX HTTP/2 の脆弱性 2 件を読む ストリームを作ったら reusable を外す @@ -3192,6
+3192,8 @@ ngx_http_v2_create_stream(ngx_http_v2_connection_t *h2c) h2c->processing++; + + ngx_reusable_connection(h2c->connection, 0); if (h2c->connection->read->timer_set) { ngx_del_timer(h2c->connection->read); } HTTP/2: reset reusable connection status on stream creation (2df48a501) 54 -
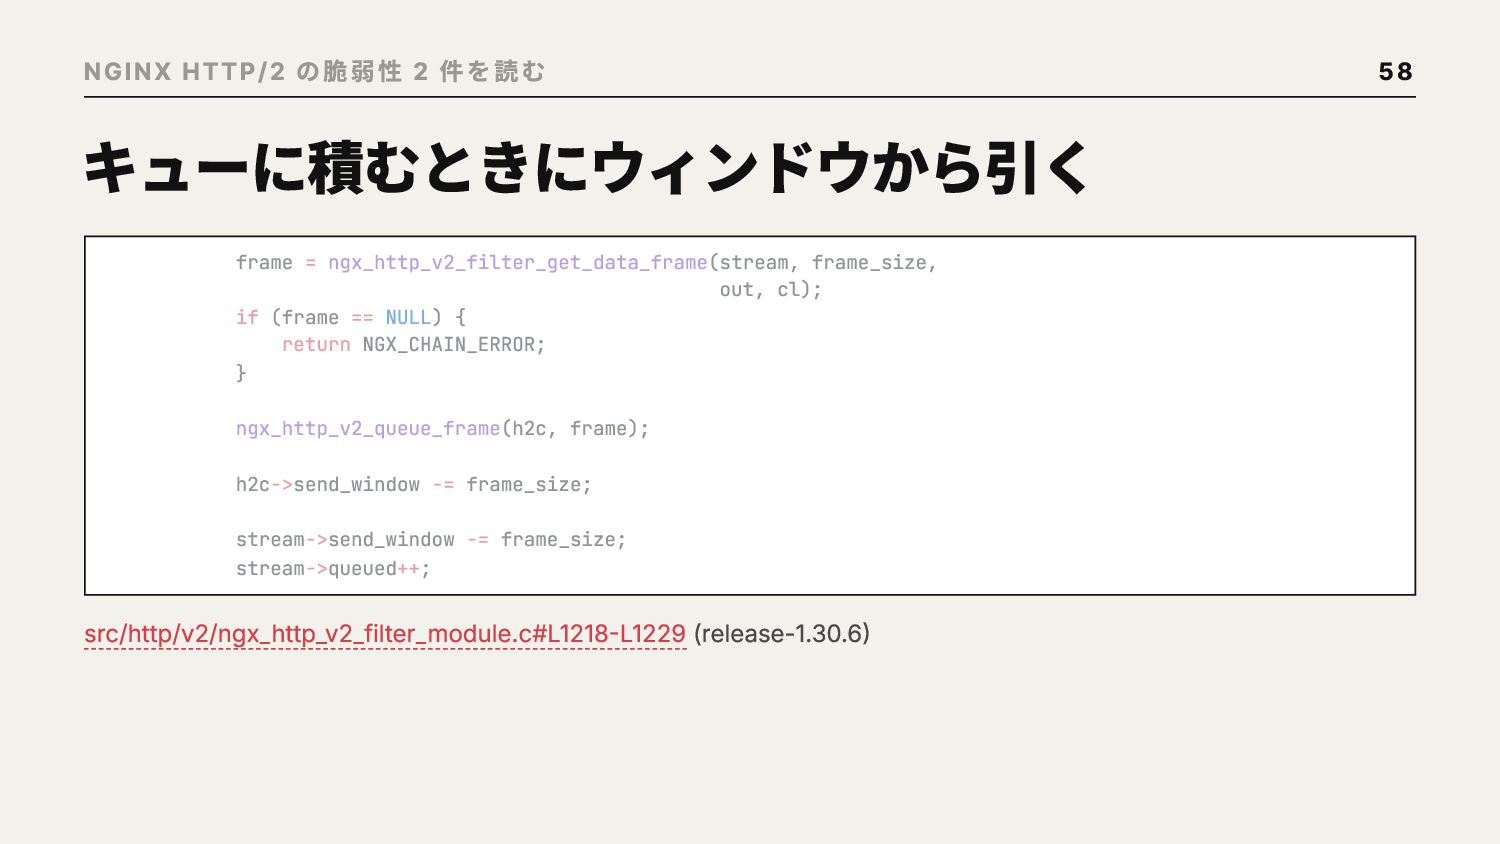
NGINX HTTP/2 の脆弱性 2 件を読む キューに積むときにウィンドウから引く frame = ngx_http_v2_filter_get_data_frame(stream, frame_size,
out, cl); if (frame == NULL) { return NGX_CHAIN_ERROR; } ngx_http_v2_queue_frame(h2c, frame); h2c->send_window -= frame_size; stream->send_window -= frame_size; stream->queued++; src/http/v2/ngx_http_v2_filter_module.c#L1218-L1229 (release-1.30.6) 58 -
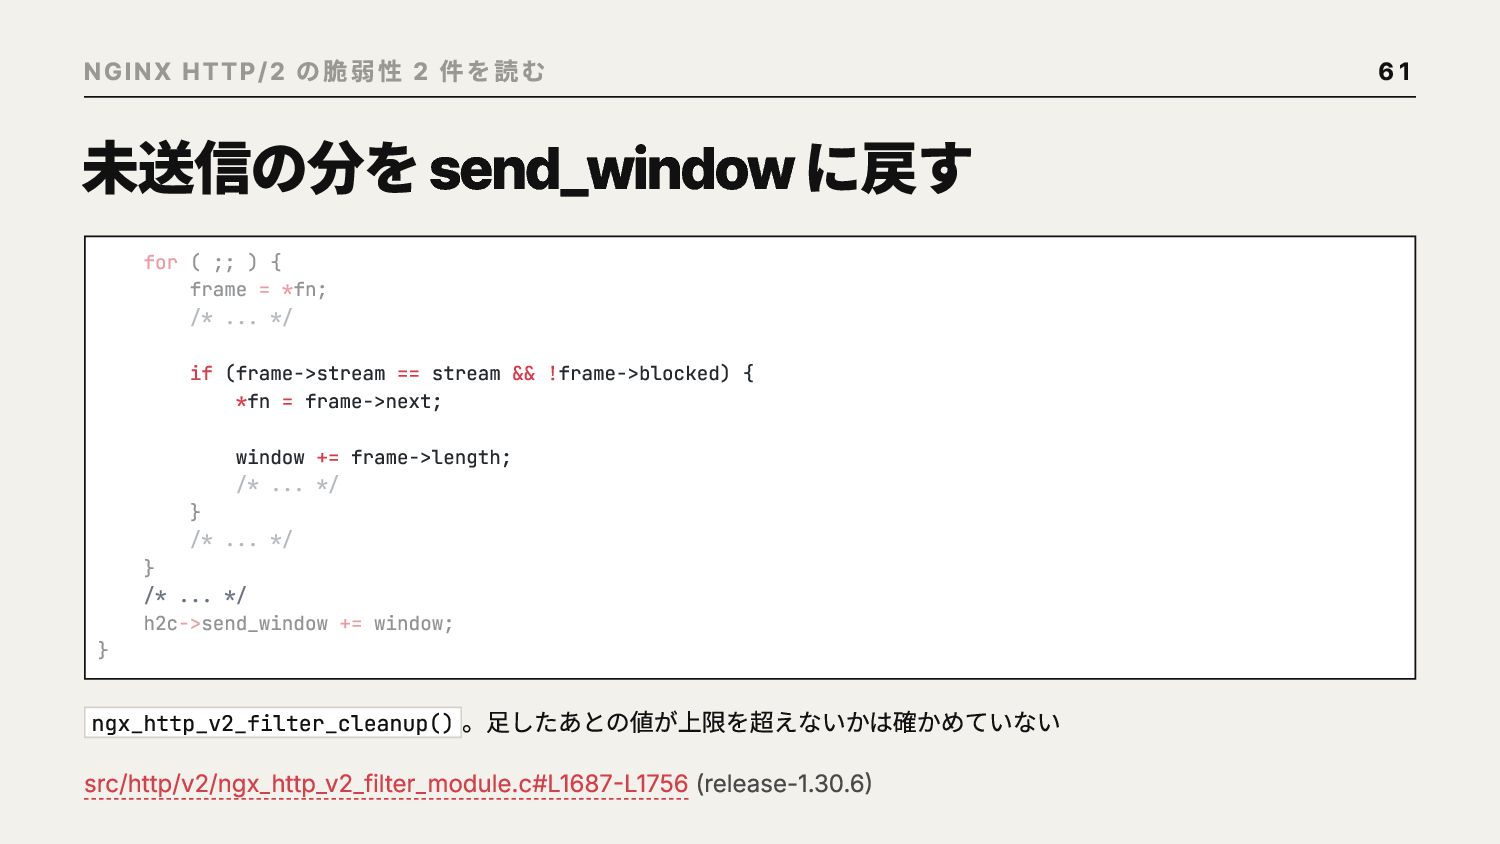
NGINX HTTP/2 の脆弱性 2 件を読む 未送信の分を send_window に戻す for (
;; ) { frame = *fn; /* ... */ if (frame->stream == stream && !frame->blocked) { *fn = frame->next; window += frame->length; /* ... */ } /* ... */ } } /* ... */ h2c->send_window += window; ngx_http_v2_filter_cleanup() 。足したあとの値が上限を超えないかは確かめていない src/http/v2/ngx_http_v2_filter_module.c#L1687-L1756 (release-1.30.6) 61 -
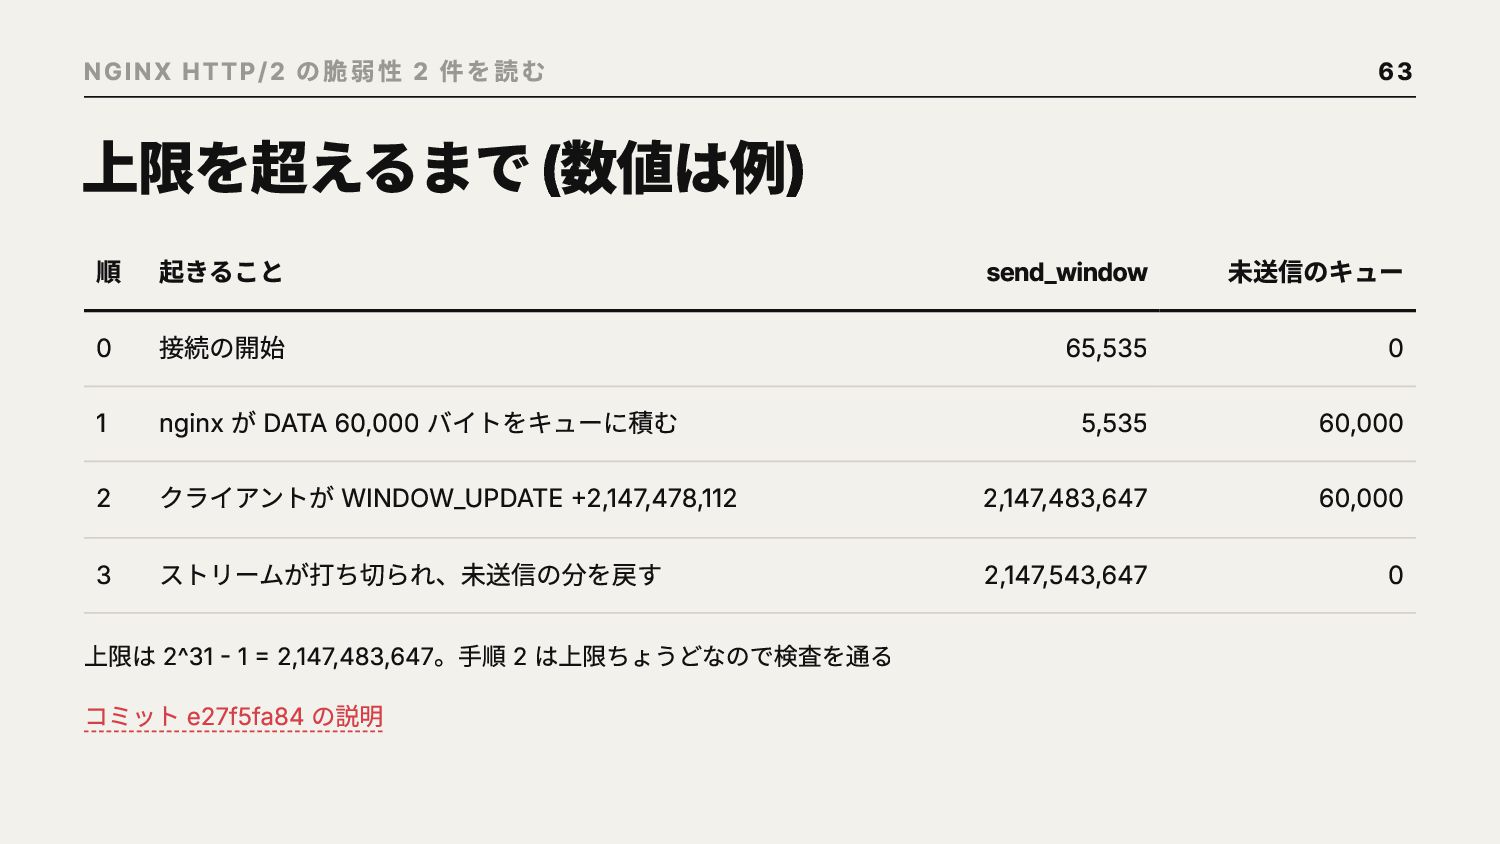
NGINX HTTP/2 の脆弱性 2 件を読む 63 上限を超えるまで (数値は例) 順 起きること
send_window 未送信のキュー 65,535 0 5,535 60,000 2 接続の開始 nginx が DATA 60,000 バイトをキューに積む クライアントが WINDOW_UPDATE +2,147,478,112 2,147,483,647 60,000 3 ストリームが打ち切られ、未送信の分を戻す 2,147,543,647 0 0 1 上限は 2^31 - 1 = 2,147,483,647。手順 2 は上限ちょうどなので検査を通る コミット e27f5fa84 の説明 -
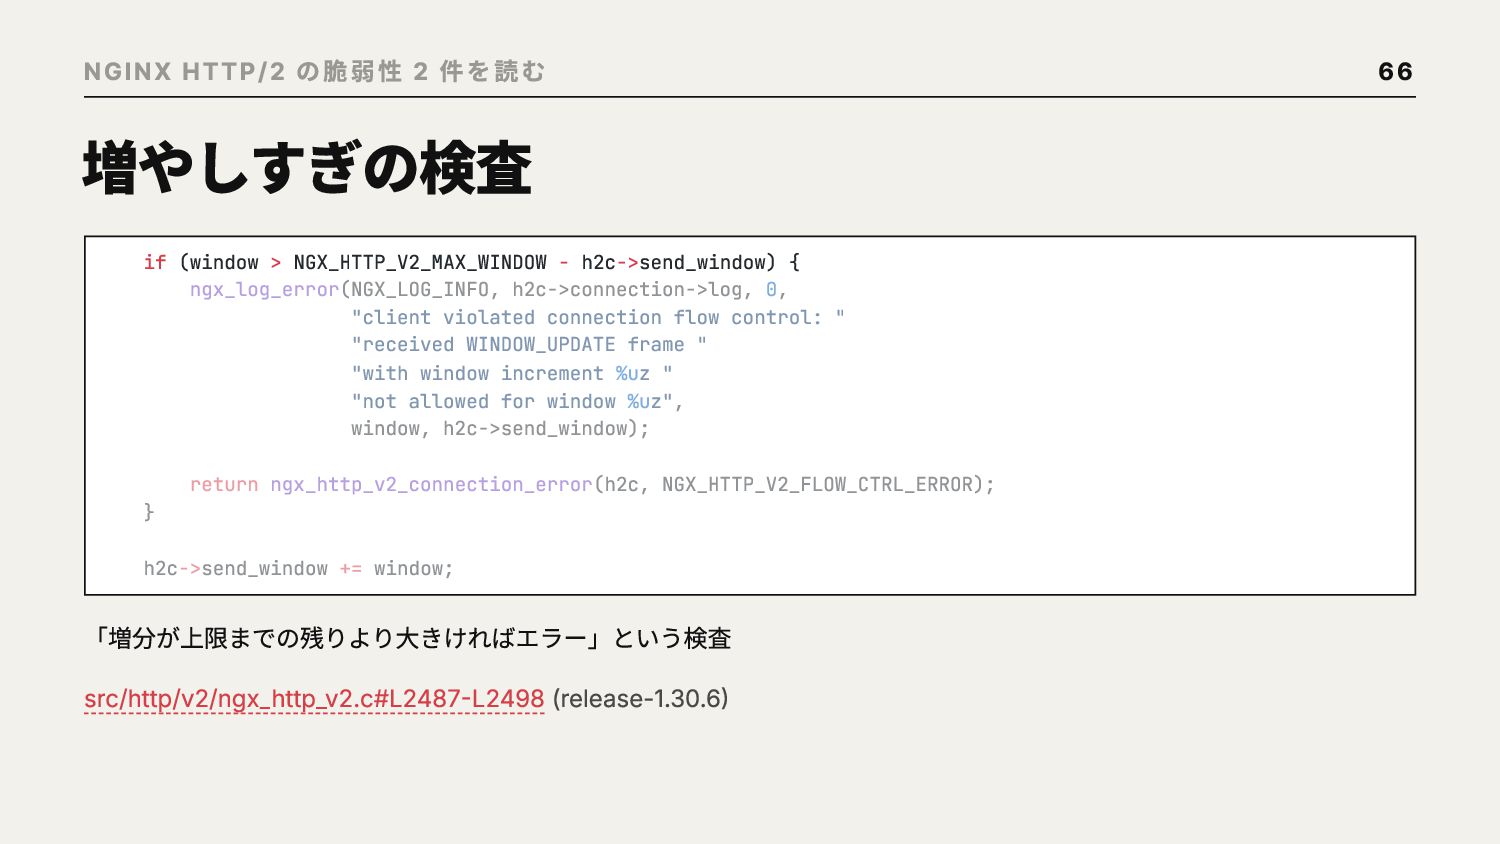
NGINX HTTP/2 の脆弱性 2 件を読む 増やしすぎの検査 if (window > NGX_HTTP_V2_MAX_WINDOW
- h2c->send_window) { ngx_log_error(NGX_LOG_INFO, h2c->connection->log, 0, "client violated connection flow control: " "received WINDOW_UPDATE frame " "with window increment %uz " "not allowed for window %uz", window, h2c->send_window); } return ngx_http_v2_connection_error(h2c, NGX_HTTP_V2_FLOW_CTRL_ERROR); h2c->send_window += window; 「増分が上限までの残りより大きければエラー」という検査 src/http/v2/ngx_http_v2.c#L2487-L2498 (release-1.30.6) 66 -
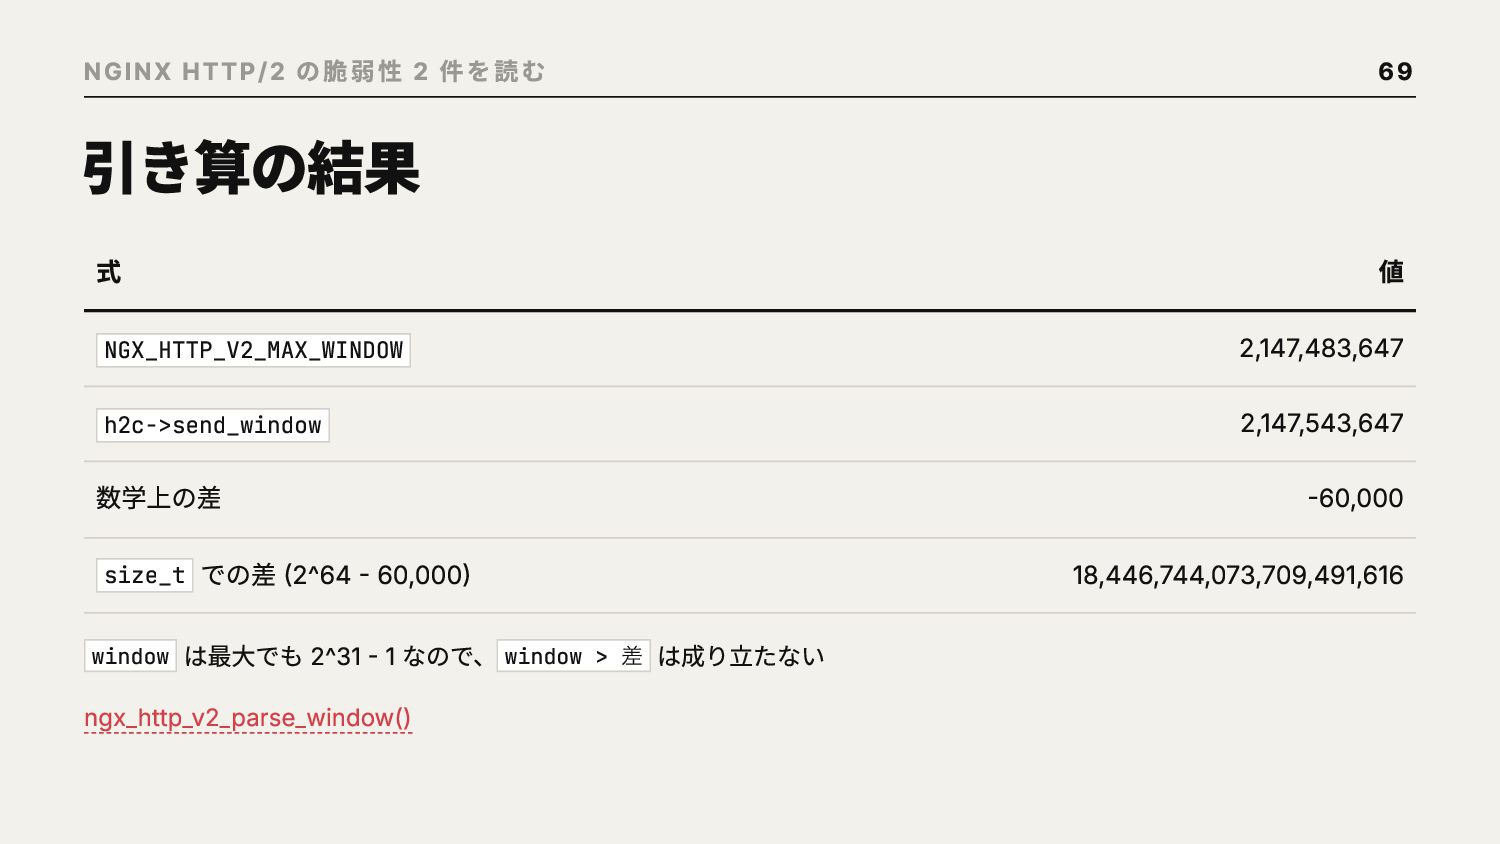
NGINX HTTP/2 の脆弱性 2 件を読む 引き算の結果 式 69 値 NGX_HTTP_V2_MAX_WINDOW
2,147,483,647 h2c->send_window 2,147,543,647 数学上の差 size_t window での差 (2^64 - 60,000) は最大でも 2^31 - 1 なので、 window > 差 は成り立たない ngx_http_v2_parse_window() -60,000 18,446,744,073,709,491,616 -
以上で 次の問題が起きる 2^63 約 2^32 回の WINDOW_UPDATE が要る。1 フレーム 13
バイトなので約 56 GB (コードからの試算) 72 / 93 -
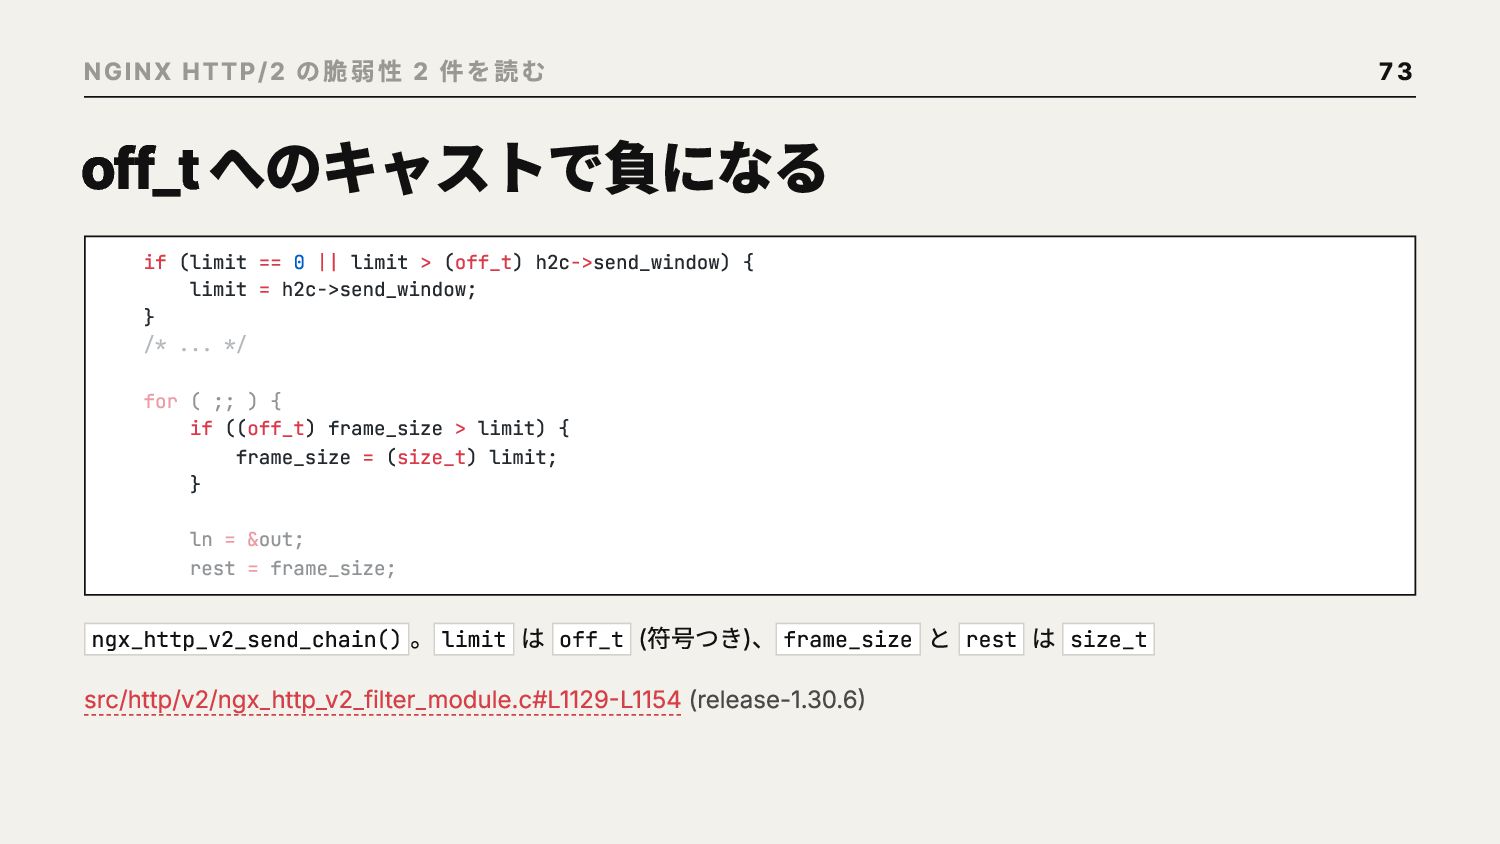
NGINX HTTP/2 off_t の脆弱性 2 件を読む へのキャストで負になる if (limit ==
0 || limit > (off_t) h2c->send_window) { limit = h2c->send_window; } /* ... */ for ( ;; ) { if ((off_t) frame_size > limit) { frame_size = (size_t) limit; } ln = &out; rest = frame_size; ngx_http_v2_send_chain() 。 limit は off_t (符号つき)、 frame_size と rest は size_t src/http/v2/ngx_http_v2_filter_module.c#L1129-L1154 (release-1.30.6) 73 -
NGINX HTTP/2 の脆弱性 2 件を読む 74 型の変換を追う 変数 型 値
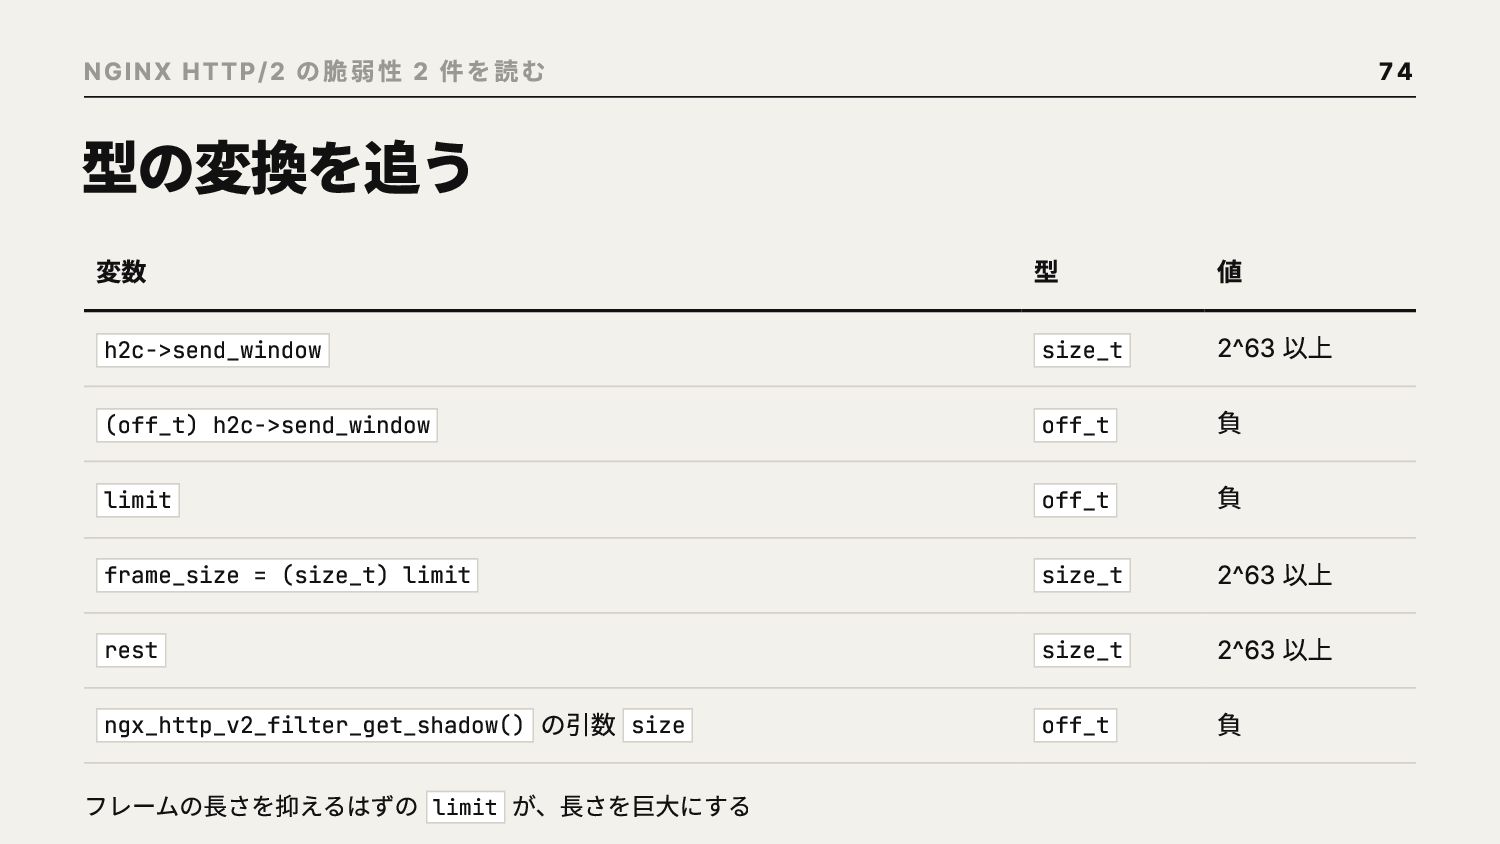
h2c->send_window size_t 2^63 以上 (off_t) h2c->send_window off_t limit off_t 負 負 frame_size = (size_t) limit size_t 2^63 以上 rest size_t 2^63 以上 off_t 負 ngx_http_v2_filter_get_shadow() の引数 size フレームの長さを抑えるはずの limit が、長さを巨大にする -
NGINX HTTP/2 の脆弱性 2 件を読む 終端が先頭より前にあるバッファ static ngx_chain_t * ngx_http_v2_filter_get_shadow(ngx_http_v2_stream_t
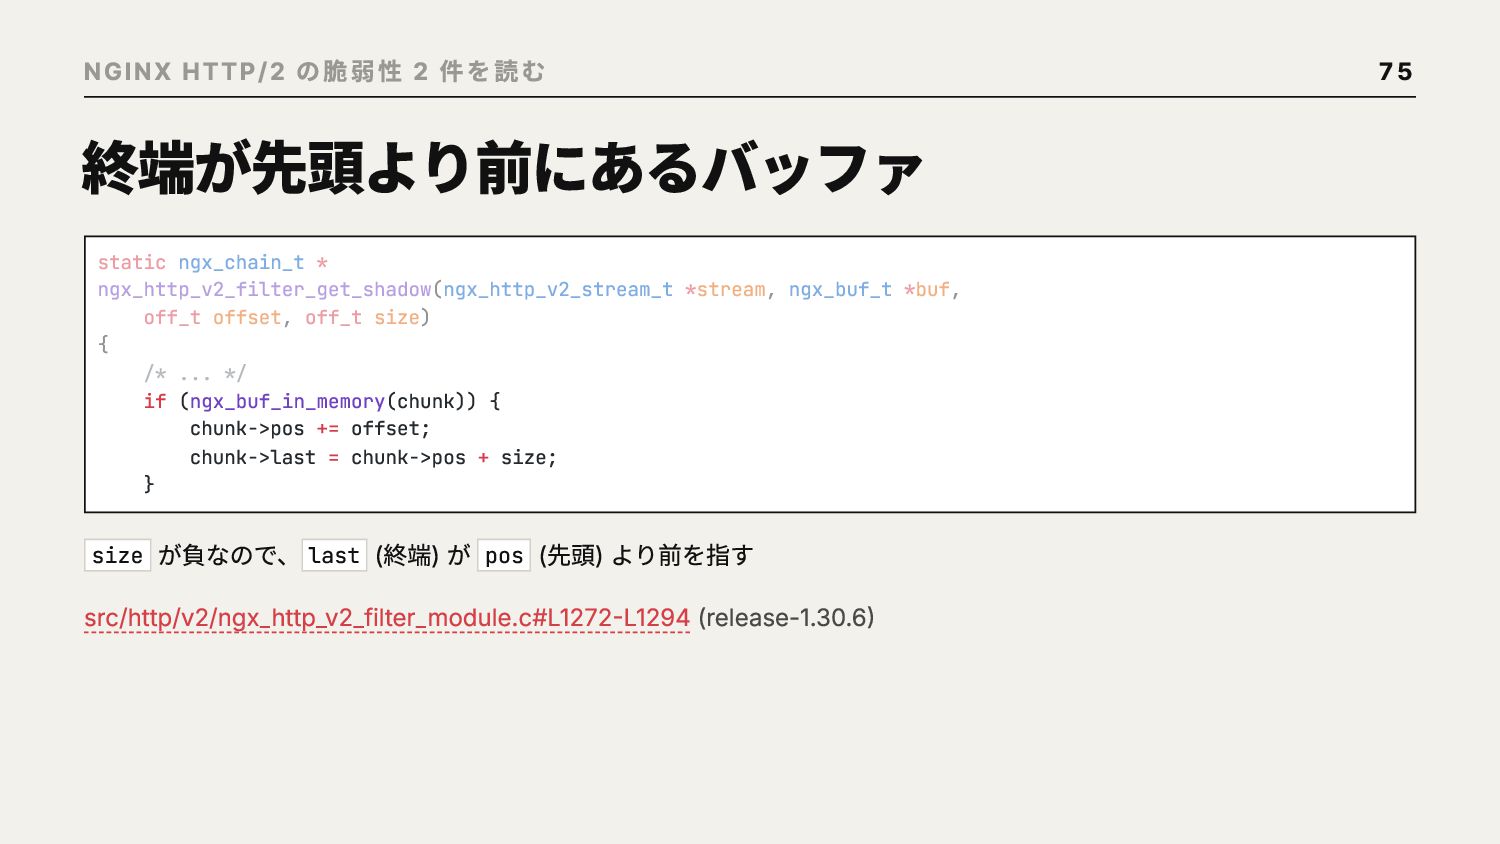
*stream, ngx_buf_t *buf, off_t offset, off_t size) { /* ... */ if (ngx_buf_in_memory(chunk)) { chunk->pos += offset; chunk->last = chunk->pos + size; } size が負なので、 last (終端) が pos (先頭) より前を指す src/http/v2/ngx_http_v2_filter_module.c#L1272-L1294 (release-1.30.6) 75 -
NGINX HTTP/2 TLS の脆弱性 2 件を読む の送信で、負の長さがコピーに渡る size = in->buf->last
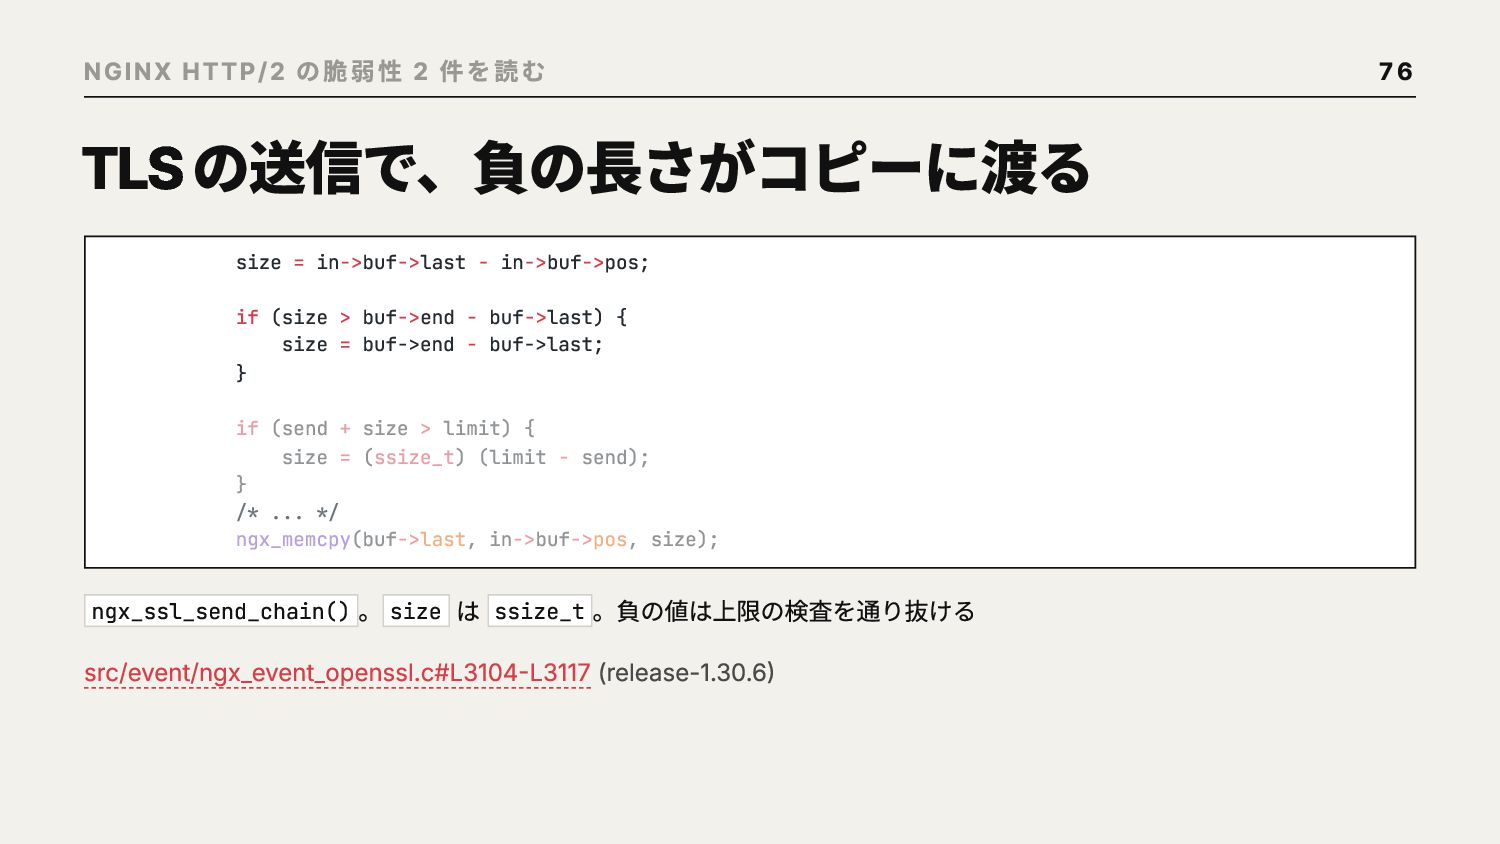
- in->buf->pos; if (size > buf->end - buf->last) { size = buf->end - buf->last; } if (send + size > limit) { size = (ssize_t) (limit - send); } /* ... */ ngx_memcpy(buf->last, in->buf->pos, size); ngx_ssl_send_chain() 。 size は ssize_t 。負の値は上限の検査を通り抜ける src/event/ngx_event_openssl.c#L3104-L3117 (release-1.30.6) 76 -
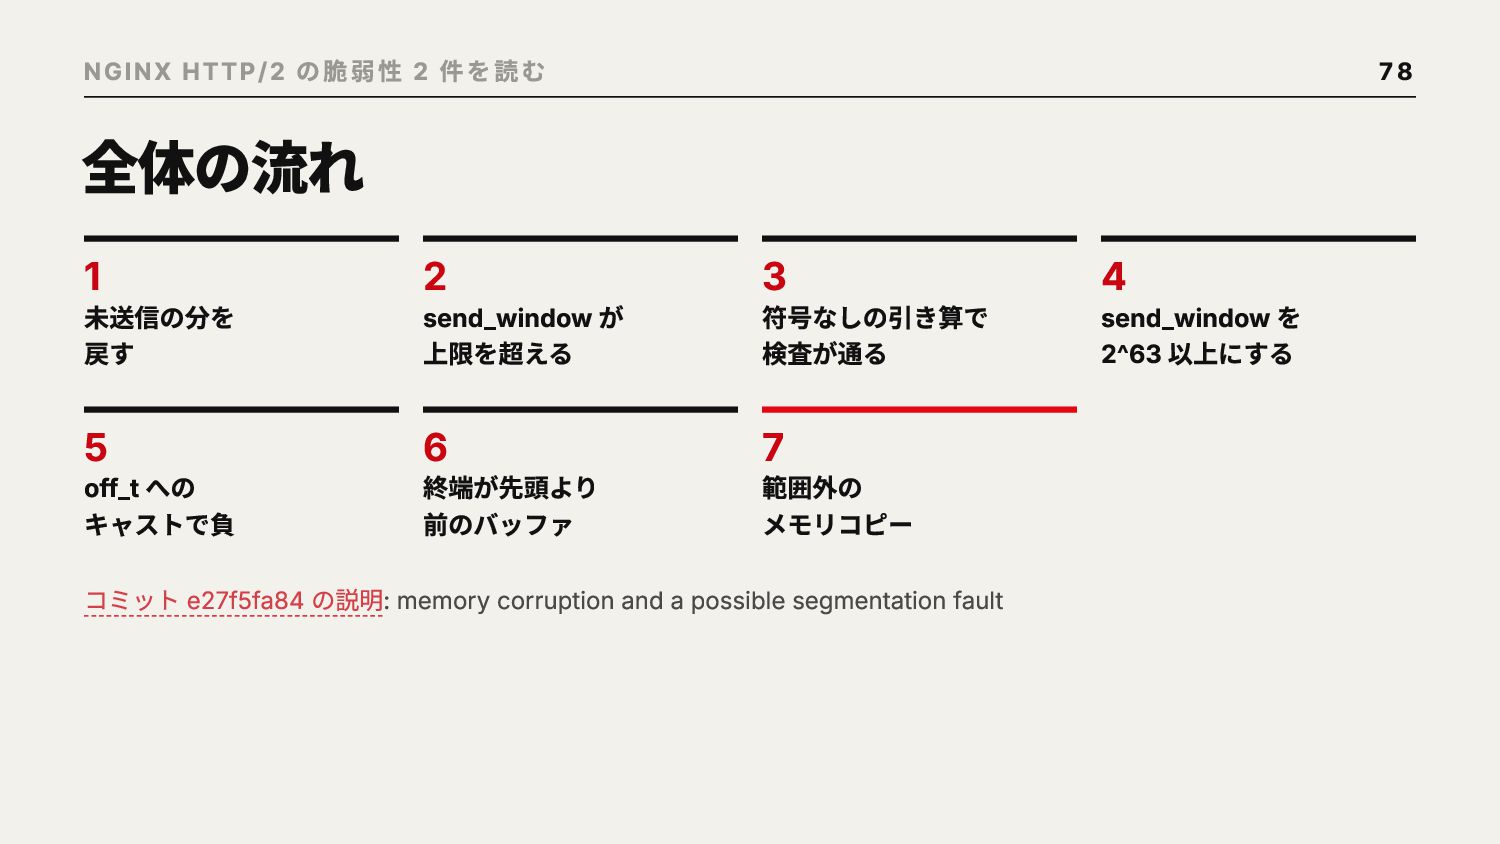
NGINX HTTP/2 の脆弱性 2 件を読む 78 全体の流れ 1 未送信の分を 戻す
2 send_window が 上限を超える 3 符号なしの引き算で 検査が通る 5 6 7 off_t への 終端が先頭より 範囲外の キャストで負 前のバッファ メモリコピー コミット e27f5fa84 の説明: memory corruption and a possible segmentation fault 4 send_window を 2^63 以上にする -
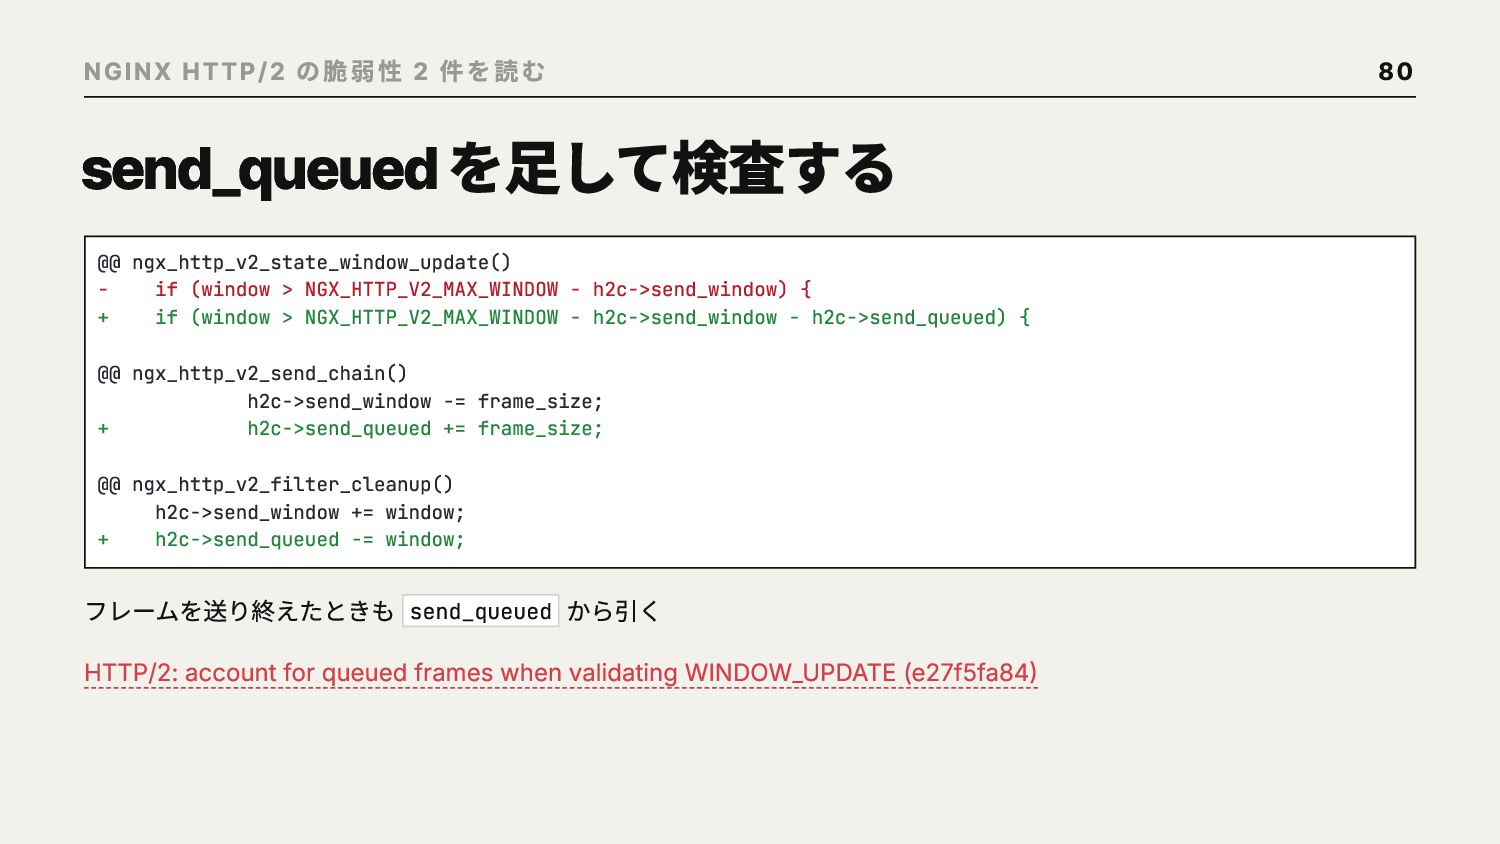
NGINX HTTP/2 の脆弱性 2 件を読む send_queued を足して検査する @@ ngx_http_v2_state_window_update() if
(window > NGX_HTTP_V2_MAX_WINDOW - h2c->send_window) { + if (window > NGX_HTTP_V2_MAX_WINDOW - h2c->send_window - h2c->send_queued) { @@ ngx_http_v2_send_chain() h2c->send_window -= frame_size; + h2c->send_queued += frame_size; @@ ngx_http_v2_filter_cleanup() h2c->send_window += window; + h2c->send_queued -= window; フレームを送り終えたときも send_queued から引く HTTP/2: account for queued frames when validating WINDOW_UPDATE (e27f5fa84) 80 -
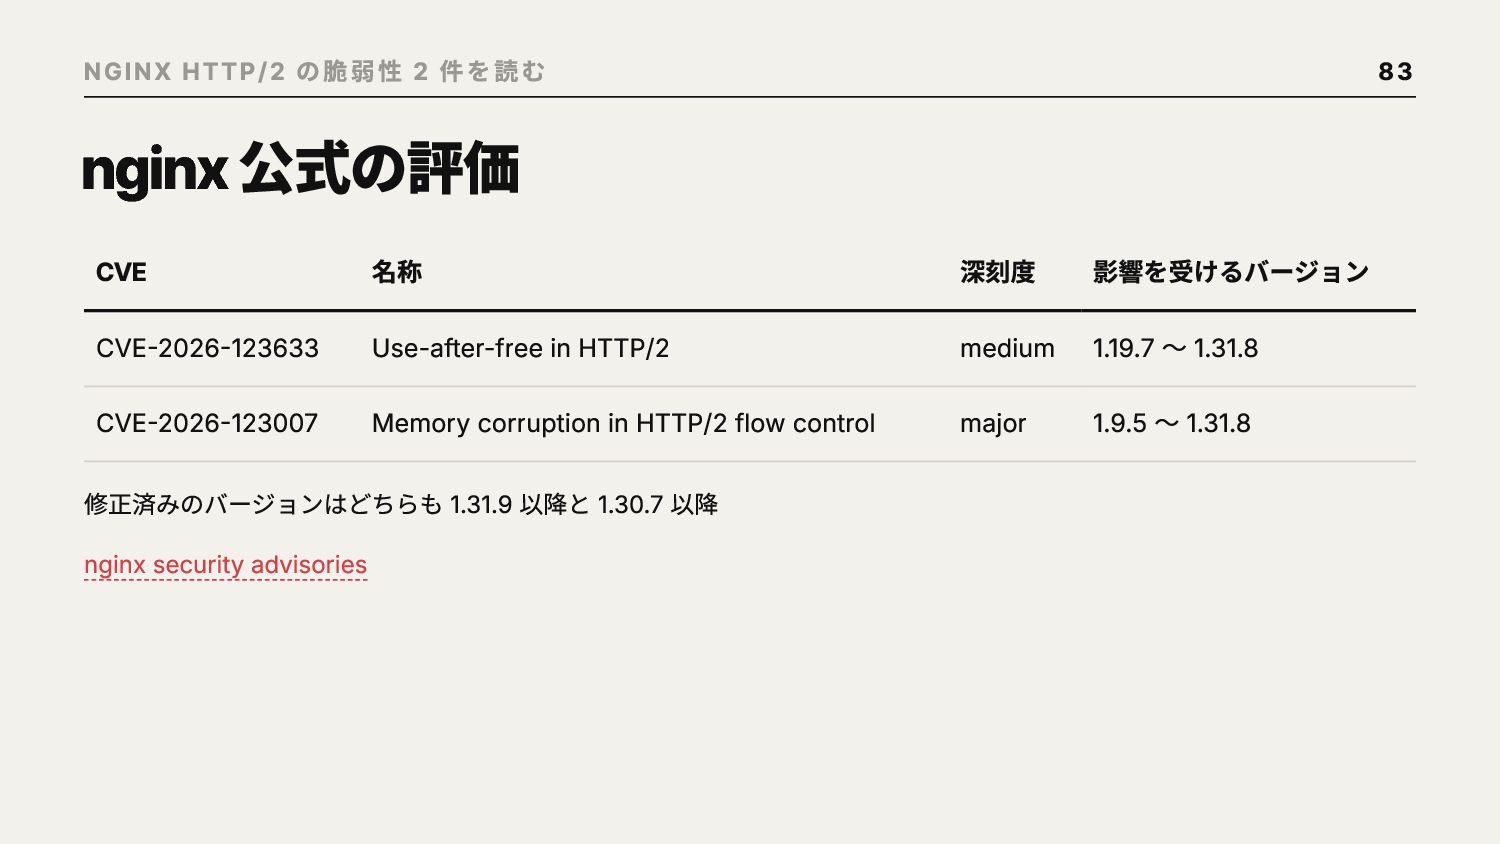
NGINX HTTP/2 nginx の脆弱性 2 件を読む 83 公式の評価 CVE 名称
深刻度 影響を受けるバージョン CVE-2026-123633 Use-after-free in HTTP/2 medium 1.19.7 〜 1.31.8 CVE-2026-123007 Memory corruption in HTTP/2 flow control major 1.9.5 〜 1.31.8 修正済みのバージョンはどちらも 1.31.9 以降と 1.30.7 以降 nginx security advisories -
CHANGES 説明 の 1 件目は「worker_connections が足りないと use-after-free が起きうる」。2 件 目は「segmentation
fault、ほかの影響の可能性」 nginx.org/en/CHANGES 84 / 93 -
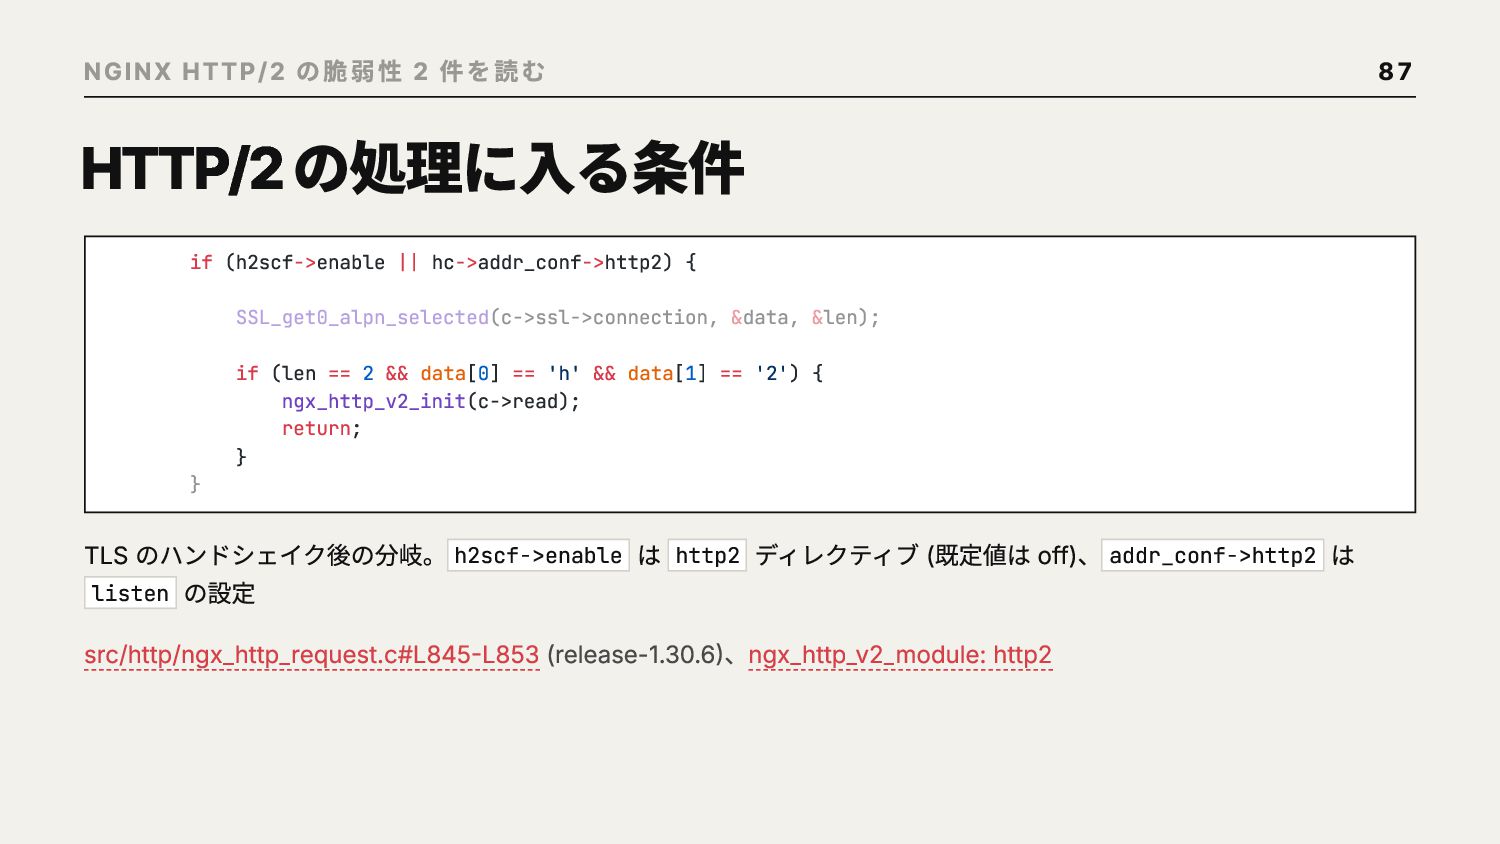
NGINX HTTP/2 HTTP/2 の脆弱性 2 件を読む の処理に入る条件 if (h2scf->enable ||
hc->addr_conf->http2) { SSL_get0_alpn_selected(c->ssl->connection, &data, &len); } if (len == 2 && data[0] == 'h' && data[1] == '2') { ngx_http_v2_init(c->read); return; } TLS のハンドシェイク後の分岐。 h2scf->enable は http2 ディレクティブ (既定値は off)、 addr_conf->http2 は listen の設定 src/http/ngx_http_request.c#L845-L853 (release-1.30.6)、ngx_http_v2_module: http2 87 -
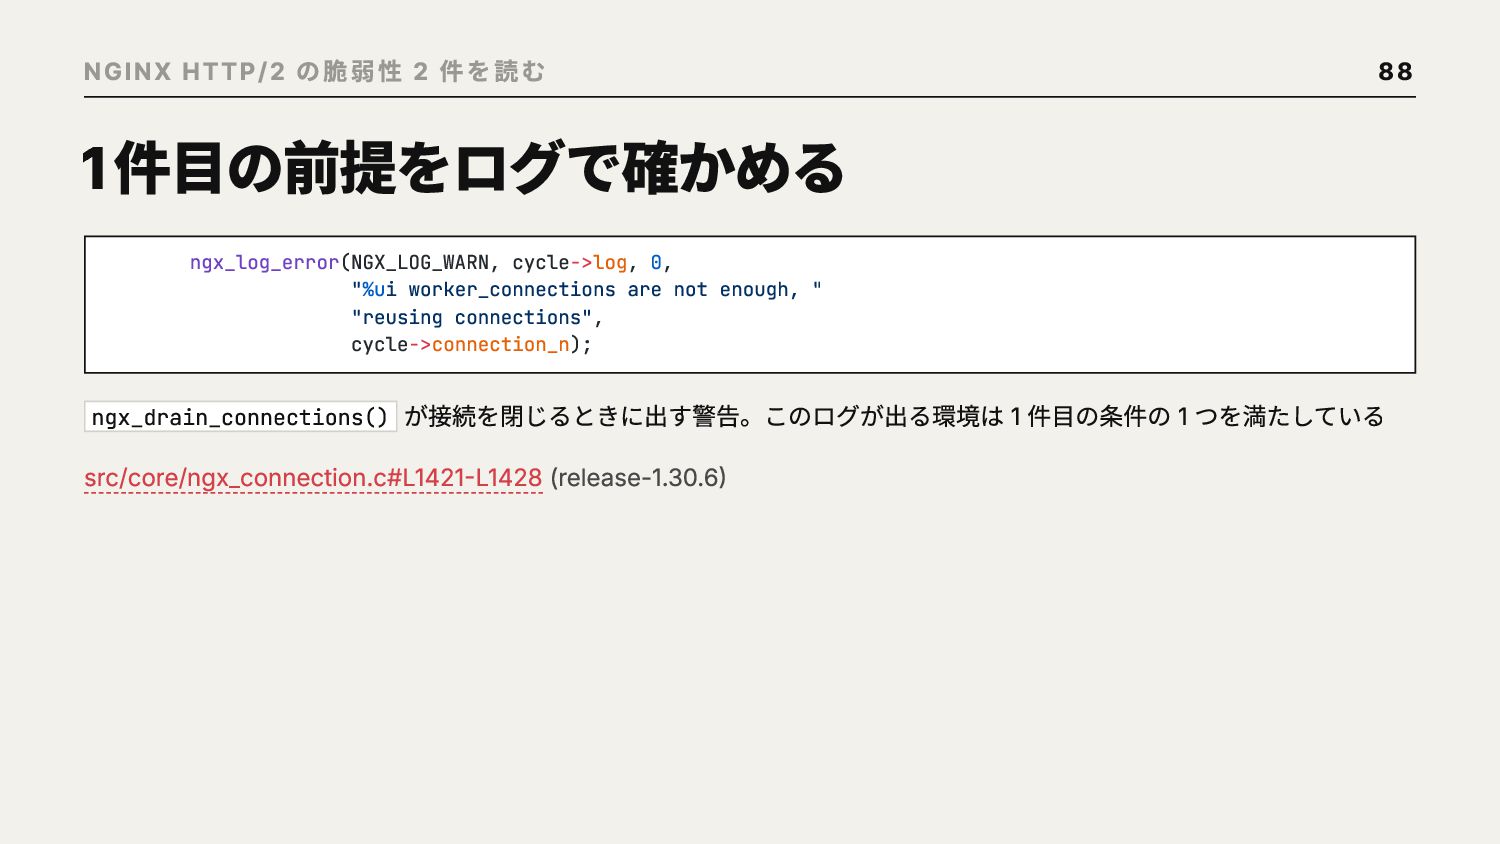
NGINX HTTP/2 1 の脆弱性 2 件を読む 件目の前提をログで確かめる 88 ngx_log_error(NGX_LOG_WARN, cycle->log,
0, "%ui worker_connections are not enough, " "reusing connections", cycle->connection_n); ngx_drain_connections() が接続を閉じるときに出す警告。このログが出る環境は 1 件目の条件の 1 つを満たしている src/core/ngx_connection.c#L1421-L1428 (release-1.30.6) -
NGINX HTTP/2 参照 の脆弱性 2 件を読む スライドテーマ: mozumasu/swiss-slidev nginx のソース
(修正前): nginx/nginx release-1.30.6 CVE-2026-123633 の修正: コミット 2df48a501 CVE-2026-123007 の修正: コミット e27f5fa84 reusable の条件を変えたコミット: 76672e650 nginx CHANGES、nginx security advisories、nginx: download Development guide、Beginner’s Guide Core functionality、ngx_http_v2_module 93