Share
Embed
How to Implement Top 10 AWS Security Best Practices (New York Edition)
Presented at the AWS Pop-up Loft in New York on September 24th and 25th, 2015.
John Martinez
September 24, 2015
Transcript
17 slides
-
How to Implement Top 10 AWS Security Best Practices AWS
Pop-up Loft NY John Martinez @ Evident.io 2015-09-24 -
About Me ▪Been doing DevOps and Cloud stuff for ~5
years ▪Helped architect and build Creative Cloud @ Adobe ▪Cut my teeth on “the cloud” at Netflix ▪UNIX and Linux throat beard for >20 years ▪Have been involved in countless security and production incidents, most at 2:00 AM ▪I now talk to people about security for a living 2 -
Tonight’s Agenda ✓AWS Shared Security Responsibility ✓Evident.io’s Top 10 List
in detail ✓Q&A ✓Quick Break ✓Evident.io Demo 4 -
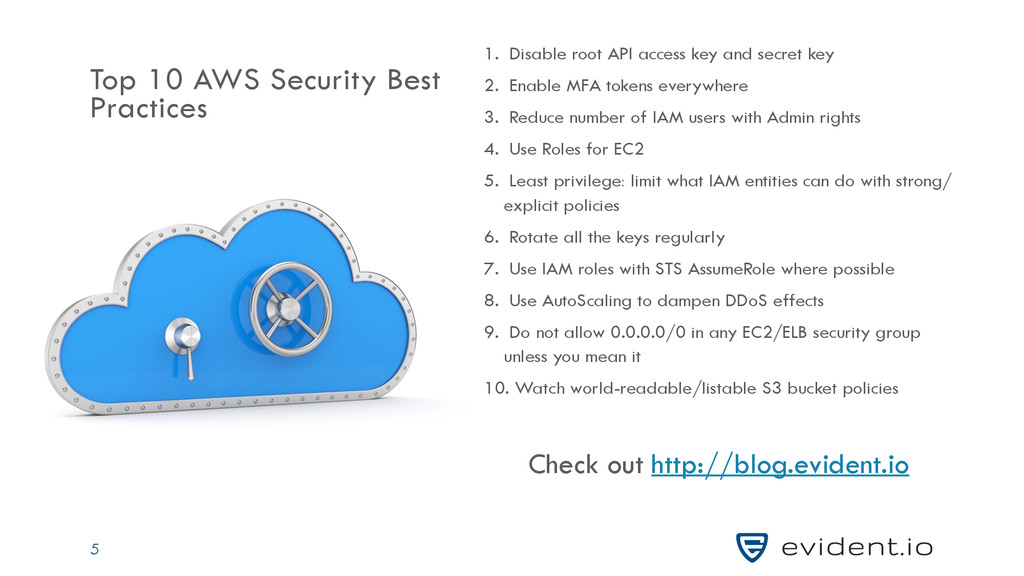
Top 10 AWS Security Best Practices 1. Disable root API
access key and secret key 2. Enable MFA tokens everywhere 3. Reduce number of IAM users with Admin rights 4. Use Roles for EC2 5. Least privilege: limit what IAM entities can do with strong/ explicit policies 6. Rotate all the keys regularly 7. Use IAM roles with STS AssumeRole where possible 8. Use AutoScaling to dampen DDoS effects 9. Do not allow 0.0.0.0/0 in any EC2/ELB security group unless you mean it 10. Watch world-readable/listable S3 bucket policies Check out http://blog.evident.io 5 -
▪“Root” account has no restrictions ▪Create administrative IAM users ▪Use
Roles for EC2 (#4) ▪Make sure billing and contact questions are filled out ▪Bonus: Set up MFA on root and throw away the key! #1 - Disable Root Account API Access Key 6 -
#2 - 1 Enable MFA Tokens Everywhere ▪Provide an additional
factor to the authentication step ▪MFA is assigned to root account and IAM users ▪Can be assigned to roles ▪Physical or virtual ▪Virtual has choices (Google Authenticator, Authy, etc.) 7 -
▪How many people have the keys to your kingdom? ▪Not
just people - apps ▪Review IAM policies on Users, Groups and Roles ▪Remember #1 ▪Consider Identity Federation #3 - Reduce Number of IAM users with Admin 8 -
▪Do your EC2 instances need to contact other AWS Services?
▪AWS SDKs and aws-cli support EC2 Roles ▪Reduced attack surface area ▪Secure DevOps on EC2 ▪Create an EC2 specific role ▪Assign a specific policy to that role ▪Launch an EC2 instance with that role ▪Easy to test with aws-cli on EC2 #4 - Use Roles for EC2 9 -
▪Programs should operate using the least amount of privilege to
get the job done ▪IAM can get very granular ▪Works in tandem with #4 on EC2 ▪Should be applied to all automated workflows, too ▪Very specific IAM policies - only allow what you mean ▪IAM managed policies make this easier ▪Use the IAM policy generator and policy simulator to help #5 - Least Privilege 10 -
▪Compromised access keys are very annoying and can cost your
business dearly ▪IAM users should have keys rotated every 90 days minimum ▪Mostly useful for when Roles for EC2 won’t work in automated workflows Sample process: ▪Track age of Access Keys ▪Create new key ▪Supply key to automation process ▪Test ▪Deactivate old key #6 - Rotate all the Keys Regularly 11 -
▪Similar to EC2 Roles ▪Can be used in place of
privileged IAM user Access Keys ▪Temporary credentials ▪Allows for 3rd parties such as Evident.io to access your AWS accounts more securely ▪Extended version of AssumeRole allows for Identity Federation #7 - Use IAM Roles with STS AssumeRole 12 -
▪AutoScaling allows you to increase number of EC2 instances automatically
▪More instances means site stays up ▪Small price to pay for site reliability ▪You may need a temporary increase in EC2 limits ▪You may need to temporarily increase desired number of instances in ASG ▪Work with AWS, they may be able to help you on the network edge #8 - Use AutoScaling to Dampen DDoS 13 -
▪Unless you really mean it ▪Like leaving the door wide
open ▪EC2 IP address range is a favorite for scanners ▪Monitor Security Groups regularly (HINT: Evident.io can help) ▪Affects not just EC2 instances, but: ▪ELBs ▪RDS Database Servers ▪ElastiCache Clusters ▪EMR Nodes ▪and others… #9 - Do not allow ALL in Security Groups 14 -
▪Open S3 buckets a favorite for trolling for API Access
Keys ▪Check your Bucket ACLs regularly ▪Watch for all grantees, including AuthenticatedUsers ▪Check your Bucket Policies regularly #10 - Watch Readable and Listable S3 Buckets 15 -
[email protected] • [email protected] • @johnmartinez • LinkedIn 17 Thank You
AWS Pop-up Loft SF!