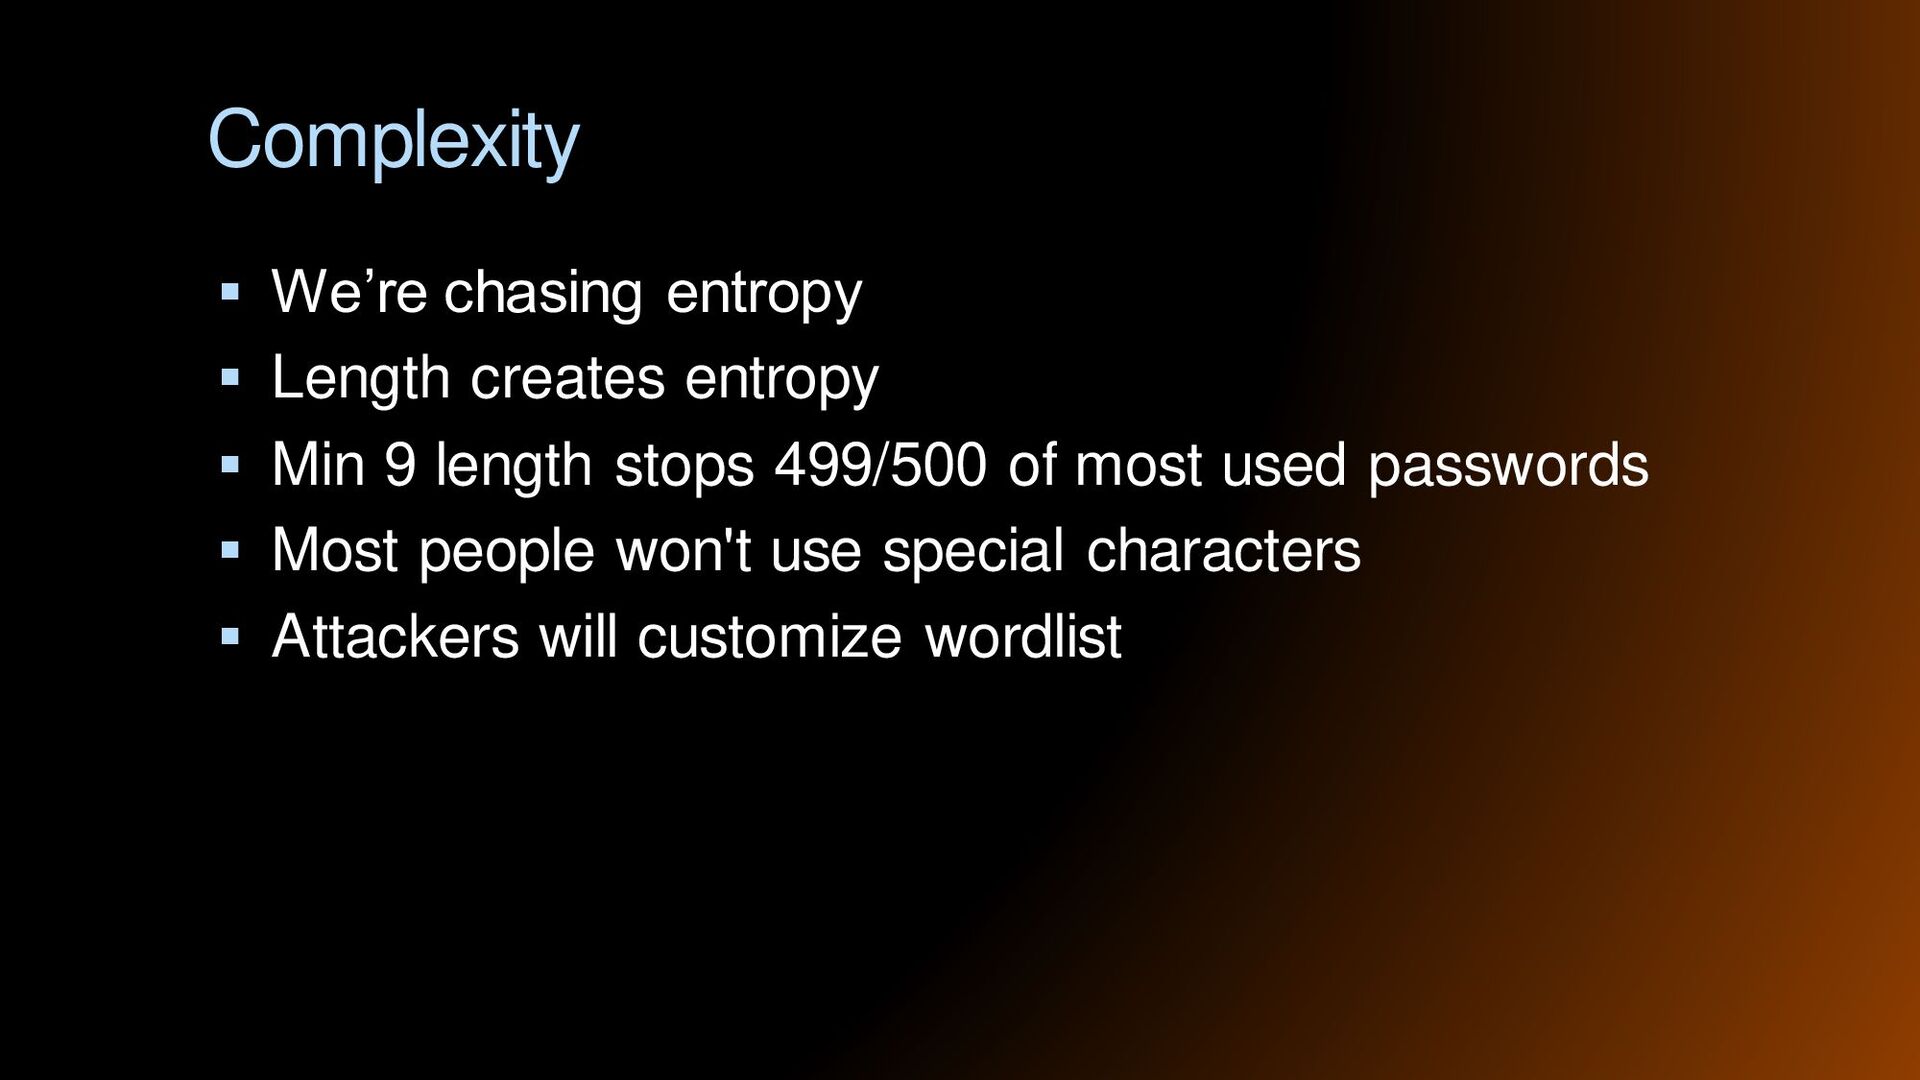
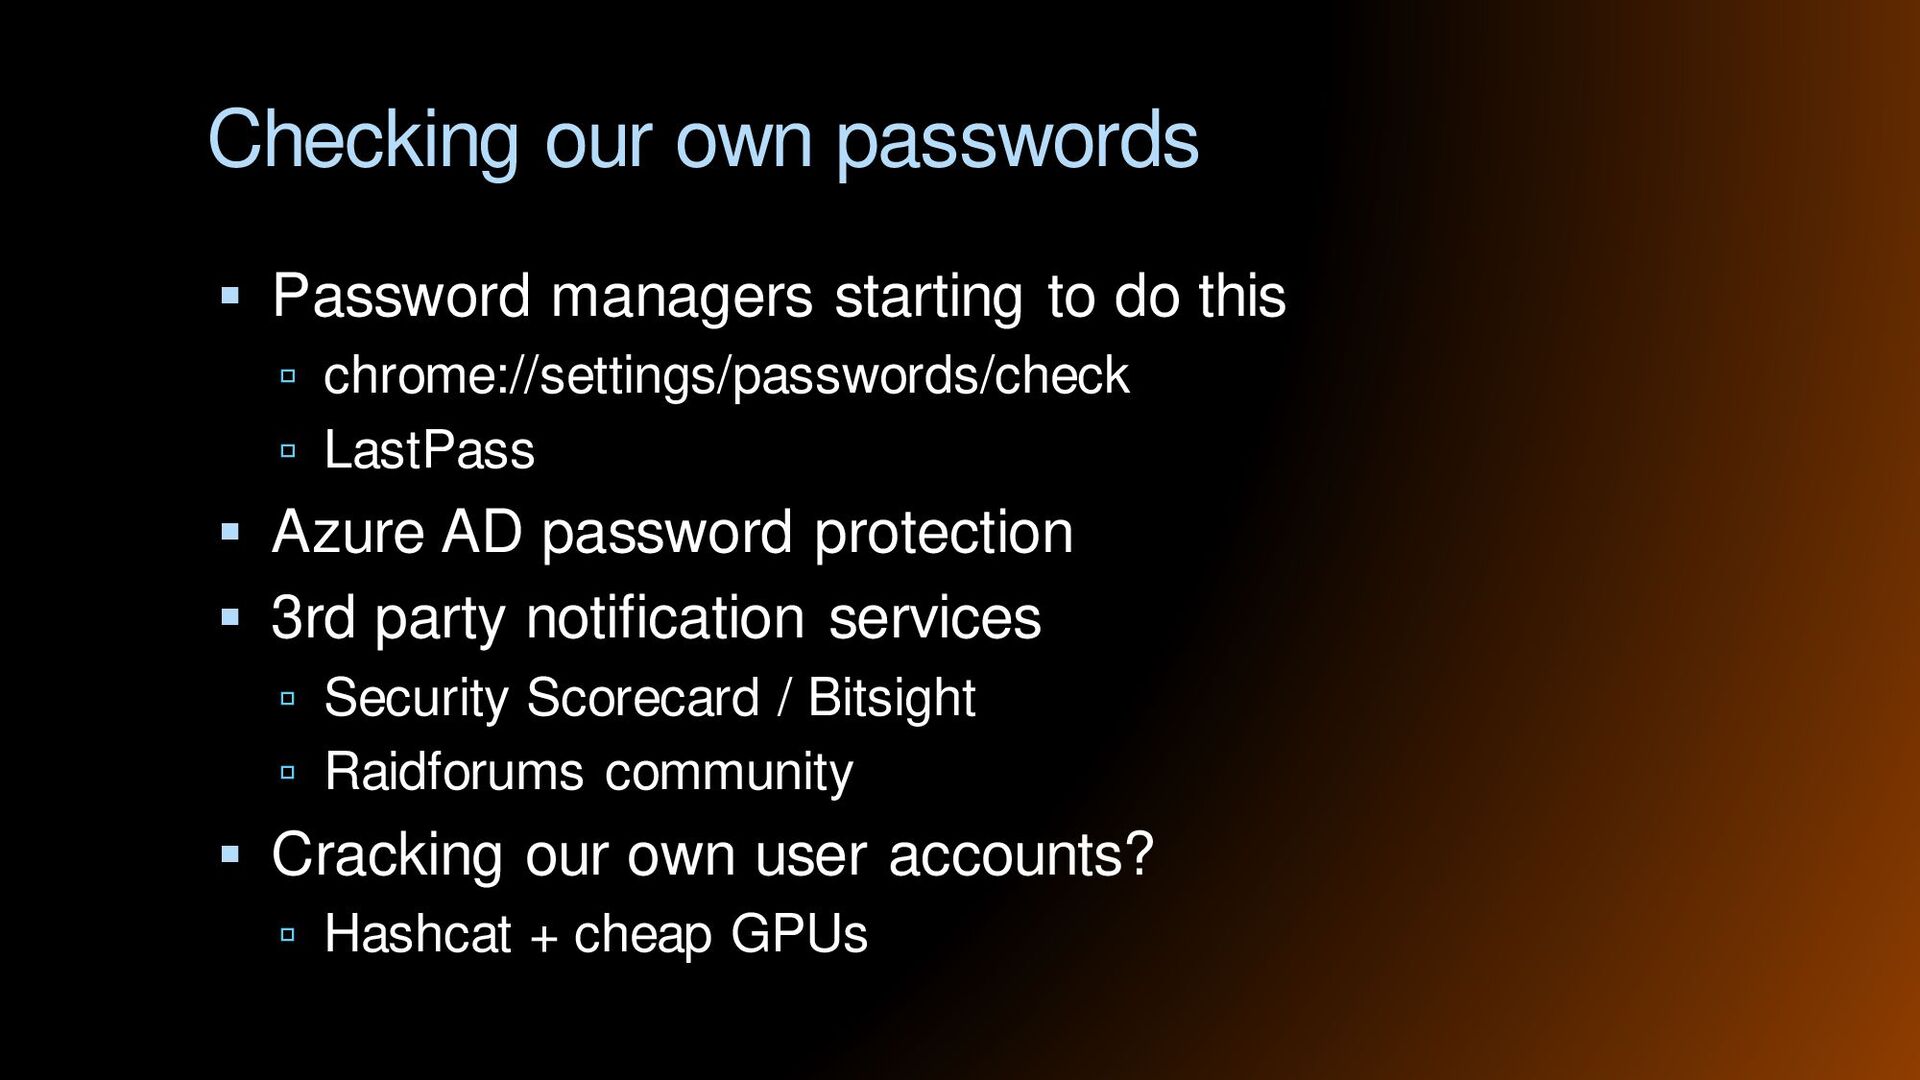
you take away only one thing, take this ▪ Happens even within infosec community ▪ https://haveibeenpwned.com/ ▪ Unique passwords per site ▪ Same local admin account firm wide
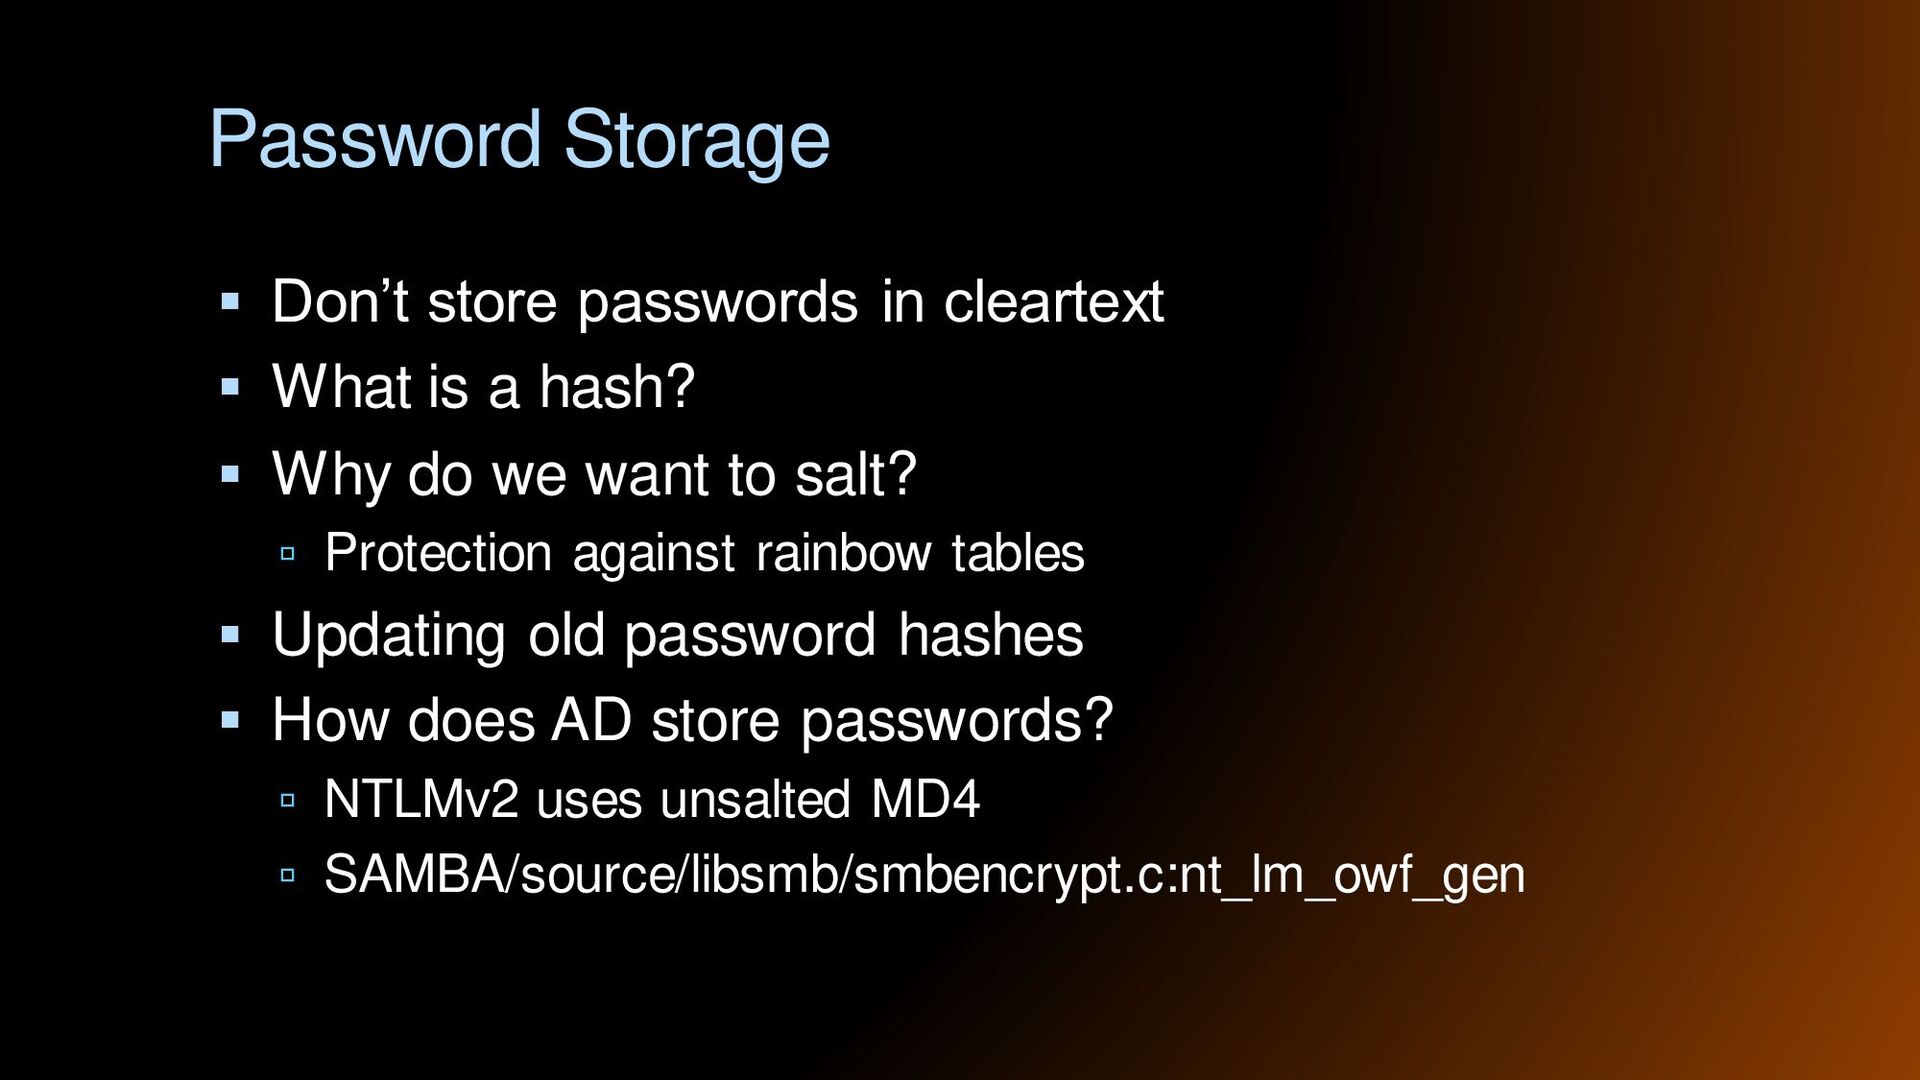
is a hash? ▪ Why do we want to salt? Protection against rainbow tables ▪ Updating old password hashes ▪ How does AD store passwords? NTLMv2 uses unsalted MD4 SAMBA/source/libsmb/smbencrypt.c:nt_lm_owf_gen
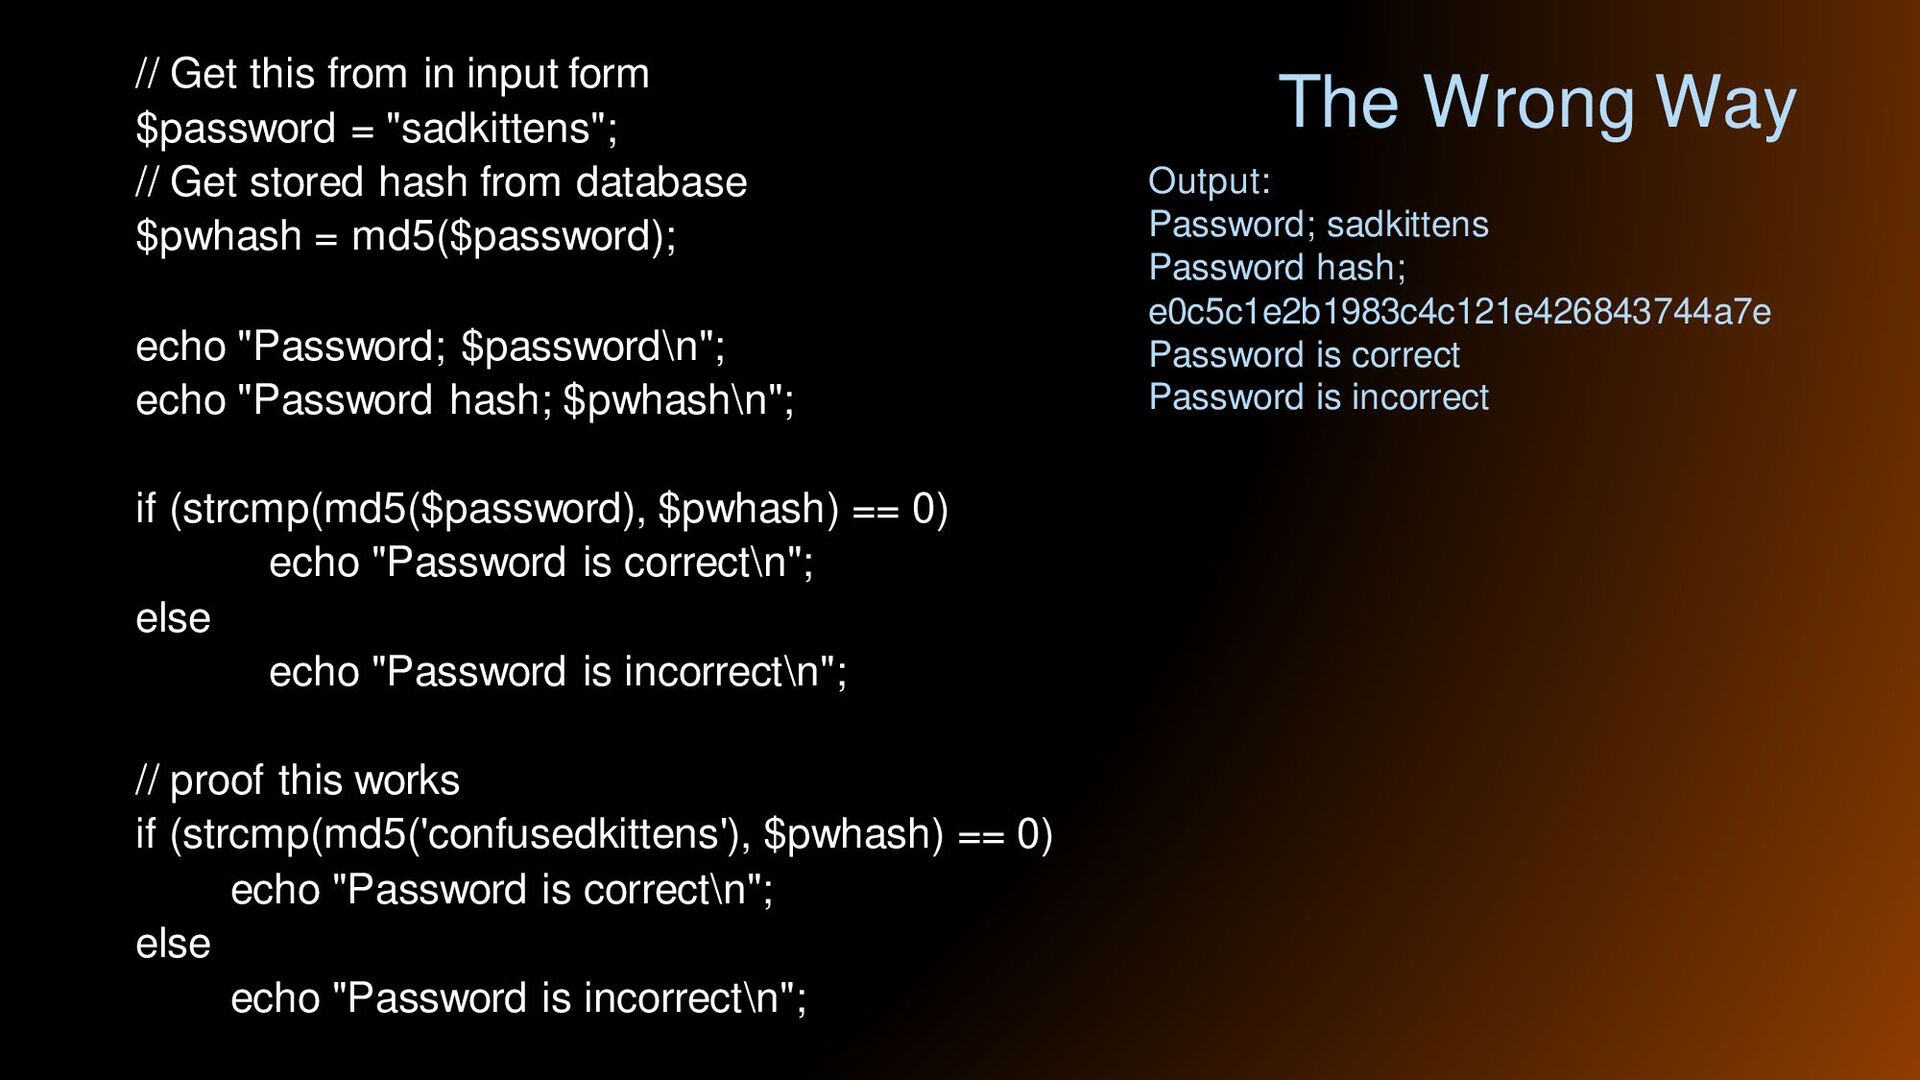
// Get stored hash from database $pwhash = md5($password); echo "Password; $password\n"; echo "Password hash; $pwhash\n"; if (strcmp(md5($password), $pwhash) == 0) echo "Password is correct\n"; else echo "Password is incorrect\n"; // proof this works if (strcmp(md5('confusedkittens'), $pwhash) == 0) echo "Password is correct\n"; else echo "Password is incorrect\n"; Output: Password; sadkittens Password hash; e0c5c1e2b1983c4c121e426843744a7e Password is correct Password is incorrect The Wrong Way
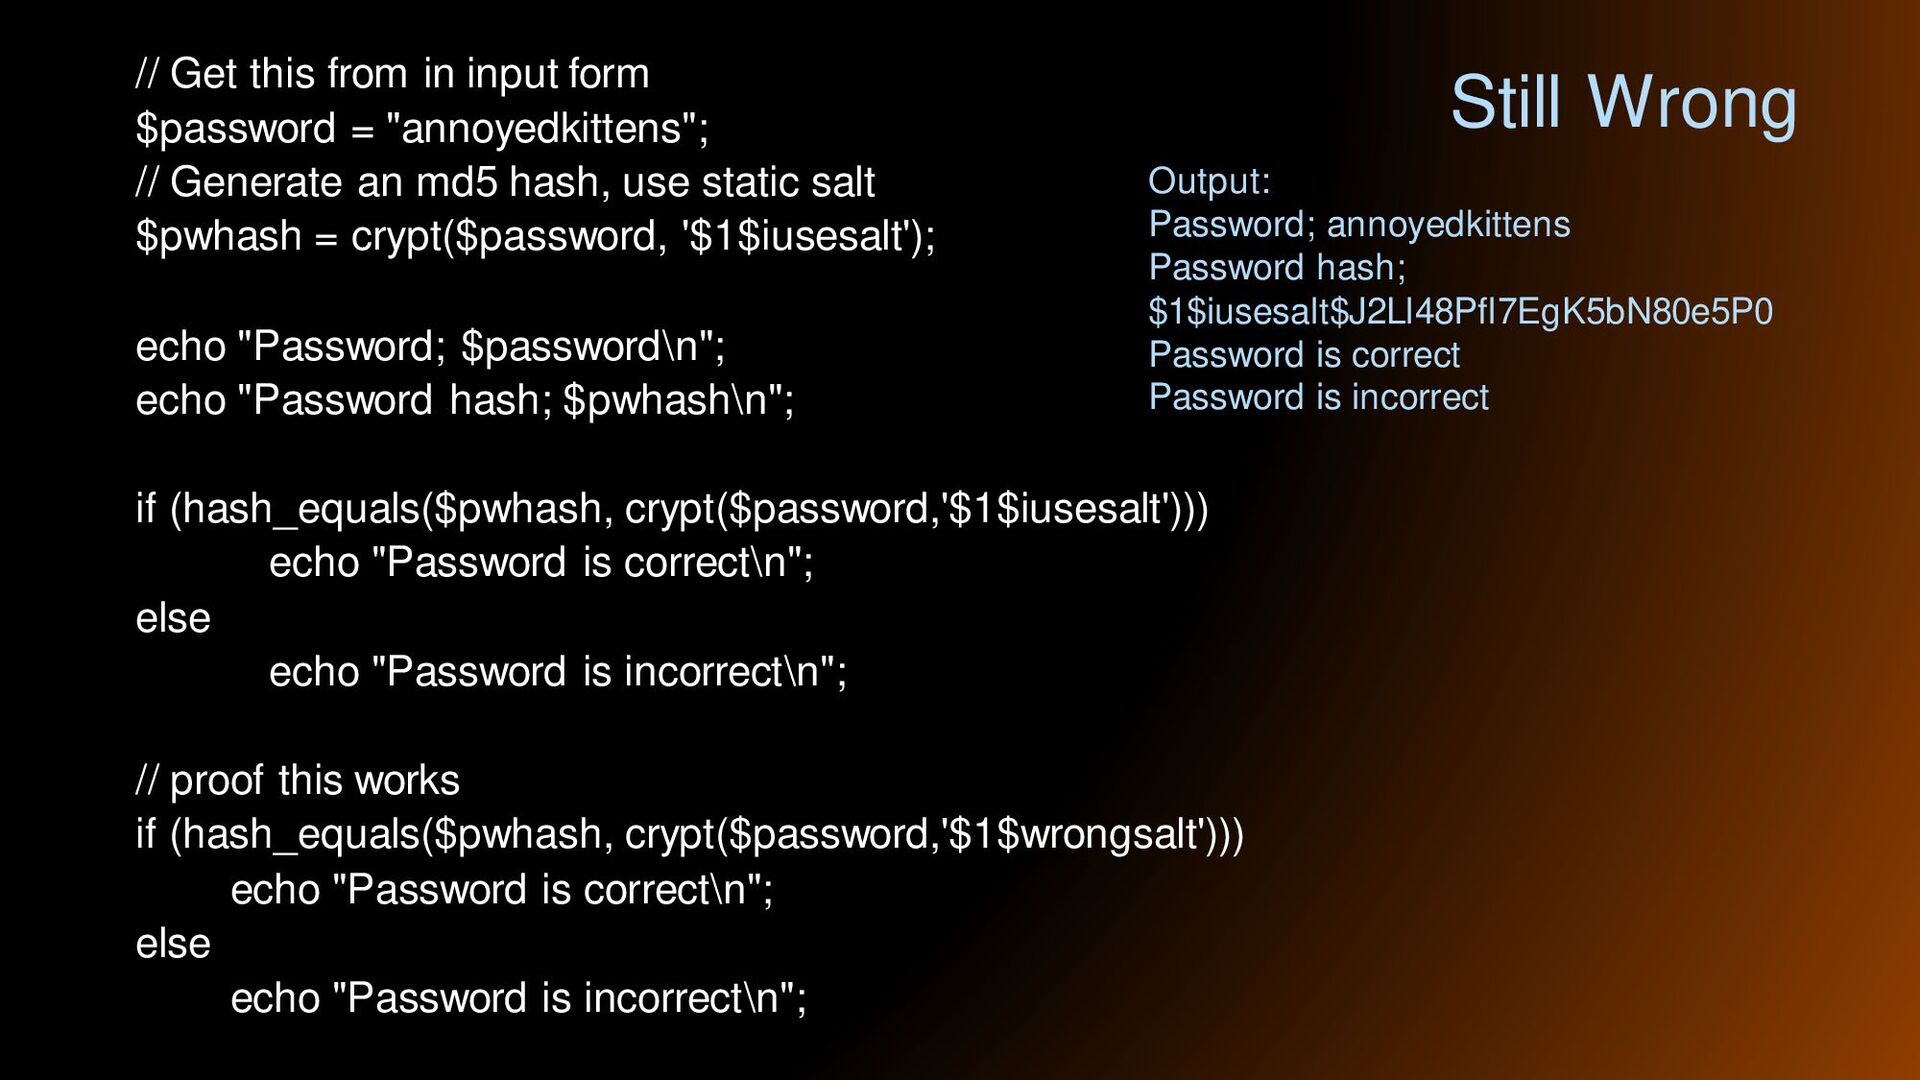
// Generate an md5 hash, use static salt $pwhash = crypt($password, '$1$iusesalt'); echo "Password; $password\n"; echo "Password hash; $pwhash\n"; if (hash_equals($pwhash, crypt($password,'$1$iusesalt'))) echo "Password is correct\n"; else echo "Password is incorrect\n"; // proof this works if (hash_equals($pwhash, crypt($password,'$1$wrongsalt'))) echo "Password is correct\n"; else echo "Password is incorrect\n"; Output: Password; annoyedkittens Password hash; $1$iusesalt$J2Ll48Pfl7EgK5bN80e5P0 Password is correct Password is incorrect Still Wrong
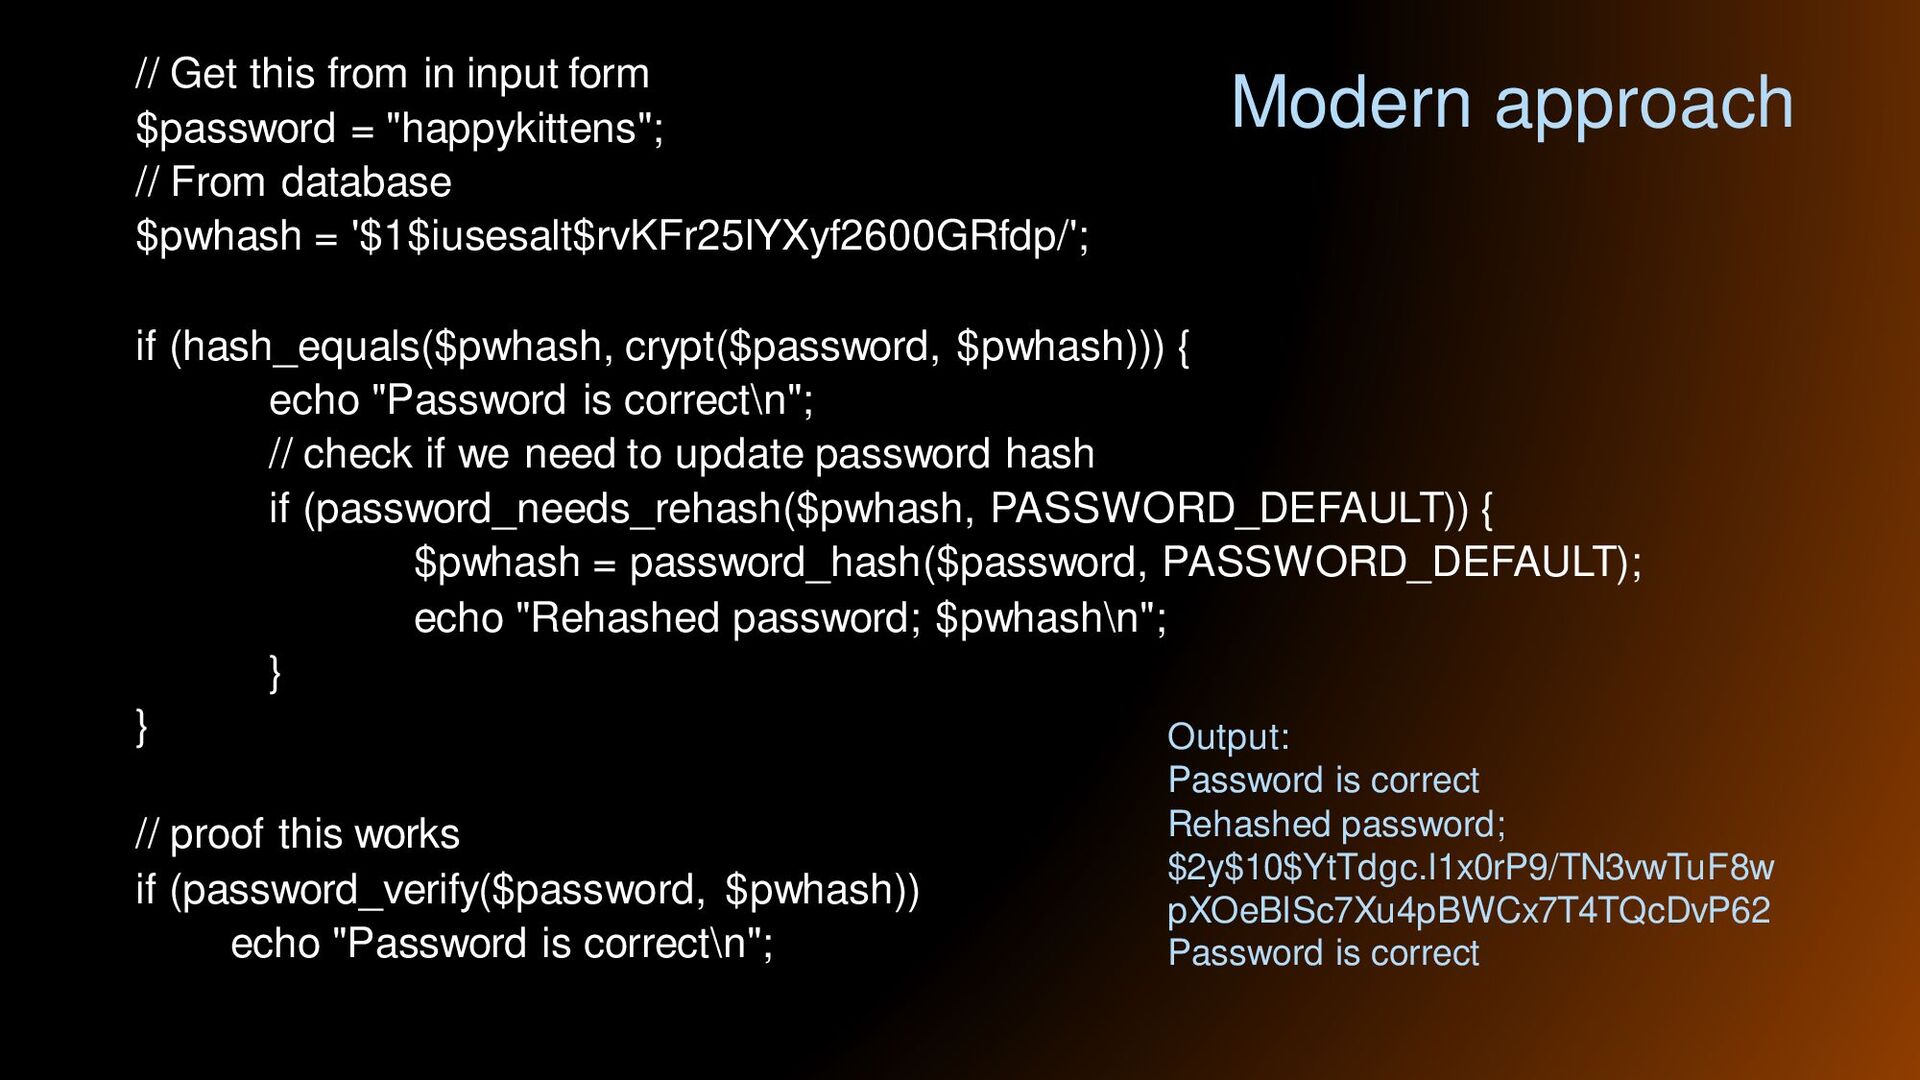
// From database $pwhash = '$1$iusesalt$rvKFr25lYXyf2600GRfdp/'; if (hash_equals($pwhash, crypt($password, $pwhash))) { echo "Password is correct\n"; // check if we need to update password hash if (password_needs_rehash($pwhash, PASSWORD_DEFAULT)) { $pwhash = password_hash($password, PASSWORD_DEFAULT); echo "Rehashed password; $pwhash\n"; } } // proof this works if (password_verify($password, $pwhash)) echo "Password is correct\n"; Output: Password is correct Rehashed password; $2y$10$YtTdgc.l1x0rP9/TN3vwTuF8w pXOeBlSc7Xu4pBWCx7T4TQcDvP62 Password is correct Modern approach
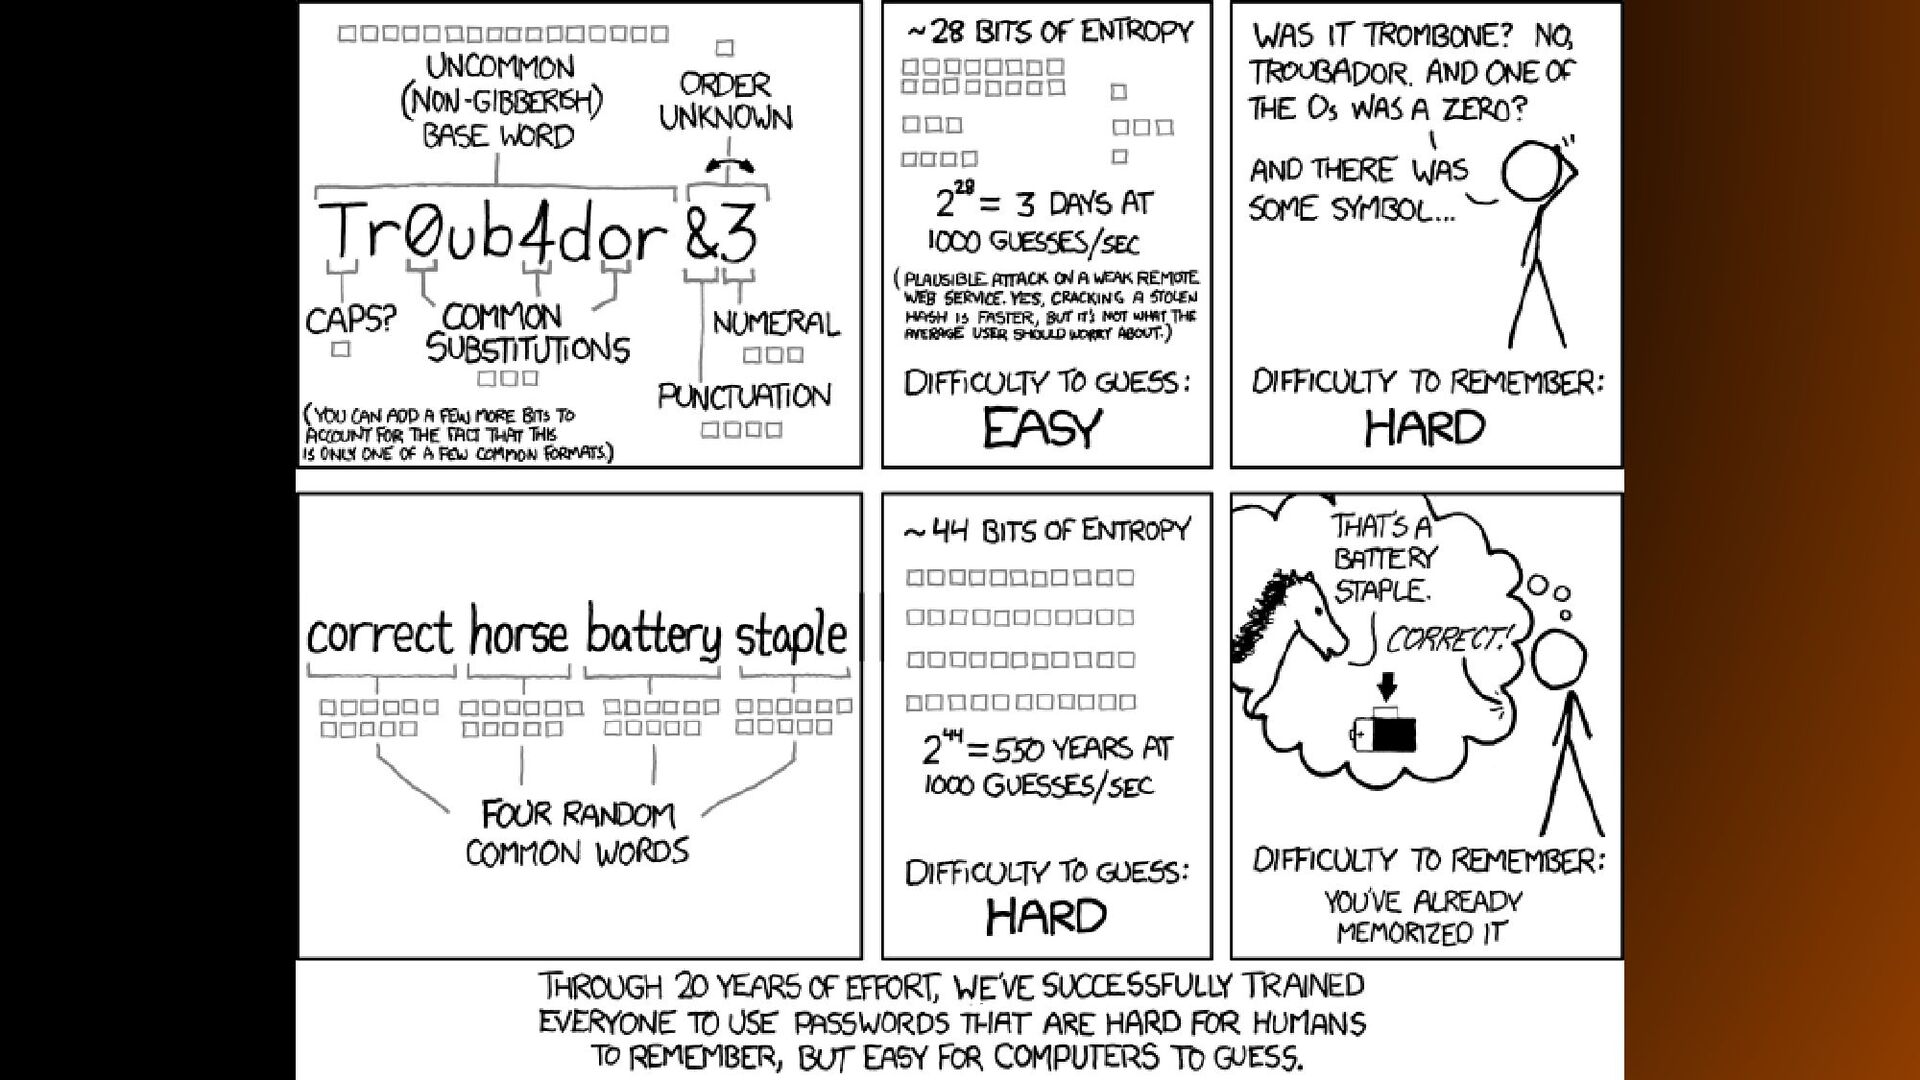
secure == can't remember New password + can remember == not secure ▪ Can we just give up on passwords? Biometrics not suitable Push notifications Apple Facebook Microsoft Office365


 jsavoie
 raeminkang
 akihisaikeda
 umigishiaoi
 dalinaum
 t0yohei
 quramy
 richargh
 rshindo
 sodainc
 kamina_zzz
 seyfoyun
 3saito
 jct
 bryan
 ks91
 addyosmani
 jdejongh
 marcelosomers
 tammyeverts
 konakalab
 erikaheidi
 portentint
 smashingmag