Upgrade to Pro — share decks privately, control downloads, hide ads and more …

Encrypting the Cloud

Sponsored · Ship Features Fearlessly Turn features on and off without deploys. Used by thousands of Ruby developers. →

Encrypting the Cloud

Encryption in the Cloud. How do we protect our data, at rest, and even from the cloud provider itself?

Julien Savoie

June 24, 2015

Transcript

8 slides
  1. Encrypting the Cloud • We're going to be talking about

    storage • Assuming you're already doing transport
  2. Why encrypt? • Loss of physical control • Insider attack

    vector • Cloud provider breach • State actors / Lawyer attacks
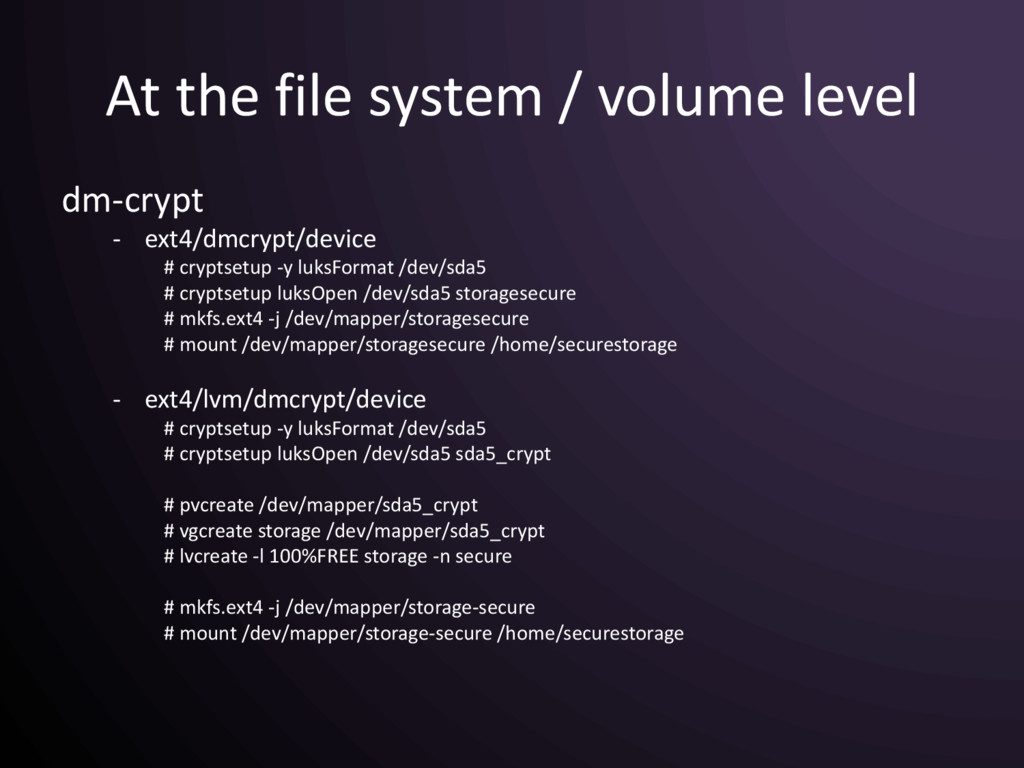
  3. At the file system / volume level dm-crypt - ext4/dmcrypt/device

    # cryptsetup -y luksFormat /dev/sda5 # cryptsetup luksOpen /dev/sda5 storagesecure # mkfs.ext4 -j /dev/mapper/storagesecure # mount /dev/mapper/storagesecure /home/securestorage - ext4/lvm/dmcrypt/device # cryptsetup -y luksFormat /dev/sda5 # cryptsetup luksOpen /dev/sda5 sda5_crypt # pvcreate /dev/mapper/sda5_crypt # vgcreate storage /dev/mapper/sda5_crypt # lvcreate -l 100%FREE storage -n secure # mkfs.ext4 -j /dev/mapper/storage-secure # mount /dev/mapper/storage-secure /home/securestorage
  4. Some problems with this • Dealing with reboots – We

    can't store passphrase on server – Remote intervention (automated or manually) • Recovering the key – If we can snapshot memory, we can scrap for key'ing data • Research on the specifics is public • Look for crypt_config struct in memory dump
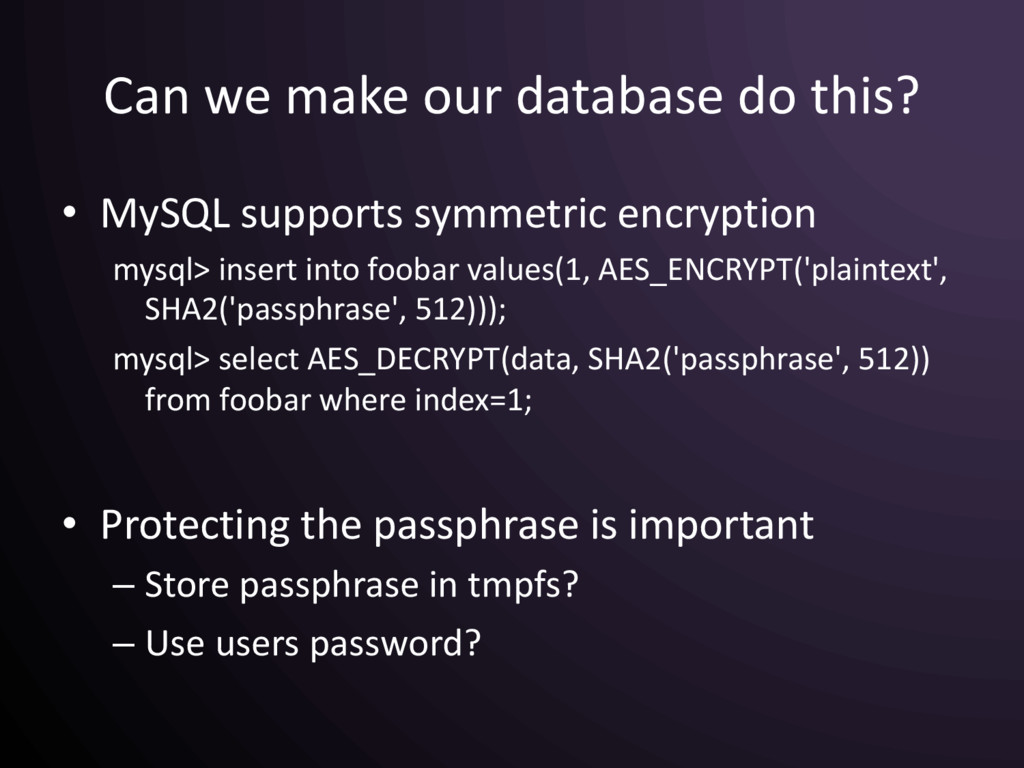
  5. Can we make our database do this? • MySQL supports

    symmetric encryption mysql> insert into foobar values(1, AES_ENCRYPT('plaintext', SHA2('passphrase', 512))); mysql> select AES_DECRYPT(data, SHA2('passphrase', 512)) from foobar where index=1; • Protecting the passphrase is important – Store passphrase in tmpfs? – Use users password?
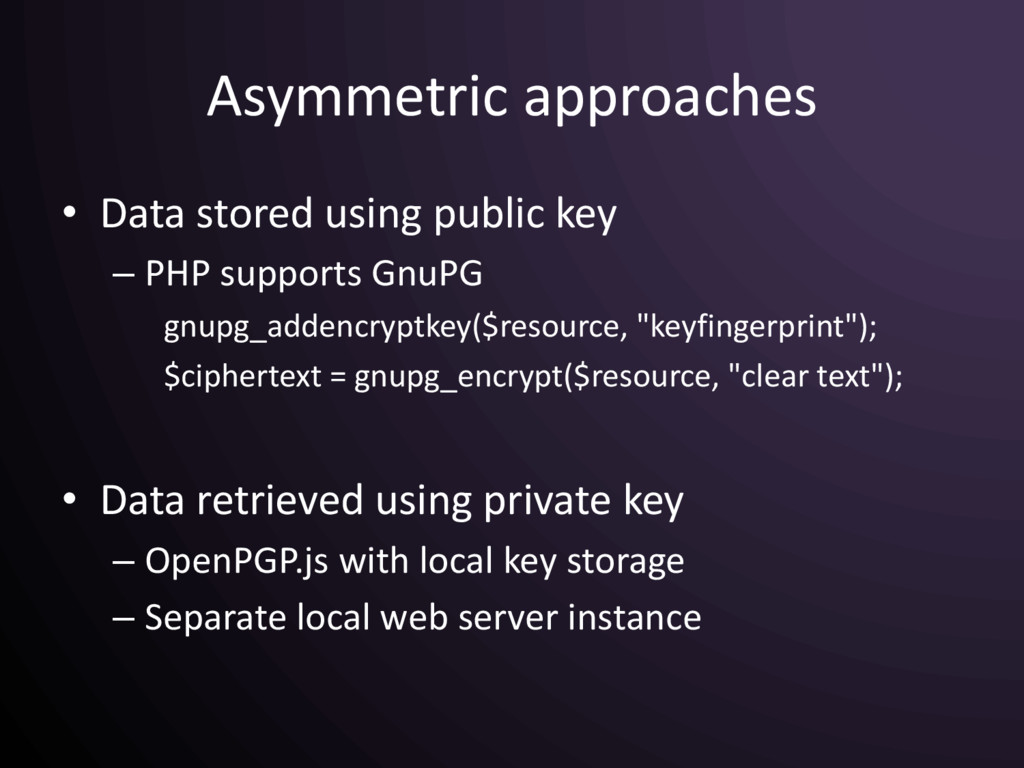
  6. Asymmetric approaches • Data stored using public key – PHP

    supports GnuPG gnupg_addencryptkey($resource, "keyfingerprint"); $ciphertext = gnupg_encrypt($resource, "clear text"); • Data retrieved using private key – OpenPGP.js with local key storage – Separate local web server instance
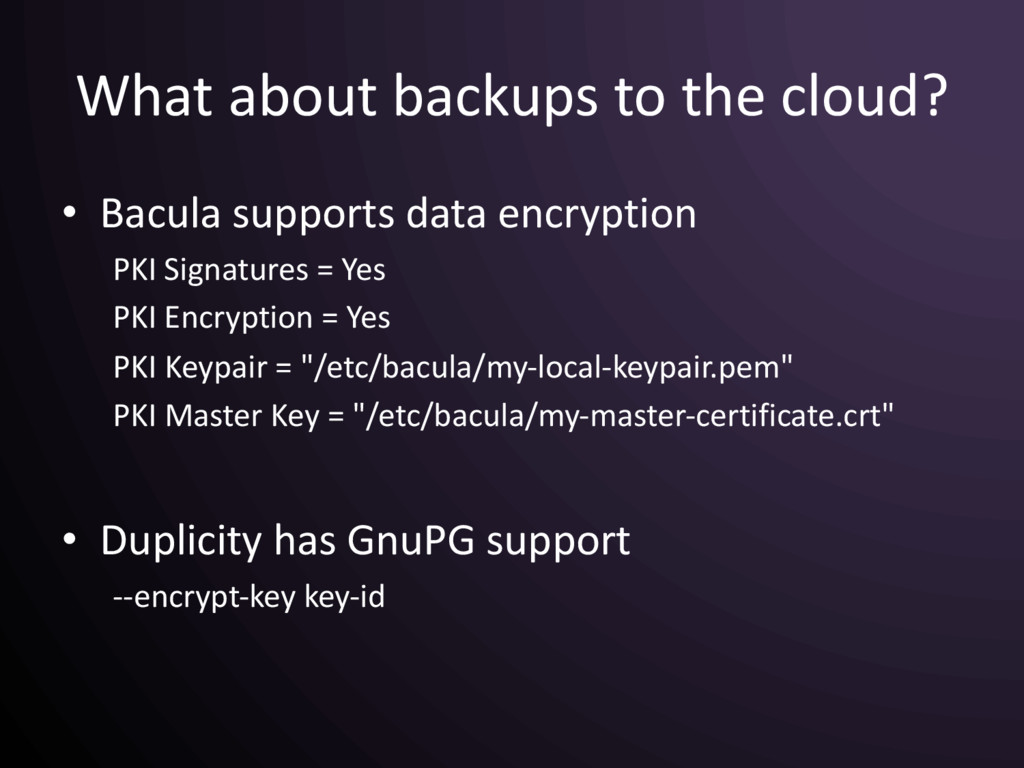
  7. What about backups to the cloud? • Bacula supports data

    encryption PKI Signatures = Yes PKI Encryption = Yes PKI Keypair = "/etc/bacula/my-local-keypair.pem" PKI Master Key = "/etc/bacula/my-master-certificate.crt" • Duplicity has GnuPG support --encrypt-key key-id
  8. We need to think about this issue more. Not enough

    discussion on this. • Follow me @jzsavoie • XMPP [email protected] • Questions, Angry Rants?

More Decks by Julien Savoie

Other Decks in Technology