Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
戳戳防毒死穴 (Kill AV in X64)
Search
kenny
December 27, 2013
Technology
320
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
戳戳防毒死穴 (Kill AV in X64)
Hack In Taiwan(HIT) 2013
[email protected]
kenny
December 27, 2013
Other Decks in Technology
See All in Technology
脆弱性診断って、何をしているの? 〜弱点を見つけて、会社の改善につなげるまで〜
keeg
0
930
AIがコードを書く時代に、エンジニアは何で自分の価値を証明するのか / In an era where AI writes code how do engineers prove their value
carta_engineering
3
1.1k
How to Design Configuration for Rails Applications
willnet
1
830
PHPカンファレンス関西の招待状 / Invitation to PHP Conference Kansai
ykanoh
0
200
『SAR衛星データ解析入門』の ご紹介とその応用
syuchimu
0
120
事業成長とデータ活用を止めないためのマネジメントへ挑戦
hiracky16
0
400
Optunaの最新リリースv5.0について
pfn
PRO
0
120
DevelopersIO 2026 知識の地図を描く ─ オントロジーとは何か?
ishikawa_satoru
1
1.7k
V8のArray.prototype.flatを最大約20倍速くするまでと、巨大OSSへの大規模コミットの道のり
riyaamemiya
0
300
オントロジーって 結局なにもの? AI エージェントに「意味」を渡す知識設計の話
greenmidori
0
230
初海外で注意すべきこと12選!!!安全快適なre:invent生活にするために
yuuuuuuu168
1
180
触りたくないデータに、どう触るか AI時代のRBACアクセスガバナンス
ivry_presentationmaterials
0
270
Featured
See All Featured
Exploring anti-patterns in Rails
aemeredith
4
540
Digital Ethics as a Driver of Design Innovation
axbom
PRO
1
460
Fireside Chat
paigeccino
43
4.1k
The Director’s Chair: Orchestrating AI for Truly Effective Learning
tmiket
1
330
Navigating Weather and Climate Data
rabernat
0
560
Navigating Algorithm Shifts & AI Overviews - #SMXNext
aleyda
1
1.7k
Large-scale JavaScript Application Architecture
addyosmani
516
110k
Designing Dashboards & Data Visualisations in Web Apps
destraynor
232
55k
Google's AI Overviews - The New Search
badams
0
1.6k
Improving Core Web Vitals using Speculation Rules API
sergeychernyshev
21
1.7k
XXLCSS - How to scale CSS and keep your sanity
sugarenia
250
1.3M
Heart Work Chapter 1 - Part 1
lfama
PRO
10
37k
Transcript
[email protected]
戳戳防毒死穴 (Kill AV in X64)
About Me 現任研究生 網駭科技 – R & D Chroot Security
Group
What’s AV?
What’s AV?
None
None
雖然她們 伴隨著 青春歲月
深埋你我 的 D:\
But~
今天主角是…….
None
None
None
主題 , 你懂得:D
Anti AntiVirus(躲避防毒)
與防毒軟體 來一次親密的 衝擊
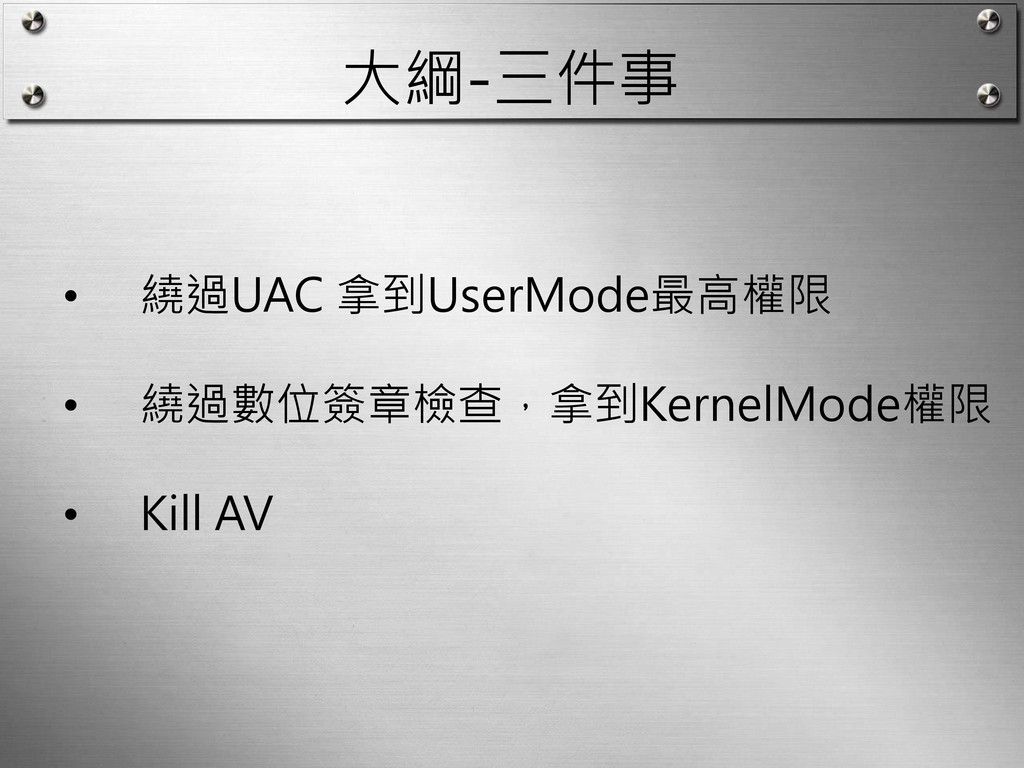
大綱-三件事 • 繞過UAC 拿到UserMode最高權限 • 繞過數位簽章檢查,拿到KernelMode權限 • Kill AV
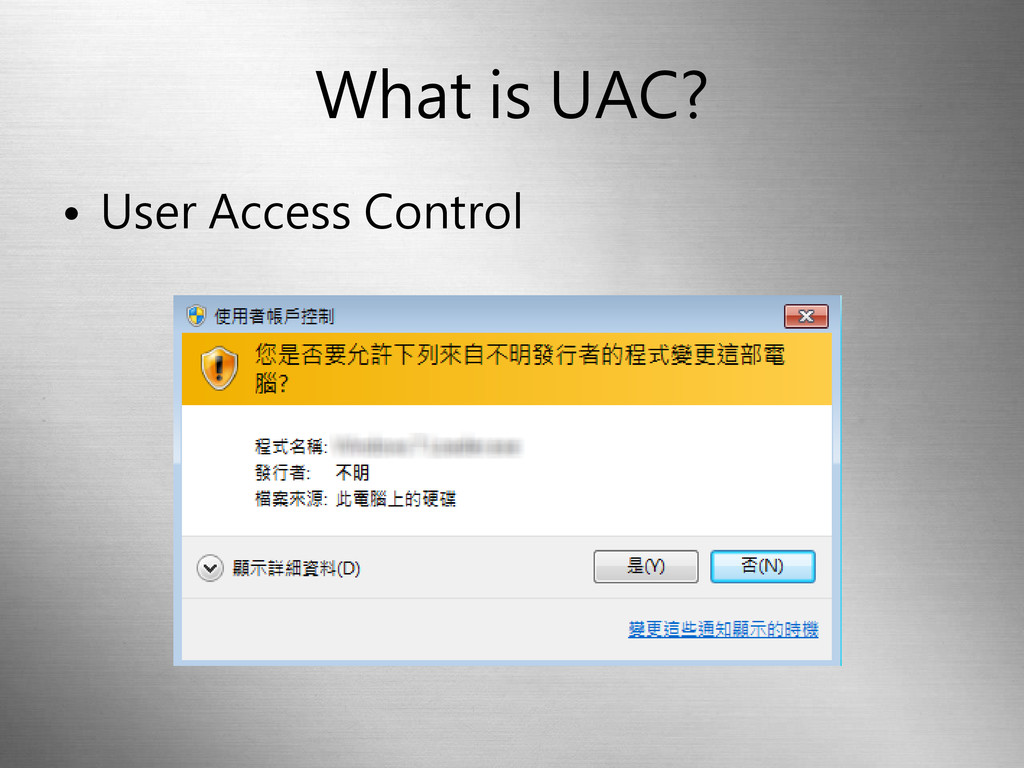
What is UAC? • User Access Control
第一件事
UAC Bypass
5th February 2009 Reference http://www.pretentiousname.com/misc/win7_uac_whitelist2.html
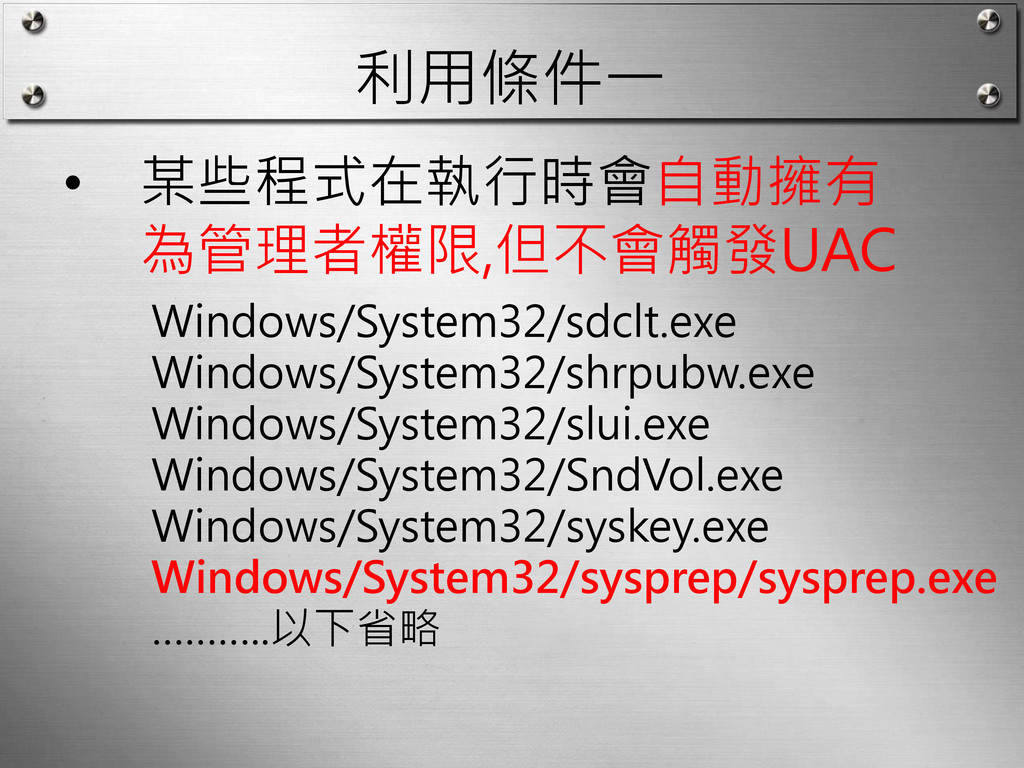
利用條件一 • 某些程式在執行時會自動擁有 為管理者權限,但不會觸發UAC Windows/System32/sdclt.exe Windows/System32/shrpubw.exe Windows/System32/slui.exe Windows/System32/SndVol.exe Windows/System32/syskey.exe Windows/System32/sysprep/sysprep.exe
………..以下省略
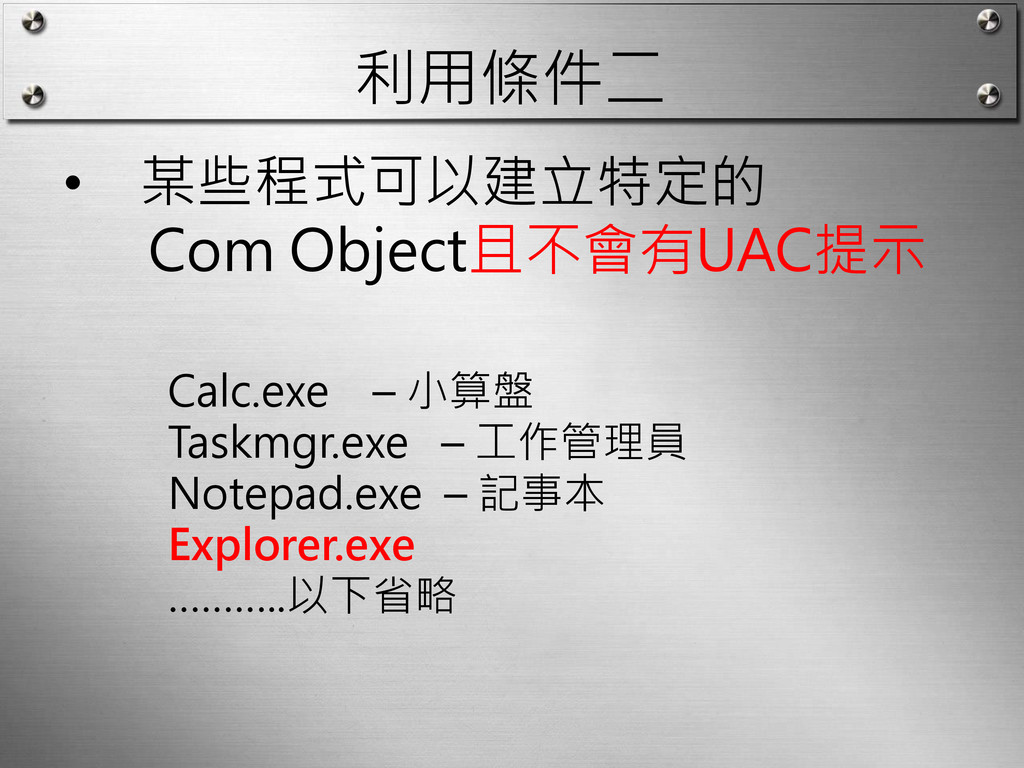
利用條件二 • 某些程式可以建立特定的 Com Object且不會有UAC提示 Calc.exe – 小算盤 Taskmgr.exe –
工作管理員 Notepad.exe – 記事本 Explorer.exe ………..以下省略
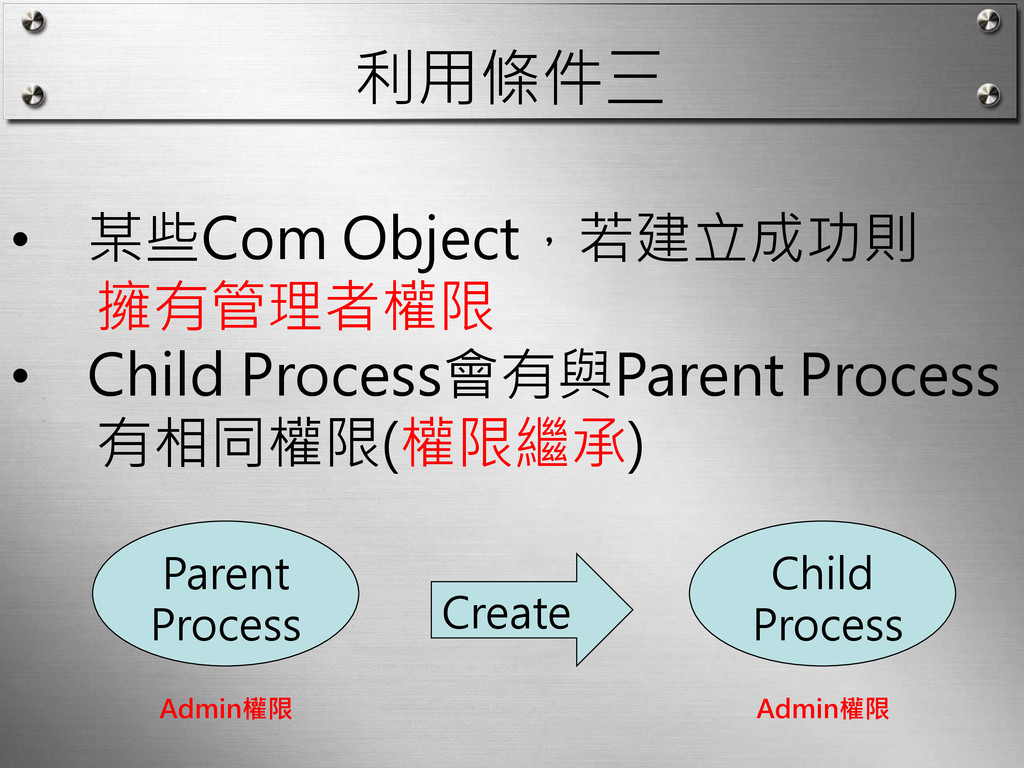
利用條件三 • 某些Com Object,若建立成功則 擁有管理者權限 • Child Process會有與Parent Process 有相同權限(權限繼承)
Parent Process Admin權限 Create Child Process Admin權限
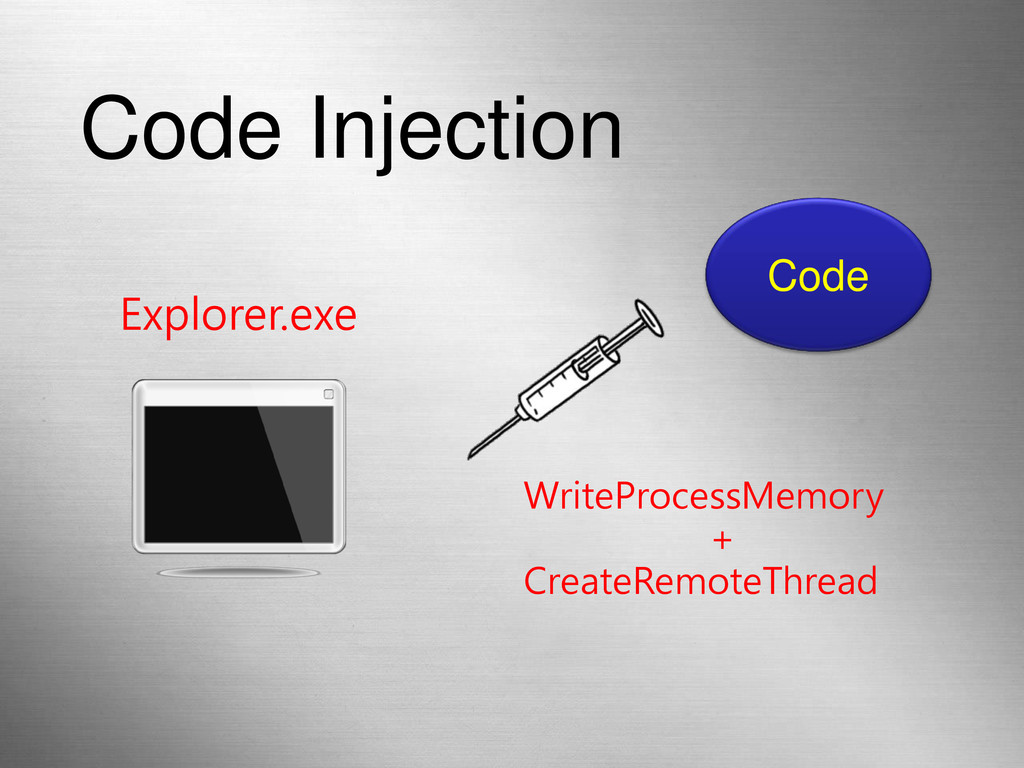
Code Injection Code WriteProcessMemory + CreateRemoteThread Explorer.exe
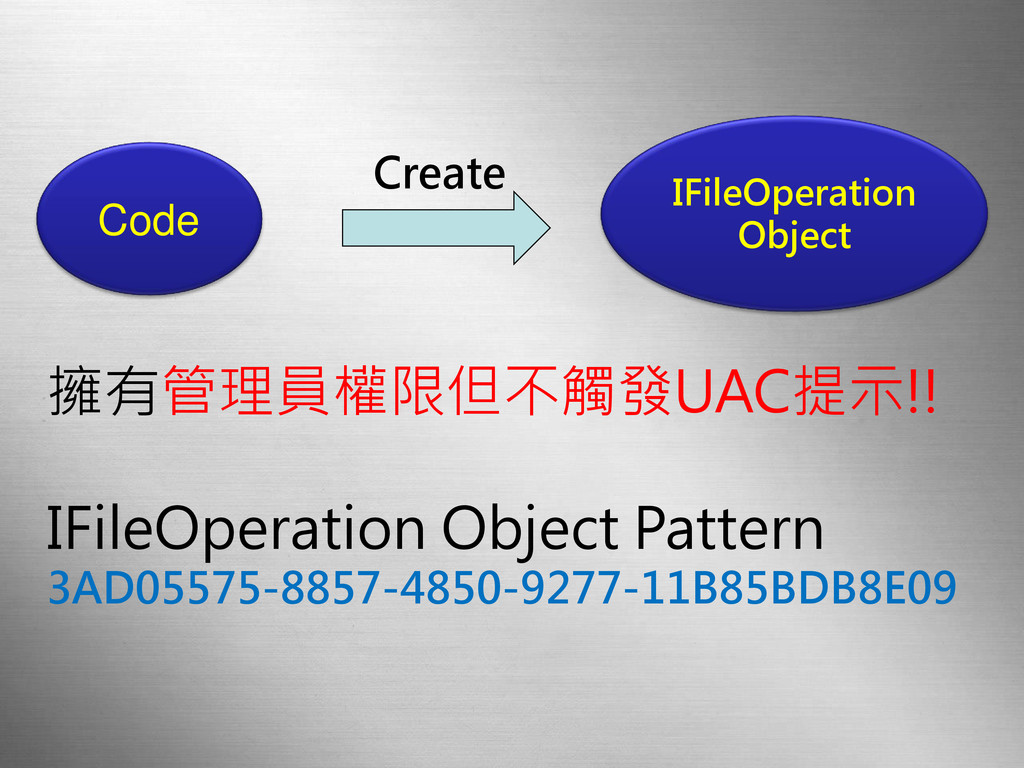
擁有管理員權限但不觸發UAC提示!! IFileOperation Object Pattern 3AD05575-8857-4850-9277-11B85BDB8E09 Code IFileOperation Object Create
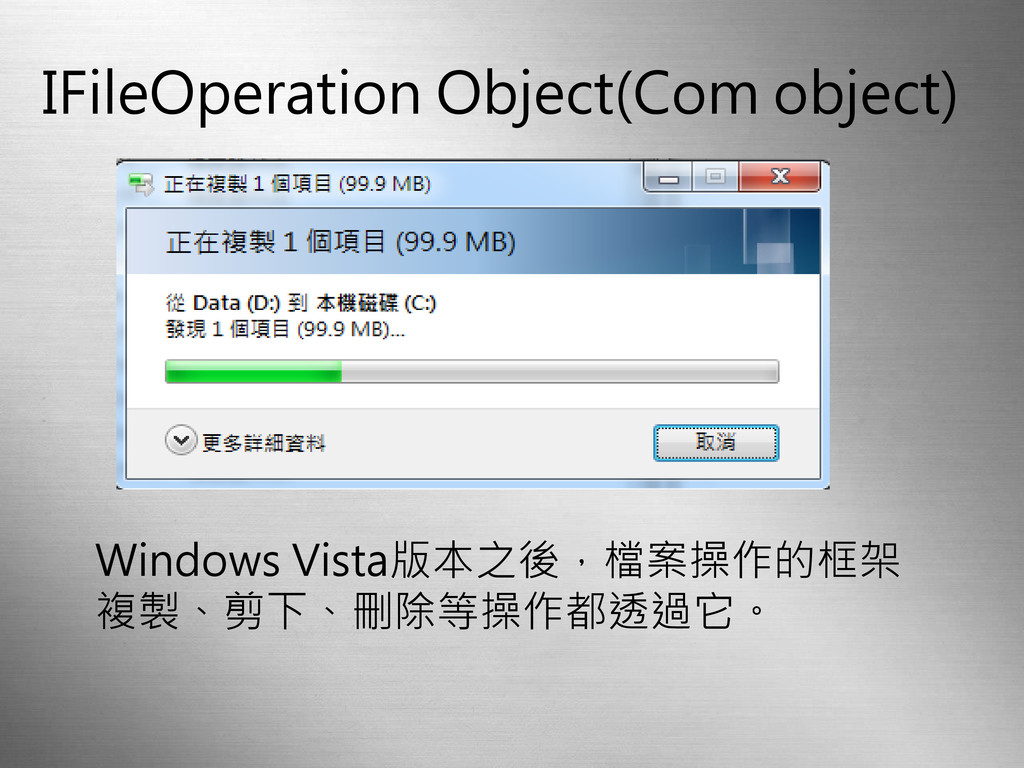
IFileOperation Object(Com object) Windows Vista版本之後,檔案操作的框架 複製、剪下、刪除等操作都透過它。
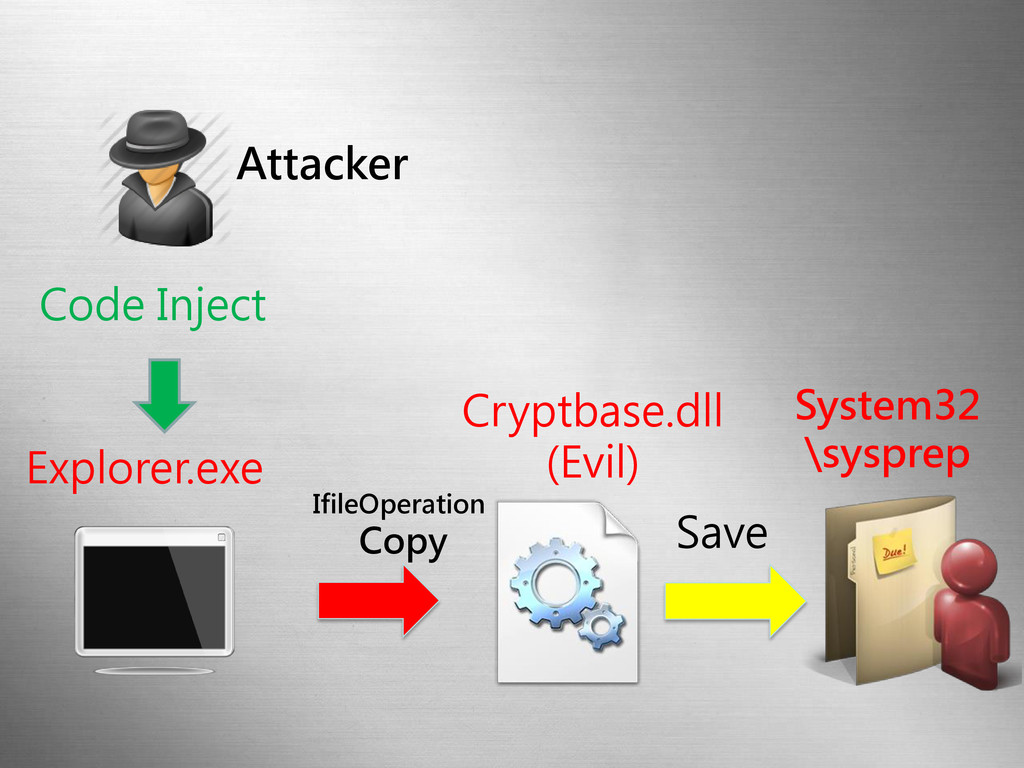
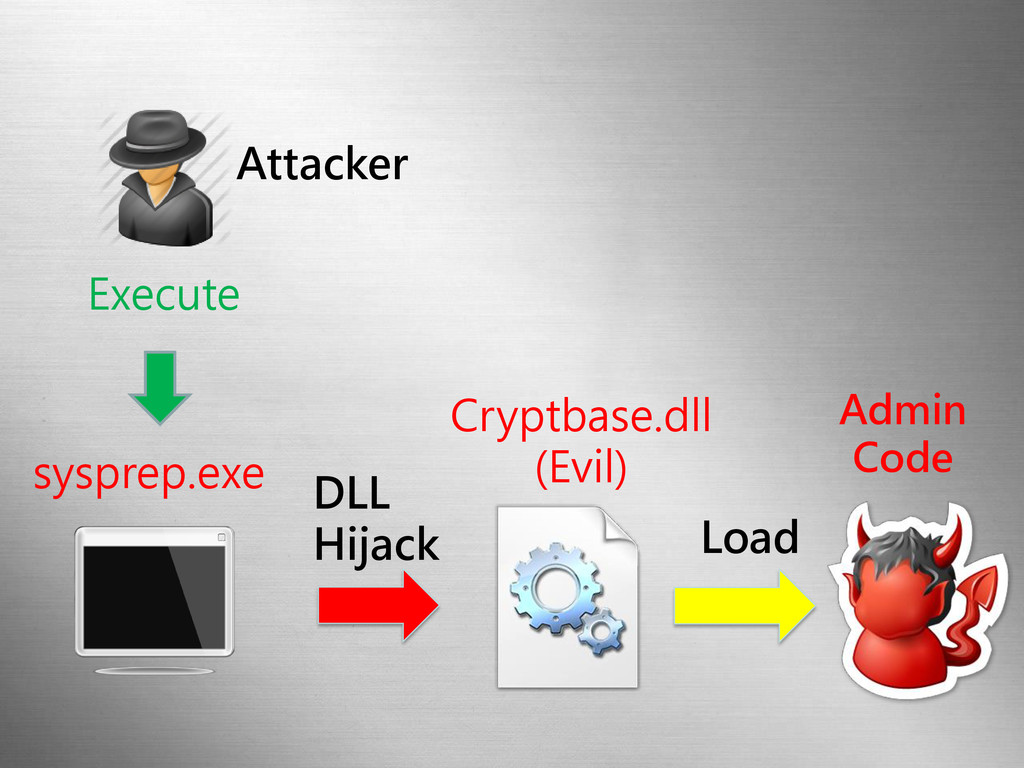
IfileOperation Copy Cryptbase.dll (Evil) Save System32 \sysprep Explorer.exe Code Inject
Attacker
Execute DLL Hijack Cryptbase.dll (Evil) Load Admin Code sysprep.exe Attacker
None
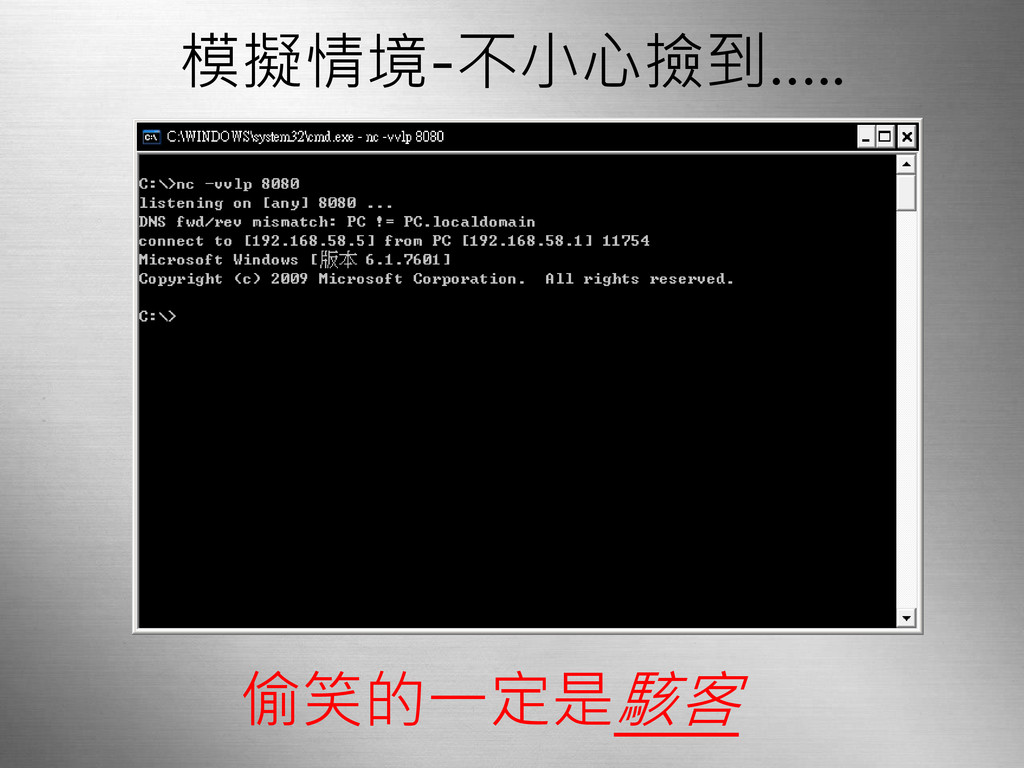
模擬情境-不小心撿到….. 偷笑的一定是駭客
None
一秒變格格
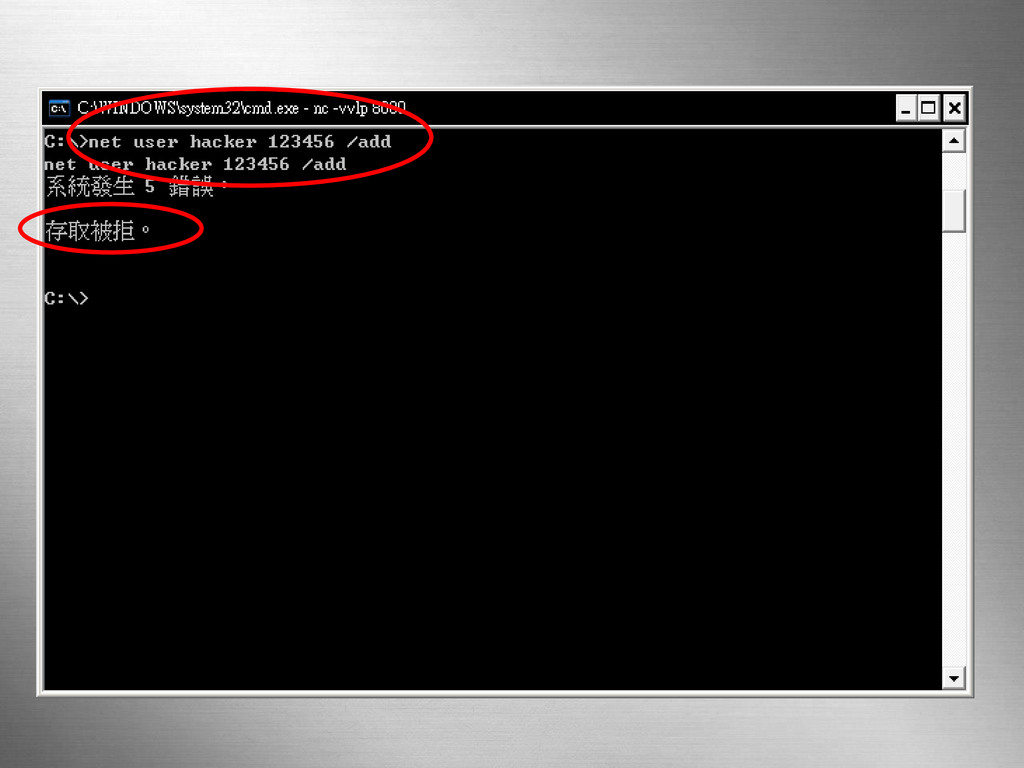
Demo 一秒變Admin
第二件事
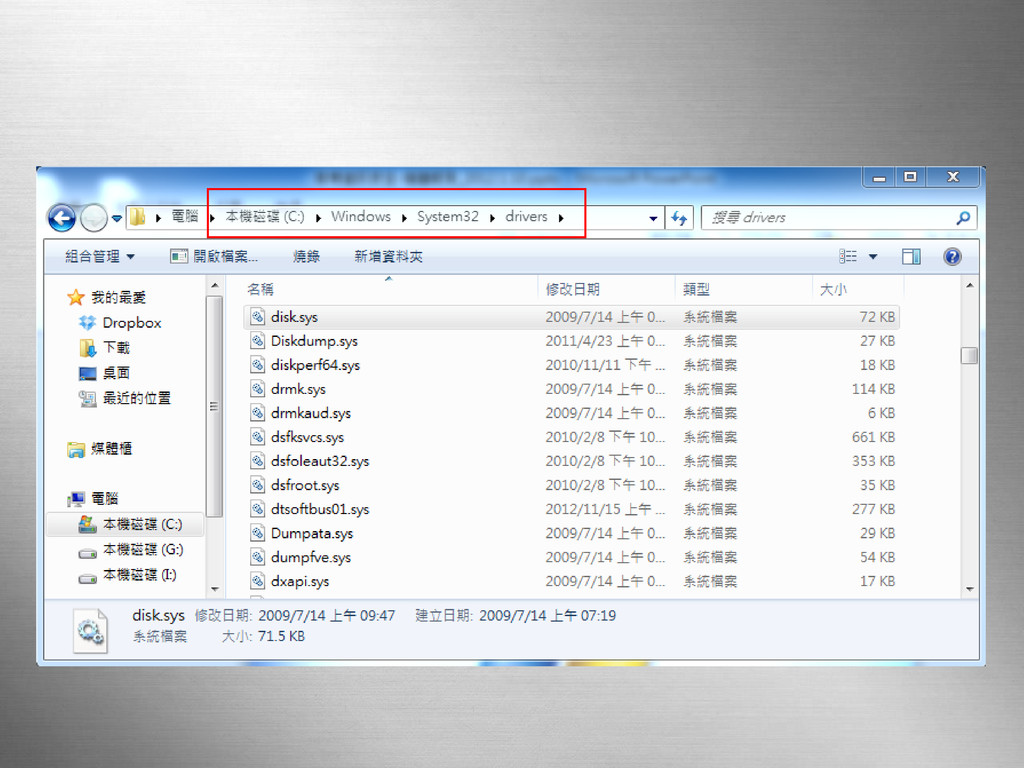
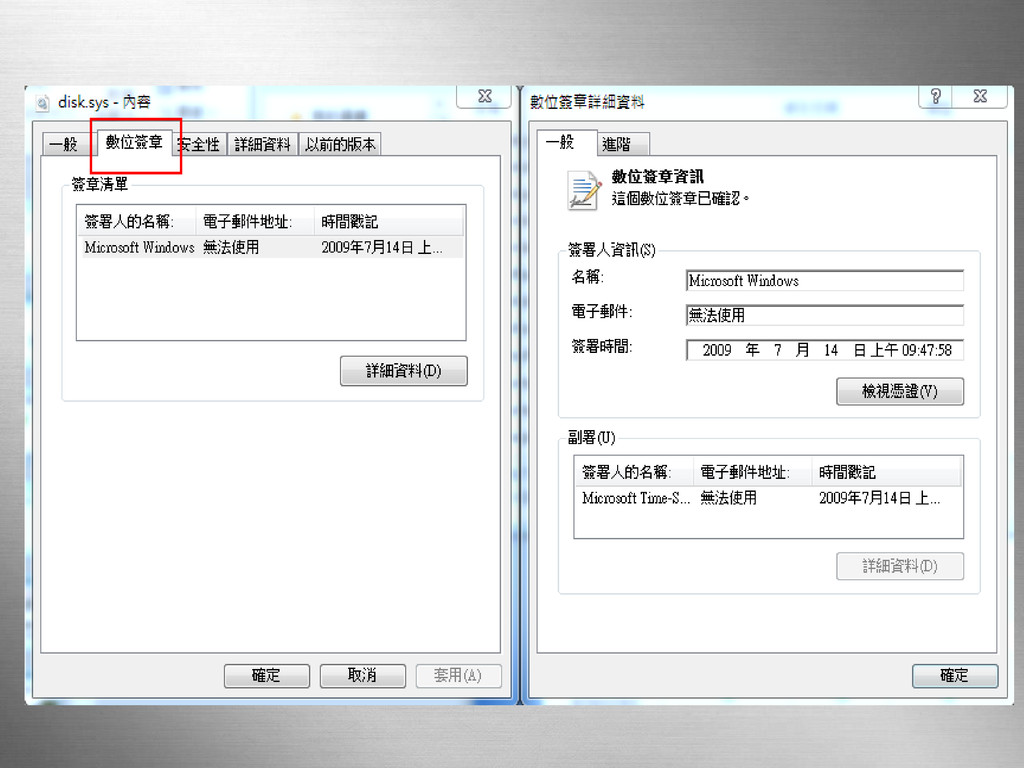
Driver數位簽章
None
None
None
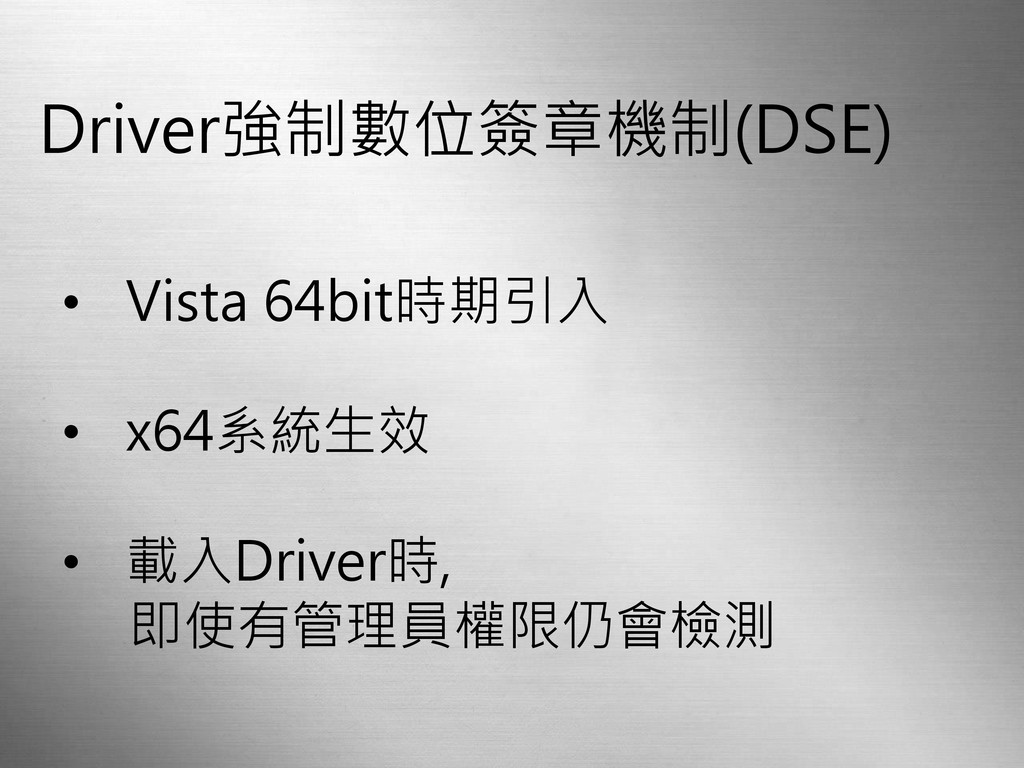
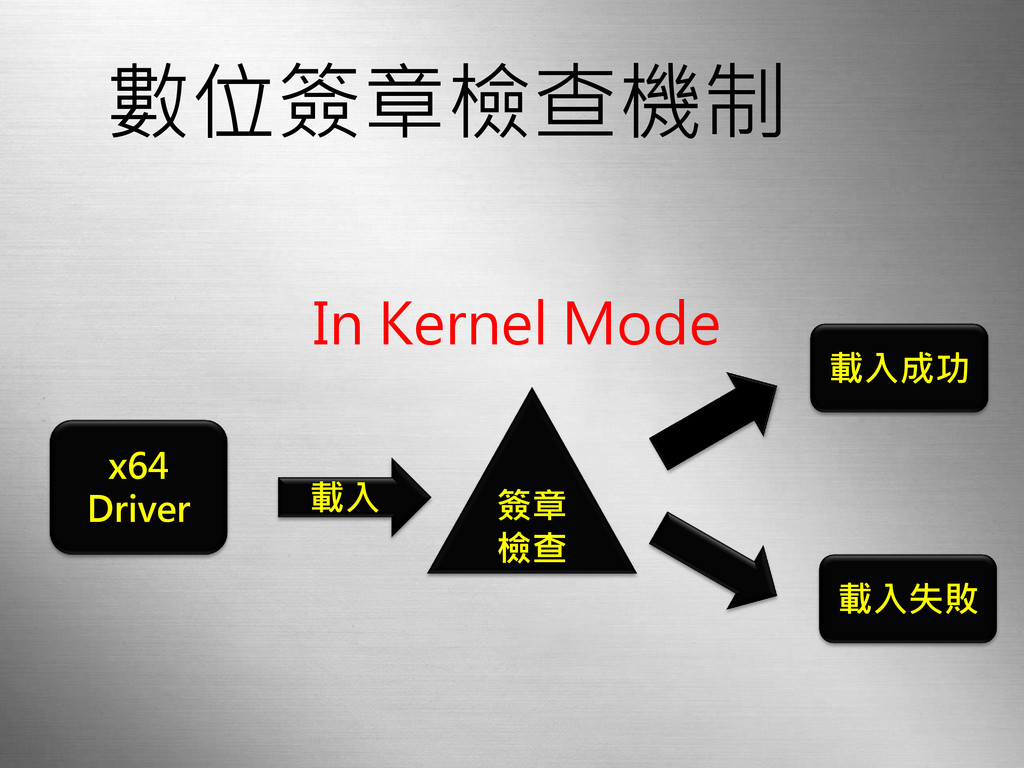
Driver強制數位簽章機制(DSE) • Vista 64bit時期引入 • x64系統生效 • 載入Driver時, 即使有管理員權限仍會檢測
數位簽章檢查機制 In Kernel Mode x64 Driver 載入 簽章 檢查 載入成功
載入失敗
How to Bypass!?
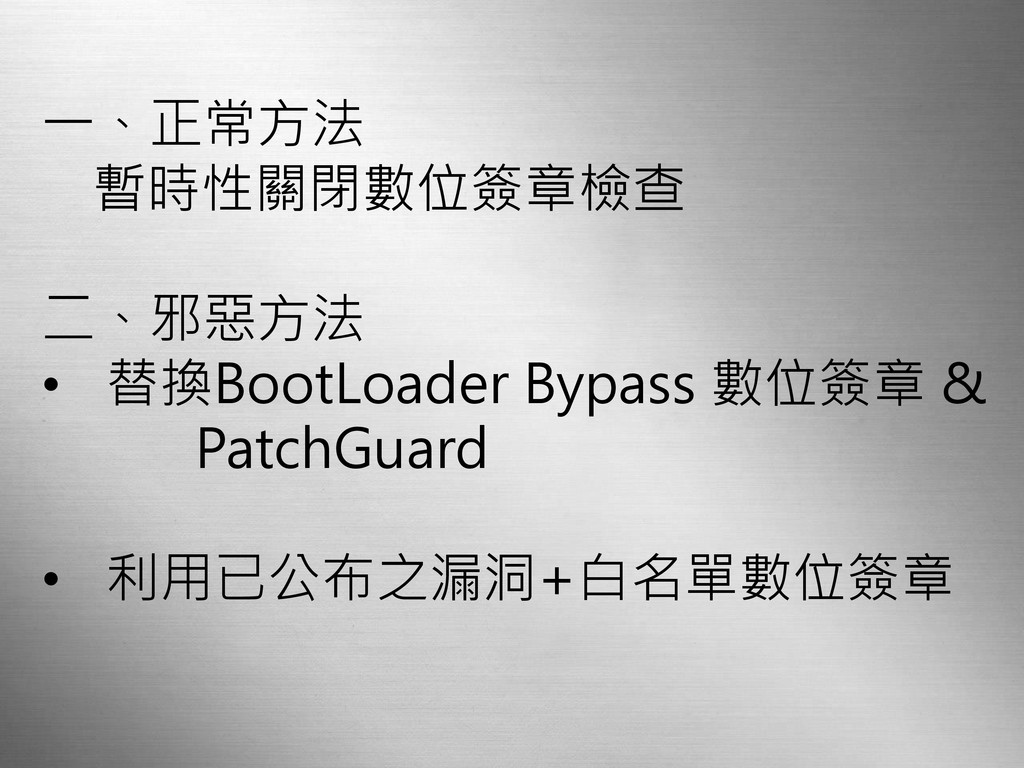
一、正常方法 暫時性關閉數位簽章檢查 二、邪惡方法 • 替換BootLoader Bypass 數位簽章 & PatchGuard •
利用已公布之漏洞+白名單數位簽章
None
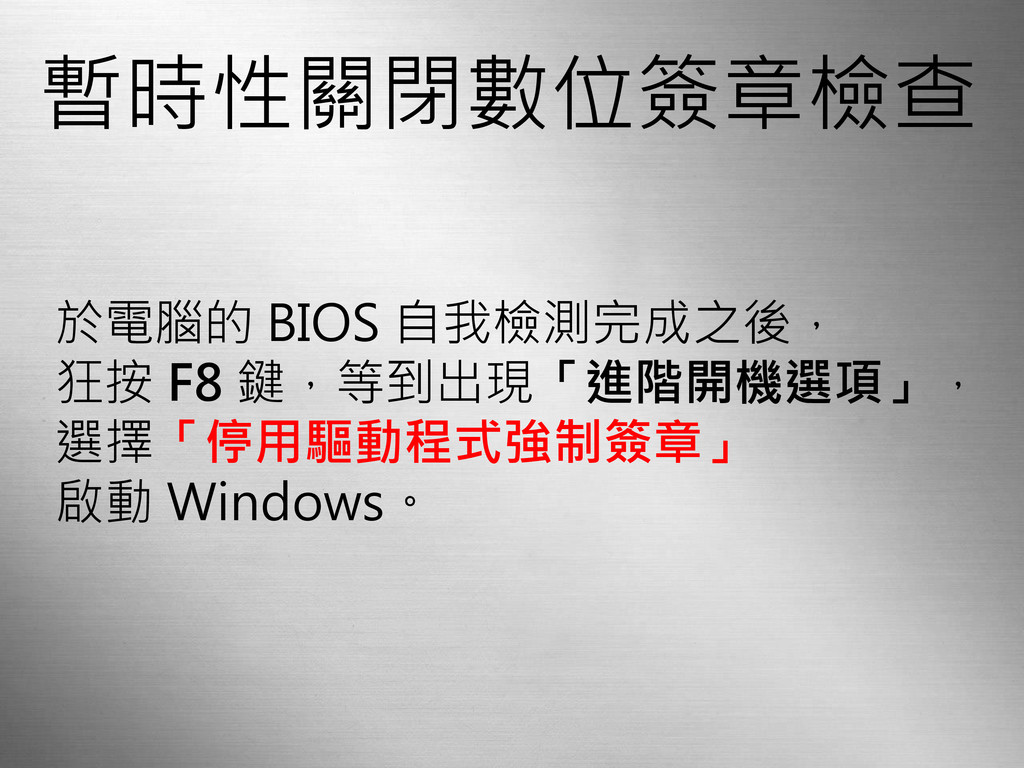
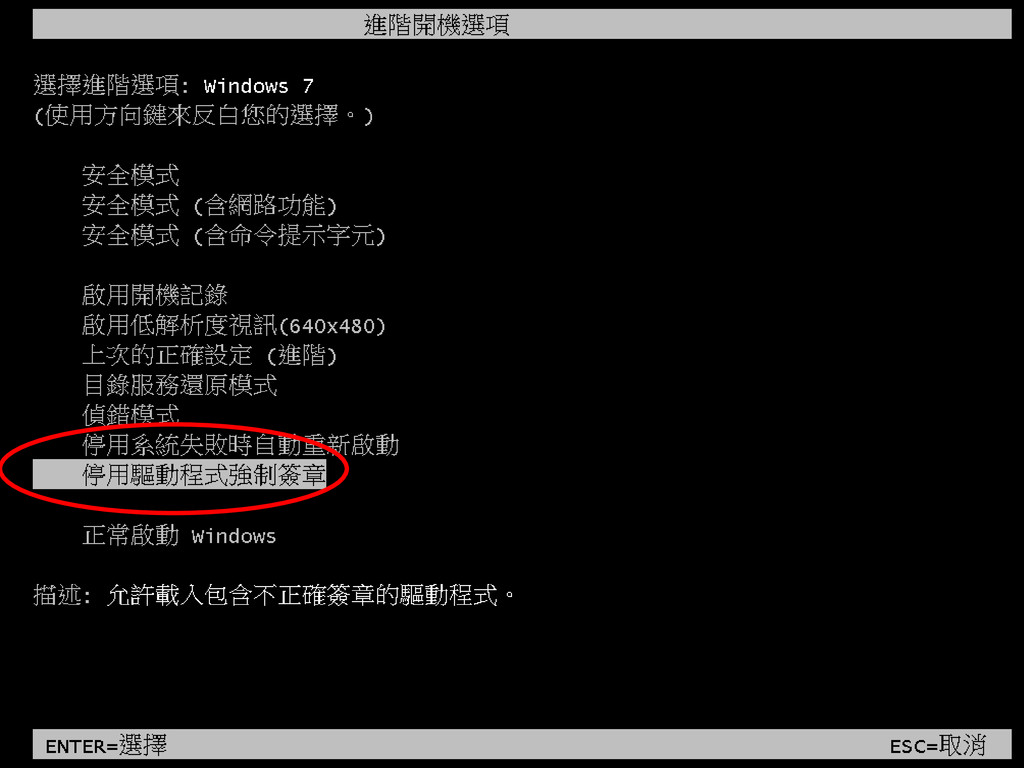
暫時性關閉數位簽章檢查 於電腦的 BIOS 自我檢測完成之後, 狂按 F8 鍵,等到出現「進階開機選項」, 選擇「停用驅動程式強制簽章」 啟動 Windows。
None
這叫
Binary Patch SystemFile 邪惡方法一
fyyre 2011/03/19 Reference http://fyyre.ivory-tower.de/
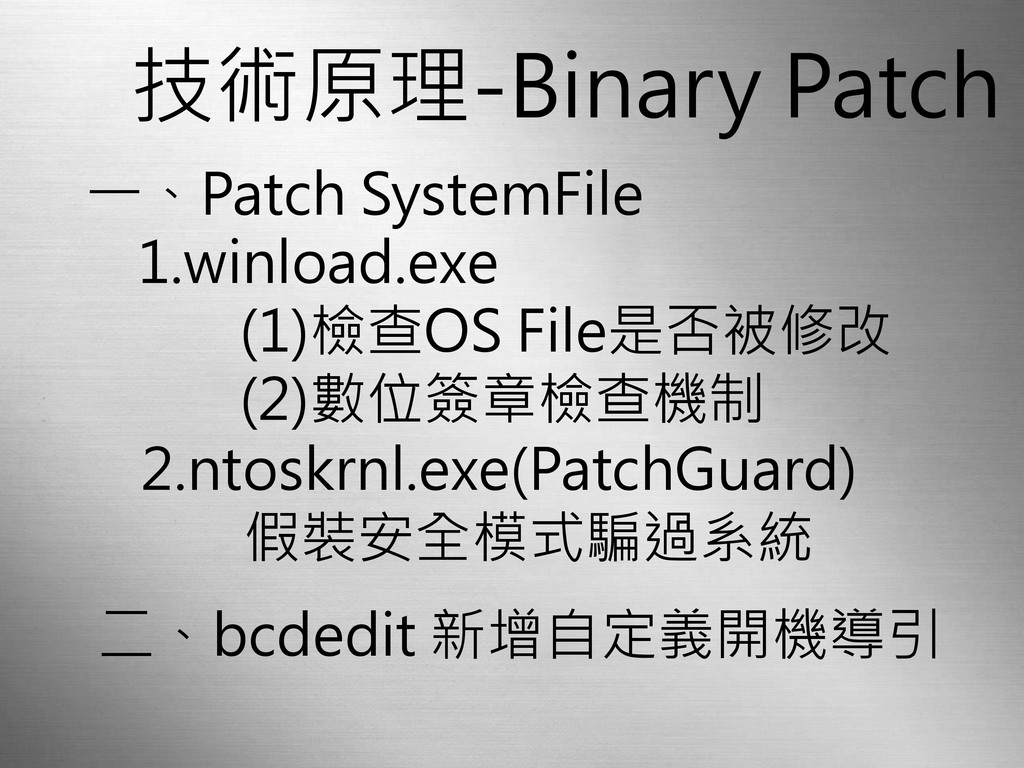
一、Patch SystemFile 1.winload.exe (1)檢查OS File是否被修改 (2)數位簽章檢查機制 技術原理-Binary Patch 2.ntoskrnl.exe(PatchGuard) 假裝安全模式騙過系統
二、bcdedit 新增自定義開機導引
None
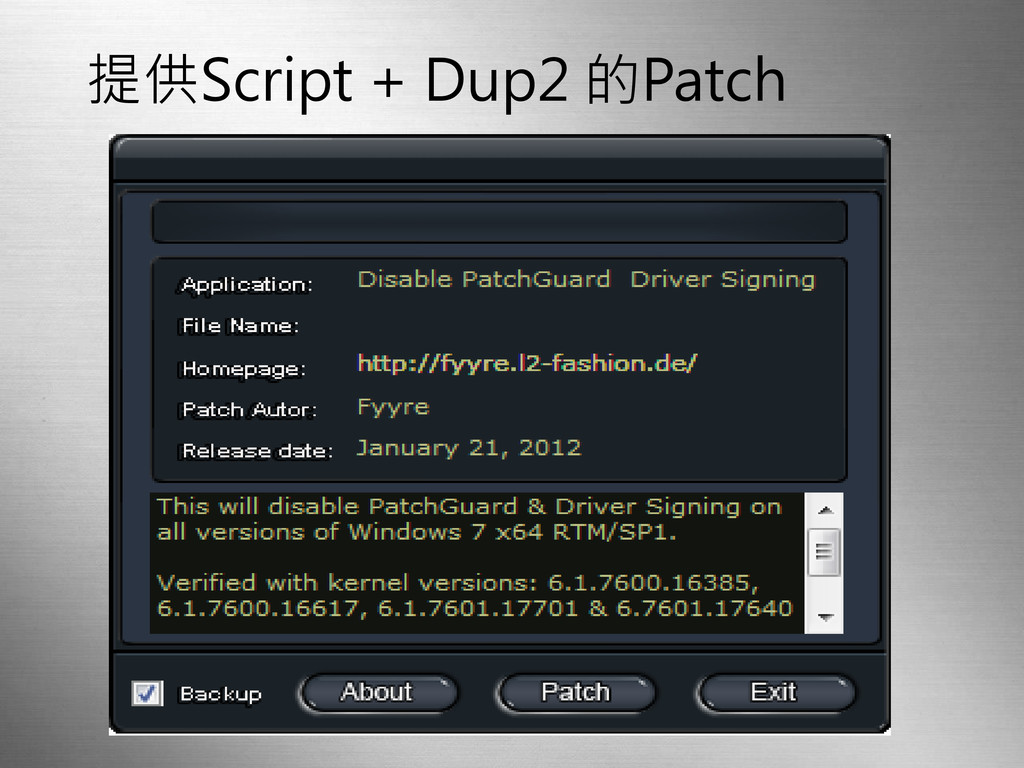
提供Script + Dup2 的Patch
缺點 一、動作太大,會被AV偵測 二、必須重開機才有效果!
邪惡方法二 利用已公布之漏洞 加上正式簽章Bypass
Reference http://j00ru.vexillium.org/?p=377 A quick insight into the Driver Signature Enforcement
j00ru 2010/06/19
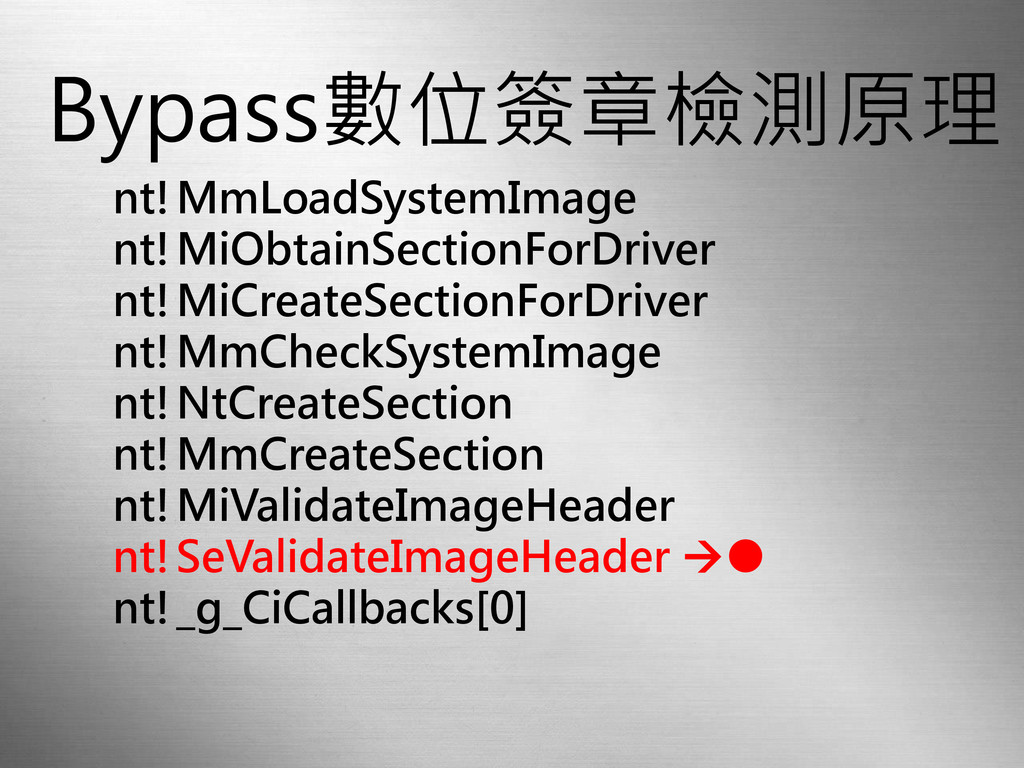
Bypass數位簽章檢測原理 nt!MmLoadSystemImage nt!MiObtainSectionForDriver nt!MiCreateSectionForDriver nt!MmCheckSystemImage nt!NtCreateSection nt!MmCreateSection nt!MiValidateImageHeader nt!SeValidateImageHeader •
nt!_g_CiCallbacks[0]
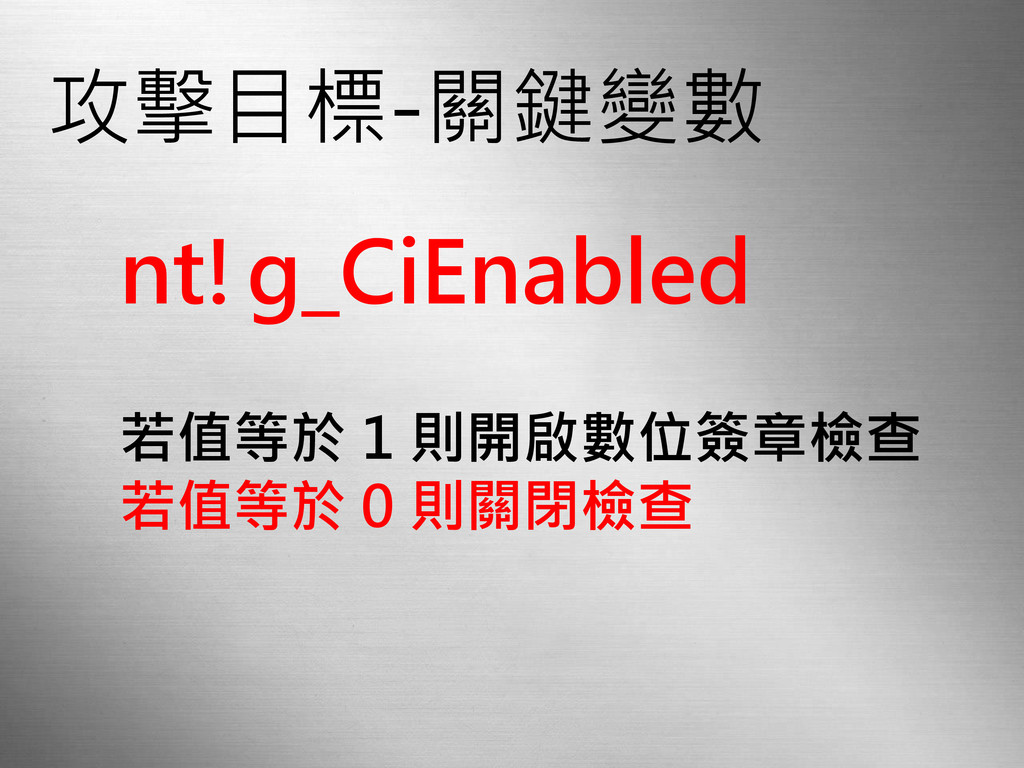
攻擊目標-關鍵變數 nt!g_CiEnabled 若值等於 1 則開啟數位簽章檢查 若值等於 0 則關閉檢查
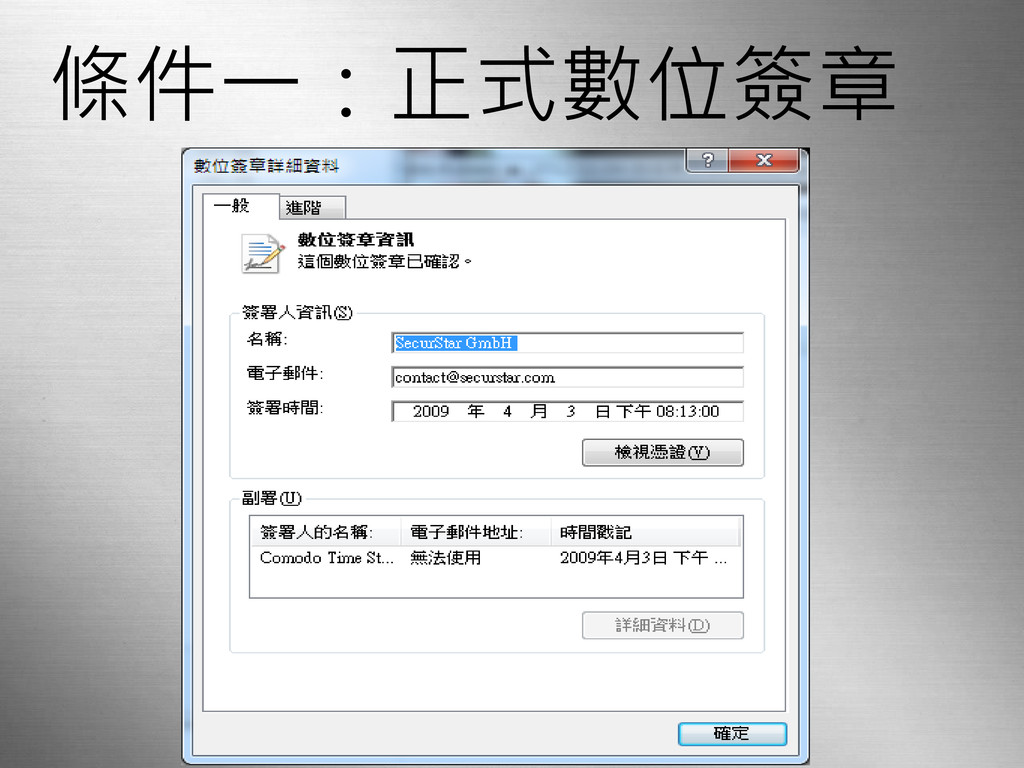
條件一:正式數位簽章
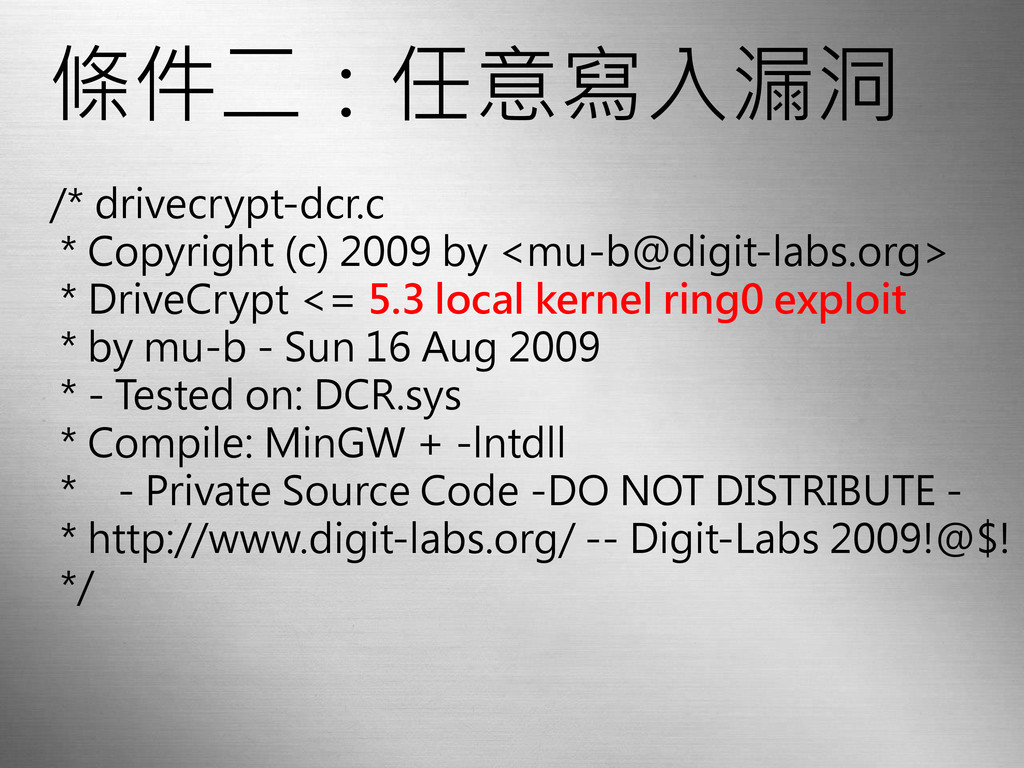
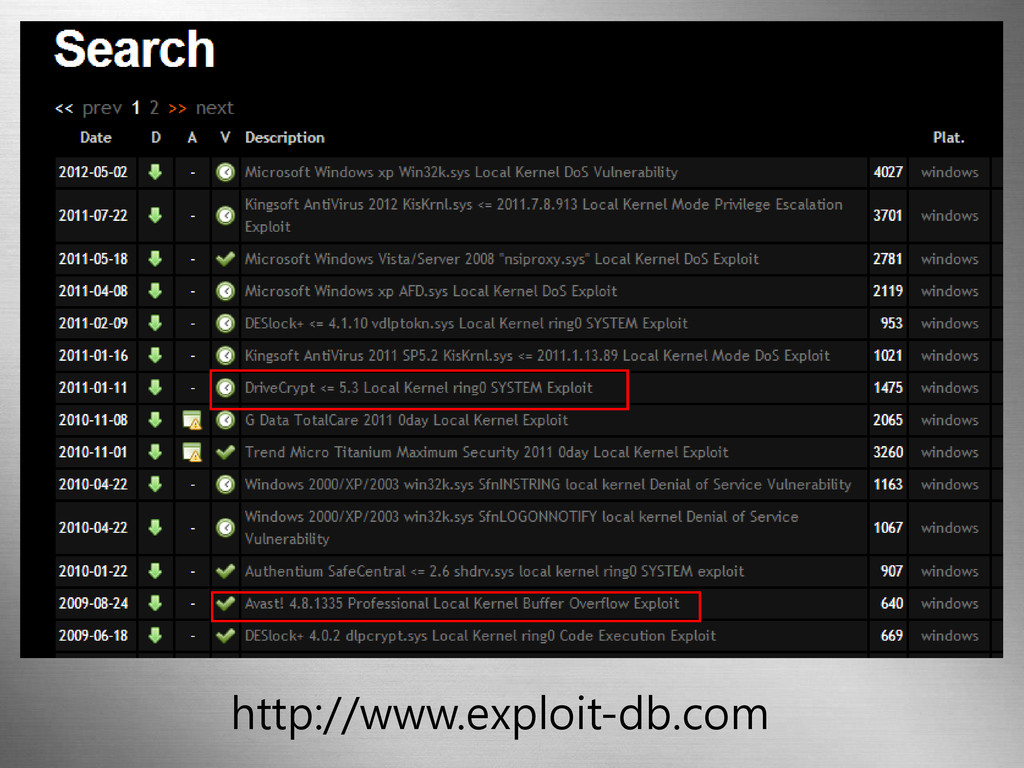
條件二:任意寫入漏洞 /* drivecrypt-dcr.c * Copyright (c) 2009 by <
[email protected]
> *
DriveCrypt <= 5.3 local kernel ring0 exploit * by mu-b - Sun 16 Aug 2009 * - Tested on: DCR.sys * Compile: MinGW + -lntdll * - Private Source Code -DO NOT DISTRIBUTE - * http://www.digit-labs.org/ -- Digit-Labs 2009!@$! */
Fuzz Exploit by yourself?
If I have seen further [than certain other men] it
is by standing upon the shoulders of giants. Isaac Newton
None
http://www.exploit-db.com
倚天劍(User mode 權限)
屠龍刀(Kernel Mode 權限)
第三件事
Kill AV
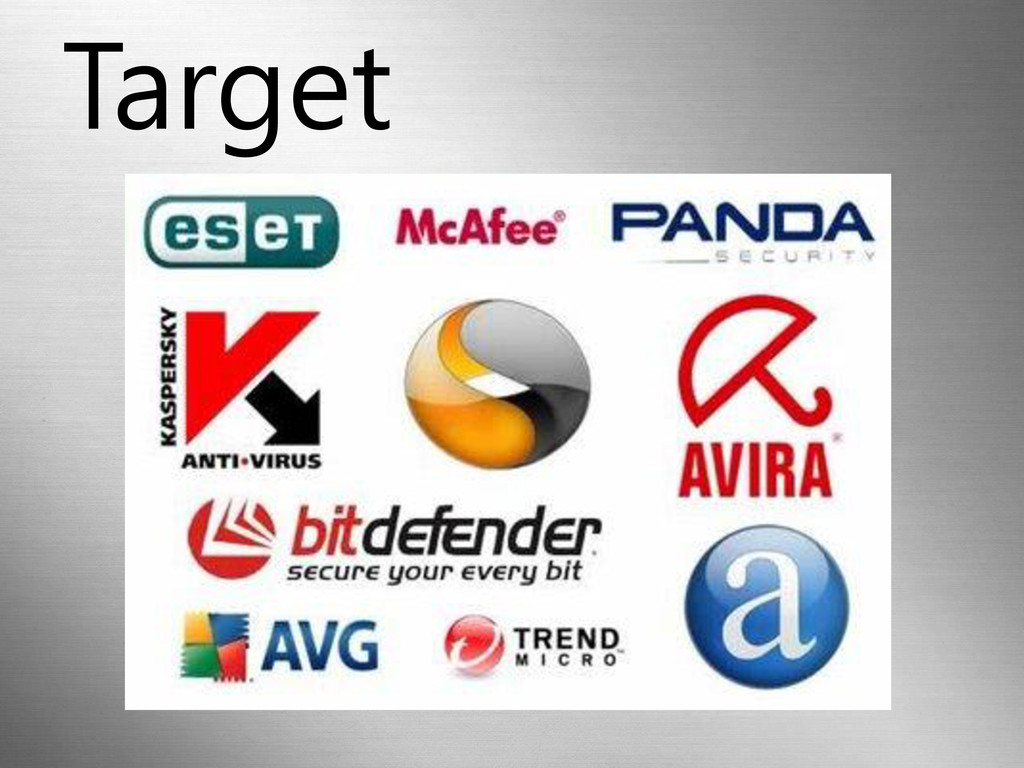
Target
How To Kill It !?
Kernel Hook in x86
But…
PatchGuard in X64
None
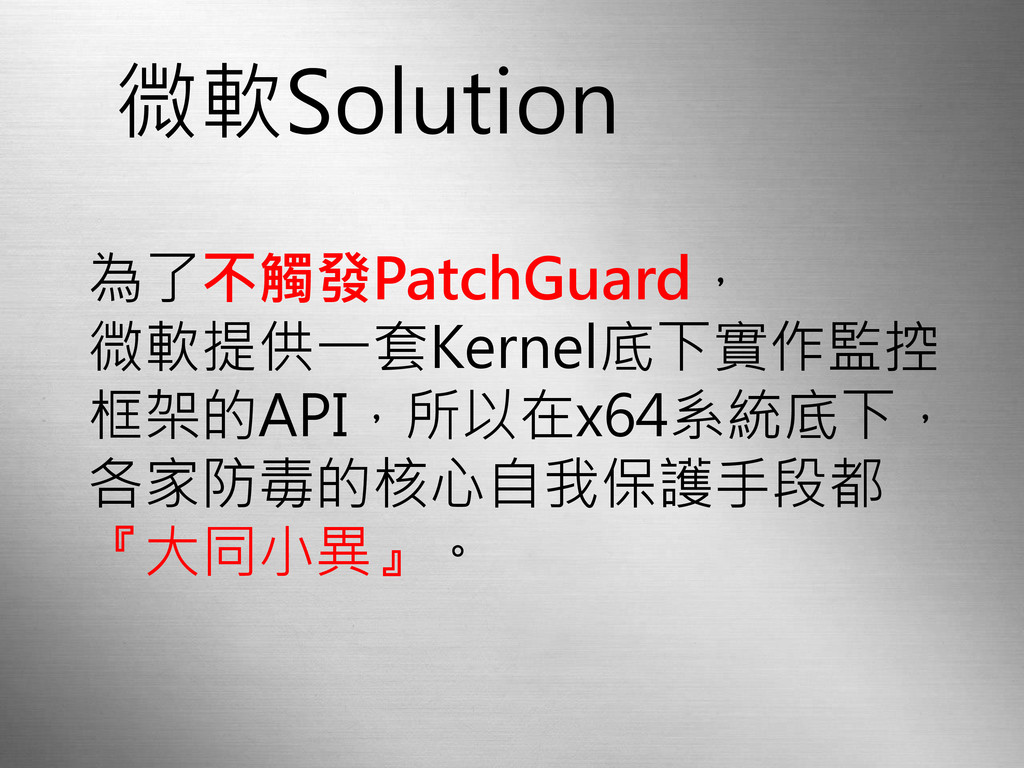
為了不觸發PatchGuard, 微軟提供一套Kernel底下實作監控 框架的API,所以在x64系統底下, 各家防毒的核心自我保護手段都 『大同小異』。 微軟Solution
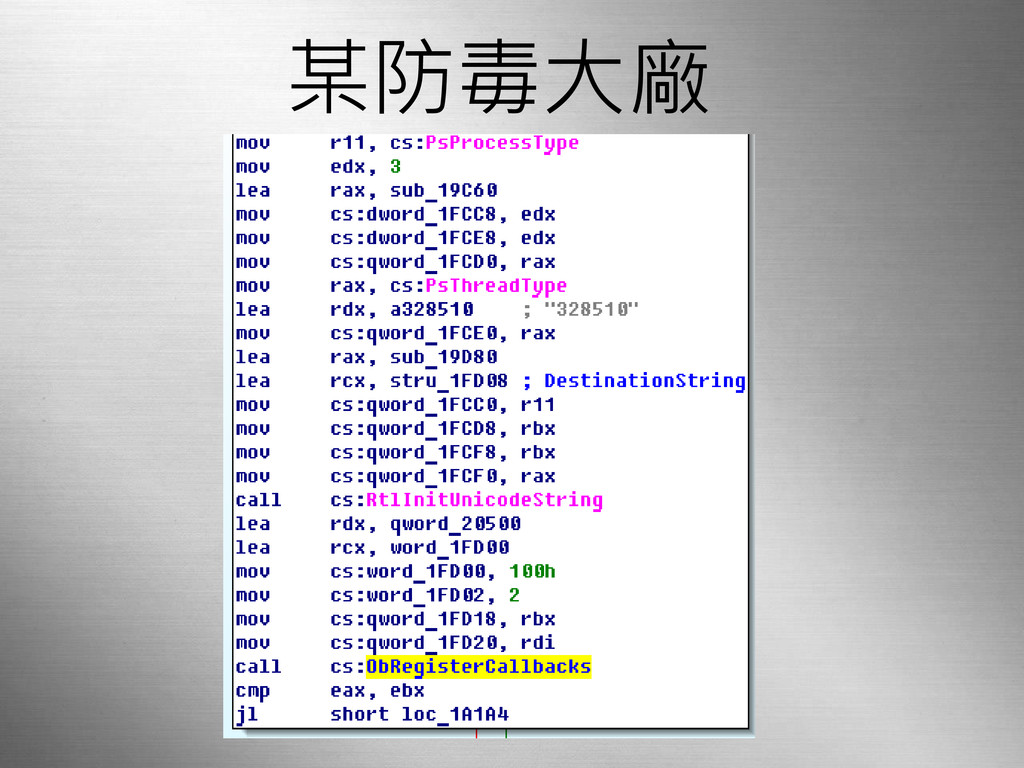
核心函數- ObRegisterCallbacks The ObRegisterCallbacks routine registers a list of callback
routines for thread and process handle operations. from MSDN
某防毒大廠
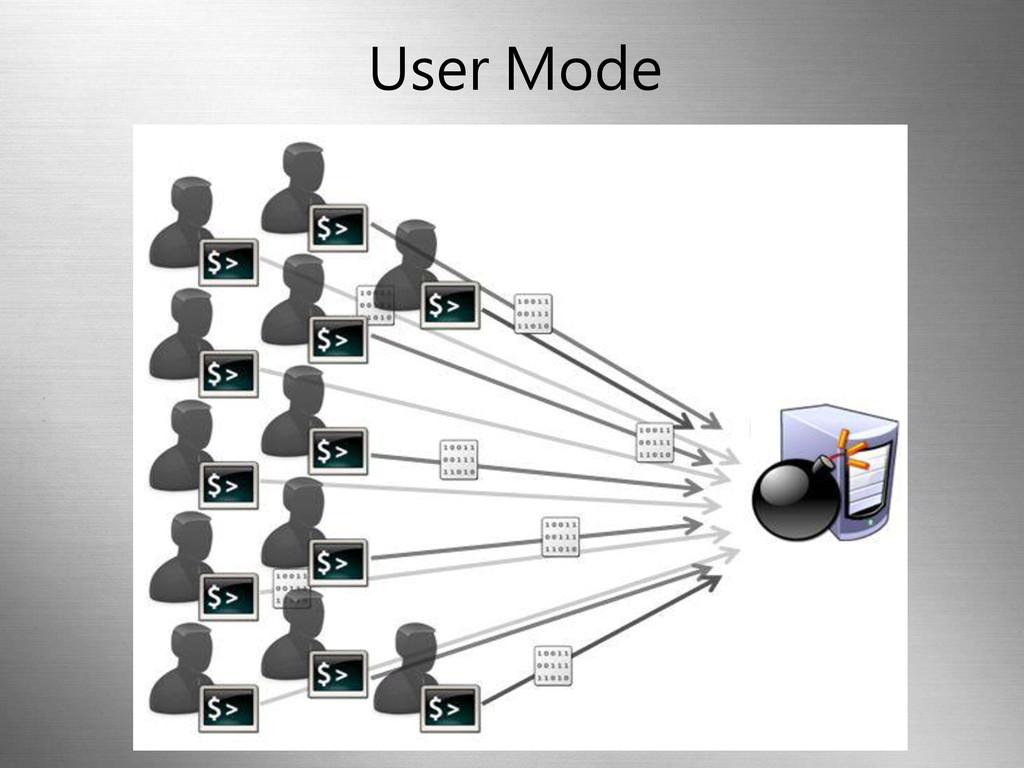
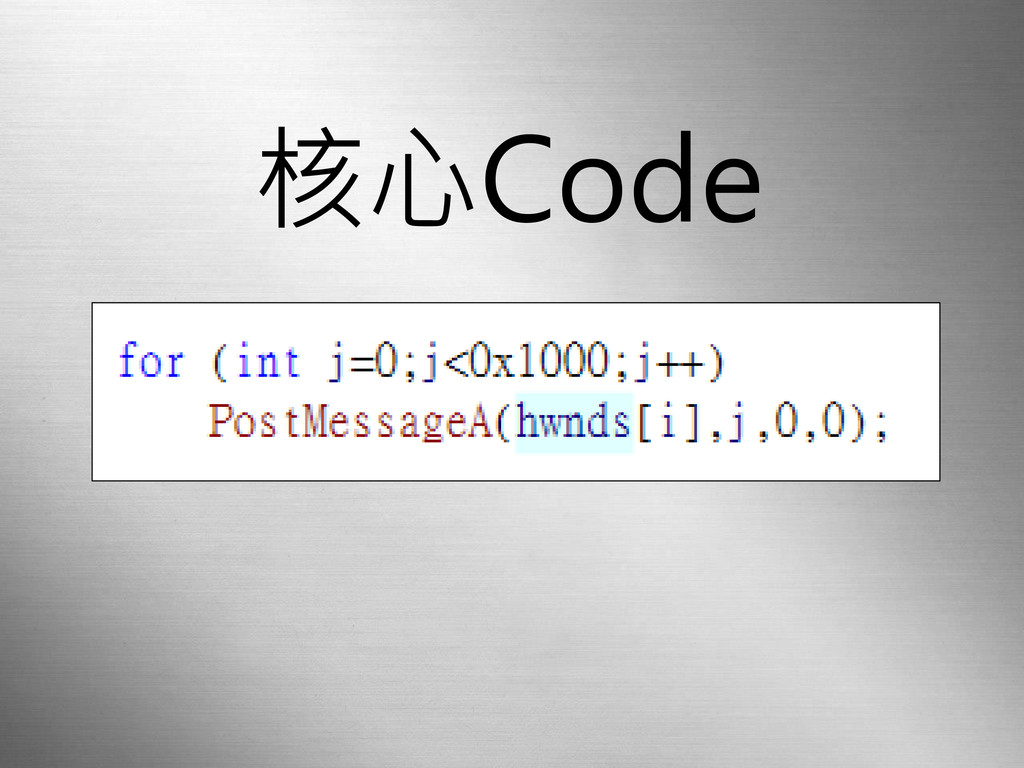
攻擊方法一 Message Flood
User Mode
核心Code
Demo
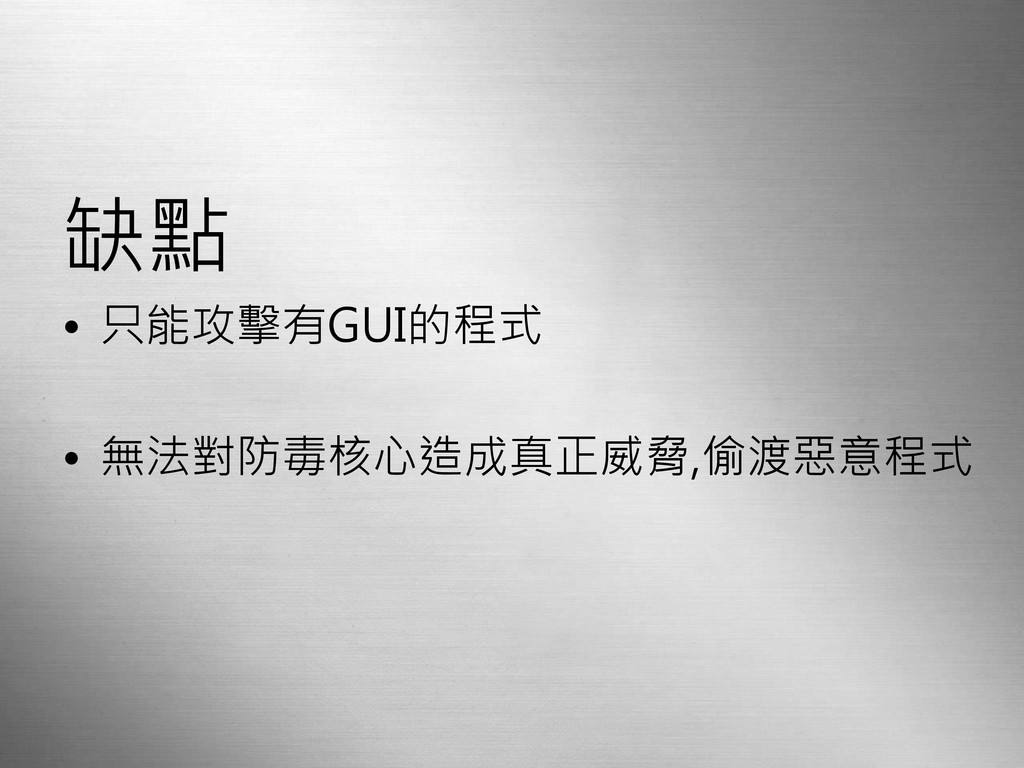
缺點 • 只能攻擊有GUI的程式 • 無法對防毒核心造成真正威脅,偷渡惡意程式
攻擊方法二
正式數位簽章 + KernelMode任意寫入漏洞
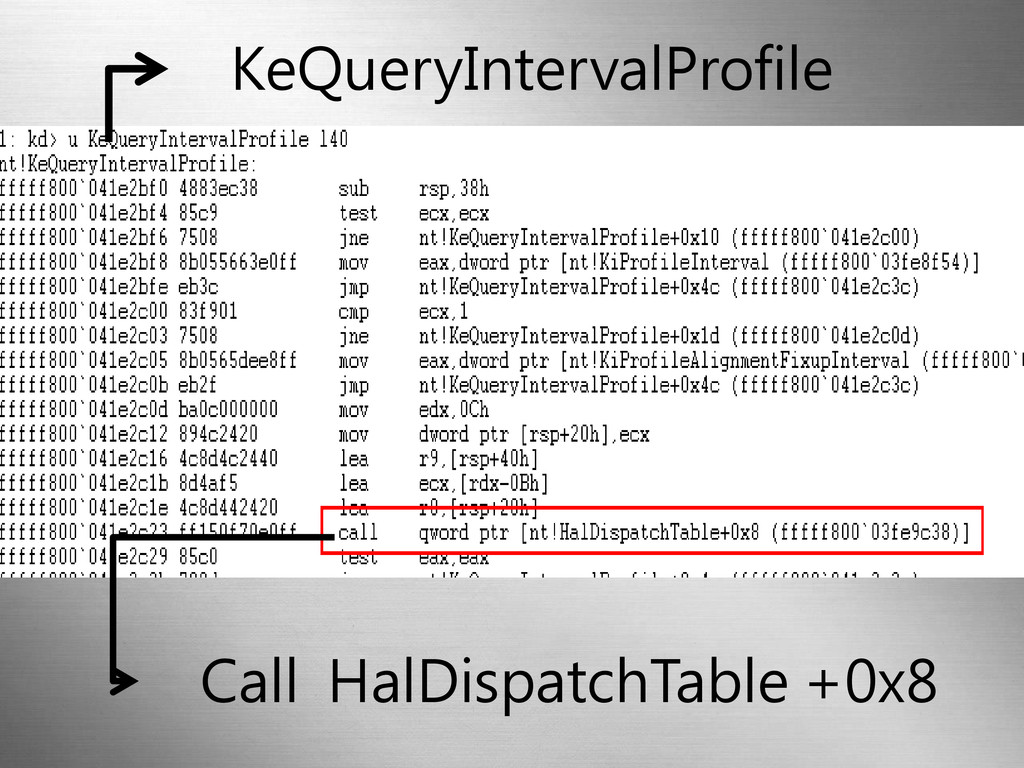
KeQueryIntervalProfile Call HalDispatchTable +0x8
Kernel ShellCode KeQueryIntervalProfile + HalDispatchTable + 0x8
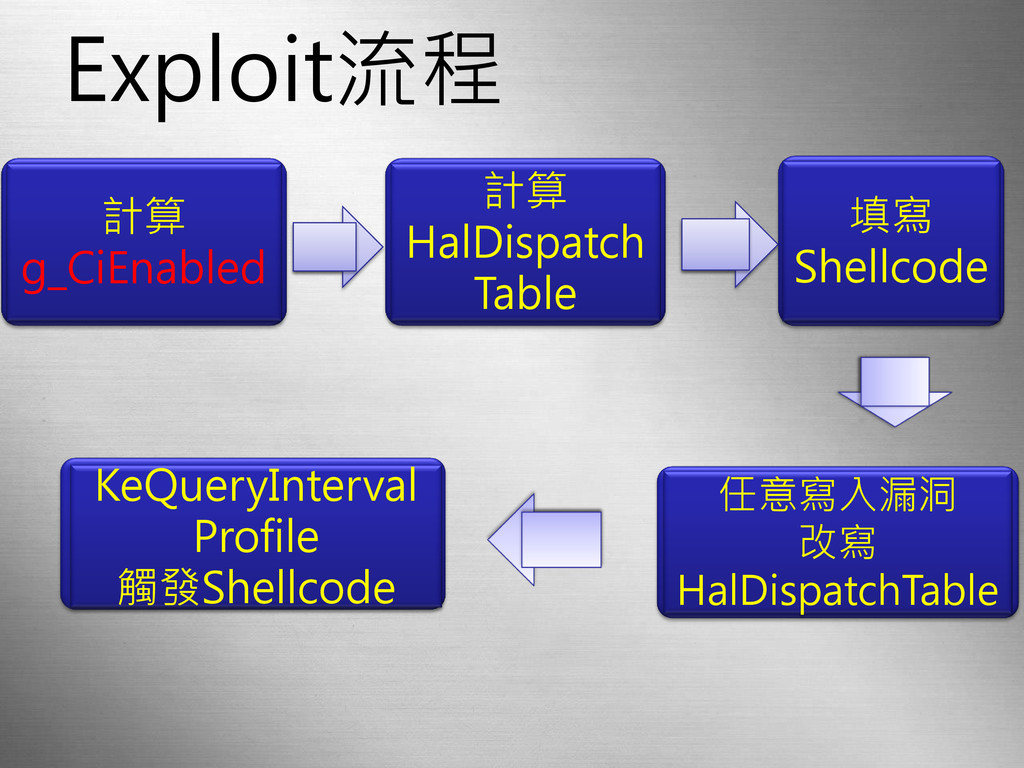
Exploit流程 計算 g_CiEnabled 計算 HalDispatch Table 填寫 Shellcode 任意寫入漏洞 改寫
HalDispatchTable KeQueryInterval Profile 觸發Shellcode
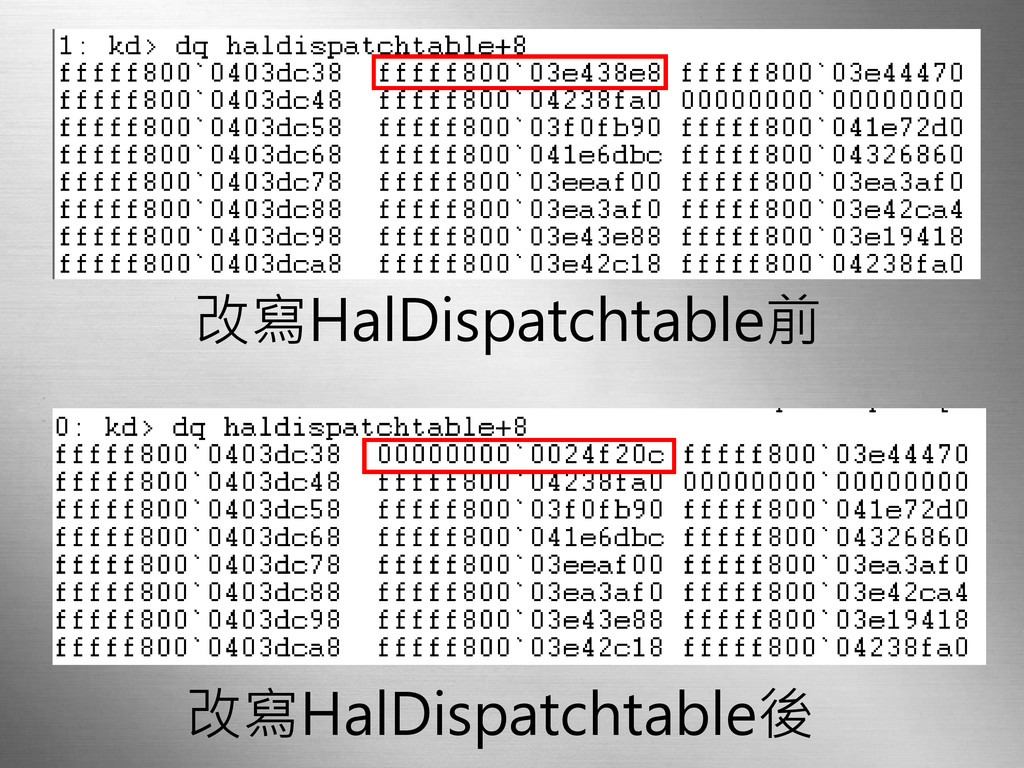
改寫HalDispatchtable前 改寫HalDispatchtable後
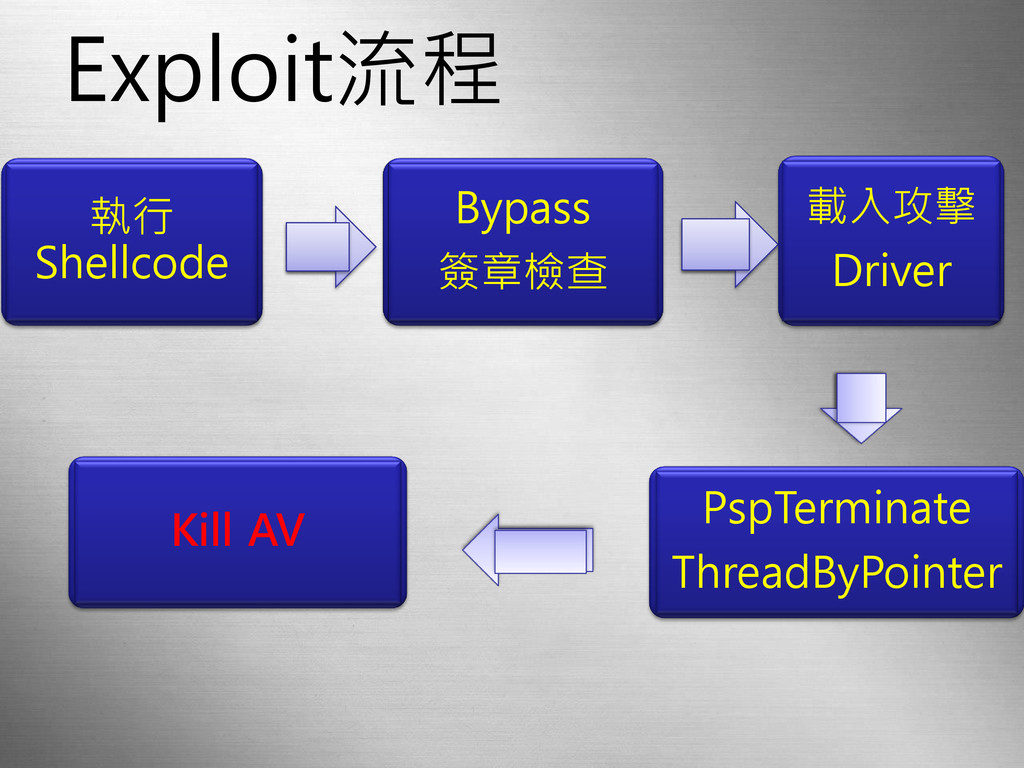
Exploit流程 執行 Shellcode Bypass 簽章檢查 載入攻擊 Driver Kill AV PspTerminate
ThreadByPointer
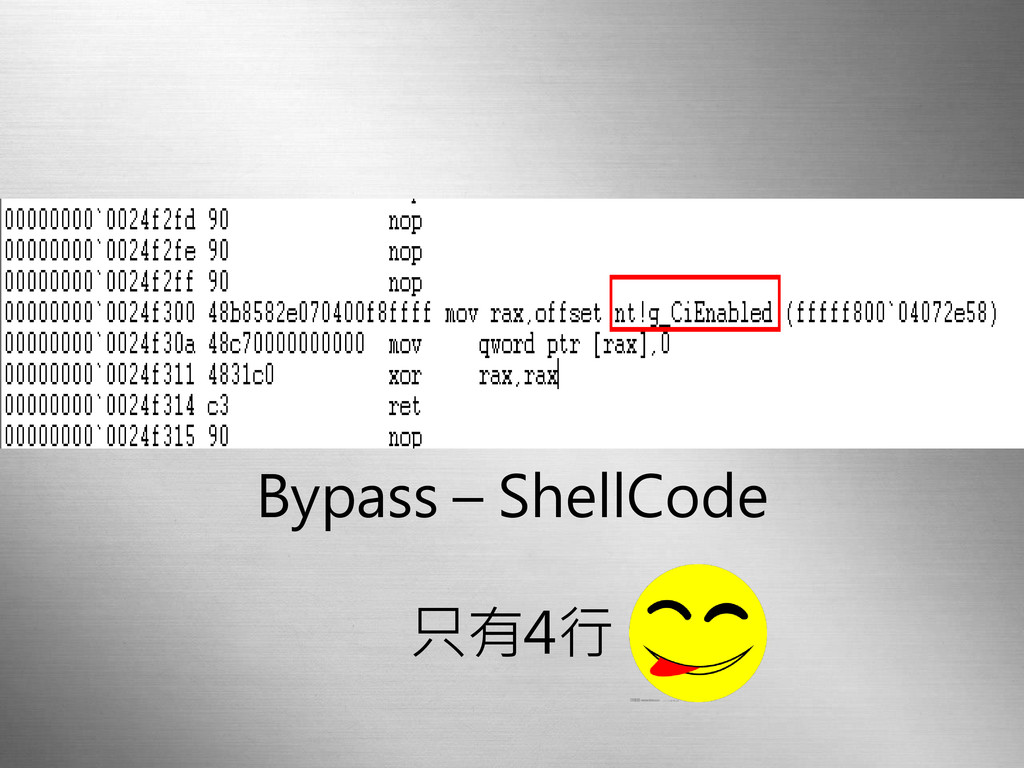
Bypass – ShellCode 只有4行
Live Demo Kill AV
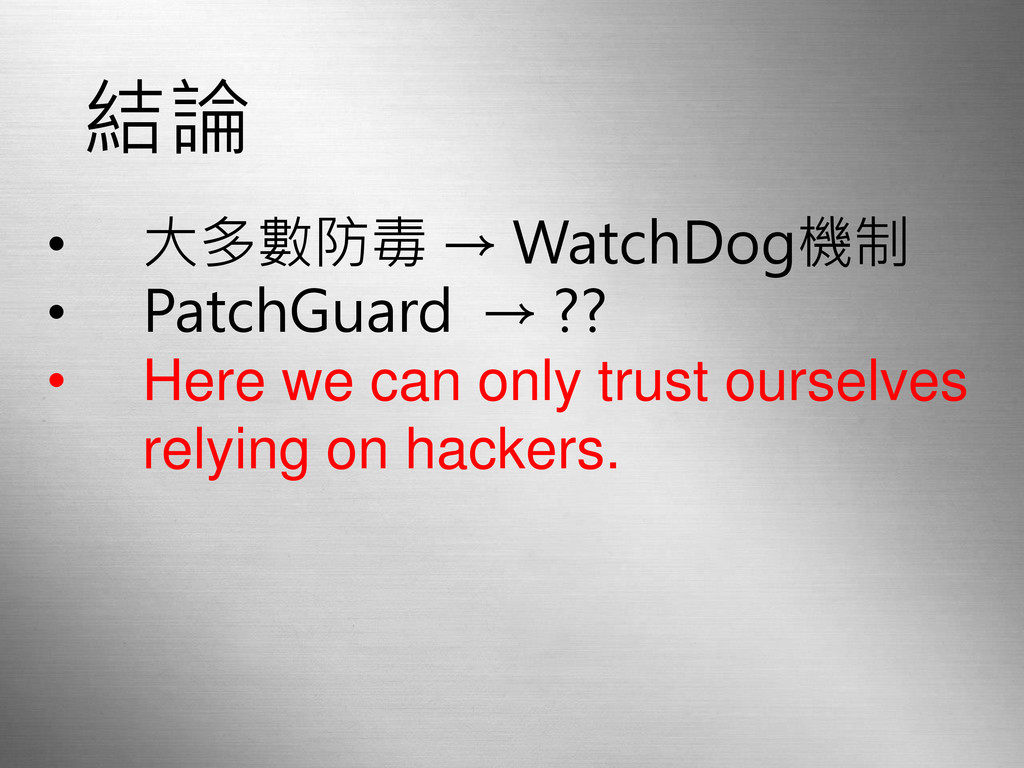
結論 • 大多數防毒 → WatchDog機制 • PatchGuard → ?? •
Here we can only trust ourselves relying on hackers.
Reference http://www.pretentiousname.com/misc/win7_uac_whitelist2.html http://fyyre.ivory-tower.de/ http://www.powerofcommunity.net/poc2012/mj0011.pdf
Reference http://echopakistan.com/wp-content/uploads/2013/04/windows8_logo_by_dracu_teufel666- d5n43o6.jpg http://stickmanlordsweb.webs.com/maddness%20kill.gif http://ext.pimg.tw/sana217/1368109769-1436612722.jpg http://zh.wikipedia.org/wiki/%E8%89%BE%E8%90%A8%E5%85%8B%C2%B7%E7%89%9B%E9%A1%BF http://1.bp.blogspot.com/- k2AluoKtRRg/TwcZ_F1P4kI/AAAAAAAAACU/jz4FXhTdQOE/s640/%25E7%2589%25A9%25E7%2590%25 86111%25E7%258F%25AD%25E5%25BE%25BD- %25E5%25BE%2590%25E9%259D%2592%25E9%259D%2592.jpg
http://www.jsswordshop.com/images/upload/Image/IMG_7258.jpg http://img0.pengfu.cn/big/36/3036.jpg http://www.giddens.tw/blog http://pic5.nipic.com/20100126/7971_151429039628_2.jpg http://soobahkdo.biz/wp-content/uploads/2011/02/easy-button-350x350.jpg http://i.imgur.com/nHIAq.jpg http://pic1.duowan.com/news/1204/198857478824/198857478830.jpg http://farm3.static.flickr.com/2096/1873199072_9c5f12a621.jpg http://www.guten-morgen-voyager.de/portal/images/flatto/dasbild/mission_impossible.jpg http://img1.guokr.com/gkimage/xa/th/ya/xathya.jpg http://img1.guokr.com/gkimage/6e/dj/1m/6edj1m.jpg http://imgs.caraq.com/UploadData/fck/image/192/19278/%E4%B8%80%E6%93%8A%E5%BF%85%E6%A E%BA.jpg http://www.nydailynews.com/img/2008/07/15/gal_allstar-derby_1.jpg
None


 keeg
 carta_engineering
 willnet
 ykanoh
 syuchimu
 hiracky16
 pfn
 ishikawa_satoru
 riyaamemiya
 greenmidori
 yuuuuuuu168
 ivry_presentationmaterials
 aemeredith
 axbom
 paigeccino
 tmiket
 rabernat
 aleyda
 addyosmani
 destraynor
 badams
 sergeychernyshev
 sugarenia
 lfama